The CPG Guys Want to Build a Business Bigger Than Podcasts
The podcasters have acquired executive groups and plan to launch a second show. https://www.adweek.com/commerce/the-cpg-guys-want-to-build-a-business-bigger-than-podcasts/
The podcasters have acquired executive groups and plan to launch a second show. https://www.adweek.com/commerce/the-cpg-guys-want-to-build-a-business-bigger-than-podcasts/
The agency will lead shopper and in-store marketing for Jameson, Absolut, and Kahlúa. https://www.adweek.com/commerce/pernod-ricard-usa-hires-vml-as-commerce-agency-of-record/
The retail firm is undergoing its first makeover since launching in 2012. https://www.adweek.com/commerce/tech-unicorn-mirakl-gets-a-rebrand-for-the-ai-age/
Its multi-agent AI platform generates the telemetry an attack would produce to fix gaps in enterprise defenses.
The post Brava Security Emerges From Stealth With $15 Million in Funding appeared first on SecurityWeek.
https://www.securityweek.com/brava-security-emerges-from-stealth-with-15-million-in-funding/
An Estonian newspaper recently revealed that a British soldier disobeyed a direct order to remove the SIM card from his cellphone before being deployed to a part of Estonia, approximately 90 miles west of the Russian border.
As a result of his refusal to engage in this element of operational security (opsec), the soldier, Daniel Barton-Kennedy, had his phone hacked, and nude photos of himself were stolen and used as blackmail against him.
Eventually, Barton-Kennedy was court-martialed for disobeying a lawful command, pled guilty, was reduced in rank, and ordered to serve 10 months in detention.
https://arstechnica.com/security/2026/11/british-soldier-ignored-order-to-pull-his-sim-card-then-got-blackmailed/
SonicWall has patched a SonicOS vulnerability that can be used to bypass SAML authentication, warning customers that it may have been exploited in attacks.
Tracked as CVE-2026-19868, the flaw affects the SSL VPN component of SonicOS, the operating system that runs on SonicWall firewalls. It’s one of seven vulnerabilities described in an advisory published on November 6.
“An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate authentication method to bypass SAML authentication controls. Successful exploitation may also bypass SAML-enforced multi-factor authentication (MFA),” reads SonicWall’s description of CVE-2026-19868.
According to the vendor, an SSL VPN is exposed only if SAML-based login is enabled. CVE-2026-19868 has a CVSS score of 7.1, which puts it in the high-severity range. The flaw was reported by Ryan Harris of The Electronic Office.
SonicWall said its product security team “has investigated a report indicating potential exploitation of this vulnerability.”
CISA added CVE-2026-19868 to its Known Exploited Vulnerabilities (KEV) catalog on the same day. Under Binding Operational Directive 26-04, federal agencies must address it by November 20.
Neither the vendor nor CISA has shared any details about the suspected attacks. It’s also unclear whether the flaw was exploited as a zero-day, before a patch became available.
Impacted devices include Gen7 TZ, NSa, NSsp and NSv firewalls with SonicOS 7.3.3-7015 or older. Gen8 TZ, NSa and NSv firewalls with SonicOS 8.2.2-8015 or older are also affected.
SonicOS versions 7.3.4-7013 and 8.2.3-8015 resolve the issue, and there are no workarounds. “Customers are strongly urged to upgrade to the latest release as soon as possible to mitigate the associated risks,” SonicWall said.
SonicWall’s advisory doesn’t mark any of the other six flaws as exploited. Two of them, each with a CVSS score of 8.8, affect the SonicOS management interface. One is a permissive cross-domain policy issue and the other is a session validation bug.
Under certain circumstances, a remote attacker could abuse either one without logging in to take unauthorized actions.
Three of the remaining flaws are pre-authentication buffer overflows in the SSL VPN service and the TACACS+ authentication client. Attackers could use them to launch DoS attacks at the application level.
The last one is a weak password hashing issue in virtual appliances. An attacker who already has high-privileged local access could exploit it to obtain a platform credential, which gives access to some of the platform’s settings.
Threat actors often exploit SonicWall product vulnerabilities. CISA’s KEV catalog currently includes 20 security holes, but the agency has yet to add CVE-2026-102255, which hackers started targeting last month, just days after its disclosure.
Related: Cisco, WatchGuard Release Patches; SonicWall Won’t Fix GMS Flaws
Related: SonicWall Warns of Two SMA1000 Zero-Days Exploited in Attacks
Related: SonicWall and Splunk Patch Critical Vulnerabilities
https://www.securityweek.com/sonicwall-patches-exploited-sonicos-bug-that-weakens-vpn-logins/
Blockchain analysis firm Chainalysis said that hackers have obtained sensitive personal information—including names, usernames, password hashes, and live tokens—for all of its users following a breach of its network security.
The accomplishment could be a major coup for the attackers. Both Chainalysis and public sources have revealed a long list of high-profile customers, including government agencies such as the FBI, US Immigration and Customs Enforcement agency, and the US Air Force, as well as private companies such as Microsoft, Coinbase, and Barclays. It’s unclear if the data theft exposed customers to additional threats.
Last Friday, Chainalysis said it had been the target of a cybersecurity incident in October that was similar to the hacks of other platforms during the same month. The external actor used AI agent-assisted offensive techniques to gain unauthorized access to Chainalysis systems and internal tools. An email the company sent to affected customers said some “non-sensitive customer data, such as user IDs, full names, email addresses, and organization role labels for users provisioned on our platform were accessed.” It’s not clear why the company considered such information “non-sensitive.”
https://arstechnica.com/security/2026/11/chainalysis-says-hackers-stole-credentials-and-tokens-for-all-of-its-customers/
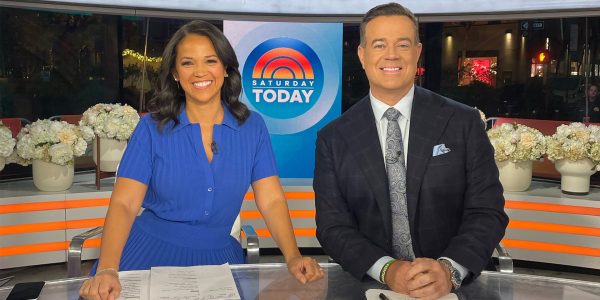
Top of the Ticker: NBC News has named Carson Daly the co-anchor of Saturday Today, beginning Saturday, November 7. Daly will continue his weekday role, expanding his duties at NBC News to six days a week.
“I’m thrilled to add Saturday Today to my weekday morning schedule,” said Daly, who will join co-anchor Laura Jarrett, feature anchor Joe Fryer, and meteorologist Angie Lassman.
Daly, who joined Today as host of the Orange Room in 2013, fills the void left by Peter Alexander, who left the program in March and later left NBC News after more than 20 years to join MS NOW.
Revolving Door: CNBC announced it has signed a new long-term agreement with Jim Cramer, which includes launching a premium subscription tier of his CNBC Investing Club in 2027.
The business network also recently announced some executive moves affecting its dayside programming and editorial operations.
Vice president of programming and senior executive producer Todd Bonin will now lead Business Day from 5 a.m. to noon ET. Sandy Cannold, vp of programming and sep will now oversee the network’s programming from noon to 6 p.m. ET.
Meanwhile, Jason Gewirtz moves to the Digital Control Room, while Anne Tironi will continue to oversee Squawk Box and Lisa Villalobos will manage all three hours of Squawk on the Street. Both will report to Bonin. In addition to leading Closing Bell: Overtime, Maria Boden will take on Fast Money. Matt Quayle will move from sep of The Exchange and Power Lunch to a new role focused on content development across platforms.
On the newsgathering and reporting front, Lacy O’Toole, vp and managing editor, will also add the network’s Specials unit to her docket. All correspondents will now report directly to O’Toole, except those aligned with the strategic verticals led by Max Meyers. In addition, correspondents based in Washington, D.C. and San Francisco will report to MC Wellons and Christina Passariello, respectively. Finally, CNBC’s Investigations unit will fall under the purview of Ken Brown, with Scott Zamost and Paige Tortorelli reporting to him.
Brand refresh: MS NOW has introduced a new brand campaign titled “Now There’s More That Unites US.” The network says this campaign was inspired by “the groundswell of participation, with millions of individuals making their voices heard, standing up for what they believe in.”
CTV expansion: MS NOW also announced that its direct-to-consumer experience, MS NOW Membership, will now be accessible via connected TV platforms, including Roku, Apple TV, Samsung, Google TV, and Amazon Fire TV. Members will be able to watch MS NOW’s 24/7 live linear feed on a TV without a cable subscription, and can also watch full episodes of all of MS NOW’s programs, available on demand.
Stork deliveries: Fox News’ Peter Doocy and CNN’s Abby Phillip recently welcomed new additions to their respective families. Doocy welcomed his third child, Molly Kate Doocy, on October 22. Phillip welcomed her second child, Maxwell Elias Richardson, a late-October surprise born on Oct. 27.
https://www.adweek.com/tvnewser/ticker-carson-daly-named-saturday-today-co-anchor/
The emergency package comes after dozens of companies and government agencies were hit by unauthorized access to their systems and leaks of client data, prompting uneasiness across Japan.
The post Japan Announces Emergency Cybersecurity Package Following a Wave of Attacks appeared first on SecurityWeek.
https://www.securityweek.com/japan-announces-emergency-cybersecurity-package-following-a-wave-of-attacks/
A camera on a tower doesn’t physically stop a thief; it changes what they think will happen next.
https://www.securitymagazine.com/blogs/14-security-blog/post/102650-cameras-only-deter-people-who-believe-theyre-being-watched