Don’t Miss Our Live Webcast: A Look at the June Lightroom Updates
Adobe is releasing its June Lightroom updates this week, and we know you’re probably wondering, “What’s new, and should I be using it?”
That’s exactly what Scott Kelby will be covering in a FREE live webcast tomorrow, Thursday, June 18 at 3:00 pm ET.
Instead of digging through release notes or trying to figure everything out on your own, join Scott as he highlights the newest additions to Lightroom, shares some of his favorite features, and shows how they can fit into your everyday editing and organizing experience. Whether you use Lightroom every day or just occasionally, this is a fun and easy way to catch up on what’s new.
If you’ve been busy making photos instead of keeping up with updates, we’ve got you covered!
Ultimate iPhone Camera Tips and Tricks with Terry White
Your iPhone camera is packed with features that most people never use.
In his latest class, Terry White walks through the settings and tools that can make an immediate difference in your photography, showing not just where they are, but when to use them.
From customizing the Camera Button and choosing the right file format to mastering Night mode, long exposures, focus and exposure lock, and action photography, Terry covers the features that matter most on the iPhone 17 Pro running iOS 26. The result is a practical guide that helps you move beyond point-and-shoot photography and start making intentional creative choices with the device you already carry every day.
Whether you’re photographing family, travel, landscapes, or everyday moments, these tips can help you get more from every shot. Watch the class here.
Sebbene il numero di casi d’uso nel nostro Paese sia ancora molto basso, le previsioni di tutti gli esperti dicono che gli agenti AI diventeranno i veri “operati” dell’automazione dei processi in azienda. Il problema è che chi dovrà gestirne la sicurezza non ha ancora l’esperienza necessaria per farsi un quadro chiaro di come questi opereranno in concreto sulla rete interna, su quella esterna e sui client. Questa carenza di visione complica enormemente la creazione di una infrastruttura di sicurezza efficace.
In particolare, governare e proteggere un numero crescente di agenti AI autonomi che operano in modo indipendente, accedono ai dati aziendali e prendono decisioni alla velocità delle macchine pone una serie di sfide che è bene affrontare insieme a chi ha già avuto modo di sperimentare con casi reali, in ambiti complessi.
A questo proposito, Zscaler ha annunciato una serie di innovazioni che estendono le funzionalità della piattaforma Zero Trust Exchange alla protezione dell’ecosistema Agentic AI con l’obiettivo di offrire quella che l’azienda definisce la prima piattaforma Zero Trust completa progettata specificamente per la nuova generazione di agenti intelligenti.
L’Agentic AI cambia le regole della sicurezza
Durante la sessione europea del loro evento annuale Zenith Live, tenutasi a Vienna, Zscaler ha condiviso la sua visione sull’evoluzione dell’AI che, a suo dire, sta introducendo complessità che le architetture di sicurezza tradizionali non sono state progettate per gestire. Gli agenti autonomi non si limitano infatti a eseguire istruzioni ricevute dagli utenti, ma possono generare task, creare subagenti, accedere a servizi, utilizzare credenziali e interagire con applicazioni e dati aziendali senza un intervento umano diretto.
Questo scenario genera nuove problematiche in termini di visibilità, governance e controllo degli accessi, rendendo più difficile comprendere quali agenti stiano operando, quali dati utilizzino e quali azioni siano autorizzati a compiere. Parallelamente, la crescente integrazione dell’AI nei processi di sviluppo software espone endpoint e workstation a plugin, estensioni e strumenti potenzialmente malevoli che molte soluzioni di sicurezza tradizionali non sono attualmente in grado di individuare efficacemente.
AI Broker: controllo sulle comunicazioni tra agenti
Una delle principali novità presentate dall’azienda è Zscaler AI Broker, una soluzione progettata per proteggere le comunicazioni tra agenti AI attraverso broker MCP (Model Context Protocol) e framework Agent-to-Agent.
Il sistema introduce un Agent Registry integrato che consente alle aziende di ottenere una visibilità dettagliata sulle risorse accessibili da ciascun agente e di applicare controlli granulari sugli accessi. L’obiettivo è evitare che gli agenti possano espandere autonomamente i propri privilegi o accedere a informazioni non necessarie per l’esecuzione delle attività assegnate.
Endpoint AI Security amplia la protezione sui dispositivi
Accanto al broker per gli agenti, Zscaler ha introdotto Endpoint AI Security, una soluzione che estende la protezione fino ai dispositivi utilizzati dai dipendenti. La piattaforma è progettata per individuare minacce nascoste all’interno di browser, estensioni, plugin e strumenti AI installati localmente, componenti che spesso sfuggono alle tradizionali piattaforme di Endpoint Detection and Response. L’approccio consente di applicare policy coerenti tra cloud ed endpoint, offrendo una visione unificata dei rischi legati all’utilizzo dell’intelligenza artificiale all’interno dell’organizzazione.
AI Access Graph punta sulla governance dei dati
Un altro tassello fondamentale della strategia presentata a Vienna è rappresentato da Zscaler AI Access Graph, una tecnologia sviluppata a partire dall’acquisizione di Symmetry Systems. La soluzione crea una mappatura delle relazioni tra identità, applicazioni, modelli AI e fonti dati, consentendo alle organizzazioni di comprendere in modo più accurato chi accede alle informazioni, attraverso quali agenti e per quali finalità.
L’integrazione con Zero Trust Exchange permette di applicare controlli più rigorosi, ridurre gli accessi non necessari e tracciare in tempo reale la lineage dei dati lungo l’intero percorso, dalla sorgente fino all’utilizzo da parte degli agenti AI. Considerato che i requisiti normativi diventano sempre più stringenti, la capacità di ricostruire i flussi informativi potrebbe diventare uno degli elementi chiave per la governance dell’intelligenza artificiale.
Più visibilità sugli asset AI e oltre 250 applicazioni GenAI monitorate
Le novità annunciate includono anche un importante aggiornamento di Zscaler AI Protect, la piattaforma introdotta all’inizio del 2026 per la protezione degli ambienti AI. Sul fronte dell’asset management, la soluzione amplia le capacità di discovery permettendo di individuare AI integrate nelle applicazioni SaaS, server MCP presenti nei cloud pubblici e rischi nascosti nei codebase agentici attraverso attività di scansione del codice. La visibilità viene inoltre estesa alle attività AI che avvengono direttamente sugli endpoint aziendali.
Particolarmente interessante è il rafforzamento delle funzionalità di Secure Access to AI, che ora consentono di estrarre e analizzare i prompt provenienti da oltre 250 applicazioni GenAI, offrendo una visione completa delle conversazioni e supportando le Compliance API di Anthropic e OpenAI. L’azienda introduce inoltre guardrail basati sull’intento dell’intera conversazione e non sul singolo prompt, un approccio che mira a ridurre i tentativi di aggiramento delle policy attraverso sequenze di richieste apparentemente innocue.
Sicurezza dell’AI lungo tutto il ciclo di vita
L’ultima area di innovazione riguarda la protezione delle applicazioni AI durante l’intero ciclo di vita. Le nuove funzionalità comprendono attività di AI red teaming dedicate ai server MCP, servizi di prompt hardening e strumenti di conformità basati su heat map che aiutano le organizzazioni a identificare le aree più esposte dal punto di vista della governance. L’obiettivo è quello di integrare la sicurezza fin dalle fasi iniziali di sviluppo e distribuzione delle applicazioni AI, evitando che i controlli vengano aggiunti solo successivamente quando i sistemi sono già operativi.
La strategia presentata da Zscaler evidenzia come a fianco della protezione dell’utente serva trovare spazio per la protezione degli agenti AI. Con l’aumento delle identità non umane, delle comunicazioni agent-to-agent e dei workflow automatizzati, le aziende avranno bisogno di strumenti in grado di garantire visibilità, controllo e governance su un ecosistema sempre più distribuito per riuscire a evitare intrusioni e garantire la governance richiesta dalle normative più recenti.
Geopolitical conflict is no longer confined to land, sea or air. Today, it unfolds silently across networks, servers and endpoints. Governments, critical infrastructure operators, and private enterprises are increasingly targeted by cyber operations designed to disrupt services, steal sensitive data, or undermine national stability.
Unlike traditional warfare, cyberwarfare does not require armies crossing borders. A coordinated attack launched from anywhere in the world can disrupt supply chains, shut down utilities, or expose millions of customer records within minutes. From ransomware attacks on healthcare systems to disruptions in logistics and satellite communications, organizations across sectors have faced outages, financial loss, and reputational damage. As organizations digitize operations and connect critical systems to the internet, the line between national security and enterprise cybersecurity continues to blur.
The Rise of Cyberwarfare
According to the European Union Agency for Cybersecurity’s 2025 Threat Landscape report, the global cyberthreat environment is shaped primarily by state-nexus actors and organized cybercriminal groups, with increasing convergence in their tools, tactics, and objectives alongside the growing professionalization of cybercrime and its alignment with geopolitical dynamics.
Critical infrastructure sectors, such as energy, transportation, finance, and telecommunications, have emerged as primary targets for these attacks. Disruptions in these areas can trigger significant economic damage and widespread societal impact, making them especially attractive to threat actors.
In 2026, geopolitical dynamics continue to be the leading influence on cyber risk strategies. According to the World Economic Forum, 64% of organizations now factor geopolitically driven cyberthreats into their security strategies, while 23% of public sector organizations report insufficient cyber resilience capabilities.
Why Enterprises are in the Crosshairs
Enterprises are no longer incidental casualties; they are deliberate targets in cyberwarfare. Organizations that run cloud platforms, digital services, supply chains, and communication infrastructure sit at the core of modern economies, making them high-impact points of disruption.
Recent developments have already validated this shift toward physical targeting of enterprise infrastructure. In early 2026, drone strikes on commercial cloud data centers in the Middle East caused structural damage and triggered widespread service disruptions across dependent digital services. These incidents marked one of the first clear instances of data centers being directly targeted in kinetic conflict, highlighting their growing role as strategic assets. The outages extended beyond the immediate blast radius, affecting critical sectors reliant on cloud infrastructure and exposing how modern conflict increasingly focuses on the core infrastructure of the digital economy.
This strategy is not limited to physical attacks. Supply chain compromises further amplify impact by exploiting trust at scale. By infiltrating a trusted enterprise platform, attackers can scale their reach exponentially across downstream organizations. Incidents such as the Sunburst supply chain attack demonstrated how deeply embedded trust relationships can be exploited, turning widely used software into vectors for national security compromise.
The use of disruptive malware in enterprise environments highlights the potential for even broader operational fallout. Wiper malware outbreaks mimicking NotPetya have crippled global shipping, manufacturing, and commerce, disrupting essential supplies and proving that the consequences extend far beyond the initial target.
What makes these attacks particularly effective is the structure of modern enterprises themselves. Deep interdependencies, reliance on shared platforms, legacy systems, and limited visibility across complex environments create ideal conditions for attackers to move quickly, amplify impact, and align cyber operations with broader geopolitical objectives.
Cybersecurity Priorities in a Geopolitically Volatile Time
As cyberwarfare becomes a permanent feature of the geopolitical landscape, organizations must rethink how they approach security. Cybersecurity can no longer be treated solely as an IT function; it must be embedded into enterprise risk management and business strategy.
Adopt a risk-based security approach: Align cybersecurity priorities with business-critical assets and evolving threat landscapes to focus efforts where impact is highest.
Ensure leadership and board-level alignment: Make cybersecurity a strategic priority with clear governance, executive ownership, and regular oversight at the leadership level.
Strengthen identity, endpoints, and visibility: Enforce least-privilege access, strong authentication, and continuous monitoring while securing endpoints and leveraging threat logs for faster detection and response.
Promote a security-first culture: Build organization-wide awareness through regular training, ensuring employees act as the first line of defense.
Enhance resilience through testing and response readiness: Continuously test defenses, maintain robust incident response plans, and ensure rapid recovery to minimize disruption.
As cyberwarfare becomes a permanent feature of the geopolitical landscape, organizations must rethink how they approach security.
Preparing for Sustained Digital Conflict
Cyberwar is no longer a distant, theoretical threat; it is an active and evolving reality shaping how nations and businesses operate. In a world where attacks can be swift, borderless, and strategically motivated, preparedness becomes a competitive advantage. Organizations that embed security into their core strategy by anticipating risks, strengthening resilience, and fostering a culture of vigilance will be far better positioned to withstand and recover from disruption.
Ultimately, the question is no longer if enterprises will be impacted by cyber conflict but when. Those that act now will not only defend against emerging threats but also build the trust and reliability required to thrive in an increasingly volatile digital landscape.
I Had 1,000+ Pokémon Cards to Sell — So I Built an App That Lists Them in My Store and Promotes Them via Buffer
I collect vintage Pokémon cards, and they’re quite hard to get a hold of. Often, the card I needed was only available in a bulk lot someone was selling. So, through trying to source cards for my own collection from old box sets and starter packs, I ended up with a lot of “spare” cards.
Selling the spares started as a side hobby, but I soon built up an inventory of over 1,000 cards and realized I needed a better process to keep the logistics smooth and manageable.
Each one needed:
its own listing with the right name, set, edition, condition, and clear photos of the front and back.
a description that would make sense to a buyer.
a social post or two, otherwise nobody beyond the people already searching for that exact card would see it.
The cards themselves were the fun part, but doing them one at a time across hundreds of cards quickly became a part-time job I didn’t sign up for.
I also noticed that social was the first thing I’d skip when it got tedious, which meant cards would end up listed and live but invisible to anyone who wasn’t already looking for them. A listing nobody sees doesn’t sell, especially with collectibles, where most demand comes from feeds and fan accounts rather than the marketplace itself.
So I built a Mac app that handles the whole pipeline end-to-end and feeds listings on my own website. Here’s how I did it:
The thing about Pokemon card collectors (and why I needed a simpler social workflow)
When I first started selling, everything went through eBay, and eBay has gotten really good at the listing-creation side of things. The platform can suggest a title, pre-fill some of the item specifics, and do a lot of the description heavy-lifting for you. That’s a huge time-saver for a seller listing one item at a time, who doesn’t mind waiting a while for buyers to naturally come across their wares in a few days or weeks.
The Pokémon card market works a little faster than, say, selling “gently-used” shoes. Pokémon card buyers don’t typically hunt for their dream card on a marketplace. They follow card accounts on Threads and Instagram, they bookmark dealers they trust, they spot a card in a feed, and click through. Social promotion is half of what makes a listing sell. And sometimes more than half, depending on the card.
Of course, there’s a lot of work that goes into manually sharing one card on social — never mind 1,000. I found myself craving a way to simplify that admin, like a built-in connection between the listing and social post processes. This turned out to be the perfect use case for the new Buffer API I’d been working on.
The Buffer API was the missing piece that turned this from a tool to just create listings into a tool that sells cards.
With this system, each listing (and its promotion) lives in one flow. Scheduling matters as much as posting. Buffer drops the posts when my audience is actually online (based on our own Best Time to Post data, which you can now find right in your publish dashboard), rather than at 11 pm on a Sunday when I happened to finish photographing a stack.
Here’s a closer look at how I closed the gap between the listings and sales.
How the app works
The (as yet nameless) app lives on my Mac, and the whole flow starts with a drag-and-drop. Here’s what a typical session looks like.
A zip of photos goes in
Originally, I built this to handle one card at a time. I’d chuck a front photo and a back photo into the app, Claude would do its thing, and I’d publish from there. It worked fine, but working through a pile this size one pair at a time was almost as tedious as listing them manually, so I added zip-file support.
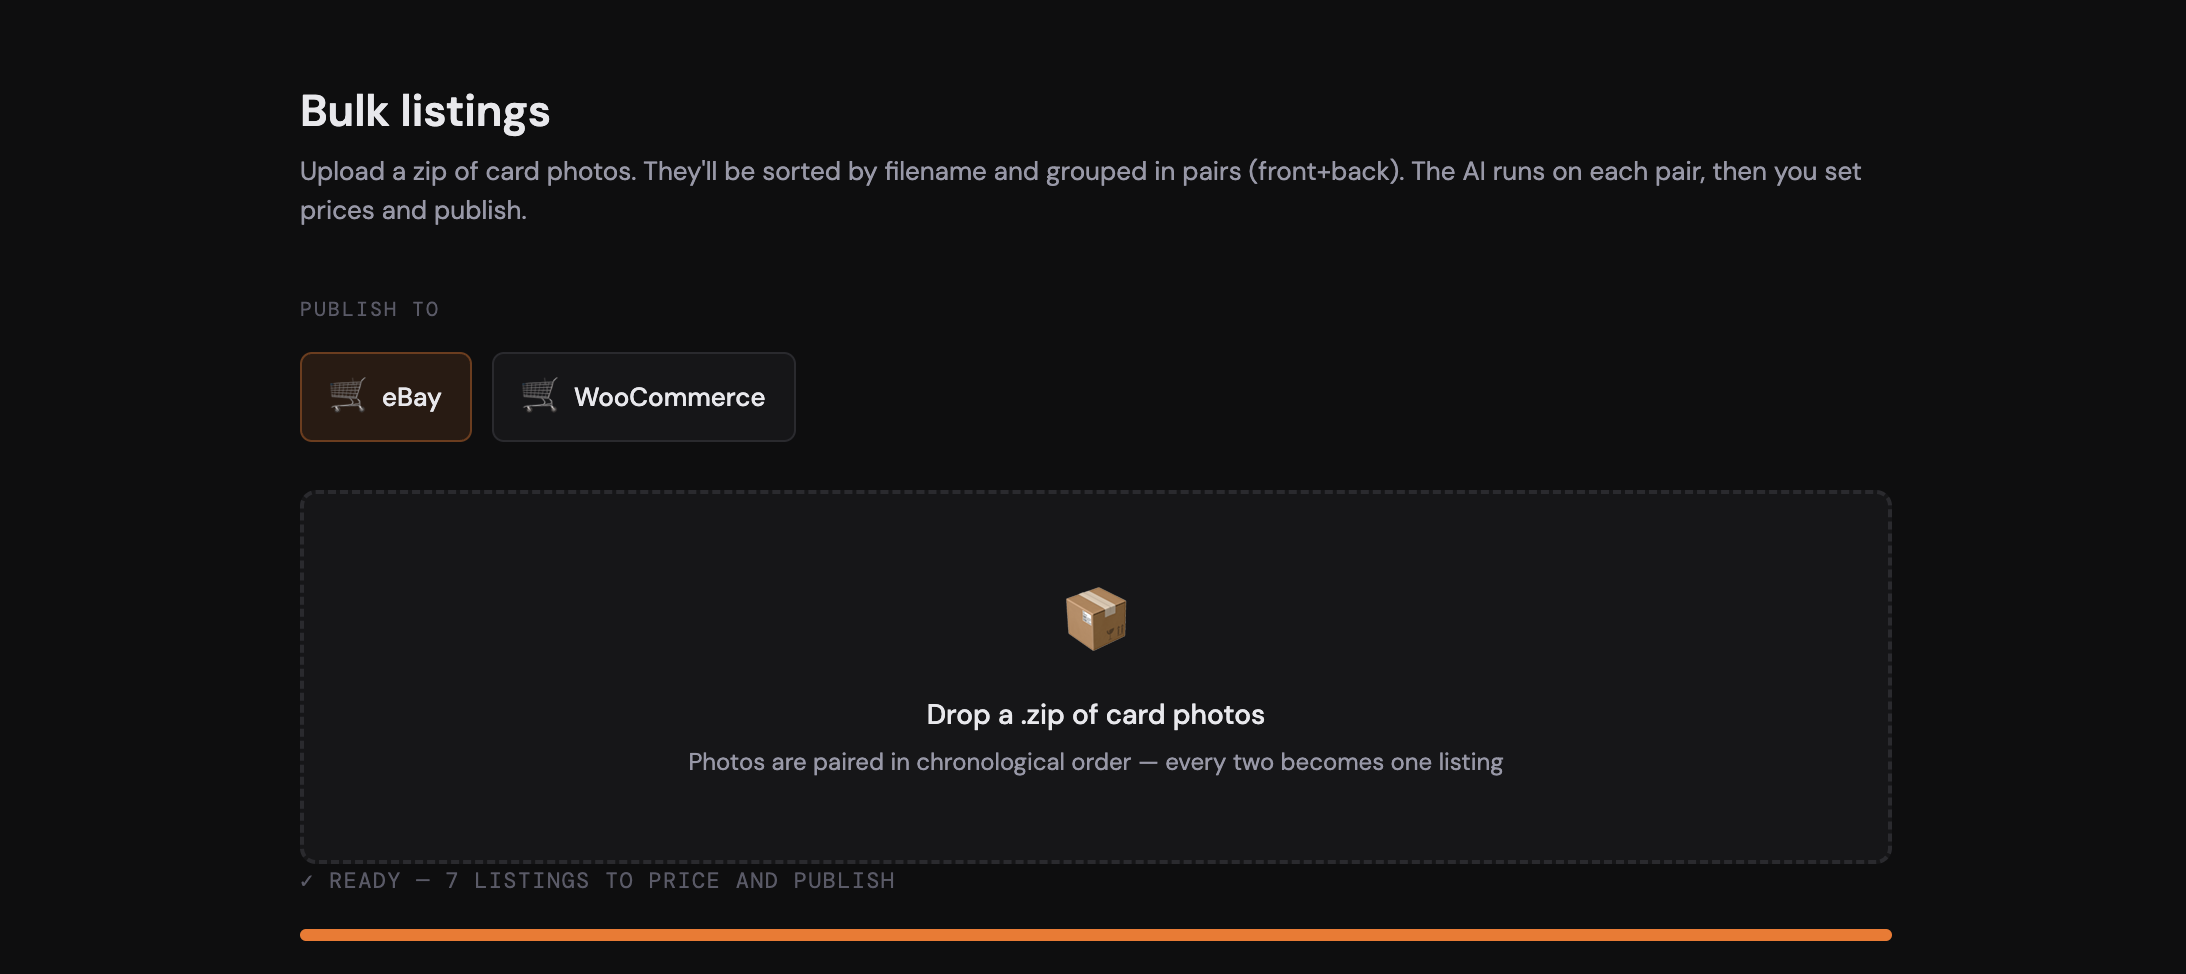
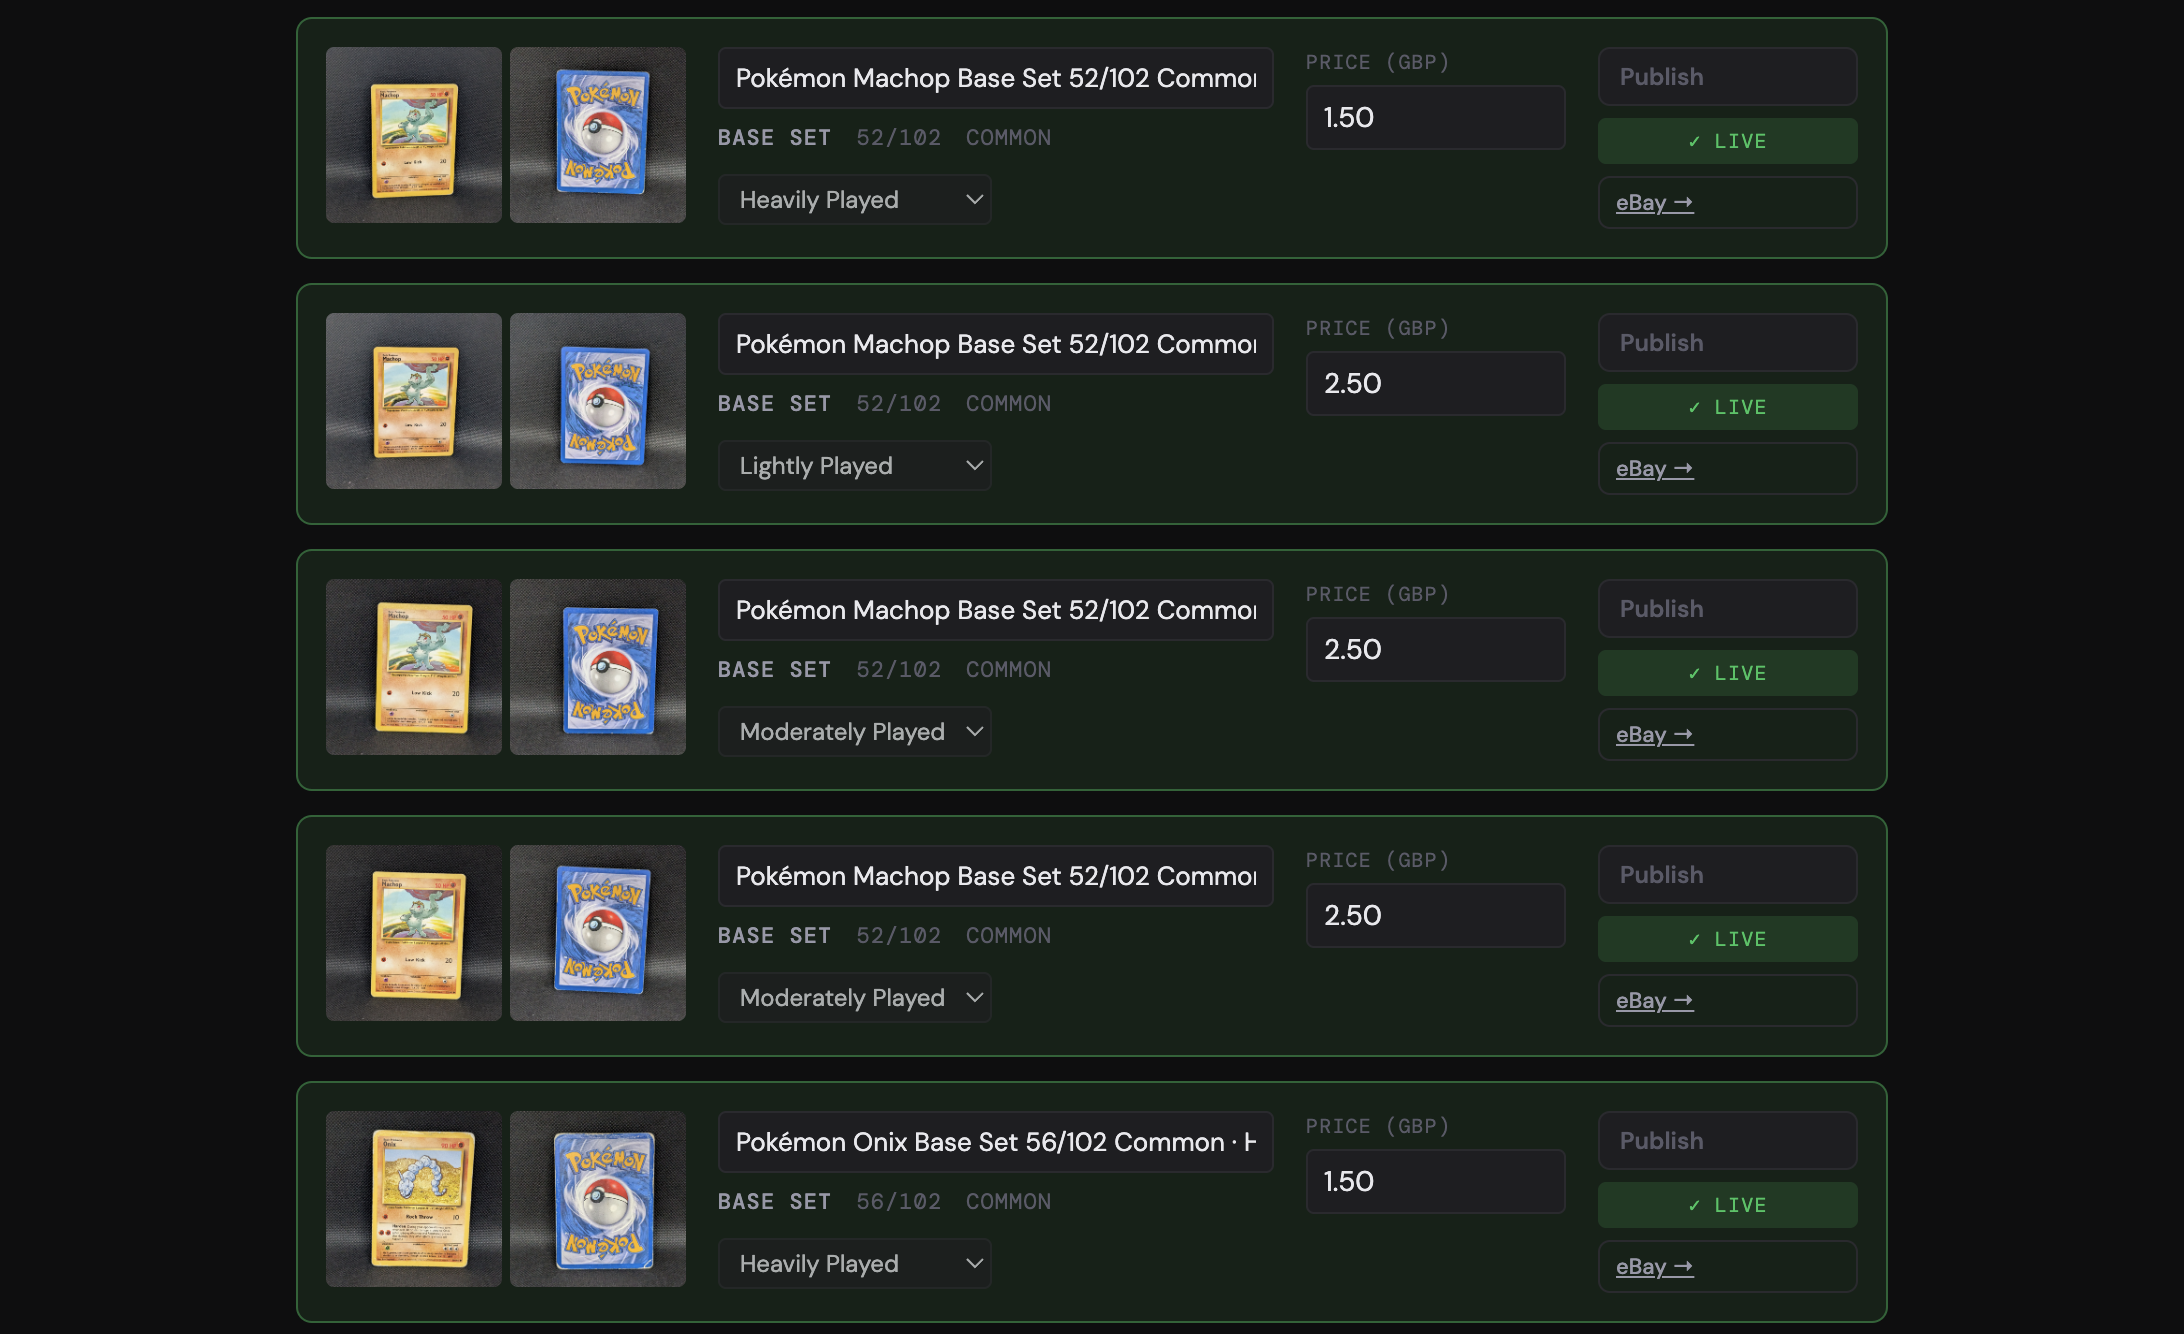
Now I shoot the cards in my little lightbox in batches, pair the photos so each card has a front shot and a back shot, zip the whole lot up, and drag the zip into the app. The app sorts the photos by filename and automatically groups them into pairs.
The upload screen also has a newer addition: a selector for where the batch should publish. When I first built the app, everything went to eBay; now I can choose eBay, WooCommerce, or both at once. It’s quite modular, so if I added another provider in the future, like Shopify, it would just be another option in the list.
In practice, I tend to do batches of around 50 cards at a time. It takes a little while for the AI to work through, but that’s fine.
With this system, I can drop the zip folder in, walk away, and come back once it’s done.
Claude reads each card
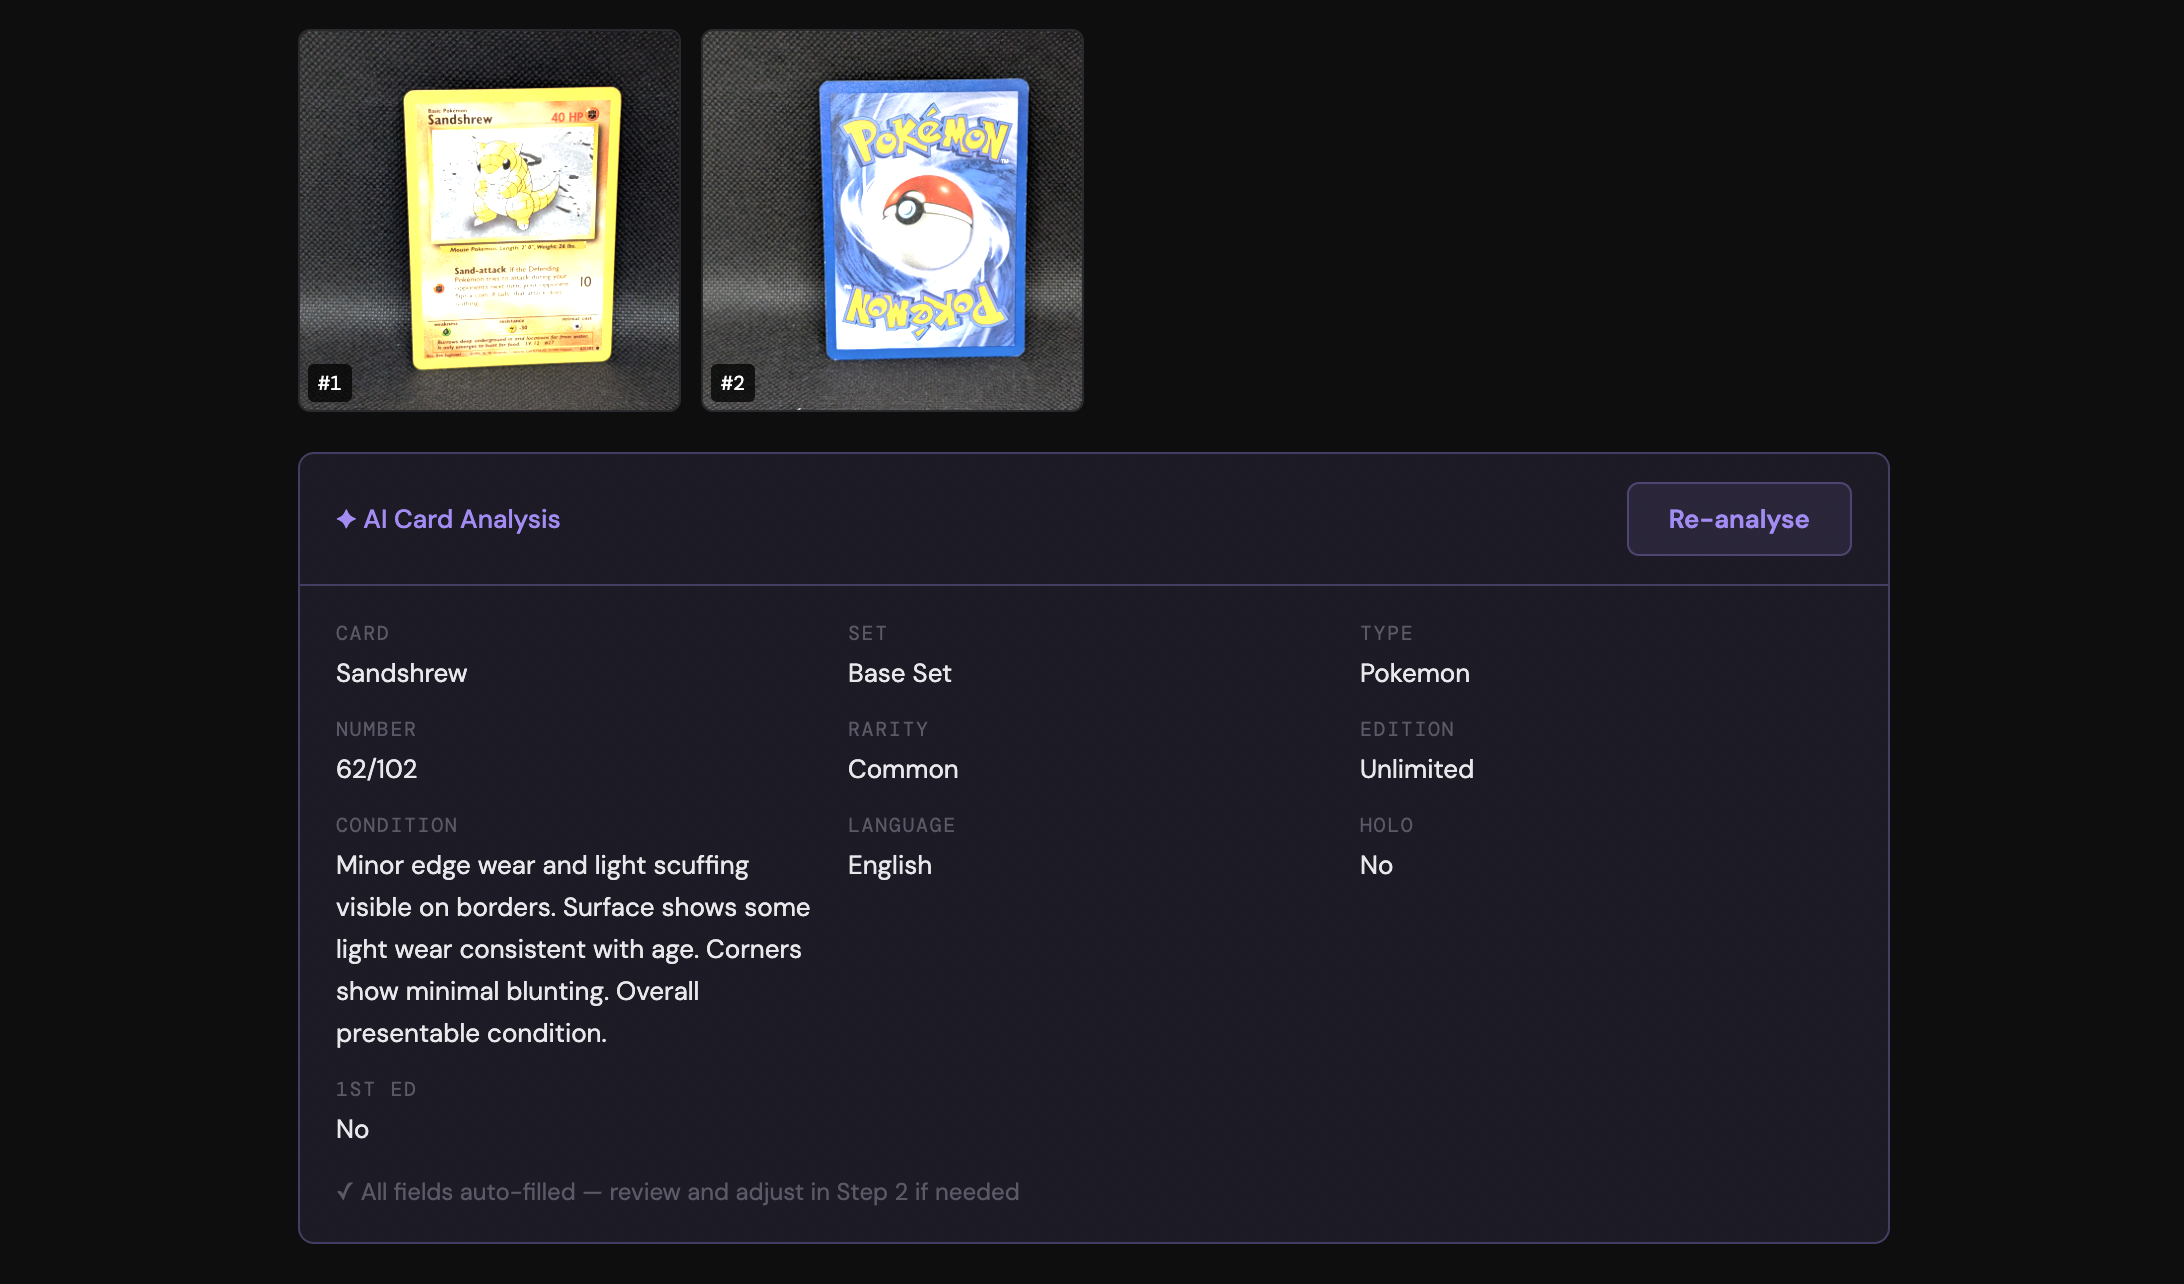
This is the slowest part of the flow, but easily the most useful one. The app sends each pair of photos to Claude, which pulls out the structured details I need for the listing: card name, set, card number, rarity, edition, language, holo or non-holo, and condition.
Condition is the field I cared about most. I used to have to spend the longest part of a listing session just squinting at corners and edges, trying to weigh up whether a card was Lightly Played or Heavily Played. Now Claude makes the call, and I just confirm whether it’s accurate or not.
Sometimes the condition isn’t quite right, and the ratings need to be nudged up or down because my photo isn’t great or the lighting in my lightbox fooled it. I’ll change that before approving the listing, but it’s usually accurate enough that I’ve stopped manually reviewing every single field. I trust Claude on the easy stuff and only look closely at the calls I’d second-guess anyway.
The listing details fill themselves in
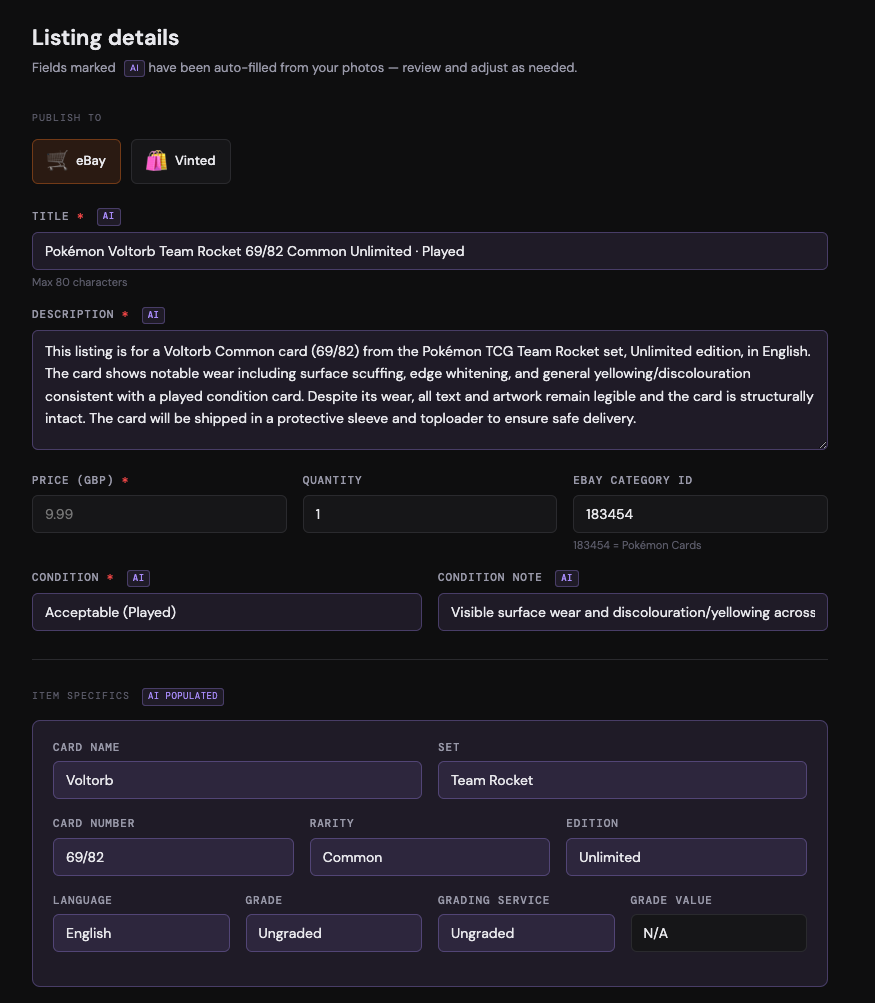
Once Claude has done its pass, every field on the listing form is already populated: title, description, condition note, item specifics, set, number, rarity, and language. The little “AI” badge next to each field is the only visual reminder that I didn’t type any of this.
The only thing I set manually at this point is the price. I’ve been looking at card market data APIs like TCGdex that could pull recent sold prices and active listings for the same card, with the goal of suggesting a number based on actual market data rather than my best guess. I haven’t found one I’m happy with yet, so for now, the price stays the one piece of human judgment in the flow.
Publish in a specific order
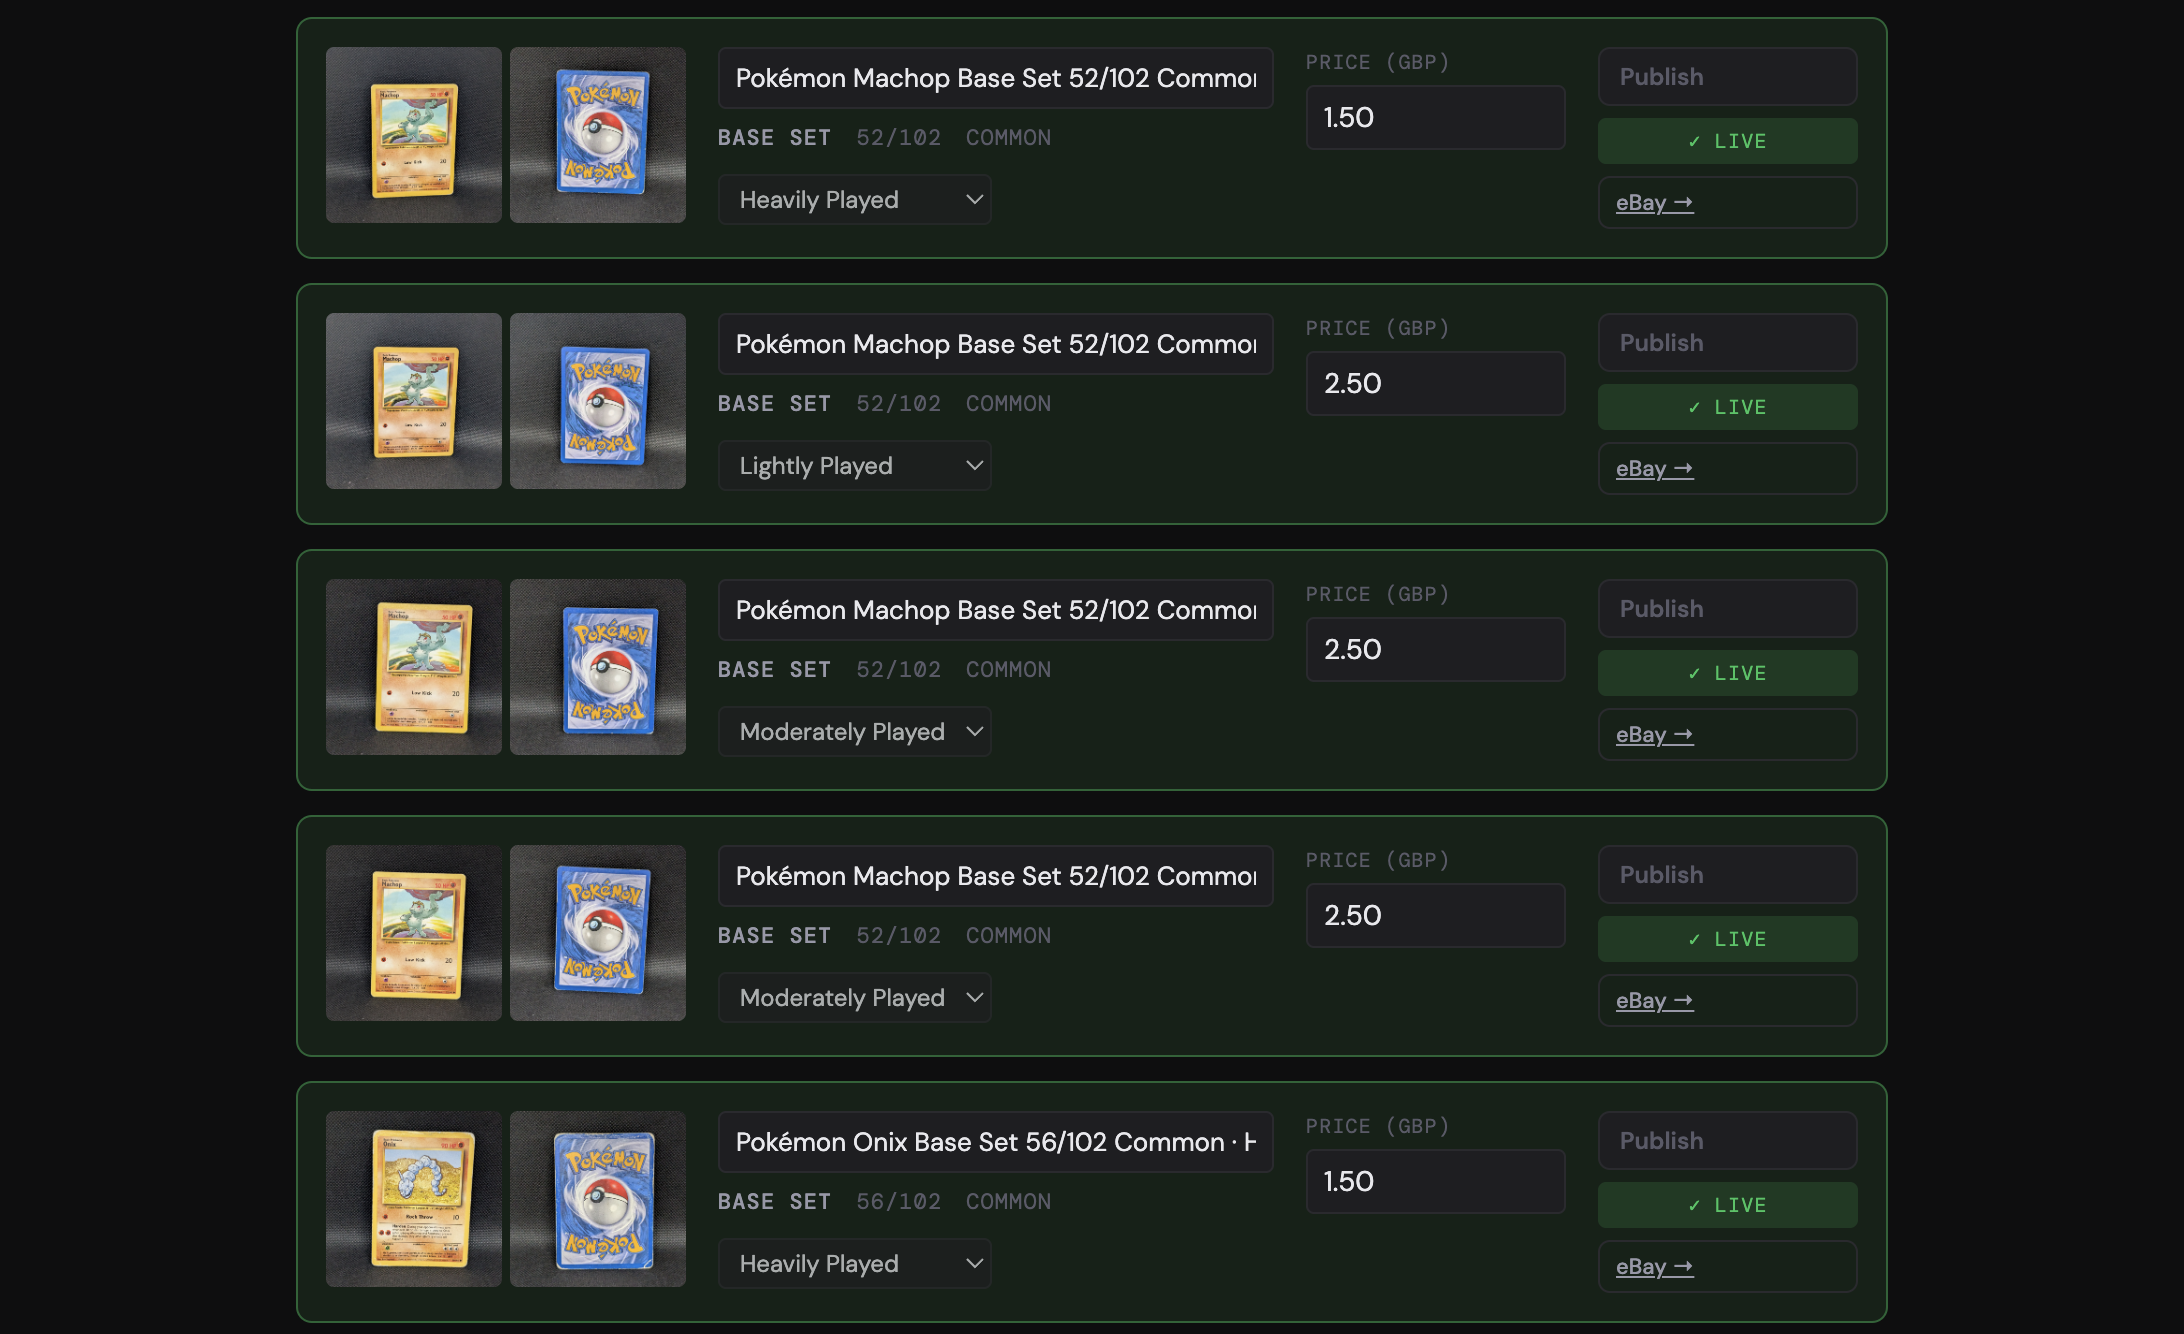
When the prices are in, I hit “publish all priced ones,” and two things happen in sequence.
First, the app creates the product in my store through the WooCommerce API (when I started, this step created an eBay listing instead). That has to go first, because the next step needs the live product URL.
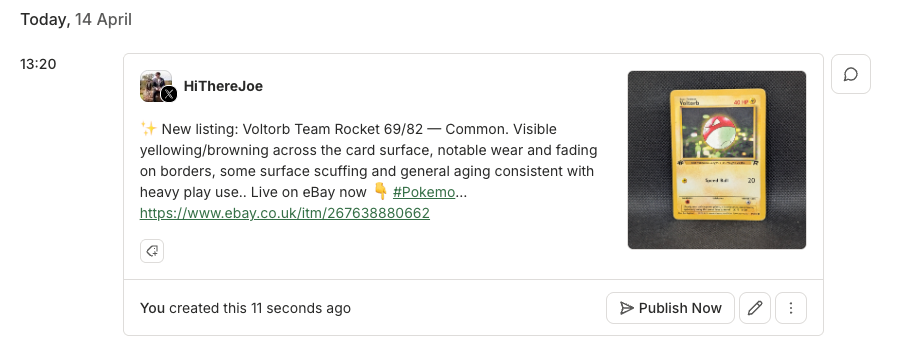
Then the app builds a social post with the
card name,
set,
condition note,
the front and back photos
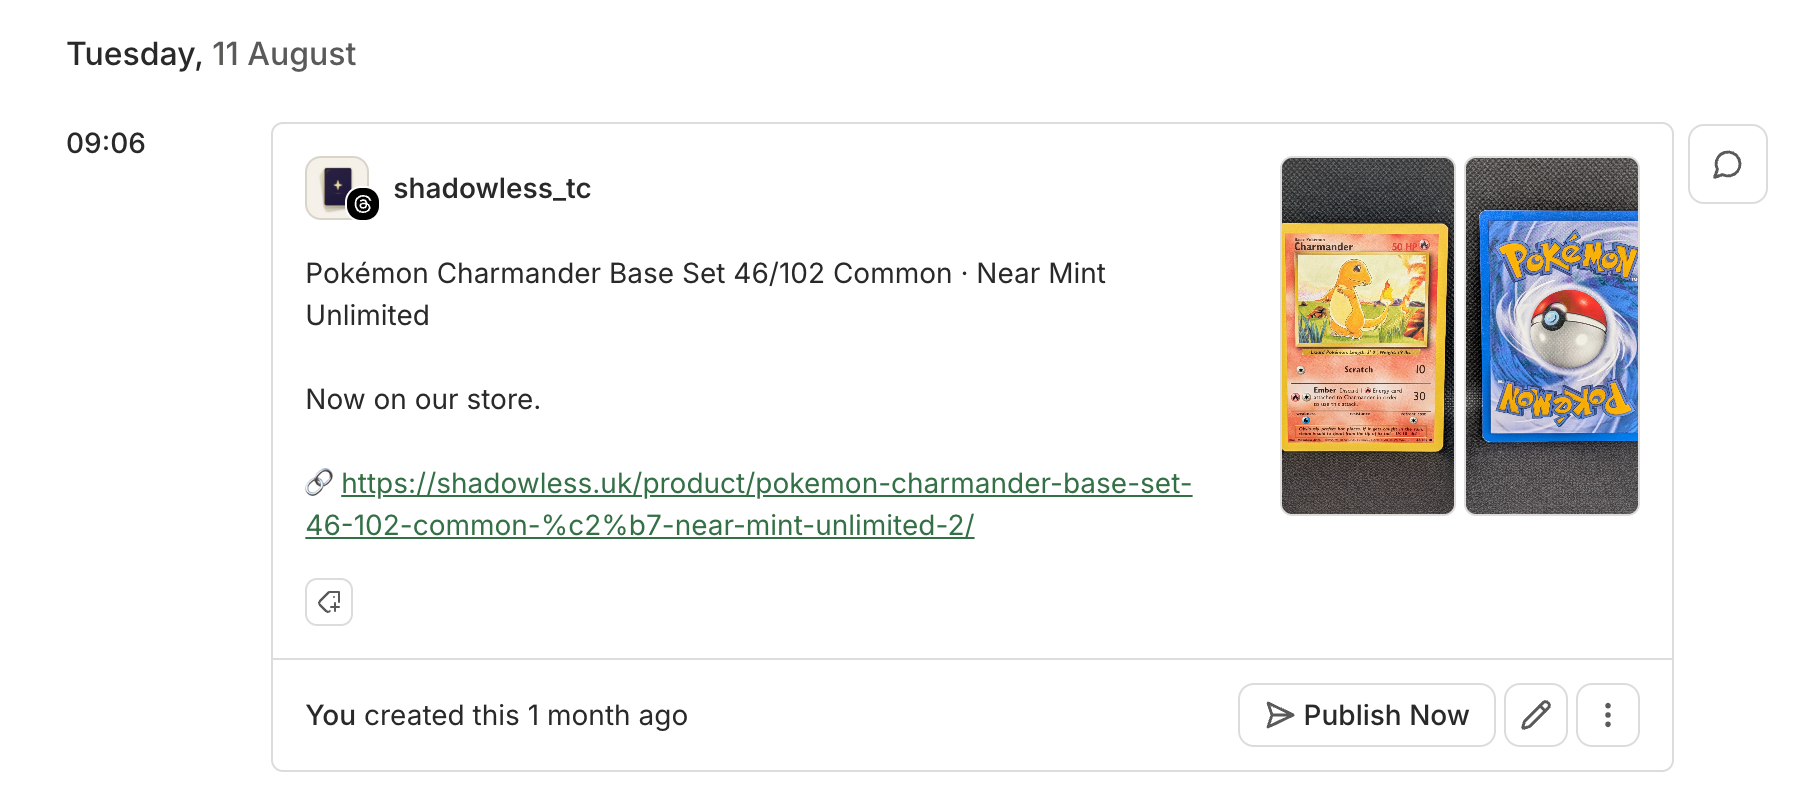
Then, it queues the post through the Buffer API across whichever channels I’ve selected. Threads gets a direct link to the listing in the post — the newer ones read “now on our store” and link straight to the product page. Instagram, where you can’t drop a clickable link in the body of a post, points to the link in bio instead.
The workflow that used to live across three apps: the marketplace, my photos folder, and a separate mental note to post on Threads later, now lives in one approval.
⚡One thing I purposely kept in the workflow is a single-card mode. If a card is rare or valuable, I don’t want to bulk-publish it alongside fifty Common cards from a Base Set. I want to look at the photos and read Claude’s description closely, set the price more thoughtfully, and then run it through. Full automation is the right default for the bulk of what I’m selling, but it’s not always what you want.
What started on eBay has grown into a store of its own
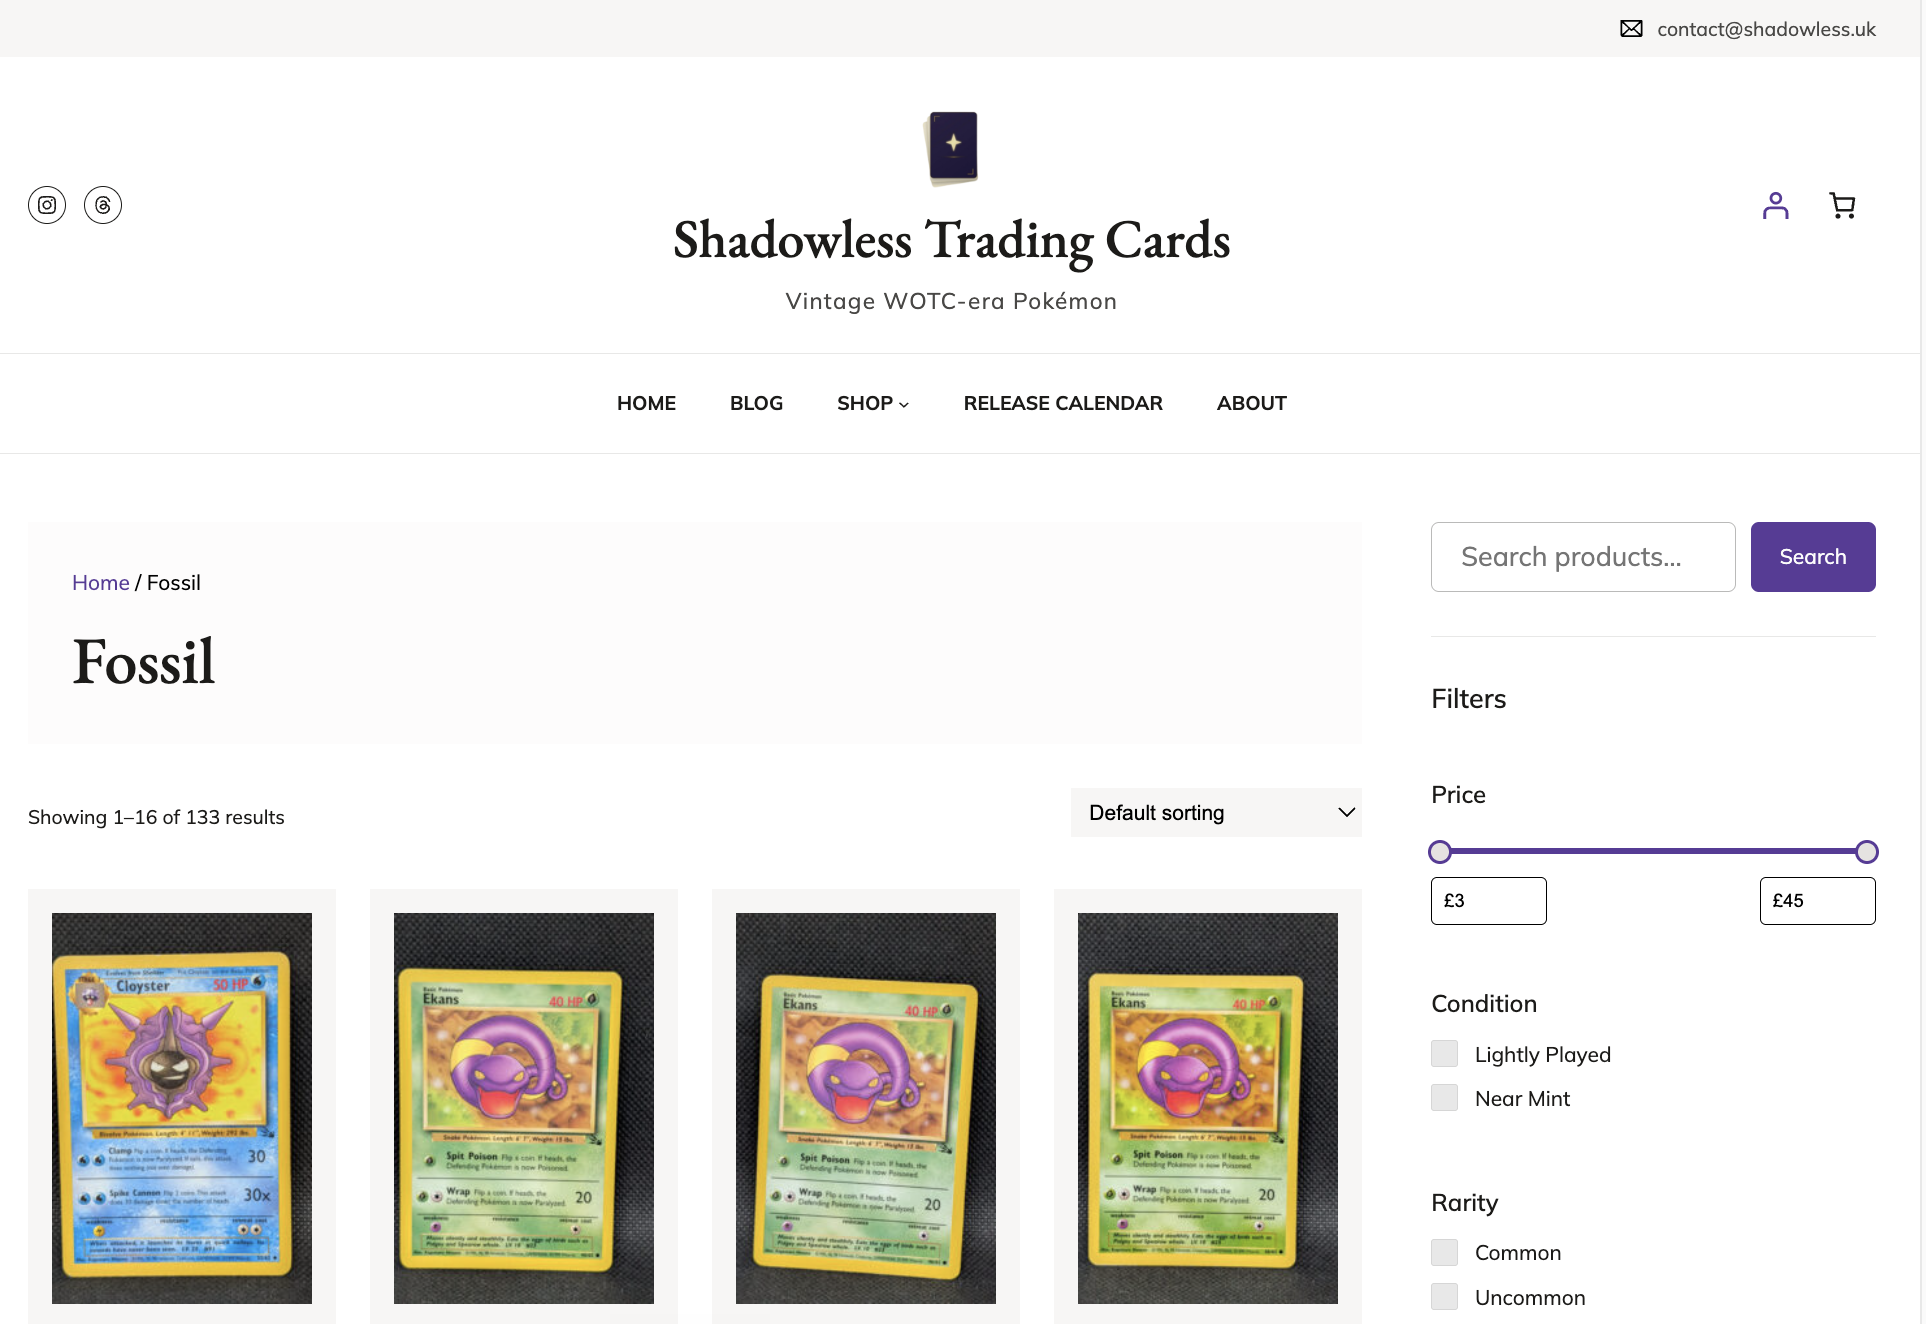
I sold through eBay for the first stretch of this project, and it served me well. The older posts in my Buffer queue still point to live eBay listings, and I’ve kept those products up for that reason. But it felt important to me to have my own brand and my own space to experiment, so I set up Shadowless, a WooCommerce store, and pointed the app at it. Because the publish step was already modular, WooCommerce support was about half a day of work on top of the eBay version.
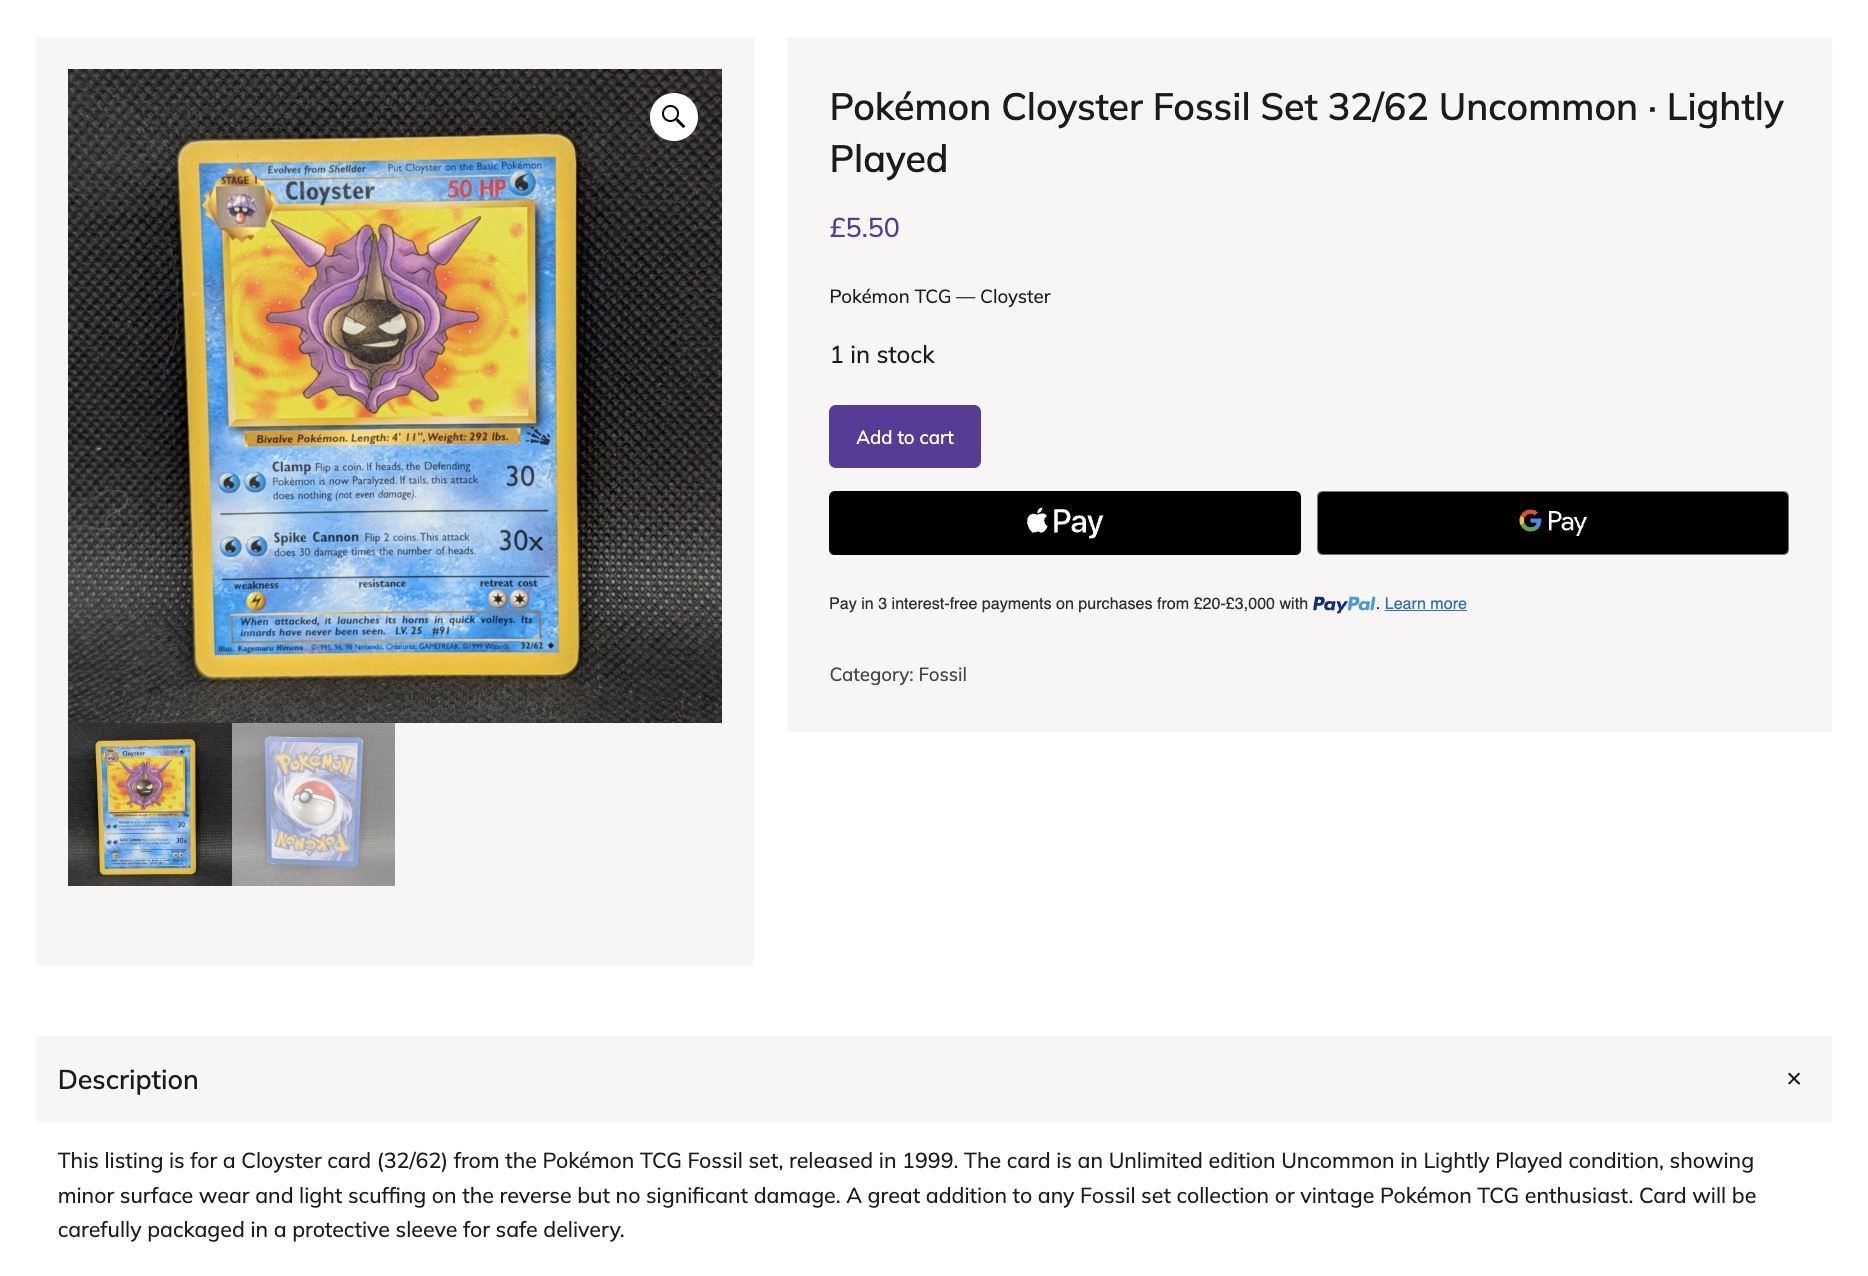
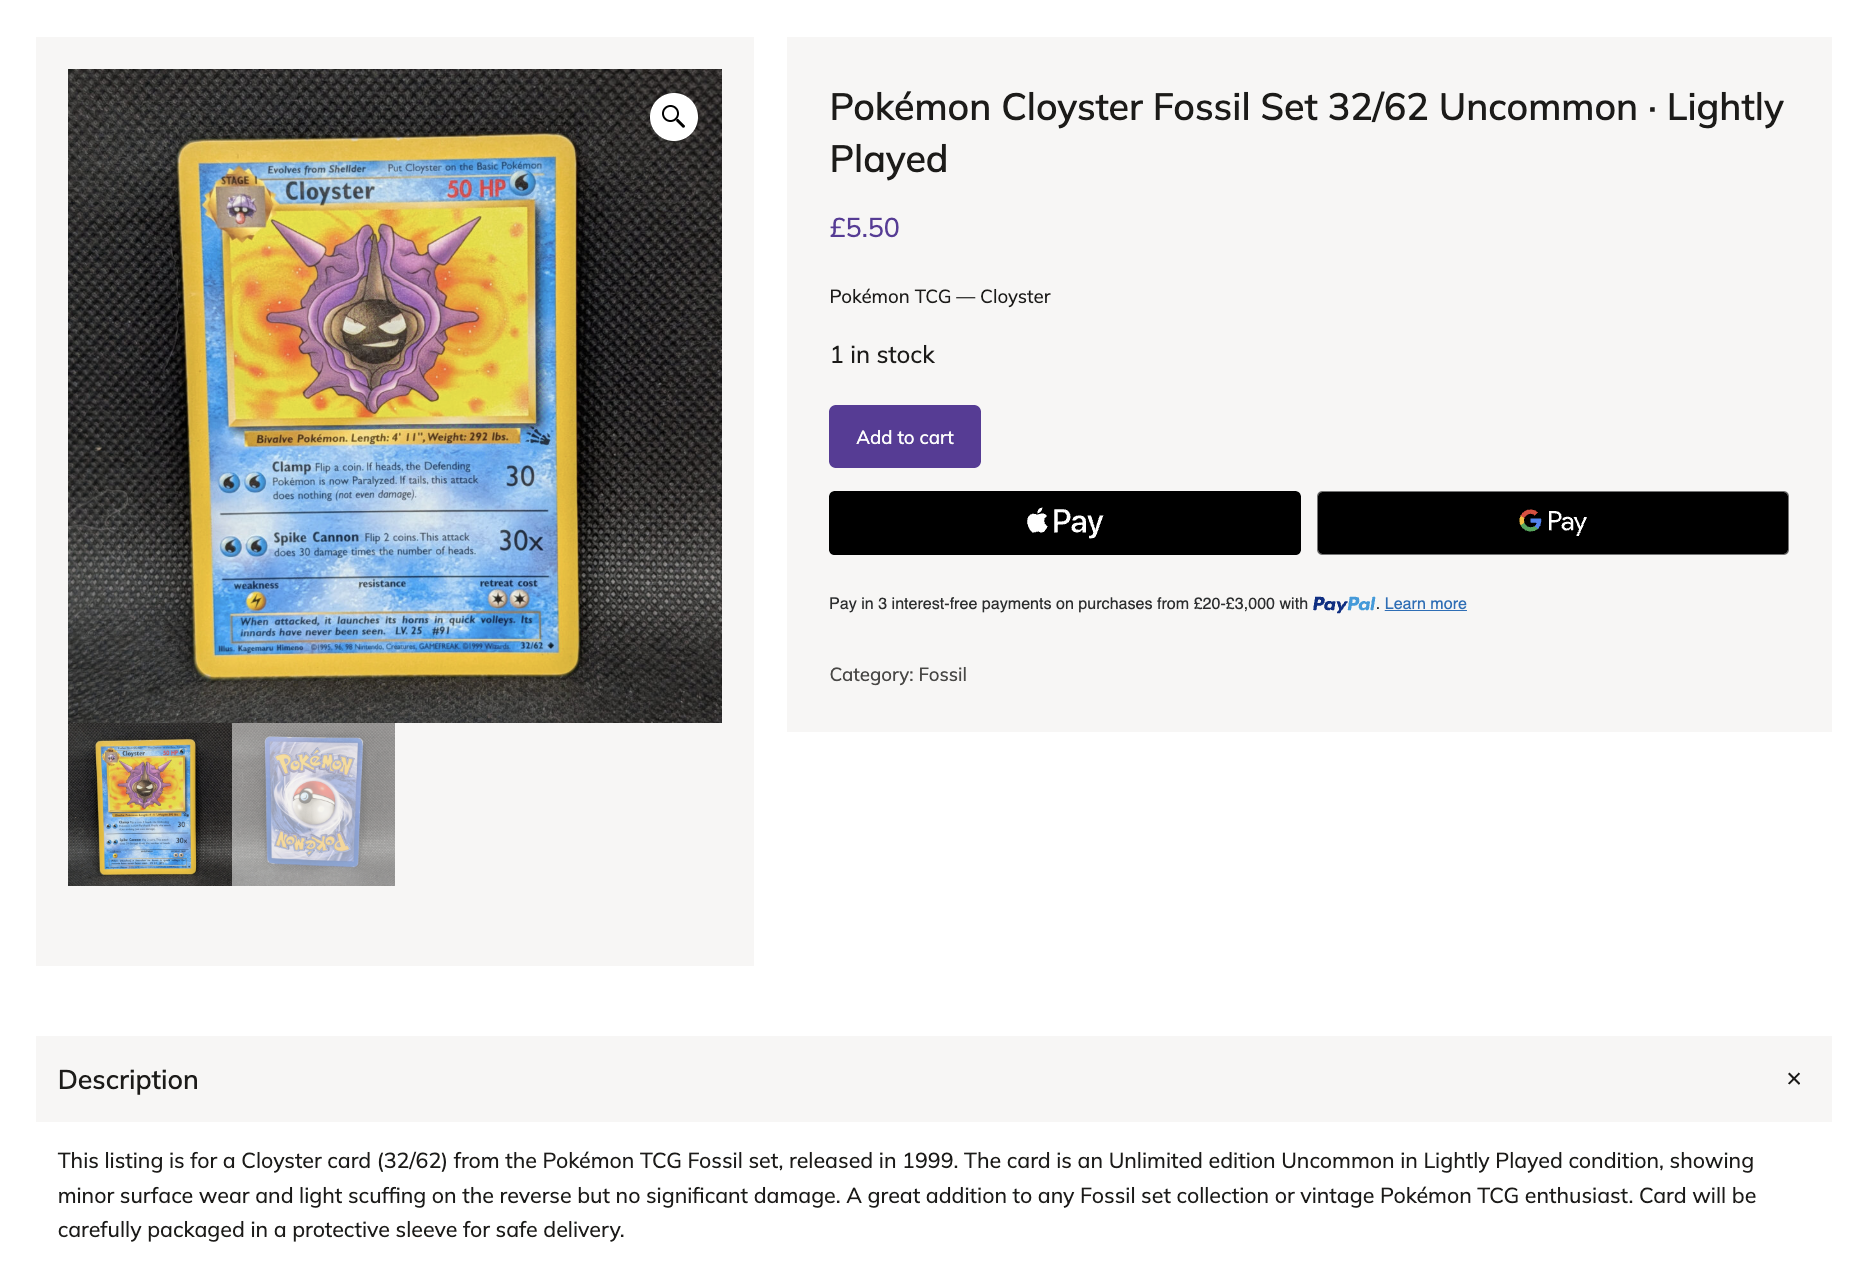
I’m most pleased with what happens to all those details Claude pulls from the photos. Every field — set, card number, rarity, edition, language — becomes a filterable attribute on the store. A buyer who only collects Rare cards from the Fossil set can filter down to exactly those cards, which is the kind of browsing experience I’d always wanted to offer buyers and could now actually build. Those attributes would have taken me ages to fill in manually, and they’re what makes the store feel like a card shop rather than a long list.
Running my own store does mean the marketing is on me too. I’m still building up traffic, and that’s a whole other project, but the listings and the social promotion were already handled the day the store went live, because the app didn’t have to change.
And then I leave it alone
The process I’ve settled goes something like this: I photograph a stack of cards on a Sunday afternoon, drop the zip into the app, set the prices when Claude finishes its pass, hit publish, and walk away. The listings go live on the store, the Buffer posts go into the queue at the times I’ve already set up — two a day to Threads and Instagram — and I get on with my evening.
My Buffer queue is sitting at over 1,000 posts now, so I’m not losing my streak any time soon. And for all the Claude image analysis behind the 1,310 products in the store (so far), I’ve spent maybe $15 to $20 in total.
The parts I’m still working on
The pricing step is the next thing I want to crack, which is the main reason I’ve been digging into card market APIs. The market moves constantly, and I don’t want to be overcharging anyone, so I’d rather keep this step manual than get it wrong. Once a data source I’m happy with is in, the last manual step in the bulk flow is gone.
The other wrinkle is stock. Some cards have started selling before their scheduled posts go out, which means a post can point to a card that’s no longer available. I’m thinking about a script that watches for stock changes and tracks down the corresponding Buffer post, but there are some complexities there I haven’t worked out yet.
Takeaways for selling anything physical
The Pokémon card-angle is my version of this story, but you can think of this flow beyond cards. It’s how any small seller can make more of their work automatic. Here are four things you can do.
Pull structured details from your photos with AI vision. Whether it’s Claude, GPT-4, or Gemini, pick whichever vision model you trust. The key is asking for structured output (for example, a JSON object with the fields you actually need) rather than a short description. Structured output is what lets the next step in the pipeline consume it without you having to parse anything by hand.
Connect to your marketplace’s API. Most of the platforms a small seller might use (eBay, Etsy, Shopify, Mercari, WooCommerce) have one. The docs are usually rougher than you might hope for, and the listing-creation endpoint is the part that takes the longest to get right, but it’s the only endpoint you really need. And if you choose to build the publish step yourself, adding a second destination is cheap. WooCommerce took me about half a day on top of the eBay version, and that same half day is what now runs my own store.
Close the loop with the Buffer API. Once the marketplace listing is live, use the listing URL to automatically generate a social post with an image, a short caption, and the link. Then queue it through Buffer across whichever channels are right for what you sell. This is the step that’s easiest to skip when you’re building, and it’s the one that turns a listing into a sale.
Keep a manual override. Full automation is the right default for the bulk of items, but add in a single-item review mode for the cases that warrant it. A high-ticket item still needs human eyes.
Listing a product and promoting it should be the same action rather than two separate workflows. Once you wire those together, the time you spend per item drops to seconds, and your products (cards in my case) stop sitting in a box in the corner of your room.
Ready to build?
If you’re taking Buffer’s API for a spin, we’ve got resources to get you moving. Our developer docs cover the GraphQL schema, auth flow, and quick-start examples. The Buffer MCP server docs walk through plugging it into Claude or any MCP-compatible AI agent.
We’d love to hear about what you make. Find us in our Discord server, or @buffer on all major social channels.
https://buffer.com/resources/pokemon-cards/
Breaking Down the Novo Nordisk Data Breach
Danish pharmaceutical firm Novo Nordisk announced it faced a data breach related to clinical trials, releasing notification letters to both patients and healthcare providers (HCPs) involved. According to the statement, a threat actor gained access to a limited number of the company’s internal IT systems, which included access to certain personal data.
“Pseudonymized clinical trial data can create a false sense of comfort, but it could have been worse,” comments John Bruggeman, vCISO at CBTS. “The risk is that with life sciences, the context around the data matters. Trial participation city or state, treatment area, demographics that were not anonymized, and research attributes can become sensitive when combined with other sources. Attackers do not need a complete patient profile to create harm. Thankfully though patient PII was not disclosed, so in today’s environment I’ll take that as a win.”
However, this doesn’t mean the incident is absent of risk.
Ross Filipek, CISO at Corsica Technologies, explains, “A breach involving clinical trial data creates a different kind of risk than a typical consumer data incident. Novo Nordisk says the exposed information was not tied directly to names, which is good. It also said no usable identifiers were obtained, which lowers the immediate risk. However, health data can still carry long-term value when it is combined with other stolen information. Even when an ePHI breach does not include patient names, attackers may try to reverse-engineer identities by pairing details like birth date, postal code, or gender with outside data sources.
“For patients, the immediate danger may be limited. The bigger concern is what happens later. Attackers can use partial medical details to build convincing phishing messages, impersonate trusted organizations, or pressure people with information that feels deeply personal. That is especially concerning in healthcare, where trust is already fragile.
“There is also a downstream business risk. Clinical trials depend on confidence from patients, providers, regulators, and research partners. Even a limited breach can create hesitation. If attackers had dwell time inside the environment, the concern shifts from data exposure to data integrity. A pharmaceutical or healthcare organization may need to determine whether research data was altered, whether regulatory obligations were triggered, and whether any intellectual property was exposed. Active trials could also face delays while the incident is investigated. Healthcare organizations need strong visibility into sensitive data, tighter access controls, and active monitoring before a contained incident becomes a broader trust problem.”
Affected patient data includes:
Patient IDs (consisting of a random alphanumeric string)
Trial participation information
Sex
Year of birth
Lifestyle factors (such as BMI, smoking, etc.)
Biomarkers
Health/immunogenicity data
Affected HCP data includes:
Name and registration number
Email address
Phone number
WhatsApp information
Office location
While patients may be at a slightly lower risk, especially when compared to other healthcare breaches, experts warn the HCPs could be at risk of targeted attacks.
Bruggeman states, “Attackers can use information stolen from Novo Nordisk to target the doctors helping to bring valuable medical research to drug makers. Now attackers can make a message feel credible, even professional, given the contact details that were compromised. Imagine a doctor involved getting a message from an attacker about a trial update that is in fact fake? Or request documents, or payments, or a medical portal password reset when the attacker has enough context.”
Was This Breach Corporate Espionage?
“There are markers to this case which suggest the possibility of corporate espionage,” asserts Joseph Perry, Cybersecurity Researcher and Advanced Services Lead at Arcova. “Novo Nordisk’s intellectual property are fabulously valuable, the accessed patient information is related to ongoing clinical trials, and based on the patient letter and hcp letter it appears the threat actor’s purpose was data exfiltration (as opposed to, e.g., ransomware). Overall, based on available information, the incursion appears to be relatively limited and, at this point, contained. However, given that the discovery and containment appear to have happened after the external copying of data, there’s an open question as to whether this was contained before or after complete mission success.
“In general, this flows with a broadening trend in cybercrime. For years, we’ve discussed the commodification of certain attacker flows (e.g., the rise of Initial Access Brokers) and the move to platforms and monolithic providers. What that all boils down to, what we’re seeing, is the ongoing professionalization of cybercrime. We don’t have any evidence as to who the attacker was, nor do we have proof of their motivation. But if the hints we’re seeing in public disclosure pan out, and this does turn out to be an act of corporate espionage, that would be yet another example of cybercrime’s mainstreaming. The calculation is simple enough; if the risk of discovery is small relative to the potential profit, at least some unscrupulous folks will attempt to leverage cybercrime as a business tactic.”
Maine Data Breach Reporting Portal Abused, Taken Offline
The Office of the Maine Attorney General has removed its public-facing data breach database due to abuse of the reporting system. According to the office’s statement, two companies are known to be affected by false reports of data breaches. The false reports have since been removed from the database.
The two companies known to be impacted by fraudulent filings are Discord and VRChat.
“After conversations with VRChat, one of two affected companies, it has become clear that the reported data breaches were hoaxes submitted by an unknown entity unrelated to either company,” the office’s statement reads.
The false report against Discord claimed 10 million individuals were affected by a breach.
The fake data breach report against VRChat claimed 2.4 million users were impacted by a data breach, exposing information such as usernames, email addresses, subscription statuses, login histories, and user IDs for connected platforms.
The office states it has no knowledge of any legitimate data breach claims against either Discord or VRChat.
“We are reviewing our procedures to make this abuse less likely in the future while preserving the public availability of such information,” the office states. “The public-facing database will remain offline until then.”
Organizations that need to submit a data breach report can continue to do so through the office’s online reporting service.
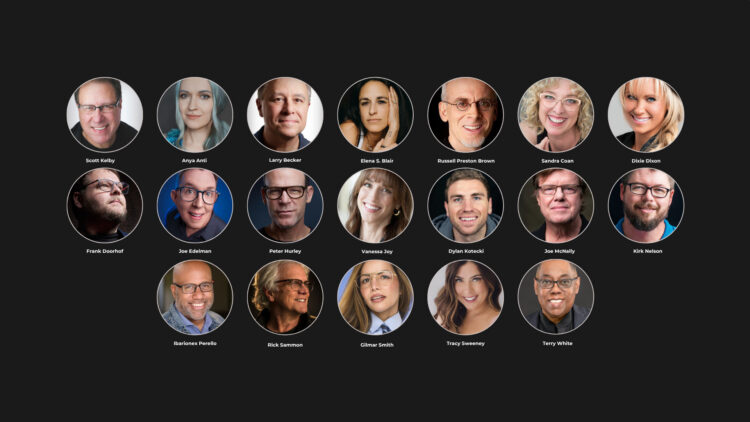
Meet Your Instructors for the Photographing People Conference
One of the best parts of every KelbyOne conference is the people who make it happen.
The Photographing People Conference brings together 19 instructors with different backgrounds, specialties, and creative approaches, all united by one goal: helping you create stronger photos of people.
And we’re not just talking about traditional portraits.
Throughout three days of live online training, you’ll learn from photographers who specialize in family photography, headshots, street photography, travel, sports portraits, weddings, self-portraits, mobile photography, creative illustration, lighting, editing, and more. Some sessions focus on technical skills like posing and flash. Others explore storytelling, connection, creativity, and finding your own style.
That variety is what makes this conference so special. Every instructor brings a unique perspective, and chances are you’ll discover techniques you never expected to use until you see them in action.
You’ll also be learning alongside an incredible community of photographers from around the world. Ask questions during live sessions, share ideas with fellow attendees, and leave inspired by what others are creating.
Whether you’re photographing clients, family, friends, or strangers on the street, these instructors are ready to help you build confidence behind the camera.
Join us online July 20–22 and learn live, or watch on your own schedule with replay access available for a full year.
Claims of 2.4M Impacted by VRChat Breach Revealed False
Update: New information reveals claims of this breach were falsified. More information on the fraudulent report can be found here. The story below is based on statement provided in the fraudulent report and was written prior to those claims being proven false.
VRChat, an online virtual world platform, experienced a data breach affecting approximately 2.4 million users. According to a notice filed by the organization, compromised information may include:
User IDs for other platforms (like Steam or Meta) that are linked to the VRChat account
Login histories (including devices, hardware identifiers, and IP addresses)
The organization has stated it has seen no evidence for the compromise if passwords, credit card or payment information, or government identification documents.
At this time, the organization has contained the incident and engaged in forensic investigation. It has also established further security measures and collaborated with cybersecurity professionals to monitor additional threats.
The organizations warns users to be cautious of phishing attempts, particularly in the case of unsolicited messages claiming to be from the platform itself.
Research shows identity crimes are increasingly leading to multiple fraud instances rather than creating isolated events. The identity Theft Resource Center’s 2026 Trends in Identity Report reveals approximately a quarter of victims (25.6%) deal with two or more concurrent events, which represents a 23.5% increase from the year prior.
Key Findings
Computers and mobile devices saw an increase in unauthorized access (78% year-over-year). These instances rose from 15.3% of identity compromises to 27.2%.
Year-over-year, scams prompting victims to share personal information decreased from 43.1% to 36.1% of instances.
Among victims with no financial loss, 53% were able to find a resolution. Conversely, among those with a financial loss, only 9% found resolution. 0% of those who experienced three or more financial repercussions found a resolution.
The most common crime against minors is fraudulent employment, accounting for 40% of misuse cases.
Identity crimes are becoming multi-layered because one successful compromise now gives criminals reusable access across multiple systems. A stolen credential set, a compromised device, or an account-problem scam can cascade into account takeover, new-account fraud, employment misuse, and other downstream abuse, especially when attackers harvest high-value PII and reuse it across channels. AI is accelerating that trend by helping criminals create more convincing, personalized outreach at scale and by making fake identities, fake profiles, and impersonation cheaper to operate.
Unauthorized device access is growing because the phone or laptop is now the control center for a person’s digital identity. If a fraudster gets onto the device, or into the cloud account tied to it, they may gain access to logged-in apps, stored credentials, messages, MFA flows, and recovery paths, which is far more valuable than tricking a victim one account at a time. AI-enhanced phishing, malware delivery, voice cloning, and account-takeover techniques are making it easier to get that foothold and use it quickly.
Cases with financial loss are much harder to resolve because the crime has already moved from compromise to monetization. At that point, victims and institutions are no longer dealing with a simple access issue; they are trying to trace and recover money that may already have moved through multiple accounts or fast payment rails, often across institutions. That is why reactive response models break down so badly once money has left the account, and why prevention at the moment of authorization matters more than remediation afterward.
Another finding: fraudulent employment is the most common crime against minors. Minors are attractive targets because they often have clean identities, little or no credit history, and less active monitoring, which makes their information useful for both synthetic identity fraud and employment-related misuse. Children’s SSNs are especially attractive because they can be paired with fabricated details to build a believable synthetic profile.
James Maude, Field CTO at BeyondTrust:
We live in an age where identity compromise is so common that only the most noteworthy losses are worth reporting. Many customer facing organizations will quickly write off losses associated with compromised customer identities as they have accepted that adding additional security that would protect customers’ accounts would only increase friction and lower the likelihood of future purchases. In the age of online shopping and instant gratification, any security mechanisms to challenge a user and verify their identity can be seen as a competitive disadvantage.
Identity has become the new perimeter as businesses and individuals move their entire lives into cloud applications and service meaning that a compromised identity can provide access to large amounts of data and systems. Within the business world we are seeing lines between personal and professional accounts blur meaning that a user’s personal accounts or devices being compromised can impact their business identity as well.
It is so common place now that almost everyone knows someone who has been the victim of identity compromise and there is often a social stigma or element of shame that leads to reduced reporting. If you have heard about scams constantly and then fall victim you might be more likely to try and ignore it and move on than report it and explain why you clicked the link.
To reiterate, identity is the new perimeter. Organizations, as well as individuals, are beginning to realize this and better understand and protect their identity attack surface. At a basic level having robust MFA controls on all high value personal accounts is absolutely essential. At the organization level being able to understand all the paths to privilege an identity has in your environment and proactively reduce those risks is key to success.