That annoying SMS phish you just got may have come from a box like this
The researchers added: “This campaign is notable in that it demonstrates how impactful smishing operations can be executed using simple, accessible infrastructure. Given the strategic utility of such equipment, it is highly likely that similar devices are already being exploited in ongoing or future smishing campaigns.”
Sekoia said it’s unclear how the devices are being compromised. One possibility is through CVE-2023-43261, a vulnerability in the routers that was fixed in 2023 with the release of version 35.3.0.7 of the device firmware. The vast majority of 572 identified as unsecured ran versions 32 or earlier.
CVE-2023-43261 stemmed from a misconfiguration that made files in a router’s storage publicly available through a web interface, according to a post published by Bipin Jitiya, the researcher who discovered the vulnerability. Among other things, some of the files contained cryptographically protected passwords for accounts, including the device administrator. While the password was encrypted, the file also included the secret encryption key used and an IV (initialization vector), allowing an attacker to obtain the plaintext password and then gain full administrative access.
The researchers said that this theory was contradicted by some of the facts uncovered in their investigation. For one, an authentication cookie found on one of the hacked routers used in the campaign “could not be decrypted using the key and IV described in the article,” the researchers wrote, without elaborating further. Further, some of the routers abused in the campaigns ran firmware versions that weren’t susceptible to CVE-2023-43261.
Milesight didn’t respond to a message seeking comment.
The phishing websites ran JavaScript that prevented pages from delivering malicious content unless it was accessed from a mobile device. One site also ran JavaScript to disable right-click actions and browser debugging tools. Both moves were likely made in an attempt to hinder analysis and reverse engineering. Sekoia also found that some of the sites logged visitor interactions through a Telegram bot known as GroozaBot. The bot is known to be operated by an actor named “Gro_oza,” who appears to speak both Arabic and French.
Given the prevalence and massive volume of smishing messages, people often wonder how scammers manage to send billions of messages per month without getting caught or shut down. Sekoia’s investigation suggests that in many cases, the resources come from small, often-overlooked boxes tucked away in janitorial closets in industrial settings.
The U.S. government has shut down as of 12:01 am on October 1, 2025.
According to AP News, the Congressional Budget Office estimates that roughly 750,000 federal employees could be furloughed each day of the shutdown.
Government shutdowns do not impact essential services, such as FBI investigators, air traffic controllers, CIA officers and members of the Armed Forces.
This post was originally published at 11:00 am ET on October 1 and will be updated with more information.
OpenSSL Vulnerabilities Allow Private Key Recovery, Code Execution, DoS Attacks
The OpenSSL Project has announced the availability of several new versions of the open source SSL/TLS toolkit, which include patches for three vulnerabilities.
Versions 3.5.4, 3.4.3, 3.3.5, 3.2.6, 3.0.18, 1.0.2zm and 1.1.1zd of the OpenSSL Library have been released. Most of them fix all three vulnerabilities, tracked as CVE-2025-9230, CVE-2025-9231 and CVE-2025-9232.
Two of the vulnerabilities have been assigned a ‘moderate severity’ rating. One of them is CVE-2025-9231, which may allow an attacker to recover the private key.
OpenSSL is used by many applications, websites and services for securing communications and an attacker who can obtain a private key may be able to decrypt encrypted traffic or conduct a man-in-the-middle (MitM) attack.
However, OpenSSL developers pointed out that only the SM2 algorithm implementation on 64-bit ARM platforms is impacted.
“OpenSSL does not directly support certificates with SM2 keys in TLS, and so this CVE is not relevant in most TLS contexts,” the developers explained. “However, given that it is possible to add support for such certificates via a custom provider, coupled with the fact that in such a custom provider context the private key may be recoverable via remote timing measurements, we consider this to be a Moderate severity issue.”
CVE-2025-9230, described as an out-of-bound read/write issue that can be exploited for arbitrary code execution or DoS attacks, has also been assigned a ‘moderate severity’ rating.
“Although the consequences of a successful exploit of this vulnerability could be severe, the probability that the attacker would be able to perform it is low,” the OpenSSL Project’s security advisory explains.
Advertisement. Scroll to continue reading.
The third vulnerability is ‘low severity’ and it can be exploited to trigger a crash that can result in a DoS condition.
The security of OpenSSL has evolved a great deal since the discovery of the notorious Heartbleed vulnerability.
While some flaws have still made headlines, the number and severity of vulnerabilities found in OpenSSL in recent years has been low. Only three other issues have been resolved to date in 2025 and only one has a ‘high severity’ rating.
The high-severity issue was discovered by Apple researchers and it can allow MitM attacks.
Secondo l’ultima ricerca di FireMon, azienda di sicurezza esperta nella gestione dei dispositivi di rete, il 60% dei firewall aziendali non supera i controlli di conformità ad alta gravità dopo lavalutazione, mentre un 34% non supera i livelli critici.
Il problema deriva non solo da sviste tecniche, ma anche da profondi problemi di governance. I rischi di questa gestione errata comprendono fallimenti degli audit, tempi di inattività operativa e un’esposizione maggiore alle minacce.
FireMon ha individuato configurazioni errate, regole obsolete e policy gonfie nei firewall degli ambienti on-premise, cloud e ibridi; tutto ciò rallenta le prestazioni e rende più difficoltoso il lavoro dei team di sicurezza, i quali fanno fatica a tenere il passo con le minacce.
“La complessità del firewall non è solo un problema di configurazione, è una minaccia alla resilienza e alla fiducia“, ha dichiarato Jody Brazil, CEO e fondatore di FireMon. “I team di sicurezza sono sepolti da policy che non riescono a spiegare, a mappare agli obiettivi aziendali o a gestire su larga scala“.
Dal report emergono anche altri dati preoccupanti: il 95% degli oggetti delle applicazioni e l’82% degli oggetti dei servizi non vengono utilizzati e creano un overhead che non solo non è necessario, ma incrementa la superficie di attacco.
Il 30% delle regole dei firewall non viene usato, mentre il 62,6% non ha documentazione, introducendo lacune di audit e riducendo la trasparenza operativa. Infine, oltre il 10% delle regole è ridondante od ombreggiato.
La situazione è allarmante: la maggior parte dei firewall aziendali non ha un adeguato livello di sicurezza e non è compliant. È necessario quindi che le organizzazioni comincino a monitorare attentamente le configurazioni delle proprie reti per individuare in tempo reale configurazioni errate, regole incomplete, ridondanti o inadatte e il reale utilizzo dei servizi attivi, preferendo un approccio proattivo.
Chinese APT ‘Phantom Taurus’ Targeting Organizations With Net-Star Malware
A Chinese state-sponsored hacking group tracked as ‘Phantom Taurus’ has been targeting government and telecommunications organizations for espionage for more than two years, Palo Alto Networks reports.
Initially observed in 2023, the APT was only recently linked to Chinese hacking groups through shared infrastructure, as its tactics, techniques and procedures (TTPs) differ from those typically associated with threat actors operating out of China.
“These enable the group to conduct highly covert operations and maintain long-term access to critical targets,” says Palo Alto Networks.
The group, the cybersecurity firm explains, uses shared operational infrastructure exclusive to Chinese APTs, and targets high-value organizations (such as ministries of foreign affairs and embassies), in line with China’s economic and geopolitical interests.
What sets Phantom Taurus apart, however, is the use of a different set of TTPs, some unique to the group, such as its Specter and Net-Star malware families, and the Ntospy malware. Tools typically used by Chinese hackers, such as China Chopper, the Potato suite, and Impacket, are also part of its inventory.
The APT has been observed targeting email servers to exfiltrate messages of interest, as well as directly targeting databases, in attacks against organizations in Africa, the Middle East, and Asia.
In 2025, the group started using Net-Star, a .NET malware suite targeting IIS web servers, which consists of three web-based backdoors: IIServerCore (a fileless backdoor) and two AssemblyExecuter variants (.NET malware loaders).
The IIServerCore backdoor operates entirely in memory. It can receive and execute payloads and arguments, and can send the result to the command-and-control (C&C) server.
Advertisement. Scroll to continue reading.
It supports built-in commands to perform file system operations, access databases, execute arbitrary code, manage web shells, evade and bypass security solutions, load payloads directly in memory, and encrypt communication with the C&C.
The first malware loader, AssemblyExecuter V1, can execute other .NET assemblies in memory, allowing the attackers to dynamically load and execute additional code post-compromise.
AssemblyExecuter V2 has the same core purpose, but features enhanced evasion capabilities, with dedicated methods for bypassing Windows’s Antimalware Scan Interface (AMSI) and Event Tracing for Windows (ETW) security mechanisms.
“We observed that the group takes an interest in diplomatic communications, defense-related intelligence and the operations of critical governmental ministries. The timing and scope of the group’s operations frequently coincide with major global events and regional security affairs,” Palo Alto Networks says.
Canadian Airline WestJet Says Hackers Stole Customer Data
Canadian airline WestJet this week confirmed that customer personal information was stolen in a June 2025 cyberattack.
The incident, disclosed on June 13, involved unauthorized access to several internal systems and impacted the availability of WestJet’s application and website.
The airline’s operations were not affected by the attack, and WestJet restored access to its application and website roughly two days after the incident.
In July, WestJet said the incident had been fully contained and additional security measures were implemented, adding that the hackers were able to steal certain data from its systems.
This week, the airline revealed that the personal information provided by travelers for reservations or travel has been compromised.
According to the company, names, contact information, government-issued IDs, and other information provided by customers was stolen, but no credit/debit card details or passwords were obtained.
“While it is possible that some of this information could be used for identity theft or fraud (including in the context of any booked travel), WestJet is not aware of any misuse of the relevant data for such purposes,” the company said.
WestJet has started notifying the potentially affected individuals and is providing them with identity theft protection services.
Advertisement. Scroll to continue reading.
The company also published an FAQ on the incident, along with identity protection recommendations.
Additionally, WestJet is warning customers to be wary of suspicious emails, text messages, or calls from individuals impersonating the airline, who might ask for payment card information.
NIST Publishes Guide for Protecting ICS Against USB-Borne Threats
NIST has published a new guide designed to help organizations reduce cybersecurity risks associated with the use of removable media devices in operational technology (OT) environments.
NIST Special Publication (SP) 1334 was authored by the National Cybersecurity Center of Excellence (NCCoE) and it focuses on the use of USB flash drives, but also mentions other types of removable media such as external hard drives and CD/DVD drives.
USB flash drives are often used in OT environments to conduct firmware updates or to retrieve data for diagnostics purposes, but such devices are also often a source of malware infections.
While the cybersecurity industry has long warned organizations about the security risks, the use of USB drives in OT environments still poses a significant threat to industrial control systems (ICS) and recent research has shown that while such drives typically carry commodity malware, threats are becoming increasingly sophisticated and targeted at OT.
“If a USB device is infected with malware, it can spread to the industrial control system and cause problems, such as disrupting operations or compromising safety,” NIST warned.
NIST SP 1334 condenses all relevant information on protecting ICS against USB-borne threats into a two-page document.
The guide covers four aspects: procedural controls, physical controls, technical controls, and transportation and sanitization.
In terms of procedural controls, the guide advises organizations to develop policies for purchasing, authorizing and managing devices they own, and to consider all other devices as untrusted. The acquired devices should adhere to modern security standards and their use should be limited to specific personnel and purposes.
Advertisement. Scroll to continue reading.
As for physical controls, devices should be stored in a physically secure location, and they should be inventoried and labeled.
The section of NIST’s guide on technical controls recommends disabling unnecessary ports to prevent unauthorized use, scanning devices for malware before and after use, disabling autorun, encrypting data stored on portable storage media, and enabling write-protection when possible.
The agency also recommends having procedures in place for transporting devices within and between organizations, and performing data sanitization prior to the disposal of the device.
Companies such as Honeywell have been offering dedicated cybersecurity solutions designed to protect industrial facilities from USB-borne threats.
Descope Raises $35 Million in Seed Round Extension
Identity and access management (IAM) provider Descope has announced raising $35 million in a seed funding extension that brings the total raised by the company to $88 million.
The cash infusion came from existing investors Cerca Partners, Dell Technologies Capital, Lightspeed Venture Partners, Notable Capital, Triventures, and Unusual Ventures.
Founded in 2022, the Los Altos, California-based startup landed a large $53 million seed funding round in 2023, aiming to disrupt the customer identity and authentication market.
Descope provides a no-code / low-code external IAM platform that supports user, business customer, partner application, and AI agent identity management, delivering comprehensive visibility and preventing account takeover.
The solution enables organizations to add new identities through visual workflows that support both the frontend experience and backend logic, to easily manage, merge, and sync identities, and add security controls to prevent phishing and credential stuffing attacks.
Descope says its solution is used by hundreds of organizations of all sizes across multiple industries in the Americas, EMEA, and APAC regions.
The startup will invest the new funds in agentic identity research and development, and plans to expand to new regions and hire more talent across its engineering, customer experience, and product teams.
“The rise of AI agents and MCP servers requires a security rethink with identity at its center. Descope is already establishing itself as a force in the customer identity market, with innovation and product velocity that have laid the groundwork for it to become the go-to identity provider for AI agents and MCP server ecosystems as well,” Notable Capital managing partner Oren Yunger said.
Cybersecurity Awareness Month 2025: Prioritizing Identity to Safeguard Critical Infrastructure
This October marks the 22nd anniversary of Cybersecurity Awareness Month, an initiative launched under the guidance of the U.S. Department of Homeland Security. Its purpose is to highlight the importance of taking daily action to reduce risks when online and when using connected devices.
This year’s theme focuses on government entities and small and medium-sized businesses that are vital to protecting the systems and services that keep our communities running. These organizations play a central role in safeguarding the nation’s critical infrastructure. Under the Cybersecurity and Infrastructure Security Agency’s (CISA) banner of “Building a Cyber Strong America,” state, local, tribal, and territorial governments, as well as private companies that own and operate critical infrastructure, are urged to strengthen their defenses against cyber threats to improve resilience and security.
Recent incidents highlight the urgency of this call. Telecom companies in the U.S. and Canada have suffered major disruptions. A U.S. National Guard unit was hacked. Other attacks have targeted critical infrastructure sectors such as communications, manufacturing, utilities, transportation, and energy. Each of these incidents demonstrates how much work remains to secure the industries that support daily life.
It is commendable that CISA uses October to spotlight the importance of cyber resilience and stronger security controls. However, security practitioners face these threats year-round and need little reminder of the risks. The real question is where organizations should invest time and resources to strengthen their cybersecurity strategies.
A closer look at the anatomy of modern cyberattacks offers guidance. Effective defense is not about the sheer number of tools in place. It is about ensuring those tools work together to disrupt the attack chain at every stage.
Why Identity Remains the Most Exploited Attack Vector
Technologies and attack techniques evolve constantly, yet one fact remains unchanged: identities are still the most common attack vector. Despite billions of dollars invested in firewalls, endpoint detection, and zero-day defenses, attackers often bypass these controls by compromising valid credentials.
Industry reports confirm what CISOs already know. More than 70 percent of breaches involve the misuse of identities, whether through credential theft, phishing, or the abuse of privileged accounts. The rapid growth of SaaS applications, cloud workloads, and remote work has made the identity perimeter the enterprise perimeter. Traditional network boundaries no longer exist. Every user, device, and application login is now a potential entry point.
Advertisement. Scroll to continue reading.
Attackers target identities because it is the most efficient path. Increasingly, adversaries are not hacking in—they are logging in. Valid credentials give them direct access for persistence, lateral movement, and data exfiltration. Unlike malware or brute-force intrusions, identity-based attacks blend in with normal activity. Phishing for employee logins or exploiting over-privileged service accounts is inexpensive, scalable, and highly effective.
Closing the Identity Gap
If identity is the new perimeter, then protecting it must be the top priority. This requires a shift from reactive, compliance-driven identity management to proactive identity security. Practical steps include:
Implementing least privilege at scale: Reduce attack surface by eliminating unnecessary access rights.
Continuous monitoring of identity behavior: Look for anomalies, not just failed logins.
Securing non-human identities: Service accounts, APIs, and machine identities are often overlooked yet highly vulnerable.
Adopting phishing-resistant authentication: Move beyond passwords and legacy multi-factor authentication (MFA) to more resilient methods.
Augmenting traditional identity and access management (IAM) tools: Incorporate emerging identity threat detection and risk mitigation solutions that enable dynamic, multi-layered risk orchestration.
The message of Cybersecurity Awareness Month 2025 is clear. Awareness alone is not enough. Identity security must move from being viewed as an IT hygiene issue to becoming a board-level priority. Attackers are no longer breaking in. They are logging in. Until organizations address identity as the foundation of their security strategy, breaches will continue to make headlines.
This October is the right time for organizations to reassess their defenses, modernize their identity protections, and build resilience against the most exploited attack vector. Identity security is not just one more layer of defense. It is the foundation of cybersecurity in 2025 and beyond.
Approccio MindShield: un modello di sicurezza multilivello per infrastrutture critiche
Questo contenuto fa parte della serie MindShield, dedicata a un paradigma innovativo di sicurezza integrata per infrastrutture critiche e servizi pubblici essenziali.
Nel presente articolo approfondiremo l’approccio MindShield, un modello metodologico multilivello progettato per potenziare gli standard di sicurezza in contesti strategici. Analizzeremo l’architettura del sistema e i suoi elementi fondanti, che integrano aspetti umani, tecnologici, normativi e di cooperazione internazionale, con l’obiettivo di costruire una rete di protezione capillare e resiliente.
MindShield per la sicurezza delle infrastrutture critiche
Avendo delineato i principi teorici possiamo introdurre l’argomento alla base di questo lavoro di ricerca, ovvero il modello Mindshield. Tale approccio metodologico ha come obiettivo quello di implementare gli standard di sicurezza delle infrastrutture critiche e dei servizi pubblici essenziali.
Presupposte quindi le criticità che tutt’oggi albergano nell’ecosistema della sicurezza infrastrutturale, si devono cercare nuove soluzioni in grado di prevenire e rispondere tempestivamente alle sfide securitarie. Tuttavia, è necessario sottolineare che tale proposta non può intendersi come un mero modello teorico, avulso quindi dal contesto attuale della security. Al contrario invece, come già anticipato, il modello MindShield pone le fondamenta nell’evoluzione normativa e tecnologica già raggiunta e si prefigge di creare una capillare rete di sicurezza a servizio di tutti i soggetti coinvolti dal cittadino alle istituzioni globali.
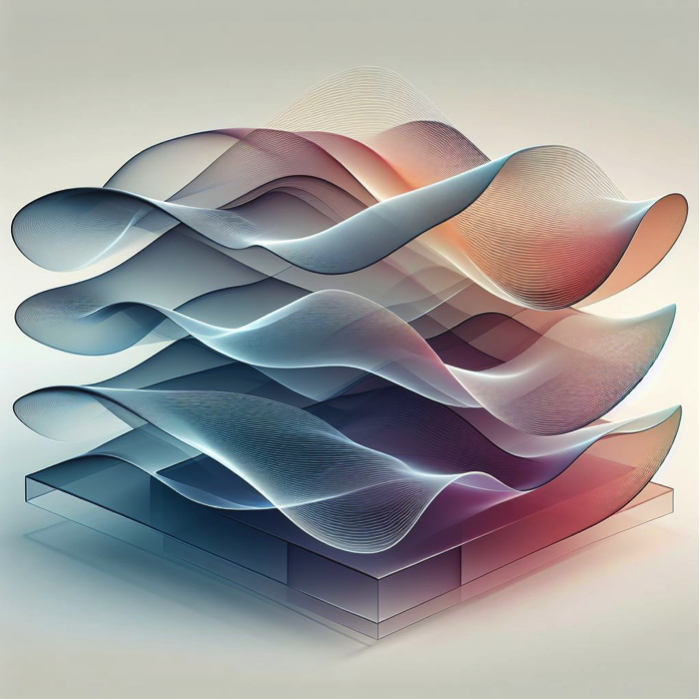
Arrivati qui ci si chiede dunque, in che modo possa essere articolato tale progetto. Ebbene MinShield si configura come un modello di sicurezza a più livelli, nel quale i singoli componenti, che possiamo immaginare come “strati di sicurezza”, sono tra essi complementari. Difatti, la sovrapposizione di tali livelli e il loro contemperamento sinergico hanno come obiettivo la creazione di un tessuto securitario il più possibile inespugnabile e resiliente.
I singoli elementi di cui MindShield si comporrà saranno meglio approfonditi nel prosieguo, tuttavia, quel che ci interessa rilevare in questa fase è che il modello proposto non ha come scopo quello di dare delle linee operative tassative bensì di fornire un approccio metodologico che potrà essere declinato secondo le circostanze e tenendo conto della domanda di sicurezza di ogni singolo contesto. È difatti innegabile che a livello territoriale, e già a partire già dalle realtà locali a noi vicine, esiste un forte divario, in tema di sicurezza.
Alcuni virtuosi esempi esistono già, tra questi a mero titolo esemplificativo ricordiamo nella realtà italiana il Porto di Civitavecchia, che continua ad investire costantemente nella sicurezza, formazione e prevenzione, così come il Comune di Fucecchio, località nella quale, nonostante le risorse limitate e le complesse sfide del territorio si continua a studiare e a operare laboriosamente per il mantenimento della sicurezza urbana.
Di contro però, esistono altresì importanti realtà ove la sicurezza risulta ancora una metà lontana ed è anche a queste ultime, così come alle realtà più virtuose, che il modello MindShield si rivolge. Peraltro, a prescindere dagli sforzi compiuti in ambito securitario dalle differenti realtà nazionali o globali, non è possibile ignorare la sempre maggiore domanda di equità, sostenibilità, libertà e rispetto dei valori. Obiettivi che, tuttavia, non possono considerarsi raggiunti ove i cittadini non si sentano o, peggio, non vivano in condizioni di sicurezza.
A conclusione di tale parte introduttiva si rimanda ad una figura evocativa per comprendere l’approccio multilivello di MindShield.
Figura 3 – MindShield – rappresentazione grafica dell’approccio multilivello
Architettura e componenti chiave dell’approccio MindShield
Il modello oggetto di questo lavoro di ricerca è stato ipotizzato come somma di più elementi. Difatti, per incrementare il grado di sicurezza complessiva delle infrastrutture critiche, come già menzionato, è necessaria l’azione sinergica di ognuno dei presenti componenti e segnatamente:
la componente umana (tale elemento racchiude tutte le attività umane a supporto della sicurezza, dai controlli fisici, all’utilizzo di tecniche come l’human intelligence e profilazione psicologica);
la componente di ricerca (ossia tutte le attività di ricerca e sviluppo in tema di sicurezza);
la componente tecnologica e di innovazione (all’interno di tale categoria troviamo tutte le tecniche e tecnologie applicabili per garantire e implementare la sicurezza delle infrastrutture critiche dall’intelligenza artificiale ai “Big Data”, dai programmi di riconoscimento facciale alle tecniche di rilevamento degli esplosivi);
la componente legislativa (che impone l’implementazione e l’armonizzazione delle normative a livello locale, nazionale e sovranazionale, ivi compresa la regolamentazione in termini di formazione e aggiornamento dei soggetti preposti alla security);
la cooperazione internazionale (mediante la creazione una cabina di regia superpartes, operante a livello globale con sedi operative distaccate in ciascuno degli Stati aderenti e previsione di agevolazioni per i Paesi che si adeguano agli standard di sicurezza adottati a livello sovranazionale);
collaborazione Stato – Privati (implementazione dei partenariati pubblico-privati, cosiddetti PPP, in tema di sicurezza)
La convergenza di tali elementi rende l’approccio MindShield non solo operativo in una moltitudine di contesti ma anche modellabile e plasmabile a qualunque realtà e stato di avanzamento delle politiche securitarie.
È bene tuttavia osservare che qualunque modello non potrà mai assicurare una prevenzione assoluta degli incidenti securitari, proprio per tale ragione questo approccio non può prescindere dal considerare la seconda anima della sicurezza ovvero quella di risposta e gestione della crisi. Investire sulla sicurezza difatti, risulta sì utile ogniqualvolta una minaccia viene evitata o una vulnerabilità sanata, ma è sensibilmente più impattante nei momenti in cui un incidente si verifica perché la gestione consapevole di tali circostanze spesso fa la differenza tra la vita e la morte delle persone coinvolte.
Rilevazione e mitigazione delle minacce
Per una gestione della sicurezza consapevole nell’era digitale risulta fondamentale un approccio metodologico fondato sulla rilevazione dei dati, l’analisi delle tendenze e la progettazione di piani di prevenzione “sartoriali”. Inoltre, la dinamicità con la quale persone e cose si spostano quotidianamente rendono necessario l’utilizzo di tecnologie avanzate per identificare, analizzare e rispondere alle minacce in tempo reale. La somma di tali processi difatti, conduce ad un risultato importante: la mitigazione delle minacce alla sicurezza delle infrastrutture critiche.
Come base di partenza per la strutturazione di questo modello sarà quindi necessario provvedere a:
Rilevazione dei dati. Garantire una rilevazione dei dati omogenea, fedele ed eticamente responsabile. Tale processo rappresenta difatti il primo passo per identificare le potenziali minacce. La rilevazione richiederà l’uso di sensori, reti di telecamere, droni, satelliti, oltre ad un ampio compendio di tecnologie che garantiranno la raccolta e la trasmissione dati in tempo reale. La fase di raccolta comprenderà altresì l’acquisizione di gradi quantità di dati provenienti dai flussi informativi e canali mediatici. A mero titolo esemplificativo le tipologie di dati raccolti potranno includere informazioni sul traffico, le condizioni meteorologiche, l’attività umana, i consumi e altro ancora. Tuttavia, è proprio l’ampia portata dei dati ottenibili a porci alcuni interrogativi sulle implicazioni etiche e legali di tale processo.
Analisi. I dati così raccolti dovranno in seguito essere analizzati e processati utilizzando algoritmi di apprendimento automatico e intelligenza artificiale ma senza tralasciare una scrupolosa supervisione umana. Questi algoritmi potranno difatti identificare modelli e tendenze nei dati, permettendo di rilevare anomalie o attività sospette. Ad esempio, un aumento improvviso del traffico in un’area specifica potrebbe indicare un potenziale attacco. Tuttavia, data la delicatezza e l’importanza strategica di tali informazioni, il loro processamento dovrà avvenire solamente alla presenza e sotto l’attenta supervisione di personale qualificato.
Piani di prevenzione. Sulla base dell’analisi dei dati, dovranno essere progettati piani di prevenzione specifici. Questi piani dovranno includere misure di sicurezza fisica, come barriere e controlli di accesso, così come misure di sicurezza cibernetica, come firewall e sistemi di rilevamento delle intrusioni. Inoltre, i piani di prevenzione dovranno disporre procedure di risposta alle emergenze, formazione del personale ed esercitazioni di simulazione.
Aggiornamento e monitoraggio costante. Infine, i piani di prevenzione dovranno essere implementati e monitorati costantemente. Questo processo comprenderà l’aggiornamento regolare dei piani in base ai nuovi dati raccolti e all’evoluzione delle minacce. Inoltre, sarà essenziale effettuare una periodica verifica dell’efficacia e adeguatezza dei piani di prevenzione rapportandogli agli incidenti di sicurezza occorsi in un dato periodo.
In conclusione, la disposizione di un protocollo di sicurezza che includa tali fasi consentirà di identificare e rispondere alle minacce in modo proattivo, proteggendo le infrastrutture critiche e garantendo la sicurezza collettiva.
Il modello MindShield rappresenta una rivoluzione nel paradigma della sicurezza integrata per infrastrutture critiche e servizi pubblici essenziali. L’approccio multilivello presentato dimostra come la convergenza tra componenti umane, tecnologiche e legislative possa creare un sistema di protezione resiliente e adattabile.
Nel prossimo contenuto della serie esploreremo le innovazioni a difesa delle infrastrutture critiche: psicologia predittiva, human intelligence e OSINT, AI e machine learning e IoT, analizzando nel dettaglio come queste tecnologie emergenti si integrano nel framework MindShield per fornire una protezione proattiva e intelligente delle nostre infrastrutture strategiche.
Note
[1] Immagine generata con l’intelligenza artificiale di Microsoft Bing URL
Profilo Autore
Laureata in Giurisprudenza all’Università degli Studi di Milano, si è specializzata con il massimo dei voti in Scienze Forensi presso l’Università La Sapienza di Roma, con focus su sicurezza globale, infrastrutture critiche e crimini contro categorie vulnerabili. Ha acquisito esperienza nella pubblica amministrazione attraverso il Servizio Civile Nazionale e lavorando per diverse amministrazioni pubbliche, occupandosi di contabilità pubblica, servizi sociali e servizio pubblico nei Ministeri degli Interni e della Giustizia. Attualmente è funzionaria presso il Ministero della Giustizia, in servizio al Tribunale di Milano – XII Sezione Civile, dove si occupa di diritto dell’immigrazione, protezione internazionale e diritto di soggiorno. Ha partecipato a formazioni di eccellenza organizzate dalla Scuola Nazionale della Magistratura, dal Ministero della Giustizia e dall’Agenzia Europea per l’Asilo (EUAA), acquisendo competenze nella valutazione delle domande di Protezione Internazionale e nella produzione di Report COI. In conclusione del tirocinio forense, mentre si prepara a conseguire il titolo di avvocato, sta perseguendo una seconda laurea magistrale in psicologia del lavoro e delle organizzazioni.