Broadcom Fails to Disclose Zero-Day Exploitation of VMware Vulnerability

A newly patched high-severity VMware vulnerability has been exploited as a zero-day since October 2024 for code execution with elevated privileges, NVISO Labs reports.

Tracked as CVE-2025-41244 (CVSS score of 7.8), the security defect impacts both VMware Aria Operations and VMware Tools.

VMware’s parent company Broadcom rolled out patches this week, warning that the flaw allows attackers to escalate their privileges to root on VMs that have VMware Tools installed and are managed by Aria Operations with SDMP enabled, but made no mention of its in-the-wild exploitation.

The company’s public advisories typically warn customers if zero-day exploitation has been detected. 

According to NVISO, which was credited for the find, a Chinese state-sponsored threat actor tracked as UNC5174 has been exploiting the bug for a year. UNC5174 was recently linked to an attack on cybersecurity firm SentinelOne.  

“We can however not assess whether this exploit was part of UNC5174’s capabilities or whether the zero-day’s usage was merely accidental due to its trivialness,” NVISO notes.

The vulnerability impacts VMware Aria Operations’ service and application discovery feature, which includes both legacy credential-based service discovery (in which VMware Tools acts as a proxy for the operation) and credential-less service discovery (metrics collection implemented in VMware Tools).

“As part of its discovery, NVISO was able to confirm the privilege escalation affects both modes, with the logic flaw hence being respectively located within VMware Aria Operations (in credential-based mode) and the VMware Tools (in credential-less mode),” NVISO explains.

Advertisement. Scroll to continue reading.

Noting that successful exploitation of CVE-2025-41244 allows unprivileged users to execute code with root privileges, NVISO warns that the open source variant of VMware Tools, namely open-vm-tools, which is included in major Linux distributions, is also impacted.

Open-vm-tools’ discovery function, NVISO says, calls a function that takes as argument a regular expression pattern that checks it to match supported service binaries.

However, because the function uses the broad‑matching \S character class in several regex patterns, it also matches non-system binaries located in directories writable to non-privileged users.

Thus, an attacker can abuse a vulnerable open-vm-tools iteration by staging a malicious binary in a broadly-matched regular expression path, and it will be elevated for version discovery.

UNC5174, NVISO notes, has been exploiting the security weakness by placing malicious binaries in the /tmp/httpd folder. To be elevated, the binaries are executed with low privileges and open a random listening socket.

Broadcom fixed the flaw in fresh releases of VMware Cloud Foundation, vSphere Foundation, Aria Operations, Telco Cloud Platform, and VMware Tools, and noted that fixes for open-vm-tools will be distributed by Linux vendors.

To detect CVE-2025-41244’s exploitation, organizations should look for uncommon child processes. In environments without monitoring, analysis of lingering metrics collector scripts and outputs in legacy credential-based mode should confirm the exploitation.

“The broad practice of mimicking system binaries (e.g., httpd) highlights the real possibility that several other malware strains have accidentally been benefiting from unintended privilege escalations for years,” NVISO says, noting that the bug could easily be found in the open-vm-tools source code by threat actors.

Related: Call for Presentations Open for 2025 CISO Forum Virtual Summit

Related: Google Patches Gemini AI Hacks Involving Poisoned Logs, Search Results

Related: Apple Updates iOS and macOS to Prevent Malicious Font Attacks

Related: Organizations Warned of Exploited Sudo Vulnerability

https://www.securityweek.com/broadcom-fails-to-disclose-zero-day-exploitation-of-vmware-vulnerability/


3 Ways to Bolster Security This Cybersecurity Awareness Month

October marks Cybersecurity Awareness Month. While improving cybersecurity is a year-round initiative, this month serves as an excellent opportunity for organizations to reorient their security priorities to better reflect the modern threat landscape. 

Below, security leaders discuss three key ways security teams can empower their organizations to better protect against cyber threats. 

1. Increase Visibility for Artificial Intelligence and Agentic AI 

Prakash Mana, CEO of Cloudbrink:

AI is the next big hurdle for security teams, especially on the software development side. Companies need to make sure that users don’t use AI to create hacking bots either on purpose or accidentally. They also need AI access controls so that AI can only access the services it should. Otherwise you leave yourself open to bad actors who could force agents to access bad sources. Visibility into AI activity is key to safe use.

Agentic AI adoption is increasing at breathtaking speed due to the huge efficiency improvements, but it also throws challenges like shadow AI, AI access controls and of course AI-targeted security attacks like zero-day threats, etc. For both Agentic AI developers, vendors and AI consumers (enterprises using AI agents), it is imperative to give visibility into shadow AI, protect their networks and infrastructure, and do all these without compromising performance of the AI Agents.”

Most AI agent developers are focused on efficiency, not security. The first step for security teams is to create visibility. Establish a way to monitor AI to see what it’s accessing, which users are using it, and what they’re using it for. If you don’t have an AI policy already, you need to create one now.

2. Bolster Identity Security 

Karl Holmqvist, Founder and CEO at Lastwall:

“Secure Our World” lands differently this year. Allied security agencies have dropped the euphemisms. Adversarial state actors are pre-positioning in critical infrastructure and on the edge gear we forget to watch. The job this year should be about moving the few levers that bend risk fastest under real-world constraints.

As we vector into 2026, try to start where the adversary does. Require routers, VPNs, and firewalls to produce forensically capable logs and prove you can pull them.

Harden identity, especially where friction pays. Make phishing-resistant MFA mandatory for admins and all critical systems. Shorten token lifetimes and bind sessions to devices. Where you need to, allow exceptions, but log and expire them quickly.

Build or maintain a live cryptography register, make sure you plan your cutovers to NIST’s post-quantum cryptography (FIPS 203/204/205), and have plans to practice rollouts so you know how various networks and systems react.

To borrow a phrase, measure what matters. Build and then improve change-latency metrics. Awareness is the start, but readiness is proof.

Organizations that practice identity integrity, edge evidence, and cryptographic agility will have an easier time navigating 2026. For most, there is a lot to change. For many, it won’t be easy to do all these things, which is why it is important to start taking the action you can now. Don’t wait until it’s too late.

3. Secure File Transfers

Jeremy Fong, VP of Product at OPSWAT:

As the 22nd annual Cybersecurity Awareness Month urges us to “Secure Our World,” the speed at which data moves is as important as the integrity with which it is managed. File transfers remain one of the most common — and most vulnerable — points of exposure. In the AI era, where adversaries weaponize automation to embed malicious content or bypass traditional defenses, organizations cannot afford to treat this as routine infrastructure.

Managed File Transfer (MFT) should be seen not as legacy technology but as a strategic control. Its value lies in verifiable security: encryption, access policies, and auditable trails that demonstrate accountability. These capabilities are increasingly non-negotiable, as regulators from the SEC to the EU’s DORA demand provable safeguards.

To “Secure Our World” year-round, leaders should take three actions:

  1. Elevate secure file transfer to the boardroom — it is a trust and resilience issue, not just an IT concern.
  2. Mandate consistent controls across cloud, hybrid, and on-prem environments.
  3. Continuously test and adapt processes to anticipate AI-driven threats.

Securing how data moves is securing how business operates. In an era defined by speed, complexity, and growing cyber risk, MFT is not optional but foundational to long-term resilience and trust — exactly the kind of proactive measure Cybersecurity Awareness Month urges every organization to adopt.

Improving Defenses This Cybersecurity Awareness Month 

These three steps can go a long way to improve security, but it is not the end of the journey. Cyber threats are constantly evolving, and with them, so must the defenses. 

Ultimately, there is no singular way to guarantee success against cyber adversaries. But by remaining aware and proactive, organizations can bolster their security and be better prepared for tomorrow’s threats. 

https://www.securitymagazine.com/articles/101938-3-ways-to-bolster-security-this-cybersecurity-awareness-month


Battering RAM Attack Breaks Intel and AMD Security Tech With $50 Device

Researchers have disclosed the details of a new hardware attack that has been demonstrated against AMD and Intel systems, but the chip giants do not appear concerned as the method requires physical access to the targeted device.

The attack method, named Battering RAM, was discovered by a team of academic researchers representing KU Leuven in Belgium and the University of Birmingham and Durham University in the UK.

The researchers late last year disclosed the details of BadRAM, an attack that used $10 equipment to break AMD’s trusted execution environment protections, enabling attackers to gain access to potentially sensitive information stored in memory.

They have now presented Battering RAM, which can bypass modern defenses delivered by Intel and AMD cloud processors. 

According to the researchers, the attack can break Intel SGX and AMD SEV-SNP confidential computing technologies that are widely used by cloud providers and designed to protect sensitive data even from malicious insiders and attackers who have access to the host system. 

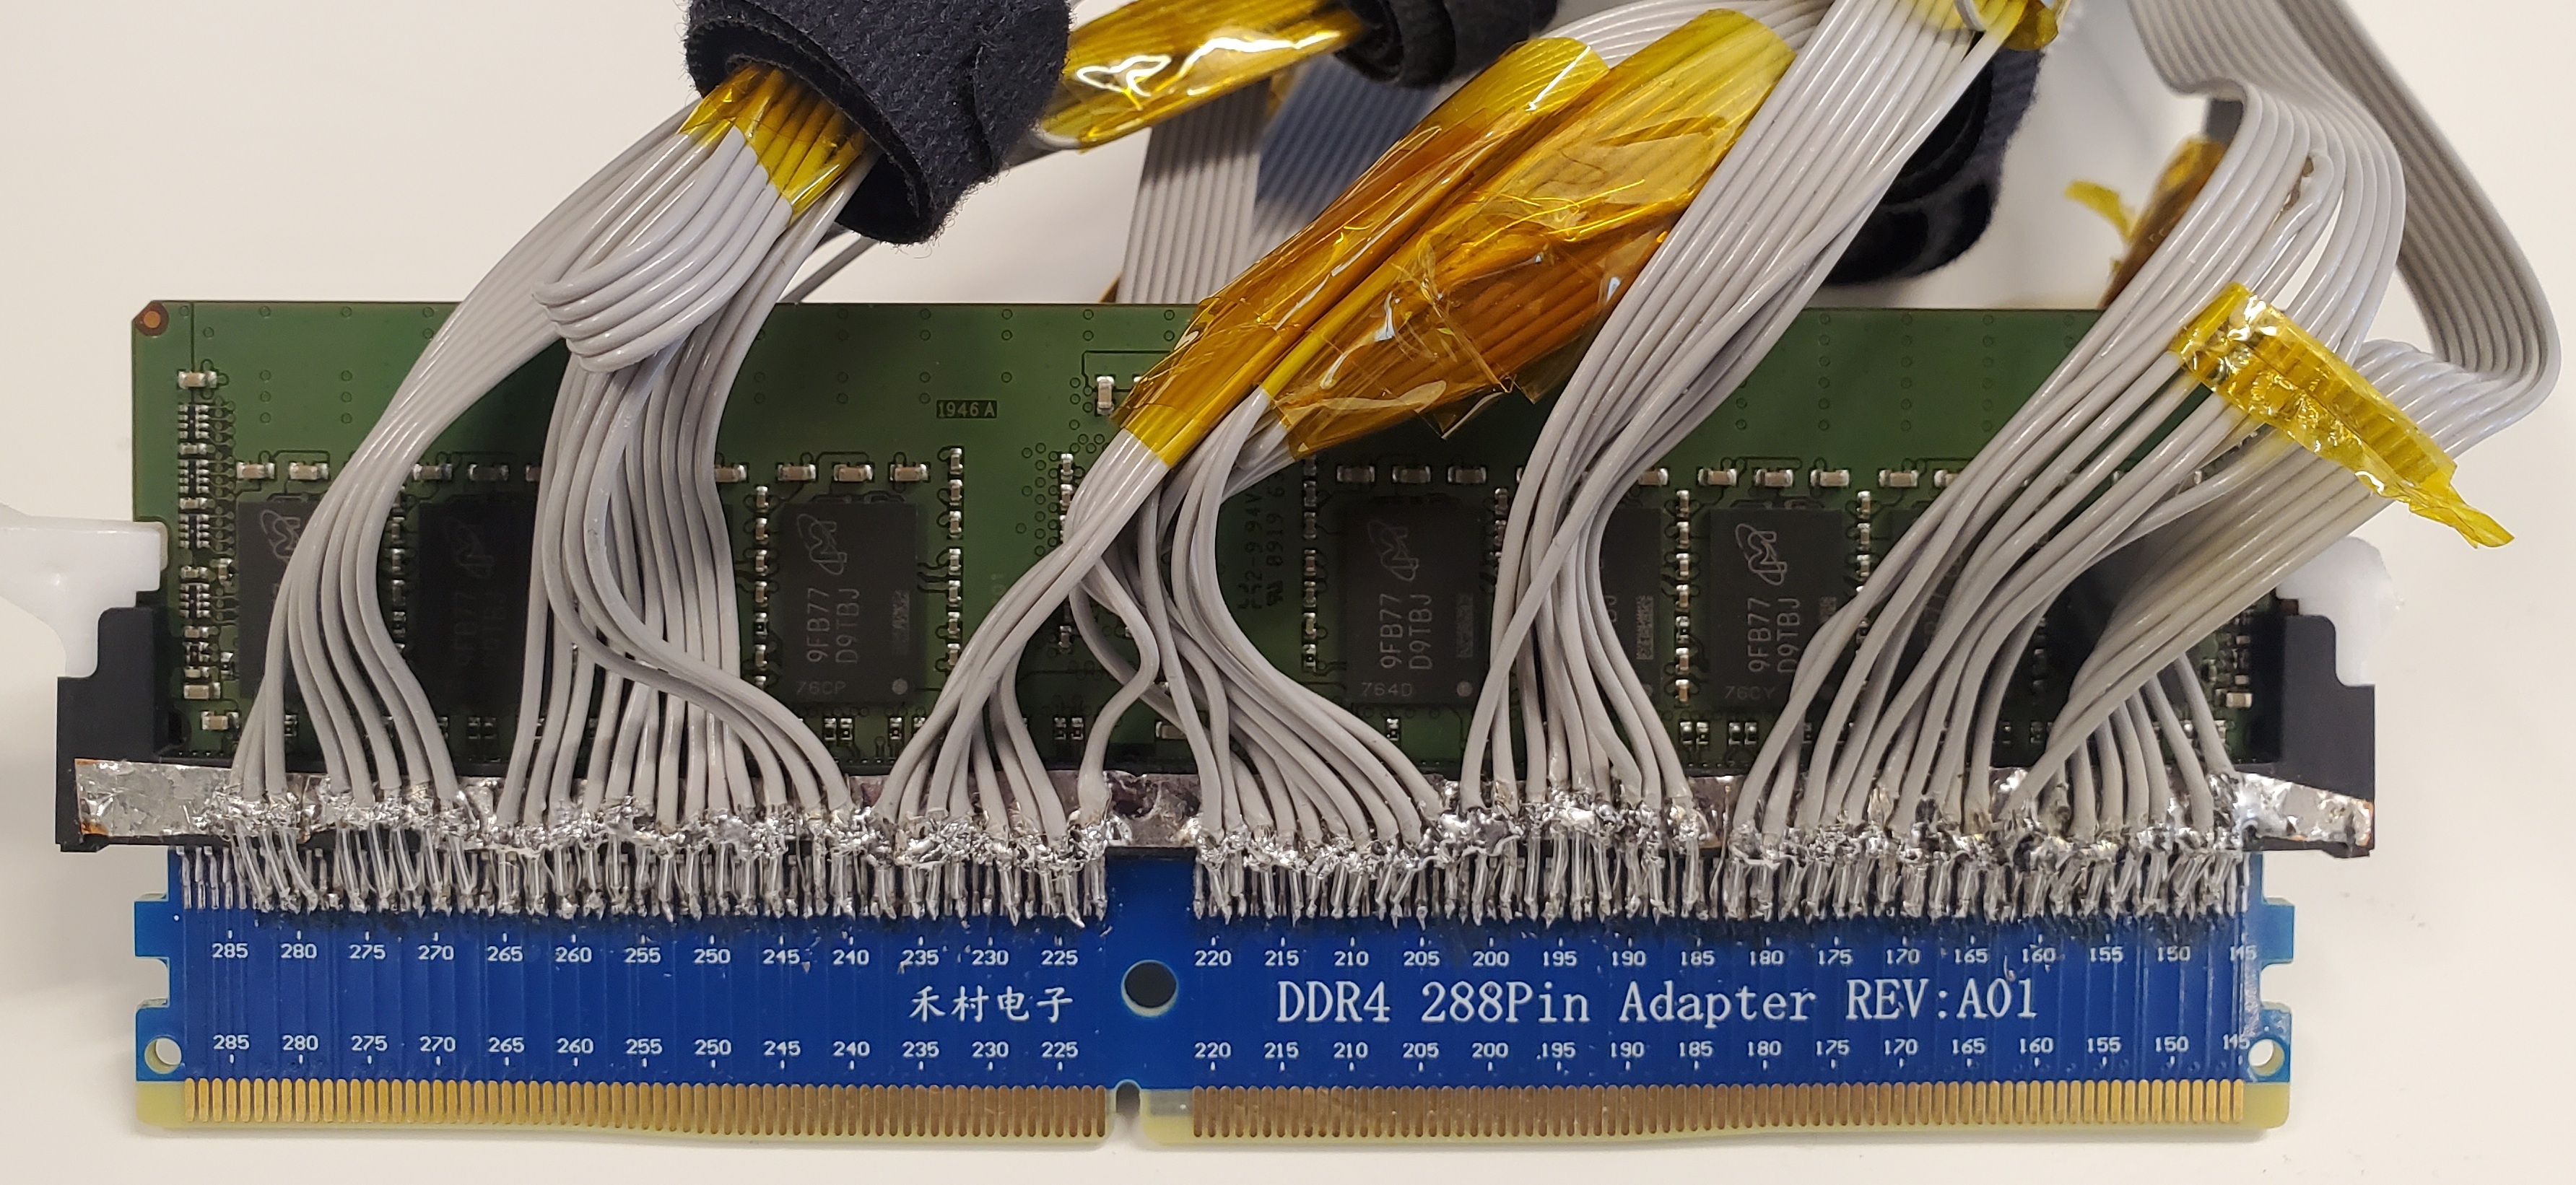
Battering RAM involves planting a device called an interposer between the CPU and the DRAM memory. The interposer, which the researchers managed to build for only $50, is attached to the DIMM and can sit quietly to avoid detection. However, with the flip of a switch, the device can be enabled to silently redirect protected memory addresses to locations controlled by the attacker.

“Our stealthy interposer bypasses both memory encryption and state-of-the-art boot-time defenses, invisible to the operating system,” the researchers explained. “It enables arbitrary plaintext access to SGX-protected memory, and breaks SEV’s attestation feature on fully patched systems. Ultimately, Battering RAM exposes the limits of today’s scalable memory encryption.”

Conducting a Battering RAM attack requires physical access to the targeted system, but the researchers argue that the attacker only needs access to the device for a short amount of time. They believe that in real world environments such attacks may be conducted by rogue cloud employees, data center technicians, law enforcement, and through supply chain attacks targeting memory modules during manufacturing or shipping.

Advertisement. Scroll to continue reading.

The researchers noted that the interposer they designed only works against DDR4 memory, but they believe a more advanced interposer may be able to conduct attacks on DDR5 as well due to the underlying issue not being fixed.

Intel and AMD were notified about the findings in February 2025. While both vendors published security advisories on Tuesday, the day the research was published, they both pointed out that attacks requiring physical access to the targeted system are not in scope of their products’ threat model.

Intel pointed out that some of its Xeon processors include a feature named Total Memory Encryption – Multi-Key (TME-MK), which can provide additional protection against such attacks. The vendor also urged customers to ensure the physical protection of devices, including through tools provided by the company. 

The researchers confirmed that software or firmware updates cannot patch the vulnerability.

In addition to a paper describing the findings, the experts made public all the technical information needed to build a Battering RAM interposer. 

Related: Intel TDX Connect Bridges the CPU-GPU Security Gap

Related: Chipmaker Patch Tuesday: Many Vulnerabilities Addressed by Intel, AMD, Nvidia

Related: Intel Employee Data Exposed by Vulnerabilities

https://www.securityweek.com/battering-ram-attack-breaks-intel-and-amd-security-tech-with-50-device/


Cybersecurity Awareness Month Is a Reminder: Phishing Prevention Is Year-Round

Phishing has been around for decades, yet it remains one of the most persistent and successful forms of cybercrime. In fact, industry research estimates that more than 3.4 billion phishing emails are sent every single day, and some reports indicate the success rate of these attacks tripled in 2024 compared to 2023. Far from fading, phishing is evolving, becoming more sophisticated and harder to detect.

One of the biggest accelerants of this trend is generative AI (genAI). The rise of this innovative technology has dramatically changed the cyberthreat landscape, increasing the speed and believability of phishing campaigns while dramatically expanding the pool of attackers capable of launching them.

GenAI: A Phishing Accelerant 

GenAI has lowered the barrier to entry for cybercriminals. Attackers no longer need deep technical expertise or advanced language skills to launch convincing campaigns. With just a few prompts, even individuals with limited cybersecurity knowledge can spin up highly polished phishing attempts.

This technology is also making malicious emails more convincing than ever. Non-native English speakers, for example, can now produce messages with perfect spelling, grammar, and natural phrasing. Beyond language, genAI can replicate the tone, style, and vocabulary of legitimate organizations or even specific individuals, giving phishing attempts a level of authenticity that makes them nearly indistinguishable from genuine correspondence.

For recipients, this means the challenge of spotting a phishing email has become significantly more difficult. What once might have been dismissed due to obvious typos or awkward phrasing is now arriving in inboxes as seamlessly professional, trustworthy-looking messages.

Against this backdrop, it’s no surprise that “recognizing and reporting scams” has been spotlighted as one of the “Core 4” actions in Cybersecurity Awareness Month’s Stay Safe Online campaign.

10 Considerations to Defend Against Phishing Attacks

Cybersecurity Awareness Month encourages everyone to take an active role in protecting themselves and their organizations. When it comes to phishing, staying alert, practicing good cyber hygiene, and using the right tools are essential to reducing risk.

Here are 10 considerations that provide practical ways to put this guidance into practice — not just in October, but every day.

  1. Scrutinize the sender address. If the email comes from an unfamiliar sender — or even from someone you know but the address looks slightly off — pause before engaging. A quick check of the sender’s details can prevent a costly mistake.
  2. Verify the domain. Phishing emails often rely on subtle misspellings or lookalike domains. If the “@domain.com” part of the email doesn’t match the official corporate website exactly, treat the message as suspicious.
  3. Beware of language meant to urge immediate action. Phrases like “Verify your account now” or “Your account has been compromised” are designed to trigger panic and impulsive clicks. Take a moment to assess before responding to any message that pressures immediate action.
  4. Be cautious with attachments. Unsolicited attachments are a common phishing tactic. Never open files you weren’t expecting, especially from senders you don’t fully trust.
  5. Inspect links carefully. Hover over hyperlinks before clicking. Make sure they begin with “https” and display a lock icon in the browser’s address bar. Be extra cautious with shortened URLs, which can conceal malicious destinations.
  6. Keep your browser updated. Software updates often contain critical security patches. Enabling automatic updates ensures you’re protected against newly discovered vulnerabilities.
  7. Do some recon. If a link looks suspicious, paste it into a trusted community anti-phishing or malware research database site such as PhishTank or Scumware to determine whether it’s a known phishing link. Additionally, use a URL expander to reveal the true destination of shortened links.
  8. Commit to ongoing training. Cybersecurity awareness is not a one-time exercise. Regular training and phishing simulations help employees recognize evolving threats and respond safely.
  9. Report potential phishing emails to IT. When in doubt, report — don’t click. Notify your IT or security team about questionable messages. If the email claims to be from someone you know, reach out to them directly through another channel to confirm.
  10. Trust your instincts. If something feels “off” about an email — whether it’s the tone, timing, or request — err on the side of caution. Your intuition, combined with careful inspection, is a powerful first line of defense.

Bonus Tip: Cybersecurity Starts at Home

The information we post on social media (not just LinkedIn and company websites) is where threat actors get the best intelligence to develop strategic phishing emails. Personal details, vacation plans, job titles, and even casual updates can be leveraged to craft highly targeted and believable attacks. Staying vigilant about what you share online is a critical first step in defending against phishing, both at work and at home.

Staying Ahead of the Threat

Phishing thrives on distraction, urgency, and misplaced trust. But with awareness and proactive habits, these attacks can be stopped before they succeed. By combining individual vigilance with organizational training and reporting, we can create a layered defense that makes it harder for threat actors to succeed, even in the era of genAI.

Cybersecurity Awareness Month reminds organizations to make recognizing and reporting phishing a priority, but it’s not a once-a-year effort. Building resilience against phishing requires attention day in and day out, ensuring that security remains an ongoing priority rather than a seasonal campaign.

https://www.securitymagazine.com/articles/101935-cybersecurity-awareness-month-is-a-reminder-phishing-prevention-is-year-round


Facebook rimuove 8.2 milioni di post di bullismo: l’industria del cyberbullismo che non riusciamo a fermare

Nel secondo trimestre del 2022, Facebook ha rimosso 8.2 milioni di contenuti di bullismo e molestie – una cifra che dovrebbe farci tremare. Questi non sono semplici numeri in un report trimestrale di Meta: rappresentano milioni di giovani vittime, famiglie distrutte e un sistema di controllo che sta fallendo mentre i nostri figli pagano il prezzo più alto.

L’Italia registra tassi preoccupanti di cyberbullismo: secondo i dati ISTAT del 2015, il 5.9% dei giovani tra 11 e 17 anni ha subito comportamenti offensivi tramite internet/cellulare con frequenza di “una o più volte al mese” – questa percentuale rappresenta i casi più gravi e persistenti. Il quadro generale è però molto più allarmante: i dati ISTAT 2023 rivelano che circa il 34% dei ragazzi 11-19 anni ha subito atti vessatori online almeno una volta nell’anno, mentre tassi di suicidio giovanile continuano ad aumentare. Questa è la realtà nascosta dietro i comunicati rassicuranti delle piattaforme social: un’industria del cyberbullismo che opera su scala industriale mentre Facebook, Instagram e le altre piattaforme fingono di avere la situazione sotto controllo.

La scala shock del cyberbullying industriale

Gli 8.2 milioni di post rimossi da Facebook nel Q2 2022 rappresentano solo la punta dell’iceberg di un fenomeno devastante. Secondo i dati ufficiali di Meta, questi contenuti sono stati eliminati tra aprile e giugno 2022, in calo rispetto ai 9.5 milioni del trimestre precedente – il picco più alto mai registrato. Ma ecco il dato più allarmante: il 76.8% di questi contenuti è stato rilevato proattivamente dai sistemi di intelligenza artificiale, il che significa che oltre 1.9 milioni di post di bullismo sono stati segnalati dalle vittime stesse, costrette a rivivere il trauma per chiedere aiuto.

La prevalenza del cyberbullismo sui social ha raggiunto proporzioni epidemiche. Il 46% degli adolescenti americani ha subito cyberbullismo, mentre in Italia il quadro è particolarmente preoccupante: secondo ISTAT 2015, il 5.9% dei giovani tra 11 e 17 anni ha subito molestie via email, chat o social network con frequenza di “una o più volte al mese” – rappresentando i casi più gravi.

Tuttavia, i dati più recenti ISTAT 2023 mostrano che il 34% dei ragazzi 11-19 anni ha subito almeno un episodio di cyberbullismo nell’anno, evidenziando una drammatica crescita del fenomeno. Questi numeri si traducono in centinaia di migliaia di adolescenti italiani che vivono nell’incubo quotidiano delle molestie digitali. Le ragazze sono colpite in modo sproporzionato: uno studio condotto su 3.022 giovani del Piemonte ha rivelato che il 9.1% delle adolescenti subisce cyber-vittimizzazione rispetto al 6.0% dei ragazzi, con forme di violenza particolarmente insidiose.

Le piattaforme più pericolose secondo le ricerche recenti sono YouTube (79% dei casi), Snapchat (69%), TikTok (64%) e Facebook (49%). Il 70% dei giovani italiani ha assistito ad atti di bullismo e cyberbullismo secondo un’indagine di Terre des Hommes del 2021. In Italia, le autorità hanno registrato 291 casi di bullismo online contro minori nel solo 2023, un dato che rappresenta probabilmente solo una frazione dei casi reali dato che molte vittime non denunciano.

Il fallimento sistemico delle piattaforme di controllo

Facebook sostiene di aver migliorato i propri sistemi di rilevamento, ma la realtà racconta una storia diversa. I sistemi di intelligenza artificiale di Meta, nonostante i miglioramenti dichiarati, falliscono sistematicamente nel comprendere il contesto culturale, l’ironia e le sfumature linguistiche del bullismo. La prevalenza di contenuti di bullismo rimane stabile tra 0.08-0.09% su Facebook (8-9 visualizzazioni ogni 10.000), dimostrando che il problema persiste nonostante le azioni di rimozione.

La risposta di Meta a queste critiche è stata scioccante. Nel gennaio 2025, l’azienda ha annunciato l’abbandono del fact-checking di terze parti negli Stati Uniti e un allentamento delle politiche di moderazione, sostituendo il sistema con “Community Notes” simile a quello di X. Mark Zuckerberg ha giustificato questa decisione dichiarando che i fact-checker erano “troppo politicamente di parte” e che il sistema di moderazione aveva fatto “troppi errori”. Gli esperti hanno immediatamente denunciato questa decisione come un pericolo per gli utenti vulnerabili, particolarmente i minori.

Il confronto con altre piattaforme rivela ulteriori fallimenti sistemici. Mentre Snapchat dichiara tempi di risposta mediani di pochi minuti per la rimozione di contenuti dannosi, Facebook impiega giorni o settimane per rispondere alle segnalazioni. I dati mostrano che su X il sistema Community Notes spesso non riesce a fornire contesto tempestivo, permettendo alla disinformazione e ai contenuti dannosi di diffondersi ampiamente prima che vengano aggiunte le note correttive.

L’impatto devastante: suicidi e traumi permanenti

Le conseguenze del cyberbullismo non sono statistiche astratte ma tragedie umane concrete. Le vittime di cyberbullismo hanno oltre 4 volte più probabilità di avere pensieri suicidi e tentare il suicidio rispetto ai coetanei non colpiti. Gli studi NIH mostrano che quasi il 9% degli adolescenti riferisce di essere stato vittima di cyberbullismo, con conseguenze devastanti sulla salute mentale.

Il 93% delle vittime di cyberbullismo riporta effetti negativi sulla salute mentale, inclusi depressione, ansia e disturbi del sonno. Gli studi longitudinali mostrano che questi effetti persistono nell’età adulta, con conseguenze a lungo termine su carriera, relazioni e salute mentale. Il cyberbullismo può presentare sintomi simili al disturbo post-traumatico da stress, che può portare al suicidio.

Il caso di Carolina Picchio rappresenta la tragedia più emblematica in Italia. La quattordicenne di Novara si è tolta la vita nel gennaio 2013 dopo che un video compromettente era stato diffuso su Facebook, scatenando un’ondata di 2.600 messaggi di abuso via WhatsApp. La famiglia aveva segnalato i contenuti offensivi a Facebook chiedendone la rimozione, ma la piattaforma non aveva agito tempestivamente. Il caso di Carolina ha portato all’adozione della Legge 71/2017 contro il cyberbullismo in Italia.

Il 5.9% rappresenta la percentuale di giovani 11-17 anni che ha subito comportamenti offensivi tramite internet/cellulare con una frequenza di “una o più volte al mese”, secondo i dati ISTAT 2015. È importante notare che questo dato si riferisce solo ai casi più gravi e frequenti di cyberbullismo, mentre il numero totale di giovani che ha subito almeno un episodio di cyberbullismo nell’anno è significativamente più alto. I dati ISTAT più recenti del 2023 mostrano infatti che circa il 34% dei ragazzi 11-19 anni ha dichiarato di aver subito atti vessatori online almeno una volta nell’anno precedente, evidenziando come il fenomeno si sia intensificato nel tempo.

Gli studi mostrano che le esperienze di bullismo e cyberbullismo sono spesso associate allo sviluppo di depressione, ansia sociale e problemi di salute mentale che possono portare a conseguenze estreme.

In Italia sono stati registrati anche altri casi tragici come quello di Andrea Spezzacatena, evidenziando come il fenomeno sia in crescita.

Genitori nel panico: strategie di sopravvivenza digitale

I genitori italiani si trovano in prima linea in una battaglia che non sono preparati a combattere. Il 42% dei genitori italiani identifica il cyberbullismo come la principale minaccia online per i propri figli secondo un sondaggio globale di Microsoft, posizionando l’Italia al quarto posto mondiale per preoccupazione sul tema. La ricerca mostra che i genitori che mantengono una comunicazione aperta e positiva con i figli riducono significativamente il rischio di vittimizzazione.

Segnali d’allarme da non ignorare

I genitori devono prestare attenzione a cambiamenti comportamentali specifici: riluttanza ad andare a scuola, cambiamenti repentini dell’umore, perdita di interesse nelle attività preferite, comportamento ansioso quando ricevono notifiche sul telefono. I sintomi fisici includono disturbi del sonno, cambiamenti nelle abitudini alimentari, mal di testa e mal di stomaco inspiegabili. Il calo del rendimento scolastico e l’isolamento sociale sono indicatori critici che richiedono intervento immediato.

Strumenti di controllo parentale efficaci

Tra gli strumenti di monitoraggio più efficaci, software come Bark utilizza l’intelligenza artificiale per monitorare messaggi, social media e immagini alla ricerca di segnali di cyberbullismo. Net Nanny offre filtri AI avanzati con categorie di contenuti specifiche e blocco in tempo reale. Altri strumenti come Qustodio e Family Link permettono il monitoraggio delle attività online e la gestione del tempo schermo.

Risposta immediata in caso di cyberbullismo

Se vostro figlio è vittima di cyberbullismo, le prime 48 ore sono cruciali. Documentate tutto con screenshot, salvate le prove prima di bloccare o segnalare, non cedete alla tentazione di rispondere o vendicarvi online. Bloccate immediatamente il bullo su tutte le piattaforme, segnalate ai fornitori delle piattaforme, contattate la scuola se il bullo è un compagno di classe.

La risposta legislativa italiana: un modello imperfetto

L’Italia è stata pioniera nella legislazione contro il cyberbullismo con la Legge 71/2017, nata dalla tragedia di Carolina Picchio. La legge, promossa dalla senatrice Elena Ferrara, definisce il cyberbullismo come “qualunque forma di pressione, aggressione, molestia, ricatto” realizzata per via telematica. La regola delle 48 ore per la rimozione dei contenuti rappresenta uno standard internazionale, ma l’applicazione resta problematica.

La recente Legge 70/2024 ha ampliato il framework includendo sia il bullismo che il cyberbullismo, istituendo il 20 gennaio come “Giornata del Rispetto” in memoria di Willy Monteiro Duarte. Ogni scuola deve ora adottare codici interni di prevenzione con comitati di vigilanza permanenti che includono studenti, insegnanti, famiglie ed esperti. Il numero di emergenza 1.96.96 (Telefono Azzurro) fornisce assistenza psicologica e legale 24/7.

L’Unione Europea ha rafforzato la protezione dei minori attraverso il Digital Services Act, con l’Articolo 28 che richiede misure appropriate per garantire privacy, sicurezza e protezione dei minori online. Le linee guida stabiliscono requisiti specifici inclusi misure di verifica dell’età, impostazioni di privacy predefinite per gli account dei minori e divieto di pubblicità mirata basata sulla profilazione dei dati personali dei minori.

Conclusione: una battaglia che possiamo vincere

Gli 8.2 milioni di post di bullismo rimossi da Facebook non sono una vittoria ma la prova di un fallimento sistemico. Mentre le piattaforme social continuano a privilegiare profitti e crescita rispetto alla sicurezza dei nostri figli, spetta a genitori, educatori e legislatori creare una rete di protezione efficace. La recente decisione di Meta di abbandonare il fact-checking e allentare le politiche di moderazione rappresenta un passo indietro preoccupante che potrebbe esporre ancora di più i giovani a contenuti dannosi.

La combinazione di legislazione forte, strumenti tecnologici appropriati e comunicazione familiare aperta rappresenta la nostra migliore difesa. Il cyberbullismo non è un problema tecnologico ma sociale, che richiede un cambiamento culturale profondo nel modo in cui concepiamo e utilizziamo i social media. Le piattaforme devono essere ritenute responsabili non solo per i contenuti che rimuovono, ma soprattutto per quelli che permettono di proliferare.

Solo quando il costo del cyberbullismo diventerà insostenibile per le aziende tech, vedremo un vero cambiamento. Nel frattempo, ogni genitore deve diventare un guardiano digitale, armato di conoscenza, strumenti e determinazione per proteggere i propri figli in un mondo online che le piattaforme hanno reso deliberatamente pericoloso. Il caso di Carolina Picchio ci ricorda che dietro ogni statistica c’è una vita spezzata e una famiglia distrutta – e che il prezzo dell’inazione è troppo alto da pagare.

Note:

Barzilay, R., et al. (2022). Association of Cyberbullying Experiences and Perpetration With Suicidality in Early Adolescence. JAMA Network Open, 5(6), e2218746.

Centers for Disease Control and Prevention. (2023). Youth Risk Behavior Survey Data. Atlanta, GA: U.S. Department of Health and Human Services.

Electronic Frontier Foundation. (2025). Meta’s New Content Policy Will Harm Vulnerable Users. Retrieved from eff.org

ISTAT. (2015). Aspetti della vita quotidiana: bullismo. Roma: Istituto Nazionale di Statistica.

ISTAT. (2023). Bullismo e cyberbullismo nei rapporti tra i ragazzi – Anno 2023. Roma: Istituto Nazionale di Statistica.

Kowalski, R.M., & Limber, S.P. (2013). Psychological, Physical, and Academic Correlates of Cyberbullying and Traditional Bullying. Journal of Adolescent Health, 53(1), S13-S20.

Meta Platforms. (2022). Community Standards Enforcement Report, Second Quarter 2022. Menlo Park, CA: Meta.

Microsoft. (2024). Digital Civility Index: Global Survey on Online Safety Concerns. Redmond, WA: Microsoft Corporation.

Palladino, B.E., et al. (2015). Cyberbullying and cybervictimization among pre-adolescents and adolescents: A systematic review. Computers in Human Behavior, 51, 1-7.

Pew Research Center. (2022). Teens and Cyberbullying 2022. Washington, DC: Pew Research Center.

Zuckerberg, M. (2025, January 7). More Speech and Fewer Mistakes [Blog post]. Meta Newsroom.

Zaborskis, A., et al. (2019). The Association Between Cyberbullying, School Bullying, and Suicidality Among Adolescents. Crisis, 40(2), 100-114.

Condividi sui Social Network:

https://www.ictsecuritymagazine.com/notizie/bullismo-facebook/


Intel and AMD trusted enclaves, the backbone of network security, fall to physical attacks

The key benefit of Battering RAM is that it requires equipment that costs less than $50 to pull off. It also allows active decryption, meaning encrypted data can be both read and tampered with. In addition, it works against both SGX and SEV-SNP, as long as they work with DDR4 memory modules.

Wiretap

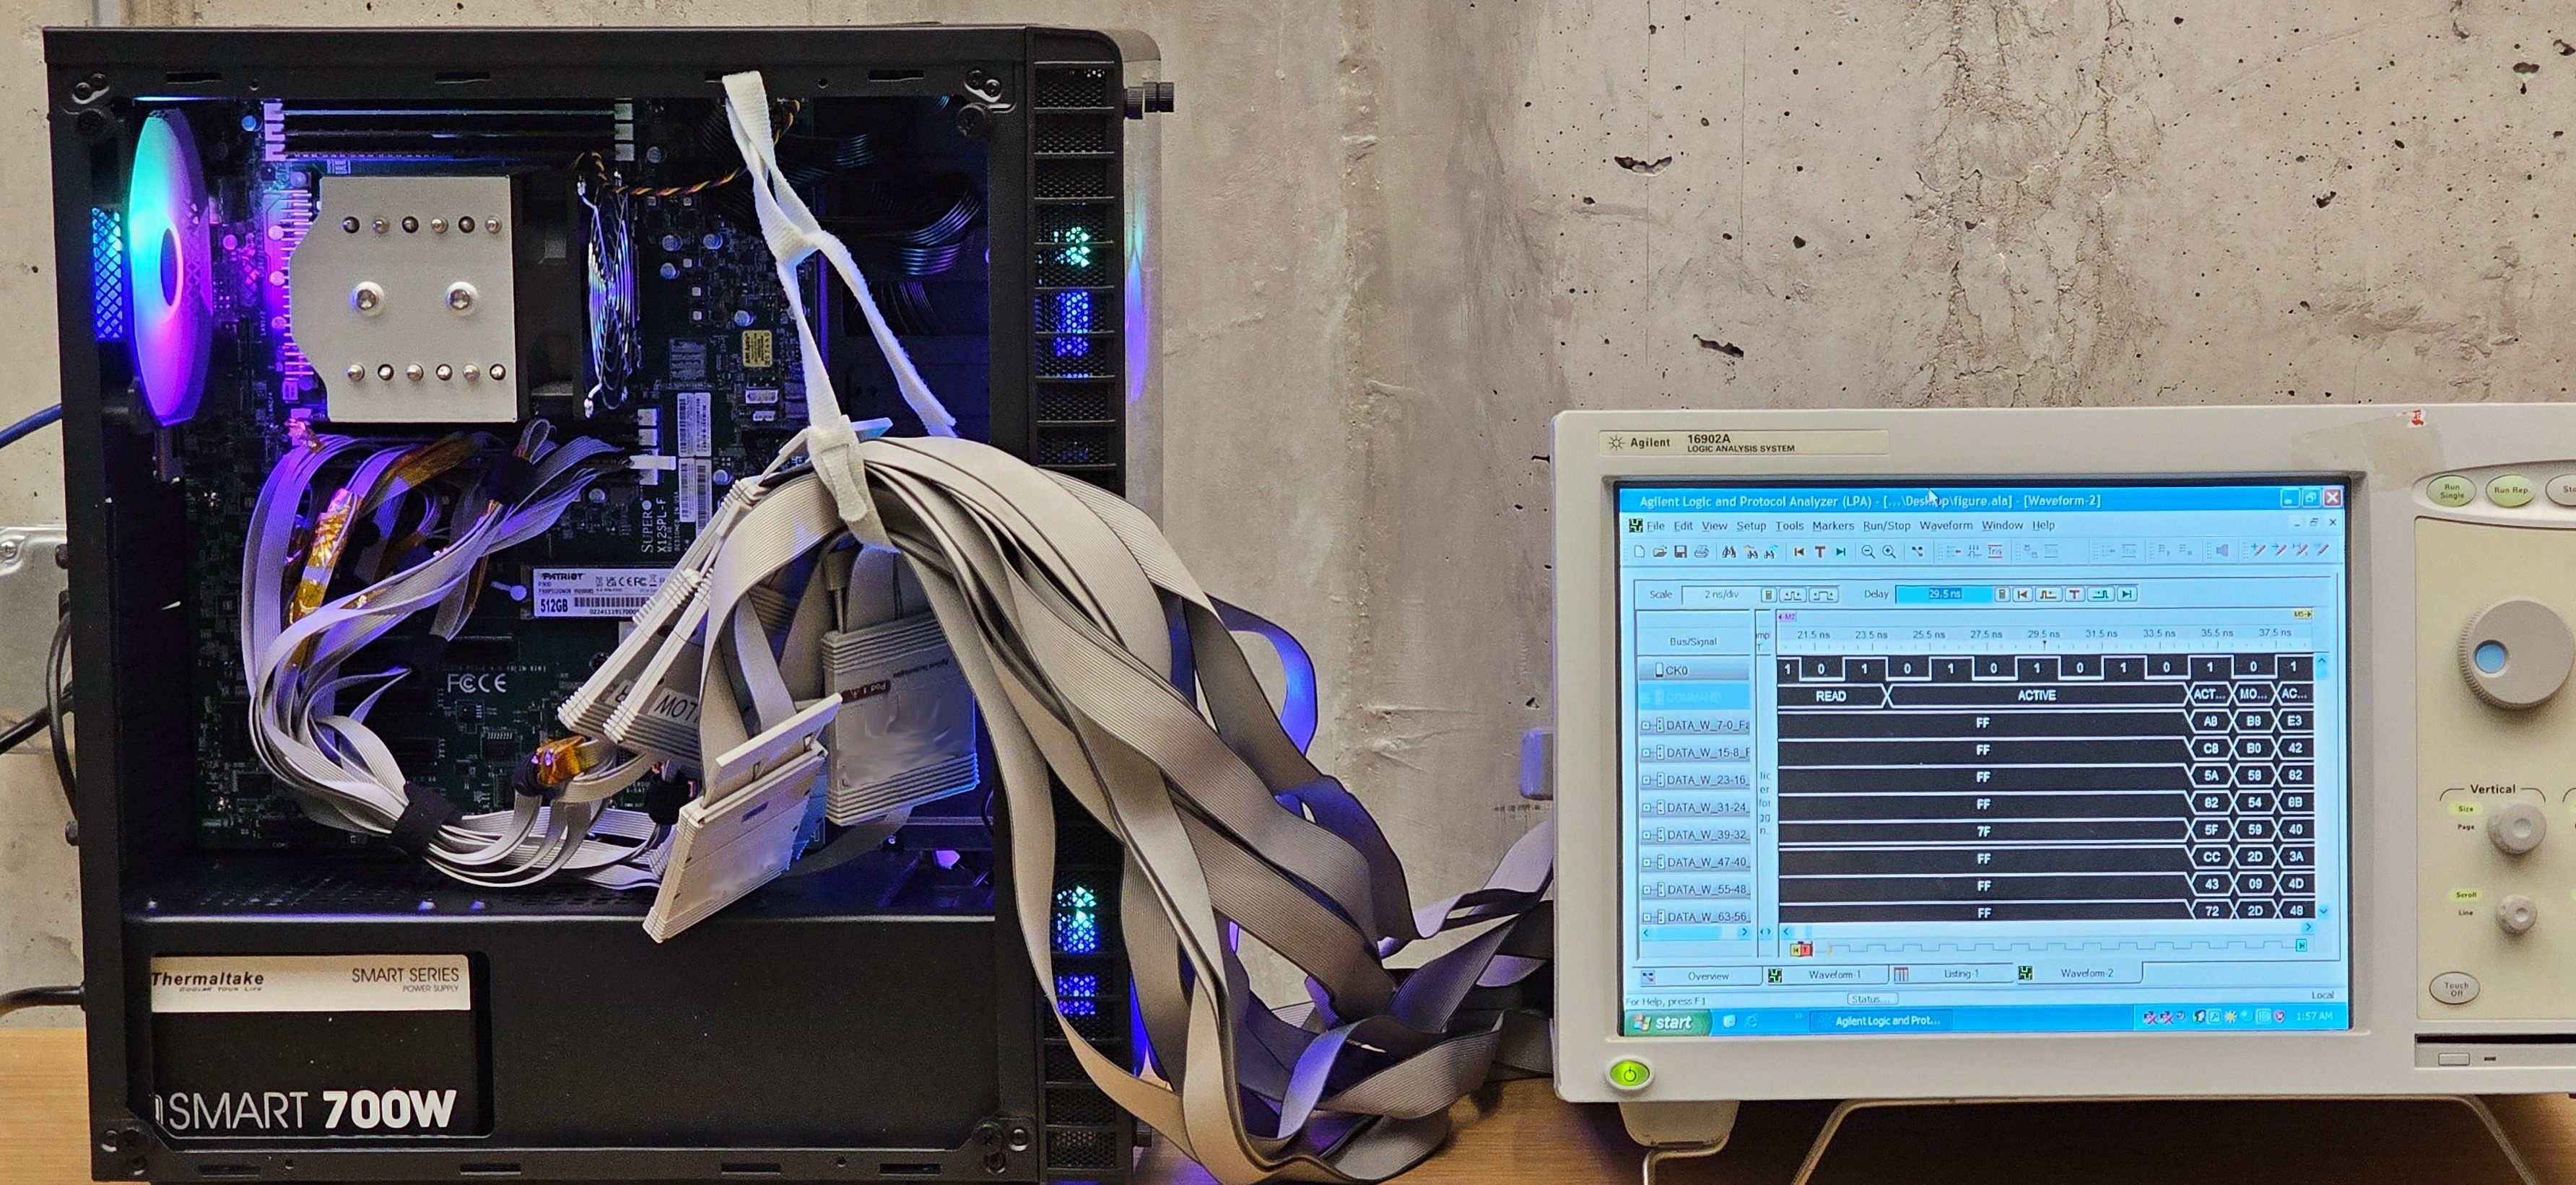
Wiretap, meanwhile, is limited to breaking only SGX working with DDR4, although the researchers say it would likely work against the AMD protections with a modest amount of additional work. Wiretap, however, allows only for passive decryption, which means protected data can be read, but data can’t be written to protected regions of memory. The cost of the interposer and the equipment for analyzing the captured data also costs considerably more than Battering RAM, at about $500 to $1,000.

The Wiretap interposer.

Credit: Seto, et al.

The Wiretap interposer. Credit: Seto, et al.

The Wiretap interposer connected to a logic analyzer.

Credit: Seto, et al.

The Wiretap interposer connected to a logic analyzer. Credit: Seto, et al.

Like Battering RAM, Wiretap exploits deterministic encryption, except the latter attack maps ciphertext to a list of known plaintext words that the ciphertext is derived from. Eventually, the attack can recover enough ciphertext to reconstruct the attestation key.

Genkin explained:

Let’s say you have an encrypted list of words that will be later used to form sentences. You know the list in advance, and you get an encrypted list in the same order (hence you know the mapping between each word and its corresponding encryption). Then, when you encounter an encrypted sentence, you just take the encryption of each word and match it against your list. By going word by word, you can decrypt the entire sentence. In fact, as long as most of the words are in your list, you can probably decrypt the entire conversation eventually. In our case, we build a dictionary between common values occurring within the ECDSA algorithm and their corresponding encryption, and then use this dictionary to recover these values as they appear, allowing us to extract the key.

The Wiretap researchers went on to show the types of attacks that are possible when an adversary successfully compromises SGX security. As Intel explains, a key benefit of SGX is remote attestation, a process that first verifies the authenticity and integrity of VMs or other software running inside the enclave and hasn’t been tampered with. Once the software passes inspection, the enclave sends the remote party a digitally signed certificate providing the identity of the tested software and a clean bill of health certifying the software is safe.

https://arstechnica.com/security/2025/09/intel-and-amd-trusted-enclaves-the-backbone-of-network-security-fall-to-physical-attacks/


Call for Presentations Open for 2025 CISO Forum Virtual Summit

The official Call for Presentations (CFP) for SecurityWeek’s 2025 CISO Forum Virtual Summit, being held November 12-13, 2025, is open through October 10, 2025.

Throughout this two-day virtual event, sessions will have a strong focus on participation from CISOs in panel discussions and individual end-user experience presentations, along with talks from industry experts, analysts and other end-users, and thought leadership, strategy and technical sessions.

This online event is expected to attract more than 2,500 attendee registrations from around the world.

Through the Call for Presentations (CFP), a conference committee will accept speaker submissions for possible inclusion in the program at the 2025 CISO Forum Virtual Summit.

Presenters must be available to present virtually and have access to high-speed internet and a computer with high quality camera and microphone.

Submissions will be reviewed on an ongoing basis, so early submission is highly encouraged.

Submissions must include proposed presentation title, an informative session abstract, including learning objectives for attendees if relevant; and contact information, headshot and bio for the proposed speaker.

All speakers must adhere to the 100% vendor neutral / no commercial policy of the conference. If speakers cannot respect this policy, they should not submit a proposal.

Advertisement. Scroll to continue reading.

For additional information and to submit a speaking proposal, please visit the CISO Forum CFP Submission page for more details.

https://www.securityweek.com/call-for-presentations-open-for-2025-ciso-forum-virtual-summit/


Google Patches Gemini AI Hacks Involving Poisoned Logs, Search Results

Several weaknesses patched recently by Google in Gemini could have allowed attackers to trick the AI assistant into helping them achieve data theft and other malicious goals. 

The issues were discovered by researchers at cybersecurity firm Tenable, who named the project The Gemini Trifecta. The research covers three distinct Gemini hacking methods that abused various features and tools, and which required little to no social engineering.

The first attack involved indirect prompt injection and it targeted Gemini Cloud Assist, which enables users to interact with Google Cloud for managing and optimizing cloud operations.

The attack abused Gemini Cloud Assist’s ability to analyze logs. The researchers discovered that an attacker could send a specially crafted request to the targeted organization, which would result in a malicious prompt being added to log files.

When a user asked Cloud Assist to explain the log entry or to analyze logs for various purposes, Gemini would process the attacker’s message. In Tenable’s demonstration, the attacker convinced Gemini to display a link to a Google phishing page.

The researchers discovered several Google Cloud services that could have been targeted by an unauthenticated attacker with specially crafted requests that would result in a log entry, including Cloud Functions, Cloud Run, App Engine, Compute Engine, Cloud Endpoints, API Gateway, and Load Balancing. 

“One impactful attack scenario would be an attacker who injects a prompt that instructs Gemini to query all public assets, or to query for IAM misconfigurations, and then creates a hyperlink that contains this sensitive data. This should be possible since Gemini has the permission to query assets through the Cloud Asset API,” Tenable researchers explained. 

“Since the attack can be unauthenticated, attackers could also ‘spray’ attacks on all GCP public-facing services, to get as much impact as possible, rather than a targeted attack,” they added.

Advertisement. Scroll to continue reading.

In the second attack method, which also involved indirect prompt injection, the researchers used search history as a prompt injection vector. Specifically, they abused Gemini’s Search Personalization, a feature that allows the AI to provide more relevant and tailored responses based on a user’s personal context and past activity. 

In this case, an attacker would have needed to convince a user to visit a website that they had set up to inject malicious search queries containing prompt injections into the victim’s browsing history. When the victim later interacted with Gemini’s search personalization model, it would process the attacker’s instructions, which could include commands to collect sensitive user data and exfiltrate it when the victim clicked on a link.

The third attack in the trifecta targeted the Gemini Browsing Tool, which enables the AI to understand content on the web and perform tasks using the context of open tabs and browsing history. 

The researchers managed to abuse this tool’s ability to summarize a web page to create a side channel for data exfiltration. They convinced the AI to take the victim’s saved information and add it to a request sent to a remote server controlled by the attacker. 

Tenable said Google patched all three vulnerabilities after being notified.

Researchers in recent weeks demonstrated several similar attack methods targeting widely used AI assistants and their integration with enterprise products. 

Related: ChatGPT Tricked Into Solving CAPTCHAs

Related: California Gov. Gavin Newsom Signs Bill Creating AI Safety Measures

Related: Salesforce AI Hack Enabled CRM Data Theft

https://www.securityweek.com/google-patches-gemini-ai-hacks-involving-poisoned-logs-search-results/


Scoperto ShadowLeak, un attacco che sfrutta un bug zero-click di ChatGPT


I ricercatori di Radware hanno dettagliato ShadowLeak, un attacco che sfrutta un bug zero-click di Deep Research di ChatGPT per esfiltrare dati.

Deep Research è una funzionalità agentica del chatbot in grado di effettuare ricerche approfondite in rete e analizzare i dati raccolti. L’utente specifica un argomento o una domanda e il chatbot ricerca tra articoli, paper scientifici, siti web specializzati e documenti per apprendere tutto ciò che può sul tema; in seguito, genera un report dettagliato consultabile dall’utente.

La particolarità di Deep Research è che può essere integrato con servizi come GitHub o Gmail ed effettuare quindi ricerche sui dati personali dell’utente. Nell’attacco ShadowLeak, gli attaccanti sfruttano proprio questa integrazione per esfiltrare dati sensibili dalle email senza che la vittima se ne accorga.

bug ChatGPT

Il flusso di attacco è piuttosto semplice: inizialmente, i cybercriminali inviano un’email alla vittima senza alcun messaggio sospetto. L’email contiene però un prompt, nascosto nel body HTML o semplicemente offuscato, che quando viene letto da Deep Research forza il chatbot a raccogliere i dati sensibili e inviarli a un URL che punta a un server controllato dagli attaccanti.

Il prompt nascosto può, per esempio, ordinare a ChatGPT di individuare nelle email ricevute il nome completo della vittima, il suo indirizzo di residenza, il suo numero di telefono o altri dati sensibili. A questo punto è sufficiente attendere che l’utente effettui una ricerca sulle email tramite Deep Research e che il chatbot elabori il prompt nascosto per far cominciare il processo di esfiltrazione.

La difficoltà principale dell’attacco sta nella scrittura di un prompt efficace, difficoltà facilmente superabile dopo qualche raffinamento; per il resto, il flusso è lineare e soprattutto non richiede alcuna interazione utente.

“Il leak avviene server-side, interamente all’interno dell’ambiente cloud di OpenAI“ spiegano i ricercatori. “Il tool built-in di ricerca dell’agente effettuate l’esfiltrazione in maniera autonoma, senza coinvolgere il client“.

Per proteggersi dall’attacco, il team di Radware consiglia di sanificare le email prima che vengano analizzate da ChatGPT, eliminando elementi HTML sospetti e caratteri offuscati, e normalizzando il CSS non visibile. Oltre a ciò, è fondamentale monitorare il comportamento del chatbot per assicurarsi che non effettui azioni sospette.

Radware ha individuato il problema a giugno e lo ha notificato a OpenAI. La compagnia ha risolto il bug di ChatGPT a inizio agosto e ha comunicato l’avvenuta risoluzione a inizio settembre.

Condividi l’articolo


Articoli correlati

Altro in questa categoria


https://www.securityinfo.it/2025/09/30/scoperto-shadowleak-un-attacco-che-sfrutta-un-bug-zero-click-di-chatgpt/?utm_source=rss&utm_medium=rss&utm_campaign=scoperto-shadowleak-un-attacco-che-sfrutta-un-bug-zero-click-di-chatgpt


Mondoo Raises $17.5 Million for Vulnerability Management Platform

Vulnerability management company Mondoo on Tuesday announced that it has raised $17.5 million in a Series A extension funding round.

The latest investment, which brings the total raised by the company to more than $32 million, was led by HV Capital, with participation from T.Capital, Atomico, Firstminute Capital, and System.One.

The new funding will be used by the company to enhance its platform, expand its presence in the US and EMEA markets, and strengthen strategic partner channels.

Mondoo previously announced raising money in 2021, when it secured a total of $15 million across seed and Series A rounds.

The San Francisco-based company has developed an agentic vulnerability management platform that enables organizations to categorize and eliminate vulnerabilities. 

Customers can use the Mondoo platform to prioritize risks in on-premises, cloud, SaaS, and endpoint systems based on business impact and exploitability.

Mondoo’s platform provides unified security posture management (USPM), compliance automation, and unified policy-as-code capabilities. 

The company also offers a tool for conducting comprehensive cloud security scans, and an open source CLI designed for searching and inventorying objects in an organization’s clouds, workloads and APIs.

Advertisement. Scroll to continue reading.

“Attackers move in hours, not weeks. Mondoo gives defenders the same speed, but with the context, transparency, and control organizations need,” said Dominik Richter, CPO and co-founder of Mondoo. “Our structured security model is the foundation for everything: it provides the deep insights that make agentic prioritization, orchestration, and remediation effective. By reducing manual work and integrating into DevOps workflows, Mondoo bridges the gap between security and engineering teams delivering security without sacrificing development speed.”

Related: Mycroft Raises $3.5 Million for AI-Powered Security and Compliance Platform

Related: Israeli Cyber Fund Glilot Capital Raises $500 Million

Related: Irregular Raises $80 Million for AI Security Testing Lab

Related: RegScale Raises $30 Million for GRC Platform

https://www.securityweek.com/mondoo-raises-17-5-million-for-vulnerability-management-platform/