Email attacks rose by 293% compared to the first half of 2023

A report by Acronis found email attack instances were 293% greater in the first half of 2024 when compared to the first half of 2023. This report, which emphasizes emerging cybersecurity trends, noted current trends in ransomware, phishing, email attacks and more. Some key findings from the report include: 

  • Ransomware detection volume increased by 32% from Q4 2023 to Q1 2024.
  • Email communications per organization increased by 25%, coinciding with a 47% in email attacks that targeted organizations.
  • 26% of targets encountered phishing attempts via malicious URLs. 
  • Social engineering schemes rose by 5% since the first half of 2023. 
  • Malware attacks decreased from 11% to 4% since the first half of 2023.

Security leaders weigh in 

Stephen Kowski, Field CTO SlashNext Email Security+:

“Organizations should implement advanced email security with AI-powered threat detection, enable multi-factor authentication and conduct regular security awareness training for employees. Leveraging real-time phishing protection that analyzes URLs and attachments can also significantly reduce email-based threats.

“SMBs must prioritize regular software updates, implement robust backup solutions and deploy next-generation endpoint protection with behavioral analysis capabilities. Utilizing a comprehensive security platform that offers ransomware-specific defenses and provides real-time threat intelligence can greatly enhance an SMB’s resilience against attacks.

“Generative AI and LLMs are enabling attackers to create more convincing phishing emails, deepfakes and automated attack scripts at scale. These technologies allow cybercriminals to personalize social engineering attempts and rapidly adapt their tactics, making traditional defenses less effective. What used to be zero-day are now zero-hour at least. Human defenders alone won’t be able to keep up.

“To counter AI-generated attacks, organizations should deploy security solutions that leverage generative AI and use machine learning to detect anomalies in email content, sender behavior and communication patterns. Implementing advanced anti-phishing technology that can identify and block sophisticated impersonation attempts in real-time is crucial for defending against these evolving threats.”

Nicole Carignan, Vice President of Strategic Cyber AI, at Darktrace:

“Despite increased focus on email security and employee training, organizations and their employees continue to get phished. Many tools used by organizations today rely on historical attack data to identify and stop known email threats from reentering inboxes. However, this approach often falls flat against new or unknown threats. With the increasing use of generative AI by threat actors, our dependence on traditional threat intelligence or rules and signature-based defense systems will lessen as threat actors now can quickly adopt and change signatures, hashes and indicators of compromise to evade defenses. 

“As sophistication of phishing attacks continue to grow, organizations cannot rely on employees to be the last line of defense against these attacks. Instead, organizations must use tools that can understand how their employees interact with their inboxes and build a profile of what activity is normal for users — their relationships, tone and sentiment, content, when and how they follow or share links. Only then can they accurately recognize suspicious activity that may indicate an attack or business email compromise.”

Mr. Mika Aalto, Co-Founder and CEO at Hoxhunt:

“To better protect their email communications, organizations need to start with the basics — multi-factor authentication and end-to-end encryption for sensitive information sharing — and from there build a vibrant security culture upon a human risk management platform. Whereas a traditional security awareness training tool is geared for compliance, a human risk management platform is based on measurable behavior change and risk reduction, starting with threat reporting. Reporting an attack alerts the SOC to the danger and an AI-powered human risk management platform automatically categorizes the report and accelerates incident response. To transform your people form your greatest risk to your greatest resource, you need dynamic phishing training that automatically adapts to the latest threats and adjusts to the user’s individual needs as they change over time.

“Language and technical barriers to social engineering are being lowered by the day with AI. The believability and sophistication of social engineering campaigns are improving by the month. Deepfake technology allows AI to create audio and video content that impersonates trusted individuals, making social engineering attacks even more effective. AI also automates the process of crafting and sending phishing emails, enabling attackers to target a larger number of victims with minimal effort. Additionally, AI can analyze publicly available data to personalize phishing emails, increasing the likelihood of success.

“The shift from malware attacks to social engineering attacks indicates that cybercriminals are increasingly focusing on exploiting human vulnerabilities rather than technical ones. This trend underscores the importance of investing in human-centric security measures, such as personalized training and awareness programs, to reduce the risk of social engineering attacks. Developing adaptive security strategies that can respond to the evolving tactics of cybercriminals is also crucial. Implementing continuous monitoring and threat detection helps quickly identify and respond to social engineering attempts. Empowering employees to act as the first line of defense by reporting suspicious activities and participating in security initiatives is vital.”

https://www.securitymagazine.com/articles/100922-email-attacks-rose-by-293-compared-to-the-first-half-of-2023


Nathan Howe: “ecco come Zscaler protegge i dispositivi IoT/OT”


Nell’era della connettività globale, la sicurezza dei dispositivi IoT e OT è diventata una priorità per le aziende di ogni settore. Con l’aumento esponenziale dei dispositivi connessi, dalle fabbriche intelligenti agli uffici moderni, le vulnerabilità si moltiplicano, mettendo a rischio dati sensibili e operazioni cruciali.

Di questo e altro abbiamo parlato con Nathan Howe, GVP Innovation di Zscaler, per scoprire un panorama in rapida evoluzione, dove le soluzioni tradizionali mostrano il fianco di fronte alle nuove sfide.

La maggior parte dei dispositivi IoT e OT infatti non è stata progettata con la sicurezza come priorità, lasciando coloro che li utilizzano esposti a rischi significativi. E la visione di Zscaler è di creare un ambiente di lavoro sicuro e produttivo, estendendo i principi di zero trust ai dispositivi IoT e OT. Tutto ciò, riducendo la complessità operativa e i costi associati alle tecnologie di sicurezza legacy.

Prima di scoprire come ciò sia possibile, però, abbiamo voluto partire dai risvolti psicologici di chi lavora per un’azienda il cui operato, come dimostra quanto accaduto con CrowdStrike, può avere ripercussioni su scala globale.

Il mondo della cybersecurity è affascinante e al contempo inquietante. Nel vostro ruolo di ‘poliziotti digitali’, come vivete la quotidianità sapendo che un vostro errore può avere ripercussioni disastrose?

Nathan Howe: Diciamo che la nostra vita sarebbe perfetta per un noir ambientato nel mondo della cybersecurity. Sarebbe davvero intrigante da leggere.

Nathan Howe è GVP Innovation di Zscaler

Nathan Howe è GVP Innovation di Zscaler.

Come hai iniziato?

Nathan Howe: Ho iniziato come penetration tester, quindi ero pagato dalle aziende per cercare vulnerabilità nei loro sistemi e migliorare la loro sicurezza. Nel corso degli anni ho lavorato in diversi settori e posso confermare che lo stress è una costante delle nostre vite. Tuttavia, c’è un’adrenalina unica che si avverte quando si affrontano queste sfide.

Oggi, comunque, il mio ruolo è cambiato: mi occupo principalmente di sviluppare nuove tecnologie di sicurezza, il che porta emozioni di un altro tipo.

Cosa succede durante una crisi? Come reagiscono le persone?

Nathan Howe: Quando un nostro cliente ha un problema – e abbiamo avuto molti clienti che hanno subito violazioni, non a causa nostra, ma per altri motivi – noi interveniamo. Ci riuniamo in call, collaboriamo con loro per sviluppare soluzioni e risolvere il problema.

Una delle sfide cruciali che affrontiamo è che i nostri clienti, nonostante le migliori intenzioni, spesso perdono di vista il quadro generale della sicurezza informatica. Per la maggior parte delle aziende, l’IT non rappresenta il core business. Utilizzano certamente la tecnologia ma non sono esperti del settore. L’informatica, di per sé, per loro non genera profitti diretti.

Di conseguenza, quando emerge una criticità, l’IT si trova a fronteggiare l’emergenza mentre cerca di mantenere operative le funzioni aziendali di routine. In queste condizioni non sempre riesce a implementare le soluzioni più efficaci o a effettuare deployment ottimali.

Di fronte a problemi seri, sono costretti a stravolgere completamente le loro priorità. E questo è ciò che definiamo il “momento Titanic”: tutti s’illudono di navigare su una nave inaffondabile, finché non si scontrano con l’iceberg rappresentato dagli hacker.

Il lato positivo dei momenti critici invece è che emerge il meglio di molti professionisti. Spesso c’è chi si fa avanti, desideroso di contribuire attivamente alla soluzione del problema. È in queste situazioni che si vede veramente la passione e la dedizione di chi lavora nella cybersecurity.

Kevin Mitnick (1963-2023), oltre che teorizzatore dell’ingegneria sociale, era amico di Nathan Howe, che ha voluto ricordarlo con belle parole nel corso dell’intervista.

Kevin Mitnick, ne L’Arte dell’Inganno, scrisse che il più grande alleato dell’ingegneria sociale è la naturale propensione umana ad aiutare, che le rende facilmente manipolabili. Quella che hai appena descritto pare la situazione ottimale per gli attaccanti…

Nathan Howe: Sono d’accordo, gli hacker sfruttano proprio l’innata predisposizione delle persone ad aiutare. Quanto a Kevin, purtroppo è venuto a mancare e lo conoscevo da anni (mi mostra una loro foto risalente al 2003, ndR). All’epoca c’era una tecnologia che molti non comprendevano appieno: le persone stavano iniziando a collegare i computer alla rete telefonica, senza capirne le implicazioni.

Kevin sapeva come sfruttare questa situazione. Era abilissimo nel manipolare sia le persone che i sistemi informatici. Conosceva i punti deboli dei vecchi sistemi PBX, i centralini telefonici usati ad esempio negli hotel. Sapeva che digitando determinati numeri poteva trovare vie d’accesso inimmaginabili.

Era talmente bravo che si diceva potesse far scoppiare una guerra con una semplice telefonata. Ma nonostante questa reputazione, era una persona davvero gentile. Credo che l’industria a volte lo abbia giudicato male e la sua scomparsa mi ha rattristato molto.

Nel corso dello Zenith Live 24 è emerso il concetto che il nuovo perimetro di sicurezza è l’individuo stesso. Tuttavia, il costante aumento dell’IoT sta espandendo il perimetro agli oggetti. Qual è allora il vero perimetro oggi? Ne esiste ancora uno?

Nathan Howe: Credo che pensare in termini di perimetro sia ormai un approccio superato. Se guardiamo alla cybersecurity, storicamente è stata concepita come una battaglia militare: tu hai il tuo lato, io ho il mio. Questo era il modello delle vecchie battaglie, della Prima e della Seconda Guerra Mondiale.

I perimetri però sono generalmente statici, possono spostarsi ma in lunghi periodi di tempo, per cui preferisco parlare di “bolle”. La mia bolla sono io; e i miei dispositivi sono bolle diverse, a sé stanti, collegate alla mia bolla personale.

La dimensione della propria bolla dipende dai ruoli e dalle responsabilità. Per esempio, il mio laptop e il mio telefono hanno requisiti di accesso e controlli completamente diversi.

Hai presente come a volte le bolle di sapone si attaccano tra loro formando gruppi di tre o quattro? Ecco, è così che dobbiamo pensare al mondo della sicurezza. Una bolla può interconnettersi alle altre quando necessario e poi staccarsi quando non serve più.
Per Nathan Howe il concetto di perimetro di sicurezza è ormai superato. E propone invece quello delle bolle.

E ora anche i dispositivi IoT e OT sono ‘diventati bolle’…

Nathan Howe: Assolutamente sì. Non sono più elementi passivi ma partecipano a pieno titolo a un ecosistema di sicurezza interconnesso. Ora sono nodi attivi in una rete di connessioni.

Ciò ci porta a ripensare completamente l’approccio alla sicurezza. Non si tratta più di proteggere un singolo perimetro ma di gestire e mettere in sicurezza una moltitudine di connessioni dinamiche tra dispositivi, persone e dati. È una sfida complessa ma anche un’opportunità per creare sistemi di sicurezza più flessibili e resilienti.

Le Zscaler Zero Trust SIM non potevano arrivare in un momento migliore. Com’è nata l’idea?

Nathan Howe: Circa tre anni fa abbiamo deciso di connettere al nostro exchange i dispositivi IoT e OT. Volevamo inserire il nostro software direttamente sulle SIM ma quelle tradizionali non erano abbastanza potenti; quindi, abbiamo deciso di salire di un livello, passando alla rete mobile.

Abbiamo così sviluppato una SIM che sembra normale ma che in realtà ha una caratteristica: quando la vendiamo a un cliente, possiamo identificarla e collegarla al suo account. Ciò significa che il traffico dati del dispositivo passa attraverso il nostro gateway, che agisce come un filtro di sicurezza.

In questo modo siete certi che ogni segnale in uscita dal dispositivo passi attraverso di voi e non vada dove non dovrebbe andare…

Nathan Howe: Esattamente.

Come funziona la configurazione?

Nathan Howe: Dipende dal dispositivo. Per quelli moderni, non serve fare nulla. Per i dispositivi più vecchi, invece, è diverso. Possiamo inviare informazioni per cambiare la configurazione ma alcuni potrebbero non supportare questa possibilità.

Possiamo inserire fino a otto IMSI su una SIM, permettendole di funzionare su otto reti diverse. E facciamo tutto da remoto. Non serve programmare la SIM direttamente; basta inserirla in un dispositivo, configurarla e controllarla. Possiamo inviare aggiornamenti e modificarla attraverso l’infrastruttura mobile, offrendo grande flessibilità e potenzialità.

La Zero Trust SIM connette i dispositivi IoT e OT al Zero Trust Exchange di Zscaler.

Tutto ciò, a quale prezzo?

Nathan Howe: Non abbiamo un prezzo fisso e il motivo è che abbiamo clienti con esigenze molto diverse. Alcuni acquistano le Zero Trust SIM a fronte di dieci megabyte al mese di traffico, e quindi pagano tariffe dati molto basse, tipo un dollaro al mese.

D’altra parte, abbiamo clienti che generano terabyte di traffico da una singola SIM, come una telecamera di sicurezza che trasmette costantemente immagini da una certa location, e pagano centinaia di dollari al mese per l’utilizzo della rete. Il prezzo si colloca tra questi estremi, variando in base all’utilizzo specifico.

Facciamo alcuni esempi di coloro che avrebbero bisogno della Zscaler Zero Trust SIM?

Nathan Howe: Certamente. Iniziamo con un esempio comune, che riguarda molti di noi, ossia quello delle società energetiche. Nelle nostre case c’è un contatore che calcola il consumo d’energia, che ha al suo interno una SIM che comunica con la società energetica, permettendole di monitorare i consumi da remoto. Si tratta di un dispositivo sensibile, che può essere vulnerabile a modifiche o a usi impropri.

Con la nostra tecnologia, però, possiamo offrire un livello di sicurezza superiore. La Zscaler Zero Trust SIM garantisce che tutti i dati passino attraverso canali sicuri, prevenendo manomissioni o accessi non autorizzati.

Un altro esempio potrebbe essere il settore dei trasporti. Immagina un sistema di monitoraggio per le flotte di veicoli commerciali, dove ogni veicolo sia equipaggiato con una nostra SIM che trasmette dati sulla posizione, il consumo di carburante e il suo stato. La sicurezza qui è essenziale per prevenire il furto di dati sensibili o la manomissione delle informazioni.

Un terzo esempio potrebbe essere nel campo medico, come nel caso di dispositivi di monitoraggio remoto dei pazienti, che trasmettono dati vitali agli ospedali e necessitano di un livello di sicurezza estremamente elevato. Le Zscaler Zero Trust SIM possono garantire che questi dati sensibili siano protetti da accessi non autorizzati, mantenendo la privacy del paziente e l’integrità delle informazioni mediche.

Sarete sorpresi di scoprire cosa si possa fare coi ceppi bloccaruota negli USA…

Interessante. Altri esempi?

Nathan Howe: Il mio preferito sono i ceppi che mettono sulle ruote quando parcheggi in divieto di sosta. Da noi questi blocchi hanno delle SIM al loro interno per monitorare la situazione: dicono alla centrale che la ruota è bloccata, da quanto tempo lo è, insieme ad altre informazioni telemetriche.

Alcuni hanno scoperto che rompendo i ceppi e rimuovendo le SIM, si può avere una connessione a internet illimitata. Così, hanno iniziato a usarle nei loro dispositivi personali per guardare ad esempio video su YouTube. Ciò ha fatto esplodere i costi di connessione internet per le aziende che gestiscono questi dispositivi. Con la nostra soluzione ciò non succederebbe, perché abbiamo pieno controllo sulle applicazioni utilizzate, il traffico e gli accessi.

Un altro esempio interessante simile riguarda le infrastrutture distribuite. Penso alle reti ferroviarie, che sono dotate di sensori lungo le linee per sapere dove si trovano i treni. Questi non possono essere connessi tramite i normali cavi, perché sarebbe troppo costoso. Così, anni fa, li hanno agganciati a reti 2G, che esistono ancora oggi.

Chiunque però può avvicinarsi ai sensori, estrarre le SIM e usarle. E siccome spesso queste comunicano attraverso reti private, si tratta di vere e proprie porte che si aprono sulle aziende ferroviarie. Il che è un bel rischio…

Altrei esempi interessanti sono i distributori automatici, che comunicano all’azienda tramite SIM la necessità di rifornimenti, o le cavigliere per i detenuti ai domiciliari. Ogni giorno, comunque, i clienti mi raccontano nuovi casi d’uso…

Immagino applicazioni molto utili nell’automotive. Siete già in discussione con alcune case?

Nathan Howe: Purtroppo non posso menzionare le aziende con cui siamo in trattativa, posso comunque dire che stiamo collaborando con diversi clienti in questo momento e che ogni auto moderna crea almeno cinque gigabyte di dati telemetrici al mese.

Parliamo di temperatura del motore, sensori della pressione dell’olio, pressione delle gomme… tutto viene raccolto e inviato ai costruttori, che così sanno tutto sulle loro macchine, ovunque si trovino nel mondo.
Le auto di oggi generano almeno cinque gigabyte di dati telemetrici al mese. In futuro, con la guida autonoma, saranno molto di più. Un mercato molto appetibile per Zscaler…

Molti privati sarebbero felici di mettere in sicurezza i loro dispositivi personali con una Zscaler Zero Trust SIM…

Nathan Howe: È qualcosa che abbiamo esplorato diverse volte con vari partner delle telecomunicazioni. Ma l’ostacolo non è la tecnologia, totalmente alla nostra portata, quanto la gestione delle policy per milioni di utenti finali.

Ad esempio, come posso configurare la mia policy in modo che sappia quando qualcosa va storto? Le aziende hanno un team di sicurezza che prende i log di sistema e capisce cosa sta succedendo. Mia mamma, invece, non saprebbe come fare.

Sono assolutamente favorevole alla protezione degli utenti finali, penso sia una grande opportunità ma è molto difficile da realizzare.

Anche perché, oltre alle policy, c’è anche un altro problema: cosa succederebbe quando, sempre mia madre, dovesse chiamare il nostro call center per chiedere supporto? Come risolveremmo il problema? Come faremmo a condividere le informazioni?

Sono però d’accordo con te che molte persone pagherebbero volentieri una somma ogni mese per disporre di questi servizi. Chissà…

Condividi l’articolo


Articoli correlati

Altro in questa categoria


https://www.securityinfo.it/2024/08/06/nathan-howe-ecco-come-zscaler-protegge-i-dispositivi-iot-ot/?utm_source=rss&utm_medium=rss&utm_campaign=nathan-howe-ecco-come-zscaler-protegge-i-dispositivi-iot-ot



The imperative of fortifying police stations with secured entry solutions

@import url(‘https://fonts.googleapis.com/css2?family=Nunito+Sans:ital,opsz,wght@0,6..12,400;0,6..12,500;0,6..12,600;0,6..12,700;1,6..12,400;1,6..12,500;1,6..12,600;1,6..12,700&family=Nunito:ital,wght@0,400;0,500;0,600;0,700;1,400;1,500;1,600;1,700&display=swap’); @import url(‘https://fonts.googleapis.com/css2?family=Architects+Daughter&family=Roboto:ital,wght@0,100;0,300;0,400;0,500;0,700;0,900;1,100;1,300;1,400;1,500;1,700;1,900&display=swap’); h3 { font-weight: bold; font-size: 18px; color: #C72026; } figure { padding: 4px; margin: auto; } figcaption { background-color: #F4F5F6; color: #404144; Nunito Sans’, Arial, sans-serif; font-size: 18px; padding: 5px; text-align: left; } .pqFull { display: block; border-width: 2px 0; border-style: solid; border-color: #58526F; padding: 1.5em 0 0.5em; margin: 1.5em 0; position: relative; } .pqFull:before { content: ‘\201C’; position: absolute; top: 0em; left: 50%; transform: translate(-50%, -50%); background: #fff; width: 3rem; height: 2rem; color: #666; text-align: center; } .pqFull:after { content:; display: block; text-align: right; font-size: 0.875em; color: #e74c3c; }

In an era where safety concerns dominate public discourse, securing police building perimeters and entrances is imperative. The sanctity of law enforcement institutions demands robust measures to safeguard against external threats and potential breaches. Active shooters, terrorists and other incidents are a reality faced by police stations across the U.S. and often, police buildings house officers and civilians. Secured entrances must balance authorized staff access with layers of security to allow the public to move seamlessly and securely while preventing perpetrators from entering the building — and allowing for containment of incidents when they occur.

Outfitting police buildings with entry solutions like turnstiles and revolving doors offers a multi-faceted approach to securing police building entrances. By implementing these physical barriers, law enforcement agencies can control the influx of individuals, ensuring that only authorized personnel gain entry. Moreover, these solutions serve as effective deterrents against unauthorized access attempts, bolstering the overall security posture of the facility. Let’s explore the importance of layered security entrances, and the solutions available, for police stations.

Layering secured entrances for maximum protection

Police stations must account for the unique requirements of the building as a whole and each entry point to properly design the best layered and secured entrance system.

Various secured entry solutions excel in managing traffic flow and detecting unauthorized access at attended entrances, enhancing overall security measures. Meanwhile, specialized solutions are designed to proactively prevent unauthorized entry at unattended entrances, addressing the evolving challenges posed by hybrid work schedules and limited budgets prevalent in police operations. Broadly, security entrances for police buildings can be categorized into three main groups: deter, detect and prevent, with each serving a distinct yet complementary role in bolstering security protocols.

  • Tripods or full-height turnstiles deter against unauthorized access, discouraging attempts to enter a facility.
  • Optical turnstiles with embedded sensor and access technologies detect unauthorized entry attempts, including tailgating and piggybacking, and issue alarms in real-time.
  • Interlocking mantrap portals or security revolving doors can be integrated with other technologies to identify unauthorized attempts and block a bad actor from entering, even without a guard present. This is the most robust method for securing access points to prevent unauthorized entry and exit, including tailgating and piggybacking.

Luckily, many modern security entrances have built-in sensor technologies to support the most effective means of balancing the necessary throughput with optimized physical access at crucial entry and egress points within law enforcement facilities.

Tourlock at Dallas Police Departmen
Tourlock at Dallas Police Department. Image courtesy of Tourlock at Dallas Police Department

Securing perimeters at police facility

To truly fortify police stations, we must address bridging the gap of unauthorized entry, starting with a sharp eye on perimeter entry points surrounding the building. Heavy-duty, full-height bi-directional turnstiles provide a first line of defense for exterior perimeters at police facilities. Built to withstand a range of weather conditions and designed for maximum protection, these turnstiles can fortify security before a malicious actor can get close to the front entrance. With access control, intercoms and video surveillance capabilities, data collected from embedded sensor systems can be used by security personnel to anticipate and measure the risk of infiltration.

The sanctity of law enforcement institutions demands robust measures to safeguard against external threats and potential breaches.

Protecting entrances and lobbies

For added layered security, where multiple robust solutions for deterrence are required, a full-height turnstile can be used at the exterior perimeter and front entrances. Based on the building design and application, high security revolving doors also provide added flexibility and protection at front entrances, balancing access for authorized staff and enabling secure entry for the public.

In buildings with more expansive lobbies and heightened risk, a more comprehensive plan can be implemented to ensure safety. In these instances, a dual front lobby entrance screening mechanism can be installed in conjunction with a single exit revolving door for traffic exiting the lobby. This layered approach can provide an additional barrier for security between areas such as initial screening and the main lobby, while the use of bullet-resistant glass protects against gun violence. Using high security revolving doors with features like tailgating and piggybacking prevention that are purpose-built for security in high-traffic areas ensures optimal protection.

Layered security entrances, such as high-security revolving doors, seamlessly integrate physical building security entrances with contemporary architectural designs, providing both aesthetic appeal and robust security features. These entrances not only enhance the overall visual appeal of modern buildings but also ensure comprehensive protection against unauthorized access, aligning seamlessly with evolving security needs.

Protecting law enforcement by adopting secure entry solutions

The adoption of entry solutions like turnstiles, revolving doors and access control systems is indispensable for securing police building perimeters and entrances. These specialized measures not only fortify defenses against external threats but also enhance operational efficiency and uphold public trust. As guardians of safety and order, law enforcement agencies must prioritize the implementation of these tailored solutions to safeguard their personnel, assets and the communities they serve.

https://www.securitymagazine.com/articles/100900-the-imperative-of-fortifying-police-stations-with-secured-entry-solutions


Product spotlight on cybersecurity

h3 { font-weight: bold; font-size: 18px; color: #C72026; } h4 { font-weight: bold; font-size: 16px; color: #58526F;

Cybersecurity is a constant priority for business as new threats emerge each day. Security magazine highlights a variety of cybersecurity products to protect data and businesses.

Beazley Security’s Managed eXtended Detection and Response (MXDR) service

BEAZLEY

Quickly Detect and Respond to Threats

Beazley Security’s Managed eXtended Detection and Response (MXDR) service combines human intelligence with advanced technologies and external data sources to provide clients around-the-clock protections. The MXDR provides total transparency to cyber operations, and uncomplicated endpoint-based pricing that includes unlimited data ingestion and long-term retention that continuously powers daily threat hunting activities. Image courtesy of Beazley

FIND OUT MORE AT BEAZLEY.COM/EN-US


Cobalt’s Pentest as a Service (PtaaS) model

COBALT

Protect Network Data and Applications

Cobalt’s Pentest as a Service (PtaaS) model combines data, technology and talent to resolve security challenges for modern web applications, mobile applications, networks and APIs. The approach applies a SaaS security platform to pentesting to help organizations to keep pace with their evolving attack surface and agile software development lifecycles. PtaaS enhances workflow efficiencies and delivers real-time insights companies need to remediate risks quickly. Image courtesy of Cobalt

FIND OUT MORE AT COBALT.IO


Secureframe

SECUREFRAME

Use AI for Risk Management

Secureframe comply provides a unified platform with AI tools to reduce the manual effort involved in maintaining compliance and managing security. Secureframe offers tools such as Comply AI for remediation, risk assessment and policy management, which automate the processes of fixing failing controls, conducting risk assessments and crafting policies. Secureframe AI provides cloud remediation guidance by generating code fixes for cloud environments. Secureframe Comply AI for Remediation provides infrastructure-as code-solutions, allowing customers to implement necessary adjustments. Image courtesy of Secureframe

FIND OUT MORE AT SECUREFRAME.COM


Guardz

GUARDZ

Scans for Threats to Prevent Cyberattacks

Guardz is a security platform that continuously scans for threats across multiple attack vectors and generates issues when a threat is detected. Issues are prioritized by severity of risk and include all the relevant details to trigger automated remediation. Guardz ensures up-to-date employee training by notifying admins of training status and recommending industry-standard best practices. Customizable campaign planning allows businesses to target specific users and meet company goals. Image courtesy of Guardz

FIND OUT MORE AT GUARDZ.COM


FortiGate VM

FORTINET

Protect the Network From Security Threats

FortiGate VM provides protection from a broad array of network threats. Running the same OS as FortiGate NGFW hardware appliances, it enables users to enforce consistent security policies across private, public, and telco clouds. Powered by AI-driven threat intelligence, FortiGate VMs provide industry-leading threat protection at scale. FortiGuard Labs uses machine learning algorithms and AI to analyze vast amounts of data and identify emerging threats in real time. Additionally, behavioral analysis powered by AI enables the identification of anomalous activities, aiding in the proactive mitigation of potential cyberattacks. Image courtesy of Fortinet

FIND OUT MORE AT FORTINET.COM


Sentinel One’s platform

SENTINEL ONE

Automatically Detects Malware

Sentinel One’s platform detects malware and zero-day exploits in milliseconds with AI-powered detection engines. The platform allows users to streamline and automate threat response with automatic quarantine of malicious objects. Users can scan objects directly in their Amazon S3 buckets and ensure no sensitive data leaves the environment. Image courtesy of Sentinel One
FIND OUT MORE AT SENTINELONE.COM

https://www.securitymagazine.com/articles/100903-product-spotlight-on-cybersecurity


Mac and Windows users infected by software updates delivered over hacked ISP

The words

Hackers delivered malware to Windows and Mac users by compromising their Internet service provider and then tampering with software updates delivered over unsecure connections, researchers said.

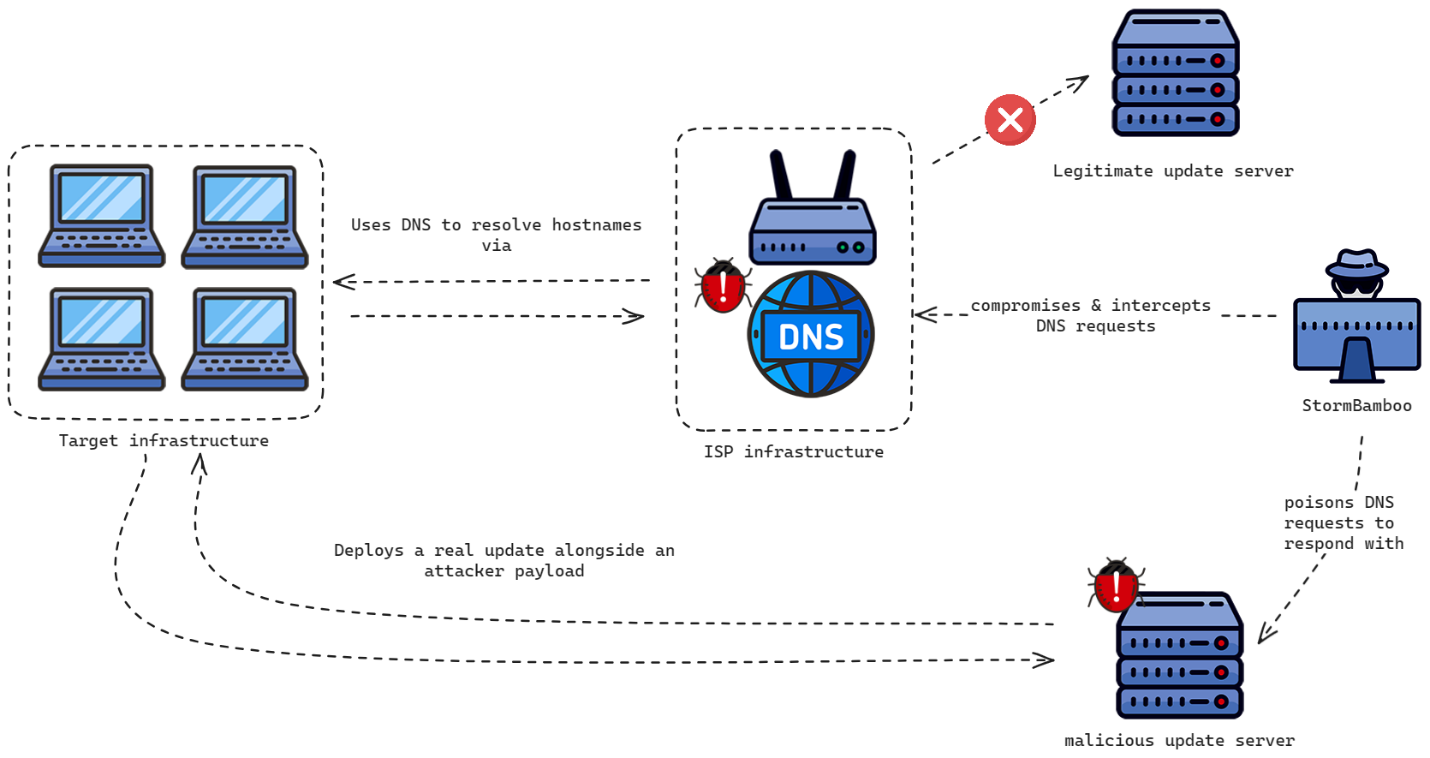
The attack, researchers from security firm Volexity said, worked by hacking routers or similar types of device infrastructure of an unnamed ISP. The attackers then used their control of the devices to poison domain name system responses for legitimate hostnames providing updates for at least six different apps written for Windows or macOS. The apps affected were the 5KPlayer, Quick Heal, Rainmeter, Partition Wizard, and those from Corel and Sogou.

These aren’t the update servers you’re looking for

Because the update mechanisms didn’t use TLS or cryptographic signatures to authenticate the connections or downloaded software, the threat actors were able to use their control of the ISP infrastructure to successfully perform machine-in-the-middle (MitM) attacks that directed targeted users to hostile servers rather than the ones operated by the affected software makers. These redirections worked even when users employed non-encrypted public DNS services such as Google’s 8.8.8.8 or Cloudflare’s 1.1.1.1 rather than the authoritative DNS server provided by the ISP.

“That is the fun/scary part—this was not the hack of the ISPs DNS servers,” Volexity CEO Steven Adair wrote in an online interview. “This was a compromise of network infrastructure for Internet traffic. The DNS queries, for example, would go to Google’s DNS servers destined for 8.8.8.8. The traffic was being intercepted to respond to the DNS queries with the IP address of the attacker’s servers.”

In other words, the DNS responses returned by any DNS server would be changed once it reached the infrastructure of the hacked ISP. The only way an end user could have thwarted the attack was to use DNS over HTTPS or DNS over TLS to ensure lookup results haven’t been tampered with or to avoid all use of apps that deliver unsigned updates over unencrypted connections.

Volexity provided the following diagram illustrating the flow of the attack:

As an example, the 5KPlayer app uses an unsecure HTTP connection rather than an encrypted HTTPS one to check if an update is available and, if so, to download a configuration file named Youtube.config. StormBamboo, the name used in the industry to track the hacking group responsible, used DNS poisoning to deliver a malicious version of the Youtube.config file from a malicious server. This file, in turn, downloaded a next-stage payload that was disguised as a PNG image. In fact, it was an executable file that installed malware tracked under the names MACMA for macOS devices or POCOSTICK for Windows devices.

MACMA first came to light in a 2021 post published by Google’s Threat Analysis Group, a team that tracks malware and cyberattacks backed by nation-states. The backdoor was written for macOS and iOS devices and provided a full suite of capabilities including device fingerprinting, screen capture, file downloading and uploading, execution of terminal commands, audio recording, and keylogging.

POCOSTICK, meanwhile, has been in use since at least 2014. Last year, security firm ESET said the malware, which it tracked under the name MGBot, was used exclusively by a Chinese-speaking threat group tracked as Evasive Panda.

ESET researchers determined that the malware was installed through legitimate updates of benign software, but they weren’t sure how that happened. One possibility, the researchers said at the time, was through a supply-chain attack that replaced the legitimate updates with malicious ones at the very source. The other possible scenario was through a MitM attack on the servers delivering the updates. Volexity’s findings now confirm that the latter explanation is the correct one.

In at least one case in the most recent attacks, StormBamboo forced a macOS device to install a browser plugin Volexity tracks under the name RELOADEXT. The extension masquerades as one that loads webpages to be compatible with Internet Explorer. In fact, Volexity said, it copies browser cookies and sends them to a Google Drive account controlled by the attackers. The data was base64 encoded and encrypted using the Advanced Encryption Standard. Despite the care taken by the hackers, they nonetheless exposed the client_id, client_secret, and refresh_token in the malicious extension.

One other technique Volexity observed was StormBamboo’s use of DNS poisoning to hijack www.msftconnecttest.com, a domain Microsoft uses to determine if Windows devices are actively connected to the Internet. By replacing the legitimate DNS resolution with an IP address pointing to a malicious site operated by the threat actors, they could intercept HTTP requests destined for any host.

Adair declined to identify the hacked ISP other than to say it’s “not a big huge one or one you’d likely know.”

“In our case the incident is contained, but we see other servers that are actively serving malicious updates but we do not know where they are being served from,” he said. “We suspect there are other active attacks around the world we do not have purview into. This could be from an ISP compromise or a localized compromise to an organization such as on their firewall.”

As noted earlier, there are many options for preventing these sorts of attacks beyond (1) eschewing all software that updates unsecurely or (2) using DNS over HTTPS or DNS over TLS. The first method is likely the best, although it likely means having to stop using a preferred app in at least some cases. The alternative DNS configurations are viable, but at the moment are offered by only a handful of DNS providers, with 8.8.8.8 and 1.1.1.1 being the best known.

https://arstechnica.com/?p=2041175


99% of Global 2000 organizations are linked to a supply chain breach

A report by SecurityScorecard reveals that almost all Global 2000 companies (99%) are connected to a supply chain breach. The report asserts that the interconnected nature of modern business may be partially responsible for this, as a vulnerability in one part of the supply chain may have far-reaching consequences, potentially impacting an entire ecosystem. 

Key findings from this report include: 

  • Supply chain breach incidents cost 17 times more to manage and remedy than first-party breaches. 
  • It is estimated that Global 2000 breaches cost between $20 billion and $80 billion within 15 months. 
  • 90% of Global 2000 companies act as vendors to each other, creating an interdependent ecosystem with concentrated risk.

20% of these companies utilize 1,000 or more products. Furthermore, at least 80% of Global 2000 companies use the top eight most widely employed vendors. Four out of the top five vendors on this list recently reported a breach. 

https://www.securitymagazine.com/articles/100916-99-of-global-2000-organizations-are-linked-to-a-supply-chain-breach


Le telecomunicazioni sono i bersagli principali dei cyberattacchi


Secondo una recente analisi di Kaspersky, le telecomunicazioni sono i principali bersagli dei cyberattacchi nel 2024: da gennaio a giugno si sono verificati 284 incidenti di cybersicurezza ogni 10.000 sistemi.

Questo settore è particolarmente allettante per gli attaccanti per via dei dati sensibili che gestisce e le relazioni di fiducia. Le telecomunicazioni hanno anche affrontato il più alto numero medio di incidenti critici, con 32 attacchi ogni 10.000 sistemi centrali per le imprese.

telecomunicazioni

Pixabay

“Un attacco riuscito, soprattutto se avanzato, a un’azienda di telecomunicazioni può esporre i dati di milioni di clienti, compresi dettagli di contatto e le informazioni sulle carte di credito. Inoltre, può servire da trampolino di lancio per ulteriori attacchi ai clienti attraverso lo sfruttamento di relazioni di fiducia. Ecco perché questo settore è così interessante per i criminali informatici” ha spiegato Sergey Soldatov, Head of Kaspersky Managed Detection and Response.

Anche le aziende di mass media e le società di costruzioni sono obiettivi interessanti per gli attaccanti: i primi hanno subito 180 attacchi ogni 10.000 sistemi, mentre i secondi 179. I ricercatori di Kaspersky spiegano che i mass media sono tradizionalmente presi di mira durante i conflitti internazionali, mentre le società di costruzioni sono interessanti perché si affidano a molti subappaltatori e l’impatto degli attacchi può diventare molto elevato.

“Le organizzazioni dei mass media, a loro volta, diventano un obiettivo sempre più frequente durante i conflitti internazionali, spesso caratterizzati da una vera e propria guerra dell’informazione in cui svolgono un ruolo cruciale. Infine, ma non meno importante, le imprese di costruzioni hanno volumi di denaro significativi e si affidano a subappaltatori, rendendoli vulnerabili agli attacchi tramite infrastrutture di partner fidati e spear phishing” ha continuato Soldatov.

attacchi informatici

Pixabay

A livello globale il numero di incidenti informatici è rimasto sostanzialmente stabile, segnando solo una leggera diminuzione. Le organizzazioni hanno cominciato a rafforzare le proprie misure di sicurezza dopo l’aumento degli attacchi nel 2021-2022, utilizzando in particolare approcci più incisivi come la valutazione delle vulnerabilità e penetration test.

Per proteggersi delle minacce informatiche, Kaspersky consiglia di installare soluzioni MDR e condurre valutazioni periodiche per valutare se i sistemi sono stati compromessi. Le imprese dovrebbero inoltre investire sulla formazione dei dipendenti, in modo che siano sempre aggiornati sulle ultime minacce e sulle tecniche di phishing e social engineering, e fornire al proprio team SOC tutte le informazioni più recenti sulle minacce dell’azienda. 

Condividi l’articolo


Articoli correlati

Altro in questa categoria


https://www.securityinfo.it/2024/08/05/le-telecomunicazioni-sono-i-bersagli-principali-dei-cyberattacchi/?utm_source=rss&utm_medium=rss&utm_campaign=le-telecomunicazioni-sono-i-bersagli-principali-dei-cyberattacchi


Alex Stamos named Chief Information Security Officer at SentinelOne

Alex Stamos has been hired as Chief Information Security Officer (CISO) at Sentinel One. In this role, the former Chief Security Officer of Meta and Chief Information Security Officer at Yahoo!, will oversee the company’s security engineering and operations teams.

Stamos, a seasoned professional in the cybersecurity field, joined SentinelOne as Chief Trust Officer in 2023 through the acquisition of the Krebs Stamos Group. His extensive experience includes serving on the Aspen Institute’s Cyber Security Task Force, the DHS Cybersecurity Advisory Committee, the Bay Area CSO Council, and the Council on Foreign Relations.

Stamos is also on the advisory board of NATO’s Collective Cybersecurity Center of Excellence and continues to teach cybersecurity and policy at Stanford University.

Congratulations!

https://www.securitymagazine.com/articles/100915-alex-stamos-named-chief-information-security-officer-at-sentinelone


Axis Communications establishes Axis Experience Center

Axis Communications has launched the Axis Experience Center (AEC) in Phoenix, AZ, promoting regional access to new technology. The expressed goal of the facility is to cultivate stronger connections with partners and customers in the area, encouraging a community of partnership and innovation for local communities and beyond. The facility features training rooms, conference rooms and demo rooms to support continued collaboration and evolution. 

The AEC also features: 

  • Real-time analytics such as people counting, hardhat detection, coughing detection and more. 
  • A retail-centered space where retail analytics are displayed in a fun environment. 
  • A theater-style demo area. 

Bill Wendlandt, Business Area Director, U.S. West at Axis Communications, says, “Localized, on-site support makes a real difference for our partners and customers, who look to us to provide them with the tools and expertise they need to improve their security, safety, and business intelligence capabilities. We at Axis are both honored and excited to grow our relationship with the flourishing Phoenix business community, and we look forward to working directly with our many partners and customers in the area to provide them with the innovative solutions they need to thrive in today’s evolving business environment.”

https://www.securitymagazine.com/articles/100914-axis-communications-establishes-axis-experience-center


Securing hospitality: Balancing guest experience and safety

@import url(‘https://fonts.googleapis.com/css2?family=Nunito+Sans:ital,opsz,wght@0,6..12,400;0,6..12,500;0,6..12,600;0,6..12,700;1,6..12,400;1,6..12,500;1,6..12,600;1,6..12,700&family=Nunito:ital,wght@0,400;0,500;0,600;0,700;1,400;1,500;1,600;1,700&display=swap’); h3 { font-weight: bold; font-size: 18px; color: #C72026; } .w3-panel:after,.w3-panel:before { content: “”; display: table; clear: both } .w3-panel { padding: 16px; margin-top: 16px; margin-bottom: 16px } .w3-leftbar { border-left: 6px solid #502d52!important } .w3-color,.w3-hover-color:hover { color: #502d52!important; background-color: #ecdeed!important } .w3-large { font-size: 20px!important } .w3-sans-serif { Nunito Sans’,Arial,sans-serif } .w3-opacity,.w3-hover-opacity:hover { opacity: 0.60 }

Ensuring the safety and well-being of guests is top of mind for hospitality security leaders. This responsibility — or duty of care — often extends beyond providing comfortable accommodations and excellent customer service, it includes physical security, health and safety, and risk management.

Here, Doug Alexander, Director of Security and Loss Prevention at Grand Hotel on Mackinac Island, Michigan discusses challenges and advice within the industry.

Duty of care

Alexander says that in his experience the hospitality industry, hotels, resorts, and other establishments must ensure the safety and well-being of their guests and staff.

“Keeping everyone safe is a top priority,” he says. “This means taking steps to prevent accidents and injuries throughout the property. Hotels need to make sure that public areas, guest rooms, and staff workspaces are free of hazards.”

He adds that using surveillance cameras, hiring security personnel, implementing access control systems, and ensuring proper lighting – especially in high-risk areas like entrances, parking lots, and behind-the-scenes locations – are key to protect against theft, vandalism, and violence.

“By prioritizing safety and security, hospitality establishments not only protect their guests and staff but also build their reputation and trustworthiness,” Alexander says. “A strong commitment to these principles shows a hotel’s dedication to providing a safe environment, which is crucial for attracting and retaining guests.”

Security challenges faced by hotels

Hotels face a range of unique security challenges due to their open nature. Security leaders are tasked with balancing the for security measures with the desire to provide a welcoming and comfortable experience for guests.

“Balancing security measures with providing a welcoming and comfortable experience for guests is a nuanced task that requires careful planning and sensitivity,” Alexander says. “Security leaders in the hospitality industry can achieve this balance through a combination of strategic design, staff training, technology integration, and clear communication.”

❝ Doug Alexander, Director of Security and Loss Prevention at Grand Hotel  Photo courtesy of Alexander

By prioritizing safety and security, hospitality establishments not only protect their guests and staff but also build their reputation and trustworthiness. A strong commitment to these principles shows a hotel’s dedication to providing a safe environment, which is crucial for attracting and retaining guests.”
— Doug Alexander, Director of Security and Loss Prevention at Grand Hotel. Photo courtesy of Alexander

Some key approaches, according to Alexander:

  • “Ensure that security personnel are present and visible enough to deter potential threats, but positioned in a way that does not intrude on the guest experience. For example, security can be stationed discreetly near entry points or common areas rather than prominently in the lobby. Establishments should also use advanced surveillance technologies such as high-definition cameras and access control systems that blend seamlessly with the hotel’s decor. This maintains a secure environment without making guests feel watched or uncomfortable. Training security personnel in customer service skills establishes clear expectations that they will interact with guests warmly and professionally. Security staff should be approachable and capable of providing assistance, directions, or information when needed. Leaders should equip security staff with uniforms that are professional but not intimidating. The design should reflect the hotel’s brand and create a sense of safety without feeling militaristic. Personnel should use mobile apps to communicate with guests about security features, emergency procedures, and personal safety tips. This approach is convenient and helps guests feel informed and secure. Communicate security policies to guests in a way that emphasizes their safety and convenience. For example, explain why certain measures are in place and how they contribute to a secure environment. Positively engage guests by providing information on how they can contribute to their safety, such as securing their valuables or being aware of their surroundings, without creating alarm.”
  • “Establishments should design the physical environment to be both secure and inviting. For instance, well-lit public spaces, secure entry points, and landscaped areas can create a safe yet pleasant atmosphere. Ensure that security checkpoints, if necessary, are designed to be comfortable and efficient. Quick and courteous processing at these points helps maintain a positive guest experience. Encourage all team members, not just security personnel, to be part of the safety and security culture. This approach includes training hotel staff to recognize and report suspicious activity discreetly. Leaders should empower staff to act confidently in situations where security may be at risk by providing them with the tools and knowledge needed to manage such situations effectively and calmly.”
  • “Leaders should regularly solicit feedback from guests regarding their perceptions of safety and comfort and use this information to adjust security practices as needed. By regularly reviewing and updating security protocols to ensure they remain effective and guest-friendly. Incorporate best practices and new technologies that enhance both security and guest satisfaction. Provide clear, easily accessible information on emergency procedures in guest rooms and common areas. Make sure guests know what to do in case of an emergency without feeling overwhelmed. During emergencies, provide frequent updates and reassurance to guests, ensuring they feel informed and cared for.”

“By focusing on these strategies, security leaders can create an environment where guests feel safe without compromising the welcoming and comfortable atmosphere that is essential in the hospitality industry,” he adds. “The goal is to integrate security seamlessly into the guest experience, making it an invisible yet effective part of their stay.”

Alexander also highlights some key security challenges specific to the hospitality industry:

  • “Hotels host numerous guests from diverse backgrounds, often with frequent check-ins and check-outs. This constant flux makes it difficult to monitor who is on the premises at any given time and increases the risk of unauthorized access. Hotels typically have multiple entry and exit points, including lobbies, restaurants, and recreational facilities, which are accessible to the public. This open access can be exploited by individuals with malicious intent. Ensuring the privacy and security of guests’ personal information and belongings is critical. This includes safeguarding against data breaches, unauthorized access to rooms and theft of personal items.”
  • “Hosting events, conferences, and large gatherings increases security demands. Hotels must manage crowd control, verify the identity of attendees, and prevent unauthorized access to event spaces. Team members in customer-facing roles, such as front desk staff and housekeeping, are at risk of encountering hostile or aggressive behavior. Establishing protocols for de-escalation and response is essential. Implementing robust security measures and staff training can mitigate these risks. Hotels must also be prepared for various emergencies, including fires, natural disasters, medical emergencies, and security threats. This requires comprehensive emergency plans, regular drills, and coordination with local authorities.”

Within the hospitality industry, security and duty of care are essential to providing a safe, enjoyable and memorable experiences for visitors. Building an effective security strategy and implementing comprehensive measures – such as training and technology – hospitality providers will protect their guests, enhance their reputations and ensure future success.

https://www.securitymagazine.com/articles/100880-securing-hospitality-balancing-guest-experience-and-safety