72% of Americans believe deepfakes may influence upcoming elections

According to a new report by Jumio, there is growing concern among Americans that AI may undermine democratic elections. This study collected the insights of more than 8,000 consumers spread equally across the United States, the United Kingdom, Singapore and Mexico. Key findings from the report include: 

  • 72% of Americans are concerned that AI and deepfake technology may impact upcoming elections in their country. 
  • Americans believe deepfakes undermine confidence in media and politicians, as 70% report increased suspicion in online content compared to the last election.
  • 46% of global consumers are confident they could spot a deepfake of a celebrity or political figure. 
  • Only 37% of Americans are confident they could spot a deepfake of a celebrity or political figure. This percentage drops by age group, as only 22% Americans over the age of 55 believe they could detect a deepfake.
  • 43% of global consumers report trusting political news they find online. Americans are less trusting, with only 32% indicating the same level of confidence. 

https://www.securitymagazine.com/articles/100886-72-of-americans-believe-deepfakes-may-influence-upcoming-elections


Una nuova campagna sfrutta Selenium Grid per il mining di Monero


I ricercatori di Wiz hanno scoperto una nuova campagna in corso che sfrutta i servizi Selenium Grid per effettuare mining di Monero. Soprannominata “SeleniumGreed“, gli attacchi fanno leva su server mal configurati dei servizi per eseguire un cryptominer.

Selenium Grid

Pixabay

Grid è un componente della suite Selenium che offre un API che consente di eseguire e interagire con browser web sulle macchine registrare. Insieme a IDE, Builder e WebDriver permettere di gestire in maniera automatizzata i browser ed è usato principalmente come framework di testing.

I ricercatori spiegano che poiché Grid è pensato solo per l’utilizzo nelle reti aziendali interne, non offre controlli di sicurezza. “Idealmente, questi servizi non dovrebbero mai essere esposti su Internet” scrive il team di Wiz Research. Il componente non ha nemmeno meccanismi di autenticazione: qualsiasi utente con accesso web all’hub di gestione può interagire con le singole macchine registrate, il che comporta un rischio di sicurezza molto elevato se il servizio vien eseguito su una macchina connessa alla rete pubblica e con protezione inadeguata.

Inizialmente gli attaccanti inviano una richiesta all’hub di Grid vulnerabile contenente uno script, il quale a sua volte contiene un payload decodificato in base64. Il payload in questione crea una reverse shell per eseguire ulteriori comandi, tra i quali il download e l’esecuzione del miner.

Il miner è XMRig, un software open-source di cryptomining molto comune tra i cyberattaccanti, che viene fatto eseguire in background. Stando all’analisi dei ricercatori, il gruppo dietro quest’ultima campagna sarebbe attivo da più di un anno.

[embedded content]

Nella documentazione di Grid, Selenium sottolinea l’importanza di non esporre il servizio sul web pubblico a causa dell’assenza di meccanismi di sicurezza, elencando i rischi che ne conseguirebbero, ma evidentemente l’avviso non è stato recepito correttamente da tutte le organizzazioni.

Nella campagna individuata dai ricercatori, gli attaccanti hanno usato una vecchia versione di Selenium (v.3.141.59) per eseguire comandi da remoto, ma il team ha confermato che è possibile eseguire lo stesso attacco anche nelle ultime versioni; per questo è probabile che la campagna si evolva per colpire le release più nuove.

Aggiornare il software in questo caso è inutile: poiché Grid è per sua natura vulnerabile, per proteggersi dagli attacchi è consigliato o rendere le macchine raggiungibili solo da rete interna, oppure implementare controlli di sicurezza mirati per restringere gli accessi e impostare meccanismi di autenticazione robusti.

Condividi l’articolo


Articoli correlati

Altro in questa categoria


https://www.securityinfo.it/2024/07/29/una-nuova-campagna-sfrutta-selenium-grid-per-il-mining-di-monero/?utm_source=rss&utm_medium=rss&utm_campaign=una-nuova-campagna-sfrutta-selenium-grid-per-il-mining-di-monero


Security flaws discovered in a popular web analytics provider

Research from Salt Security unveils a security flaw within the popular web analytics provider, Hotjar. A cross-site scripting (XSS) issue was discovered by researchers, notably when combining it with OAuth technology. OAuth is deployed by a wide range of web services, as it plays a pivotal role in social-login functions. 

Malicious actors can leverage this vulnerability by sending the target a valid link to the service they want to exploit. Since the link is legitimate, the target will have virtually no means to recognize whether or not it is part of a larger attack without a deeper, more technical examination. This link can be sent via email, text message, social media or any other channel. Once the link is clicked, a malicious actor can exert full control over the account, enabling them to gain access to stored data or perform any desired action on the account. 

Hotjar is a tool complementing Google Analytics, collecting large volumes of sensitive data. The data collected includes personally identifiable information (PII), bank details, private messages and possibly credentials. Furthermore, Hotjar services more than one million websites, including major entities like Microsoft. Therefore, the vulnerabilities in Hotjar could allow malicious actors to gain unlimited access to data within these services, potentially impacting millions of users and organizations globally. 

While the research focused on specific entities, the researchers emphasize that the popularity of OAuth and the frequency of XSS issues suggest that this vulnerability is not limited to Hotjar. The research argues that it is likely this issue exists in a variety of web services.

https://www.securitymagazine.com/articles/100885-security-flaws-discovered-in-a-popular-web-analytics-provider


The bad actor’s best friend: Dormant service accounts

Dormant accounts, also known as inactive accounts, are accounts that haven’t been used or updated in at least 90 days. This extended period of inactivity gives them their “dormant” classification. 

Since these accounts are not being actively used, it’s common for application owners not to know they exist. The lack of knowledge can be attributed to the fact that these accounts aren’t being accessed or updated, meaning they don’t appear in system logs or trigger any security alerts. They go unnoticed and essentially become invisible within the system, slipping under the radar. Inactive accounts are a hotbed of opportunity for attackers, even more so if accounts remain dormant for long periods of time. 

An attacker can leverage the inactivity to their advantage, as the account’s lack of use means that any unauthorized activities are less likely to be noticed immediately. This provides a window of opportunity for nefarious activities to go undetected, making dormant accounts a significant security risk an attacker can easily take advantage of.

Risks involved with dormant accounts

A dormant account’s biggest weakness is the age of its password, and because credential reuse (specifically passwords) is a widespread issue, cybercriminals look for these signs to attack. Password reuse is the number one enabler of breaches. This essential security issue can be found across all companies, from the smallest organizations to multi-billion dollar corporations employing some of the brightest minds in the world. 

Let’s consider the tech giant, Microsoft. In January of 2024, Microsoft detected a significant breach within its internal systems. The perpetrators of this breach zeroed in on a non-production administrator account, which was specifically used for testing. By deploying a password spray attack, they were able to crack the account’s weak password. The absence of multi-factor authentication (MFA) on this account provided an unobstructed path for the attacker to log in. 

Once the attacker had infiltrated the system, they had access to a wealth of sensitive information. Emails and valuable data pertaining to high-ranking Microsoft leadership and their cybersecurity and legal teams were now at the attacker’s disposal. 

One month later, in February of 2024, Tangerine, the Australian telecom company, announced that they had suffered a cyberattack, which resulted in the loss of 232,000 customers’ personal data. This data encompassed a wide range of sensitive information, such as names, email addresses, birth dates and account numbers. 

According to Tangerine, the root cause of this devastating breach was a “legacy customer base” accessed by “login credentials of a single user engaged by Tangerine on a contract basis.”

In both of these massive companies, the underlying cause of the breach was the same: dormant accounts with weak passwords.

What can organizations do? 

The first step in protecting dormant accounts is being able to discover them in the organization’s environment. Leveraging a dynamic identity vulnerability solution that discovers and monitors all accounts and their access chains can help reveal dormant accounts in systems that are being improperly managed or used. 

Once they are revealed, organizations should deactivate or delete accounts that do not serve a current business function. Then, they should take the time to establish a strong password policy.

While preventing users from reusing their passwords can be challenging, accounts can be configured to rotate passwords every 90 days or automatically “lock” if they go unused after a certain period of time. 

To further impede attacks like spraying, stuffing and brute force attacks, it is advisable to implement a password complexity requirement, which makes the password less susceptible to guessing. 

Finally, multi-factor authentication (MFA) should be enabled for every account. This will prevent attackers from accessing the account even if they guess (or know) the password. 

Robust security posture requires robust identity security tools 

Dormant accounts remain a significant risk to organizations of all sizes and are low-hanging fruit for attackers, providing an easy, often overlooked entry point. Couple their nature as prime targets with detrimental practices such as password reuse and the non-implementation of MFA, and these accounts become the epicenter of security risks. 

Fortunately, there are identity vulnerability solutions that help to discover all dormant accounts easily and monitor environments for them. These solutions can track password rotation to ensure all accounts are complying with password policies, protecting an organization from an easily avoidable attack.

https://www.securitymagazine.com/articles/100884-the-bad-actors-best-friend-dormant-service-accounts


97% of CrowdStrike systems are back online; Microsoft suggests Windows changes

A bad update to CrowdStrike's Falcon security software crashed millions of Windows PCs last week.
Enlarge / A bad update to CrowdStrike’s Falcon security software crashed millions of Windows PCs last week.
CrowdStrike

CrowdStrike CEO George Kurtz said Thursday that 97 percent of all Windows systems running its Falcon sensor software were back online, a week after an update-related outage to the corporate security software delayed flights and took down emergency response systems, among many other disruptions. The update, which caused Windows PCs to throw the dreaded Blue Screen of Death and reboot, affected about 8.5 million systems by Microsoft’s count, leaving roughly 250,000 that still need to be brought back online.

Microsoft VP John Cable said in a blog post that the company has “engaged over 5,000 support engineers working 24×7” to help clean up the mess created by CrowdStrike’s update and hinted at Windows changes that could help—if they don’t run afoul of regulators, anyway.

“This incident shows clearly that Windows must prioritize change and innovation in the area of end-to-end resilience,” wrote Cable. “These improvements must go hand in hand with ongoing improvements in security and be in close cooperation with our many partners, who also care deeply about the security of the Windows ecosystem.”

Cable pointed to VBS enclaves and Azure Attestation as examples of products that could keep Windows secure without requiring kernel-level access, as most Windows-based security products (including CrowdStrike’s Falcon sensor) do now. But he stopped short of outlining what specific changes might be made to Windows, saying only that Microsoft would continue to “harden our platform, and do even more to improve the resiliency of the Windows ecosystem, working openly and collaboratively with the broad security community.”

When running in kernel mode rather than user mode, security software has full access to a system’s hardware and software, which makes it more powerful and flexible; this also means that a bad update like CrowdStrike’s can cause a lot more problems.

Recent versions of macOS have deprecated third-party kernel extensions for exactly this reason, one explanation for why Macs weren’t taken down by the CrowdStrike update. But past efforts by Microsoft to lock third-party security companies out of the Windows kernel—most recently in the Windows Vista era—have been met with pushback from European Commission regulators. That level of skepticism is warranted, given Microsoft’s past (and continuing) record of using Windows’ market position to push its own products and services. Any present-day attempt to restrict third-party vendors’ access to the Windows kernel would be likely to draw similar scrutiny.

Microsoft has also had plenty of its own security problems to deal with recently, to the point that it has promised to restructure the company to make security more of a focus.

CrowdStrike’s aftermath

CrowdStrike has made its own promises in the wake of the outage, including more thorough testing of updates and a phased-rollout system that could prevent a bad update file from causing quite as much trouble as the one last week did. The company’s initial incident report pointed to a lapse in its testing procedures as the cause of the problem.

Meanwhile, recovery continues. Some systems could be fixed simply by rebooting, though they had to do it as many as 15 times—this could give systems a chance to grab a new update file before they could crash. For the rest, IT admins were left to either restore them from backups or delete the bad update file manually. Microsoft published a bootable tool that could help automate the process of deleting that file, but it still required laying hands on every single affected Windows install, whether on a virtual machine or a physical system.

And not all of CrowdStrike’s remediation solutions have been well-received. The company sent out $10 UberEats promo codes to cover some of its partners’ “next cup of coffee or late night snack,” which occasioned some eye-rolling on social media sites (the code was also briefly unusable because Uber flagged it as fraudulent, according to a CrowdStrike representative). For context, analytics company Parametrix Insurance estimated the cost of the outage to Fortune 500 companies somewhere in the realm of $5.4 billion.

https://arstechnica.com/?p=2039500


At the Olympics, AI is watching you

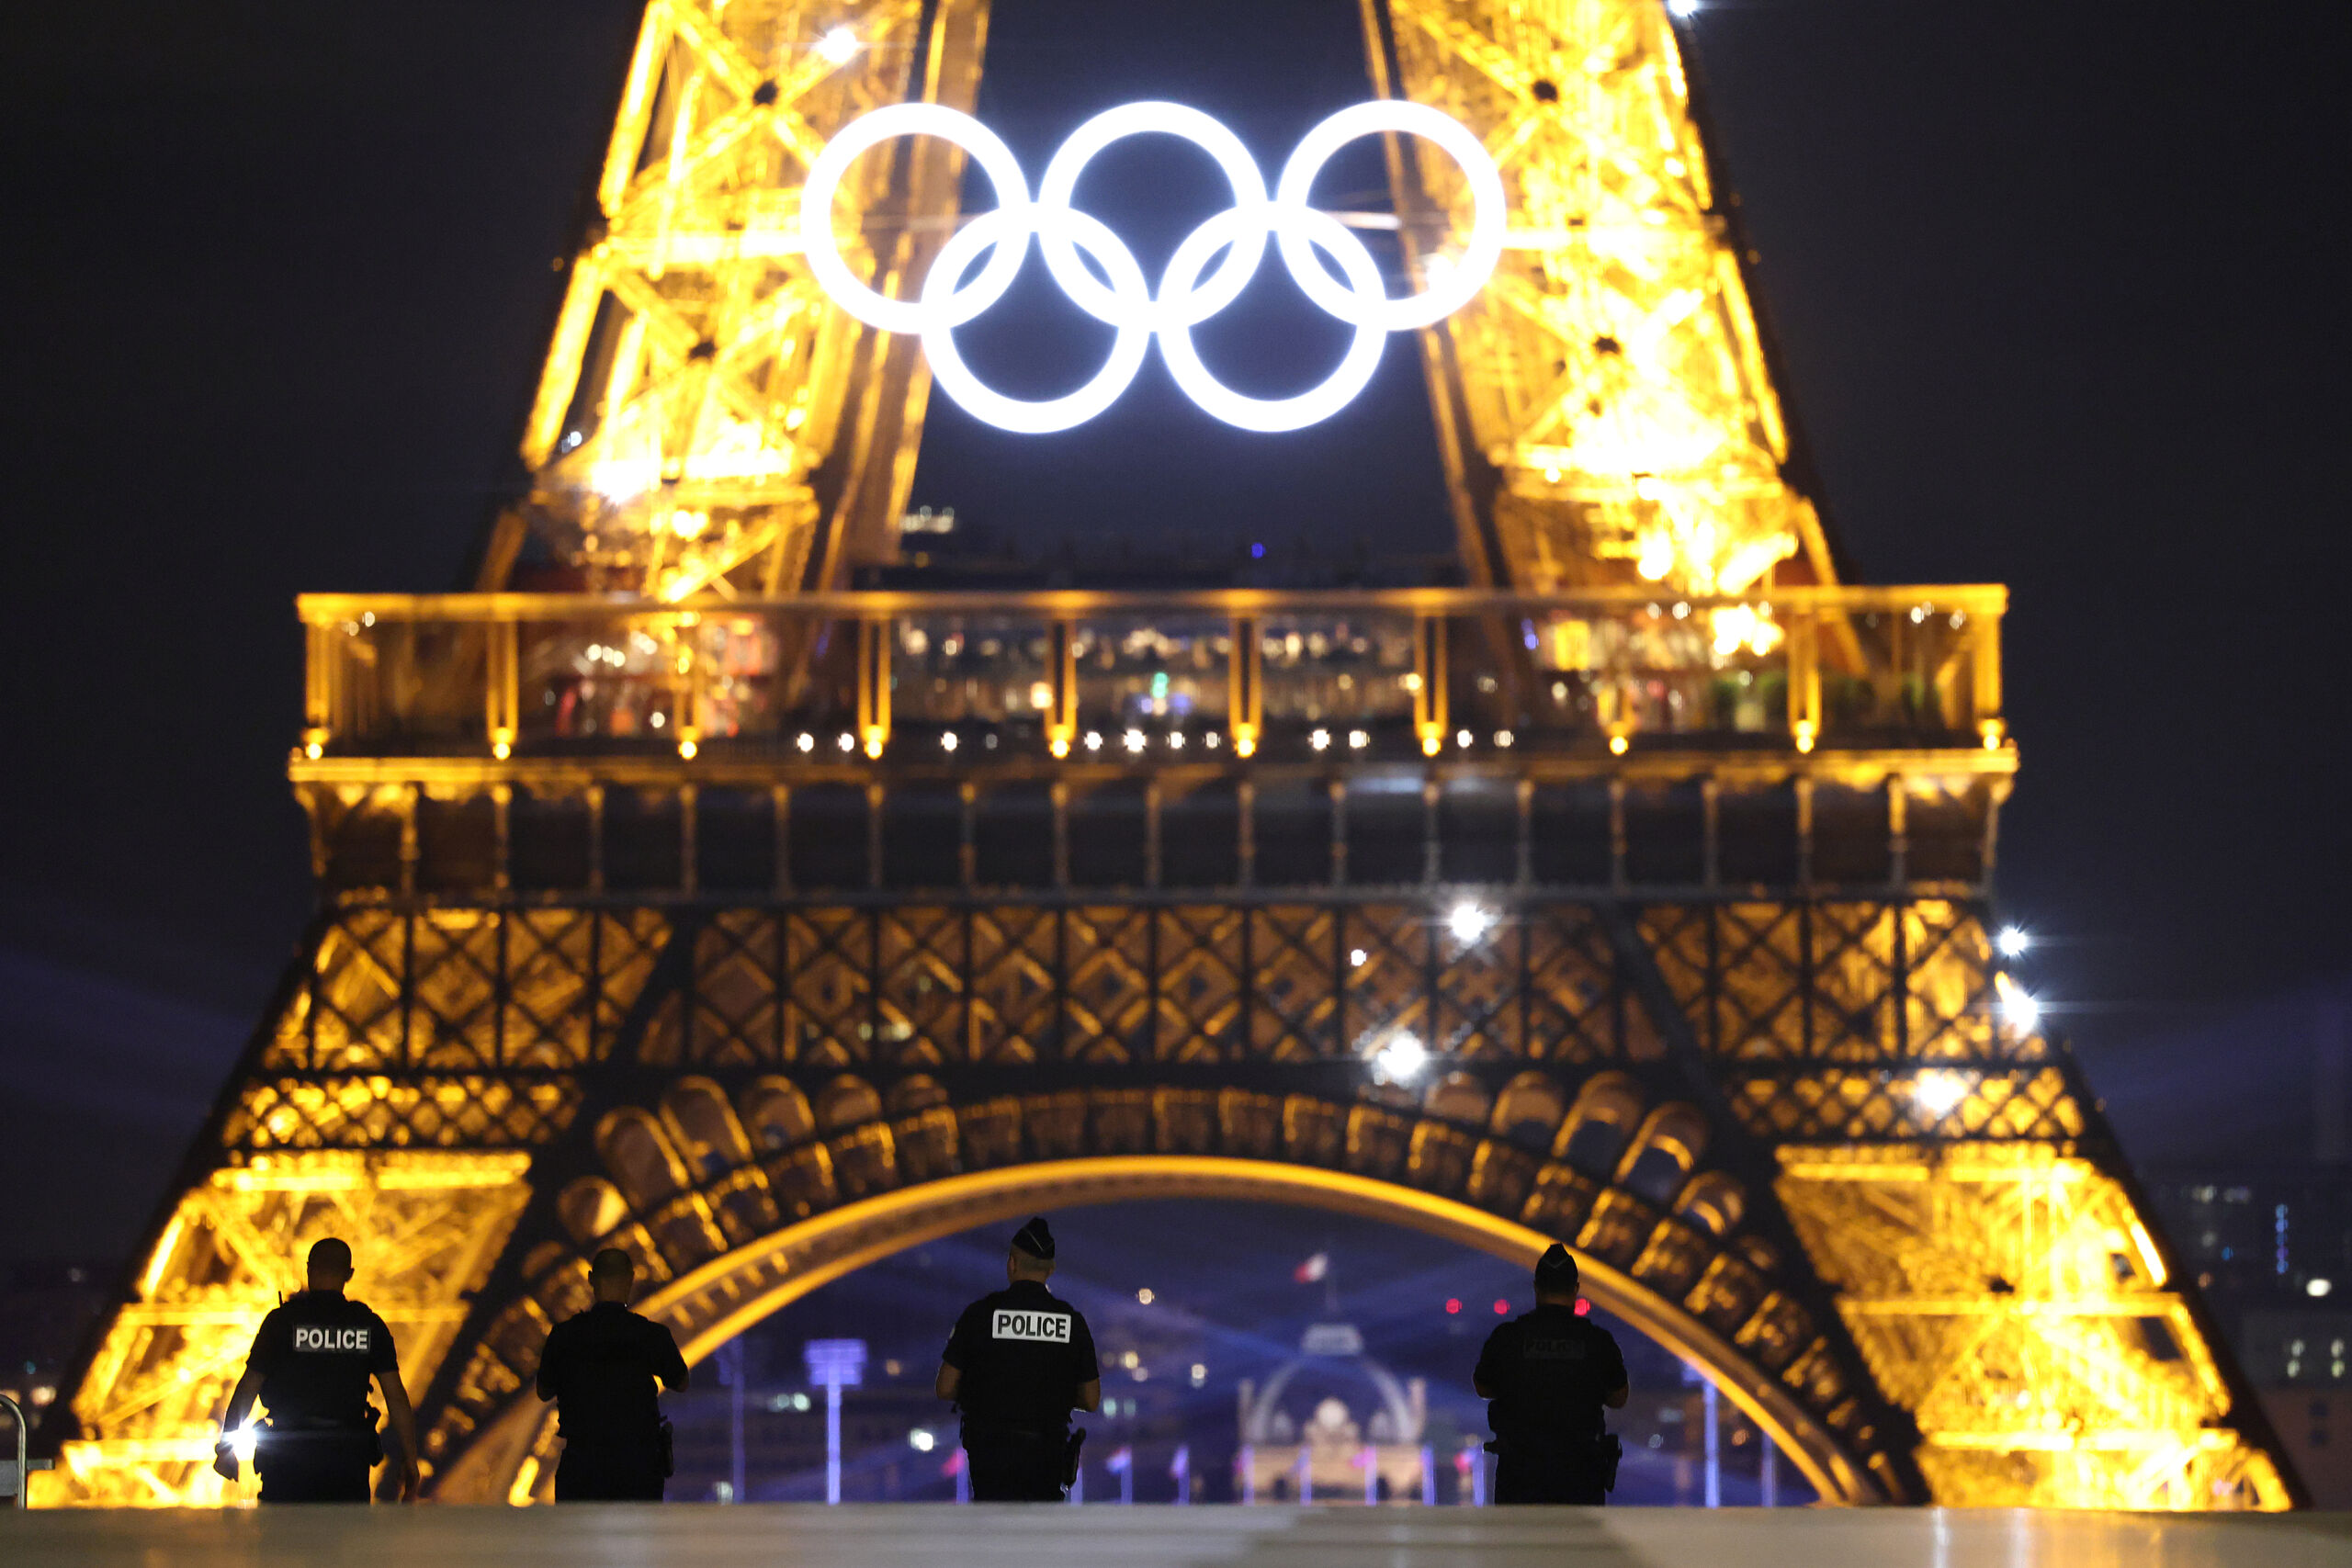
Police observe the Eiffel Tower from Trocadero ahead of the Paris 2024 Olympic Games.
Enlarge / Police observe the Eiffel Tower from Trocadero ahead of the Paris 2024 Olympic Games on July 22, 2024.

On the eve of the Olympics opening ceremony, Paris is a city swamped in security. Forty thousand barriers divide the French capital. Packs of police officers wearing stab vests patrol pretty, cobbled streets. The river Seine is out of bounds to anyone who has not already been vetted and issued a personal QR code. Khaki-clad soldiers, present since the 2015 terrorist attacks, linger near a canal-side boulangerie, wearing berets and clutching large guns to their chests.

French interior minister Gérald Darmanin has spent the past week justifying these measures as vigilance—not overkill. France is facing the “biggest security challenge any country has ever had to organize in a time of peace,” he told reporters on Tuesday. In an interview with weekly newspaper Le Journal du Dimanche, he explained that “potentially dangerous individuals” have been caught applying to work or volunteer at the Olympics, including 257 radical Islamists, 181 members of the far left, and 95 from the far right. Yesterday, he told French news broadcaster BFM that a Russian citizen had been arrested on suspicion of plotting “large scale” acts of “destabilization” during the Games.

Parisians are still grumbling about road closures and bike lanes that abruptly end without warning, while human rights groups are denouncing “unacceptable risks to fundamental rights.” For the Games, this is nothing new. Complaints about dystopian security are almost an Olympics tradition. Previous iterations have been characterized as Lockdown London, Fortress Tokyo, and the “arms race” in Rio. This time, it is the least-visible security measures that have emerged as some of the most controversial. Security measures in Paris have been turbocharged by a new type of AI, as the city enables controversial algorithms to crawl CCTV footage of transport stations looking for threats. The system was first tested in Paris back in March at two Depeche Mode concerts.

For critics and supporters alike, algorithmic oversight of CCTV footage offers a glimpse of the security systems of the future, where there is simply too much surveillance footage for human operators to physically watch. “The software is an extension of the police,” says Noémie Levain, a member of the activist group La Quadrature du Net, which opposes AI surveillance. “It’s the eyes of the police multiplied.”

Near the entrance of the Porte de Pantin metro station, surveillance cameras are bolted to the ceiling, encased in an easily overlooked gray metal box. A small sign is pinned to the wall above the bin, informing anyone willing to stop and read that they are part of a “video surveillance analysis experiment.” The company which runs the Paris metro RATP “is likely” to use “automated analysis in real time” of the CCTV images “in which you can appear,” the sign explains to the oblivious passengers rushing past. The experiment, it says, runs until March 2025.

Porte de Pantin is on the edge of the park La Villette, home to the Olympics’ Park of Nations, where fans can eat or drink in pavilions dedicated to 15 different countries. The Metro stop is also one of 46 train and metro stations where the CCTV algorithms will be deployed during the Olympics, according to an announcement by the Prefecture du Paris, a unit of the interior ministry. City representatives did not reply to WIRED’s questions on whether there are plans to use AI surveillance outside the transport network. Under a March 2023 law, algorithms are allowed to search CCTV footage in real-time for eight “events,” including crowd surges, abnormally large groups of people, abandoned objects, weapons, or a person falling to the ground.

“What we’re doing is transforming CCTV cameras into a powerful monitoring tool,” says Matthias Houllier, cofounder of Wintics, one of four French companies that won contracts to have their algorithms deployed at the Olympics. “With thousands of cameras, it’s impossible for police officers [to react to every camera].”

https://arstechnica.com/?p=2039514


Are deepfake fraud risks overhyped? Where enterprises are exposed

Deepfakes are the hot new enterprise risk. British engineering group Arup lost $25 million recently after scammers used AI deepfakes to falsely pose as the group’s CFO and request transfers from an employee to fraudulent bank accounts. 

But will deepfakes become the number one avenue for fraudsters to steal money? Likely not. There are far more common and pervasive cyber fraud attack methods, specifically business email compromise (BEC) schemes. Data shows that 83% of companies faced an increase in cyber fraud attempts from activity such as BEC attacks, hacking and highly sophisticated phishing schemes. In fact, fraudsters use BEC scams (31%) and hacking (31%) more often than deepfakes (11%) to dupe organizations.

Deepfakes are still a threat and it’s important for corporates to take steps to fight these types of attacks. But don’t get caught up in the hype and overlook BEC schemes as a critical point of entry. Actively bolster organizational defenses now. 

Today’s cyber fraud landscape

Cybersecurity and fraud prevention are now inextricably intertwined. The vast majority of cyberattacks are perpetrated to commit financial crimes such as payment fraud. Ninety-six percent of U.S. companies faced a payment fraud attempt in the past year, a 71% increase from the prior year. 

Once a cybercriminal breaches a company’s internal defenses, they go on the prowl to find weak links where they can steal money. The weak link is often human workers — especially those with access to financials and payments. A recent study found that 31% of employees made errors that could impact the security of their workplace. Falling victim to phishing scams and sharing passwords with colleagues were cited as top mistakes. Finance, treasury and procurement teams have become targets of fraudsters because they hold the purse strings. 

As AI advances, cybercriminals are scaling BEC attacks across thousands of companies simultaneously. AI is also making it significantly easier for fraudsters to write convincing phishing emails that are difficult for even the trained eye to spot as fraud. Social engineering-based BEC attacks have risen by 1,760% in the past year, mostly fueled by the advancements in generative AI. 

The main reason why BEC attacks are a far greater threat comes down to a general comfortability in certain channels of communication. Most professional workers would not share payment details or authorize a transaction on a video conference line. Sharing this sensitive information over email is much more common, making BEC attacks the one to watch for. 

Most organizations have robust firewalls, secure operating systems and intrusion detection systems but BEC attacks bypass these preventative measures through social engineering techniques where employees give up sensitive information over email and enable hackers to infiltrate their systems. These types of attacks can be much harder to spot, control and avoid.

For example, a fraudster may use a sophisticated phishing email to extract important information about a company’s payment process and target employees with access to that sensitive information. They will use an aggressive social engineering email scheme to trick that employee in charge of the payment information into wiring a seemingly real business payment to a fraudulent bank account. 

Most leaders believe their investments in cybersecurity measures are enough, but cybersecurity only goes so far if not backed by strong fraud prevention mechanisms. 

Where enterprises are exposed 

There are several main types of BEC scams where enterprises are exposed.

  • Invoice fraud: These appear to be emails from legitimate suppliers with real invoices, but the bank accounts belong to fraudsters. Thirty percent of U.S. companies faced this type of attack in 2023. 
  • CEO/CFO fraud: Emails from the CEO or senior executives’ accounts will request transfers of funds to fraudulent accounts. This type of attack is the third most common type of fraud. 
  • Hacked accounts: An employee’s email account will request invoice payments from suppliers. Payments are diverted to the scammer’s account.
  • Data theft: Employees in HR and accounts departments are targeted for personally identifiable information (PII) or tax information on employees. This can be used to divert payroll funds. 
  • Law firm information requests: Emails seemingly from a company’s law firm will request confidential information.

Sophisticated BEC attacks are varied and challenging to spot, meaning enterprises should prioritize the following defensive measures in the second half of 2024.

Three steps to protect against BEC attacks 

Companies have three clear steps they can take to fight back against BEC attacks. 

1. Implement two lines of defenses

Data breaches have surged to an all-time high, with over 17 billion records compromised in 2023. Despite significant investment in cyber defenses, it’s not working. Fraud prevention investment is lagging, with only 28% of companies reporting they have fraud prevention tech in place. 

Consider implementing fraud prevention software that will stop fraudsters in their tracks by using automation to confirm that each business payment is going to a legitimate bank account that matches the company they are supposed to be paying. Even if a criminal gets access to a vendor’s email account and requests a payment to a fraudulent bank account, technology can flag the illegitimacy of the bank account before the fraudster steals millions. 

2. Ensure payment data is accurate 

Companies often think that the risk of fraud comes from the payment itself. In fact, the risk comes from the payment data. Large companies work with thousands of vendors. Vendor data is not always accurate or up-to-date. It is estimated that 30% of existing vendor data in financial systems is outdated, whether because a vendor decides to work with a new bank, is acquired by another organization, or another reason. Those changes don’t always get captured in organizations’ vendor databases, which exposes them to fraud.

Preventing fraud requires regularly and actively screening and cleaning vendor data, making sure it’s up to date and then validating the account at the time of payment so organizations are confidently paying the right vendor every time.

3. Enable collaboration across internal teams associated with payments 

Finance, treasury and procurement professionals all share responsibility for fraud prevention. Each plays a different role. But today, most of these teams operate in silos, with little to no communication and visibility around payments. And often, each team thinks the other is primarily responsible for the fight against fraud. 

The moments in between process handoffs can easily be exploited by fraudsters using sophisticated BEC attacks. They could request a change to bank account information right after the finance team takes over, without procurement knowing or being able to confirm whether the change is fraudulent. It’s important to create a culture of collaboration with the teams associated with payments — and enable them with technology that can monitor the potential risks and enable teams to address them before fraud happens. 

Looking forward

Deepfakes are the shiny new toy for fraudsters. As deepfakes enter the cybersecurity and fraud prevention conversation, outsized hype has been placed on their risks. It’s important that leaders do not overlook BEC attacks, as they are a critically vulnerable entry point for fraudsters to swipe millions. 

https://www.securitymagazine.com/articles/100882-are-deepfake-fraud-risks-overhyped-where-enterprises-are-exposed


Il 25% dei Wi-Fi pubblici di Parigi non è sicuro


Parigi è al centro dell’attenzione mondiale per le Olimpiadi: la cerimonia d’apertura è attesa per questa sera alle 19:30, dopo la quale i Giochi Olimpici avranno ufficialmente inizio. Il governo francese ha investito notevolmente sul rafforzamento delle misure di sicurezza per atleti e pubblico, ma a quanto pare non abbastanza, almeno dal punto di vista cyber: secondo gli esperti di Kaspersky, il 25% delle reti Wi-Fi pubbliche di Parigi non è sicuro.

Nel dettaglio, le reti hanno una crittografia debole o del tutto assente; ciò espone gli utenti al rischio di furto di dati personali e bancari. Dal report emerge inoltre che solo il 6% delle reti adotta il più recente protocollo di sicurezza WPA3.

Analizzando 47.891  in luoghi molto frequentati e nelle sedi olimpiche, è emerso che quasi una rete su cinque è configurata con WPS, un algoritmo obsoleto facilmente compromettibile.

“Come gli sportivi che si allenano per l’estate all’insegna dello sport in Francia, anche i criminali informatici si sono preparati ad accogliere in modo sgradevole milioni di persone in direzione di hotel, fan zone ed eventi parigini, in cui potrebbero creare punti di accesso falsi o compromettere le reti legittime per intercettare e manipolare i trasferimenti di dati” ha spiegato Amin Hasbini, Head of META Research Group del GReAT (Global Research and Analysis Team) di Kaspersky. “Le reti Wi-Fi pubbliche e mal configurate sono particolarmente attraenti per i criminali, poiché consentono di rubare password, dati delle carte di credito e altri dati sensibili degli utenti“.

La situazione delle reti Wi-Fi di Parigi deve sensibilizzare gli utenti nell’usare in maniera sicura le reti pubbliche. Gli esperti di Kaspersky consigliano di usare una VPN per avere un ulteriore livello di sicurezza, sfruttando la cifrature delle connessioni e il mascheramento dell’indirizzo IP.

Occorre inoltre evitare le transazioni sensibili quando si è collegati al Wi-Fi pubblico, verificare la legittimità della rete, attivare il firewall e disattivare la condivisione dei file. In generale, si ricorda di usare password efficaci e robuste ed eseguire regolarmente gli aggiornamenti dei software in uso.

Condividi l’articolo


Articoli correlati

Altro in questa categoria


https://www.securityinfo.it/2024/07/26/il-25-dei-wi-fi-pubblici-di-parigi-non-e-sicuro/?utm_source=rss&utm_medium=rss&utm_campaign=il-25-dei-wi-fi-pubblici-di-parigi-non-e-sicuro


Starting a job in tech? Read this advice to maximize your experience

It’s that time of the year. New graduates have just begun to enter the workforce, re-fueling a cybersecurity industry that desperately needs talent around the world. Right now, the shortage sits at just under four million unfilled cybersecurity jobs globally, with the gap rising year-over-year, according to the nonprofit ISC2. 

It is imperative that the industry do all it can to retain new graduates who are entering the industry, but there are steps that grads can take to make the transition from school into a Security Operations Center as smooth as possible. Cybersecurity is a fast-paced environment in which the circumstances can change on a dime, or at least as fast as the adversary can execute, innovate and adapt. With constant change, I have found it incredibly beneficial to identify and internalize, a mission-driven approach to work.

Let me explain. As a new graduate, your responsibilities may afford you a bit of extra time, and your scope of work might be narrow until you gather the ‘lay of the land’ at your company. But taking ownership of those limited options by being curious and asking questions, building relationships by engaging with your colleagues, and getting a bit uncomfortable by taking on tasks that you may not be perfectly ready to say ‘yes’ to in your role will fuel your professional growth faster than anything else. 

As a junior employee, taking the initiative to understand how different teams and departments at your organization function alongside each other, offering insight where you can and over-communicating with your colleagues will show that you are ready to grow while immersing yourself in the company. It will help your colleagues and managers build trust in you that they might otherwise reserve for more senior employees and jumpstart your career right out of the gate. Do not underestimate the value of learning the company culture. Get involved in clubs or programs that you are passionate about.   

It is also important to remember that not everyone lands their perfect role in the perfect part of the organization immediately after graduation. Just because you may have accepted or are applying for roles because they are interesting, this does not equate to immediate long-term success. I was always interested in math, for example, but a professor encouraged me to pivot myself to computer science. It was considered a more practical field than mathematics when I realized teaching was not what I was interested in as a career. In my case, the first part of my CS internship did not enthuse me at all before I discovered network and security. Even when I did develop a passion for security, it took several separate roles to figure out what I wanted to specialize in, from compliance, incident management, to security operations center management.

The bottom line is that career trajectories are rarely ever linear, and many people learn more about what they don’t like before finding something they do like. While on this journey myself, I received great advice and mentorship from the people I met along the way: my first internship role, colleagues over the years, at conferences, networking events and meetups; connecting both in-person and online to share stories and best practices in the cybersecurity world through to career advancement. The first few months of a new role are the best time you will ever have to soak up the wisdom of your colleagues, and to take it all in. This is the best time to build relationships, get involved with the company culture, learn to interact with new teammates, find passion in the industry, and meet interesting people who are willing to impart their knowledge with eager, tenacious new graduates. There is only one time in your life that you will be a new grad entering the workforce. Plunge into the experience and enjoy the journey. 

https://www.securitymagazine.com/blogs/14-security-blog/post/100881-starting-a-job-in-tech-read-this-advice-to-maximize-your-experience


Il Ruolo dei Big Data nell’Evoluzione del Commercio Elettronico

I Big Data stanno cambiando le regole del commercio online. Finalmente le aziende possono comprendere davvero i propri clienti, grazie a insight ottenuti dall’analisi di terabyte di informazioni.

In questo articolo mostreremo come i leader di mercato stiano sfruttando appieno il loro potenziale, per vendere di più sì, ma anche per proporre nuove esperienze. Scopriremo come la segmentazione permetta promozioni su misura, capaci di intercettare con precisione i reali bisogni dei consumatori. Non soltanto marketing, anche logistica e supply chain guadagnano in efficienza grazie alle previsioni abilitate dall’AI.

Uno sguardo al presente e al futuro di un settore in evoluzione, guidato dalla rivoluzione data-driven ancora in corso.

La rilevanza dei Big Data nel commercio elettronico

L’adozione dei Big Data nel commercio elettronico ha trasformato il modo in cui le aziende comprendono e interagiscono con i loro clienti. I dati provengono da una varietà di fonti, tra cui transazioni online, interazioni sui social media, recensioni dei clienti e dati di navigazione web. Analizzandoli, le aziende possono identificare tendenze e modelli di comportamento, così da anticipare le esigenze dei consumatori e personalizzare le offerte in modo più accurato.

L’analisi dei Big Data dà modo di segmentare il mercato in maniera molto dettagliata, e identificare di conseguenza gruppi specifici di consumatori con caratteristiche e comportamenti simili. Tale segmentazione rende possibile alle aziende creare campagne di marketing altamente personalizzate. Il risultato? L’aumento dell’efficacia delle strategie di vendita e una migliore esperienza complessiva del cliente.

Come i Big Data migliorano la comprensione dei comportamenti dei consumatori

Uno dei principali vantaggi dei Big Data è la loro capacità di fornire una visione dettagliata e in tempo reale dei comportamenti dei consumatori. Le aziende possono monitorare le attività dei clienti sui loro siti web, analizzare le preferenze di acquisto e identificare i prodotti più popolari. Una conoscenza talmente approfondita da permettere di prevedere le tendenze future e adattare rapidamente le strategie di vendita alle mutevoli esigenze del mercato.

I Big Data danno anche la possibilità di comprendere meglio le dinamiche di acquisto dei consumatori, come ad esempio il processo decisionale che porta all’acquisto di un prodotto. Analizzando i dati sulle interazioni dei clienti con il sito web, si possono identificare i punti di forza e di debolezza del percorso di acquisto e apportare miglioramenti per rendere l’esperienza di acquisto più fluida e intuitiva.

L’Intelligenza Artificiale e la trasformazione dei Big Data in insight

Quando si parla di trasformazione dei Big Data in insight utili per il business, non si può prescindere dal menzionare l’intelligenza artificiale (AI). I servizi di intelligenza artificiale sono infatti in grado di analizzare enormi volumi di dati in modo rapido e preciso, identificando modelli complessi e fornendo raccomandazioni basate su dati concreti. Un simile processo consente alle aziende di prendere decisioni ponderate e sviluppare strategie di vendita più efficaci.

Ad esempio, l’AI può essere utilizzata per identificare i prodotti che potrebbero essere di interesse per specifici segmenti di mercato e ottimizzare le campagne di marketing. Oppure, può aiutare a migliorare la gestione dell’inventario, prevedendo la domanda futura e ottimizzando i livelli di stock per evitare sia eccessi che carenze di prodotti.

Per sfruttare appieno il potenziale dell’AI serve una strategia a prova di futuro. Il processo di adozione inizia con l’esplorazione delle tecnologie disponibili e la loro applicazione specifica nel contesto aziendale, seguito dall’evoluzione dei processi in ottica AI, fino alla misurazione dei risultati e dell’impatto dell’iniziativa. Per realizzare tutto ciò, le organizzazioni devono adottare soluzioni AI per aziende come quelle proposte da NTT DATA, per rimanere competitive e cogliere appieno le opportunità offerte dall’intelligenza artificiale.

Ottimizzazione delle strategie di vendita attraverso i Big Data

L’ottimizzazione delle strategie di vendita è uno degli obiettivi principali dell’utilizzo dei Big Data nel commercio elettronico. Le aziende possono utilizzare i dati per personalizzare le offerte, migliorare la customer experience e incrementare le vendite. Ad esempio, l’analisi dei dati di acquisto può rivelare quali prodotti sono più popolari tra determinati gruppi di consumatori, e sviluppare di conseguenza promozioni mirate.

I Big Data vengono utilizzati anche per migliorare le campagne di marketing, identificare i canali più efficaci per raggiungere i clienti e ottimizzare i messaggi pubblicitari: l’analisi dei dati sulle interazioni dei clienti con le campagne di marketing consente di valutare l’efficacia delle diverse strategie e di apportare modifiche in tempo reale per massimizzare i risultati.

L’uso dei Big Data e dell’intelligenza artificiale nel commercio elettronico può trasformare il modo in cui le aziende operano, viste le nuove opportunità per comprendere meglio i consumatori e ottimizzare le strategie di vendita.

Condividi sui Social Network:

https://www.ictsecuritymagazine.com/notizie/il-ruolo-dei-big-data-nellevoluzione-del-commercio-elettronico/