How organizations can save CISOs amidst increasing federal regulations

In an effort to bolster data security and privacy practices amidst increasing cyberattacks, new data breach reporting rules enforced by the Federal Trade Commission (FTC) and Securities and Exchange Commission (SEC) have taken effect for various organizations and financial institutions. Since May 13, 2024, non-banking financial institutions (including mortgage brokers, payday lenders and tax preparation firms) must report data breaches to the FTC within 30 days of discovery. This new mandate, which is part of the FTC’s Safeguards Rule, expands the breach notification requirements to a broader range of financial entities not overseen by the SEC. Furthermore, companies with a public float under $250 million or annual revenues under $100 million were required to comply with the SEC’s new cybersecurity incident reporting rules by June 15 — aligning their disclosure obligations with those of larger corporations.

While these rulings mark a significant step towards enhancing transparency and accountability in data breach reporting, they squarely put CISOs in the hot seat, compounding the challenges they’re already facing to protect their organization. Burdened by being held solely responsible for breaches while facing new cyber threats, shrinking budgets and a growing skills gap, our security leaders are in desperate need of a lifeline. How can an organization save its CISO? It starts with these four key strategies.

1. Encourage collaboration and shared responsibility

First is creating an environment of shared responsibility by holding executive leaders accountable for protecting against security risks. While CISOs do have a responsibility to protect customer data and ensure continuity of operations, these new regulations are making CISOs feel like scapegoats. Not only do they have their reputation at stake, but now they have to think about monetary fines and jail time. To address this, organizations must establish policies that hold other executive leaders accountable for following cybersecurity practices and incident response measures. This approach fosters a culture of shared responsibility across the organization, ensuring that business risk isn’t resting entirely on the CISO’s shoulders. Additionally, organizations must promote industry cooperation through Information Sharing and Analysis Centers (ISACs) and shared intelligence, and common frameworks to ensure positive outcomes over sophisticated adversaries weaponizing advancing technologies like AI.

2. The importance of balance

Gartner reports regulatory pressure and attack surface expansion will result in almost half of a CISO’s responsibilities expanding beyond cybersecurity by 2027. This is a clear indication that CISOs need a better balance so they have time to focus on the most pressing matters. Effective cross-department collaboration helps teams outside of security understand and enforce standardized processes for safeguarding data. This approach enables early detection and proactive risk management, reducing the frequency and severity of incidents that require the CISO’s direct intervention. As a result of deploying data-centric security tools in tandem with cross-department collaboration, CISOs can concentrate on strategic priorities instead of constant oversight.

3. Determine budget allocation for cybersecurity

Third, when cybersecurity budgets are in question and teams are faced with doing more with less manpower, financial decision-makers need to communicate with CISOs to understand the ROI of a proactive cybersecurity posture that can protect the company when — not if — a breach occurs. Establishing a budget allocation for cybersecurity ensures security teams have enough financial resources to invest in and maintain the most effective security tools and measures. To maximize resources during a shortage, CISOs must advocate for prioritizing investing in data-centric security solutions; this is critical in today’s multi-cloud world as they provide a more granular and effective way to protect data as traditional boundary controls become less relevant. 

By implementing tools that focus on securing the data itself, CISOs can confidently execute consistent, scalable and regulatory-compliant protection across diverse and distributed environments. These tools also help identify and monitor sensitive data across the cloud and on-premises, aligning with regulatory compliance and ensuring proper policy enforcement. Moreover, company decision-makers must pair tool adoption with broader organizational strategies to alleviate the pressure associated with increased scrutiny and complex disclosure requirements. In addition, technology like AI can automate repetitive manual tasks such as data scanning and classification, streamlining workloads. 

4. Awareness and education are key

Lastly, instilling a cybersecurity mindset across the organization through awareness training can reduce CISOs’ concerns about internal risks such as human error-related breaches. Establishing clear internal incident response practices ensures that all staff members know how to react quickly and efficiently in case of a security incident, minimizing impact and potential damage. This proactive approach not only minimizes pressure for CISOs by preventing avoidable security lapses but also establishes the organization’s holistic security posture and a culture of cybersecurity.

We must continue to call on policymakers to create legislation and frameworks that can help address, and more importantly, support the challenges CISOs face without adding complexity to their role. In the meantime, organizations can use these four steps to help CISOs fall back in love with being security leaders. 

https://www.securitymagazine.com/articles/100877-how-organizations-can-save-cisos-amidst-increasing-federal-regulations


Scoperto EvilVideo, una vulnerabilità zero-day di Telegram per Android


I ricercatori di ESET hanno scoperto EvilVideo, una vulnerabilità zero-day che colpisce le versioni di Telegram per Android. Sfruttando il bug, gli attaccanti possono condividere payload malevoli su canali, gruppi e chat Telegram mascherandoli come file multimediali.

La particolarità dell’exploit è che gli attaccanti possono creare payload specifici sfruttando l’API di Telegram; ciò gli consente di inviare il payload malevolo e farlo apparire come una preview multimediale, non come un file binario allegato. Nell’esempio condiviso dai ricercatori, il payload, una volta condiviso in chat, viene visualizzato come un breve video.

EvilVideo exploit- Credits: ESET

Credits: ESET

Di default, tutti i media ricevuti su Telegram vendono scaricati immediatamente, quindi gli utenti che hanno ancora abilitata questa opzione scaricheranno automaticamente il payload non appena aprono la chat.

Se la vittima cerca di aprire il video, Telegram mostra un messaggio di errore specificando che non riesce a leggerlo e propone all’utente di utilizzare un’applicazione esterna. Se poi l’utente procede, gli verrà chiesto di installare un’applicazione (malevola) per visualizzare il video; installando l’app, il malware distribuito dall’attaccante viene eseguito sul dispositivo colpito.

I ricercatori hanno confermato che l’exploit funziona solo su Android: nel caso di Telegram Web e del client Desktop, il file malevolo è stato scaricato non come .apk ma come file .mp4, il che ha bloccato l’esecuzione del malware.

Al momento non è chiaro chi sia l’attaccante o gli attaccanti dietro l’exploit di EvilVideo. Lo stesso cybercriminale (o gruppo) sta vendendo anche un cryptor-as-a-service per Android che viene presentato come “Fully Undetectable” (FUD), ovvero che non può essere individuato da antivirus e prodotti di sicurezza.

Il team di ESET ha scoperto l’exploit in vendita su un forum del dark web il 6 giugno scorso e ha segnalato la vulnerabilità a Telegram il 26 giugno; l’11 luglio, la compagnia ha rilasciato un aggiornamento che risolve il bug (versioni 10.14.5 e superiori). Il consiglio è di aggiornare il prima possibile l’applicazione.

Condividi l’articolo


Articoli correlati

Altro in questa categoria


https://www.securityinfo.it/2024/07/25/scoperto-evilvideo-una-vulnerabilita-zero-day-di-telegram-per-android/?utm_source=rss&utm_medium=rss&utm_campaign=scoperto-evilvideo-una-vulnerabilita-zero-day-di-telegram-per-android


Creating a safer workplace: California Senate Bill 553 becomes law

California’s Senate Bill 553 (SB 553) mandates that nearly all employers in the state establish written workplace violence prevention plans by July 1, 2024. This law amends California’s labor and civil procedure codes, requiring most organizations to create prevention plans and employee training programs. Exceptions are made for employers already covered by healthcare standards and small, non-public businesses with fewer than ten employees. The law will be enforced by Cal/OSHA, though the specifics of enforcement and the definition of “effective” measures remain unclear.

SB 553, driven by a 2021 workplace shooting and increased violence during the COVID-19 pandemic, is one of the most comprehensive workplace violence prevention laws. It requires plans to address four types of workplace violence:

  1. Criminal intent: Violence by individuals with no legitimate business at the workplace.
  2. Customer/client: Violence by customers, clients, patients, students, inmates or visitors.
  3. Worker-on-worker: Violence by current or former employees, supervisors or managers.
  4. Personal relationships: Violence by individuals with personal relationships with employees.

Employers must log violent incidents, train employees and regularly review and update their plans. Required elements of the plans include:

  • Identifying responsible individuals for implementing the plan.
  • Procedures for employee involvement in hazard reporting and communication.
  • Responses to workplace violence emergencies and post-incident investigations.
  • Annual review and necessary revisions of the plans.

Training must be customized to reflect the specific workplace violence plan, covering reporting procedures, corrective measures and harm avoidance strategies. Detailed logs of violent incidents must be maintained for five years. The law also allows employers and collective bargaining representatives to obtain temporary restraining orders on behalf of employees, expanding protection to those facing harassment.

Key concerns

  1. Enforcement uncertainty: There is ambiguity about how Cal/OSHA will enforce the law, particularly what constitutes “effective” measures. Businesses are unsure what will be deemed sufficient, which could lead to inconsistent compliance and potential penalties.
  2. Burden on small businesses: Small businesses may struggle to meet the law’s requirements due to limited resources and staff. Creating, implementing and maintaining a comprehensive prevention plan and training program could be particularly challenging.
  3. Exemption ambiguities: The criteria for exemptions are not entirely clear. For instance, what qualifies as “no public access” to an office with fewer than ten employees is open to interpretation. Cal/OSHA has the authority to reassess exemptions, adding to the uncertainty.
  4. Contractor and third-party responsibilities: The law does not clearly define the responsibilities regarding contractors and other third parties. Businesses need clarity on whether these individuals must be trained under their violence prevention plans.

Opportunities

  1. Enhanced workplace safety: SB 553 aims to create safer work environments across various industries by mandating comprehensive violence prevention plans, potentially reducing incidents of workplace violence.
  2. Proactive incident management: By requiring detailed logs and regular training, employers can better manage and mitigate workplace violence risks, leading to a more prepared and responsive workforce.
  3. Legal and regulatory compliance: Developing robust workplace violence prevention plans can help businesses comply with the law and avoid steep fines for violations, which can range up to $159,000 for willful and repeat offenses.
  4. Template plans and resources: California’s Department of Industrial Relations has developed a model workplace violence prevention plan as a starting point for employers, which can be customized to meet specific workplace needs.

Employers across the United States should monitor the continued rollout of SB 553, as similar legislation is being considered in other states. The law, while challenging to implement, represents a significant step towards comprehensively addressing workplace violence. Businesses are encouraged to make good faith efforts in compliance while awaiting further guidance from Cal/OSHA to clarify the law’s ambiguous aspects.

From a security professional’s perspective, SB 553 will ultimately help security practitioners lobby for larger budgets, as much of the responsibility for compliance will fall on the security department. While legal/compliance, human resources and business continuity departments will be involved, the Chief Security Officer (CSO) in large organizations will play a critical role in the implementation and management of the workplace violence prevention plan.

https://www.securitymagazine.com/articles/100876-creating-a-safer-workplace-california-senate-bill-553-becomes-law


Digital forensics e cyber security: caso Cellebrite Ufed vs Signal

Dal punto di vista tecnico-operativo, le indagini di digital forensics vengono svolte utilizzando specifici strumenti hardware e software[1] che, una volta collegati al sistema informatico da acquisire, ne esplorano le aree di memoria e ne producono una copia[2] – nella quale vengono ricompresi lo spazio non allocato e le parti di file cancellati ma non definitivamente eliminati – che successivamente viene esfiltrata verso un file di backup appositamente creato sul dispositivo hardware usato per l’acquisizione e dove viene, quindi, dislocata la copia forense del sistema sotto indagine. Concluse le operazioni di acquisizione, il clone informatico viene poi analizzato mediante programmi di analisi che permettono di prendere visione del contenuto digitale in esame. In particolare, questi software hanno il compito di scandagliare a fondo tutti i singoli file che sono presenti nella copia forense, visionandone tutte le parti, metadati inclusi, verificando che non vi siano contenuti occultati e nel caso procedendo ad analisi dei medesimi[3].

È ovvio che più il programma di analisi è moderno e aggiornato più sarà in grado di scovare file nascosti e di conseguenza maggiore sarà la resa in termini di risultato finale.

Qualora, invece, i file siano protetti da password, occorrerà procedere allo sblocco del loro contenuto mediante attacchi brute force volti all’individuazione della chiave che custodisce i dati[4].

In estrema sintesi e senza tecnicismi, l’attività di individuazione della digital evidence è suddivisibile in due fasi: la prima è quella di acquisizione in copia forense della memoria del dispositivo, mentre la seconda prevede l’analisi della copia estratta, fase nella quale, più precisamente, vengono rintracciate e identificate le evidenze digitali stoccate in memoria che si sospettavano poter essere presenti sul dispositivo al momento del sequestro.

Per entrambe le fasi, in situazioni particolari, possono profilarsi problemi di sicurezza informatica. Durante tali momenti, ad esempio, delle criticità potrebbero insorgere qualora il dispositivo da acquisire e analizzare sia infetto da un virus informatico. Clonando la memoria inevitabilmente verrebbe clonato anche il programma malevolo, che per conseguenza si estenderebbe alla copia forense.

Ora, se l’infezione sul dispositivo originario fosse nota, il problema in realtà non si porrebbe. In tal caso, infatti, l’ostacolo potrebbe essere facilmente aggirato acquisendo più copie del dispositivo e quindi procedendo alla disinfezione del virus da una di esse, per poi confrontarla con le altre per valutare se l’operazione di eliminazione del malware abbia comportato la compromissione di dati oppure abbia mantenuto inalterate le informazioni[5].

Il problema emerge quando il virus informatico passa inosservato all’occhio dei software adoperati per le operazioni forensi. Si consideri sul punto che, al pari degli altri programmi informatici, anche gli strumenti adoperati per la digital forensics possono avere delle vulnerabilità nella sicurezza, soprattutto quando il sistema non viene regolarmente aggiornato. In linea teorica, pertanto, potrebbe capitare che un malware sfugga al controllo e continui a svolgere indisturbato il compito per il quale è stato progettato.

In particolare, esistono alcuni tipi di malware che una volta sottoposti all’azione dei programmi di analisi sono in grado di corromperne l’algoritmo e alterarne il funzionamento per far commettere al software operazioni per le quali originariamente non era settato o che non era stato autorizzato a svolgere. È superfluo specificare che in simili evenienze l’attendibilità delle risultanze ottenute con l’analisi forense sarebbe del tutto assente.

Ad ogni modo, vulnerabilità di questo tipo non colpirebbero la genuinità del procedimento di formazione della copia forense, ma esclusivamente il successivo passaggio di analisi, compromettendo quindi non l’acquisizione in sé (consistente in una mera copiatura dei byte della memoria originale senza attività di elaborazione) ma solo i sistemi di analisi e in conseguenza l’analisi che ne scaturisce[6].

Un recente caso di cronaca, andato alla ribalta delle testate giornalistiche che si occupano di cybersicurezza, ha messo in chiaro come quanto appena descritto non sia solo un’ipotesi di scuola, bensì potrebbe realmente accadere, o meglio, sarebbe già accaduto. Il caso riguarda lo scambio di battute avutosi tra fine 2020 e prima metà del 2021 tra la nota app di messaggistica Signal e l’azienda israeliana produttrice di strumenti di informatica forense – tra le più affermate sul mercato – Cellebrite Ufed.

La disputa aveva origine allorché l’azienda israeliana comunicava pubblicamente di aver trovato il modo per violare le difese dell’applicazione di messaggistica – come noto tra le più sicure e tra le più improntate alla garanzia della privacy degli utenti – affermando di esserne persino riuscita decifrare i contenuti delle chat e i relativi allegati. Successivamente, sebbene l’azienda, sul presupposto delle polemiche che stavano emergendo, avesse tentato di ridimensionare la portata sensazionalistica della comunicazione originale, si scatenava ugualmente la reazione di Signal.

Per tutta risposta infatti quest’ultima, a mezzo di un articolo pubblicato pochi mesi dopo dal proprio amministratore delegato[7], nello sminuire ulteriormente la notizia dell’hackeraggio[8] controbatteva insinuando di essere stata a sua volta in grado di individuare alcune vulnerabilità presenti sul software di analisi Physical Analyzer, sviluppato e distribuito sul mercato dalla società israeliana.

In pratica, secondo l’amministratore delegato di Signal, il software della Cellebrite dopo il lancio nel 2012 non sarebbe più stato implementato con i necessari aggiornamenti, sicché avrebbe presentato diverse falle nel proprio sistema di sicurezza. Sfruttando queste mancanze sarebbe stato possibile eseguire sul software dei codici capaci di modificare sia i report di Cellebrite relativi all’attacco sia quelli precedenti e futuri, creati a partire da dispositivi acquisiti in precedenza. Inoltre, sarebbe stato possibile attuare modifiche rilevanti nel contenuto analizzato: inserire o rimuovere parti testuali, messaggi di posta elettronica, immagini, contatti, file e qualunque tipo di dato, il tutto sfuggendo completamente ai controlli dei checksum. Nei casi peggiori, come riporta sempre Signal, un attacco simile avrebbe addirittura potuto causare la fuoriuscita dei dati presenti sul dispositivo analizzato, il tutto con ovvia ripercussione sull’attendibilità dell’analisi stessa[9].

Il caso appena esaminato rende evidente le maggiori criticità di cybersecurity che possono inficiare la funzionalità degli strumenti per le analisi forensi. Il rischio è che malware capaci di agire nei termini su visti possano presto divenire una realtà largamente diffusa.

Secondo gli esperti, tuttavia, si potrebbe ricorrere ad alcune contromisure. In particolare, per ovviare alle problematiche di file illeciti di questo genere una soluzione potrebbe essere quella di rivolgere lo sguardo agli strumenti di machine learning; ovvero a algoritmi che facendo ricorso a logiche matematiche e di elaborazioni computazionale sono in grado di apprendere informazioni direttamente dai dati che gli vengono sottoposti, senza che abbiano ricevuto in precedenza delle istruzioni specifiche. Una volta “addestrati” questi algoritmi sono in grado di adattarsi a situazioni nuove e potenzialmente, in chiave predittiva, a riconoscere programmi che si comportano in maniera difforme dalla normalità, potendo quindi teoricamente scoprire file malevoli che si camuffano da altri programmi.

L’applicazione delle logiche del machine learning alla digital forensics[10], in fase di esame della copia forense, potrebbe quindi aiutare il programma di analisi a individuare possibili programmi malevoli e catalogarli come file sospetti.

Su un piano più tecnico gli algoritmi di machine learning, operando una verifica dei metadati dei programmi presenti sulla copia, sarebbero in grado di comprendere se un file possa essere potenzialmente dannoso mediante un confronto con i metadati di programmi già noti al sistema o dal medesimo già considerati sospetti[11].
Di certo l’applicazione degli algoritmi di machine learning non può costituire l’unica soluzione. Una buona strategia difensiva non può prescindere, ad esempio, dal costante aggiornamento del sistema e dalla applicazione delle altre comuni buone pratiche e accorgimenti che costituiscono i principi fondanti della sicurezza informatica.

Questo articolo è stato estratto dal white paper “La Digital forensics nel processo penale” disponibile in maniera libera e gratuita al seguente link: https://www.ictsecuritymagazine.com/pubblicazioni/digital-forensics-nel-processo-penale/

Note

[1] Per un approfondimento delle diverse tipologie di software che vengono utilizzati nelle operazioni di informatica forense e sul funzionamento degli stessi si rimanda a M. VITIELLO, “Il laboratorio di informatica forense: i software, gli strumenti hardware, i costi” consultabile sul sito https://www.agendadigitale.eu/documenti/il-laboratorio-di-informatica-forense-i-software-gli-strumenti-hardware-i-costi/#:~:text=Ad%20esempio%20Magnet%20Axiom%20%C3%A8,maggior%20numero%20di%20evidenze%20possibili.

[2] Si rammenta che per impedire che i dati da acquisire vengano corrotti dallo strumento di acquisizione medesimo è necessario che questo abbia la funzione di blocco di scrittura (write blocking).

[3] Per recuperare file cancellati oppure danneggiati vengono impiegati appositi strumenti di file recovery che servono proprio a ripristinare contenuti parziali.

[4] L’attacco di brute force «consiste nel provare tutte le possibili combinazioni di lettere, caratteri speciali e numeri finché non individua la mescolanza giusta. Un’operazione che viene, ovviamente, eseguita da un software. Il tempo di riuscita dell’impresa dipende dalla velocità di calcolo del computer, nonché dalla complessità e la lunghezza della password (quanti e quali caratteri sono stati utilizzati)». La definizione è tratta da R. RIJITANO, “Brute force: cosa sono, come fare e prevenire gli attacchi a forza bruta”, consultabile sul sito https://www.cybersecurity360.it/nuove-minacce/brute-force-cosa-sono-gli-attacchi-a-forza-bruta-come-farli-e-prevenirli/.

[5] Ovviamente, in ogni caso, in sede processuale bisognerà capire se e in che modo il programma malevolo possa aver corrotto le informazioni sulla copia originale prima che venisse rilevato.

[6] Quanto finora riferito e la disamina che segue trae le mosse da P. DAL CHECCO, “Signal ha hackerato Cellebrite, svelate vulnerabilità nelle app di hacking telefonico: i risvolti”, in Cybersecurity360 consultabile sul sito https://www.cybersecurity360.it/nuove-minacce/signal-ha-hackerato-cellebrite-svelate-vulnerabilita-nelle-app-di-hacking-telefonico-i-risvolti/.

[7] L’articolo è consultabile sul sito Signal >> Blog >> Exploiting vulnerabilities in Cellebrite UFED and Physical Analyzer from an app’s perspective.

[8] Secondo quanto sostenuto da Signal, infatti, in realtà Cellebrite sarebbe riuscita semplicemente a capire dove si trovasse la chiave di cifratura con la quale i messaggi venivano localmente cifrati, cioè sul dispositivo analizzato, e non a forzare il meccanismo di cifratura delle chat dell’applicazione.

[9] Per un maggiore approfondimento si rimanda nuovamente a P. DAL CHECCO, op. cit., in Cybersecurity360.

[10] Si rimanda a N. BASSETTI, “Machine learning per l’identificazione dei file sospetti: tecniche e sviluppi”, in Cybersecurity360, consultabile sul sito https://www.cybersecurity360.it/soluzioni-aziendali/machine-learning-per-lidentificazione-dei-file-sospetti-tecniche-e-sviluppi/.

[11] Ibidem.

Articolo a cura di Francesco Lazzini

Profilo Autore

Laureato in giurisprudenza con successivo conseguimento dei master in Scienze Forensi (Criminologia-Investigazione-Security-Intelligence) e in Informatica giuridica, nuove tecnologie e diritto dell’informatica. Attività di studio postuniversitario focalizzata in materia di indagini con l’utilizzo del captatore informatico e digital forensics.

Condividi sui Social Network:

https://www.ictsecuritymagazine.com/articoli/digital-forensics-e-cyber-security-caso-cellebrite-ufed-vs-signal/



Daggerfly sta usando una nuova versione di Macma, una backdoor per macOS


Daggerfly, gruppo di cybercriminali cinesi conosciuto anche come Evasive Panda e Bronze Highland, ha di recente aggiornato il proprio arsenale di strumenti di attacco. Tra le novità c’è una nuova famiglia di malware basata su MgBot, il framework modulare di malware del gruppo, e una nuova versione di Macma, una backdoor per macOS.

Finora i ricercatori di sicurezza non erano riusciti ad associare Macma a uno specifico gruppo hacker; è stato il Threat Hunter Team di Symantec a scoprire il legame tra Daggerfly e Macma analizzando una serie di attacchi che hanno colpito organizzazioni a Taiwan e una NGO statunitense con sede in Cina.

Macma backdoor

Pixabay

Macma è una backdoor per macOS documentata per la prima volta nel 2021, ma sembra che sia attiva in realtà almeno dal 2019. La backdoor è stata utilizzata inizialmente in una serie di attacchi watering holes contro siti web di Hong Kong; questo tipo di attacchi mira a colpire i dispositivi di un gruppo specifico di utenti, di solito appartenenti a un determinato settore o a un’azienda, infettando con diversi malware i siti web che visitano più spesso.

Nel caso di Macma, gli attacchi sfruttavano exploit per iOS e macOS; in particolare, per i dispositivi macOS gli attaccanti usavano la CVE-2021-30869, una vulnerabilità di privilege escalation che gli permetteva di installare la backdoor sui sistemi.

Macma si presenta come una backdoor modulare in grado di eseguire comandi sul dispositivo, catturare istantanee dello schermo, effettuare keylogging, registrare audio e caricare e scaricare file.

Gli ultimi aggiornamenti della backdoor incrementano le sue funzionalità tramite nuovi moduli. Il modulo principale presenta ora una nuova logica per ottenere la lista di file del dispositivo, parametrizzazione e logging di debug addizionali e un nuovo file legato alla feature “autoScreenCaptureInfo”.

Secondo il Threat Hunter Team di Symantec, ci sono indizi chiari che legano Macma a Daggerfly: la backdoor si collega a un server C2 già utilizzato da un dropper di MgBot; inoltre, Macma e il malware di Daggerfly contengono codice che proviene dalla stessa libreria condivisa.

Non solo Macma: Daggerfly usa una nuova backdoor

Il team di Symantec ha scoperto che, tra le novità dell’arsenale di Daggerfly c’è un’altra backdoor oltre a Macma: in questo caso è una backdoor per Windows, la Trojan.Suzasfk conosciuta anche come Nightdoor. Questa backdoor ha fatto la sua apparizione più di recente (lo scorso marzo), quando è stata usata insieme a MgBot. Anche in questo caso, la libreria usata per sviluppare il malware è la stessa di MgBot e Macma.

Nightdoor è una backdoor multi-stage in grado di usare TCP e OneDrive per la comunicazione con gli attaccanti. A giudicare dal codice individuato da Symantec, la funzionalità per connettersi a OneDrive è in sviluppo o potrebbe essere presente in altre varianti del malware. La backdoor può inoltre individuare macchine virtuali, sandbox ed effettuare l’analisi dell’ambiente in cui si trova.

Il Threat Hunter Team di Symantec sottolinea che Daggerfly è un gruppo molto capace, in grado di sviluppare velocemente nuovi tool per colpire diverse piattaforme, con funzionalità sempre nuove. “Daggerfly sembra essere in grado di reagire allo smascheramento aggiornando rapidamente il suo set di strumenti per continuare le sue attività di spionaggio con interruzioni minime“ conclude il team.

Condividi l’articolo


Articoli correlati

Altro in questa categoria


https://www.securityinfo.it/2024/07/25/daggerfly-sta-usando-una-nuova-versione-di-macma-una-backdoor-per-macos/?utm_source=rss&utm_medium=rss&utm_campaign=daggerfly-sta-usando-una-nuova-versione-di-macma-una-backdoor-per-macos


12.9 million individuals affected by MediSecure cyber breach

MediSecure, an Australian electronic prescriptions provider, was the target of a recent cyber attack. This data breach potentially exposed the personal and health information of many customers, including healthcare provider information and prescription information. The impacted data is connected to prescriptions distributed until November 2023. 

According to the Australian Department of Home Affairs, approximately 12.9 million individuals were affected.

Dr. Martin J. Kraemer, Security Awareness Advocate at KnowBe4, comments, “This is a remarkable incident. Firstly, half of the Australian population now has sensitive data out there, including name and contact information as well as prescriptions and information on their medical history. This data set is a treasure trove for cybercriminals who want to launch targeted attacks at people, tricking them into behavior based on their health concerns. Rightly so, the Australian authorities warn about online scams, provide online advice and have even opened a mental health hotline.

“A national crisis committee has come together to coordinate a response to the incident. As one of formerly two online e-script providers, MediSecure was an integral part of the country’s infrastructure. The incident must be a wake-up call for others. Healthcare is the most targeted sector across the globe. It is part of the critical infrastructure. It holds highly sensitive and valuable information. It often has sub-par cybersecurity, especially when it comes to governance and risk management — healthcare operations have IT systems and organizations that have organically grown over the years. The incident must fuel regulatory and legislative efforts to secure critical infrastructure and its supply chain. The most likely way of entry at MediSecure was a supplier.”

https://www.securitymagazine.com/articles/100875-129-million-individuals-affected-by-medisecure-cyber-breach


North Korean hacker got hired by US security vendor, immediately loaded malware

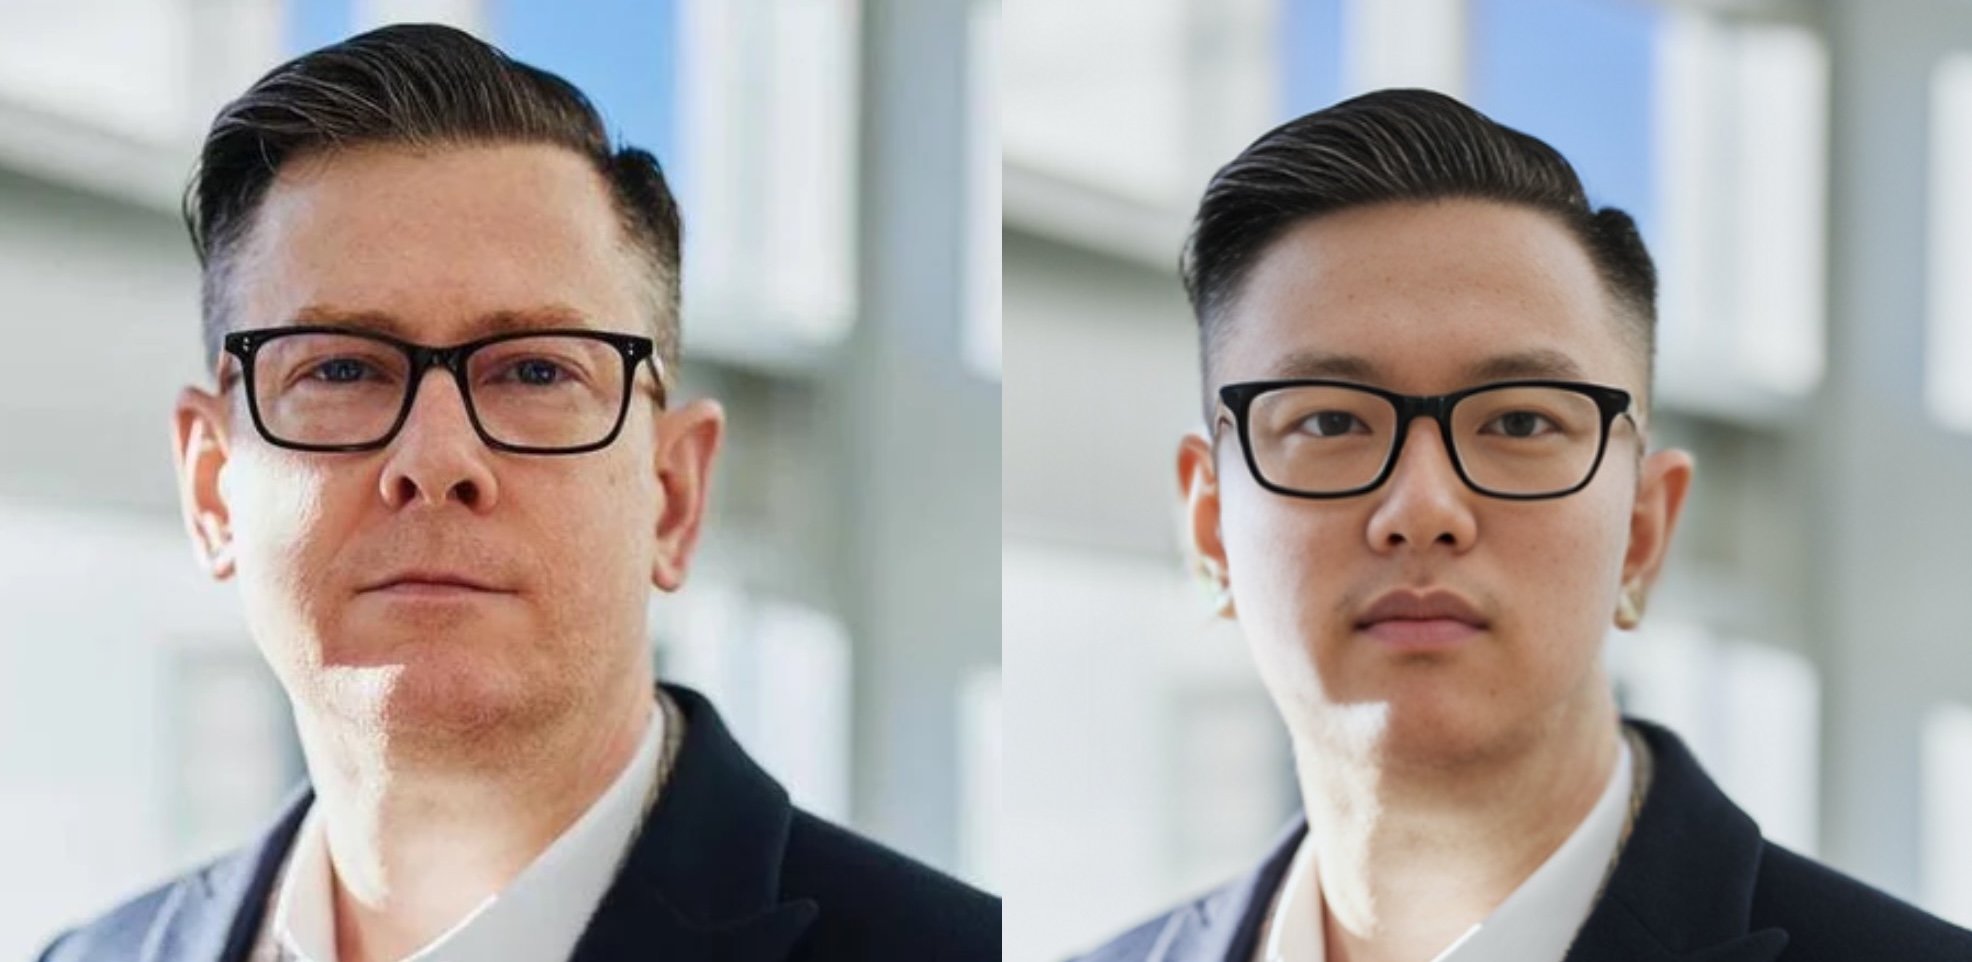
Two headshots of adult men. One is a real stock photograph while the other is an
Enlarge / On the left, a stock photo. On the right, an AI-enhanced image based on the stock photo. The AI-enhanced image was submitted to KnowBe4 by a job applicant.

KnowBe4, a US-based security vendor, revealed that it unwittingly hired a North Korean hacker who attempted to load malware into the company’s network. KnowBe4 CEO and founder Stu Sjouwerman described the incident in a blog post yesterday, calling it a cautionary tale that was fortunately detected before causing any major problems.

“First of all: No illegal access was gained, and no data was lost, compromised, or exfiltrated on any KnowBe4 systems,” Sjouwerman wrote. “This is not a data breach notification, there was none. See it as an organizational learning moment I am sharing with you. If it can happen to us, it can happen to almost anyone. Don’t let it happen to you.”

KnowBe4 said it was looking for a software engineer for its internal IT AI team. The firm hired a person who, it turns out, was from North Korea and was “using a valid but stolen US-based identity” and a photo that was “enhanced” by artificial intelligence. There is now an active FBI investigation amid suspicion that the worker is what KnowBe4’s blog post called “an Insider Threat/Nation State Actor.”

KnowBe4 operates in 11 countries and is headquartered in Florida. It provides security awareness training, including phishing security tests, to corporate customers. If you occasionally receive a fake phishing email from your employer, you might be working for a company that uses the KnowBe4 service to test its employees’ ability to spot scams.

Person passed background check and video interviews

KnowBe4 hired the North Korean hacker through its usual process. “We posted the job, received resumes, conducted interviews, performed background checks, verified references, and hired the person. We sent them their Mac workstation, and the moment it was received, it immediately started to load malware,” the company said.

Even though the photo provided to HR was fake, the person who was interviewed for the job apparently looked enough like it to pass. KnowBe4’s HR team “conducted four video conference based interviews on separate occasions, confirming the individual matched the photo provided on their application,” the post said. “Additionally, a background check and all other standard pre-hiring checks were performed and came back clear due to the stolen identity being used. This was a real person using a valid but stolen US-based identity. The picture was AI ‘enhanced.'”

The two images at the top of this story are a stock photo and what KnowBe4 says is the AI fake based on the stock photo. The stock photo is on the left, and the AI fake is on the right.

The employee, referred to as “XXXX” in the blog post, was hired as a principal software engineer. The new hire’s suspicious activities were flagged by security software, leading KnowBe4’s Security Operations Center (SOC) to investigate:

On July 15, 2024, a series of suspicious activities were detected on the user beginning at 9:55 pm EST. When these alerts came in KnowBe4’s SOC team reached out to the user to inquire about the anomalous activity and possible cause. XXXX responded to SOC that he was following steps on his router guide to troubleshoot a speed issue and that it may have caused a compromise.

The attacker performed various actions to manipulate session history files, transfer potentially harmful files, and execute unauthorized software. He used a Raspberry Pi to download the malware. SOC attempted to get more details from XXXX including getting him on a call. XXXX stated he was unavailable for a call and later became unresponsive. At around 10:20 pm EST SOC contained XXXX’s device.

“Fake IT worker from North Korea”

The SOC analysis indicated that the loading of malware “may have been intentional by the user,” and the group “suspected he may be an Insider Threat/Nation State Actor,” the blog post said.

“We shared the collected data with our friends at Mandiant, a leading global cybersecurity expert, and the FBI, to corroborate our initial findings. It turns out this was a fake IT worker from North Korea,” Sjouwerman wrote.

KnowBe4 said it can’t provide much detail because of the active FBI investigation. But the person hired for the job may have logged into the company computer remotely from North Korea, Sjouwerman explained:

How this works is that the fake worker asks to get their workstation sent to an address that is basically an “IT mule laptop farm.” They then VPN in from where they really physically are (North Korea or over the border in China) and work the night shift so that they seem to be working in US daytime. The scam is that they are actually doing the work, getting paid well, and give a large amount to North Korea to fund their illegal programs. I don’t have to tell you about the severe risk of this. It’s good we have new employees in a highly restricted area when they start, and have no access to production systems. Our controls caught it, but that was sure a learning moment that I am happy to share with everyone.

https://arstechnica.com/?p=2039069


AI is coming for company credentials — Here’s how to fight back

The GenAI explosion is something to behold, with advancements in the technology emerging on a seemingly daily basis. But the cynical security professional in me also sighs, “This is why we can’t have nice things.” Where businesses see AI as a tool for efficiency and market differentiation, cyber attackers are in mustache-twirling mode, devising new schemes to exploit undefined learning curves. 

As someone who spends each workday trying to make identity and access safer amid the scale and complexity of modern business, I can attest to the concerning frequency with which cybercriminals use new technology to gain access to corporate systems. For example, AI can be used to create realistic and effective phishing attacks and algorithms that can automate brute-force attacks by attempting millions of password combinations at high speeds. AI also can analyze leaked password databases and user information to predict commonly used passwords or patterns, making them easier to crack.

We’re also seeing how AI can contextualize network traffic, user behavior patterns and access control configurations to identify and exploit accounts or systems with excessive permissions or outdated software with known vulnerabilities. Once attackers gain a foothold, they can use AI to automate their processes and escalate privileges to gain access to sensitive data and resources. Almost every successful attack you read about in the news leveraged this approach, and now AI is making it easier and faster.

All of this begs the multibillion-dollar question: How do we stop it? We can’t, but we can make it inherently more difficult by implementing a policy of least privilege. 

The benefits of a least privilege policy

Microsoft found that 90% of identities use less than 5% of the access permissions granted. This year’s Verizon Data Breach Incident Report found that stolen credentials are now the most common action taken by attackers. These findings show that companies are unnecessarily opening themselves up to attacks by not protecting access and privileges. Attackers don’t need any advantages, especially as they weaponize AI to access your sensitive data.  

By implementing a least privilege policy, companies can rein in access and privilege to reduce risk to a bare minimum. Least privilege is based on a relatively simple concept: Users only have the right amount of access for the right amount of time that they need to do their job. When access is viewed as an asset in a limited capacity — as opposed to a birthright — companies drastically reduce risk and reap several benefits.

For example, limiting access permissions reduces the potential attack surface. Even if compromised credentials grant access, the attacker’s ability to move laterally within the system is significantly restricted. This compartmentalization, similar to a well-organized and consolidated view of your access ecosystem, makes it more difficult to reach sensitive data.

Organizations that implement least privilege also limit the damage an attacker can cause should they break through. With least privilege, the access a stolen credential allows is limited, reducing the potential for attackers to steal sensitive data, disrupt operations or install malware.

Additionally, a least privilege strategy enhances accountability by clearly defining access permissions for each role. Least privilege enables easier identification of suspicious activity, and if an account with limited access attempts to access restricted resources, it raises a red flag, potentially indicating a compromised credential.

Pillars of a least privilege policy

While every company will have nuances based on industry, compliance regulations, etc., there are three pillars that every least privilege policy should feature.

Granular access control

It’s critical to move away from broad access groups and start defining access based on specific roles and job functions — all while scrutinizing the “why” behind access. This strategy ensures users only have the keys to the resources they absolutely need. Applying access control methods — like role-based access control (RBAC), group-based access control (GBAC) and attribute-based access control (ABAC) — restricts access to varying degrees of granularity. The key is that access decisions are made on specific criteria based on need, as opposed to immediate, up-front access.

Just-in-time (JIT) provisioning

A common contributor to access risk is just-in-case (JIC) provisioning, which gives employees access to data and assets in perpetuity. This leads to over-provisioning and is in stark contrast to a least privilege implementation. Instead, companies should adopt a just-in-time provisioning approach, which grants access only when necessary and for a predetermined period. JIT provisioning minimizes the window of opportunity for attackers who might exploit stolen credentials. Think of it like a hotel room key — it grants access only for the duration of your stay, and you only get the key when you check in and need it..

Privileged account management (PAM)

Sometimes called privileged access management or privileged identity management, some users (admins and service accounts, for example) will need more traditional access privileges, so it’s important to implement special controls for privileged accounts that hold extensive access. These controls might include multi-factor authentication (MFA), session monitoring and dedicated privileged access workstations (PAWs) that isolate privileged activity. 

Implementing a least privilege strategy

Successfully implementing a least privilege policy requires careful planning and ongoing maintenance. With attackers using AI to exploit access vulnerabilities, it will be important to continuously evaluate your methods to ensure they’re up to speed and effective with emerging attack methods. 

The first step is reducing access. Start by eliminating excessive accounts that are widening your attack surface. For all accounts that remain, apply JIT where possible, making access time-bound. Get granular by scrutinizing every privilege in each repository, ensuring users only have access to the assets necessary to perform required functions. It’s also essential to monitor and refine access over time. For example, an employee may have been granted access to assets that they haven’t used in a while. If that’s the case, remove access or convert to JIT if they may need access at some point in the future. Staying on top of evolving access needs and making the necessary adjustments is the best way to maintain a narrow attack surface.

Next, create a plan for implementation. Adopting least privilege isn’t like flipping a switch, so create a clear and achievable timeline for adoption (a year is a reasonable amount of time for such a change). Adoption should take place in phases to make acclimation more seamless. To that end, put in extra legwork to get buy-in from users by highlighting the benefits of least privilege — such as protecting data against rising AI-powered attacks. Include continuous least privilege education for employees, emphasizing how least privilege protects them from being wrongly implicated in the event of a security issue. 

It’s also important to form a group of business leaders and senior individual contributors to lead the least privilege implementation to ensure the process stays as close to the proposed timeline as possible. This group should also collaborate with senior engineering and IT staff to create a program and architecture document, which details the least privilege strategy with deadlines for account reduction, privilege limitation and other essential milestones.

The rise of AI-powered attacks presents a significant challenge to traditional security measures. However, by embracing the principle of least privilege, organizations can significantly bolster their defenses. Implementing a least privilege strategy with a clear plan for maintaining it empowers your organization to reduce the probability of successful AI-powered threats and protect your nice things.  

https://www.securitymagazine.com/blogs/14-security-blog/post/100874-ai-is-coming-for-company-credentials-heres-how-to-fight-back


Qual è la causa dei disservizi di venerdì scorso? Ce la rivela CrowdStrike


Il 19 luglio 2024 è una data che rimarrà impressa per molto tempo nella nostra memoria: a partire dalle prime ore della mattinata, milioni di dispositivi Windows hanno smesso di funzionare a causa di un aggiornamento fallato della piattaforma Falcon di CrowdStrike.

Aeroporti, stazioni, emittenti radiofoniche e televisive ma anche servizi di emergenza si sono trovati all’improvviso con schermate blu di errore e dispositivi che non riuscivano più ad avviarsi correttamente. Le macchine sono rimaste in un loop di boot provocando interruzioni di servizio per ore e ore, tanto che numerose compagnie aeree hanno dovuto sospendere i voli in programma fino alla risoluzione del problema.

CrowdStrike

Pixabay

Oggi CrowdStrike ha rilasciato un report in cui spiega cosa è accaduto e illustra agli utenti come risolvere la problematica nel caso in cui non l’avessero ancora fatto.

“Venerdì 19 luglio alle 04:09 UTC (le 06:09 ora italiana, n.d.r.), come parte di regolari attività, CrowdStrike ha rilasciato un aggiornamento di configurazione per i sensori Windows per ottenere telemetria su potenziali nuove tecniche di attacco” si legge nel report. “Questi aggiornamenti sono parte dei meccanismi di protezione dinamica della piattaforma Falcon. La nuova configurazione problematica di Rapid Response Content ha causato il crash dei sistemi Windows“.

Tutta colpa di un aggiornamento fallato

I dispositivi “vittime” dell’aggiornamento sono quelli che eseguono versioni del sensore dalla 7.11 in su che erano online tra le 06:09 (ora italiana) e le 07:27 di venerdì e che hanno ricevuto l’aggiornamento. L’update fallato è stato ripristinato alle 07:27 e tutti i dispositivi che hanno scaricato l’update dopo quell’orario non sono stati impattati dal problema.

Il problema era nel Channel File 291, un tipo di file che viene usato per aggiornare le configurazioni di Falcon che sfruttano la behavioral analysis per individuare e fermare le minacce. Nel dettaglio, il file conteneva un aggiornamento che migliorava il modo in cui Falcon valuta l’esecuzione delle “named pipe”, ovvero un comune meccanismo di comunicazione tra processi.

Nel file però era presente un errore di logica che non è stato individuato durante la validazione dell’update, e il bug quindi è stato distribuito inavvertitamente a tutte le macchine online nel lasso di tempo indicato da CrowdStrike.

Il contenuto del Channel File 291, una volta ricevuto dal sensor e caricato nel Content Interpreter, ha provocato una out-of-bound memory read che a sua volta ha causato un’eccezione non gestita; poiché Falcon è integrato col kernel Windows, l’eccezione ha portato poi al crash del sistema.

Pixabay

CrowdStrike rassicura gli utenti

Il disservizio diffuso di venerdì scorso è stato indubbiamente uno dei più grandi ai quali abbiamo assistito finora, se non il più grande. L’aggiornamento ha creato molti problemi ad aziende di diversi settori e c’è voluto molto tempo per ritornare alla completa operatività.

“Assicuriamo ai nostri clienti che CrowdStrike sta operando normalmente e che questo problema non riguarda i sistemi della piattaforma Falcon. Se i vostri sistemi funzionano normalmente, non c’è alcun impatto sulla loro protezione se il sensore Falcon è installato. I servizi Falcon Complete e OverWatch non sono stati interrotti da questo incidente” ha chiarito la compagnia.

Anche George Kurtz, fondatore e CEO di CrowdStrike, ha detto la sua in merito: “Voglio scusarmi sinceramente con tutti voi per l’interruzione del servizio. Tutta CrowdStrike comprende la gravità e l’impatto della situazione. Abbiamo rapidamente identificato il problema e implementato una soluzione, permettendoci di concentrarci diligentemente sul ripristino dei sistemi dei clienti come nostra massima priorità” ha spiegato.

La compagnia ha promesso di migliorare i test per la validazione degli aggiornamenti e di fornire ai propri clienti più controllo sugli update, permettendogli di decidere quando installarli; fino a ora venivano installati automaticamente.

Condividi l’articolo


Articoli correlati

Altro in questa categoria


https://www.securityinfo.it/2024/07/24/qual-e-la-causa-dei-disservizi-di-venerdi-scorso-ce-la-spiega-crowdstrike/?utm_source=rss&utm_medium=rss&utm_campaign=qual-e-la-causa-dei-disservizi-di-venerdi-scorso-ce-la-spiega-crowdstrike


SEC establishes Interagency Securities Council (ISC)

The SEC has established the Interagency Securities Council (ISC) to foster collaboration between federal, state and local agencies. Agencies involved in the ISC will meet quarterly to review threat trends and mitigation strategies. 

The expressed objectives of the council are the following: 

  • Solidify cohesion between federal, state and local agencies 
  • Improve collaborative efforts on cases to protect investors
  • Offer insights and perspectives across the ecosystems 
  • Establish a forum to combat financial fraud as a unified front

The ISC consists of representatives from more than 100 agencies and departments, such as federal agencies, local police departments, sheriff’s offices, state police and state offices of attorneys general. 

https://www.securitymagazine.com/articles/100871-sec-establishes-interagency-securities-council-isc