Il Lato oscuro dell’Intelligenza Artificiale: approccio della threat intelligence alle nuove tipologie di vulnerabilità e minacce del cybercrime – Francesco Arruzzoli

Durante la Cyber Crime Conference 2024, Francesco Arruzzoli, Sr. Cyber Security Threat Intelligence Architect, ha tenuto un intervento di grande rilievo sull’evoluzione dell’intelligenza artificiale (IA) nel campo della Cyber Threat Intelligence sottolineando l’importanza di un approccio critico e multidimensionale verso le nuove tecnologie. Ha poi illustrato come l’IA sia diventata uno strumento fondamentale per analizzare e gestire enormi quantità di dati, sia strutturati che non.

Guarda il video completo dell’intervento:

[embedded content]

Intelligenza Artificiale, l’Importanza dell’Elaborazione del Linguaggio Umano

Il relatore ci racconta come l’aspetto chiave dell’intelligenza artificiale risieda nella sua capacità di elaborare e comprendere il linguaggio umano, un salto evolutivo descritto attraverso le ricerche di Jeff Hawkins, neuroscienziato e pioniere nell’AI, che nel 2023 gli ha permesso di analizzare circa 120 zettabyte di dati, una quantità impressionante che equivale a 36.000 anni di video in HD.

Monopolio delle Informazioni e Implicazioni Etiche

Un punto critico sollevato durante l’intervento riguarda il monopolio delle informazioni detenuto da poche aziende, che oggi rappresenta un problema significativo per la democratizzazione della tecnologia. Questo aspetto è cruciale per comprendere le dinamiche di potere nel settore tecnologico e le implicazioni etiche che ne derivano.

Intelligenza Artificiale Generativa: Il Futuro della Tecnologia

Arruzzoli ha anche introdotto il concetto di intelligenza artificiale generativa in quanto diventerà un pilastro fondamentale entro la fine del 2025. Questo nuovo tipo di IA avrà la capacità di generare conversazioni eliminando l’uso di dispositivi tradizionali come tastiera e mouse, e integrando l’IA più profondamente nella nostra vita quotidiana attraverso applicazioni, portando come esempio attuale Microsoft CoPilot.

Integrazione dell’IA nel Cloud e l’Evoluzione dell’AIoT

Questo ha portato ad un altro tema cardine, l’integrazione dell’IA nel Cloud che si pone come risposta alla necessità di un’infrastruttura sempre attiva per supportare queste tecnologie avanzate accompagnando così verso l’evoluzione degli “Artificial Intelligence IoT” (AIoT) e promettendo di rendere i dispositivi connessi ancora più intelligenti, trasformando così l’ambiente fisico in uno spazio altamente tecnologico.

Sfide Etiche e Normative dell’Intelligenza Artificiale

Durante il suo intervento, l’esperto di Cyber Threat Intelligence ha poi esplorato le sfide etiche e normative che emergono dall’uso dell’IA, come la gestione della privacy e l’implicazione del “nudging”, capace di influenzare sottilmente le decisioni umane. Ha proseguito sottolineando l’importanza di mantenere l’essere umano nel loop decisionale per evitare che l’intelligenza artificiale operi incontrollata.

L’IA nella Medicina: Superare le Capacità Umane

Uno degli esempi più significativi menzionati durante la presentazione ha riguardato l’uso dell’IA nella medicina, dove algoritmi avanzati sono capaci di riconoscere patologie da immagini radiologiche con una precisione superiore a quella umana, a dimostrazione di come l’IA stia, in alcuni ambiti specifici, superando le capacità umane.

Attacchi Cognitivi e Rischi delle Tecnologie Non Regolamentate

Infine, Arruzzoli ha affrontato le implicazioni dei cosiddetti attacchi cognitivi, dove l’intelligenza artificiale può essere utilizzata per creare attacchi o difendere dalle minacce in modi che superano la comprensione umana. Ha citato un esempio in cui false notizie generate da IA hanno causato un crollo nel mercato azionario, a dimostrazione della reale pericolosità di queste tecnologie se non regolamentate adeguatamente.

Un Approccio Bilanciato all’Intelligenza Artificiale

In conclusione, il discorso ha messo in luce l’importanza di un approccio bilanciato e consapevole nei confronti dell’intelligenza artificiale, evidenziando sia le sue potenzialità rivoluzionarie sia le sfide etiche e normative che dobbiamo affrontare per integrarla responsabilmente nella nostra società.

Il programma completo della Cyber Crime Conference 2024 è disponibile al seguente link: https://www.ictsecuritymagazine.com/eventi/cybercrimeconference2024#programma

Iscriviti alla nostra newsletter per rimanere aggiornate sulle nostre iniziative: https://www.ictsecuritymagazine.com/newsletter/

Condividi sui Social Network:

https://www.ictsecuritymagazine.com/cybersecurity-video/il-lato-oscuro-dellintelligenza-artificiale-approccio-della-threat-intelligence-alle-nuove-tipologie-di-vulnerabilita-e-minacce-del-cybercrime-francesco-arruzzoli/


39% of MSPs adapting to new technologies is their biggest challenge

A new report reveals the attitudes and perspectives of Managed Service Providers (MSPs) in 2024. According to the report, 39% of MSPs state that their greatest challenge is keeping up with emerging cybersecurity solutions and technologies. 

This research was conducted in March of 2024 by surveying 350 MSPs in the United States, the United Kingdom, Australia and Germany, offering insights into modern MSP operations. 

Security leaders weigh in 

Tom Corn, Chief Product Officer at Ontinue:

“Traditionally organizations have amassed far too many security tools from far too many vendors — and that complexity has not only added cost, but risk. Aligning policy and the position of these controls becomes infinitely harder in those environments — and that misalignment creates opportunity for attackers. This fact has precipitated more and more organizations to rationalize their security infrastructure.  Every organization still has a variety of security controls from different vendors, and multiple surfaces to protect — but increasingly there are shrinking that set down, especially in domains like SIEM, EDR, etc.” 

Chad Graham, Manager of Cyber Incident Response Team (CIRT) at Critical Start:

“The rapid pace of innovation in cybersecurity means that MSPs must stay ahead of several key trends. These include the increasing use of AI and machine learning for threat detection and response, the growing importance of zero trust architecture, and the integration of advanced analytics for predictive threat modeling. Additionally, regulatory changes and the increasing need for compliance will drive MSPs to adopt more rigorous security practices. To remain competitive, MSPs should invest in continuous training for their staff, foster strong vendor relationships and adopt flexible, scalable security solutions that can adapt to the changing threat landscape.

“The skills shortage in cybersecurity is a significant concern that cannot be overlooked. MSPs must prioritize developing in-house talent through training and certifications while also leveraging automation and AI to augment human capabilities. Building a strong cybersecurity culture within the organization and focusing on employee retention can help mitigate the impact of this shortage. Additionally, collaboration within the cybersecurity community, including information sharing and joint threat intelligence efforts, can enhance the overall security posture and resilience of MSPs.” 

Dave Gerry, CEO at Bugcrowd:

“The availability of automation, machine learning and broader AI use cases will continue to facilitate a more efficient operating environment for MSPs. Pair that with a smaller total number of technology offerings and this will enable MSPs to reduce the breadth of hiring needs that they have a refocus those efforts on hiring the right people to serve their customer needs.” 

https://www.securitymagazine.com/articles/100737-39-of-msps-adapting-to-new-technologies-is-their-biggest-challenge


Ticketmaster hacked in what’s believed to be a spree hitting Snowflake customers

Ticketmaster hacked in what’s believed to be a spree hitting Snowflake customers
Getty Images

Cloud storage provider Snowflake said that accounts belonging to multiple customers have been hacked after threat actors obtained credentials through info-stealing malware or by purchasing them on online crime forums.

Ticketmaster parent Live Nation—which disclosed Friday that hackers gained access to data it stored through an unnamed third-party provider—told TechCrunch the provider was Snowflake. The live-event ticket broker said it identified the hack on May 20, and a week later, a “criminal threat actor offered what it alleged to be Company user data for sale via the dark web.”

Ticketmaster is one of six Snowflake customers to be hit in the hacking campaign, said independent security researcher Kevin Beaumont, citing conversations with people inside the affected companies. Australia’s Signal Directorate said Saturday it knew of “successful compromises of several companies utilizing Snowflake environments.” Researchers with security firm Hudson Rock said in a now-deleted post that Santander, Spain’s biggest bank, was also hacked in the campaign. The researchers cited online text conversations with the threat actor. Last month, Santander disclosed a data breach affecting customers in Chile, Spain, and Uruguay.

“The tl;dr of the Snowflake thing is mass scraping has been happening, but nobody noticed, and they’re pointing at customers for having poor credentials,” Beaumont wrote on Mastodon. “It appears a lot of data has gone walkies from a bunch of orgs.”

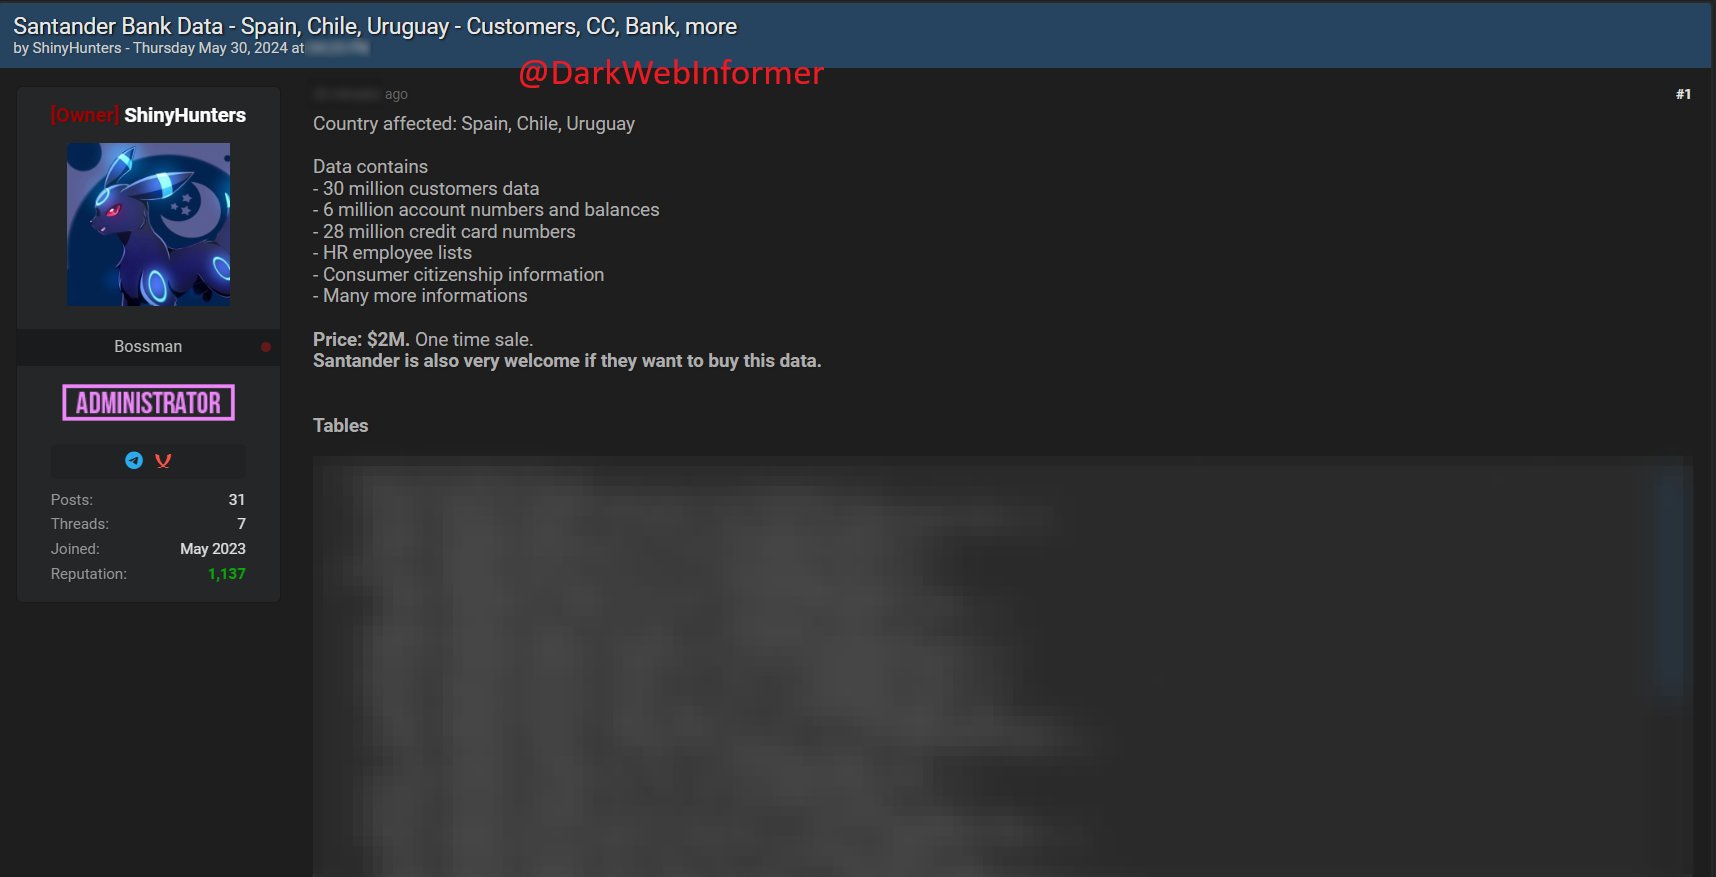
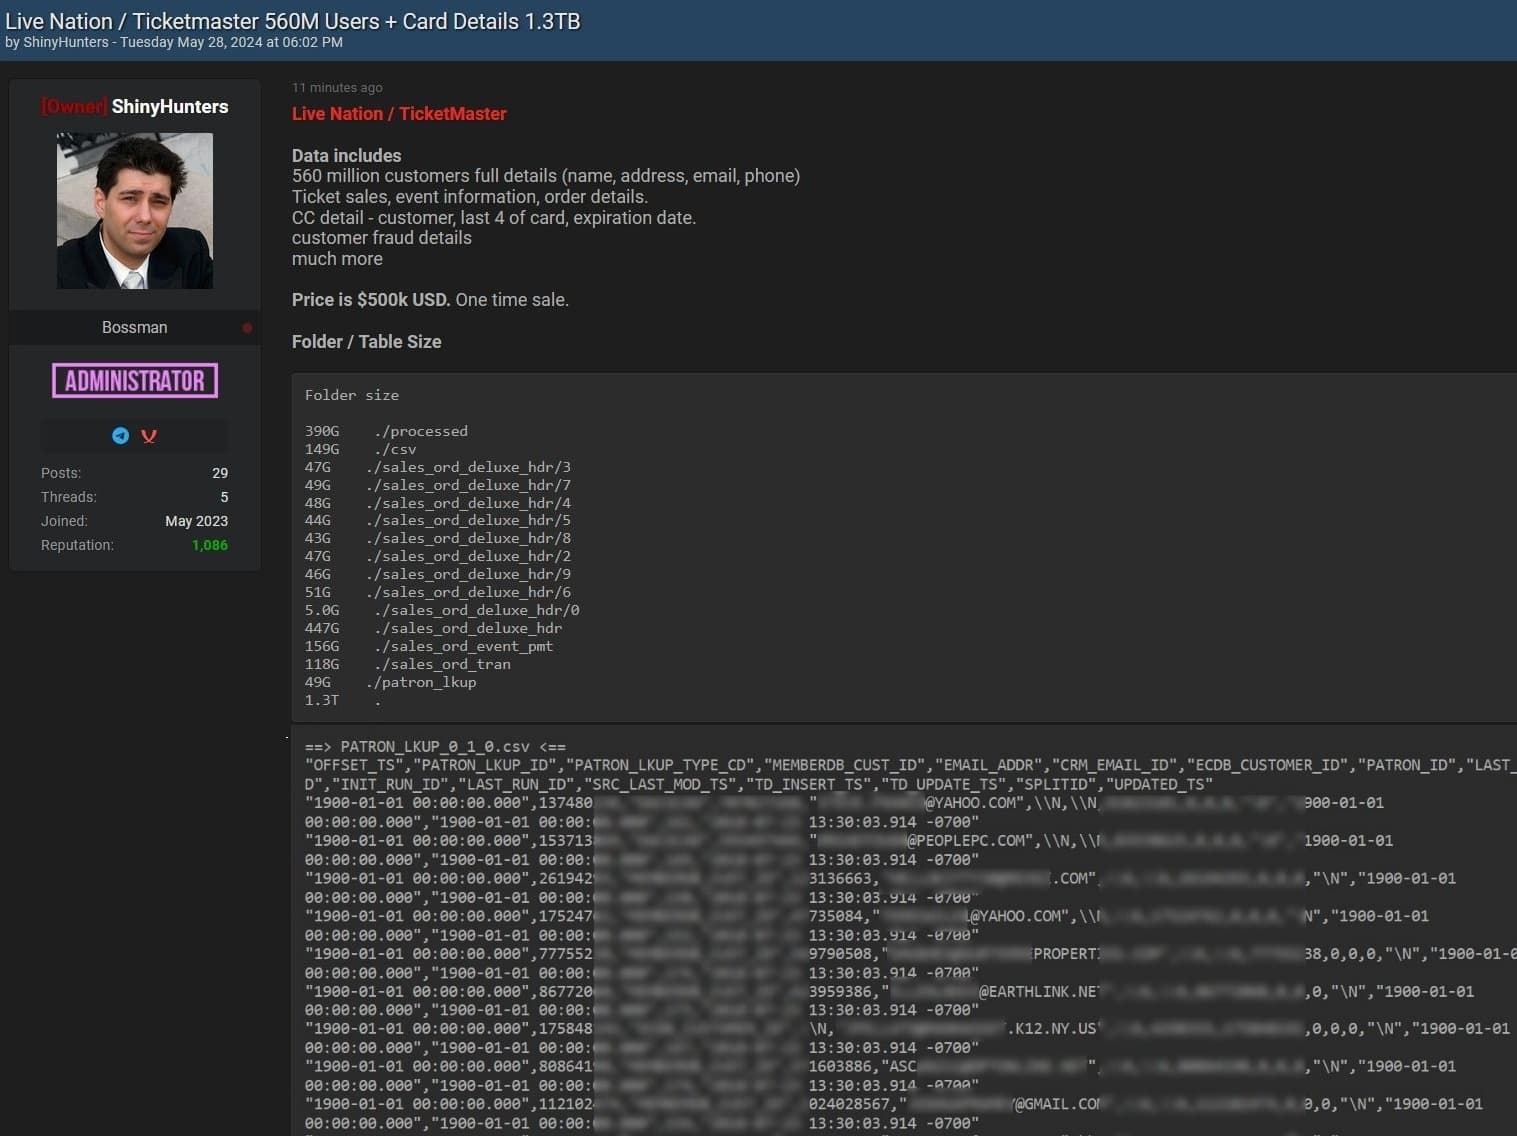
Word of the hacks came weeks after a hacking group calling itself ShinyHunters took credit for breaching Santander and Ticketmaster and posted data purportedly belonging to both as evidence. The group took to a Breach forum to seek $2 million for the Santander data, which it said included 30 million customer records, 6 million account numbers, and 28 million credit card numbers. It sought $500,000 for the Ticketmaster data, which the group claimed included full names, addresses, phone numbers, and partial credit card numbers for 560 million customers.

Post by ShinyHunters seeking $2 million for Santander data.
Enlarge / Post by ShinyHunters seeking $2 million for Santander data.
Post by ShinyHunters seeking $500,000 for Ticketmaster data.
Enlarge / Post by ShinyHunters seeking $500,000 for Ticketmaster data.

Beaumont didn’t name the group behind the attacks against Snowflake customers but described it as “a teen crimeware group who’ve been active publicly on Telegram for a while and regularly relies on infostealer malware to obtain sensitive credentials.

The group has been responsible for hacks on dozens of organizations, with a small number of them including:

According to Snowflake, the threat actor used already compromised account credentials in the campaign against its customers. Those accounts weren’t protected by multifactor authentication (MFA).

Snowflake also said that the threat actor used compromised credentials to a former employee account that wasn’t protected by MFA. That account, the company said, was created for demonstration purposes.

“It did not contain sensitive data,” Snowflake’s notification stated. “Demo accounts are not connected to Snowflake’s production or corporate systems.”

The company urges all customers to ensure all their accounts are protected with MFA. The statement added that customers should also check their accounts for signs of compromise using these indicators.

“Throughout the course of our ongoing investigation, we have promptly informed the limited number of customers who we believe may have been impacted,” the company said in the post.

Snowflake and the two security firms it has retained to investigate the incident—Mandiant and Crowdstrike—said they have yet to find any evidence the breaches are a result of a “vulnerability, misconfiguration, or breach of Snowflake’s platform.” But Beaumont said the cloud provider shares some of the responsibility for the breaches because setting up MFA on the Snowflake is too cumbersome. He cited the breach of the former employee’s demo account as support.

“They need to, at an engineering and secure by design level, go back and review how authentication works—as it’s pretty transparent that given the number of victims and scale of the breach that the status quo hasn’t worked,” Beaumont wrote. “Secure authentication should not be optional. And they’ve got to be completely transparent about steps they are taking off the back of this incident to strengthen things.”

https://arstechnica.com/?p=2028710


49% of organizations feel somewhat prepared to handle a breach

Cybersecurity readiness was analyzed in a recent report by CDW. Eighty-eight percent of respondents said they are somewhat (50%) or very (38%) confident that they have sufficient visibility into their cybersecurity posture. Of those who were very confident, 61% indicated that identity and access management (IAM) solutions were very effective in enhancing visibility into their environment. Despite the confidence around visibility, about half (49%) of respondents still feel only somewhat prepared to handle a breach.

One aspect of critical strategy for cybersecurity is zero trust. Survey results indicated that over 41% of respondents have reached an advanced level of maturity in their zero trust journey, yet just 12% reported feeling that they have achieved an optimal level. Additionally, more than 43% of respondents indicated they had suffered a breach costing between $1 million and $10 million in downtime.

The report found that insufficient or ineffective employee cybersecurity training (31%) and budgetary resources (27%) are two of the biggest items missing from respondents’ cybersecurity approach. In making the case for funding, 76% of respondents indicated that showing the cost of a data breach was an effective method in making the case for additional investments in cybersecurity.

Download the report

https://www.securitymagazine.com/articles/100739-49-of-organizations-feel-somewhat-prepared-to-handle-a-breach


A new malicious email campaign uses piano-themed scams to lure targets

A recent discovery by Proofpoint shows that a new malicious email campaign is sending piano-themed emails as bait for scams. According to the report, the campaign primarily targets colleges and universities in North America; however, targets were also observed in healthcare and food and beverage services. 

In the observed email, the malicious actor offers a piano to the target. If the target accepts and sends money to cover the shipping costs, the malicious actor takes the money and vanishes. This campaign emphasizes the way malicious actors utilize emotional appeal to lure their targets — for instance, inventing stories of passed family members who previously owned the piano. 

As of January 2024, the research on this malicious email campaign has found that more than 125,000 messages have been sent. Furthermore, at least one Bitcoin wallet has been associated with the scam, containing more than $900,000 in transactions. 

https://www.securitymagazine.com/articles/100734-a-new-malicious-email-campaign-uses-piano-themed-scams-to-lure-targets


Cybersecurity e intelligenza artificiale: una nuova era nella difesa digitale


L’intelligenza artificiale è uno degli argomenti più caldi del momento. E se la si abbina alla sicurezza informatica, le possibilità (ma anche le sfide) risultanti, sono sbalorditive.

Per molti professionisti della sicurezza è scontato che l’integrazione dell’IA con la cybersecurity migliori le capacità di difesa informatiche di chi è colpito da attacchi sempre più sofisticati. Purtroppo, però, anche i criminali informatici si avvalgono dell’intelligenza artificiale, rendendo nuovamente incerto l’esito dello scontro.

Check Point, multinazionale israeliana specializzata in soluzioni di sicurezza informatica, ha collaborato con la società di ricerca Vanson Bourne per scoprire come i professionisti della sicurezza stiano adottando l’IA generativa.

Nonostante oltre il 70% degli intervistati si senta fiducioso in merito alle difese della propria azienda, l’89% riconosce che l’assunzione di personale qualificato rappresenti una sfida.

Ciò conferma, una volta di più, il problema rappresentato dalla carenza di talenti in questo ambito. Ed ostacola seriamente l’efficacia delle organizzazioni di creare le giuste difese contro il crimine informatico “potenziato” dall’intelligenza artificiale.

Nessuna organizzazione, grande o piccola, può ignorare il potenziale impatto di un grave attacco informatico. E i numeri lo confermano: tra gli intervistati, il 98% di chi ha subito un attacco ha dichiarato di aver registrato un “impatto” sulle operazioni di sicurezza. Di questi, il 40% ha parlato di un “forte impatto”.

Di conseguenza, le organizzazioni intervistate hanno dichiarato di essersi rivolte a strumenti basati sull’IA per potenziare la loro sicurezza informatica come la risposta agli incidenti, la protezione dalle minacce e dalla perdita di dati.

L’intelligenza artificiale sta assumendo un ruolo sempre più importante nel fornire una migliore protezione al panorama digitale. Ecco perché una parte significativa degli intervistati ha dichiarato di utilizzarla da oltre un anno per migliorare la propria sicurezza.

In tutto il mondo è diffuso il convincimento che gli strumenti di GenAI offrano una migliore comprensione del comportamento e delle anomalie degli utenti. Tuttavia, ci sono delle differenze tra gli intervistati delle diverse regioni.

Gli strumenti di GenAI offrono una migliore comprensione del comportamento e delle anomalie degli utenti.

Rispetto ad altre parti del mondo, gli europei sono meno d’accordo sul fatto che l’IA possa essere collegata a una maggiore efficienza, e quindi che migliori la prevenzione e il rilevamento delle minacce, o che riduca il lavoro manuale dei team e semplifichi le operazioni di sicurezza e l’allocazione delle risorse. Quest’ultimo aspetto, invece, riceve un  maggior sostegno da parte dei professionisti dell’area dell’Asia Pacifica (APAC), con quasi il 50% delle risposte a favore.

La GenAI può essere un alleato nell’affrontare il divario di competenze. Offre, infatti, un modo per aumentare le capacità esistenti e migliorare l’efficienza, soprattutto nei settori con un’elevata richiesta di competenze in materia di sicurezza informatica. Il suo impatto varia a seconda degli ambiti merceologici, con particolari benefici avvertiti nella sanità e nella finanza.

Questi settori riconoscono il potenziale della GenAI nel ridurre significativamente il lavoro manuale e nell’aumentare l’efficienza della risposta agli incidenti. Alla domanda “Pensando a GenAI/AI/ML Deep-Learning, in che misura sei d’accordo o meno con le seguenti affermazioni?”, la maggior parte degli intervistati concorda sul fatto che gli strumenti di IA miglioreranno la loro efficienza, aumenteranno i tassi di risposta agli incidenti e contribuiranno a colmare le lacune nelle competenze delle loro organizzazioni.

Entrando nel dettaglio, la sanità crede che l’IA riduca o possa ridurre in modo significativo (32% in meno) il lavoro manuale per i team di sicurezza. Per i settori di energia, petrolio/gas e servizi pubblici, l’IA, il machine learning e il deep learning possono aumentare del 36% l’efficienza nella risposta agli incidenti.

Guardando invece ai settori finanza/bancario/investimenti, l’intelligenza artificiale ha fatto o può fare aumentare il tasso di rilevamento del 35% e ha contribuito o può contribuire a colmare il divario di competenze in materia di sicurezza informatica del 28%.

L’impegno per l’integrazione dell’IA generativa nella sicurezza informatica è forte, col 90% delle organizzazioni che conta di dare la priorità agli strumenti che offre. Ciò comporta l’aumento previsto negli stanziamenti a livello di budget.

Sebbene le prospettive siano ottimistiche, rimangono comunque preoccupazioni e sfide. Le organizzazioni, ad esempio, sottolineano l’importanza di mantenere aggiornati i modelli di IA, così come di garantire la conformità alle normative sui dati. Appare comunque chiaro che l’IA contribuirà a trasformare le organizzazioni, aprendo la strada a un futuro digitale più sicuro e resiliente.

Condividi l’articolo


Articoli correlati

Altro in questa categoria


https://www.securityinfo.it/2024/06/03/cybersecurity-intelligenza-artificiale-nuova-era-difesa-digitale/?utm_source=rss&utm_medium=rss&utm_campaign=cybersecurity-intelligenza-artificiale-nuova-era-difesa-digitale


Defeating current DNS-based attacks

Domain name systems (DNS) has been undergirding the internet for more than four decades — and still it’s a daily pathway for cyberattacks. Considering how long security pros have had to create a better way to secure it, DNS security continues to lag, posing a significant security risk today. It remains responsible, at least to some extent, for a significant portion of cyber-attacks.

There’s a wide array of attacks based on DNS available to bad actors, including DDoS attacks, malware, phishing and domain theft. Attacks like these have the potential to cause significant disruption to an organization. Though there are many examples to draw from, the Google Cloud and  ChatGPT outages are some of the most high-profile current incidents. Almost every aspect of modern malware uses DNS in some way.

Let’s examine ways that criminals are leveraging DNS currently and, crucially, what a security team can improve upon to maintain the upper hand.

Three main cybercriminal tactics

The average user combats five malicious DNS queries daily, according to DNSFilter’s annual security report. That comes out to a yearly total of around 1,825 malicious queries for each user. Year over year, there was an increase in detection of malware (40%) and phishing attempts (106%). Bad actors rely on social engineering, phishing and malicious web links to conduct their ransomware attacks. According to CISA, in fact, 9 out of 10 cyberattacks start via a phishing attack. If that’s not enough to wake people up to the reality of the need for DNS defense, probably nothing will.

It’s possible to spot trends by taking a look at some of the main tactics that cybercriminals are currently using, such as:

  • Phishing with phony Office365 pages — An analysis revealed that criminals often use Office365 as a lure. They create realistic-looking fake pages that unsuspecting victims willingly click on, which leads to the spread of malware and more.
  • Redirection — It’s a common occurrence for people to get redirected via traffic distribution systems. These are well-known or long-standing domains that send people to a malware landing page. This could be a fake website or casino, for instance, or an actual OneDrive page that has links leading to a fake Office365 phishing login page. The criminal is relying on the standard user behavior of checking the OneDrive URL not the second URL.
  • A revolving door of domain names — Researchers witnessed the strange phenomenon of daily domain name changes that are based on a newly registered (one-day-old) domain name. The purpose is still unclear, but the tactic involves a new kind of server that employs the same range of IP addresses but also random domains that look like someone just smashed their hands onto a keyboard. This may happen many times a day. Over 100 organizations in our network have experienced this tactic.

What drives DNS security challenges?

For criminals, DNS represents an easy target. Though you might assume that security is built into DNS at this point, you would be wrong. It’s still standard practice to not monitor, encrypt or secure DNS. The creator of DNS was going for speed and reliability, not security. For over 40 years, security teams have essentially ignored this integral and universal aspect of the internet, even though it’s used in most attacks and breaches.

Another DNS security challenge is the fallibility of humans. People tend to rush through their online transactions and don’t always stop to check the links they click on or the email sender’s address. This is the underlying reason for the ongoing success of phishing attacks.

Cybercriminals are becoming more sophisticated with the help of AI and other emerging technologies. They can personalize phishing emails with AI, which makes them seem more legitimate and helps them evade spam filters. And they can use AI to automate actions such as checking for vulnerabilities in DNS servers and configurations. In these ways, bad actors can efficiently find targets and focus on exploiting their weaknesses.

Reclaiming control of DNS 

Typically, DNS is not the focus of security teams. They are trying to fix more immediate problems like users clicking a bad link and getting phished or downloading ransomware that infects the network. But as our data shows, it’s critical to pay attention to DNS. The Cybersecurity and Infrastructure Security Agency (CISA) and the National Security Agency (NSA) advocated for this position three years ago.

Their recommendations are beginning to catch on. Around the world, organizations are adding DNS security solutions to their arsenal — especially due to the “work from anywhere” trend. When employees are dispersed, security teams must protect not only the corporate network but all the endpoints that remote staff use, too.

A prevention, detection and response strategy is what’s needed. Security teams need the proper tools — specifically, AI and automation. Malicious actors use these technologies, and good actors can also use them for actions like checking every domain that users access. They can also use machine learning-driven domain categorization to find zero-day threats, which stops threats before they can enter the network.

Cyber hygiene is also part of DNS security. Companies should train employees so they are more cyber-aware and know what bad links look like, so they don’t click on them. Since people are usually in a perpetual hurry, it’s important to provide ongoing education so that cyber hygiene becomes ingrained.

Secure DNS, more secure company

Organizations should have been securing their DNS for decades — and now the need is extreme, as statistics and guidelines from the likes of CISA and the NSA demonstrate. Attackers’ use of AI and automation, along with the foibles of human nature, create security risks, but defensive teams can use those technologies to protect the network. They can also keep training current for all employees. This two-pronged approach will enable companies to confidently face whatever comes at them.

https://www.securitymagazine.com/articles/100736-defeating-current-dns-based-attacks


Research discovers the 25 most hacked pop culture passwords

New research from Mailsuite reveals the most hacked pop culture passwords in 2024. By analyzing more than 300 million exposed passwords from the Pwned database, the research determined the top 25 hacked passwords from pop culture. These passwords include media franchise characters, musicians, sports teams and more. 

Below are the most hacked passwords as well as the number of appearances they made in analyzed data breaches. 

  1. Superman (584,697)
  2. Blink-182 (482,244)
  3. Batman (352,422)
  4. Star Wars (323,546)
  5. Eminem (286,263)
  6. 50 Cent (267,691)
  7. Metallica (264,913)
  8. Slipknot (258,281)
  9. Spider-Man (253,179)
  10. Minecraft (215,934)
  11. Hello Kitty (188,126)
  12. Barbie (186,730)
  13. New York Yankees (170,241)
  14. Green Day (142,561)
  15. Slayer (136,810)
  16. Flo Rida (135,310)
  17. Pantera (121,665)
  18. Warcraft (121,473)
  19. Linkin Park (118,856)
  20. Boston Red Sox (116,987)
  21. Rammstein (106,897)
  22. Harry Potter (104,544)
  23. Avatar (100,612)
  24. Terminator (100,128)
  25. Pikachu (96,430)

The report notes that exposed passwords should be promptly updated and avoided in the future. 

https://www.securitymagazine.com/articles/100733-research-discovers-the-25-most-hacked-pop-culture-passwords


L’obsolescenza tecnologica degli impianti industriali e le sfide per la cybersecurity

La cybersecurity degli impianti industriali è una sfida sempre più importante per le aziende che vogliono proteggere i propri dati, processi e infrastrutture da possibili attacchi informatici. Lo è anche per chi, abituato al mondo ICT aziendale tradizionale, si trova ad adattare strategie e tecnologie ad un contesto che ha, invece, le sue caratteristiche peculiari.

Un sistema di automazione e controllo industriale deve garantire il corretto funzionamento delle sue attività per tutta la durata del suo impiego sul campo. L’obsolescenza si verifica quando il produttore non fornisce più assistenza all’hardware o software e non produce più componenti di ricambio o di aggiornamento. Il mantenimento di una tecnologia obsoleta implica una serie di rischi che devono essere valutati (ad esempio la disponibilità di pezzi di ricambio, la competenza e l’affidabilità) e tra questi la cybersecurity è un aspetto fondamentale.

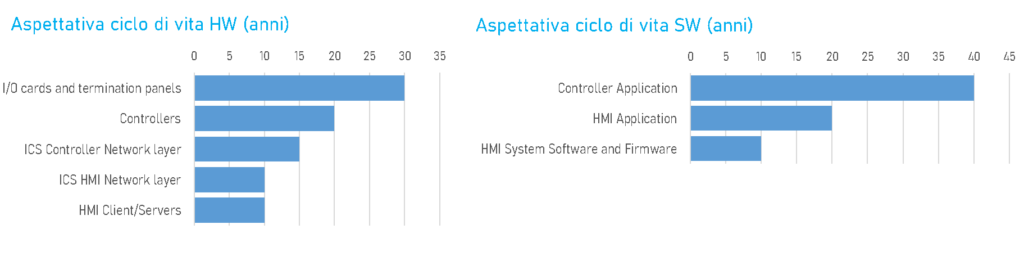
Un tipico ciclo di vita di un sistema di automazione come un PLC, un DCS o uno SCADA è di 10-15 anni; ma guardando lo scenario complessivo alcuni componenti possono arrivare a cicli di durata molto maggiore (figura 1). Inoltre bisogna tenere conto di quando è stata lanciata sul mercato la versione specifica del prodotto che si vuole installare, perché il suo ciclo di vita non parte da quando viene installato ma potrebbe essere iniziato da molto prima. Quindi, può succedere che il sistema di controllo scelto arrivi alla fine del suo ciclo prima di quanto si pensi.

Figura 1. Aspettativa media di durata del ciclo di vita di componenti industriali (fonte: Obsolescence and life cycle management for automation systems, International Association of Oil & Gas Producers)

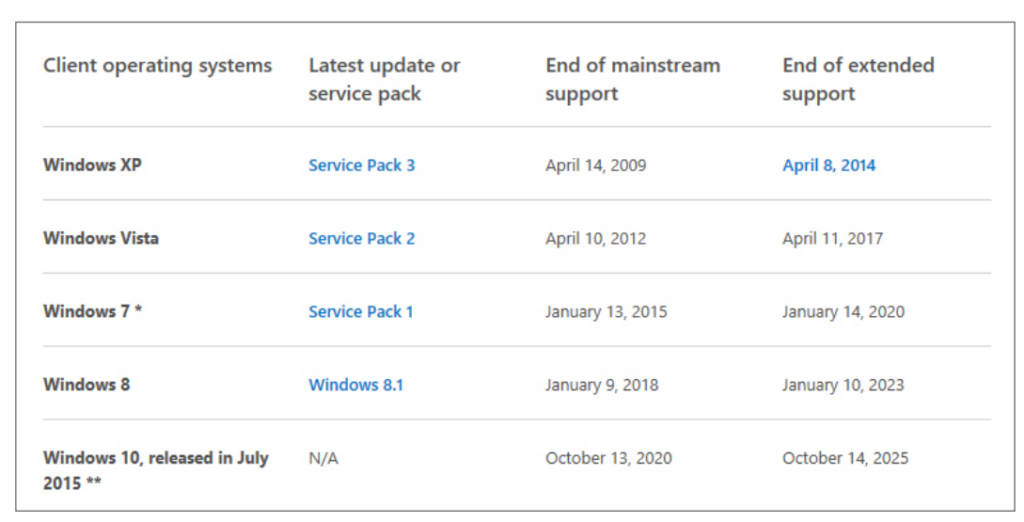
Un altro problema che si presenta nell’impiego di sistemi commerciali è gestire il ciclo di vita del software e dei sistemi “terzi” (come i sistemi operativi Microsoft, figura 2) che hanno una durata inferiore rispetto al ciclo di vita previsto del sistema di automazione. Questo significa che, nel caso dei sistemi operativi Microsoft, il software può essere supportato per circa 10 anni se si tiene conto dell’extended support (quest’ultimo estende la durata del supporto tradizionale e prevede solo il rilascio di patch di sicurezza). Inoltre, bisogna considerare che l’inizio del ciclo di vita del sistema operativo raramente coincide con il lancio di un nuovo prodotto, per cui una delle componenti del sistema può diventare obsoleta anche in breve tempo.

Figura 2. Fine ciclo di vita per i principali sistemi operativi Microsoft

L’aggiornamento del software, inoltre, spesso richiede la sostituzione dell’hardware del PC o del server; e i nuovi HWw E SW dovranno essere compatibili con il software applicativo del sistema di automazione. È facile che prodotti degli anni 2000 siano compatibili solo con Windows XP o richiedano solo connessioni seriali per scaricare i programmi di controllo, attualmente non più presenti tra le periferiche dei PC. La necessità di sostituire o integrare i sistemi obsoleti con nuove tecnologie può quindi richiedere investimenti elevati, competenze specifiche e tempi lunghi.

Per questi motivi l’aggiornamento diventa un fattore non banale ed è comune trovare componenti obsoleti all’interno di un sistema industriale, aspetto che crea importanti limitazioni per l’applicazione di una strategia di cyber security efficace.

I principali rischi sono correlati ai seguenti scenari:

  • Software, protocolli e interfacce vulnerabili: l’emergere di nuove vulnerabilità, anche significative e facilmente sfruttabili, su sistemi non più supportati è una possibilità concreta. Non essendoci più supporto da parte del fornitore, si può provare ad applicare soluzioni di protezione contingenti, ma non è garantito possano avere efficacia completa. In situazioni più eclatanti e ad alto impatto, il fornitore può decidere di rilasciare ugualmente una patch (ad esempio è quanto accaduto da parte di Microsoft per proteggere i sistemi più vecchi dal ransomware WannaCry). Ma anche in questo caso molte aziende non hanno potuto o voluto aggiornare i propri sistemi e così alcuni di questi si sono ritrovati colpiti dal WannaCry anche a distanza di anni dalla sua
  • Risorse di sistema che diventano insufficienti: i sistemi di protezione e monitoraggio che operano attivamente richiedono l’impiego di risorse di sistema che in alcuni casi sono appena sufficienti per far funzionare i servizi di automazione. Una normale attività di analisi o di protezione in ambiente ICT tradizionale, come un Vulnerability Assessment o la scansione estesa di un Antivirus, in un ambiente industriale può tramutarsi nel blocco di uno o più sistemi. L’instabilità in condizioni operative non standard facilita, inoltre, l’efficacia di attacchi cosiddetti di “Denial of Service” (DoS) che mirano a saturare le risorse per rendere inutilizzabili i sistemi colpiti.
  • Problemi di retrocompatibilità dei sistemi di protezione: i sistemi di protezione e raccolta degli eventi di sicurezza evolvono nel tempo. Per far funzionare i prodotti su più versioni di un sistema operativo si devono eseguire test, verifiche e adattamenti che impiegano sforzi significativi. Di conseguenza è normale che un produttore ad un certo punto cessi di garantire la compatibilità con le versioni le più vecchie e così, su alcuni sistemi obsoleti, ci si può trovare di fronte a situazioni in cui gli aggiornamenti delle protezioni possono generare comportamenti anomali o non funzionare del tutto. È quindi sconsigliabile a priori installare le protezioni su sistemi non supportati, in quanto non vi è alcuna garanzia del loro funzionamento corretto. Questo vale anche di fronte all’ipotesi di installare versioni “vecchie” delle protezioni precedentemente supportate, in quanto non è garantito che svolgano adeguatamente la loro funzione (es. che un antivirus riesca ad aggiornare correttamente le firme sulle nuove minacce).

Negli ultimi anni, il mondo ha assistito allo sfruttamento delle vulnerabilità dei sistemi per una serie di attacchi informatici mirati a danneggiare o sabotare le infrastrutture critiche di diversi paesi, come centrali elettriche, reti di trasporto, ospedali e impianti industriali. Questi attacchi sono spesso attribuiti a gruppi sponsorizzati da governi ostili o rivali, che cercano di ottenere vantaggi strategici, politici ed economici. Quanto accaduto negli Stati Uniti nel maggio 2021 dimostra come gli effetti di un attacco cyber possano non solo determinare la chiusura di un oleodotto che rifornisce circa la metà della costa orientale USA ma, indirettamente, arrivare a mettere a rischio la tenuta del tessuto socio-economico di intere aree. La crescita degli attacchi è progressiva, fino a colpire anche settori in precedenza meno attenzionati; lo dimostra ad esempio il settore manifatturiero, che negli ultimi ha visto una crescita significativa degli incidenti cyber.

Non solo: dopo la crescita degli attacchi a fini di estorsione, il cyber spionaggio sugli impianti industriali è recentemente diventato uno strumento sempre più usato nelle guerre tra paesi, sia come strumento di aggressione che di difesa. L’obsolescenza dei sistemi e le poco consolidate pratiche di protezione sono tra i principali vettori che permettono ad attori non autorizzati di entrare negli impianti, rimanendo in ascolto e in attesa senza essere scoperti. Certi attacchi, infatti, rappresentano l’esito di compromissioni verificatesi persino più di un anno prima.

Per arginare i rischi evidenziati, occorre operare su più fronti. A livello delle singole imprese è importante intraprendere programmi che innalzino il livello di sicurezza attraverso, ad esempio:

  • segregazione dei sistemi e controllo dei flussi dati: dove ci sono limitazioni nell’intervenire direttamente sui sistemi interessati, in particolare su quelli obsoleti, lo spazio di manovra non può che spostarsi nel contesto dove sono collocati. È necessario definire strette misure per la segmentazione della rete industriale e il controllo dei flussi dati. Un ruolo chiave è svolto dalla realizzazione della cosiddetta zona demilitarizzata (DMZ) a protezione del perimetro logico dell’impianto;
  • uso di sistemi di protezione “passivi”: le misure di cybersecurity vanno impostate tenendo in considerazione le caratteristiche tipiche del contesto, favorendo ove possibile modalità di analisi “passive” o, comunque, che possano ridurre al minimo il loro impatto sull’insieme delle componenti industriali coinvolte;
  • gestione strutturata del ciclo di vita: una corretta gestione del ciclo di vita delle varie componenti industriali deve includere gli aspetti relativi al “fine ciclo” dei vari elementi, permettendo di effettuare scelte ponderate sull’approccio al loro aggiornamento e rinnovo; in caso l’impianto sia in gestione ad un fornitore, la relazione con quest’ultimo deve essere condotta con attenzione affinché sia un elemento proattivo nella protezione e non diventi, invece, un elemento di continuità con il passato.

Ma le protezioni non bastano. All’emergere di nuove vulnerabilità, infatti, queste sono prontamente sfruttate da attaccanti sempre più capaci e rapidi, prima che sia possibile adeguare le contromisure di sicurezza adottate. È quindi importante anticiparne le mosse, per cui sono richieste capacità di Threat Intelligence che possono contribuire a identificare fonti, modalità e intenzioni degli attacchi informatici, nonché a fornire indicazioni per la loro prevenzione e mitigazione. Per questo negli impianti è in crescita l’adozione di sistemi in grado di fare da collettori dei dati provenienti dai vari dispositivi e di confrontarli con tempestive informazioni sulle vulnerabilità, tecniche e attività degli aggressori informatici, il tutto gestito da competenze specifiche sulla sicurezza delle tecnologie industriali che sempre più vanno a integrarsi nelle strutture tradizionali dei Security Operation Center.

Non solo: l’intelligence può operare su ulteriori e diversi livelli.

A livello strategico, può fornire una visione complessiva delle minacce informatiche e delle loro implicazioni per la sicurezza nazionale e internazionale, nonché delle opportunità di cooperazione tra gli attori coinvolti. A livello tattico può supportare la pianificazione e l’esecuzione di azioni di difesa e di risposta agli attacchi informatici – nonché la valutazione dei loro effetti – oltre a fornire informazioni specifiche e tempestive sulle vulnerabilità, le tecniche e le attività degli aggressori informatici. Questo anche a supporto dell’attività normativa in evoluzione per la creazione di sistemi industriali resilienti e la protezione, in particolare delle, infrastrutture critiche; il tutto con l’obiettivo di rafforzare la cultura complessiva della cybersecurity unitamente alla collaborazione e coordinazione tra gli attori coinvolti, sia a livello nazionale che internazionale, per migliorare le capacità di prevenzione, rilevazione e risposta agli attacchi informatici, contribuendo alla diffusione delle buone pratiche e degli standard di qualità in linea con le attuali sfide del settore industriale.

Articolo a cura di Michele Fabbri

Profilo Autore

Cyber Security Group Director – CISO presso De Nora S.p.A.
Esperto di sicurezza informatica, in oltre 25 anni ha ricoperto varie mansioni all’interno di aziende multinazionali quali Vodafone Italia S.p.A., come ICT Security Manager e Privacy & Data Protection Manager, Eni S.p.A, in qualità di Cyber Security Operations Manager e Saras S.p.A., con il ruolo di CISO.
Contribuisce alla divulgazione della cyber security tramite la sua partecipazione in vari advisory board e pubblicazioni. Attualmente è membro del direttivo dell’associazione AIPSA.

Condividi sui Social Network:

https://www.ictsecuritymagazine.com/articoli/lobsolescenza-tecnologica-degli-impianti-industriali-e-le-sfide-per-la-cybersecurity/


Polycrises are Exhausting Your Security Team: Tips to Navigate the Challenges

Monitoring multiple simultaneous or overlapping crises pose significant challenges for companies and security teams. Organizations face a myriad of potential crises that can unfold rapidly and escalate in unexpected ways. From cyber-attacks and natural disasters to supply chain disruptions, the concept of polycrisis has become a defining feature of the modern security era. The repercussions of these events can rapidly overwhelm a security or intelligence team’s ability to respond efficiently. In such times of perpetual crisis, the ability to navigate through uncertainty and adapt quickly is paramount for ensuring the resilience and continuity of organizations worldwide.

With heightened workloads, difficulties in reallocating resources, a diffusion of focus on strategic priorities, and challenges in coordinating and communicating within the team become the norm.

Navigating through these turbulent times requires a strategic reassessment of how security operations are conducted, with a keen focus on adaptability and foresight.

One of the primary hurdles security teams encounter is the difficulty in effectively monitoring, assessing, and reporting on a polycrisis. The interconnected nature of these crises amplifies their impact, making it crucial for organizations to have comprehensive visibility across their operations. However, traditional monitoring mechanisms often fall short in capturing the intricate web of threats posed by multiple crises, leaving security teams scrambling to keep pace.

Moreover, the reactive nature of many security protocols poses a significant challenge in the face of a polycrisis. Historically, security measures have been designed to respond to singular incidents rather than continuous, evolving threats. As a result, security teams find themselves playing catch-up, perpetually reacting to the latest crisis rather than proactively mitigating risks.

So how does an organization begin to shift their approaches to operate in a world of multiple or rolling crises?

Complexity:

  • Employ advanced analytics and artificial intelligence (AI) and machine learning algorithms to identify patterns, anomalies, and underlying factors across diverse data sources.
  • Collaborate with subject matter experts from various domains, such as geopolitics, economics, social sciences, and technology, to provide multidisciplinary perspectives.
  • Develop scenario-based planning and wargaming exercises to anticipate and prepare for complex crisis situations.  

Data Overload:

  • Implement automated incident response systems to prioritize and streamline the handling of security alerts based on predefined risk criteria.
  • Utilize natural language processing (NLP) techniques to extract actionable insights from unstructured data sources, such as social media feeds and news articles.
  • Employ data visualization tools to see where events are taking place in relation to your business operations, assets, and people.  

Siloed Information:

  • Foster a culture of information sharing and collaboration across departments and teams.
  • Implement enterprise-wide intelligence platforms to capture and disseminate relevant insights and best practices.
  • Establish cross-functional crisis management teams or fusion centers to promote information sharing and coordinated decision-making.  

Rapidly Evolving Threat Landscape:

  • Develop dynamic threat models that adapt in real-time based on evolving threat intelligence and environmental factors.
  • Leverage real-time data streams and advanced analytics to identify emerging threats and patterns as they unfold.
  • Adopt agile and iterative crisis management processes to adapt quickly to rapidly evolving situations.  

Resource Constraints:

  • Explore threat and risk intelligence solutions with advanced monitoring and expert-curated search capabilities without significant upfront time investments saving time to value.
  • Leverage open-source intelligence (OSINT) and publicly available data sources categorized and customized to your organization to help cut through the noise.
  • Collaborate with industry associations, government agencies, or research institutions to share resources and leverage collective intelligence.

By implementing these solutions and continuously adapting to evolving challenges, companies and security teams can enhance their ability to monitor polycrisis proactively and effectively, mitigating risks and safeguarding their interests in an increasingly complex and interconnected world.

Incorporating a tool like Seerist’s risk intelligence platform can support organizations in navigating the complexities of polycrises. Seerist provides advanced threat and risk intelligence solutions that leverages AI, machine learning, and on-the-ground analysts to offer expert-curated insights. This enables security teams to stay ahead of emerging threats, cut through the noise with tailored OSINT data, and collaborate more effectively across functions. By integrating Seerist into its security operations, organizations can enhance its resilience, improve strategic decision-making, and ensure a more proactive stance in managing continuous and evolving crises.

https://www.securitymagazine.com/articles/100704-polycrises-are-exhausting-your-security-team-tips-to-navigate-the-challenges