Aumentano gli attacchi alle aziende: +40% in Italia


Le aziende italiane continuano a essere uno degli obiettivi preferiti dai cybercriminali: secondo il report Data Gathering di CybergON, nel 2023 si è registrato un aumento del 40% degli attacchi rispetto ai 6.000 tentativi per settimana tracciati nel 2022.

La ricerca ha coinvolto 130 aziende di piccole, medie e grandi dimensioni appartenenti a 9 settori merceologici; a partire da questo gruppo, sono stati tracciati 976 asset comprendenti gli strumenti informatici, sia hardware che software, utili al funzionamento efficace di un’azienda.

Il monitoraggio di CybergON evidenzia una tendenza degli asset crescente direttamente proporzionale alla dimensione dell’organizzazione: le grandi realtà hanno il doppio degli asset delle medie imprese e il quadruplo di quelli delle piccole aziende.

L’andamento del cybercrimine è aumentato gradualmente nel corso dell’anno, con due picchi registrati ad aprile e a settembre corrispondenti alle vacanze pasquali e al ritorno dei lavoratori nelle aziende.

Pixabay

Analizzando i dati sugli IP bloccati, è emerso che Azerbaigian, Russia e Olanda sono stati i Paesi da cui è partita la maggior parte degli attacchi, con numerose connessioni pericolose. Per le grandi aziende sono stati rilevati 6.000 tentativi di attacchi per settimana da parte di Olanda, Russia e Bulgaria, seguiti dai 5.865 dell’Azerbaigian. Nella lista delle nazioni più pericolose si aggiungono anche Hong Kong e Israele.

Riguardo le medie aziende, si parla di 200 tentativi di attacchi per settimana sempre da Olanda, Russia e Bulgaria, mentre per le piccole imprese il numero si riduce a un massimo di 27 tentativi settimanali, soprattutto da parte di Cina, Stati Uniti, Olanda, Emirati Arabi e Svizzera.

Le vulnerabilità sono state determinanti per consentire l’accesso dei cybercriminali ai sistemi, con le piccole aziende che hanno registrato 146 bug a rischio alto, seguite dalle grandi con 109 e dalle medie con 89. La classifica rimane invariata quando si parla di vulnerabilità critiche: per le piccole imprese si parla di 237 bug, 188 nelle grandi aziende e 98 nelle medie imprese.

Riguardo i tempi di remediation dei bug, la media si attesta sui 103 giorni per le vulnerabilità a rischio alto e sui 148 per quelle a rischio critico.

“A fronte di questa analisi possiamo affermare che si sta tracciando un nuovo panorama con le più recenti tecniche di attacco e con Paesi che stanno acquisendo sempre più rilevanza nella geografia del crimine informatico” ha commentato Elisa Ballerio, Marketing Director di CybergON. “Per l’anno in corso stiamo già osservando come stia prendendo piede, tra gli attaccanti, il trend dell’infostealer. Si tratta di malware progettati per rubare dati sensibili da dispositivi compromessi, incluse credenziali di accesso e documenti che operano tramite e-mail infette, download dannosi o sfruttando vulnerabilità del software. Una volta installati, raccolgono informazioni e le inviano a server controllati dai cybercriminali. Gli attacchi DDoS, in aggiunta, continuano a occupare un posto predominante nello scenario del cybercrime diventando più frequenti e sofisticati”.

Condividi l’articolo


Articoli correlati

Altro in questa categoria


https://www.securityinfo.it/2024/05/08/aumentano-gli-attacchi-alle-aziende-40-in-italia/?utm_source=rss&utm_medium=rss&utm_campaign=aumentano-gli-attacchi-alle-aziende-40-in-italia


“Selfie spoofing” scams are growing in popularity

A report from Socure found an increase in “selfie spoofing” scams, or scams in which a fraud actor takes a target’s selfie in order to authenticate a stolen identity and open fraudulent accounts. The report found that selfie spoofing accounted for 20% of identification document fraud in 2023, preceded only by tampered headshots (21%) and document image-of-image techniques (63%). Selfie spoofing can be easily and quickly deployed due to the accessibility of social media profiles, providing a simple avenue for fraudsters to carry out identity fraud. 

Senior citizens (aged 50 years and above) are the most common target of selfie spoofing scams. Around 49% of selfie spoofing scams target senior citizens, making this demographic four times as likely to experience a selfie spoofing incident. According to the report, this is likely due to a couple of factors. Firstly, senior citizens typically have greater assets than younger demographics, making them a more appealing target to a fraud actor. Furthermore, senior citizens are often not as tech savvy, meaning they may be more susceptible to scams. 

https://www.securitymagazine.com/articles/100637-selfie-spoofing-scams-are-growing-in-popularity


L’indispensabile rivoluzione nell’Incident Response: Automazione per una Risposta più Efficace

Da qualche tempo il mondo della sicurezza informatica ha subito una trasformazione significativa.

Il cambiamento, come sempre nella storia dell’uomo risulta guidato dalla crescente complessità degli attacchi informatici. In questo contesto, l’automazione ha dimostrato di essere un’arma potente nel combattere tali minacce, soprattutto nell’ambito della risposta agli incidenti. L’integrazione di processi finemente automatizzati nella gestione degli incidenti non solo migliora sensibilmente l’efficienza, ma offre anche una maggiore capacità di risposta e un controllo più rapido sulle violazioni della sicurezza.

In questo articolo, come Indiana Jones all’interno di un templio maledetto esploreremo il ruolo fondamentale dell’automazione nel fornire visibilità, contenere, ed eradicare.

Senza dimenticarci dei nostri amici IT Manager o CISO; infatti da qualche parte nell’articolo si nascondono diverse indicazioni fondamentali durante la gestione di un incident che non possono essere ignorati da chi ricopre tale ruolo.

Visibilità potenziata attraverso l’Automazione

La visibilità è il primo passo cruciale per affrontare un incidente di sicurezza.

Senza una comprensione chiara di ciò che sta accadendo nei sistemi e nelle reti, è impossibile rispondere in modo efficace. Qui entra in gioco il fondamentale fattore portato dall’automazione la velocità e l’integrazione.

Strumenti di rilevamento delle minacce e sistemi di monitoraggio continuo possono identificare anomalie e comportamenti sospetti in tempo reale, fornendo agli esperti di sicurezza visibilità immediata sulle attività malevole, ma tutto questo può essere abbastanza? Possiamo fidarci ciecamente dei software di difesa commerciali che gli attaccanti studiano minuziosamente al fine di continuare a compromettere infrastrutture informatiche più o meno complesse?

No. Sennò non lavorerei nel campo dell’incident response.

L’automation dedicata alle attività di risposta agli incidenti infatti si concentra su tutti quegli aspetti in cui non vi è certezza ne standard, infatti, se un software di sicurezza come potrebbe essere un HIDS o un EDR può vantare sia il tempo che la cura da parte di chi lo installa; un software scritto per incident response può solo sognarsi questo tipo di lusso.

Infatti l’obbiettivo è molto simile a quello di un malware, come le funzionalità d’altronde. Senza però lo scudo di firme digitali o whitelist assicurate nei sistemi dove opera, dove spesso, regna il caos; non è infatti difficile trovarsi ad eseguire questo tipo di automazioni in Virtual Machines scollegate dalla rete con uno o più EDR che non aspettano altro di identificare e bloccare software che ha l’obbiettivo di raccogliere quanti più artefatti e dati possibili.

Il tema visibilità risulta centrale, infatti, uno strumento completo per il triage di un endpoint infetto non si ferma all’estrazione di artefatti comuni come UsnJ, MFT, Shimcache e via dicendo; ma esegue DUMP di LSASS.exe, ricerca keywords all’interno del filesystem per trovare credenziali salvate su file o chiavi di registro in modo non sicuro e molto altro ancora!

Per erogare un servizio di Incident Response sublime è necessario conoscere le tecniche dell’attaccante, ed utilizzarle per ottenere la stessa o maggiore visibilità sui sistemi da esso compromessi. Velocemente; soprattutto nel caso in cui l’attaccante sia ancora collegato sui sistemi e non abbia cominciato fasi distruttive come la cifratura dei files o peggio, dei VMDK.

Contenimento Pronto e Deciso

Una volta estratti gli artefatti ed individuata l’attività sospetta, è essenziale agire prontamente per contenere il danno potenziale. L’automazione gioca un ruolo cruciale in questo processo, consentendo la messa in quarantena rapida dei sistemi compromessi o la disattivazione degli account compromessi.

Messaggio per gli “Incident response team” che leggono: bisogna essere pronti con automation vendor agnostic. In ogni caso. Non c’è tempo da perdere quando veniamo chiamati ad operare.

Oltre ad un’abile ricognizione è quindi fondamentale applicare alle nostre custom automation un’intelligenza in grado di rispondere con determinate pattern attive in caso di rilevazioni critiche.

Gli algoritmi di intelligenza artificiale remota possono identificare i pattern delle minacce e attivare automaticamente le politiche di sicurezza necessarie per bloccare l’accesso non autorizzato e limitare la propagazione dell’attacco. Ciò riduce drasticamente il tempo di risposta e limita l’impatto degli incidenti sulla continuità operativa, ovviamente questo tipo di implementazione non risulta facilissimo, tuttavia, è doveroso farla.

Alcuni esempi di automazioni utili al contenimento ed eradication possono essere:

  • Filesystem Watcher Defense
    • Binario che monitora costantemente le modifiche al filesystem tramite le librerie NetFramework “FilesystemWatcher”. In sintesi, è una componente utile per creare applicazioni reattive che possono monitorare e rispondere dinamicamente ai cambiamenti nel sistema file, contribuendo così a migliorare l’automazione e l’efficienza delle operazioni di gestione dei file.
    • Le applicazioni pratiche possono essere: antiransomware, filechange content analysis, reactive remediation basata sul monitoraggio combinato di filesystem e processi.
  • MemDump Analysis
    • Qui volatility viene in nostro aiuto nel fornirci il framework su cui sviluppare detection di pattern malevole in memoria. Non mi dilungo oltre, sky is the limit.
  • Filesystem Scan con yara
    • Chi lavora nella sicurezza lo sa, non esiste vendor che abbia tutte le firme nei propri database. Chi gestisce incidenti 24/7 però può vantare di averne uno “bello aggiornato”. Perchè non sfruttarlo per generare delle Yara rules da utilizzare in scansioni mirate durante la raccolta di artefatti per il triage? Multithreading is the way! E poi al cliente compromesso non dispiacerà se utilizzate i suoi sistemi al 100% delle risorse per qualche minuto in questi casi, dico bene?

Eradicazione delle Minacce con Precisione

Una volta contenuta la situazione, è essenziale procedere con l’eradicazione delle minacce per ripristinare completamente l’integrità del sistema. L’automazione permette di eseguire rapidamente scansioni approfondite dei sistemi compromessi per individuare e rimuovere completamente il malware persistente come backdoor o altre componenti dannose.

Gli strumenti di automazione più avanzati possono anche identificare e mitigare le vulnerabilità di sicurezza che potrebbero aver consentito agli attaccanti di infiltrarsi inizialmente nel sistema. Non è sempre possibile eseguire patching, ma in casi di crisi per mantenere attivi servizi critici riducendo al minimo il rischio di lateral movement risulta fondamentale poter implementare cross hardening automatizzato.

Questo processo di eradicazione, se combinato come detto in precedenza, alla creazione di regole sartoriali all’incidente in gestione riduce al minimo il rischio di una reinfezione e ripristina la sicurezza dei sistemi in modo efficiente.

Efiltrazione e notifica al garante

Infine, l’automazione svolge un ruolo cruciale nell’affrontare la fase post-incidente, inclusa l’analisi delle attività inerenti l’esfiltrazione dei dati. Gli strumenti automatizzati possono tracciare e valutare il flusso di dati per identificare eventuali tentativi di estrarre informazioni sensibili dai sistemi compromessi. Inoltre, le automation per l’incident response possono essere configurate per notificare automaticamente chi sta eseguendo le analisi circa la presenza di strumenti comunemente utilizzati dai Threat Actor al fine dell’exfiltration, in questo modo sarà più facile identificare l’entità del danno subito dal cliente.

Una volta ottenuti i giusti elementi è possibile procedere con implementazioni alle notifiche preliminari al garante con tutte le rilevazioni e contromisure / attività messe in atto dall’azienda colpita. Ricordate si hanno solo 72 ore dopo la scoperta dell’incidente per eseguire il primo atto di notifica preliminare, gli elementi chiave che rendono necessaria ed indispensabile la pratica sono:

  • Indisponibilità del dato
  • Perdita di confidenzialità
  • Perdita di integrità

In conclusione, l’automazione sta rivoluzionando il modo in cui affrontiamo gli incidenti di sicurezza informatica. Fornendo visibilità immediata, velocità di risposta senza precedenti e precisione nell’eradicazione delle minacce, l’automazione si sta dimostrando un alleato indispensabile nella lotta contro le minacce informatiche sempre più sofisticate. Tuttavia, è importante sottolineare che l’automazione non sostituisce completamente l’esperienza umana e il discernimento, ma piuttosto ne potenzia le capacità, consentendo agli esperti di concentrarsi su compiti ad alto valore aggiunto. Investire nell’automazione della risposta agli incidenti è essenziale per garantire una difesa informatica robusta e resiliente nell’era digitale.

Stay safe.

Facciamo un gioco…

Lvuzurxsz! Xjxvz nr riw lv lz jxyziizj zyanrz lj mklnazj evkrprzj, zlxmwnx aj bmch lm eqflmax snxlc qj oxmnhxqn jc otqlxne?

Articolo a cura di Nicolas Fasolo

Profilo Autore

Nicolas Fasolo è il Team Leader del Incident Response Team di Yarix (Vargroup). Nel tempo libero lavora come “Security Researcher” e “Malware Developer” indipendente con una passione sfrenata per l’analisi del malware. Durante il suo percorso formativo di certificazione Master CEH ha ottenuto il Top 1 al mondo per il “Quarter 4 Dicembre 2021”. Autore di “Cybersecurity Podcast” e “Cybersecurity Warrior”.

Condividi sui Social Network:

https://www.ictsecuritymagazine.com/articoli/lindispensabile-rivoluzione-nellincident-response-automazione-per-una-risposta-piu-efficace/


It May be Time to Review Your Cyber Hygiene

The backbone of any connected security system — and especially a super-connected smart building — is the network, which is increasingly vulnerable the more things you connect to it. That is why the cyber-stance, or cyber-hygiene, a facility puts in place is absolutely critical to keeping things running smoothly and helping protect against damaging hacking attacks. 

A recent report by ExtraHop found that some cyber leaders may be a little too confident in their organization’s cybersecurity posture. In the report, 88 percent of cyber leaders expressed confidence in their organization’s risk management abilities, yet the report also found that many organizations are unprepared to mitigate risk — largely due to poor cyber hygiene and inadequate budgets. 

Poor cyber hygiene is particularly problematic of cyber risk in the agricultural, educational and government sectors, with 51 percent of respondents reporting that more than half of their organization’s cyber events are related to poor cyber hygiene, and one out of two organizations deploying one or more insecure network protocols that malicious actors have been known to leverage. 

Equally concerning, A report by Bitsight and Diligent, which received contributions from 4,000 medium to large-sized companies across the globe, found that only 5 percent of businesses have a cyber expert as a member of staff. 

“It takes a village to perform well in cybersecurity,” said Ken Dunham, cyber threat director at Qualys Threat Research Unit about the report. “It’s not enough to only elevate the visibility and authority of the CISO, or have a board involved in cybersecurity matters. It takes an entire ecosystem and culture of an organization, united and aligned, with clear focus and priorities, to achieve cybersecurity maturity manifested in operations.”

Dunham also gave this practical advice: “Pillars of success frequently involve top-down leadership that understands this vision and what risk really is, and how to unify, empower, and align global disparate teams. Organizationally everyone is involved from the board down to separate mature teams of risk, audit, SecOps, and others, all working together in regulatory, compliance, and cybersecurity framework-driven operations to ensure efficiency and efficacy in outcomes. Once an organization is able to become process driven, instead of people being solely dependent on SecOps, the governance risk management process can be automated and optimized to prioritize risk with measurable results, compared to those that do not implement these core components of a risk management program.”

Cyber hygiene is going to become even more of a critical need the more AI and generative AI become involved in business life.

The AI Security & Governance Report released by Immuta found that 80 percent of data experts see AI as increasing data security challenges. What’s more, 55 percent say the possibility that sensitive information may be inadvertently exposed by large language models (LLMs) is their greatest concern, while 52 percent are worried that sensitive information may be exposed to LLMs through user prompts.

Even more — 57 percent — reported an increase in AI-driven attacks in the last year. 

The good news about AI is it may be helping increase both the sense of urgency companies feel when it comes to preparing for cyber threats and the tools they have to do so.

For example, a recent report from Netacea  found that 100 percent of security leaders considered their organizations’ security stack to be improved since the adoption of AI tools. 

However, the other side of that coin is the majority of those surveyed also expect that AI will become a more prevalent tool in the tool kit of cybercriminals, with 93 percent predicting that AI cyberattacks will become a daily occurrence by 2025. 

There are also challenges from within companies who are trying to improve their cyber-stance. A report from LogRhythm  found that while 95 percent of organizations were altering their cybersecurity strategies there is a gap in efficient communication between security teams and non-security leaders: 44 percent of non-security leaders do not understand the regulations that the organization must comply with, and 59 percent have difficulty explaining the importance of specific security systems to non-security stakeholders. 

With near daily cyber-attacks making the news these days, it is more critical than ever to make sure all the stakeholders in your organization know both the “what’s” and the “why’s” of the policies, as well as to make sure those policies are as up-to-date as possible. 

As Dunham explained, commenting on the recent nation-state cyberattack at  MITRE Corporation, “The race to patch against vulnerabilities and de-risk is real in a world where adversaries are lying in wait to attack upon opportunity. In 2024, companies must apply due diligence at every step of the entire lifecycle of threat and vulnerability management (TVM) lifecycle, with the ability to rapidly prioritize patching, workarounds and other forms of remediation, when justified by escalating threats. The need for strong cyber threat intelligence (CTI) driven programs has never been stronger to proactively reduce risk, quickly detect and remove threats as fast as possible in the war against cyber threats. Excellence in SecOps includes lowering the impact of an incident by ensuring controls internally to identify and remove threats quickly as well as reduce the blast radius when an attack occurs.”

https://www.securitymagazine.com/articles/100646-it-may-be-time-to-review-your-cyber-hygiene


Vulnerability exploitation on the rise

Popular threat actors utilize a variety of vulnerabilities to access companies’ sensitive information. Visa analyzed payment-related fraud and data breaches throughout 2023. According to the report, the most impactful ransomware attack of 2023 affected an estimated 2,620 organizations along with 77.2 million individuals whose PII was breached across the infiltrated organizations.

The ransomware threat group known as CL0P claimed responsibility for the attack on 6 June 2023, but researchers for the report suspect that CL0P began leveraging a zero-day vulnerability (CVE-2023-34362) as early as July 2021. This followed CL0P’s deployment of ransomware on 31 January 2023 exploiting a vulnerability (CVE-2023-0669) in a different file transfer software, which allowed threat actors to obtain data from 130 organizations.

The targeted file transfer service was a common vendor across numerous merchants including financial services and institutions, retail, education, healthcare as well as other merchant sectors and industries.

Additionally, the report identified North America as the most impacted region in terms of ransomware/data breach incidents impacting the payments ecosystem. The North America region experienced nearly three times the number of ransomware attacks compared to the Europe region, which experienced the second highest level of incidents based on Visa PFD ransomware incident tracking.

Find out more here.

https://www.securitymagazine.com/articles/100639-vulnerability-exploitation-on-the-rise


Data breaches increased throughout 2023

With advancing technology, companies must always be prepared for the potential of a data breach. Threat actors often work nonstop while trying to gain access to sensitive company data, meaning security leaders need to work around the clock to keep themselves safe. Data breaches in 2023 were analyzed in a recent report by the Identity Theft Resource Center.

According to this report, U.S. data compromises surpassed 3,000 over the course of 2023. The total number of data breaches, exposures, leaks and “unspecified events” reached 3,205, impacting an estimated 353,027,892 victims, including those affected by multiple compromises. The 2023 compromises represent a 78% increase over the previous year and a 72% increase from the previous all-time high number of compromises set in 2021.

More than 9% of the U.S. publicly traded companies issued a data breach notice in 2023, according to the report. Public companies accounted for 40% of all data compromise victims. Publicly traded companies withheld information about an attack in 47% of notices compared to 46% of private companies, government agencies, education institutions and nonprofit organizations.

Physical breaches are down 65% since 2018. The estimated number of victims impacted represents a 16% decrease 2022, when more than half of the total annual victim count was related to three breaches announced late in the previous year. Three industries reported more than double the number of compromises compared to 2022: healthcare, financial services and transportation. Healthcare led all industries in terms of the number of reported compromises in each of the past five years, but utilities companies led in the estimated number of victims in 2023.

Find out more here.

https://www.securitymagazine.com/articles/100638-data-breaches-increased-throughout-2023


Monitor Organizational Risks to Protect Yourself and Your Employees

Organizations have to consider a number of factors when it comes to keeping themselves and their employees safe. Severe weather, crime, economic and political unrest all pose risks to an organization. Some, such as severe weather and crime, increase the likelihood of exterior threats, while factors such as civil unrest may increase the risk of insider threats. 

OnSolve’s recent “2024 Global Risk Impact Report” analyzes some of the recent and prevalent risks facing businesses today. The report looked at four types of physical threats: floods, theft, geopolitical conflict and civil unrest. According to the report, the majority of leaders surveyed said that their agency isn’t taking a proactive approach to identifying and managing risk. 

Thirty-nine percent of executives who say their organization experienced a physical threat in the last 24 months and 43% of federal leaders found that physical threats most affected employee safety. The report found that local leaders and emergency managers ranked public and employee safety first when asked what areas were most impacted by unexpected physical threats. For executives, the other areas impacted the most were supply chain (38%) and employee confidence (34%), while federal leaders said the top areas impacted by these threats were compliance (37%) and agency reputation (35%). 

The report found that sixty-three percent of executives and 51% of federal leaders said their organization or agency experienced unanticipated impacts “most of the time” or “always” as a result of the physical threats they experienced in the past 24 months. Twenty-six percent of state and local leaders said there were unanticipated impacts on their agency “always” or “most of the time” when they indirectly experienced threats or hazards.

According to the report, 72% of state and local leaders surveyed said crime poses the biggest risk to response and recovery in 2024. However, the report found that 26% of executives and 35% of federal leaders surveyed said crime poses the biggest risk to resilience in 2024.

The report found that 36% of executives surveyed said natural disasters and infrastructure/technology failures pose the biggest risk to their organization in 2024. Thirty-nine percent of federal leaders surveyed said infrastructure/ technology failures and transportation accidents pose the biggest risk to

According to the report, 56% of executives and 53% of federal leaders said their top priority is preparing for a physical threat crisis that puts employee safety or operations at risk. However, 45% of executives have a mitigation plan in place for natural disasters, even though it’s the top physical threat on their radar for 2024. Likewise, 72% of state and local leaders say the biggest risk in 2024 is crime, yet 63% have a mitigation plan in place for this threat.

The report found that 28% of executives and 22% of federal leaders say that threat detection, real-time intelligence and alerts have the greatest potential to help improve their resilience program. A similar percentage of executives (17%) and state and local leaders (18%) believe incident/task management will help, while 27% of federal leaders think historical threat data reporting/analysis holds the most promise when it comes to improving resilience.

The report included the following recommendations to protect employees from risks:

  • Evaluate your current resilience program. 
  • Take a hard look at the results of your evaluation and take note of the biggest barriers to being proactive. 
  • Use historical data to plan and prepare for physical threats and the unanticipated outcomes.
  • Invest in technology that enables you to be proactive and detect threats early. 
  • Build the right framework to accelerate discovery. 

No matter what the threat is, organizations need to be clear while communicating to their employees. A lack of transparency leads to a lack of trust among employees, which can lead to a number of issues in the event of an emergency. While developing a strong resilience program, keep employees involved in the process.

https://www.securitymagazine.com/articles/100647-monitor-organizational-risks-to-protect-yourself-and-your-employees


Ransomware mastermind LockBitSupp reveled in his anonymity—now he’s been ID’d

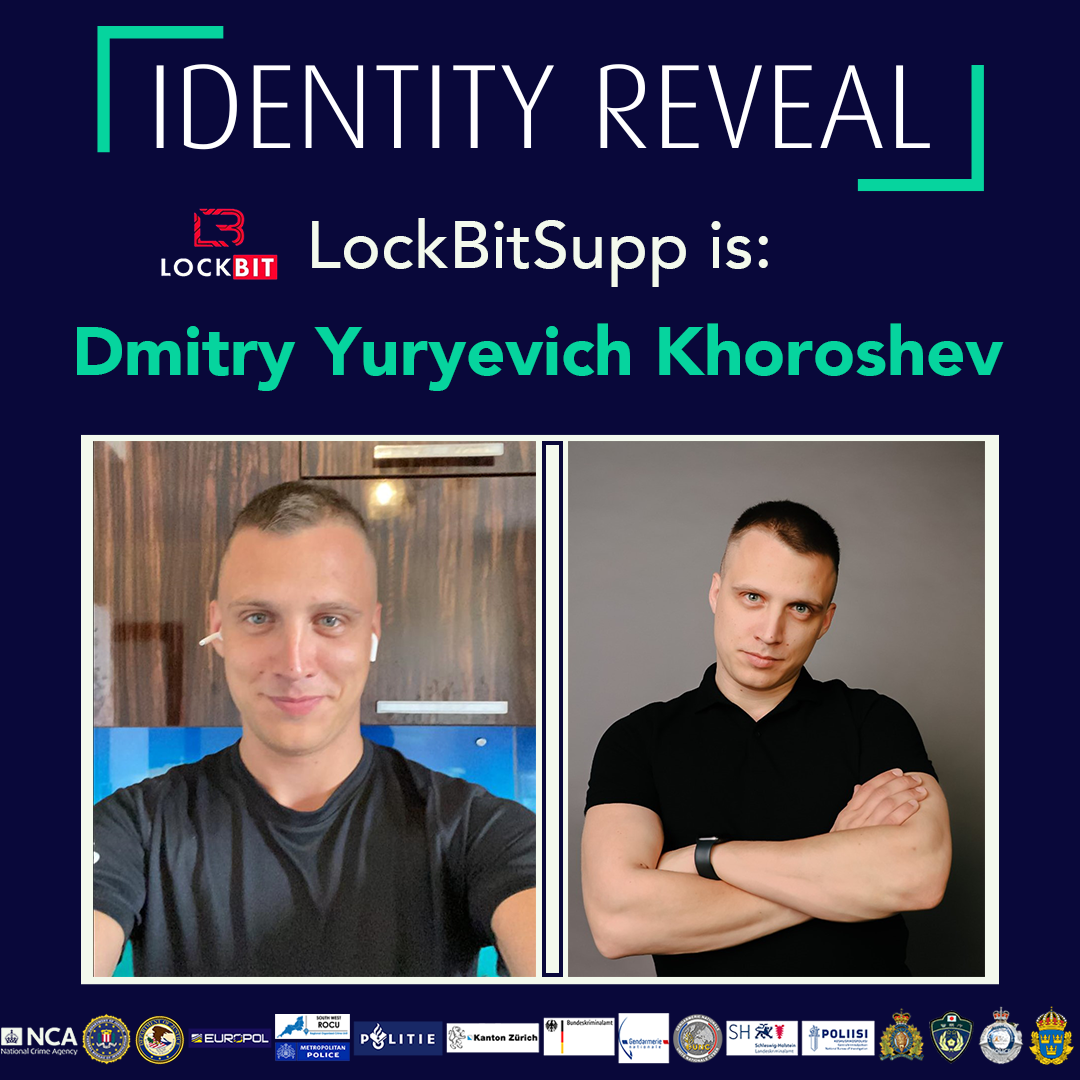
Dmitry Yuryevich Khoroshev, aka LockBitSupp
Enlarge / Dmitry Yuryevich Khoroshev, aka LockBitSupp
UK National Crime Agency

Since at least 2019, a shadowy figure hiding behind several pseudonyms has publicly gloated for extorting millions of dollars from thousands of victims he and his associates had hacked. Now, for the first time, “LockBitSupp” has been unmasked by an international law enforcement team, and a $10 million bounty has been placed for his arrest.

In an indictment unsealed Tuesday, US federal prosecutors unmasked the flamboyant persona as Dmitry Yuryevich Khoroshev, a 31-year-old Russian national. Prosecutors said that during his five years at the helm of LockBit—one of the most prolific ransomware groups—Khoroshev and his subordinates have extorted $500 million from some 2,500 victims, roughly 1,800 of which were located in the US. His cut of the revenue was allegedly about $100 million.

Damage in the billions of dollars

“Beyond ransom payments and demands, LockBit attacks also severely disrupted their victims’ operations, causing lost revenue and expenses associated with incident response and recovery,” federal prosecutors wrote. “With these losses included, LockBit caused damage around the world totaling billions of US dollars. Moreover, the data Khoroshev and his LockBit affiliate co-conspirators stole—containing highly sensitive organizational and personal information—remained unsecure and compromised in perpetuity, notwithstanding Khoroshev’s and his co-conspirators’ false promises to the contrary.”

The indictment charges the Russian national with one count of conspiracy to commit fraud, extortion, and related activity in connection with computers, one count of conspiracy to commit wire fraud, eight counts of intentional damage to a protected computer, eight counts of extortion in relation to confidential information from a protected computer, and eight counts of extortion in relation to damage to a protected computer. If convicted, Khoroshev faces a maximum penalty of 185 years in prison.

In addition to the indictment, officials in the US Treasury Department—along with counterparts in the UK and Australia—announced sanctions against Khoroshev. Among other things, the US sanctions allow officials to impose civil penalties on any US person who makes or facilitates payments to the LockBit group. The US State Department also announced a $10 million reward for any information leading to Khoroshev’s arrest and or conviction.

Rooting out LockBit

Tuesday’s actions come 11 weeks after law enforcement agencies in the US and 10 other countries struck a major blow to the infrastructure LockBit members used to operate their ransomware-as-a-service enterprise. Images federal authorities posted to the dark web site where LockBit named and shamed victims indicated they had taken control of /etc/shadow, a Linux file that stores cryptographically hashed passwords. The file, among the most security-sensitive ones in Linux, can be accessed only by a user with root, the highest level of system privileges.

In all, the authorities said in February, they seized control of 14,000 LockBit-associated accounts and 34 servers located in the Netherlands, Germany, Finland, France, Switzerland, Australia, the US, and the UK. Two LockBit suspects were arrested in Poland and Ukraine, and five indictments and three arrest warrants were issued. The authorities also froze 200 cryptocurrency accounts linked to the ransomware operation. The UK’s National Crime Agency on Tuesday said the number of active LockBit affiliates has fallen from 114 to 69 since the February action, named Operation Cronos.

In mid-March, an Ontario, Canada, man convicted on charges for working for LockBit was sentenced to four years in prison. Mikhail Vasiliev, 33 years old at the time of sentencing, was arrested in November 2022 and charged with conspiring to infect protected computers with ransomware and sending ransom demands to victims. He pleaded guilty in February to eight counts of cyber extortion, mischief, and weapons charges.

The real-world identity of Khoroshev’s LockBitSupp alter ego has been hotly sought after for years. LockBitSupp thrived on his anonymity in frequent posts to Russian-speaking hacking forums, where he boasted about the prowess and acumen of his work. At one point, he promised a $10 million reward to anyone who revealed his identity. After February’s operation taking down much of the LockBit infrastructure, prosecutors hinted that they knew who LockBitSupp was but stopped short of naming him.

LockBit has operated since at least 2019 and has also been known under the name “ABCD” in the past. Within three years of its founding, the group’s malware was the most widely circulating ransomware. Like most of its peers, LockBit has operated under what’s known as ransomware-as-a-service, in which it provides software and infrastructure to affiliates who use it to do the actual hacking. LockBit and the affiliates then divide any resulting revenue.

Story updated to correct Khoroshev’s age. Initially the State Department said his date of birth was 17 April 1973. Later, the agency said it was 17 April 1993.

https://arstechnica.com/?p=2022656


Faulty valve scuttles Starliner’s first crew launch

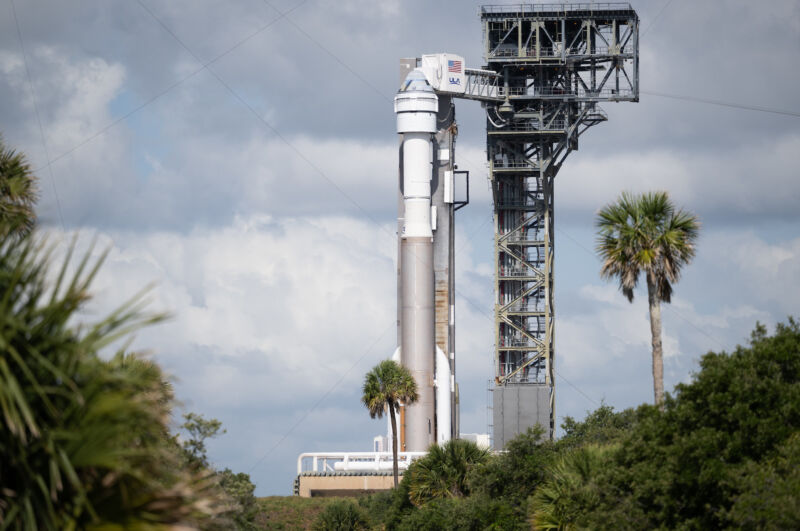
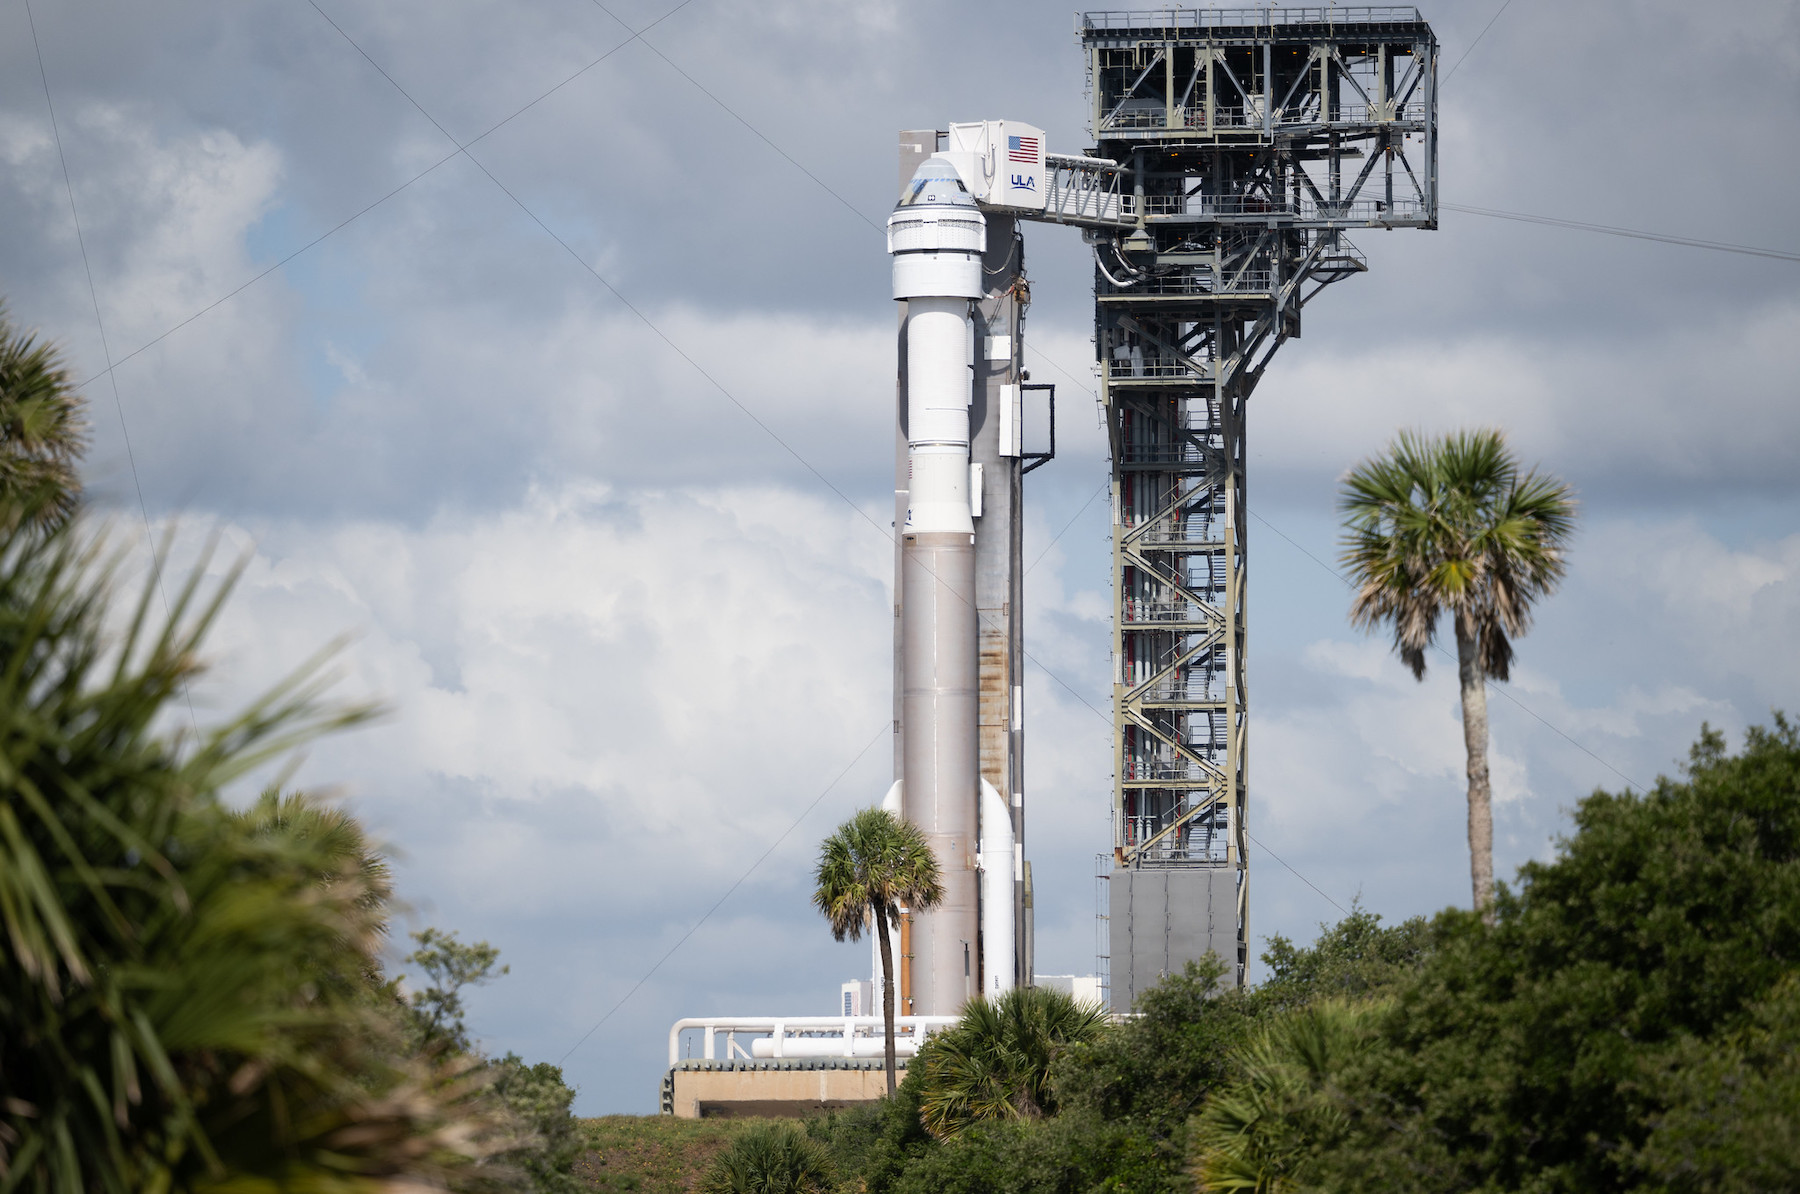
The Atlas V rocket and Starliner spacecraft on their launch pad Monday.
Enlarge / The Atlas V rocket and Starliner spacecraft on their launch pad Monday.

Astronauts Butch Wilmore and Suni Williams climbed into their seats inside Boeing’s Starliner spacecraft Monday night in Florida, but trouble with the capsule’s Atlas V rocket kept the commercial ship’s long-delayed crew test flight on the ground.

Around two hours before launch time, shortly after 8:30 pm EDT (00:30 UTC), United Launch Alliance’s launch team stopped the countdown. “The engineering team has evaluated, the vehicle is not in a configuration where we can proceed with flight today,” said Doug Lebo, ULA’s launch conductor.

The culprit was a misbehaving valve on the rocket’s Centaur upper stage, which has two RL10 engines fed by super-cold liquid hydrogen and liquid oxygen propellants.

“We saw a self-regulating valve on the LOX (liquid oxygen) side had a bit of a buzz; it was moving in a strange behavior,” said Steve Stich, NASA’s commercial crew program manager. “The flight rules had been laid out for this flight ahead of time. With the crew at the launch pad, the proper action was to scrub.”

The next opportunity to launch Starliner on its first crew test flight will be Friday night at 9 pm EDT (01:00 UTC Saturday). NASA announced overnight that officials decided to skip a launch opportunity Tuesday night to allow engineers more time to study the valve problem and decide whether they need to replace it.

Work ahead

Everything else was going smoothly in the countdown Monday night. This mission will also be the first time astronauts have flown on ULA’s Atlas V rocket, which has logged 99 successful flights since 2002. It is the culmination of nearly a decade-and-a-half of development by Boeing, which has a $4.2 billion contract with NASA to ready Starliner for crew missions, then carry out six long-duration crew ferry flights to and from the International Space Station.

This crew test flight will last at least eight days, taking Wilmore and Williams to the space station to verify Starliner’s readiness for operational missions. Once Starliner flies, NASA will have two human-rated spacecraft on contract. SpaceX’s Crew Dragon has been in service since 2020.

When officials scrubbed Monday night’s launch attempt, Wilmore and Williams were already aboard the Starliner spacecraft on top of the Atlas V rocket at Cape Canaveral Space Force Station, Florida. The Boeing and ULA support team helped them out of the capsule and drove them back to crew quarters at the nearby Kennedy Space Center to wait for the next launch attempt.

“I promised Butch and Suni a boring evening,” said Tory Bruno, ULA’s CEO. “I didn’t mean for it to be quite this boring, but we’re going to follow our rules, and we’re going to make sure that the crew is safe.”

When the next launch attempt actually occurs depends on whether ULA engineers determine they can resolve the problem without rolling the Atlas V rocket back to its hangar for repairs.

The valve in question vents gas from the liquid oxygen tank on the Centaur upper stage to maintain the tank at proper pressures. This is important for two reasons. The tank needs to be at the correct pressure for the RL10 engines to receive propellant during the flight, and the Centaur upper stage itself has ultra-thin walls to reduce weight, and requires pressure to maintain structural integrity.

https://arstechnica.com/?p=2022345


Cuckoo, l’infostealer persistente che colpisce macOS


A fine aprile i ricercatori di Kandji, piattaforma per la gestione e la sicurezza dei dispositivi Apple, ha individuato Cuckoo, un malware che colpisce i dispositivi macOS.

Cuckoo si presenta come un infostealer che colleziona diverse informazioni sul dispositivo colpito, ma ha anche dimostrato capacità di mantenere la persistenza sui sistemi, una caratteristica tipica degli spyware. Dopo l’installazione, il malware crea una copia di se stesso e si salva in una cartella nella directory home dell’utente.

In seguito, Cuckoo effettua l’escalation dei privilegi mostrando un prompt che invita l’utente a inserire la sua password. Il popup non chiede esplicitamente la password del sistema, ma richiede l’accesso alle impostazioni di sistema.

Tra i dati raccolti ci sono i preferiti, i cookie e la cronologia di Safari, le informazioni contenute nella directory Keychain, come password e dati sull’account, e le note salvate. Il malware cerca anche file di vario tipo sul Desktop e nella cartella Documenti, come documenti .pdf, .rtf e .txt, immagini .jpg e file .sql e .ovpn. Cuckoo può inoltre effettuare screenshot dello schermo e inviarlo al server C2 degli attaccanti.

apple mac

Pixabay

Cuckoo è in grado di colpire sia i device macOS basati su Intel che su Arm e viene distribuito come binario su siti quali dumpmedia[.]com, tunesolo[.]com, fonedog[.]com, tunesfun[.]com e tunefab[.]com, spacciandosi per un’applicazione per scaricare musica dai servizi di streaming e convertire le tracce in MP3.

Un’altra caratteristica del malware è che, una volta scaricato e installato sul dispositivo, prima di proseguire con le attività malevole controlla se il dispositivo è in lingua armena, bielorussa, kazaka, russa o ucraina e, in caso affermativo, non procede con l’infezione. 

Secondo i ricercatori, è molto probabile che Cuckoo sia diffuso anche su altri siti web e applicazioni e non sia ancora stato individuato. 

Condividi l’articolo


Articoli correlati

Altro in questa categoria


https://www.securityinfo.it/2024/05/07/cuckoo-lo-spyware-persistente-che-colpisce-macos/?utm_source=rss&utm_medium=rss&utm_campaign=cuckoo-lo-spyware-persistente-che-colpisce-macos