Hybrid-cloud: the best of both worlds

The advent of cloud technology has facilitated faster, easier physical security deployments. As businesses rationalize their costs, concerns and approach to migrating to the cloud, hybrid-cloud deployments are gaining traction across the physical security industry. Recent research conducted by Genetec shows that 60% of organizations are moving towards a blend of on-premises (on-prem) and cloud-based solutions. Such deployments offer organizations the benefits of the cloud while enabling them to keep some infrastructure on-premises.

Becoming more agile 

A hybrid approach gives organizations freedom and flexibility when implementing solutions. Businesses with numerous locations can consider each site’s unique requirements. For instance, they might run some larger density sites on local infrastructure, monitor global deployments in a fully hosted environment, and set up smaller remote sites with direct-to-cloud devices.

No matter how many systems are running on local devices or connected to the cloud, organizations can bring them all back to a central head end. This allows them to streamline monitoring, response and maintenance tasks across their operations to boost efficiencies. To the user, it’s a seamless experience.

Simplifying maintenance and cybersecurity tasks 

With hybrid-cloud solutions, security teams no longer need to travel to various locations to manage infrastructure or check system health. Cloud-based physical security software providers invest significant time and resources in cybersecurity, upholding various standards and certifications around the world. They monitor the latest threats and initiate regular third-party penetration testing and auditing. Thus, operators get immediate access to the latest updates and benefit from continuous innovation. This helps teams quickly address issues and strengthen their organization’s cyber posture.

When is hybrid-cloud the right solution?

Here are some of the most common scenarios when an organization might want to consider a hybrid-cloud deployment model.

Long-term retention

Cloud computing resources and capabilities have surged in the last few years. Many organizations are now taking advantage of the cloud for long-term video retention while keeping short-term, high-resolution archives on local infrastructure. It can provide added layers of redundancy or simply allow them to keep video for longer periods.

Visibility and control over independent sites

Cloud technology is highly scalable, making it easier for businesses to extend security across multiple sites. Organizations can connect their on-prem system to the cloud and manage security across their independent sites with more control. For example, they can easily add cameras or access control readers to remote locations using cloud services, simplifying the set-up process.

Manage heavy in-office traffic

Larger organizations may combine an on-prem video management system (VMS) and cloud-based access control as a service (ACaaS) to lessen the load on their servers and reduce costs.

With this strategy, on-premises infrastructure does the heavy lifting required for video management, while less demanding access control applications are hosted in the cloud.

Busting long-held myths about the cloud

For many businesses, migrating to the cloud can seem unnecessarily risky or just not the right fit. There are a few long-held beliefs about cloud services that may be holding them back. However, hybrid-cloud solutions have progressed significantly, and these beliefs are often no longer true.

The cloud isn’t optimized for larger organizations

The larger the deployment, the more bandwidth throughput you need to stream to the cloud. Adding cloud-connected appliances can help alleviate this challenge by customizing how and when you store information or stream video.

Moving to the cloud will require a total technology replacement

Transitioning to the cloud doesn’t have to happen all at once. Moving one site at a time or using a cloud-connected appliance to get existing infrastructure cloud-ready can happen in a phased approach.

Migration means re-training the entire security team

With hybrid-cloud infrastructure, organizations can manage all of their on-prem, edge computing, and cloud systems using one single unified platform. This simplifies setup, training, and operations.

The cloud isn’t as secure

Cloud solutions come with myriad built-in cybersecurity features and tools that help automate processes and stay on top of threats.

Hybrid-cloud systems allow organizations to leverage their investment in on-prem security devices and infrastructure, while adopting cloud technology such as video and access control as-a-service at their own pace, and to accommodate specific sites or use cases. They provide a cost-effective way to leverage the benefits of both technologies and stay flexible to changing requirements across an organization. 

https://www.securitymagazine.com/articles/100595-hybrid-cloud-the-best-of-both-worlds


Report finds a near 20% increase in ransomware victims year-over-year

A new report by GuidePoint Security has found a near 20% increase in victims of ransomware attacks since Q1 of 2023. This data comes from public resources and threat analysis. 

Although two prominent ransomware groups were disrupted (Lockbit and Alphv), the number of acting ransomware groups has risen by 55% year-over-year. The report studied the active ransomware groups, determining the top three most active: LockBit, Blackbasta and Play. The disruption of law enforcement in February 2024 did not prevent LockBit from attaining the prominent spot among other RaaS service operations. Although operations were hindered by law enforcement, LockBit claimed 219 victims. This includes an average of three victims per day prior to February 2024, then an average of two victims per day following law enforcement disruption. 

More than half of the total ransomware victims were in the United States, accounting for 537 victims. The most impacted industries were manufacturing, retail and healthcare. 

https://www.securitymagazine.com/articles/100592-report-finds-a-near-20-increase-in-ransomware-victims-year-over-year


Cresce il numero di attacchi informatici: +28% rispetto al 2023


Il mondo del cybercrimine continua a mettere in difficoltà le organizzazioni di tutto il mondo: stando al nuovo report di Check Point Research, nel primo trimestre del 2024 il numero medio di attacchi informatici è cresciuto notevolmente, raggiungendo quota 1.308 a settimana; si tratta di un aumento del 5% rispetto allo stesso periodo del 2023 e del 28% rispetto all’ultimo trimestre del 2023.

andamento attacchi informatici nel 2024. Credits: Check Point Research

Credits: Check Point Research

Guardando al dettaglio dei settori, quello dell’istruzione e della ricerca è il più colpito con 2.454 attacchi settimanali per organizzazione, seguito dal settore governativo/militare con 1.692 attacchi e quello sanitario con 1.605 attacchi. Questi dati evidenziano una situazione preoccupante in cui i settori più vulnerabili sono quelli centrali per il funzionamento della società.

La ricerca sottolinea però un cambiamento strategico nella preferenza degli obiettivi da parte dei cybercriminali per via del sostanziale aumento su base annua degli attacchi al settore dei fornitori di hardware, con un incremento del 37%.

Tra le regioni più colpite spicca l’Africa, con una media di 2.373 attacchi settimanali per organizzazione, un aumento del 20% rispetto allo stesso periodo del 2023; al contrario, l’America Latina ha registrato un calo del 20%. Check Point Research spiega che i motivi potrebbero essere legati sia a uno spostamento dell’attenzione dei cybercriminali verso aree più vulnerabili, sia un miglioramento delle misure difensive della regione.

Gli attacchi ransomware non si arrestano

I ransomware continuano a mettere in difficoltà le aziende di tutto il mondo, con il Nord America che è risultato la regione più colpita da questo tipo di attacchi, registrando il 59% dei quasi 1.000 attacchi pubblicati; a seguire troviamo l’Europa (24%) e l’APAC (12%).

L’Europa ha registrato l’aumento maggiore di anno in anno con un +64% rispetto al 2023. L’aumento potrebbe dipendere da una maggiore digitalizzazione dei servizi e il cambiamento delle normative che rende le organizzazioni più vulnerabili.

Il settore più colpito dai ransomware è il manifatturiero (29% degli attacchi), con un aumento di quasi il doppio rispetto all’anno precedente. Segue il settore sanitario con l’11% degli attacchi e un aumento del 63% rispetto al 2023 e il commercio al dettaglio con l’8% del totale.

È invece il settore delle comunicazioni ad aver registrato il più alto incremento su base annua degli attacchi ransomware (+177%), pur costituendo solo il 4% degli attacchi pubblicati nel trimestre. In questo caso l’aumento degli attacchi potrebbe essere stato alimentato dalla rapida trasformazione digitale, mentre il suo ruolo critico e la gestione di dati sensibili lo rendono un obiettivo primario per diverse minacce, tra cui lo spionaggio promosso dagli Stati e il furto di dati.

Il settore manifatturiero ha registrato il secondo più alto aumento di attacchi ransomware con il 96% su base annua. Questo settore è un obiettivo primario comune a causa della sua forte dipendenza dalla tecnologia interconnessa e delle capacità di sicurezza indebolite dall’uso di tecnologie industriali tradizionali. 

Proteggersi dagli attacchi informatici

Vista l’evoluzione del panorama delle minacce, le imprese devono migliorare il proprio assetto di sicurezza per far fronte agli attacchi informatici in crescita. Check Point Research sottolinea l’importanza di misure robuste che comprendano backup dei dati, corsi di formazione costanti, patch di sicurezza tempestive, autenticazione forte degli utenti e soluzioni anti-ransomware avanzate.

In risposta ad attacchi sempre più sofisticati, è essenziale ricorrere a soluzioni per il rilevamento precoce e l’analisi delle anomalie, soprattutto per proteggersi da modelli di attacco che sfruttano l’intelligenza artificiale. L’IA rappresenta un ottimo alleato anche per la cybersecurity, e le aziende dovrebbero valutare l’introduzione di strumenti che sfruttano questa tecnologia per contrastare le minacce più sofisticate.

“ L’aumento degli attacchi a settori e regioni specifiche, unito alla complessità delle tattiche del ransomware, evidenzia la necessità di approcci alla sicurezza informatica completi e orientati alla prevenzione” afferma la compagnia. “Mentre continuiamo a navigare in questo terreno difficile, la consapevolezza, la preparazione e l’innovazione nelle strategie di difesa rimangono i nostri alleati più forti“.

Condividi l’articolo


Articoli correlati

Altro in questa categoria


https://www.securityinfo.it/2024/04/19/cresce-il-numero-di-attacchi-informatici-28-rispetto-al-2023/?utm_source=rss&utm_medium=rss&utm_campaign=cresce-il-numero-di-attacchi-informatici-28-rispetto-al-2023


Accelerating discovery and recovery in today’s threat landscape

Security professionals know that the threat of cyberattacks is ever-present and something organizations must always be on alert for. In today’s constantly evolving threat landscape, the ability to quickly detect and respond to security incidents is critical. 

Governments, businesses, individuals, and organizations are continuously challenged by increasingly sophisticated cyberattacks. A recent report, based on a survey of more than 800 global IT professionals and security executives, showed 92% of IT leaders state that cyberattacks have grown in frequency since 2023. The report also revealed that cyberattacks are increasing in sophistication with 95% of those surveyed reporting that cyberattacks are so sophisticated that they feel unprepared for the emerging threat vectors.

Another report shows 87% of C-suite and board members are citing ransomware as a high or top priority, while 55% of C-suite and board-level executives stated ransomware attack mitigation as the top priority in their company. Forty percent of respondents ranked security threats and data privacy among the top causes of complexity in their storage infrastructure.

Working together, discovery and recovery incorporates the proactive and reactive measures organizations take to swiftly detect, respond to, and recover from security incidents. That’s why it is important for organizations of all sizes to have a comprehensive security plan in place to discover cyberattacks and take action quickly. 

The Identity Defined Security Alliance (IDSA) 2023 Trends in Identity Security report, based on an online survey of more than 500 identity and security professionals, provides insight into the progress organizations are making in defending against the rapid increase in cyberattacks and the approaches large companies are taking toward security and identity. According to that report, 90% of organizations reported at least one identity-related incident in the last 12 months, a 6% increase from last year’s report. The report also revealed identity stakeholders are facing an increasing number of barriers without the support from leadership with 49% reporting their leadership teams understand identity and security risks and proactively invest in protection before suffering an incident, while 29% only engage and support after an incident.

The integration of discovery and recovery is essential for effectively managing security incidents and minimizing their impact on an organization. Proper coordination between detection and response teams ensures that critical information is shared promptly, and appropriate actions are taken in a timely manner. Continuous improvement based on lessons learned from past incidents is also key to strengthening an organization’s security posture and resilience against future threats. 

A recent report detailed how data protection and recovery remain a challenge for many organizations, with 71% of respondents who experienced a ransomware attack reporting it taking days or even weeks to restore full operations. To help address this, 78% of organizations say they plan to increase investments in ransomware protection solutions throughout this year.

With the cybersecurity threat landscape constantly evolving, it is often said it isn’t a matter of if a cyberattack will occur, but when. This is why the ability to quickly detect and respond to security incidents is critical for organizations.

https://www.securitymagazine.com/articles/100596-accelerating-discovery-and-recovery-in-todays-threat-landscape


L’IA generativa complica la gestione sicura delle applicazioni SaaS


La corsa all’IA generativa ha spinto i produttori di applicazioni SaaS (Software-as-a-Service) ad aggiornare i propri strumenti integrando nuove funzionalità intelligenti per aumentare la produttività.

La GenAI si sta confermando come un assistente indispensabile per facilitare lo sviluppo di software, velocizzare la scrittura di documenti ed email e supportare la creazione di contenuti di valore.

The Hacker News sottolinea che i grandi nomi del panorama tecnologico, tra cui Microsoft, Google, GitHub e Salesforce, hanno già integrato funzionalità di IA generativa nella propria offerta di applicazioni in cloud, e a breve queste feature diventeranno lo standard dei servizi SaaS.

A fronte degli indubbi vantaggi che porta, l’IA generativa nelle applicazioni cloud comporta anche una serie di nuovi rischi di sicurezza che non andrebbero sottovalutati. La diffusione dei nuovi tool ha complicato il panorama delle minacce informatiche, preoccupando le organizzazioni.

La risposta delle aziende ai rischi dell’IA generativa

I modelli usati per alimentare i chatbot di IA generativa utilizzano i dati inseriti dagli utenti per migliorare il proprio addestramento e la qualità delle risposte, rendendoli potenzialmente accessibili agli sviluppatori che lavorano ai modelli; ciò amplia notevolmente la superficie di attacco delle organizzazioni. Anche se gli strumenti avvertono gli utenti di non condividere dati sensibili o informazioni relative alla propria azienda nella maggior parte dei casi questo avvertimento viene ignorato.

Tra i rischi principali ci sono la perdita di IP, dati riservati dei clienti e PII, oltre al fatto che i cybercriminali possono sfruttare le informazioni condivise dagli utenti per eseguire attacchi di phishing e furti di identità.

Le organizzazioni sono preoccupate dai rischi dell’IA generativa, tanto che alcune di esse, soprattutto quelle in industrie e settori che trattano dati riservati, hanno già vietato l’uso di questi tool. The Hacker News riporta che il settore bancario è stato il primo a vietare l’IA generativa, nonostante i manager del settore si dicano fiduciosi sui vantaggi dell’uso dell’IA per migliorare l’efficienza operativa.

Anche il Governo degli Stati Uniti sta seguendo una linea molto severa nei confronti della GenAI: dopo aver bloccato ChatGPT su tutti i PC in dotazione al governo, il mese scorso il Congresso ha vietato l’utilizzo di Copilot di Microsoft.

I divieti imposti dalle organizzazioni rivelano un’incapacità di base nel monitorare l’uso delle applicazioni SaaS basate su IA generativa a causa di un’importante carenza di competenze, sia nella forza lavoro che tra i leader.

I blocchi non impediscono però ai dipendenti di usare comunque i tool di GenAI, spesso appoggiandosi ai dispositivi personali: uno studio di Salesforce ha rivelato che più della metà degli utenti di IA generativa usa strumenti non approvati dal proprio datore di lavoro. I mancati controlli su questi comportamenti e l’assenza di policy chiare per l’uso dell’IA sta mettendo a serio rischio i business.

Pixabay

È ora di riprendere il controllo delle proprie applicazioni

La rapida evoluzione della tecnologia e la diffusione del lavoro ibrido e remoto ha complicato il lavoro degli esperti di cybersecurity. Sempre più organizzazioni si affidano a soluzioni SaaS che spesso soffrono di configurazioni errate e di meccanismi di controllo dell’identità e degli accessi inadeguati.

I cybercriminali stanno sfruttando queste debolezze per distribuire malware ed eseguire attacchi di vario tipo, e l’uso non autorizzato e incontrollato di strumenti di intelligenza artificiale generativa complica un quadro già difficile.

Impedire la diffusione della GenAI è impossibile e contro produttivo; le aziende dovrebbero quindi rivalutare la propria postura di sicurezza e dotarsi di strumenti capaci di gestire la nuova generazione di minacce.

Per ottenere il controllo e la visibilità sulle applicazioni SaaS di IA generativa è necessario mettere in campo soluzioni di sicurezza avanzate basate sul principio di zero-trust che consentono di abilitare l’uso dell’IA riducendone i rischi. Solo con una visione completa delle applicazioni in uso è possibile prevenire, rilevare e rispondere alle minacce, proteggendo al contempo i dati e i processi centrali per il business.

Condividi l’articolo


Articoli correlati

Altro in questa categoria


https://www.securityinfo.it/2024/04/18/ia-generativa-complica-gestione-sicura-applicazioni-saas/?utm_source=rss&utm_medium=rss&utm_campaign=ia-generativa-complica-gestione-sicura-applicazioni-saas


In aumento gli attacchi brute-force a VPN e servizi SSH


I ricercatori di Cisco Talos hanno individuato un preoccupante aumento di attacchi brute-force in tutto il mondo a partire dal 18 marzo. Tra gli obiettivi principali degli attaccanti ci sono i servizi VPN, le interfacce di autenticazione per applicazioni web e i servizi SSH.

Secondo l’analisi, gli indirizzi IP legati agli attacchi sono associati a diversi servizi proxy, tra i quali TOR, VPN Gate, IPIDEA Proxy, BigMama Proxy, Space Proxies, Nexus Proxy, Proxy Rack e altri.

“A seconda dell’ambiente colpito, attacchi di successo di questo tipo possono portare ad accessi di rete non autorizzati, blocco degli account o interruzioni di servizio” spiegano i ricercatori. Il team sottolinea che il volume di questi attacchi continuerà ad aumentare anche nei prossimi mesi.

Tra i servizi colpiti ci sono Cisco Secure Firewall VPN, Checkpoint VPN, Fortinet VPN, SonicWall VPN, RD Web Services, Miktrotik, Draytek e Ubiquiti.

Gli attacchi analizzati finora hanno colpito organizzazioni di ogni regione e industria e non sembrano essere diretti a degli obiettivi particolari. I ricercatori riportano che i tentativi di brute-force hanno usato sia username generici che specifici contro le aziende.

Cisco Talos ha aggiunto gli IP tracciati alla blocklist della propria VPN, ma, visto che gli attacchi proseguono e aumentano in numero, è altamente probabile che l’elenco di indirizzi IP malevoli cambierà.

Pr proteggersi da questo tipo di attacchi è necessario usare password robuste e aggiornarle regolarmente. Gli amministratori dei servizi e dei siti web dovrebbero ridurre il numero di tentativi di login possibili e abilitare l’autenticazione a due fattori. È importante inoltre monitorare gli indirizzi IP sospetti ed eventualmente bloccarli con soluzioni di rilevamento e prevenzione delle intrusioni.

Condividi l’articolo


Articoli correlati

Altro in questa categoria


https://www.securityinfo.it/2024/04/18/in-aumento-gli-attacchi-brute-force-a-vpn-e-servizi-ssh/?utm_source=rss&utm_medium=rss&utm_campaign=in-aumento-gli-attacchi-brute-force-a-vpn-e-servizi-ssh


The cat and mouse ransomware game may threaten smaller organizations

The practice of cybersecurity is ever-changing, marked by a continual dance between the attackers and the defenders. Each side is in a constant state of adaptation, reacting to the strategies of the other. The ongoing evolution of ransomware cybercrime is a prime illustration of this dynamic.

Historically, ransomware attacks were somewhat isolated events. Today, they have morphed into coordinated global threats that target essential infrastructure, seeking substantial ransoms. The audacious attack on UnitedHealth by the BlackCat/ALPHV ransomware gang in February 2024 emphasizes acute vulnerabilities within vital sectors and showcases the insolent nature of these cybercriminals. 

It would make sense to assume that these two operations were among the efforts carried out by the International Counter Ransomware Task Force (ICRTF). The ICRTF was formally established in January 2023, as part of the White House-led International Counter Ransomware Initiative (CRI), bringing together policy, law enforcement and operational agencies from around the world with a shared desire to defend against and disrupt ransomware, while building resilience against malicious cyber actors. To disrupt ransomware, the members aim to alter the current cost-reward-risk equation of cybercriminals. By increasing the cost of attacks (e.g., as a result of the need to recover damaged infrastructures), reducing the reward (e.g., through restrictions on ransom payments) and elevating the risk of legal consequences (e.g., through international law enforcement cooperation), the initiative seeks to undermine the currently lucrative ransomware business model. 

Strategic campaigns significantly impact the overall strategic environment, often forcing adversaries to reevaluate and alter their schemes and approach. The ICRTF campaign is no different: as the current implementation changes the cost-reward-risk equation, it is possible that the cybercriminals will shift from few large-scale, high-stake ransomware attacks to a broader array of smaller-scale attacks. This strategic adjustment would be a calculated move by cybercriminals to reduce the costs and risks while compensating for the lower ransomware reward with quantity. The logic behind this focus is simple: they represent the low-hanging fruit with the least resistance.

This evolution could pose an increased risk to smaller organizations, which often have less robust cybersecurity defenses, making them attractive targets for ransomware gangs. If this shift occurs, it will eventually require a shift in the CRI’s focus towards the implementation of stringent cybersecurity protocols in small companies, including embracing basic cybersecurity practices and promoting a culture of security awareness across the board.

For now, there are four actions small and midsize organizations can take now to bolster their security posture against ransomware:

  1. Raise awareness through training and education: Empower employees with knowledge on identifying phishing emails and suspicious links, as they are often the first line of defense against ransomware.
  2. Keep systems updated: Regularly update all software to patch vulnerabilities that could be exploited by ransomware attackers.
  3. Back up data: Implement a robust data backup strategy, ensuring backups are performed regularly and stored in a secure, off-site location or in cloud services. This reduces the impact of data loss in case of an attack.
  4. Prepare an incident response plan: Formulate an incident response plan that includes specific procedures for ransomware attacks. This plan should detail roles and responsibilities, communication protocols and recovery processes to be efficiently activated in the event of an attack.

https://www.securitymagazine.com/articles/100591-the-cat-and-mouse-ransomware-game-may-threaten-smaller-organizations


Are AI data poisoning attacks the new software supply chain attack?

With rapid AI adoption happening across varying business units, maintaining the integrity of those systems — and preventing AI data poisoning attacks — is a growing concern.

But how do these attacks occur, and why should businesses be worried? 

Much of it has to do with third-party access to business systems and data. In Venafi’s 2023 State of Cloud Native Security Report, 75% of security professionals stated their software supply chain presents their biggest security blind spot. 

AI models are more susceptible to hacker exploits because they are programmed on vast datasets to generate the outputs they do. For example, Open AI’s ChatGPT-4 consists of eight models, each trained on approximately 220 billion parameters, or 1.76 trillion parameters. A training pipeline of that size introduces risk to connected systems, services, and devices and the AI itself. 

Tracking data provenance and maintaining integrity across the collection, storage and preparation of that data is crucial. Without it, AI models can be easily swayed, even by simple, minor manipulation. 

What is an AI data poisoning attack?

AI data poisoning attacks occur when threat actors corrupt the underlying data used to train and operate a machine learning model. By doing this, threat actors effectively manipulate the algorithms used to build the system, poisoning models with as little as 0.1% of their training data. 

There are several ways to conduct this type of attack, but they’re typically carried out with the desire to change the very function and outputs of a model, such as compromising standard operating procedures causing AI systems to behave erratically, discriminately or unsafely. 

How are AI poisoning attacks and software supply chain attacks related? 

If a security team is trying to grapple with AI cybersecurity, the issue of maintaining data privacy and integrity has no doubt already cropped up. It’s like software supply chain issues, but on a larger, even more complex scale. 

If a company is relying on a web-based AI model, and that compromised model has or gains access to additional systems in the organization — including production or distribution environments — the company may experience an impact similar to that of a supply chain attack.

How do AI data poisoning attacks happen?

Hackers have quite the arsenal to pick from when deciding how to carry out an AI data poisoning attack, including:

  • Backdoor tampering
  • Flooding
  • API targeting

Backdoor tampering

Backdoor tampering can occur in a few different ways, including untrusted source material or through an extremely broad training scope. In a recent study, researchers discovered that it’s possible to deliberately misalign models that, during training, appear to behave normally. However, when they are pushed into production, behave according to unsafe, concealed instructions. Since the AI showed no signs of malignant behavior during training, it gave the humans training it a false sense of security, and if this were a real-world situation where the “harmless” AI was pushed into production, it could result in disaster.

Flood attacks

Flood attacks occur when hackers send copious amounts of non-malicious data through an AI system. Once the AI system has been trained to recognize this correspondence and begins to see it as a “normal” pattern of communication, a hacker will then attempt to slip a malicious message (like a phishing email) past an AI system. If the flood attack was successful, the AI will let that malicious message pass by, undetected.

API targeting

Large Language Models (LLMs) with access to APIs present several security issues, and without robust authentication procedures, LLMs can call on and connect APIs without a user’s knowledge. If this LLM were compromised, it could be convinced to behave unsafely, or distribute malware further down the software supply chain. 

How Retrieval Augmented Generation (RAG) can help prevent AI data poisoning attacks

Many AI models, including those from OpenAI, are trained on vast internet data sets, posing challenges in verifying and authenticating the data. To address this, experts suggest integrating Refined Access Guidance (RAG) into AI models. While not all models support RAG, it can safeguard organizations from AI model poisoning by providing tailored context atop the base Language Model (LLM). 

Instead of relying solely on broad model outputs, RAG furnishes refined information, such as business-specific data, reducing the risk of AI data poisoning and generating more coherent content. As AI models are built on extensive data, understanding their creation pipeline is already complex. Handling compromised data or “forgetting” information is costly and time-consuming, impacting performance. 

How can machine identity management help prevent AI data poisoning attacks?

By building a solid foundation through machine identity management, security leaders can ensure that AI data poisoning attacks don’t have the opportunity to wreak havoc on an organization’s AI technologies, systems or customers’ systems. Examples include:

  • When using third-party AI models, treat them like any third-party software: authenticate access and evaluate thoroughly before deployment.
  • Ensure robust authentication for AI and non-AI APIs, connecting only trusted APIs and enabling blocking of suspicious requests. 
  • Implement secure code signing to prevent unauthorized executions. Maintain end-to-end security and traceability of AI model origins.
  • Adopt a centralized, unified control plane for machine identity management. With a control plane, security leaders can discover, monitor and automate the orchestration of all types of machine identities across all environments and teams, making it easy to see which AI models can be trusted.

The proliferation of AI/ML tools, and their enormous data training sets (often with uncertain origins), opens the door for new types of software supply chain threats, including the poisoning of AI training data. To safely capitalize on AI technology, companies need to manage all types of machine identities, including TLS/SSL, code signing, mTLS, SPIFFE, SSH and others. By taking the steps above, organizations will be better prepared to safeguard against growing AI toolsets and risks. 

https://www.securitymagazine.com/articles/100590-are-ai-data-poisoning-attacks-the-new-software-supply-chain-attack


Kremlin-backed actors spread disinformation ahead of US elections

Kremlin-backed actors spread disinformation ahead of US elections

Kremlin-backed actors have stepped up efforts to interfere with the US presidential election by planting disinformation and false narratives on social media and fake news sites, analysts with Microsoft reported Wednesday.

The analysts have identified several unique influence-peddling groups affiliated with the Russian government seeking to influence the election outcome, with the objective in large part to reduce US support of Ukraine and sow domestic infighting. These groups have so far been less active during the current election cycle than they were during previous ones, likely because of a less contested primary season.

Stoking divisions

Over the past 45 days, the groups have seeded a growing number of social media posts and fake news articles that attempt to foment opposition to US support of Ukraine and stoke divisions over hot-button issues such as election fraud. The influence campaigns also promote questions about President Biden’s mental health and corrupt judges. In all, Microsoft has tracked scores of such operations in recent weeks.

In a report published Wednesday, the Microsoft analysts wrote:

The deteriorated geopolitical relationship between the United States and Russia leaves the Kremlin with little to lose and much to gain by targeting the US 2024 presidential election. In doing so, Kremlin-backed actors attempt to influence American policy regarding the war in Ukraine, reduce social and political support to NATO, and ensnare the United States in domestic infighting to distract from the world stage. Russia’s efforts thus far in 2024 are not novel, but rather a continuation of a decade-long strategy to “win through the force of politics, rather than the politics of force,” or active measures. Messaging regarding Ukraine—via traditional media and social media—picked up steam over the last two months with a mix of covert and overt campaigns from at least 70 Russia-affiliated activity sets we track.

The most prolific of the influence-peddling groups, Microsoft said, is tied to the Russian Presidential Administration, which according to the Marshal Center think tank, is a secretive institution that acts as the main gatekeeper for President Vladimir Putin. The affiliation highlights the “the increasingly centralized nature of Russian influence campaigns,” a departure from campaigns in previous years that primarily relied on intelligence services and a group known as the Internet Research Agency.

“Each Russian actor has shown the capability and willingness to target English-speaking—and in some cases Spanish-speaking—audiences in the US, pushing social and political disinformation meant to portray Ukrainian President Volodymyr Zelensky as unethical and incompetent, Ukraine as a puppet or failed state, and any American aid to Ukraine as directly supporting a corrupt and conspiratorial regime,” the analysts wrote.

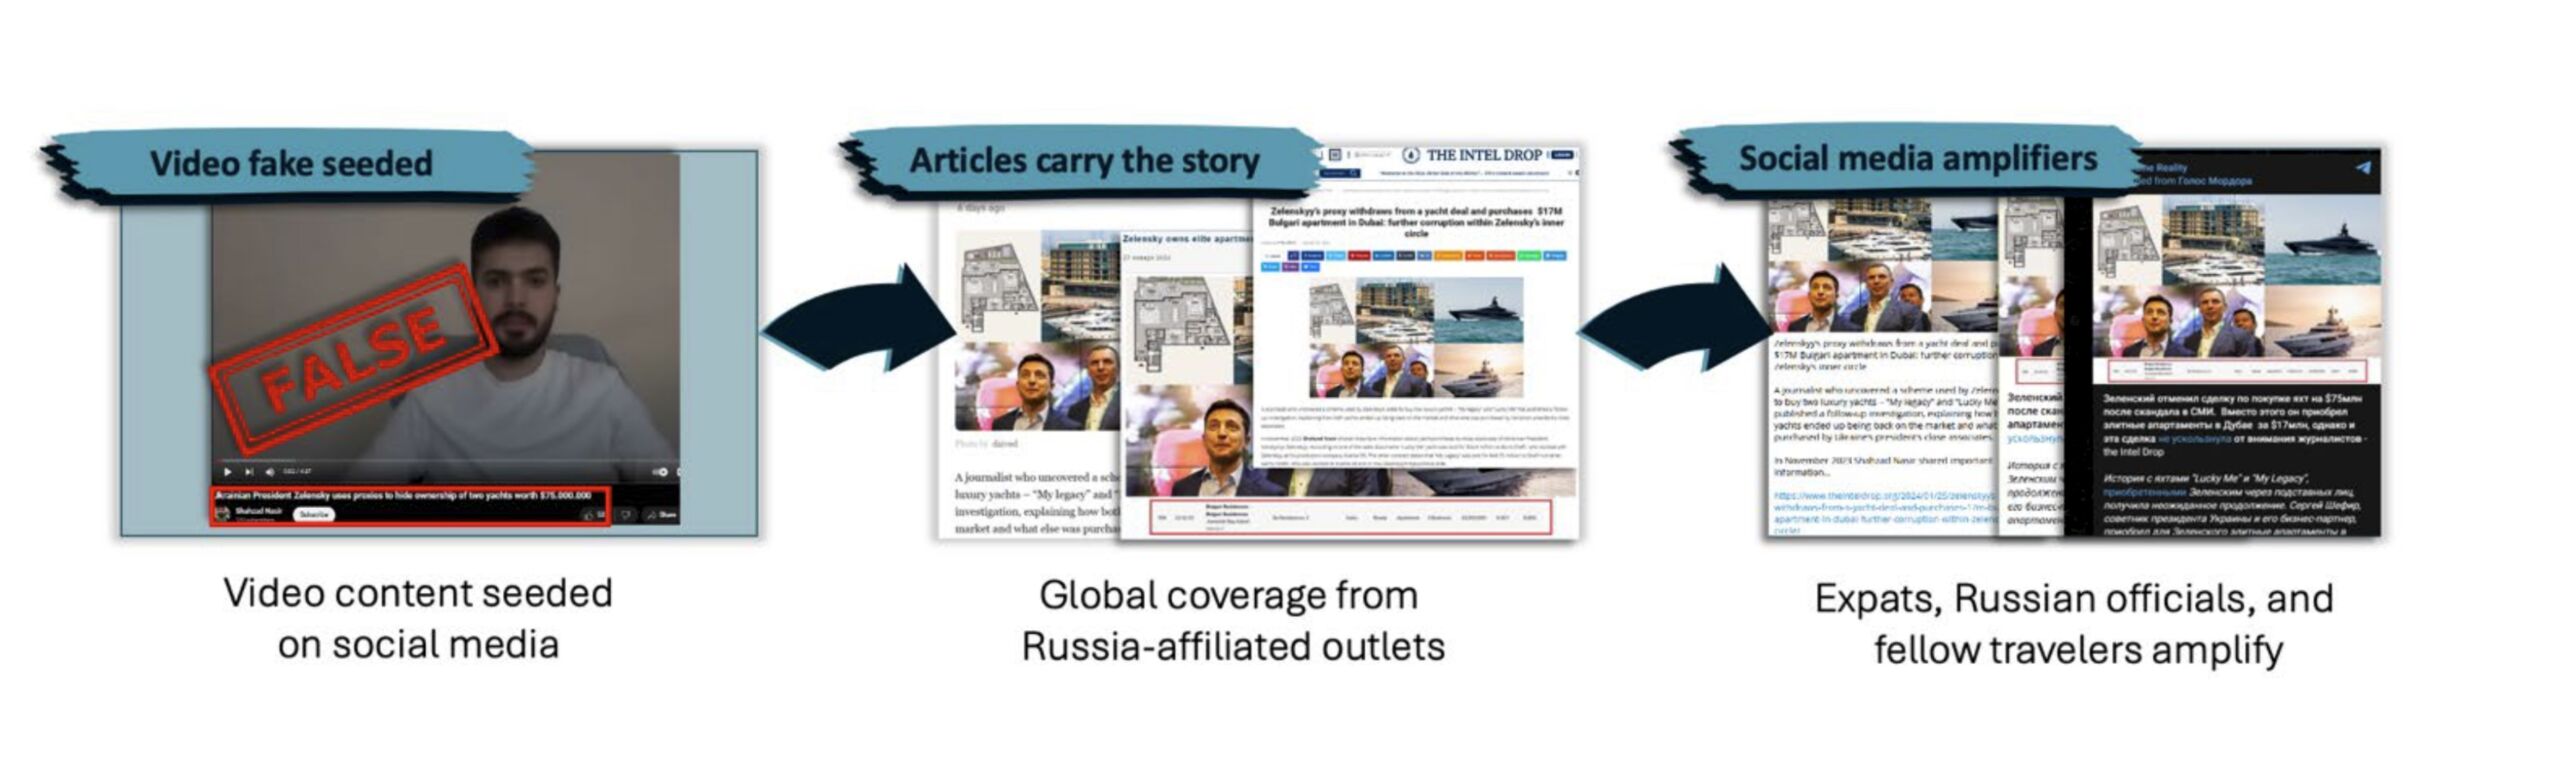
An example is Storm-1516, the name Microsoft uses to track a group seeding anti-Ukraine narratives through US Internet and media sources. Content, published in English, Russian, French, Arabic, and Finnish, frequently originates through disinformation seeded by a purported whistleblower or citizen journalist over a purpose-built video channel and then picked up by a network of Storm-1516-controlled websites posing as independent news sources. These fake news sites reside in the Middle East and Africa as well as in the US, with DC Weekly, Miami Chronicle, and the Intel Drop among them.

Eventually, once the disinformation has circulated in subsequent days, US audiences begin amplifying it, in many cases without being aware of the original source. The following graphic illustrates the flow.

Storm-1516 process for laundering anti-Ukraine disinformation.
Enlarge / Storm-1516 process for laundering anti-Ukraine disinformation.

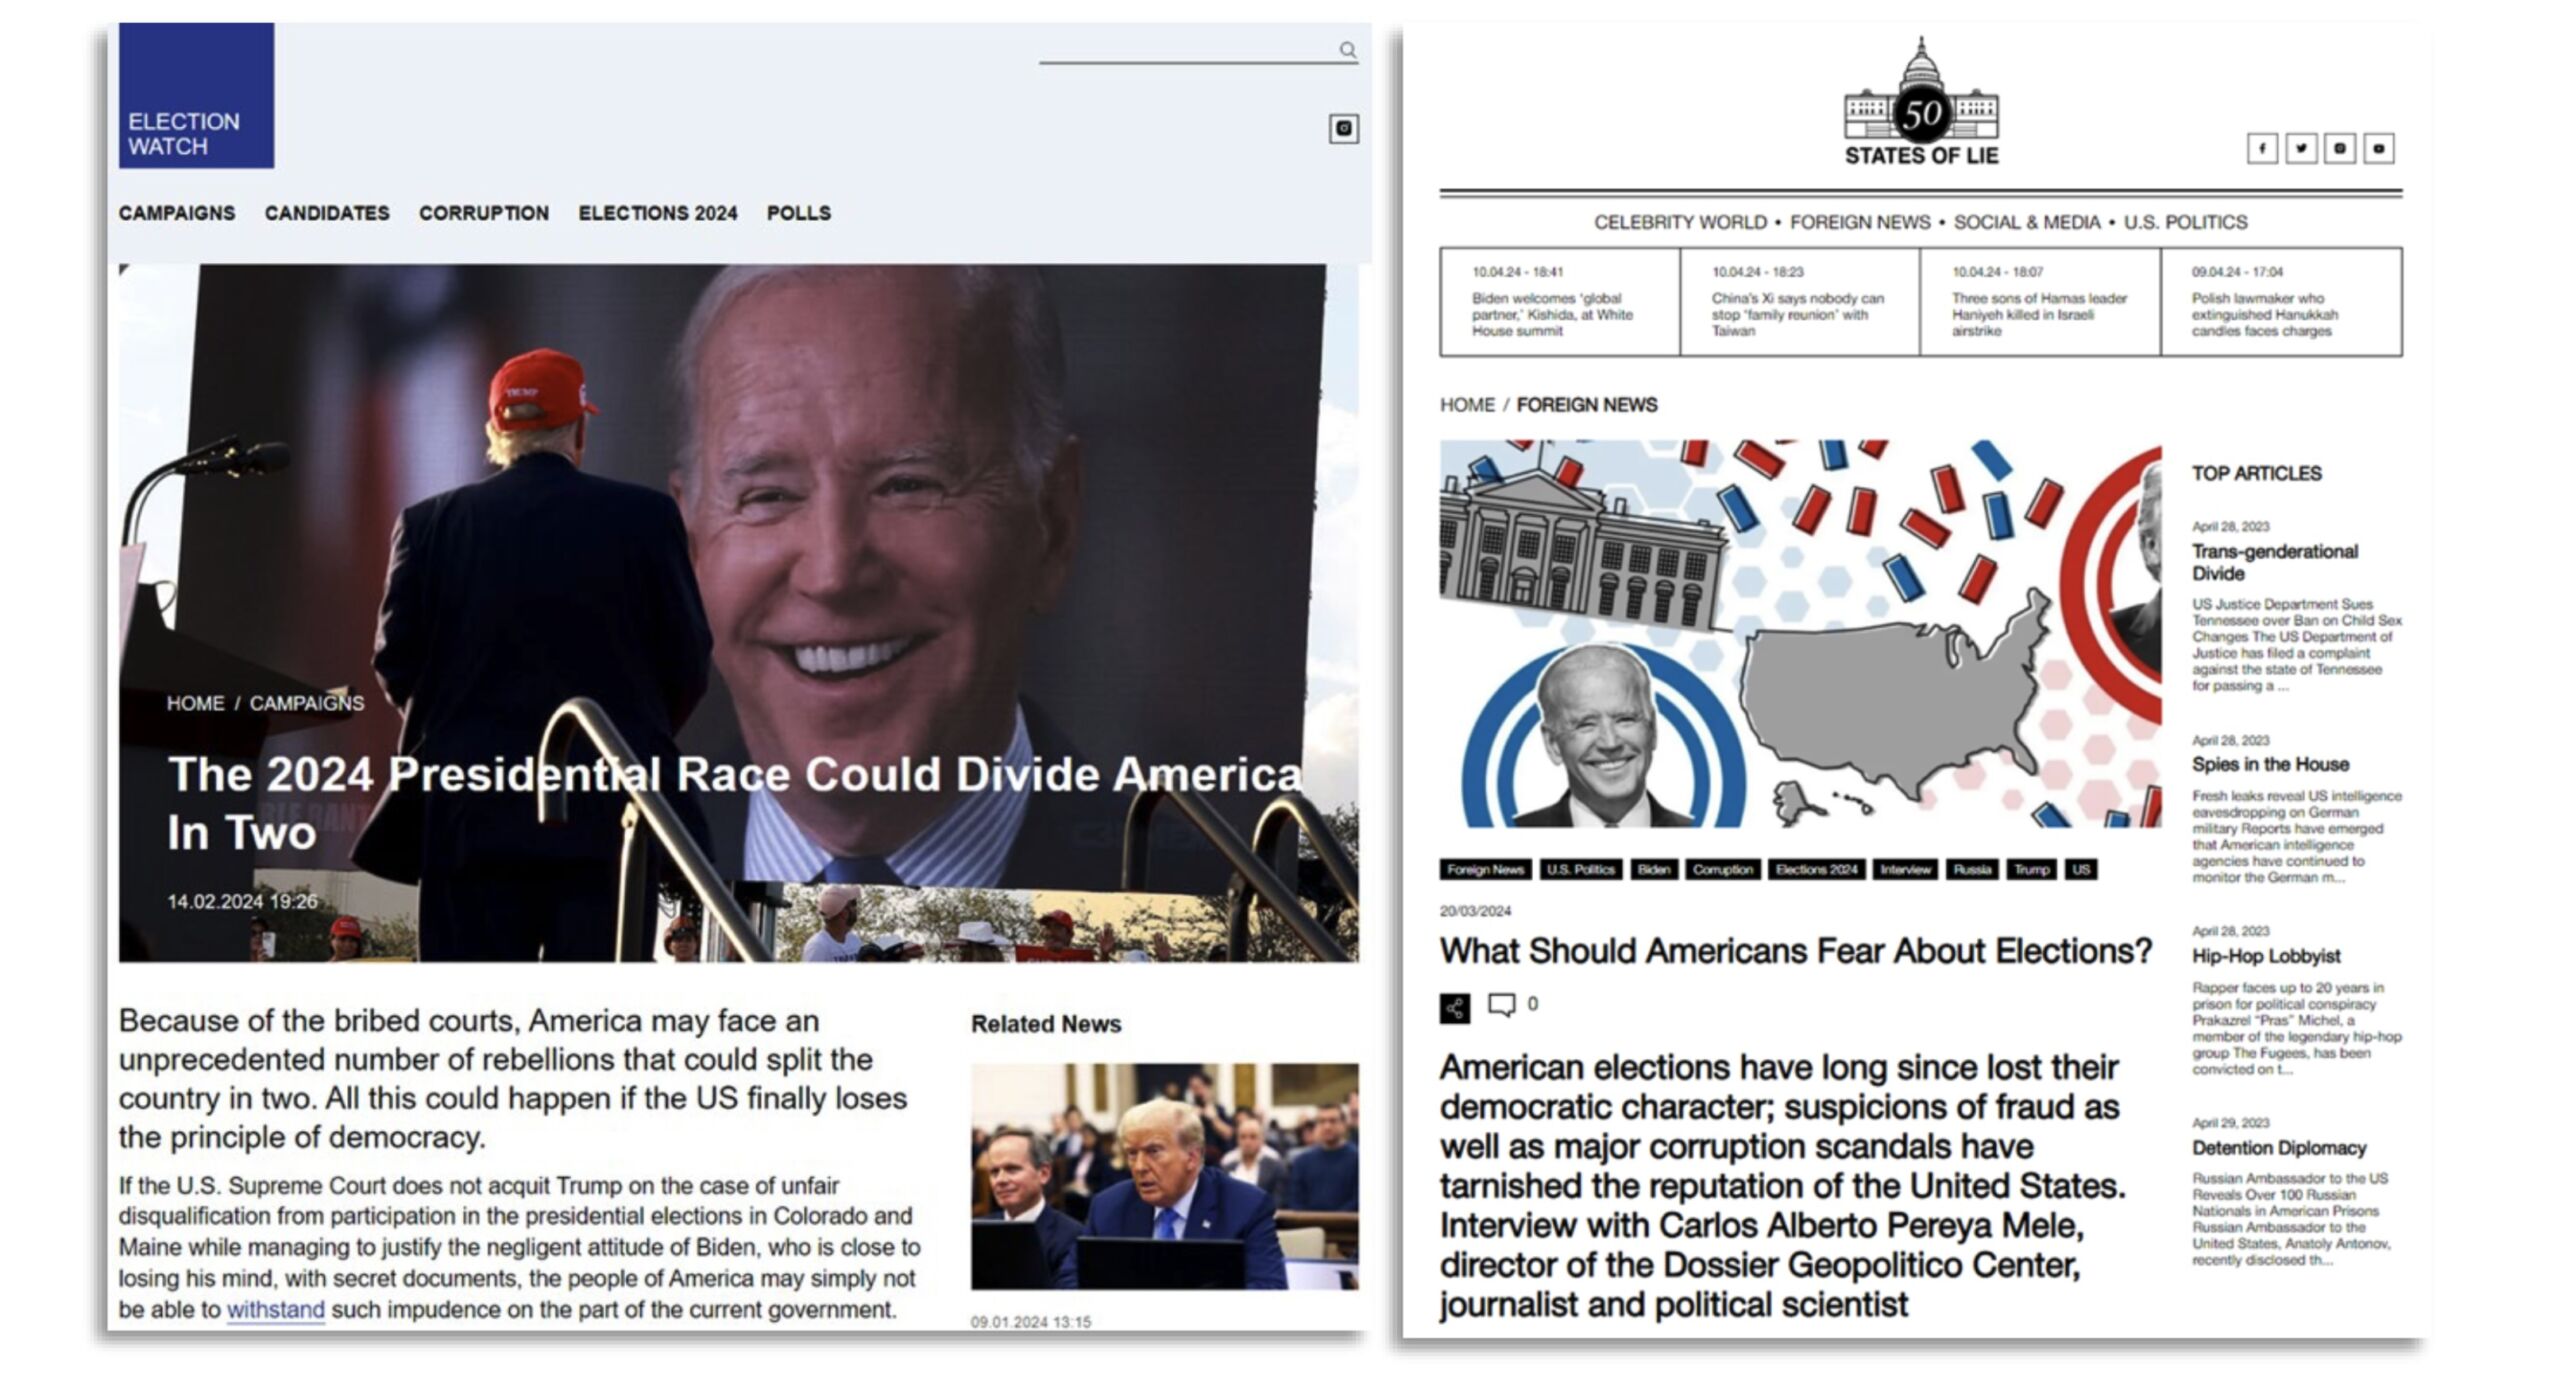
Wednesday’s report also referred to another group tracked as Storm-1099, which is best known for a campaign called Doppelganger. According to the disinformation research group Disinfo Research Lab, the campaign has targeted multiple countries since 2022 with content designed to undermine support for Ukraine and sow divisions among audiences. Two US outlets tied to Storm-1099 are Election Watch and 50 States of Lie, Microsoft said. The image below shows content recently published by the outlets:

Storm-1099 sites.
Enlarge / Storm-1099 sites.

Wednesday’s report also touched on two other Kremlin-tied operations. One attempts to revive a campaign perpetuated by NABU Leaks, a website that published content alleging then-Vice President Joe Biden colluded with former Ukrainian leader Petro Poroshenko, according to Reuters. In January, Andrei Derkoch—the ex-Ukrainian Parliamentarian and US-sanctioned Russian agent responsible for NABU Leaks—reemerged on social media for the first time in two years. In an interview, Derkoch propagated both old and new claims about Biden and other US political figures.

The other operation follows a playbook known as hack and leak, in which operatives obtain private information through hacking and leak it to news outlets.

https://arstechnica.com/?p=2018090


Billions of public Discord messages may be sold through a scraping service

Discord logo, warped by vertical perspective over a phone displaying the app
Getty Images

It’s easy to get the impression that Discord chat messages are ephemeral, especially across different public servers, where lines fly upward at a near-unreadable pace. But someone claims to be catching and compiling that data and is offering packages that can track more than 600 million users across more than 14,000 servers.

Joseph Cox at 404 Media confirmed that Spy Pet, a service that sells access to a database of purportedly 3 billion Discord messages, offers data “credits” to customers who pay in bitcoin, ethereum, or other cryptocurrency. Searching individual users will reveal the servers that Spy Pet can track them across, a raw and exportable table of their messages, and connected accounts, such as GitHub. Ominously, Spy Pet lists more than 86,000 other servers in which it has “no bots,” but “we know it exists.”

As Cox notes, Discord doesn’t make messages inside server channels, like blog posts or unlocked social media feeds, easy to publicly access and search. But many Discord users many not expect their messages, server memberships, bans, or other data to be grabbed by a bot, compiled, and sold to anybody wishing to pin them all on a particular user. 404 Media confirmed the service’s function with multiple user examples. Private messages are not mentioned by Spy Pet and are presumably still secure.

Spy Pet openly asks those training AI models, or “federal agents looking for a new source of intel,” to contact them for deals. As noted by 404 Media and confirmed by Ars, clicking on the “Request Removal” link plays a clip of J. Jonah Jameson from Spider-Man (the Tobey Maguire/Sam Raimi version) laughing at the idea of advance payment before an abrupt “You’re serious?” Users of Spy Pet, however, are assured of “secure and confidential” searches, with random usernames.

This author found nearly every public Discord he had ever dropped into for research or reporting in Spy Pet’s server list. Those who haven’t paid for message access can only see fairly benign public-facing elements, like stickers, emojis, and charted member totals over time. But as an indication of the reach of Spy Pet’s scraping, it’s an effective warning, or enticement, depending on your goals.

Ars has reached out to Spy Pet for comment and will update this post if we receive a response. A Discord spokesperson told Ars that the company is investigating whether Spy Pet violated its terms of service and community guidelines. It will take “appropriate steps to enforce our policies,” the company said, and could not provide further comment.

https://arstechnica.com/?p=2017957