Is your financial data safe this tax season?
Tax season is always a stressful time, and with the IRS tax deadline just around the corner, many individuals and businesses are rushing to get their returns filed in time. In this scramble, it’s easy to overlook the plethora of serious privacy and security concerns surrounding the sensitive financial data entrusted to tax preparation companies. 

There are few documents more personal and sensitive than a tax return, which is why you shouldn’t trust just any tax preparation company. Unfortunately, in recent years we’ve seen numerous cases of these companies misusing or failing to properly protect their customers’ personal and financial information. In fact, last year, a congressional report showed that some of America’s largest tax-prep companies had been sharing clients’ sensitive financial data with tech giants for years. This data includes income, mortgage information, etc., and was allegedly used to target individuals with tailored financial advertisements and product offers, potentially in violation of federal law. To make things worse, some of these companies still do not know whether the shared data still remains in the hands of these tech platforms. Customers put their trust (often blindly) in these tax prep companies to handle their most sensitive financial details, and they deserve to know that their information will be protected.

In addition to the violation of consumer trust we’ve seen from tax prep companies themselves, tax season marks a peak in cybercriminal activity. The increase of sensitive information being shared during this time makes it perfect for bad actors to take advantage. Last year, the IRS identity theft detection identified more than 1.1 million tax returns as potentially fraudulent, with the total refunds claimed totaling over $6 billion. Individuals and businesses must be extra vigilant when sharing their financial data, especially during tax season.

This piece will explore strategies for individuals, as well as tax preparation organizations, to ensure their data and their clients’ data is protected this tax season and beyond. 

Protecting your personal data

First and foremost, it is important to be extremely cautious about which tax prep company you choose to work with. Research their privacy policies, data security practices and any past incidents of data breaches or misuse before moving forward. 

Additionally, individuals should utilize encryption and password managers when sharing financial documents digitally. Encryption should be the standard for all sensitive information, whether stored locally, in the cloud or transmitted over networks. Utilizing strong encryption algorithms ensures that even if data is compromised, it remains unreadable to unauthorized parties. It is also vital to use strong, unique passwords for all accounts and be wary of phishing scams that use convincing tactics to encourage individuals to reveal sensitive information — never send sensitive information like Social Security numbers or bank account details via unsecured email or file sharing. Instead, look for tax prep companies that offer secure client portals or encrypted file transfer options.

Finally, individuals should monitor credit reports and financial accounts, even after their taxes have been filed. Signs of identity theft or unauthorized activity may not appear immediately, so continuous monitoring is important. 

Best practices for tax prep companies and professionals

As a tax prep company, it is vital that sensitive client information is protected. These organizations must be aware of two types of rise — people risks and systems risks. They should invest in tools that automatically enhance data security for both people and systems. For example, data security can be simplified through automating encryption and decryption processes to ensure robust protection of sensitive information.

Access control is also critical to limit exposure to sensitive data, by not only enforcing the least privilege principle but also continuously monitoring and adjusting access rights based on role changes or project completions. Advanced access management systems, integrating multi-factor authentication (MFA), can automatically adjust permissions based on the user’s location, device security posture and the sensitivity of the accessed data.

Tax preparation companies should foster a culture where data protection is a shared responsibility across the organization. They should offer and require comprehensive training programs to enhance security awareness, ensuring their clients’ sensitive financial information is consistently secure. This must also be a requirement for temporary workers. Because of the increased workload during tax season, many organizations hire temporary workers. While this practice is common, it does pose increased data security risks. Temporary workers may have access to sensitive financial information, and without proper safeguards, this information could be compromised. It is vital that organizations conduct proper background checks, require intense training and instill the proactive data protection mindset for temporary workers as well, to reduce the risk of insider threats.

It is also important for these companies to consider the risks AI poses to client data. With AI, it is easier than ever to generate deepfakes and implement large-scale social engineering tactics to obtain taxpayer information by pretending to be tax preparers. This poses a particular risk to more vulnerable populations like the elderly, who may not be aware of these tactics and are increasingly targeted. With this, it is vital that tax professionals are educated on how to properly collect information, only using the secure, approved portal, rather than over the phone or via email. In the unfortunate event that tax filers become a victim of Stolen Identity Refund Fraud, it is essential that they notify the IRS immediately, so they can promptly investigate and pursue the issue on their end. 

Finally, ongoing security and risk assessments are necessary to understand the organization’s threat landscape and evaluate the effectiveness of existing controls. These assessments should include penetration testing, vulnerability scanning and risk analysis processes to identify weaknesses and develop strategies for mitigation. 

Protecting customer privacy should be the top priority for any business handling sensitive financial data. Tax prep companies have a responsibility to ensure the security of their clients’ data. They must consider the evolving threat landscape and improve their security protocols as needed. When these companies fail to meet this responsibility, it is important that clients themselves are informed, know how to implement proper security protocols, and continue to advocate for stronger data privacy protections.

https://www.securitymagazine.com/blogs/14-security-blog/post/100584-is-your-financial-data-safe-this-tax-season

Framework’s software and firmware have been a mess, but it’s working on them

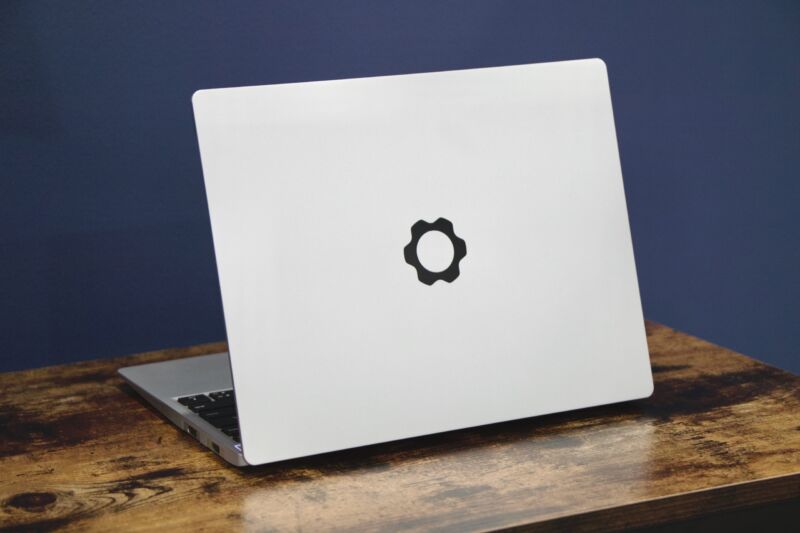
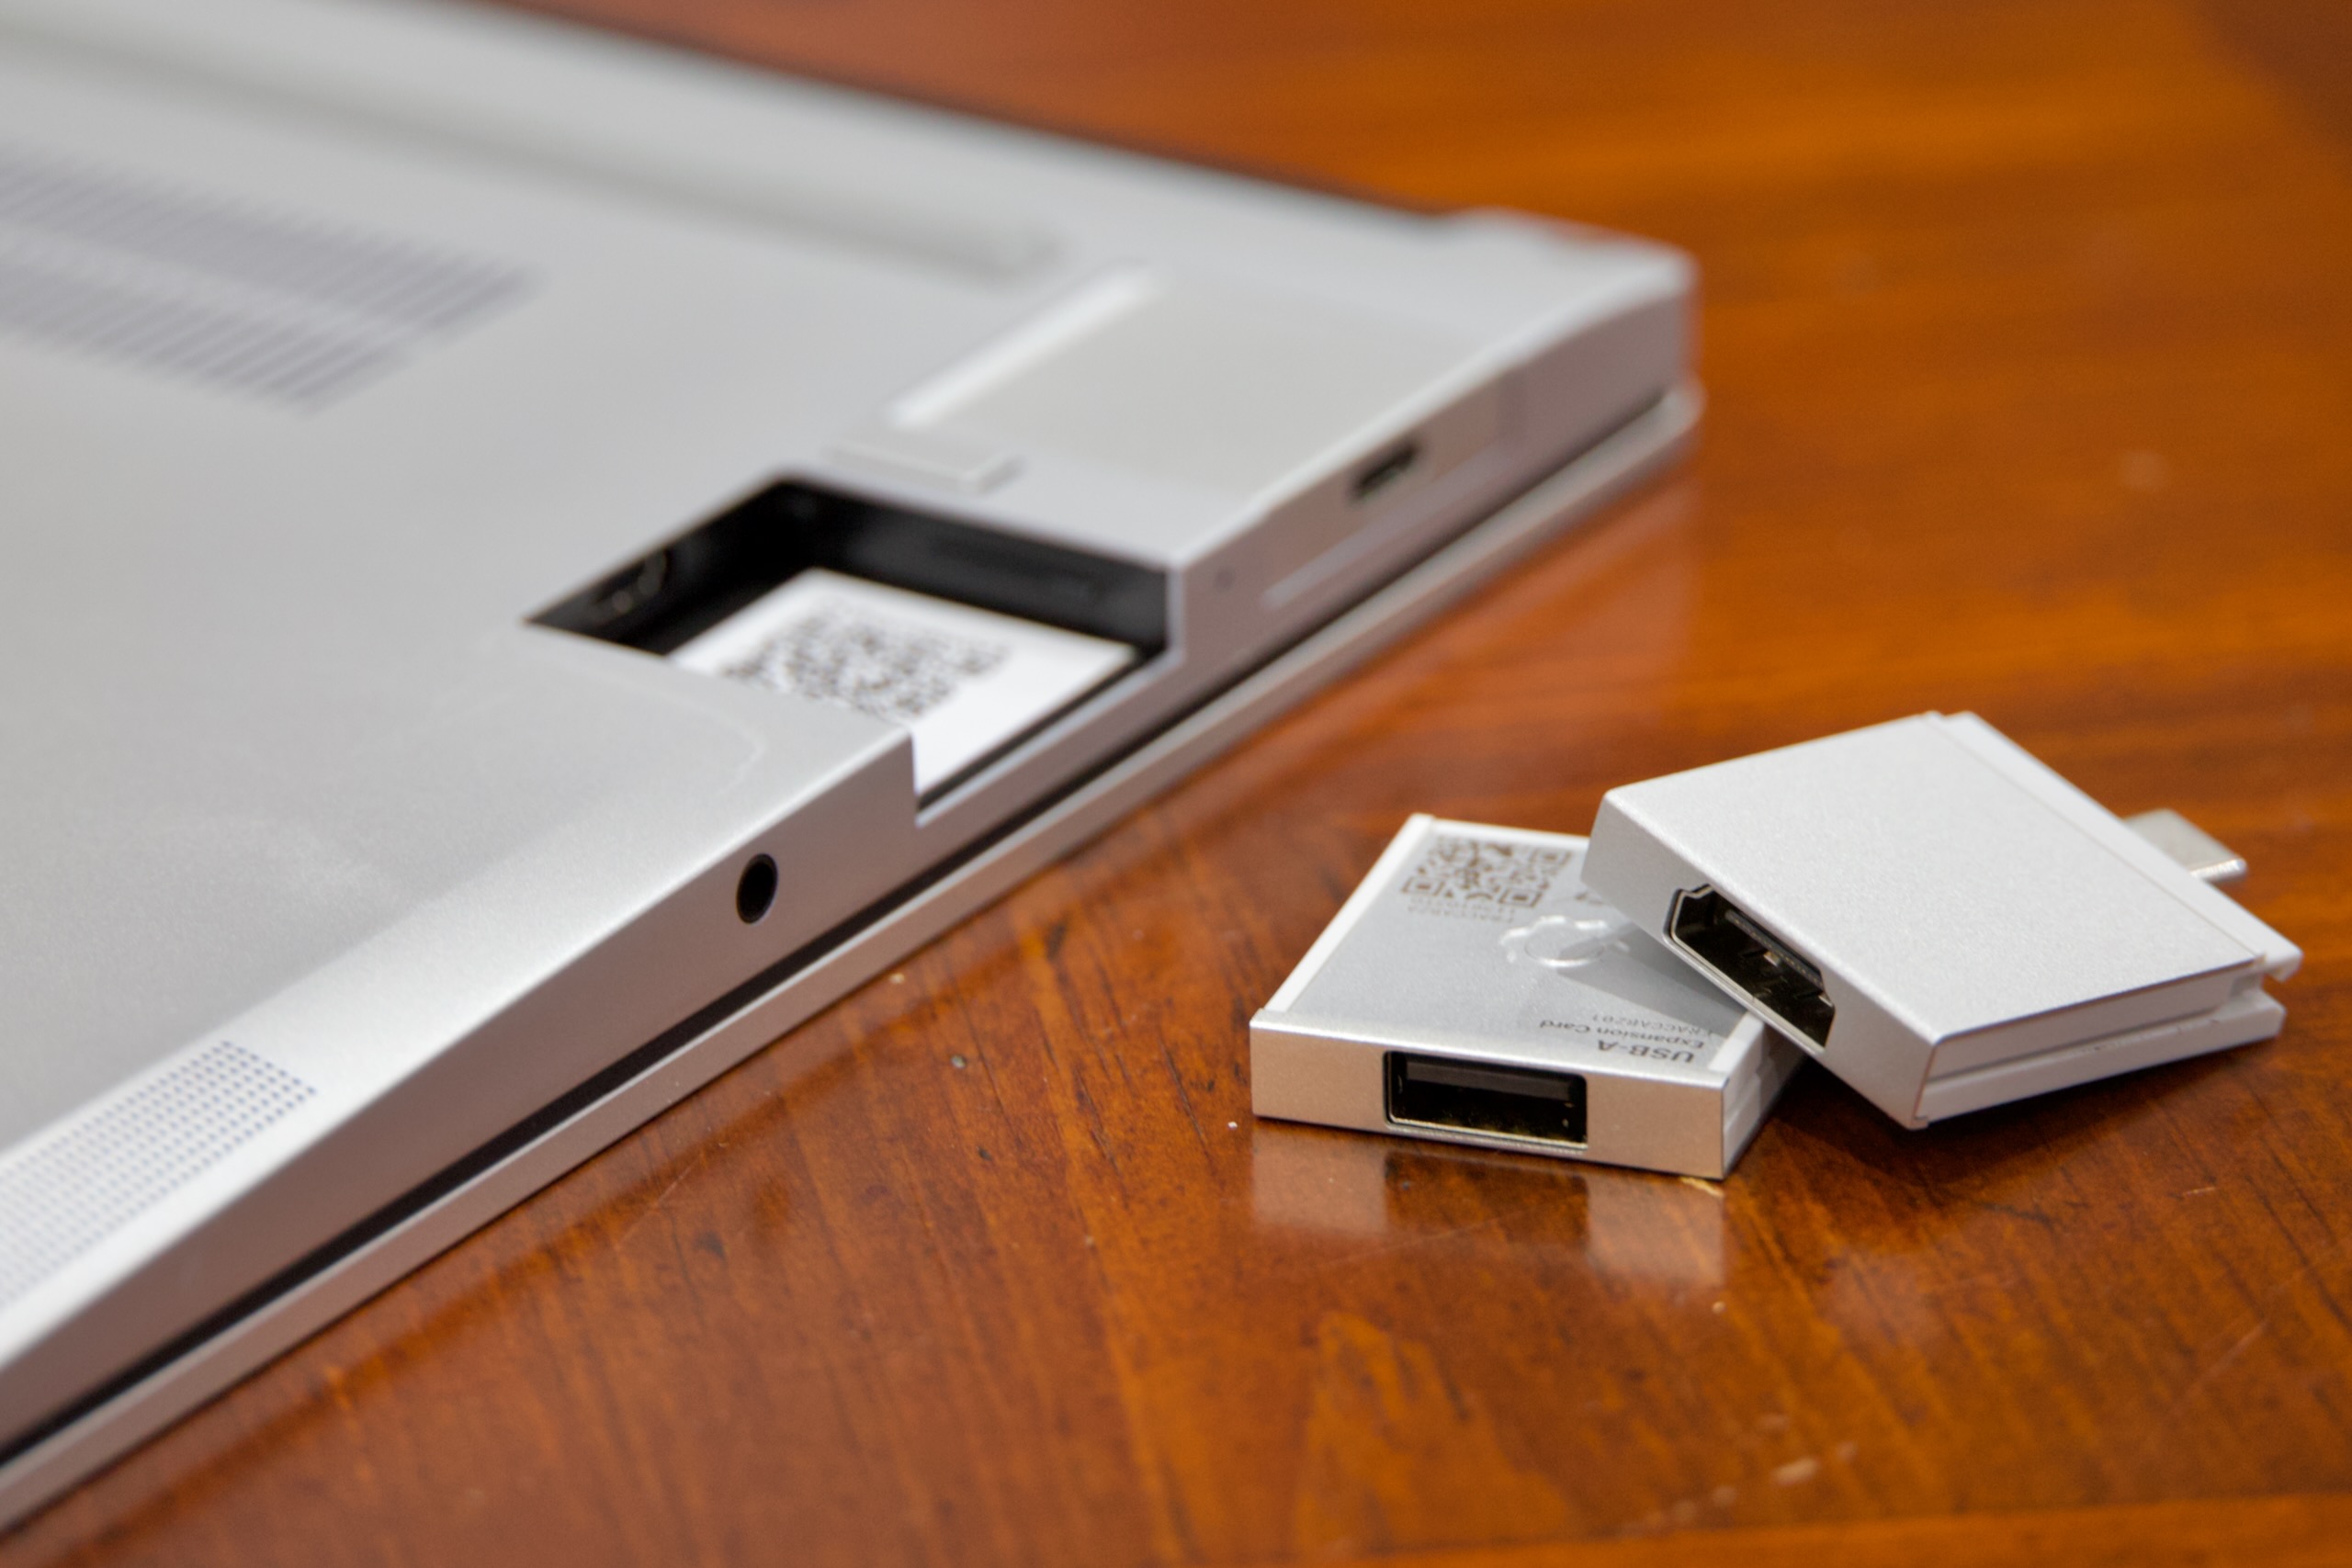
The Framework Laptop 13.
Enlarge / The Framework Laptop 13.
Andrew Cunningham

Since Framework showed off its first prototypes in February 2021, we’ve generally been fans of the company’s modular, repairable, upgradeable laptops.

Not that the company’s hardware releases to date have been perfect—each Framework Laptop 13 model has had quirks and flaws that range from minor to quite significant, and the Laptop 16’s upsides struggle to balance its downsides. But the hardware mostly does a good job of functioning as a regular laptop while being much more tinkerer-friendly than your typical MacBook, XPS, or ThinkPad.

But even as it builds new upgrades for its systems, expands sales of refurbished and B-stock hardware as budget options, and promotes the re-use of its products via external enclosures, Framework has struggled with the other side of computing longevity and sustainability: providing up-to-date software.

Driver bundles remain un-updated for years after their initial release. BIOS updates go through long and confusing beta processes, keeping users from getting feature improvements, bug fixes, and security updates. In its community support forums, Framework employees, including founder and CEO Nirav Patel, have acknowledged these issues and promised fixes but have remained inconsistent and vague about actual timelines.

But according to Patel, the company is working on fixing these issues, and it has taken some steps to address them. We spoke to him about the causes of and the solutions to these issues, and the company’s approach to the software side of its efforts to promote repairability and upgradeability.

Promises made

Here’s a case in point: the 12th-generation Intel version of the Framework Laptop 13, which prompted me to start monitoring Framework’s software and firmware updates in the first place.

In November 2022, Patel announced that this model, then the latest version, was getting a nice, free-of-charge spec bump. All four of the laptop’s recessed USB-C ports would now become full-speed Thunderbolt ports. This wasn’t a dramatic functional change, especially for people who were mostly using those ports for basic Framework expansion modules like USB-A or HDMI, but the upgrade opened the door to high-speed external accessories, and all it would need was a BIOS update.

The recessed USB-C ports in the 12th-gen Intel version of the Framework Laptop 13 can be upgraded to fully certified Thunderbolt ports, but only if you're willing to install one in a long series of still-in-testing beta BIOSes.
Enlarge / The recessed USB-C ports in the 12th-gen Intel version of the Framework Laptop 13 can be upgraded to fully certified Thunderbolt ports, but only if you’re willing to install one in a long series of still-in-testing beta BIOSes.
Andrew Cunningham

A final version of this BIOS update finally showed up this week, nearly a year and a half later. Up until last week, Framework’s support page for that 12th-gen Intel laptop still said that there was “no new BIOS available” for a laptop that began shipping in the summer of 2022. This factory-installed BIOS, version 3.04, also didn’t include fixes for the LogoFAIL UEFI security vulnerability or any other firmware-based security patches that have cropped up in the last year and a half.

And it’s not just that the updates don’t come out in a timely way; the company has been bad about estimating when they might come out. That old12th-gen Framework BIOS also didn’t support the 61 WHr battery that the company released in early 2023 alongside the 13th-gen Intel refresh. Framework originally told me that BIOS update would be out in May of 2023. A battery-supporting update for the 11th-gen Intel version was also promised in May 2023; it came out this past January.

Framework has been trying, but it keeps running into issues. A beta 3.06 BIOS update with the promised improvements for the 12th-gen Intel Framework Laptop was posted back in December of 2022, but a final version was never released. The newer 3.08 BIOS beta entered testing in January 2024 but still gave users some problems. Users would go for weeks or months without any communication from anyone at Framework.

The result is multiple long forum threads of frustrated users asking for updates, interspersed with not-untrue but unsatisfying responses from Framework employees (some version of “we’re a small company” is one of the most common).

https://arstechnica.com/?p=2012352


Le aziende italiane peccano nella sicurezza degli ambienti OT


Il 41% delle imprese italiane subisce mensilmente attacchi informatici agli ambienti di tecnologia operativa (OT), e nonostante ciò solo il 28% di esse considera la sicurezza OT una priorità.

L’ultimo report di Palo Alto Networks, “The State of OT Security: a Comprehensive Guide to Trends, Risks, and Cyber Resilience”, evidenzia un panorama piuttosto preoccupante: mentre le minacce alle sicurezza degli ambienti industriali aumentano in numero e gravità, l’impegno delle imprese italiane non è sufficiente per contrastarle, col risultato che il livello di resilienza aziendale è molto basso.

“L’Italia è un’economia leader nell’automazione industriale, con una scala globale e molte infrastrutture critiche. Per mantenere questa posizione di forza anche in futuro, l’OT industriale deve essere protetto. Questo report spiega perché gli ambienti OT sono diventati un obiettivo così attraente nelle operazioni industriali: la loro complessità e un’architettura tecnologica frammentata li rendono vulnerabili ad attacchi informatici che possono avere immense implicazioni finanziarie e politiche” ha affermato Helmut Reisinger, CEO EMEA e LATAM di Palo Alto Networks.

Gli ambienti OT sono molto interessanti per i cybercriminali: un attacco riuscito nelle realtà industriale può avere gravi conseguenze sull’economia e sulla società. Solo nell’ultimo anno il 72% delle imprese italiane ha subito un attacco informatico OT, con il 42% che afferma che ciò avviene su base mensile, e il 20% di esse ha dovuto interrompere le operazioni dopo l’incidente.

I tipi di attacchi che prendono di mira le attività industriali variano, ma malware, ransomware e la presenza di APT rimangono quelli che preoccupano maggiormente gli esperti di cybersecurity. Un’altra ricerca di Unit 42, il team di threat intelligence di Palo Alto Networks, ha rilevato che il settore manifatturiero italiano è il più colpito dal ransomware, rappresentando il 20% di tutti gli attacchi ransomware in Italia nel 2023.

L’IA affascina e spaventa le aziende

Il 74% degli intervistati italiani considera gli attacchi basati su intelligenza artificiale alle infrastrutture OT un problema critico già oggi, mentre il 58% afferma che lo diventeranno nei prossimi tre anni.

C’è comunque un consenso generale sul fatto che le soluzioni abilitate da IA svolgeranno un ruolo centrale nel proteggere gli ambienti OT: l’85% degli intervistati ritiene che le soluzioni basate su IA saranno fondamentali per bloccare gli attacchi alle infrastrutture, e il 73% delle aziende ritiene che lo saranno anche i SOC.

La metà delle imprese prevede inoltre che l’IA nelle soluzioni di protezione OT contribuirà a risolvere le carenze di competenze in materia di sicurezza nei prossimi anni.

La complessità OT ostacola l’adozione di soluzioni di sicurezza

Il 60% delle aziende italiane ritiene che la sfida principale nell’acquisto di software e nell’implementazione di apparati per la sicurezza OT è la complessità dei prodotti, evidenziando la necessità di tecnologie più semplici. Un’altra delle difficoltà maggiori riscontrate dalle imprese è la carenza di esperti qualificati in sicurezza OT, evidenziata dal 53% degli intervistati.

Semplificare le architetture e adottando un approccio alla cybersecurity basato sulla piattaforma è possibile proteggere in modo più efficace gli ambienti complessi; per questo la maggior parte delle aziende italiane (76%) ha in previsione di consolidare le tecnologie di sicurezza IT e OT e ridurre i rischi insiti negli ambienti.

“Con la crescita del volume e della sofisticazione degli attacchi informatici, la necessità di rafforzare la resilienza informatica degli ambienti OT non è mai stata così critica. Affrontare questa sfida richiede uno stretto coordinamento e allineamento tra i team IT e OT per ottenere risultati migliori in termini di cybersecurity” ha dichiarato Michele Lamartina, Country Manager di Palo Alto Networks Italia e Malta. “Ciò richiede l’abbattimento dei tradizionali silos e l’adozione di un approccio più unificato con strategie di sicurezza olistiche, policy e piattaforme che affrontino vulnerabilità e rischi insiti in entrambi gli ambienti”.

Michele Lamartina, Country Manager di Palo Alto Networks Italia e Malta

Michele Lamartina, Country Manager di Palo Alto Networks Italia e Malta

Umberto Pirovano, Senior Manager Systems Engineering di Palo Alto Networks, evidenzia comunque una situazione incoraggiante dal punto di vista degli sforzi delle aziende italiane: il 75% degli intervistati dispone già di un piano di risposta agli incidenti OT, mentre il 58% prevede di aumentare gli investimenti in cybersicurezza OT nei prossimi due anni.

“Palo Alto Networks continua nel suo impegno a supportare tutti i clienti nella creazione di framework di sicurezza IT e OT che promuovano la convergenza, riducano la complessità, salvaguardino l’infrastruttura e mitighino le minacce in continua evoluzione” ha affermato Pirovano.

Condividi l’articolo


Articoli correlati

Altro in questa categoria


https://www.securityinfo.it/2024/04/15/le-aziende-italiane-peccano-nella-sicurezza-degli-ambienti-ot/?utm_source=rss&utm_medium=rss&utm_campaign=le-aziende-italiane-peccano-nella-sicurezza-degli-ambienti-ot


Potenziare la Sicurezza Digitale in Italia: il contributo di Cinetix

Le interazioni di natura digitale, su rete pubblica o all’interno di reti private, hanno assunto un ruolo predominante nelle relazioni sia interpersonali che di business. Per questo è fondamentale intervenire affinché il tutto possa avvenire in un ambiente online sicuro. Per le reti pubbliche, le recenti disposizioni di legge hanno imposto agli operatori (ISP, Internet Service Providers) di rafforzare i loro servizi a tutela dei diritti in due ambiti specifici:

  1. il Parental Control
  2. il Diritto d’autore (Anti-pirateria)

La responsabilità di ottemperare a queste normative ricade sugli ISP e l’implementazione di questi sistemi richiede soluzioni tecniche robuste ed affidabili.

Cinetix, ingaggiata in questi progetti da un’importante azienda di telecomunicazioni Italiana, ha risposto prontamente grazie al suo duplice ruolo di system integrator e di fornitore di dispositivi avanzati (con i network packet broker) che nelle loro funzionalità prevedono anche il blocco degli indirizzi IP.

Parental Control: proteggere gli utenti più giovani dai rischi della rete

La proliferazione dell’accesso ad Internet tra i minori ha sollevato preoccupazioni riguardo alla loro esposizione a contenuti inappropriati. Riconoscendo ciò, i legislatori hanno imposto agli ISP di offrire gratuitamente il servizio di Parental Control ai propri abbonati. Il cliente di Cinetix ha richiesto una soluzione che fosse efficace ed allo stesso tempo semplice da usare.

Cinetix, in sinergia con l’ISP, ha condotto in una prima fase un’analisi di mercato per identificare una componente di base della soluzione da integrare con le proprie componenti e che fosse rispondente alla normativa italiana, in linea con i requisiti tecnici del Cliente e tale da rispettare i tempi dell’entrata in vigore. Tra le soluzioni visionate, la scelta è ricaduta su Peacemaker di Whalebone1, soluzione caratterizzata da approccio innovativo che si basa sul processo di risoluzione2 del DNS. La piattaforma, pienamente integrata nell’architettura di rete dell’azienda cliente, consente un filtraggio flessibile basato su categorie di contenuti, garantendo nel contempo la conformità agli standard normativi stabiliti da AGCOM.

L’architettura del sistema realizzato comprende un mix di risorse on-premises e cloud:

  • un DNS resolver locale assicura un servizio ininterrotto anche in assenza di connettività verso il cloud
  • algoritmi di AI e di Machine Learning garantiscono una previsione avanzata ed un’azione proattiva delle minacce correnti e future

Anti-pirateria: combattere la distribuzione di streaming illeciti

La diffusione sempre maggiore di contenuti piratati ha spinto all’azione legislativa per arginare le attività di streaming illegali. Cinetix ha implementato una soluzione anti-pirateria completa, arginando le attività di condivisione di streaming non autorizzati che permettevano di accedere illegalmente a contenuti televisivi a pagamento, senza aver sottoscritto un regolare abbonamento.

Utilizzando ancora il mix tra le capacità di Peacemaker per il blocco FQDN e la tecnologia Aster di Cinetix per il blocco degli indirizzi IP, il cliente ha a disposizione un meccanismo solido di difesa contro la diffusione dei contenuti illegali. La piattaforma, alimentata dall’infrastruttura di AGCOM “Piracy Shield”, consente il blocco degli indirizzi segnalati entro i tempi rigorosi definiti dalla normativa (30 minuti dalla segnalazione).

L’adozione del software di monitoraggio Dardo, sviluppato dal reparto R&D di Cinetix, consente di ottimizzare la gestione di tutti i dispositivi hardware impegnati dalle continue richieste di blocco di domini e indirizzi IP.

Le possibili evoluzioni

Grazie alla sua solidità di base, la soluzione realizzata si presta ad un ampio insieme di estensioni funzionali che rientrano nell’ambito della Cyber Security:

  • la protezione da attacchi malevoli per tutti i dipendenti quando questi operano al di fuori dalla rete aziendale (lavoro remoto)
  • la segnalazione, a protezione dell’identità degli utenti, di account trafugati e trattati su siti di dark web
  • il miglioramento della sicurezza per tutti i dispositivi di tipo IoT che sono di sempre maggiore utilizzo.

In questo scenario sempre più digitale ed in evoluzione, l’attenzione alla innovazione è fondamentale. Per garantire un futuro digitale più sicuro e salvaguardare i propri ecosistemi online, è strategica la collaborazione con partner tecnologici come Cinetix che fornisce soluzioni end-to-end per il monitoraggio ed il controllo del traffico nonché la salvaguardia e la sicurezza dei dati aziendali.

Note

1 Whalebone è un’azienda della Repubblica Ceca di cybersecurity e protezione della vita digitale. Dal 2016, Whalebone fornisce sicurezza DNS in tempo reale a più di 300 telco, ISP, imprese e istituzioni in tutto il mondo, proteggendo gli utenti di Internet dalle minacce informatiche attraverso una combinazione di threat intelligence e machine learning.

2 Il DNS (Domain Name System) è il servizio Intenet che assicura la traduzione (risoluzione) dei nomi di dominio (ad esempio www.esempio.com) nel corrispondente indirizzo IP (ad esempio 192.0.2.1), cosa necessaria per consentire la navigazione. L’utenza di internet può inserire il nome del dominio nella barra degli indirizzi del proprio browser ed il DNS, funzionando come una sorta di rubrica telefonica, lo traduce in un indirizzo IP numerico riconosciuto dalla rete.

Condividi sui Social Network:

https://www.ictsecuritymagazine.com/notizie/potenziare-la-sicurezza-digitale-in-italia-il-contributo-di-cinetix/


Stay a step ahead with the missing link in cybercrime defense: OSINT

Chief Information Security Officers (CISOs) require a comprehensive set of tools, services and skilled people to succeed in the never-ending battle against cybercrime. They stand as the last line of defense to protect their organizations from losing data, money, reputation and, in extreme cases, the business itself. Adding OSINT-driven threat intelligence to the CISO toolkit can be a game-changer, delivering insights that enable a more proactive rather than reactive approach to cybercrime defenses.

Whether launched by criminal syndicates, nation-states or their proxies, ransomware and other forms of cybercrime have become a constant threat that requires real-time analysis and defense to effectively identify, mitigate and counter these attacks. To minimize risks and avoid surprises, CISOs must utilize technical tools and expertise, as well as threat intelligence to gain predictive insights on cybercrimes.

CISOs commonly adopt a two-pronged strategy. The first approach is to use technical tools and expertise, sometimes as a security operations center (SOC), either internally or as a service. The second is to educate and develop IT personnel and other staff who should be able to detect phishing and business email compromise (BEC) attacks in their day-to-day work. Open-source intelligence (OSINT) can be the missing third prong of an effective cybersecurity strategy. 

The intersection of OSINT and cybersecurity

OSINT is the process of collecting, filtering and analyzing publicly and commercially available data from across the surface web, the deep web and the dark web. It has recently grown in popularity as a primary intelligence discipline in national security and defense circles due to the need to quickly detect risks across overwhelming and exponentially increasing volumes of online data and is now being adopted in the corporate sector as well for similar reasons. 

The open web consists of the sites people use daily, which everyone can access, such as public websites, social media sites, chat groups and discussion forums. The deep web constitutes the hidden part of the web that is not indexed by traditional search engines, including sites are secured with some form of protection, such as passwords or additional security measures to ensure only authorized people can gain access. The dark web has a mystical aura but is simply a part of the encrypted internet and is only accessible with specialized tools, such as The Onion Router, or “Tor.” What gives the dark web its aura are the criminal actors that take advantage of its anonymity to share information and plan attacks.

With specialized OSINT capabilities, SOC teams scan the dark web chatter between cybercriminals, extracting volumes of information on their activities. The discussions range from what new or improved tools and techniques are available to which companies or industries are in the spotlight, new data on supply chain vulnerabilities to exploit and more. It is also possible to identify breaches almost immediately after they occur when people boast about their achievements or release personal information or intellectual property.

Large volumes of data are collected in this manner and analyzed to deliver usable information. The growth of artificial intelligence (AI) augments this analysis as algorithms can pick up trends and indicators that are undetectable by human analysts. 

Cybercrime insights hidden in plain sight

Many ransomware gangs are starting to post data stolen from their victims on the open web to encourage them to pay up because their data is potentially exposed to over 2 billion people using the web each day. Although unfortunate for the victims, this situation can provide valuable data analysis and intelligence-gathering information. It highlights compromised companies, information, passwords and newly found vulnerabilities.

OSINT threat intelligence also aids in supply chain risk management, delivering relevant insights about partners, service providers and other companies along the supply chain. A cloud provider, for example, could be under attack, which, if successful, will impact its customers’ ability to operate. Similarly, compromised downstream partners, such as retail outlets or resellers, can pose unique threats to an organization’s operations.

Without OSINT threat intelligence to enhance their cybersecurity strategies, corporations lose a critical edge in their proactive defense posture, leaving them at risk of data loss, brand reputation damage, compliance fines, revenue loss and more.

Pre-emptive defense strategies – the role of OSINT

The need for OSINT is not secondary to cybercrime tools, education and skills; it supplements, supports and enhances cybersecurity strategy with intelligence on attackers’ targets, malware, motivations, methods and more. Effective OSINT solutions enable the practical use of AI-enabled analytics by filtering mountains of data to identify and alert suspicious activities that may indicate an imminent breach.

The State of Ransomware 2023 report highlights that “an exploited vulnerability was the most common root cause of ransomware attacks (36%), followed by compromised credentials (29%).” Only 3% were due to a brute force attack — what most people define as hacking. OSINT threat intelligence, therefore, can potentially play a vital role in helping to prevent more than 50% of ransomware attacks. 

People like to talk, and cyber criminals are no different; perhaps they are even more inclined to boast when defeating a large corporation. OSINT specialists within SOCs can gain insights into what industries and companies are being targeted, newly released malware and what new vulnerabilities they exploit — even before the Cybersecurity and Infrastructure Security Agency (CISA) or law enforcement agencies release a public warning.

More than data loss

Corporate governance, risk management and compliance are critical factors affecting corporate reputation and the sentiment of stakeholders, especially investors. Similarly, cyber resilience quickly evolved into a reputational influencer. Publicly traded companies must now report material cyber breaches within four days, and annual reports must include information on the business’s cyber governance and hygiene.

Managing their organization’s cybersecurity posture and dealing with constant threats, especially ransomware, places CISOs under extreme pressure. Coping with the demands is only possible if a cybersecurity strategy complemented by OSINT is integrated into technology platforms to deliver more timely and predictive insights about potential cyber risks facing the company and its supply chain. This strategy empowers CISOs to be prepared to proactively mitigate vulnerabilities.

https://www.securitymagazine.com/articles/100561-stay-a-step-ahead-with-the-missing-link-in-cybercrime-defense-osint


Redefining Security: Proactive Measures Transform Industrial Protection

In the era of automation and lean staffing, the significance of industrial security has escalated. Fewer onsite employees overseeing larger asset pools have inadvertently heightened the appeal of these sites to criminals. 

Concurrently, the demand for labor emphasizes the need to prioritize and visibly enhance employee safety, not just for compliance but as a critical component of workforce attraction and retention. Facing both sophisticated cyber and physical threats, industries are compelled to adopt a multi-layered security approach. This strategy ensures comprehensive protection against diverse risks, maintaining the integrity of assets and the safety of workers in an evolving threat landscape.

Today’s Industrial Security Challenges

The industrial sector faces a complex array of security challenges, extending far beyond the traditional concerns of theft and vandalism. A notable challenge arises from the frequently insufficient police response time, potentially exposing businesses to vulnerability during crucial moments. This delay in law enforcement support highlights the imperative for industries to implement comprehensive, proactive security measures. Given the strain on police resources, dual verification may be necessary for them to effectively respond to threats.

Internal risks, such as employee misconduct, further complicate the security landscape. These can range from theft and sabotage to negligence, posing a multifaceted threat to operations and safety. Moreover, the reliance on human security guards introduces variables of human error and inconsistency. Guards, while essential, may not offer the continuous, unfailing surveillance required to deter or detect sophisticated criminal activities.

Another critical challenge is the prevalence of reactive security measures within the industry. Traditional security systems, which often alert businesses only after a breach has occurred, are proving inadequate. This reactive approach fails to prevent unauthorized access or damage, highlighting the urgent need for preventative strategies that can stop incidents before they unfold.

Additionally, technological vulnerabilities, such as cyber-attacks targeting industrial control systems, have emerged as a significant threat. The convergence of physical and cyber security risks demands a more integrated approach to industrial security, one that can address the full spectrum of potential threats.

These challenges illustrate the complexity of securing industrial environments. They necessitate a nuanced, comprehensive security strategy that not only responds to incidents but actively works to prevent them, ensuring a secure and resilient industrial environment.

A Case for a Proactive and Layered Industrial Security Protocol

In the face of these diverse challenges, protecting industrial assets requires a multifaceted strategy. Perimeter security, including advanced solutions like electric fencing, forms the initial defense layer, deterring potential intruders with a visible barrier that also acts as a psychological deterrent. 

However, given the limitations of police response and the potential for human error in guard-based security, integrating technology becomes crucial. Access control systems and surveillance technologies offer continuous, reliable monitoring and management of entry points, significantly reducing the risk of unauthorized access.

Moreover, the adoption of intelligent surveillance systems equipped with motion sensors and AI-driven anomaly detection can preemptively identify potential security breaches, offering a substantial improvement over reactive security measures. These systems can analyze patterns and alert security personnel to unusual activities, effectively reducing the reliance on human vigilance alone.

The integration of cyber security measures is equally important, especially as industrial operations become more reliant on digital technologies. Protecting the digital interfaces of physical security systems from hacking and ensuring the security of industrial control systems are critical components of a comprehensive asset protection strategy.

Ensuring Worker Safety

Worker safety is integral to industrial security, necessitating measures that extend beyond the protection of physical assets. The implementation of emergency response protocols is essential, providing clear, actionable steps in the event of an incident. Training and education programs equip workers with the knowledge to recognize potential security risks and respond appropriately.

Personal Protective Equipment (PPE) and regular safety drills reinforce a proactive approach to safety, preparing employees for a variety of scenarios. However, the challenge of maintaining consistency and reducing human error remains. To address this, industries are increasingly leveraging technology, such as wearable safety devices that monitor workers’ health and environmental conditions, providing real-time data to prevent accidents before they occur.

Integrating these technologies with traditional safety measures creates a comprehensive safety ecosystem that prioritizes worker well-being. This approach not only ensures compliance with safety regulations but also contributes to a culture of safety that is attractive to current and prospective employees, addressing the critical need for labor in an era of automation and lean staffing.

Together, these strategies for protecting assets and ensuring worker safety reflect a holistic approach to industrial security. By addressing both physical and cyber threats with a blend of technological and human-centric solutions, industries can create a secure and resilient environment that safeguards both their assets and their most valuable resource: their workers.

Companies Putting This Security Standard into Practice

Transportation Company’s Battle Against Catalytic Converter Theft

A prominent transportation company, with a significant business unit in busing, faced relentless catalytic converter thefts across multiple locations. Despite implementing a variety of reactive security measures, including surveillance cameras and infrared beams, the thefts persisted, occurring with alarming regularity every weekend. 

The turning point came with the adoption of preventative security measures, notably electric fencing, which effectively halted theft incidents. This shift from reactive to proactive security underscored the critical importance of anticipating and preventing criminal activity before it could occur, dramatically enhancing the company’s asset protection without altering its business operations.

Scaling Security with Uniform Preventative Measures

A company heavily reliant on third-party security guards encountered significant challenges in scaling its operations. The effectiveness of the guards varied widely across different cities and states, leading to inconsistent security outcomes. 

By transitioning to a more uniform security solution that included cameras, talk-down speakers, and electric fencing as a preventative measure, the company not only standardized its security approach but also significantly reduced its security-related expenditures. This strategic overhaul improved security outcomes across all locations, demonstrating the value of a cohesive and preventative security strategy in achieving scalable and reliable protection.

A Look at The Future of Industrial Security

These case studies highlight a shift towards more innovative and integrated security solutions in the industrial and commercial sectors. The successful implementation of electric fencing and other preventative measures points to a broader trend: the increasing reliance on technology-driven security systems that preempt rather than react to threats. This evolution suggests several future trends:

  1. Integration of Physical and Cybersecurity Measures: As physical security solutions become more technologically advanced, their integration with cybersecurity measures will become more seamless, offering comprehensive protection against a range of threats.
  2. Advanced Anomaly Detection: The use of AI and machine learning for anomaly detection will become more sophisticated, allowing businesses to identify and respond to potential threats with greater accuracy and speed.
  3. Automation in Security Monitoring: The automation of security monitoring, through drones and AI-driven surveillance, will enhance the ability to oversee large and complex operations efficiently, reducing the reliance on human monitoring.
  4. Customized Security Solutions: The trend towards tailored security solutions, as demonstrated by the case studies, will grow, with businesses seeking security setups that address their specific vulnerabilities and operational needs.
  5. Sustainability in Security: As environmental considerations become increasingly important, the development of sustainable security solutions that minimize ecological impact while maximizing protection will gain momentum.

These trends indicate a move towards more proactive, technology-enabled security strategies that prioritize early detection and prevention, ensuring robust protection for assets and workers alike.

In conclusion, the evolving landscape of industrial and commercial security, characterized by sophisticated threats and the need for scalable solutions, underscores the importance of a proactive, multi-layered approach to security. The case studies of a transportation company and a business reliant on third-party guards illustrate the transformative impact of adopting preventative security measures, such as electric fencing and integrated technology solutions. These examples not only highlight the effectiveness of such measures in stopping crime and improving operational scalability but also point towards future trends in security: a greater integration of technology, customization, and sustainability. As businesses navigate this complex terrain, the adoption of advanced, reliable security strategies will be paramount in safeguarding both assets and workers, ensuring the resilience and sustainability of operations in the face of emerging challenges.

Would you like a free threat assessment of your property with a security expert? Identify your current level of susceptibility to property theft, damage or unwanted intrusion.  Request yours here.

h3 { font-weight: bold; font-size: 18px; color: #C72026; }

https://www.securitymagazine.com/articles/100583-redefining-security-proactive-measures-transform-industrial-protection


Building cyber resilience through cyber tabletop exercises

.w3-panel:after,.w3-panel:before { content: ""; display: table; clear: both } .w3-panel { padding: 16px; margin-top: 16px; margin-bottom: 16px } .w3-leftbar { border-left: 6px solid #660066!important } .w3-color,.w3-hover-color:hover { color: #660066!important; background-color: #f9ecf2!important } .w3-large { font-size: 20px!important } .w3-sans-serif { font-family: 'Nunito Sans',Arial,sans-serif } .w3-opacity,.w3-hover-opacity:hover { opacity: 0.60 }

Regular Cyber Tabletop Exercise (CTTX) drills act like a cyberattack simulation, revealing vulnerabilities and honing response skills before real attacks strike. By simulating diverse threats, from phishing scams to ransomware outbreaks, CTTX expose gaps in plans and strengthen overall organizational resiliency. A cybersecurity sandbox lets organizations refine their incident response playbook and ensure seamless integration with broader security strategies.

Imagine peering into a microscope to examine the inner-workings of a cyberattack. CTTX do just that, offering a magnified view of how cyber threats might infiltrate your organization’s critical functions.

Participants actively engage in simulated scenarios, from phishing scams to ransomware outbreaks. This hands-on approach sheds light on potential disruptions to business processes, revenue streams, customer trust and overall resilience.

CTTX breaks down departmental walls, fostering collaboration and refining crucial incident response skills. This is crucially important, as ISACA’s State of Cybersecurity 2023 report shows that incident response rates are among the most urgently needed technical skills on the cybersecurity landscape. Through CTTX, teams learn to seamlessly synchronize their roles while participants sharpen communication under pressure, ensuring clear and timely information flow to all stakeholders — both internal and external — during a real cyber event.

The learning does not stop with the simulation. Observations, feedback and debrief sessions fuel continuous improvement. Scenarios and materials are refined based on lessons learned, ensuring CTTX remains relevant and impactful.

Regularly scheduled exercises, integration with training programs and collaboration with external partners all contribute to a more robust CTTX program. This comprehensive approach ensures your organization is constantly evolving its defenses against ever-changing cyber threats.

But how do you know if your CTTX program is working? Key performance indicators (KPIs) provide quantifiable metrics to track progress and demonstrate the value of your preparedness efforts. This transparency and accountability keep everyone invested in building a cyber-resilient organization.

In essence, CTTX is not just a simulation; it’s a proactive investment in your organization’s future. By unearthing vulnerabilities, fostering continuous improvement and measuring success, CTTX equips you to face the ever-evolving landscape of cyber threats with confidence.

❝

In essence, CTTX is not just a simulation; it’s a proactive investment in your organization’s future.”

The following key steps provide a comprehensive guide to establishing an effective CTTX program:

  1. LAY THE FOUNDATION:

    • Set Clear Goals: Define what you want to achieve through CTTX. Target specific cybersecurity areas and business resilience aspects for testing and improvement.
    • Assemble the A-Team: Form a cross-functional planning team with diverse expertise from IT, security, business continuity, legal, communications and more. This ensures a holistic approach to cyber threats and resilience.
    • Prioritize the Threats: Analyze your risk landscape and prioritize scenarios based on their potential impact on critical functions and overall resilience.
  2. CRAFT COMPELLING SCENARIOS:

    • Develop Realistic Simulations: Create believable cyber threat scenarios aligned with your risk profile and objectives. Think phishing attacks, ransomware outbreaks, data breaches and system outages.
    • Gather the Tools: Prepare comprehensive exercise materials, including scenario descriptions, additional information injections and supporting documentation.
  3. RUN THE DRILL:

    • Expert Facilitation: Assign a skilled facilitator to guide participants through each stage of the simulated incident response process.
    • Continuous Feedback: Capture both strengths and weaknesses by documenting observations and participant feedback during the exercise. Dedicate debrief sessions to discuss participants’ experiences and gather insights for future improvements.
  4. MEASURE AND REPORT SUCCESS. A FEW KPIS TO CONSIDER ARE:

    • Number of vulnerabilities identified and remediated: Tracks the program’s ability to uncover weaknesses in your defenses.
    • Improvement in incident response time: Measures the effectiveness of your response procedures after CTTX exercises.
    • Reduction in simulated damage: Tracks the effectiveness of your response plans in mitigating simulated attacks.
    • Completion rate and attendance: Tracks participation and commitment to the CTTX program.
    • Improvement in security awareness and culture: Surveys can gauge changes in employee cybersecurity understanding and behavior.
  5. OPTIMIZE AND EVOLVE:

    • Test Your Resources: Use CTTX to evaluate resource allocation during cyber incidents. Analyze your management strategies for personnel, technology and financial resources.
    • Continuous Improvement: Implement an iterative feedback loop. Use observations and feedback to adjust scenarios, materials and processes, ensuring your CTTX program constantly evolves.
    • Measure and Report: Regularly track outcomes, improvements made and the overall impact on organizational readiness. Transparency and accountability keep everyone invested in building cyber resilience.

By following these steps, organizations can turn CTTX from a simulation into a powerful tool for building a robust and adaptable cyber defense. Think of CTTX as a high-octane training ground for your cyber defenses. These simulated attack scenarios, from phishing scams to ransomware outbreaks, expose vulnerabilities and hone response skills before real threats strike. In this controlled environment, organizations can test and integrate both cybersecurity measures and broader business continuity plans, forging a robust and adaptable shield against the ever-shifting landscape of cyber threats.

https://www.securitymagazine.com/articles/100580-building-cyber-resilience-through-cyber-tabletop-exercises


Change Healthcare faces another ransomware threat—and it looks credible

Medical Data Breach text write on keyboard isolated on laptop background

For months, Change Healthcare has faced an immensely messy ransomware debacle that has left hundreds of pharmacies and medical practices across the United States unable to process claims. Now, thanks to an apparent dispute within the ransomware criminal ecosystem, it may have just become far messier still.

In March, the ransomware group AlphV, which had claimed credit for encrypting Change Healthcare’s network and threatened to leak reams of the company’s sensitive health care data, received a $22 million payment—evidence, publicly captured on bitcoin’s blockchain, that Change Healthcare had very likely caved to its tormentors’ ransom demand, though the company has yet to confirm that it paid. But in a new definition of a worst-case ransomware, a different ransomware group claims to be holding Change Healthcare’s stolen data and is demanding a payment of their own.

Since Monday, RansomHub, a relatively new ransomware group, has posted to its dark-web site that it has 4 terabytes of Change Healthcare’s stolen data, which it threatened to sell to the “highest bidder” if Change Healthcare didn’t pay an unspecified ransom. RansomHub tells WIRED it is not affiliated with AlphV and “can’t say” how much it’s demanding as a ransom payment.

RansomHub initially declined to publish or provide WIRED any sample data from that stolen trove to prove its claim. But on Friday, a representative for the group sent WIRED several screenshots of what appeared to be patient records and a data-sharing contract for United Healthcare, which owns Change Healthcare, and Emdeon, which acquired Change Healthcare in 2014 and later took its name.

While WIRED could not fully confirm RansomHub’s claims, the samples suggest that this second extortion attempt against Change Healthcare may be more than an empty threat. “For anyone doubting that we have the data, and to anyone speculating the criticality and the sensitivity of the data, the images should be enough to show the magnitude and importance of the situation and clear the unrealistic and childish theories,” the RansomHub contact tells WIRED in an email.

Change Healthcare didn’t immediately respond to WIRED’s request for comment on RansomHub’s extortion demand.

Brett Callow, a ransomware analyst with security firm Emsisoft, says he believes AlphV did not originally publish any data from the incident, and the origin of RansomHub’s data is unclear. “I obviously don’t know whether the data is real—it could have been pulled from elsewhere—but nor do I see anything that indicates it may not be authentic,” he says of the data shared by RansomHub.

Jon DiMaggio, chief security strategist at threat intelligence firm Analyst1, says he believes RansomHub is “telling the truth and does have Change HealthCare’s data,” after reviewing the information sent to WIRED. While RansomHub is a new ransomware threat actor, DiMaggio says, they are quickly “gaining momentum.”

If RansomHub’s claims are real, it will mean that Change Healthcare’s already catastrophic ransomware ordeal has become a kind of cautionary tale about the dangers of trusting ransomware groups to follow through on their promises, even after a ransom is paid. In March, someone who goes by the name “notchy” posted to a Russian cybercriminal forum that AlphV had pocketed that $22 million payment and disappeared without sharing a commission with the “affiliate” hackers who typically partner with ransomware groups and often penetrate victims’ networks on their behalf.

https://arstechnica.com/?p=2017095


“Highly capable” hackers root corporate networks by exploiting firewall 0-day

The word ZERO-DAY is hidden amidst a screen filled with ones and zeroes.

Highly capable hackers are rooting multiple corporate networks by exploiting a maximum-severity zero-day vulnerability in a firewall product from Palo Alto Networks, researchers said Friday.

The vulnerability, which has been under active exploitation for at least two weeks now, allows the hackers with no authentication to execute malicious code with root privileges, the highest possible level of system access, researchers said. The extent of the compromise, along with the ease of exploitation, has earned the CVE-2024-3400 vulnerability the maximum severity rating of 10.0. The ongoing attacks are the latest in a rash of attacks aimed at firewalls, VPNs, and file-transfer appliances, which are popular targets because of their wealth of vulnerabilities and direct pipeline into the most sensitive parts of a network.

“Highly capable” UTA0218 likely to be joined by others

The zero-day is present in PAN-OS 10.2, PAN-OS 11.0, and/or PAN-OS 11.1 firewalls when they are configured to use both the GlobalProtect gateway and device telemetry. Palo Alto Networks has yet to patch the vulnerability but is urging affected customers to follow the workaround and mitigation guidance provided here. The advice includes enabling Threat ID 95187 for those with subscriptions to the company’s Threat Prevention service and ensuring vulnerability protection has been applied to their GlobalProtect interface. When that’s not possible, customers should temporarily disable telemetry until a patch is available.

Volexity, the security firm that discovered the zero-day attacks, said that it’s currently unable to tie the attackers to any previously known groups. However, based on the resources required and the organizations targeted, they are “highly capable” and likely backed by a nation-state. So far, only a single threat group—which Volexity tracks as UTA0218—is known to be leveraging the vulnerability in limited attacks. The company warned that as new groups learn of the vulnerability, CVE-2024-3400, is likely to come under mass exploitation, just as recent zero-days affecting products from the likes of Ivanti, Atlassian, Citrix, and Progress have in recent months.

“As with previous public disclosures of vulnerabilities in these kinds of devices, Volexity assesses that it is likely a spike in exploitation will be observed over the next few days by UTA0218 and potentially other threat actors who may develop exploits for this vulnerability,” company researchers wrote Friday. “This spike in activity will be driven by the urgency of this window of access closing due to mitigations and patches being deployed. It is therefore imperative that organizations act quickly to deploy recommended mitigations and perform compromise reviews of their devices to check whether further internal investigation of their networks is required.”

The earliest attacks Volexity has seen took place on March 26 in what company researchers suspect was UTA0218 testing the vulnerability by placing zero-byte files on firewall devices to validate exploitability. On April 7, the researchers observed the group trying unsuccessfully to install a backdoor on a customer’s firewall. Three days later, the group’s attacks were successfully deploying malicious payloads. Since then, the threat group has deployed custom, never-before-seen post-exploitation malware. The backdoor, which is written in the Python language, allows the attackers to use specially crafted network requests to execute additional commands on hacked devices.

https://arstechnica.com/?p=2017043


Cresce il numero di credenziali compromesse: bisogna istruire gli utenti


In occasione del Privacy Tour 2024, l’iniziativa del Garante della Protezione dei Dati Personali che mira a portare i temi del valore dei dati e dell’educazione al digitale nei piccoli centri, Kaspersky ha ancora una volta sottolineato l’importanza della sicurezza dei dati sensibili.

Il panorama delle minacce è sempre più preoccupante ed è necessario ridurre il digital gap e aumentare la consapevolezza sulla sicurezza informatica. Il team di Digital Footprint Intelligence di Kaspersky riporta che solo nel 2023 i data-stealer hanno compromesso 10.000.000 di dispositivi personali e aziendali, registrando un aumento del 643% negli ultimi tre anni.

Nonostante nel 2023 il numero di infezioni abbia subito solo un calo minimo (9%) rispetto al 2022, la richiesta di login e password da parte dei cybercriminali non accenna a diminuire. Kaspersky ritiene che il numero effettivo di infezioni sia più alto del misurato e dovrebbe raggiungere i 16.000.000 nel 2024.

Pexels

In media i cybercriminali rubano 50,9 credenziali per ogni dispositivo infetto e le riusano per attacchi informatici, vendita o distribuzione gratuita sul dark web. Negli ultimi 5 anni Kaspersky ha rilevato 443.000 siti web che hanno subito violazioni di credenziali.

Per quanto riguarda i dati del 2023, il dominio .com è il primo per numero di credenziali compromesse. In Europa, il dominio .it è al terzo posto con 4,2 milioni di account compromessi.

Il dark web pullula di credenziali in vendita

La vendita di credenziali compromesse è una parte significativa del mercato del dark web. Le credenziali solitamente comprendono login per social media, servizi bancari online, portafogli di criptovalute e servizi aziendali.

Il team Digital Footprint Intelligence ha rivelato quasi 40.000 post, in media 1.731 al mese, riguardanti la vendita di informazioni aziendali riservate con lo scopo di acquistare, vendere o diffondere i dati rubati. Anche i dati per accedere alle infrastrutture aziendali sono molto diffusi: tra gennaio 2022 e novembre 2023 Kaspersky ha contato più di 6.000 post, con una crescita media mensile pari al 16%.

“Il valore nel dark-web dei file di log con credenziali di accesso varia a seconda dell’interesse dei dati e del modo in cui vengono commercializzati. Le credenziali possono essere vendute tramite un servizio di abbonamento con aggiornamenti regolari, un cosiddetto “aggregatore”, per richieste specifiche, o tramite un “negozio” che vende credenziali di accesso acquisite di recente esclusivamente ad acquirenti selezionati. I prezzi in questi negozi partono di solito da 10 dollari per file di log” spiega Cesare D’Angelo, General Manager Italy & Mediterranean di Kaspersky. “Questo evidenzia quanto sia fondamentale sia per i singoli che per le aziende prestare sempre attenzione, soprattutto nel caso di grandi community di utenti online. Le credenziali divulgate rappresentano una grave minaccia, in quanto consentono ai criminali informatici di eseguire vari attacchi come accessi non autorizzati, social engineering o impersonificazione”.

Cesare D’Angelo, General Manager Italy & Mediterranean di Kaspersky

Cesare D’Angelo, General Manager Italy & Mediterranean di Kaspersky

I cybercriminali colpiscono i servizi di IA

In seguito alla rapida diffusione dei servizi online di intelligenza artificiale, i cybercriminali hanno cominciato a interessarsi alle credenziali per queste piattaforme. Kaspersky rivela che negli ultimi tre anni sono state compromesse 1.160.000 credenziali di accesso a Canva, strumento di progettazione grafica che integra l’IA.

I dati mostrano inoltre che tra il 2021 e il 2023 sono state compromesse quasi 668.000 credenziali di accesso ai servizi di OpenAI, compreso ChatGPT; in particolare, nel il numero di login e password compromesse è aumento di quasi 33 volte rispetto all’anno precedente.

Per proteggersi dai data-stealer è essenziale scegliere una soluzione di sicurezza completa e soprattutto istruire gli utenti sulle minacce più diffuse, aiutandoli a mettere in campo le migliori strategie di prevenzione.

Condividi l’articolo


Articoli correlati

Altro in questa categoria


https://www.securityinfo.it/2024/04/12/cresce-numero-credenziali-compromesse-istruire-utenti/?utm_source=rss&utm_medium=rss&utm_campaign=cresce-numero-credenziali-compromesse-istruire-utenti