Adapting to the latest SEC disclosures
The latest federal guidelines demand unwavering transparency and immediate action to safeguard organizations, stakeholders, customers, and communities. Cybersecurity teams must swiftly adapt to these new directives, while security leaders need to take charge and ensure full compliance with the updated regulations.

Last July, the Securities and Exchange Commission (SEC) published new cybersecurity disclosure requirements concerning cybersecurity incidents and their disclosures, which have been in effect since December. Now, companies must disclose any security incidents within a tight deadline and provide comprehensive details about their governance, security strategies, and risk management.

Given the unprecedented increase in cyberattacks in 2023 and the exorbitant rise in ransom prices, these new guidelines aim to establish a more systematic approach and improve how security incidents are reported. It is crucial to note that these rules are not exclusive to U.S. companies; any company listed on the U.S. exchanges must comply with the SEC reporting requirements and adhere to the disclosure regulations.

As we begin 2024, organizations must understand and comply with these new mandates.

What is the SEC?

In the aftermath of the 1929 Wall Street crash, the SEC was established as an autonomous U.S. federal government agency to ensure strict enforcement of security laws against market manipulation. The organization is committed to safeguarding investors’ interests, promoting capital formation, enforcing federal securities laws, regulating securities markets, and providing critical financial data.

From issuing timely alerts about emerging scams and compiling comprehensive resources for small businesses to aggregating and reporting APIs for financial data, the agency leaves no stone unturned in its efforts to protect American households from unethical market practices.

So, What Are These New Guidelines?

Cybersecurity threats such as cyberattacks, supply chain attacks, network intrusions, and ransomware have become an everyday occurrence, causing significant damage to the industrial, financial, and federal government sectors. The average cost of a data breach reached an all-time high last year – approximately $4.45 million.

To combat these threats, cybersecurity governing bodies are enforcing strict policies and regulations. The federal government introduced the Cyber Incident Reporting for Critical Infrastructure Act (CIRCIA) in March of 2022 to standardize the reporting of cyber incidents and ransomware to the Cybersecurity and Infrastructure Security Agency (CISA).

To ensure companies take cybersecurity seriously, the latest SEC disclosure rules that took effect at the end of last year require companies to disclose specific security incidents and overall cybersecurity strategies within four days of incident investigation.

These measures emphasize the vital role of security strategies, considerations, and accountability in corporate governance and reporting. These new regulations aim to prioritize the protection of company data and assets while fulfilling any obligations to clients and investors.

How Do I Comply?

To meet the revised requirements, it is mandatory for public and private companies to immediately inform their investors about any data loss issues or security breaches within four business days of the incident investigation. Moreover, these companies must provide yearly updates regarding their comprehensive security measures, risk management tactics, and broader cybersecurity strategy. To comply with structured data requirements, disclosures must be tagged in the Inline eXtensible Business Reporting Language within established timeframes.

It is worth noting that non-compliance can lead to severe legal consequences and hefty fines. Last year, the SEC filed 784 enforcement actions, ordered $5 billion in financial remedies, and distributed $1 billion to affected investors. While safeguarding whistleblowers and investors, the agency charged different violators, including public companies like Goldman Sachs and some social media influencers. The charges included a wide range of violations, from billion-dollar fraud to threats from crypto investors involving asset securities and cybersecurity.

What’s Next?

Looking ahead to 2024, companies must prioritize a culture of responsible and transparent cybersecurity practices in the rapidly evolving digital world. Timely disclosures that are detailed and candid in their severity can build trust between companies and their investors, customers, and community.

To revamp cybersecurity and risk management strategies, consider implementing the following:

  • Develop a robust system for identifying, reporting, and defending against cybersecurity threats and events.
  • Assess the risks involved in working with third-party applications or companies — particularly those with investor or client relationships.
  • Refresh employees on how to basic security measures and how to respond to security incidents of any kind appropriately.
  • If a security incident occurs, disclose sufficient insights about the incident to investors to avoid legal issues while ensuring that no further risks are posed to the company.

The new requirements should strengthen an investor’s position and increase their awareness of what they are financing. These new conditions for the incident and annual strategy disclosures will now provide them insights into breaches or risks that could affect their investment decisions.

It’s high time for organizations to take cybersecurity seriously. This year, all companies must prioritize finding cybersecurity solutions that consolidate and reinforce their defenses and increase cybersecurity posture to satisfy these new SEC regulations.

https://www.securitymagazine.com/articles/100575-adapting-to-the-latest-sec-disclosures


An ally for organizations navigating the complex cyber terrain

The evolution of the NIST Cybersecurity Framework in its 2.0 iteration underscores a significant paradigm shift towards a governance-focused approach. This update is not merely about identifying risks but about embedding cybersecurity into the very fabric of business operations. The ‘govern’ section crystallizes this by emphasizing the holistic impacts of cybersecurity. 

NIST CSF 2.0 has been commended for its operational effectiveness. It doesn’t just outline risks but offers detailed controls, enabling strategies for businesses, and provides a comprehensive view of the security lifecycle. This hands-on, detailed approach marks a shift from the abstract to the actionable, providing organizations with a blueprint for operational resilience. 

A standout feature of the framework is its comprehensive crosswalks, which bridge the gaps between various frameworks, streamlining compliance and operational efforts across industries. The ability to easily export controls is a testament to the framework’s commitment to improving operational efficiency. 

Effective communication about risk management is another cornerstone of the updated framework. It seeks to ensure that risk communication is effective at all organizational levels, from practitioners to executives, to facilitate comprehensive risk mitigation. This speaks to the necessity of a shared understanding of cybersecurity risks within an organization. 

The CSF 2.0 also introduces maturity levels, providing organizations with a means to gauge the implementation and adaptiveness of their cybersecurity practices. This feature helps organizations to not just implement but also to measure and improve their security postures. 

In an era where privacy concerns and new technologies like AI and LLMs are at the forefront, the framework integrates privacy considerations and addresses these emerging technologies, ensuring that the framework remains relevant and robust in a rapidly evolving tech landscape. 

Lastly, the framework places a renewed emphasis on supply chain risk management, a reflection of recent global cybersecurity incidents. It stresses the need for solid risk management strategies to safeguard against supply chain vulnerabilities, like those exposed by the Log4j incident, thus acknowledging the interconnectedness of modern digital ecosystems. 

However, there are challenges and roadblocks in getting organizations to adopt this framework, despite its voluntary nature becoming increasingly referenced in regulations and state legislature: 

Complexity and cost

For many organizations, especially small and medium-sized enterprises (SMEs), the complexity and cost of implementing the framework can be significant. Aligning with multiple standards requires a deep understanding of each and the resources to implement necessary controls and processes.

Resource constraints

Organizations, particularly in sectors where cybersecurity has not been a historical focus, may lack the skilled personnel needed to implement and manage the framework effectively. 

Regulatory overlap and confusion

While CSF 2.0’s closer mapping to other standards is designed to minimize confusion, organizations operating internationally might still face challenges in prioritizing which frameworks to align with primarily. International organizations may opt for ISO as their primary framework and NIST as secondary, whereas U.S.-based organizations might reverse this alignment. This duality can lead to confusion and inefficiencies in compliance efforts. 

Cultural and organizational resistance

Changing organizational culture to prioritize cybersecurity and risk management can be a slow and challenging process. Gaining buy-in from all levels of an organization is crucial but often difficult to achieve. 

While pointing out these challenges the following would be beneficial to see from the government and sought out by organizations:

Simplify implementation for SMEs

Develop simplified versions of the framework tailored to small and medium-sized enterprises (SMEs) with guidance that is straightforward and actionable. This could include checklists, templates, and case studies relevant to SMEs. 

Provide training and education

Invest in cybersecurity training and education to grow the talent pool and provide organizations with the skilled personnel they need to implement and manage the framework effectively. 

Leverage technology solutions

Utilize automated tools and services that can assist with compliance and implementation of the CSF. These tools can reduce complexity by automating the mapping of controls and management of documentation. 

Clarify regulatory expectations

Engage in a dialogue with regulators to develop clear guidance on how the CSF aligns with other regulatory requirements. This can help reduce overlap and confusion for organizations operating internationally. 

Foster a culture of cybersecurity

Build a cybersecurity culture within organizations by emphasizing the importance of security at all levels. Initiatives could include regular training, simulations, and executive briefings to ensure cybersecurity is a shared responsibility. 

Enhance governance support

Provide resources and guidance to help organizations integrate the ‘Govern’ function into their strategic management. This can involve developing governance frameworks that are compatible with CSF 2.0. 

Utilize maturity models

Encourage organizations to use the maturity level guidelines to incrementally adopt the framework. This allows them to scale their efforts and make continual improvements over time. 

Address privacy and emerging tech

Keep the framework dynamic by regularly updating it to address new technologies and privacy issues. Create specialized working groups or task forces to stay ahead of emerging threats. 

Strengthen supply chain collaboration

Promote collaboration among businesses in supply chains to collectively address cybersecurity risks. This can include shared tools, services, and best practices. 

Government incentives and support

Governments could offer incentives such as tax breaks, grants, or recognition programs for organizations that demonstrate robust cybersecurity practices aligned with the CSF. 

By taking these steps, organizations can not only overcome the barriers to adopting the NIST CSF 2.0 but can also integrate cybersecurity into their business strategy, ensuring a more resilient and secure operational landscape. 

In essence, NIST CSF 2.0 is a strategic ally for organizations navigating the complex cyber terrain, arming them with the governance, tools, and guidance needed to establish a resilient and responsive cybersecurity posture. 

https://www.securitymagazine.com/articles/100576-an-ally-for-organizations-navigating-the-complex-cyber-terrain


Protecting ships from cyber terrorism

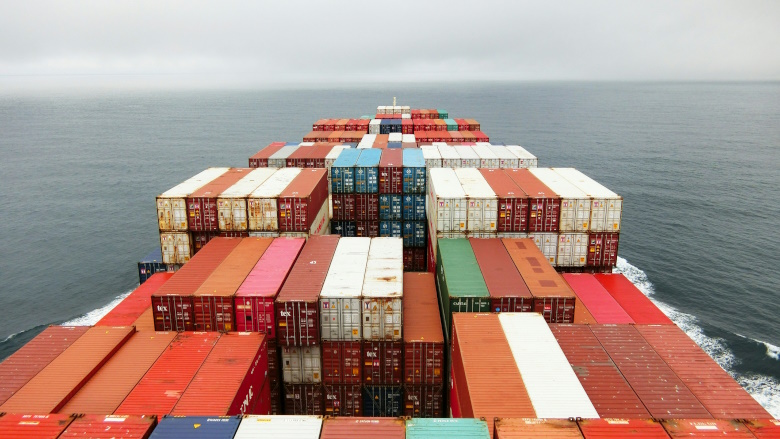
The investigation into Baltimore’s Francis Scott Key Bridge collapse has only just begun, but we’ve already seen news reports containing an unclassified memo from the Cybersecurity and Infrastructure Security Agency (CISA) and comments from the Department of Homeland Security concerning the cause. Maryland Governor, Wes Moore, said he could confirm that “The crew notified authorities of a power issue,” adding that the ship had lost power before smashing into one of the columns supporting the bridge. At this time, there is no evidence that the incident was anything more than a tragic accident, but the involvement of these U.S. government agencies indicates concerns of a cyberattack. 

Those concerns are highly warranted. For some time, maritime cybersecurity has been top of mind for regional, national and global policymakers. In February, the Biden administration issued an executive order to bolster and safeguard critical maritime infrastructure across the United States. Other countries and regions are on alert as well. NIS2, the updated Directive from the European Union slated to go into effect later this year, also addresses maritime cybersecurity. The International Maritime Organization’s (IMO) cybersecurity guidelines encourage shipping companies and vessel operators to address cybersecurity risks and implement measures to protect their assets, as do frameworks and guidelines from additional regulatory bodies.    

Vulnerable maritime systems

The numerous operational technologies (OT) on seafaring vessels have kept pace with digital transformations in other industries. Once powered solely by onboard fuel and propelled by engines, modern ships are hybrids, utilizing a combination of solar energy and fossil fuels in concert with a variety of smart engines. Modern propulsion systems now employ multiple connected technologies that reduce fluid friction and optimize performance. But these and other technologies can be cyber-compromised.

There are plenty of onboard systems to attack. Hackers are known to intercept satellite communications used extensively by ships at sea. They can also spoof or jam GPS systems, manipulate the automatic ID system (AIS), steal vital data, or inject malware or ransomware into any number of onboard systems via infected devices or files. Such attacks can throw a ship off course. When combined with a compromised propulsion system, the consequences can be horrific.  

Attacks on operating vessels aren’t the only vulnerabilities that shippers need to be concerned about. Risk starts early in the shipbuilding process. The long, complicated process of shipbuilding introduces a complex supply chain, where numerous parts and software products originating from multiple locations and a variety of international vendors become part of the ship’s essence. During manufacture, ship components may be compromised with latent malware, as threat actors patiently wait for the right future moment to interfere with communication or navigation systems, or to exploit a remote-access backdoor to take control of the ship. 

Ports and offshore facilities are also major elements of the maritime ecosystem, and they expose a collection of additional attack surfaces. Equipment and systems operating on loading docks and even oil rigs are inviting targets. These communicate with ships and can unknowingly share malware. Equipment and systems — from Chinese-made cranes to container-stacking machinery to drilling mechanisms — are in the hacker’s sights. 

Consequences of maritime cyberattacks

Regardless of whether this disruptive, deadly crash was an unfortunate accident or the result of a repugnant cyber attack, it highlights the potential consequences of cyber terrorism on the maritime industry. Contacting just one column of the 1.6-mile-long bridge, the ship was able to bring large portions crashing into the water and tragically end the lives of six construction workers. 

The economic damage is extensive. The Port of Baltimore — one of the busiest car import/export points in the US and home to some of the largest retailer distribution centers like FedEx, Amazon, and Home Depot — is shut down until further notice. Many of the 15,000 employees who work directly for the Port and 140,000 other employees supported by the Port’s ecosystem are out of work. 

Meanwhile, the Key Bridge, a vital road transportation route, is shut down indefinitely, forcing 30,000 daily commuters to find alternate routes. 

Shielding the maritime industry 

Safeguarding maritime vessels and infrastructure against cyberattacks is complicated, especially considering the deployment of Chinese-manufactured cranes throughout US seaports. Maritime cybersecurity demands a multifaceted approach rooted in robust cybersecurity measures and continuous vigilance. A comprehensive prevention program encompassing accurate risk management, stringent access controls, continuous threat detection, and incident response planning is called for immediately. 

By prioritizing cybersecurity measures in the face of evolving threats, maritime organizations can fortify their resilience against cyberattacks, ensuring the safety and integrity of their operations and to the public at large. 

While this particular incident may turn out to be a very unfortunate accident, the next one might come as a result of a cyber incident. Let’s not wait. 

https://www.securitymagazine.com/articles/100574-protecting-ships-from-cyber-terrorism


Ivanti risolve vulnerabilità che consentono attacchi DoS e RCE


Dopo aver risolto un bug critico a fine marzo, Ivanti ha reso nota l’esistenza di altre quattro vulnerabilità nei suoi prodotti. Una di queste, la CVE-2024-21894, consente a un attaccante non autenticato di attuare attacchi DoS ed eseguire codice da remoto (RCE).

Il bug colpisce il componente IPSec di Ivanti Connect Secure, la soluzione PVN SSL per le aziende, e di Ivanti Policy Secure, soluzione per il controllo degli accessi in rete. La vulnerabilità di heap overflow non richiede l’interazione utente per essere sfruttata.

Ivanti ha affermato che la vulnerabilità può essere sfruttata solo sotto certe condizioni, ma non ha specificato quali né quanto sono complesse da raggiungere.

Pixabay

Tra gli altri bug spicca la CVE-2024-22053, un’altra vulnerabilità di heap overflow che colpisce IPSec e, oltre a causare un DoS, può permettere la lettura di contenuti dalla memoria. Il componente IPSec soffre anche del bug CVE-2024-22052, una vulnerabilità di null pointer dereference che consente a un attaccante di inviare richieste costruite ad hoc per interrompere i servizi.

Infine, Ivanti ha informato i suoi clienti anche della vulnerabilità CVE-2024-22023, un bug di XML entity expansion che colpisce il componente SAML di Ivanti Connect Secure e Ivanti Policy Secure. Questa vulnerabilità consente a un attaccante non autenticato di inviare specifiche richieste XML per provocare un esaurimento di risorse e provocare un DoS a tempo limitato. 

Le patch sono disponibili per tutti i prodotti e Ivanti invita caldamente i suoi utenti ad aggiornare il prima possibile i software vulnerabili. Al momento non ci sono evidenze di attacchi che hanno sfruttato le vulnerabilità, ma è opportuno mantenere gli ambienti protetti.

Condividi l’articolo


Articoli correlati

Altro in questa categoria


https://www.securityinfo.it/2024/04/05/ivanti-risolve-vulnerabilita-che-consentono-attacchi-dos-e-rce/?utm_source=rss&utm_medium=rss&utm_campaign=ivanti-risolve-vulnerabilita-che-consentono-attacchi-dos-e-rce


Talent shortage is leading to automation and outsourcing

A report by Auvik surveyed 2,100 IT and MSP professionals to discover the trends and challenges among IT teams. The report found that the most notable challenge among IT teams was a lack of skilled workers. Due to this lack of talent, a trend toward automation and outsourcing emerged. IT teams are adopting new tools and resources to increase productivity while minimizing the burden on front-line IT team members. 

Compared to 2023, there was a 24% increase in plans for automation investments. Automation is prevalent among IT teams, as 96% utilize at least one AI or ML resource. At the same time, 29% of SaaS, network or other related tasks are done manually. 

IT teams are also outsourcing tasks or functions related to network duties. Nearly 75% of the respondents surveyed reported that some of these tasks are delegated to external workers. 

https://www.securitymagazine.com/articles/100572-talent-shortage-is-leading-to-automation-and-outsourcing


Nuovi attacchi sfruttano la condivisione dei documenti per rubare le credenziali utente


È emerso un nuovo attacco nel panorama delle minacce informatiche: Cisco Talos ha evidenziato che sempre più cybercriminali stanno usando i siti per la pubblicazione e condivisione dei documenti (DPP – Digital Document Publishing) per sottrarre credenziali e token di accesso.

L’attacco sfrutta tecniche di phishing per condividere con gli utenti aziendali un link che punta a un documento ospitato su un sito DPP. Una volta scaricato e aperto il file, la vittima clicca su uno dei link nel documento e naviga su un sito controllato dagli attaccanti che imita una pagina di autenticazione aziendale progettata per rubare le credenziali di accesso.

Pixabay

I siti per la condivisione dei documenti offrono un buon livello di personalizzazione che rende l’attacco ancora più credibile: non solo si può personalizzare il documento, ma anche la pagina che lo ospita, in modo da replicare il layout delle pagine aziendali.

Le pagine DPP, inoltre, sono temporanee e ciò complica il processo di rilevamento e risposta da parte dei team di cybersecurity: gli attaccanti sono in grado di impostare una scadenza per i contenuti pubblicati, in modo che dopo un certo lasso di tempo vengano cancellati automaticamente e non siano più rintracciabili.

Essendo ancora poco conosciuti dagli utenti, questi attacchi sono molto pericolosi ed efficaci; inoltre, i sistemi di sicurezza in uso non sempre sono in grado di rilevarli.

Il consiglio è di adottare strumenti di rilevamento e risposta degli endpoint (EDR) per bloccare l’uso dei siti DPP e dei domini dei siti contenuti nei messaggi di phishing.

Condividi l’articolo


Articoli correlati

Altro in questa categoria


https://www.securityinfo.it/2024/04/05/nuovi-attacchi-sfruttano-la-condivisione-dei-documenti-per-rubare-le-credenziali-utente/?utm_source=rss&utm_medium=rss&utm_campaign=nuovi-attacchi-sfruttano-la-condivisione-dei-documenti-per-rubare-le-credenziali-utente


DHS proposes reporting rules for critical infrastructure

The Department of Homeland Security (DHS) has announced a proposed set of rules for critical infrastructure reporting. In the event of a cyberattack or other cyber incident, these rules will outline how critical infrastructure organizations will be expected to report to the federal government. The process of reporting incidents will be overseen by the CISA, as is stipulated by the Cyber Incident Reporting for Critical Infrastructure Act (CIRCIA). 

Security leaders weigh in 

Jose Seara, CEO and Founder at DeNexus:

“The convergence and alignment of cybersecurity requirements by industry regulators and government agencies such as the SEC and CISA is much needed. It will allow corporations to simplify and therefore deploy more effective cybersecurity programs. We also recommend enterprises start with a cyber risk quantification exercise to bring clarity on where they’re most at risk and how to prioritize risk mitigation projects.”

John Gallagher, Vice President of Viakoo Labs at Viakoo:

“Kudos for the progress CISA has made with CIRCIA.  CIRCIA is a key milestone in moving critical infrastructure (and organizations in general) towards more awareness and coordinated response to cyber threats.  It’s not the destination (secure and resilient infrastructure), but an important waypoint towards it. 

“As the attack surface within critical industries has shifted towards IoT/OT/ICS vulnerabilities, CIRCIA has been forward-thinking in its focus on these types of vulnerabilities, and has acted as an accelerant to industry-level information and best practice sharing.   However, there needs to be a lot more effort in terms of benchmarking of preparedness and more structure around what ethical disclosure means for critical infrastructure/Cyber-Physical System (which is different than data theft).    

“The impact of critical infrastructure being breached is both enormous and highly time-sensitive, so by bringing the reporting timing down it significantly reduced the window of vulnerability from the breach.  For example, if the threat actor can rely on delayed reporting it opens up a much larger potential for organizational to be breached.  Shortening the reporting time directly shortens a cyber-criminal being able to act unnoticed.  

“It’s particularly notable that CISA has established different reporting timelines for cyber incident reporting (72 hours) versus ransomware payment (24 hours).  A longer timing for incident reporting helps to reduce false alarms and gives more time to assess the overall threat.  Ransomware payment is completely different, and if it isn’t outlawed at least there is a short reporting window.  

“Having clear definitions of what organizations are covered and details around there requirements also gives cyber insurance providers a way to work with critical infrastructure organizations and leverage these guidelines to base underwriting decisions.  

“Another aspect that stands out is the estimated costs.  Estimated costs of $2.6B over 11 years ($236M per year) is modest compared to the scale of cyber-crime or the impact of critical infrastructure incidents. Underfunding critical infrastructure or cyber-physical system security is a questionable decision.”

https://www.securitymagazine.com/articles/100568-dhs-proposes-reporting-rules-for-critical-infrastructure


Google blocca il furto dei cookie legando le sessioni al dispositivo


Google ha annunciato Device Bound Session Credentials (DBSC), una nuova funzionalità di sicurezza volta a contrastare il furto dei cookie delle sessioni di autenticazione.

Oggi una delle principali minacce alla sicurezza online sono i malware in grado di sottrarre i cookie di sessione che permettono agli attaccanti di accedere agli account utente compromessi. Il furto di cookie avviene dopo che l’utente ha effettuato il login, in modo da eludere l’autenticazione a due fattori e altri controlli. Mitigare questi attacchi con un antivirus non è semplice perché i cookie sono validi anche dopo che il malware è stato individuato e rimosso.

Per risolvere il problema, la funzionalità di Google lega la sessione di autenticazione al dispositivo dell’utente usando la crittografia; in questo modo, anche se un attaccante dovesse entrare in possesso dei cookie, non sarebbe in grado di usarli. L’unica via per sfruttarli sarebbe agire localmente sul dispositivo, e a quel punto la detection on-device sarebbe più efficace.

Pexels

Google contrasta il furto dei cookie sfruttando il dispositivo

Quando il browser inizializza una nuova sessione di autenticazione, DBSC crea una nuova coppia di chiavi pubblica/privata che viene salvata sul dispositivo. Nel dettaglio, Chrome utilizza il chip Trusted Platform Modules (TPM) per memorizzare e proteggere la chiave privata.

DBSC permette al server di associare una sessione al dispositivo usando la chiave pubblica come complemento o rimpiazzo dei cookie e verificare la presenza della chiave privata durante tutta la durata della sessione; ciò consente di verificare a intervalli regolari che la sessione avviene sempre sullo stesso dispositivo.

Ogni sessione è caratterizzata da una coppia di chiavi unica e DBSC non consente ai siti di correlare le chiavi delle diverse sessioni allo stesso dispositivo, in modo che non ci sia tracking dell’utente. L’utente può cancellare le chiavi sul dispositivo in qualsiasi momento semplicemente cancellando i dati di navigazione dal browser.

chrome navigazione

Pexels

La feature si allineerà con le direttive di Google per l’eliminazione dei cookie di terze parti, lasciando all’utente il controllo sulle preferenze. “Vogliamo evitare che il DBSC diventi un nuovo vettore di tracciamento una volta che i cookie di terze parti saranno gradualmente eliminati, garantendo al contempo che tali cookie possano essere completamente protetti” ha affermato Kristian Monsen, ingegnere del team Counter Abuse di Chrome.  “Se l’utente rinuncia completamente ai cookie, ai cookie di terze parti o ai cookie di un sito specifico, disabilita anche il DBSC”.

Diversi provider hanno già espresso il loro interesse verso la funzionalità per proteggere i propri utenti. “Stiamo collaborando con tutte le parti interessate per assicurarci di poter presentare uno standard che funzioni per diversi tipi di siti web in modo da preservare la privacy” ha spiegato Monsen.

Al momento la funzionalità è ancora in fase di completamento, ma è già disponibile da attivare nella versione 125 del browser. DBSC può essere abilitata navigando su chrome://flags/ e cercando “Device Bound Session Credentials” tra le feature attive. Essendo ancora in fase di sperimentazione, Google chiede di usarla con massima attenzione.

Condividi l’articolo


Articoli correlati

Altro in questa categoria


https://www.securityinfo.it/2024/04/04/google-blocca-il-furto-dei-cookie-legando-le-sessioni-al-dispositivo/?utm_source=rss&utm_medium=rss&utm_campaign=google-blocca-il-furto-dei-cookie-legando-le-sessioni-al-dispositivo


Cybercrime e best practices per la sicurezza informatica nelle aziende

Comprendere il cybercrime

Il cybercrime, noto anche come crimine informatico o crimine digitale, si riferisce a qualsiasi attività criminale che coinvolge l’utilizzo di computer, reti informatiche o dispositivi digitali.

Le principali attività illegali riscontrate fino ad oggi sono l’accesso non autorizzato a sistemi informatici, il furto di dati, la diffusione di virus informatici con conseguente danneggiamento o richiesta estorsiva per la riduzione in pristino, l’intercettazione illegale di comunicazioni, la frode informatica e varie altre forme di violazione della sicurezza informatica.

Quello che si nota nella comune esperienza è che il cyberattack proviene, molto spesso, dall’interno della realtà aziendale.

Questa c.d. insider threat e, cioè, la minaccia proveniente da persone interne all’organizzazione (dipendenti, fornitori, partner economici, soci etc.) si alterna a sistemi di attacco esterno che riescono a prendere il controllo del sistema informatico anche a migliaia di chilometri tramite, ad esempio, il RAT (Remote Administration Tool).

Ad oggi, le società sono chiamate ad affrontare una sfida in termini di prevenzione e persuasione, oltre che di contenimento del danno economico – e non – provocato dal crimine informatico e cibernetico, con un approccio su larga scala che consenta di fronteggiare la criminalità in rete in ogni sua declinazione.

Impatto del cybercrime sulle aziende

Gli effetti del cybercrime sono spesso immediati e devastanti per un’azienda.

Questa può subire perdite finanziarie, sia dirette che indirette, a causa del furto di fondi o di dati finanziari, dovendo mettere in contro anche successivi costi per l’individuazione e la risoluzione della violazione, la riparazione dei sistemi di sicurezza e l’eventuale risarcimento di clienti per le perdite subite.

Il danno economico molto spesso si affianca a quello reputazionale, che si può manifestare in modo incalcolabile: quando la reputazione di un’azienda viene danneggiata da un attacco informatico, si può verificare una perdita di fiducia dei clienti e dei partner commerciali, il che può avere un impatto a lungo termine sulle vendite e sui profitti aziendali.

Di seguito, si ricordano alcuni recenti attacchi informatici che hanno causato un impatto significativo sulle aziende.

L’attacco di ransomware WannaCry del 2017 che ha colpito numerose aziende, inclusi ospedali e istituzioni governative, bloccando l’accesso ai dati e richiedendo un riscatto per sbloccarli.

Il caso Equifax, una delle più grandi agenzie di reporting del credito negli USA. Nel 2017, Equifax ha rivelato che i dati personali di 143 milioni di americani erano stati esposti a causa di una violazione della sicurezza. Questo incidente è costato ad Equifax oltre 1,4 miliardi di dollari in spese legate alla violazione e la reputazione dell’azienda ne è stata gravemente danneggiata.

Recentissimo è il caso truffa finanziaria a danno della multinazionale britannica con sede a Hong Kong che ha spostato “per errore” 200 milioni di dollari da Hong Kong su cinque conti sconosciuti, operazione effettuata da un dipendente truffato tramite una video call dove ha pensato di parlare e prendere ordini dai suoi referenti – che, in realtà, erano un prodotto del deep fake -, disponendo lo spostamento di denaro ancora non ritrovato.

E come non citare il cyberattak subito da Leonardo S.p.A. nel 2017, commesso da un insider, il quale ha causato la fuoriuscita di “oltre 100mila file, riguardano, oltre i dati personali dei dipendenti, la progettazione di componenti di aeromobili civili e di velivoli militari destinati al mercato interno e internazionale”.

Durante le indagini effettuate dalla Polizia di Stato di Napoli e dal C.N.A.I.P.I.C. (Centro Nazionale Anticrimine Informatico per la Protezione delle Infrastrutture Critiche), emerse che “per quasi due anni, tra maggio 2015 e gennaio 2017, le strutture informatiche di Leonardo Spa erano state colpite da un attacco informatico mirato e persistente (noto come Advanced Persistent Threat o APT), realizzato con installazione nei sistemi, nelle reti e nelle macchine bersaglio, di un codice malevolo finalizzato alla creazione ed al mantenimento di attivi canali di comunicazione idonei a consentire una perdita di dati lenta e continua di elevati quantitativi di dati e informazioni di importante valore aziendale” [1].

È quindi evidente che per prevenire e mitigare il serio rischio di cybercrime, le aziende devono prendere coscienza del problema ed adottare misure di sicurezza informatica efficienti.

Legislazione e normative sulla cybersecurity

Nel campo penale, il nostro codice prevede numerose – ma non ancora sufficienti – fattispecie criminose che puniscono, tra le altre, l’accesso abusivo a sistemi informatici o telematici (art. 615 ter c.p.), la detenzione di apparecchiatura atta a intercettare, impedire o interrompere comunicazioni o conversazioni telegrafiche o telefoniche (art. 617 bis c.p.), il danneggiamento di informazioni, dati e programmi informatici (art. 635 bis c.p.) o di sistemi informatici o telematici (art. 635 quater c.p.).

Tali reati sono, inoltre, richiamati quali reati presupposto dagli artt. 24 e 24 bis D.Lgs. 231/2001, che puniscono le società (tramite severe sanzioni interdittive e pecuniarie) a vantaggio delle quali è stata commessa una frode informatica o delitto informatico o un trattamento illecito dei dati, di cui agli articoli sopra richiamati del codice penale.

Questo significa che, se un soggetto che ricopre funzioni di rappresentanza, amministrazione o direzione della società o di una sua unità organizzativa dotata di autonomia funzionale e finanziaria, oppure che gestisce o controlla la società, o un suo sottoposto, commette un reato tipico del cybercrime nell’interesse o a vantaggio della società, questa sarà chiamata a rispondere nel procedimento 231 instauratosi a suo carico.

Certo, vi è sempre la possibilità di difendersi nel procedimento 231, anche al fine di dimostrare l’estraneità dell’ente e/o del legale rappresentante dello stesso.

Ma ciò al pesante costo di essere comunque sottoposti al procedimento davanti alle autorità competenti, con anche la possibilità di vedersi applicare eventuali misure cautelari quali sequestri o commissariamenti giudiziari e, dunque, ad una generale perdita economica e reputazionale.

Ecco, quindi, l’importanza della compliance aziendale in materia 231 che non significa solo adottare un modello di organizzazione, gestione e controllo e un codice etico, ma soprattutto renderli concreti e manifesti, anche tramite un efficace processo di adozione di protocolli di gestione della sicurezza informatica, nei quali vi sia una specifica disciplina aziendale in materia di prevenzione, contenimento e risposta al cybercrime.

In merito, si evidenziano quelle che secondo la prassi più diffusa rappresentano le best practices aziendali da seguire per adeguare la società all’attuale normativa:

  • Individuazione del bene aziendale da tutelare e dei rischi ai quali è potenzialmente esposto;
  • formazione e sensibilizzazione del personale su minacce e misure di sicurezza, anche addestrando a riconoscere messaggi appositamente creati per essere ingannevoli (c.d. phishing);
  • adozione di software di sicurezza per proteggere i sistemi aziendali, filesystem di nuova generazione, sistemi criptati di accesso a determinate informazioni sensibili;
  • implementazione di politiche di accesso (c.d. least privilege) e controllo ai sistemi aziendali. In particolare, limitazioni dell’accesso al solo personale autorizzato e previsione di una rigorosa separazione dei ruoli nel sistema di logging;
  • costante backup e ripristino dei dati;
  • monitoraggio dell’ambiente informatico per rilevare potenziali minacce, anche tramite un sistema di segnalazione interna (c.d. whistleblowing);
  • implementazione del sistema di prevenzione (sandbox, NIDS, blocco automatico di codici javascript, antivirus e antimalware, etc.);
  • predisposizione, implementazione e costante aggiornamento di un documento di security policy.

Conclusioni

Pur se coperti da norme penali, al giorno d’oggi resta ancora molto difficile perseguire i colpevoli di reati informatici e, ancor di più, strutturare un sistema di prevenzione degli stessi.

Questo vulnus, reso ancor più grave dalla scarsità di risorse tecniche disponibili, di forze di polizia e di difficoltà nel coordinamento sul territorio internazionale, si riversa in primis quale rischio reputazionale ed economico per le società e, post factum, rappresenta una distorsione nel sistema processuale penalistico che lo rende sempre meno al passo con i tempi.

La difesa nel processo dell’ente è materia tecnico giuridica da affidare agli esperti del settore, ma la predisposizione di modelli di organizzazione, gestione e controllo che tutelino l’ente dal rischio di commissione di reati anche informatici è di competenza di ciascuna realtà societaria, unitamente alla necessità che suddetto modello venga adottato e aggiornato in concerto con il codice etico e la security policy aziendale.

La società dovrà prendere coscienza dei rischi tecnologici sempre più concreti e della necessità di operare con strutture organizzate ed idonee per prevenirli o, quanto meno, per contenerne i danni.

Note

[1] D. Fioroni, Attacco Hacker a Leonardo Spa, 2 arresti, in www.poliziadistato.it, 5 dicembre 2020

Articolo a cura di Lorenzo Nicolò Meazza e Olivia de Paris

Profilo Autore

Avvocato penalista, titolare dell’omonimo Studio legale sito in Milano e Vicepresidente della Camera Penale di Milano, ove ha costituito la Commissione sull’intelligenza artificiale.
Si occupa prevalentemente di diritto penale d’impresa, con un focus particolare su criminalità informatica, compliance, diritto penale delle nuove tecnologie e digital forensics. Membro e presidente di numerosi Organismi di Vigilanza, il suo studio ha acquisito particolare esperienza nella redazione di Modelli Organizzativi e Regolamenti informatici aziendali.
È stato selezionato dall’Ordine forense di Milano e dal Pool Reati Informatici della Procura milanese tra gli avvocati esperti in diritto dell’informatica, con particolare competenza nella trattazione dei reati informatici.

Profilo Autore

Avvocato penalista dello Studio Legale Meazza, laureata presso l’Università Bocconi, con esperienza consolidata nel diritto penale dell’economia e del diritto penale tributario. Componente di Organismi di Vigilanza, autore di pubblicazioni in materia, focalizzata su delitti informatici e best practice per la sicurezza informatica aziendale, con particolare attenzione ai recenti progressi dei nuovi sistemi di Intelligenza Artificiale.

Condividi sui Social Network:

https://www.ictsecuritymagazine.com/articoli/cybercrime-e-best-practices-per-la-sicurezza-informatica-nelle-aziende/


Gli utenti sono preoccupati per la propria sicurezza online, ma hanno molti punti deboli


I consumatori sono preoccupati dalle nuove minacce informatiche, soprattutto ora che i cybercriminali hanno cominciato ad adottare l’intelligenza artificiale per sferrare i loro attacchi.

Secondo il Report Consumer Cybersecurity Assessment 2024 di Bitdefender, sondaggio condotto su più di 7.000 consumatori in Australia, Francia, Germania, Italia, Spagna, Regno Unito e Stati Uniti, la maggior parte degli utenti (67%) è preoccupata per la sicurezza e la privacy dell’intelligenza artificiale. In Italia questa percentuale scende al 49%. I consumatori temono che le tradizionali normative sulla protezione dei dati non siano in grado di risolvere le preoccupazioni in merito all’archiviazione, all’uso e all’accesso ai dati.

Il 48% degli intervistati si è detto preoccupato della possibilità che i criminali informatici possano accedere alle loro finanze tramite i dispositivi personali, e il 17% teme per il furto di identità. Il 78% degli utenti, anche in Italia, ha dichiarato di usare un dispositivo mobile per effettuare transazioni sensibili, ma il 45% di essi non usa alcun tipo di sicurezza mobile. Il 38% degli intervistati si fida della sicurezza iOS e Android, mentre un 23% ha dichiarato di non sapere che esistono soluzioni di sicurezza per dispositivi mobile.

Quasi un quarto degli intervistati (24%) ha dichiarato di aver subito uno o più incidenti di sicurezza nell’ultimo anno. Tra i Paesi coinvolti nel sondaggio, l’Italia ha registrato la percentuale più bassa, il 16,14%. Il 37,5% degli intervistati di età compresa tra i 16 e i 24 anni ha dichiarato di aver subito un incidente di sicurezza, rispetto ad appena l’11,9% degli intervistati di età superiore ai 55 anni.

Pexels

A minacciare maggiormente i consumatori sono le truffe via SMS, sperimentate dal 45,4% degli intervistati, seguito dai tentativi di frode (44%), dalle email di phishing (42%), dall’esposizione dei dati (27,5%), dalle infezioni malware (18,3%) e dal doxing (9,7%). L’Italia è uno dei Paesi che ha registrato il maggior numero di tentativi di phishing. Le infezioni malware sono state segnalate soprattutto tra i 35 e i 44 anni, il che suggerisce che i Millennials sono più inclini a scaricare software non ufficiali.

Il sondaggio riporta inoltre che il 35,7% degli intervistati gestisce da 6 a 10 account online, tra siti di e-commerce, servizi bancari, social media o piattaforme di intrattenimento. Quasi la metà degli intervistati (48,3%) utilizza una VPN, mentre in Italia il 51,5% ha affermato di non utilizzarne affatto una. Tra chi usa la VPN, il 27% ha affermato che è per  trovare offerte basate sulla posizione o per lo streaming di contenuti non disponibili nella propria regione. In Italia solo il 13% dei consumatori ha dichiarato di utilizzare una VPN per crittografare i dati e rendere più sicure le comunicazioni.

I punti deboli nella sicurezza degli utenti

Nonostante gli utenti siano abbastanza consapevoli dei rischi di sicurezza, hanno ancora molti punti deboli. Il problema principale è la gestione delle password: più di un terzo (37%) annota le proprie password, sia su carta che su appunti digitali, e l’Italia si posiziona al primo posto con il 50,4%.

Il 34% usa la stessa password per due o più account, mentre il 17,3% utilizza la funzione di compilazione automatica del browser web e il 14,4% la funzione di compilazione automatica della password efficace di Apple. Solo il 23% degli intervistati (il 19% in Italia) usa un gestore di password.

La maggior parte degli utenti non ritiene di essere un potenziale bersaglio dei cybercriminali o di non essere sicuro. L’Italia ha registrato la percentuale più alta (43,4%) di intervistati che ritengono di non essere un obiettivo per i criminali informatici. Dietro questa affermazione c’è l’idea sbagliata comune che gli hacker prendano di mira un singolo individuo, quando in realtà cercano sistemi vulnerabili e sfruttano a loro vantaggio comportamenti di scarsa sicurezza per eseguire attacchi su scala.

La maggior parte degli intervistati è consapevole dei rischi di esposizione dei bambini alle minacce on line: circa il 70% ha dichiarato di essere preoccupato per la privacy e la sicurezza dei più piccoli. L’Italia registra la percentuale più bassa dove il 48,9% degli intervistati si è detto preoccupato e solo il 13,9% molto preoccupato.

Infine, per quanto riguarda il pericolo di doxing, il 54,2% degli intervistati si è detto preoccupato. In Italia, ha espresso preoccupazione il 42% degli intervistati, la percentuale più bassa tra tutti gli altri Paesi.

Pixabay

“I risultati di questo sondaggio dimostrano, più che mai, l’importanza della sensibilizzazione alla sicurezza informatica, dato il costante incremento della frequenza e della sofisticatezza degli attacchi lanciati dai criminali informatici” ha dichiarato Ciprian Istrate, senior vice president of operations, Bitdefender Consumer Solutions Group. 

“Il repentino aumento dell’adozione dell’intelligenza artificiale da parte dei criminali informatici ha cambiato le carte in tavola e rappresenta una minaccia senza precedenti per la sicurezza digitale dei consumatori. Con l’aumento delle truffe via SMS supportate dall’intelligenza artificiale, dei tentativi di frode e di email di phishing realizzate a regola d’arte, è indispensabile che i consumatori rimangano vigili per comprendere le migliori pratiche di sicurezza informatica e applicarle costantemente” ha concluso Istrate.

Condividi l’articolo


Articoli correlati

Altro in questa categoria


https://www.securityinfo.it/2024/04/04/gli-utenti-sono-preoccupati-per-la-propria-sicurezza-online-ma-hanno-molti-punti-deboli/?utm_source=rss&utm_medium=rss&utm_campaign=gli-utenti-sono-preoccupati-per-la-propria-sicurezza-online-ma-hanno-molti-punti-deboli