How to hack the Jacksonville Jaguars’ jumbotron (and end up in jail for 220 years)

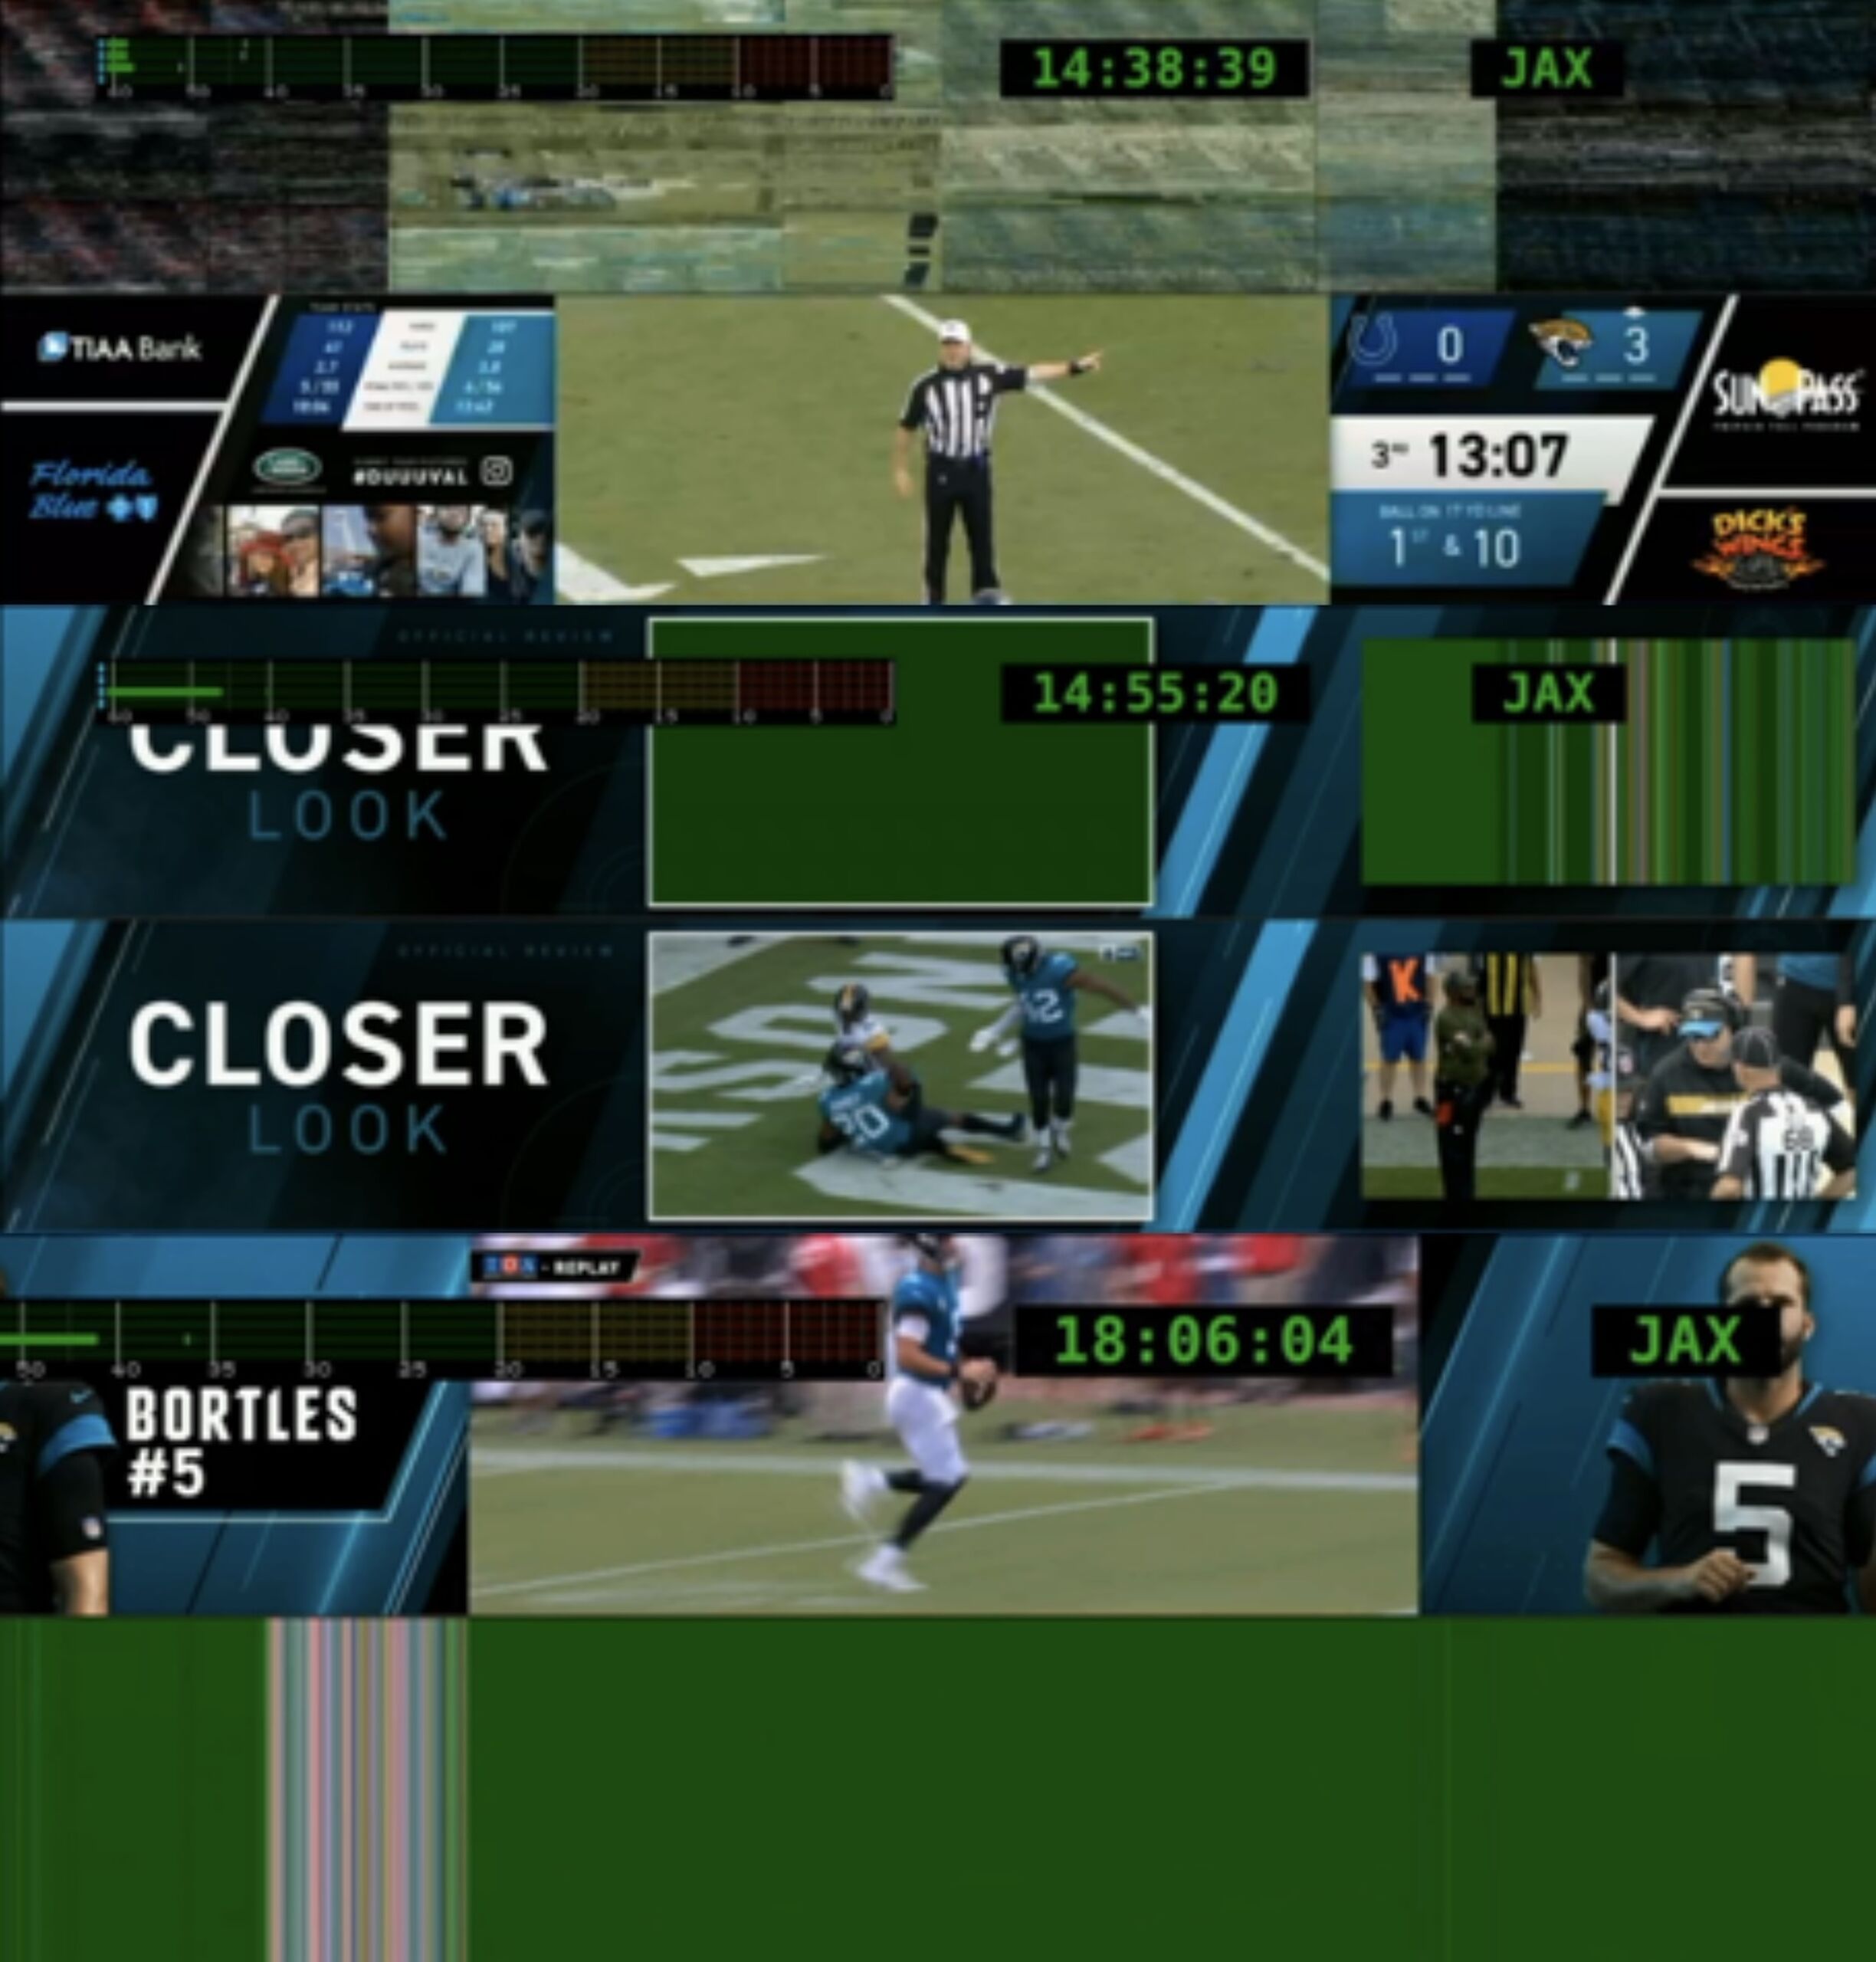
Three examples of the video screen tampering.
Enlarge / Three examples of the video screen tampering.

Was someone messing with the Jacksonville Jaguars’ giant jumbotron?

On September 16, 2018, the Jaguars were playing the New England Patriots when the in-stadium screen experienced, in the US government’s words, “a loss in reference sync which manifested as a large horizontal green lines [sic] appearing across one whole video board.”

On November 18, during a game against the Pittsburgh Steelers, it happened again—but this time, entire video sub-boards filled with green.

Then, on December 2, 2018, the Indianapolis Colts came to town and the jumbotron glitched a third time as “a single video board experienced a change of what seemed to be the zoom of one of the base graphics displayed.”

The Jaguars’ IT staff could not at the time replicate any of these video errors, and they began to suspect that what they were seeing was not a technical problem but some sort of attack. Digging into log files, they quickly found that the source of the December 2 problem was “a command to change a specific parameter” of the video control software.

Where had the command come from? An Abekas Mira video control server known as MIRA9120. The Abekas Mira was meant to help in the production and display of instant replay video to be shown in-stadium on the massive jumbotron, but this particular server had been either decommissioned or kept on hand as a spare. In any event, the team thought the server was in storage. But when they went looking, MIRA9120 turned out to be sitting in the main server room, installed on a rack just beside the active Abekas Mira servers.

IT staffers started poking around in MIRA9120 and found the remote-access software TeamViewer, suggesting that someone had been controlling MIRA9120 from somewhere else. But only limited data about the culprit could be gleaned, because the TeamViewer instance had connection logging disabled.

On December 3, the Jaguars’ IT staff disconnected MIRA9120 from the other video control servers—but they left it powered on and in place. Then they turned TeamViewer’s connection logging back on. The idea was to set up a honeypot in case the attacker returned.

During the December 16 game against Washington, TeamViewer recorded another connection into MIRA9120. The TeamViewer account number that accessed the machine was logged, and the information was passed to the FBI, which was now actively investigating the situation. Agents sent a subpoena to TeamViewer, which in February 2019 provided the IP address of the machine that had used the account in question on that day.

This IP address was controlled by Comcast, so a subpoena to Comcast finally turned up the information the Jaguars wanted: MIRA9120 was accessed on December 16 from a home in St. Augustine, Florida—a home where Samuel Arthur Thompson was living.

The secret

The Jags knew Thompson. He had spent nearly five years as a contractor for the football team, helping Jacksonville design and install their stadium screen technology. After installation, Thompson helped to run the system during football games.

Thompson also had a secret: He had been convicted of sexually abusing a 14-year-old boy in Alabama in 1988. Thompson had not reported this to the Jaguars, either, though his contract required such a disclosure.

Someone had found out about the conviction and sent an anonymous letter about it to the Jaguars’ management. Once the letter arrived, the Jaguars terminated Thompson’s contract. His last day with the team had been February 23, 2018. The relationship was thought to be over—but maybe it wasn’t.

A closer search of network traffic and log files from that February day revealed that Thompson himself had installed TeamViewer onto MIRA9120 at 9:09 am. So the pieces all fit: disgruntled employee on final day of work, the TeamViewer install, the IP address in St. Augustine.

But the FBI didn’t secure a warrant until the summer of 2019. Only in July did the FBI raid Thompson’s home in rather polite style, simply knocking on the door. (Thompson would later complain in a court filing that agents should have yelled out who they were and why they were there. He was strongly displeased about being surprised.) Thompson’s child opened the door. When Thompson himself came over, he still had his unlocked iPhone in hand—and an agent immediately grabbed it.

Then the case became something else entirely—because the phone had child sex abuse material (CSAM) on it.

https://arstechnica.com/?p=2014671


How do security leaders protect PII and other important data?

h3 { font-weight: bold; font-size: 18px; color: #C72026; } .pod { width: 100%; border: solid 3px #C72026; padding: 7px; margin: 20px 0; justify-content: center; }

With rapidly changing restrictions and guidelines, security leaders have to be careful when protecting personally identifiable information (PII). From company-wide information to a single employee’s password, data is everywhere in modern-day life.

Shiva Nathan, Founder and CEO of Onymos, provides insight to recent government requirements for PII protection and how security leaders can implement them.

Or check it out on our Apple Podcasts or Spotify channels. Don’t forget to like, follow, and rate and review our podcasts!

https://www.securitymagazine.com/articles/100567-how-do-security-leaders-protect-pii-and-other-important-data


Hacktivisti rubano un database di detenuti in Russia per far luce sulla morte di Naval’nyj


Un gruppo di hacktivisti oppositori del Cremlino ha vendicato la morte di Alexey Naval’nyj attaccando i server di una prigione russa e sottraendo i dati relativi a centinaia di migliaia di detenuti in Russia, compresi i prigionieri della prigione dove è morto l’oppositore del governo di Putin.

La CNN riporta che gli hacker appartengono a diverse nazionalità e comprendono anche persone ucraine ed espatriati russi. L’obiettivo del gruppo è condividere le informazioni sui prigionieri, comprensive di numeri di telefono e indirizzi email, “nella speranza che qualcuno riesca a contattarli e riuscire a capire ciò che è accaduto a Naval’nyj” ha affermato uno degli hacker coinvolti.

Naval’nyjè morto in circostanze ancora completamente da verificare lo scorso 16 febbraio mentre si trovava in un carcere del circondario autonomo Jamalo-Nenec, situato nella regione artica. Tra i più noti oppositori di Putin, è morto per “sindrome da morte improvvisa” come riportato dai media russi, ma diversi leader internazionali, tra i quali Biden, hanno accusato il Cremlino della scomparsa dell’uomo. 

hacktivisti russia

Pexels

Gli hacker hanno pubblicato diversi messaggi sulle pagine web del sito della prigione e inserito foto che ritraevano Naval’nyj durante diverse manifestazioni politiche. Stando alle informazioni che ha condiviso con la CNN, il gruppo sarebbe entrato in possesso di più di 800.000 prigionieri e dei loro parenti. Oltre ai messaggi lasciati sul sito, il gruppo ha anche modificato i prezzi di molti articoli dello spaccio del carcere abbassandoli a poco più di 1 centesimo di dollaro.

Sono passate diverse ore prima che gli amministratori del sito si accorgessero dell’attacco e ci sono voluti tre giorni prima che il team IT della prigione riuscisse a ripristinare il sito e i prezzi corretti dei prodotti. Sembra che il gruppo abbia inviato un messaggio agli amministratori dello shop avvertendoli di non togliere i messaggi pro-Naval’nyj e, dopo il rifiuto dell’IT, gli hacker avrebbero messo offline uno dei server del sito.

“Noi, specialisti IT, abbiamo lasciato la Russia di oggi” si leggeva in un messaggio sul sito web dello spaccio della prigione, condiviso in seguito dalla CNN in uno screenshot. “Amiamo il nostro Paese e torneremo quando sarà libero dal regime di Putin. E andremo fino in fondo”.

Condividi l’articolo


Articoli correlati

Altro in questa categoria


https://www.securityinfo.it/2024/04/03/hacktivisti-rubano-un-database-di-detenuti-in-russia-per-far-luce-sulla-morte-di-navalnyj/?utm_source=rss&utm_medium=rss&utm_campaign=hacktivisti-rubano-un-database-di-detenuti-in-russia-per-far-luce-sulla-morte-di-navalnyj


Research reveals a resurfaced botnet targeting end-of-life devices

Research from the Black Lotus Labs team at Lumen Technologies has identified multi-year efforts to target end-of-life (EoL) and IoT devices. Small home and small office routers are a particular target of this campaign, which is associated with an updated version of malware known as TheMoon.

“As we’ve expanded the types of devices that have operating systems in them, we haven’t kept up with the lessons learned from desktop and server computing, namely that automatic updates are the norm. This problem is exacerbated by consumers using devices for much longer periods of time than manufacturers want,” says John Bambenek, President at Bambenek Consulting. “By using security updates as leverage for buying new products, the net result is infected devices that are used in cybercrime. Criminals have all the time in the world to be patient, they are already netting a strong cash flow and there are more infectable devices than they have time to exploit.”

TheMoon emerged in 2014 and has been operating quietly ever since. Between January and February of 2024, it has grown to more than 40,000 bots across 88 countries. Many of these bots are deployed as the foundation of a cybercriminal-focused proxy service called Faceless. 

Faceless is a malicious service, offering anonymity services to cybercriminals for a negligible price. Malicious actors utilizing Faceless services can divert their traffic to hide their origins. 

Jason Soroko, the Senior Vice President of Product at Sectigo, says, “Routers and other networking equipment that use passwords have been easy victims to pray and spray attacks for years. It is unfortunate that stronger forms of authentication are not common. What’s new here is the usage of proxy networks for C2 traffic obfuscation.  It shows that de-anonymizing Tor and VPN traffic is not only happening, but has been successfully used against attackers.”

https://www.securitymagazine.com/articles/100564-research-reveals-a-resurfaced-botnet-targeting-end-of-life-devices


PROXYLIB trasforma gli smartphone in nodi proxy residenziali


Il team di threat intelligence di HUMAN ha identificato numerose applicazioni VPN disponibili sul Play Store che trasformavano i dispositivi utente in un nodo proxy senza che ne fossero a conoscenza. La campagna, identificata come PROXYLIB, ha permesso agli attaccanti di creare una rete di proxy residenziali ed eseguire altri attacchi, come il web scraping, l’esecuzione di transazioni o il furto di identità.

I ricercatori hanno individuato una prima applicazione malevola, Oko VPN, sul Play Store a maggio 2023, e un’analisi approfondita ha fatto emergere altre 28 applicazioni legate all’operazione PROXYLIB; in seguito, il team ha individuato anche LumiApps, una versione più avanzata dell’SDK precedente.

Le applicazioni che contenevano l’SDK di PROXYLIB includevano una libreria malevola in grado di stabilire una connessione bidirezionale a una rete di proxy, trasformando il dispositivo dell’utente in un nodo proxy residenziale senza interazione umana. La maggior parte delle applicazioni individuate dal team erano pubblicate sul Play Store come app gratuite per la VPN.

Pixabay

Poco tempo dopo il team ha scoperto un nuovo SDK, lumiapps.io, che possedeva le stesse funzionalità e usava la stessa infrastruttura server della prima versione di PROXYLIB. Nel caso di LumiApps, oltre a poter integrare un SDK malevolo nelle loro applicazioni, gli attaccanti potevano usare una piattaforma che, caricato un APK, integrava automaticamente l’SDK per la creazione dei nodi proxy.

Il servizio consentiva a chiunque di caricare un APK senza possedere il codice sorgente e modificarlo inserendovi le funzionalità LumiApps, per poi caricarlo sul Play Store.

La monetizzazione tramite Asocks

Secondo l’analisi di HUMAN, l’operazione PROXYLIB sarebbe legata ad Asocks, un rivenditore di proxy residenziali: il gruppo utilizzerebbe la piattaforma per vendere l’accesso alla rete di proxy creata tramite le proprie applicazioni. I ricercatori hanno individuato numerose richieste del malware PROXYLIB dirette verso asocks.com provenienti dai dispositivi infetti.

Per incentivare gli sviluppatori a utilizzare l’SDK malevolo nelle proprie applicazioni e monetizzare le connessioni, gli attaccanti hanno cominciato a promuovere LumiApps e gli SDK collegati come un metodo alternativo di guadagno: stando alle FAQ presenti sul sito, la piattaforma ricompensa gli sviluppatori con pagamenti in denaro in base alla quantità di traffico instradato tramite i nodi proxy creati con le applicazioni.

Pixabay

PROXYLIB continuerà a evolvere

Al momento Google ha eliminato le 28 applicazioni dal Play Store che contenevano l’SDK PROXYLIB, ma è probabile che ne nascano altre. “Gli attaccanti continuano a usare la piattaforma LumiApps e rilasciare nuove versioni dell’SDK che può essere usato in altre applicazioni” spiegano i ricercatori.

Google Play Protect avvisa gli utenti Android di potenziali applicazioni malevole, in alcuni casi bloccandole direttamente, anche quando non sono state scaricate dallo store ufficiale. Sebbene sia un’importante strumento di protezione da tenere sempre attivo, alcune applicazioni potrebbero sfuggire ai controlli di sicurezza.

HUMAN ricorda agli utenti di scaricare applicazioni solo da marketplace ufficiali ed evitare cloni di app popolari che potrebbero contenere malware o funzionalità indesiderate come quella del proxy.

Condividi l’articolo


Articoli correlati

Altro in questa categoria


https://www.securityinfo.it/2024/04/03/proxylib-trasforma-gli-smartphone-in-nodi-proxy-residenziali/?utm_source=rss&utm_medium=rss&utm_campaign=proxylib-trasforma-gli-smartphone-in-nodi-proxy-residenziali


Missouri county declares state of emergency amid suspected ransomware attack

Downtown Kansas City, Missouri, which is part of Jackson County.
Enlarge / Downtown Kansas City, Missouri, which is part of Jackson County.

Jackson County, Missouri, has declared a state of emergency and closed key offices indefinitely as it responds to what officials believe is a ransomware attack that has made some of its IT systems inoperable.

“Jackson County has identified significant disruptions within its IT systems, potentially attributable to a ransomware attack,” officials wrote Tuesday. “Early indications suggest operational inconsistencies across its digital infrastructure and certain systems have been rendered inoperative while others continue to function as normal.”

The systems confirmed inoperable include tax and online property payments, issuance of marriage licenses, and inmate searches. In response, the Assessment, Collection and Recorder of Deeds offices at all county locations are closed until further notice.

The closure occurred the same day that the county was holding a special election to vote on a proposed sales tax to fund a stadium for MLB’s Kansas City Royals and the NFL’s Kansas City Chiefs. Neither the Jackson County Board of Elections nor the Kansas City Board of Elections have been affected by the attack; both remain open.

To date, ransomware attacks have hit 28 county, municipal, or tribal governments this year, according to Brett Callow, a threat analyst with security firm Emsisoft. Last year, there were 95; 106 occurred in 2022.

The Jackson County website says there are 654,000 residents in the 607-square-mile county, which includes most of Kansas City, the biggest city in Missouri.

The response to the attack and the investigation into it have just begun, but so far, officials said they had no evidence that data had been compromised.

“We are currently in the early stages of our diagnostic procedures, working closely with our cybersecurity partners to thoroughly explore all possibilities and identify the root cause of the situation,” officials wrote. “While the investigation considers ransomware as a potential cause, comprehensive analyses are underway to confirm the exact nature of the disruption.”

Jackson County Executive Frank White Jr. has issued an executive order declaring a state of emergency.

“The potential significant budgetary impact of this incident may require appropriations from the County’s emergency fund and, if these funds are found to be insufficient, the enactment of additional budgetary adjustments or cuts,” White wrote. “It is directed that all county staff are to take whatever steps are necessary to protect resident data, county assets, and continue essential services, thereby mitigating the impact of this potential ransomware attack.”

The attack first came to attention Tuesday morning, county officials said on Facebook.

The county has notified law enforcement and retained IT security contractors to help investigate and remediate the attack.

“The County recognizes the impact these closures have on its residents,” officials wrote. “We appreciate the community’s patience and understanding during this time and will provide more information as it becomes available.”

https://arstechnica.com/?p=2014470


FTC denies new COPPA application

The Federal Trade Commission (FTC) has denied an application “without prejudice” by the Entertainment Software Rating Board, Yoti and SuperAwesome for FTC approval of a new mechanism for obtaining parental consent under the Children’s Online Privacy Protection Rule (COPPA Rule). The applicants in 2023 requested approval for the use of “Privacy-Protective Facial Age Estimation” technology, which analyzes the geometry of a user’s face to confirm that they are an adult.

Under the COPPA Rule, online sites and services directed to children under 13, and those that have actual knowledge they are collecting personal information from children under 13, must obtain parental consent before collecting, using, or disclosing personal information from a child. The rule lays out a number of acceptable methods for gaining parental consent but also includes a provision allowing interested parties to submit new verifiable parental consent methods to the FTC for approval.

After receiving more than 350 comments, the FTC voted 4-0 to deny the application without prejudice to the applicants filing in the future, when the FTC anticipates that additional information will be available to assist the FTC and the public in better understanding age verification technologies and the application. In declining the application at this time, the FTC is taking no position on the merits of the application.

https://www.securitymagazine.com/articles/100562-ftc-denies-new-coppa-application


Government agencies collaborate on a guide to address DDoS attacks

The CISA, FBI and Multi-State Information Sharing and Analysis Center (MS-ISAC) collaborated to create a document guideline for organizations to defend against DDoS attacks. As DDoS attacks can be a challenge to trace and block, the vector is often leveraged by hacktivists, nation-state groups and other politically motivated actors. Therefore, government websites are common targets. 

The guideline emphasized three notable forms of DDoS attacks that the public sector should prepare for: 

  1. Protocol-based attacks, in which malicious actors target vulnerable protocol implementations to reduce a target’s performance and potentially cause a malfunction. 
  2. Volume-based attacks, which take up a target system’s resources by overloading it with a large volume of traffic.
  3. Application layer-based attacks, which target weaknesses within specific applications to take up its processing power or cause a malfunction. 

The advisory warns that these attacks are not mutually exclusive, as malicious actors can deploy multiple methods to launch sophisticated attacks. Additionally, attack methods are constantly evolving. 

Security leaders weigh in 

Ken Dunham, Cyber Threat Director at Qualys Threat Research Unit:

“DDoS attacks have proven to be the most effective by bad actors for payouts and disruption when timed against a target’s primary business needs. For example, targeting a gambling institution just prior to a sporting event, which would make it more likely to payout to make the DDoS attacks stop. DDoS attack tactics have changed tremendously over the years with changes in technology. We’re seeing massive throughputs that are impossible to defend against unless you have specific DDoS countermeasures in place, proactively, starting at the edge of your border gateway. In keeping with the themes of the joint advisory, organizations would be wise to proactively identify actors, threats, and TTPs specific to their organization to prioritize what might be more likely to hit and thus plan countermeasures more effectively.”

Darren Guccione, CEO and Co-Founder at Keeper Security:

“The latest joint advisory highlights the critical need for government entities to protect themselves against the persistent threat being presented by DDoS attacks. Because DDoS attacks are relatively easy to execute and can cause significant reputational and financial losses as a result of disrupting the target organization’s services, they are a prominent tool in bad actors’ arsenal. While not every attack can be prevented, this advisory offers steps that can be taken to mitigate the damage caused by cybercriminals and minimize impacts on systems and operations.

“Aligning with cybersecurity best practices, the joint advisory provides useful guidance to mitigating and responding to DDoS attacks. It emphasizes the importance of implementing network monitoring, regularly analyzing network traffic to have an established baseline and implementing captcha to differentiate between human users and bots. Additionally, organizations should consider developing a robust incident response plan, employing DDoS mitigation services and evaluating and potentially increasing bandwidth capacity to effectively mitigate the impact of these attacks.”

John Gallagher, Vice President of Viakoo Labs at Viakoo:

“The joint advisory issued by the US Government around DDoS attacks is important and needed to keep organizations vigilant about these threats.  In particular, breaking down the different methods of attack helps organizations refine their current (insufficient) strategies based on what their infrastructure is.  

“Calling out application-layer attacks (as  well as protocol based attacks) helps provide context to DDoS attacks – all too often it is just the volume-based attacks that defenses are based around.  DDoS attacks, like many other forms of cyber attack, often grows within an organization one application at a time.  Having application-based discovery methods, and a way to create a “dictionary” of device, port, and application connections can be effective in combating these attacks. 

“Where this advisory could have gone further is in recommending putting effort into bot eradication.  DDoS attack are quickly rising because threat actors have deployed vast botnet armies; where is the focus on removing those armies?  Especially where there are fleets of IoT devices (a typical place for bots to reside), some guidance and push should be made to eradicate these armies.”  

https://www.securitymagazine.com/articles/100555-government-agencies-collaborate-on-a-guide-to-address-ddos-attacks


AT&T acknowledges data leak that hit 73 million current and former users

A person walks past an AT&T store on a city street.
Getty Images | VIEW press

AT&T reset passcodes for millions of customers after acknowledging a massive leak involving the data of 73 million current and former subscribers.

“Based on our preliminary analysis, the data set appears to be from 2019 or earlier, impacting approximately 7.6 million current AT&T account holders and approximately 65.4 million former account holders,” AT&T said in an update posted to its website on Saturday.

An AT&T support article said the carrier is “reaching out to all 7.6 million impacted customers and have reset their passcodes. In addition, we will be communicating with current and former account holders with compromised sensitive personal information.” AT&T said the leaked information varied by customer but included full names, email addresses, mailing addresses, phone numbers, Social Security numbers, dates of birth, AT&T account numbers, and passcodes.

AT&T’s acknowledgement of the leak described it as “AT&T data-specific fields [that] were contained in a data set released on the dark web.” But the same data appears to be on the open web as well. As security researcher Troy Hunt wrote, the data is “out there in plain sight on a public forum easily accessed by a normal web browser.”

The hacking forum has a public version accessible with any browser and a hidden service that requires a Tor network connection. Based on forum posts we viewed today, the leak seems to have appeared on both the public and Tor versions of the hacking forum on March 17 of this year. Viewing the AT&T data requires a hacking forum account and site “credits” that can be purchased or earned by posting on the forum.

Hunt told Ars today that the term “dark web” is “incorrect and misleading” in this case. The forum where the AT&T data appeared “does not meet the definition of dark web,” he wrote in an email. “No special software, no special network, just a plain old browser. It’s easily discoverable via a Google search and immediately shows many PII [Personal Identifiable Information] records from the AT&T breach. Registration is then free for anyone with the only remaining barrier being obtaining credits.”

We contacted AT&T today and will update this article if we get a response.

49 million email addresses

Hunt’s post on March 19 said the leaked information included a file with 73,481,539 lines of data that contained 49,102,176 unique email addresses. Another file with decrypted Social Security numbers had 43,989,217 lines, he wrote.

Hunt, who runs the “Have I Been Pwned” database that lets you check if your email was in a data breach, says the 49 million email addresses in the AT&T leak have been added to his database.

BleepingComputer covered the leak two weeks ago, writing that it is the same data involved in a 2021 incident in which a hacker shared samples of the data and attempted to sell the entire data set for $1 million. In 2021, AT&T told BleepingComputer that “the information that appeared in an Internet chat room does not appear to have come from our systems.”

AT&T maintained that position last month. “AT&T continues to tell BleepingComputer today that they still see no evidence of a breach in their systems and still believe that this data did not originate from them,” the news site’s March 17, 2024, article said.

AT&T says data may have come from itself or vendor

AT&T’s update on March 30 acknowledged that the data may have come from AT&T itself, but said it also may have come from an AT&T vendor:

AT&T has determined that AT&T data-specific fields were contained in a data set released on the dark web approximately two weeks ago. While AT&T has made this determination, it is not yet known whether the data in those fields originated from AT&T or one of its vendors. With respect to the balance of the data set, which includes personal information such as Social Security numbers, the source of the data is still being assessed.

“Currently, AT&T does not have evidence of unauthorized access to its systems resulting in exfiltration of the data set,” the company update also said. AT&T said it “is communicating proactively with those impacted and will be offering credit monitoring at our expense where applicable.”

AT&T said the passcodes that it reset are generally four digits and are different from AT&T account passwords. The passcodes are used when calling customer support, when managing an account at a retail store, and when signing in to the AT&T website “if you’ve chosen extra security.”

https://arstechnica.com/?p=2014073


Florida Pediatric Associates health data impacted by data breach

Florida Pediatric Associates (FPA) announced that a data breach experienced by Bowden Barlow Law may have affected FPA health information. No FPA systems were impacted by the event, which was limited to Bowden Barlow’s environment.

On December 27, 2023, Bowden Barlow informed FPA that it had experienced a potential data security incident, and as a result, certain FPA patient data may have been acquired without authorization. Bowden Barlow did not know the scope of the impact to FPA data. On February 9, 2024, FPA’s investigation identified that some patient and guarantor information may have been involved in the incident.

On March 28, 2024, FPA provided notice of the incident to potentially impacted individuals along with resources to assist them. The potentially affected information may include the following: individuals’ names, dates of birth, account numbers, Social Security numbers, health insurance information, claims information and treatment information.

https://www.securitymagazine.com/articles/100553-florida-pediatric-associates-health-data-impacted-by-data-breach