Deepfake e Intelligenza Artificiale: tra rischi di sicurezza e vantaggi

La diffusione di attacchi e di minacce le quali utilizzano come vettore il deepfake e la manipolazione delle informazioni rappresentano sfide significative per la sicurezza e l’integrità delle informazioni. I contesti in cui è opportuno porre attenzione sono plurimi, vedasi l’ambito politico, aziendale e sociale e pertanto, nel mare magnum delle molteplici minacce che permeano il panorama del mondo cibernetico, tali attacchi richiedono l’impiego di tecniche e strumenti difensivi che si dimostrino non solo efficienti, ma altresì altamente rapidi nella loro evoluzione.

Deepfake: cosa sono e come si sono evoluti

I deepfake sono contenuti multimediali manipolati, spesso video, che utilizzano la tecnologia dell’intelligenza artificiale (IA) per creare immagini realistiche di persone o situazioni che in realtà non sono accadute. Vengono quindi sviluppati attraverso tecniche per la sintesi dell’immagine umana basata sull’intelligenza artificiale, usata per combinare e sovrapporre immagini e video esistenti con video o immagini originali, tramite un procedimento di apprendimento automatico, conosciuto come rete antagonista generativa (comunemente nota come GAN (dall’inglese “Generative Adversarial Network”). Le reti GAN sono composte da due componenti principali, i quali lavorano in maniera antagonista: il generatore e il discriminatore.

  • Generatore (Generator): Il generatore in una rete GAN ha il compito di creare dati artificiali che dovrebbero sembrare il più possibile simili ai dati di addestramento reali. Ad esempio, nel contesto dei deepfake, il generatore potrebbe produrre immagini o audio che sembrano provenire da una persona specifica, anche se sono in realtà completamente sintetiche.
  • Discriminatore (Discriminator): Il discriminatore, d’altra parte, è un modello di apprendimento che cerca di distinguere tra dati reali e dati generati dal generatore. Nel contesto dei deepfake, il discriminatore valuta se un’immagine o un audio è autentico o se è il risultato della generazione del generatore. Il suo obiettivo è migliorare nel riconoscere la differenza tra dati reali e dati sintetici.

In sostanza quindi, il processo di addestramento di una rete GAN è basato su una competizione continua tra il generatore e il discriminatore. Il generatore cerca di migliorare costantemente la sua capacità di generare dati falsi che sembrano reali, mentre il discriminatore cerca di diventare sempre più abile nel distinguere tra dati reali e generati. Questo ciclo di retroazione continua fa sì che entrambi i componenti della rete migliorino nel corso del tempo.

Tale tecnologia, quindi, può essere adoperata per la creazione di notizie fasulle, la disseminazione di informazioni ingannevoli e l’organizzazione di truffe, dando luogo a comportamenti quali il cyberbullismo o altri reati informatici di varia natura. Allo stesso modo, può essere utilizzata a fini satirici.

L’affermazione “Se non vedo non credo”, come proferito da san Tommaso d’Aquino in merito alla risurrezione di Gesù, precedentemente contestata dai suoi apostoli, risulta ora obsoleta e, persino pericolosa. L’avvento della tecnologia deepfake sta alterando profondamente le dinamiche, esigendo dagli utenti della Rete una vigilanza sempre più acuta sulla genuinità dei contenuti da loro fruiti.

D’altronde è sufficiente vedere gli esempi riportati nel link di seguito: https://www.creativebloq.com/features/deepfake-examples per rendersi conto del grado di pericolosità che un’azione così mistificatoria e anche apparentemente satirica può provocare. Danni a persone e cose, azioni e reazioni sono solo alcune delle conseguenze plausibili che questa affascinante e pericolosa tecnologia può generare. Per comprendere al meglio quindi il processo che si cela dietro la creazione dei deepfake è opportuno sciogliere l’argomento nei suoi passaggi chiave:

  1. Raccolta dei dati: Per creare un deepfake audio convincente, è necessario raccogliere un ampio set di dati vocali dalla persona di destinazione. Questi dati possono essere estratti da interviste, discorsi pubblici, podcast o altri contenuti vocali disponibili.
  2. elaborazione dei dati: I dati vocali raccolti vengono elaborati per estrarre le caratteristiche significative della voce, come il tono, la modulazione, il ritmo e altri tratti distintivi.
  3. Addestramento del modello: Un modello di apprendimento profondo, come una rete neurale, viene addestrato utilizzando il set di dati vocali della persona di destinazione. Durante l’addestramento, la rete impara a riconoscere e riprodurre le caratteristiche vocali specifiche della persona.
  4. Generazione del deepfake audio: Una volta addestrato il modello, è possibile utilizzarlo per generare nuovi segmenti vocali. Questi segmenti possono essere basati su script specifici o generati in modo più libero, a seconda degli obiettivi dell’utilizzatore del deepfake audio.
  5. Ottimizzazione: Il risultato del deepfake audio può essere ottimizzato per renderlo più realistico e convincente. Questo potrebbe coinvolgere l’aggiunta di rumori ambientali, la regolazione di parametri specifici o altre tecniche di perfezionamento.
  6. Distribuzione o utilizzo: Una volta creato il deepfake audio, può essere distribuito o utilizzato per vari scopi, che vanno dall’intrattenimento alla manipolazione di informazioni.

“Come mai potrebbero vivere i ciarlatani e gl’imbroglioni, se non gettassero l’amo all’ingenua turba con qualche scrignetto o qualche borsa piena di denaro sonante? Come i pesci si prendono coll’esca, così gli uomini non si potrebbero gabbare, se non si desse loro qualche speranza da mordere”. (Petronio Arbitro).

Le tipologie di deepfake

Esistono diverse tipologie di deepfake, e la tecnologia continua a evolversi. Alcune delle principali categorie di deepfake includono:

Face swaps: In questa categoria, il viso di una persona di origine (source) viene sovrapposto su una persona destinataria (target). Questa pratica è comunemente utilizzata per creare contenuti ironici sui social media, spesso facendo uso dei volti di celebrità. Le tecnologie attuali, come le reti neurali profonde (Deep Neural Network – DNN), sono impiegate per questo scopo, anche se le prime forme di face swap risalgono agli anni ’90 con l’uso di software come Adobe Photoshop.

Lip-syncing: In questa tipologia, un video viene modificato per far sembrare che la persona destinataria pronunci frasi fittizie. Questo processo coinvolge l’utilizzo della voce registrata da una o più fonti, sincronizzata con un altro video per renderlo autentico. Un esempio iniziale di questa tecnica è stato Face2Face, un modello creato da ricercatori di Stanford nel 2017, che fa uso delle Reti Neurali Ricorrenti (Recurrent Neural Networks – RNN).

Puppet-master: Questo tipo di deepfake coinvolge l’imposizione dell’aspetto di una persona destinataria (puppet) su un’altra persona che compie azioni. Una metodologia comune per creare questo tipo di deepfake utilizza le reti generative avversarie (GAN), in cui un “generatore” di dati falsi sfida un “discriminatore” il cui compito è distinguere tra dati reali e falsi. L’efficacia di questo modello dipende dalla capacità del generatore di “ingannare” il discriminatore.

Deepfake e impatto sulla società

Abbiamo capito quindi quali sono le enormi potenzialità di questo strumento. Ora è opportuno fare un ragionamento relativo ai possibili ambiti che possono risentire dell’alterazione della realtà causata dallo sfruttamento di potenti tool tecnologici uniti alla fantasia umana.

Implicazioni politiche: La diffusione di deepfake e la manipolazione delle informazioni possono portare gravi conseguenze nel contesto politico. Può diventare difficile distinguere la realtà dalla finzione, e questo potrebbe influenzare l’opinione pubblica, le elezioni e la stabilità politica. Basti pensare al simulato episodio in cui Renzi, apparentemente presente, manifestava il suo dissenso attraverso un gesto volgare verso Mattarella durante una trasmissione satirica come “Striscia la Notizia”. Come spesso accade, è stato necessario un programma di satira per porre l’attenzione su una questione estremamente seria. Non si trattava né di un imitatore né di un sosia; questa volta, la tecnologia si è rivelata l’ultima frontiera della manipolazione. Non solo è in grado di acquisire i tratti di un volto e sovrapporlo a chiunque altro ma può anche catturare l’autentico timbro della tua voce, rimodulandolo per far pronunciare parole che non sono mai state dette. Quindi, eventuali implicazioni di natura politica potrebbero riverberarsi sulla stabilità nazionale. Politici e leader possono diventare bersagli di deepfake, con la creazione di contenuti falsi atti a danneggiare la loro reputazione o influenzano l’immagine pubblica. Questo potrebbe avere conseguenze sulla loro carriera politica e sulla stabilità delle istituzioni. La manipolazione di discorsi e dichiarazioni di leader politici, può alimentare confusione o portare a malintesi diplomatici con gravi conseguenze gravi relazioni internazionali e nella diplomazia. (https://www.youtube.com/watch?v=JZl3cQTL6U0).

Ma, anche ponendo il caso che l’arguzia umana superi la sofisticatezza tecnologica, si potrebbe ingenerare un fenomeno quasi contrario. Il bombardamento mediatico di contenuti manipolati e manipolatori potrebbe contribuire a una crescente sfiducia nella veridicità delle informazioni e delle immagini. La manipolazione digitale potrebbe mettere in discussione l’autenticità di qualsiasi dichiarazione o evento, complicando la formazione di opinioni informate. Per concludere, o nei confronti della reputazione personale o anche peggio contro la stabilità politica e nazionale, questi contenuti possono risultare machiavellici e dannosi.

Implicazioni aziendali: Nel mondo complesso e sempre più interconnesso delle aziende, la manipolazione delle informazioni è senza dubbio una minaccia reale. Questa pratica non solo punta a danneggiare la reputazione delle organizzazioni, ma può anche avere impatti significativi sui mercati finanziari, generando danni notevoli.

Si può immaginare una situazione in cui notizie false sulle performance finanziarie di un’azienda vengono disseminate intenzionalmente. Un simile scenario potrebbe causare turbolenze finanziarie e minare la fiducia degli investitori, gettando un’ombra sull’integrità aziendale. La veridicità delle informazioni è un pilastro fondamentale nelle dinamiche aziendali, e la manipolazione di dati finanziari tramite deepfake costituisce una minaccia tangibile.

In aggiunta, emerge il rischio di frode, dove i deepfake diventano strumenti per ingannare le aziende. Basti pensare alla creazione di video contraffatti di dirigenti aziendali, i quali veicolano messaggi falsi o transazioni finanziarie manipolate. Questa forma di inganno può arrecare danni irreparabili alla reputazione delle aziende e dei loro leader.

Tuttavia, le preoccupazioni non si limitano alle questioni finanziarie. L’utilizzo dei deepfake apre la porta a nuove minacce per la sicurezza informatica. Criminali potrebbero sfruttare questa tecnologia per eludere sistemi di autenticazione basati su riconoscimento facciale o vocale. Inoltre, i dipendenti stessi potrebbero essere vittime di deepfake senza il loro consenso, un’azione che viola la loro privacy e crea situazioni dannose sia a livello personale che professionale.

Deepfake audio: quali sono i possibili rischi

Il deepfake audio è una tecnica che utilizza l’intelligenza artificiale, in particolare il deep learning, per manipolare e generare file audio falsi che sembrano autentici. Questa tecnologia può essere utilizzata per alterare voci, creare discorsi o dialoghi inventati, o persino imitare voci di persone specifiche in modo convincente. Le moderne simulazioni vocali hanno raggiunto oltretutto una precisione tale da imitare con straordinaria fedeltà l’intonazione, il ritmo e le sfumature di una voce umana (impressionanti a tal proposito sono i deepfake che utilizzano voci di cantanti famosi deceduti utilizzandole in canzoni moderne ampiamente diffuse https://www.youtube.com/watch?v=Num0q-l-ldc). Questa capacità le rende virtualmente indistinguibili dalla realtà, diventando un potente strumento nelle mani dei criminali per truffare individui e aziende.

Un esempio recente, riportato dal New York Times, coinvolge un falso robocall che impersona il presidente Biden, il quale mira allo scopo di influenzare le primarie del New Hampshire. La chiamata, che sembra provenire da Kathy Sullivan, ex presidente del Partito Democratico del New Hampshire, scoraggia gli elettori dal partecipare alle primarie. Biden non è in corsa nelle primarie del New Hampshire, ma la chiamata è stata manipolata per sembrare legata a una campagna a livello statale che incoraggia a votare per lui.

Ma perché i deepfake audio sono così complessi da distinguere, a tal punto che sono tra i più utilizzati in truffe e tentativi di frode? Uno studio (Warning: Humans cannot reliably detect speech deepfakes) ha dimostrato che i partecipanti hanno fallito il 25% delle volte nel tentativo di rilevare i deepfake vocali. La metà dei partecipanti ha ricevuto una formazione preliminare ascoltando cinque esempi di voce sintetizzata, ma la loro prestazione è stata migliore solo del 3% rispetto al gruppo non addestrato. Questo perché l’audio è soggettivo. A differenza del rilevamento dei deepfake visivi, in cui l’autenticità può essere giudicata osservando oggetti e sfondi, la natura soggettiva del parlato fa sì che le percezioni varino maggiormente. Le onde sonore assumono frequenze diverse attraversando l’aria o un mezzo solido e quindi la voce ha un timbro diverso. Inoltre, un registratore altera la voce, anche se in maniera minima. Durante la registrazione, infatti, il suono viene “tradotto” da onde sonore meccano-elastiche (cioè vibrazioni) a onde elettromagnetiche (cioè segnali elettrici), mentre per l’ascolto avviene il processo inverso: così la voce che esce da questi passaggi non è mai perfettamente identica all’originale, e questo chiaramente ci rende meno attenti ai messaggi veicolati tramite voce, dato che siamo abituati a sentire anche voci a noi care come diverse via messaggio vocale. Il cervello umano è generalmente più sensibile e attento alle informazioni visive rispetto a quelle uditive e, dato che il riconoscimento di voci e tratti vocali è un processo complesso, è più difficile individuare anomalie nell’audio rispetto a segnali visivi. Nel video, inoltre, ci sono più punti di riferimento visivi, come espressioni facciali, movimenti degli occhi, ecc, i quali possono essere utilizzati per individuare incongruenze. Nell’audio, tali punti di riferimento sono meno evidenti, rendendo difficile l’individuazione di manipolazioni.

Un ulteriore elemento discriminatorio si riscontra nel fatto che le persone possono essere più propense a sospettare di manipolazioni visive rispetto a manipolazioni uditive. Ciò può essere dovuto allo stigma che il concetto di “vedere per credere ” è più radicato nella società rispetto al “sentire per credere”.

Deepfake: quali sono i vantaggi che possono apportare nella società

I deepfake, se utilizzati in modo etico e responsabile, presentano diverse applicazioni potenzialmente vantaggiose in diversi settori. Basti pensare a quante possibilità possono verificarsi in contesti in cui il limite pare essere solo quello della propria fantasia, che, si spera sempre di più, possa essere delineato dalle norme.

Di seguito sono stati fatti alcuni ragionamenti liberi rispetto ad ambiti in cui i deepfake possono trovare utilità:

Nel settore della formazione e dello sviluppo aziendale, l’integrazione dei deepfake può trasformare il modo in cui i dipendenti acquisiscono competenze. Le simulazioni realistiche, come colloqui, sessioni di coaching o scenari di interazione con i clienti, potrebbero offrire un ambiente di apprendimento più coinvolgente ed efficace. Ciò potrebbe tradursi in una migliore preparazione dei dipendenti e, di conseguenza, in un miglioramento delle prestazioni aziendali.

Per quanto riguarda la produzione di contenuti multimediali, soprattutto nell’industria dell’intrattenimento, i deepfake rappresentano un’opportunità unica. La capacità di creare personaggi digitali convincenti può ridurre significativamente i costi di produzione nella post-produzione, consentendo una maggiore flessibilità creativa. Questo potrebbe portare a storie più coinvolgenti, effetti speciali avanzati e un processo di produzione più efficiente nel complesso.

Un esempio su tutti di utilizzo di Deepfake con scopi migliorativi lo si può trovare in ambito sanitario: il progetto Revoice. La tecnologia deepfake può restituire la voce a coloro che hanno perso la capacità di parlare a causa di malattie come la SLA. L’iniziativa denominata “Progetto Revoice” ha come obiettivo primario la completa ricreazione dell’essenza unica di qualsiasi voce, al fine di sviluppare un clone digitale della stessa destinato all’utilizzo quotidiano mediante dispositivi di Comunicazione Aumentata/Alternativa (AAC).

Sfide nella verifica

A causa della crescente sofisticazione delle tecnologie di manipolazione, la verifica dell’autenticità delle informazioni sta diventando una vera e propria sfida. Per questo motivo i grandi players dell’industria tecnologica si stanno adoperando per trovare delle contromisure al fine di limitare e contenere l’efficacia degli attacchi massivi e fraudolenti tramite deepfake.

Ad esempio, durante l’evento Consumer Electronics Show 2024, McAfee ha presentato Project Mockingbird, una soluzione che fa leva sull’intelligenza artificiale per mitigare i rischi legati alle frodi ai danni degli amministratori delegati (Ceo fraud) e ai deepfake audio. Project Mockingbird sta sviluppando una forma di riconoscimento attraverso l’integrazione di modelli di rilevamento contestuali, comportamentali e categoriali, impiegando l’intelligenza artificiale per determinare se l’audio di un video è probabilmente generato da un sistema di intelligenza artificiale. Anche Google ha intensificato la sua lotta contro i deepfake, immagini e video generati artificialmente, attraverso un aggiornamento della funzione “Informazioni su questa immagine”. Questa funzionalità fornisce agli utenti dati utili per verificare l’autenticità di un’immagine online. L’aggiornamento ora è integrato nel motore di ricerca di Google. Gli utenti possono cliccare sui tre punti nell’angolo in alto a destra di un’immagine nei risultati di ricerca per accedere a informazioni specifiche. Questo include dettagli su quando l’immagine è apparsa per la prima volta su Google e altre pagine web, nonché l’utilizzo e la descrizione della foto da parte dei siti. Inoltre, per aiutare a identificare i deepfake, Google consente di visualizzare i metadati aggiunti a un’immagine, inclusi quelli che potrebbero indicare la generazione o il miglioramento tramite intelligenza artificiale. Tuttavia, ciò dipende dalla corretta inserzione dei metadati da parte del proprietario dell’immagine. Esistono software più avanzati e a pagamento, come Sensity.ai, Sentinel, e il recente software di Intel con il detector “FakeCatcher”, che utilizzano l’intelligenza artificiale, in particolare reti neurali, per analizzare il contenuto alla ricerca di anomalie, ottenendo un’elevata percentuale di successo nell’identificazione dei deepfake. Tuttavia, attualmente, tali software con elevate capacità di calcolo e precisione sono limitati e prevalentemente utilizzati da grandi aziende e istituzioni. È opportuno quindi puntare sulla educazione delle persone e dare loro degli strumenti difensivi basati sulla consapevolezza. Puntare al fattore umano quindi, come baluardo della difesa personale e aziendale.

Educazione e consapevolezza

Come visto pocanzi quindi, l’educazione del pubblico sulla possibilità di manipolazioni delle informazioni è fondamentale. La consapevolezza del problema può e deve aiutare le persone a essere più critiche nelle valutazioni delle informazioni che incontrano online. La sfida che viene posta oggi è: come si può creare un percorso di Awareness che ci possa istruire al meglio su questa nuova minaccia?

Certamente è opportuno porre l’attenzione sulla formazione tecnica, magari offrendo corsi o risorse online che insegnino le basi delle tecnologie utilizzate per creare deepfake, oppure promuovere il pensiero critico, fornendo esempi pratici e aggiornando le persone tramite newsletter, oltre che sensibilizzare il pubblico sui tool suddetti di detection.

Proviamo ora a stilare noi una lista di elementi dei quali è opportuno tener conto per difendersi da attacchi generati con i Deepfake:

Occhi: La replicazione del naturale movimento degli occhi e dello sbattere delle ciglia risulta ancora complessa, poiché il soggetto spesso segue o fissa l’interlocutore durante una conversazione. Un movimento degli occhi innaturale o distorto può essere un segnale di possibile presenza di deepfake. Nel caso di immagini, è importante osservare la pupilla del soggetto, poiché spesso viene ricreata in modo inaccurato con bordi sfocati e una forma poco definita.

Viso ed espressioni facciali: I deepfake spesso coinvolgono sovrapposizioni di immagini, generando espressioni facciali distorte e innaturali. La pelle può essere un indicatore utile, specialmente se presenta discromie evidenti, texture irrealistiche (troppo liscia o troppo rugosa), ombre strane e barba o baffi con forme e definizioni anomale.

Denti e capelli: La ricostruzione di denti e capelli tramite intelligenza artificiale è difficile, e questo può rendere i sorrisi nei deepfake strani e poco definiti o i capelli troppo piatti e luminosi, come se fossero un oggetto unico.

Rumori o audio incoerente: Nell’analisi di un video, è essenziale prestare attenzione all’audio e cercare di correlarlo con il movimento delle labbra della persona che parla. La mancanza di coerenza tra audio e movimenti labiali può indicare la presenza di un deepfake.

Distorsioni visive: Pixel visibili, ombre innaturali o la presenza di oggetti fuori posto costituiscono indicatori importanti di un possibile deepfake.

Attendibilità della fonte: Oltre all’analisi visiva del presunto deepfake, è cruciale considerare la fonte in cui l’immagine o il video è stato pubblicato, valutandone l’affidabilità e la reputazione.

Affrontare queste sfide richiederà sforzi coordinati tra governi, aziende, organizzazioni non governative e individui. La ricerca continua, lo sviluppo di tecnologie di difesa avanzate e la promozione della consapevolezza sono tutte parti cruciali di una strategia globale contro la manipolazione delle informazioni.

Riferimenti bibliografici

Articolo a cura di Riccardo Laurenti
Profilo Autore

Consegue la Laurea magistrale in Scienze Politiche e Relazioni Internazionali presso la LUISS, improntando il percorso formativo in analisi e contrasto a fenomeni terroristici attraverso fonti OSINT e divulgazione mediatica.
Perfeziona il piano di studi prima con il Diploma di Specializzazione di 1° livello in Geopolitica e Sicurezza Globale, con particolare Focus al terrorismo di matrice islamica, poi con il Master 2° livello Homeland Security presso l’ Università Campus Bio-Medico di Roma, nel quale vengono approfonditi aspetti e tematiche di Cyber Security, OSINT, Business Continuity e Sicurezza delle infrastrutture critiche.
Dopo alcune esperienze lavorative nel settore della Reputation Intelligence, tra cui una in un importante player nazionale del settore energetico, attualmente è impiegato in Deep Cyber srl, con il ruolo di Cyber Secuirty Specialist, per il quale si occupa di analisi di minacce Cyber attraverso tools di simulazione e di Social Engineering (phishing, spear phishing, vishing, smishing, etc.) analisi OSINT e SOCMINT mediante strumenti di intelligence e Forensics investigations di compagnie, manager e 3°parti, al fine di supportare il management nei processi decisionali e di compliance.

Condividi sui Social Network:

https://www.ictsecuritymagazine.com/articoli/deepfake-e-intelligenza-artificiale-tra-rischi-di-sicurezza-e-vantaggi/


Better software supply chain security through SBOMs

.w3-panel:after,.w3-panel:before { content: “”; display: table; clear: both } .w3-panel { padding: 16px } .w3-panel { margin-top: 16px; margin-bottom: 16px } .w3-leftbar { border-left: 6px solid #58526F!important } .w3-sand,.w3-hover-sand:hover { color: #FFF!important; background-color: #908aa8!important } .w3-xlarge { font-size: 20px!important } .w3-xxlarge { font-size: 36px!important } .w3-sans-serif { Nunito Sans’,Arial,sans-serif } .w3-opacity,.w3-hover-opacity:hover { opacity: 0.60 }

An executive order from President Biden in 2021 focused on enhancing software supply chain security. This added transparency can help to identify and mitigate security risks, such as vulnerabilities in open source components or malicious code that has been inserted into the supply chain. These Software Bills of Materials (SBOMs) play an important role in enhancing software supply chain security by providing transparency into the components used to build software. This requirement is designed to help the government to better understand and manage the security risks associated with the software it uses.

The development of commercial software often lacks transparency, security focus, and safeguards against tampering. To ensure software functions securely and as intended, especially critical software, there is a need for more robust and predictable mechanisms. With this in mind, let’s explore the concept of a Supplier/Vendor Software Bill of Materials (SBOM).

In today’s interconnected digital landscape, the integrity and security of software components used in products and services are of paramount importance. As organizations rely on an intricate network of suppliers and vendors to source these components, ensuring transparency and understanding the composition of these software elements becomes crucial. This is where the concept of an SBOM comes into play.

What is a SBOM? It is a comprehensive document that provides a detailed inventory of all software components and dependencies used in a particular product or system, including those contributed by suppliers and vendors. It serves as a critical element of supply chain risk management and cybersecurity governance. The SBOM lists each binary component, its version, origin and potential vulnerabilities, enabling organizations to assess the security and compliance of their software supply chain thoroughly.

SBOM serves as a critical tool for transparency, security and risk management. It empowers organizations to make informed decisions about their software components, enabling them to build more secure, compliant and resilient products and services.

Creating a cybersecurity supply chain governance framework is a critical step in securing your organization’s digital supply chain. Here’s a step-by-step guide to get started:

Governance structure: Establish a dedicated cross-functional team responsible for SBOM governance. This team should include representatives from cybersecurity, software development, procurement, legal and compliance.

Policy and standards: Develop clear policies and standards that mandate the creation, maintenance and sharing of SBOMs for all software products used within the organization. These policies should outline the frequency of updates, data format and sharing mechanisms.

SBOM creation: Define a standardized process for creating SBOMs for each software product. This process should involve automated tools and manual reviews to ensure accuracy and completeness.

Inventory management: Maintain an up-to-date inventory of software components, libraries, frameworks and dependencies used in each software product. Track versions, origins and licenses for all components.


In an era of increasing cyber threats and regulatory scrutiny, the SBOM is a valuable tool that enhances transparency, security, and risk mitigation within the supply chain, ultimately safeguarding the integrity of software, firmware or products.”

Integration with development lifecycle: Integrate SBOM creation and maintenance into the software development lifecycle. Developers should generate SBOMs automatically during the build process, ensuring that each software release is accompanied by an accurate SBOM.

Supplier engagement: Collaborate with software suppliers and vendors to obtain SBOMs for third-party components. Mandate the provision of accurate and timely SBOMs as part of procurement agreements.

Continuous monitoring: Implement continuous monitoring of software components and their vulnerabilities. Regularly update SBOMs to include information about newly discovered vulnerabilities and available patches.

Vulnerability assessment: Integrate vulnerability assessment tools to analyze SBOMs and identify known vulnerabilities and security issues in software components. Prioritize addressing high-risk vulnerabilities.

Remediation and patching: Develop a process for addressing vulnerabilities identified in SBOMs. Define responsibilities for patch management and ensure timely remediation of identified vulnerabilities.

Sharing and transparency: Promote transparency by sharing SBOMs with relevant stakeholders, including internal teams, customers and partners. This fosters accountability and enables better risk assessment.

Compliance and reporting: Ensure compliance with relevant industry standards and regulations that require SBOMs. Generate reports that demonstrate the organization’s commitment to software transparency and security.

Incident Response: Incorporate SBOMs into the incident response process. In the case of a security breach or vulnerability exploit, having an accurate SBOM will help identify affected systems quickly.

Training and awareness: Educate software developers, procurement teams and relevant stakeholders about the importance of SBOMs, their role in cybersecurity and the procedures for generating and managing them.

Automation and tools: Invest in automation tools and software solutions that facilitate the creation, maintenance and analysis of SBOMs. These tools can streamline the process and enhance accuracy.

Continuous improvement: Regularly review and update the SBOM governance model to incorporate lessons learned from incidents, changes in software development practices, and evolving cybersecurity threats.

By maintaining an SBOM, organizations can swiftly identify and remediate vulnerabilities, respond to security incidents and ensure that software components are up-to-date and compliant with regulatory requirements. In an era of increasing cyber threats and regulatory scrutiny, the SBOM is a valuable tool that enhances transparency, security, and risk mitigation within the supply chain, ultimately safeguarding the integrity of software, firmware or products.

Remember that cybersecurity supply chain governance is an ongoing process. It requires adaptability and a commitment to continuous improvement to stay ahead of evolving cyber threats and vulnerabilities in today’s interconnected business environment.

https://www.securitymagazine.com/articles/100377-better-software-supply-chain-security-through-sboms


Canada declares Flipper Zero public enemy No. 1 in car-theft crackdown

A Flipper Zero device
Enlarge / A Flipper Zero device
https://flipperzero.one/

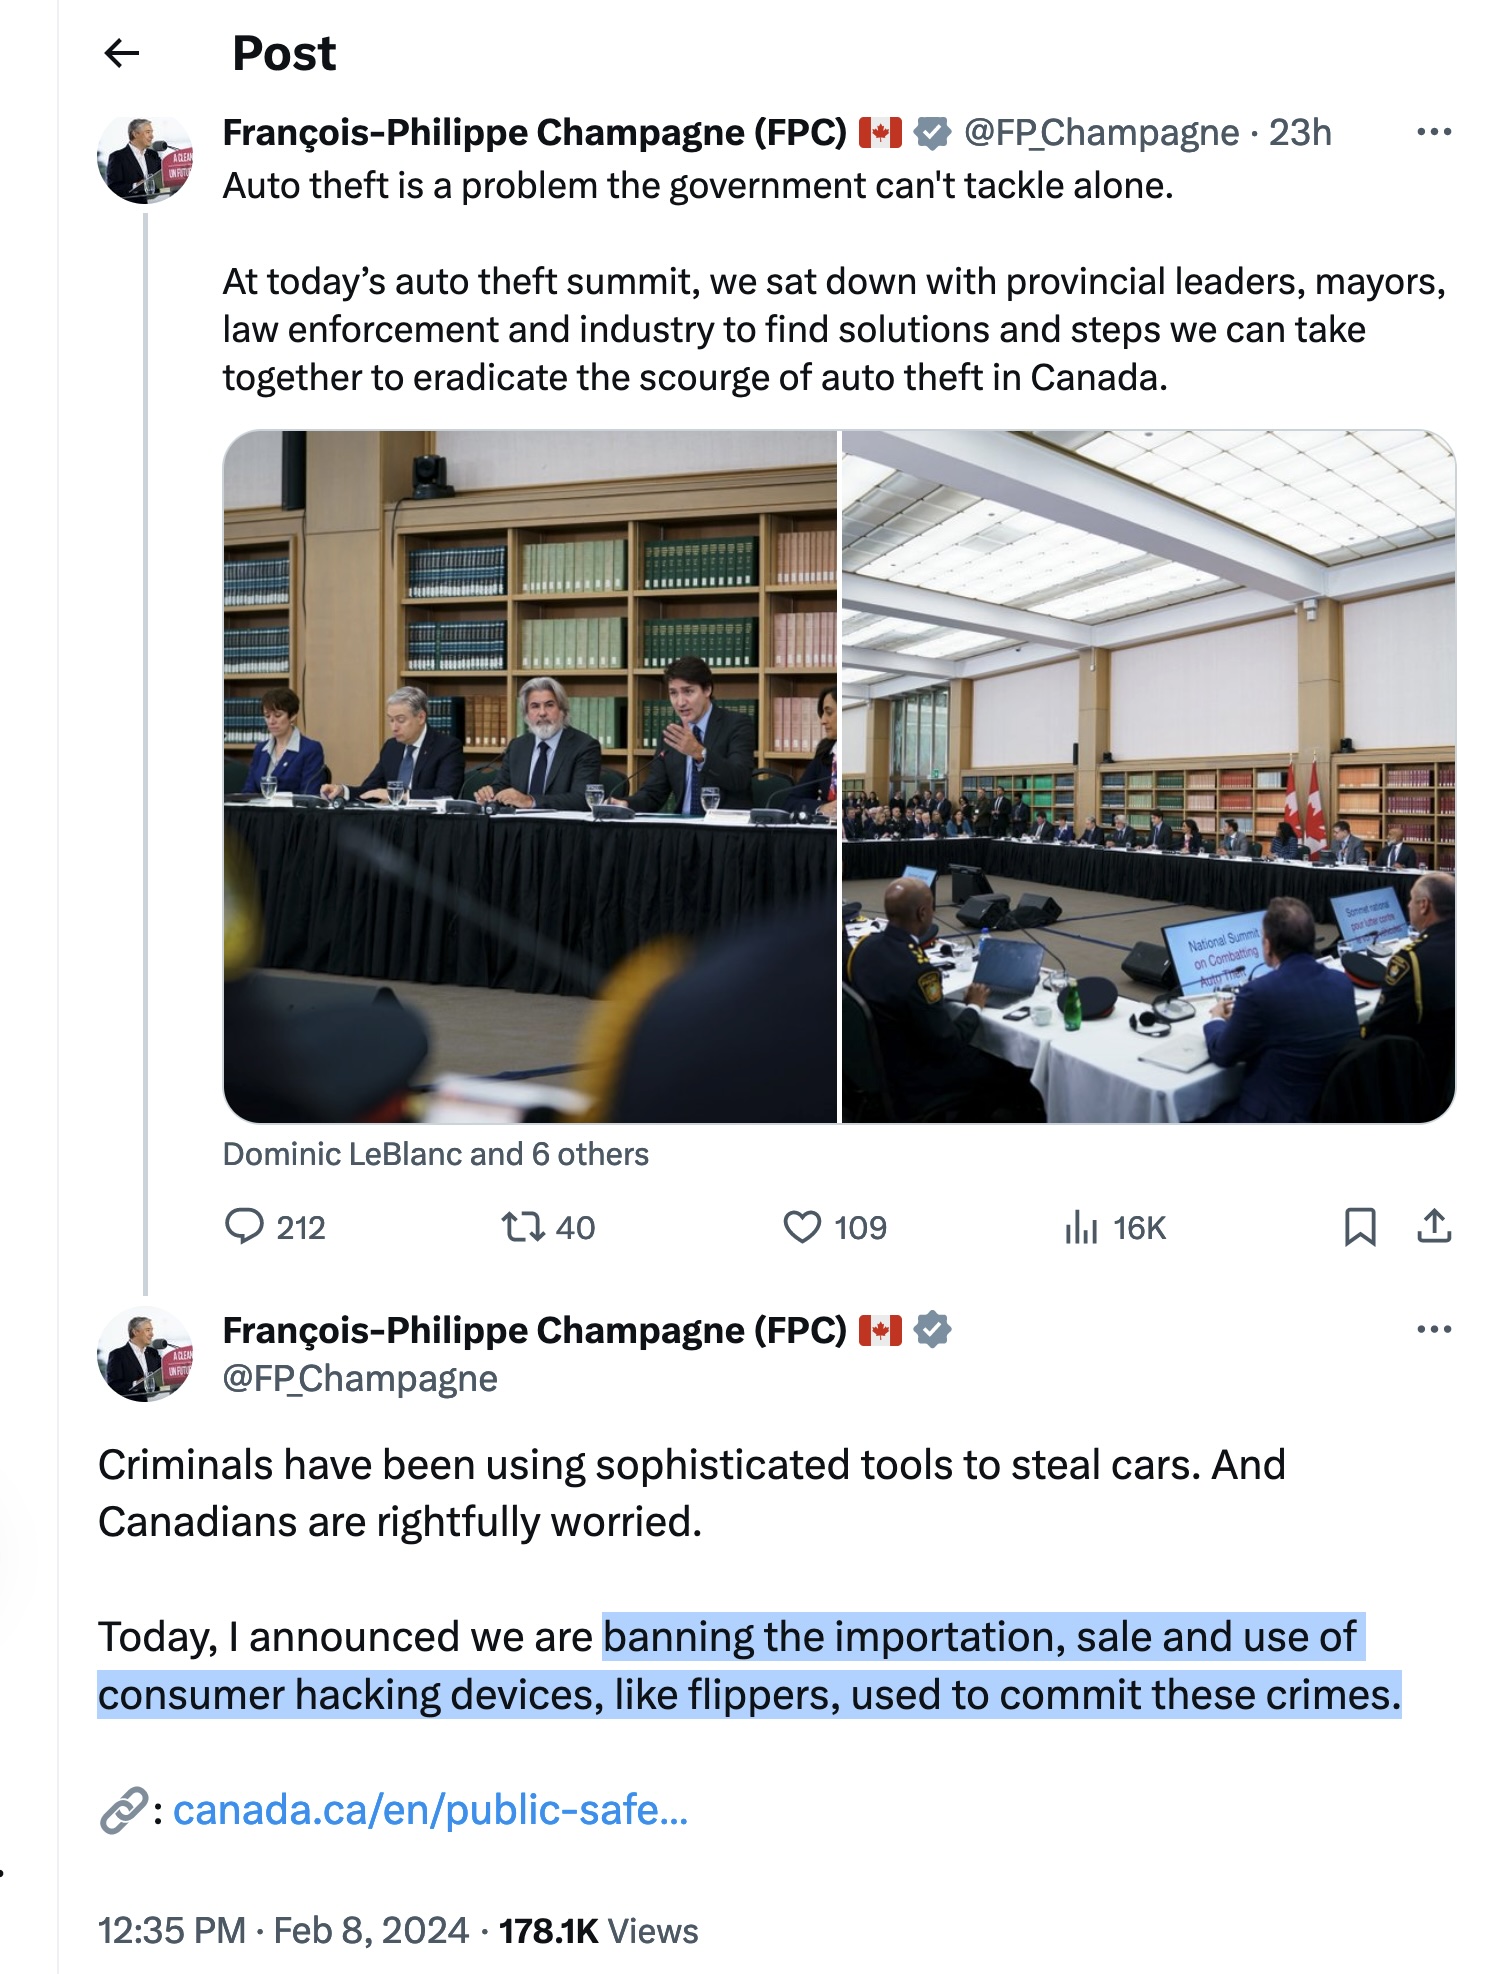
Canadian Prime Minister Justin Trudeau has identified an unlikely public enemy No. 1 in his new crackdown on car theft: the Flipper Zero, a $200 piece of open source hardware used to capture, analyze and interact with simple radio communications.

On Thursday, the Innovation, Science and Economic Development Canada agency said it will “pursue all avenues to ban devices used to steal vehicles by copying the wireless signals for remote keyless entry, such as the Flipper Zero, which would allow for the removal of those devices from the Canadian marketplace through collaboration with law enforcement agencies.” A social media post by François-Philippe Champagne, the minister of that agency, said that as part of the push “we are banning the importation, sale and use of consumer hacking devices, like flippers, used to commit these crimes.”

In remarks made the same day, Trudeau said the push will target similar tools that he said can be used to defeat anti-theft protections built into virtually all new cars.

“In reality, it has become too easy for criminals to obtain sophisticated electronic devices that make their jobs easier,” he said. “For example, to copy car keys. It is unacceptable that it is possible to buy tools that help car theft on major online shopping platforms.”

Presumably, such tools subject to the ban would include HackRF One and LimeSDR, which have become crucial for analyzing and testing the security of all kinds of electronic devices to find vulnerabilities before they’re exploited. None of the government officials identified any of these tools, but in an email, a representative of the Canadian government reiterated the use of the phrase “pursuing all avenues to ban devices used to steal vehicles by copying the wireless signals for remote keyless entry.”

A humble hobbyist device

The push to ban any of these tools has been met with fierce criticism from hobbyists and security professionals. Their case has only been strengthened by Trudeau’s focus on Flipper Zero. This slim, lightweight device bearing the logo of an adorable dolphin acts as a Swiss Army knife for sending, receiving, and analyzing all kinds of wireless communications. It can interact with radio signals, including RFID, NFC, Bluetooth, Wi-Fi, or standard radio. People can use them to change the channels of a TV at a bar covertly, clone simple hotel key cards, read the RFID chip implanted in pets, open and close some garage doors, and, until Apple issued a patch, send iPhones into a never-ending DoS loop.

The price and ease of use make Flipper Zero ideal for beginners and hobbyists who want to understand how increasingly ubiquitous communications protocols such as NFC and Wi-Fi work. It bundles various open source hardware and software into a portable form factor that sells for an affordable price. Lost on the Canadian government, the device isn’t especially useful in stealing cars because it lacks the more advanced capabilities required to bypass anti-theft protections introduced in more than two decades.

One thing the Flipper Zero is exceedingly ill-equipped for is defeating modern antihack protections built into cars, smartcards, phones, and other electronic devices.

The most prevalent form of electronics-assisted car theft these days, for instance, uses what are known as signal amplification relay devices against keyless ignition and entry systems. This form of hack works by holding one device near a key fob and a second device near the vehicle the fob works with. In the most typical scenario, the fob is located on a shelf near a locked front door, and the car is several dozen feet away in a driveway. By placing one device near the front door and another one next to the car, the hack beams the radio signals necessary to unlock and start the device.

https://arstechnica.com/?p=2002579


AI-generated voices in robocalls declared illegal by the FCC

AI-generated voices have been declared as “artificial” under the Telephone Consumer Protection Act (TCPA). This new ruling made by the Federal Communications Commission has made AI voice cloning technology used for robocall scams illegal. This will allow State Attorneys Generals to pursue the actors behind these robocall scams.  

A Notice of Inquiry launched in November of 2023 encouraged this ruling. The purpose of this Notice of Inquiry was to address the involvement of AI in robocall scams and explore ways to prevent these calls with AI pattern recognition that could root out AI-generated calls.

This ruling follows the rise of robocall scams that use AI to impersonate political figures, celebrities, or family members to extort individuals. Prior to this decision, the State Attorneys Generals could only pursue the resulting scam of a robocall, but not the AI-generated voice call itself. Now, perpetrators of these fraudulent calls can be held accountable through more legal avenues. 

https://www.securitymagazine.com/articles/100394-ai-generated-voices-in-robocalls-declared-illegal-by-the-fcc


London Underground is testing real-time AI surveillance tools to spot crime

Commuters wait on the platform as a Central Line tube train arrives at Liverpool Street London Transport Tube Station in 2023.

Thousands of people using the London Underground had their movements, behavior, and body language watched by AI surveillance software designed to see if they were committing crimes or were in unsafe situations, new documents obtained by WIRED reveal. The machine-learning software was combined with live CCTV footage to try to detect aggressive behavior and guns or knives being brandished, as well as looking for people falling onto Tube tracks or dodging fares.

From October 2022 until the end of September 2023, Transport for London (TfL), which operates the city’s Tube and bus network, tested 11 algorithms to monitor people passing through Willesden Green Tube station, in the northwest of the city. The proof of concept trial is the first time the transport body has combined AI and live video footage to generate alerts that are sent to frontline staff. More than 44,000 alerts were issued during the test, with 19,000 being delivered to station staff in real time.

Documents sent to WIRED in response to a Freedom of Information Act request detail how TfL used a wide range of computer vision algorithms to track people’s behavior while they were at the station. It is the first time the full details of the trial have been reported, and it follows TfL saying, in December, that it will expand its use of AI to detect fare dodging to more stations across the British capital.

In the trial at Willesden Green—a station that had 25,000 visitors per day before the COVID-19 pandemic—the AI system was set up to detect potential safety incidents to allow staff to help people in need, but it also targeted criminal and antisocial behavior. Three documents provided to WIRED detail how AI models were used to detect wheelchairs, prams, vaping, people accessing unauthorized areas, or putting themselves in danger by getting close to the edge of the train platforms.

The documents, which are partially redacted, also show how the AI made errors during the trial, such as flagging children who were following their parents through ticket barriers as potential fare dodgers, or not being able to tell the difference between a folding bike and a non-folding bike. Police officers also assisted the trial by holding a machete and a gun in the view of CCTV cameras, while the station was closed, to help the system better detect weapons.

Privacy experts who reviewed the documents question the accuracy of object detection algorithms. They also say it is not clear how many people knew about the trial, and warn that such surveillance systems could easily be expanded in the future to include more sophisticated detection systems or face recognition software that attempts to identify specific individuals. “While this trial did not involve facial recognition, the use of AI in a public space to identify behaviors, analyze body language, and infer protected characteristics raises many of the same scientific, ethical, legal, and societal questions raised by facial recognition technologies,” says Michael Birtwistle, associate director at the independent research institute the Ada Lovelace Institute.

In response to WIRED’s Freedom of Information request, the TfL says it used existing CCTV images, AI algorithms, and “numerous detection models” to detect patterns of behavior. “By providing station staff with insights and notifications on customer movement and behaviour they will hopefully be able to respond to any situations more quickly,” the response says. It also says the trial has provided insight into fare evasion that will “assist us in our future approaches and interventions,” and the data gathered is in line with its data policies.

In a statement sent after publication of this article, Mandy McGregor, TfL’s head of policy and community safety, says the trial results are continuing to be analyzed and adds, “there was no evidence of bias” in the data collected from the trial. During the trial, McGregor says, there were no signs in place at the station that mentioned the tests of AI surveillance tools.

“We are currently considering the design and scope of a second phase of the trial. No other decisions have been taken about expanding the use of this technology, either to further stations or adding capability.” McGregor says. “Any wider roll out of the technology beyond a pilot would be dependent on a full consultation with local communities and other relevant stakeholders, including experts in the field.”

https://arstechnica.com/?p=2002361


Americans received 15 spam calls a month in Q4 2023

Fraud calls around the globe were analyzed in a recent report by Hiya. According to the report, there were 7.3 billion unwanted calls globally in Q3 2023, up from 6.55 billion in Q3. The number of spam calls peaked at 357 million the week after Thanksgiving, when U.S. consumers are shopping, distracted and therefore particularly vulnerable to scams.

American consumers in Q4 received an average of 15 spam calls per month, which was higher than all the European countries listed in the report but not as high as some countries in South America. The U.S.’s spam rate for the quarter was a relatively high 29% but 1% of those unwanted calls are fraud, giving it one of the lowest fraud rates in the world. Most fraud calls in the U.S. are blocked by the carrier at the network level, so they never reach consumers.

The most commonly reported scams targeting Americans in Q4 involved Medicare, insurance, taxes, Amazon, credit cards, relief (debt relief, tax relief, etc.) and payment platform apps such as Venmo, PayPal, Zelle and Cash App. While many of the scams remained steady throughout the quarter, Medicare and health insurance scams spiked during the health care open enrollment period, which runs from late October to early December each year.

Residents of France and Spain received the same number of unwanted calls each month: an average of 10 per person. But in Q4, France overtook Spain as the European country with the highest spam rate, hitting 47%. The most prolific phone scam in France in Q4 impersonated the French electric utility company, EDF Energy. With this scam, imposters lure victims with government-funded energy subsidies, solar panel installation and other schemes to save money on energy costs. Also popular were scams impersonating bank officials and ploys to cheat citizens out of their Compte Personnel de Formation funds, which are provided by the French government to pay for professional training.

Scam calls impersonating banks were the most-reported type of fraud in Spain during Q4; insurance scams came in a close second. Package delivery and cryptocurrency scams were also common in Spain, as they are in many other countries. Also making the list were family member scams, in which fraudsters posed as a daughter, son, grandchild or other family member in trouble and in need of an urgent money transfer.

U.K. residents received four spam calls per person each month in Q4, according to the report. The U.K.’s spam rate of 28% was about the same as the U.S., but it gets more fraud calls. Common in Q4 were HMRC tax scams and Amazon imposter scams.

Read the full report here.

https://www.securitymagazine.com/articles/100393-americans-received-15-spam-calls-a-month-in-q4-2023


L’evoluzione dei cyberattacchi iraniani contro Israele


Dopo l’attacco di Hamas a Israele lo scorso ottobre, la guerra è continuata non solo sul campo fisico, ma anche su quello virtuale: numerosi gruppi legati all’Iran hanno lanciato diverse campagne di cyberattacchi, insieme a operazioni di propaganda e disinformazione, con l’obiettivo di indebolire Israele e i suoi alleati.

Anche se all’inizio le operazioni erano piuttosto affrettate e caotiche, col tempo i gruppi cybercriminali iraniani si sono dimostrati più coordinati e le loro campagne più efficaci.

Una recente analisi di Microsoft sul fenomeno ha evidenziato che il numero di gruppi iraniani attivi contro Israele è cresciuto da 9 della prima settimana di guerra a 14 nella seconda settimana, mentre gli attacchi sono arrivati da 1 a 11 al mese. Negli ultimi mesi i cyberattacchi sono diventati sempre più mirati e distruttivi, e le campagne di disinformazione sono diventate molto sofisticate anche grazie a una fitta rete di account falsi sui social media.

La propaganda iraniana ha raggiunto anche gli alleati israeliani, in particolare i Paesi anglofoni come il Regno Unito, gli Stati Uniti, il Canada, l’Australia e la Nuova Zelanda. Ciò ha portato a un aumento del 42% del traffico verso i siti di notizie iraniani durante la prima settimana del conflitto; la percentuale in seguito è scesa, ma è rimasta comunque di un 28% più alta rispetto ai livelli pre-guerra.

cyberattacchi Israele

Pixabay

Le tre fasi dei cyberattacchi contro Israele

Il Microsoft Threat Analysis Center ha suddiviso le operazioni iraniane in tre fasi: la prima, più confusa, è nata in reazione all’attacco di Hamas; la seconda fase ha visto una maggior organizzazione da parte dei gruppi, tutti focalizzati sul sostenere la causa di Hamas; infine, durante la terza fase gli attaccanti hanno lavorato per espandere il proprio raggio d’azione.

La prima fase è stata caratterizzata da attacchi opportunisti e conseguenti affermazioni fuorvianti da parte dei media di stato iraniani. Un esempio è stato l’agenzia di stampa Tasnimche ha affermato che un gruppo chiamato Cyber Avengers aveva condotto attacchi informatici contro una centrale elettrica israeliana durante gli attacchi di Hamas, ma le prove dell’operazione si riferivano a notizie vecchie di settimane e interruzioni di corrente non meglio identificate.

Durante questa fase gli attaccanti hanno sfruttato accessi ai sistemi già presenti e hanno riutilizzato vecchi materiali e notizie per ingrandire la portata delle loro azioni.

La seconda fase, più strutturata, è cominciata a partire da metà-fine ottobre. In questo periodo il numero di gruppi affiliati alla causa di Hamas è aumentato significativamente e in più occasioni gli attaccanti hanno collaborato tra loro per colpire la stessa organizzazione o base militare israeliana.

Durante questa fase sono aumentati anche gli attacchi di propaganda e disinformazione, arrivando a 10 campagne solo nelle ultime due settimane di ottobre.

Infine, a partire da fine novembre i cyberattaccanti hanno cominciato a prendere di mira tutti i Paesi che hanno manifestato il loro supporto a Israele. Il caso più eclatante è l’attacco ai PLC delle stazioni idriche statunitensi: il gruppo iraniano Cyb3rAvengers ha compromesso i PLC Unitronics, di manifattura israeliana, presenti in diversi centri idrici.

La propaganda dei gruppi iraniani

I cyberattaccanti iraniani non hanno impersonato solo figure israeliane, ma anche simboli e personaggi legati ad Hamas: di recente i gruppi iraniani hanno utilizzato il nome e il logo del dell’ala militare di Hamas per diffondere messaggi falsi e minacciare il personale delle forze di difesa isrealiane.

Nel corso dei mesi l’Iran ha fatto uso di campagne di messaggi e e-mail per potenziare gli effetti psicologici delle operazioni di propaganda. “I messaggi che appaiono sui telefoni o nelle caselle di posta elettronica delle persone hanno un impatto maggiore rispetto agli account falsi sui social media” ha spiegato Clint Watts, General Manager di Microsoft Threat Analysis Center.” L’Iran utilizza media conosciuti e occulti legati all’IRGC (Corpo delle guardie della rivoluzione islamica) per amplificare le campagne di propaganda e, a volte, esagerarne gli effetti”.

Pixabay

Gli obiettivi dei cyberattaccanti

Le operazioni dei cyberattaccanti iraniani mirano a destabilizzare Israele e a esacerbare le fratture politiche e sociali interne, come nel caso dei 240 ostaggi quando gli attaccanti diffondevano la notizia che si tratta di gruppi di attivisti che criticavano il governo israeliano.

Gran parte degli attacchi iraniani nascono da un desiderio di vendetta diretta: il gruppo Cyb3rAvengers ha affermato di aver preso di mira le infrastrutture israeliane per l’elettricità, l’acqua e il carburante come vendicarsi del fatto che Israele ha dichiarato che avrebbe tagliato l’elettricità, l’acqua e il carburante a Gaza e altrove.

Le operazioni dei gruppi iraniani hanno come obiettivo anche quello di intimidire la popolazione israeliana, in particolare le famiglie dei soldati delle forze di difesa, e gli alleati. Infine, le campagne mirano a ridurre o indebolire gli aiuti internazionali per Israele sottolineando le colpe del Paese e le conseguenze su Gaza.

Il team di Microsoft ritiene che gli attacchi iraniani continueranno a progredire e diventare sempre più mirati, collaborativi e distruttivi. Le campagne saranno una minaccia ancora maggiore nel 2024 e renderanno il panorama delle minacce più complesso.

Condividi l’articolo


Articoli correlati

Altro in questa categoria


https://www.securityinfo.it/2024/02/09/levoluzione-dei-cyberattacchi-iraniani-contro-israele/?utm_source=rss&utm_medium=rss&utm_campaign=levoluzione-dei-cyberattacchi-iraniani-contro-israele


Protecting the workforce amidst geopolitical threats

In December, International SOS released its annual 2024 Risk Outlook Report, created to identify top concerns that organizations are expected to face in the coming year and how to mitigate them to protect a workforce, meet duty of care needs and ensure business continuity. According to this year’s report, geopolitical tensions and instability are expected to be the second highest security risk with 74% of respondents believing their organization will be impacted in some way. On top of this, organizations have also reported higher levels of unpreparedness for security concerns caused by geopolitical tensions, which encompass a broad spectrum of interconnected issues, from regional conflicts and political instabilities flowing to economic uncertainties and global power dynamics. Moreover, according to Statista, 2024 will witness national level elections in 60 countries — involving approximately a quarter of the world’s population.

Another catalyst that will drive geopolitical challenges for organizations in 2024 will be climate-related crises. Persistent climate-related crises are expected to drive primary, secondary and tertiary issues, including conflict, migration, price volatility of essential goods and their corresponding drivers of acute social and political division. In 2023, International SOS intelligence teams saw a significant rising trend in the number of climate-related alerts issued, with 80% more medical climate-related alerts and 30% more security climate-related alerts. These included a fourfold increase in climate-related special advisories, those that, due to their severity and immediacy, are considered a direct threat to life. Although climate-related threats are expected to continue to cause challenges for organizations in 2024, only half of Risk Outlook respondents say they have factored climate change into their health and security plans, emphasizing how vulnerable many organizations could be. 

Organizations must be attuned to these types of threats, recognizing their potential impact on employee safety and business operations, in addition to supply chain and other threats in a highly connected world. In 2024, geopolitical awareness will not just be a strategic advantage; it will be a fundamental necessity. The following strategies will help organizations mitigate the associated risks. 

Comprehensive risk assessments:

To ensure the safety of employees, organizations must conduct thorough risk assessments that extend beyond direct and immediate concerns to incorporate global factors. This proactive approach involves analyzing international relations, political stability and regional tensions to identify potential threats that may affect resilience. Comprehensive assessments also cover cybersecurity and physical security risks, allowing organizations to allocate resources for targeted risk mitigation strategically. By fortifying their security posture in response to identified vulnerabilities, organizations not only protect assets but also cultivate a culture of preparedness and adaptability among employees. Integrating geopolitical considerations, including climate change-related impacts and scenario planning, into risk assessments ensures a strategic approach to navigating the complexities of the interconnected world. Through a holistic approach, organizations can craft targeted strategies for mitigating risks and enhancing workplace safety.

Adaptive crisis management & emergency response plans:

In the current global landscape, organizations must adopt a proactive approach to effectively alter their response plans. Constant monitoring of the prevailing geopolitical, social and environmental factors is paramount to staying ahead of potential threats. Flexibility becomes a key component, necessitating regular reviews and updates to response strategies to align with the dynamic nature of risks. Embracing technology for real-time communication and coordination also enhances the responsiveness of emergency plans. Additionally, fostering a culture of continuous training and scenario-based simulations ensures that employees are well-prepared to navigate the unique challenges presented by the current climate. Exercising plans, performing thorough post-crisis reviews and constantly improving is critical to organizational resilience. But it must also be balanced and recognize that organizations are in a state of permacrisis, perpetually trying to manage their business as usual in addition to managing crises, often crises and major incidents that are occurring concurrently. Recognizing and structuring teams in light of the foreseeable risk of crisis fatigue, including the attendant mental health implications, remains a key factor to be addressed explicitly and systematically. 

Employee training and awareness programs:

Empowering employees with a thorough understanding of geopolitical threats is instrumental in fostering an organization’s resilience. In addition to the conventional measures stated above, organizations should invest in comprehensive training programs that provide in-depth knowledge and accessible resources for employees, including for under-represented minorities such as the LGBTQ+ members of an organization. These programs should cover not only the identification of potential risks but also provide insights into evacuation procedures and the effective utilization of safety resources. By ensuring that employees are well-informed and trained to navigate diverse scenarios, organizations establish a proactive line of defense against current and potential threats. Such training not only enhances the individual preparedness of employees but also contributes to creating collective responsiveness within the workforce.

Technological solutions for surveillance and communication:

Many organizations stand at the forefront of technological advancements, where the use of cutting-edge technologies becomes essential for effective monitoring and response to emerging threats. By integrating advanced surveillance systems and communication tools into their security infrastructure, organizations gain a real-time understanding of their surroundings and empower themselves with the agility required for swift decision-making and seamless response coordination. These sophisticated technologies go beyond conventional measures, offering a comprehensive and proactive approach to threat detection, communication and response.

Collaboration with global partners:

Organizations frequently extend their operations across borders, underscoring the need for strategic collaborations to effectively navigate the intricate web of geopolitical challenges on a global scale. Establishing and nurturing collaborative partnerships with international counterparts, local authorities and relevant agencies is paramount, as these partnerships facilitate the exchange of critical information and insights and foster a shared understanding of potential threats. By engaging in collaborative efforts, organizations can leverage the expertise and resources of various stakeholders, enhancing their collective capacity to anticipate, prepare for and respond to global challenges.

As security leaders continue to live through an ever-changing landscape of geopolitical threats, workplace safety will require a proactive and adaptive approach in 2024. Leaders in the workplace play a pivotal role in shaping the resilience of organizations and ensuring the safety and well-being of their most valuable asset — employees. By staying informed, embracing technology, fostering international collaboration and prioritizing duty of care, businesses can navigate these uncertainties and emerge stronger in the face of adversity.

https://www.securitymagazine.com/articles/100383-protecting-the-workforce-amidst-geopolitical-threats


The evolving disaster preparedness landscape: AI, ML and data modeling

In 1970, the Sanders Barotropic Tropical Cyclone Track Prediction Model (SANBAR) forever changed the world’s approach to natural disasters by introducing predictive modeling. In the 50 years since then, U.S. agencies like the National Oceanic and Atmospheric Administration and the National Hurricane Center have built on this work by creating and utilizing their own models to help inform and protect the public from extreme weather events. 

Fueled by the accessibility boom of machine learning (ML), artificial intelligence (AI) and advanced data modeling, local agencies and private enterprises are empowered to proactively model critical events in a way that was previously cost-restricted to federal agencies or large universities. As a result, the field of disaster preparedness and response is undergoing yet another transformative shift. 

As advancements and acceptance of AI and ML reshape industries all over the world, disaster management should be no exception. To keep up with the growing threat of natural disasters, organizations will capitalize on these technologies — shifting from reactive to proactive strategies that are complementary to the crucial role played by experienced emergency managers.

Predictive modeling and critical event management

AI and ML have revolutionized disaster preparedness through predictive modeling. With the democratization of these technologies, diverse organizations are creating new and innovative models to better anticipate, manage and respond to catastrophic events.

ML-powered predictive modeling has elevated critical event management by introducing a more comprehensive analysis of potential scenarios. Traditionally, disaster preparedness focused on limited sets of variables, yet with ML, a broader spectrum of factors can be assessed and considered. The more comprehensive and accurate the data that is fed into such technologies, the more effective they become in predicting and managing critical events. Variables such as traffic control points, accessible shelters and other dynamic elements are now available for integration into predictive models, thus providing a more nuanced and realistic picture of disaster scenarios and appropriate responses.

Predictive models have recently become more dynamic and adaptable than ever. The integration of AI into existing ML technologies enables sophisticated and accurate risk assessments. By analyzing historical data, current environmental conditions and real-time information feeds, predictive models can generate precise risk profiles for specific regions which, as disasters evolve, allow for agile emergency response.

Predictive models only play a supporting role for emergency response

AI- and ML-powered predictive models give organizations powerful insights about both future and ongoing disaster events. They facilitate faster decision-making and real-time orchestration of emergency responses with the most up-to-date information. However, this is only the first step in properly approaching these scenarios. Knowing how to respond and executing said response are two different ball games. 

Predictive modeling enables emergency managers and security professionals to explore various scenarios, assess potential risks and optimize response strategies in a controlled digital environment. That said, the criticality of emergency and security professionals becomes self-evident when shifting from digital simulations to the dynamic, more chaotic physical world. Despite its advantages, simulations inherently lack the nuance and contextual understanding that human experience affords. Real-world emergencies often involve complex and unforeseen variables that may not be adequately captured by even the most advanced AI models.

Experienced emergency managers and security professionals bring a wealth of knowledge, intuition, and adaptability that complements the capabilities of AI and ML. They possess the ability to make nuanced judgments, consider unpredicted aspects of affected populations and navigate the intricacies of communities and their cultures during times of crisis. Human judgment, empathy and the ability to make split-second decisions in high-stress situations are all invaluable skills that emergency personnel bring to the table, which AI cannot offer.

Conclusion

The integration of machine learning and artificial intelligence into predictive data modeling allows more organizations than ever to shift from reactive to proactive strategies and empowers them to better anticipate, plan for and respond to critical events. While AI and ML play a crucial supporting role, experienced emergency and security managers remain indispensable in translating digital simulations into effective physical responses. The collaboration between predictive modeling and human expertise is key to building resilient and adaptive disaster management systems for the challenges of the future.

https://www.securitymagazine.com/articles/100384-the-evolving-disaster-preparedness-landscape-ai-ml-and-data-modeling


Selecting the right mobile incident management solution

A security threat can happen anywhere and at any time. That means flexible security solutions are a must when trying to keep people and operations safe. However, many organizations limit their ability to respond to a threat by selecting solutions that keep security personnel tied to a desk or restrict access, which narrows a tool’s usefulness. Mobile security solutions offer the ability to manage situations from anywhere, but in a crowded marketplace, it can be difficult to understand what to look for to address an organization’s needs.  

A mobile solution requires an app team members can access from their mobile devices. This is the first step in expanding access broadening an organization’s ability to respond to incidents from anywhere. With a mobile app, people do not need to get to their desktops to start reporting the incident to others, which can save crucial seconds or in some cases minutes in getting the word out and sending help to those in need. When an emergency occurs, every moment counts, so the quicker organizations can respond the better chance they have of mitigating the impact of an event. 

Having an app is one thing, but what that app can do is another. Too often, organizations select single-use solutions that address specific needs. While it is good to be aware of the challenges an organization may encounter, having a unique solution for each issue is rarely effective. Needing to activate multiple apps to complete specific tasks can be time-consuming and cumbersome. And the more apps an organization needs, the more likely it is someone forgets to activate one, which may put others at risk. The more an app can do, the more value it can bring to an organization’s security strategy by enabling them to alert, manage, and respond to incidents from a single interface. 

To do that, a mobile security solution needs to be flexible. That starts with being able to build custom messages for whatever kind of crisis an organization may face. Whether it’s an active shooter, severe weather, medical emergency, or some other crisis, having preloaded messages on a mobile app that are easy to send to others saves time and eliminates the need to come up with appropriate messaging on the fly. With a few simple taps, critical messages can be sent out. A mobile security solution should also give an organization the ability to segment messages to specific audiences. Some emergencies may require alerting an entire organization, while others may only require alerting specific teams, like security, or people in a specific area. Being able to send those messages as SMS text, push notifications, email and audio messages helps organizations deliver information in a way that is most convenient for the recipient while helping ensure that they are doing everything they can to get the message in front of everyone so they receive it quickly. 

True flexibility though comes when a mobile solution is also able to integrate with on-premises devices like speakers, digital signage, and desktop computers. Being able to leverage text, audio, and visual alerts that get sent directly to mobile devices and throughout a facility means clear, consistent emergency messages are being communicated to everyone so they can stop what they are doing and take steps to keep themselves safe. Intrusiveness is key, and the more an organization can leverage a solution to ensure messages can’t be ignored, the faster they can spur people to action. 

Once alerts have been sent, a mobile security solution should also empower stakeholders to actively manage an incident as it unfolds. This includes viewing real-time insights like responses from other members to understand who needs assistance and who is safe. It can also include the ability to access vital resources like floor plans to understand where an incident has occurred and how to best direct a response. Once an event has ended, a mobile security solution should also help organizations resume normal operations. Being able to send an “All Clear” message from a mobile app helps inform people that danger has passed the moment an issue has been resolved.

Of course, not everyone within an organization needs to be able to send emergency alerts or manage an incident, but everyone should have the ability to request help should they need it. Mobile security solutions that offer panic button capabilities can be especially valuable for organizations looking to provide individualized protection for their people. With a panic button on their phone, individuals can request help wherever they are. This can be particularly useful for large organizations that have sizable properties and parking lots that workers may need to access that otherwise do not have easily accessible safety resources. With the right tool, when a mobile panic button is activated, security teams can receive an alert with the individual’s name and location so they can send immediate help. The person who activated the panic button can connect directly with the security team via a phone call to speak with someone about the situation they are experiencing until help arrives. 

Organizations looking to invest in mobile security solutions need to have a clear vision of what issues they want to address. Mobile security solutions allow key stakeholders to go where they are needed, assess situations firsthand, and collaborate on a response with others while still being connected to others to stay on top of ongoing crisis events. Ultimately, a mobile security solution should make stakeholders’ lives easier and responses more efficient when incidents occur. 

https://www.securitymagazine.com/articles/100382-selecting-the-right-mobile-incident-management-solution