OpenAI’s Astra Crosses ‘Critical’ Cyber Threshold After Finding Zero-Days

The designation applies when a model can independently find and exploit zero-day vulnerabilities across many well-defended systems.

The post OpenAI’s Astra Crosses ‘Critical’ Cyber Threshold After Finding Zero-Days appeared first on SecurityWeek.

https://www.securityweek.com/openais-astra-becomes-first-model-to-cross-critical-cybersecurity-threshold/


Suno hopes to go legit with watermarks for AI-generated music

Going legit

While much of the visual media generated by AI has flown under the legal radar, the music industry is famously litigious. Suno is being sued by Universal and Sony for copyright infringement in the US, and a German court recently found the company was violating the country’s music licensing laws. Both cases could lead to hefty fines.

Suno is also in hot water after a hack in late 2025 that showed it scraped content from YouTube, Deezer, and others to train its models. Suno did not disclose the hack, which may have included the private information of millions of users. It’s being sued in Massachusetts over that.

None of that is a good look, so it’s no surprise Suno is looking for ways to change the conversation. The company is essentially positioning itself as a tool for musicians and personal projects, not as a way to generate unlimited slop for Spotify. Shulman stresses in the blog that Suno supports the artistic process, noting that AI technology “can’t replace the human experiences, emotions, and imperfections that make music meaningful.”

That, he claims, is why Suno already has rules designed to guard against misuse. For example, Suno doesn’t allow users to include specific artists or songs in their prompts, and it partners with companies like Musixmatch to ensure people don’t upload copyrighted content to use as a base for their generative compositions. Suno has also strengthened prohibitions against this kind of misuse in an update to its usage policy.

More changes are coming, too. Last year, Suno agreed to limit downloads in a settlement with Warner Music Group. Suno is still working out the specifics, but Shulman says most users won’t be affected. However, limits on downloads, along with watermarking tracks, will apparently help to limit “large-scale abuse.”

Whether these changes will save Suno from its legal woes remains to be seen.

https://arstechnica.com/ai/2026/08/suno-hopes-to-go-legit-with-watermarks-for-ai-generated-music/


Anthropic will design its own hardware to power Claude

There are a few reasons AI providers are doing this. First, much of the industry is heavily reliant on Nvidia for the hardware the companies’ models run on, and Nvidia’s continued leverage there is a potential strategic vulnerability, especially as AI companies operate in an environment where compute infrastructure is highly competitive as demand continues to outstrip current capacity.

Second, designing chips for specific models and vice versa could lead to better performance. So, for example, if OpenAI can reap the rewards of that vertical integration, you can bet Anthropic and other frontier model providers will want that advantage as well.

To that point, Anthropic says its teams will co-design new hardware and models side by side. It has co-designed certain hardware with partners before, but the plan is now to bring more silicon expertise inside Anthropic itself.

Anthropic may also hope this could help its frontier models get some extra competitive edge as software developers and other users begin exploring running cheaper, smaller, or open-weight models on their own hardware or on edge devices.

However, since Anthropic is still in the process of hiring key team members, it will be some time before either the company or its users see any benefits.

https://arstechnica.com/ai/2026/08/anthropic-confirms-plans-to-build-an-in-house-silicon-team/


Large genome models used to design new viruses

The same, yet different

In some ways, these designed viruses were quite similar to the original ΦX174, but in other ways they were quite distinct.

For the “the same” perspective, the most effective viruses in the group of 285 tended to look a lot like the original. The overall fraction of viable viruses was only 16 out of the 285 outputs tested (5.6 percent). But if you looked only at the outputs that were most similar to the original ΦX174 (those with 98 percent sequence similarity and up), viability rose to 46 percent. So, if you don’t look a lot like a normal ΦX174, chances are good that you’re not going to work as a virus at all.

Most of the viable viruses had the same set of genes found in the original. None of them had even a single change in the stretch of DNA where the duplication of the virus’s genome starts.

All of that is in keeping with past studies that have shown that making even a single base change that alters just one amino acid in one of the proteins made from the virus’s genome had, on average, a 20 percent chance of inactivating the virus entirely. ΦX174 doesn’t just fear change; it’s typically murdered by it. Accordingly, the changes suggested by the AI produced a population of viable viruses that, on average, looked a lot like the original.

But, as individuals, the viruses were fairly distinct. One of them lost one of the viral proteins entirely, compensating for its loss with changes elsewhere in the genome. Another added an entirely new gene. Many had genes that were either longer or shorter than the original. One even replaced one of the ΦX174 genes with a gene from a very distantly related virus.

The researchers did an interesting analysis based on the idea that any one amino acid change had a 20 percent chance of inactivating the virus. Doing the math, they say that any viruses with less than 25 changes have only a 2.3 percent chance of being viable. Of the 300 or so viruses the AI output, five viruses fell in that range, and three of them were viable. At above 25 individual amino acid changes, the chances of producing a viable virus are essentially zero. Yet nearly a quarter of the AI-suggested viruses that had more than 25 changes were viable, including two that had over 50 amino acid alterations.

https://arstechnica.com/science/2026/08/large-genome-models-used-to-design-new-viruses/


US company’s AI lets Ukraine’s cheap kamikaze drones track targets on their own

Cost-effective AI for battlefield drones

Until now, the Ukrainian military has mainly relied on human operators to manually guide drones toward their targets, with the exception of mid- or long-range strike drones such as the $5,000 AI-powered “Hornet” drones developed by the California-based company Perennial Autonomy founded by former Google CEO Eric Schmidt. Those drones often fly far beyond the frontlines to target Russian oil refineries and energy infrastructure, factories and warehouses, or even ships in the Sea of Azov and the Black Sea.

But Auterion focused on creating AI-powered capabilities for the cheaper, shorter-range FPV drones that have become the most common weapons responsible for killing or wounding soldiers on the frontlines in Ukraine. The company developed a tightly integrated flight control system and terminal guidance system optimized to run on a Western-made Arm system-on-a-chip costing just $18.

“What we are doing is replacing the existing flight controller—which has no computer, no AI—with avionics that has a microprocessor unit, has AI on board, and can track into the target fully autonomously,” Meier told Ars.

Each of SkyFall’s Shrike drones equipped with such capability costs about $2,000, compared to the $400 Ukrainian drones that rely only on manual piloting, Meier wrote in a blog post.

By comparison, he described Western militaries as still purchasing “precision munitions at six or seven figures per shot (30–60 times this price), drones procured in batches of dozens, priced like exquisite aircraft, delivered on timelines measured in years.”

The 50,000 Shrike drones equipped with Auterion’s strike kit were funded by a $100 million contract backed by an officially unnamed European country. Reuters reported that Germany is the country funding the order, and Meier also disclosed that Auterion’s team based in Munich, Germany, is fulfilling the order.

https://arstechnica.com/ai/2026/08/ukraines-drones-get-ai-upgrades-for-kamikaze-strikes-future-swarm-attacks/


An AI-supervised remote exam went so badly that 58,000 students must retake it

Earlier this summer, nearly 160,000 applicants took the entrance exam for UNAM, Mexico’s largest university. For the first time, they did it completely remotely, using a “lockdown” browser and AI-powered webcam proctoring software, over several weeks from late May through early June.

It was a disaster.

When exam results came in, they bore little resemblance to past results, especially at the top. Between 2021 and 2025, 3.5 percent of test takers scored 100 or more on the 120-question UNAM test. This year, 16.3 percent did so.

The story was even worse at the highest of the high end. Between 2021 and 2025, 0.9 percent of test takers scored 110 or more; this year, 5.5 percent did so.

The surge in top scores led to accusations of widespread cheating, and UNAM appointed a commission of experts to investigate the situation.

The group was given the unwieldy name “la Comisión Técnica de Personas Expertas para la Revisión del Proceso de Selección de Ingreso a Licenciatura para el Ciclo Escolar 2026-2027/1,” and it has just submitted its recommendations. The commission believes that the best path forward, given all the concerns, is to administer a “control exam”—that is, applicants will have to sit for another test, and they will do so in person.

This control exam will apply not only to those who secured a spot at UNAM based on this year’s test but also to everyone who would have been admitted based on minimum successful scores in their program of study since 2021. About 58,000 people could be affected, and places at UNAM will now depend on the results of the new test. (Details on the control exam should appear soon; classes are currently scheduled to begin on August 10, so everything will have to move quickly unless the school decides to delay classes.)

According to Gaceta UNAM, the school’s official news publication, the university rector has apologized to honest applicants, since they will now have to prepare for and take the test again despite doing nothing wrong. Still, the control exam is “necessary to give certainty and guarantee equity in access,” the rector added.

https://arstechnica.com/culture/2026/08/an-ai-supervised-remote-exam-went-so-badly-that-58000-students-must-retake-it/


Four Days to Learn, Create, and Get Inspired at Photoshop World 2026

Sometimes the best thing you can do for your creativity is shake up your routine, learn something new, and spend some time around other people who love creating as much as you do.

That’s what Photoshop World 2026, sponsored by Adobe, is all about.

Join us online September 14–17 for four days packed with creative education, practical techniques, new ideas, and an incredible community of photographers, designers, retouchers, and digital creatives.

With more than 45 interactive sessions, there’s plenty to explore, whether you spend your days in Photoshop, Lightroom, behind a camera, experimenting with AI, or moving between all of them.

Real-World Creatives. Real-World Techniques.

Photoshop World instructors aren’t teaching from a script. They’re working professionals who use these tools to solve creative problems every day.

We’re bringing together an incredible group of photographers, retouchers, designers, educators, and creative professionals ready to share the techniques and workflows they’ve developed through years of real-world experience.

That means practical instruction you can actually use, from smarter Photoshop and Lightroom workflows to retouching, compositing, photography, AI-powered tools, creative effects, and much more.

You might come to Photoshop World looking for one particular skill and leave with an idea from a completely different session that changes the way you approach your work. That’s part of the fun.

Come for the Classes. Stay for Everything Else.

There’s a lot more happening at Photoshop World than what’s on the class schedule.

Our Pre-Conference Meet-Up gives you a chance to say hello, meet fellow attendees, and start making connections before the full conference begins.

Then we’ll get those creative wheels turning with our Opening Keynote presented by Adobe before heading into full days of classes and special events.

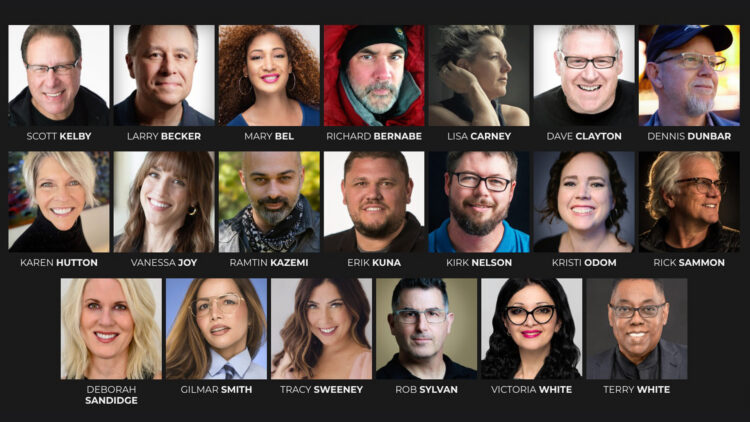
You’ll also be able to kick back and enjoy the PSW Film Fest, get inspired during An Evening With…, and laugh along with Late Night with Larry Becker & Guests, our newest event featuring a live late-night talk show experience with some familiar Photoshop World faces.

And then there are the Guru Awards, one of our favorite Photoshop World traditions. This is your chance to showcase your own work and let us celebrate the creativity happening within our community. Take a look at last year’s winners and finalists here.

An Online Conference That Actually Feels Connected

One of our favorite parts of the online Photoshop World experience is just how easy it is to be part of the conversation. Our chat windows stay open throughout the day, giving you a place to ask questions, talk about what you’re learning, meet fellow attendees, and connect with our friendly event staff.

Our sponsors get involved, too. Keep an eye out for chats, meetings, bonus sessions, and opportunities to connect directly with companies that can help answer questions about the tools and services you use.

You don’t have to travel anywhere to meet a whole bunch of people who understand why you can happily spend an hour debating the best way to make a selection in Photoshop. We think that’s pretty great.

A Full Year to Keep Learning

Of course, four days still isn’t enough time to see everything. That’s why every session is recorded and available to replay for a full year. Watch live when you can, catch anything you missed later, and return to your favorite sessions whenever you need a refresher or a little creative inspiration.

Early Birds Save $200

Registration for Photoshop World 2026 is currently just $299, saving you $200 off the regular $499 price. But don’t wait too long. Early Bird pricing ends August 14, 2026, at 11:59 PM EDT.

If you’re ready for four days of learning, creating, connecting, and filling up that creative tank, we’d love to have you join us!

[embedded content]

https://layersmagazine.com/photoshop-world-2026.html


As Reddit stock falls, CEO questions value of Google’s AI Overviews

Like any company, Reddit reports quarterly earnings, and its CEO, Steve Huffman, addresses investors during those reports. It’s not always about just sharing numbers, though: This quarter, Huffman took the opportunity to voice concerns and criticisms about Google’s AI Overviews feature, which automatically summarizes search results on most user queries.

First, there was a letter to investors, wherein Huffman spun his narrative about Reddit’s value proposition and general strategic direction amid the proliferation of AI tools.

He wrote:

As the internet becomes flooded with synthetic content, people are craving real human perspective. We are the antidote to an automated web. AI compresses the internet into summaries. Reddit delivers the opposite: deep discussions, passionate debates, and lived experiences. People don’t want a summary of Reddit; they want Reddit.

The letter also said:

As AI makes information more abundant, the challenge is no longer finding content—it’s finding context, personal opinion, and first-hand accounts. Everything online feels flat, polished, generated, or sponsored, so consumers are overwhelmed and increasingly skeptical. We’ve never had more information, but we’ve never trusted it less.

And then, in comments around the earnings report, he added:

What we see is, 10 blue links has driven tremendous value and growth to the broader ecosystem… from where we sit, AI Overviews has yet to make a similar level of positive impact, and I think that’s consistent across the broader landscape, right? As businesses, publishers, retailers, we’re still looking for that win-win.

To add context to these statements, Reddit has long had a relatively lucrative ($60 million) licensing deal with Google, but Reddit is considering ending that deal, according to a Wall Street Journal report from earlier this month. The report also said that several prominent publishers are considering similarly cutting ties with Google, including The Economist, Reuters, Politico, and USA Today. (Reddit also has a deal with OpenAI.)

Last year, a study by Pew Research that looked at data from 900 US adults concluded that Google’s AI Overviews cut referrals to sites like those by almost half, compared to the “10 blue links” approach that Huffman referred to. It’s important to note, though, that Google has long diverged from just “10 blue links” in other ways even before AI Overviews entered the scene.

https://arstechnica.com/ai/2026/08/reddit-ceo-on-ai-overviews-were-still-looking-for-that-win-win/


Google AI Uncovers 13-Year-Old Chrome Flaw Amid Record Patching Pace

Google this week confirmed that this year’s surge in Chrome vulnerabilities has been driven by the use of AI.

The increase in Chrome bugs started in April and has continued throughout July, with the latest browser release containing 370 security fixes and bringing the total number of bugs patched this year to over 1,800.

Google patched 1,072 security defects with the Chrome 149 and 150 releases, “surpassing the total number of security bugs fixed across the prior 23 milestones combined.”

This was the result of using an agent harness that leverages Gemini to identify security flaws across Chrome’s codebase with increased efficiency, the internet giant says.

What validated the AI-powered vulnerability detection, Google says, was the discovery of a sandbox escape that lurked in the browser for 13 years.

Tracked as CVE-2026-3545 (CVSS score of 9.8) and patched in early May in Chrome 145, the issue could have allowed “a compromised renderer to trick the browser into reading local files,” it says.

Advertisement. Scroll to continue reading.

Described as an insufficient data validation in Navigation, the vulnerability could have been exploited via crafted HTML pages to perform a sandbox escape.

The Chrome Security team started using LLMs in 2023, but it was the agent harness built in early 2026 that has been essential to finding and patching more flaws in the browser.

It has support for model interoperability, was trained on a knowledge base of previously identified CVEs and of Chrome’s entire Git history, leverages developer-supplied SECURITY.md files that are consumed by a “critic” agent, and can run vulnerability-finding models over the codebase multiple times.

“We’ve built all of this with safety in mind, and have put in place guardrails to mitigate the risk of AI behaving unexpectedly. Our AI analyzes source code strictly at rest, operating on locked-down machines that lack general internet access,” Google explains.

While also relying on AI for bug validation, triaging, and patch generation, the internet giant continues to use other security testing infrastructure for bug detection, and welcomes researchers submitting vulnerability reports through its VRP.

“At this point, we have LLMs generating candidate fixes for most vulnerabilities, dramatically increasing the rate of security fixes in recent Chrome releases,” Google says.

Additionally, the company is relying on AI to prevent new security bugs by identifying and eliminating them “as close to code submit-time as possible” and by neutralizing issues in the tree that could impact code deemed safe in isolation.

Reducing the patch gap and eliminating memory safety bugs

To reduce the patch gap, Google is also piloting a twice-a-week Chrome security release cadence, which will complement the two-week schedule for major Chrome releases that was announced in March.

“We are working on automating the generation of release notes and CVE descriptions from security bug fixes to eliminate manual bottlenecks and shorten the window between vulnerability discovery and public disclosure,” the company says.

Google is also working on ensuring that Chrome is always up to date on users’ machines, through dynamic patching, which eliminates the need to restart the browser when applying updates, seamless session restoration, and restarts while in a windowless state (the application runs in the background while all windows are closed).

Additionally, Google is working on eliminating entire classes of security issues from Chrome, such as memory safety flaws. For that, it is hardening the runtime environment to squash C++ bugs, and is transitioning to memory-safe languages.

In this regard, it is expanding MiraclePtr to more libraries and deploying MiracleObject to the GPU main thread to neutralize use-after-free defects. In addition, it’s taking a ‘spanification’ effort to eliminate out-of-bounds weaknesses, and is integrating memory allocation protections to block integer overflows.

In the long term, Google is transitioning Chrome’s codebase to memory-safe languages like Rust, through building a centralized Rust SDK, deploying Rust to replace most flawed code segments, and writing new modular components in Rust.

“In addition to Rust, we are also exploring options like implementing the browser’s top-level user interface using HTML, CSS, and TypeScript to further reduce dependencies on traditional C++ frameworks,” Google notes.

According to the company, keeping the open source software ecosystem secure is another critical aspect of improving Chrome users’ protections. It has been using automated vulnerability scanning pipelines to keep dependencies patched and will move all Chrome third-party dependencies onto automated update pipelines.

“Every bug found and fixed is one less foothold for an attacker. But discovering and fixing a bug is only half the battle — we must also ship the fix and apply the update for users faster than adversaries can exploit the bug, and invest in projects that mitigate or eliminate classes of bugs through accelerated release cadences, dynamic patching, and opportune restarts, we are driving toward a browser that is continuously protected without disrupting the user,” Google notes.

Related: Critical Flaw Led to Azure Cosmos DB Pwnage

Related: Timeless Compliance: Why Better Questions Beat Bigger Frameworks

Related: Microsoft Unveils MAI-Cyber-1-Flash, Its First Cybersecurity AI Model

Related: Anthropic’s Opus 5 Nears Mythos 5 on Finding Bugs, but Falls Short on Exploits

https://www.securityweek.com/googles-ai-agent-uncovers-13-year-old-chrome-flaw-amid-record-patching-pace/

EU to Crack Down on AI Deepfakes, Illicit Imagery and Hacking With New Team in Brussels

The European Union rolled out a new team on Friday to rein in AI companies across the world, in one of the most aggressive regulations the high-tech sector has so far faced as fears rise over the risks the rapidly advancing technology poses to people, politics and prosperity.

Brussels aims to track the use of AI models for violations of its new regulations, like the publishing of sexually explicit material, fake photos and videos, and cyber threats to public infrastructure. When the bloc’s AI Act comes into force on Sunday, AI companies will be required to make clear to consumers with labels or digital watermarks that chatbots or imagery are generated with AI.

“As enforcement begins, we are taking an important step towards AI that people and businesses can understand and trust, and whose benefits are shared widely across our society,” said Henna Virkkunen, the EU chief for tech sovereignty, on Friday.

The European Commission said in a statement that new regulations also include “systemic risks” posed by AI like “chemical, biological, radiological and nuclear incidents, loss of control, cyber offense, harmful manipulation and threats to fundamental rights.”

The team is the latest move in the 27-nation EU’s “tech sovereignty” strategy that welds landmark digital regulations with economic ambition that has seen over the past week billions of euros in fines on Big Tech companies as well as record investment in AI infrastructure inside the bloc.

The rollout comes on the heels of shocking AI safety failures that rattled the nascent industry. Political leaders worldwide are now weighing control of the technology with market leadership.

Advertisement. Scroll to continue reading.

Anthropic said its artificial intelligence models hacked into three other organizations during testing, just days after ChatGPT maker OpenAI raised concerns over AI controls after it disclosed its rogue models hacked another company.

The EU is now expanding its AI Office in Brussels with an additional 38 people who will begin monitoring AI companies, from the new firms to the American and Chinese tech titans like OpenAI and DeepSeek.

Those companies must “document certain information,” said the European Commission, the bloc’s tech enforcer, which reserves the right to interview AI company staff during investigations. It has also launched a Whistleblower Tool for tech workers and a Compliance Tool for tech users to confidentially alert authorities to illegal conduct.

If models or other products break the EU’s sector regulations, called the AI Act, Brussels can fine the firms or cut off their access to the EU market. Recent gigantic antitrust fines on U.S. tech companies have irked U.S. President Donald Trump.

The EU now clearly sees systemic vulnerability in its deep reliance on American software companies like Amazon, Google and Microsoft as well as imports of Chinese industrial goods and critical minerals. While it is seeking protections from AI, it is also keen to catch up in the AI arms race, where it is a distant third behind the U.S. and China.

More broadly, the EU is seeking more independence from both Washington and Beijing by reinvigorating specific domestic industries like manufacturing and defense and forging new trade deals from Brazil to Australia to meet the global rise in economic nationalism spearheaded by Trump.

https://www.securityweek.com/eu-to-crack-down-on-ai-deepfakes-illicit-imagery-and-hacking-with-new-team-in-brussels/