DeepSeek tests “sparse attention” to slash AI processing costs
The attention bottleneck

In AI, “attention” is a term for a software technique that determines which words in a text are most relevant to understanding each other. Those relationships map out context, and context builds meaning in language. For example, in the sentence “The bank raised interest rates,” attention helps the model establish that “bank” relates to “interest rates” in a financial context, not a riverbank context. Through attention, conceptual relationships become quantified as numbers stored in a neural network. Attention also governs how AI language models choose what information “matters most” when generating each word of their response.

Calculating context with a machine is tricky, and it wasn’t practical at scale until chips like GPUs that can calculate these relationships in parallel reached a certain level of capability. Even so, the original Transformer architecture from 2017 checked the relationship of each word in a prompt with every other word in a kind of brute force way. So if you fed 1,000 words of a prompt into the AI model, it resulted in 1,000 x 1,000 comparisons, or 1 million relationships to compute. With 10,000 words, that becomes 100 million relationships. The cost grows quadratically, which creates a fundamental bottleneck for processing long conversations.

Although it’s likely that OpenAI uses some sparse attention techniques in GPT-5, long conversations still suffer performance penalties. Every time you submit a new response to ChatGPT, the AI model at its core processes context comparisons for the entire conversation history all over again.

Of course, the researchers behind the original Transformer model designed it for machine translation with relatively short sequences (maybe a few hundred tokens, which are chunks of data that represent words), where quadratic attention was manageable. It’s when people started scaling to thousands or tens of thousands of tokens that the quadratic cost became prohibitive.

https://arstechnica.com/ai/2025/09/deepseek-tests-sparse-attention-to-slash-ai-processing-costs/



ChatGPT’s new branching feature is a good reminder that AI chatbots aren’t people

On Thursday, OpenAI announced that ChatGPT users can now branch conversations into multiple parallel threads, serving as a useful reminder that AI chatbots aren’t people with fixed viewpoints but rather malleable tools you can rewind and redirect. The company released the feature for all logged-in web users following years of user requests for the capability.

The feature works by letting users hover over any message in a ChatGPT conversation, click “More actions,” and select “Branch in new chat.” This creates a new conversation thread that includes all the conversation history up to that specific point, while preserving the original conversation intact.

Think of it almost like creating a new copy of a “document” to edit while keeping the original version safe—except that “document” is an ongoing AI conversation with all its accumulated context. For example, a marketing team brainstorming ad copy can now create separate branches to test a formal tone, a humorous approach, or an entirely different strategy—all stemming from the same initial setup.

The feature addresses a longstanding limitation in the AI model where ChatGPT users who wanted to try different approaches had to either overwrite their existing conversation after a certain point by changing a previous prompt or start completely fresh. Branching allows exploring what-if scenarios easily—and unlike in a human conversation, you can try multiple different approaches.

A 2024 study conducted by researchers from Tsinghua University and Beijing Institute of Technology suggested that linear dialogue interfaces for LLMs poorly serve scenarios involving “multiple layers, and many subtasks—such as brainstorming, structured knowledge learning, and large project analysis.” The study found that linear interaction forces users to “repeatedly compare, modify, and copy previous content,” increasing cognitive load and reducing efficiency.

Some software developers have already responded positively to the update, with some comparing the feature to Git, the version control system that lets programmers create separate branches of code to test changes without affecting the main codebase. The comparison makes sense: Both allow you to experiment with different approaches while preserving your original work.

https://arstechnica.com/ai/2025/09/chatgpts-new-branching-feature-is-a-good-reminder-that-ai-chatbots-arent-people/


The number of mis-issued 1.1.1.1 certificates grows. Here’s the latest.

Cloudflare on Thursday acknowledged this failure, writing:

We failed three times. The first time because 1.1.1.1 is an IP certificate and our system failed to alert on these. The second time because even if we were to receive certificate issuance alerts, as any of our customers can, we did not implement sufficient filtering. With the sheer number of names and issuances we manage it has not been possible for us to keep up with manual reviews. Finally, because of this noisy monitoring, we did not enable alerting for all of our domains. We are addressing all three shortcomings.

Ultimately, the fault lies with Fina; however, given the fragility of the TLS PKI, it’s incumbent on all stakeholders to ensure system requirements are being met.

And what about Microsoft? Is it at fault, too?

There’s some controversy on this point, as I quickly learned on Wednesday from social media and Ars reader comments. Critics of Microsoft’s handling of this case say that, among other things, its responsibility for ensuring the security of its Root Certificate Program includes checking the transparency logs. Had it done so, critics said, the company would have found that Fina had never issued certificates for 1.1.1.1 and looked further into the matter.

Additionally, at least some of the certificates had non-compliant encoding and listed domain names with non-existent top-level domains. This certificate, for example, lists ssltest5 as its common name.

Instead, like the rest of the world, Microsoft learned of the certificates from an online discussion forum.

Some TLS experts I spoke to said it’s not within the scope of a root program to do continuous monitoring for these types of problems.

In any event, Microsoft said it’s in the process of making all certificates part of a disallow list.

Microsoft has also faced long-standing criticism that it’s too lenient in the requirements it imposes on CAs included in its Root Certificate Program. In fact, Microsoft and one other entity, the EU Trust Service, are the only ones that, by default, trust Fina. Google, Apple, and Mozilla don’t.

“The story here is less the 1.1.1.1 certificate and more why Microsoft trusts this carelessly operated CA,” Filippo Valsorda, a Web/PKI expert, said in an interview.

I asked Microsoft about all of this and have yet to receive a response.

https://arstechnica.com/information-technology/2025/09/the-number-of-mis-issued-1-1-1-1-certificates-grows-heres-the-latest/


Microsoft open-sources Bill Gates’ 6502 BASIC from 1978

On Wednesday, Microsoft released the complete source code for Microsoft BASIC for 6502 Version 1.1, the 1978 interpreter that powered the Commodore PET, VIC-20, Commodore 64, and Apple II through custom adaptations. The company posted 6,955 lines of assembly language code to GitHub under an MIT license, allowing anyone to freely use, modify, and distribute the code that helped launch the personal computer revolution.

“Rick Weiland and I (Bill Gates) wrote the 6502 BASIC,” Gates commented on the Page Table blog in 2010. “I put the WAIT command in.”

For millions of people in the late 1970s and early 1980s, variations of Microsoft’s BASIC interpreter provided their first experience with programming. Users could type simple commands like “10 PRINT ‘HELLO'” and “20 GOTO 10” to create an endless loop of text on their screens, for example—often their first taste of controlling a computer directly. The interpreter translated these human-readable commands into instructions that the processor could execute, one line at a time.

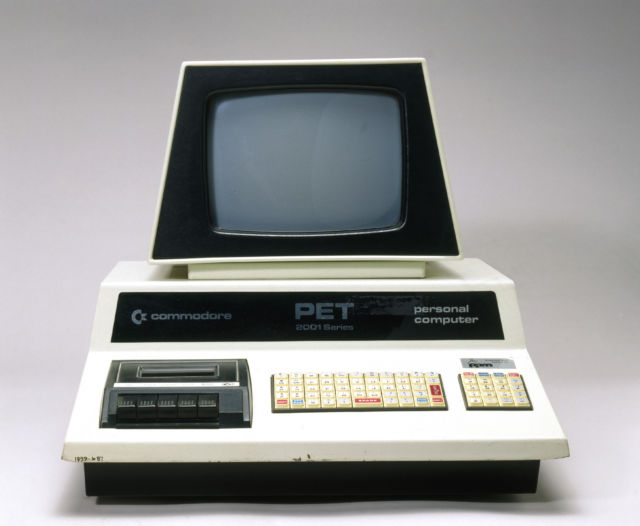
The Commodore PET (Personal Electronic Transactor) was released in January 1977 and used the MOS 6502 and ran a variation of Microsoft BASIC. Credit: SSPL/Getty Images

At just 6,955 lines of assembly language—Microsoft’s low-level 6502 code talked almost directly to the processor. Microsoft’s BASIC squeezed remarkable functionality into minimal memory, a key achievement when RAM cost hundreds of dollars per kilobyte.

In the early personal computer space, cost was king. The MOS 6502 processor that ran this BASIC cost about $25, while competitors charged $200 for similar chips. Designer Chuck Peddle created the 6502 specifically to bring computing to the masses, and manufacturers built variations of the chip into the Atari 2600, Nintendo Entertainment System, and millions of Commodore computers.

The deal that got away

In 1977, Commodore licensed Microsoft’s 6502 BASIC for a flat fee of $25,000. Jack Tramiel’s company got perpetual rights to ship the software on unlimited machines—no royalties, no per-unit fees. While $25,000 seemed substantial then, Commodore went on to sell millions of computers with Microsoft BASIC inside. Had Microsoft negotiated a per-unit licensing fee like they did with later products, the deal could have generated tens of millions in revenue.

The version Microsoft released—labeled 1.1—contains bug fixes that Commodore engineer John Feagans and Gates jointly implemented in 1978 when Feagans traveled to Microsoft’s Bellevue, Washington, offices. The code includes memory management improvements (called “garbage collection” in programming terms) and shipped as “BASIC V2” on the Commodore PET.

https://arstechnica.com/gadgets/2025/09/microsoft-open-sources-bill-gates-6502-basic-from-1978/


New AI model turns photos into explorable 3D worlds, with caveats

Training with automated data pipeline

Voyager builds on Tencent’s earlier HunyuanWorld 1.0, released in July. Voyager is also part of Tencent’s broader “Hunyuan” ecosystem, which includes the Hunyuan3D-2 model for text-to-3D generation and the previously covered HunyuanVideo for video synthesis.

To train Voyager, researchers developed software that automatically analyzes existing videos to process camera movements and calculate depth for every frame—eliminating the need for humans to manually label thousands of hours of footage. The system processed over 100,000 video clips from both real-world recordings and the aforementioned Unreal Engine renders.

A diagram of the Voyager world creation pipeline.
A diagram of the Voyager world creation pipeline. Credit: Tencent

The model demands serious computing power to run, requiring at least 60GB of GPU memory for 540p resolution, though Tencent recommends 80GB for better results. Tencent published the model weights on Hugging Face and included code that works with both single and multi-GPU setups.

The model comes with notable licensing restrictions. Like other Hunyuan models from Tencent, the license prohibits usage in the European Union, the United Kingdom, and South Korea. Additionally, commercial deployments serving over 100 million monthly active users require separate licensing from Tencent.

On the WorldScore benchmark developed by Stanford University researchers, Voyager reportedly achieved the highest overall score of 77.62, compared to 72.69 for WonderWorld and 62.15 for CogVideoX-I2V. The model reportedly excelled in object control (66.92), style consistency (84.89), and subjective quality (71.09), though it placed second in camera control (85.95) behind WonderWorld’s 92.98. WorldScore evaluates world generation approaches across multiple criteria, including 3D consistency and content alignment.

While these self-reported benchmark results seem promising, wider deployment still faces challenges due to the computational muscle involved. For developers needing faster processing, the system supports parallel inference across multiple GPUs using the xDiT framework. Running on eight GPUs delivers processing speeds 6.69 times faster than single-GPU setups.

Given the processing power required and the limitations in generating long, coherent “worlds,” it may be a while before we see real-time interactive experiences using a similar technique. But as we’ve seen so far with experiments like Google’s Genie, we’re potentially witnessing very early steps into a new interactive, generative art form.

https://arstechnica.com/ai/2025/09/new-ai-model-turns-photos-into-explorable-3d-worlds-with-caveats/


Mis-issued certificates for 1.1.1.1 DNS service pose a threat to the Internet

The certificates are a key part of the Transport Layer Protocol. They bind a specific domain to a public key. The certificate authority posesses the private key certifying that the certificate is valid. Anyone in possession of a TLS certificate can cryptographically impersonate the domain for which it was issued.

The holder of the 1.1.1.1 certificates could potentially use them in active adversary-in-the-middle attacks that intercept communications passing between end users and the Cloudflare DNS service, Ryan Hurst, CEO of Peculiar Ventures and a TLS and public key infrastructure expert, told Ars.

“Doing so would require a BGP hijack to trick your host to think your [rogue] 1.1.1.1 was the one I should connect to,” he explained. BGP is short for Border Gateway Protocol, a specification used to link regional networks scattered around the world, known as Autonomous Systems, to each other. By manipulating the system through false notices, attackers regularly take control of legitimate IP addresses, including those belonging to telecoms, banks, and Internet services.

As several Ars commenters have noted, there are likely many other ways an attacker could exploit the certificates to mount an adversary-in-the-middle attack.

From there, attackers with possession of the 1.1.1.1 certificates could decrypt, view, and tamper with traffic from the Cloudflare DNS service, Hurst said. He added that Cloudflare’s WARP VPN service may also be similarly affected.

Wednesday’s discovery exposes key failures of the public key infrastructure that’s responsible for ensuring trust of the entire Internet. They are the only thing ensuring that gmail.com, bankofamerica.com, irs.gov, and any other sensitive website is controlled by the entity claiming ownership.

Given the pivotal role of certificates, CAs are required to provide the IP addresses they used to verify that a party applying for a certificate controls the address they want covered. None of the three certificates provides that information. The incident also reflects poorly on Microsoft for failing to catch the mis-issued certificate and allowing Windows to trust it for such a long period of time.

Also at partial fault are Cloudflare and the PKI stakeholders at large, since all issued certificates are published to a publicly available transparency log. The purpose of the log is to quickly identify mis-issued certificates before they can be actively used. The public discovery of the certificates four months after they were issued suggests the transparency logs didn’t receive the attention they were intended to get.

Post updated to correct explanation of TLS certificates.

https://arstechnica.com/security/2025/09/mis-issued-certificates-for-1-1-1-1-dns-service-pose-a-threat-to-the-internet/


Zuckerberg’s AI hires disrupt Meta with swift exits and threats to leave

“While TBD Labs is still relatively new, we believe it has the greatest compute-per-researcher in the industry, and that will only increase,” Meta said.

Wang and other former Scale staffers have struggled with some of the idiosyncratic ways of working at Meta, according to someone familiar with his thinking, for example having to adjust to not having revenue goals as they once did as a startup.

Despite teething problems, some have celebrated the leadership shift, including the appointment of popular entrepreneur and venture capitalist Friedman as head of Products and Applied Research, the team tasked with integrating the models into Meta’s own apps.

The hiring of Zhao, a top technical expert, has also been regarded as a coup by some at Meta and in the industry, who feel he has the decisiveness to propel the company’s AI development.

The shake-up has partially sidelined other Meta leaders. Yann LeCun, Meta’s chief AI scientist, has remained in the role but is now reporting into Wang.

Ahmad Al-Dahle, who led Meta’s Llama and generative AI efforts earlier in the year, has not been named as head of any teams. Cox remains chief product officer, but Wang reports directly into Zuckerberg—cutting Cox out of overseeing generative AI, an area that was previously under his purview.

Meta said that Cox “remains heavily involved” in its broader AI efforts, including overseeing its recommendation systems.

Going forward, Meta is weighing potential cuts to the AI team, one person said. In a memo shared with managers last week, seen by the Financial Times, Meta said that it was “temporarily pausing hiring across all [Meta Superintelligence Labs] teams, with the exception of business critical roles.”

Wang’s staff would evaluate requested hires on a case-by-case basis, but the freeze “will allow leadership to thoughtfully plan our 2026 headcount growth as we work through our strategy,” the memo said.

© 2025 The Financial Times Ltd. All rights reserved. Not to be redistributed, copied, or modified in any way.

https://arstechnica.com/ai/2025/08/zuckerbergs-ai-hires-disrupt-meta-with-swift-exits-and-threats-to-leave/


Google warns that mass data theft hitting Salesloft AI agent has grown bigger

Google is advising users of the Salesloft Drift AI chat agent to consider all security tokens connected to the platform compromised following the discovery that unknown attackers used some of the credentials to access email from Google Workspace accounts.

In response, Google has revoked the tokens that were used in the breaches and disabled integration between the Salesloft Drift agent and all Workspace accounts as it investigates further. The company has also notified all affected account holders of the compromise.

Scope expanded

The discovery, reported Thursday in an advisory update, indicates that a Salesloft Drift breach it reported on Tuesday is broader than previously known. Prior to the update, members of the Google Threat Intelligence Group said the compromised tokens were limited to Salesloft Drift integrations with Salesforce. The compromise of the Workspace accounts prompted Google to change that assessment.

“Based on new information identified by GTIG, the scope of this compromise is not exclusive to the Salesforce integration with Salesloft Drift and impacts other integrations,” Thursday’s update stated. “We now advise all Salesloft Drift customers to treat any and all authentication tokens stored in or connected to the Drift platform as potentially compromised.”

On Thursday, Salesloft’s security guidance page made no reference to the new information and instead continued to indicate that the breach affected only Drift integrations with Salesforce. Company representatives didn’t immediately respond to an email seeking confirmation of the Google finding.

https://arstechnica.com/security/2025/08/google-warns-that-mass-data-theft-hitting-salesloft-ai-agent-has-grown-bigger/


High-severity vulnerability in Passwordstate credential manager. Patch now.

The maker of Passwordstate, an enterprise-grade password manager for storing companies’ most privileged credentials, is urging them to promptly install an update fixing a high-severity vulnerability that hackers can exploit to gain administrative access to their vaults.

The authentication bypass allows hackers to create a URL that accesses an emergency access page for Passwordstate. From there, an attacker could pivot to the administrative section of the password manager. A CVE identifier isn’t yet available.

Safeguarding enterprises’ most privileged credentials

Click Studios, the Australia-based maker of Passwordstate, says the credential manager is used by 29,000 customers and 370,000 security professionals. The product is designed to safeguard organizations’ most privileged and sensitive credentials. Among other things, it integrates into Active Directory, the service Windows network admins use to create, change, and modify user accounts. It can also be used for handling password resets, event auditing, and remote session logins.

On Thursday, Click Studios notified customers that it had released an update that patches two vulnerabilities.

The authentication bypass vulnerability is “associated with accessing the core Passwordstate Products’ Emergency Access page, by using a carefully crafted URL, which could allow access to the Passwordstate Administration section,” Click Studios said. The company said the severity level of the vulnerability was high.

https://arstechnica.com/security/2025/08/high-severity-vulnerability-in-passwordstate-credential-manager-patch-now/


Unpacking Passkeys Pwned: Possibly the most specious research in decades

Don’t believe everything you read—especially when it’s part of a marketing pitch designed to sell security services.

The latest example of the runaway hype that can come from such pitches is research published today by SquareX, a startup selling services for securing browsers and other client-side applications. It claims, without basis, to have found a “major passkey vulnerability” that undermines the lofty security promises made by Apple, Google, Microsoft, and thousands of other companies that have enthusiastically embraced passkeys.

Ahoy, face-palm ahead

“Passkeys Pwned,” the attack described in the research, was demonstrated earlier this month in a Defcon presentation. It relies on a malicious browser extension, installed in an earlier social engineering attack, that hijacks the process for creating a passkey for use on Gmail, Microsoft 365, or any of the other thousands of sites that now use the alternative form of authentication.

Behind the scenes, the extension allows a keypair to be created and binds it to the legitimate gmail.com domain, but the keypair is created by the malware and controlled by the attacker. With that, the adversary has access to cloud apps that organizations use for their most sensitive operations.

“This discovery breaks the myth that passkeys cannot be stolen, demonstrating that ‘passkey stealing’ is not only possible, but as trivial as traditional credential stealing,” SquareX researchers wrote in a draft version of Thursday’s research paper sent to me. “This serves as a wake up call that while passkeys appear more secure, much of this perception stems from a new technology that has not yet gone through decades of security research and trial by fire.”

https://arstechnica.com/security/2025/08/new-research-claiming-passkeys-can-be-stolen-is-pure-nonsense/