Qilin Ransomware Suspect Arrested in Japan, Extradited to Germany

An alleged member of the Qilin ransomware group was arrested in Japan and subsequently extradited to Germany.

The suspect, a 28-year-old Russian national, was detained in Osaka in May and was reportedly handed over to the German authorities on October 2.

Believed to be a core member of the ransomware gang, the individual was wanted in Germany for hacking into a logistics company in September 2024, encrypting data on its systems, and extorting it of over $160,000 in cryptocurrency.

Also known as Agenda, Qilin has been active since August 2022 and has become one of the most prolific ransomware-as-a-service (RaaS) operations, hitting hundreds of organizations worldwide and causing millions of dollars in damages.

In 2024, the group was blamed for hacking into pathology lab services provider Synnovis and causing disruptions at multiple London hospitals run by the National Health Service.

Last year, Qilin claimed responsibility for hacking beer giant Asahi Group. The incident caused operational disruptions and resulted in the personal information of roughly 2 million people being compromised.

Advertisement. Scroll to continue reading.

Throughout 2025, the group listed 400 victims on its Tor-based leak site, including Lee Enterprises and pharma company Inotiv.

In June this year, Qilin was exploiting a critical authentication bypass vulnerability in Check Point VPN and firewall products, tracked as CVE-2026-50751.

In August, the US Bureau of Alcohol, Tobacco, Firearms and Explosives (ATF) confirmed it had fallen victim to a cyberattack after Qilin added it to its leak site.

Related: FBI Arrests ‘Most Wanted’ Developer of Ploutus ATM Malware

Related: Alleged ShinyHunters Leader Arrested in Jordan

Related: In Rare Move, Alleged Iranian State Hacker Extradited to US

Related: Police Shut Down KillSec Ransomware, Identify Alleged Teen Leader

https://www.securityweek.com/qilin-ransomware-suspect-arrested-in-japan-extradited-to-germany/


FBI Blames Contractor’s Missed Patch for ShinyHunters Breach

The FBI has removed an Accenture contractor over a data breach that exposed personal information of thousands of bureau employees.

The post FBI Blames Contractor’s Missed Patch for ShinyHunters Breach appeared first on SecurityWeek.

https://www.securityweek.com/fbi-blames-contractors-missed-patch-for-shinyhunters-breach/


FBI Arrests ‘Most Wanted’ Developer of Ploutus ATM Malware

An alleged leader of Tren de Aragua’s ATM jackpotting activities, Canelon Aguirre was on the FBI’s top 10 most wanted list since March 2026.

The post FBI Arrests ‘Most Wanted’ Developer of Ploutus ATM Malware appeared first on SecurityWeek.

https://www.securityweek.com/fbi-arrests-most-wanted-developer-of-ploutus-atm-malware/


Crypto Scammers Hijack Microsoft’s Official X Account

Hackers used the account, which has 13 million followers, to amplify a Clippy-themed cryptocurrency account.

The post Crypto Scammers Hijack Microsoft’s Official X Account appeared first on SecurityWeek.

https://www.securityweek.com/crypto-scammers-hijack-microsofts-official-x-account/


In Rare Move, Alleged Iranian State Hacker Extradited to US

Amir Barati, an alleged member of the Mabna Institute, was indicted for targeting universities, private organizations, and government entities in the US and abroad.

The post In Rare Move, Alleged Iranian State Hacker Extradited to US appeared first on SecurityWeek.

https://www.securityweek.com/in-rare-move-iranian-hacker-accused-of-working-for-irgc-extradited-to-us/


North Korea Suspected in $351 Million Bitget Crypto Heist

Cryptocurrency exchange Bitget says the hackers who stole roughly $351.6 million in digital assets from its systems used techniques that closely resemble those of known North Korean threat actors.

“Based on IP behavior patterns and on-chain analysis, the attack method in this incident is highly consistent with known patterns of North Korean hacker organizations,” Bitget CEO Gracy Chen said in a Friday post on X.

Chen’s post did not name a specific threat group, and Bitget has not detailed the evidence behind its assessment. She said the incident has been reported to the relevant authorities.

Founded in 2018, Bitget runs a centralized exchange for spot and derivatives crypto trading. It also offers Bitget Wallet, a self-custodial wallet that the company says runs on separate infrastructure and was not affected.

Bitget said its security systems caught the unauthorized transfers on September 24. The funds came from a small number of the exchange’s hot wallets. According to the company, its cold wallets were not touched.

The stolen funds include ETH, XRP, BNB, AVAX, USDT and USDC, spread across several blockchains. XRP accounts for the largest loss on a single chain. According to Chen, some blockchain foundations have frozen wallet addresses linked to the attacker.

Advertisement. Scroll to continue reading.

The company hasn’t yet worked out how the attacker got in. However, it said the hacker compromised a critical backend system in its wallet infrastructure and abused it to get fraudulent transfers approved. Bitget said private keys were not compromised.

Mandiant and blockchain security firm SlowMist are helping with the investigation.

North Korean state-sponsored hackers have stolen billions of dollars’ worth of cryptocurrency in recent years. The FBI blamed North Korea for the February 2025 heist in which roughly $1.5 billion was stolen from Bybit.

Related: $290 Million Kelp DAO Crypto Heist Blamed on North Korea

Related: CryptoBandits Malware Doubles as a Backdoor, Abuses Tor

Related: Party’s Over for Crypto Scammers Who Went on a Spending Spree After a $240 Million Bitcoin Theft

https://www.securityweek.com/north-korea-suspected-in-351-million-bitget-crypto-heist/


In Other News: Ransomware Developer Sentenced, Plugin4Shell AI Attack, Critical SAP Flaw

SecurityWeek’s weekly cybersecurity news roundup offers a concise overview of important developments that may not receive full standalone coverage yet remain relevant to the broader threat landscape.

This curated summary highlights key stories across vulnerability disclosures, emerging attack methods, policy updates, industry reports, and other noteworthy events to help readers stay well-informed about the evolving cybersecurity environment.

Here are this week’s highlights: 

Raindrop raises $35 million for AI agent monitoring

Raindrop, designed to detect unknown failures in autonomous agents, announced a Series A funding round of $35 million, adding to last year’s $15 million seed round. Raindrop continuously analyzes agent behavior to surface silent and emerging failure modes, and to help AI systems repair and learn from them.

Advertisement. Scroll to continue reading.

Mandiant’s 2026 AI risk report highlights agentic attack escalation

Mandiant’s latest AI Risk and Resilience report finds that attackers have moved from prompting AI chatbots for research to letting autonomous agents run entire intrusions, citing incidents where a hijacked coding assistant helped spread a self-propagating worm across roughly 100 repositories and a compromised CI/CD credential let an attacker co-debug exfiltration tools with an LLM in real time. Separately, the report flags a new financial risk category, detailing a case where a corrupted value sent an accounting agent into a runaway reasoning loop that racked up over 15,000 API calls and roughly $50,000 in cloud costs in under an hour. 

Npm info-stealer author cashes in on bug bounty programs

CrowdStrike has tied an npm-based information stealer called PhantomRaven to a financially motivated actor who moonlights as a bug bounty hunter. The JavaScript malware, distributed through typosquatted npm packages, is assessed with high confidence to have been written by an LLM based on its verbose comments and placeholder code, and it harvests system details plus CI/CD environment variables from GitHub Actions, GitLab CI, Jenkins, and CircleCI. CrowdStrike found no evidence the stolen data is sold on criminal marketplaces, suggesting the operator uses it purely to flag compromises for bounty payouts.

Black Axe leaders extradited to US over cybercrime network

Five leaders of the Cape Town chapter of Nigeria’s Black Axe crime syndicate have been extradited from South Africa to New Jersey to face wire fraud and money laundering conspiracy charges. Prosecutors say the group ran romance scams and advance-fee schemes against US victims from 2011 to 2021. The defendants, arrested in South Africa in 2021, also face related wire fraud and identity theft counts tied to business email compromise.

Ransomware developer gets 13-year prison sentence in Switzerland

A Zurich court sentenced a Ukrainian IT specialist to nearly 13 years in prison for developing ransomware used in extortion attacks on companies including Stadler Rail. The court identified him as the lead developer behind the Lockergoga, MegaCortex, and Nefilim ransomware families, though it described his role as closer to a technical consultant than the operation’s mastermind. Prosecutors estimated total damages from the campaign at roughly $123 million, and the verdict remains subject to appeal.

NIST, CISA detail defenses against token theft in the cloud

NIST and CISA have published a final joint report giving federal agencies and cloud providers implementation guidance for protecting the signed tokens and identity assertions that underpin single sign-on, federation, and API access. The report addresses token validation, secrets management, and detection at scale, incorporating feedback gathered through CISA’s Joint Cyber Defense Collaborative on an earlier draft. It builds on NIST’s existing security and privacy controls guidance and supports Secure by Design principles.

Organizations warned of critical SAP vulnerability

Organizations using SAP have been warned about CVE-2026-44756, a maximum-severity flaw in its Extended Passport processing code that lets unauthenticated attackers trigger memory corruption before any login check occurs. Onapsis discovered the vulnerability and dubbed it OVERPASS. Researchers from Pathlock and nullFaktor confirmed remote code execution is achievable over HTTP/HTTPS and NGRFC in lab testing, and warned that public technical write-ups released within 48 hours of the patch lower the bar for exploit development. The bug touches a wide range of SAP products, including S/4HANA, NetWeaver, and Business Suite. SAP is urging emergency patching of internet-facing systems.

WordPress plugin bug fuels mass webshell uploads

Defiant says attackers have exploited a critical file-upload flaw in the WooCommerce Wholesale Lead Capture plugin, blocking more than 100,000 exploit attempts since the bug was disclosed in February. The flaw lets unauthenticated visitors bypass file-type checks and upload PHP webshells because the plugin trusts an attacker-supplied list of allowed extensions instead of its own configuration. Site owners are urged to update to version 2.0.3.2 and check for suspicious PHP files, particularly in the uploads directory.

TP-Link patches Tapo camera flaw that skips password checks

OPSWAT researchers found two flaws in TP-Link’s Tapo C200 security camera, including an authentication bypass that lets an attacker on the network replay a value from the camera’s own challenge-response process to gain admin access without a password. A second bug allows a denial-of-service attack by sending oversized Wi-Fi credential data during device onboarding, crashing the camera’s HTTPS service. TP-Link fixed both issues, tracked as CVE-2026-15315 and CVE-2026-15316, in firmware V5_1.4.6 released in August.

Plugin auto-updates open door to silent AI agent takeover

Researchers at Air’s security lab disclosed Plugin4Shell, a zero-click flaw affecting Claude Code, OpenAI Codex, GitHub Copilot, and Gemini CLI that lets an attacker controlling a plugin’s repository swap a pinned, reviewed commit for malicious code without tripping the SHA-pinning check. Because the affected agents check out a requested commit without verifying what actually landed, an attacker can name a branch after the pinned hash so git resolves to it instead, and background auto-updates push the malicious version to already-installed plugins with no user action. Anthropic and OpenAI have shipped fixes for Claude Code and Codex, Microsoft has not yet patched Copilot, and Google says the deprecated Gemini CLI will not be fixed at all.

Related: In Other News: InjectEave Attack, SIM Swapper Sentenced, Glasswing Findings Review

Related: In Other News: Microsoft’s Cloud Patches, Hacked Dropbox Accounts, Guardio’s $1.1B Valuation

https://www.securityweek.com/in-other-news-ransomware-developer-sentenced-plugin4shell-ai-attack-critical-sap-flaw/
NightmareStresser DDoS Service Disrupted in International Operation

NightmareStresser, one of the longest-running distributed denial-of-service (DDoS) for-hire services in the world, has been disrupted.

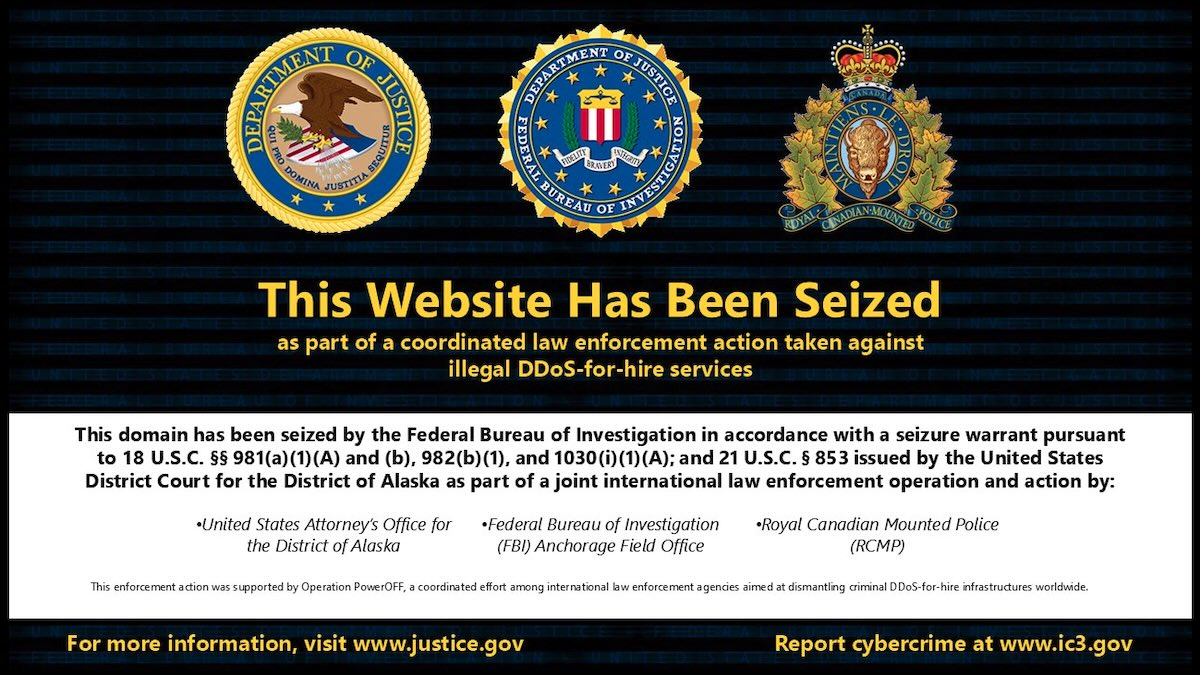
The US Department of Justice announced this week that the FBI has seized the internet domains associated with the booter service.

Visitors to nightmare-stresser[.]com and nightmarestresser[.]org are now served a seizure banner.

Authorities said NightmareStresser had been active since at least 2022 and was used to launch hundreds of thousands of DDoS attacks against victims worldwide.

However, security researcher Alex Carter reported last year that NightmareStresser was likely founded in 2016 and became popular in 2018, after rival services were disrupted, becoming the largest DDoS tool in 2019.

By 2025, it had grown to nearly 1 million users. It could launch between 3,000 and 4,000 attacks per hour, accepted cryptocurrency payments, but avoided government, education, and hospital domains.

Advertisement. Scroll to continue reading.

The NightmareStresser takedown was part of Operation PowerOFF, a coordinated global effort to dismantle DDoS-for-hire infrastructures globally and hold the individuals behind these services accountable.

DDoS-for-hire services, also referred to as booters or stressers, have been proliferating over the past years, as they represent low-entry barriers for cybercriminal-wannabes, the DoJ notes.

Over the past eight years, the US charged 12 DDoS attack facilitators and seized over 100 domains associated with booter services.

In April, law enforcement agencies in 21 countries disrupted 53 domains associated with DDoS-for-hire services. Last year, the US disrupted the RapperBot DDoS botnet, and 27 websites linked to booter services were seized in 2024.

In addition to disrupting DDoS-for-hire infrastructure, law enforcement agencies have been tracking and charging both the administrators and the users of these services.

Related: 23-Year-Old Sality P2P Botnet Disrupted

Related: US Disrupts Chinese Hacking Platform Used in Military and Critical Infrastructure Attacks

Related: Google, FBI Disrupt NetNut Residential Proxy Network Powered by Millions of Devices

Related: 15,000 WordPress Websites Cleaned Up in SocGholish Botnet Takedown

https://www.securityweek.com/nightmarestresser-ddos-service-disrupted-in-international-operation/


In Other News: InjectEave Attack, SIM Swapper Sentenced, Glasswing Findings Review

Noteworthy stories that might have slipped under the radar: Invisible Unicode slips past phishing filters, US puts $10 million bounty on Iranian cyber official, military ties of Chinese hacking group QTFY.

The post In Other News: InjectEave Attack, SIM Swapper Sentenced, Glasswing Findings Review appeared first on SecurityWeek.

https://www.securityweek.com/in-other-news-injecteave-attack-sim-swapper-sentenced-glasswing-findings-review/


Ukrainian Conti Ransomware Developer Sentenced to 4 Years in US Prison

Oleksii Oleksiyovych Lytvynenko has been sentenced to 4 years in prison after he was arrested in Ireland in 2023.

The post Ukrainian Conti Ransomware Developer Sentenced to 4 Years in US Prison appeared first on SecurityWeek.

https://www.securityweek.com/ukrainian-conti-ransomware-developer-sentenced-to-4-years-in-us-prison/