Google Feature Blamed for Retool Breach That Led to Cryptocurrency Firm Hacks 
A recently introduced Google account sync feature has been blamed by software development firm Retool after sophisticated hackers gained access to its systems and targeted over two dozen of its customers from the cryptocurrency sector.

Retool is a San Francisco, California-based company that provides a development platform designed for building custom business tools without the need for advanced programming skills. Its customers include major companies such as Amazon, DoorDash, Unity, NBC, Mercedes-Benz, Volvo, Lyft and Peloton.

The company revealed this week that 27 of its cloud customers were notified in late August that there had been unauthorized access to their accounts. Retool said on-prem and managed accounts were not impacted.

Hackers launched account takeover attacks against these customers, changing user emails and resetting passwords. All of the victims were from the cryptocurrency industry.

Retool said the attack was quickly detected and the company rushed to take action to revert the 27 account takeovers. 

However, CoinDesk reported that at least one customer, Fortress Trust, had $15 million worth of cryptocurrency stolen as a result of the attack. 

The sophisticated attack started with SMS-based spear phishing aimed at Retool employees. The messages, received by several employees, appeared to come from a member of the company’s IT team and instructed recipients to access a legitimate-looking link in order to address some payroll and open enrollment (healthcare-related) issues. 

Advertisement. Scroll to continue reading.

Only one employee fell for the attack and accessed the link, which led them to a phishing page that tricked them into handing over their credentials and multi-factor authentication (MFA) data. 

The hackers then followed up with a phone call in which they deepfaked an employee’s actual voice. The person making the call raised some suspicion, but ultimately the employee did provide the attacker an additional MFA code that they needed. The attacker was convincing because they were familiar with the office’s floor plan, internal processes, and other employees. 

“The additional OTP token shared over the call was critical, because it allowed the attacker to add their own personal device to the employee’s Okta account, which allowed them to produce their own Okta MFA from that point forward. This enabled them to have an active GSuite session on that device,” Retool explained in a blog post.

The company said it uses one-time passwords (OTPs) for authentication to Google, Okta, an internal VPN, and internal Retool instances. The attacker was able to obtain access to all the MFA tokens in the targeted employee’s account — and then access internal systems — due to a recently launched Google Authenticator feature that syncs MFA codes to the cloud. 

If the feature is active — it was active in the case of the Retool employee — hackers can obtain all of the targeted user’s MFA codes if their Google account is compromised. 

“If you install Google Authenticator from the app store directly, and follow the suggested instructions, your MFA codes are by default saved to the cloud. If you want to disable it, there isn’t a clear way to ‘disable syncing to the cloud’, instead there is just a ‘unlink Google account’ option. In our corporate Google account, there is also no way for an administrator to centrally disable Google Authenticator’s sync ‘feature’,” Retool complained.

“The fact that Google Authenticator syncs to the cloud is a novel attack vector,” Retool noted. “What we had originally implemented was multi-factor authentication. But through this Google update, what was previously multi-factor-authentication had silently (to administrators) become single-factor-authentication, because control of the Okta account led to control of the Google account, which led to control of all OTPs stored in Google Authenticator.”

It’s unclear who is behind the attack, but the incident seems to have some similarities to recent attacks attributed to a financially motivated threat group tracked as 0ktapus, Scattered Spider and UNC3944. The group is known for its sophisticated social engineering tactics, the use of SMS-based phishing messages, and the targeting of cryptocurrency firms. The same gang also appears to be behind the recent highly disruptive attack on MGM Resorts. 

Regarding the use of deepfakes for social engineering, this seems to be an increasingly popular tactic. US agencies CISA, FBI and NSA this week published a cybersecurity report on deepfakes, warning that video, audio and text deepfakes can be used for a wide range of malicious purposes, including business email compromise (BEC) attacks and cryptocurrency scams. 

UPDATE: Google has provided SecurityWeek the following statement:

“Our first priority is the safety and security of all online users, whether consumer or enterprise, and this event is another example of why we remain dedicated to improving our authentication technologies. Beyond this, we also continue to encourage the move toward safer authentication technologies as a whole, such as passkeys, which are phishing resistant. Phishing and social engineering risks with legacy authentication technologies, like ones based on OTP, are why the industry is heavily investing in these FIDO-based technologies. While we continue to work toward these changes, we want to ensure Google Authenticator users know they have a choice whether to sync their OTPs to their Google Account, or to keep them stored only locally. In the meantime, we’ll continue to work on balancing security with usability as we consider future improvements to Google Authenticator.”

Related: FBI Finds 1,580 Bitcoin in Crypto Wallets Linked to North Korean Hackers 

Related: North Korean Hackers Steal $53 Million in Cryptocurrency From CoinEx

Related: 3 Cryptocurrency Firms Suffer Data Breach After Kroll SIM Swapping Attack

https://www.securityweek.com/google-feature-blamed-for-retool-breach-that-led-to-cryptocurrency-firm-hacks/


A Second Major British Police Force Suffers a Cyberattack in Less Than a Month

Personal details of thousands of police officers and staff from Greater Manchester Police have been hacked from a company that makes identity cards, the second such cyberattack to affect a major British police force in less than a month.

Details on identity badges and warrant cards, including names, photos and identity numbers or police collar numbers, were stolen in the ransomware attack, Greater Manchester Police said Thursday. The third-party supplier was not identified.

The force said no home addresses of officers or any financial information about individuals was stolen.

“This is being treated extremely seriously, with a nationally led criminal investigation into the attack,” Assistant Chief Constable Colin McFarlane said in a statement.

Britain’s National Crime Agency is leading the investigation into the ransomware attack.

The federation that represents officers in Greater Manchester said it is working with the police force to limit the damage.

“Our colleagues are undertaking some of the most difficult and dangerous roles imaginable to catch criminals and keep the public safe,” said Mike Peake, chair of the Greater Manchester Police Federation. “To have any personal details potentially leaked out into the public domain in this manner — for all to possibly see — will understandably cause many officers concern and anxiety.”

Advertisement. Scroll to continue reading.

The attack follows the news on Aug. 26 that London’s Metropolitan Police suffered a similar security breach involving one of its suppliers. It also referred the incident to the National Crime Agency.

The breaches follow an incident in July in which the Police Service of Northern Ireland acknowledged that it had inadvertently published personal information of more than 10,000 officers and staff in response to a freedom of information request.

Officials fear the information has been obtained by Irish Republican Army dissidents who continue to mount occasional attacks on police 25 years after Northern Ireland’s peace accord.

https://www.securityweek.com/a-second-major-british-police-force-suffers-a-cyberattack-in-less-than-a-month/


North Korean Hackers Steal $53 Million in Cryptocurrency From CoinEx

North Korean hackers are suspected of stealing roughly $53 million worth of cryptocurrency from crypto exchange CoinEx, after a private key was leaked.

The incident was identified on September 12, when the exchange observed “anomalous withdrawals from several hot wallet addresses” in which CoinEx was temporarily storing user assets.

“It is currently preliminarily determined that the cause of the incident was the leakage of the hot wallet private key,” the company explains in an incident notification.

Immediately after identifying the attack, the exchange transferred the remaining assets in the targeted hot wallets to cold storage, suspended all deposit and withdrawal services, and shut down the hot wallet server.

CoinEx says it has started rebuilding and redeploying the wallet system and that deposit and withdrawal services will resume incrementally.

The exchange has published a list of suspicious cryptocurrency addresses involved in the attack, urging relevant project teams and fellow exchanges to help it in freezing the attackers’ funds.

“We are actively collaborating with the affected crypto projects to formulate a solution. Furthermore, we urge crypto projects and our fellow crypto exchanges to remain vigilant. If you detect any unusual or related activities from the aforementioned wallet addresses, please contact us immediately,” the exchange said on social media.

Advertisement. Scroll to continue reading.

While CoinEx did not share details on the stolen amounts, organizations tracking the involved crypto addresses have determined that roughly $53 million in Bitcoin, Ethereum, Smart Chain Coin, TRON, and other cryptocurrency was stolen in the heist.

Web3 security firm CertiK notes that at least $377 million worth of cryptocurrency have been stolen this year as result of private key compromises, and says that North Korea-linked hacking group Lazarus is the culprit.

The security firm has identified a connection between the recent Atomic Wallet, Alphapo, CoinsPaid, Stake.com, and CoinEx heists, all of which were the result of private key leakage, and all seemingly the work of Lazarus.

“Historical data, including the Ronin Bridge and CoinsPaid exploits, pinpoints the Lazarus Group’s modus operandi: spear-phishing targeting Web3 company personnel to hijack sensitive credentials. Employees in the Web3 sphere need to be acutely vigilant of unsolicited job pitches, especially those boasting overly lucrative compensation packages,” CertiK notes.

Related: FBI Finds 1,580 Bitcoin in Crypto Wallets Linked to North Korean Hackers

Related: GitHub Warns of North Korean Social Engineering Attacks Targeting Tech Firm Employees

Related: JumpCloud Cyberattack Linked to North Korean Hackers

https://www.securityweek.com/north-korean-hackers-steal-53-million-in-cryptocurrency-from-coinex/


Airbus Launches Investigation After Hacker Leaks Data

Airbus has launched an investigation after a hacker leaked information allegedly stolen from the French aerospace giant’s systems. 

Cybercrime intelligence firm Hudson Rock reported on Tuesday that a hacker who uses the online moniker ‘USDoD’ claimed earlier this month on a cybercrime forum that they had hacked Airbus.

The same hacker previously claimed to have breached the FBI’s InfraGard database, which stores information on 80,000 people, including business leaders, IT professionals, and military, law enforcement, and government officials. 

The hacker, who recently announced joining an emerging ransomware group, apparently obtained the personal information of 3,200 people associated with Airbus vendors, including  Rockwell Collins and Thales. The compromised data includes names, job titles, addresses, email addresses, and phone numbers. 

The attacker said they had gained access to Airbus systems using a compromised account belonging to an employee at a Turkish airline. Airbus confirmed to Hudson Rock that this was indeed the attack vector.

The cybersecurity firm’s investigation showed that the hacker obtained the targeted airline employee’s credentials for Airbus systems with the aid of malware. 

Information-stealing malware collects vast amounts of credentials from infected computers, and the malware operators then sell those credentials to others. In this case, Hudson Rock determined that the employee likely got their device infected with RedLine malware after downloading a pirated version of .NET. 

Advertisement. Scroll to continue reading.

“Credentials obtained from info-stealer infections, which have become the primary initial attack vector in recent years, provide threat actors with easy entry points into companies, facilitating data breaches and ransomware attacks,” Hudson Rock said.

The security firm regularly analyzes data obtained by such info-stealers, which have also been observed stealing hacker forum credentials. 

In a statement provided to SecurityWeek, an Airbus spokesperson said, “Airbus has launched an investigation into a cyber event during which an IT account associated with an Airbus customer has been attacked. This account was used to download business documents dedicated to this customer from an Airbus web portal.”

“Immediate remedial and follow-up measures were taken by our security teams to prevent our systems from being compromised,” the spokesperson added.

Related: Black Hat Hacker Exposes Real Identity After Infecting Own Computer With Malware

Related: Airbus CyberSecurity Subsidiary Stormshield Discloses Data Breach

Related: Airbus Says Taking ‘Appropriate Measures’ Against Hackers

https://www.securityweek.com/airbus-launches-investigation-after-hacker-leaks-data/


Iranian Cyberspies Deployed New Backdoor to 34 Organizations

Iran-linked cyberespionage group Charming Kitten has been observed infecting 34 victims with a new backdoor, cybersecurity firm ESET reports.

Believed to be operating on behalf of Iran’s Islamic Revolutionary Guard Corps (IRGC) and also tracked as APT42, Ballistic Bobcat, Mint Sandstorm (formerly Phosphorus), and NewsBeef, Charming Kitten has been targeting activists, government organizations and journalists for more than a decade.

Recently, the advanced persistent threat (APT) actor has been engaging in financially motivated ransomware operations and was seen targeting critical infrastructure organizations in the US last year.

Since 2021, the newly identified Sponsor backdoor has been deployed mainly against organizations in Israel, in the automotive, engineering, financial services, healthcare, manufacturing, media, technology, and telecommunications sectors.

For initial access, Charming Kitten exploited known vulnerabilities in internet-facing Microsoft Exchange servers. However, many of the identified victims lack an obvious intelligence value, suggesting that the attacks were not targeted, but rather a scan-and-exploit operation.

This theory is also supported by the fact that 16 of the 34 identified victims were compromised by other threat actors as well, ESET notes.

Written in C++, the Sponsor backdoor is executed as a persistent service that uses configuration files dropped on the disk, which contain an interval for contacting the command-and-control (C&C) server to receive commands, and a list of C&C servers.

Advertisement. Scroll to continue reading.

The backdoor gathers system information and sends it to the C&C server, which responds with a node ID. The malware also collects the host’s Windows domain and the current username.

Sponsor’s operators can issue commands to retrieve the backdoor’s process ID, execute a command on the host system, receive files and execute them, sleep, and to update the list of C&Cs and predetermined check-in intervals.

Charming Kitten has been observed using two versions of the backdoor, with no changes in functionality between them. As part of the campaign, the APT used previously known infrastructure, as well as a new C&C server and multiple IPs to deploy various open source tools in support of its operations.

“The group continues to use a diverse open source toolset supplemented with several custom applications, including its Sponsor backdoor. Defenders would be well advised to patch any internet-exposed devices and remain vigilant for new applications popping up within their organizations,” ESET notes.

Related: Iranian Cyberspies Target US-Based Think Tank With New macOS Malware

Related: Microsoft: Iranian APTs Exploiting Recent PaperCut Vulnerability

Related: UK Gov Warns of Phishing Attacks Launched by Iranian, Russian Cyberspies

https://www.securityweek.com/iranian-cyberspies-deployed-new-backdoor-to-34-organizations/


MGM Resorts Confirms ‘Cybersecurity Issue’, Shuts Down Systems

Hospitality and entertainment giant MGM Resorts on Monday said a “cybersecurity issue” forced the shutdown of certain computer systems, including the websites for some of the biggest Las Vegas and New York properties.

A brief note posted to X (the website formerly known as Twitter) said external cybersecurity experts and law enforcement are involved in an investigation that has all the hallmarks of a ransomware extortion attack.

Here’s the full MGM Resorts statement:

“MGM Resorts recently identified a cybersecurity issue affecting some of the Company’s systems. Promptly after detecting the issue, we quickly began an investigation with assistance from leading external cybersecurity experts. We also notified law enforcement and took prompt action to protect our systems and data, including shutting down certain systems.

Our investigation is ongoing, and we are working diligently to determine the nature and scope of the matter.”

MGM Resorts properties include the Mandalay Bay (the site of the Black Hat security conference), Bellagio, MGM Grand, Aria, Luxor and the Cosmopolitan.

The incident began sometime on Sunday and affected hotel reservation systems throughout the United States and other IT systems that run the casino floors.

Advertisement. Scroll to continue reading.

At 1:00PM PST Monday, services on the company’s homepage remained unavailable.

Related: BetMGM Confirms Breach Affecting 1.5 Million Customers

Related: Hospitality Chain Hit by Ransomware Attack

Related: Payments Giant NCR Hit by Ransomware

https://www.securityweek.com/mgm-resorts-confirms-cybersecurity-issue-shuts-down-systems/


After Microsoft and X, Hackers Launch DDoS Attack on Telegram

The hacker group Anonymous Sudan has launched a distributed denial-of-service (DDoS) attack against Telegram in retaliation to the messaging platform’s decision to suspend their primary account, threat intelligence firm SOCRadar reports.

Claiming to be a hacktivist group motivated by political and religious causes, Anonymous Sudan has orchestrated DDoS attacks against organizations in Australia, Denmark, France, Germany, India, Israel, Sweden, and the UK.

The group has been active since the beginning of the year and established its Telegram channel on January 18, announcing intent to launch cyberattacks against any entity opposing Sudan. The group’s activity began with the targeting of several Swedish sites.

However, Anonymous Sudan came to fame in June, after launching a series of disruptive DDoS attacks targeting Microsoft 365, impacting Outlook, Microsoft Teams, OneDrive for Business, and SharePoint Online. Microsoft’s Azure cloud computing platform was also affected.

Anonymous Sudan boasted about the attack on its Telegram channel, and Microsoft, which tracks the group as Storm-1359, confirmed DDoS attacks were indeed the cause of disruption.

In late August, the group targeted X (formerly Twitter) as part of a disruptive DDoS attack meant to pressure Elon Musk into launching the Starlink service in Sudan.

The attack on Telegram, however, had a different motivation compared to the group’s typical interests, but did not achieve its purpose, and the hacktivists have moved their main Telegram channel for the time being, SOCRadar says.

Advertisement. Scroll to continue reading.

The reason for the Telegram ban is unclear, but the threat intelligence firm believes it might be related to the use of bot accounts or to the recent attack on X.

According to previous reports from SOCRadar and Truesec, the Anonymous Sudan group currently engaging in DDoS and defacement attacks might not operate out of Sudan and might, in fact, have ties to the Russian hacking group KillNet.

The observed campaigns have no link to political issues related to Sudan, the group does not seek the support of pro-Islamic groups and only interacts with Russian hackers, and mainly posts in English and Russian, instead of Arabic.

Furthermore, the group does not appear to be linked to the original Anonymous Sudan hacktivists – which emerged in Sudan in 2019 – nor with Anonymous, the decentralized, anti-political hacktivist movement.

Related: CISA Releases Guidance on Adopting DDoS Mitigations

Related: US Seizes Domains of 13 DDoS-for-Hire Services

Related: Record-Breaking 71 Million RPS DDoS Attack Seen by Cloudflare

https://www.securityweek.com/after-microsoft-and-x-hackers-launch-ddos-attack-on-telegram/


FBI Blames North Korean Hackers for $41 Million Stake.com Heist

The FBI says that the North Korea-linked hacking group Lazarus is responsible for the theft of $41 million in cryptocurrency from online casino and betting platform Stake.com.

The incident occurred on September 4, when the Australian-Curaçaoan online platform Stake.com announced that hackers had stolen funds from its Ethereum (ETH) and Binance Smart Chain (BSC) hot wallets.

The hackers, cryptocurrency security researcher ZachXBT discovered by tracking the transactions, stole roughly $15.7 million in Ethereum and another $25.6 million in BSC and Polygon.

Shortly after the heist, ZachXBT suggested that North Korea’s Lazarus might be responsible for the attack, and the FBI has confirmed it.

“The FBI investigation has revealed that DPRK cyber actors moved stolen funds associated with the Ethereum, Binance Smart Chain (BSC), and Polygon networks from Stake.com,” the agency said last week.

The FBI has published a list of virtual currency addresses associated with Lazarus’ activity and encourages organizations to avoid engaging in transactions with them.

The FBI’s warning comes less than two months after GitHub exposed a North Korea-linked social engineering campaign targeting accounts linked to the blockchain, cryptocurrency, and online gambling sectors.

Advertisement. Scroll to continue reading.

Over the past several years, Lazarus has been blamed for numerous high-profile cyber-heists, starting with the $81 million theft from Bangladesh’s account at the New York Federal Reserve Bank, in 2016.

Deemed a serious threat to banks in 2017, Lazarus shifted focus to cryptocurrency exchanges in 2018, and is said to have continued to conduct attacks against organizations in this sector, to generate funds for the North Korean regime.

According to the FBI, this year alone, the North Korean state-sponsored group has stolen more than $200 million in virtual currency.

In July, Lazarus drained $60 million in cryptocurrency from Alphapo and another $37 million from CoinsPaid in July. In June, the hackers stole $100 million from Atomic Wallet. Lazarus is also blamed for a $100 million Horizon bridge crypto heist.

Related: FBI Finds 1,580 Bitcoin in Crypto Wallets Linked to North Korean Hackers

Related: UN Experts: North Korean Hackers Stole Record Virtual Assets

https://www.securityweek.com/fbi-blames-north-korean-hackers-for-41-million-stake-com-heist/


Powerful Ethnic Militia in Myanmar Repatriates 1,200 Chinese Suspected of Involvement in Cybercrime

One of Myanmar’s biggest and most powerful ethnic minority militias has arrested and repatriated more than 1,200 Chinese nationals allegedly involved in criminal online scam operations, an official of the group said Saturday.

The arrests were carried out in territory controlled by the United Wa State Army, or UWSA, in eastern Shan state in raids on Tuesday and Wednesday, Nyi Rang, a liaison officer from the militia, told The Associated Press.

He said in a text message that the arrested people were handed over to Chinese police at the border gate in Panghsang — also known as Pangkham city — the capital of Wa-administered territory on the border with China’s Yunnan province.

Cybercrime scams have become a major issue in Asia, as many of the workers employed to carry out the online scams are themselves victims of criminal gangs, who lure them with fake job offers and then force them to work in conditions of virtual slavery.

The Office of the U.N. High Commissioner for Human Rights said in a report last month that the gangs have forced hundreds of thousands of people in Southeast Asia into participating in scam operations that include false romance ploys, bogus investment pitches and illegal gambling schemes.

The reporthttps://www.ohchr.org/en/press-releases/2023/08/hundreds-thousands-trafficked-work-online-scammers-se-asia-says-un-report said that at least 120,000 people in strife-torn Myanmar and roughly 100,000 in Cambodia “may be held in situations where they are forced to carry out online scams.”

It said the online scam centers in Myanmar are allegedly located in the towns in southeastern Kayin state along the Thai border and Kokang Self-Administered Zone, and the Wa-administered city of Mong La in Shan state on the Chinese border.

Advertisement. Scroll to continue reading.

Wa liaison officer Nyi Rang said that the online fraud operations aren’t allowed in the territory administered by the UWSA and its political arm, the United Wa State Party, and similar arrests had been made previously.

The UWSA’s online media outlet, WSTV, said Friday on its Facebook account that a total of 1,207 Chinese nationals who were arrested by the Wa state police for online fraud were handed over to the Chinese police. China’s state Xinhua news agency, citing Beijing’s Ministry of Public Security, reported the same figure of those turned over Wednesday, and said they included 41 fugitives from justice.

The United Wa State Army is the biggest and strongest ethnic armed organization among the major ethnic minority groups in Myanmar, with an army of approximately 30,000 well-equipped soldiers and sophisticated weaponry including heavy artillery and helicopters, from China, with which it maintains close relations.

The Wa administer their territory with no interference from Myanmar’s central government in two separate enclaves in northeastern and southern parts of Shan state, the former bordering China and the other Thailand.

China also maintains good relations with Myanmar’s military rulers, who took power after the army ousted the elected government of Aung San Suu Kyi in February 2021.

In July, Chinese Ambassador Chen Hai urged Myanmar’s Foreign Affairs Minister Than Swe during a meeting in the capital Naypyitaw to work together with other neighboring countries to suppress and root out online gambling and scam centers operating in the border areas of Myanmar and rescue trapped Chinese citizens.

Chen Hai visited Naypyitaw at least three times between June and August to discuss China-Myanmar border security matters.

The U.N. report about Southeast Asian cybercrime said the online fraud gangs were also active in southeastern Kayin state on the Thai border.

Shwe Kokko, a small town in northern part of Kayin state’s Myawaddy township, is notorious for casino complexes that allegedly host major organized crime operations, including online scamming, gambling and human trafficking. The complexes were developed by Chinese investors in cooperation with the local Border Guard Forces, which are militias affiliated with Myanmar’s army.

Related: Digital Warfare: Myanmar’s Cyber Crackdown Explained

https://www.securityweek.com/powerful-ethnic-militia-in-myanmar-repatriates-1200-chinese-suspected-of-involvement-in-cybercrime/


The International Criminal Court will now prosecute cyberwar crimes

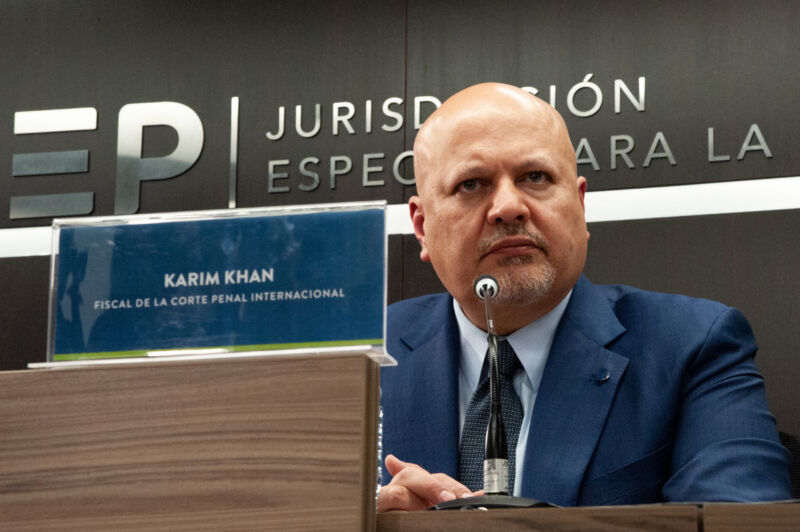
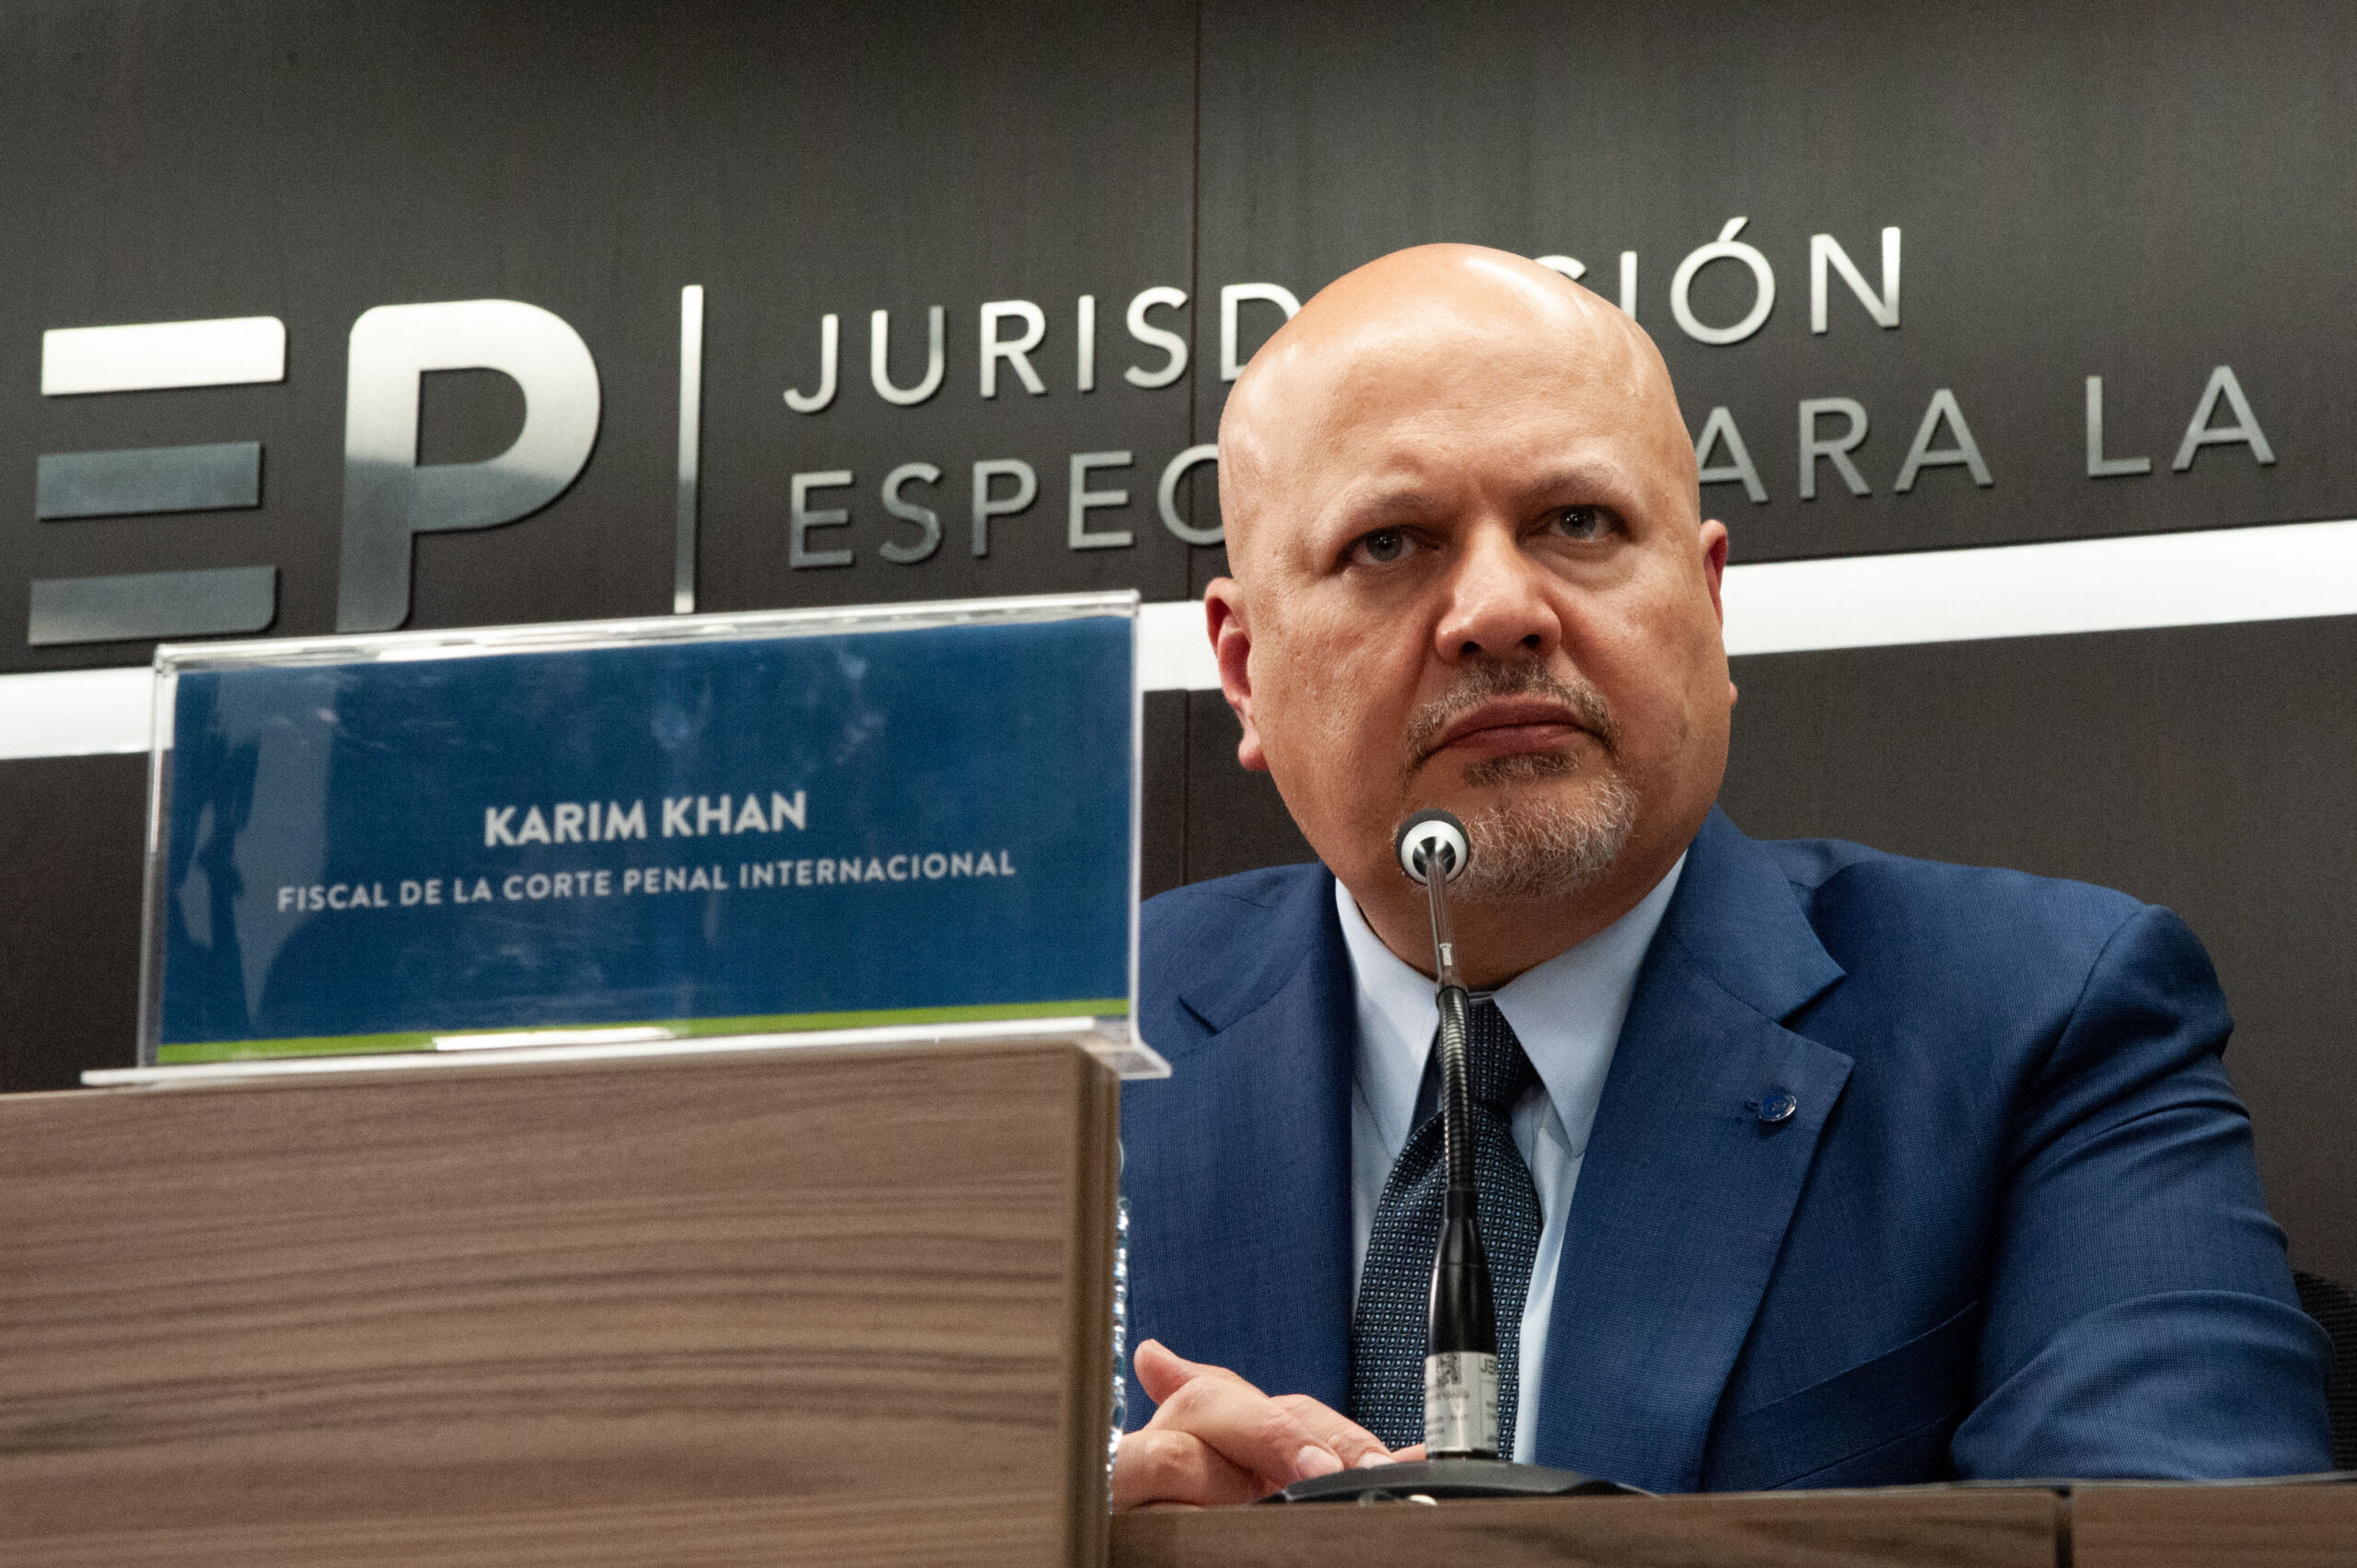
Karim Khan speaks at Colombia's Special Jurisdiction for Peace during the visit of the Prosecutor of the International Criminal Court in Bogota, Colombia, on June 6, 2023.
Enlarge / Karim Khan speaks at Colombia’s Special Jurisdiction for Peace during the visit of the Prosecutor of the International Criminal Court in Bogota, Colombia, on June 6, 2023.

For years, some cybersecurity defenders and advocates have called for a kind of Geneva Convention for cyberwar, new international laws that would create clear consequences for anyone hacking civilian critical infrastructure, like power grids, banks, and hospitals. Now the lead prosecutor of the International Criminal Court at the Hague has made it clear that he intends to enforce those consequences—no new Geneva Convention required. Instead, he has explicitly stated for the first time that the Hague will investigate and prosecute any hacking crimes that violate existing international law, just as it does for war crimes committed in the physical world.

In a little-noticed article released last month in the quarterly publication Foreign Policy Analytics, the International Criminal Court’s lead prosecutor, Karim Khan, spelled out that new commitment: His office will investigate cybercrimes that potentially violate the Rome Statute, the treaty that defines the court’s authority to prosecute illegal acts, including war crimes, crimes against humanity, and genocide.  

“Cyberwarfare does not play out in the abstract. Rather, it can have a profound impact on people’s lives,” Khan writes. “Attempts to impact critical infrastructure such as medical facilities or control systems for power generation may result in immediate consequences for many, particularly the most vulnerable. Consequently, as part of its investigations, my Office will collect and review evidence of such conduct.”

When WIRED reached out to the International Criminal Court, a spokesperson for the office of the prosecutor confirmed that this is now the office’s official stance. “The Office considers that, in appropriate circumstances, conduct in cyberspace may potentially amount to war crimes, crimes against humanity, genocide, and/or the crime of aggression,” the spokesperson writes, “and that such conduct may potentially be prosecuted before the Court where the case is sufficiently grave.”

Neither Khan’s article nor his office’s statement to WIRED mention Russia or Ukraine. But the new statement of the ICC prosecutor’s intent to investigate and prosecute hacking crimes comes in the midst of growing international focus on Russia’s cyberattacks targeting Ukraine both before and after its full-blown invasion of its neighbor in early 2022. In March of last year, the Human Rights Center at UC Berkeley’s School of Law sent a formal request to the ICC prosecutor’s office urging it to consider war crime prosecutions of Russian hackers for their cyberattacks in Ukraine—even as the prosecutors continued to gather evidence of more traditional, physical war crimes that Russia has carried out in its invasion.

In the Berkeley Human Rights Center’s request, formally known as an Article 15 document, the Human Rights Center focused on cyberattacks carried out by a Russian group known as Sandworm, a unit within Russia’s GRU military intelligence agency. Since 2014, the GRU and Sandworm, in particular, have carried out a series of cyberwar attacks against civilian critical infrastructure in Ukraine beyond anything seen in the history of the internet. Their brazen hacking has ranged from targeting Ukrainian electric utilities and triggering the only two blackouts ever caused by cyberattacks to the release of the data-destroying NotPetya malware that spread from Ukraine to the rest of the world and inflicted more than $10 billion in damage, including to hospital networks in both Ukraine and the United States.

Though the Berkeley group’s submission initially focused on Sandworm’s 2015 and 2016 attacks on Ukraine’s power grid as the clearest example of cyberattacks with physical effects comparable to those of traditional warfare, it later expanded its argument to include Sandworm’s NotPetya cyberattack, as well as a third attempt by the hackers to sabotage Ukraine’s power grid and another cyberattack on the Viasat satellite modem network used by Ukraine’s military, which caused outages of the satellite modems across Europe.

https://arstechnica.com/?p=1966589