Nuclear Flash Cards: US Secrets Exposed on Learning Apps

US troops charged with guarding nuclear weapons in Europe used popular education websites to create flash cards, exposing their exact locations and top-secret security protocols, according to the investigative site Bellingcat Friday.

To familiarize themselves with things like which shelters in various locations had “hot” vaults with live nuclear bombs, with security patrol schedules, and with identification badge details, the soldiers created digital flash card sets on apps like Chegg Prep, Quizlet and Cram.

“By simply searching online for terms publicly known to be associated with nuclear weapons, Bellingcat was able to discover cards used by military personnel serving at all six European military bases reported to store nuclear devices,” wrote Foeke Postma, the author of the Bellingcat article.

They found one set of 70 flashcards on Chegg, entitled “Study!”, which noted the exact shelters containing nuclear weapons at Volkel Air Base in the Netherlands.

“How many WS3 vaults are there on Volkel ab,” said the question side of one virtual flash card, referring to the military term for weapons storage and security systems.

“eleven (11)” it read on the answer side.

Another card from the same set indicated that five of the eleven vaults were “hot” with nuclear bombs while the other 6 were “cold,” and specified which vaults.

A set of 80 cards on the Cram flashcard site detailed hot and cold vaults at Aviano Air Base in Italy, and revealed how a soldier should respond in activating them based on the different level of alarms they receive.

Other cards exposed secrets at bases in Turkey, Belgium and Germany. Some detailed the location of security cameras; others gave the secret “duress words” that a soldier, perhaps seized by attackers, would say over a phone to indicate he had been taken prisoner.

The flashcards Bellingcat discovered were publicly available as far back as 2013, and some were being used as recently as April 2021.

Bellingcat said those it had viewed appeared to have been removed after it contacted NATO and the US military for comment before it published its article.

view counter

© AFP 2020

Previous Columns by AFP:
Tags:

http://feedproxy.google.com/~r/securityweek/~3/U5RxIM6m4zs/nuclear-flash-cards-us-secrets-exposed-learning-apps


Security Analytics Firm Uptycs Raises $50 Million

Cloud-native security analytics provider Uptycs has closed a $50 million Series C funding round, bringing the total raised by the company to date up to $93 million.

The latest funding round was led by Norwest Venture Partners, with additional participation from Sapphire Ventures and ServiceNow Ventures.

Based in Waltham, Massachusetts, Uptycs provides customers with a platform that integrates capabilities such as extended detection and response, management of cloud security posture, and protection for cloud workloads.

Through its security analytics platform, the company seeks to help professionals investigate and respond to potential threats across both on-premises and cloud environments.

Founded in 2016, Uptycs says it has registered triple-digit growth over the past few consecutive years, and has added several large organizations to its customer base.

The new funding round will help the company expand its cloud-native security analytics platform, as well as invest in global sales and marketing.

“Data doesn’t live solely on the corporate network; productivity endpoints are mobile; production workloads are elastic and distributed across clouds; identity and access management has morphed into today’s firewall; and sensitive data lives in cloud-based apps like G Suite, Salesforce, and GitHub. It’s a completely different challenge to secure these attack surfaces, and we’re innovating to deliver a comprehensive solution,” Ganesh Pai, Uptycs CEO, said.

Related: Material Security Raises $40 Million

Related: Salt Security Raises $70 Million in Series C Funding

Related: Tessian Raises $65 Million at $500 Million Valuation 

view counter

Ionut Arghire is an international correspondent for SecurityWeek.

Previous Columns by Ionut Arghire:
Tags:

http://feedproxy.google.com/~r/securityweek/~3/ELq5GPS1oz8/security-analytics-firm-uptycs-raises-50-million


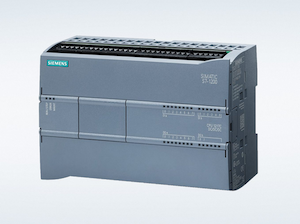
Newly Disclosed Vulnerability Allows Remote Hacking of Siemens PLCs

Researchers at industrial cybersecurity firm Claroty have identified a serious vulnerability that can be exploited by a remote and unauthenticated attacker to hack some of the programmable logic controllers (PLCs) made by Siemens.

The vulnerability is tracked as CVE-2020-15782 and it has been described as a high-severity memory protection bypass issue that allows an attacker with network access to TCP port 102 to write or read data in protected memory areas.

Siemens PLCs can be hacked remotely via new vulnerabilitySiemens says the security hole impacts its SIMATIC S7-1200 and S7-1500 CPUs. The German industrial giant has released firmware updates for some of the impacted devices and it has provided workarounds for products for which patches have yet to be released.

According to Claroty, the vulnerability can be exploited to gain native code execution on Siemens S7 PLCs by bypassing the sandbox where engineering code normally runs and gaining direct access to the device’s memory.

The company’s researchers showed how an attacker could bypass protections and write shellcode directly into protected memory. An attack exploiting this vulnerability would be difficult to detect, the researchers claim.

“Escaping the sandbox means an attacker would be able to read and write from anywhere on the PLC, and could patch an existing VM opcode in memory with malicious code to root the device,” Claroty researchers explained in a blog post published on Friday.

“Claroty, for example, was able to inject ARM/MIPS shellcode directly to an internal operating system structure in such a way that when the operating system uses a specific opcode that we chose, our malicious shellcode would execute, giving us remote code execution. We used this technique to install a kernel-level program with some functionality that is completely hidden to the operating system,” they added.

Claroty’s blog post describes the PLC sandbox and the role CVE-2020-15782 could play in an attack.

Related: Serious Vulnerabilities Found in Schneider Electric Power Meters

Related: Unprotected Private Key Allows Remote Hacking of Rockwell Controllers

Related: Vulnerabilities in CodeMeter Licensing Product Expose ICS to Remote Attacks

view counter

Eduard Kovacs (@EduardKovacs) is a contributing editor at SecurityWeek. He worked as a high school IT teacher for two years before starting a career in journalism as Softpedia’s security news reporter. Eduard holds a bachelor’s degree in industrial informatics and a master’s degree in computer techniques applied in electrical engineering.

Previous Columns by Eduard Kovacs:
Tags:

http://feedproxy.google.com/~r/securityweek/~3/hSgTTqLiIR0/newly-disclosed-vulnerability-allows-remote-hacking-siemens-plcs


Chinese Hackers Started Covering Tracks Days Before Public Exposure of Operations

One of the Chinese threat actors targeting Pulse Secure VPN appliances via a recently disclosed vulnerability has been attempting to cover its tracks by removing its webshells from victim networks, FireEye reports.

Tracked as CVE-2021-22893, the vulnerability was made public in late April, after security researchers discovered that threat actors had already been exploiting it in attacks targeting organizations in the defense, financial, government, high tech, and transportation sectors in the U.S. and Europe.

At the time, FireEye revealed that at least two Chinese threat actors believed to be state-sponsored — UNC2630 and UNC2717 — had been exploiting the vulnerability for initial compromise. The company identified 12 malware families used in attacks associated with the exploitation of CVE-2021-22893 and three other bugs in Pulse Secure VPN appliances.

A patch was shipped on May 3, two weeks after the security hole was publicly disclosed, but the activity surrounding it and the other flaws did not stop. In fact, FireEye says it has since identified four other malware families used in these attacks, namely BLOODMINE, BLOODBANK, CLEANPULSE, and RAPIDPULSE.

On the other hand, just days before FireEye made its findings public in April, UNC2630 was spotted removing its webshells from dozens of devices.

However, the security firm reveals that, in at least one instance, UNC2630 deleted the webshells deployed in their attack but did not remove the persistence patcher, thus ensuring they could return to the compromised environment when needed.

“It is unusual for Chinese espionage actors to remove a large number of backdoors across several victim environments on or around the time of public disclosure. This action displays an interesting concern for operational security and a sensitivity to publicity,” FireEye notes.

To avoid detection, both UNC2630 and UNC2717 modify file timestamps, and tamper with forensic evidence, including logs, web server core dumps, and data harvested for exfiltration. Additionally, the adversaries show advanced knowledge of victim networks, making it difficult for defenders to identify all of the tools employed, stolen data, or intrusion artefacts.

In a Thursday update to its alert on the targeting of Pulse Secure VPN appliances, the U.S. Cybersecurity and Infrastructure Security Agency (CISA) also noted that one of the identified threat actors has started cleanup operations, in an attempt to hide their tracks.

CISA also mentions a new tool from IT management and security firm Ivanti, which is designed to help administrators ensure the integrity of Pulse Connect Secure software.

Related: APT Abuses Pulse Secure, SolarWinds Appliances at the Same Organization

Related: FBI Shares IOCs for APT Attacks Exploiting Fortinet Vulnerabilities

Related: SolarWinds Hackers Impersonate U.S. Government Agency in New Attacks

view counter

Ionut Arghire is an international correspondent for SecurityWeek.

Previous Columns by Ionut Arghire:
Tags:

http://feedproxy.google.com/~r/securityweek/~3/Cyl5GcRrljY/chinese-hackers-started-covering-tracks-days-public-exposure-operations


Canada Post Says 950,000 Customers Hit by Breach at Supplier

Canada Post, the primary postal operator in Canada, has informed 44 of its large business customers that some information was compromised as a result of a malware attack at a supplier.

The impacted supplier is Commport Communications, an electronic data interchange (EDI) provider that Canada Post uses to manage shipping manifest data for large parcel business customers.

In a May 14 post seen by SecurityWeek on a popular hacking forum, someone claimed that a ransomware gang known as Lorenz had stolen tens of gigabytes of data from Commport.

Canada Post said it learned about the data breach on May 19, but its IT subsidiary, Innovapost, was informed in November 2020 that there had been a ransomware attack on Commport. However, at the time, Commport claimed it had found no evidence that customer data was compromised.

According to Canada Post, the attackers gained access to shipping manifests, which are used to fulfill customer orders and which typically include contact information for the sender and recipient.

An investigation conducted by the organization revealed that the information of more than 950,000 receiving customers was stored in the compromised shipping manifests. For 97 percent of these customers, only their name and address was stored, and for the remaining 3 percent the files also included an email address and/or phone number. The compromised information was collected between July 2016 and March 2019.

“We are proactively informing the impacted business customers and providing the information and support necessary to help them determine their next steps. As well, the Office of the Privacy Commissioner has been notified,” Canada Post said.

Related: Thousands of Canadian Government Accounts Hacked

Related: Russia, China ‘Cyber Threats’ Target Canada: Report

Related: Canada Says it Was Targeted by Russian Cyber Attacks

view counter

Eduard Kovacs (@EduardKovacs) is a contributing editor at SecurityWeek. He worked as a high school IT teacher for two years before starting a career in journalism as Softpedia’s security news reporter. Eduard holds a bachelor’s degree in industrial informatics and a master’s degree in computer techniques applied in electrical engineering.

Previous Columns by Eduard Kovacs:
Tags:

http://feedproxy.google.com/~r/securityweek/~3/kA7auQwYJYQ/canada-post-says-950000-customers-hit-breach-supplier


FBI Shares IOCs for APT Attacks Exploiting Fortinet Vulnerabilities

The FBI on Thursday published indicators of compromise (IOCs) associated with the continuous exploitation of Fortinet FortiOS vulnerabilities in attacks targeting commercial, government, and technology services networks.

In early April, the FBI along with the Cybersecurity and Infrastructure Security Agency (CISA) warned that threat actors had been targeting serious security holes in Fortinet’s flagship operating system FortiOS for initial access into victims’ networks.

The targeted bugs include CVE-2018-13379 (a path traversal in the FortiOS SSL VPN web portal), CVE-2020-12812 (a bypass of FortiOS SSL VPN two-factor authentication), and CVE-2019-5591 (default configurations ship without LDAP server identity verification).

While initial activity only involved scanning for devices vulnerable to the FortiOS SSL VPN web portal flaw (on ports 4443, 8443, and 10443), as well as enumeration of devices potentially impacted by the other two bugs, the attackers have since moved to network compromise and additional malicious activity.

“As of at least May 2021, an APT actor group almost certainly exploited a Fortigate appliance to access a webserver hosting the domain for a U.S. municipal government. The APT actors likely created an account with the username ‘elie’ to further enable malicious activity on the network,” the FBI now says.

The agency says that another account likely associated with this activity is “WADGUtilityAccount,” which, similar to “elie,” threat actors might have established on active directories, domain controllers, servers, and workstations. Network administrators should also look for other unrecognized accounts.

Additionally, admins should be wary of executable files such as Audio.exe (or frpc.exe) and Frps.exe, of outbound FTP traffic on port 443, a scheduled task named “SynchronizeTimeZone,” and the use of tools such as Mimikatz, MinerGate, WinPEAS, SharpWMI, BitLocker, WinRARwhere, and FileZilla. Some of these might be benign, unless used when unexpected, the FBI notes.

Administrators are also advised to take all the necessary measures to ensure the security of networks, including keeping systems patched and continuously updated, implementing network segmentation and multi-factor authentication, applying the principle of least privilege, keeping data backed up, employing malware detection tools, and periodically checking the environment for suspicious activity.

Related: Cring Ransomware Targets Industrial Organizations

Related: Industry Reactions to FBI Cleaning Up Hacked Exchange Servers: Feedback Friday

Related: FBI: 16 Conti Ransomware Attacks Targeted Healthcare, First Responders in U.S.

view counter

Ionut Arghire is an international correspondent for SecurityWeek.

Previous Columns by Ionut Arghire:
Tags:

http://feedproxy.google.com/~r/securityweek/~3/rrxefi0cSyQ/fbi-shares-iocs-apt-attacks-exploiting-fortinet-vulnerabilities


SolarWinds Hackers Impersonate U.S. Government Agency in New Attacks

The Russia-linked threat group believed to be behind the SolarWinds attack has been observed launching a new campaign this week. The attacks have targeted the United States and other countries, and involve a legitimate mass mailing service and impersonation of a government agency.

The latest attacks were analyzed by Microsoft, which tracks the threat actor as Nobelium, and by incident response firm Volexity, which has found some links to APT29, a notorious cyberspy group previously linked to Russia.

The campaign appears to have started on May 25 and Microsoft said it involved malicious emails being sent to roughly 3,000 accounts across over 150 organizations in 24 countries. The highest percentage of emails went to the United States, but Volexity also saw a significant number of victims in Europe.

Targeted organizations include government agencies, think tanks, NGOs, and consultants. Microsoft said at least a quarter of the targets are involved in human rights and international development work.

For this attack, Nobelium managed to compromise the Constant Contact account of the United States Agency for International Development (USAID), which is responsible for civilian foreign aid and development assistance. Constant Contact is an email marketing service, and by compromising the Constant Contact account of USAID the attackers were able to send out legitimate-looking emails containing malicious links.

The emails had subject lines such as “USAID Special Alert!” and they carried links that, when clicked, directed victims to a website controlled by Nobelium, through the Constant Contact service.

The Nobelium website is set up to deliver a malicious ISO file containing a shortcut file that executes a Cobalt Strike Beacon loader, a decoy document displayed to the victim, and the actual Cobalt Strike loader, which Microsoft described as a backdoor named NativeZone.

“The successful deployment of these payloads enables NOBELIUM to achieve persistent access to compromised systems. Then, the successful execution of these malicious payloads could enable NOBELIUM to conduct action-on objectives, such as lateral movement, data exfiltration, and delivery of additional malware,” Microsoft said in a blog post.

Both Microsoft and Volexity have made available indicators of compromise (IoC) that organizations can use to detect attacks.

Microsoft said its security solutions blocked many of the attacks aimed at its customers and the tech giant has started notifying targets. Volexity believes at least some organizations were successfully breached.

Earlier this month, government agencies in the US and UK warned that the SolarWinds hackers had started using the open-source adversary simulation framework Sliver after some of their operations were exposed.

Related: Three New Malware Strains Linked to SolarWinds Hackers

Related: CISA: Disconnect Internet for 3-5 Days to Evict SolarWinds Hackers From Network

Related: Hackers Targeted SolarWinds Earlier Than Previously Known

view counter

Eduard Kovacs (@EduardKovacs) is a contributing editor at SecurityWeek. He worked as a high school IT teacher for two years before starting a career in journalism as Softpedia’s security news reporter. Eduard holds a bachelor’s degree in industrial informatics and a master’s degree in computer techniques applied in electrical engineering.

Previous Columns by Eduard Kovacs:
Tags:

http://feedproxy.google.com/~r/securityweek/~3/ZC9CKbzxsZc/solarwinds-hackers-impersonate-us-government-agency-new-attacks


U.S. Charges 22 in Stolen Payment Cards Crackdown

The U.S. Justice Department this week announced indictments against 22 individuals who allegedly purchased and used payment cards stolen from a national retail chain.

Using point-of-sale malware installed at multiple retail locations of the target company, threat actors stole information of over three million payment cards, including credit, debit, and gift cards used at over 400 of the company’s retail stores.

According to the indictment, the co-conspirators then sold the hijacked data for $4 million in Bitcoin to an individual who sold it to thousands of other people, including the 22 now facing charges by the U.S. Department of Justice.

Twenty of the defendants have been arrested while the other two remain are large, likely abroad, the authorities said.

The 22 individuals are charged with using the payment card information to make various purchases, including at gas stations, hotels, and restaurants.

The indictment alleges that one of the defendants purchased more than 13,000 payment cards stolen from the retail chain, while another purchased more than 6,000 such cards. Others purchased between 2,000 and 4,000 payment cards. 

According to the Justice Department, each defendant faces up to 20 years in federal prison for charges of wire fraud and a two-year mandatory, consecutive prison sentence for aggravated identity theft.

Related: US Charges Swiss ‘Hacktivist’ for Data Theft and Leaks

Related: U.S. Charges North Korean Hackers Over $1.3B Bank Heists

Related: US Indicts Head of Alleged Crime Chat Comms Service

view counter

Ionut Arghire is an international correspondent for SecurityWeek.

Previous Columns by Ionut Arghire:
Tags:

http://feedproxy.google.com/~r/securityweek/~3/bwDeoUDUfuY/us-charges-22-stolen-payment-cards-crackdown


Japanese Ministries Confirm Impact from Fujitsu Data Breach

Japan’s Ministry of Foreign Affairs and Ministry of Land, Infrastructure, Transport and Tourism this week confirmed impact from a data breach at service provider Fujitsu Limited.

Earlier this week, the Japanese multinational provider of IT services and products confirmed it suffered a cyberattack resulting in unauthorized access to ProjectWEB, a tool that allows organizations to share data within and outside their environments.

The company said that it stopped the service, to prevent further unauthorized access, but confirmed that “some of the information entrusted to us by our customers was stolen,” without providing further information on the matter.

“The scope and cause of this incident are currently under investigation, and the operation of ProjectWEB has been suspended to prevent further unauthorized access,” Fujitsu said.

On Wednesday, Japan’s Ministry of Foreign Affairs announced that it was impacted by the incident, saying that study material was stolen, and that some personally identifiable information might have been affected as well.

The ministry notes that the affected individuals were informed of the data leak and that the study information doesn’t impact its systems or operations.

Also on Wednesday, the Ministry of Land, Infrastructure, Transport and Tourism said that approximately 76,000 email addresses of individuals both within and outside the ministry were likely compromised in the incident.

“No unauthorized access has been confirmed to the ministry’s system,” the ministry said, adding that it experienced no interruptions as result of the data leak. The ministry also revealed plans to contact the individuals whose email addresses were compromised.

Related: City of Chicago Hit by Data Breach at Law Firm Jones Day

Related: Cybercriminals Publish Data Stolen From Shell, Universities

Related: Belden Says Health-Related Information Exposed in Data Breach

view counter

Ionut Arghire is an international correspondent for SecurityWeek.

Previous Columns by Ionut Arghire:
Tags:

http://feedproxy.google.com/~r/securityweek/~3/0rviAC4e-CU/japanese-ministries-confirm-impact-fujitsu-data-breach


DataDome Raises $35 Million for Its Anti-Bot Solution

DataDome, a company that provides a SaaS solution for protecting businesses against bad bots and fraud, this week announced that it raised $35 million in a Series B funding round.

The investment round, which brings the company’s total funding to nearly $40 million, was led by venture capital firm Elephant, with participation from ISAI. DataDome plans on investing the money in sales, marketing, and R&D.

DataDome has developed an AI-powered platform that processes vast amounts of data in an effort to provide protection against various types of online threats, including payment fraud, DDoS attacks, account takeover attempts, and web scraping.

The company says its solution can provide real-time bot protection for websites, mobile applications and APIs. DataDome has offices in New York, Singapore and Paris, and it claims to have more than 130 customers worldwide.

Related: Goldman Sachs Buys Anti-Bot Startup White Ops

Related: The Anti-Fraud Lifecycle

Related: Microsoft, PayPal Invest in Anti-Fraud Startup Arkose Labs

Related: PerimeterX Banks $57 Million for Bot Protection Expansion

view counter

Eduard Kovacs (@EduardKovacs) is a contributing editor at SecurityWeek. He worked as a high school IT teacher for two years before starting a career in journalism as Softpedia’s security news reporter. Eduard holds a bachelor’s degree in industrial informatics and a master’s degree in computer techniques applied in electrical engineering.

Previous Columns by Eduard Kovacs:
Tags:

http://feedproxy.google.com/~r/securityweek/~3/s5ds0sDmUsI/datadome-raises-35-million-its-anti-bot-solution