Microsoft: Ongoing, Expanding Campaign Bypassing Phishing Protections

A phishing email campaign detailed earlier this month is expanding with the use of additional email services to hide malicious intent, according to a warning from software giant Microsoft.

Dubbed ‘Compact’ Campaign, the operation has been ongoing since December 2020, targeting thousands of users. In early March, researchers with the WMC Global Threat Intelligence Team estimated that more than 400,000 Outlook Web Access and Office 365 credentials had been compromised in multiple, connected campaigns.

At the time, the researchers revealed that the adversary behind the campaign was leveraging trusted domains to ensure that phishing emails successfully bypass email protections.

Compromised accounts at the SendGrid email delivery service were used to send many of the emails. After the researchers and SendGrid started terminating the sending accounts, the threat actor switched to MailGun to send the phishing messages.

Now, Microsoft says that the phishing messages are relying on compromised accounts on email marketing services and leverage configuration settings to bypass phishing protections that organizations might have in place.

In addition to SendGrid, the tech giant reveals, the campaign’s operators abused Amazon SES last year, and started leveraging Mailgun for the same purposes since January.

“Microsoft Defender for Office 365 data shows that this phishing operation is still active today and continues to expand,” the company said on Twitter.

“The attackers abuse another legitimate service to further mask the malicious intent of their phishing emails. To evade domain reputation-based solutions, they use Appspot to create multiple unique phishing URLs per recipient,” the tech giant added.

Microsoft also notes that Appspot has been notified on the abuse, and that the company has already confirmed that the reported URLs are malicious. Appspot already took action against the offending projects and is working with Microsoft on tracking this operation.

Some of the phishing emails used in these attacks masquerade as notifications from video conferencing services, while recent attacks spoof security solutions and productivity tools, Microsoft reveals.

“Because this campaign uses compromised email marketing accounts, we strongly recommend orgs to review mail flow rules for broad exceptions that may be letting phishing emails through,” the company concludes.

Related: Phishers Target C-Suite with Fake Office 365 Password Expiration Reports

Related: Majority of Phishing and Malware Campaigns Are Small-Scale, Short-Lived

Related: FBI Warns of Employee Credential Phishing via Phone, Chat

view counter

Ionut Arghire is an international correspondent for SecurityWeek.

Previous Columns by Ionut Arghire:
Tags:

http://feedproxy.google.com/~r/Securityweek/~3/QUshzdyYGdY/microsoft-ongoing-expanding-campaign-bypassing-phishing-protections


Vulnerabilities in TBox RTUs Can Expose Industrial Organizations to Remote Attacks

UK-based industrial automation company Ovarro recently patched a series of vulnerabilities in its TBox remote terminal units (RTUs). Cybersecurity experts say these flaws could pose a serious risk to organizations.

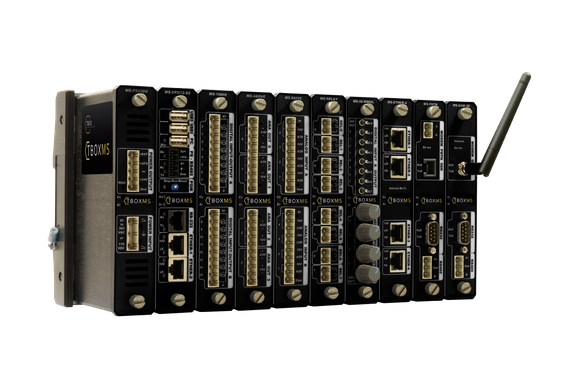
Ovarro’s TBox RTUs are described by the vendor as a remote telemetry solution for remote automation and monitoring of critical assets. These devices are used worldwide, including in the water, oil and gas, power, transportation and process industries.

Tbox RTU vulnerabilitiesResearchers at industrial cybersecurity firm Claroty discovered last year that the TBox RTUs, as well as the associated TWinSoft engineering software, are affected by five types of vulnerabilities.

Information about the vulnerabilities — all of which have been rated “high severity” — is available in a blog post published by Claroty and advisories released by the U.S. Cybersecurity and Infrastructure Security Agency (CISA) and Ovarro.

Learn More About Vulnerabilities in Industrial Products at SecurityWeek’s ICS Cyber Security Conference and SecurityWeek’s Security Summits Virtual Event Series

The vulnerabilities can allow an attacker to bypass protection features, cause a denial-of-service (DoS) condition, and execute arbitrary code on a targeted device.

“The risks associated with these flaws threaten not only the integrity of automation processes, but also, in some cases public safety,” Claroty said in its blog post. “Using these security shortcomings, we were able to find web-based interfaces, similar to HMIs, that monitor process levels and other industrial activity. We’ve seen in the past what could go wrong when such an interface is exposed to the internet without security; the fact such interfaces are exposed online removes many barriers to entry for adversaries of all types.”

The company has conducted a search for TBox RTUs and discovered that more than 62% of the systems exposed to the internet did not require authentication.

Claroty reported last month that the number of vulnerabilities discovered in industrial control system (ICS) products in 2020 increased significantly compared to previous years. The company said nearly 900 flaws were disclosed last year.

Related: Hackers Can Target Rockwell Industrial Software With Malicious EDS Files

Related: Industrial Firms Informed About Serious Vulnerabilities in Matrikon OPC Product

Related: Industrial Systems Can Be Hacked Remotely via VPN Vulnerabilities

view counter

Eduard Kovacs (@EduardKovacs) is a contributing editor at SecurityWeek. He worked as a high school IT teacher for two years before starting a career in journalism as Softpedia’s security news reporter. Eduard holds a bachelor’s degree in industrial informatics and a master’s degree in computer techniques applied in electrical engineering.

Previous Columns by Eduard Kovacs:
Tags:

http://feedproxy.google.com/~r/Securityweek/~3/md1mnuTbuKQ/vulnerabilities-tbox-rtus-can-expose-industrial-organizations-remote-attacks


Insurer CNA Says Cyberattack Caused Network Disruption

Commercial insurer CNA on Tuesday announced that it was recently targeted in what it described as a sophisticated cyberattack.

The Chicago, Illinois-based company is one of the largest commercial insurers in the United States, offering cyber insurance policies alongside a broad range of other insurance products.

In a March 23 announcement, the company revealed that, over the weekend, it fell victim to a cyberattack that impacted certain systems, and which resulted in network disruptions.

“On March 21, 2021, CNA determined that it sustained a sophisticated cybersecurity attack. The attack caused a network disruption and impacted certain CNA systems, including corporate email,” the company says in an incident notification on its website.

The insurance giant says that it has started an investigation immediately after learning of the attack, to determine the full scope of the incident. The investigation is ongoing and law enforcement has been alerted.

“Out of an abundance of caution, we have disconnected our systems from our network, which continue to function,” CNA also says.

The company also revealed that employees were notified of the attack, and that they were “provided workarounds where possible,” so that they would be able to continue operating.

CNA has yet to determine whether any information related to its clients or other type of data has been impacted in the incident.

“The security of our data and that of our insureds’ and other stakeholders is of the utmost importance to us. Should we determine that this incident impacted our insureds’ or policyholders’ data, we’ll notify those parties directly,” the company notes.

While CNA hasn’t revealed the nature of the cyber-attack, there is a possibility that the company fell victim to ransomware operators, which would explain why systems were disconnected from the network (likely to prevent further data encryption).

Related: Sierra Wireless Says Ransomware Disrupted Production at Manufacturing Facilities

Related: Information Posted Online After N Carolina Ransomware Attack

Related: Inside the Ransomware Economy

view counter

Ionut Arghire is an international correspondent for SecurityWeek.

Previous Columns by Ionut Arghire:
Tags:

http://feedproxy.google.com/~r/Securityweek/~3/W4tzFmwxvbo/insurer-cna-says-cyberattack-caused-network-disruption


Honeywell Says Malware Disrupted IT Systems

Industrial giant Honeywell on Tuesday revealed that some of its IT systems were disrupted as a result of a malware attack.

The company said the intrusion was detected “recently” and only a “limited number” of IT systems were disrupted. No other information has been provided regarding impact.

An investigation into the incident is ongoing, but Honeywell says it has found no evidence to date that the attacker managed to exfiltrate data from systems that store customer information. However, based on its statement, it cannot completely rule out that some customer data may have been compromised.

“At this time, we do not expect this incident will have a material impact on Honeywell,” the company stated. “We promptly took steps to address the incident, including partnering with Microsoft to assess and remediate the situation. Our systems have since been secured, we identified the point of entry, and all unauthorized access has been revoked.”

Law enforcement has been notified and impacted services should be working properly by now.

SecurityWeek has reached out to Honeywell to find out if the incident involved a piece of ransomware.

The news from Honeywell comes shortly after Canada-based IoT company Sierra Wireless revealed that some of its internal IT systems were recently hit by ransomware. Sierra, which also provides solutions for — among others — industrial organizations, said the incident disrupted production at manufacturing facilities.

Other major companies that recently reported disruption to production operations due to a cyberattack include beverage conglomerate Molson Coors and packaging giant WestRock.

Related: Vulnerabilities Allow Hackers to Access Honeywell Fire Alarm Systems

Related: Serious Vulnerabilities Expose Honeywell Surveillance Systems to Attacks

Related: Honeywell Sees Rise in USB-Borne Malware That Can Cause Major ICS Disruption

view counter

Eduard Kovacs (@EduardKovacs) is a contributing editor at SecurityWeek. He worked as a high school IT teacher for two years before starting a career in journalism as Softpedia’s security news reporter. Eduard holds a bachelor’s degree in industrial informatics and a master’s degree in computer techniques applied in electrical engineering.

Previous Columns by Eduard Kovacs:
Tags:

http://feedproxy.google.com/~r/Securityweek/~3/ypXgbqKDXbw/honeywell-says-malware-disrupted-it-systems


Purple Fox Malware Squirms Like a Worm on Windows

Malware hunters at Guardicore are warning that an aggressive botnet operator has turned to SMB password brute-forcing to infect and spread like a worm across the Microsoft Windows ecosystem.

The malware campaign, dubbed Purple Fox, has been active since at least 2018 and the discovery of the new worm-like infection vector is yet another sign that consumer-grade malware continues to reap profits for cybercriminals.

According to Guardicore researcher Amit Serper, the Purple Fox operators primarily used exploit kits and phishing emails to build botnets for crypto-mining and other nefarious uses.  

Now, the new SMB brute-force method is being combined with rootkit capabilities to hide and spread widely across internet-facing Windows computers with weak passwords.

“Throughout the end of 2020 and the beginning of 2021, Guardicore Global Sensors Network (GGSN) detected Purple Fox’s novel spreading technique via indiscriminate port scanning and exploitation of exposed SMB services with weak passwords and hashes,” Serper explained.

Serper said May 2020 saw a “significant amount of malicious activity” where the number of infections climbed by roughly 600% and amounted to a total of 90,000 attacks.

Serper’s blog, which contains IOCs to help defenders hunt for signs of infection, explains the aggressiveness of the malware operator:

“While it appears that the functionality of Purple Fox hasn’t changed much post exploitation, its spreading and distribution methods – and its worm-like behavior – are much different than described in previously published articles. Throughout our research, we have observed an infrastructure that appears to be made out of a hodge-podge of vulnerable and exploited servers hosting the initial payload of the malware, infected machines which are serving as nodes of those constantly worming campaigns, and server infrastructure that appears to be related to other malware campaigns.

Serper’s team at Guardicore warned that the attackers are hosting various MSI packages on nearly 2,000 servers, most of which are compromised machines which were repurposed to host malicious payloads. 

“We have established that the vast majority of the servers, which are serving the initial payload, are running on relatively old versions of Windows Server running IIS version 7.5 and Microsoft FTP, which are known to have multiple vulnerabilities with varying severity levels,” Guardicore said in a technical blog post.

The company found the campaign spreading via two distinct mechanisms — a worm payload after a victim machine is compromised through a vulnerable exposed service (such as SMB); or the worm payload is being sent via email through a phishing campaign.

The company is encouraging malware hunters to use public indicators of compromise to find signs of malicious activity related to this threat.

view counter

Ryan Naraine is Editor-at-Large at SecurityWeek and host of the popular Security Conversations podcast series. Ryan is a journalist and cybersecurity strategist with more than 20 years experience covering IT security and technology trends. He is a regular speaker at cybersecurity conferences around the world.
Ryan has built security engagement programs at major global brands, including Intel Corp., Bishop Fox and Kaspersky GReAT. He is a co-founder of Threatpost and the global SAS conference series. Ryan’s career as a journalist includes bylines at major technology publications including Ziff Davis eWEEK, CBS Interactive’s ZDNet, PCMag and PC World.
Follow Ryan on Twitter @ryanaraine.

Previous Columns by Ryan Naraine:
Tags:

http://feedproxy.google.com/~r/Securityweek/~3/w-pskMTDmDI/purple-fox-malware-squirms-worm-windows


China Slams US Plan to Expel Phone Carriers in Tech Clash

China’s government on Thursday called on Washington to drop efforts to expel three state-owned Chinese phone companies from the United States in a new clash over technology and security.

The Federal Communications Commission voted Wednesday to begin revoking the companies’ U.S. licenses. It said they are security risks controlled by the communist Beijing government.

The foreign ministry accused Washington of misusing security complaints to hurt Chinese commercial competitors.

The United States should “stop the wrong practice of generalizing the concept of national security and politicizing economic issues” and “stop abusing state power to unreasonably suppress Chinese enterprises,” said a ministry spokesman, Zhao Lijian.

The decision adds to mounting U.S.-Chinese conflict over the ruling Communist Party’s industrial plans, access to American technology and accusations of computer attacks and theft of business secrets.

President Joe Biden has said he wants a better relations with Beijing but has given no indication he will roll back sanctions imposed by his predecessor, Donald Trump, that limit Chinese access to U.S. technology and financial markets.

The latest announcement came as U.S. and Chinese envoys were flying to Alaska for the highest-level face-to-face meeting between the two sides since Biden took office in January.

Zhao said Beijing will “take necessary measures to safeguard the legitimate rights and interests of Chinese enterprises” but gave no details. Officials have issued similar warnings in the past but those usually have resulted in no action.

The latest action targets China Unicom Americas, a unit of China Unicom Ltd.; Pacific Networks Corp. and ComNet (USA) LLC, a unit of Pacific Networks. They sell international voice and data service.

The companies were ordered to explain their ownership and operations, and “failed to address the serious national security threats posed by their continued operation in the U.S.,” said Commissioner Brendan Car in a statement.

National security officials “advise that traffic on these networks ‘remains subject to exploitation, influence, and control by the Chinese government,’” Carr said. He said some Chinese telecom companies have operated in the United States for decades and “security threats have evolved substantially in the intervening years.”

Earlier, state-owned China Mobile Ltd. was blocked in 2019 from entering the U.S. market on security grounds.

Trump also blocked access to most U.S. technology for telecom equipment giant Huawei Technologies Ltd. and some other Chinese tech companies. Trump issued an order prohibiting Americans from investing in securities of companies deemed by the Pentagon to be linked to China’s military.

Related: Huawei and Supply Chain Security – The Great Geopolitical Debate

view counter

Previous Columns by Associated Press:
Tags:

http://feedproxy.google.com/~r/Securityweek/~3/84YCt4rDoGQ/china-slams-us-plan-expel-phone-carriers-tech-clash


Google: Sophisticated APT Group Burned 11 Zero-Days in Mass Spying Operation

Google has added new details on a pair of exploit servers used by a sophisticated threat actor to hit users of Windows, iOS and Android devices.

Malware hunters at Google continue to call attention to a sophisticated APT group that burned through at least 11 zero-days exploits in less than a year to conduct mass spying across a range of platforms and devices.

The group has actively used “watering hole” attacks to redirect specific targets to a pair of exploit servers delivering malware on Windows, iOS and Android devices.

The cross-platform capabilities and the willingness to use almost a dozen zero-days in less than a year signals a well-resourced actor with the ability to access hacking tools and exploits from related teams.

In a new blog post, Google Project Zero researcher Maddie Stone released additional details on the exploit chains discovered in the wild last October and warned that the latest discovery is tied to a February 2020 campaign that included the use of multiple zero-days.

According to Stone, the actor from the February 2020 campaign went dark for a few months but returned in October with dozens of websites redirecting to an exploit server. 

“Once our analysis began, we discovered links to a second exploit server on the same website. After initial fingerprinting (appearing to be based on the origin of the IP address and the user-agent), an iframe was injected into the website pointing to one of the two exploit servers. 

In our testing, both of the exploit servers existed on all of the discovered domains,” Stone explained.

The first exploit server initially responded only to Apple iOS and Microsoft Windows user-agents and was active for at least a week after Google’s researchers started retrieving the hacking tools.  This server included exploits for a remote code execution bug in the Google Chrome rendering engine and a v8 zero-day after the initial bug was patched.  

Stone said the first server briefly responded to Android user-agents, suggesting exploits existed for all the major platforms.

Google also flagged a second exploit server that responded to Android user-agents and remained alive for at least 36 hours. This server contained malware cocktails exploiting zero-days in the Chrome and Samsung browsers on Android devices. 

Interestingly, Stone noted that the attackers used a unique obfuscation and anti-analysis check on iOS devices where those exploits were encrypted with ephemeral keys, “meaning that the exploits couldn’t be recovered from the packet dump alone, instead requiring an active MITM on our side to rewrite the exploit on-the-fly.”

Stone also noted signs that multiple entities may be sharing tools and exploits in these campaigns.  

“Both exploit servers used the Chrome Freetype RCE (CVE-2020-15999) as the renderer exploit for Windows (exploit server #1) and Android (exploit server #2), but the code that surrounded these exploits was quite different. The fact that the two servers went down at different times also lends us to believe that there were two distinct operators,” Stone added.

In all, Stone and the Google Project Zero team snagged one full exploit chain hitting Chrome on Windows, two partial exploit chains targeting fully patched Android devices running Chrome and the Samsung Browser; and remote code-execution exploits for iOS 11 and iOS 13.

Stone’s analysis also show the APT group is prolific with the types of vulnerabilities used in exploit chains. “The vulnerabilities cover a fairly broad spectrum of issues – from a modern JIT vulnerability to a large cache of font bugs. Overall each of the exploits themselves showed an expert understanding of exploit development and the vulnerability being exploited,” she explained.

“In the case of the Chrome Freetype 0-day, the exploitation method was novel to Project Zero. The process to figure out how to trigger the iOS kernel privilege vulnerability would have been non-trivial. The obfuscation methods were varied and time-consuming to figure out,” she added. 

view counter

Ryan Naraine is Editor-at-Large at SecurityWeek and host of the popular Security Conversations podcast series. Ryan is a journalist and cybersecurity strategist with more than 20 years experience covering IT security and technology trends. He is a regular speaker at cybersecurity conferences around the world.
Ryan has built security engagement programs at major global brands, including Intel Corp., Bishop Fox and Kaspersky GReAT. He is a co-founder of Threatpost and the global SAS conference series. Ryan’s career as a journalist includes bylines at major technology publications including Ziff Davis eWEEK, CBS Interactive’s ZDNet, PCMag and PC World.
Follow Ryan on Twitter @ryanaraine.

Previous Columns by Ryan Naraine:
Tags:

http://feedproxy.google.com/~r/Securityweek/~3/VzPiRrEJH48/google-sophisticated-apt-group-burned-11-zero-days-mass-spying-operation


Russian Man Pleads Guilty to Role in Attempt to Plant Malware on Tesla Systems

The Russian national who attempted to convince a Tesla employee to plant malware on the company’s computers has pleaded guilty, the U.S. Justice Department announced on Thursday.

Egor Igorevich Kriuchkov, 27, has pleaded guilty to one count of conspiracy to intentionally cause damage to a protected computer. He initially faced up to five years in prison, but he will likely get a lighter sentence as a result of his plea agreement.

Kriuchkov is accused of conspiring with others to convince an employee of Tesla to plant malware on the electric car maker’s network as part of a ransomware attack. They had also planned on launching a DDoS attack to distract the company while the malware allowed them to steal valuable data.

The Russian traveled to the U.S. in July 2020 on a tourist visa and contacted the targeted Tesla employee, who was located in Nevada, shortly after.

The employee was initially offered $500,000 for his assistance, but the offer was later doubled. Even so, the employee decided to inform Tesla about the cybercriminals’ plan and the company notified the FBI, which organized a sting operation.

Kriuchkov was arrested in August 2020 and in September he pleaded not guilty. He will be sentenced on May 10.

Related: Elon Musk Confirms Russian Hackers Attempted to Recruit Tesla Employee

Related: Russian Found Guilty of Hacking LinkedIn, Formspring, Dropbox

Related: Russian Pleads Guilty in Virginia to Large-Scale Card Fraud

Related: Denmark Charges Russian Citizen With Spying for Russia

view counter

Eduard Kovacs (@EduardKovacs) is a contributing editor at SecurityWeek. He worked as a high school IT teacher for two years before starting a career in journalism as Softpedia’s security news reporter. Eduard holds a bachelor’s degree in industrial informatics and a master’s degree in computer techniques applied in electrical engineering.

Previous Columns by Eduard Kovacs:
Tags:

http://feedproxy.google.com/~r/Securityweek/~3/_eEa431-8RM/russian-man-pleads-guilty-role-attempt-plant-malware-tesla-systems


Microsoft Defender Antivirus Now Protects Users Against Ongoing Exchange Attacks

Microsoft informed customers on Thursday that Defender Antivirus and System Center Endpoint Protection now provide automatic protection against attacks exploiting the recently disclosed Exchange Server vulnerabilities.

Microsoft has released patches, detailed guidance, and a one-click mitigation tool to ensure that Exchange Server users are protected against attacks. The tech giant has now taken another step to protect customers who haven’t managed to install the available patches but who have Defender deployed on vulnerable servers.

The Exchange vulnerabilities are tracked as CVE-2021-26855, CVE-2021-26857, CVE-2021-26858 and CVE-2021-27065, and they are tracked as ProxyLogon. They can be exploited by an unauthenticated attacker to execute arbitrary code on targeted servers and gain access to emails and other sensitive information.

When Microsoft disclosed the flaws and announced patches in early March, it warned that a threat actor linked to China had been exploiting them in attacks. Roughly one week after disclosure, others reported that several cyberspy and cybercrime groups had started exploiting the vulnerabilities.

On March 12, Microsoft reported that more than 80,000 Exchange servers had still not been updated.

As threat actors increasingly start to target these vulnerabilities, Microsoft has now decided to release a security intelligence update for Defender Antivirus and System Center Endpoint Protection (build 1.333.747.0 or newer), which according to the company “breaks the attack chain by mitigating CVE-2021-26855,” the first vulnerability exploited in the ProxyLogon chain.

List of resources to help incident response teams and IT administrators respond to this global incident.

Microsoft described this as an “interim mitigation” that should help customers protect their systems until they can install the patches.

“Microsoft Defender Antivirus will automatically identify if a vulnerable version of Exchange Server is installed and apply the mitigations the first time the security intelligence update is deployed. The mitigation is deployed once per machine,” Microsoft explained.

Related: At Least 10 Threat Actors Targeting Recent Microsoft Exchange Vulnerabilities

Related: Ransomware Operators Start Targeting Microsoft Exchange Vulnerabilities

Related: Hackers Looking for Exchange Servers Affected by Recently Patched Flaw

view counter

Eduard Kovacs (@EduardKovacs) is a contributing editor at SecurityWeek. He worked as a high school IT teacher for two years before starting a career in journalism as Softpedia’s security news reporter. Eduard holds a bachelor’s degree in industrial informatics and a master’s degree in computer techniques applied in electrical engineering.

Previous Columns by Eduard Kovacs:
Tags:

http://feedproxy.google.com/~r/Securityweek/~3/T2LIwFCaheI/microsoft-defender-antivirus-now-protects-users-against-ongoing-exchange-attacks


Facebook Paid Out $50K for Vulnerabilities Allowing Access to Internal Systems

A researcher says he has earned more than $50,000 from Facebook after discovering vulnerabilities that could have been exploited to gain access to some of the social media giant’s internal systems.

Cybersecurity engineer and bug bounty hunter Alaa Abdulridha revealed in December 2020 that he had earned $7,500 from Facebook for discovering a vulnerability in a service apparently used by the company’s legal department. The researcher said the security hole could have been exploited to reset the password of any account for a web application used internally by Facebook employees.

Internal Facebook app hacked

In a blog post published on Thursday, the researcher said he continued analyzing the same application and once again managed to gain access to it. From there he claimed he was able to launch a server-side request forgery (SSRF) attack and gain access to Facebook’s internal network. Facebook described this as an attacker being able to send HTTP requests to internal systems and read their responses.

“I was able to scan the ports of the local servers and browse the local applications/web apps that the company uses in their infrastructure,” the researcher told SecurityWeek. “I’m sure such a vulnerability in the wrong hands could be escalated to RCE and can pose a huge risk for the company and its customers.”

The social media giant awarded him nearly $50,000 for this second exploit chain.

Abdulridha also claimed the account takeover attack may have allowed a hacker to access accounts for other internal Facebook applications as well, but Facebook told SecurityWeek it had not found any evidence to suggest that the flaw could be escalated to access other internal accounts.

Facebook has clarified that the vulnerabilities reported by Abdulridha actually affected a third-party service designed for signing documents and they impacted anyone using this service, not just Facebook. The company said it worked with the third-party vendor to quickly get the flaws fixed and said it had found no evidence of malicious exploitation, noting that exploiting the weaknesses was a complex task.

The company also pointed out that the first vulnerability only allowed access to accounts within the third-party document signing app, but did not grant access to any employee accounts used for other internal applications.

While the researcher claimed that it took Facebook nearly 6 months to patch the second round of vulnerabilities, the company told SecurityWeek that while the report was only closed in February, the bugs were actually completely fixed — by both Facebook and the third-party vendor — within a few days.

Facebook also said that while it paid out a bug bounty based on the maximum possible impact it could determine, it did not agree with the researcher’s belief that the SSRF vulnerabilities could have been escalated to remote code execution.

Related: Facebook Announces Payout Guidelines for Bug Bounty Program

Related: Facebook Awards Big Bounties for Invisible Post and Account Takeover Vulnerabilities

Related: Facebook Pays $60,000 for Vulnerability in Messenger for Android

view counter

Eduard Kovacs (@EduardKovacs) is a contributing editor at SecurityWeek. He worked as a high school IT teacher for two years before starting a career in journalism as Softpedia’s security news reporter. Eduard holds a bachelor’s degree in industrial informatics and a master’s degree in computer techniques applied in electrical engineering.

Previous Columns by Eduard Kovacs:
Tags:

http://feedproxy.google.com/~r/Securityweek/~3/4qCvsGF0k4U/facebook-paid-out-50k-vulnerabilities-allowing-access-internal-systems