Here’s How Security Flaws in GE Relays Could Be Exploited in Real World Attacks

Organizations using Universal Relay (UR) products made by GE’s Grid Solutions have been informed this week that many of the devices in this product line are affected by nearly a dozen vulnerabilities.

Grid Solutions is a GE Renewable Energy business that provides electricity management solutions for the energy sector, including oil and gas, as well as industry and infrastructure organizations.

Advisories published this week by the U.S. Cybersecurity and Infrastructure Security Agency (CISA) and GE Grid Solutions (account required) inform customers that more than a dozen UR protection and control relays are impacted by a series of vulnerabilities to which 10 different CVE identifiers have been assigned. The vendor has released firmware updates that should patch the vulnerabilities.
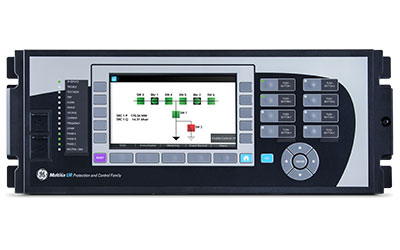
GE grid relay vulnerabilitiesThe flaws are related to inadequate encryption of communications, exposure of potentially sensitive information, cross-site scripting (XSS) attacks, denial-of-service (DoS) attacks, unauthorized firmware uploading, the inability to disable a factory service mode, and the presence of hardcoded credentials in the bootloader. More than half of the vulnerabilities have a severity rating of high or critical.

Researchers from SCADA-X, Verve Industrial, VuMetric and the Department of Energy’s Cyber Testing for Resilient Industrial Control Systems (CyTRICS) program have been credited for finding the security holes.

Ron Brash, director of cyber security insights at ICS management and cybersecurity provider Verve Industrial Protection, told SecurityWeek that he has identified two or possibly three of the vulnerabilities — he says it’s difficult to say exactly due to multiple disclosures and some likely overlap. These include flaws that can be exploited to upload malicious firmware to the device, obtain potentially sensitive information, and access a device or disrupt it.

According to Brash, exploitation of these vulnerabilities requires direct or network access to the targeted system.

“Generally these devices are not found on the Internet directly unless someone has not applied any secure deployment strategies, or has inadvertently misconfigured various network infrastructure devices/security apparatuses,” he explained.

Learn more about vulnerabilities in industrial systems at SecurityWeek’s ICS Cyber Security Conference and SecurityWeek’s Security Summits virtual event series

In terms of impact, the expert pointed out that while the vulnerable relays are used within the energy industry, they are not limited to the “grid.”

“For example, a mine may be generating power, and these types of devices might be present,” Brash explained. “This can mean that the results or motivations of what ‘an attacker could do’ might be situationally dependent, or require specific contexts. Therefore, in continuation of the example, if your mine needs energy to keep liquids unfrozen (e.g., washes, effluent management systems, etc), and the mine is located in Canada’s North, then you might have a BIG problem during winter. Secondly, if you can get access to these devices, and upload your own logic or firmware, then you can effectively brick them, upload malicious functionality, and the consequences will be highly negative.”

He added, “I don’t wish to speculate as to the motives, or what could be accomplished by an attacker, but if exploited at scale (which by the way, takes a great level of skill, budget, and organization) – nothing positive would result.”

Contacted by SecurityWeek, GE said it’s currently not aware of any attacks exploiting these vulnerabilities.

“GE was made aware of vulnerabilities related to GE’s Grid Solutions’ Universal Relay (UR) family products and immediately worked to assess any potential impact and remediate the reported vulnerabilities. GE’s UR firmware Version 8.10 and greater resolve the identified vulnerabilities, and we encourage our customers to visit the Grid Solutions customer portal and/or the CISA Advisory for additional information and mitigation recommendations,” said a GE spokesperson.

Related: Critical Flaw in GE Protection Relays Exposes Power Grid

Related: Over 100 GE Healthcare Devices Affected by Critical Vulnerability

Related: Open Source Tool Helps Organizations Secure GE CIMPLICITY HMI/SCADA Systems

view counter

Eduard Kovacs (@EduardKovacs) is a contributing editor at SecurityWeek. He worked as a high school IT teacher for two years before starting a career in journalism as Softpedia’s security news reporter. Eduard holds a bachelor’s degree in industrial informatics and a master’s degree in computer techniques applied in electrical engineering.

Previous Columns by Eduard Kovacs:
Tags:

http://feedproxy.google.com/~r/Securityweek/~3/Z6dFJUL__NY/heres-how-recently-patched-ge-relay-flaws-could-be-exploited-real-world-attacks


US Charges Swiss ‘Hacktivist’ for Data Theft and Leaks

The Justice Department has charged a Swiss hacker with computer intrusion and identity theft, just over a week after the hacker took credit for helping to break into the online systems of a U.S. security-camera startup.

An indictment against 21-year-old Till Kottmann was brought Thursday by a grand jury in the Seattle-based Western District of Washington.

Federal prosecutors said Thursday that Kottmann, of Lucerne, Switzerland, was initially charged in September. The range of allegations date back to 2019 and involve stealing credentials and data and publishing source code and proprietary information from more than 100 entities, including companies and government agencies.

Kottmann had described the most recent hack and leak of camera footage from customers of California security-camera provider Verkada as part of a “hacktivist” cause of exposing the dangers of mass surveillance.

Acting U.S. Attorney Tessa Gorman rejected those motives in a statement Thursday.

“These actions can increase vulnerabilities for everyone from large corporations to individual consumers,” Gorman wrote. “Wrapping oneself in an allegedly altruistic motive does not remove the criminal stench from such intrusion, theft, and fraud.”

Kottmann didn’t immediately return an online request for comment Thursday.

Swiss authorities said they had raided Kottmann’s home in Lucerne late last week at the request of U.S. authorities. It’s not clear if U.S. prosecutors intend to extradite Kottmann, who remains in Lucerne and was notified of the pending charges. Prosecutors say the FBI recently seized a website domain that Kottmann used to publish hacked data online.

The indictment ties a number of hacks to Kottmann over the past year, including one targeting an unnamed security device manufacturer based in the Seattle region and another affecting a maker of tactical equipment.

In several cases, prosecutors said Kottmann improperly used valid employee credentials to gain access to source code databases. The indictment says Kottmann also hacked the Washington state Department of Transportation, an automobile manufacturer and a financial investment company.

The indictment doesn’t specifically mention last week’s high-profile hack of Verkada, which drew attention because it exposed live camera feeds and archived video footage from schools, jails, factories, gyms and corporate offices.

Kottmann, who uses they/them pronouns, told The Associated Press last week they belonged to a group nicknamed APT-69420 Arson Cats, a small collective of “primarily queer hackers, not backed by any nations or capital but instead backed by the desire for fun, being gay and a better world.”

Kottmann has previously attracted attention for leaking hacked material to expose security flaws, including from U.S. chipmaker Intel last year.

The indictment attempts to tie Kottmann’s efforts at self-promotion, including designing and selling clothing related to hacking and “anti-intellectual-property ideology,” into part of a broader conspiracy to commit computer fraud.

view counter

Previous Columns by Associated Press:
Tags:

http://feedproxy.google.com/~r/Securityweek/~3/g3bcq1mJIKQ/us-charges-swiss-%E2%80%98hacktivist%E2%80%99-data-theft-and-leaks


Finland IDs Hackers Linked to Parliament Spying Attack

Finland’s domestic security agency said Thursday that the cybergroup APT31, which is generally linked to the Chinese government, was likely behind a cyberspying attack on the information systems of the Nordic country’s parliament.

The Finnish Security and Intelligence Service, known by the abbreviation Supo, said it had “identified a cyber espionage operation targeted in 2020 against parliament with the aim of intruding into parliament’s IT systems.”

The agency added that “according to Supo intelligence, APT31 was responsible for the attack”. It didn’t mention China by name or the group’s alleged links to the government in Beijing. The statement posted also on the agency’s Twitter site in English.

Finland’s National Bureau of Investigation, NBI, said late December that it had started an investigation into suspected gross hacking and espionage attacks on the information systems of Eduskunta, the Finnish legislature. Among other things, some lawmakers’ email accounts were compromised.

Parliament has since upgraded the systems’ security features.

NBI’s Tero Muurman, who is in charge of the investigation, said Thursday his agency was probing further Supo’s allegation of APT31′s involvement. He said the breach likely aimed to “acquire information for the benefit of a foreign nation or to harm Finland.”

FireEye, one of the world’s major cybersecurity firms, and other data security firms have linked APT31 to the Chinese government or operations conducted on its orders.

APT is an abbreviation for “advanced persistent threat,” a general term to describe an attack in which an intruder — or intruders — establishes an illicit and usually long-term presence on a network to acquire highly sensitive data.

Earlier this month, Supo said that the intelligence services of foreign powers have expanded their cyber espionage operations in Finland during the COVID-19 pandemic through either directly targeting Finnish organizations or using Finnish infrastructure.

The agency has earlier named China and Russia as being the most active countries spying on Finland.

Arctic issues is an area of particular interest to China in the Nordic countries.

The Finnish public broadcaster YLE reported earlier March that the state-funded Polar Research Institute of China attempted in 2018 to buy or lease an airport near the small northern town of Kemijarvi in the Lapland area, Finland’s Arctic region, for research flights over the North Pole and other Arctic regions. The Finnish military, however, blocked the deal on security concerns, as the airport is close to a military area.

The parliament of Norway, Finland’s Nordic neighbor, was hit by a cyberattack last year that the country’s domestic security agency said was probably done by the hacking group APT28, which has been linked to Russia’s GRU military intelligence agency.

Related: Finland to Investigate Suspected Nokia Chinese Data Breach

view counter

Previous Columns by Associated Press:
Tags:

http://feedproxy.google.com/~r/Securityweek/~3/A0vwQYUzY8E/finland-ids-hackers-linked-parliament-spying-attack


New XcodeSpy Mac Malware Targets Software Developers

A recently discovered Mac malware has been used by unknown threat actors to target software developers who use Apple’s Xcode integrated development environment.

Endpoint security company SentinelOne reported on Thursday that the malware, which it has named XcodeSpy, appears to deliver a custom variant of a backdoor known as EggShell, which allows its operators to spy on users. The backdoor can be used to upload and download files, and capture data from the victim’s camera, microphone and keyboard.

SentinelOne learned about the malware from an anonymous researcher, but the company also spotted XcodeSpy in the wild in late 2020 at an organization in the United States. This victim told SentinelOne that it’s regularly targeted by threat actors linked to North Korea and they came across the malware while conducting threat hunting activities.

Based on samples uploaded to VirusTotal, the malware may have also been used in attacks aimed at developers in Japan.

The cybersecurity firm has found evidence that the campaign involving XcodeSpy was active at least between July and October 2020. In at least one instance, the malware was delivered as a trojanized version of an open source Xcode project offered to iOS developers.

“The XcodeSpy version has been subtly changed to execute an obfuscated Run Script when the developer’s build target is launched,” SentinelOne explained in its blog post. “The script contacts the attackers’ C2 and drops a custom variant of the EggShell backdoor on the development machine.”

The company has not found any other trojanized Xcode projects, but believes that other similar malicious projects could exist.

“While XcodeSpy appears to be directly targeted at the developers themselves rather than developers’ products or clients, it’s a short step from backdooring a developer’s working environment to delivering malware to users of that developer’s software,” SentinelOne said.

This is not the first piece of malware that has been observed targeting Xcode developers. Back in 2015, a threat named XcodeGhost had allowed attackers to inject malicious code into hundreds of legitimate applications using rogue versions of Xcode that developers downloaded from third-party websites.

More recently, a piece of Mac malware named XCSSET was seen spreading through code injected into Xcode projects, with the payload being executed when the project was built. XCSSET allows its operators to launch ransomware attacks and steal data from victims. It was recently analyzed by researchers at Kaspersky, who discovered a variant designed to run on devices powered by Apple’s M1 chip.

Related: Several New Mac Malware Families Attributed to North Korean Hackers

Related: ThiefQuest Mac Malware Includes Ransomware, Data Theft Capabilities

Related: Repurposing Mac Malware Not Difficult, Researcher Shows

view counter

Eduard Kovacs (@EduardKovacs) is a contributing editor at SecurityWeek. He worked as a high school IT teacher for two years before starting a career in journalism as Softpedia’s security news reporter. Eduard holds a bachelor’s degree in industrial informatics and a master’s degree in computer techniques applied in electrical engineering.

Previous Columns by Eduard Kovacs:
Tags:

http://feedproxy.google.com/~r/Securityweek/~3/ZgybnsoXWu4/new-xcodespy-mac-malware-targets-software-developers


Five Months After Takedown Attempt, CISA and FBI Warn of Ongoing TrickBot Attacks

Attacks employing the TrickBot malware continue, leveraging phishing emails as the initial infection vector, the Cybersecurity and Infrastructure Security Agency (CISA) and Federal Bureau of Investigation (FBI) warn.

In a joint advisory published on Wednesday, the two agencies revealed that a sophisticated group of cybercrime actors is leveraging a traffic infringement phishing scheme to lure victims into downloading the TrickBot malware.

Initially observed in 2016 and believed to be the work of the threat actors behind the Dyre Trojan, TrickBot has become one of the most prevalent malware families out there, ensnaring machines into a botnet that was being offered under a malware-as-a-service model to both nation-states and cyber-crime groups.

In October 2020, Microsoft announced the takedown of the infrastructure behind TrickBot, but the malware survived the attempt. In fact, weeks later, it received several updates that increased its resilience against similar attempts and also provided it further compromise capabilities.

Now, CISA and the FBI reveal they have observed “continued targeting through spearphishing campaigns using TrickBot malware in North America,” thus confirming that TrickBot’s operators were able to restore their malicious operation.

“CISA and FBI are aware of recent attacks that use phishing emails, claiming to contain proof of a traffic violation, to steal sensitive information. The phishing emails contain links that redirect to a website hosted on a compromised server that prompts the victim to click on photo proof of their traffic violation,” the joint advisory reads.

Once the victim clicks on the image, however, a malicious JavaScript file is downloaded. When executed, the file connects to the attackers’ command and control (C&C) server to fetch and run TrickBot on the victim’s system.

A modular piece of malware, TrickBot is capable of stealing information from the victims’ browsers, spread laterally across the network, gather system information, manipulate system data, exfiltrate information, mine for crypto-currency, search for vulnerabilities in system firmware, and drop additional payloads onto the system, such as Emotet or the Ryuk and Conti ransomware.

In their joint advisory, CISA and FBI included a series of recommendations for network defenders looking to improve their security posture and stay better protected against TrickBot attacks. The recommendations apply to security teams at federal, state, local, tribal, and territorial governments, but also to those in the private sector.

Related: CISA Issues Advisory for High-Severity Vulnerabilities in Fuji Electric HMI Products

Related: CISA Says Many Victims of SolarWinds Hackers Had No Direct Link to SolarWinds

Related: CISA Warns Organizations About Attacks on Cloud Services

view counter

Ionut Arghire is an international correspondent for SecurityWeek.

Previous Columns by Ionut Arghire:
Tags:

http://feedproxy.google.com/~r/Securityweek/~3/XE-TEJGZpmI/five-months-after-takedown-attempt-cisa-and-fbi-warn-ongoing-trickbot-attacks


Facebook Now Lets Mobile Users Secure Accounts with Security Keys

Social media and advertising giant Facebook today announced that it is now allowing mobile users to secure their accounts with the help of security keys.

Available for Facebook’s desktop users since 2017, the authentication method requires that the user confirm authentication requests with the help of a physical security key.

This additional authentication step is meant to significantly increase account protection, as it relies on the use of a physical device that an attacker is assumed to never have access to.

“Starting today, you can set up two-factor authentication and log into Facebook on iOS and Android mobile devices using a security key, available to anyone in the world,” Facebook announced.

Two-factor authentication (2FA) has evolved from codes sent via SMS or email to the use of authenticator applications and security keys, making it increasingly difficult for a threat actor to come in the possession of both the account password and the second factor.

Since 2017, Facebook has been providing users the option to enable 2FA and choose physical security keys as the second authentication factor, with that feature now available for iOS and Android users as well.

Users who may need such strong authentication protection are those most exposed to malicious attacks, including public figures, politicians, journalists, and human rights defenders, among others.

“We strongly recommend that everyone considers using physical security keys to increase the security of their accounts, no matter what device you use,” Facebook says.

Security keys can be connected either via Bluetooth or can be directly plugged into phones.

To enable the use of security keys as the authentication method, Facebook users should head over to the Security and Login section of the Settings menu.

The social platform also says it plans to expand the availability of its Facebook Protect program to include additional at-risk groups, alongside political campaigns and candidates.

Related: Twitter Users Can Now Secure Accounts With Multiple Security Keys

Related: New YubiKey 5C NFC Security Key Brings NFC, USB-C Connections 

view counter

Ionut Arghire is an international correspondent for SecurityWeek.

Previous Columns by Ionut Arghire:
Tags:

http://feedproxy.google.com/~r/Securityweek/~3/14vNnXceNuw/facebook-now-lets-mobile-users-secure-accounts-security-keys


Healthcare IoT Security Firm Cylera Closes $10 Million Series A Round

Healthcare IoT cybersecurity and intelligence provider Cylera today announced that it has raised $10 million in Series A funding. To date, the company has secured $17 million in funding.

Founded in 2017 and headquartered in New York City, Cylera seeks to protect both healthcare organizations and patients, providing a security and analytics platform that aims to deliver asset management, risk analysis, and threat detection for IoT, ICS, and IoMT (Internet of Medical Things).

Cylera seeks to secure the entire connected environment, providing insights and recommendations that simplify response, accelerate remediation, and improve the decision making process.

Cylera’s Series A funding round was led by Concord Health Partners and Maverick Ventures. Previous investors include Dreamit Ventures, Great Oaks Venture Capital, Red Bear Angels, and Samsung NEXT.

The funds will help the company expand to new global markets, as well as make its technology available for new verticals. Furthermore, Cylera plans to expand its research and development, customer success, channel support, and sales and marketing teams.

“Over the past year there has been a further acceleration of the digitalization and adoption of IoT devices across hospitals, pharmaceutical companies, biotech, life sciences and manufacturing in an effort to decrease operational risk and increase efficiencies. […] With our latest round of funding, Cylera is fueling the next phase of innovation to safeguard organizations against attacks on connected devices,” Cylera co-founder and CEO Timur Ozekcin said.

Related: HD Moore Banks $5M Funding for Rumble Asset Management

Related: Aqua Security Hits Unicorn Status After $135 Million Funding Round

Related: Cyber Insurance Company Coalition Raises $175 Million

view counter

Ionut Arghire is an international correspondent for SecurityWeek.

Previous Columns by Ionut Arghire:
Tags:

http://feedproxy.google.com/~r/Securityweek/~3/a5KE8ovM3a0/healthcare-iot-security-firm-cylera-closes-10-million-series-round


FBI: Cybercrime Victims Reported Losses of $4.2 Billion in 2020

Internet Crime Report for 2020

The FBI this week published its Internet Crime Report for 2020, and the agency said it received nearly 800,000 cybercrime complaints last year, with reported losses totaling $4.2 billion.

The number of complaints received by the FBI in 2020 increased significantly compared to the previous year, when it got roughly 467,000 complaints. The total reported losses for 2019 were approximately $3.5 billion. Since 2016, reported losses total $13.3 billion, the agency said.

The FBI said its Recovery Asset Team, which it established in 2018 to help victims recover their money from banks, had a success rate of 82% last year, managing to get banks to freeze $380 million.

In 2020, the law enforcement agency received 240,000 complaints related to phishing, vishing or smishing. Many complaints, more than 108,000, were related to non-payment or non-delivery schemes. Other types of crimes with many complaints include extortion (76,000), personal data breach (45,000), identity theft (43,000), and spoofing (28,000). The smallest number of complaints was related to hacktivists, with only 52 complaints.

In addition to the United States, many complaints came from victims in the UK, Canada, India, Greece, Australia, South Africa, France, Germany, Mexico and Belgium.

Unsurprisingly, the highest losses were reported as a result of business email compromise (BEC) and email account compromise (EAC) scams, totaling $1.8 billion, followed by confidence fraud and romance scams ($600 million), and investment scams ($336 million).

In the case of ransomware attacks, the FBI received 2,400 complaints, with reported losses of nearly $30 million, but the organization pointed out that this does not include estimates of lost business, wages, time, or remediation services purchased by the victim as a result of the attack.

There has been a significant increase in complaints related to phishing and non-payment/non-delivery schemes. In the case of non-payment scams, losses increased from $196 million to $265 million, but losses remained roughly the same in the case of phishing attacks. The losses reported as a result of tech support scams, however, nearly tripled from 2019 to 2020.

The complete 2020 Internet Crime Report is available in the website of the Internet Crime Complaint Center.

Related: BEC Losses Surpassed $1.7 Billion in 2019: FBI

Related: FBI Warns of Employee Credential Phishing via Phone, Chat

Related: FBI Official: Number of Coronavirus Cyber Complaints on Rise

view counter

Eduard Kovacs (@EduardKovacs) is a contributing editor at SecurityWeek. He worked as a high school IT teacher for two years before starting a career in journalism as Softpedia’s security news reporter. Eduard holds a bachelor’s degree in industrial informatics and a master’s degree in computer techniques applied in electrical engineering.

Previous Columns by Eduard Kovacs:
Tags:

http://feedproxy.google.com/~r/Securityweek/~3/poQ4jlzA0rc/fbi-cybercrime-victims-reported-losses-42-billion-2020


U.S. Says Russia, Iran Attempted Interference in 2020 Presidential Election

A declassified joint report from several United States agencies assesses that Russian and Iranian threat actors did attempt to meddle in the 2020 U.S. presidential election, but claims that the technical integrity of the voting process wasn’t affected.

The declassified version of the report includes key judgments from the classified report to the president, but without full supporting information and without providing details on specific intelligence methods, reports, and sources.

The joint report is meant to provide information on the extent to which foreign actors attempted interference with the 2020 U.S. elections, along with details on whether these adversaries targeted political organizations, campaigns, or election candidates, and an assessment on whether the attacks were able to successfully compromise the targeted infrastructure.

Without attempting to assess the effect of foreign interference on public perception or on the behavior of voters, the joint report reveals that there’s no evidence that foreign government-affiliated actors were able to prevent or alter votes, or disrupt the ability to tally votes or deliver election results, or compromised the integrity of voter registration information.

However, Russian and Iranian adversaries did target critical infrastructure sectors and successfully compromised “the security of several networks that managed some election functions.” The integrity of voter data and the technical aspect of the voting process, however, were not impacted.

“We identified several incidents when Russian, Chinese, and Iranian government-affiliated actors materially impacted the security of networks associated with or pertaining to US political organizations, candidates, and campaigns during 2020 federal elections,” the Department of Justice (DOJ) and the Department of Homeland Security (DHS) say.

According to the report, the Kremlin authorized influence operations that sought to denigrate President Biden’s candidacy, undermine people’s confidence in the election process, or support former President Trump. However, there were no persistent attempts from Russian actors to compromise the election infrastructure, the report reveals.

State-sponsored Iranian threat actors, the report claims, engaged in an influence campaign meant to “undercut former President Trump’s reelection prospects” and undermine confidence in the election process.

China, on the other hand, “did not deploy interference efforts and considered but did not deploy influence efforts intended to change the outcome of the U.S. Presidential election,” the report reads. The reason, the agencies say, was that China was looking to strengthen its relations with the U.S.

Other foreign actors, such as Lebanese Hizballah, Cuba, and Venezuela, also made small attempts to influence the elections, mainly driven by financial reasons. However, they are believed to have failed in their attempts, despite public claims, the report reads.

“We have no evidence—not through intelligence collection on the foreign actors themselves, not through physical security and cybersecurity monitoring of voting systems across the country, not through post-election audits, and not through any other means—that a foreign government or other actors compromised election infrastructure to manipulate election results,” the DoJ and DHS say.

Regardless, the agencies do make a series of recommendations on how to improve the overall resilience of the electoral process to interference attempts, including through cyber and physical security hygiene, management of third-party vendor security and supply-chain risks, and public messaging and education.

Related: Report Highlights Cyber Risks to US Election Systems

Related: Trump Fires Head of DHS Election Security Agency

Related: Russian Election Threat Potent, But Interference So Far Slim

view counter

Ionut Arghire is an international correspondent for SecurityWeek.

Previous Columns by Ionut Arghire:
Tags:

http://feedproxy.google.com/~r/Securityweek/~3/bXbyzcjJiL0/us-says-russia-iran-attempted-interference-2020-presidential-election


Identity Verification Company Socure Raises $100 Million at $1.3 Billion Valuation

Digital identity verification firm Socure this week announced raising $100 million in a Series D funding round.

The round, which brings the total invested into the company to $196 million, was led by Accel, with participation from Commerce Ventures, Scale Venture Partners, Flint Capital, Citi Ventures, Wells Fargo Strategic Capital, Synchrony, Sorenson, and Two Sigma Ventures, among others.

Socure says it will use the money to support its expansion and accelerate product development.

“The COVID-19 year accelerated our global shift to a digital-first economy and with that came security challenges,” said Amit Jhawar, Partner at Accel. “The Socure team accurately predicted the immediate need for identity verification solutions in industries like banking and fintech, and we’re excited by the tremendous opportunity as Socure expands to support new industries.”

Following this funding round, the company has been valued at $1.3 billion, which technically makes it a so-called “unicorn.”

The term “unicorn” was originally assigned to companies that had a valuation of over $1 billion because they were so rare. However, in the past four months alone, at least nine security companies (Aqua, Axonius, BigID, Coalition, Forter, Lacework, OwnBackup, Venafi, Wiz) announced valuations exceeding $1 billion, which means unicorns are not that rare anymore.

Socure provides a predictive analytics platform that leverages AI, machine learning and data intelligence to verify identities in real time. The solution is designed to help organizations detect identity fraud risk, eliminate synthetic identity fraud, meet compliance requirements, and perform risk-based document verification.

The company claims to have more than 350 customers in the financial services, telecom, gaming and e-commerce sectors.

Related: Anti-Fraud Platform Provider SpyCloud Raises $30 Million

Related: Beyond Identity Raises $75 Million to Expand Passwordless Identity Platform

Related: Enterprise Identity Protection Firm Semperis Raises $40 Million

Related: Strata Raises $11 Million to Tackle Multi-Cloud Identity Management

view counter

Eduard Kovacs (@EduardKovacs) is a contributing editor at SecurityWeek. He worked as a high school IT teacher for two years before starting a career in journalism as Softpedia’s security news reporter. Eduard holds a bachelor’s degree in industrial informatics and a master’s degree in computer techniques applied in electrical engineering.

Previous Columns by Eduard Kovacs:
Tags:

http://feedproxy.google.com/~r/Securityweek/~3/S2yW9OsHqsc/identity-verification-company-socure-raises-100-million-13-billion-valuation