US Moves Closer to Retaliation Over Hacking as Cyber Woes Grow

A senior US official said Friday the Biden administration is close to a decision on retaliation for state-sponsored hacking as fears grew over the fallout from the latest of two major cyberattacks.

The official said the White House was working closely with the private sector to ramp up cyber defenses following the attacks which targeted Microsoft Exchange servers and SolarWinds security software, potentially compromising thousands of government and private computer networks.

US officials had previously hinted at moves against Russia, which has been linked to the massive SolarWinds hack that shook the government and corporate security last year. The latest comments suggested forthcoming actions.

“You can expect further announcements on that in weeks, not months,” the senior official said, in reference to SolarWinds, in a briefing with reporters on the two hacking incidents.

The official, who asked not to be identified, said federal agencies had made progress in patching systems at nine federal agencies affected by the SolarWinds attack.

But an urgent effort is underway to remedy the Microsoft Exchange hack, which opened security holes that are actively being exploited by cybercriminals and others.

To help find solutions, “for the first time we’ve invited private sector companies to participate” in key national security meetings on the attacks, the official said.

The response “is still evolving,” according to the official, who noted: “We really have a short window to get vulnerable servers patched, measured in hours, not days.”

– New ransomware emerges –

The comments came as a new strain of ransomware has emerged which exploits a security flaw in Microsoft Exchange servers, signaling potentially damaging consequences from the high-profile hack.

Microsoft and other security researchers said the new ransomware dubbed “DearCry” was showing up in servers affected by the breach attributed to a Chinese hacker group.

“We have detected and are now blocking a new family of ransomware being used after an initial compromise of unpatched on-premises Exchange Servers,” said a tweet from Microsoft Security Intelligence.

Other researchers including Michael Gillespie, founder of the ID Ransomware service, noted the new strain of malware on Thursday, which could lead to a new wave of attacks that encrypt computer systems and seek to extract payments from operators.

This is the latest sign that the security flaw which became public this month could open the door to a variety of hackers, cybercriminals and cyberespionage operators.

“While patching to prevent compromises will be easy, remediating any systems that have already been compromised will not,” said Brett Callow of the security firm Emsisoft.

“At this point, it’s absolutely critical that governments quickly come up with a strategy to help organizations secure their Exchange servers and remediate any compromises before an already bad situation becomes even worse.”

Earlier this week the FBI and Department of Homeland Security warned that the Exchange server vulnerability may be exploited for nefarious purposes.

A joint statement by the agencies said that “adversaries could exploit these vulnerabilities to compromise networks, steal information, encrypt data for ransom, or even execute a destructive attack.”

The DHS Cybersecurity and Infrastructure Security Agency has been pressing for patches to be applied to networks in both government and the private sector.

The potentially devastating hack is believed to have affected at least 30,000 Microsoft email servers in government and private networks and has prompted calls for a firm response to state-sponsored attacks which could involve “hacking back” or other measures.

Related: Ransomware Operators Start Targeting Microsoft Exchange Vulnerabilities

Related: At Least 10 Threat Actors Targeting Recent Microsoft Exchange Vulnerabilities

view counter

© AFP 2020

Previous Columns by AFP:
Tags:

http://feedproxy.google.com/~r/Securityweek/~3/XJGVentzPC0/us-moves-closer-retaliation-over-hacking-cyber-woes-grow


Mac Malware ‘XCSSET’ Adapted for Devices With M1 Chips

An increasing number of Mac malware developers have started creating variants that are specifically designed to run on devices powered by Apple’s M1 chip.

Apple unveiled its M1 system-on-chip in November 2020 and the first malware created specifically for systems with the arm64 CPU architecture used by the M1 was apparently created in December. This was a variant of Pirrit, a piece of adware that has been around for several years.

A few days after the existence of this Pirrit variant came to light, managed detection and response firm Red Canary reported identifying a mysterious piece of Mac malware that had infected tens of thousands of devices around the world. This malware, named Silver Sparrow, also had a variant specifically designed for M1 systems.

Kaspersky reported on Friday that it too has spotted a piece of malware with a variant compiled for devices with M1 chips, specifically a variant of the malware known as XCSSET.

XCSSET is a mysterious piece of malware first detailed by Trend Micro and Mac security company Intego in August 2020. It does not appear to have been linked to any known threat group or activity, but a majority of infections spotted at the time were in China and India.

The malware is designed to allow its operator to launch ransomware attacks (i.e. encrypt files and display a ransom note), and steal information from infected devices, including data associated with the Evernote, Skype, Notes, QQ, WeChat, and Telegram apps.

It can also launch universal cross-site scripting (UXSS) attacks in an effort to inject arbitrary JavaScript code into the websites visited by the victim. This allows it to modify sites, including replacing cryptocurrency addresses, and phish credentials and payment card information.

XCSSET spreads through code injected into projects for Xcode, Apple’s integrated development environment. The payload is executed when the project is built.

Kaspersky has seen an XCSSET sample compiled for the arm64 architecture. This sample was uploaded to the VirusTotal malware analysis service on February 24, which has led the company’s researchers to believe that the campaign is likely still ongoing.

Kaspersky noted that in many cases Mac malware is delivered in the Mach-O format, which includes the malicious code compiled for several architectures — depending on what type of device the malware lands on, the code corresponding to that architecture is executed.

“With the new M1 chip, Apple has certainly pushed its performance and energy saving limits on Mac computers, but malware developers kept an eye on those innovations and quickly adapted their executables to Apple Silicon by porting the code to the ARM64 architecture,” Kaspersky researchers wrote in a blog post.

They added, “We have observed various attempts to port executables not just among typical adware such as Pirrit or Bnodlero samples, but also among malicious packages, such as the Silver Sparrow threat and XCSSET downloadable malicious modules. This certainly will give a kickstart to other malware adversaries to begin adapting their code for running on Apple M1 chips.”

Related: Several New Mac Malware Families Attributed to North Korean Hackers

Related: ThiefQuest Mac Malware Includes Ransomware, Data Theft Capabilities

Related: Repurposing Mac Malware Not Difficult, Researcher Shows

view counter

Eduard Kovacs (@EduardKovacs) is a contributing editor at SecurityWeek. He worked as a high school IT teacher for two years before starting a career in journalism as Softpedia’s security news reporter. Eduard holds a bachelor’s degree in industrial informatics and a master’s degree in computer techniques applied in electrical engineering.

Previous Columns by Eduard Kovacs:
Tags:

http://feedproxy.google.com/~r/Securityweek/~3/KxGkCruqoRw/mac-malware-xcsset-adapted-devices-m1-chips


Ransomware Operators Start Targeting Microsoft Exchange Vulnerabilities

In addition to state-sponsored threat actors, the recently disclosed vulnerabilities affecting Microsoft Exchange Server are now being targeted by ransomware operators.

A total of four critical zero-day vulnerabilities that are collectively referred to as ProxyLogon were patched in Exchange Server at the beginning of this month, and activity surrounding the bugs has only intensified since.

This week, ESET revealed that it has identified at least 10 threat actors that are attempting to exploit these vulnerabilities in their attacks, including Calypso, LuckyMouse (also tracked as APT27), Mikroceen, ShadowPad, Tick (also known as Bronze Butler), Tonto Team (CactusPete), Websiic, Winnti Group (BARIUM, APT41), and DLTMiner.

Some of these threat actors had been targeting the vulnerabilities before Microsoft released patches for them, while others have been picking up exploits for them after that.

Now, security researchers say that ransomware operators too are starting to target these vulnerabilities in their attacks. According to Microsoft security researcher Phillip Misner, the attacks are hands-on-keyboard and not automated.

“Microsoft observed a new family of human operated ransomware attack customers – detected as Ransom:Win32/DoejoCrypt.A. Human operated ransomware attacks are utilizing the Microsoft Exchange vulnerabilities to exploit customers,” Misner said on Twitter.

The ransomware family used in these attacks is also referred to as DearCry, and Microsoft’s researchers are not the only ones to notice the activity.

Thousands of Exchange servers are believed to be vulnerable to attacks, and at least hundreds of them have already been compromised since the attacks started. This week, the FBI and CISA issued a joint advisory to warn of these attacks.

“Unfortunately, we recently became aware of several hundred organizations in Switzerland that got compromised by a threat actor that exploited the said vulnerability,” the Swiss Government Computer Emergency Response Team (GovCERT.ch) said earlier this week.

“As a result, we have started informing possible compromised organizations based on information provided to us by trusted third parties,” GovCERT.ch added.

Amid increasingly numerous reports of attacks on Exchange servers, a Vietnamese independent security researcher, Nguyen Jang, this week published proof-of-concept code exploiting the vulnerabilities, only to see it removed from the Microsoft-owned software development platform GitHub several hours later.

SecurityWeek has contacted Microsoft for a comment on the removal of the PoC and will update the article as soon as a reply arrives.

Related: Microsoft Shares Additional Mitigations for Exchange Server Vulnerabilities Under Attack

Related: Disruptions at Pan-American Life Likely Caused by Ransomware

view counter

Ionut Arghire is an international correspondent for SecurityWeek.

Previous Columns by Ionut Arghire:
Tags:

http://feedproxy.google.com/~r/Securityweek/~3/yKbRo1y3XI4/ransomware-operators-start-targeting-microsoft-exchange-vulnerabilities


Breach Exposes Data of 200K Health System Staff, Patients

A medical practice management firm that provides support to Tacoma-based MultiCare Health System has alerted over 200,000 patients, providers and staff that their personal information may have been exposed.

Woodcreek Provider Services announced Tuesday that after a ransomware attack of its tech vendor, the information was retrieved upon paying an undisclosed ransom, The News Tribune reported.

Woodcreek says an investigation by its vendor, Netgain Technology, determined the breach happened sometime between November 24 and December 3, 2020, although it’s possible that it happened as early as September.

“The server containing Woodcreek’s medical records system was untouched; however, scanned clinical and financial data and other business records on an archive server was stolen by the attackers,” the company said Tuesday.

The attack allowed access to personal information which for some includes Social Security numbers, dates of birth and other data.

On Feb. 17, counsel for Woodcreek notified the Washington state Attorney General’s Office that it would send notifications to more than 200,000 people whose information was potentially compromised.

In response to questions from The News Tribune on Tuesday about the breach, MultiCare noted the breach was isolated to Woodcreek’s server and said that Woodcreek manages “a small number of pediatric clinics in the Puget Sound region for Mary Bridge Children’s Hospital and Health Network.”

The health system said that it “deeply regrets that this breach has occurred on a vendor platform of one of our affiliated providers.”

Related: U.S. Hospitals Warned of Imminent Ransomware Attacks From Russia

Related: Greater Baltimore Medical Center Hit by Ransomware Attack

Related: Highly Targeted ‘Zeppelin’ Ransomware Hits Tech, Healthcare Firms

view counter

Previous Columns by Associated Press:
Tags:

http://feedproxy.google.com/~r/Securityweek/~3/Bsyg0rxwqvA/breach-exposes-data-200k-health-system-staff-patients


Cyber Insurance Firm Cowbell Raises $20 Million

California-based cyber insurance firm Cowbell Cyber this week announced raising $20 million in a Series A funding round.

The company previously raised $3.3 million in seed funding, which it announced in September 2019 when it emerged from stealth mode.

The Series A round was led by Brewer Lane Ventures, with participation from Pivot Investment Partners, Avanta Ventures, Markel Corporation, ManchesterStory, Tri-Valley Ventures, and Holmes Murphy. The money will be used to increase Cowbell’s footprint and to boost product development, risk engineering, sales, and marketing.

Cowbell did not disclose a valuation for the latest funding round. However, sources close to the company put the valuation close to $100 million.

Cowbell, which offers its services to businesses with a revenue of up to $1 billion, describes itself as the first cyber insurance provider to use AI for risk selection and pricing.

The company claims to have a network of over 4,500 agents and brokers, and a risk pool of 10 million monitored organizations.

“Cybersecurity is now a risk management issue that is critical to the future of the insurance industry and is evolving at a pace that insurers have rarely seen,” said Jack Kudale, founder and CEO of Cowbell Cyber. “Cowbell Cyber has capitalized on businesses’ accelerated digitization and an ever-changing threat landscape. Cowbell embraces AI and machine learning to gain efficiency and accuracy when assessing and underwriting cyber risk while focusing on the fundamental needs of our policyholders: keeping their businesses protected from evolving cyber threats.”

Also this week, cyber insurance provider Corvus announced raising $100 million in a Series C funding round, bringing the total investment obtained by the firm to $147 million.

Related: Plugging the Discrepancy Between Cyber Insurance Coverage and Actual Risk

Related: The Case for Cyber Insurance

Related: Cyber Insurance Provider Coalition Raises $90 Million

Related: Zurich Announces New Cyber Insurance for Manufacturing Industry

view counter

Eduard Kovacs (@EduardKovacs) is a contributing editor at SecurityWeek. He worked as a high school IT teacher for two years before starting a career in journalism as Softpedia’s security news reporter. Eduard holds a bachelor’s degree in industrial informatics and a master’s degree in computer techniques applied in electrical engineering.

Previous Columns by Eduard Kovacs:
Tags:

http://feedproxy.google.com/~r/Securityweek/~3/6UBvhR7TZBw/cyber-insurance-firm-cowbell-raises-20-million


Data Privacy Management Firm DataGrail Raises $30 Million

California-based data privacy management company DataGrail this week announced that it raised $30 million in a Series B funding round.

The company previously raised $5.2 million in a Series A round in 2019. The latest funding round was led by Felicis Ventures, with participation from HubSpot, Okta, Next47 (venture firm backed by Siemens), Basis Set Ventures, Operator Collective, and previous investors.

DataGrail provides a platform designed to help organizations simplify, automate and scale their privacy programs. The platform, which automates data subject requests, is powered by a live data map that enables customers to know exactly where data lives on their systems, with any changes being automatically reflected.

DataGrail provides integration with more than 900 apps and infrastructure, and integrations are maintained by the company itself.

The company says its services are used by millions of consumers through firms such as Overstock, RH, Databricks and Outreach.

“Privacy laws, like CCPA and GDPR, give people the right to have their data deleted, or refuse its sale, but modern organizations are ill-prepared for the Privacy Era,” said Daniel Barber, CEO and co-founder of DataGrail. “To combat the massive privacy challenges businesses face today, we’ve built a platform that makes it remarkably easy to untangle what’s become a spider web of data across the entire tech stack. DataGrail elegantly solves this near-impossible task for organizations that want to do right by their customers.”

Related: Data Governance and Security Provider Privacera Raises $13.5 Million

Related: Developer Security Firm Snyk Raises $300 Million at $4.7 Billion Valuation

Related: Aqua Security Achieves Unicorn Status After $135 Million Funding Round

Related: XDR Firm Cynet Raises $40 Million Series C Funding

view counter

Eduard Kovacs (@EduardKovacs) is a contributing editor at SecurityWeek. He worked as a high school IT teacher for two years before starting a career in journalism as Softpedia’s security news reporter. Eduard holds a bachelor’s degree in industrial informatics and a master’s degree in computer techniques applied in electrical engineering.

Previous Columns by Eduard Kovacs:
Tags:

http://feedproxy.google.com/~r/Securityweek/~3/D5ZCcd5u09A/data-privacy-management-firm-datagrail-raises-30-million


Data Security and Governance Provider Privacera Raises $50 Million

Cloud data governance and security solutions provider Privacera this week announced that it has closed a $50 million Series B funding round, roughly half a year after raising $13.5 million in a Series A round.

Founded in 2016 by the creators of Apache Ranger, Privacera plans to use the new funds to accelerate its go-to-market strategy and extend its portfolio to support multiple cloud services.

The funding round was led by Insight Partners, but also saw participation from Battery Ventures, Sapphire Ventures, Accel, Cervin, and Point 72.

The new infusion of cash, the company says, will be used to extend investment in Privacera’s unified system for data governance and privacy across cloud services, such as Databricks and Snowflake.

The company says it registered a 2.5X ARR growth last year, which it claims was accompanied by an “explosive” increase in customer base.

Privacera provides a SaaS-based data security and governance platform that can automatically identify sensitive data, and offers unified access control and encryption across cloud services such as AWS, Azure, Google Cloud, Databricks, and Snowflake.

“Having pioneered the industry’s first SaaS-based data governance and security solution capable of integrating privacy and compliance across multiple cloud services, we help organizations use data effectively and responsibly, so they remain compliant with an ever-growing number of regulations,” Privacera CEO Balaji Ganesan commented.

Related: Developer Security Firm Snyk Raises $300 Million at $4.7 Billion Valuation

Related: Cyber Insurance Provider Corvus Raises $100 Million

Related: Aqua Security Achieves Unicorn Status After $135 Million Funding Round

view counter

Ionut Arghire is an international correspondent for SecurityWeek.

Previous Columns by Ionut Arghire:
Tags:

http://feedproxy.google.com/~r/Securityweek/~3/D2UCcapfPLk/data-security-and-governance-provider-privacera-raises-50-million


Serious Vulnerabilities Found in Schneider Electric Power Meters

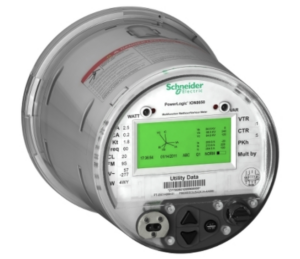
Industrial cybersecurity firm Claroty this week disclosed technical details for two potentially serious vulnerabilities affecting PowerLogic smart meters made by Schneider Electric.

PowerLogic is a line of revenue and power quality meters that are used not only by utilities, but also industrial companies, healthcare organizations, and data centers for monitoring electrical networks.

Researchers at Claroty discovered that some of the PowerLogic ION and PM series smart meters are affected by vulnerabilities that can be exploited remotely by an unauthenticated attacker by sending specially crafted TCP packets to the targeted device.

Vulnerabilities found in Schneider Electric PowerLogic power meters“These smart meters communicate using a proprietary ION protocol over TCP port 7700, and packets received by the device are parsed by a state machine function,” Claroty explained in a blog post. “We found that It is possible to trigger the flaw during the packet-parsing process by the main state machine function by sending a crafted request. This can be done without authentication because the request is fully parsed before it is handled or authentication is checked.”

Claroty said its researchers identified two different exploitation paths — depending on the architecture of the targeted device — and two different CVE identifiers have been assigned.

One of them, CVE-2021-22714, is considered critical as it allows an attacker to cause the targeted meter to reboot (i.e. DoS condition) and possibly even to execute arbitrary code. The other one, CVE-2021-22713, can only be exploited to force the device to reboot and it has been assigned a high severity rating.

Learn more about vulnerabilities in industrial systems at SecurityWeek’s ICS Cyber Security Conference and SecurityWeek’s Security Summits virtual event series

The vulnerabilities impact several PowerLogic ION device models and one PM model. Security updates for some of the impacted devices were released in July 2020, while others were patched in January and March 2021. Some of the impacted power meters will not receive patches as they are no longer supported.

Vulnerabilities affecting smart meters have been known to pose a risk to both consumers and utilities so it’s important that users of the affected Schneider Electric products apply the patches or mitigations to prevent potential attacks, particularly since information about the flaws has been made public.

Additional details about the patches and mitigations are available in the advisories (CVE-2021-22714 and CVE-2021-22713) released this week by Schneider Electric.

Related: Several Vulnerabilities Found in GE Power Meter Software

Related: Siemens Says Power Meters Affected by Urgent/11 Vulnerabilities

Related: ICS-CERT Issues Alerts After Expert Discloses Power Meter Flaws

view counter

Eduard Kovacs (@EduardKovacs) is a contributing editor at SecurityWeek. He worked as a high school IT teacher for two years before starting a career in journalism as Softpedia’s security news reporter. Eduard holds a bachelor’s degree in industrial informatics and a master’s degree in computer techniques applied in electrical engineering.

Previous Columns by Eduard Kovacs:
Tags:

http://feedproxy.google.com/~r/Securityweek/~3/PJ8CycY3iQc/serious-vulnerabilities-found-schneider-electric-power-meters


XDR Firm Cynet Raises $40 Million Series C Funding

Venture funding continues to flow this week, with extended detection and response (XDR) firm Cynet adding $40 million to its coffers via a Series C funding round led by Greenfield Partners.

Cynet

Founded in 2015, Cynet offers an autonomous XDR platform designed to help organizations of all sizes detect threats and respond to incidents by automating monitoring, attack prevention and detection, and response orchestration capabilities. Dubbed Cynet 360, the platform leverages sensors that continuously collect and analyze endpoint, file, user, and network activity across the customer’s entire environment.

According to the company, the added funding will be used to support growth and maintain its expansion in the North American and European markets.

Cynet previously raised $13 million in a Series B funding round in June 2018, and $18 million in a Series B+ round in June 2020.

Cynet’s platform is backed by a 24/7 Managed Detection and Response (MDR) service that is included for all clients at no extra cost, an attractive proposition for smaller security teams.

The Series C funding round also had participation from existing investors Norwest Venture Partners, Vintage Investment Partners, BlueRed Partners and Deutsche Telekom. 

Related: Reinventing Managed Security Services’ Detection and Response

Related: Putting the Pieces Together for Extended Detection and Response

view counter

For more than 10 years, Mike Lennon has been closely monitoring the threat landscape and analyzing trends in the National Security and enterprise cybersecurity space. In his role at SecurityWeek, he oversees the editorial direction of the publication and is the Director of several leading security industry conferences around the world.

Previous Columns by Mike Lennon:
Tags:

http://feedproxy.google.com/~r/Securityweek/~3/NjxaP8zONBE/xdr-firm-cynet-raises-40-million-series-c-funding


Facial Recognition Company Sued by California Activists

Civil liberties activists are suing a company that provides facial recognition services to law enforcement agencies and private companies around the world, contending that Clearview AI illegally stockpiled data on 3 billion people without their knowledge or permission.

The lawsuit, filed Tuesday in Alameda County Superior Court in the San Francisco Bay Area, contends that the New York-based firm violates California’s constitution and seeks an injunction to bar it from collecting biometric information in California and requiring it to delete data on Californians.

The lawsuit says the company has built “the most dangerous” facial recognition database in the nation, has fielded requests from more than 2,000 law enforcement agencies and private companies, and has amassed a database nearly seven times larger than the FBI’s.

The lawsuit was filed by four activists and the groups Mijente and Norcal Resist, who have supported causes such as Black Lives Matter and have been critical of the policies of U.S. Immigration and Customs Enforcement, which has a contract with Clearview AI.

“Clearview has provided thousands of governments, government agencies, and private entities access to its database, which they can use to identify people with dissident views, monitor their associations, and track their speech,” the lawsuit contends.

The lawsuit said Clearview AI scrapes dozens of internet sites, such as Facebook, Twitter, Google and Venmo, to gather facial photos. Scraping involves the use of computer programs to automatically scan and copy data, which the lawsuit says is analyzed by Clearview AI to identify individual biometrics such as eye shape and size that are then put into a “faceprint” database that clients can use to ID people.

The images scraped include those posted not only by individuals and their family and friends but also those of people who are inadvertently captured in the background of strangers’ photos, according to the lawsuit.

The company also offers its services to law enforcement even in cities that ban the use of facial recognition, the lawsuit alleges.

Several cities around the country, including the Bay Area cities of Alameda, San Francisco, Oakland and Berkeley, have limited or banned the use of facial recognition technology by local law enforcement.

“Clearview AI complies with all applicable law and its conduct is fully protected by the First Amendment,” said a statement from attorney Floyd Abrams, representing the company.

The company has said it saw law enforcement use of its technology jump 26% following January’s deadly riot at the U.S. Capitol.

Facial recognition systems have faced criticism because of their mass surveillance capabilities, which raise privacy concerns, and because some studies have shown that the technology is far more likely to misidentify Blacks and other people of color than whites, which has resulted in mistaken arrests.

However, Clearview AI’s CEO, Hoan Ton-That, said in a statement that “an independent study has indicated the Clearview AI has no racial bias.”

“As a person of mixed race, having non-biased technology is important to me,” he said.

He also argued that the use of accurate facial recognition technology can reduce the chance of wrongful arrests.

The lawsuit said Facebook, Twitter, Google and other social media firms have asked Clearview AI to stop scraping images because it violated their terms of service with users.

Clearview AI also is facing other challenges. A lawsuit filed in Illinois alleges the company violates that state’s biometric privacy act, while privacy watchdogs in both Canada and the European Union have issued statements of concern.

Clearview stopped operations in Canada last year. But privacy commissioners this year asked the firm to remove data on Canadian citizens, with one commissioner arguing that the system puts all Canadians “continually in a police lineup.”

Related: Canada Probe Concludes Clearview AI Breached Privacy Laws

Related: Facial Recognition: IT and Police in Delicate Dance

view counter

Previous Columns by Associated Press:
Tags:

http://feedproxy.google.com/~r/Securityweek/~3/FoRE_AJa5zY/facial-recognition-company-sued-california-activists