Red Canary Raises $81 Million to Grow Security Operations Business

Red Canary, a Denver, Colo.-based managed detection and response (MDR) firm, has raised $81 million through a Series C founding round led by Summit Partners.

The provider of SaaS-based security operations solutions has now raised more than $125 million to-date, with the new funding being used to support product and personnel expansion.

Red Canary offers SaaS threat detection and 24/7 outsourced security operations services.

Red Canary

MDR aims to increase the speed of detection and response, consequently reducing the dwell time and the opportunity for bad actors to complete their purpose.

Founded in 2014 by Brian Beyer, Chris Rothe, and Keith McCammon, Red Canary serves hundreds of customers ranging from Fortune 100 to small businesses, and said it has experience 270% revenue growth over the past two years.

“With a cyber-attack occurring every 11 seconds, even the most well-staffed and experienced security teams are actively looking for an ally to help them stay ahead of threats,” said Beyer, who serves as CEO of Red Canary. 

Existing investors Noro-Moseley Partners and Access Venture Partners also participated in the Series C round.

view counter

Previous Columns by SecurityWeek News:
Tags:

http://feedproxy.google.com/~r/Securityweek/~3/XTEZTalQMyU/red-canary-raises-81-million-grow-security-operations-business


Research Shows How Solar Energy Installations Can Be Abused by Hackers

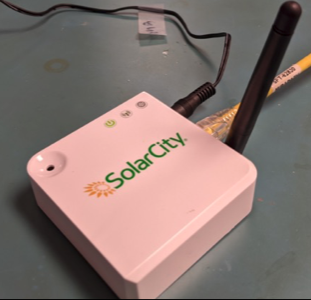
Researchers at cybersecurity firm FireEye have analyzed a gateway device used for solar energy installations, and discovered vulnerabilities that could be useful to malicious hackers.

The targeted device is the ConnectPort X2e made by Digi International, a US-based company that provides IT, networking and IoT solutions for industrial, enterprise and smart city applications. FireEye conducted its research on a version of the device offered by Tesla under the SolarCity brand — Tesla acquired solar panel maker SolarCity in 2016.

The X2e device is a programmable gateway used for residential and small commercial solar installations. It’s typically used to read data from a solar inverter and provide a connection to cloud-based applications.

FireEye’s research involved a physical inspection of the device, an analysis of debugging interfaces, removing the NAND storage, analyzing the file system and bootloader, glitch attacks, and software exploitation.

SolarCity device vulnerabilities

The research led to the discovery of two vulnerabilities: one related to the existence of hardcoded credentials (CVE-2020-9306), and a privilege escalation flaw (CVE-2020-12878) — both were classified as high severity. The security holes were reported to both Tesla and Digi, and they have been patched.

According to FireEye, an attacker who has network access to the targeted device could exploit the vulnerabilities to obtain a root shell and remotely take complete control of the device.

“If an attacker is able to compromise an X2e device, they would have access to a networked device in a home or enterprise,” FireEye researchers Jake Valletta and Sam Sabetan told SecurityWeek.

“X2e’s are typically only used for data collection purposes and if compromised, an attacker could install a backdoor on the X2e which could be used to laterally move in a network, call out to a remote server for persistent access, or stage a larger attack on the victim’s network,” they added, clarifying that “this scenario holds for any compromised IoT device on a network.”

The researchers noted that the device is typically behind a residential firewall so remote attacks directly from the internet should not be possible, unless the user has intentionally made it accessible from the web.

“However, ConnectPort X2e’s are used for various purposes and are not exclusive to solar installations. Therefore, it is possible some X2e devices, based on their use case, are exposed to the Internet,” they explained.

FireEye has made available detailed technical information on its research into the X2e device [part 1 and part 2].

Related: Malware Found on USB Drives Shipped With Schneider Solar Products

Related: Vulnerabilities Found in Popular Solar Park Monitoring System

Related: Solar Panel Flaws Put Power Grids at Risk: Researcher

view counter

Eduard Kovacs (@EduardKovacs) is a contributing editor at SecurityWeek. He worked as a high school IT teacher for two years before starting a career in journalism as Softpedia’s security news reporter. Eduard holds a bachelor’s degree in industrial informatics and a master’s degree in computer techniques applied in electrical engineering.

Previous Columns by Eduard Kovacs:
Tags:

http://feedproxy.google.com/~r/Securityweek/~3/FM5NPtRz1oM/research-shows-how-solar-energy-installations-can-be-abused-hackers


DHS Retreats on Possible Facial Screening of US Citizens

The Homeland Security Department is backing away from requiring that U.S. citizens submit to facial-recognition technology when they leave or enter the country.

The department said Thursday that it has no plans to expand facial recognition to U.S. citizens. A spokesman said DHS will delete the idea from its regulatory agenda, where privacy advocates spotted it this week.

The advocates and lawmakers accused DHS of reneging on repeated promises not to force American citizens to be photographed leaving or entering the United States, a process that is required for foreign visitors.

Sen. Edward Markey, D-Mass., called the administration’s retreat “a victory for every single American traveler who flies on a plane.” He credited public pressure for the about-face. He said, however, that he still plans to introduce legislation to ban biometric surveillance of Americans.

Edward Hasbrouck, a privacy advocate who pointed out the proposal, said the matter might not be settled.

“Was this a trial balloon to find out whether the DHS had finally reached the limits of our willingness to be treated like criminals whenever we fly?” he said. “And if so, has the DHS partially backed off, at least for now? Maybe.”

Customs and Border Protection officials say they originally considered including U.S. citizens in the biometrics program because having one system for Americans and another for foreigners adds complexity and could compromise security or make lines longer.

But after meeting with lawmakers and privacy experts — including this week — it decided it was better to continue letting Americans opt out.

Privacy experts have questioned the accuracy of facial recognition and warned that personal information could be vulnerable to hackers or used improperly by companies holding the data. In response to those criticisms, DHS made some changes, including shortening the time it will retain photographs from 14 days to 12 hours.

Facial recognition is used to screen passengers at more than a dozen U.S. airports. Some airlines, including Delta and JetBlue, tout it as a convenience for passengers who no longer need to show boarding passes and identification.

view counter

Previous Columns by Associated Press:

Tags:

http://feedproxy.google.com/~r/Securityweek/~3/Z4jJBaqmFIA/dhs-retreats-possible-facial-screening-us-citizens


Russian ‘Gamaredon’ Hackers Back at Targeting Ukraine Officials

The Russian state-sponsored hacking group known as Gamaredon has been targeting various Ukrainian diplomats, government and military officials, and law enforcement since mid-October 2019, threat intelligence company Anomali reports.

Active since at least mid-2013 and also known as Primitive Bear, the Gamaredon group was first analyzed in April 2015. Over the past years, it has been observed engaged in various attacks targeting individuals involved with the Ukrainian government.

In mid-October, the hackers started a campaign against various individuals and entities in Ukraine, including diplomats, government officials and employees, journalists, law enforcement, military officials and personnel, NGOs, and the country’s Ministry of Foreign Affairs.

Weaponized documents were used as the initial infection vector in this campaign, likely delivered via spear-phishing. Analysis of these documents revealed malicious activity starting in September and continuing until November 25, Anomali’s security researchers explain in a report (PDF).

The researchers retrieved three lure documents: one addressed to the Dnipro Control System and discussing military-related matters, another produced by the NGO media watchdog Detector Media, and a third targeting the Ministry of Foreign Affairs of Ukraine.

The initial document connects to a remote server to download a document template (.dot) that contains VBA macros. The .dot is executed in the background, while the VBA macro writes a VBScript file to the startup folder.

Upon reboot, the VBScript performs an HTTP GET request to fetch an encrypted stage from a dynamic DNS domain. The payload, however, is only sent if the target is deemed of interest.

If delivered, the second-stage file appears to be an executable that is stored directly in the startup folder, to ensure it runs at system reboot. Anomali’s researchers, however, did not observe a payload being delivered from the server.

The malicious campaign appears to be ongoing, with the intended targets and the Tactics, Techniques and Procedures (TTPs) falling well in line with previous activity associated with the Russian hacking group Gamaredon.

“Russian-sponsored cyber capabilities have been well-documented over numerous malicious campaigns found and attributed by the security community, and this activity […] indicates the risk posed to entities by APT threat groups. Governments around the globe utilize campaigns for strategic purposes, and in Russia’s case, sometimes to coincide with armed forces activity,” Anomali concludes.

Related: EvilGnome Malware Helps Hackers Spy on Linux Users

Related: “Gamaredon” Group Uses Custom Malware in Ukraine Attacks

view counter

Ionut Arghire is an international correspondent for SecurityWeek.

Previous Columns by Ionut Arghire:

Tags:

http://feedproxy.google.com/~r/Securityweek/~3/YCp00YCk0Yw/russian-gamaredon-hackers-back-targeting-ukraine-officials


Vulnerabilities Found in Aviatrix Enterprise VPN

Two local privilege escalation vulnerabilities have been identified by a researcher in an enterprise VPN product from cloud-native networking solutions provider Aviatrix.

Aviatrix claims to have over 400 customers worldwide, including companies such as Netflix, United Airlines, Docker, Epsilon, and some major hotel chains.

Immersive Labs researcher Alex Seymour discovered that the Aviatrix VPN, which is based on OpenVPN, is affected by two vulnerabilities. The weaknesses were reported to the vendor in early October and patched less than one month later with the release of version 2.4.10.

The vulnerabilities allow an attacker who already has access to the targeted machine to elevate privileges and gain access to data and services they may not be able to access with the permissions of a regular user.

One of the privilege escalation flaws, tracked as CVE-2019-17388, is caused by weak file permissions, while the other, tracked as CVE-2019-17387, involves service code execution. They both allow an attacker to execute arbitrary code with elevated privileges.

“Coming hot on the heels of the UK and US Government warnings about VPN vulnerabilities, this underlines that often the technology protecting enterprises needs to be managed as tightly as the people using it,” Seymour explained. “People tend to think of their VPN as one of the more secure elements of their security posture, so it should be a bit of a wakeup call for the industry.”

Immersive Labs has published a blog post containing technical details for both vulnerabilities.

In an advisory published for these vulnerabilities, Aviatrix clarified that only the local machine running the VPN Client is affected — they do not impact the VPN Gateway or machines running other OpenVPN-compatible VPN clients, and they would be useless to attackers who already have administrator privileges on the targeted system. The attacks work on all operating systems supported by Aviatrix.

Threat actors have been known to exploit vulnerabilities in enterprise VPNs, and while the Aviatrix flaws might seem less attractive for hackers, they should not be ignored and the vendor has advised customers to update the client immediately.

Related: VPN Connection Hijacking Vulnerability Affects Linux, Unix Systems

Related: Enterprise VPN Vulnerabilities Expose Organizations to Hacking, Espionage

Related: Vulnerability Patched in Forcepoint VPN Client for Windows

view counter

Eduard Kovacs (@EduardKovacs) is a contributing editor at SecurityWeek. He worked as a high school IT teacher for two years before starting a career in journalism as Softpedia’s security news reporter. Eduard holds a bachelor’s degree in industrial informatics and a master’s degree in computer techniques applied in electrical engineering.

Previous Columns by Eduard Kovacs:

Tags:

http://feedproxy.google.com/~r/Securityweek/~3/MY6FOJCsUJo/vulnerabilities-found-aviatrix-enterprise-vpn


Facebook Sues Chinese Company Over Ad Fraud

Facebook on Thursday filed suit in California against one organization and two individuals for engaging in ad fraud on the social media platform.

The defendants, Hong Kong-based ILikeAd Media International Company Ltd. and its employees, Chen Xiao Cong and Huang Tao, tricked Facebook users into installing malware that provided them with the ability to compromise people’s accounts.

Using the hijacked Facebook accounts, the defendants ran ads that promoted items such as counterfeit goods and diet pills.

Facebook filed the lawsuit to hold the Chinese company accountable for creating the malware, deceiving individuals into installing it, and then compromising people’s accounts to run the deceptive ads through them.

In some cases, the defendants used images of celebrities (“celeb bait”) to entice people into clicking on ads, the social platform says.

In other instances, they engaged in a practice known as cloaking, where they deliberately disguised the destination of the link in their ads. Specifically, the version of the ad’s landing page displayed to Facebook’s systems was different from the version delivered to Facebook users.

Cloaking schemes, the company explains, are often sophisticated and well organized, and holding the entities behind them accountable isn’t easy. Thus, there have been few legal actions taken against such schemes.

The social platform says it has refunded victims of this scheme and also helped them secure their accounts.

“To protect Facebook users and disrupt these types of schemes, we will continue our work to detect malicious behavior directed towards our platform and enforce against violations of our Terms and Policies,” the company also notes.

Related: Facebook Nixes Billions of Fake Accounts

Related: Facebook: Third-Party App Developers Improperly Accessed User Information

Related: Facebook Expands, Enhances Bug Bounty Programs

view counter

Ionut Arghire is an international correspondent for SecurityWeek.

Previous Columns by Ionut Arghire:

Tags:

http://feedproxy.google.com/~r/Securityweek/~3/dVGZJOO6Xys/facebook-sues-chinese-company-over-ad-fraud


Panorays Raises $15 Million in Series A Funding Round

Automated third-party security lifecycle management provider Panorays this week announced it raised $15 million as part of a Series A funding round.

The funding, the company says, will help it expand marketing and sales initiatives, speed up its global expansion, and evolve its Security-as-a-Service (SaaS) platform to adapt to growing privacy regulations and eliminate inefficient workflows.

Panorays provides customers with a SaaS platform to accelerate third-party security evaluation processes. The platform promises a 360° view of the supplier, both testing it for weaknesses and ensuring it complies with security policies and practices.

The percentage of third parties sharing an organization’s sensitive and confidential data has increased from 37% in 2016 to 43% in 2018, and Panorays seeks to help companies mitigate that risk.

Through its SaaS platform, Panorays delivers the visibility and control companies need when looking to build and scale third-party security programs through automation.

Customizable questionnaires are combined with a continuous hacker’s view of the evaluated vendor to help companies speed up their third-party security evaluation process.

Panorays, which has already seen adoption from technology, software, financial, healthcare, automotive, and retail companies, says it has experienced a 400% revenue growth over its previous year and claims to have helped customers save an average of 94% of expenses incurred by third-party security programs.

Related: Detectify Raises $23.7 Million in Series B Funding Round

Related: Clumio Completes $135 Million Series C Funding Round

Related: Security Automation Firm ZecOps Raises $10 Million in Seed Funding

view counter

Ionut Arghire is an international correspondent for SecurityWeek.

Previous Columns by Ionut Arghire:

Tags:

http://feedproxy.google.com/~r/Securityweek/~3/UWAPPkt5M7U/panorays-raises-15-million-series-funding-round


Weidmueller Patches Critical Vulnerabilities in Industrial Switches

Germany-based industrial connectivity solutions provider Weidmueller has released firmware updates for many of its managed industrial Ethernet switches to address critical vulnerabilities.

Weidmueller has six manufacturing plants and a presence in 60 locations around the world. According to the DHS’s Cybersecurity and Infrastructure Security Agency (CISA), the impacted products are used worldwide, particularly in the critical manufacturing and IT sectors.Weidmueller patches critical vulnerabilities in industrial switches

Advisories published recently by CISA, Germany’s [email protected] and Weidmuller show that 40 IE-SW series switches are impacted by five types of vulnerabilities.

The most serious flaws, based on their CVSS score, are related to the lack of brute-force protection for the authentication mechanism, the transmission of credentials in clear text, and the use of predictable authentication information in a cookie. All of these issues are considered critical, with a CVSS score of 9.8.

The industrial switches are also affected by a high-severity flaw related to the storage of passwords in clear text. This weakness allows anyone with access to the device to obtain the passwords.

Learn More About Vulnerabilities in Industrial Products at SecurityWeek’s 2020 ICS Cyber Security Conference

Finally, Weidmueller discovered a medium-severity issue that allows a remote, authenticated attacker to crash the device using specially crafted packets.

Weidmueller has released firmware updates for each of the impacted switches. Users have also been informed that they can configure their devices to only use encrypted connections, which can prevent some types of attacks. Some weaknesses are related to the use of an unencrypted search service, which should be disabled — an encrypted search service is available.

The vendor has provided detailed instructions on how mitigations can be applied.

Related: Moxa Addresses Industrial AP Vulnerabilities Several Months After Disclosure

Related: Flaws Expose Phoenix Contact Industrial Switches to Attacks

Related: Critical Vulnerabilities Found in WAGO Industrial Switches

view counter

Eduard Kovacs (@EduardKovacs) is a contributing editor at SecurityWeek. He worked as a high school IT teacher for two years before starting a career in journalism as Softpedia’s security news reporter. Eduard holds a bachelor’s degree in industrial informatics and a master’s degree in computer techniques applied in electrical engineering.

Previous Columns by Eduard Kovacs:

Tags:

http://feedproxy.google.com/~r/Securityweek/~3/6HfzMR2jtlk/weidmueller-patches-critical-vulnerabilities-industrial-switches


U.S. Authorities Take Action Against 600 Money Mules

Authorities in the United States recently stopped the activities of more than 600 domestic money mules, the Department of Justice announced on Wednesday.

Money mules are individuals who assist fraud schemes by receiving money from victims and transferring proceeds to perpetrators. Many of the victims are elderly, while the cybercriminals behind the fraud schemes are usually located in other countries.

As part of the newly revealed initiative, which took place over a period of two months, money mule networks were disrupted all around the country. Overall, action was taken to stop the activity of over 600 money mules spanning more than 85 federal districts.

The DoJ also revealed that over 30 individuals were indicted for their roles in receiving money from victims and forwarding proceedings to cybercriminals, a number that is three times higher than last year.

Fraud scheme types targeted this year included “grandparent scams, romance scams, lottery and sweepstakes scams, IRS and Social Security Administration imposter scams, veteran and social security benefit redirection scams, and technical-support scams.”

More than 550 individuals were interviewed and over 500 warning letters were sent to individuals who recently served as money mules. The recipients were told they could be prosecuted if they continued aiding and abetting fraud schemes.

Authorities also executed search warrants to secure evidence from those who knowingly aided and abetted fraud schemes, including transnational elder fraud schemes.

In November, the DoJ’s Transnational Elder Fraud Strike Force indicted a Georgia man for a $6.5 million online romance scam and business email compromise fraud, four other Georgia residents for fraud schemes targeting retirees and federal benefit programs, and six other individuals involved in a prize-notification scheme.

“The Money Mule initiative highlights the importance of partnership to stop fraud schemes, and it sends a message to all who are engaged in money mule activity that they will be caught and prosecuted,” said FBI Director Christopher Wray.

A similar initiative against money mules was announced this week in Europe, where authorities said they had identified over 3,800 money mules and 386 recruiters, of which 228 were arrested.

Related: U.S. Charges 80 in Massive Online Fraud Scheme

Related: FBI Steps Up Efforts Against ‘Money Mules’ Online Fraud

Related: 168 Arrested in Money Mule Crackdown

view counter

Ionut Arghire is an international correspondent for SecurityWeek.

Previous Columns by Ionut Arghire:

Tags:

http://feedproxy.google.com/~r/Securityweek/~3/QFtrNOH4w44/us-authorities-take-action-against-600-money-mules


VMware Patches ESXi Vulnerability That Earned Hacker $200,000

VMware on Thursday informed customers that it has released patches for a critical remote code execution vulnerability in ESXi that was disclosed recently at the Tianfu Cup hacking competition in China.

According to organizers of the Tianfu Cup, a member of the 360Vulcan team demonstrated a virtual machine escape and took control of the host operating system. The exploit only took 24 seconds to execute and earned the hacker $200,000, the highest single payout at the event.

VMware representatives were present at the competition so they were provided the details of the exploit immediately after the demonstration on November 17.

The company’s investigation revealed that the vulnerability exploited at the event affects ESXi versions 6.0, 6.5 and 6.7 running on any platform, and the Horizon cloud desktop-as-a-service (DaaS) platform version 8.x.

Patches have been released for ESXi, but VMware is still working on a fix for Horizon DaaS. The vulnerability is tracked as CVE-2019-5544 and it has been assigned a CVSS score of 9.8, which makes it a critical issue.

VMware says the flaw is a heap overwrite issue related to the OpenSLP open source implementation of the Service Location Protocol (SLP), which is designed for locating resources on a network.

“A malicious actor with network access to port 427 on an ESXi host or on any Horizon DaaS management appliance may be able to overwrite the heap of the OpenSLP service resulting in remote code execution,” VMware said in its advisory.

This year it took VMware more than two weeks to address the vulnerability disclosed at the Tianfu Cup contest, but in 2018 it took the company less than a week to patch a Workstation vulnerability that earned a researcher $100,000 at the hacking event.

At this year’s Tianfu Cup, white hat hackers earned $545,000 for demonstrating exploits against products from VMware, Microsoft, Google, Apple, D-Link, and Adobe.

Related: VMware Patches Six Vulnerabilities in Various Products

Related: VMware Patches Critical Harbor Vulnerability

Related: VMware Patches Potentially Serious Pixel Shader Vulnerabilities

view counter

Eduard Kovacs (@EduardKovacs) is a contributing editor at SecurityWeek. He worked as a high school IT teacher for two years before starting a career in journalism as Softpedia’s security news reporter. Eduard holds a bachelor’s degree in industrial informatics and a master’s degree in computer techniques applied in electrical engineering.

Previous Columns by Eduard Kovacs:

Tags:

http://feedproxy.google.com/~r/Securityweek/~3/kyI5Eg-JzV4/vmware-patches-esxi-vulnerability-earned-hacker-200000