Supply Chain Security Fears Escalate as Iranian APTs Caught Hitting IT Services Sector

Fears of software supply chain attacks escalated again this week with a new warning from Microsoft that it has caught Iranian threat actors breaking into IT services shops in India and Israel and using that access to hit the real targets.

Two of Redmond’s premier threat hunting units  — the Microsoft Threat Intelligence Center (MSTIC) and Microsoft Digital Security Unit (DSU) — are sounding the alarm for a series of intrusions at companies that sell business management and integration software to millions of global organizations.

Once inside the IT services organizations, Microsoft said the Iranian hackers are “extending their attacks to compromise downstream customers,” much like the SolarWinds supply chain mega-hack that snagged thousands of corporate victims globally.

Microsoft warned of a significant surge in these attacks — more than 1,600 notifications to over 40 IT companies in response to Iranian targeting, compared to 48 notifications in 2020 — and warned that downstream attacks are targeting organizations in the defense, energy, and legal sectors

“As India and other nations rise as major IT services hubs, more nation state actors follow the supply chain to target these providers’ public and private sector customers around the world matching nation state interests,” Microsoft said in a report calling attention to the surge in these Iran-linked attacks.

[ READ: Hacked SolarWinds Software Lacked Basic Anti-Exploit Mitigation ]

In July 2021 this year, Microsoft said it caught a threat actor based in Iran that compromised a single Israel-based IT company that provides business management software.  Microsoft said the hacking group then used access to that IT company to extend their attacks and compromise downstream customers in the defense, energy, and legal sectors in Israel. 

A few months later, Redmond’s threat hunting teams caught  a separate Iranian group hacking into email accounts at a Bahrain-based IT integration company that works on IT integration with Bahrain government clients.

Microsoft surmises that the downstream Bahrain government clients “were likely the ultimate target” and warned that the group has also compromised various accounts at a partially government-owned organization in the Middle East that provide information and communications technology to the defense and transportation sectors.

The hacking group maintained persistence at the Bahrain IT integration organization from September through at least October.

[ READ: Microsoft Exposes Iran-Linked APT Targeting U.S., Israeli Defense ]

Microsoft said credential theft from the original compromises of IT services companies are used in the downstream attacks.  [The Iranian attackers] dumped credentials from the on-premises network of an IT provider based in Israel in early July. Over the next two months, the group compromised at least a dozen other organizations, several of which have strong public relations with the compromised IT company,” Microsoft explained.

The company said at least four of those victims were compromised using the acquired credentials and access from the IT company in the July and August attacks. 

Redmond’s telemetry has picked up a major surge in these and other Iranian groups targeting IT companies based in India beginning in mid-August. From mid-August to late September, Microsoft said it issued 1,788 nation state notifications (NSNs) across Iranian actors to enterprise customers in India, roughly 80% of which were to IT companies.   

Over the three previous years, Microsoft barely issued 10 such notifications in response to Iranian hacking activity and because there are no obvious geo-political reasons for the India targeting, the company believes the Indian IT shops are being used “for indirect access to subsidiaries and clients outside India.”

Related: Microsoft Exposes Iran-Linked APT Targeting U.S., Israeli Defense

Related: Hacked SolarWinds Software Lacked Basic Anti-Exploit Mitigation

Related: Researchers Link Mysterious ‘MeteorExpress’ Wiper to Iranian Train Cyber Attack 

Related: New Code Execution Flaws In Solarwinds Orion Platform

view counter

Ryan Naraine is Editor-at-Large at SecurityWeek and host of the popular Security Conversations podcast series. He is a journalist and cybersecurity strategist with more than 20 years experience covering IT security and technology trends.
Ryan has built security engagement programs at major global brands, including Intel Corp., Bishop Fox and Kaspersky GReAT. He is a co-founder of Threatpost and the global SAS conference series. Ryan’s career as a journalist includes bylines at major technology publications including Ziff Davis eWEEK, CBS Interactive’s ZDNet, PCMag and PC World.
Ryan is a director of the Security Tinkerers non-profit, and a regular speaker at security conferences around the world.
Follow Ryan on Twitter @ryanaraine.

Previous Columns by Ryan Naraine:
Tags:

https://www.securityweek.com/supply-chain-security-fears-escalate-iranian-apts-caught-hitting-it-services-sector


Microsoft Says HTML Smuggling Attacks On The Rise

Microsoft says it has observed an increase in the use of HTML smuggling in malicious attacks distributing remote access Trojans (RATs), banking malware, and other malicious payloads.

HTML smuggling leverages HTML5/JavaScript for the download of files onto a victim machine, which in this case of these attacks is an encoded malicious script designed to assemble the final payload directly on the victim computer.

Phishing emails are used to either deliver specially crafted HTML attachments or to direct the intended victim to a web page malicious page designed to smuggle the script.

Microsoft said it observed the Chinese threat actor NOBELIUM leveraged the technique in a series of attacks in May, and is now seeing the same method being used to deliver AsyncRAT/NJRAT, Trickbot, and the banking Trojan Mekotio.

Because the malicious payload is built behind the firewall, the technique allows adversaries to easily bypass standard perimeter security controls that check network traffic for suspicious attachments or patterns.

“Because the malicious files are created only after the HTML file is loaded on the endpoint through the browser, what some protection solutions only see at the onset are benign HTML and JavaScript traffic, which can also be obfuscated to further hide their true purpose,” Microsoft said.

[ Related: Ongoing Campaign Uses HTML Smuggling for Malware Delivery ]

The tech giant said it observed HTML smuggling being used in attacks against banking users in Brazil, Mexico, Spain, Peru, and Portugal, where adversaries were looking to infect victim systems with either Mekotio or Ousaban.

The technique is also making its way into the arsenal of sophisticated threat actors, such as NOBELIUM.

In July and August, adversaries employed HTML smuggling to deliver remote access Trojans (RATs) such as AsyncRAT/NJRAT, while in September the method was used to deploy Trickbot, likely by DEV-0193, an emerging financially motivated cybercrime ring.

The threat actor mainly targets healthcare and education organizations, and shows close connections with ransomware operators, such as those behind Ryuk. DEV-0193 seeks to compromise organizations to sell unauthorized access to ransomware operators.

Disabling JavaScript could prevent such attacks, but that option might not be viable within enterprise environments, where business-related pages and other legitimate resources depend on JavaScript. Thus, a multi-layered defensive approach is recommended.

Related: Ongoing Campaign Uses HTML Smuggling for Malware Delivery

Related: IcedID Trojan Operators Experimenting With New Delivery Methods

view counter

Ionut Arghire is an international correspondent for SecurityWeek.

Previous Columns by Ionut Arghire:
Tags:

https://www.securityweek.com/microsoft-says-html-smuggling-attacks-rise


Cloudflare Battles 2 Tbps DDoS Attack Launched by Mirai Botnet

Web security services provider Cloudflare says it mitigated a distributed denial-of-service (DDoS) attack that peaked at almost 2 terabytes per second (Tbps).

The multi-vector assault was launched by a botnet of approximately 15,000 machines infected with a variant of the original Mirai malware. The bots included Internet of Things (IoT) devices and GitLab instances, Cloudflare said in a new report.

GitLab instances ensnared into the botnet are affected by CVE-2021-22205, a critical (CVSS score of 10) vulnerability that was patched more than six months ago, but which continues to expose tens of thousands of systems.

The 2 Tbps DDoS attack only lasted one minute. The assault combined DNS amplification and UDP floods, company said.

[ READ: ‘BotenaGo’ Malware Targets Routers, IoT Devices with Over 30 Exploits ]

Cloudflare notes that it observed an overall increase  in the number of terabit-strong DDoS attacks over the last quarter, and that network-layer incidents were up 44% quarter-over-quarter.

The trends appear to continue into the fourth quarter of the year as well, with multiple terabit-strong attacks already hitting Cloudflare’s infrastructure.

In August, the web protection firm said it observed a Mirai-variant botnet launching multiple 1Tbps attacks, some peaking at 1.2 Tbps.

Last month, Microsoft said in August it mitigated a massive 2.4 Tbps assault originating from 70,000 sources worldwide. Last year, Amazon and Google said they mitigated 2.3 Tbps and 2.5 Tbps DDoS attacks, respectively.

Related: Operator of ‘DownThem’ DDoS Attack Service Convicted

Related: Mēris Botnet Flexes Muscles With 22 Million RPS DDoS Attack

Related: Organizations Warned: STUN Servers Increasingly Abused for DDoS Attacks

view counter

Ionut Arghire is an international correspondent for SecurityWeek.

Previous Columns by Ionut Arghire:
Tags:

https://www.securityweek.com/cloudflare-mitigates-2-tbps-ddos-attack-launched-mirai-botnet


Costco Hit by Card Skimming Attack Heading Into Holiday Season

Costco, one of the world’s largest retailers, has warned customers that they may have had bank card details stolen, following reports that payment card skimming devices were discovered at Costco warehouses.

“If unauthorized parties were able to remove information from the device before it was discovered, they may have acquired the magnetic stripe of your payment card, including your name, card expiration date, and CVV,” Kevin Green, VP Midwest region operations at Costco, wrote in a letter to potentially affected customers.

The letter, dated November 5, 2021, was uploaded to Documentcloud by Bleeping Computer.

The letter offers customers who may have been affected free credit monitoring from IDX for 12 months, but provides no further details on the device itself, nor the period in which it was operational. 

It was discovered “as a result of regular pin pad inspections conducted by Costco personnel.” It was therefore potentially operational for any part of the period between this and the previous inspection. Fox Business reports that a total of five skimmers were found in four different Chicago-area warehouses during pin pad inspections at the end of August. 

“The data that the attacker can obtain from the magnetic strip on a card actually depends on the card itself. While things like the credit card number, full name, expiration, and country code is universal, other cards can contain additional information like billing address or rewards account numbers,” comments Randy Watkins, CTO at managed detection and response firm Critical Start.

Armen Najarian, chief identity officer at Outseer, warns that we can expect to see a growth in such attacks as we get closer to the holiday season – a threat made worse by staff shortages cause by the pandemic. “As we head into the holiday season, hackers and other bad actors will target retailers made vulnerable by short staffing and high transaction volumes,” he said. 

“All of this, unfortunately, will be amplified this year as pandemic-induced labor shortages reach unprecedented levels. If retailers want to keep their customers safe and happy this holiday season, they need to prioritize payment authentication software for in-store and online transactions alike.”

Such physical attacks only affect the users of the compromised devices and should not be confused with the software skimming technique of a Magecart attack.  At Black Hat Europe on November 10, 2021, external attack surface management firm Cyberpion announced the possibility of a new wave of Magecart attacks. It analyzed more than 30,000 Magecart vulnerabilities over the last two years and found that more than 10,000 are still active. 

“There were also severe lapses in enterprises disclosing security vulnerabilities or exploits occurring along their digital supply chains to their customers, ultimately placing all connected organizations at severe risk of a critical breach.”

Magecart is the common name for a style of cyber attack used by multiple threat actors. Hackers compromise third party code (typically JavaScript that runs in browsers) to steal, or scrape, information such as credit card data from web-applications (for example, online checkout software) or websites that incorporate the code. Big name victims of such attacks include British Airways and Ticketmaster in 2018, Forbes magazine in 2019, plus local US government portals and messaging service Telegram 2020.

“Our conclusion from the analysis is that as of today, organizations fail to face Magecart threats and detect the vulnerabilities and exploits that hackers leverage to conduct these attacks,” said Cyberpion CEO Nethanel Gelernter. “Victims are often the last to know as it’s only later that organizations find that their data was sold or exploited, with the problem extending beyond any single vendor or client relationship. For enterprises in particular, Magecart attacks pose a significant challenge because it is problematic to set up a solution at scale.”

Related: Online Retailers Ill-Prepared for Holiday Season

Related: Hackers Favoring Shimmers Over Skimmers for ATM Attacks

Related: Hunting for Magecart With URLscan.io

view counter

Kevin Townsend is a Senior Contributor at SecurityWeek. He has been writing about high tech issues since before the birth of Microsoft. For the last 15 years he has specialized in information security; and has had many thousands of articles published in dozens of different magazines – from The Times and the Financial Times to current and long-gone computer magazines.

Previous Columns by Kevin Townsend:
Tags:

https://www.securityweek.com/costco-hit-card-skimming-attack-head-holiday-season


Cybersecurity M&A Roundup for Second Week of November 2021

Cybersecurity M&A roundup for second week of November 2021

Eight cybersecurity-related acquisitions were announced in the second week of November 2021 (November 8-14).

Cegeka acquires SecurIT

IT company Cegeka has acquired SecurIT, which specializes in identity and access management (IAM). Both companies are based in the Netherlands, but SecurIT is also active in North America. The acquisition enables Cegeka to expand its cybersecurity capabilities.

DomainTools acquires Farsight Security

DomainTools has announced buying Farsight Security. Both companies are based in the United States and they both specialize in DNS-based threat intelligence. The companies have been working together for several years, with Farsight’s DNS data being leveraged by DomainTools’ Iris investigation platform.

IK Partners acquires Truesec

UK-based private equity firm IK Partners has acquired Sweden-based Truesec, which provides a wide range of cybersecurity services, including risk assessments and penetration testing, and threat detection and response. Truesec said the deal will enable it to expand.

Kerv acquires Gyrocom

Cloud solutions provider Kerv has acquired Gyrocom, which provides cloud, networking, and network security services. The companies are based in the United Kingdom. Gyrocom will become Kerv’s networking and security division following the acquisition.

Lacework acquires Soluble

Cloud security company Lacework purchased cloud infrastructure management firm Soluble, which specializes in infrastructure as code (IaC). Lacework said the acquisition will enable it to strengthen its cloud security platform with new DevSecOps capabilities.

OpenText acquires Zix

Enterprise information management solutions provider OpenText announced the acquisition of email security company Zix for $860 million. Zix said the acquisition by OpenText will help it grow further, with the deal expected to result in more resources and product capabilities.

Sesa acquires majority stake in Datef

Italy-based IT services provider Sesa has acquired — through its subsidiary Var Group — a majority stake in Datef, an Italian company that provides cloud and cybersecurity services, including threat detection and response and industrial cybersecurity. The deal will enable Sesa to expand, as well as to strengthen its position in managed services, cloud and cybersecurity.

Valeo Networks acquires On Time Tech

Managed security service provider (MSSP) Valeo Networks has acquired MSP On Time Tech as part of its national growth strategy. Valeo said the acquisition enables it to expand in California. On Time Tech will continue to operate independently.

Related: Cybersecurity M&A Roundup for First Week of November 2021

Related: Cybersecurity M&A Roundup: 41 Deals Announced in October 2021

view counter

Eduard Kovacs (@EduardKovacs) is a contributing editor at SecurityWeek. He worked as a high school IT teacher for two years before starting a career in journalism as Softpedia’s security news reporter. Eduard holds a bachelor’s degree in industrial informatics and a master’s degree in computer techniques applied in electrical engineering.

Previous Columns by Eduard Kovacs:
Tags:

https://www.securityweek.com/cybersecurity-ma-roundup-second-week-november-2021


Diebold Nixdorf ATM Flaws Allowed Attackers to Modify Firmware, Steal Cash

Security researchers with Positive Technologies have published information on a couple of vulnerabilities in Diebold Nixdorf ATMs that could have allowed for an attacker to replace the firmware on the system and withdraw cash.

Tracked as CVE-2018-9099 and CVE-2018-9100, the flaws were identified in the CMD-V5 and RM3/CRS dispensers – one in each device – of the Wincor Cineo ATMs and were addressed a couple of years ago. Diebold acquired Wincor Nixdorf in 2016 and the companies later merged.

During research sanctioned by the vendor, Positive Technologies discovered that, while the ATMs had in place a series of security measures meant to prevent blackbox attacks, such as end-to-end encrypted communication with the cash dispenser, it was actually possible to work around these.

Specifically, the researchers figured out the command encryption between the ATM computer and the cash dispenser, bypassed it, replaced the ATM firmware with an outdated one, and exploited the vulnerabilities to tell the system to spew cash.

While encryption is used to prevent blackbox attacks, the researchers discovered that an attacker could actually extract the keys used for encryption and then forge their own firmware to load on the compromised ATM.

The system performs firmware integrity checks as an additional protection step, but the researchers were able to identify the components involved in the check process in the code responsible for verifying the firmware signature and in the firmware, “namely the public key and the signed data itself.”

“As a signature verification algorithm, RSA was used with an exponent equal to 7, and the bit count of the key was determined by the size of the public part N. It turned out that if you fitted into the offsets at which the signature and public key were written, you could set almost any length,” Positive Technologies explains.

Before being able to withdraw cash from the ATM, an attacker also needed to find a way to send commands to the dispenser and to specify the amount of money in each cassette.

Diebold Nixdorf, which issued patches for these vulnerabilities in 2019, recommends enabling physical authentication when an operator performs firmware installation, to further prevent unauthorized access. Earlier this year, the vendor warned of an uptick in jackpotting attacks on RM3-based Cineo systems in Europe.

Related: France Says Breaks Up International ATM ‘Jackpotting’ Network

Related: Driver Vulnerabilities Facilitate Attacks on ATMs, PoS Systems

Related: The Latest Threats to ATM Security

view counter

Ionut Arghire is an international correspondent for SecurityWeek.

Previous Columns by Ionut Arghire:
Tags:

https://www.securityweek.com/diebold-nixdorf-atm-flaws-allowed-attackers-modify-firmware-steal-cash


IoT Protocol Used by NASA, Siemens and Volkswagen Can Be Exploited by Hackers

Researchers Warn DDS Protocol Can Be Abused for Lateral Movement and Malware C&C

Researchers have shown that a widely used protocol named Data Distribution Service (DDS) is affected by vulnerabilities that could be exploited by threat actors for various purposes.

Maintained by the standards development organization Object Management Group (OMG), DDS is a middleware protocol and API standard for data connectivity that is advertised as ideal for business-critical IoT systems. DDS has been used in sectors such as public transportation, air traffic management, aerospace, autonomous driving, industrial robotics, medical devices, and missile and other military systems.

DDS has been used by organizations such as NASA, Siemens, and Volkswagen, as well as in the popular Robot Operating System (ROS).

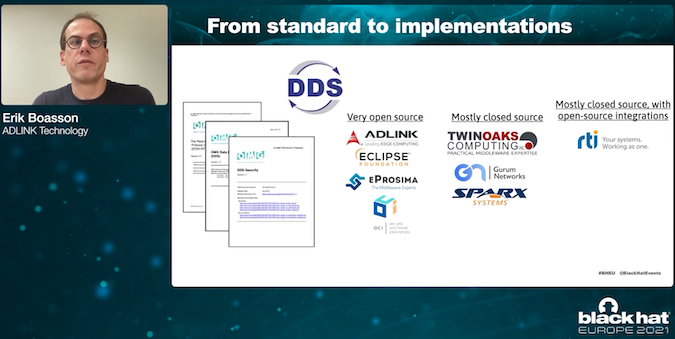
There are both open source and closed source implementations of DDS, including by ADLINK Technology, Eclipse (CycloneDDS), eProsima (Fast DDS), OCI (OpenDDS), TwinOaks Computing (CoreDX DDS), Gurum Networks (GurumDDS), and RTI (Connext DDS).

Researchers from Trend Micro, TXOne Networks, Alias Robotics, and ADLINK Technology have analyzed the DDS standard and the aforementioned implementations and discovered a total of more than a dozen vulnerabilities.

The researchers disclosed some of their findings at the Black Hat Europe 2021 cybersecurity conference last week, with a research paper detailing their work being planned for early next year.

DDS security research presented at Black Hat

In the meantime, the U.S. Cybersecurity and Infrastructure Security Agency (CISA) has released an industrial control systems (ICS) advisory related to the research.

“CISA is issuing this advisory to provide early notice of the reported vulnerabilities and identify baseline mitigations for reducing risks to these and other cybersecurity attacks,” CISA said.

According to CISA, patches have been released for CycloneDDS, FastDDS, OpenDDS, Connext DDS, and CoreDX DDS. There do not appear to be any patches from Gurum, which the researchers said ignored several notification attempts.

Identified vulnerabilities include write-what-where condition, improper handling of invalid structure, network amplification, buffer allocation, and buffer overflow issues.

The flaws can be exploited by threat actors for arbitrary code execution, obtaining information, or causing a denial of service (DoS) condition.

However, the researchers noted in their presentation at Black Hat that since DDS is typically deployed locally and deep in the control network, it’s unlikely that attackers would find internet-exposed systems.

On the other hand, they pointed out that DDS could still be abused by an attacker who already has access to the targeted entity’s systems for the discovery of other endpoints, lateral movement, and for malware command and control (C&C).

The researchers noted that the DDS codebase is large and complex and this research only scratches the surface.

Related: Vulnerabilities in OpENer Stack Expose Industrial Devices to Attacks

Related: Industrial Firms Informed About Serious Vulnerabilities in Matrikon OPC Product

Related: Vulnerabilities in Protocol Gateways Can Facilitate Attacks on Industrial Systems

view counter

Eduard Kovacs (@EduardKovacs) is a contributing editor at SecurityWeek. He worked as a high school IT teacher for two years before starting a career in journalism as Softpedia’s security news reporter. Eduard holds a bachelor’s degree in industrial informatics and a master’s degree in computer techniques applied in electrical engineering.

Previous Columns by Eduard Kovacs:
Tags:

https://www.securityweek.com/iot-protocol-used-nasa-siemens-and-volkswagen-can-be-exploited-hackers


Network Security Company Netography Raises $45 Million

Network detection and response (NDR) solutions provider Netography has raised $45 million in Series A funding, which brings the total raised by the company to $47.6 million.

The new investment round was led by Bessemer Venture Partners and SYN Ventures. Existing investors Andreessen Horowitz, Harpoon Ventures, Mango Capital, and Wing Venture Capital also contributed.

The network security firm says it will use the capital for the development of new technology and for channel expansion. The company says it also plans to invest in sales.

Founded in 2018, Netography provides customers with a cloud-native SaaS NDR platform that aims to secure what the company calls the atomized network: “the complex, multi-cloud, plus on-premises, plus legacy infrastructure that comprise most enterprise networks today.”

For that, the Maryland, United States-based startup ingests metadata from all systems, to deliver visibility into assets and detection of attacks.

“The appliance model and deep packet inspection will provide less and less utility as we move forward, and it’s time for a new architecture that addresses the needs of modern network environments. By upending this model and approaching security with the mindset of securing atomized networks, Netography provides security teams the protection they actually need for the way their networks look today and going forward as they mbrace a distributed, Web 3.0 world,” Martin Roesch, Netography CEO, said.

Related: Contrast Security Raises $150 Million at ‘Unicorn’ Valuation

Related: Socure Raises $450 Million at $4.5 Billion Valuation

Related: Compliance-as-a-Service Platform Laika Raises $35 Million

Related: Encryption-as-a-Service Provider Vaultree Emerges From Stealth

view counter

Ionut Arghire is an international correspondent for SecurityWeek.

Previous Columns by Ionut Arghire:
Tags:

https://www.securityweek.com/network-security-company-netography-raises-45-million


Fake Emails Sent From FBI Address via Compromised Law Enforcement Portal

Thousands of fake emails coming from an FBI email address were sent out on Friday by someone who exploited a vulnerability in a law enforcement portal. The FBI has confirmed the breach, but said impact was limited.

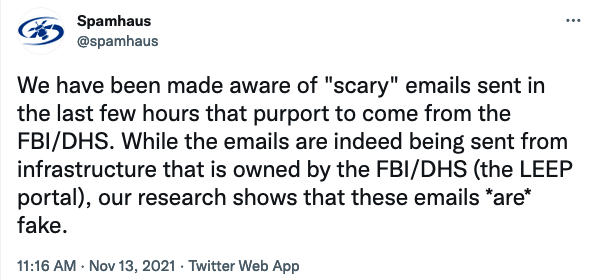
Threat intelligence organization Spamhaus reported seeing more than 100,000 fake emails being sent out in two waves.

Spamhaus warning

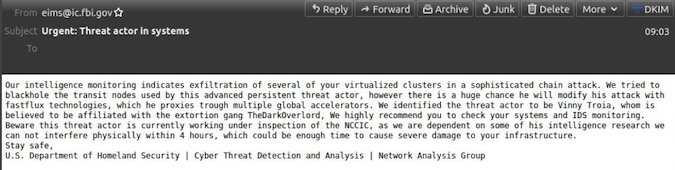
The hoax emails, coming from “[email protected],” carried the subject line “Urgent: Threat actor in systems.” The message appeared to come from the DHS and it informed recipients about “exfiltration of several of your virtualized clusters in a sophisticated chain attack.”

Fake FBI email

The emails claimed the threat actor was identified as Vinny Troia. Troia is a security researcher who claims to have been targeted numerous times by some hackers for exposing them.

Troia on Twitter said he suspected an individual who uses the online moniker “pompompur_in” was behind the attack. He said the individual is associated with a cybercrime group named The Dark Overlord, whose alleged members were exposed in a report published last year by Troia’s company, NightLion Security.

Indeed, an individual with the online nickname pompompurin contacted security blogger Brian Krebs shortly after the fake FBI emails were sent out, taking credit for the attack.

In a statement issued on Sunday, the FBI said the emails were sent out by someone who leveraged a “software misconfiguration” affecting the Law Enforcement Enterprise Portal (LEEP), which is used by the agency to communicate with state and local law enforcement partners.

“While the illegitimate email originated from an FBI operated server, that server was dedicated to pushing notifications for LEEP and was not part of the FBI’s corporate email service,” the FBI stated. “No actor was able to access or compromise any data or PII on the FBI’s network. Once we learned of the incident, we quickly remediated the software vulnerability, warned partners to disregard the fake emails, and confirmed the integrity of our networks.”

Pompompurin told Krebs that they exploited a vulnerability in the LEEP portal account registration process to be able to send out emails from the fbi.gov email address.

Specifically, the registration process involves sending a one-time passcode to the email address of the user who creates an account on the LEEP portal. Pompompurin discovered — or learned from someone else — that this one-time passcode was generated on the client side and included in a POST request. The same request also included parameters for the subject and body content of an email coming from eims(at)ic.fbi.gov, which the hacker replaced with their own subject and content.

The hacker created a script that automated the process, enabling them to send out thousands of fake emails.

The FBI says it has taken steps to prevent exploitation of the weakness leveraged in this attack.

Related: ​​Phishers Target C-Suite with Fake Office 365 Password Expiration Reports

Related: Enterprises Warned About Zix-Themed Credential Phishing Attacks

view counter

Eduard Kovacs (@EduardKovacs) is a contributing editor at SecurityWeek. He worked as a high school IT teacher for two years before starting a career in journalism as Softpedia’s security news reporter. Eduard holds a bachelor’s degree in industrial informatics and a master’s degree in computer techniques applied in electrical engineering.

Previous Columns by Eduard Kovacs:
Tags:

https://www.securityweek.com/fake-emails-sent-fbi-address-compromised-law-enforcement-portal


Intel, AMD Patch High Severity Security Flaws

Chipmakers Intel and AMD this week released patches for multiple security vulnerabilities in a wide range of product lines, including fixes for a series of high-risk issues in software drivers.

AMD published three bulletins this week documenting at least 27 security problems in the AMD Graphics Driver for Windows 10.

Exploitation of these flaws could allow an attacker to escalate privileges on a vulnerable system, leak information, bypass KASLR, cause a denial of service condition, or write arbitrary data to kernel memory, the company said.

AMD rated 18 of vulnerabilities as high-severity, while the remaining 9 are considered medium-risk. Some of these issues were identified and reported last year, and all are addressed with the release of Radeon software 21.4.1 and higher, and 21.Q2 Enterprise Driver.

[READ: Researchers Disclose New Side-Channel Attacks Affecting All AMD CPUs ]

Separately, Intel published a total of 25 advisories this week with patches for many of these vulnerabilities are also available for Intel Core processors with Radeon RX Vega M GL integrated graphics.

The flaws impact Intel Core i5-8305G and i7-8706G processors that feature AMD’s integrated graphics, as well as the Intel graphics driver for Windows 10 64-bit for NUC8i7HNK and NUC8i7HVK. Intel said Version 21.10 or later of these drivers address the bugs.  

Intel also shipped patches for high severity vulnerabilities in PROSet/Wireless WiFi and Killer WiFi, Solid State Drive (SSD) Data Center (DC) products, SoC Watch driver, and Intel processors.

Adversaries could exploit these vulnerabilities to cause a denial of service condition, escalate privileges, or leak information, the company said.

Related: Researchers Disclose New Side-Channel Attacks Affecting All AMD CPUs

Related: Intel Fixes Bugs in NUC 9 Extreme Laptops, Ethernet Linux Drivers

view counter

Ionut Arghire is an international correspondent for SecurityWeek.

Previous Columns by Ionut Arghire:
Tags:

https://www.securityweek.com/intel-amd-patch-high-severity-security-flaws