As ISPs seek payments from Big Tech, Google criticizes “sender-pays” model
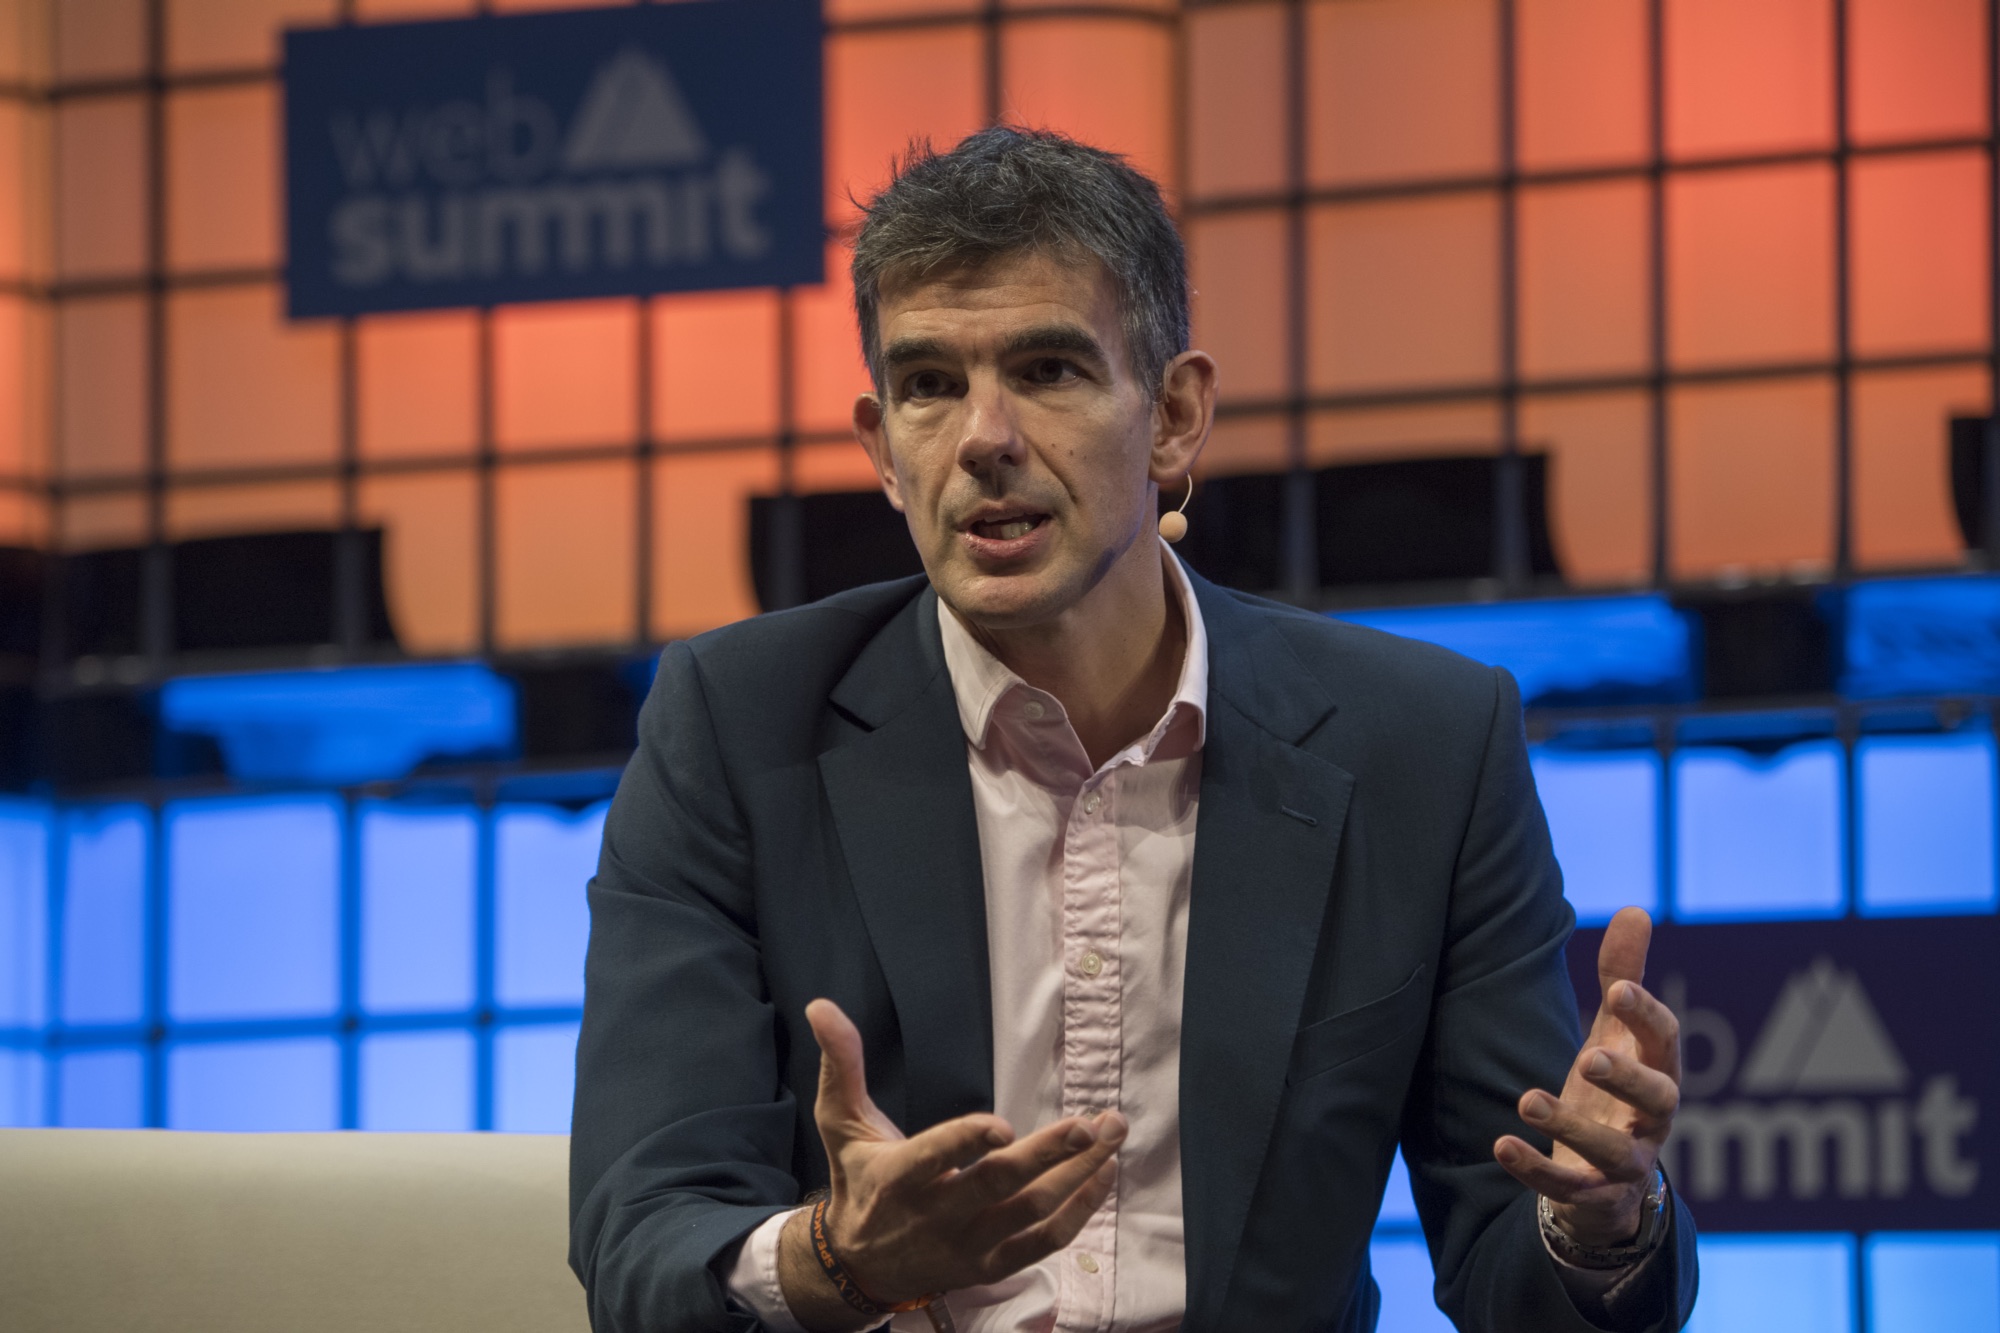
Enlarge/ Google’s Matt Brittin, president of EMEA Business and Operations, speaks at the Web Summit on November 9, 2017, in Lisbon, Portugal.
Getty Images | Horacio Villalobos
Big Tech companies shouldn’t have to pay for Internet service providers’ network-upgrade costs, a Google executive said today amid a push in Europe to have tech companies pay for broadband expansions and improvements.
“Introducing a sender-pays principle is not a new idea, and would upend many of the principles of the open Internet. These arguments are similar to those we heard 10 or more years ago and we have not seen new data that changes the situation,” said Matt Brittin, president of Google’s EMEA business and operations.
Brittin spoke today in a keynote panel at the Tech and Politics Forum presented by Financial Times and telecom lobby group ETNO. Google provided Ars with a copy of his prepared remarks.
Brittin pointed out that Google already invests in network infrastructure “on our own and in collaboration with others,” reducing the strain on broadband network operators. “We carry traffic 99 percent of the way, bringing it closer to users and making it more efficient for our telco partners,” he said.
ISPs want Big Tech to pay
In November 2021, the CEOs of 13 large European telecom companies called on tech giants to pay for a portion of the Internet service providers’ network upgrade costs. “Large and increasing part of network traffic is generated and monetized by big tech platforms, but it requires continuous, intensive network investment and planning by the telecommunications sector,” the telco CEOs wrote in a joint letter. “This model—which enables EU citizens to enjoy the fruits of the digital transformation—can only be sustainable if such big tech platforms also contribute fairly to network costs.”
EU regulators are taking the idea seriously. “The European Union’s executive body will launch a consultation early next year on whether tech giants should bear some of the costs of Europe’s telecoms network,” Reuters wrote on September 9, citing a statement by EU Commissioner for Internal Market Thierry Breton. “Breton said the consultation would be launched in the first quarter of 2023 and take five to six months,” and the European Commission will make proposals after that, Reuters wrote.
The new push to require payments from tech companies has been expected for months, and the idea drew protest from 54 members of the European Parliament (MEPs). “Large telecom companies have tried for decades to require compensation from content providers for providing access to customers, despite the fact that the telecom companies are already being paid by their own customers to provide access,” they wrote in a July 2022 letter.
Letting ISPs collect these payments “would reverse decades of successful Internet economics by requiring the providers of websites and applications to pay fees to ISPs that have never existed before,” and “abolish key net neutrality guarantees that Europeans fought hard for,” the letter said.
https://arstechnica.com/?p=1884596
TikTok can keep operating in US under deal being worked out with Biden
Millions of Americans share data daily on the video-streaming app TikTok—data the federal government considers a national security risk because the app is owned by China, a foreign adversary. Now it has been left up to President Joe Biden to figure out a way to minimize the national security risks without forcing the sale of TikTok or taking away one of America’s favorite apps, as former President Donald Trump tried and failed to do in 2020.
Today, The New York Times reported that Biden may be close to arriving at a potential solution to the TikTok problem. “Four people with knowledge of the discussions” told NYT that over the past few months, the Biden administration has drafted a preliminary agreement with TikTok “to resolve national security concerns.”
Because the negotiation is confidential, all sources requested anonymity, and not much is yet known about the terms. However, there are three main areas of change in the current draft. The first focuses on preventing China-based employees from accessing American data by storing all TikTok data solely on US servers. The second is designed to block Chinese propaganda or disinformation campaigns by granting US-based Oracle power to monitor what’s recommended by algorithms. The last provides some oversight by forming a TikTok board of security experts that oversees TikTok’s US operations and reports directly to the US government. (Oracle declined to comment to NYT and did not immediately respond to Ars.)
Three sources confirmed that the compromise means TikTok has agreed to change how it collects data and who has control over data. However, under the agreement, current TikTok owner ByteDance would retain ownership.
NYT reported that negotiations have not been easy, and high-ranking officials from the Justice Department and the Treasury Department have criticized the current draft as not tough enough on China or doing enough to fully resolve national security risks.
With some of the seemingly key terms of the agreement not yet ironed out, sources told NYT that, ahead of the midterm elections, the ensuing back and forth between the Biden administration and TikTok could “drag out a final resolution for months.”
Every day the resolution is delayed, TikTok continues gulping data, with the most sensitive data points, Trump claimed, “potentially allowing China to track the locations of Federal employees and contractors, build dossiers of personal information for blackmail, and conduct corporate espionage.” NYT reported that the Biden administration’s stance on China “is not substantially different” from Trump’s.
TikTok stirred up controversy when a Buzzfeed News report showed in June that China-based employees had access to US user data that should have been restricted. Buzzfeed’s coverage triggered more public scrutiny on how Biden was approaching the TikTok problem. Back in June, a TikTok spokesperson told Buzzfeed, “We know we’re among the most scrutinized platforms from a security standpoint, and we aim to remove any doubt about the security of US user data. That’s why we hire experts in their fields, continually work to validate our security standards, and bring in reputable, independent third parties to test our defenses.”
Now, TikTok has said that it expects an agreement will be reached with the US—at least as long as Biden’s terms are deemed “reasonable.”
“We will not comment on the specifics of confidential discussions with the US government, but we are confident that we are on a path to fully satisfy all reasonable US national security concerns,” a TikTok spokesperson told Ars.
Any agreement reached, NYT reported, would need to be approved by the Committee on Foreign Investment in the United States and possibly Biden. Neither the White House nor the Justice Department provided comments for the NYT report.
https://arstechnica.com/?p=1884533
Amazon hires unsafe trucking firms twice as often as peers, WSJ finds
For years, people in cars stuck behind blue delivery trucks in traffic have echoed media reports criticizing Amazon for clogging American roadways. It’s well-known that the Amazon drivers steering these fleets of trucks and vans don’t actually work for Amazon but are hired by companies contracted by Amazon, and Amazon has repeatedly denied liability for any dangerous driving reported, though.
Because Amazon has contracts with more than 50,000 firms, just how dangerous Amazon’s contracted drivers really are remains a question that is hard to track. However, The Information reported last year that horrific car crashes are part and parcel of Amazon’s culture of convenience. And then more recently, The Wall Street Journal provided another window into how deadly America’s favorite speedy delivery service can be. Since 2015, WSJ reported this week, “Trucking companies hauling freight for Amazon have been involved in crashes that killed more than 75 people.”
To arrive at this number, WSJ partnered with Jason Miller—a Michigan State University professor who researches transportation safety—to analyze various sources of government data from “3,512 trucking companies that were inspected by authorities three or more times while hauling trailers for Amazon since February 2020.”
The resulting report, WSJ said, “for the first time showed how the safety performance of Amazon’s trucking contractors compared with their peers.” And their results didn’t appear good for Amazon. For example, a review of Department of Transportation data on unsafe driving scores of more than 1,300 Amazon trucking contractors from February 2020 to early August 2022 found that contractors who worked the most with Amazon were “more than twice as likely as all other similar companies to receive bad unsafe driving scores.”
WSJ also found evidence of dozens of companies that Amazon contracted that had “conditional” ratings, which is like DOT putting them on probation—a black mark that typically alienates most firms from contracting them. One Illinois-based company contracted by Amazon “scored worse than the level DOT officials consider problematic” every month of WSJ’s review period.
DOT did not immediately respond to Ars’ request for comment.
Amazon’s response
Amazon spokesperson Kelly Nantel told Ars that WSJ’s report “contains misleading and inaccurate assertions.”
“First and foremost, the insinuation that Amazon puts more value on meeting deadlines than on human lives is categorically false,” Nantel told Ars. “Any accident involving one of our partners or community members is a tragedy, and we always work with our contractors to prevent accidents or learn from them, so they don’t happen again.”
However, WSJ reported that, although Amazon suspends contractors who violate its safety standards, that doesn’t always end concerns of dangerous driving. The Journal’s review of government data showed one Amazon contractor that continued hauling 55 loads after Amazon suspended its contract.
The safety director of Amazon’s freight unit, Steve DasGupta, told WSJ that Amazon’s goal for its “very safe network of tens of thousands of carriers” is “zero accidents, zero fatalities.” A company spokesperson told WSJ that Amazon “offers condolences to families of people killed in crashes that involve its contractors” and noted that Amazon contractors had “a rate of fatalities per vehicle mile about 7 percent lower than the industry average in 2020.”
Since WSJ first contacted Amazon about their report more than two months ago, Amazon has suspended all contractors involved in car crashes described in WSJ’s report, suspended or terminated 80 percent of contracts where WSJ found unsafe driving scores, and made changes to its screening process.
Amazon also told WSJ that “so far this year it has warned or suspended about 1,200 companies in connection with violations” where WSJ found contractors were sub-contracting deliveries—yet another scenario where the keys to the big blue vans could end up in the hands of drivers who might not meet Amazon safety standards.
Nantel told Ars that another issue with WSJ’s report was that the thousands of firms in WSJ’s sample were not representative of Amazon’s network, which contains more than 50,000 contractors. Amazon’s DasGupta told WSJ that the company also prefers to analyze a company’s safety score over a monthly period, not the nearly two-year period that WSJ relied on for its analysis. However, Miller—who helped WSJ with its methodology for their data analysis—told Ars that the two-year window is more appropriate because inspections can be so infrequent.
“Amazon’s critique that only one month of scores should be examined has minimal merit,” Miller told Ars, noting that the longer window ensures “enough inspections are present for meaningful decisions to be made.”
Could Amazon ever be held liable for drivers?
WSJ reported that Amazon has argued in court “that it has little role in overseeing its contractors’ safety on the road.”
Last year, after an Amazon delivery driver barreling down a highway nearly 14 miles per hour over the speed limit slammed into a Tesla, the Tesla driver, Ans Rana, wound up with life-threatening injuries, including spinal cord damage and traumatic brain injury.
Rana sued Amazon, and his case seemed to be the first test of whether Amazon could be held liable for the drivers it contracts. Rana accused the company of everything from informing the driver of the wrong speed limit on its app to negligent practices like sending text message reminders to seemingly prompt drivers to go faster when they fall behind promised delivery times—or risk being terminated.
Among claims Rana made about Amazon’s negligence in the suit was a claim of “mandating a delivery schedule that was unrealistic such that it forced the drivers to rush to the point it was unsafe and as a practical matter made it impossible to drive safely.”
Rana’s case was due to drag on for many more months, with discovery extended until 2023, but Rana’s trial attorney Scott Harrison of Monge & Associates told Ars that mediation has begun. In the next few weeks, the mediation results could reveal more about the larger role that the courts might see Amazon playing when it contracts services from allegedly unsafe delivery drivers. Amazon declined to comment on the lawsuit.
https://arstechnica.com/?p=1884201
Starlink is getting a lot slower as more people use it, speed tests show
Starlink’s median download speeds in the US dropped from 90.6Mbps to 62.5Mbps between the first and second quarters of 2022, according to Ookla speed tests. Starlink’s median upload speeds in the US dropped from 9.3Mbps to 7.2Mbps in the same timeframe.
Median latency also got a little worse for Starlink’s US customers, rising from 43 ms to 48 ms. The latest numbers are in Ooka’s Q2 2022 report on Starlink speeds around the world, released Tuesday. “Starlink speeds decreased in every country we surveyed over the past year as more users sign up for service,” this week’s report said. The Q1 report is available here.
The Q2 report notes significant year-over-year decreases in Starlink speeds in numerous countries, while pointing out that overall performance is still pretty good:
Speedtest Intelligence reveals that median download speeds for Starlink fell across Canada, France, Germany, New Zealand, the UK, and the US, dropping between 9 percent and 54 percent from Q2 2021 to Q2 2022 as more users signed up for the service. However, Starlink still reached a median download speed of at least 60Mbps in North America during Q2 2022, which is more than enough for at least one connected device to do most everything on the Internet including streaming video, downloading games, and chatting on video with friends and family.
Upload speeds also slowed on Starlink, with speeds decreasing across all of the countries we’ve tracked over the past year. Latency fared a little better with latency remaining relatively flat (though high when compared to fixed broadband) in most countries. New Zealand was the outlier, with latency dropping 23 ms. For most users, we still suspect these dips are still worthwhile for areas that have no service, slow service, or few affordable options for fast Internet.
A year ago, in Q2 2021, Ookla reported Starlink median download speeds in the US of 97.2Mbps, uploads of 13.9Mbps, and latency of 45 ms. On its website, Starlink says users should expect download speeds of 50 to 200Mbps, upload speeds of 10 to 20Mbps, and latency of 20 to 40 ms.
FCC cited Ookla tests when denying Starlink grant
Ookla reports, based on user-initiated speed tests, were cited by the Federal Communications Commission last month when it rejected Starlink’s application to receive $885.51 million in broadband funding that had been tentatively awarded during then-Chairman Ajit Pai’s tenure. The FCC said it doubts whether Starlink can provide the grant’s required speeds of 100Mbps downloads and 20Mbps uploads.
“We observe that Ookla data reported as of July 31, 2022 indicate that Starlink’s speeds have been declining from the last quarter of 2021 to the second quarter of 2022, including upload speeds that are falling well below 20Mbps,” the FCC said at the time. Ookla, a private company, operates a widely used speed testing service and boasts that its data is often used by government and regulatory bodies.
The FCC’s doubts are also fueled by what the agency called Starlink’s “recognized capacity constraints.” SpaceX CEO Elon Musk has acknowledged Starlink’s capacity limits several times, for example, saying the satellite service will face “a challenge [serving everyone] when we get into the several million user range.” Starlink had nearly 500,000 users in 32 countries, according to a SpaceX presentation Musk posted on his Twitter account in early June.
This month, Starlink asked the FCC to reverse the grant decision and award the funding, saying the agency “relied on unauthorized outside speed tests.” Starlink also said speeds would improve as it launches more satellites. “First, the Ookla data covers a period of time more than three years before SpaceX’s first mandatory deployment milestone in 2025. But by 2025, the Starlink Network will have substantially more capacity than it did at the time of the speed tests in question,” the SpaceX division told the FCC.
Starlink has more than 3,000 satellites in orbit so far. The Internet provider has FCC permission to deploy nearly 12,000 satellites, including those already being operated, and is seeking authorization to launch tens of thousands eventually.
Users complain of slowing speeds
In addition to speed tests, anecdotal evidence suggests Starlink slowed down as the number of users grew. A PCMag article in July quoted several users complaining about speeds, including a Texas user who “encountered download rates on his Starlink dish that can dive as low as 1Mbps, especially during the evenings.” More users complained of slowdowns in threads on the Starlink subreddit.
Despite the evidence of Starlink getting slower, Ookla’s second-quarter data shows it clearly outperforms Viasat and HughesNet satellite services that have lower speeds and much worse latency. In the US, Viasat posted median download speeds of 23.7Mbps, upload speeds of 2.8Mbps, and 631 ms latency. HughesNet was measured at 22.6Mbps downloads, 2.5Mbps uploads, and 716 ms latency.
Wireline broadband is still the best. Overall, fixed broadband services in the US posted median download speeds of 150.1Mbps, uploads of 21.5Mbps, and 14 ms latency, the Q2 Ookla report said.
From the beginning, it was clear that Starlink is most appropriate for people who don’t have a solid cable or fiber connection in their homes. The recent data doesn’t change that overall conclusion, but Starlink users who are getting slower-than-expected speeds have good reason to be frustrated.
https://arstechnica.com/?p=1884083
Report: UK authorities have arrested a teenager linked to GTA VI leak
Enlarge/ Artist’s rendition of the recent arrest of a 17-year-old hacker in the UK.
Rockstar Games
A Thursday night arrest of a 17-year-old in the UK may have led to the capture of one of the biggest video game-related leakers in recent history.
London police forces confirmed their apprehension of an Oxford suspect on a social media channel regularly used for police arrest updates, and it clarified the suspect’s age, a vague charge of “suspicion of hacking,” and that the investigation was coordinated with the UK’s National Crime Agency (NCA) and specifically its National Cyber Crime Unit.
The gaming leak in question was among the highest profile in recent history, as it essentially contained the world premiere of highly anticipated video game Grand Theft Auto VI. Up until this week’s leak, series fans were left with rumors and hearsay about its potential setting (a Miami-like city that resembles the series’ Vice City) and its protagonists (a “Bonnie and Clyde” pair of protagonists, including the first playable woman in a mainline GTA game). Both of those rumors were confirmed by the leak, which Rockstar eventually confirmed was legitimate and sourced from a 3-year-old version of the game.
Before Thursday’s arrest, the GTA VI gameplay leaker originally claimed involvement in a recent massive breach of Uber’s data, as well—and Uber publicly blamed the hacking collective Lapsus$ for that intrusion. Previously, at least one teenage boy from Oxford had been linked to the hacking efforts of Lapsus$ by a BBC report. UK authorities did not confirm that report’s veracity at the time, due to privacy rules about underage suspects. Thus, while the GTA VI leak could be connected to efforts by Lapsus$, that connection remains unconfirmed as of press time.
Ars Technica’s Dan Goodin previously reported on Lapsus$’s hacking efforts as they were chronicled by members on their official Telegram chat channels. Many of the group’s methods, at least as publicly revealed, took advantage of vulnerabilities in standard “two-factor” multifactor authentication systems—which usually revolve around less secure backup login options that an attacker can exploit. The GTA VI leaker previously suggested that they gained unauthorized access to Rockstar’s source code via accessing the company’s Slack chat interface, but as of press time, it’s unclear whether this too was a matter of “MFA bombing” to trick an employee into unwittingly accepting something like a phone call prompt.
Should this week’s Oxford arrest be connected to the GTA VI leak, that timeline would be far more accelerated than we saw in another memorable European source code leak. German hacker Axel Gembe eventually recounted the story of his apprehension after he breached Valve’s computer systems to download the source code to Half-Life 2. That raid and subsequent arrest took place roughly eight months after the leak was originally reported.
https://arstechnica.com/?p=1884067
Facebook users sue Meta for bypassing beefy Apple security to spy on millions
Meta’s business model depends on selling user data to advertisers, and it seems that the owner of Facebook and Instagram sought new paths to continue widely gathering data and to recover from the suddenly lost revenue. Last month, a privacy researcher and former Google engineer, Felix Krause, alleged that one way Meta sought to recover its losses was by directing any link a user clicks in the app to open in-browser, where Krause reported that Meta was able to inject a code, alter the external websites, and track “anything you do on any website,” including tracking passwords, without user consent.
Now, within the past week, two class action lawsuits [1][2] from three Facebook and iOS users—who point directly to Krause’s research—are suing Meta on behalf of all iOS users impacted, accusing Meta of concealing privacy risks, circumventing iOS user privacy choices, and intercepting, monitoring, and recording all activity on third-party websites viewed in Facebook or Instagram’s browser. This includes form entries and screenshots granting Meta a secretive pipeline through its in-app browser to access “personally identifiable information, private health details, text entries, and other sensitive confidential facts”—seemingly without users even knowing the data collection is happening.
The most recent complaint was filed yesterday by California-based Gabriele Willis and Louisiana-based Kerreisha Davis. A lawyer from their legal team at Girard Sharp LLP, Adam Polk, told Ars that it was an important case to stop Meta from getting away with concealing ongoing privacy invasions. In the complaint, the legal team pointed to prior Meta misdeeds in gathering user information without consent, noting for the court that a Federal Trade Commission investigation resulted in a $5 billion fine for Meta.
“Merely using an app doesn’t give the app company license to look over your shoulder when you click on a link,” Polk told Ars. “This litigation seeks to hold Meta accountable for secretly monitoring people’s browsing activity through its in-app tracking even when they haven’t allowed Meta to do that.”
Meta did not immediately respond to Ars’ request for comment. Krause told Ars he prefers not to comment.
Meta allegedly secretly tracks data
According to the complaints, which rely on the same facts, Krause’s research “revealed that Meta has been injecting code into third-party websites, a practice that allows Meta to track users and intercept data that would otherwise be unavailable to it.”
To investigate the potential privacy issue, Krause built a website called inappbrowser.com, where users could “detect whether a particular in-app browser is injecting code into third-party websites.” He compared an app like Telegram, which doesn’t inject JavaScript code into third-party websites to track user data in its in-app browser, with the Facebook app by tracking what happens in the HTML file when a user clicks a link.
In the case of tests run on Facebook and Instagram apps, Krause reported that the HTML file clearly showed that “Meta uses JavaScript to alter websites and override its users’ default privacy settings by directing users to Facebook’s in-app browser instead of their pre-programmed default web browser.”
The complaints note that this tactic of injecting code seemingly employed by Meta to “eavesdrop” on users was originally known as a JavaScript Injection Attack. The lawsuit defines that as instances where “a threat actor injects malicious code directly into the client-side JavaScript. This allows the threat actor to manipulate the website or web application and collect sensitive data, such as personally identifiable information (PII) or payment information.”
“Meta now is using this coding tool to gain an advantage over its competitors and, in relation to iOS users, preserve its ability to intercept and track their communications,” the complaint alleges.
According to the complaints, “Meta acknowledged that it tracks Facebook users’ in-app browsing activity” when Krause reported the issue to its bug bounty program. The complaints say that Meta also confirmed at that time that it uses data collected from in-app browsing for targeted advertising.
https://arstechnica.com/?p=1883760
Florida to Supreme Court: Let us regulate social networks as common carriers
Florida yesterday asked the US Supreme Court to reinstate its social media regulation law that made it illegal for sites like Facebook and Twitter to ban politicians.
Florida’s petition said the Supreme Court should answer the questions of whether the First Amendment prohibits states “from requiring that social-media companies host third-party communications, and from regulating the time, place, and manner in which they do so,” and whether the First Amendment prohibits states “from requiring social-media companies to notify and provide an explanation to their users when they censor the user’s speech.”
The Florida law is currently blocked by an order issued by the US Court of Appeals for the 11th Circuit, which made its ruling in a lawsuit filed by Big Tech industry groups. Florida filed its Supreme Court petition several days after a Texas social media law was reinstated by the US Court of Appeals for the 5th Circuit.
Florida’s petition points to the contrasting decisions by the 5th and 11th Circuit courts as evidence that the Supreme Court should settle the over-arching questions relevant to both cases. Florida said the case over its own law is “an ideal vehicle” for considering “whether social-media platforms are ‘speaking’ when they host third-party speech.”
A previous 5th Circuit ruling in the Texas case was vacated by the Supreme Court in May, suggesting the states face an uphill battle. The governors of Florida and Texas have both argued that state laws are needed to prevent censorship of conservatives on social media.
The Big Tech industry groups that sued Florida also said they want the Supreme Court to decide the case.
Florida wants common-carrier rules for social networks
Florida told the Supreme Court the “Eleventh Circuit erred at the outset when it concluded that the hosting regulations in Florida’s social-media law triggered heightened First Amendment scrutiny.” Florida also said the court “erred in its alternative holding that the platforms’ hosting decisions were inherently expressive.”
“Next, the Eleventh Circuit erroneously concluded that Florida could not regulate social-media platforms as common carriers, and in doing so, require the platforms to openly accept users,” Florida argued. The state pointed to Supreme Court Justice Clarence Thomas’ opinion backing the idea that social media companies can be treated as common carriers.
The Florida law says a social media platform “may not willfully deplatform a candidate for office” and imposes fines of up to $250,000 per day on social media companies that ban candidates for elected office. The law also says social platforms “may not apply or use post-prioritization or shadow banning algorithms for content and material posted by or about… a candidate,” and may not “censor, deplatform, or shadow ban a journalistic enterprise based on the content of its publication or broadcast.”
The Texas law says a “social media platform may not censor a user” based on the user’s “viewpoint” and defines “censor” as “block, ban, remove, deplatform, demonetize, de-boost, restrict, deny equal access or visibility to, or otherwise discriminate against expression.”
https://arstechnica.com/?p=1883762
NTSB wants alcohol detection systems installed in all new cars in US
Getty Images | rolfo
The US National Transportation Safety Board (NTSB) yesterday recommended that all new vehicles be equipped with alcohol detection systems that can stop people from driving when drunk.
The NTSB can’t issue such a regulation on its own but urged the National Highway Traffic Safety Administration (NHTSA) to do so. The NTSB said it “is recommending measures leveraging new in-vehicle technologies that can limit or prohibit impaired drivers from operating their vehicles as well as technologies to prevent speeding.”
If adopted, this would require “passive vehicle-integrated alcohol impairment detection systems, advanced driver monitoring systems or a combination of the two that would be capable of preventing or limiting vehicle operation if it detects driver impairment by alcohol,” the NTSB said. The agency urged the NHTSA to “require all new vehicles to be equipped with such systems.”
Under a US law enacted last year, the NHTSA is already required to examine whether it can issue this type of rule.
While drunk driving is a longstanding problem that has caused many deaths, the NTSB said its recommendation was spurred by its investigation into one crash that killed nine people—including seven children—in January 2021 on State Route 33 near Avenal, California. On that two-lane highway with a speed limit of 55 mph, an SUV driver leaving a New Year’s Day gathering “was driving at a speed between 88 and 98 mph,” the NTSB report said.
Nine dead in drunk-driving crash
The driver failed to maintain control of his vehicle due to alcohol use, and “his blood alcohol concentration was more than double California’s per se legal limit of 0.08 grams per deciliter,” the NTSB said. The crash killed the SUV driver and eight people in a pickup truck, the agency said:
The SUV partially departed from the paved roadway onto a dirt and gravel shoulder area to the right. The SUV driver then made a steering correction to the left, causing the vehicle to go out of control. The SUV crossed the highway centerline and intruded into the northbound lane directly in front of a northbound pickup truck, which was occupied by an adult driver and seven passengers, ranging in age from 6 to 15 years old, and was traveling at a speed between 64 and 70 mph. The SUV and pickup truck collided head-on. The pickup truck immediately caught on fire, and other vehicle operators on SR 33 who stopped at the crash scene had insufficient time to extricate any occupants before fire engulfed the truck. As a result of the crash, the SUV driver and all eight pickup truck occupants died.
While post-crash toxicology tests “detected evidence of cannabis use, the NTSB was unable to determine whether the effects of cannabis use contributed to the driver’s impairment,” the NTSB said. The probable cause of the fatal crash “was the failure of the sport utility vehicle (SUV) driver to control his vehicle due to a high level of alcohol impairment,” the NTSB said.
We asked the NHTSA today if it plans to require new vehicles to be equipped with alcohol detection systems. An NHTSA spokesperson responded with a statement saying, “The only acceptable number of impaired driving crashes is zero. The agency has initiated work to meet the Bipartisan Infrastructure Law’s requirement for rulemaking concerning advanced impaired driving technology in vehicles.” The law was enacted in November 2021.
https://arstechnica.com/?p=1883361
Telegram has a serious doxxing problem
Eugene Mymrin / Getty Images
Burmese influencer Han Nyein Oo rose to prominence in 2020, posting memes and gossip about Burmese celebrities on Facebook to an audience that grew to several hundred thousand people in Myanmar by early 2021. Then, after the country’s military seized power that February, he lurched rightwards, becoming a full-blooded supporter of the junta, which has killed more than 1,500 people and arrested thousands more in bloody crackdowns.
He was soon banned from Facebook for violating its terms of service, so he moved to Telegram, the encrypted messaging app and social sharing platform. There, he posted messages of support for the military, graphic pictures of murdered civilians, and doctored pornographic images purporting to be female opposition figures. Often, these were cross-posted in other channels run by a network of pro-junta influencers, reaching tens of thousands of users.
This year, Han Nyein Oo moved on to direct threats. Opponents of the junta planned to mark the anniversary of the coup on February 1 with a “silent strike,” closing businesses and staying home to leave the streets abandoned. On his Telegram channel, Han Nyein Oo raged, asking his followers to send him photos of shops and businesses that were planning to shut. They obliged, and he began posting the images and addresses to his 100,000 followers. Dozens of premises were raided by police. Han Nyein Oo claimed credit. He did not respond to a request to comment.
“That was the start of the doxxing campaign,” says Wai Phyo Myint, a Burmese digital rights activist. “Since then there’s been an escalation.”
Over the past eight months, Han Nyein Oo’s Telegram channels, and those of other pro-coup figures, including self-defined journalist Thazin Oo and influencers Kyaw Swar and Sergeant Phoe Si, have doxxed hundreds of people that they accuse of siding with the resistance movement, from high-profile celebrities to small-business owners and students. Dozens have since been arrested or been killed in vigilante violence.
Han Nyein Oo’s channel was taken down in March after it was reported for breaching Telegram’s rules on disseminating pornography, but within days he had started another. It now has more than 70,000 followers.
Telegram’s doxxing problem goes far beyond Myanmar. WIRED spoke to activists and experts in the Middle East, Southeast Asia, and Eastern Europe who said that the platform has ignored their warnings about an epidemic of politically motivated doxxing, allowing dangerous content to proliferate, leading to intimidation, violence, and deaths.
In a Telegram message, company spokesperson Remi Vaughn said: “Since its launch, Telegram has actively moderated harmful content on its platform—including the publication of private information. Our moderators proactively monitor public parts of the app as well as accepting user reports in order to remove content that breaches our terms.”
Telegram, which now claims more than 700 million active users worldwide, has a publicly stated philosophy that private communications should be beyond the reach of governments. That has made it popular among people living under authoritarian regimes all over the world (and among conspiracy theorists, anti-vaxxers, and “sovereign citizens” in democratic countries).
But the service’s structure—part encrypted messaging app, part social media platform—and its almost complete lack of active moderation has made it “the perfect tool” for the kind of doxxing campaigns occurring in Myanmar, according to digital rights activist Victoire Rio.
This structure makes it easy for users to crowdsource attacks, posting a target for doxxing and encouraging their followers to dig up or share private information, which they can then broadcast more widely. Misinformation or doxxing content can move seamlessly from anonymous individual accounts to channels with thousands of users. Cross-posting is straightforward, so that channels can feed off one another, creating a kind of virality without algorithms that actively promote harmful content. “Structurally, it’s suited to this use case,” Rio says.
https://arstechnica.com/?p=1883287
US lawmakers escalate pressure on Chinese chipmaker YMTC
Top US lawmakers are urging the Biden administration to put Chinese semiconductor company Yangtze Memory Technologies Co on a blacklist for allegedly violating export controls by supplying Huawei.
Democratic Senate Majority Leader Chuck Schumer told the Financial Times that he was concerned about a report, obtained by the FT, that showed YMTC has provided NAND memory chips for the Mate Xs 2, the new flagship foldable phone from Huawei, the Chinese telecoms equipment giant.
“This report is extremely troubling and further underscores the need for the administration to act swiftly to add YMTC to the entity list,” Schumer said, in a reference to the commerce department blacklist that effectively bars US companies from selling technology to groups on the list.
YMTC is one of many Chinese technology companies to have come under scrutiny in the US over security concerns. Washington is also implementing a range of measures to boost the US chip industry while making it harder for China to gain access to technology, particularly for cutting-edge chips.
According to the report from IP Research Group, a consultancy that analyzes electronic devices, YMTC is providing Huawei with chips for the phone, suggesting a possible violation of the US Foreign Direct Product Rule.
The rule, introduced by the Trump administration in 2020, bars companies from supplying Huawei with technology that is made in America.
Senator Mark Warner and Senator Marco Rubio—the Democratic chair and Republican vice-chair of the Senate Intelligence Committee, respectively—also supported adding YMTC to the entity list. Their call for action was joined by Michael McCaul, the top Republican on the House Foreign Affairs Committee.
“It has been clear for some time now that YMTC is a bad actor—and a key part of the Chinese Communist Party’s goal of shifting control of global microelectronics to the PRC [People’s Republic of China]” Warner said. “It’s long past time to act.”
The White House has described YMTC as a Chinese “national champion.” US lawmakers and officials are also concerned that as YMTC produces more advanced chips, it will dump them at below-market prices, putting pressure on US, European, and other Asian manufacturers.
“Make no mistake: when it comes to enriching the Chinese Communist Party, what Huawei does for phones, YMTC does for memory chips,” Rubio told the FT. “It’s no surprise the two Chinese companies continue to break US law by partnering together.”
Rubio added: “The longer that President Biden drags his feet in recognizing this, the more it signals to greedy corporations that it’s OK to do business with them and other Beijing-directed firms.”
The FT reported in April that the commerce department was examining claims that YMTC had supplied memory chips to Huawei for another phone.
“This report closes down any question that YMTC is not violating US export controls,” McCaul said on Tuesday. “This is a problem that could be solved with the stroke of a pen. Why is [commerce secretary Gina] Raimondo ignoring this problem?”
A commerce department official declined to comment on YMTC but said the Bureau of Industry and Security was “conducting a review of existing policies related to China and will potentially seek to employ a variety of legal, regulatory, and, when relevant, enforcement tools to keep advanced technologies out of the wrong hands.”
US lawmakers have also put pressure on Apple over YMTC, after the iPhone maker told the FT it was considering procuring memory chips from the Wuhan-based company.
To prove that YMTC has violated the FDPR, the US would have to show that it knew its chips were destined for Huawei, which might not be the case if they were sold through an intermediary.
But one person familiar with an analysis of the Mate Xs 2 said it contained Huawei-produced components that would require the phone manufacturer to deal directly with YMTC in order to tailor the chips for the foldable smartphone.
Huawei declined to comment. YMTC did not immediately respond to a request for comment.