Big gaming companies get DHS help to keep players from becoming terrorists
Big gaming companies get DHS help to keep players from becoming terrorists

Last December, the United Nations warned of an overlooked but critical “emerging terrorist threat”: extremists radicalizing members of online gaming communities.

Despite ample interest in saving gamers from such exploitation, experts say that a lack of research funding on the topic has put the gaming industry behind social networks when it comes to counterterrorism efforts. That’s starting to change, though. Within the past week, researchers told Ars that the US Department of Homeland Security has, for the first time, awarded funding—nearly $700,000—to a research group working directly with major gaming companies to develop effective counterterrorism methods and protect vulnerable gamers.

The new project will span two years. It’s spearheaded by Middlebury College’s Institute of International Studies, which hosts the Center on Terrorism, Extremism, and Counterterrorism (CTEC). Vice reported that other partners include a nonprofit called Take This, which focuses on gaming impacts on mental health, and a tech company called Logically, which Vice says works “to solve the problem of bad online behavior at scale.”

The researchers have summarized their overarching goals for the DHS project as “the development of a set of best practices and centralized resources for monitoring and evaluation of extremist activities as well as a series of training workshops for the monitoring, detection, and prevention of extremist exploitation in gaming spaces for community managers, multiplayer designers, lore developers, mechanics designers, and trust and safety professionals.”

Take This research director Rachel Kowert told Ars that the primary objective of the project is to develop gaming industry-focused resources. Her group’s ambitious plan is to reach out to big companies first, then engage smaller companies and indie developers for maximum impact.

Alex Newhouse, deputy director of CTEC, told Ars that the project will start by targeting big gaming companies that “essentially act like social platforms,” including Roblox, Activision Blizzard, and Bungie.

Although project funding was just approved, Newhouse said that CTEC’s work has already begun. For six months, the group has been working with Roblox, and Newhouse said it is also in “very preliminary” talks with the Entertainment Software Association about ways to expand the project.

Borrowing social media counterterrorism methods

Newhouse said that within DHS, the FBI has become increasingly interested in research like CTEC’s to combat domestic terrorism—but, to his knowledge, no federal organization has funded such data collection. Although his project is only funded for two years, Newhouse wants to push the gaming industry within five years to implement the same standards for combating extremism that social networking platforms already have.

“I want game developers, especially big ones like Roblox and Microsoft, to have dedicated counterextremism in-games teams,” Newhouse told Ars. “In these days, we need to push to be that sophisticated on the games industry side as well.”

Newhouse plans to rely on his experience helping tech giants like Google and Facebook organize counterterrorism teams. He says that CTEC’s biggest priority is convincing the gaming industry to invest in proactively moderating extremist content by “implementing increasingly sophisticated proactive detection and moderation systems” that social networks also use.

Historically, Newhouse said that gaming companies have relied mostly on players to report extremist content for moderation. That’s not a good enough strategy, he said, because radicalization often works by pumping up a gamer’s self-esteem, and people who are manipulated to view this sort of online engagement as positive often don’t self-report these radicalizing events. By relying strictly on user reports, gaming companies are “not going to actually detect anything on the initial recruitment and radicalization level,” he said.

Daniel Kelley, the associate director for the Anti-Defamation League’s Center for Technology and Society, told Ars that online gaming companies are approximately 10 years behind social media companies in flagging this issue as critical.

Limited funding for online gaming counterextremism efforts

Kowert, of Take This, first became interested in the link between online gaming communities and real-world violent extremism after she encountered a 2019 nationally representative survey from ADL. It found that nearly 1 in 4 respondents “were exposed to extremist white supremacist ideology in online games.” Newhouse said that estimate is “probably too conservative at this point.”

Still, ADL said, “the evidence of the widespread extremist recruiting or organizing in online game environments (such as in Fortnite or other popular titles) remains anecdotal at best, and more research is required before any broad-based claims can be made.”

Today, the research base remains limited, but it has become apparent that the issue is not just impacting adults. When ADL expanded its survey in 2021 to reach almost 100 million respondents, the survey included young gamers ages 13–17 for the first time. ADL found that 10 percent of young gamers were “exposed to white supremacist ideologies in the context of online multiplayer games.”

Kowert immediately responded to the 2019 ADL report by pivoting her research and teaming up with Newhouse. She told Ars that the reason there’s so little research is because there’s so little funding.

Kelley told Ars that while it’s good to see research finally receive funding, ADL recommends that government inject way more funding into nipping the issue in the bud. “This is not a time to be supporting stuff with drop-in-the-bucket funds,” Kelley said. “There’s a lot more that the Department of Justice needs to do to fund these kinds of efforts.”

https://arstechnica.com/?p=1882731


Apple is top funder of lobby group that says it represents small developers

A large Apple logo seen at an Apple Store.

Apple provides over half the funding for a lobby group that says it represents small app developers, according to a Bloomberg article published today. Apple isn’t a member of what’s called the App Association, but “it plays a dominant behind-the-scenes role shaping the group’s policy positions, according to four former App Association employees who asked not to be named discussing internal matters,” Bloomberg wrote.

The App Association says it “gives a voice to small technology companies” and that its “policy priorities reflect the opportunities and challenges today’s small business app developers and IoT innovators face in the app ecosystem.” But its positions on major legislation have aligned with Apple’s. The group’s list of policy statements going back to early 2017 include some specifically praising Apple and others opposing legislation that Apple also opposes, such as antitrust bills targeting Big Tech.

One bill opposed by the App Association is the Open App Markets Act, which aimed to help app developers use alternative in-app payment systems and avoid Apple’s standard cuts of 15 to 30 percent. The Apple-funded group also opposed the American Innovation and Choice Online Act, which would have prohibited app stores and other large online platforms from giving preference to their own products at the expense of competitors. Both bills have stalled in the face of Big Tech opposition.

According to Bloomberg, the App Association (also known as “ACT”) confirmed that over half its funding comes from Apple, but “former employees say the actual percentage is much higher.” The group’s total funding was over $9 million in 2020.

“ACT representatives regularly testify in Congress, file court briefs in defense of Apple’s positions and host annual ‘fly-in’ meetings for developers with lawmakers,” Bloomberg wrote.

Apple drove increase in group’s funding

An App Association spokesperson told Ars that in 2020, “Apple’s commitment contributed more than 50 percent of the App Association’s sponsorship revenue, making their support one of many contributors for the year.” The App Association did not answer our question about what role Apple plays in shaping its policy.

The group also told Ars it “is proud to represent thousands of independent developers to foster an inclusive and secure developer ecosystem and app marketplace. Our members drive the organization’s policy and legislative agenda.”

“As per our preliminary 2020 [Form] 990 filings, the organization saw an increase in sponsorship revenue to support our small business members’ advocacy efforts such as privacy, broadband, and in helping our members navigate the early stages of the pandemic, including connected health, workforce maintenance/development, and access to government funding for ongoing business operations,” the App Association said.

The App Association’s website lists about two dozen employees and says the group “represents more than 5,000 app makers and connected device companies in the mobile economy.” The “members are located around the world, in all 27 member countries of the European Union and in all 435 congressional districts of the United States.”

The App Association told Ars that its full member list is proprietary, but 38 that agreed to be named publicly are listed here. US-based members include Concentric Sky, Startup Health, SheerID, Dogtown Media, Wellbeyond, Stroll Health, Project Hosts, Colorado Technology Consultants, MotionMobs, Rimidi, Southern DNA, Devscale, BadVR, CannedSpinach, BitSource, SentryOne, and AirStrip.

We contacted Apple today and will update this article if we get a response.

Group denies being mere front for Apple

According to Bloomberg, ACT President Morgan Reed “and other ACT executives said that they determine policy positions based on the preferences of their members and don’t take direction from Apple, though they take Apple’s positions into account.” Reed told Bloomberg in an interview “that it ‘doesn’t pass the laugh test’ to say the association is fronting for Apple.”

“Our job is to make sure we’re paying attention to the way that government can have an impact, unintended or otherwise, on all of those small businesses making cool software products,” he said.

Another group, called the Coalition for App Fairness, whose members include Basecamp, Deezer, Epic Games, Match Group, Proton, Spotify, and others, has lobbied in favor of Big Tech antitrust legislation. For example, the group argued that the American Innovation and Choice Online Act would “bar monopolistic platforms from discriminating among business users in a way that materially harms competition.”

The Coalition for App Fairness criticized the App Association in a tweet today. “An association that is funded primarily by Apple and represents Apple’s interests against developers and their customers, is a front group for Apple no matter how it brands itself,” the group said.

Apple has also opposed antitrust legislation in more direct ways. CEO Tim Cook publicly spoke out against legislation that would require Apple to allow sideloading, and the company ramped up federal lobbying expenditures and became one of the main funders of a new group called the Chamber of Progress.

https://arstechnica.com/?p=1882617


Punishment, puppies, and science: Bringing dog training to heel

Teenager playing fetch with her dog
Enlarge / Teenager playing fetch with her dog

Three years ago, Valli Fraser-Celin adopted a blonde husky mix puppy, whom she named Husk. Fraser-Celin soon started looking for ways to curb Husk’s “totally wild” behavior, she said, like stealing food from the kitchen counter and barking incessantly at strangers. Based on the advice of a YouTube trainer, Fraser-Celin started using an electronic collar, or e-collar, that delivered a small shock when Husk misbehaved, but said she felt “yucky” about it.

Fraser-Celin rethought her approach after hearing about an animal trainer who taught a grizzly bear to cooperate with medical treatment using only positive reinforcement. If that hulking animal could learn with treats and praise, she thought, why were dog trainers using prong and shock collars? “That was the catalyst into my advocacy,” said Fraser-Celin, who studied African wild dogs for her Ph.D. and now works as a remote community liaison for the Winnipeg Humane Society and advocates independently for positive reinforcement training on Instagram. “I really think that there needs to be regulations that are put into place,” she said, “based on the science and the studies that have shown the best type of training for dogs.”

Fraser-Celin is not alone. Many researchers, trainers, and veterinary and training professional organizations are advocating for greater oversight for dog training, which is largely unregulated worldwide—though they sometimes disagree on the best path of action and choose to focus on the research that reinforces their preferred approach. “Right now, it’s the wild, wild West,” said Anamarie Johnson, a psychology Ph.D. student at Arizona State University with a background in animal behavior and dog training. She recently published a study that analyzed the websites of 100 highly-rated dog trainers across the US, which found that most gave no indication whether the trainer had relevant education or certification.

“Anyone can identify as a dog trainer—they can put up a social media page, they can offer services to the public, and there’s no expectations for their education, their continuing education, or their standards of practice,” said Bradley Phifer, the executive director of the Certification Council for Professional Dog Trainers, or CCPDT, an organization promoting science-based training standards. People with little or no education in animal behavior may be advising owners on handling aggression, he added. “There’s a big consumer protection piece here, that if you’re not adequately trained, or you don’t have adequate experience in the industry or in the content, then you shouldn’t be advising people on how to prevent dog bites.”

Some experts and organizations are pushing for greater regulation of the industry. Under an umbrella organization known as the Alliance for Professionalism in Dog Training, two major certification bodies—the CCPDT and the Association of Professional Dog Trainers, or APDT—have jointly proposed model legislation that they hope could be adopted on a state-by-state basis. The legislation would require trainer licensure by a state board, create accountability standards, and require trainers to engage in continued education. Phifer said he’s currently working with legislators in New Jersey, where regulations for dog trainers were first proposed in 2019, and that the joint effort is also making progress in California and Illinois.

But the push for regulation has exposed a schism in the industry over using punishments versus rewards. Under the proposed legislation, certifying bodies would be required to uphold a policy that prioritizes positive reinforcement, though does not entirely rule out punishment—an approach generally backed by research on efficacy and welfare and increasingly popular among training professionals. While researchers and trainers largely agree that punishment-heavy approaches are harmful, they are at odds whether all-out bans on aversive tools are productive, since the approach may work in limited circumstances.

Without clearer rules, the broad gaps in dog training pose “a potentially very large safety risk to the public,” said Johnson, because dog owners are trusting trainers to modify the behavior of animals with “sharp, pointy teeth that live in our house.”

Modern dog training is rooted in the mid-20th-century work of American psychologist B.F. Skinner, who suggested four categories for behavior modification: positive reinforcement, positive punishment, negative reinforcement, and negative punishment. Here, positive and negative don’t necessarily mean good or bad. Positive reinforcement adds something a dog likes to reinforce a behavior, such as a treat or a toy for sitting on cue, while positive punishment adds something aversive, like a tug on a leash, to decrease a behavior. Negative reinforcement removes something the dog dislikes, such as stopping a shock collar when a dog obeys a command, while negative punishment removes something desirable, such as facing away from a dog that is jumping for attention.

Many trainers and animal behavior experts say that aversive methods, which include positive punishment and negative reinforcement, are overused. Two major professional organizations that represent trainers—the APDT and the International Association of Animal Behavior Consultants—now limit the use of tools like e-collars among their members.

In October last year, the American Veterinary Society of Animal Behavior, which includes both veterinarians and behaviorists with doctorate-level education in animal behavior, issued a statement: “There is no evidence that aversive training is necessary for dog training or behavior modification,” referencing 21 studies on the effectiveness of reward-based methods and risks of aversive methods. Alexandra Protopopova, an animal welfare researcher at The University of British Columbia, wrote in an email to Undark that the recent research cited by the statement reflected the “undeniable” risks of aversive techniques, adding: “Ultimately, recent research has also shown that aversive methods do not result in better trained dogs; thereby making traditional aversive dog training methods obsolete.”

The research has raised concerns about dog welfare. In one small study, dogs trained with rewards appeared to be more playful and better at learning a novel behavior than dogs whose owners reported using punishment. In another, dogs reportedly trained with aversive tools were, as the researchers put it, more “pessimistic” than dogs that were not, based on their hesitation in approaching a bowl of food. Some evidence also suggests that use of punishment in training can diminish the bond between a dog owner and their canine.

https://arstechnica.com/?p=1881676


Federal court upholds law banning tech companies from censoring viewpoints

Federal court upholds law banning tech companies from censoring viewpoints

For the past year, Texas has been fighting in court to uphold a controversial law that would ban tech companies from content moderation based on viewpoints. In May, the Supreme Court narrowly blocked the law, but this seemed to do little to settle the matter. Today, the 5th Circuit Court of Appeals overturned a lower Texas court’s decision to block the law, ruling instead that the Texas law be upheld, The Washington Post reported.

According to the Post, because two circuit courts arrived at differing opinions, the ruling is “likely setting up a Supreme Court showdown over the future of online speech.” In the meantime, the 5th Circuit Court’s opinion could make it tempting for other states to pass similar laws.

Trump-nominated Judge Andrew Stephen Oldham joined two other conservative judges in ruling that the First Amendment doesn’t grant protections for corporations to “muzzle speech.”

John Bergmayer, the legal director of Public Knowledge (a public interest group defending online consumer rights), provided a statement to Ars suggesting that the 5th Circuit Court’s decision may not stand.

“The Fifth Circuit has ignored decades of First Amendment and Supreme Court precedent— and contrary to recent Supreme Court orders—to reach a seemingly politically motivated decision that will have disastrous effects if it is not immediately reversed,” Bergmayer said.

The Post reported that some tech industry representatives also oppose the most recent decision to uphold the law and plan to weigh options to appeal. Matt Schruers, president of the Computer & Communications Industry Association, is a vocal challenger of the Texas law. He’s quoted by the Post as calling the ruling “Orwellian” because it grants government power to dictate “what businesses must say” in the name of protecting free speech.

“The Texas law compels private enterprises to distribute dangerous content ranging from foreign propaganda to terrorist incitement, and places Americans at risk,” Schruers said.

Bergmayer said the verdict could cause platforms to lose their ability to effectively stop the spread of hate speech, abuse, and misinformation. He suggests the ruling implies that newspapers could be ordered to publish propaganda or email spam filters could become illegal because it’s a tech company blocking political speech.

“Platforms need to be regulated in many respects, but rulings like this set back serious attempts to protect consumers online,” Bergmayer warned.

https://arstechnica.com/?p=1882409


Russian official says civilian satellites may be “legitimate” military target

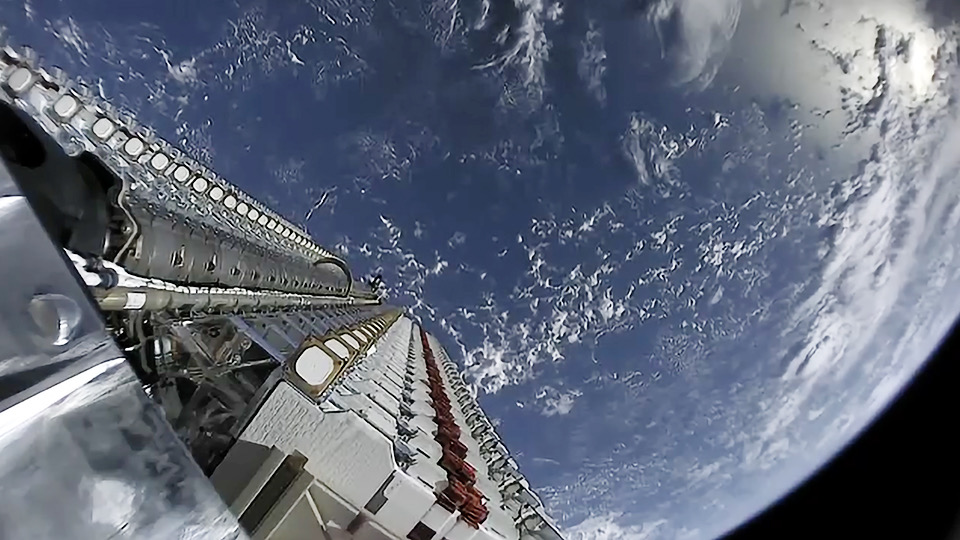
A stack of 60 Starlink satellites being launched into space, with Earth in the background.
Enlarge / A stack of 60 Starlink satellites launched in 2019.

A Russian diplomat said civilian satellites could be legitimate military targets in a statement that seems to refer to Starlink providing broadband access in Ukraine. Civilian satellites “may become a legitimate target for retaliation,” the Russian official said in a statement to the United Nations’ open-ended working group on reducing space threats.

The quote is from an unofficial English translation of the statement on September 12 by Konstantin Vorontsov, head of the Russian delegation to the United Nations Office for Disarmament Affairs (UNODA) working group. The translation is provided with other countries’ statements from the session on the UNODA’s meeting website.

Vorontsov said:

We would like to underline an extremely dangerous trend that goes beyond the harmless use of outer space technologies and has become apparent during the events in Ukraine. Namely, the use by the United States and its allies of the elements of civilian, including commercial, infrastructure in outer space for military purposes. It seems like our colleagues do not realize that such actions in fact constitute indirect involvement in military conflicts. Quasi-civilian infrastructure may become a legitimate target for retaliation.

SpaceX’s Starlink division sent satellite terminals to Ukraine after Russia’s invasion of the country disrupted broadband networks, with the US providing funding for the effort. Satellite Internet access has been useful in Ukraine’s military operations against Russian forces.

Vorontsov’s statement went on to claim that the use of civilian satellites might violate the Outer Space Treaty:

Actions of the Western countries needlessly put at risk the sustainability of peaceful space activities, as well as numerous social and economic processes on Earth that affect the well-being of people, in particular in developing countries. At the very least, this provocative use of civilian satellites is questionable under the Outer Space Treaty, which provides for the exclusively peaceful use of outer space, and must be strongly condemned by the international community.

Russian news agency Tass identified Vorontsov in October 2021 as acting deputy director of the Foreign Ministry Department for Nonproliferation and Arms Control, but he no longer holds that position.

SpaceX CEO Elon Musk warned in March of a “high” probability that Russia will attack Starlink equipment in Ukraine, though he was referring to the user terminals on the ground rather than satellites in space. A Russian cyberattack was able to temporarily disrupt satellite service provided by Viasat when the war began.

Musk later reported that Starlink resisted Russian jamming and hacking attacks. Then-Russian space agency chief Dmitry Rogozin criticized Musk for helping Ukraine.

Russia’s anti-satellite missile test drew condemnation

Russia conducted an anti-satellite missile test in November 2021. “Afterward, US officials condemned the act of shooting down the two-ton satellite at an altitude below 500 km, which is high enough that debris will remain in orbit for at least the next five to 10 years and may threaten many valuable assets, including the International Space Station,” an Ars article said at the time.

A Space.com article today on Vorontsov’s remark notes that “Russia’s statement at the UN OEWG on space threats come just one day after two more nations, Germany and Japan, pledged not to conduct destructive anti-satellite (ASAT) tests, joining a chorus of countries including the United States, Canada, and New Zealand that have committed to reducing space debris following a November 2021 Russian test that drew widespread international condemnation. Russia has yet to make such a pledge.”

In April, Vice President Kamala Harris said the US “commits not to conduct destructive direct-ascent anti-satellite missile testing” and called on all other countries to follow suit. “Simply put: These tests are dangerous, and we will not conduct them,” Harris said.

Attacking Starlink in space would be no simple matter because SpaceX has launched more than 3,000 satellites and is seeking permission to eventually launch tens of thousands.

The Space.com article notes that Starlink hasn’t been the only satellite operator providing important services in response to Russia’s war against Ukraine. “In addition to Starlink, commercial satellite imagery firms such as Planet, Maxar and BlackSky have been providing crucial intelligence by taking pictures of the conflict from above and sharing them openly, playing an unexpectedly important role throughout the Russian invasion,” the article said.

https://arstechnica.com/?p=1882347


Musk filing claims “conspiracy among Twitter executives” to deceive public

Photo illustration with Elon Musk’s Twitter account displayed on the screen of an iPhone.
Getty Images | Chesnot

Elon Musk filed an amended countersuit against Twitter, claiming the allegations by Twitter’s former security chief, Peiter “Mudge” Zatko, give Musk new legal grounds to kill the merger deal.

“Needless to say, the newest revelations make undeniably clear that the Musk Parties have the full right to walk away from the Merger Agreement—for numerous independently sufficient reasons,” the amended countersuit claims. “In short, the Musk Parties and Twitter’s many other investors were sold a different company than the Twitter that actually exists—one that was more valuable, more popular, more secure, and more compliant with governing law.”

The amended countersuit was filed under seal last week and a public version was released yesterday. Delaware Court of Chancery Judge Kathaleen McCormick had granted Musk’s request to amend the countersuit but rejected his attempt to delay the trial by at least four weeks, so the trial is still scheduled to begin October 17.

Musk’s original countersuit focused primarily on his unproven claim that Twitter lied about spam data in its public disclosure that less than 5 percent of its monetizable daily active users (mDAU) are spam or fake. Musk’s amended countersuit says the alleged mDAU misrepresentations “were only one component of a broader conspiracy among Twitter executives to deceive the public, its investors, and the government about the dysfunction at the heart of the company.”

Musk tries to prove “material adverse effect”

Musk is trying to prove that Twitter is reasonably likely to suffer a material adverse effect (MAE) that would give him grounds to exit the $44 billion merger deal.

Twitter previously denied that Zatko’s claims give Musk enough reason to exit the deal in a filing that opposed Musk’s motion to amend his countersuit. “Musk’s new theory is as unavailing as its predecessors,” Twitter wrote. “To escape his obligation to close, Musk must show a failure of one of Twitter’s representations that creates a Material Adverse Effect. Musk cannot even plead this adequately, let alone prove it.”

Musk’s amended counterclaims called Zatko’s whistleblower complaint, which was submitted to Congress and federal agencies, “one of the most significant whistleblower complaints in recent history.”

“According to the Zatko Complaint, Twitter suffers from serious information security vulnerabilities; depends critically on algorithms that infringe intellectual property rights; and is flouting a 2011 FTC consent decree, as well as other privacy and cybersecurity regulations,” the Musk countersuit said.

Musk further claimed the mDAU and security “episodes reveal the vast and unlawful lengths that Twitter will go to avoid disclosing the true state of the company—its ‘key’ financial metrics, security infrastructure, intellectual property infringement, and legal compliance—to the public.”

https://arstechnica.com/?p=1882164


Facebook reverses permanent ban on Holocaust movie after outcry

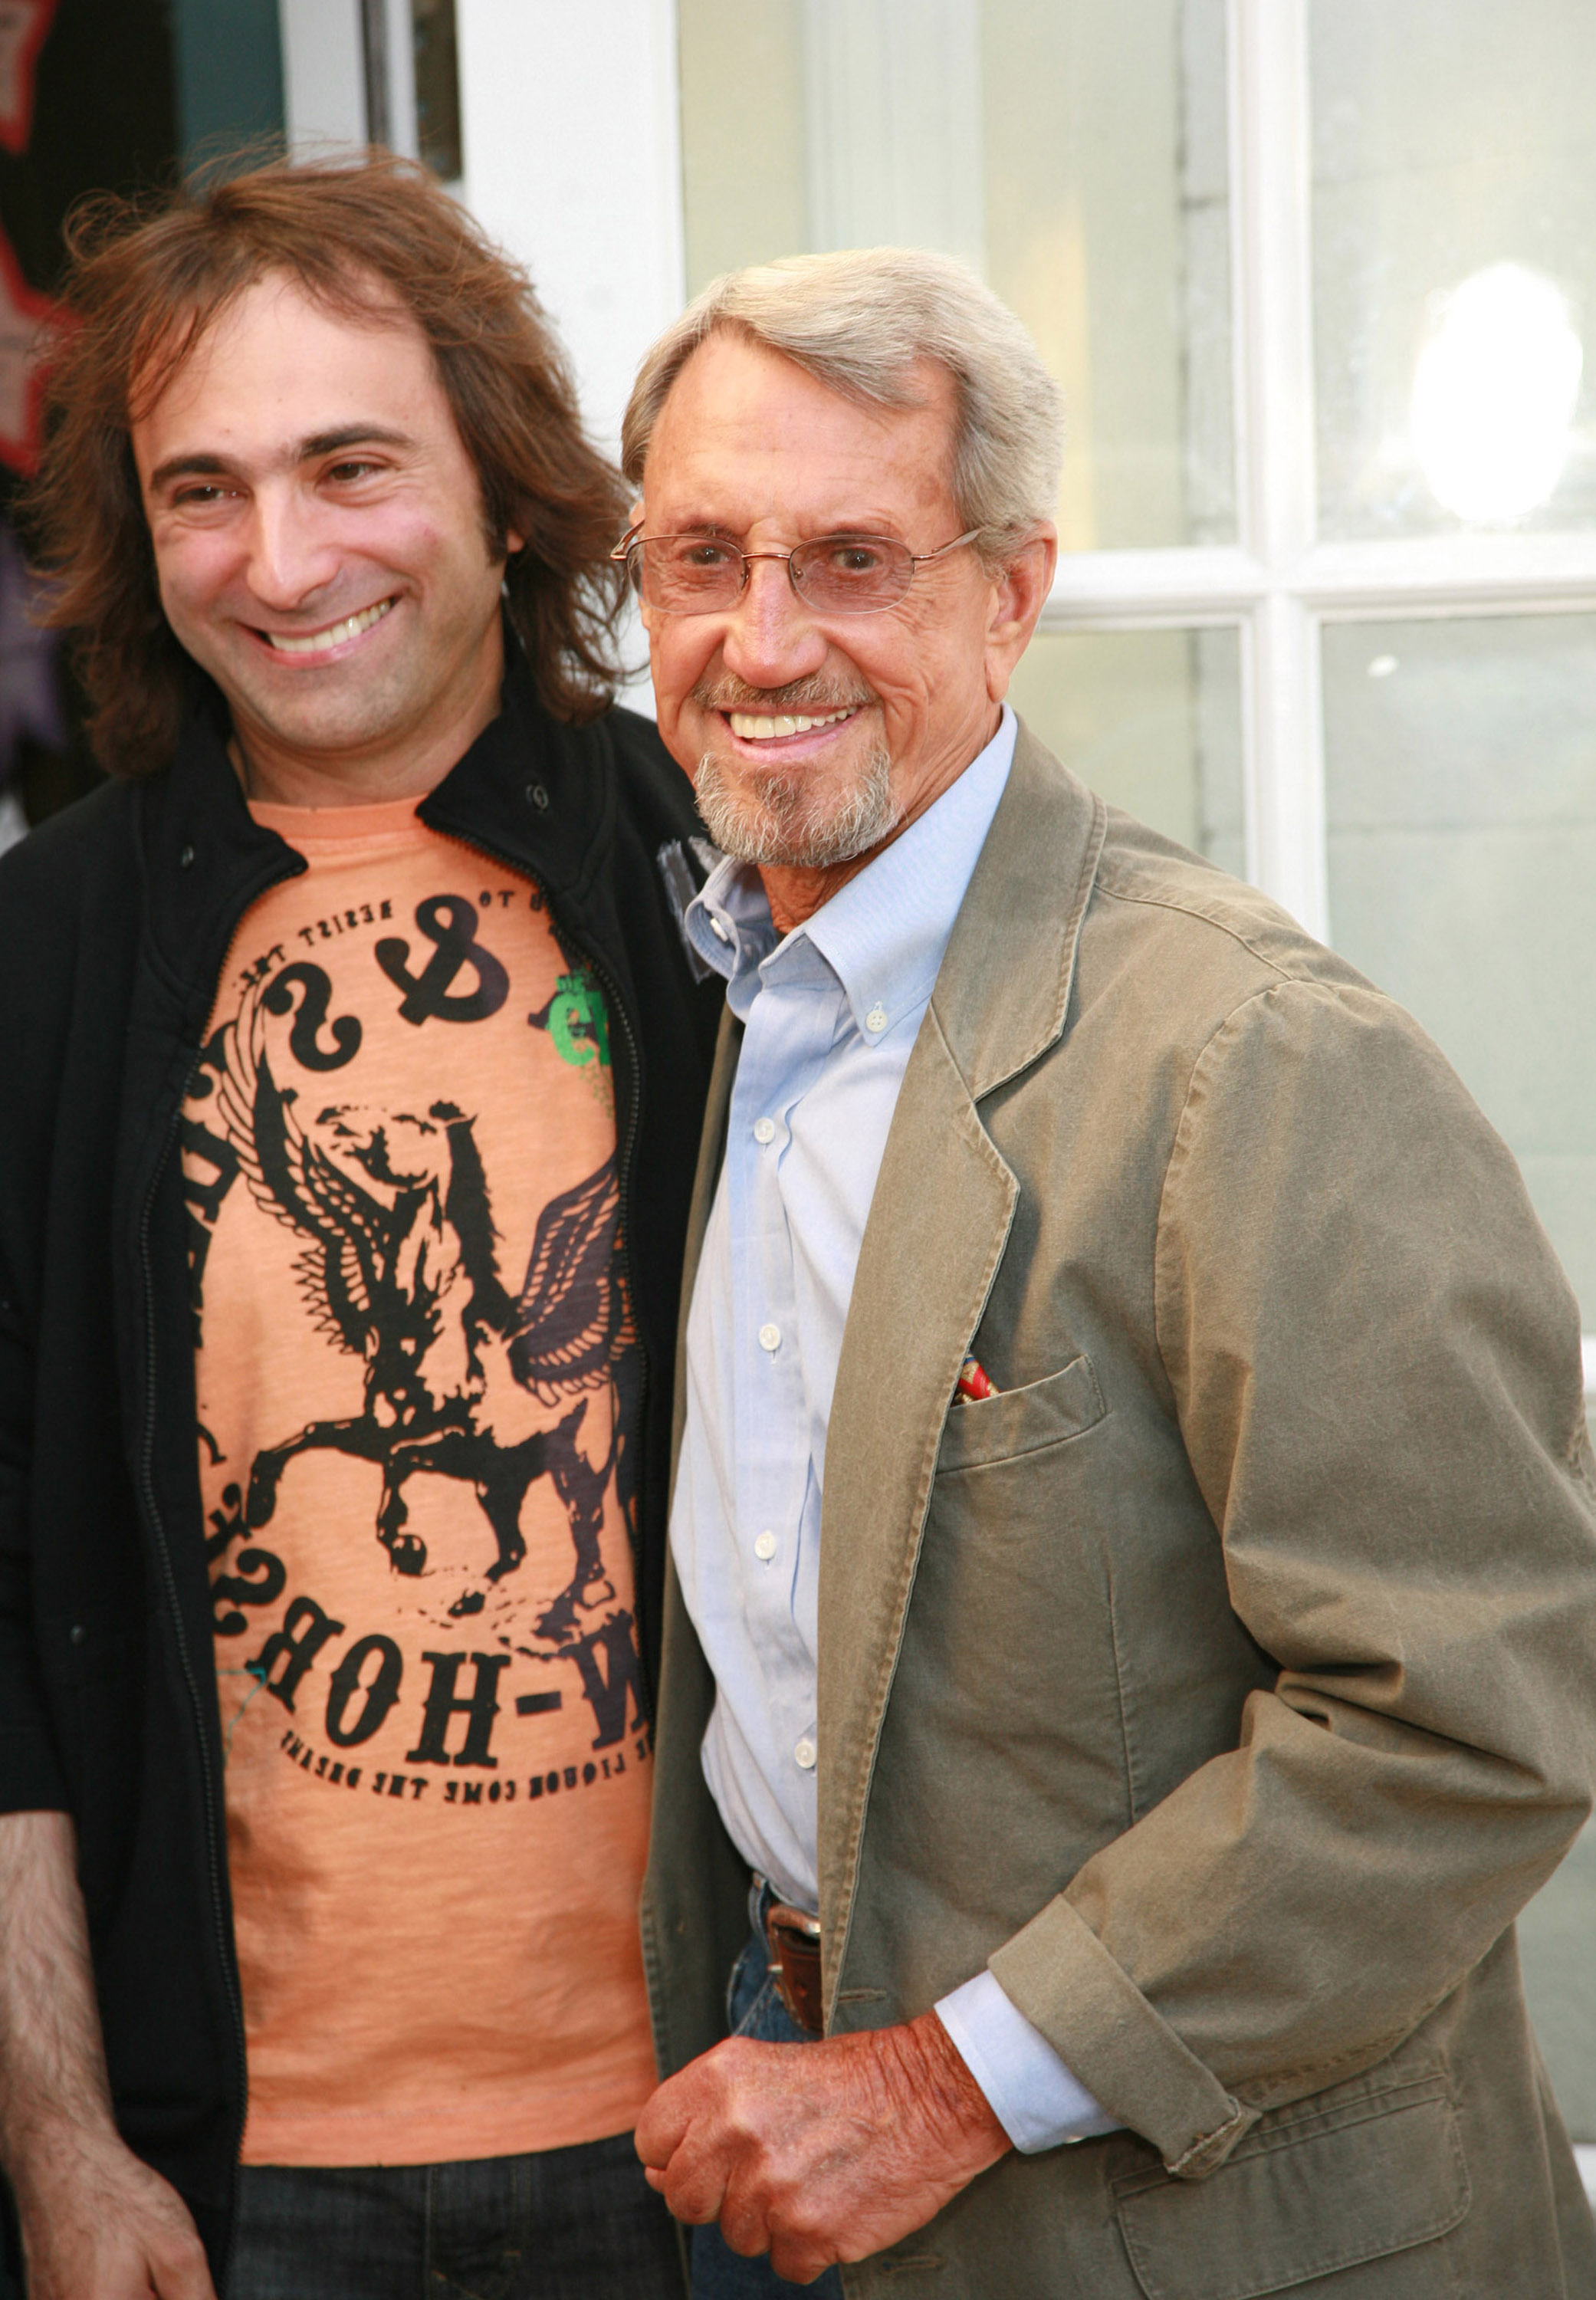
Writer-director Joshua Newton and actor Roy Scheider.
Enlarge / Writer-director Joshua Newton and actor Roy Scheider.

This September, British filmmaker Joshua Newton prepared to rerelease his 2009 film Beautiful Blue Eyes. The 2022 premiere was important to Newton, as he’d waited more than a decade to finally share with the world a version of the movie that was previously lost.

Roy Scheider starred in Newton’s movie, and it ended up being his final role. Scheider—who is best known for playing the beloved Jaws police chief who says, “You’re gonna need a bigger boat”—portrayed a New York cop who reunites with his estranged son and tracks down the Nazi responsible for murdering his family members during the Holocaust. Because a camera malfunctioned and damaged some of Newton’s footage and Scheider died while filming, Newton previously thought he’d lost the edit he liked best. But then more than a decade passed, and Newton told Rolling Stone that AI technology had finally advanced enough that the filmmaker could repair lost film frames.

Excited to put this cut of his thriller in front of audiences, Newton prepared to promote the rerelease on Facebook. But in the days leading up to the premiere, Newton told Rolling Stone that he received an email informing him that in a rare turn of events, “Facebook had banned the filmmakers from promoting or advertising” the movie.

Following Rolling Stone’s report, Meta told Ars the Facebook owner reviewed the case and decided to reverse the ban.

“We reviewed the ads and page in question and determined that the enforcement was made in error, so we lifted the restriction,” a Meta spokesperson told Ars.

Why was the film banned?

Facebook moderators told Newton that his film was banned because the company’s ad policy restricts content that “includes direct or indirect assertions or implications about a person’s race.” Because Newton’s movie in the US is titled Beautiful Blue Eyes, Facebook moderators banned its promotion in Facebook ads, seemingly reading the title as hinting at race.

Newton told Rolling Stone that his parents survived the Holocaust and that the movie was based on his late father’s life. His own son, Alexander Newton, featured in the film and performed its titular song. Alexander tweeted that his song was also banned on Facebook and Instagram.

“This is the action of haters—and there are sadly many in our society—who seek to damage the film in order to trivialize the Holocaust,” Joshua Newton told Rolling Stone. “Surely, Mark Zuckerberg did not intend this to happen.”

Newton’s production company did not immediately respond to Ars’ requests for comment since Meta lifted the ban.

How Facebook made its decision

According to Newton, after he received the email informing him that he would not be allowed to promote his film on Facebook, he immediately appealed the decision. Rolling Stone shared the message that Facebook sent in response to Newton’s appeal, informing the filmmaker that advertising and even trailers were “permanently restricted.”

“After a requested review of your Facebook account, we confirmed it didn’t comply with our Advertising Policies or other standards. You can no longer advertise using Facebook Products. This is our final decision,” the message said.

Newton’s movie is now being screened in hundreds of movie theaters that are also simultaneously rereleasing Jaws in IMAX. It’s a double feature that seems designed as a celebration of Scheider through his best-known and final roles. Newton said he is disgusted that Facebook has seemingly limited the reach of his film. Rolling Stone noted that Facebook has rarely taken such action in content reviews of movies, finding one other instance in 2020 when a pro-Trump documentary was censored ahead of the election.

“Every decent and sane human being on this planet should be alarmed by Meta-Facebook’s ban on the advertising of a Holocaust-related film,” Newton told Rolling Stone. “Mark Zuckerberg has created a monster that has no oversight. It’s one thing to be flagged by an algorithm. It’s another for Meta-Facebook employees to review the flag and uphold it, knowing full well that the title is not discriminatory and that the film is Holocaust-related.”

Newton told Rolling Stone that he is considering legal action against Facebook, but Meta told Ars that all restrictions on his movie’s Facebook page and ads have been lifted.

Increased scrutiny on Facebook censorship

Although resolved, Newton’s case adds another data point in the ongoing controversy over invalid censorship that has taken place on Facebook for years, with the government increasingly pressuring Facebook to beef up content moderation and the general public mostly confused over why and when certain content is restricted.

For years, the American Civil Liberties Union has taken the stance that Facebook shouldn’t censor any offensive speech—a policy that would ensure filmmakers like Newton never have to worry about how to promote their movies without Facebook.

Recently, there has been some new information shared publicly on Facebook content moderation decisions. The Wall Street Journal last week posted an opinion piece from its Editorial Board after emails shared in court showed how Facebook and other tech companies directly coordinate with federal officials to decide what gets removed. The WSJ board called on Facebook to release more emails so the public can better understand the government’s role in Facebook’s moderation practices.

https://arstechnica.com/?p=1882105


Patreon denies child sex trafficking claims in viral TikTok “conspiracy” theory

Patreon denies child sex trafficking claims in viral TikTok “conspiracy” theory

After a TikTok accusing Patreon of ignoring reports and knowingly profiting off accounts posting child sexual abuse materials (CSAM) attracted hundreds of thousands of views, more TikTokers piled on, generating more interest. Patreon immediately responded by branding the TikToks as disinformation. In a blog, Patreon denied allegations, accusing TikTokers of spreading a “conspiracy that Patreon knowingly hosts illegal and child-exploitative material.”

According to Patreon, the conspiracy theory sprang from a fake post on a job-posting site; Vice later reported that site was Glassdoor. The Glassdoor review was posted in August and claimed that Patreon refused to respond to reports of accounts suspected of “selling lewd photographs” of children. As TikTokers described their failed attempts to report these accounts, Patreon laid off members of its security team and, Patreon said, “onlookers inaccurately linked” the “small-scale staffing changes we made last week to our security organization.” The TikTokers claimed that Patreon laid off its staff specifically for not complying with orders to allow CSAM to stay on the platform.

“Dangerous and conspiratorial disinformation began circulating on social media recently,” Patreon said. “We want to let all of our creators and patrons know that these claims are unequivocally false and set the record straight.”

In the TikTok videos, the “lewd photos” from Patreon, Vice’s reporting found, were from a mixture of family accounts and accounts featuring adult models engaging in “age play” and posing as children. The creator of the age play account, Vice reported, was eventually banned from Patreon and other platforms. Patreon US Policy Head Ellen Satterwhite told Vice that “Patreon has zero tolerance for the sexualization of children or teenagers and will remove any user and all associated content found to be in violation of this policy.” Patreon told Ars it has no further comment at this time.

Developing tech to block all CSAM

Based on 2020 data, UK-based Internet Watch Foundation reported that more than a fifth of global CSAM is hosted in the US. Worldwide, the problem has increased by 15,000 percent in the last 15 years, according to Thorn, an organization that develops new technologies to combat online child sexual abuse (founded by Ashton Kutcher and Demi Moore).

Patreon said in its statement that it works with Thorn and other organizations, like the National Center for Missing and Exploited Children (NCMEC) and INHOPE, to “keep the Internet safer.” Organizations like these, dedicated to ending child sexual abuse, are tasked with raising awareness of CSAM abuses online, while also experiencing a potential drain on their resources driven by hysteria over fraudulent sex trafficking charges, which, Vice reported, has become common fodder for viral TikToks.

A Thorn spokesperson told Ars that it can’t comment on the TikTok case but could explain more about their partnership with Patreon.

Because the issue of “CSAM on technology platforms is pervasive and continues to grow exponentially,” a Thorn spokesperson said that “any platform with an upload button can be—and likely is—used to distribute CSAM.” Today, Thorn said that “predators have more access to children and the ability to distribute CSAM than ever before,” and that’s why Thorn works with tech companies like Patreon, which have widely used platforms, to try to push for “systems-level change” to a “ubiquitous problem.”

As part of its partnership with Thorn, Patreon uses a Thorn tool called Safer to “identify, detect, and report CSAM at scale,” in part by using “Safer’s hashing and matching technology” to block content from being shared that’s already flagged in a CSAM database, such as NCMEC’s.

Thorn is one organization serving as a cog between police and tech companies to produce more impactful solutions, but the IWF data suggests that the US has a long way to go to effectively put an end to CSAM online.

Because Patreon remains a widely used platform, the potential that CSAM will be posted on its platform remains, Thorn’s spokesperson said. “The Internet has evolved in a way that makes it easy for abusers to share child sexual abuse material within communities that can flourish on the same platforms we all use every day,” Thorn said.

https://arstechnica.com/?p=1881861


Iranians hacked US companies, sent ransom demands to printers, indictment says

Illustration of a hooded figure in dark room typing on a laptop. In the background, the wall is covered in ones and zeroes.
Getty Images | Bill Hinton

Three Iranian nationals charged with hacking into US-based computer networks sent ransom demands to the printers of at least some of their victims, according to an indictment unsealed today. The ransom demands allegedly sought payments in exchange for BitLocker decryption keys that the victims could use to regain access to their data.

The three defendants remain at large and outside the US, the DOJ said.

“The defendants’ hacking campaign exploited known vulnerabilities in commonly used network devices and software applications to gain access and exfiltrate data and information from victims’ computer systems,” the US Department of Justice said in a press release. Defendants Mansour Ahmadi, Ahmad Khatibi, Amir Hossein Nickaein “and others also conducted encryption attacks against victims’ computer systems, denying victims access to their systems and data unless a ransom payment was made.”

The indictment in US District Court for the District of New Jersey describes a few incidents in which ransom demands were sent to printers on hacked networks. In one case, a printed message sent to an accounting firm allegedly said, “We will sell your data if you decide not to pay or try to recover them.”

In another incident, the indictment said a Pennsylvania-based domestic violence shelter hacked in December 2021 received a message on its printers that said, “Hi. Do not take any action for recovery. Your files may be corrupted and not recoverable. Just contact us.”

Khatibi later “sent an email to a representative of the Domestic Violence Shelter asking for payment of one Bitcoin,” the indictment said. The shelter ultimately paid the equivalent of $13,000 to the hacker’s Bitcoin wallet, the indictment said, adding that Khatibi then “provided decryption keys to enable the Domestic Violence Shelter to restore access to its systems and data.”

Before sending the ransom demand, “a member of the conspiracy gained unauthorized access to the Domestic Violence Shelter’s computer system and launched an encryption attack by activating BitLocker, thereby denying the Domestic Violence Shelter access to some of its systems and data,” the indictment said. BitLocker is an encryption tool used in Windows.

“YOU HAVE TO CONTACT US IMMEDIATELY”

Victims included small businesses, government agencies, nonprofit programs, educational and religious institutions, and “multiple critical infrastructure sectors, including health care centers, transportation services and utility providers,” the DOJ press release said. The three indicted hackers and co-conspirators “collected payments in Bitcoin and other cryptocurrencies from certain victims that paid the ransom to decrypt their data,” the indictment said.

The Iranians hacked networks in several countries, “gain[ing] unauthorized access to the computer systems of hundreds of victims in the United States, the United Kingdom, Israel, Iran, and elsewhere,” the DOJ said. The US agency accused Iran’s government of “creat[ing] a safe haven where cyber criminals acting for personal gain flourish and defendants like these are able to hack and extort victims, including critical infrastructure providers.”

In April 2021, “Nickaein sent a ransom demand communication to the printers” of an Illinois company referred to as “Accounting Firm 2,” the indictment said. The ransom demand allegedly told the firm to contact an email account controlled by Nickaein and included the following text:

Hi!

IF YOU ARE READING THIS, IT MEANS YOUR DATA IS ENCRYPTED AND YOUR PRIVATE SENSITIVE INFORMATION IS STOLEN!

READ CAREFULLY THE WHOLE INSTRUCTIONS TO AVOID ANY PROBLEMS

YOU HAVE TO CONTACT US IMMEDIATELY TO RESOLVE THIS ISSUE AND MAKE A DEAL!

…

We will sell your data if you decide not to pay or try to recover them.

Before sending the ransom demand, Nickaein hacked into the company’s network, “stole data, and launched an encryption attack using BitLocker, thereby denying Accounting Firm 2 access to certain of its systems and data,” the indictment said.

This is not the first hacking campaign to use the tactic, sometimes called “print bombing,” of sending ransom demands to printers on the infected network.

https://arstechnica.com/?p=1881431


Regulators put the brakes on Microsoft’s Activision acquisition

An Xbox controller on a table next to a Call of Duty game.
Getty Images | Bloomberg

Microsoft’s $75 billion acquisition of video game maker Activision Blizzard faces in-depth probes in Brussels and the UK following growing concerns the deal is anti-competitive and will exclude rivals from accessing the blockbuster game Call of Duty.

It comes as the UK’s Competition and Markets Authority is expected to launch an in-depth investigation this week after Microsoft decided not to offer any remedies at this stage, according to two individuals with knowledge of the situation.

Earlier this month, the CMA became the first global antitrust regulator to sound the alarm over the transaction, giving Microsoft five days to come up with undertakings that would resolve its worries or face an extended “phase 2” probe.

The companies have already been in talks with regulators in Brussels since the deal was announced eight months ago, in what is known as the pre-notification stage—an indication of how scrupulous officials will be during the probe.

Regulators and others involved in the deal expect a prolonged EU investigation once Microsoft officially files its case in Brussels in the coming weeks. People familiar with the EU’s thinking say regulators will take their time to examine this deal because of its size, the nature of the buyer and the rising concerns from rivals, including Sony.

“It is a big deal, a difficult deal,” said a person in Brussels familiar with the transaction. “It needs an extensive investigation.”

It comes after Sony last week accused Microsoft of misleading the games industry and regulators about its commitments to keep Call of Duty on PlayStation consoles. It said Microsoft had only offered to keep releasing Activision’s hit game on PlayStation for a limited number of years.

The move by the UK lays out the issues that Microsoft will have to overcome to pull off its biggest-ever deal. The US tech giant is hoping to close the deal by the end of June next year but must first clear regulatory hurdles in countries from New Zealand to America.

Microsoft opted not to offer any remedies to the CMA at this stage because there were no obvious commitments the UK regulator would be likely to accept, according to people with knowledge of the situation.

The watchdog does not generally accept behavioral remedies, such as commitments to maintain access to a product or service, at the end of a phase 1 probe apart from in rare circumstances.

One competition lawyer with knowledge of the case said it was “almost impossible” for Microsoft to offer a remedy that would prevent the investigation moving to an in-depth antitrust probe.

The Activision deal comes at a time when regulators around the world are concerned they have not been as interventionist as they should have been with regards to previous Big Tech deals.

Gaming rivals say they fear that Microsoft will offer commitments it could easily “wriggle out of” and that are not long lasting. Sony and others want the commission to force Microsoft to offer guarantees that they will be able to access all games “on equal terms and in perpetuity.”

Microsoft has said it will continue to make Call of Duty available on other companies’ gaming consoles, such as PlayStation, rather than turning it into an exclusive title on Microsoft’s Xbox. Brad Smith, Microsoft’s president and vice-chair, had previously said “we want people to have more access to games, not less.”

The company could choose to enter a formal commitment to the CMA to guarantee its rivals’ access to games during the second phase of the investigation, when an independent panel will analyze the deal in depth and consider potential solutions to antitrust issues.

© 2022 The Financial Times Ltd. All rights reserved Not to be redistributed, copied, or modified in any way.

https://arstechnica.com/?p=1881530