Trump hasn’t followed through on plan to withdraw US from WHO
Enlarge/ World Health Organization Director-General Tedros Adhanom Ghebreyesus at a press conference on COVID-19 at WHO headquarters in Geneva on March 11, 2020.
Getty Images | Fabrice Coffrini
On May 29, President Trump said his administration would take immediate action to withdraw the US from the World Health Organization.
“Because they have failed to make the requested and greatly needed reforms, we will be today terminating our relationship with the World Health Organization, and redirecting those funds to other worldwide and deserving, urgent global public health needs,” Trump said at the time, while criticizing the WHO’s response to the coronavirus pandemic and claiming that “China has total control” over the United Nations agency.
But now, two weeks later, there’s nothing to indicate that Trump has followed through on his plan. In an article yesterday titled “US hasn’t taken action to withdraw from WHO despite Trump pledge,” The Hill wrote that “no steps toward a formal withdrawal have been taken,” and that “a WHO spokesman told The Hill that the agency had received no formal notification that the United States would withdraw.”
Another article yesterday in Stat, a health news website, said that “none of the levers that would need to be pulled to follow through on [Trump’s WHO] decision has been pulled.” For example, the Trump administration has “not paid outstanding financial obligations to the WHO, a step that would be required before the United States could pull out under a joint resolution signed by Congress,” the article said.
“The US is not out of WHO”
These reports follow a Vanity Fair article published Monday that describes “the secret plan to unwithdraw from the WHO after Trump’s ‘bizarre,’ ‘ruinous’ exit.”
Trump’s WHO announcement “blindsided top federal officials,” who had been working “to salvage America’s relationship with the WHO” after Trump’s April decision to temporarily halt US funding and his criticism of the WHO in mid-May, Vanity Fair wrote. The article continued:
Now, Vanity Fair has learned, secret negotiations aimed at reversing Trump’s decision have begun between [US] Ambassador [Andrew] Bremberg and the WHO’s director general, Dr. Tedros Adhanom Ghebreyesus. A phone call Saturday between the two men resulted in a possible framework agreement to restore the relationship, which the US diplomatic corps views as essential to the global fight against coronavirus and myriad other public health issues.
The framework would allow for both increased scrutiny of China’s conduct and an independent review of the WHO’s performance in the first six months of the outbreak. And discussions continue over whether the WHO would exert pressure on China to turn over original samples of the live virus and allow its scientists to be interviewed regarding the virus’s origins. “It’s fair to say the US is not out of WHO, and negotiations are ongoing to address concerns and hopefully walk back from this decision,” said an official who participated in a call with G7 partners, an alliance of countries with advanced economies, where this information was shared.
The US generally provides about 15 percent of the WHO’s budget and gave the organization $893 million during the WHO’s two-year funding cycle that ended on December 31.
The Trump administration could still try to follow through on Trump’s announced plan. But Trump’s statement on May 29 was false insofar as he said the US would be “terminating our relationship” on that very day.
“Some question whether the president has the legal authority to pull the country out of the WHO—whose own constitution includes no mechanism for withdrawal by a member state,” Stat wrote. “Others argue that the only way the US can withdraw was prescribed in the joint resolution of Congress that passed in 1948, meaning the US would have to file a formal notice of its intention to leave and pay its outstanding financial obligations.”
A Health and Human Services (HHS) spokesperson said the US “will not be contributing funding to WHO but is happy to provide technical expertise or guidance to help end [the current Ebola] outbreak,” according to Stat. A State Department spokesperson “reiterated the president’s complaints against the agency and his intention to withdraw,” Stat also wrote.
US and WHO had “good discussion” on Ebola
There were seemingly conflicting statements at a press conference on Wednesday about whether the US continues to support the WHO financially.
“We had a very good discussion with [HHS] secretary [Alex] Azar last week and he assured me of US’ continued commitment to support in the fight, especially against Ebola,” the WHO’s Dr. Tedros said. But later in the same press conference, Tedros clarified that he “didn’t say” whether the WHO is “receiving funding directly from the US” for the fight against Ebola in the Democratic Republic of the Congo.
“I said it many times, I think in our relationship with the US, it’s not about the money,” Tedros said. “You know, working together, the relationship, I think, is more important, and [I] hope we will work side by side to control or contain the outbreak in western DRC as soon as possible, but the cooperation doesn’t involve the financing part directly to WHO.”
Dr. Anthony Fauci, director of the National Institute of Allergy and Infectious Diseases, expressed his support for a continued US/WHO partnership yesterday. “I would hope that we could continue to benefit from what the WHO can do at the same time that they continue to improve themselves,” Fauci told CBC News. “I’ve had good relationships with the WHO and the world needs the WHO.”
https://arstechnica.com/?p=1683556
New Google rule bans discriminatory targeting for housing ads
Enlarge/ A sign on the street is visible to anyone who walks or drives by. A sign online can be strategically, and illegally, targeted away from people against whom you may have a bias.
Google is taking action to reduce unlawful discrimination on its advertising platform a year after the federal government sued its largest competitor, Facebook, over the same thing.
The company is “introducing a new personalized advertising policy for certain types of ads,” a Google executive shared in a company blog post today. The policy prohibits entities placing ads for employment, housing, or credit services from targeting or excluding ads “based on gender, age, parental status, marital status, or ZIP Code.”
The federal Fair Housing Act explicitly prohibits landlords and sellers from discriminating against potential renters or buyers on the basis of race, color, national origin, religion, sex, familial status, or disability. (“Family status” includes a ban on discriminating against someone who is pregnant or families with children.) That applies to the advertising of units as well as who actually gets to sign the lease or the mortgage and what they have to pay.
Google already prohibits personalization based explicitly on “race, religion, ethnicity, sexual orientation, national origin, or disability,” the post explains. Some of today’s new additions to the list, such as marital or parental status, are already protected categories. Others, such as ZIP code, can all too easily be used as proxies for other categories, such as race or ethnicity, as many existing neighborhoods are highly segregated.
This is not a new problem, and Google—which dominates the online advertising market—is not alone. A ProPublica report in 2016 found that Facebook’s system allowed for the placement of housing ads to groups that explicitly excluded certain “ethnic affinities.” A group of users sued Facebook shortly after, alleging that the site was violating federal law. Facebook promised to do better, but a full year later, in 2017, ProPublica was still able to place explicitly discriminatory rental ads, despite updated Facebook policies theoretically prohibiting the practice.
In 2019, the Department of Housing and Urban Development took legal action, alleging Facebook was acting in violation of the Fair Housing Act by “encouraging, enabling, and causing housing discrimination through the company’s advertising platform.”
Google said in its update that it has been “working closely” with HUD on these changes. “As part of our effort, we’ll provide housing advertisers with additional information about fair housing to help ensure they are acting in ways that support access to housing opportunities,” Google added.
HUD Secretary Ben Carson also issued a statement about the new Google policy. “Advertising practices may continue to evolve, but our nation’s laws are unwavering,” Carson said. “It is one of our key duties at HUD to enforce the Fair Housing Act and ensure that all Americans have housing choice. Improvements are underway in the online advertising space, and HUD encourages platforms, such as Google, to take these types of steps to eliminate unlawful discrimination in advertising and seek to ensure compliance with our nation’s Fair Housing laws.”
https://arstechnica.com/?p=1683512
OpenZFS removed offensive terminology from its code
Enlarge/ Replacements for outdated master/slave terminology tend to be considerably more accurate, as well as less offensive.
On Wednesday evening, ZFS founding developer Matthew Ahrens submitted what should have been a simple, non-controversial pull request to the OpenZFS project: wherever possible without causing technical issues, the patch removed references to “slaves” and replaced them with “dependents.”
This patch in question doesn’t change the way the code functions—it simply changes variable names in a way that brings them in conformance with Linux upstream device-mapper terminology, in 48 total lines of code (42 removed and 48 added; with one comment block expanded slightly to be more descriptive).
But this being the Internet, unfortunately, outraged naysayers descended on the pull request, and the comments were quickly closed to non-contributors. I first became aware of this as the moderator of the r/zfs subreddit where the overflow spilled once comments on the PR itself were no longer possible.
Updating terminology is technically sound
There are several valid answers to the “Why patch?” question. For those who refuse to think of anything but clarity, there is no good descriptive relationship between any technology and human slavery—and the human term far predates any engineering or technical use. Replacing “master/slave” terminology generally results in a more precise, easily discoverable technical description.
OpenZFS is not on the leading edge of this disambiguation effort. Some notable projects which have discarded and replaced master/slave terminology include the BIND DNS server, Drupal Web application framework, and Redis datastore. It is particularly telling that, although all three projects used the same original “master/slave” terms, the replacements were different. That’s because the actual relationship described is different in each project, and so the most sensible replacement for the same original term is different for each project.
For the BIND DNS server, the Internet Systems Consortium replaced master/slave with primary/secondary. For Drupal, the replacement is primary/replica, and for Redis, it’s leader/follower. The different replacement terms exist because the real functions are different—and the replacement for the original terminology is therefore more descriptive of what’s actually happening underneath the hood.
Similar historical updates
As mentioned previously, OpenZFS is by no means the first project to update its codebase and documentation to remove references to slavery. Although complaints about master/slave terminology circulated at least as far back as the 1990s, the first large mainstream American exposure came from Los Angeles in 2003, where a black employee of the county filed a complaint concerning master/slave labels on videotape devices.
In addition to specific terminology updates in specific projects, the IETF (Internet Engineering Task Force) published a memo in 2018 acknowledging and outlining the problem and offering specific alternatives to both master/slave and blacklist/whitelist terminology.
Motivation and context
While technical accuracy and precedent are valid reasons to remove master/slave terminology from a codebase, they are of course not the only reason. Ahrens’ own pull request describes this eloquently enough:
The horrible effects of human slavery continue to impact society. The casual use of the term “slave” in computer software is an unnecessary reference to a painful human experience.
There should be nothing controversial about this, even if this were a drive-by pull request from a first-time contributor. Ahrens, of course, is anything but—he was one of the three founding Sun Microsystems ZFS developers beginning in 2001, and he remains a lead developer of the OpenZFS project today.
More importantly, it should be obvious that one person’s impervious reaction to casual slavery-based analogies does not negate another person’s experiences with slavery’s historical reality and its ongoing generational effects.
Ahrens’ pull request has been reviewed by fellow lead developers Brian Behlendorf and Ryan Moeller and merged into the OpenZFS project repository.
https://arstechnica.com/?p=1683434
3M sues price-gougers who used Amazon to sell masks at 1,800% markup
Enlarge/ The (replica) disembodied marble head of David probably didn’t need a 3M mask, but he nonetheless looked fashionable sporting it in the window of a jewelry shop in Switzerland in March 2020.
3M—which manufactures N95 filtration masks that have been in high demand since the COVID-19 pandemic began—is suing merchants who used Amazon to sell 3M and counterfeit masks for more than 18 times their standard price.
A group of third-party merchants on Amazon “operated an illegal scheme to advertise and sell counterfeit, damaged, deficient, or otherwise altered respirators” to customers, 3M alleges in the complaint (PDF), filed in federal court in California.
3M has drastically increased its production of N95 respirator masks, the company says, but has kept its pricing between $0.63 and $3.40 per mask, depending on the model. The resellers in the suit, however, were allegedly selling a model that has a typical list price of $1.27 for for an average of $23.21 per mask, more than 18 times higher than 3M’s price.
Amazon has already taken down the listings in question, 3M notes in the suit, but due to the way Amazon’s third-party marketplace works, “banned” goods and sellers pop back up all the time. This case is likely to be no different, 3M claims, writing that the defendants have a history of launching “multiple front entities to perpetuate their unlawful activities” and adding that the defendants will probably keep doing it “until they are enjoined by this court.”
3M seeks financial penalties against the resellers but says any monetary awards it receives “will be donated to charitable COVID-19 relief efforts.”
The company has filed more than a dozen similar lawsuits in recent months, The Wall Street Journal notes. “The lawsuits are one tool in our tool kit to go after this kind of activity,” Kevin Rhodes, deputy general counsel for 3M, told the WSJ.
Price gouging for critical protective gear became rampant on US online platforms in February and March as the spread of the novel coronavirus caused a massive spike in demand. Suppliers couldn’t keep up, and so prices rose sharply for goods such as disposable gloves, masks, and hand sanitizer.
eBay outright banned listings for masks, hand sanitizers, and disinfectant wipes in early March amid rampant price-gouging and potential fraud. Amazon did not follow suit, instead turning to algorithmic detection and consumer complaints to remove problem listings.
More than 30 states’ attorneys general late in March asked online retailers, including Amazon, to take stronger, more proactive action against price-gouging merchants. “Rather than playing whack-a-mole to stop price gouging after it has already occurred,” the attorneys general wrote, “online retail platforms should prevent unconscionable price increases from occurring in the first place by creating and enforcing strong policies.”
https://arstechnica.com/?p=1682665
Researchers say online voting tech used in 5 states is fatally flawed
Enlarge/ Voting machines are shown at a polling location on June 9, 2020 in West Columbia, South Carolina.
Sean Rayford/Getty Images
OmniBallot is election software that is used by dozens of jurisdictions in the United States. In addition to delivering ballots and helping voters mark them, it includes an option for online voting. At least three states—West Virginia, Delaware, and New Jersey—have used the technology or are planning to do so in an upcoming election. Four local jurisdictions in Oregon and Washington state use the online voting feature as well. But new research from a pair of computer scientists, MIT’s Michael Specter and the University of Michigan’s Alex Halderman, finds that the software has inadequate security protections, creating a serious risk to election integrity.
Democracy Live, the company behind OmniBallot, defended its software in an email response to Ars Technica. “The report did not find any technical vulnerabilities in OmniBallot,” wrote Democracy Live CEO Bryan Finney.
This is true in a sense—the researchers didn’t find any major bugs in the OmniBallot code. But it also misses the point of their analysis. The security of software not only depends on the software itself but also on the security of the environment on which the system runs. For example, it’s impossible to keep voting software secure if it runs on a computer infected with malware. And millions of PCs in the United States are infected with malware.
The issue has particular urgency right now because the ongoing COVID-19 pandemic is forcing election officials to make significant changes to election procedures. Right now, most jurisdictions using the OmniBallot software don’t use its “electronic ballot delivery” feature. But enabling the feature would require little more than a configuration change. There’s a risk that election officials, under pressure to make remote voting easier, will decide to enable the software’s online voting feature for this November’s general election.
How OmniBallot works
Experimenting with a live election system would be unethical and likely illegal. Instead, Specter and Halderman obtained a copy of the OmniBallot software, reverse-engineered it, and then created new server software that mimicked the behavior of the real server. This allowed them to experiment with the software without risking interference with a real election.
OmniBallot offers a number of different capabilities that state election officials have the option to offer to voters. The most basic is a blank ballot delivery feature that will provide a voter with a PDF ballot that can be printed out and mailed back to the polling place.
Jurisdictions can also offer a ballot-marking feature, which will mark a ballot on the voter’s behalf before it’s printed out. This can enable blind voters to fill out a ballot independently. It can also prevent overvotes (voting for two or more candidates) and warn voters about undervotes (failing to vote in a race).
But Specter and Halderman argue that this capability comes with some added risks. Malicious software could be programmed to switch votes some fraction of the time. Theoretically, voters are supposed to check that the votes are correct before mailing in their ballot, but research suggests voters are lax about doing so. One study by Halderman and others found that only 6.6 percent of voters in a realistic mock election reported a changed vote to election supervisors.
By default, the software generates the marked ballot PDF on an OmniBallot server, not on the user’s own device. This creates an unnecessary risk to the privacy of the voter’s ballot, Specter and Halderman argue, since it means that Democracy Live gets an unnecessary copy of the voter’s votes.
Fortunately, Democracy Live also offers an option for client-side ballot marking. Andrew Appel, a computer scientist at Princeton, told Ars that this option was added at the insistence of California officials who objected to server-side ballot marking. When this option is chosen by election administrators, the ballot is marked on the user’s own device, without sharing the data with Democracy Live’s servers. The computer scientists recommend that all jurisdictions using OmniBallot’s ballot marking feature switch to the client-side version of the software.
The problems with online voting
While there are some security concerns with ballot-marking software, the researchers say that these problems pale in comparison to security vulnerabilities of OmniBallot’s “electronic ballot delivery” system.
The fundamental problem is that the complexity and opacity of online voting systems creates numerous opportunities for a hacker to tamper with a ballot during the submission process. Malware on the client device could modify the ballot before it’s transmitted to Democracy Live’s servers. OmniBallot is built on Amazon Web Services using JavaScript libraries delivered by Google and Cloudflare. So hackers or malicious insiders at any of these companies could potentially alter ballots if they had access to one of these companies’ systems.
And the nature of online voting means there’s no reliable way for a voter to verify that a ballot was transmitted correctly. Software engineers have developed theoretical designs for voting systems with end-to-end security. These systems use sophisticated cryptography to enable voters to cryptographically verify that their vote has been counted correctly. But Democracy Live doesn’t do anything like that. In their paper, Specter and Halderman describe how an attacker could exploit the lack of end-to-end verification.
“The web app would show a ballot containing the selections the voter intended, but the ballot that got cast would have selections chosen by the attacker,” they write. “The attack would execute on the client, with no unusual interactions with Democracy Live, so there would be no way for the company (or election officials) to discover it.”
Auditing doesn’t fix the problem
Democracy Live conducts post-election audits using Amazon’s AWS CloudTrail software to verify that no Democracy Live employees abused their access to company servers. These checks could detect some forms of election tampering, but Specter and Halderman point out that they are far from foolproof.
These methods wouldn’t detect any attacks executed from the client side. If malware on a user’s PC modified the user’s ballot before sending it to Democracy Live’s servers, that wouldn’t show up in the CloudTrail logs. If someone with access to Google or Cloudflare servers delivered malicious JavaScript libraries to OmniBallot users, that wouldn’t show up in AWS logs. Someone with administrative access to Amazon’s servers might be able to modify Democracy Live’s software in a way that wouldn’t show up in the logs.
Of course, most of these attacks wouldn’t be trivial to pull off. Google, Amazon, and Cloudflare are three of the most sophisticated software companies in the world and take elaborate precautions to defend their systems. The audit I linked to above is from an election for the King County Conservation District. It’s farfetched that anyone would go to so much trouble to attack such a low-stakes election.
But sophisticated attacks would become far more plausible if the software were used to elect members of Congress and even the president. In that case, we can imagine foreign governments like Russia or China being willing to invest significant resources to compromise election results in a way that’s difficult to detect. We don’t know the full extent of these countries’ offensive capabilities, of course. But it’s reasonable to think that they’d be able to compromise OmniBallot’s software in ways that wouldn’t be revealed in a post-election audit.
To be fair to Democracy Live, the issues the researchers highlighted aren’t unique to the OmniBallot software. Rather, there’s an overwhelming consensus among computer security experts that Internet-based voting is a bad idea in general. Halderman and Specter cite a 2018 report from the National Academies of Sciences, Engineering, and Medicine that found that “no known technology guarantees the secrecy, security, and verifiability of a marked ballot transmitted over the Internet.”
https://arstechnica.com/?p=1682291
Ajit Pai caves to SpaceX but is still skeptical of Musk’s latency claims
Getty Images | Yuichiro Chino
The Federal Communications Commission has reversed course on whether to let SpaceX and other satellite providers apply for rural-broadband funding as low-latency providers. But Chairman Ajit Pai said companies like SpaceX will have to prove they can offer low latencies, as the FCC does not plan to “fund untested technologies.”
Pai’s original proposal classified SpaceX and all other satellite operators as high-latency providers for purposes of the funding distribution, saying the companies haven’t proven they can deliver latencies below the FCC standard of 100ms. Pai’s plan to shut satellite companies out of the low-latency category would have put them at a disadvantage in a reverse auction that will distribute $16 billion from the Rural Digital Opportunity Fund (RDOF).
But SpaceX is launching low-Earth-orbit (LEO) satellites in altitudes ranging from 540km to 570km, a fraction of the 35,000km used with geostationary satellites, providing much lower latency than traditional satellite service. SpaceX told the FCC that its Starlink service will easily clear the 100ms cutoff, and FCC Commissioner Michael O’Rielly urged Pai to let LEO companies apply in the low-latency tier.
The FCC voted to approve the updated auction rules yesterday. The final order isn’t public yet, but it’s clear from statements by Pai and other commissioners that SpaceX and other LEO companies will be allowed to apply in the low-latency tier. The satellite companies won’t gain automatic entry into the low-latency tier, but they will be given a chance to prove that they can deliver latencies below 100ms.
“I am grateful to the chairman for agreeing to expand eligibility for the low-latency performance tier and change language that was prejudicial to certain providers,” O’Rielly said at yesterday’s FCC meeting. “While a technology-neutral policy across the board may have been more effective in promoting innovation and maximizing the value of ratepayer investments, I recognize that a balancing act was necessary to reach the current disposition.”
Pai: FCC will apply “very close scrutiny”
Pai said that he agreed to the change “at the request of one of my fellow commissioners.” The final rules “don’t entirely close the door on low-Earth orbit satellite providers bidding in the low-latency tier,” Pai continued. “However, it is also important to keep in mind the following point: The purpose of the Rural Digital Opportunity Fund is to ensure that Americans have access to broadband, no matter where they live. It is not a technology incubator to fund untested technologies. And we will not allow taxpayer funding to be wasted. A new technology may sound good in theory and look great on paper. But this multi-billion-dollar broadband program will require ‘t’s to be crossed—not fingers. So any such application will be given very close scrutiny.”
When contacted by Ars today, Pai’s office confirmed that “the commission modified the draft to permit LEO service providers to apply to bid in the low-latency tier instead of limiting them to the high-latency tier, and staff will be closely reviewing all applications to ensure they can meet the FCC’s performance requirements for service providers.”
SpaceX is aiming to provide service later this year, and CEO Elon Musk has said the company is aiming for latency below 20ms.
Commissioner Geoffrey Starks supported the low-latency change in his statement:
I appreciate Commissioner O’Rielly’s work in revising this Public Notice to eliminate the categorical bar on low-Earth orbit satellite systems bidding in the low-latency tier, especially now that we have evidence in the record that those systems can meet the 100-millisecond latency standard. At the same time, I see no need for the Public Notice’s predictive judgments about the merits of short-form applications from low-Earth orbit satellite operators. As I have stated previously, next-generation satellite broadband holds tremendous technological promise for addressing the digital divide and is led by strong American companies with a lengthy record of success. Commission staff should evaluate those applications on their own merits.
Pai and O’Rielly are Republicans, while Starks is part of the FCC’s Democratic minority.
SpaceX excluded from gigabit tier
The $16 billion in phone and broadband subsidies will be distributed in a reverse auction scheduled to begin on October 29. ISPs can seek funding in census blocks where no provider offers home-Internet speeds of at least 25Mbps downstream and 3Mbps upstream. The $16 billion will be distributed over 10 years, so ISPs that get funded will collect a total of about $1.6 billion a year and face requirements to deploy broadband service to a certain number of homes and businesses.
Pai’s auction rules also shut SpaceX and other satellite operators out of applying for funding in the gigabit tier. SpaceX could still apply for funding in the 100Mbps-and-below categories, but the auction will prioritize applications in the gigabit category. SpaceX has said in the past that it would offer gigabit speeds, but the company seems to have only objected to the latency restriction.
The commissioners’ statements did not mention any change to the policy excluding all satellite providers from the gigabit tier. The gigabit tier requires 1Gbps download speeds and 500Mbps upload speeds, which in practice may restrict the category primarily to fiber-to-the-home providers or cable companies that adopt full-duplex DOCSIS technology.
Pai said the FCC is allowing fixed-wireless and DSL providers to apply in the gigabit tier but said that “commission staff will conduct a careful, case-by-case review of applications to ensure that bidders will be able to meet required performance obligations.” There’s apparently still no allowance for LEO-satellite providers to bid in the gigabit tier.
Technology neutrality
O’Rielly said he wanted the FCC to let all types of providers apply for all speed tiers, with the requirement that they demonstrate their ability to deliver those speeds:
One of the key principles that I have sought to advance, in both the auction context and elsewhere, is the concept of technology neutrality… in the auction context, it involves crafting rules that offer a fair shot to innovators across all sectors and don’t unduly tilt the playing field toward particular providers. Therefore, I would have preferred an auction design without up-front technology restrictions; all interested providers should have the opportunity to demonstrate whether they can meet our speed and latency benchmarks at the short-form application stage. After all, the whole point of the auction is to support the deployment of broadband services that wouldn’t otherwise exist in the absence of subsidies.
Before Pai changed his mind, the draft plan said, “In the absence of a real world example of a non-geostationary orbit satellite network offering mass market fixed service to residential consumers that is able to meet our 100ms round trip latency requirements, Commission staff could not conclude that such an applicant is reasonably capable of meeting the Commission’s low latency requirements, and so we foreclose such applications.”
SpaceX met with commission staff over the last few days of May, telling them that its broadband system “easily clears the commission’s 100ms threshold for low-latency services, even including its ‘processing time’ during unrealistic worst-case scenarios.” We contacted SpaceX today about the low-latency change and will update this story if we get a response.
https://arstechnica.com/?p=1682670
FCC failed to monitor Chinese telecoms for almost 20 years: Senate report
The Federal Communications Commission and other US agencies have failed to properly oversee Chinese telecom companies that operate in the United States, according to a bipartisan Senate report released today.
After a year-long investigation, the staff report by the US Senate’s Permanent Subcommittee on Investigations “found that the FCC and ‘Team Telecom’—an informal group comprised of officials from the Departments of Justice, Homeland Security, and Defense—have failed to monitor these three Chinese government-owned carriers,” a joint announcement by the subcommittee’s Republican and Democratic leaders said. The three carriers the subcommittee referred to are China Telecom Americas (CTA), China Unicom Americas (CUA), and ComNet USA. The companies “operated in the US for nearly 20 Years with little to no oversight from the federal government,” the senators’ announcement said.
“The Chinese government engages in cyber and economic espionage efforts against the United States and may use telecommunications carriers operating in the United States to further these efforts,” the report said.
The report comes two months after the FCC stepped up its scrutiny of telecom companies controlled by the Chinese government. The FCC issued orders to China Telecom, China Unicom, ComNet, and ComNet owner Pacific Networks, directing them “to explain why the Commission should not start the process of revoking their domestic and international section authorizations enabling them to operate in the United States.” But the FCC and other agencies had previously failed to exercise proper oversight of these companies, the Senate report said.
The lack of oversight described in the report occurred during both Republican and Democratic administrations. “An FCC spokesman said the commission looks forward to reviewing the Senate report,” according to a Reuters article today.
China Telecom faced little US review
Team Telecom—the informal grouping of the Department of Justice, Department of Homeland Security, and Department of Defense—evaluates national security and law enforcement concerns about telecom carriers and makes recommendations to the FCC.
A section of the report on China Telecom says the company “is ultimately owned by the Chinese government” and has operated in the US for nearly 20 years. The company’s “US operations provide opportunities for China to engage in economic espionage against the United States,” the report said.
When China Telecom applied for authorization to operate in the US in 2001, Team Telecom did not object, and the FCC thus “streamlined the application and approved it two weeks after accepting it for filing.” The original authorization “limited CTA to providing international services between the United States and international points, other than China,” but the FCC shortly thereafter approved another “authorization to serve as a facilities-based carrier between the United States and China.”
After those two authorizations, “Team Telecom did not interact with CTA between 2002 and 2007” and “documents suggest that Team Telecom may not have understood that, prior to 2007, CTA was providing services between the United States and China,” the Senate report said.
CTA notified the FCC of a change in ownership in July 2007, though this “change had no impact on CTA’s ultimate ownership” by the Chinese government, the report said. The restructuring triggered a new FCC review, in which CTA told the agency that “its customers were split among enterprise customers and other telecommunications carriers throughout the United States.” CTA also “provided Team Telecom with a list of its top three executives—all of whom were Chinese nationals.”
“Team Telecom determined that security measures were warranted,” and “the parties negotiated a three-page security agreement” that among other things was intended “to prevent unauthorized access to, or disclosure of the content of, communications or US records.”
But the US government barely followed up with CTA after that agreement. “Team Telecom’s oversight of CTA since 2007 has consisted of two site visits and intermittent email communication,” the Senate report said.
“When asked to explain the lack of oversight during this period, despite the security agreement being in effect, Team Telecom officials pointed to the security agreement, noting that because it was broadly written, demonstrating compliance was straightforward,” the report said.
Hands-off approach ends
Team Telecom finally began “substantive oversight of CTA” in 2017, in part with a site visit that “identified concerns related to CTA’s storage of US customer data.” The report also said there have been “allegations of China Telecom hijacking communications data dat[ing] back to 2010,” but “Team Telecom did not question CTA about these reports until January 2019.”
CTA denied the allegations, and “Team Telecom appears to have relied on CTA’s written representations regarding the alleged incidents. Team Telecom provided no records or explanation of it conducting further interviews, requesting or reviewing additional documentation, or otherwise questioning CTA’s assertions,” the Senate report said.
The hands-off approach changed by April 2020, when Team Telecom “recommended the FCC revoke and terminate CTA’s Section 214 authorizations because of ‘substantial and unacceptable’ national security risks.” Team Telecom “warned that CTA’s facilities-based authorizations allow it to request interconnections with US carriers” and that CTA had “already established relationships with major US carriers, including Verizon, CenturyLink, and AT&T.”
“Neither Verizon, AT&T, nor CenturyLink maintains any mitigation or other agreement focused on network security with CTA or its parent company,” though these US carriers “maintain company-wide cybersecurity defenses that apply to all external traffic,” the Senate report said.
The report says that “CTA is untrustworthy,” arguing that the company’s “delayed response” to document and information requests in April 2018 “called into question CTA’s willingness to comply with the security agreement.” Team Telecom also found that “CTA had breached the security agreement by failing to implement a formal written information security policy prior to December 1, 2018.”
China Telecom denies “purely hypothetical risks”
The FCC is still considering the Team Telecom recommendation to revoke CTA’s authorizations. CTA disputed the allegations in an FCC filing yesterday, saying that the FCC “inquiry unfairly and improperly places the burden on CTA to prove a negative regarding unspecified national security concerns about ‘exploitation’ and ‘influence’ of the Chinese government. These vague terms are left undefined in the Order or, to CTA’s knowledge, anywhere in the FCC’s rules or decisions.” CTA’s redacted filing says the company “serv[es] many US customers” and employs “many US citizens and permanent residents.”
“[E]ven if the commission were to credit the purely hypothetical risks suggested by the [Team Telecom] recommendation, none of which have actually occurred, the commission would have to consider whether there is a remedy short of revocation that would foreclose these risks while preserving the services used by thousands of CTA customers. Team Telecom’s summary refusal even to consider potential mitigation measures is not justified,” China Telecom wrote.
CTA also wrote that “the Communications Act and Commission precedent permit revocation of CTA’s authorizations only if there is clear and convincing evidence of egregious misconduct by CTA.”
https://arstechnica.com/?p=1682529
1 billion robocalls net $225M FCC fine that will likely never be collected
Getty Images | Juj Winn
The Federal Communications Commission today proposed a $225 million fine for health-insurance telemarketers who “made approximately 1 billion spoofed robocalls across the country during the first four and a half months of 2019.” But the FCC’s track record in collecting on proposed fines is so poor that the fine is unlikely to ever be collected at anywhere close to the proposed amount.
Rising Eagle, a Texas-based health insurance telemarketer, made 1 billion calls “on behalf of clients that sell short-term, limited-duration health insurance plans,” the FCC said. Here’s how the FCC described the robocalls:
The robocalls falsely claimed to offer health insurance plans from well-known health insurance companies such as Aetna, Blue Cross Blue Shield, Cigna, and UnitedHealth Group. For example, one call stated: “Are you looking for affordable health insurance with benefits from a company you know? Policies have all been reduced nationwide such as Cigna, Blue Cross, Aetna, and United just a quick phone call away. Press 3 to get connected to a licensed agent or press 7 to be added to the Do Not Call list.” If they did press 3, consumers were transferred to a call center with no affiliation to the named companies, where call center representatives then would attempt to convince the consumer to purchase an insurance product sold by one of Rising Eagle’s clients. Rising Eagle’s largest client, Health Advisors of America, was sued by the Missouri Attorney General for telemarketing violations in February 2019.
The proposed $225 million fine is for “apparent violations by John C. Spiller and Jakob A. Mears, who used business names including Rising Eagle and JSquared Telecom,” the FCC said. It’s a proposed fine because that’s how the FCC process works: the commission issues a Notice of Apparent Liability for Forfeiture containing allegations, and the alleged robocaller is given an opportunity to respond and provide evidence. The process can end in a settlement or a fine that cannot exceed the proposed amount of $225 million. The amount of $225 million would be the largest-ever FCC fine, but the commission has a disappointing track record in collecting on these proposed penalties.
“Over the last several years the FCC has levied hundreds of millions in fines against robocallers just like the folks we have here today. But so far collections on these eye-popping fines have netted next to nothing,” FCC Commissioner Jessica Rosenworcel, one of two Democrats on the Republican-majority commission, said in a statement sent to reporters today. “In fact, it was last year that The Wall Street Journal did the math and found that we had collected no more than $6,790 on hundreds of millions in fines. Why? Well, one reason is that the FCC looks to the Department of Justice to collect on the agency’s fines against robocallers. We need them to help. So when they don’t get involved—as here—that’s not a good sign.”
According to the FCC press release, “Spiller admitted to the USTelecom Industry Traceback Group that he knowingly called consumers on the Do Not Call list as he believed that it was more profitable to target these consumers. He also admitted that he made millions of calls per day, and that he was using spoofed numbers.”
The FCC investigation into Rising Eagle found that its calls “were spoofed in order to deceive consumers, targeted millions of Do Not Call list participants, and were received on many wireless phones without prior consumer consent.” The Rising Eagle “scam also caused the companies whose caller IDs were spoofed to become overwhelmed with angry call-backs from aggrieved consumers. At least one company was hit with several lawsuits because its number was spoofed, and another was so overwhelmed with calls that its telephone network became unusable.”
Spoofing of Caller ID lets callers hide their identities by making phone calls appear to come from other numbers. The FCC, following instructions from Congress, is mandating that carriers deploy the STIR/SHAKEN framework that uses digital certificates to verify the accuracy of Caller ID. The FCC has also been pressuring US-based carriers to stop accepting suspicious foreign call traffic, but the robocall problem is so big that it may never be fully solved.
Update at 3:30pm ET: After this story published, FCC Chairman Ajit Pai announced that seven state attorneys general today sued Rising Eagle and the other robocallers in the case in US District Court for the Southern District of Texas. The court complaint seeks a permanent injunction and damages of up to $3,000 for each violation.
https://arstechnica.com/?p=1682403
Brazil pulls all coronavirus stats, then releases incompatible numbers
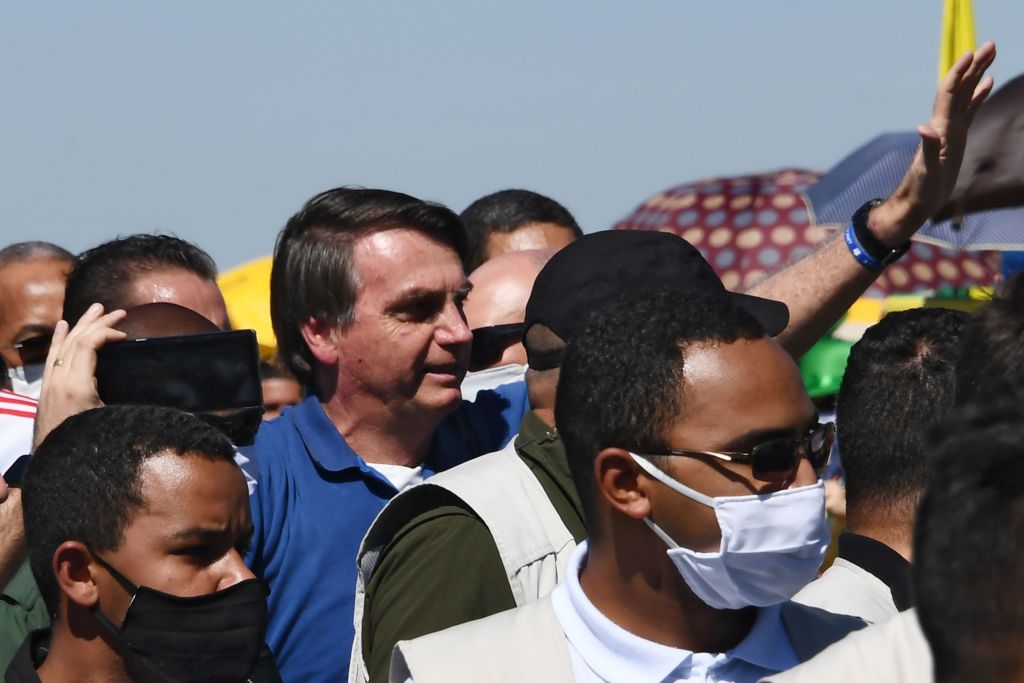
Enlarge/ For Brazilian President Jair Bolsonaro, shown here without a face mask, public health precautions are for other people.
Outside of the United States, Brazil has the largest number of confirmed SARS-CoV-2 infections; it’s behind only the US and UK in terms of confirmed COVID-caused deaths. Meanwhile, its leader, President Jair Bolsonaro, has frequently minimized the risks posed by the pandemic and has frequently been photographed taking minimal precautions—going without a face mask and hugging supporters.
Complicating his country’s policy response, Bolsonaro has also fired his health minister in the midst of the pandemic, only to see his replacement quit after a month on the job.
All of that took place, however, against a backdrop of detailed data about the known extent of the COVID-19 pandemic within the country, allowing Bolsonaro’s public proclamations to be tested against the facts. Over the weekend, however, all of that data was taken down from government websites. After a brief hiatus, it was replaced by a simple tally of cases and deaths—only to see that replaced by a different set of numbers shortly afterwards.
Previously, the government website provided access to data that tracked the progress of the pandemic over time and broke it down by state. Information on larger municipalities was also present. This data could be useful for tracking the spread of the disease over time and designing policies to limit its spread from areas where it’s highly prevalent to those with a lower case burden.
Instead, the website has been replaced by a page that simply lists new cases, deaths, and recoveries, with new being defined as within the last day. A separate report of the total cases and deaths, however, listed numbers that were inconsistent with the ones found at the daily update site. By Monday, the numbers had been brought into alignment, but the reason for the discrepancy hadn’t been disclosed.
As in the US, the government’s response to the pandemic has been heavily politicized, which has led to accusations that the decision to limit data availability was meant to obscure the extent of the pandemic in Brazil. On the opposite side of the political spectrum, a government minister accused state and local governments of inflating their figures in order to receive more funding. On Sunday, that same minister announced he was stepping down after threats of a boycott of his businesses.
Math is hard
Even in countries where there’s no indication that reporting of basic medical statistics is being distorted, however, getting accurate numbers can be a challenge. On Monday, The Washington Post released a state-by-state analysis of pandemic figures submitted to the Centers for Disease Control. It finds that fewer than half the states are following the CDC guidelines for the data they submit.
Due to the frequent problems the US has had with providing sufficient testing capacity, many people with COVID-19 symptoms—including some who ultimately died—were never tested. As a result, the CDC was advised to include suspected cases in with its figures. But, even months after this guidance was issued, many states haven’t submitted the data on suspected cases. Their submission of any data is voluntary, and states contacted listed a variety of reasons for not complying with the CDC’s requests. But in at least one case (Illinois), the state indicated it was not submitting data for reasons that echo the accusations in Brazil: “concern from the public that the number of deaths is being inflated.”
Many countries that have strong national health systems made testing available shortly after the outbreak reached them. These likely have accurate counts of the total cases. But for many countries, we’ll probably have to wait for a detailed analysis of nationwide mortality figures to get a complete picture of the scope of the pandemic. That’s a process that could take years—assuming it occurs without political interference.
https://arstechnica.com/?p=1682149
Cox slows Internet speeds in entire neighborhoods to punish any heavy users
Cox Communications is lowering Internet upload speeds in entire neighborhoods to stop what it considers “excessive usage,” in a decision that punishes both heavy Internet users and their neighbors.
Cox, a cable company with about 5.2 million broadband customers in the United States, has been sending notices to some heavy Internet users warning them to use less data and notifying them of neighborhood-wide speed decreases. In the case we will describe in this article, a gigabit customer who was paying $50 extra per month for unlimited data was flagged by Cox because he was using 8TB to 12TB a month.
Cox responded by lowering the upload speeds on the gigabit-download plan from 35Mbps to 10Mbps for the customer’s whole neighborhood. Cox confirmed to Ars that it has imposed neighborhood-wide slowdowns in multiple neighborhoods in cases like this one but didn’t say how many excessive users are enough to trigger a speed decrease.
Mike, a Cox customer from Gainesville, Florida, pays $150 a month, including $100 for 1Gbps download speeds and 35Mbps upload speeds, and another $50 for “unlimited data” so that he can go over Cox’s 1TB data cap. Mike told Ars via email that most of his 8TB+ monthly use consists of scheduled device backups and “data sharing via various (encrypted) information-sharing protocols,” such as peer-to-peer networks, between 1am and 8am. (We agreed to publish Mike’s first name only but reviewed his bills and confirmed the basic details of his account with Cox.)
Generally speaking, data usage for most households declines significantly during those 1am-8am overnight hours, so a robustly built broadband network should be able to handle the traffic. In any case, Mike couldn’t use more than 35Mbps for uploads at any given time because that’s the limit Cox always imposed on its gigabit-download cable plan. Mike said his household’s daytime and evening use is more like a typical Internet user’s, with work-from-home activities during the day and streaming video in high-definition during the evening.
Mike also said his level of Internet usage has been roughly the same for the past four years that he’s been using Cox—but it was only in mid-May that the company flagged him for excessive use. This may suggest that Cox is struggling to handle pandemic-level broadband traffic, but Cox says that the vast majority of its network is “performing very well.”
“Scheduled for termination”
First, Mike got three calls from Cox including one that left a voicemail saying, “we need to speak with you regarding your Internet usage. Your home is using an extraordinarily high amount of Internet data and adjustments need to be made immediately.” The voicemail warned that your “Internet will be scheduled for termination” unless usage reductions are “made within five days,” according to Mike.
Mike explained how he responded:
Since I work from home, I naturally was very concerned they would pull the plug on me and I’d be unable to work. Immediately calling the number [provided in the voicemail], I was funneled directly to a department for “questions about your recent Internet speed changes,” and spoke with a representative there. He went on to explain that their network is overburdened and since I was an above-average user, I was being targeted to lower my usage or else have my account terminated… I tried to explain that my usage is not out of the ordinary for me. My day-time bandwidth usage is paltry (most of my bandwidth consumption is scheduled from 1am-8am), and that Cox should have been upgrading their infrastructure instead of oversubscribing nodes and pocketing the record revenue. I was told if I did not make a substantial decrease in my upload data usage, my service would be terminated.
Comments in a Reddit thread last month confirm that Mike isn’t the only Cox customer being warned to cut upload speeds in order to avoid being kicked off the network. Cox didn’t tell Mike exactly how much data he’d have to shave off his monthly usage. There was “no magic number or threshold, just an arbitrary amount of decrease, a Cox-deemed ‘good effort,'” or his service would be cut off, he said.
Shortly after that phone call, Mike received an email from Cox with the subject line, “Alert: Action required to continue your Internet service.” Mike provided Ars with a copy of the email.
“We’ve recently tried getting in touch with you about your service—your account has been identified as using an extremely high level of bandwidth, which is causing a negative impact on our network and our other customers across your neighborhood,” the email said. Mike’s “extraordinarily high” upload usage “is negatively impacting Internet service of other customers, which is a violation of our Acceptable Use Policy, the email said. The policy contains a broad prohibition on transmitting amounts of data large enough to disrupt the network, but it doesn’t specify an amount.
The real kicker is that Cox’s email to Mike said that everyone in his neighborhood will get lower upload speeds until July 15:
During these unprecedented times, many people are working and schooling from home, and maintaining connectivity is important. We are working to provide a positive Internet experience for everyone, so we’ve adjusted our Gigablast upload speeds in your neighborhood from 35Mbps to 10Mbps, now through July 15, 2020. Your download speeds have not changed.
Cox’s email doesn’t specifically state that Mike’s usage spurred the decision to impose a neighborhood-wide slowdown, but this is apparently only happening in a small percentage of neighborhoods where Cox has seen heavier use than elsewhere in its network.
Questions for Cox
This raises several questions that we asked Cox. We asked the cable company why its network is “unable to handle Mike’s uploads in the middle of the night” and whether it has “considered adding capacity to its network instead of forcing unlimited-data customers to use less data.” We asked Cox how much data, specifically, customers who pay for unlimited data are actually allowed to use, and “Why isn’t Mike allowed to use unlimited data when he is paying for the highest speeds and paying extra for unlimited data?”
We also asked why Cox is imposing slowdowns throughout entire neighborhoods instead of only on the people allegedly violating the Acceptable Use Policy and whether the slowdowns are imposed even when only a single customer in a neighborhood is flagged for excessive usage. We also asked how many people in Mike’s neighborhood are affected by the upload-speed decrease and whether they will get discounts to reflect their reduced service.
Cox didn’t provide as much detail as we were looking for, but it confirmed the neighborhood-wide speed decreases, saying it has “identified a small number of neighborhoods where performance can be improved for all customers in the neighborhood by temporarily increasing or maintaining download speeds and changing upload speeds for some of our service tiers.”
Cox defended the temporary 10Mbps upload speed for its gigabit-download plan, saying that “10Mbps is plenty of speed for the vast majority of customers to continue their regular activity and have a positive experience.” Of course, customers paying extra for Cox’s fastest plan and unlimited data are more likely to be outliers who do need high upstream bandwidth. Unlike fiber-to-the-home service, in which ISPs offer symmetrical upstream and downstream speeds, cable service generally has much lower uploads than downloads. Cox offers symmetrical gigabit speeds in some areas where it has deployed fiber directly to homes but provides slower upload speeds on its cable network. Cable users may eventually get symmetrical upload and download speeds from an upgrade to DOCSIS, the Data Over Cable Service Interface Specification.
A Cox webpage that was updated on April 30 says that the gigabit plan’s upload speeds are now “10Mbps in limited areas to support consistent service across customers during periods of sustained increased Internet usage.”
The now-repealed net neutrality rules likely wouldn’t have prevented this kind of data slowdown, as the slowdown would presumably fall under an exception for “reasonable network management.” But the Obama-era system in which ISPs were regulated as common carriers gave more rights to consumers to complain about unreasonable rates and practices, perhaps giving extra impetus to ISPs to upgrade their networks instead of limiting their users. Cox is a private company and thus doesn’t report network-upgrade spending publicly, but major ISPs such as Comcast, AT&T, and Charter have reduced network spending since the FCC repealed its net neutrality rules and common-carrier regulation.
Cox says network “performing very well”
Cox told Ars its “network is performing very well overall” during the pandemic, and that out of 28,000 neighborhood nodes across the US, 98 to 99 percent “are performing with adequate capacity even with the tremendous level of increased peak usage.” If Cox’s 5.2 million paying broadband customers are spread equally across nodes, each node would serve about 185 households.
Cox said that it always “keep[s] a close eye at the individual node level to make sure we don’t approach any congestion thresholds and need to make any adjustments. Similar to our normal process, if we see the network reach or exceed utilization thresholds we will accelerate network upgrade plans in the impacted areas. This could include splitting nodes, pulling additional fiber, equipment swaps and/or core network changes, all of which add capacity to the area.”
But those measures apparently aren’t enough to handle users like Mike, Cox said:
In some instances a number of excessive users, like the customer you referenced, are causing congestion problems in a small number of neighborhoods by utilizing over 100-200 times more upstream bandwidth than the average household. This type of excessive usage is negatively impacting the service of other customers, which is a violation of our Acceptable Use Policy. It is not our desire to terminate anyone’s service, but we may need to address excessive usage out of fairness to the rest of our customers, especially during this time when households are even more dependent on a good Internet experience…
In the case of the customer you mentioned, we have communicated with him about our concerns and it appears he has made adjustments to his usage to operate within our Acceptable Use Policy.
Mike confirmed to Ars that he has lowered his use by limiting overnight upload speeds to 400kbps, “so that it is always throttled.” His usage in the 2.5 weeks since May 22 is 2.1TB, putting him well below his usual monthly pace.
Pandemic spurs extra broadband use
Broadband networks have mostly held up well during the pandemic. Cable-lobby group NCTA, which represents Cox and other cable companies, says that “networks are engineered to provide superior performance throughout the day” and that “provider-backbone networks have significant capacity and show no signs of congestion.” Since March 1, NCTA says that peak upstream traffic has risen 26.2 percent and peak download traffic has risen 9.1 percent.
Mike said he suspects Cox is limiting upload speeds “because their network can’t handle the increase of residential live video conference streaming” that’s happened during the pandemic. Recently, Mike said he’s been seeing upload speeds of only 4Mbps to 5Mbps.
Coming soon: A price increase
Mike’s bill is currently lower than usual because Cox, like other ISPs, is providing unlimited data to all customers during the pandemic. The waiver of the $50 monthly unlimited-data charge temporarily knocked his bill down to $100, and Cox provided a further $20 discount on his latest bill. Mike’s bill doesn’t explain the reason for the $20 credit, but it could be because of the new upload-data limit.
But Cox is already signaling that Mike is in for a price increase in the near future. Today, Mike told Ars that “I just got an alert after logging in that my one-year introduction rate is now over, so I’ll be paying $175 a month for ‘unlimited’ data once the current data-overage exceptions expire. Yay.”