Reddit will require you to log in to use old.reddit.com
Reddit will start requiring people to be logged into Reddit to use old.reddit.com.

The new requirement will take effect “over the next month,” a Reddit employee going by the username boat-botany announced on the social media platform today. The person claimed that the change is part of an ongoing effort to “tighten how automated systems access Reddit.”

The Reddit employee wrote:

Old Reddit’s logged-out experience is a significant source of abusive scraping and automated traffic on the platform. It’s also an important interface for many long-time mods and Redditors. To strike the right balance between preserving your access to Old Reddit while preventing abusive scraping and automated traffic, over the next month we will start requiring everyone to log in.

In a follow-up comment, boat-botany defined abusive behavior as that which violates Reddit’s rule prohibiting activity that interferes with the platform’s “normal use” or that “create[s] programs or applications” that break Reddit’s (controversial) API rules.

“By logging in, we get a lot more signal that allows us to detect whether an account is breaking the rules, and then we can block that traffic or enforce those accounts,” boat-botany said.

As of this writing, Ars was still able to use old.reddit.com without logging in.

The news is likely to upset some longtime Reddit users who have relied on old.reddit.com for a familiar look that they find easier to navigate and digest and who also want to view Reddit without logging in for convenience and/or privacy.

When a user asked boat-botany why New Reddit isn’t scraped as often as Old Reddit, the Reddit employee pointed to a comment by another user.

“[T]he shape of malicious traffic is always changing,” the user, Nestramutat, wrote. “It’s going to be a constant cat and mouse game[.] As you ban one method, a new one gets developed. It’s easy to see abusive traffic in hindsight, but it’s harder to pre-emptively block it. Given that they’re claiming Old Reddit doesn’t have the modern security stack, this is likely proving to be an even greater challenge.”

https://arstechnica.com/gadgets/2026/06/reddit-will-require-you-to-log-in-to-use-old-reddit-com/

Apple takes Epic fight over app store fees to the Supreme Court

According to Reuters, the Supreme Court will likely hear the case during its next term, which begins this October.

Apple’s math will likely be challenged

Apple’s filing said that Epic is hoping that the court fight will end with Apple charging a de minimis rate to developers who want to have more control over how transactions are completed in their apps.

In litigation that has been paused during the Supreme Court review, Epic expects to force Apple to show receipts explaining why commission rates are so high.

So far, Apple has claimed that commission fees “ensure that Apple can continue to receive compensation for use of its IP-protected tools, technologies, and services—the very things that attract developers and enable app creation.”

For example, with Epic, Apple claims that purchases like even a single “skin” that Fortnite players buy to make their characters look unique require a fee. Those commissions help Apple develop and update “the iPhone screen that displays it, the iPhone touch controls that direct the virtual character, the Apple silicon chip that processes all iOS software, the app development tools Epic used to build Fortnite for iOS, and the App Store platform that downloads, updates, and maintains the app,” their filing said.

If the Supreme Court sides with Apple and reverses the contempt finding, Apple is hoping to wriggle out of sharing “confidential business data regarding the company’s decision-making concerning the App Store, its implementation of linked-out purchases for developers, and its internal discussions regarding compliance with the injunction.”

Meanwhile, the UK is also hoping to analyze Apple’s actual costs. The CMA has suggested that Apple “could still levy fees” for allowing link-outs, “but that such charges would have to be applied fairly,” the Guardian reported. Like Epic, the Coalition for App Fairness suggested that any app store developer “charges should be justified by ‘transparent data’ from Apple and Google explaining any underlying cost to the tech companies.”

Apple did not immediately respond to Ars’ request to comment.

https://arstechnica.com/tech-policy/2026/06/apple-takes-epic-fight-over-app-store-fees-to-the-supreme-court/


Trump’s plan to redesign every .gov website leads to AI-designed horrors

Single-page launches, odd redirects

Ars conducted a comprehensive review of launched sites to assess NDS’s progress so far.

Most of the few dozen websites NDS has launched consist of a single page, where visitors can do little more than fill out a sign-up form. The most useful offering may be TrumpRX, which includes a search tool for comparing drug prices. For anything else, visitors must visit a legacy site.

There are also many newly registered domains—like live.gov, onlyfarms.gov, aliens.gov, and why.gov—which currently redirect to legacy sites. Some of those old sites may be updated with NDS’s signature flair, but the ones that don’t look as pretty remain the primary resource for Americans seeking government information or assistance online.

At least one website, 250.gov, which celebrates 250 years of US history, curiously redirects to a dot-org rather than a dot-gov, which is unusual for a government site and could erode visitor trust.

Among the few larger sites that NDS has launched is its own, ndstudio.gov. Currently, that site catalogs the team’s launches, shares a brief timeline of US design achievements, discusses the team’s AI and accessibility efforts, and encourages talented designers to “apply now.”

It also briefly hosted a store marketing a $47 limited edition MAHA poster and a $400 “collector’s edition” with Secretary of Health and Human Services Robert Kennedy, Jr.’s autograph, NextGov reported. The store disappeared after the White House faced questions about where the profits from sales would go. A White House spokesperson told NextGov that the posters were never “actually for sale,” as the store’s items did not include a “purchase button.”

The only other site of similar scope is merrychristmas.gov, which, beyond the homepage, includes one page for each of the 12 days of Christmas. An apparent vanity project rather than a government resource, the site is also a celebration of NDS designs and culminates on Christmas with a page praising the group for building sites reflecting “a belief that thoughtful design can strengthen democracy and improve civic life.”

https://arstechnica.com/tech-policy/2026/06/trumps-plan-to-redesign-every-gov-website-leads-to-ai-designed-horrors/


Streaming services’ obnoxiously loud ads become illegal on July 1 in California

The Motion Picture Association, which includes Netflix, Disney, Amazon Prime Video, and Paramount, and the Streaming Innovation Alliance, which includes Netflix, Disney, Peacock, and Pluto TV, opposed the bill. The groups argued that “many” streaming services were already trying to manage the “loudness of advertisements that come from server-side ad insertion that may be inconsistent with the loudness of the programs,” per a state Assembly analysis (PDF) from September 2025. Server-side ads can have differing volumes due to companies using various encoding pipelines.

Additionally, as the opposing groups previously pointed out, streaming services must contend with a broad range of output devices, including TVs, tablets, and phones.

Reporting on how streaming services might follow the California law, trade publication TV Tech in December reported: “Streaming providers will need to integrate file-based and, in some cases, real-time processing and loudness control into their server-side commercial insertion workflow, just as they currently do for their primary programming.”

The obstacles in managing the loudness of ads are underscored when considering the dissatisfaction that remains among broadcast, cable, and satellite viewers. The FCC said it received “at least” 1,700 complaints about this in 2024, about 825 in 2023, and approximately 750 in 2022.

https://arstechnica.com/gadgets/2026/06/streaming-services-obnoxiously-loud-ads-become-illegal-on-july-1-in-california/


NYT slams Microsoft for building copyright-infringing supercomputer for OpenAI

NYT targets Microsoft supercomputer

In 2023, the NYT became the first major publisher to sue OpenAI. The prominent newspaper alleged that ChatGPT was illegally trained on its articles, infringed on its copyrights by outputting articles verbatim, and caused market harms by positioning ChatGPT as a substitute for a NYT subscription, as well as reputational harms by falsely attributing claims to NYT reporting. Additionally, ChatGPT outputs summarizing Wirecutter reviews robbed writers of commissions from lost clicks on affiliate links, the NYT alleged.

In the initial complaint, the NYT discussed Microsoft’s supercomputing systems as if they were providing generic cloud computing services. The updated complaint seeks to specify that the supercomputer was tailor-made to help OpenAI infringe and allege that it was built for the explicit purpose of training AI on copyrighted works without permission. And as the NYT alleged, its articles were more heavily weighted by this system, as both firms hoped to train models on the highest-quality journalism possible, so that level of writing could be confidently mimicked in outputs.

By building this “unusually complex” machine, Microsoft not only helped select the works that were infringed but also provided a means to seize copyrighted works without permission, the NYT alleged.

“Microsoft specifically designed it for the purpose of using essentially the whole Internet—curated to disproportionately feature Times Works—to train the most capable LLM in history,” the NYT alleged.

And now it’s allegedly unfairly profiting.

“Microsoft’s deployment of Times-trained LLMs throughout its product line helped boost its market capitalization by a trillion dollars in the past year alone,” the NYT alleged.

Model outputs show market harms, NYT alleged

For the NYT, outputs shared during discovery—including a huge chunk of users’ ChatGPT sessions—remain some of the strongest evidence that OpenAI and Microsoft built tools that allegedly replaced the NYT by producing near-verbatim excerpts of its copyrighted works.

In some cases, users told ChatGPT they were trying to skirt paywalls and were able to see significant chunks of articles by requesting to see the “next paragraph.” In other cases, “models simply spit out several paragraphs” without such finagling. To prove market harms caused by substitution, they shared examples in their complaints of side-by-side comparisons, as well as screenshots of allegedly infringing outputs:

https://arstechnica.com/tech-policy/2026/06/microsoft-built-supercomputer-to-help-openai-infringe-copyrights-nyt-alleged/


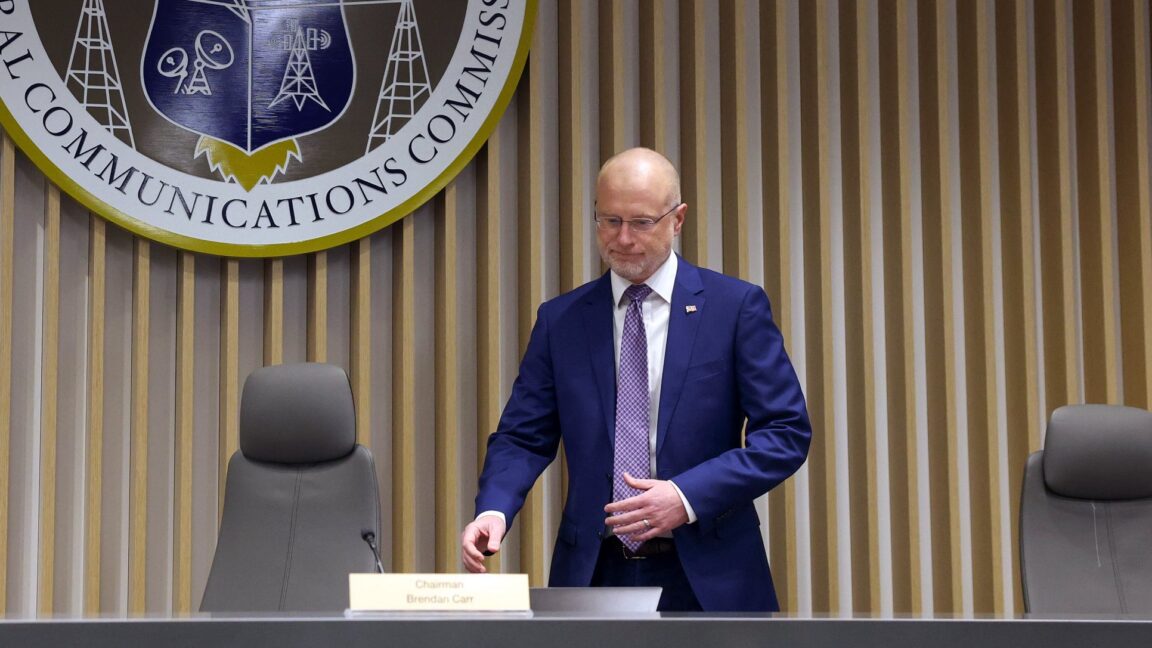
FCC accused of hiding Chairman Carr’s messages with DOGE and Musk

The FCC “has sought to delay the production of responsive documents and obfuscate the existence of responsive records,” and “made it clear that it will not undertake a good faith effort to produce responsive documents,” the filing said. “Accordingly, discovery is required and will speed the document production process by helping the Plaintiffs identify responsive documents.”

Carr’s phone

The filing said there is evidence that Carr has Signal messaging set up on a phone he uses for FCC business. Carr’s phone number was previously disclosed in a FoIA request that turned up a November 2024 email from a Fox News producer who was confirming an interview. Entering that “number into the Signal app shows that he has an active Signal account under the username ‘Brendan Carr,’” the filing said.

A court filing submitted by the FCC on June 3 said that Carr did not have phone numbers for DOGE personnel and that “it is agency policy not to download additional messaging applications on FCC phones (e.g., Signal, WhatsApp).” Plaintiffs counter that Carr likely exchanged messages with Musk or other high-ranking DOGE officials.

“Plaintiffs do not know whether the number identified in Exs. 4 and 5 belongs to Carr’s personal phone or a government issued phone,” the filing said. “What we do know is that a phone is being used for government business and that it has a Signal account in Carr’s name. Based on information and belief Carr regularly conducts government business through text and Signal messages, communicating with journalists, industry professional and individuals who work for regulated entities, such as Musk and SpaceX.”

Plaintiffs said the FCC’s statement that Carr did not have phone numbers for DOGE personnel doesn’t settle the matter.

“It is unlikely that Carr would have communicated with individuals at that level. Carr would have communicated with Musk or other highly placed DOGE officials,” the filing said. Plaintiffs said a previous case involving DOGE showed that “DOGE personnel routinely conducted business on their personal phones using text messages, especially the Signal app.”

The filing separately accused the FCC of limiting its records search to emails with FCC, DOGE, and GSA (General Services Administration) domains, despite plaintiffs’ objections. It also said that travel documents provided by the FCC did not include anything about Carr’s visits to Starlink facilities.

We contacted the FCC today and will update this article if it provides any comment.

https://arstechnica.com/tech-policy/2026/06/fcc-accused-of-hiding-chairman-carrs-messages-with-doge-and-musk/


SpaceX plans to launch Starlink mobile service in the US

During the IPO roadshow, Musk sold investors on future plans to launch data centers into space and build a colony on Mars. Analysts at its lead underwriter Goldman have predicted a 100-fold surge in its AI revenues to $322 billion by 2030.

While describing expanding Starlink as another key growth pillar in its IPO prospectus, SpaceX has never publicly confirmed that it plans to launch a retail mobile service.

There have been months of speculation over SpaceX’s future mobile plans after it paid $17 billion to rival EchoStar for wireless spectrum licenses to bolster its Starlink satellite network last September. Many analysts viewed the deal as laying the groundwork for an eventual retail offering.

In its bond offering prospectus, seen by the FT, SpaceX said that while it expected the Starlink Mobile service currently “to be most impactful for customers in remote areas uncovered by terrestrial mobile networks,” its longer-term ambitions appeared broader.

As its performance improves and satellite constellation grows, the prospectus suggests the company would “compete to be the preferred connectivity experience to our customers no matter where they are located, whether in rural, suburban or urban areas.”

The launch of a consumer Starlink mobile retail service would also complement the company’s existing broadband Internet option, which served 10.3 million customers worldwide as of March.

However, the plans have been met with trepidation by analysts who have cautioned that the idea may simply be a gamble to extract better deals from Starlink’s telecoms partners and warned of the billions of dollars in build costs and radio wave spectrum needed to roll out mobile networks.

New Street Research estimates that the three US mobile network operators have a total of about 1,020MHz of spectrum, while SpaceX has just 65MHz.

David Barden, partner at New Street Research, said that building a “wireless network in saturated markets around the world would be incredibly hard.”

“[But] as a starting point for negotiating the best possible revenue-sharing deal with mobile network operator partners? It makes tremendous sense,” he added.

Additional reporting by Ryan McMorrow in San Francisco

© 2026 The Financial Times Ltd. All rights reserved. Not to be redistributed, copied, or modified in any way.

https://arstechnica.com/space/2026/06/spacex-plans-to-launch-starlink-mobile-service-in-the-us/


FCC may kill $2B program that connects schools and libraries to Internet

The Federal Communications Commission was roundly criticized today for proposing to scale back or eliminate E-Rate, a $2 billion-a-year Universal Service program that provides discounts for telecom services and equipment in schools and libraries.

FCC Chairman Brendan Carr said E-Rate should be changed because students are getting too much screen time. He led a 2-1 vote to issue a Notice of Proposed Rulemaking (NPRM) that proposes changes and asks the public to comment on them.

“Over the last decade, school districts across the country experimented with a massive increase in screen time for students,” Carr said at today’s meeting.

Carr blamed schools for replacing books and pencils with digital tools and said data shows “that more than half of students now use a computer for up to four hours a day, and a quarter of them spend more than four hours on screens.” He said that E-Rate began in 1997 “with a clear focus—supporting basic Internet access to schools and libraries for educational purposes,” but has “expanded exponentially.”

“We seek comment on whether the program should be reoriented in light of all of the above developments, as well as the increase in connectivity to schools and libraries across the country since 1997,” Carr said.

FCC seeks comment on ending E-Rate

Despite Carr’s use of the word “reoriented,” the options on the table include shutting down E-Rate. This is made clear in a public draft of the NPRM, which asks for comment on whether E-Rate should be limited or sunset:

Should the E-Rate program be limited or sunset to reflect today’s extensive connectivity rates? At what point should policymakers conclude that the program’s core objective has been achieved? We seek comment on whether Congress intended E-Rate to operate indefinitely, regardless of the extent to which schools and libraries have achieved universal connectivity.

Commissioner Anna Gomez, the FCC’s only Democrat, asked Carr’s office to remove the language seeking comment on whether to sunset the E-Rate program. The chair’s office declined that request, a spokesperson for Gomez told Ars today.

https://arstechnica.com/tech-policy/2026/06/fcc-may-kill-2b-program-that-connects-schools-and-libraries-to-internet/


Anthropic says Alibaba must be punished for largest Claude cloning attack

Anthropic accused Alibaba of “brazenly” racing to make a copycat Claude, seemingly unfazed by Trump’s threats to crack down on foreign efforts to copy US frontier models despite depending on US investors.

“Alibaba is listed on the New York Stock Exchange, maintains business operations in the United States, and is accountable to US investors and regulators,” Anthropic’s letter noted, “yet this activity unfolded in the weeks after” Trump’s memo warned that cloning attempts were “unacceptable.”

Ars could not immediately reach Alibaba for comment.

Anthropic wants firms like Alibaba punished

Alibaba is already preparing to clash with Trump, though. In a lawsuit filed Tuesday, Alibaba accused the Trump administration of blacklisting the company after falsely linking the company to the Chinese military, Reuters reported. Alibaba is seeking to remove the Trump designation, which they claimed has “no basis in fact or law.”

“Alibaba is governed by an independent board, none of whom has any military affiliation,” Alibaba said. “Its products and services are built for retail, logistics, and enterprise information technology—not weapons, defense, or intelligence.”

Anthropic appears unconvinced, however, that Alibaba isn’t working with the Chinese government. In the letter, Anthropic warned that without stronger interventions, these distillation attacks will “help China reach Mythos Preview-level capabilities sooner.”

To keep the US ahead of China, Anthropic recommended that Congress pass legislation with three objectives. First, antitrust laws must be updated to allow AI firms to share information about evolving Chinese tactics to deter more threats.

Second, the US needs more export controls on chips to hamstring Chinese access to advanced compute so that they simply can’t train on US model outputs. That could make conducting distillation attacks pointless, Anthropic suggested.

Finally, Congress should pass laws penalizing Chinese labs’ “bad behavior” so that it’s “more difficult and costly” to rely on distillation attacks to advance Chinese models. Penalties could include limiting Chinese firms from accessing US models or advanced US chips or from relying on data centers outside of China, Anthropic suggested.

https://arstechnica.com/tech-policy/2026/06/anthropic-claims-alibaba-defied-trump-to-attack-claude-and-steal-capabilities/


White House drastically shortens deadline for dropping quantum-vulnerable crypto

The White House is drastically shortening the deadline for government agencies and organizations to adopt new quantum-resistant encryption systems that will withstand attacks that use quantum computers, as the federal government seeks to protect decades’ worth of secrets belonging to militaries, banks, governments, and most individuals on Earth.

The executive order, titled Securing the Nation against Advanced Cryptographic Attacks, requires computing systems for “high-value assets” and “high-impact systems” to transition to post-quantum cryptographic key establishment schemes by December 31, 2030, and to quantum-safe digital signature schemes by December 31, 2031.

Heading off a significant threat

The new deadline, which for many organizations is about five years sooner than the previous one, comes on the heels of recent research showing that the resources and cost for building a cryptographically relevant quantum computer are far less than previous consensus estimates. In response, Google, Cloudflare, and other companies recently tightened their timelines for moving off vulnerable systems to 2029.

“The advent of large-scale quantum computers, particularly in the hands of adversaries, will pose a significant threat to widely used cryptographic security systems,” Monday’s executive order stated. “Ongoing cyber activity against our Nation also presents the risk of adversaries collecting United States information now, and decrypting it later once large-scale quantum computers are operational.”

Under a timeline the National Security Agency published in 2022, “National Security Systems”—a class including only defense and intelligence systems under the authority of the agency—were under orders to be quantum-ready between 2030 and 2033. Most other organizations had until 2035 to complete the transition. Now, many of them will be required to transition much sooner.

“So, for any system that falls into this new bucket of high-value assets and high-impact systems, their transition timelines just got shortened by 4-5 years (from 2035 to 2030/2031),” Brian LaMacchia, a cryptography engineer who oversaw Microsoft’s post-quantum transition from 2015 to 2022 and now works at Farcaster Consulting Group, told Ars. “That is a significant shortening of the transition timeline for these systems, and it follows similar timeline revisions from Google and Cloudflare that we saw announced back in late March/early April.”

https://arstechnica.com/information-technology/2026/06/executive-order-bumps-up-deadline-to-move-off-quantum-vulnerable-crypto/