Facebook privacy goof makes posts by 14 million users readable to anyone

Facebook disclosed a new privacy blunder on Thursday in a statement that said the site accidentally made the posts of 14 million users public even when they designated the posts to be shared with only a limited number of contacts.

The mixup was the result of a bug that automatically suggested posts be set to public, meaning the posts could be viewed by anyone, including people not logged on to Facebook. As a result, from May 18 to May 27, as many as 14 million users who intended posts to be available only to select individuals were, in fact, accessible to anyone on the Internet.

“We have fixed this issue, and, starting today, we are letting everyone affected know and asking them to review any posts they made during that time,” Facebook Chief Privacy Officer Erin Egan said in the statement. “To be clear, this bug did not impact anything people had posted before–and they could still choose their audience just as they always have. We’d like to apologize for this mistake.”

Read 5 remaining paragraphs | Comments

https://arstechnica.com/?p=1323177


Handbook on European data protection law – 2018 edition

Di  Council of Europe , European Court of Human Rights , European Data Protection Supervisor , European Union Agency for Fundamental Rights

Data di pubblicazione: 30 maggio 2018

ISBN: 978-92-9491-903-8

Pagine: 402

Prezzo: € 19,78


L’Agenzia dell’Unione Europea per i Diritti Fondamentali (FRA) ha pubblicato il manuale aggiornato sul diritto europeo in materia di protezione dei dati. Il manuale è stato pensato per promuovere la conoscenza delle norme, rivolgendosi in particolare ai professionisti del settore legale non specializzati.


The rapid development of information technology has exacerbated the need for robust personal data protection, the right to which is safeguarded by both European Union (EU) and Council of Europe (CoE) instruments. Safeguarding this important right entails new and signifi cant challenges as technological advances expand the frontiers of areas such as surveillance, communication interception and data storage.


This handbook is designed to familiarise legal practitioners not specialised in data protection with this emerging area of the law. It provides an overview of the EU’s and the CoE’sapplicable legal frameworks.


It also explains key case law, summarising major rulings of both the Court of Justice of the European Union and the European Court of Human Rights. In addition, it presents hypothetical scenarios that serve as practical illustrations of the diverse issues encountered in this ever-evolving field.


Per scaricare la versione pdf del libro clicca qui.

The post Handbook on European data protection law – 2018 edition appeared first on Key4biz.

https://www.key4biz.it/handbook-on-european-data-protection-law-2018-edition/223627/


HR Software Firm PageUp Suffers Data Breach

PageUp, an Australian company that provides HR software, informed customers this week that it launched an investigation on May 23 after detecting suspicious activity on its IT infrastructure.

read more

http://feedproxy.google.com/~r/Securityweek/~3/2tTrrDl8ajg/hr-software-firm-pageup-suffers-data-breach


In seconds, we faked our way into a political campaign, got unsecured voter data

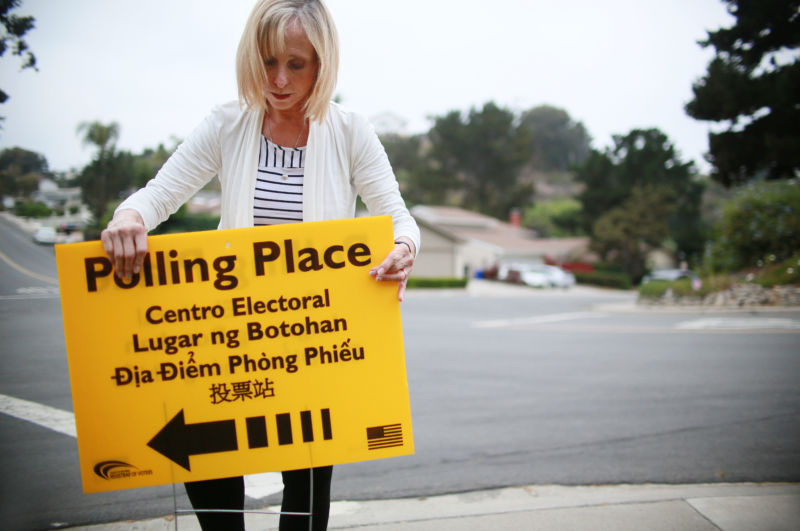
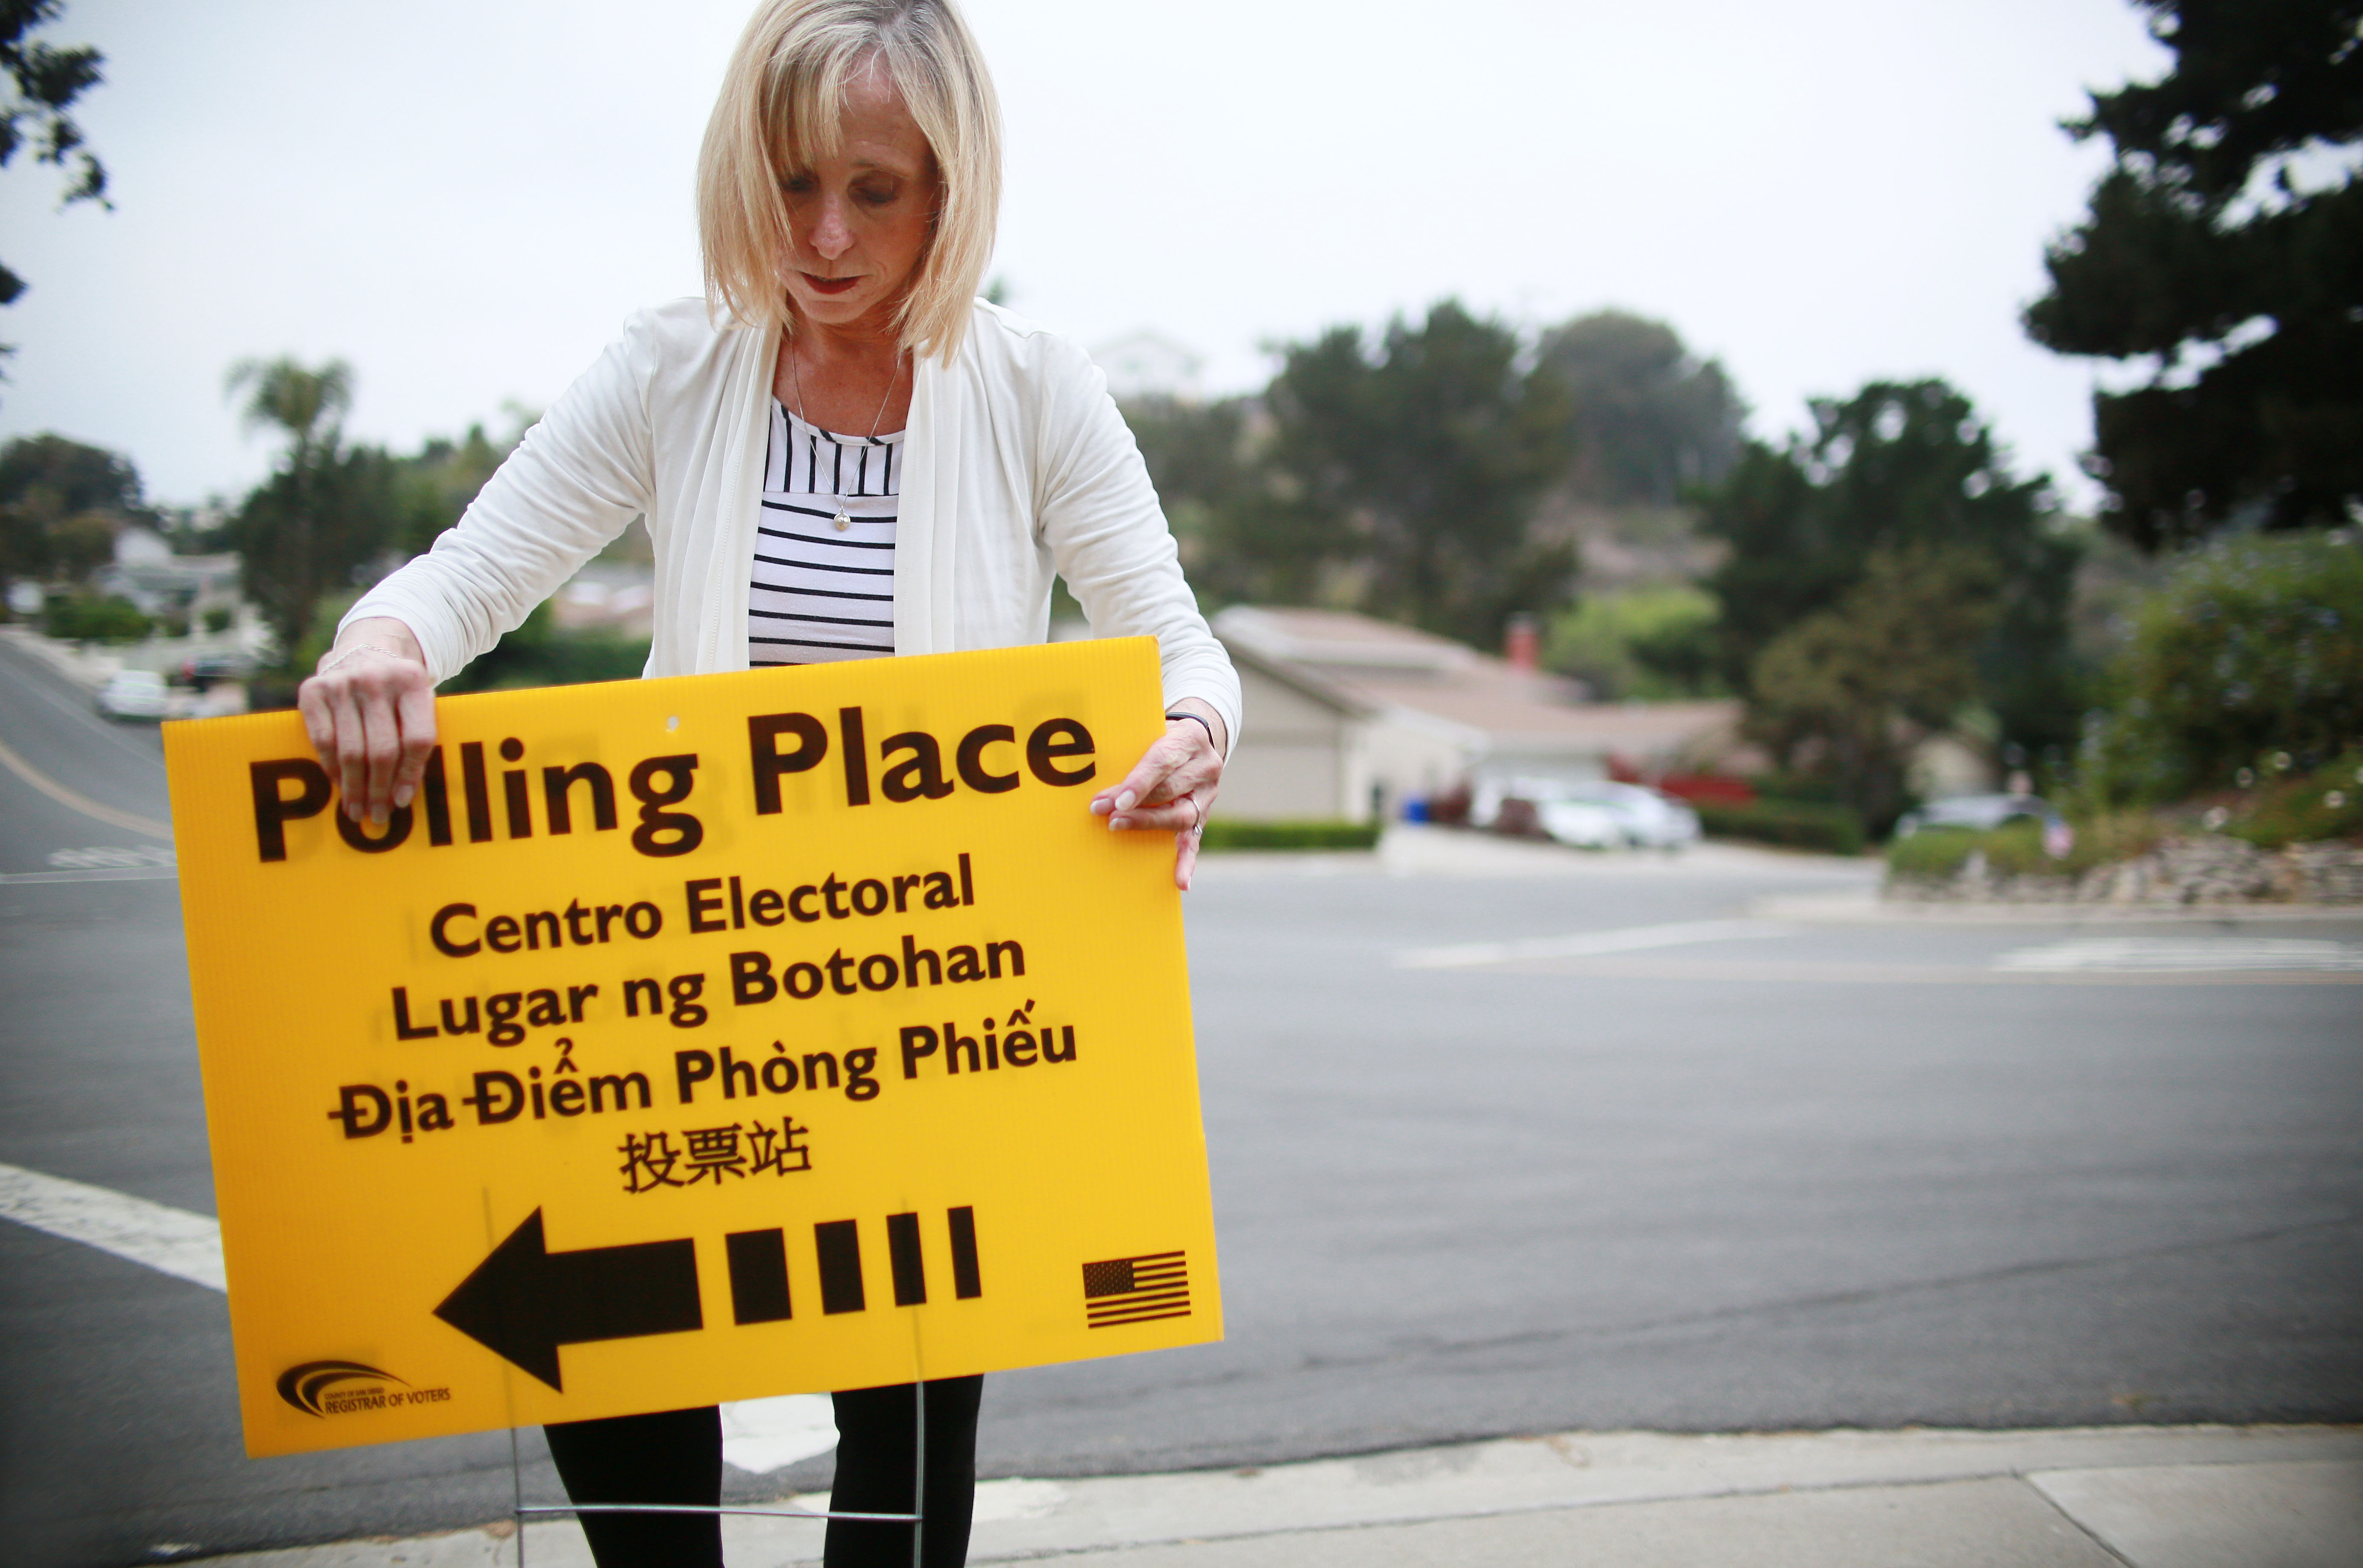
Enlarge / Volunteer Janice MacGurn sets up a polling station sign before opening on primary election day June 5, 2018 in San Diego, California. There are several highly competitive races throughout the state including those for governor and U.S. House and Senate seats. (credit: Sandy Huffaker/Getty Images)

On Tuesday, polls will be open to voters in eight states, including California, which holds gubernatorial primaries among many other national, state, and local elections.

Under California law (Section 2194 of the Election Code), voter data (name, address, phone, age, party affiliation) is supposed to be “confidential and shall not appear on any computer terminal… or other medium routinely available to the public.”

However, there’s a big exception to that law: this data can be made available to political campaigns, including companies that provide digital analysis services to campaigns. In other words, candidates and their contractors can get voter data, but there’s little definition in the law about how those parties are required to be custodians of that data and how that data ought to be secured.

Read 19 remaining paragraphs | Comments

https://arstechnica.com/?p=1321085


A host of new security enhancements is coming to iOS and macOS

(credit: Nathan Mattise)

Apple on Monday previewed a variety of security and privacy features it plans to add to macOS and iOS operating systems, including encrypted Facetime group calls, password-management tools, and camera and microphone protections. The company also released a beta version of the upcoming iOS 12 that, according to Motherboard, all but kills off two iPhone unlocking tools used by police forces around the world.

The feature, known as USB Restricted Mode, requires that users unlock their iPhone with a password when connecting to it a USB device. Motherboard said the beta requires a password each time a phone that hasn’t been unlocked in the past hour tries to connect to a device using a Lightning connection. The password requirement largely neutralizes iPhone unlocking tools provided by companies called Cellebrite and GrayShift, which reportedly use USB connectivity to bypass iOS restrictions on the number of incorrect PIN guesses can be entered into an unlocked iPhone. With those limitations removed, police can make an unlimited number of PIN guesses when attempting to unlock a confiscated iPhone.

Previous iOS betas had USB restrictions that required the entering of a password when it hadn’t been unlocked for seven days. Those USB Restricted Modes were later removed before Apple issued final versions of iOS. The restrictions this time around are much more stringent, because police would have no more than 60 minutes between the time they obtain an iPhone and connect it to an unlocking tool. Readers should remember that Apple has previously removed USB Restricted Mode before releasing final versions and may do so again with iOS 12.

Read 5 remaining paragraphs | Comments

https://arstechnica.com/?p=1320893


Apple Touts Privacy Features of New Operating Systems

Apple on Monday said new operating systems powering its mobile devices and computers would include features designed to thwart the use of secret trackers to monitor people’s online activities.

read more

http://feedproxy.google.com/~r/Securityweek/~3/LafJIdywO1A/apple-touts-privacy-features-new-operating-systems


Privacy barattata, nuovo scandalo Facebook. Fa spiare gli utenti da 60 produttori di smartphone e tablet

Datagate nuovo capitolo. Dopo Cambridge Analytica, Facebook è ancora una volta nella bufera per la gestione della privacy degli utenti. Il New York Times ha scoperto che da 10 anni la società, guidata da Mark Zuckerberg, consente ad almeno 60 produttori di smartphone, tablet, smart Tv e console per videogiochi, di spiare i dati dei suoi 2 miliardi di iscritti in cambio di servizi sui device per “migliorare l’esperienza sul social”. La condivisione avviene senza il consenso esplicito degli utenti ed è prevista da accordi siglati tra gli altri, con Apple, Amazon, BlackBerry, Microsoft e Samsung. Partnership, si legge nell’inchiesta giornalistica, ancora in vigore, sebbene da aprile scorso la società di Menlo Park ne abbia chiuse ventidue.

Lo stato delle relazioni degli utenti di Facebook, la religione, le opinioni politiche e gli eventi imminenti a cui si è data conferma di partecipare. Queste sono solo alcune delle tipologie di dati a cui i 60 produttori di smartphone, tablet e altri dispositivi tecnologici accedono, proprio come avviene, ha dimostrato il Times nel suo test, con app di terze parti. Apple ha dichiarato di aver avuto accesso ai dati privati degli utenti Facebook quando hanno pubblicato foto sul social attraverso i servizi di iPhone e iPad e non aprendo direttamente l’applicazione del social network. La società della mela morsicata ha anche aggiunto che questa pratica è stata cessata da settembre scorso. BlackBerry, in una nota, ha fatto sapere che non ha abusato dei dati e li ha utilizzati solo per fornire ai suoi clienti l’accesso al social, “perché da sempre punta alla protezione, alla monetizzazione dei dati dei clienti”. Mentre Samsung e Amazon non hanno rilasciato nessuna dichiarazione.

La replica di Facebook?

E Facebook? La società ha difeso la condivisione dei dati perché “coerente con le sue politiche sulla privacy e con quanto decretato dalla Federal Trade Commission (FTC)”, e ha aggiunto di “non essere a conoscenza di casi in cui le informazioni erano state utilizzate in modo improprio”. L’abuso dei dati, invece, è avvenuto perché, si legge nell’articolo del Times, alcune società hanno archiviato i dati nei loro server. Ma per capire se Facebook ha ragione o torno ancora una volta, occorre capire cosa stabilisce il decreto della FTC di luglio 2012.

La Federal Trade Commission, che aveva aperto un’indagine sulla condivisione dei dati di Facebook ad app e siti esterni alla piattaforma, ha stabilito che la migrazione dei dati può avvenire solo con il consenso esplicito dei consumatori. E, in questo nuovo scandalo scoperchiato dal Times, Facebook dichiara di non aver violato la privacy degli utenti perché, secondo la società, “le corsie preferenziali con i partner hardware non violano il decreto della FTC perché i fornitori di servizi sono simili a un servizio di cloud computing pagato per archiviare dati di Facebook o come una società incaricata di elaborare le transazioni con carta di credito”. Dunque secondo l’interpretazione di Facebook del decreto, “la società non ha bisogno di chiedere ulteriori consensi per condividere i dati degli utenti e dei loro amici con i fornitori di servizi”.

Ha ribattuto a muso duro a Facebook Jessica Rich, ex funzionaria della FTC, ora in una associazione dei consumatori americana: “Secondo l’interpretazione di Facebook l’eccezione fa la regola. Non è vero che ogni condivisione dei dati con terze parti è necessaria per migliorare l’esperienza sul social network. E questo comportamento cozza con quanto annunciato nel 2014 e dopo lo scandalo Cambridge Analytica di limitare l’accesso alle app di terze parti ai dati degli utenti e degli amici”.

Come ha fatto il New York Times a scoprire lo scandalo?

Uno dei giornalisti autori dell’inchiesta ha scaricato sul suo BlackBerry del 2013 l’app Hub, progettata per consentire agli utenti BlackBerry di visualizzare tutti i messaggi e profili social in’unica app. E appena Michael LaForgia ha collegato il suo account Facebook all’app Hub ha visto la migrazione dei seguenti dati presenti sul social allo smartphone: ID utente, nome, immagine, informazioni personali, posizione, e-mail e numero di cellulare. Il dispositivo ha quindi recuperato i messaggi privati ​​del giornalista e le risposte con gli amici, insieme al nome e all’ID utente di ciascuna persona con cui ha scambiato i messaggi. Dopo essersi collegato a Facebook attraverso l’app Blackberry, il reporter ha visto che lo smartphone è in grado di spiare dati dettagliati dei suoi 556 amici sul social, tra cui lo stato delle relazioni sentimentali, la religione e le opinioni politiche e gli eventi a cui gli utenti sono prossimi partecipare.

In sostanza, il suo smartphone BlackBerry, attraverso Hub, è stato capace di recuperare informazioni identificative per quasi 295.000 utenti di Facebook. Molti di loro erano amici di Facebook ‘alla larga’ del giornalista o amici di amici.

In generale, Facebook consente ai dispositivi BlackBerry di accedere a più di 50 tipi di informazioni sugli utenti Facebook e i loro amici, secondo il test del Times.

Il tutto all’oscuro dei clienti BlackBerry e degli altri dispositivi realizzati dai 60 produttori. Facebook sostiene che non ci sia violazione dei dati personali degli iscritti, ma se questa condivisione non è esplicitata chiaramente nell’informativa allora gli utenti la vedono, ancora una volta, come un’intrusione illegittima della privacy. Non rispettata e difesa, ma barattata.

The post Privacy barattata, nuovo scandalo Facebook. Fa spiare gli utenti da 60 produttori di smartphone e tablet appeared first on Key4biz.

https://www.key4biz.it/privacy-barattata-nuovo-scandalo-facebook-fa-spiare-gli-utenti-da-60-produttori-di-smartphone-e-tablet/223158/


Personal Data Compromised in Ticketfly Hack

Ticketfly hacked

Eventbrite-owned ticket distribution service Ticketfly shut down its website on Thursday after it was defaced by a hacker who calls himself “IsHaKdZ.”

read more

http://feedproxy.google.com/~r/Securityweek/~3/6AWjyaOLrfE/personal-data-compromised-ticketfly-hack


German Spy Agency Can Keep Tabs on Internet Hubs: Court

Germany’s spy agency can monitor major internet hubs if Berlin deems it necessary for strategic security interests, a federal court has ruled.

read more

http://feedproxy.google.com/~r/Securityweek/~3/F16pknfCYTY/german-spy-agency-can-keep-tabs-internet-hubs-court


ProtonMail Launches VPN Application for macOS

Encrypted email service provider ProtonMail on Wednesday announced the availability of a virtual private network (VPN) service for macOS users.

read more

http://feedproxy.google.com/~r/Securityweek/~3/oLdgUkvULz8/protonmail-launches-vpn-application-macos