Canada Bans WeChat and Kaspersky on Government Phones

Canada on Monday banned popular Chinese messaging app WeChat and Russian platform Kaspersky from government smartphones and other mobile devices, citing privacy and security risks.

The suite of applications would be immediately removed from government-issued devices and users will be blocked from downloading them in the future, said a statement.

Treasury Board President Anita Anand, who overseas Canada’s federal public service, said the nation’s chief information officer determined the apps “present an unacceptable level of risk to privacy and security.”

No breaches have been detected but the platforms’ data collection methods on mobile devices, she added, “provide considerable access to the device’s contents.”

“The decision to remove and block the WeChat and the Kaspersky applications was made to ensure that government of Canada networks and data remain secure and protected and are in line with the approach of our international partners,” Anand concluded.

The move comes after Ottawa in February also banned TikTok — a platform owned by ByteDance in China — on government devices.

Oracle last year was tapped to store all TikTok data from US users after President Joe Biden revoked his predecessor Donald Trump’s executive orders seeking to ban TikTok and WeChat from US markets on national security concerns.

Advertisement. Scroll to continue reading.

Relations between Ottawa and Beijing — already strained over tit-for-tat detentions of a Huawei senior executive and two Canadian nationals in December 2018 — hit a new low earlier this year.

Ottawa accused Beijing of meddling in Canadian elections and the attempted intimidation of MPs that led to the expulsion of a Chinese diplomat in May. Last week, the Canadian government warned of a “Spamouflage” disinformation campaign linked to China that used waves of online posts and deepfake videos manipulated to try to disparage and discredit Canadian lawmakers, including Prime Minister Justin Trudeau.

A public inquiry into foreign interference accusations — which China has rejected — kicked off in September.

https://www.securityweek.com/canada-bans-wechat-and-kaspersky-on-government-phones/


Apple Improves iMessage Security With Contact Key Verification

Apple on Friday introduced contact key verification, a new capability meant to improve the security of its iMessage service.

To ensure the privacy of conversations, iMessage offers end-to-end encryption, so that only the sender and receiver can read a message, and relies on sets of encryption keys, where public keys are stored on a key directory service, while private keys rest on the device and never leave it.

Key directory services, like Apple’s identity directory service, represent a single point of failure, where a powerful adversary may be able to compromise the service to intercept or monitor encrypted messages.

To address the shortcoming, iMessage contact key verification, Apple explains, relies on key transparency, a mechanism that uses a verifiable log-backed map data structure to deliver cryptographic proofs of inclusion, ensuring user privacy and allowing audits.

“iMessage contact key verification advances the state of the art of key transparency deployments by having user devices themselves verify consistency proofs and ensure consistency of the KT system across all user devices for an account,” Apple says.

This mechanism, the tech giant notes, is meant to protect against both key directory and transparency service compromises, allowing changes to the log-backed map while making device keys immediately verifiable.

iMessage contact key verification, Apple explains, uses an account-level elliptic curve digital signature algorithm (ECDSA) signing key that is generated on the device, stored in iCloud keychain, and available to the user on their trusted devices only.

Advertisement. Scroll to continue reading.

“Each device uses the synchronized account key to sign its iMessage public keys. The account keys and signatures are included in the IDS service database along with the existing data,” Apple notes.

When the user enables iMessage contact key verification, their devices verify that the key transparency map includes the data presented by the identity directory service, and notifies the user if a validation error occurs.

Users’ devices will periodically query the service for account information, verify the response against the key transparency mechanism, and flag inconsistencies.

“[The user’s] devices will additionally compare the KT data for identifiers, device records, and opt-in state against records stored in an end-to-end encrypted CloudKit container. This database is maintained by [the user’s] devices and is not readable or modifiable by Apple,” the tech giant explains.

Additionally, iMessage contact key verification allows users to perform manual contact verification code comparisons using the Vaudenay SAS protocol. Upon successful verification, the hash of the peer’s account key is saved to an end-to-end encrypted CloudKit container and linked to the peer’s card.

“Because the contact card is linked, all conversations with the peer’s identifiers — phone number and email address — are marked as verified. Group chats with peers that have been independently verified one-to-one are also automatically marked as verified,” Apple explains.

iMessage contact key verification is now available in the developer previews of iOS 17.2, macOS 14.2, and watchOS 10.2.

Related: Stealth Techniques Used in ‘Operation Triangulation’ iOS Attack Dissected

Related: Apple Patches Actively Exploited iOS, macOS Zero-Days

Related: NSO Group Used at Least 3 iOS Zero-Click Exploits in 2022: Citizen Lab

https://www.securityweek.com/apple-improves-imessage-security-with-contact-key-verification/


The UK’s problematic Online Safety Act is now law

The UK’s problematic Online Safety Act is now law
panorios/Getty Images

Jeremy Wright was the first of five UK ministers charged with pushing through the British government’s landmark legislation on regulating the Internet, the Online Safety Bill. The current UK government likes to brand its initiatives as “world-beating,” but for a brief period in 2019 that might have been right. Back then, three prime ministers ago, the bill—or at least the white paper that would form its basis—outlined an approach that recognized that social media platforms were already de facto arbiters of what was acceptable speech on large parts of the Internet, but that this was a responsibility they didn’t necessarily want and weren’t always capable of discharging. Tech companies were pilloried for things that they missed, but also, by free speech advocates, for those they took down. “There was a sort of emerging realization that self-regulation wasn’t going to be viable for very much longer,” Wright says. “And therefore, governments needed to be involved.”

The bill set out to define a way to handle “legal but harmful” content—material that wasn’t explicitly against the law but which, individually or in aggregate, posed a risk, such as health care disinformation, posts encouraging suicide or eating disorders, or political disinformation with the potential to undermine democracy or create panic. The bill had its critics—notably, those who worried it gave Big Tech too much power. But it was widely praised as a thoughtful attempt to deal with a problem that was growing and evolving faster than politics and society were able to adapt. Of his 17 years in parliament, Wright says, “I’m not sure I’ve seen anything by way of potential legislation that’s had as broadly based a political consensus behind it.”

Having passed, eventually, through the UK’s two houses of Parliament, the bill received royal assent this week. It is no longer world-beating—the European Union’s competing Digital Services Act came into force in August. And the Online Safety Act enters into law as a broader, more controversial piece of legislation than the one that Wright championed. The act’s more than 200 clauses cover a wide spectrum of illegal content that platforms will be required to address and give platforms a “duty of care” over what their users—particularly children—see online. Some of the more nuanced principles around the harms caused by legal but harmful content have been watered down, and added in is a highly divisive requirement for messaging platforms to scan users’ messages for illegal material, such as child sexual abuse material, which tech companies and privacy campaigners say is an unwarranted attack on encryption.

Companies, from Big Tech down to smaller platforms and messaging apps, will need to comply with a long list of new requirements, starting with age verification for their users. (Wikipedia, the eighth-most-visited website in the UK, has said it won’t be able to comply with the rule because it violates the Wikimedia Foundation’s principles on collecting data about its users.) Platforms will have to prevent younger users from seeing age-inappropriate content, such as pornography, cyberbullying, and harassment; release risk assessments on potential dangers to children on their services; and give parents easy pathways to report concerns. Sending threats of violence, including rape, online will now be illegal, as will assisting or encouraging self-harm online or transmitting deepfake pornography, and companies will need to quickly act to remove them from their platforms, along with scam adverts.

In a statement, UK Technology Secretary Michelle Donelan said: “The Bill protects free speech, empowers adults and will ensure that platforms remove illegal content. At the heart of this Bill, however, is the protection of children. I would like to thank the campaigners, parliamentarians, survivors of abuse and charities that have worked tirelessly, not only to get this Act over the finishing line, but to ensure that it will make the UK the safest place to be online in the world.”

Enforcement of the act will be left to the UK’s telecommunications regulator, Ofcom, which said in June that it would begin consultations with industry after royal assent was granted. It’s unlikely that enforcement will begin immediately, but the law will apply to any platform with a significant number of users in the UK. Companies that fail to comply with the new rules face fines of up to £18 million ($21.9 million) or 10 percent of their annual revenue, whichever is larger.

Some of the controversy around the act is less about what is in it and more about what isn’t. The long passage of the legislation means that its development straddled the Covid-19 pandemic, giving legislators a live view of the social impact of mis- and disinformation. The spread of anti-vaccination and anti-lockdown messages became an impediment to public health initiatives. After the worst of the pandemic was over, those same falsehoods fed into other conspiracy theories that continue to disrupt society. The original white paper that was the bill’s foundation included proposals for compelling platforms to tackle this kind of content—which individually might not be illegal but which en masse creates dangers. That’s not in the final legislation, although the act does create a new offense of “false communications,” criminalizing deliberately causing harm by communicating something the sender knows to be untrue.

https://arstechnica.com/?p=1979426


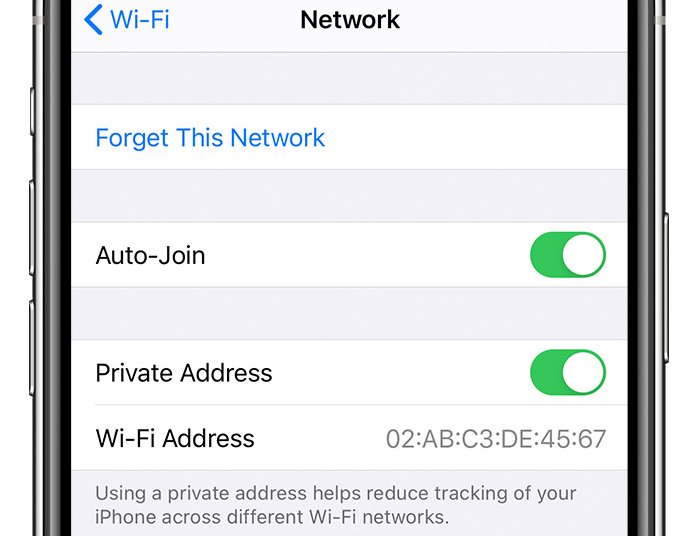
iPhones have been exposing your unique MAC despite Apple’s promises otherwise

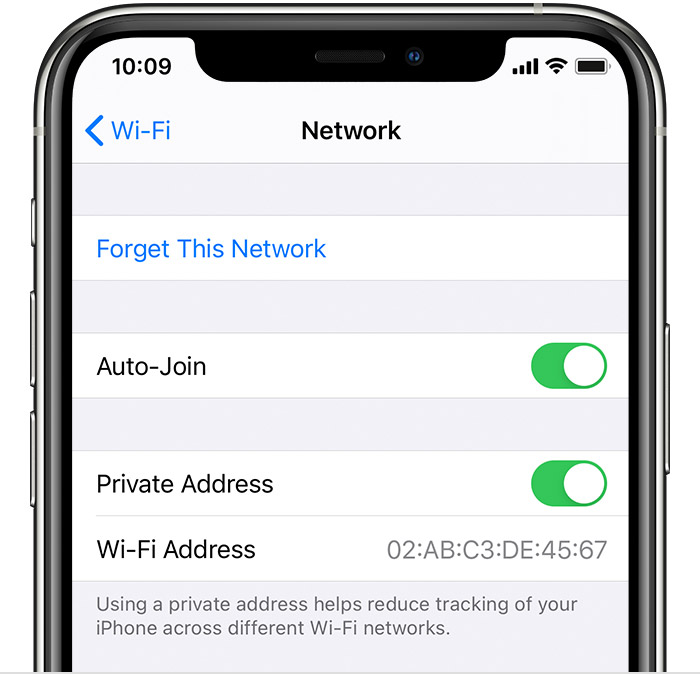
Private Wi-Fi address setting on an iPhone.
Enlarge / Private Wi-Fi address setting on an iPhone.

Three years ago, Apple introduced a privacy-enhancing feature that hid the Wi-Fi address of iPhones and iPads when they joined a network. On Wednesday, the world learned that the feature has never worked as advertised. Despite promises that this never-changing address would be hidden and replaced with a private one that was unique to each SSID, Apple devices have continued to display the real one, which in turn got broadcast to every other connected device on the network.

The problem is that a Wi-Fi media access control address—typically called a media access control address or simply a MAC—can be used to track individuals from network to network, in much the way a license plate number can be used to track a vehicle as it moves around a city. Case in point: In 2013, a researcher unveiled a proof-of-concept device that logged the MAC of all devices it came into contact with. The idea was to distribute lots of them throughout a neighborhood or city and build a profile of iPhone users, including the social media sites they visited and the many locations they visited each day.

In the decade since, HTTPS-encrypted communications have become standard, so the ability of people on the same network to monitor other people’s traffic is generally not feasible. Still, a permanent MAC provides plenty of trackability, even now.

As I wrote at the time:

Enter CreepyDOL, a low-cost, distributed network of Wi-Fi sensors that stalks people as they move about neighborhoods or even entire cities. At 4.5 inches by 3.5 inches by 1.25 inches, each node is small enough to be slipped into a wall socket at the nearby gym, cafe, or break room. And with the ability for each one to share the Internet traffic it collects with every other node, the system can assemble a detailed dossier of personal data, including the schedules, e-mail addresses, personal photos, and current or past whereabouts of the person or people it monitors.

In 2020, Apple released iOS 14 with a feature that, by default, hid Wi-Fi MACs when devices connected to a network. Instead, the device displayed what Apple called a “private Wi-Fi address” that was different for each SSID. Over time, Apple has enhanced the feature, for instance, by allowing users to assign a new private Wi-Fi address for a given SSID.

On Wednesday, Apple released iOS 17.1. Among the various fixes was a patch for a vulnerability, tracked as CVE-2023-42846, which prevented the privacy feature from working. Tommy Mysk, one of the two security researchers Apple credited with discovering and reporting the vulnerability (Talal Haj Bakry was the other), told Ars that he tested all recent iOS releases and found the flaw dates back to version 14, released in September 2020.

“From the get-go, this feature was useless because of this bug,” he said. “We couldn’t stop the devices from sending these discovery requests, even with a VPN. Even in the Lockdown Mode.”

When an iPhone or any other device joins a network, it triggers a multicast message that is sent to all other devices on the network. By necessity, this message must include a MAC. Beginning with iOS 14, this value was, by default, different for each SSID.

To the casual observer, the feature appeared to work as advertised. The “source” listed in the request was the private Wi-Fi address. Digging in a little further, however, it became clear that the real, permanent MAC was still broadcast to all other connected devices, just in a different field of the request.

Mysk published a short video showing a Mac using the Wireshark packet sniffer to monitor traffic on the local network the Mac is connected to. When an iPhone running iOS prior to version 17.1 joins, it shares its real Wi-Fi MAC on port 5353/UDP.

[embedded content]
Upgrade to iOS 17.1 to prevent your iPhone from being tracked across Wi-Fi networks.

In fairness to Apple, the feature wasn’t useless, because it did prevent passive sniffing by devices such as the above-referended CreepyDOL. But the failure to remove the real MAC from the port 5353/UDP still meant that anyone connected to a network could pull the unique identifier with no trouble.

The fallout for most iPhone and iPad users is likely to be minimal, if at all. But for people with strict privacy threat models, the failure of these devices to hide real MACs for three years could be a real problem, particularly given Apple’s express promise that using the feature “helps reduce tracking of your iPhone across different Wi-Fi networks.”

Apple hasn’t explained how a failure as basic as this one escaped notice for so long. The advisory the company issued Wednesday said only that the fix worked by “removing the vulnerable code.”

This post has been updated to add paragraphs 3 and 11 to provide additional context.

https://arstechnica.com/?p=1979099


Signal Pours Cold Water on Zero-Day Exploit Rumors

Privacy-focused messaging firm Signal is pouring cold water on widespread rumors of a zero-day exploit in its popular encrypted chat app.

“We have seen the vague viral reports alleging a Signal 0-day vulnerability. After responsible investigation *we have no evidence that suggests this vulnerability is real* nor has any additional info been shared via our official reporting channels,” Signal said late Sunday night.

Rumors of a Signal zero-day started circulating over the weekend with what appears to be a copy-pasted warning the “generate link preview” feature could be exploited to take full control of devices.

“To close the vulnerability, have everyone go to settings under your profile in signal> chats> deselect “generate link preview”. Also make sure your signal app is up to date,” according to the cryptic note.

The original source for the zero-day warning is unknown but Signal said it checked with its contacts across the US Government, since the copy-paste report claimed USG as a source.  “Those we spoke to have no info suggesting this is a valid claim,” the company said on X, the social media site previously known as Twitter.

The “generate link preview” feature is known to have privacy and security risks and has led to critical-severity vulnerability problems on Meta’s WhatsApp platform. 

The feature, on by default on some Signal installations, displays a short summary and preview image of a URL being sent but experts have long warned that it provides attack surface to leak IP addresses, expose links sent in end-to-end encrypted chats, and unnecessarily downloading gigabytes of data quietly in the background.

Advertisement. Scroll to continue reading.

Interestingly, Apple’s optional LockDown Mode disables the iMessage link preview feature in response to malicious targeting by surveillance spyware vendors.

Related: Link Previews in Chat Apps Pose Privacy, Security Issues

Related: Signal Discloses Impact From Twilio Hack

Related: Vulnerability in WhatsApp Desktop Exposed User Files

Related: Can ‘Lockdown Mode’ Solve Apple’s Mercenary Spyware Problem?

https://www.securityweek.com/signal-pours-cold-water-on-zero-day-exploit-rumors/


23andMe says private user data is up for sale after being scraped

The 23andMe logo displayed on a smartphone screen.
Enlarge / The 23andMe logo displayed on a smartphone screen.

Genetic profiling service 23andMe has commenced an investigation after private user data was been scraped off its website

Friday’s confirmation comes five days after an unknown entity took to an online crime forum to advertise the sale of private information for millions of 23andMe users. The forum posts claimed that the stolen data included origin estimation, phenotype, health information, photos, and identification data. The posts claimed that 23andMe’s CEO was aware the company had been “hacked” two months earlier and never revealed the incident. In a statement emailed after this post went live, a 23andMe representative said “nothing they have posted publicly indicates they actually have any ‘health information.’ These are all unsubstantiated claims at this point.”

23andMe officials on Friday confirmed that private data for some of its users is, in fact, up for sale. The cause of the leak, the officials said, is data scraping, a technique that essentially reassembles large amounts of data by systematically extracting smaller amounts of information available to individual users of a service. Attackers gained unauthorized access to the individual 23andMe accounts, all of which had been configured by the user to opt in to a DNA relative feature that allows them to find potential relatives.

In a statement, the officials wrote:

We do not have any indication at this time that there has been a data security incident within our systems. Rather, the preliminary results of this investigation suggest that the login credentials used in these access attempts may have been gathered by a threat actor from data leaked during incidents involving other online platforms where users have recycled login credentials.

We believe that the threat actor may have then, in violation of our terms of service, accessed 23andme.com accounts without authorization and obtained information from those accounts. We are taking this issue seriously and will continue our investigation to confirm these preliminary results.

The DNA relative feature allows users who opt in to view basic profile information of others who also allow their profiles to be visible to DNA Relative participants, a spokesperson said. If the DNA of one opting-in user matches another, each gets to access the other’s ancestry information.

The crime forum post claimed the attackers obtained “13M pieces of data.” 23andMe officials have provided no details about the leaked information available online, the number of users it belongs to, or where it’s being made available. On Friday, The Record and Bleeping Computer reported that one leaked database contained information for 1 million users of Ashkenazi heritage, all of whom had opted in to the DNA relative service. The Record said a second database included 300,000 users of Chinese heritage who also had opted in.

The data included profile and account ID numbers, display names, gender, birth year, maternal and paternal haplogroups, ancestral heritage results, and data on whether or not each user has opted into 23andme’s health data. Some of this data is included only when users choose to share it.

The Record also reported that 23andMe website allows people who know the profile ID of a user to view that user’s profile photo, name, birth year, and location. The 23andMe representative said that “anyone who a 23andMe account who has opted into DNA Relatives can view basic profile information of any other account who has also explicitly optend into making their profile visible to other DNA Relative participants.”

By now, it has become clear that storing genetic information online carries risks. In 2018, MyHeritage revealed that email addresses and hashed passwords for more than 92 million users had been stolen through a breach of its network that occurred seven months earlier.
That same year, law enforcement officials in California said they used a different genealogy site to track down a long-sought suspect in a string of grisly murders that occurred 40 years earlier. Investigators matched DNA left at a crime scene with the suspect’s DNA. The suspect had never submitted a sample to the service, which is known as GEDMatch. Instead, the match was made with a GEDMatch user related to the suspect.

While there are benefits to storing genetic information online so people can trace their heritage and track down relatives, there are clear privacy threats. Even if a user chooses a strong password and uses two-factor authentication as 23andMe has long urged, their data can still be swept up in scraping incidents like the one recently confirmed. The only sure way to protect it from online theft is to not store it there in the first place.

This post has been updated to include details 23andMe provided.

https://arstechnica.com/?p=1974265


In Other News: RSA Encryption Attack, Meta AI Privacy, ShinyHunters Hacker Guilty Plea

SecurityWeek is publishing a weekly cybersecurity roundup that provides a concise compilation of noteworthy stories that might have slipped under the radar.

We provide a valuable summary of stories that may not warrant an entire article, but are nonetheless important for a comprehensive understanding of the cybersecurity landscape.

Each week, we will curate and present a collection of noteworthy developments, ranging from the latest vulnerability discoveries and emerging attack techniques to significant policy changes and industry reports.

Here are this week’s stories:  

Cybercriminals targeting hotels, booking sites and travel agents

Cybercriminals are deploying infostealer malware on the systems of hotels, booking sites and travel agents, and then use the access they have obtained to reach out to their customers through legitimate communication channels. The goal is to trick the targeted company’s customers to hand over payment card information, Akamai reported. 

Diplomatic phishing operations of Russia’s APT29 

Advertisement. Scroll to continue reading.

Mandiant has published a technical report describing the diplomatic phishing operations of Russia’s APT29 cyberespionage group since the start of the war in Ukraine. The cybersecurity firm has seen significant changes in the threat actor’s tooling and tradecraft. 

Spanish aerospace company targeted by North Korean hackers

A Spanish aerospace company has been targeted by the North Korean hacker group Lazarus with a previously unknown backdoor named LightlessCan. The attackers gained initial access to the company’s systems after posing as a recruiter for Meta, ESET reported.

ShadowSyndicate working with various ransomware groups

Group-IB has analyzed the activities of a threat actor named ShadowSyndicate, which has worked with various ransomware groups and affiliates since July 2022. There is evidence that the group was involved in Quantum, Nokoyawa, ALPHV, Royal, Cl0p, Cactus, and Play ransomware operations.

APT and financial attacks on industrial organizations 

Kaspersky has published a report summarizing the state-sponsored and financially motivated attacks launched against industrial organizations in the first half of 2023. 

Fort Lauderdale loses $1.2 million in BEC attack

The city of Fort Lauderdale in Florida has lost $1.2 million in a BEC attack that involved the attackers posing as a construction company the city has been working with, CNN reported. The cybercriminals provided documents that made their request for the money seem legitimate. 

French hacker pleads guilty in the US

Sebastien Raoult, aka Sezyo Kaizen, a French citizen and member of the notorious ShinyHunters cybercrime group, has pleaded guilty in a US court to fraud and identity theft charges. He was arrested last year in Morocco and extradited to the US in January. Authorities say Raoult and his accomplices stole hundreds of millions of user records and caused losses of over $6 million.

US sanctions Russian and Chinese firms over national security risks

The US has sanctioned companies in China, Russia and other countries, citing national security risks. 

Marvin attack on RSA encryption

A researcher has disclosed the details of Marvin, a new attack method against RSA encryption that demonstrates Bleichenbacher-style attacks work against many software implementations of the PKCS#1 v1.5 padding scheme for RSA key exchange that were until now believed to be safe. 

Meta describes privacy safeguards in new generative AI features

Meta has described the privacy safeguards implemented in its new generative AI features in an effort to protect users’ information. The new features include a conversational assistant, AI stickers, as well as 28 more AIs with unique personalities and interests. 

Related: In Other News: New Analysis of Snowden Files, Yubico Goes Public, Election Hacking

Related: In Other News: China Blames NSA for Hack, AI Jailbreaks, Netography Spin-Off

https://www.securityweek.com/in-other-news-rsa-encryption-attack-meta-ai-privacy-shinyhunters-hacker-guilty-plea/


Researchers Extract Sounds From Still Images on Smartphone Cameras

A group of academic researchers has devised a technique to extract sounds from still images captured using smartphone cameras with rolling shutter and movable lens structures.

The movement of camera hardware, such as the Complementary Metal-oxide–Semiconductor (CMOS) rolling shutters and the moving lenses used for Optical Image Stabilization (OIS) and Auto Focus (AF), create sounds that are modulated into images as imperceptible distortions.

These types of smartphone cameras, the researchers explain in a research paper (PDF), create a “point-of-view (POV) optical-acoustic side channel for acoustic eavesdropping” that requires no line of sight, nor the presence of an object within the camera’s field of view.

Focusing on the limitations of this side channel – which relies on a “suitable mechanical path from the sound source to the smartphone” to support sound propagation, the researchers extract and analyze the leaked acoustic information identifying with high accuracy different speakers, genders, and spoken digits.

The academics relied on machine learning to recover information from human speech broadcast by speakers, in the context of an attacker that has a malicious application running on the smartphone but does not have access to the device’s microphone.

However, the threat model assumes that the attacker can captures a video with the victim’s camera and that they can acquire speech samples of the target individuals beforehand, to use them as part of the learning process.

Using a dataset of 10,000 samples of signal-digit utterances, the researchers performed three classification tasks (gender, identity, and digit recognition) and trained their model for each task. They used Google Pixel, Samsung Galaxy, and Apple iPhone devices for the experiments.

Advertisement. Scroll to continue reading.

“Our evaluation with 10 smartphones on a spoken digit dataset reports 80.66%, 91.28%, and 99.67% accuracies on recognizing 10 spoken digits, 20 speakers, and 2 genders respectively,” the academics say.

Lower quality cameras, the researchers say, would limit the potential information leakage associated with this type of attack. Keeping smartphones away from speakers and adding vibration-isolation dampening materials between the phone and the transmitting surface should also help.

Smartphone makers can mitigate the attack through higher rolling shutter frequencies, random-code rolling shutters, tougher lens suspension springs, and lens locking mechanisms.

“We believe the high classification accuracies obtained in our evaluation and the related work using motion sensors suggest this optical-acoustic side channel can support more diverse malicious applications by incorporating speech reconstruction functionality in the signal processing pipeline,” the researchers added.

Related: Researchers Demo Electromagnetic Fault Injection Attacks on Drones

Related: Open Source Tool For Hunting Node.js Security Flaws

Related: New Speculative Execution Attack Against Apple M1 Chips

https://www.securityweek.com/researchers-extract-sounds-from-still-images-on-smartphone-cameras/


A Key US Government Surveillance Tool Should Face New Limits, a Divided Privacy Oversight Board Says

Federal spy agencies should be required to get court approval before reviewing the communications of U.S. citizens collected through a secretive foreign surveillance program, a sharply divided privacy oversight board recommended on Thursday.

The recommendation came in a report from a three-member Democratic majority of the Privacy and Civil Liberties Oversight Board, an independent agency within the executive branch, and was made despite the opposition of Biden administration officials who warn that such a requirement could snarl fast-moving terrorism and espionage investigations and weaken national security as a result.

The report comes as a White House push to secure the reauthorization of the program known as Section 702 of the Foreign Intelligence Surveillance Act is encountering major bipartisan opposition in Congress and during a spate of revelations that FBI employees have periodically mishandled access to a repository of intelligence gathered under the law, violations that have spurred outrage from civil liberties advocates.

Section 702 permits allow spy agencies without a warrant to collect swaths of emails and other communications from foreigners located abroad, even when those foreigners are in touch with people in the United States.

Officials in President Joe Biden’s administration have said the program is essential for disrupting foreign terror attacks, espionage operations from Russia and China and cyberattacks against critical infrastructure. But many Democratic and Republican lawmakers say they won’t vote to renew Section 702 when it expires at the end of the year without major changes targeting how the FBI uses foreign surveillance data to investigate Americans.

The privacy board recommended that the program be renewed despite being divided about what reforms were needed.

The opposition to reauthorization has united unusual bedfellows, bringing together civil liberties-minded Democrats who have long supported limits on government surveillance powers with Republicans still angry over what they see as abuses during the investigation into ties between Russia and Donald Trump’s 2016 presidential campaign.

Advertisement. Scroll to continue reading.

A central point of contention is analysts’ use of the foreign intelligence database to search for information about people, businesses or phone numbers located in the U.S. Those queries are permissible if there’s reason to believe they will retrieve foreign intelligence information. The FBI can also search the database if it believes it will turn up evidence of a crime, though a court order is required to review the results of those queries.

A succession of unsealed court opinions in recent months have revealed FBI violations in how those queries have been done, including improper searches of Section 702 databases for information related to the Jan. 6, 2021, riot at the U.S. Capitol and the 2020 protests following the police killing of George Floyd. FBI officials say significant safeguards have since been imposed.

In a recommendation Thursday that critics say would impose a significant hurdle and mark a dramatic break from the status quo, three members of the board said executive branch agencies, with limited exceptions, should have to get permission from the secretive Foreign Intelligence Surveillance Court to read the results of their database queries on U.S. citizens.

“The scale of U.S. person queries, the number of compliance issues surrounding U.S. person queries, and the failure of current law and procedures to protect U.S. persons compels the Board to recommend a new approach,” the report said.

Underscoring the blurred political lines of the debate, the two Republican members of the board joined the White House in objecting to the proposal as unduly burdensome. Those two members refused to sign on to the report issued by their colleagues and instead issued their own document lambasting some of the conclusions.

“Eliminating U.S. person queries, or making it bureaucratically infeasible to conduct them — as the Majority recommends — would effectively destroy the crucial portion of the program that enables the U.S. government to prevent, among other things, terrorist attacks on our soil,” they wrote.

Separately, the White House said that seeking a judge’s permission to read through intelligence that’s already been lawfully collected was legally unnecessary and would interminably slow national security investigations that require fast action.

“That is operationally unworkable and would blind us to information already in our holdings that, often, must be acted upon in time-sensitive ways in order to prevent lethal plotting on U.S. soil, the recruitment of spies by hostile actors, the hacking of U.S. companies, and more,” a National Security Council spokesperson said in a statement.

“We urge Congress to continue to work with us on alternative reforms that can strengthen Section 702 this reauthorization cycle without causing the type of detrimental effects to U.S. national security that this recommendation would generate,” the statement added.

Speaking Thursday at a luncheon at the National Press Club, Gen. Paul Nakasone, the director of the National Security Agency, said the U.S. must balance national security needs with civil liberties and privacy.

“It can’t be out of balance,” he said. “That’s my concern and just being able to balance that equation. And that’s something we always work towards.”

Jamil Jaffer, founder and executive director of the National Security Institute at George Mason University’s law school and a senior Justice Department official at the time the law was created, was more pointed. He said in a statement that the position of the board’s majority would create a “wall” between law enforcement and intelligence and “represent a drastic break from the consistent view of all four presidents to have served” since the Sept. 11, 2001 attacks.

The Privacy and Civil Liberties Oversight Board was formed in 2007 following a recommendation from the Sept. 11 commission, intended as a way to create checks and balances on the government’s expanding spy powers. The five members are nominated by the president and receive Senate approval.

https://www.securityweek.com/a-key-us-government-surveillance-tool-should-face-new-limits-a-divided-privacy-oversight-board-says/

UK’s New Online Safety Law Adds to Crackdown on Big Tech Companies

British lawmakers have approved an ambitious but controversial new internet safety law with wide-ranging powers to crack down on digital and social media companies like TikTok, Google, and Facebook and Instagram parent Meta.

The government says the online safety bill passed this week will make Britain the safest place in the world to be online. But digital rights groups say it threatens online privacy and freedom of speech.

The new law is the U.K.’s contribution to efforts in Europe and elsewhere to clamp down on the freewheeling tech industry dominated by U.S. companies. The European Union has its Digital Services Act, which took effect last month with similar provisions aimed at cleaning up social media for users in the 27-nation bloc.

Here’s a closer look at Britain’s law:

What is the Online Safety Law?

The sprawling piece of legislation has been in the works since 2021.

The new law requires social media platforms to take down illegal content, including child sexual abuse, hate speech and terrorism, revenge porn and posts promoting self-harm. They also will have to stop such content from appearing in the first place and give users more controls, including blocking anonymous trolls.

Advertisement. Scroll to continue reading.

The government says the law takes a “zero tolerance” approach to protecting kids by making platforms legally responsible for their online safety. Platforms will be required to stop children from accessing content that, while not illegal, could be harmful or not age-appropriate, including porn, bullying or, for example, glorifying eating disorders or providing instructions for suicide.

Social media platforms will be legally required to verify that users are old enough, typically 13, and porn websites will have to make sure users are 18.

The bill criminalizes some online activity, such as cyberflashing, which is sending someone unwanted explicit images.

What if Big Tech Doesn’t Comply?

The law applies to any internet company, no matter where it’s based as long as a U.K. user can access its services. Companies that don’t fall in line face fines of up to 18 million pounds ($22 million) or 10% of annual global sales, whichever is greater.

Senior managers at tech companies also face criminal prosecution and prison time if they fail to answer information requests from U.K. regulators. They’ll also be held criminally liable if their company fails to comply with regulators’ notices about child sex abuse and exploitation.

Ofcom, the U.K. communications regulator, will enforce the law. It will focus first on illegal content as the government takes a “phased approach” to bring it into force.

Beyond that, it’s unclear how the law will be enforced because details haven’t been provided.

What do Critics Say?

The U.K.-based Open Rights Group and the Electronic Frontier Foundation in the U.S. said that if tech companies have to ensure content is not harmful for children, they could end up being forced to choose between sanitizing their platforms or making users verify their ages by uploading official ID or using privacy-intrusive face scans to estimate how old they are.

The law also sets up a clash between the British government and tech companies over encryption technology. It gives regulators the power to require encrypted messaging services to install “accredited technology” to scan encrypted messages for terrorist or child sex abuse content.

Experts say that would provide a backdoor for private communications that ends up making everyone less safe.

Meta said last month that it plans to start adding end-to-end encryption to all Messenger chats by default by the end of year. But the U.K. government called on the company not to do so without measures to protect children from sex abuse and exploitation.

https://www.securityweek.com/uks-new-online-safety-law-adds-to-crackdown-on-big-tech-companies/