La privacy nel metaverso è davvero impossibile?
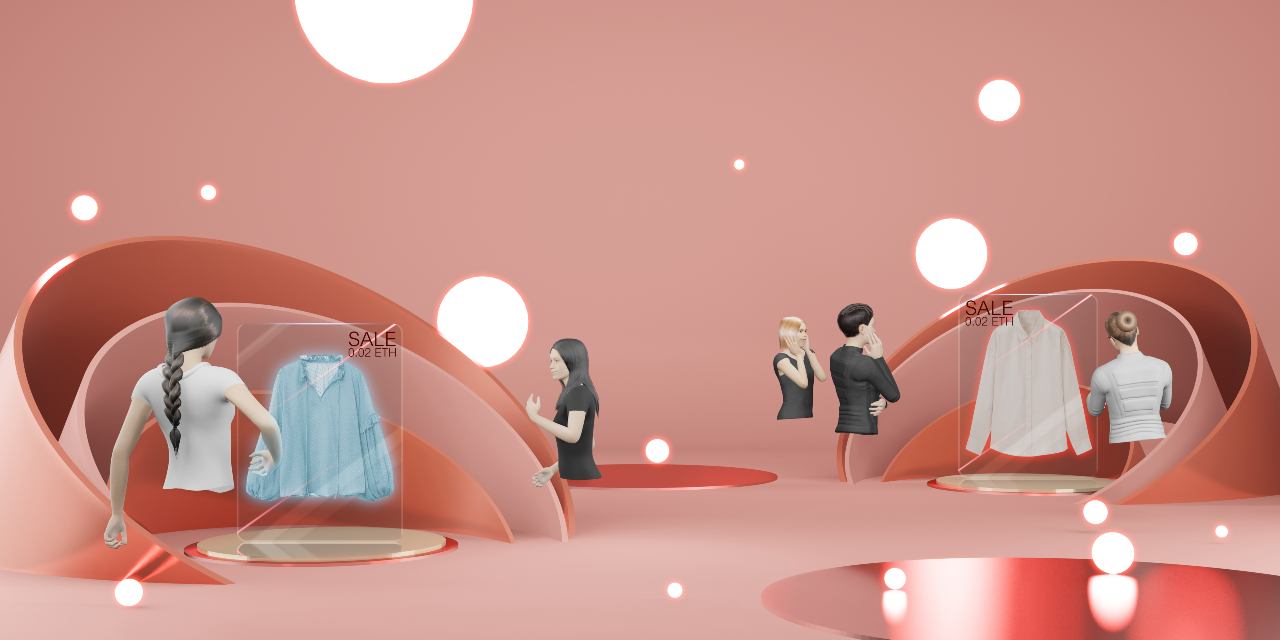
Un nuovo documento appena pubblicato dall’università di Berkeley sancisce nero su bianco che la privacy nel metaverso rischia di essere impossibile senza nuove salvaguardie per proteggere gli utenti.   

Guidato dal ricercatore laureato Vivek Nair, lo studio recentemente pubblicato è stato condotto presso il Center for Responsible Decentralized Intelligence (RDI) e ha coinvolto il più grande set di dati di interazioni degli utenti nella realtà virtuale (VR) che sia mai stato analizzato per i rischi per la privacy.

Il risultato più sorprendente dello studio è quanto pochi dati siano necessari per identificare  in modo univoco un utente nel metaverso, potenzialmente eliminando ogni possibilità di una vera anonimità nei diversi mondi virtuali del metaverso. 

Dati di movimento

Come sfondo, la maggior parte dei ricercatori e dei responsabili politici che studiano la privacy del metaverso si concentrano sulle numerose telecamere e microfoni nei moderni visori VR che catturano informazioni dettagliate sulle caratteristiche facciali, le qualità vocali e i movimenti degli occhi dell’utente, insieme a informazioni ambientali sulla casa o sull’ufficio dell’utente.

Alcuni ricercatori si preoccupano persino delle tecnologie emergenti come i sensori EEG per il monitoraggio cerebrale, in grado di rilevare un’attività cerebrale unica attraverso il cuoio capelluto. Mentre questi ricchi flussi di dati pongono seri rischi per la privacy nel metaverso, disattivarli tutti potrebbe non garantire l’anonimato.

Questo perché il flusso di dati più basilare necessario per interagire con un mondo virtuale – semplici dati di movimento – potrebbe essere tutto ciò che è necessario per identificare in modo univoco un utente all’interno di una vasta popolazione.

E per “semplici dati di movimento” intendo i tre punti dati più basilari tracciati dai sistemi di realtà virtuale: un punto sulla testa dell’utente e uno su ciascuna mano. I ricercatori spesso si riferiscono a questo come “dati di telemetria” e rappresenta il set di dati minimo richiesto per consentire a un utente di interagire naturalmente in un ambiente virtuale.

Identificazione univoca in pochi secondi

E qu entra in gioco il nuovo studio di Berkeley, “Identificazione unica di oltre 50.000 utenti di realtà virtuale da dati di movimento della testa e della mano”. La ricerca ha analizzato oltre 2,5 milioni di registrazioni di dati VR (completamente anonimizzate) di oltre 50mila giocatori della popolare app Beat Saber e ha scoperto che i singoli utenti potevano essere identificati in modo univoco con una precisione superiore al 94% utilizzando solo 100 secondi di dati di movimento.

Ancora più sorprendente è stato il fatto che la metà di tutti gli utenti potesse essere identificata in modo univoco con solo 2 secondi di dati di movimento. Raggiungere questo livello di accuratezza richiedeva tecniche di intelligenza artificiale innovative, ma ancora una volta i dati utilizzati erano estremamente scarsi: solo tre punti spaziali per ogni utente monitorati nel tempo.

In altre parole, ogni volta che gli utenti indossano un hedset per realtà mista, prendono in mano i due controller standard e cominciano ad interagire in un mondo virtuale o aumentato, stanno lasciando dietro di sé tracce digitali che possono identificarli in maniera univoca.

Naturalmente, questo pone la domanda: come si confrontano queste impronte digitali con le impronte digitali del mondo reale nella loro capacità di identificare in modo univoco gli utenti?

Eliminare l’anonimato

D’altra parte, lo studio di Berkeley suggerisce che quando un utente di realtà virtuale fa oscillare una sciabola virtuale contro un oggetto che vola verso di lui, i dati di movimento che si lasciano alle spalle possono essere identificabili in modo più univoco rispetto alla loro effettiva impronta digitale nel mondo reale.

Ciò rappresenta un rischio per la privacy molto serio, in quanto elimina potenzialmente l’anonimato nel metaverso. Inoltre, questi stessi dati di movimento possono essere utilizzati per dedurre con precisione una serie di caratteristiche personali specifiche sugli utenti, tra cui altezza, manualità e sesso.

E se combinato con altri dati comunemente tracciati in ambienti virtuali e potenziati, è probabile che questo metodo di fingerprinting basato sul movimento produca identificazioni ancora più accurate.

In altre parole, ci saranno nel metaverso delle impronte digitali basate sul movimento degli utenti, che potranno così essere identificati negli ambiti più disparati. Un dei quali ad esempio sarà certamente la spesa al negozio virtuale, con l’utente che prende i prodotto dallo scaffale e lo fa muovendosi nel modo suo, unico e riconoscibile. Cosa succederà? Sarà necessario oscurare i movimenti dal metaverso?

https://www.key4biz.it/la-privacy-nel-metaverso-e-davvero-impossibile/436616/


TikTok Banned From EU Commission Phones Over Cybersecurity

The European Union’s executive branch said Thursday that it has temporarily banned TikTok from phones used by employees as a cybersecurity measure, reflecting widening worries from Western officials over the Chinese-owned video sharing app.

In a first for the European Commission, its Corporate Management Board suspended the use of TikTok on devices issued to staff or personal devices that staff use for work.

TikTok faces intensifying scrutiny from Europe and the U.S. over security and data privacy amid worries that the hugely popular app could be used to promote pro-Beijing views or sweep up users’ information. It comes as China and the West are locked in a wider tug of war over technology ranging from spy balloons to computer chips.

The EU’s action follows similar moves in the U.S., where more than half of the states and Congress have banned TikTok from official government devices.

TikTok faces intensifying scrutiny from Europe and the U.S. over security and data privacy

“The reason why this decision has been taken is to … increase the commission’s cybersecurity,” commission spokesperson Sonya Gospodinova said at a press briefing in Brussels. “Also, the measure aims to protect the commission against cybersecurity threats and actions which may be exploited for cyberattacks against the corporate environment of the commission.”

TikTok didn’t respond immediately to a request for comment.

Commission spokespeople declined to say whether something specific triggered the suspension or what’s needed to get it lifted.

Staffers would be required to delete TikTok from private devices that they use for professional business by March 15, EU representatives said, but did not provide any details on how that would be enforced.

In Norway, which is not a member of the 27-nation EU, the justice minister was forced to apologize this month for failing to disclose that she had installed TikTok on her government-issued phone.

TikTok also has come under pressure from the EU to comply with upcoming new digital regulations aimed at getting big online platforms to clean up toxic and illegal content along with the bloc’s strict data privacy rules.

The company has said it plans to open two more European data centers to allay data privacy fears.

https://www.securityweek.com/tiktok-banned-from-eu-commission-phones-over-cybersecurity/


Facebook rischia il blocco dell’invio dei dati di utenti europei negli Usa entro due mesi

Facebook e Instagram potrebbero dover interrompere l’invio dei dati degli utenti europei agli Stati Uniti nei prossimi due mesi per motivi di privacy.

Il gruppo europeo di regolatori della privacy, il Comitato europeo per la protezione dei dati (EDPB), emetterà una decisione vincolante su un caso che esaminerà i trasferimenti di dati di Meta negli Stati Uniti entro il 14 aprile, ha detto un portavoce a Politico.eu martedì.

Meta in precedenza ha affermato che potrebbe dover chiudere i suoi servizi in Europa se le autorità di regolamentazione ritenessero illegale la sua base legale per i trasferimenti di dati.

Un nuovo accordo sui dati transatlantici è in fase di finalizzazione e dovrebbe arrivare prima dell’estate. Ma potrebbe essere troppo tardi, in quanto lascerebbe Meta senza una base legale adeguata per trasferire i dati di cittadini europei in suo possesso tra la decisione dei regolatori e l’entrata in vigore del nuovo accordo.

Il caso nasce da un reclamo sulla privacy presentato dall’attivista austriaco Max Schrems nel 2013. La Commissione irlandese per la protezione dei dati nel luglio 2022 ha inizialmente proposto di vietare a Meta di utilizzare uno strumento legale noto come “clausole contrattuali standard” per inviare i dati degli utenti negli Stati Uniti. Tale decisione è arrivato dopo che la corte suprema dell’UE aveva annullato l’accordo UE-USA Privacy Shield, stabilendo che non proteggeva sufficientemente i dati dei cittadini dell’UE dall’accesso da parte delle autorità statunitensi.

Il regolatore irlandese dei dati alla fine di gennaio ha attivato un meccanismo di risoluzione delle controversie, noto come articolo 65, dopo che non è riuscito a risolvere le obiezioni sollevate da altre autorità europee per la protezione dei dati sulla sua decisione. Il portavoce dell’EDPB ha detto che la procedura ufficiale per il segretariato per preparare una decisione vincolante è iniziata formalmente oggi e dovrà affrontare una scadenza di due mesi.

https://www.key4biz.it/facebook-rischia-il-blocco-dellinvio-dei-dati-di-utenti-europei-negli-usa-entro-due-mesi/435454/


Tor Network Under DDoS Pressure for 7 Months

For the past seven months, the Tor anonymity network has been hit with numerous distributed denial-of-service (DDoS) attacks, its maintainers announced this week.

Some of the attacks have been severe enough to prevent users from loading pages or accessing onion services, the Tor Project says.

Publicly released in 2003, Tor directs traffic through a global network of more than 7,000 relays, to help users maintain anonymity and protect their privacy while navigating the web. Despite its legitimate purpose, Tor has also been used for illegal activities.

Attacks against Tor are not new, with many of them seeking to deanonymize users. In DDoS attacks, the target is flooded with rogue network traffic originating from multiple different sources in an effort to disrupt the target service by depleting resources.

According to the Tor Project, despite its efforts to mitigate the impact of the experienced DDoS attacks, continuous shifts in methods are making the task difficult.

“The methods and targets of these attacks have changed over time and we are adapting as these attacks continue. It’s not possible to determine with certainty who is conducting these attacks or their intentions,” Tor says.

To improve defenses, the Tor Project is adding two new members to its network team, to focus on the development of the onion services.

At the same time, the organization is making an appeal to the community to help it fund onion service development through donations. Offering services for free, the Tor Project is funded from donations, with support coming from the Electronic Frontier Foundation (EFF), various US governmental agencies, individuals, and other third-parties.

Related: US Charges Six in Operation Targeting 48 DDoS-for-Hire Websites

Related:US Agencies Issue Guidance on Responding to DDoS Attacks

Related:Pro-Russian Group DDoS-ing Governments, Critical Infrastructure in Ukraine, NATO Countries

https://www.securityweek.com/tor-network-under-ddos-pressure-for-7-months/


US Downs Chinese Balloon Off Carolina Coast

President Joe Biden said on Saturday that he ordered U.S. officials to shoot down the suspected Chinese spy balloon earlier this week and that national security leaders decided the best time for the operation was when the it got over water.

“They successfully took it down and I want to complement our aviators who did it,” Biden said after getting off Air Force One en route to Camp David.

Fighter jets shot down the giant white balloon off the Carolina coast after it traversed sensitive military sites across North America and became the latest flashpoint in tensions between Washington and Beijing.

Defense Secretary Lloyd Austin said in a statement that Biden approved the shootdown on Wednesday, saying it should be done “as soon as the mission could be accomplished without undue risk to American lives under the balloon’s path.”

Austin said that due to the size and altitude of the balloon , which was moving at about 60,000 feet in the air, the military had determined that taking it down over land would pose an undue risk to people on the ground.

The balloon was spotted Saturday morning over the Carolinas as it approached the coast. In preparation for the operation, the FAA Administration temporarily closed airspace over the Carolina coastline, including the airports in Charleston and Myrtle Beach, South Carolina, and Wilmington, North Carolina. The FAA rerouted air traffic from the area and warned of delays as a result of the flight restrictions.

An operation was underway in U.S. territorial waters in the Atlantic Ocean to recover debris from the balloon, which had been flying at about 60,000 feet and was estimated to be about the size of three school buses. The balloon was downed by Air Force fighter aircraft, according to two officials who were not authorized to publicly discuss the matter and spoke on condition of anonymity.

President Joe Biden had told reporters earlier Saturday that “we’re going to take care of it,” when asked about the balloon. The Federal Aviation Administration and Coast Guard worked to clear the airspace and water below the balloon as it reached the ocean.

Television footage showed a small explosion, followed by the balloon descending toward the water. U.S. military jets were seen flying in the vicinity and ships were deployed in the water to mount the recovery operation.

Officials were aiming to time the operation so they could recover as much of the debris as possible before it sinks into the ocean. The Pentagon had previously estimated that any debris field would be substantial.

The balloon was spotted Saturday morning over the Carolinas as it approached the coast. In preparation for the operation, the FAA Administration temporarily closed airspace over the Carolina coastline, including the airports in Charleston and Myrtle Beach, South Carolina, and Wilmington, North Carolina. The FAA rerouted air traffic from the area and warned of delays as a result of the flight restrictions.

The Coast Guard advised mariners to immediately leave the area because of U.S. military operations “that present a significant hazard.”

Biden had been inclined to down the balloon over land when he was first briefed on it on Tuesday, but Pentagon officials advised against it, warning that the potential risk to people on the ground outweighed the assessment of potential Chinese intelligence gains.

The public disclosure of the balloon this week prompted the cancellation of a visit by U.S. Secretary of State Antony Blinken to Beijing scheduled for Sunday for talks aimed at reducing U.S.-China tensions. The Chinese government on Saturday sought to play down the cancellation.

“In actuality, the U.S. and China have never announced any visit, the U.S. making any such announcement is their own business, and we respect that,” China’s Ministry of Foreign Affairs said in a statement Saturday morning.

China has continued to claim that the balloon was merely a weather research “airship” that had been blown off course. The Pentagon rejected that out of hand — as well as China’s contention that it was not being used for surveillance and had only limited navigational ability.

The balloon was spotted over Montana, which is home to one of America’s three nuclear missile silo fields at Malmstrom Air Force Base.

The Pentagon also acknowledged reports of a second balloon flying over Latin America. “We now assess it is another Chinese surveillance balloon,” Brig. Gen. Pat Ryder, Pentagon press secretary, said in a statement.

China’s Ministry of Foreign Affairs did not immediately respond to a question about the second balloon.

Blinken, who had been due to depart Washington for Beijing late Friday, said he had told senior Chinese diplomat Wang Yi in a phone call that sending the balloon over the U.S. was “an irresponsible act and that (China’s) decision to take this action on the eve of my visit is detrimental to the substantive discussions that we were prepared to have.”

Uncensored reactions on the Chinese internet mirrored the official government stance that the U.S. was hyping the situation. Some used it as a chance to poke fun at U.S. defenses, saying it couldn’t even defend against a balloon, and nationalist influencers leapt to use the news to mock the U.S.

China has denied any claims of spying and said it is a civilian-use balloon intended for meteorology research. The Ministry of Foreign Affairs emphasized that the balloon’s journey was out of its control and urged the U.S. not to “smear” it based on the balloon.

https://www.securityweek.com/us-downs-chinese-balloon-off-carolina-coast/


China Says It’s Looking Into Report of Spy Balloon Over US

China said Friday it is looking into reports that a Chinese spy balloon has been flying in U.S. airspace and urged calm, adding that it has “no intention of violating the territory and airspace of any sovereign country.”

Foreign Ministry spokesperson Mao Ning also said she had no information about whether a trip to China by U.S. Secretary of State Antony Blinken planned for next week will proceed as scheduled.

At a daily briefing, Mao said that politicians and the public should withhold judgment “before we have a clear understanding of the facts” about the spy balloon reports.

Blinken would be the highest-ranking member of President Joe Biden’s administration to visit China, arriving amid efforts to mitigate a sharp downturn in relations between Beijing and Washington over trade, Taiwan, human rights and China’s claims in the South China Sea.

“China is a responsible country and has always strictly abided by international laws, and China has no intention of violating the territory and airspace of any sovereign country. As for the balloon, as I’ve mentioned just now, we are looking into and verifying the situation and hope that both sides can handle this together calmly and carefully,” Mao said.

“As for Blinken’s visit to China, I have no information,” she said.

A senior defense official told Pentagon reporters that the U.S. has “very high confidence” that the object was a Chinese high-altitude balloon and was flying over sensitive sites to collect information.

One of the places the balloon was spotted was over the state of Montana, which is home to one of America’s three nuclear missile silo fields at Malmstrom Air Force Base. The official spoke on condition of anonymity to discuss sensitive information.

Pentagon press secretary Brig. Gen. Patrick Ryder said the balloon is “currently traveling at an altitude well above commercial air traffic and does not present a military or physical threat to people on the ground.”

Ryder said similar balloon activity has been seen in the past several years and the government has taken steps to ensure no sensitive information was stolen.

President Biden was briefed and asked the military to present options, according to a senior administration official, who was also not authorized to publicly discuss sensitive information.

Defense Secretary Lloyd Austin and Army Gen. Mark Milley, chairman of the Joint Chiefs of Staff, advised against taking “kinetic action” because of risks to the safety of people on the ground. Biden accepted that recommendation.

The defense official said the U.S. has “engaged” Chinese officials through multiple channels and communicated the seriousness of the matter.

Blinken’s visit was expected to start this Sunday in an effort to try to find common ground on issues from trade policy to climate change. Although the trip has not been formally announced, both Beijing and Washington have been talking about his imminent arrival.

The senior defense official said the U.S. prepared fighter jets, including F-22s, to shoot down the balloon if ordered. The Pentagon ultimately recommended against it, noting that even as the balloon was over a sparsely populated area of Montana, its size would create a debris field large enough that it could have put people at risk.

It was not clear what will happen with the balloon if it isn’t brought down.

The defense official said the spy balloon was trying to fly over the Montana missile fields, but the U.S. has assessed that it has “limited” value in terms of providing intelligence it couldn’t obtain by other technologies, such as spy satellites.

The official would not specify the size of the balloon but said commercial pilots could spot it from their cockpits. All air traffic was halted at Montana’s Billings Logan International Airport from 1:30 p.m. to 3:30 p.m. Wednesday, as the military provided options to the White House.

A photograph of a large white balloon lingering over the area was captured by The Billings Gazette. The balloon could be seen drifting in and out of clouds and had what appeared to be a solar array hanging from the bottom, said Gazette photographer Larry Mayer.

The balloon’s appearance adds to national security concerns among lawmakers over China’s influence in the U.S., ranging from the prevalence of the hugely popular smartphone app TikTok to purchases of American farmland.

“China’s brazen disregard for U.S. sovereignty is a destabilizing action that must be addressed,” Republican Party House Speaker Kevin McCarthy tweeted.

Tensions with China are particularly high on numerous issues, ranging from Taiwan and the South China Sea to human rights in China’s western Xinjiang region and the clampdown on democracy activists in Hong Kong. Not least on that list of irritants are China’s tacit support for Russia’s invasion of Ukraine, its refusal to rein in North Korea’s expanding ballistic missile program and ongoing disputes over trade and technology.

On Tuesday, Taiwan scrambled fighter jets, put its navy on alert and activated missile systems in response to nearby operations by 34 Chinese military aircraft and nine warships that are part Beijing’s strategy to unsettle and intimidate the self-governing island democracy.

Twenty of those aircraft crossed the central line in the Taiwan Strait that has long been an unofficial buffer zone between the two sides, which separated during a civil war in 1949.

Beijing has also increased preparations for a potential blockade or military action against Taiwan, which has stirred increasing concern among military leaders, diplomats and elected officials in the U.S., Taiwan’s key ally.

The surveillance balloon was first reported by NBC News.

From an office window in Billings, Montana, Chase Doak said he saw a “big white circle in the sky” that he said was too small to be the moon.

“I thought maybe it was a legitimate UFO,” Doak said. “So I wanted to make sure I documented it and took as many photos as I could.”

https://www.securityweek.com/china-says-its-looking-into-report-of-spy-balloon-over-us/


The flight tracker that powered @ElonJet has taken a left turn

Picture of airplane with visual overlay
SeongJoon Cho/Bloomberg/Getty Images

A major independent flight tracking platform, which has made enemies of the Saudi royal family and Elon Musk, has been sold to a subsidiary of a private equity firm. And its users are furious.

ADS-B Exchange has made headlines in recent months for, as AFP put it, irking “billionaires and baddies.” But in a Wednesday morning press release, aviation intelligence firm Jetnet announced it had acquired the scrappy open source operation for an undisclosed sum.

Jetnet mostly provides intelligence for the aviation industry and was itself acquired by private equity firm Silversmith Capital Partners last year. According to a company press release, “the acquisition is the second of what the company anticipates will be several future acquisitions as Jetnet expands its data-driven product offerings for the aviation industry.”

The deal wasn’t exactly welcomed by the user base that makes up ADBS-B Exchange. “I don’t see a long future for ADSBx under a PE [private equity] firm,” one user wrote on ADS-B Exchange’s Discord server. “And definitely not the information-for-all we-show-all-the-data service it is today. The paycheck was bigger than the vision.”

“Wouldn’t surprise me if it becomes censored because it’s owned by a PE,” another user chimed in.

ADS-B Exchange, like bigger competitors FlightRadar24 and FlightAware, allows users armed with the aircraft registration details to follow planes’ flight paths and access historical travel data. That data, as WIRED reported last month, is enormously helpful for plane spotters, open source investigators, and aviation regulators.

What separates ADS-B Exchange from the other, more established operations is where it sources its data. FlightAware and FlightRadar24 have a dedicated team of volunteer and amateur data collectors, or feeders, but they also rely heavily on government feeds, including from the US Federal Aviation Authority (FAA).

ADS-B Exchange, on the other hand, is entirely user-supported. Across the globe, volunteers set up receivers—which can be built, or bought for relatively cheap—designed to receive real-time data from planes in mid-flight. They, in turn, feed that data into ADS-B Exchange’s software, which compiles the thousands of inputs and displays a real-time map of all the world’s in-transit flights.

The standard the exchange relies on, Automatic Dependent Surveillance-Broadcast (ADS-B), is becoming increasingly ubiquitous and is mandated by the FAA. It’s that standard that has made ADS-B Exchange so reviled by Musk and the Saudis. Plane owners who wish to hide their flight paths from the general public can submit a request to the FAA, which can require that downstream users of their feeds, like FlightRadar24 and FlightAware, suppress that information. Because ADS-B is transmitted without encryption, directly from the planes themselves, that kind of censorship isn’t possible.

ADS-B Exchange’s administrators pride themselves on never hiding flight data. James Stanford, one of ADS-B Exchange’s senior administrators, told WIRED their website has been used to track gold smugglers and kidnappers, and it has been threatened by billionaires and warlords who aren’t keen on having their private jets tracked.

https://arstechnica.com/?p=1913176


Le dieci priorità di protezione e privacy dei dati del 2023

La Giornata mondiale della privacy, che si celebra ogni anno il 28 gennaio, serve a sottolineare l’importanza della protezione dei dati personali nell’era digitale. Con la tecnologia che continua a fare progressi, sono sempre di più le informazioni che vengono condivise online, motivo per cui utenti e organizzazioni devono adottare le giuste misure per salvaguardarle.

Nuove normative, come il DORA (Digital Operational Resiliency ACT), impongono alle organizzazioni di creare piani per la gestione del rischio, la segnalazione degli incidenti e i test di resilienza. Queste normative definiscono policy di gestione dei dati, tra cui crittografia, localizzazione e ciclo di vita. Secondo Gartner, “entro il 2023, il 65% della popolazione mondiale avrà i propri dati personali coperti da diverse normative sulla privacy, cosa che impone alle aziende la scelta di soluzioni flessibili in grado di adattarsi alla moltitudine di regolamenti.” Navigare in questo ambiente complesso può essere effettivamente molto impegnativo sia per i singoli che per le aziende.

La data privacy è la protezione delle informazioni personali e la possibilità di controllare il modo in cui i dati vengono raccolti, utilizzati e conservati. D’altra parte, la protezione si riferisce alle misure tecniche e organizzative messe in atto per salvaguardare i dati (compresi quelli personali) da accesso, uso, alterazione o distruzione non autorizzati. Comprende la privacy e altre aree, tra cui backup e ripristino, disaster recovery, sicurezza e molto altro.

Per affrontare questa complessità, analizziamo i 10 argomenti principali da considerare nella gestione della privacy e della protezione dei dati.

1. Strategia di data protection

Le aziende dovrebbero iniziare a creare o aggiornare un piano di protezione, backup e ripristino dei dati e di disaster recovery come parte di una strategia globale di sicurezza dei dati. Sono numerose le sfaccettature di un piano affidabile e riguardano in particolare la protezione dei dati privati che i clienti hanno condiviso con l’organizzazione.

2. Crittografia

La crittografia è una funzionalità fondamentale della protezione e della tutela dei dati privati. Quella dei dati a riposo e in transito aiuta a prevenire l’accesso non autorizzato alle informazioni personali, aspetto particolarmente importante per le organizzazioni che gestiscono grandi quantità di dati privati, come i fornitori di servizi sanitari e le istituzioni finanziarie. I dati non risiedono più solo nei data center aziendali, poiché la maggior parte delle aziende dispone di uno o più cloud pubblici in cui sono memorizzati workload e informazioni. L’uso della crittografia, a rafforzare la protezione, aiuta a mitigare il rischio di potenziali attacchi nel corso dell’intera vita dei dati.

3. Autenticazione multi-person

Oltre a proteggere i dati con la crittografia, le aziende devono salvaguardare i propri sistemi da attacchi dannosi. L’utilizzo dell’autenticazione multi-persona (MPA) per i sistemi di protezione dei dati prevede per le attività critiche la necessità di più approvazioni da parte di utenti previamente autorizzati. Spesso trascurato, è uno dei modi più semplici per prevenire operazioni come l’esfiltrazione o l’eliminazione dei dati.

4. Storage immutabile

Lo storage immutabile consente di scrivere dati, privati o di altro tipo, che non possono essere ulteriormente modificati o cancellati, garantendo il mantenimento della loro integrità. I requisiti di storage immutabile stanno rapidamente diventando una componente standard delle normative sulla governance dei dati come GDPR, HIPAA e altre. In combinazione con l’MPA, è possibile creare livelli di archiviazione dei dati altamente sicuri, perfetti per l’archiviazione di quelli riservati e privati.

5. Sovranità dei dati

Nello sviluppo di una strategia di protezione dei dati, le organizzazioni devono tenere conto delle normative relative all’archiviazione delle informazioni private, che includono l’ubicazione dello storage e la conformità alle normative sulla sovranità dei dati. Può essere richiesto che un determinato set di dati rimanga anche fisicamente all’interno di una regione specifica, o ne segua regole altrettanto specifiche. Ad esempio, un workload basato su cloud su GCP in Europa o contenente dati di cittadini dell’UE deve essere conforme alle normative dell’UE.

6. Data Governance & Discovery

In una recente indagine, il 57% dei CISO ha ammesso di non sapere dove si trovino alcuni o tutti i propri dati o come siano protetti. Con la continua crescita della quantità di dati privati, il numero di normative si estende in modo esponenziale generando confusione su cosa deve essere protetto e come. Di conseguenza, le aziende devono capire quali dati possiedono, dove si trovano e quali sono a rischio ed è fondamentale essere in grado di stabilire un ordine di priorità in base alle policy, agli obiettivi e alle normative applicabili dell’organizzazione.

7. Classificazione dei dati

Sapere quali dati esistono e dove risiedono è solo una parte della soluzione, perché le organizzazioni devono considerare gli stessi dati in termini di importanza relativa, per i clienti o per la stessa azienda. Proteggendo solo i dati on-premise potrebbero sfuggirne alcuni critici che risiedono nella soluzione CRM basata su SaaS. A questo proposito, per la sicurezza dei dati non si può dipendere solo dal fornitore SaaS o di cloud IaaS, che possono fornire alcuni SLA e un determinato livello di ridondanza, ma non possono sostituire completamente un solido piano di protezione. Anche la gestione della classificazione dei dati non è un’operazione puntuale, dato che i dati crescono esponenzialmente ogni anno.

8. Conservazione

È fondamentale sapere quali dati esistono e quanto sono importanti, ma per quanto tempo questi stessi dati rimangono rilevanti? Per la maggior parte delle organizzazioni è difficile rispondere a questa domanda, che si ripropone ogni anno con l’acquisto di sistemi di archiviazione sempre più grandi per ospitare i dati aziendali. Essere in grado di assegnare una durata di vita prevista può avere un impatto notevole sui profitti dell’azienda e proteggere i dati privati dei clienti. Disporre di sistemi per individuare, classificare e impostare automaticamente la conservazione dei dati ridurrà la probabilità di una loro dispersione, il tempo necessario per recuperare quelli inutilizzati e i costi.

9. Test del piano di resilienza e risposta agli incidenti

Il test del piano di resilienza, spesso definito runbook, è un’area spesso trascurata di una strategia di protezione dei dati. Creare o aggiornare un piano obsoleto può essere un compito scoraggiante, ma collaborare con fornitori di soluzioni di protezione dei dati con esperienza può ridurre significativamente il tempo necessario per aggiornarlo. La creazione di aggiornamenti con cadenza regolare crea una postura organizzativa pronta ad affrontare le minacce alla sicurezza.

10. Valutazione del rischio

Come già per il runbook, sarebbe opportuno collaborare con fornitori strategici per eseguire una valutazione dei rischi su base semestrale o annuale. Le valutazioni programmate possono aiutare a costruire la memoria per una solida mentalità di protezione di dati e privacy.

Implementando queste azioni e aggiornando regolarmente il piano di resilienza, si potrà avere certezza che le informazioni personali siano sicure e conformi alle più recenti normative sulla privacy.

A cura di Vincenzo Costantino, Senior Director, Sales Engineering South Western Europe di Commvault

Condividi sui Social Network:

https://www.ictsecuritymagazine.com/notizie/le-dieci-priorita-di-protezione-e-privacy-dei-dati-del-2023/


EU’s Breton Warns TikTok CEO: Comply With New Digital Rules

The European Union’s digital policy chief warned TikTok’s boss Thursday that the social media app will have to fall in line with tough new rules for online platforms set to take effect later this year.

EU Commissioner Thierry Breton held a video call with Shou Zi Chew, the CEO of TikTok, the popular Chinese-owned video sharing app that’s coming under increasing scrutiny from Western authorities over fears about data privacy, cybersecurity and misinformation.

The two discussed the company’s plans to comply with the bloc’s Digital Services Act, which is set to take effect for the biggest online companies in September. The act is a set of sweeping rules that will require platforms to reduce harmful online content and combat online risks.

“With younger audiences comes greater responsibility,” Breton said, according to a readout of the call. “It is not acceptable that behind seemingly fun and harmless features, it takes users seconds to access harmful and sometimes even life-threatening content.

Breton added that, with millions of young users in Europe, TikTok has a “special responsibility” to ensure its content is safe.

TikTok is hugely popular with young people but its Chinese ownership has stoked fears that Beijing could use it to scoop up user data or push pro-China narratives or misinformation. TikTok is owned by ByteDance, a Chinese company that moved its headquarters to Singapore in 2020.

Earlier this month, Shou met four other officials from the EU’s executive Commission in Brussels to discuss concerns ranging from child safety to investigations into user data flowing to China. In the U.S., at least 22 states, the military and Congress have banned the TikTok app from government-issued devices.

A London-based spokesperson for TikTok didn’t respond immediately to a request for comment. The company’s Brussels-based director of public policy and government relations, Caroline Greer, said on Twitter that Breton’s talk with Shou was a “good exchange” and that the “safety of our users is paramount.”

Breton said he is also concerned about allegations TikTok is spying on journalists and transferring reams of personal user data outside of Europe, in violation of the 27-country bloc’s strict privacy rules.

Bretaon said he “explicitly conveyed” to Shou that TikTok needs to “step up efforts to comply” with EU rules on data protection, copyright as well as the Digital Services At, which includes provisions for heavy fines or even a ban from the EU for repeat offenses that threaten the people’s lives or safety.

“We will not hesitate to adopt the full scope of sanctions to protect our citizens if audits do not show full compliance,” he said.

Greer said TikTok “welcomed the opportunity” to reiterate its commitment to the Digital Services Act and outlined efforts to comply with EU rules on privacy and a voluntary code of practice on disinformation for tech companies.

Related: Five Ways TikTok Is Seen as Threat to US National Security

Related: FBI Director Raises National Security Concerns About TikTok

Related: China’s ByteDance Admits Using TikTok Data to Track Journalists

view counter

Previous Columns by Associated Press:
Tags:

https://www.securityweek.com/eus-breton-warns-tiktok-ceo-comply-new-digital-rules


Meta Slapped With 5.5 Million Euro Fine for EU Data Breach

Social media giant Meta has been fined an additional 5.5 million euros ($5.9 million) for violating EU data protection regulations with its instant messaging platform WhatsApp, Ireland’s regulator announced Thursday.

The penalty follows a far larger 390-million-euro fine for Meta’s Instagram and Facebook platforms two weeks ago after they were found to have flouted the same EU rules.

In its new decision, the Irish Data Protection Commission (DPC) found the group acted “in breach of its obligations in relation to transparency,” the watchdog said in a statement.

In addition, Meta relied on an incorrect legal basis “for its processing of personal data for the purposes of service improvement and security,” the DPC added, giving the group six months to comply.

{ Read: Has Facebook Sidestepped GDPR’s User Consent Requirements? }

The fine was imposed by the Irish regulator because Meta — along with other US tech firms — has its European headquarters in Dublin.

In response on Thursday, Meta said it was opposed to the DPC decision and would look to overturn it.

“We strongly believe that the way the service operates is both technically and legally compliant,” a WhatsApp spokesperson said.

“We disagree with the decision and we intend to appeal.”

The breaches are similar to those explained in the regulator’s action against Meta earlier in January.

But the earlier decision also accused the Meta platforms of breaking rules over the processing of personal data for the purpose of targeted advertising.

In that instance the company, co-founded by social media magnate Mark Zuckerberg, was given only three months to respond to comply with the Irish regulator.

Meta announced its intention to appeal the 4 January decision, adding the regulatory ruling did not prevent targeted or personalised advertising.

The DPC said its more recent fine was considerably less because of a 225 million euro fine imposed on WhatsApp for “for breaches of this and other transparency obligations over the same period of time”.

Thursday’s Whatsapp fine was also far lower because it did not relate to targeted advertising.

The Irish regulator had fined Meta 405 million euros in September for failures in handling the data of minors, and 265 million euros in November for not sufficiently protecting users’ data.

This latest round of fines follows the adoption of three binding decisions by the European Data Protection Board (EDPB), the EU’s data protection regulator, in early December.

The Vienna-based privacy group NOYB, which brought the three complaints against Meta in 2018, had accused the social media behemoth of reinterpreting consent as a civil law contract, which stopped users from refusing targeted advertising.

In reaction to Thursday’s news, NOYB criticised the “tiny” size of the latest fine — and slammed the DPC for ignoring how WhatsApp shares data within the group for advertising purposes.

“We are astonished how the DPC simply ignores the core of the case after a 4.5-year procedure,” said NOYB founder Max Schrems.

In October 2021, the Irish authority had proposed a draft decision that validated the legal basis used by the group and suggested a fine of up to 36 million euros for Facebook and up to 23 million euros for Instagram, over their lack of transparency.

France’s CNIL regulator and other European bodies disagreed with the draft sanction, which they considered to be far too low.

They asked the EDPB to judge the dispute with the EU data regulator deciding in their favour.

The EDPB has also asked the Irish regulator to investigate Meta’s use of personal data.

However in its statement the DPC pushed back saying the the EU body does not have the power to “direct an authority to engage in open-ended and speculative investigation”.

The regulator said it will seek to annul the EDPB’s request before the European Union’s Court of Justice.

view counter

© AFP 2022

Previous Columns by AFP:
Tags:

https://www.securityweek.com/meta-slapped-55-million-euro-fine-eu-data-breach