Data Discovery: il primo passo verso la protezione dei dati sensibili – Webinar gratuito
Martedì 19 Luglio 2022 – ore 10:00
Registrati QUI al Webinar

Sapevate che nel 2021 quasi 50 milioni di persone negli Stati Uniti hanno subito una violazione dei loro dati sanitari sensibili, è un numero che è triplicato negli ultimi tre anni*.

I dati americani confermano una tendenza anche italiana, con il numero di violazioni in aumento anche nel nostro paese. L’Italia è seconda in Europa per numero di violazioni con 83 interventi dell’Autorità Garante (in testa c’è la Spagna con più di 250 sanzioni, segue la Romania con 57) ed è al terzo posto per multe complessive con quasi 80 milioni di euro**

In questo caso un approccio alla protezione dato-centrico è fondamentale per le istituzioni sanitarie e governative che hanno a che fare con dati sensibili come PII, PCI e PHI.

Quanto siete certi che non accadrebbe con i dati dei vostri cittadini e clienti? E come potreste evitare che accada?

Da dove parte un progetto sulla privacy e la sicurezza dei dati?

Molti Ciso hanno già espresso le loro difficoltà: la sfida è trovare i dati, capirne il percorso e tenerne traccia in un ambiente dinamico. Semplicemente non si può proteggere ciò che non si conosce. L’operatività della privacy dei dati inizia con il monitoraggio dell’inventario degli elementi sensibili dei dati.

In questo webinar presenteremo quali sono gli strumenti che possono essere utili per la scoperta e la classificazione dei dati strutturati e non strutturati, quali sono le best practice e le esperienze delle aziende che hanno già implementato un programma di gestione del ciclo di vita dei dati personali.

  • Dati personali e sensibili, quali sono le sfide di oggi
  • Scoprire i dati strutturati e non strutturati: introduzione di File Analysis Suite (FAS) e Structured Data Manager (SDM)
  • Come affrontare la protezione dei dati: vantaggi e punti di forza
  • DEMO

Scopri perché la Data Discovery è un requisito essenziale per migliorare la resilienza aziendale e gestire efficacemente i dati critici

“Data Discovery: il primo passo verso la protezione dei dati sensibili”

Martedì 19 Luglio 2022 – ore 10:00

Registrati QUI al Webinar

Fonte: * Politico ** Report DLA Piper 2022

Condividi sui Social Network:

https://www.ictsecuritymagazine.com/notizie/data-discovery-il-primo-passo-verso-la-protezione-dei-dati-sensibili/


The danger of license plate readers in post-Roe America

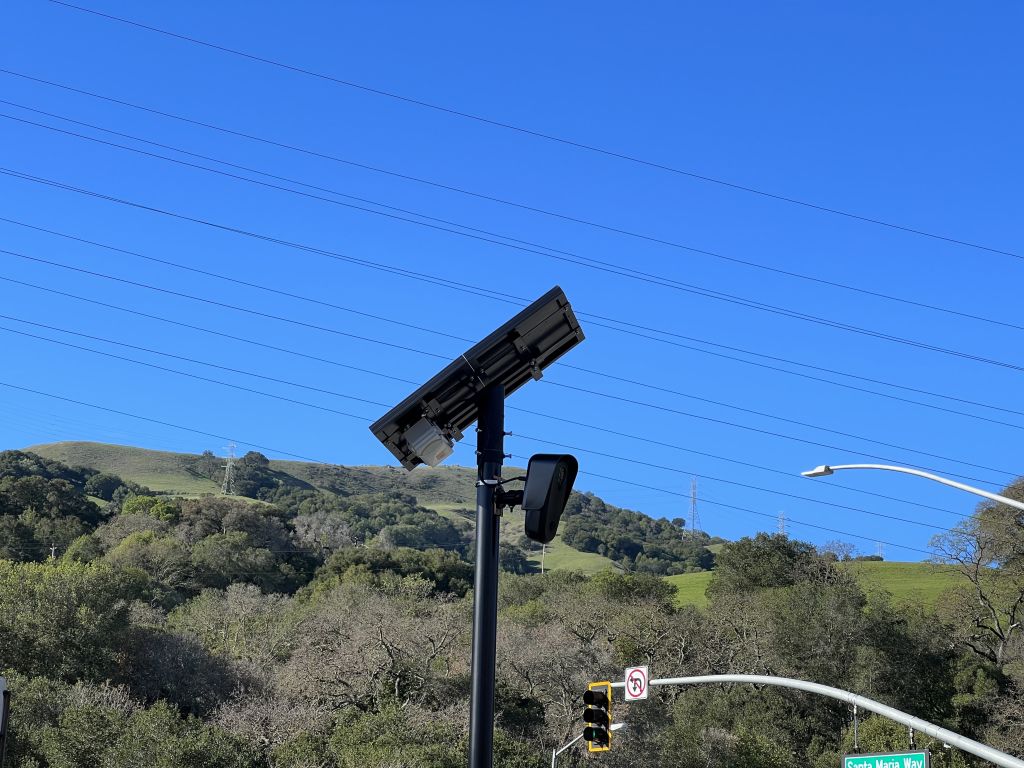
A license plate reader in California.
Enlarge / A license plate reader in California.

Since the United States Supreme Court overturned Roe v. Wade last month, America’s extensive surveillance state could soon be turned against those seeking abortions or providing abortion care.

Currently, nine states have almost entirely banned abortion, and more are expected to follow suit. Many Republican lawmakers in these states are discussing the possibility of preventing people from traveling across state lines to obtain an abortion. If such plans are enacted and withstand legal scrutiny, one of the key technologies that could be deployed to track people trying to cross state lines is automated license plate readers (ALPRs). They’re employed heavily by police forces across the US, but they’re also used by private actors.

ALPRs are cameras that are mounted on street poles, overpasses, and elsewhere that can identify and capture license plate numbers on passing cars for the purpose of issuing speeding tickets and tolls, locating stolen cars, and more. State and local police maintain databases of captured license plates and frequently use those databases in criminal investigations.

The police have access to not only license plate data collected by their own ALPRs but also data gathered by private companies. Firms like Flock Safety and Motorola Solutions have their own networks of ALPRs that are mounted to the vehicles of private companies and organizations they work with, such as car repossession outfits. Flock, for instance, claims it’s collecting license plate data in roughly 1,500 cities and can capture data from over a billion vehicles every month.

“They have fleets of cars that have ALPRs on them that just suck up data. They sell that to various clients, including repo firms and government agencies. They also sell them to police departments,” says Jay Stanley, a senior policy analyst at the ACLU. “It’s a giant, nationwide mass surveillance system. That obviously has serious implications should interstate travel become part of forced-birth enforcement.”

In a statement to WIRED, a Flock Safety spokesperson said the company does not provide customer data to third parties. “We will never share or sell customer data to any third parties. While we cannot speak for any other vendors, we have never and will never sell data to repossession companies or third-party organizations, including anti-abortion groups,” the company said.

However, anyone can become a first party by purchasing the company’s cameras. (Its customers often include neighborhoods and home owners associations.) Flock Safety says its cameras are installed in more than 1,500 cities in 42 states, which are connected to Flock’s centralized camera network. A March 2021 Vice investigation based on Flock-related emails obtained from nearly 20 police departments allows anyone who administers a Flock camera to “make the data Flock captures available to, say, the police, the home owner association’s board, or the individual members of an entire neighborhood.” In addition to private customers, Flock has also reportedly partnered with hundreds of police departments across the US.

Motorola Solutions did not respond to a request for comment prior to publication.

https://arstechnica.com/?p=1865115


Contrattazione sui controlli a distanza dei lavoratori: quando il diritto del lavoro ha bisogno di un po’ di privacy!

La rubrica “Digital & Law” è curata da D&L Net e offre una lettura delle materie dell’innovazione digitale da una prospettiva che sia in grado di offrire piena padronanza degli strumenti e dei diritti digitali, anche ai non addetti ai lavori. Per consultare tutti gli articoli clicca qui.

Il sindacato moderno dovrà avere il logo “PRIVACY”?

Nel corso degli anni abbiamo assistito ad un’evoluzione del concetto dei diritti: sempre più il contenuto ha dovuto prendere la forma del contenitore e questo contenitore “vita” è divenuto sempre più vario.

Il risultato – nel contesto giuslavoristico – è stato quello per cui i diritti contenuti nello statuto dei lavoratori, e nella specie l’art. 4 Stat. Lav. (L 300/1970) in materia di controlli a distanza, appaiono in parte oggi obsoleti e si sta cercando nel tempo di rimodernarli e adeguarli alle circostanze del presente.

Nel tema dei controlli a distanza, ad esempio, dopo differenti interventi normativi che hanno cambiato l’assetto della norma dello Statuto, nel 2015 e nel 2016 (d.lgs. 151/2015 e d.lgs. 185/2016), pare ci si stia attestando su una maggiore consapevolezza e rispetto della privacy nella raccolta e rilevazione dei dati sul lavoro derivanti dal controllo degli apparecchi informatici (che siano telecamere, dispositivi di posizione o smart phone).

Infatti, il controllo del lavoratore tramite strumenti digitali, anche involontariamente a volte a causa del massivo utilizzo di tecnologia, sta diventando da eccezione a regola, all’interno dei contesti lavorativi, anche più piccoli.  La gestione dei dati e delle scelte tramite algoritmi e intelligenze artificiali trova strada e spazio per una ottimizzazione di tempo e di risorse, ma per essere veramente una risorsa i dati vanno ben gestiti e trattati.

In particolare, nel controllo a distanza è importante che il moderno sindacato si occupi di “contrattazione degli algoritmi” ovvero pretenda che tutti i dati dei lavoratori, e in particolar modo quelli più sensibili, vengano preventivamente sottoposti a consenso informato e che il lavoratore – nell’attuale background digitale – sia coscienteche quello che sta scrivendo con lo smart phone aziendale possa essere sottoposto a lettura anche del suo capo o che il titolare dell’azienda, con un semplice monitoraggio del software, sappia che giro abbia fatto il suo dipendente autista e se si sia fermato una o due ore in pausa pranzo o in altri luoghi o che durante l’orario di lavoro effettui degli acquisti tramite shopping on line con il pc aziendale, magari anche in smart working.

Ci vuole correttezza da parte del lavoratore? Certo! Prima di tutto questo ci si auspica essere presente in un rapporto di lavoro, ma vi sono dati – soprattutto quelli intimi e interni ad una corrispondenza privata tracciata in un terminale aziendale – che non è giustificato violare al solo fine dell’indagine a tappeto o verifica ex ante di una qualche violazione disciplinare!

La legittimità del controllo a distanza del lavoratore

Nelle recenti pronunce giurisprudenziali, e in particolare nelle ultime Cassazioni del 2021 e nella sentenza del Tribunale di Genova del 14.12.2021, in primo grado ma esplicativa di tutto un percorso giurisprudenziale degli ultimi 5 anni, si chiarisce proprio che perché un dato possa essere utilizzato, anche ai fini processuali, e perché quindi il controllo del lavoratore si possa dire legittimo, occorre che le informazioni raccolte in esito ad esso siano coperte da un pieno rispetto dei diritti della privacy, così come alla eventuale contrattazione sindacale per quel che attiene gli strumenti di cui all’art. 4 Stat. Lav. comma 1.

I controlli a distanza potranno essere disposti, allora, sia per ragioni di controllo ordinario e di tutela del patrimonio aziendale, o anche come strumento difensivo generale o in senso stretto (che si realizzano rispettivamente, a seconda che il dato venga raccolto ex ante il sospetto di illecito o ex post il sospetto del comportamento del lavoratore, e in quest’ultimo caso non si ricadrà nel campo della norma dello “strumento di controllo” ex art. 4 stat.lav.).

In conclusione, si ritiene che, indipendentemente che si rientri oppure no nell’ambito di applicazione dell’art. 4 Stat. Lav. occorrerà sempre rispettare la privacy: se non ce lo dice l’art. 4 c. 3 Stat. Lav. ce lo dice l’art. 8 CEDU nel momento in cui parla di “bilanciamento della dignità” dei diritti e di diritto alla privacy nella vita privata intesa anche come “vita lavorativa”.

Les jeux sont fait, quindi!

La più moderna contrattazione sul lavoro tende al rispetto della dignità umana e professionale del lavoratore!

https://www.key4biz.it/contrattazione-sui-controlli-a-distanza-dei-lavoratori-quando-il-diritto-del-lavoro-ha-bisogno-di-un-po-di-privacy/409814/


End-to-end encryption’s central role in modern self-defense

A tunnel made of ones and zeroes.

A number of course-altering US Supreme Court decisions last month—including the reversal of a constitutional right to abortion and the overturning of a century-old limit on certain firearms permits—have activists and average Americans around the country anticipating the fallout for rights and privacy as abortion “trigger laws,” expanded access to concealed carry permits, and other regulations are expected to take effect in some states. And as people seeking abortions scramble to protect their digital privacy and researchers plumb the relationship between abortion speech and tech regulations, encryption proponents have a clear message: Access to end-to-end encrypted services in the US is more important than ever.

Studies, including those commissioned by tech giants like Meta, have repeatedly and definitively shown that access to encrypted communications is a human rights issue in the digital age. End-to-end encryption makes your messages, phone calls, and video chats unintelligible everywhere except on the devices involved in the conversations, so snoops and interlopers can’t access what you’re saying—and neither can the company that offers the platform. As the legal climate in the US evolves, people who once thought they had nothing to hide may realize that era is now over.

“There are plenty of people in the US for whom it has always been true that the state wasn’t really helping them and was mostly harming them,” says Riana Pfefferkorn, a research scholar at the Stanford Internet Observatory. “But for those who are now losing faith in traditional institutions of government, it provides room for them to say, ‘OK, what technologies exist for taking back some control?’”

Over the past decades, law enforcement officials around the world have increasingly marked encryption as a hindrance to investigations and, therefore, a threat. The US Department of Justice and other agencies worldwide have campaigned to undermine encryption features with backdoors or make it economically infeasible for companies to offer the protection. While it is important to prevent violence and prosecute activity like the distribution of child sexual abuse materials, researchers consistently note that criminals will deploy and use encryption to protect their data whether the tools are legal or not—as has been the case with terrorist groups like al-Qaida and the Islamic state group.

Moxie Marlinkspike, the cryptographer who founded the open source, end-to-end encrypted messaging service Signal, explored the question of criminality and access to secure communications in a blog post nearly 10 years ago. “Police already abuse the immense power they have, but if everyone’s every action were being monitored, and everyone technically violates some obscure law at some time, then punishment becomes purely selective,” he wrote. “Those in power will essentially have what they need to punish anyone they’d like, whenever they choose.”

https://arstechnica.com/?p=1864680


Google closes data loophole amid privacy fears over abortion ruling

Google closes data loophole amid privacy fears over abortion ruling

Google is closing a loophole that has allowed thousands of companies to monitor and sell sensitive personal data from Android smartphones, an effort welcomed by privacy campaigners in the wake of the US Supreme Court’s decision to end women’s constitutional right to abortion.

It also took a further step on Friday to limit the risk that smartphone data could be used to police new abortion restrictions, announcing it would automatically delete the location history on phones that have been close to a sensitive medical location, such as an abortion clinic.

The Silicon Valley company’s moves come amid growing fears that mobile apps will be weaponized by US states to police new abortion restrictions in the country.

Companies have previously harvested and sold information on the open market, including lists of Android users using apps related to period tracking, pregnancy, and family planning, such as Planned Parenthood Direct.

Over the past week, privacy researchers and advocates have called for women to delete period-tracking apps from their phones to avoid being tracked or penalized for considering abortions.

The US tech giant announced last March that it would restrict the feature, which allows developers to see which other apps are installed and deleted on individuals’ phones. That change was meant to be implemented last summer, but the company failed to meet that deadline, citing the pandemic, among other reasons.

The new deadline of July 12 will hit just weeks after the overturning of Roe vs Wade, a ruling that has thrown a spotlight on how smartphone apps could be used for surveillance by US states with new anti-abortion laws.

“It’s long overdue. Data brokers have been banned from using the data under Google’s terms for a long time, but Google didn’t build safeguards into the app approvals process to catch this behavior. They just ignored it,” said Zach Edwards, an independent cyber security researcher who has been investigating the loophole since 2020.

“So now anyone with a credit card can purchase this data online,” he added.

Google said: “In March 2021, we announced that we planned to restrict access to this permission, so that only utility apps, such as device search, antivirus, and file manager apps, can see what other apps are installed on a phone.”

It added: “Collecting app inventory data to sell it or share it for analytics or ads monetization purposes has never been allowed on Google Play.”

Despite widespread usage by app developers, users remain unaware of this feature in Android software—a Google-designed programming interface, or API, known as the “Query All Packages.” It allows apps, or snippets of third-party code inside them, to query the inventory of all other apps on a person’s phone. Google itself has referred to this type of data as high-risk and “sensitive,” and it has been discovered being sold to third parties.

Researchers have found that app inventories “can be used to precisely deduce end users’ interests and personal traits,” including gender, race, and marital status, among other things.

Edwards has found that one data marketplace, Narrative.io, was openly selling data obtained by intermediaries in this way, including smartphones using Planned Parenthood and various period tracking apps.

Narrative said it removed pregnancy tracking and menstruation app data from its platform in May in response to the leaked draft outlining the Supreme Court’s forthcoming decision.

Another research company, Pixalate, discovered that consumer apps, like a simple weather app, were running bits of code that exploited the same Android feature and were harvesting data for a Panamanian company with ties to US defense contractors.

Google said it “never sells user data, and Google Play strictly prohibits the sale of user data by developers. When we discover violations we take action,” adding it had sanctioned multiple companies believed to be selling user data.

Google said it would restrict the Query All Packages feature to only those who require it from July 12. App developers will be required to fill out a declaration explaining why they need access and notify Google of this before the deadline so it can be vetted.

“Deceptive and undeclared uses of these permissions may result in a suspension of your app and/or termination of your developer account,” the company warned.

Additional reporting by Richard Waters.

© 2022 The Financial Times Ltd. All rights reserved Not to be redistributed, copied, or modified in any way.

https://arstechnica.com/?p=1864151


Google hit with more privacy complaints for “deceptive” sign-up process [Updated]

Google hit with more privacy complaints for “deceptive” sign-up process [Updated]

More than a billion people worldwide have signed up for Google accounts, clicking through screens promising that “your personal info is private and safe.” This week, Google’s sign-up process came under fire when European Union consumer rights groups issued new privacy complaints suggesting that the opposite is true—that Google intentionally designs default settings to deceive new users into granting permissions to harvest and share a broad swath of personal info.

“The language Google uses at every step of the registration process is unclear, incomplete, and misleading,” the European consumer organization BEUC told Reuters. BEUC is helping to coordinate a potential civil lawsuit in Germany and several new complaints to data-protection authorities from consumer rights groups in France, Greece, the Czech Republic, Norway, and Slovenia.

The key issue in these complaints is how hard Google makes it for account users to choose privacy-friendly options. It’s much easier, the consumer groups argue, to set up an account to share personal info than to protect it. As Tech Crunch reported, Google designed a one-click “express personalization” option allowing data tracking, while “manual personalization” requires 10 clicks to turn off tracking.

A Google spokesperson told Reuters that “we are committed to ensuring these choices are clear and simple,” denying any wrongdoing because “these options are clearly labelled and designed to be simple to understand. We have based them on extensive research efforts and guidance from DPAs (data protection authorities) and feedback from testers.”

Google did not immediately respond to a request to comment on any plans to alter the sign-up process. (Update: Google responded with a statement that added that they “welcome the opportunity” to engage with consumer advocates and regulators regarding privacy concerns.)

Do better

BEUC maintains that Google could do better.

“Contrary to what Google claims about protecting consumers’ privacy, tens of millions of Europeans have been placed on a fast track to surveillance when they signed up to a Google account,” said Ursula Pachl, deputy director-general of BEUC, in a statement. “It takes one simple step to let Google monitor and exploit everything you do.”

Instead, she countered, “Privacy protection should be the default and easiest choice for consumers.”

BEUC sees Google as a repeat offender, pointing to additional privacy complaints dating back four years and past fines by EU antitrust regulators amounting to more than $8 billion. Reuters reported that the tech company “could face fines worth up to 2 percent of its global turnover if found guilty of breaching EU privacy rules.”

BEUC expects that the newest complaints from consumer rights groups will pressure regulators to take action against Google. BEUC is working to ensure that account holders are always in control and clearly understand how their data is used.

For now, anyone creating a new account by default grants Google permission to save web and app activity, including their entire YouTube history and use of Google services like search, to personalize ads. On the Privacy and Terms page, users are told that “you’re in control,” with “more options” to turn off these particular settings linked below summaries that explain why the default settings to widely share data are beneficial.

Pachl said the EU complaints will continue until Google accounts are no longer “subjected to surveillance by design and by default,” as required by the EU’s data protection law, the General Data Protection Regulation.

https://arstechnica.com/?p=1863933


Aborto vietato negli Usa, privacy a rischio per tutte le donne in età riproduttiva

Dopo la sentenza che abolisce il diritto all’aborto negli Usa, i dati online di tutte le donne in età riproduttiva potrebbero essere utilizzati contro le persone che fanno ricerche sull’aborto. Una conseguenza diretta sulla nostra privacy, quindi, ora che la sentenza Roe vs. Wade è stata ribaltata rendendo di fatto illegale l’aborto in gran parte degli Stati Uniti.

Grido d’allarme per la privacy

E’ questo il grido d’allarme che si è alzato negli Usa, dopo la sentenza della Corte Suprema americana che ha abolito il diritto di interrompere la gravidanza. Secondo gli esperti, oltre a privare le donne dei diritti di abortire, la sentenza della Corte Suprema Usa modifica alla radice il rapporto delle donne con la Rete e con il mondo digitale tout court. Lo scrive il sito specializzato The Conversation, in un’interessante articolo di commento.

Chiunque si rivolga a internet per cercare informazioni sull’aborto, oppure prodotti e servizi legati all’aborto, nei paesi dove questa pratica è diventata all’improvviso illegale è a rischio di sorveglianza online.

Tutte le donne in età da figli, a prescindere da quanto si possano sentire sicure o privilegiate, si troveranno d’ora in poi marginalizzate e a rischio privacy, come parte della popolazione più vulnerabile e a rischio.

Tutti sanno da tempo come Google, i social media e i dati di Internet in genere possono essere utilizzati per la sorveglianza da parte delle forze dell’ordine per lanciare reti a strascico digitali. Le donne sono a rischio non solo per ciò che rivelano sul loro stato riproduttivo sui social media, ma anche per i dati delle loro applicazioni sanitarie, che potrebbero incriminarle se venissero citate in giudizio.

Chi è sotto controllo e come

Le persone più vulnerabili all’invasione della privacy online e all’uso o abuso dei loro dati sono tradizionalmente quelle che la società considera meno degne di protezione: persone senza mezzi, potere o posizione sociale. La sorveglianza rivolta alle persone emarginate riflette non solo una mancanza di interesse a proteggerle, ma anche una presunzione che, in virtù della loro identità sociale, abbiano maggiori probabilità di commettere crimini o trasgredire in modi che potrebbero giustificare attività di polizia preventiva.

Molte persone emarginate sono donne, comprese le madri a basso reddito, per le quali il semplice atto di richiedere l’assistenza pubblica può sottoporle a presunzioni di intento criminale. Queste presunzioni sono spesso utilizzate per giustificare le invasioni della loro privacy. Ora, con la legislazione anti-aborto che sta investendo gli stati controllati dai repubblicani e pronta ad entrare in vigore con la fine di Roe v. Wade, è probabile che tutte le donne in età riproduttiva in quegli stati siano soggette a quelle stesse presunzioni.

Prima, le donne dovevano preoccuparsi solo che Target o Amazon potessero venire a conoscenza delle loro gravidanze. Sulla base di ciò che è già noto sulle incursioni della privacy da parte delle forze dell’ordine contro le persone emarginate, è probabile che nel mondo post-Roe le donne saranno più nel mirino della scientifica digitale. Ad esempio, le forze dell’ordine utilizzano regolarmente strumenti forensi per perquisire i cellulari delle persone quando indagano su un’ampia gamma di crimini, a volte senza un mandato di perquisizione.

App del ciclo mestruale

Immagina uno scenario in cui un collega o un vicino denuncia qualcuno alle autorità, il che fornisce alle forze dell’ordine motivi per perseguire le prove digitali. Tali prove potrebbero includere, ad esempio, ricerche su Internet su fornitori di aborti e dati di app per il ciclo che mostrano periodi mancati.

Il rischio è particolarmente acuto nei luoghi che favoriscono la caccia di taglie. In uno stato come il Texas, dove c’è la possibilità che i cittadini abbiano la possibilità di citare in giudizio le persone che aiutano gli altri ad accedere ai servizi di aborto, tutto ciò che dici o fai in qualsiasi contesto diventa rilevante perché non c’è una causa probabile che ostacoli l’accesso ai tuoi dati.

Al di fuori di questo caso, è difficile rendere pienamente giustizia a tutti i rischi perché il contesto è importante e diverse combinazioni di circostanze possono cospirare per aumentare i danni. Ecco i rischi da tenere a mente:

Condividere sui social media informazioni sulla tua gravidanza

Comportamento di ricerca su Internet correlato direttamente o indirettamente alla gravidanza o alla salute riproduttiva, indipendentemente dal motore di ricerca utilizzato.

Tracciamento della posizione tramite il telefono, ad esempio mostrando che hai visitato un luogo che potrebbe essere collegato alla tua salute riproduttiva.

Utilizzo di app che rivelano dati sensibili rilevanti, come il ciclo mestruale.

Essere troppo sicuri nell’usare la crittografia o strumenti anonimi.

https://www.key4biz.it/aborto-vietato-negli-usa-privacy-a-rischio-per-tutte-le-donne-in-eta-riproduttiva/408389/


Spurred by Roe overturn, senators seek FTC probe of iOS and Android tracking

A Illustration of a smartphone at the center of a target.

Four Democratic US senators today asked the Federal Trade Commission to “investigate Apple and Google for engaging in unfair and deceptive practices by enabling the collection and sale of hundreds of millions of mobile phone users’ personal data.”

“The FTC should investigate Apple and Google’s role in transforming online advertising into an intense system of surveillance that incentivizes and facilitates the unrestrained collection and constant sale of Americans’ personal data,” they wrote. “These companies have failed to inform consumers of the privacy and security dangers involved in using those products. It is beyond time to bring an end to the privacy harms forced on consumers by these companies.”

The letter cited the Supreme Court decision overturning Roe v. Wade, saying that women “seeking abortions and other reproductive healthcare will become particularly vulnerable to privacy harms, including through the collection and sharing of their location data.” It continued:

Data brokers are already selling, licensing, and sharing the location information of people that visit abortion providers to anyone with a credit card. Prosecutors in states where abortion becomes illegal will soon be able to obtain warrants for location information about anyone who has visited an abortion provider. Private actors will also be incentivized by state bounty laws to hunt down women who have obtained or are seeking an abortion by accessing location information through shady data brokers.

iOS, Android “fueled unregulated data broker market”

The letter was sent to FTC Chair Lina Khan by Sens. Ron Wyden (D-Ore.), Elizabeth Warren (D-Mass.), Cory Booker (D-N.J.), and Sara Jacobs (D-Calif.). Apple and Google “knowingly facilitated these harmful practices by building advertising-specific tracking IDs into their mobile operating systems,” the senators wrote.

“Apple and Google both designed their mobile operating systems, iOS and Android, to include unique tracking identifiers which they have specifically marketed for advertising purposes,” the letter said. “These identifiers have fueled the unregulated data broker market by creating a single piece of information linked to a device that data brokers and their customers can use to link to other data about consumers. This data is bought or acquired from app developers and online advertisers, and can include consumers’ movements and web browsing activity.”

While Apple has stopped enabling the tracking identifiers by default, the senators wrote that both companies harmed consumers:

Both Apple and Google now allow consumers to opt out of this tracking. Until recently, however, Apple enabled this tracking ID by default and required consumers to dig through confusing phone settings to turn it off. Google still enables this tracking identifier by default, and until recently did not even provide consumers with an opt-out. By failing to warn consumers about the predictable harms that would result by using their phones with the default settings that these companies chose, Apple and Google enabled governments and private actors to exploit advertising tracking systems for their own surveillance and exposed hundreds of millions of Americans to serious privacy harms.

Last week, Warren proposed legislation that would prohibit data brokers from selling Americans’ location and health data.

“Anonymous” identifiers can be linked to people

The advertising identifiers are “purportedly anonymous” but in reality “are easily linkable back to individual users,” the letter said. “This is because some data brokers sell databases that explicitly link these advertising identifiers to consumers’ names, email addresses, and telephone numbers. But even without buying this additional data, it is often possible to easily identify a particular consumer in a dataset of ‘anonymous’ location records by looking to see where they sleep at night.”

We asked Apple and Google for comment on the letter and will update this story if we get any response.

Update at 2:55 pm ET: Google responded to Ars, touting its efforts to block apps that violate Google Play policies and the bans it has imposed on companies that apparently sold user data. “Google never sells user data, and Google Play strictly prohibits the sale of user data by developers,” the company said in a statement. “The advertising ID was created to give users more control and provide developers with a more private way to effectively monetize their apps. Additionally, Google Play has policies in place that prohibit using this data for purposes other than advertising and user analytics. Any claims that advertising ID was created to facilitate data sale are simply false.”

Google also said its Android Privacy Sandbox will “enable new, more private advertising solutions that limit sharing of user data with third parties and operate without cross-party identifiers, including advertising IDs.” Ars reporter Ron Amadeo’s coverage of that initiative called it “toothless.”

EFF calls for action by Congress and tech companies

The senators’ letter was prepared before the official release of the Supreme Court’s abortion decision, which came out today after a draft was leaked in early May. Reacting to the court ruling today, the Electronic Frontier Foundation said it “underscores the importance of fair and meaningful protections for data privacy.”

“Everyone deserves to have strong controls over the collection and use of information they necessarily leave behind as they go about their normal activities, like using apps, search engine queries, posting on social media, texting friends, and so on,” the EFF said. “But those seeking, offering, or facilitating abortion access must now assume that any data they provide online or offline could be sought by law enforcement.”

The EFF urged state and federal lawmakers to “pass meaningful privacy legislation” and said companies should protect privacy “by allowing anonymous access, stopping behavioral tracking, strengthening data deletion policies, encrypting data in transit, enabling end-to-end message encryption by default, preventing location tracking, and ensuring that users get notice when their data is being sought.”

Last month, more than 40 Democratic members of Congress called on Google to stop collecting and retaining customer location data that prosecutors could use to identify women who obtain abortions. Lawmakers have also been working on comprehensive data privacy legislation, but no proposal is close to being passed.

https://arstechnica.com/?p=1862757


Facebook is receiving sensitive medical information from hospital websites

Facebook is receiving sensitive medical information from hospital websites
Aurich Lawson | Getty Images

A tracking tool installed on many hospitals’ websites has been collecting patients’ sensitive health information—including details about their medical conditions, prescriptions, and doctor’s appointments—and sending it to Facebook.

The Markup tested the websites of Newsweek’s top 100 hospitals in America. On 33 of them we found the tracker, called the Meta Pixel, sending Facebook a packet of data whenever a person clicked a button to schedule a doctor’s appointment. The data is connected to an IP address—an identifier that’s like a computer’s mailing address and can generally be linked to a specific individual or household—creating an intimate receipt of the appointment request for Facebook.

On the website of University Hospitals Cleveland Medical Center, for example, clicking the “Schedule Online” button on a doctor’s page prompted the Meta Pixel to send Facebook the text of the button, the doctor’s name, and the search term we used to find her: “pregnancy termination.”

Clicking the “Schedule Online Now” button for a doctor on the website of Froedtert Hospital, in Wisconsin, prompted the Meta Pixel to send Facebook the text of the button, the doctor’s name, and the condition we selected from a dropdown menu: “Alzheimer’s.”

The Markup also found the Meta Pixel installed inside the password-protected patient portals of seven health systems. On five of those systems’ pages, we documented the pixel sending Facebook data about real patients who volunteered to participate in the Pixel Hunt project, a collaboration between The Markup and Mozilla Rally. The project is a crowd-sourced undertaking in which anyone can install Mozilla’s Rally browser add-on in order to send The Markup data on the Meta Pixel as it appears on sites that they visit. The data sent to hospitals included the names of patients’ medications, descriptions of their allergic reactions, and details about their upcoming doctor’s appointments.

Former regulators, health data security experts, and privacy advocates who reviewed The Markup’s findings said the hospitals in question may have violated the federal Health Insurance Portability and Accountability Act (HIPAA). The law prohibits covered entities like hospitals from sharing personally identifiable health information with third parties like Facebook, except when an individual has expressly consented in advance or under certain contracts.

Neither the hospitals nor Meta said they had such contracts in place, and The Markup found no evidence that the hospitals or Meta were otherwise obtaining patients’ express consent.

“I am deeply troubled by what [the hospitals] are doing with the capture of their data and the sharing of it,” said David Holtzman, a health privacy consultant who previously served as a senior privacy adviser in the U.S. Department of Health and Human Services’ Office for Civil Rights, which enforces HIPAA. “I cannot say [sharing this data] is for certain a HIPAA violation. It is quite likely a HIPAA violation.”

University Hospitals Cleveland Medical Center spokesperson George Stamatis did not respond to The Markup’s questions but said in a brief statement that the hospital “comport[s] with all applicable federal and state laws and regulatory requirements.”

After reviewing The Markup’s findings, Froedtert Hospital removed the Meta Pixel from its website “out of an abundance of caution,” Steve Schooff, a spokesperson for the hospital, wrote in a statement.

As of June 15, six other hospitals had also removed pixels from their appointment booking pages and at least five of the seven health systems that had Meta Pixels installed in their patient portals had removed those pixels.

The 33 hospitals The Markup found sending patient appointment details to Facebook collectively reported more than 26 million patient admissions and outpatient visits in 2020, according to the most recent data available from the American Hospital Association. Our investigation was limited to just over 100 hospitals; the data sharing likely affects many more patients and institutions than we identified.

Facebook itself is not subject to HIPAA, but the experts interviewed for this story expressed concerns about how the advertising giant might use the personal health data it’s collecting for its own profit.

“This is an extreme example of exactly how far the tentacles of Big Tech reach into what we think of as a protected data space,” said Nicholson Price, a University of Michigan law professor who studies big data and health care. “I think this is creepy, problematic, and potentially illegal” from the hospitals’ point of view.

The Markup was unable to determine whether Facebook used the data to target advertisements, train its recommendation algorithms, or profit in other ways.

https://arstechnica.com/?p=1861234


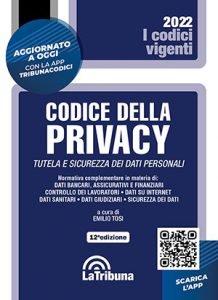
Codice della Privacy

A cura di Emilio Tosi
Pubblicato: maggio 2022
Editore: La Tribuna
Pagine: 1.728
ISBN: 9788829110254
Prezzo: 35,00 euro
XII edizione

“Dalla data dell’entrata in vigore della prima normativa quadro in materia di trattamento dei dati personali – 8 maggio 1997 – ad oggi” – così scrive il curatore dell’opera Emilio Tosi, Professore Associato di Diritto Privato nell’Università di Milano Bicocca, Direttore Diritto Nuove Tecnologie® e Managing Partner di Tosi & Partners High Tech Legal nell’aggiornatissimo Codice recentemente pubblicato per i tipi La Tribuna – “si è progressivamente rafforzata e sviluppata una diffusa cultura della tutela e sicurezza dei dati personali in Italia e nella UE. Il rapido susseguirsi di interventi normativi generali e settoriali in materia ha, però, creato non poche difficoltà operative di interpretazione e coordinamento tanto ai giuristi che agli operatori economici e ai cittadini ormai destinati – tutti – a confrontarsi quotidianamente con tali nuove e delicate problematiche.

Si pensi alle pervasive problematiche poste dal trattamento dei dati personali raccolti mediante piattaforme digitali, motori di ricerca, social network, Internet of Things (IoT), wearables, droni, rilevatori biometrici e last but not least ai big data e al trattamento dei dati genetici.

Tenuto conto della complessità e attualità della materia e della già considerevole elaborazione normativa ad oggi formatasi, si è ritenuto utile – a supporto dell’opera interpretativa del giurista, dell’applicazione aziendale della normativa e della tutela dei diritti della persona fisica – raccogliere in un Codice della Privacy la normativa comunitaria, interna e internazionale inerente la tutela e la sicurezza dei dati personali, unitamente ai più significativi provvedimenti del Garante per la protezione dei dati personali”.

Il Codice si compone di una prima parte generale dedicata alla normativa comune seguita da una corposa parte speciale ordinata in voci alfabetiche di cui si segnalano le voci principali e precisamente: Amministratori di sistema; Autorità garante per la protezione dei dati personali; Autorizzazioni generali per il trattamento dei dati particolari; Autorizzazioni generali al trasferimento dei dati all’estero; Beni culturali e del paesaggio; Carte magnetiche; Casellario giudiziale; Codici deontologici; Contratti telematici, firme elettroniche e firma digitale; Dati anagrafici e stato civile; Dati assicurativi; Dati bancari; Dati biometrici; Dati sulla circolazione stradale; Dati customer care; Dati etichette RFID; Dati finanziari; Dati fiscali; Dati genetici; Dati giudiziari; Dati PMI; Dati sanitari; Dati traffico telefonico e telematico; Fidelity card; Furti di identità; Indagini difensive; Media conciliazione; Misure minime di sicurezza; Pubblica sicurezza; Regolarizzazione dei ricorsi; Semplificazione dei riti civili; Servizi di comunicazione; Servizi di informazione; Telecomunicazioni; Tutela dei lavoratori; Videosorveglianza; Vigilanza privata.

Come noto la disciplina della tutela della riservatezza e protezione dei dati personali è assicurata oggi da un doppio livello normativo:

  • europeo: in forza del Regolamento (UE) 2016/679 del Parlamento europeo e del Consiglio, del 27 aprile 2016, relativo alla protezione delle persone fisiche con riguardo al trattamento dei dati personali, nonché alla libera circolazione di tali dati, c.d. General Data Protection Regulation (di seguito per brevità, “GDPR”);
  • interno: in forza del D. Lgs. 30 giugno 2003, n. 196, c.d. Codice della Privacy (di seguito per brevità, “Codice”) come armonizzato dal D.Lgs. 10 agosto 2018, n. 101 recante disposizioni per l’adeguamento dell’ordinamento nazionale al GDPR.

Tale doppio livello di regolazione della protezione e circolazione dei dati personali è articolato in rapporto gerarchico tra fonti europee sovraordinate e fonti interne sottoordinate.

Riservatezza e protezione dei dati personali sono diritti fondamentali della persona tutelati dall’art. 7 e 8 della Carta dei diritti fondamentali della UE.

Si tenga presente quale criterio ermeneutico generale che l’interprete – in caso di contrasti tra norme o dubbi interpretativi – deve ritenere prevalente la fonte europea sovraordinata – il GDPR – rispetto a quella sottordinata del Codice.

Il Codice è stato, infatti, conservato solo dopo essere stato ampiamente emendato e armonizzato al GDPR in forza del citato D.Lgs. 101/2018 e da ultimo ulteriromente aggiornato dalla L.  205/2021.

Non a caso gli artt. 1 e 2 del Codice armonizzato recitano quanto segue:

– Art. 1 Oggetto: Il trattamento dei dati personali avviene secondo le norme del Regolamento (UE) 2016/679 del Parlamento europeo e del Consiglio, del 27 aprile 2016, di seguito «Regolamento», e del presente Codice, nel rispetto della dignita’ umana, dei diritti e delle liberta’ fondamentali della persona;

Art. 2. Finalità: Il presente codice reca disposizioni per l’adeguamento dell’ordinamento nazionale alle disposizioni del regolamento.

Il Codice armonizzato ha, fra l’altro, abrogato a far data dal 19/9/2018, ampie parti della normativa italiana previgente che ha assunto, quindi, carattere residuale e recessivo rispetto a quella prevalente europea.

Il GDPR come noto è divenuto pienamente applicativo a far data dal 25 maggio 2018 ed è divenuto rapidamente un legal benchmark globale per la protezione dei dati personali.

Unica criticità da stigmatizzare: la tanto attesa riforma della privacy nelle comunicazioni elettroniche – c.d. e-privacy – che completerà il quadro normativo europeo in materia di protezione dei dati personali – riformando la Direttiva CE 2002/58 aggiornata dalla Direttiva CE 209/136 – è tutt’ora in corso.

L’aumento esponenziale del trattamento massivo e pervasivo dei dati personali nella società della sorveglianza digitale richiede da tempo anche tale ultimo tassello normativo”.

Il presente Codice – di sicuro interesse per Data Protection Officer, Giuristi di Impresa, Avvocati, Magistrati, Notai, Docenti Universitari, studenti di materie giuridiche ed appassionati della materia – è aggiornato alla G.U. n. 110 del 12/5/2022.

Emilio Tosi, è Professore Associato Diritto Privato e Diritto delle Nuove Tecnologie, Università degli Studi di Milano Bicocca.

https://www.key4biz.it/codice-della-privacy-3/406790/