New ‘SharkBot’ Android Banking Malware Hitting U.S., UK and Italy Targets

A new Android banking trojan has been found, targeting international banks from the United Kingdom and Italy (including in the U.S.). and five different cryptocurrency services. Twenty-two instances have been discovered, but more are expected.

The malware, first detected at the end of October 2021, appears to be new and still being developed. It was discovered by Cleafy, a Milan, Italy-based online fraud detection and prevention firm. Cleafy calls it ‘SharkBot’, named after the frequency of the word ‘sharked’ in its binaries.

SharkBot is not found in Google’s official marketplace. This means it must be sideloaded by delivering the APK to the device and ensuring it is manually loaded. In a technical analysis of the malware, Cleafy notes that it poses as a legitimate application using common names and icons.

If the deception succeeds and the malware is installed, it immediately attempts to enable Android’s Accessibility Services by delivering fake pop-ups to the victim – such as ‘Allow Media Player to have full control of your device’. If this is successful, SharkBot has all the permissions it needs. 

Once accepted the malware can enable keylogging (to steal typed credentials), intercept SMS messages (to circumvent MFA), deliver overlay attacks (to steal login credentials and credit card information) and remotely control the device because permissions were granted via the fake pop-up. “Basically,” comments Corey Nachreiner, CSO at WatchGuard Technologies, “the malicious Accessibility Services can read anything a user can read and can recreate any action a user can on the device.”

Notably, SharkBot also attempts a relatively novel technique known as an Automatic Transfer Systems (ATS) attack. “This technique has been seen recently from other banking trojans, such as Gustuff,” explains Cleafy. “ATS is an advanced attack technique (fairly new on Android) which enables attackers to auto-fill fields in legitimate mobile banking apps and initiate money transfers from the compromised devices.” 

The ATS functionality is contained in a module downloaded separately from the C2. “Given its modular architecture,” comments Cleafy, “we don’t exclude the existence of botnets with other configurations and targets.”

[ READ: Android Trojan Targets Banks, Crypto-Currencies, e-Commerce ] 

The assumption is that ATS is used by SharkBot to bypass the behavioral detection measures used by many financial institutions. If ATS is used on what is a trusted device, a ‘new device enrollment’ phase is not necessary, SMS-based MFA can be bypassed,  and behavioral biometrics are not effective.

Although relatively few instances of SharkBot have been discovered in the wild, Cleafy suspects that the threat will grow. This is partly because it is new, and apparently still being developed.  

“The implications of becoming infected with SharkBot could be severe, so it’s important,” says Nachreiner, “to avoid being infected altogether.” This is not yet easy. The malware is new and not well detected by existing detection means. Apart from the DGA for its C2s, it also uses anti-analysis techniques including obfuscated strings and emulator detection.

The best solution is to avoid side-loading religiously. Without 100% certainty in the authenticity of the application and the validity of its source, simply do not install it. 

Related: Android Banking Trojan ‘Vultur’ Abusing Accessibility Services

Related: Android Trojan Targets Banks, Crypto-Currencies, e-Commerce

Related: Automatic Transfer System Evades Security Measures, Automates Bank Fraud

view counter

Kevin Townsend is a Senior Contributor at SecurityWeek. He has been writing about high tech issues since before the birth of Microsoft. For the last 15 years he has specialized in information security; and has had many thousands of articles published in dozens of different magazines – from The Times and the Financial Times to current and long-gone computer magazines.

Previous Columns by Kevin Townsend:
Tags:

https://www.securityweek.com/new-%E2%80%98sharkbot%E2%80%99-android-banking-malware-hitting-us-uk-and-italy-targets


Privacy e wearable, il lato oscuro dei dispositivi indossabili

Rubrica settimanale SosTech, frutto della collaborazione tra Key4biz e SosTariffe. Per consultare gli articoli precedenti, clicca qui.

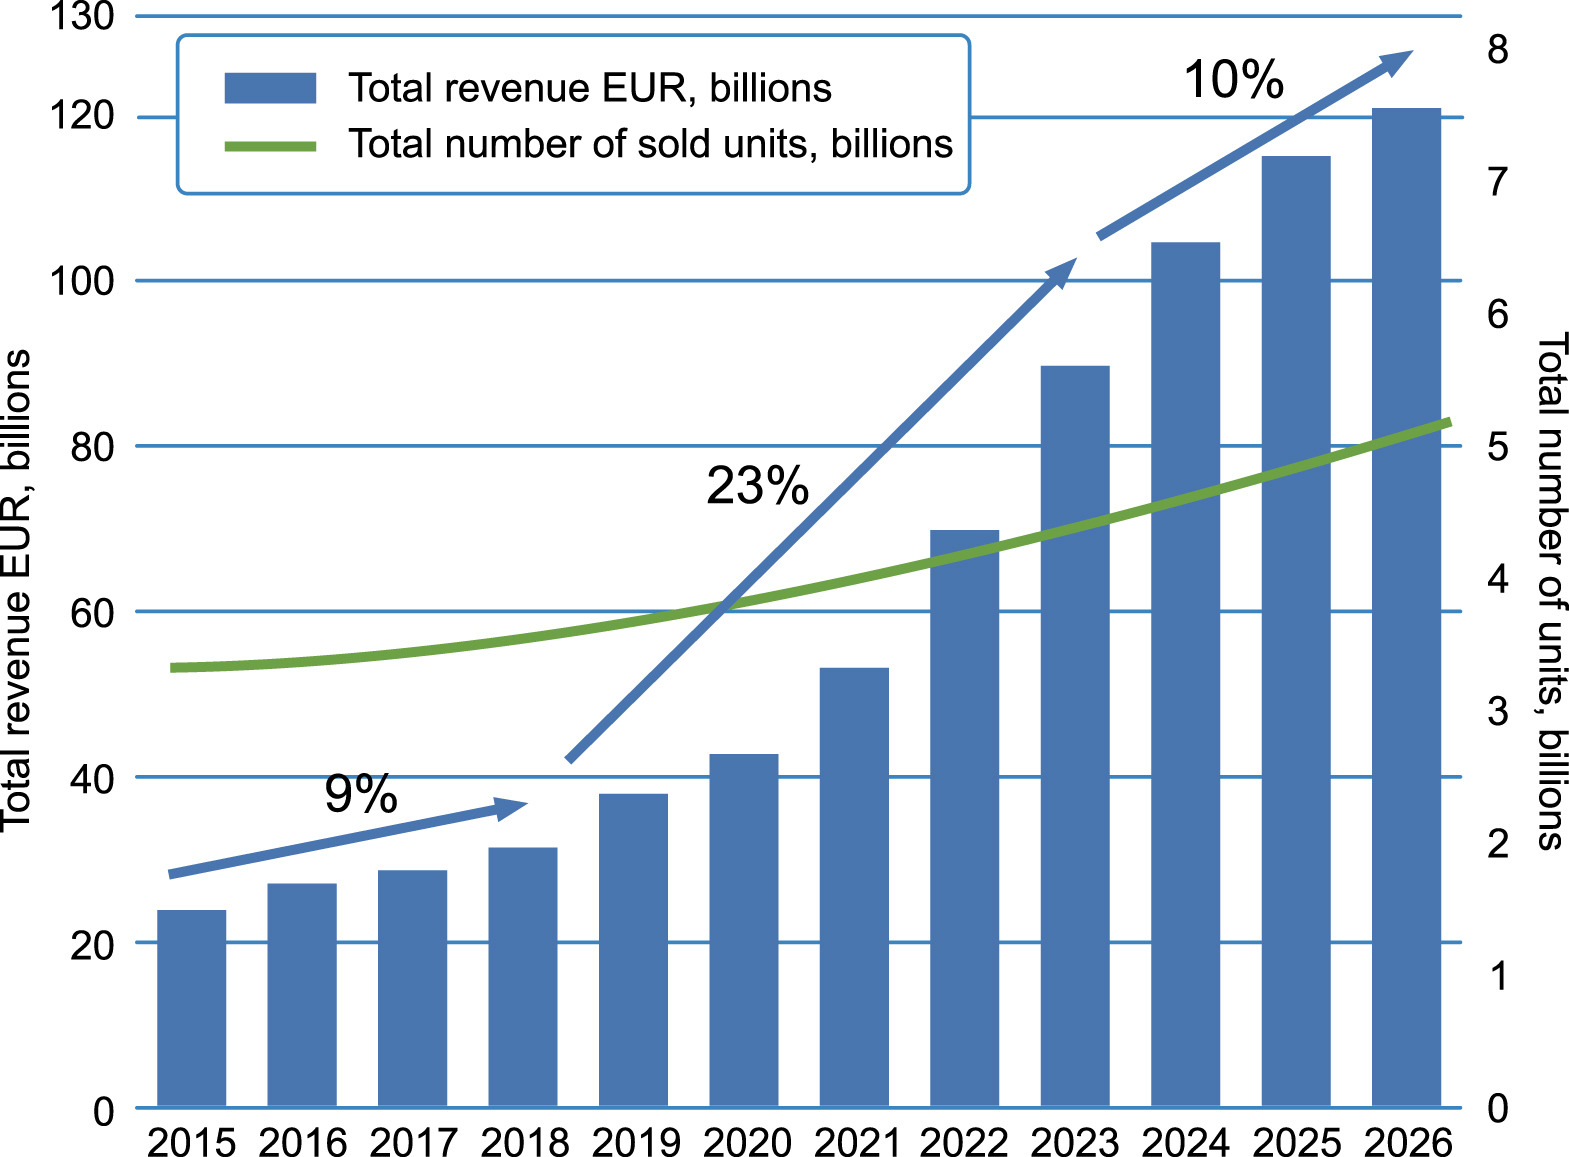
Fra tutte le profezie futuribili di qualche decennio fa, forse quella dei wearable era la più scontata. Non c’è quasi romanzo o film di fantascienza che non mostri il protagonista interagire con un orologio digitale, degli occhiali speciali o altri dispositivi nati per essere indossati per accedere a una varietà di funzioni. Puntualmente, il wearable, negli anni passati, è diventato realtà, anche se accompagnato da una dose di scetticismo superiore a quella degli altri oggetti (smartphone in primis) che definiscono le nostre nuove routine. Ma pazienti e ostinati, anche gli indossabili si sono conquistati a poco a poco la nostra fiducia, e ci accompagnano durante le nostre sessioni di corsa o misurano quanti piani di scale abbiamo fatto, controllano il battito cardiaco e ci consentono perfino di telefonare o interagire con messaggi. L’implementazione di sensori biometrici sempre più avanzati unito all’arrivo di speciali e-SIM per Internet mobile (su SOSTariffe.it si possono trovare le più convenienti) ha aperto al mondo gli smartwatch che si vedono sempre più spesso al polso non solo degli sportivissimi. I numeri parlano chiaro: il mercato globale delle tecnologie indossabili passerà, secondo le previsioni, dai 116,2 miliardi del 2021 ai 265,4 miliardi del 2026, in Europa da 2,514 miliardi a 5,950 miliardi. Nel 2022, si calcola che un miliardo di consumatori potranno accedere a dispositivi indossabili. Eppure, ci sono anche degli aspetti sui quali è legittimo essere più perplessi.

Privacy e wearable: chi controlla i nostri spostamenti?

Il primo, naturalmente, è legato alla grande questione degli ultimi decenni: la privacy. Mentre le grandi società hi-tech, incalzate dai governi, fanno rapidamente dietrofront rispetto alle condotte adottate tradizionalmente – Facebook cambia nome e promette una maggior cura dei dati sensibili rispetto a quella (disastrosa) della gestione fino ad oggi, Apple fa infuriare i produttori di app che fatturano tramite la pubblicità inserendo nel sistema, alla prima apertura, un avviso che permette all’utente di scegliere se e quali dati fornire – i dispositivi indossabili appaiono potenzialmente molto efficaci per il controllo di ogni movimento dell’utente. Avere sempre il GPS attivo è molto utile se vogliamo misurare le calorie che perdiamo ogni giorno, ma allo stesso tempo in teoria rivela i nostri spostamenti, le nostre abitudini, i luoghi che frequentiamo più spesso. Sapere chi controlla i nostri dati, e che politica adotta riguardo ad essi, è essenziale, e non si può dire che fino ad ora i big dell’industria digitale siano stati un esempio di correttezza e trasparenza. Ma c’è anche altro.

Privacy e wearable: il “digital divide” della salute

Basta guardare una qualsiasi presentazione di smartwatch per capire che il fattore su cui le aziende stanno puntando maggiormente negli ultimi tempi non è tanto la potenzialità per lo sport e l’attività fisica, ma per il controllo medico. La pandemia ha ulteriormente acuito l’attenzione alla propria salute, e il ricorso massiccio ad apparecchi come i saturimetri per controllare l’ossigenazione del sangue ha convinto anche i più scettici sull’importanza di non perdere di vista i propri dati vitali; i wearable permettono proprio questo grazie a funzionalità sempre più sofisticate, che consentono di effettuare un elettrocardiogramma al volo, valutare aritmie cardiache o respiratorie, studiare i cicli del sonno e in futuro chissà che altro. Ma, allo stesso tempo, si tratta di dispositivi costosi, a volte molto; e se ormai uno smartphone costa poco più di un centinaio di euro ed è quasi indispensabile per chiunque anche solo per motivi di comunicazione, uno smartwatch è in media più costoso, se di buona qualità, e appare ancora fondamentalmente uno sfizio. In altre parole, è un regalo per benestanti, anche per la maggior cura verso sé stessi che di solito hanno le persone con più denaro e una migliore educazione; un dato che rischia di acuire ulteriormente il già ampio gap tra chi può permettersi cure di qualità e che invece, per reddito e istruzione, ne è tagliato fuori.

Un recente studio ha mostrato che le persone con uno status socioeconomico inferiore hanno sovente una minore alfabetizzazione per quanto riguarda la “salute elettronica”, in quanto senza denaro sufficiente per comprarsi uno di questi dispositivi o senza le conoscenze necessarie per utilizzarli nel modo migliore. Il problema è che la tutela della salute si concentra sempre di più sulla digitalizzazione dei comportamenti e della raccolta dei dati, grazie all’introduzione di sistemi che permettono di monitorare le condizioni dei pazienti anche quando si trovano a casa e lontano da un istituto di cura, senza contare i registri digitali per le cartelle cliniche e un sempre maggior supporto alla telemedicina, che allo stesso tempo rende possibile effettuare interventi a distanza ma richiede l’adozione di apparecchiature dal costo non indifferente. Tutto questo rischia di tradursi in una cura della salute sempre più sofisticata per i ricchi e viceversa un’attenzione molto minore al benessere di chi ha meno mezzi.

Ma gli “indossabili“ ci proteggono

Naturalmente, è ovvio che questi motivi di perplessità vadano analizzati con la massima attenzione ma senza che questo significhi una mancata adozione dei wearable e dei loro vantaggi, anche perché se c’è una cosa che la storia insegna in materia di novità tecnologiche è che è molto difficile tornare indietro; perfino ciò che sembrava un flop epocale qualche anno fa, i Google Glasses, non cessa di rispuntare sotto altra forma, come i Ray-Ban Stories di Facebook (ora Meta), ed è assai probabile che ci abitueremo anche all’utilizzo di occhiali digitali anche se ci vediamo benissimo.

Non sempre, inoltre, la tecnologia segue i percorsi che avevamo previsto. Sono sempre di più le startup dedicate alla sicurezza sul lavoro tramite tecnologia indossabile che raccolgono investimenti miliardari, man mano che i dispositivi diventano più piccoli, meno cari e più leggeri, e diventano un aiuto indispensabile per chi svolge lavori di precisione o molto pericolosi, con sensori in grado di indicare un livello di stress termico pericoloso, la perdita di attenzione in un momento cruciale o un’eccessiva sollecitazione di una parte del corpo. I wearable sono indubbiamente qui per restare, bisognerà non smettere di fare attenzione a come gestirli.

https://www.key4biz.it/privacy-e-wearable-il-lato-oscuro-dei-dispositivi-indossabili/382714/


Zoom Patches High-Risk Flaws in Meeting Connector, Keybase Client

Video messaging technology giant Zoom has shipped patches for high-severity vulnerabilities that expose enterprise users to remote code execution and command injection attacks.

The company released multiple security bulletins to warn of the risks and called special attention to a pair of “high-risk” bugs affecting its on-prem meeting connector software and the popular Keybase Client.

“The network proxy page on the web portal for the [affected] products fails to validate input sent in requests to set the network proxy password. This could lead to remote command injection by a web portal administrator,” Zoom said in a note.

The CVE-2021-34417 carries a CVSS Base Score of 7.9, and affects multiple Zoom software components — Zoom On-Premise Meeting Connector Controller, Zoom On-Premise Meeting Connector MMR, Zoom On-Premise Recording Connector, Zoom On-Premise Virtual Room Connector. 

[ READ: Vulnerability Allowed Attackers to Join Zoom Meetings ]

A second high-severity bulletin was also released with patches for CVE-2021-34422, a path traversal bug affecting Keybase Client for Windows.

From Zoom’s advisory:

“The Keybase Client for Windows before version 5.7.0 contains a path traversal vulnerability when checking the name of a file uploaded to a team folder. A malicious user could upload a file to a shared folder with a specially crafted file name which could allow a user to execute an application which was not intended on their host machine.” 

“If a malicious user leveraged this issue with the public folder sharing feature of the Keybase client, this could lead to remote code execution.”

Zoom said the issue was fixed in the 5.7.0 Keybase Client for Windows release.  

Zoom’s security response team also shipped patches for a medium-risk bug (CVE-2021-34420) in the Zoom Client for Meetings installer.  “The Zoom Client for Meetings for Windows installer before version 5.5.4 does not properly verify the signature of files with .msi, .ps1, and .bat extensions. This could lead to a malicious actor installing malicious software on a customer’s computer,” the company warned.

The Zoom software does not have an automatic update mechanism.  Users are urged to manually check for software updates within the Zoom client.

Related: Remote Code Execution Flaw in Palo Alto GlobalProtect VPN

Related: Adobe Patches Critical RoboHelp Server Security Flaw

Related: Zero-Days Under Attack: Microsoft Plugs Exchange Server, Excel Holes

view counter

Ryan Naraine is Editor-at-Large at SecurityWeek and host of the popular Security Conversations podcast series. He is a journalist and cybersecurity strategist with more than 20 years experience covering IT security and technology trends.
Ryan has built security engagement programs at major global brands, including Intel Corp., Bishop Fox and Kaspersky GReAT. He is a co-founder of Threatpost and the global SAS conference series. Ryan’s career as a journalist includes bylines at major technology publications including Ziff Davis eWEEK, CBS Interactive’s ZDNet, PCMag and PC World.
Ryan is a director of the Security Tinkerers non-profit, and a regular speaker at security conferences around the world.
Follow Ryan on Twitter @ryanaraine.

Previous Columns by Ryan Naraine:
Tags:

https://www.securityweek.com/zoom-patches-high-risk-flaws-meeting-connector-keybase-client


U.S. Gov Announces Support for ‘Paris Call’ Cybersecurity Effort

United States Vice President Kamala Harris on Wednesday formally announced support for the Paris Call for Trust and Security in Cyberspace, an international collaborative initiative aimed at advancing cybersecurity.

Issued in 2018, the Paris Call details nine principles to improve stability in cyberspace through global collaboration, and has been already signed by 79 countries.

The principles promoted by the Call include:

  • Protecting individuals and infrastructure
  • Protecting against activity that affects the availability of the Internet
  • Protecting the electoral process
  • Protecting intellectual property
  • Preventing the proliferation of malware and nefarious practices
  • Improving the security of digital processes, products and services
  • Strengthening an advanced cyber hygiene
  • Preventing non-state actors from hacking back
  • Promoting international norms in cyberspace

Through supporting the Call, the United States said it will commit to advancing cybersecurity and preserving an open and reliable Internet.

Vice President Harris said the U.S. will work with France and other countries, as well as with private companies and civil society globally to promote responsible behavior in cyberspace.

“This includes working with like minded countries to attribute and hold accountable States that engage in destructive, disruptive, and destabilizing cyber activity,” according to a White House statement.

The decision to support the Call falls in line with the U.S. government’s current effort to improve cybersecurity for both individuals and businesses and to accelerate international cooperation to combat cybercrime.

Related: US Bans China Telecom Over National Security Concerns

Related: Nations Vow to Combat Ransomware at US-Led Summit

Related: US to Curb Hacking Tool Exports to Russia, China

view counter

Ionut Arghire is an international correspondent for SecurityWeek.

Previous Columns by Ionut Arghire:
Tags:

https://www.securityweek.com/us-gov-announces-support-paris-call-cybersecurity-effort


Privacy, il 25 novembre Forum Nazionale dei DPO e Responsabili della Conservazione (RDC)

Giovedì 25 novembre si terrà il Forum nazionale dei DPO e Responsabili della Conservazione ideato e promosso da ANORC organizzato da Digital & Law e trasmesso gratuitamente in diretta streaming su piattaforma DIG.eat.

Il Forum intende proprio favorire un confronto pratico su problemi di grande rilevanza tra Data Protection Officer (DPO) e Responsabili della Conservazione (RDC) invitati a confrontarsi sull’esperienza maturata nel campo, per quanto attiene nello specifico la gestione di attacchi informatici e data breach. L’incontro sarà l’occasione per condividere le best practices utili a gestire e comunicare in maniera adeguata gli eventi legati alle minacce più comuni, in ambito pubblico e privato.

L’evento organizzato è patrocinato da: AgID, ANDIP, Clusit, CNA, CNA Professioni, Galileo, Istituto Italiano Privacy, Privacy Italia, PROCEDAMUS, PROTECH, SIT, SOS Archivi, THEMIS.

Sull’evento il Centro di ricerca ReCEPL e la cattedra Jean Monnet Protech ha dichiarato: “L’idea della protezione dei dati personali non si limita al loro trattamento legal compliance, ma si estende propriamente alla loro sicurezza, intesa come protezione dagli attacchi informatici. Il fenomeno del data breach colpisce tutte le realtà imprenditoriali e professionali: è necessario esserne consapevoli e mettere in campo tutti gli strumenti idonei ad evitarlo. In ragione di ciò l’evento Anorc rappresenta un momento indispensabile per l’acquisizione di competenze essenziali ai fini della salvaguardia del patrimonio dati funzionale all’esercizio della propria attività”.

L’associazione Galileo ha fatto sapere che “sostiene l’evento di Anorc perché lo ritiene interlocutore di primo livello sul tema della protezione da minacce informatiche di Pubblica amministrazione e aziende. Il think tank con sede nel Principato di Monaco è impegnato nello studio e nell’analisi di questa delicata e centrale issue”.

Il Centro ricerca Themis ha motivato così la propria adesione: “Aderiamo con piacere all’iniziativa di Anorc perché affronta concretamente la sicurezza informatica con una pluralità di competenze, che riteniamo l’approccio vincente in questa sfida- ha dichiarato Isabella Corradini, presidente del Centro Ricerche Themis, che sarà anche tra i relatori- Fare crescere la consapevolezza digitale è oggi fondamentale se vogliamo contrastare le minacce informatiche in modo efficace, lo dimostra il fatto che molti attacchi sono legati al fattore umano. Ecco perché è importante partecipare all’iniziativa Anorc“.

Forum Nazionale dei DPO e Responsabili della Conservazione (RDC): programma e come seguire il forum

SESSIONE MATTUTINA
Dalle 10.00 alle 12.30

INTRODUCE

  • Dott. Alessandro Selam – Direttore di ANORC

MODERA

  • Avv. Andrea Lisi – Presidente di ANORC Professioni, Titolare Studio Legale Lisi, coordinatore di Digital & Law Department

INTERVENGONO
(in ordine alfabetico)

  • Dott. Raffale Barberio – Fondatore e Editor in Chief di Key4biz, è presidente di Privacy Italia e direttore dell’International Cybersecurity Observatory
  • Esponente del Garante per la protezione dei dati personali*
  • Dott.ssa Isabella Corradini – Psicologa sociale e criminologa, è esperta di sicurezza (safety e cybersecurity) con approccio basato sul fattore umano e di “digital awareness”, Presidente di Themis, centro ricerche socio-psicologiche e criminologico-forensi
  • Prof. Corrado Giustozzi – Senior Cyber Security strategist
  • Esponente del Gruppo Privacy nell’ambito del Nucleo Speciale Tutela Privacy e Frodi Tecnologiche della Guardia di Finanza*
  • Dott. Massimiliano Pucciarelli – Presidente del Comitato Direzione Tecnica – gara Consip SPC Cloud lotto1″ -COMMUNITY CLOUD DELLA PA presso l’Agenzia per l’Italia Digitale

SESSIONE POMERIDIANA
Dalle 15.00 alle 18.00

MODERANO:

  • Avv. Luigi Foglia – Segretario Generale di ANORC, esperto in diritto dell’informatica e archivi digitali
  • Avv. Sarah Ungaro – Vice presidente di ANORC Professioni, esperta in diritto dell’informatica e privacy

Dalle 15:00 alle 18:00

INTERVENGONO:

  • Avv. Laura Ferola* – DPO del Garante per la protezione dei dati personali
  • Avv. Raffaella Vai – DPO dell’Agenzia per l’Italia Digitale (AgID)
  • Dott.ssa Stefania Vitucci* – DPO della Presidenza del Consiglio dei Ministri

Confronto tra i Responsabili della Conservazione (RDC), Data Protection Officer (DPO), Responsabili della Gestione Documentale (RGD) e Responsabili Transizione Digitale (RTD) delle Pubbliche Amministrazioni e iscritti ad ANORC.

*Relatori invitati e in attesa di conferma

La partecipazione è gratuita previa iscrizione alla piattaforma digeat.it.

Per partecipare al forum clicca qui.

https://www.key4biz.it/privacy-il-25-novembre-forum-nazionale-dei-dpo-e-responsabili-della-conservazione-rdc/381589/


AI, Wiewiórowski (EDPS) ‘Ue non ancora pronta per il riconoscimento facciale’

Il Garante Privacy europeo Wojciech Wiewiórowski (European Data Protection Supervisor) ritiene che l’Europa non sia ancora pronta per il riconoscimento facciale per il controllo pubblico delle persone.

“La società europea non è ancora pronta”, ha detto Wojciech Wiewiórowski told in un’intervista a Politico. 

La tecnologia e le sue applicazioni hanno diviso l’Europa. La proposta Ue di legislazione sull’AI mette al bando la maggior parte delle applicazioni di identificazione biometrica da remoto, a partire dal riconoscimento facciale nei luoghi pubblici dalle forze dell’ordine, ma fa delle eccezioni per combattere la criminalità “grave”, che potrebbe includere il terrorismo.

Leggi anche: Intelligenza artificiale affidabile ed etica. Le regole dell’Ue. Vestager: “Da noi no sorveglianza di massa”

Siamo pronti per un controllo permanente?

Chi sostiene l’uso della tecnologia, vale a dire le forze dell’ordine e alcuni governi più attenti alla sicurezza, dice che la polizia ha bisogno della tecnologia per catturare i criminali. Ma attivisti per la privacy, alcuni legislatori europei e lo stesso Wiewiórowski sono invece a favore di un divieto assoluto.

L’uso della tecnologia “trasformerebbe la società, trasformerebbe i nostri cittadini, trasformerebbe i luoghi in cui viviamo, in luoghi in cui siamo permanentemente riconoscibili… Non sono sicuro che la società sia davvero pronta per questo”, dice Wiewiórowski.

Attenzione alle deroghe

L’organizzazione da lui guidata, l’EDPS, è l’autorità interna per la protezione dei dati dell’UE, che garantisce che le singole agenzie nazionali dell’UE si attengano alle rigide norme sulla privacy del continente. Fornisce inoltre consulenza alla Commissione europea sulle sue iniziative legislative.

Wiewiórowski ha lanciato un monito: consentire delle eccezioni all’uso delle tecnologie potrebbe aprire la porta a tutti i tipi di sorveglianza, compreso il riconoscimento emotivo, e potrebbe essere aperto anche alle società private.

“Molti politici credono che l’uso di queste tecnologie debba essere consentito ad altre organizzazioni, altre entità, il che è un po’ sorprendente per me in realtà”, ha detto Wiewiórowski.

Essere più specifici

Wiewiórowski ha inoltre sottolineato che i legislatori devono ancora definire che cosa intendono esattamente per intelligenza artificiale che vogliono regolare, un fattore che potrebbe avere un peso significativo su quali aziende e quali applicazioni saranno regolamentate.

L’appello di Wiewiórowski è stato raccolto dai paesi della Ue, che a loro volta hanno chiesto definizioni più precise su quale tipo di intelligenza artificiale debba ricadere sotto la legislazione europea. Danimarca, Francia, Italia e altri paesi hanno lamentato che l’AI Act è troppo ampio, e rischia di imbrigliare modelli statistici di base in una regolamentazione pesante.

Riferendosi all’ampia rete della legislazione, Wiewiórowski ha affermato: “Stiamo usando la nozione di marketing dell’intelligenza artificiale per le tecnologie e sappiamo che la maggior parte di queste tecnologie non sono in realtà così intelligenti”.

“Dobbiamo stare più attenti a quello che pensiamo di ricomprendere e quello che resterà fuori dalla regolazione. Se qualcosa è sofisticato non significa che si tratti di intelligenza artificiale”, ha detto aggiungendo che in base all’attuale bozza di legge, sistemi che controllano i limiti di velocità in autostrada (autovelox ndr) rientrerebbero nella definizione di intelligenza artificiale.

https://www.key4biz.it/ai-wiewiorowski-edps-ue-non-ancora-pronta-per-il-riconoscimento-facciale/380538/


Employees pleaded with Facebook to stop letting politicians bend rules

One hundred cardboard cutouts of Facebook founder and CEO Mark Zuckerberg stand outside the US Capitol in Washington, DC, April 10, 2018.
Enlarge / One hundred cardboard cutouts of Facebook founder and CEO Mark Zuckerberg stand outside the US Capitol in Washington, DC, April 10, 2018.
Saul Loeb | Getty Images

Facebook’s senior executives interfered to allow US politicians and celebrities to post whatever they wanted on its social network despite pleas from employees to stop, leaked internal documents suggest.

Employees claim in the documents that while Facebook has long insisted that it is politically neutral, it allowed rightwing figures to break rules designed to curb misinformation and harmful content, after being stung by accusations of bias from conservatives.

In September 2020, just ahead of the US presidential election, the author of an internal memo wrote that “director-level employees” had “written internally that they would prefer to formally exclude political considerations from the decision-making process.”

The author called for the company’s leadership to create a “firewall” around its content moderation teams to stop this from happening and to make sure Facebook did not keep up or take down posts because of external political and media pressure.

In another internal note, dated December 2020, an employee claimed that Facebook’s public policy team blocked decisions to take down posts “when they see that they could harm powerful political actors.”

“In multiple cases the final judgment about whether a prominent post violates a certain written policy are made by senior executives, sometimes Mark Zuckerberg,” the author added, referring to Facebook’s chief executive. Parts of the note were previously reported by BuzzFeed.

In a further example from 2019, Zuckerberg was alleged to have been personally involved in a decision to allow a video that made the false claim that abortion is “never medically necessary.”

The post, which had been taken down by a moderator, was reinstated following complaints by Republican politicians, the document said.

The documents, part of a wider cache dubbed the Facebook Papers, were disclosed to US regulators and provided to Congress in redacted form by the legal counsel of whistleblower Frances Haugen. A consortium of news organisations, including the Financial Times, has obtained the redacted versions received by Congress.

Facebook declined to respond to queries about the outcome of any discussions about separating its content team from the policy and communications teams.

Joe Osborne, a Facebook spokesperson, said: “At the heart of these stories is a premise which is false. Yes, we’re a business and we make profit, but the idea that we do so at the expense of people’s safety or wellbeing misunderstands where our own commercial interests lie. The truth is we’ve invested $13bn and have over 40,000 people to do one job: keep people safe on Facebook.”

Staff told to aim for ‘“unimpeachable neutrality”

A former Facebook executive told the FT that Zuckerberg had long told staff to aim for what he called “unimpeachable neutrality.”

This was important particularly around US political groups, employees were told, because the company did not want to be accused of breaking campaign rules by giving a donation in kind.

But three other former employees said they had observed how Facebook applied its own rules in an inconsistent and haphazard way, with special treatment for celebrities.

One former integrity team employee said: “For the people running Facebook, it seems like they care much more about not appearing biased than actually not being biased. Often their efforts at the former make the latter worse.”

https://arstechnica.com/?p=1807122


Organizations Can Now Try Out End-to-End Encrypted Microsoft Teams Calls

Microsoft Teams end-to-end encryption (E2EE)

Microsoft this week announced that organizations can now enable their employees to make one-to-one calls on Teams that are protected by end-to-end encryption.

First announced at the tech giant’s Ignite event in March, end-to-end encryption (E2EE) for one-to-one Teams calls is now rolling out to public preview. Organizations can take advantage of the new capability, but IT admins and users will have to manually enable it.

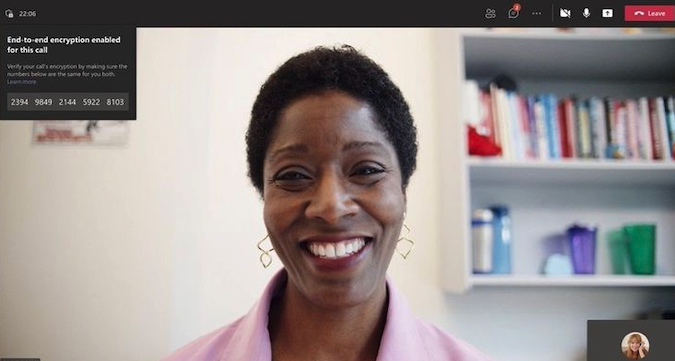
When E2EE is used, conversations are encrypted in a way that prevents anyone, including Microsoft, from intercepting them. However, at this point, only the real-time media flow, which includes video and voice data, is encrypted end-to-end, and the users on both ends of the call will need to enable it.

E2EE is available for Teams on Windows, macOS, Android and iOS, and once it has been enabled for an account it can be used across all of a user’s devices. An end-to-end encryption indicator is displayed during a call so that the user knows their conversation is protected.

If users need to use Teams features that are not covered by end-to-end encryption — this includes recording, live caption and transcription, call transfer and merge, and group calls — they have to temporarily disable E2EE.

“In normal call flows, negotiation of the encryption key occurs over the call signaling channel. In an end-to-end encrypted call, the signaling flow is the same as a regular one-to-one Teams call. However, Teams uses DTLS to derive an encryption key based on per-call certificates generated on both client endpoints. Since DTLS derives the key based on client certificates, the key is opaque to Microsoft. Once both clients agree upon the key, the media begins to flow using this DTLS-negotiated encryption key over SRTP,” Microsoft explained.

It added, “To protect against a man-in-the-middle attack between the caller and callee, Teams derives a 20-digit security code from the SHA-256 thumbprints of the caller’s and callee’s endpoint call certificates. The caller and callee can validate the 20-digit security codes by reading them to each other to see if they match. If the codes don’t match, then the connection between the caller and callee has been intercepted by a man-in-the-middle attack. If the call has been compromised, users can terminate the call manually.”

Microsoft noted that even though E2EE is currently only available for one-to-one calls, other features such as group calls and chats are still protected by Microsoft 365 encryption. The company plans on adding E2EE to online meetings as well at some point in the future.

Microsoft has shared instructions on how end-to-end encryption can be enabled for Teams running on desktop and mobile devices.

Related: Zoom Introduces End-to-End Encrypted Phone Calls

Related: Facebook Adds End-to-End Encryption to Calls in Messenger

view counter

Eduard Kovacs (@EduardKovacs) is a contributing editor at SecurityWeek. He worked as a high school IT teacher for two years before starting a career in journalism as Softpedia’s security news reporter. Eduard holds a bachelor’s degree in industrial informatics and a master’s degree in computer techniques applied in electrical engineering.

Previous Columns by Eduard Kovacs:
Tags:

http://feedproxy.google.com/~r/securityweek/~3/BLr9ZV52f_Q/organizations-can-now-try-out-end-end-encrypted-microsoft-teams-calls


Snap’s Stock Drops as iPhone Privacy Controls Pinch Ad Sales

Snapchat’s corporate parent disclosed Thursday that its ad sales are being hurt by a privacy crackdown that rolled out on Apple’s iPhones earlier this year, raising investor fears that the app’s financial growth is going into a tailspin.

The revelation in Snap Inc.’s third-quarter earnings report sparked a sell-off in after-hours trading that could foreshadow one of the biggest one-day drops in the company’s stock since it went public in 2017.

Snap’s shares plunged by nearly 22% in Thursday’s extended trading. If that decrease is mirrored in Friday’s regular trading session, it will approach the stock’s previous one-day nadir in May 2018 when its price also plummeted by nearly 22%. A decline of that magnitude would wipe out nearly $30 billion in shareholder wealth.

The alarms set off by Snap’s disappointing performance could foreshadow troubles for other apps that may be having more problems tracking their users online activities because of an Apple update to the iPhone’s iOS software released in April.

The change blocks online tracking on iPhones unless a user grants explicit permission to do so, making it more difficult for companies that sell ads based on the information they collect about people’s interests and location.

In a statement, Snap CEO Evan Spiegel said the Santa Monica, California, company has had to recalibrate its operations to “navigate significant headwinds, including changes to the iOS platform that impact the way advertising is targeted.”

Facebook, an outspoken critic of Apple’s new privacy controls, had already told investors that its ad sales could suffer because of the change, but Snap’s results indicated the blow may be even bigger than Wall Street anticipated. Facebook’s shares shed more than 4% in Thursday’s extending trading. The social networking company is scheduled to release its latest quarterly results Monday.

Snap reported revenue of $1.07 billion for the July-September period, a 57% increase from the same time last year, but that was about $30 million below the projections of Wall Street analysts who steer investor expectations.

Perhaps even more troubling to investors, Snap predicted its revenue for the current quarter will range from $1.17 billion to $1.21 billion. Analysts had been forecasting revenue of $1.36 billion, according to FactSet.

Related: Apple Moving Forward on App Privacy, Despite Pushback

Related: Facebook Fails in Bid to Derail $15 Bn Privacy Suit

Related: Apple CEO Escalates Battle With Facebook Over Online Privacy

view counter

Previous Columns by Associated Press:
Tags:

http://feedproxy.google.com/~r/securityweek/~3/C2Xr0e_c5Lk/snaps-stock-drops-iphone-privacy-controls-pinch-ad-sales


Data Privacy Compliance Startup CYTRIO Launches With $3.5 Million in Funding

Data privacy compliance startup CYTRIO this week announced its launch with $3.5 million in seed funding from Dreamit Ventures, Food Retail Ventures and Rockwood Group, as well as angel investors.

CYTRIO was founded by Vijay Basani (chief executive officer), Pankaj Parekh (chief privacy officer), and Darshan Joshi (chief technology officer), who collectively have 50 years of experience in data, privacy and security. Basani previously founded WebManage Technologies (acquired by NetApp), AppIQ (acquired by HP), and Cygilant.

The company offers a solution that simplifies and automates data privacy management for mid-sized enterprises, arguing that “solutions designed for large companies are not suitable for mid-market organizations due to deployment complexity, long time-to-value, and a need for dedicated privacy teams.”

CYTRIO’s product is designed to automatically discover personal information across cloud and on-premises stores, orchestrate data subject access requests, and give customers control over their data.

“Today, we launch CYTRIO to enable mid-size companies to comply with numerous privacy regulations, while building customers’ trust that is essential to thrive in today’s digital economy,” said Basani.

“Our mission to deliver an easy-to-deploy SaaS privacy rights management solution will help mid-market enterprises swiftly and cost-effectively comply with data privacy regulations with minimal resources. We are leveling the playing field for mid-sized enterprises to compete and thrive in the data-driven digital economy, where consumers have control of their private, personal information (PI),” he added.

Related: Data Privacy Startup TripleBlind Raises $8.2 Million in Seed Funding

Related: Gravwell Emerges From Stealth With Data Fusion Platform for Security Teams

Related: Data Security Startup Code-X Emerges From Stealth With $5 Million in Funding

Related: Data Security Company Symmetry Systems Emerges From Stealth

view counter

Eduard Kovacs (@EduardKovacs) is a contributing editor at SecurityWeek. He worked as a high school IT teacher for two years before starting a career in journalism as Softpedia’s security news reporter. Eduard holds a bachelor’s degree in industrial informatics and a master’s degree in computer techniques applied in electrical engineering.

Previous Columns by Eduard Kovacs:
Tags:

http://feedproxy.google.com/~r/securityweek/~3/jDlz1iBOblo/data-privacy-compliance-startup-cytrio-launches-35-million-funding