Apple releases iOS 14.5, the biggest update since iOS 14 first launched
Apple's 2020 iPad Air.
Enlarge / Apple’s 2020 iPad Air.
Samuel Axon

Today is the day: Apple has finally released iOS 14.5 and iPadOS 14.5 worldwide after a longer-than-usual beta period. If you’re using a supported device, you should be able to find the update on the software update page in the iPhone, iPad, or iPod touch’s Settings app.

This is arguably the biggest update of the iOS 14 cycle that began with iOS 14.0 and iPadOS 14.0 on September 16 of last year. The most consequential change for many is App Tracking Transparency, a new policy whereby app developers are required to get user opt-in to track users between apps.

But iOS 14 and iPadOS 14.5 also introduce a long-needed workaround for using Face ID when wearing a mask, support for the new AirTag accessory, several changes aimed at making experiences within the software more inclusive for a diverse user base, new Siri features and voices, and changes to the Reminders, News, Music, and Podcasts apps, among other things.

Here’s what you can expect to see when you install the new software.

App Tracking Transparency

Apple’s long-debated, long-awaited App Tracking Transparency feature and policy will now be fully enforced starting with today’s release of iOS 14.5 and iPadOS 14.5 (as well as tvOS 14.5, which we wrote about earlier today).

A large portion of the apps in the App Store for these devices utilizes a tracking technique called ID for Advertisers (IDFA) to track users’ activity between multiple apps published by multiple companies, to inform ad targeting and other monetization and data collection techniques.

Last year, Apple announced that it would begin requiring all apps to ask for users’ permission in advance to do this on an app-by-app basis. Anticipating that many users would opt out and that the change would therefore significantly impact revenue, various app developers and ad networks have criticized the move, saying it will hurt big and small businesses alike.

Those critics are not making that up: the move is likely to have a significant impact on the bottomline for many types of apps that rely on advertising for revenue. But Apple maintains that users’ control over how they are tracked and how their data is used and accessed is the most important concern at hand.

Apple initially delayed the move (which was originally planned for the first iOS 14 release) so developers and advertisers could have more time to prepare. Today’s launch of iOS and iPadOS 14.5 is the point of no return; the requirement will now be enforced. (Some apps already implemented it before today’s release.)

A COVID-mask Face ID workaround: Use your Apple Watch

Face ID seemed like an overall win over Touch ID after it was first introduced in 2017, but as we all know, the COVID-19 pandemic in 2020 put Face ID phones in a tough spot.

With people all around the world wearing masks to protect themselves and others from the virus, Face ID phones are unable to use their main method of authentication for getting past the lock screen or using features like Apple Pay.

Now, users who update their iPhones to iOS 14.5 and their Apple Watches to the also-just-released watchOS 7.4 can unlock their said phones with said watches.

When you’re wearing an Apple Watch and that watch is unlocked and close to your iPhone, you should now be able to just glance at the iPhone screen and see it unlocked via the watch’s own authentication. The watch will give you haptic feedback to let you know the iPhone has been unlocked.

This works on all Face ID iPhones paired with an Apple Watch Series 3 or later, provided both devices are running the latest software.

Diversity and inclusion

Apple has made a few small but meaningful changes to better represent iPhone users in a couple of parts of the iPhone and iPad experience.

First off, Siri has two new voices in the United States modeled after Black American English. You’ll find these in the Siri page for voices within the Settings app. Select “American” under variety and, in addition to the two existing American accents, you’ll find two more voices: a Black female voice, and a Black male voice.

Further, Siri no longer has a single voice that’s treated as the default. Users select from multiple options when first setting up their phones now.

Apple has also introduced new emojis meant to allow users to express themselves better. In addition to various new heart and face emojis, Apple has added a woman with a beard emoji in various skin colors, as well as the ability to independently select the skin color for each of the two people in the emojis of couples hugging and the like.

New Siri and Maps capabilities

Siri can now be used to initiate FaceTime calls with groups of people; you just need to ask it to call any already existing Messages group.

Also, iOS and iPadOS 14.5 give Siri the ability to announce incoming calls through connected AirPods or Beats headphones. They also support “calling emergency contacts if the iPhone owner needs assistance and is unable to make a call,” Apple says.

When driving, users can tell Siri about hazards on the road so other drivers can be warned, for example by saying, “Hey Siri, there’s a crash up ahead.” Users can also tell Siri when a previously reported incident has been resolved.

And while we’re on the subject of cars and maps, we’ll use this opportunity to mention that Maps users can now share their ETA with contacts when traveling with walking or cycling directions. That’s a feature that people have been requesting for a while now. Additionally, CarPlay users can use Share ETA with Siri.

Apple app updates

Apple has introduced a few new features and design changes to some of the iOS apps it has made itself. For example, Podcasts now has a redesigned show page, plus top charts section and new categories and curated collections in the search tab. Users can also save and download episodes individually and see them added to the library automatically.

Apple News likewise has a redesigned Apple News+ tab with a prominent place to manage and download magazine and newspaper issues. It also has some improvements to search, with a category-based results page.

Apple Fitness+ within the Fitness app can stream audio and video to any AirPlay 2-enabled TV or device, potentially expanding the places the service can be conveniently used in the home or other setting.

Apple Music now offers users the option to share individual lyrics segments via Messages, Facebook, or Instagram Stories. It also has city-specific playlists for several large urban centers like Los Angeles, Chicago, Dublin, Berlin, Jakarta, Istanbul, Tokyo, Seoul, and Dubai, among many others.

Reminders has new sort options within reminder lists; users can now sort by title, priority, due date, or creation date. They can also print reminder lists with an easily accessible widget within the app.

Grab bag

There are a few other features that don’t neatly fit into the buckets above. They include:

  • Support for AirTags, Apple’s new geolocation devices.
  • Dual SIM support that “enables 5G connectivity on the line that’s using cellular data on iPhone 12 models”
  • The ability to tweak playback speed in the Translation app by long-pressing the play button
  • Support for the PlayStation 5’s DualSense controller and Xbox Series X|S controllers via Bluetooth
  • Several bug fixes, which are listed in the full update notes below

https://arstechnica.com/?p=1760177


EU lawmakers propose strict curbs on use of facial recognition

EU lawmakers propose strict curbs on use of facial recognition

EU regulators have proposed strict curbs on the use of facial recognition in public spaces, limiting the controversial technology to a small number of public-interest scenarios, according to new draft legislation seen by the Financial Times.

In a confidential 138-page document, officials said facial recognition systems infringed on individuals’ civil rights and therefore should only be used in scenarios in which they were deemed essential, for instance in the search for missing children and the policing of terrorist events.

The draft legislation added that “real-time” facial recognition—which uses live tracking rather than past footage or photographs—in public spaces by the authorities should only ever be used for limited periods of time, and it should be subject to prior consent by a judge or a national authority.

The document comes as privacy advocates, politicians, and European citizens have become increasingly vocal about regulating the use of live facial recognition. At present, there are no clear rules around how and where the technology can be used on the general public, so the proposed legislation would be the first to codify these limitations into law.

The introduction of tougher curbs on the use of facial recognition technology would likely reignite debate over whether the practice should be banned altogether, as experts warn that it is still fraught with risks.

In a landmark ruling last August, the UK Court of Appeal said that the use of facial recognition technology by South Wales Police was unlawful and found that it breached privacy rights, data protection laws, and equality laws.

The EU’s draft legislation also addressed a range of related issues such as algorithmic bias, arguing that technology used in contexts such as recruitment and finance should be developed so as not to replicate “historical patterns of discrimination” against minority groups.

EU regulators proposed hefty fines of up to 6 percent of a company’s global turnover if it is found to have abused artificial intelligence in this way or fails to detect biases when hiring workers or providing services.

They added that so-called social-scoring practices, which assess a person’s trustworthiness from behavioral data gathered about them, should also be banned. In China, for instance, a system is being developed that calculates a person’s credit score using information about their online habits.

“The social score obtained… may lead to the detrimental or unfavorable treatment of [people or groups]… which are unrelated to the context in which the data was originally generated,” the leak said.

The proposals, which will be presented on Wednesday in Brussels, will now be debated by the European Parliament and member states until at least 2023 before becoming law.

© 2021 The Financial Times Ltd. All rights reserved Not to be redistributed, copied, or modified in any way.

https://arstechnica.com/?p=1758740


Commissione Ue pronta a vietare l’utilizzo dell’IA per la sorveglianza indiscriminata dei cittadini

L’intelligenza artificiale (IA) è considerata a ragione una tecnologia strategica per la crescita economica, l’innovazione industriale e il raggiungimento dei più alti livelli di competitività delle imprese sui mercati globali. Prova ne è la crescente spesa, a livello europeo e globale, in questo tipo di soluzioni.

L’Europa vuole un posto di leadership nel settore, ma deve prima trovare un approccio comune di tutti i suoi Stati all’implementazione dell’IA ad ogni livello, con norme e limiti di ordine etico, regolatorio e finanziario, ma anche culturale e relativi a privacy e sicurezza.

<!-- LARGE RECTANGLE POST - CORPO TESTO

-->

Approccio etico dell’Europa all’IA

A riguardo, la Commissione europea proporrà entro l’anno in corso un pacchetto di regole per l’intelligenza artificiale, mirato a salvaguardare i valori etici e i diritti fondamentali dell’essere umano, quindi teso a stabilire i requisiti di sicurezza ed affidabilità di questa tecnologia.

Nella bozza di documento “European approach for artificial intelligence”, visionato in anteprima da euractive.com, si manifesta la volontà della Commissione di vietare l’utilizzo di sistemi IA per le operazioni di sorveglianza indiscriminata dei cittadini.

Entro la prossima settimana, si legge sul sito, saranno proposti nuovi criteri e parametri per l’utilizzo dell’IA in questo tipo di operazioni. Tra i diversi metodi di sorveglianza sono citati quelli che includono il monitoraggio e il tracciamento delle persone fisiche, sia in ambiti tradizionali, sia digitali, ma anche l’aggregazione e l’analisi automatizzate di dati personali provenienti da varie fonti.

Divieti e sanzioni, le deroghe per la sicurezza nazionale

Ulteriori divieti saranno proposti per ogni uso dell’intelligenza artificiale che violi i valori di base dell’Unione e i diritti umani più in generale.

Si pensa di estendere il divieto di utilizzo dell’IA anche a quel tipo di sorveglianza tesa a manipolare, controllare o limitare il comportamento e la libertà di spostamento degli esseri umani, soprattutto a vantaggio di terzi.

In termini di sanzioni, potrebbero essere previste multe fino al 4% del fatturato annuo globale di un’azienda che non rispetti tali divieti.

Nel documento è però precisato che in caso di motivi di sicurezza nazionale tali divieti non varranno per i Governi e le Autorità pubbliche che impiegheranno l’IA anche nei modi sopra descritti.

Questo significa che gli Stati europei potrebbero in futuro impiegare l’intelligenza artificiale anche per la sorveglianza di massa o il tracciamento dei nostri dati, se per comprovati motivi di sicurezza interna.

Applicazioni IA ad alto rischio

Altre applicazioni IA ad alto rischio sono l’identificazione biometrica remota di ignari cittadini in spazi accessibili al pubblico, tra cui il riconoscimento facciale, l’integrazione nelle infrastrutture pubbliche strategiche, come quelle relative ai trasporti, alla fornitura di acqua ed energia, la Difesa.

Per tutti questi motivi, la Commissione propone l’istituzione di un Board europeo per l’intelligenza artificiale, composto da 27 rappresentanti degli Stati membri, dal Garante europeo per la protezione dei dati e da un rappresentate della Commissione europea.

La proposta, infine, dovrebbe essere presentata ufficialmente dal Vice Presidente esecutivo per il digitale della Commissione europea, Margrethe Vestager, il prossimo 21 aprile. Seguirà il parere del Consiglio e il voto del Parlamento europeo.

https://www.key4biz.it/commissione-ue-pronta-a-vietare-lutilizzo-dellia-per-la-sorveglianza-indiscriminata-dei-cittadini/355745/


Euro digitale: ok di cittadini e imprese alla Bce, ma prioritario tutelare la privacy

Pubblicati oggi i risultati della consultazione pubblica della Banca centrale europea (Bce) sull’euro digitale. Dal documento potrebbero emergere secondo gli esperti indicazioni rilevanti per le attività di analisi e sperimentazione della Bce.

La consultazione

Suggerimenti utili anche per la prossima decisione del Consiglio direttivo sull’opportunità di avviare una fase di indagine formale per l’eventuale emissione di una valuta digitale per la metà dell’anno in corso.

<!-- LARGE RECTANGLE POST - CORPO TESTO

-->

Al centro delle preoccupazioni degli europei riguardo l’euro digitale sembrerebbero trovarsi la tutela dei dati personali e la sicurezza delle transazioni.

“Un euro digitale può avere successo soltanto se risponde alle esigenze dei cittadini europei”, ha dichiarato in una nota Fabio Panetta, membro del Comitato esecutivo della BCE: “Faremo del nostro meglio per assicurare che un euro digitale sia in linea con le aspettative dei cittadini che sono emerse dalla consultazione pubblica”.

Principali indicazioni sull’euro digitale

Si confermano così le prime osservazioni già raccolte dalla Bce: innanzitutto una più decisa tutela della privacy per il 43% dei partecipanti, seguita dalla sicurezza (18%), dalla possibilità di utilizzarla in tutta l’area dell’euro (11%), senza costi aggiuntivi (9%) e offline (8%).

Il mondo delle imprese e più nello specifico i commercianti chiedono ulteriori requisiti volti a prevenire attività illecite, mentre meno di un cittadino su dieci è favorevole al completo anonimato.

L’euro digitale è inoltre visto come valido strumento per rendere i pagamenti transfrontalieri più rapidi e meno costosi.

Quasi la metà dei partecipanti ha menzionato la necessità di stabilire limiti all’ammontare detenuto, ma si delinea una certa preferenza per l’integrazione di un euro digitale negli attuali sistemi bancari e di pagamento.

Da un punto di vista tecnologico, infine, sono considerate preferibili le soluzioni con carta (o smartcard) o con un sistema sicuro nello smartphone per gli utenti finali.

La consultazione pubblica ha ricevuto più di 8.200 risposte, provenienti perlopiù dalla Germania (47%), dall’Italia (15%) e dalla Francia (11%).

https://www.key4biz.it/euro-digitale-ok-di-cittadini-e-imprese-ma-prioritario-tutelare-la-privacy/355613/


No password required: Mobile carrier exposes data for millions of accounts

No password required: Mobile carrier exposes data for millions of accounts
Getty Images

Q Link Wireless, a provider of low-cost mobile phone and data services to 2 million US-based customers, has been making sensitive account data available to anyone who knows a valid phone number on the carrier’s network, an analysis of the company’s account management app shows.

Dania, Florida-based Q Link Wireless is what’s known as a Mobile Virtual Network Operator, meaning it doesn’t operate its own wireless network but rather buys services in bulk from other carriers and resells them. It provides government-subsidized phones and service to low-income consumers through the FCC’s Lifeline Program. It also offers a range of low-cost service plans through its Hello Mobile brand. In 2019, Q Link Wireless said it had 2 million customers.

The carrier offers an app called My Mobile Account (for both iOS and Android) that customers can use to monitor text and minutes histories, data and minute usage, or to buy additional minutes or data. The app also displays the customer’s:

  • First and last name
  • Home address
  • Phone call history (from/to)
  • Text message history (from/to)
  • Phone carrier account number needed for porting
  • Email address
  • Last four digits of the associated payment card

Screenshots from the iOS version look like this:

No password required . . . what?

Since at least December and possibly much earlier, My Mobile Account has been displaying this information for every customer account whenever it is presented with a valid Q Link Wireless phone number. That’s right—no password or anything else required.

When I first saw a Reddit thread discussing the app, I thought for sure there was some kind of mistake. So I installed the app, got the permission from another thread reader, and entered his phone number. I was immediately viewing his personal information, as the redacted images above demonstrate.

The person who started the Reddit thread said in an email that he first reported this glaring insecurity to Q Link Wireless sometime last year. Emails he provided show that he notified support twice again this year, first in February and again this month.

Feedback left in reviews for both the iOS and Android offerings also reported this issue, in several cases with a response from a Q Link Wireless representative thanking the person for the feedback.

Downright negligence

The data exposure is serious because phone numbers are so easy to come by. We give them to prospective employers, car mechanics, and other strangers. And of course, phone numbers are easily obtained by private detectives, abusive spouses, stalkers, and other people who have an interest in a particular person. Q Link Wireless making customer data freely available to anyone who knows a customer’s phone number is an act of downright negligence.

I began emailing the carrier about the insecurity on Wednesday and followed up with almost a dozen more messages. Q Link Wireless CEO and founder Issa Asad didn’t respond despite my noting that every hour he allowed the data exposure to continue compounded the risk to his customers.

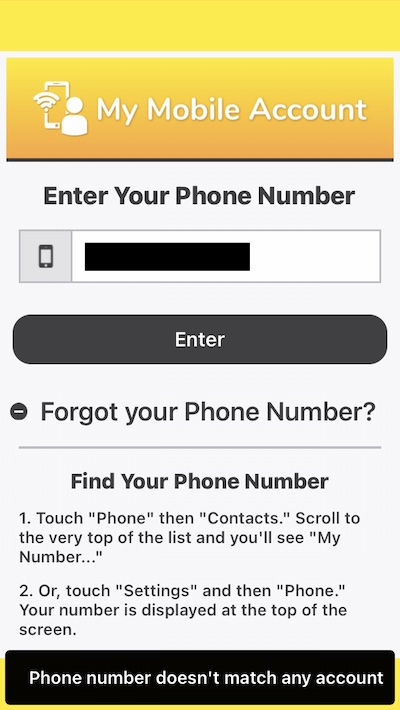
Then late on Thursday, My Mobile Account stopped connecting to customers’ accounts. When presented with the number of a Q Link Wireless customer, the app responds with a message saying, “Phone number doesn’t match any account.” The iOS and Android versions of the app were last updated in February, suggesting that the fix is the result of a change Q Link Wireless made to a server.

While My Mobile Account displayed customers’ personal information, it didn’t provide a means to change that data. The app also didn’t display passwords. That means a person couldn’t exploit this leak to perform a SIM swap or lock users out of their accounts, although the exposure might make it easier for a would-be SIM swapper to social engineer a Q Link Wireless employee into porting a number to a new phone.

There are no indications one way or the other that this leakage was actively exploited. Researchers from security firm Intel471 found no discussions in criminal forums about the available data, but there’s no way to know if it was abused on a smaller scale, say by someone a Q Link Wireless customer knows or has interacted with.

As phone users seeking low-cost, no-frills mobile service, Q Link Customers are a part of a population that may be least able to afford data breach services and other privacy services. The carrier has yet to notify customers of the data exposure. People using the service should consider any data displayed by the app to be available to anyone who has their phone number.

https://arstechnica.com/?p=1755853


Cost of Sandboxing Prompts Shift to Memory-Safe Languages. A Little Too Late?

NEWS ANALYSIS: Google’s decision to promote Rust for low-level Android programming is another sign that the shelf-life for memory corruption mitigations are no match for the speed of in-the-wild exploit development.

Just 13 years after Google introduced the sandbox in Chrome touting “a new approach in browser security,” the company is now blaming the limitations — and high processing cost — of sandboxing for a new decision to promote Rust as the low-level programming language of choice for the Android operating system.

The decision to promote Rust over C and C++ isn’t exactly a surprise but the language used in Google’s announcement signals a sad end to the sandbox as an effective anti-exploit mitigation for a vexing problem haunting software engineering since the mid-1990s.

“Sandboxing is expensive,” says Jeff Vander Stoep, a member of Google’s Android team. “Sandboxing doesn’t eliminate vulnerabilities from the code and its efficacy is reduced by high bug density, allowing attackers to chain multiple vulnerabilities together,” he added.

He said Google is turning to memory-safe languages like Rust to help overcome these “limitations” by lowering the density of bugs in the Android code and increasing the effectiveness of the existing sandbox.

More importantly, Vander Stoep says the move reduces Google’s sandboxing needs entirely and enables the creation and introduction of new software features that are both safer and lighter on resources.

HIGH SEVERITY 

He said memory safety problems in C and C++ continue to be the “most-difficult-to-address” issue in modern software engineering and noted that the Android team — like the rest of the tech industry — spent heavily to mitigate a class of vulnerabilities without much success.

“In spite of these efforts [to detect, fix and mitigate these issues], memory safety bugs continue to be a top contributor of stability issues, and consistently represent more than 70 percent  of Android’s high severity security vulnerabilities,” Vander Stoep added.

The problem isn’t limited to Android.  Published data from Google Project Zero shows that the majority of in-the-wild zero-day attacks over the last few years are dominated by buffer overflows and use-after-free memory corruption issues.

Ever since the mid-1990s, the brightest minds in cybersecurity have attempted to find approaches to solve memory corruption issues.  These long-term, cross-industry efforts produced many exciting mitigations and effectively raised the cost for attackers.

However, these mitigations came with heavy costs and the shelf-life for things like sandboxing has gotten shorter and shorter as attackers quickly found ways to bypass these roadblocks.

CAT AND MOUSE

“It’s a cat-and-mouse we can’t win,” says an ex-Google software engineer who requested anonymity. “We spend a lot on these mitigations. We spend a lot to address CPU performance hits, we spend a ton more on software development costs and, poof, someone comes up with a bypass and it feels like we’re back to square one.”

“Should we really have spent so much on sandboxing?  Should we really have spent so much all the control-flow integrity mitigations that didn’t really move the bar?  I’m not sure this was money and resources well spent,” he said in exasperation.

Despite these frustrations, the sandbox has been an effective mitigation that made it very difficult to exploit software programs.  Prior to the popularity of sandboxing, attackers could simply exploit a single buffer overflow vulnerability to achieve remote code execution, the holy grail of attacks.

Once sandboxes became a key feature in browsers and desktop apps, the cost of a remote code execution exploit was raised. Where a single bug won the Pwn2Own contest 10 years ago, attackers today must chain exploits for multiple vulnerabilities and include an expensive “sandbox escape” to achieve full code execution.

Now, there’s a shift to using memory-safe languages to effectively eliminate memory corruption as a bug class. For example, on the Android OS, managed languages like Java and Kotlin have become the go-to choice for app development because of ease of use, portability, and safety.  In addition, the Android Runtime (ART) manages memory on behalf of the developer.

The Android OS uses Java extensively, effectively protecting large portions of the Android platform from memory corruption bugs. However, Java and Kotlin are not options for lower layers of the operating system, as Google explains here:

Lower levels of the OS require systems programming languages like C, C++, and Rust. These languages are designed with control and predictability as goals. They provide access to low level system resources and hardware. They are light on resources and have more predictable performance characteristics.

For C and C++, the developer is responsible for managing memory lifetime. Unfortunately, it’s easy to make mistakes when doing this, especially in complex and multithreaded codebases.

Rust provides memory safety guarantees by using a combination of compile-time checks to enforce object lifetime/ownership and runtime checks to ensure that memory accesses are valid. This safety is achieved while providing equivalent performance to C and C++.

Google describes the addition of a new language to the Android platform is a large undertaking and warned that there are toolchains and dependencies that need to be maintained, test infrastructure and tooling that must be updated, and developers that need to be trained. “Scaling this to more of the OS is a multi-year project,” the company said.

NO SILVER BULLET

Still, security experts warn that moving to Rust isn’t going to solve all memory lifetime issues.

“Certain patterns just turn them into application logic bugs vs. RCE. An improvement, but no silver bullet,” says Halvar Flake, a security industry pioneer who has worked on memory corruption mitigations.

On a recent podcast interview, head of privacy and security at Lyft Nico Waisman also discussed the shift to memory-safe languages and predicted a future of app logic bugs and a continued dependence on C and C++ code in legacy software products.

Memory safety issues will continue to haunt the security landscape for decades to come but there is optimism that a combination of new technology — especially around memory tagging — and the adoption of safer programming languages will point to a brighter future.

But, as history has shown, mitigations have a shelf-life and novel techniques and bypasses are always just a Black Hat presentation away.  The sandbox was effective and it made life more difficult for attackers but, as Google’s decision shows, there’s a hefty price tag and no signs that sandbox-bypass exploits are going away.

The sandbox had a good run but it’s time to acknowledge this mitigation has seen its time in the sun.

view counter

Ryan Naraine is Editor-at-Large at SecurityWeek and host of the popular Security Conversations podcast series. Ryan is a journalist and cybersecurity strategist with more than 20 years experience covering IT security and technology trends. He is a regular speaker at cybersecurity conferences around the world.
Ryan has built security engagement programs at major global brands, including Intel Corp., Bishop Fox and Kaspersky GReAT. He is a co-founder of Threatpost and the global SAS conference series. Ryan’s career as a journalist includes bylines at major technology publications including Ziff Davis eWEEK, CBS Interactive’s ZDNet, PCMag and PC World.
Follow Ryan on Twitter @ryanaraine.

Previous Columns by Ryan Naraine:
Tags:

http://feedproxy.google.com/~r/Securityweek/~3/w3Q6T2GCDbU/cost-sandboxing-prompts-shift-memory-safe-languages-little-too-late


How Apple’s new App Tracking Transparency policy works

This week, Apple published a new white paper that describes the ways apps typically track users and handle their data, outlines the company’s privacy philosophy, and offers several details and clarifications about the upcoming App Tracking Transparency change, which will (among other things) require app developers to get a user’s permission to engage in the common practice of creating an identifier (called IDFA) to track that user and their activities between multiple apps.

The paper states that the change will go fully into effect with the release of an update to iOS and other Apple operating systems in “early spring” (Apple has previously said this would happen in iOS 14.5, which is now in a late stage of beta testing), but the company has reportedly already started enforcing some aspects of the new policy with new app submissions, suggesting that the full transition is very imminent. One recent survey found that only about 38.5 percent of users plan to opt in to tracking.

Most of the paper is dedicated to explaining exactly how apps track users to begin with, by using a hypothetical example of a father and daughter traveling to the playground with their personal mobile technology and apps in tow. There are no new revelations in this section for people who are already familiar with how these systems work, but the information is accurate, and most people don’t actually know all that much about how their data is tracked and used, so it might be useful to some.

Apple also uses a section in the paper to describe its app privacy labels, which are kind of like food nutrition labels, but instead of describing the nutrients in a meal, they describe the ways an app tracks you or accesses your data. It’s worth noting, though, that these app privacy labels are largely self-reported, and independent observers have found many examples of apps that have inaccurate or incomplete information in these labels.

Trust and antitrust

While the paper is partly aimed at users who want to know more about iOS’ privacy features and how personal data is handled by mobile apps generally, it also repeatedly tries to make the case that the upcoming App Tracking Transparency change will not negatively impact most advertising-supported businesses in a severe way. “The introduction of past features, such as Safari Intelligent Tracking Prevention, have shown that advertising can continue to be successful while enhancing users’ privacy protections,” the authors argue.

Some companies, like Facebook, have explored the idea of making an antitrust case against Apple, arguing that Apple is making third-party apps follow rules that the smartphone maker’s apps don’t have to follow. But this paper argues that Apple’s own apps don’t present an opt-in prompt for tracking because they don’t track across third-party apps for advertising purposes to begin with.

Most of the meaty clarifications are in the paper’s FAQ (frequently asked questions) section. For example, Apple writes that “app developers cannot require you to permit tracking in order to use the app’s full capabilities”—meaning users won’t get reduced functionality in apps if they opt out of the tracking. This gets at one critical caveat about Apple’s upcoming change: the policy prevents tracking across multiple third-party apps if a user opts out, but both Apple and any other company can still track users across multiple apps if all the apps in question are operated by the same company. The same thing that gives Apple a pass could also apply to, say, Google tracking you across Gmail, Google News, Docs, and so on. But as soon as Google wants to use a technique that can also see what you’re doing in Apple’s or Facebook’s apps, for example, that’s when the opt-in is required.

Apple offers a separate toggle labeled “Personalized Ads”—totally distinct from the IDFA-related opt-in prompt—that allows users to decide whether they want to be tracked within Apple’s first-party apps.

And related to the recent flurry of App Store submission rejections, Apple clarifies that a developer “is also required to respect your choice beyond the advertising identifier.” This means that once a user has opted out of IDFA tracking, the developer must also not track the user through any other method that generates a similar result, like device fingerprinting. Device fingerprinting was apparently what caused the wave of rejections we reported last week. “If we learn that a developer is tracking users who ask not to be tracked, we will require that they update their practices to respect your choice, or their app may be rejected from the App Store,” the paper says.

The FAQ also addresses the criticisms of the efficacy of the App Store’s privacy labels, albeit not very effectively. It confirms that the data is self-reported and says, “if we learn that a developer may have provided inaccurate information, we will work with them to ensure the accuracy of the information.”

Listing image by Samuel Axon

https://arstechnica.com/?p=1755111


Facebook Says Hackers ‘Scraped’ Data of 533 Million Users in 2019 Leak

Facebook said Tuesday that hackers “scraped” personal data of some half-billion users back in 2019 by taking advantage of a feature designed to help people easily find friends using contact lists.

A trove of information about more than 530 million Facebook users was shared over the weekend at a hacker forum, prompting the leading social network to explain what happened and call on people to be vigilant about privacy settings.

“It is important to understand that malicious actors obtained this data not through hacking our systems but by scraping it from our platform prior to September 2019,” Facebook product management director Mike Clark said in a post.

“This is another example of the ongoing, adversarial relationship technology companies have with fraudsters who intentionally break platform policies to scrape internet services.”

The data included phone numbers, birth dates, and email addresses, and some of the data appeared to be current, according to US media reports.

The stolen data did not include passwords or financial data, according to Facebook.

Scraping is a tactic that involves using automated software to gather up information shared publicly online.

“All 533,000,000 Facebook records were just leaked for free,” Alon Gal, chief technology officer at the Hudson Rock cybercrime intelligence firm, said Saturday on Twitter.

He denounced what he called the “absolute negligence” of Facebook.

“Bad actors will certainly use the information for social engineering, scamming, hacking and marketing,” Gal said on Twitter.

Clark urged members of the social network to check their privacy settings to control what information can be seen publicly, and to tighten account security with two-factor authentication.

This is not the first time leaks or use of data from the world’s largest social network — with nearly two billion users — has embroiled Facebook in controversy.

In 2016, a scandal around Cambridge Analytica, a British consulting firm that used the personal data of millions of Facebook users to target political ads, cast a shadow over the social network and its handling of private information.

view counter

© AFP 2020

Previous Columns by AFP:
Tags:

http://feedproxy.google.com/~r/Securityweek/~3/7TBc0m9mlFM/facebook-says-hackers-scraped-data-533-million-users-2019-leak


US lawmakers Press Online Ad Auctioneers Over User Data

A bipartisan group of US senators on Friday sent letters to major digital ad exchanges, including Google and Twitter, asking whether user data was sold to foreign entities who could use it for blackmail or other malicious ends.

In the real-time bidding process to decide which personalized ads a user sees when a web page loads, hundreds of businesses receive a user’s personal information, including search history, IP address, age and gender.

Questions about the sale of data gathered during the auction process were also sent to AT&T, Index Exchange, Magnite, OpenX, PubMatic and Verizon, according to the office of Senator Ron Wyden, a Democrat representing Oregon.

“Few Americans realize that some auction participants are siphoning off and storing ‘bidstream’ data to compile exhaustive dossiers about them,” Wyden and other senators wrote in letters to the companies.

“This information would be a goldmine for foreign intelligence services that could exploit it to inform and supercharge hacking, blackmail, and influence campaigns.”

While online ad exchanges use automated bidding systems to determine which ads to show people using internet services, data such as user locations, devices, and web activity can be gathered, according to the senators.

“These dossiers are being openly sold to anyone with a credit card, including to hedge funds, political campaigns, and even to governments,” the senators wrote.

Questions sent to the companies included what information is gathered about people in the course of serving up ads and which foreign firms have bought such data from them, according to the release.

The companies were given until May 4 to provide answers.

Twitter told AFP it had received the letter and intended to respond. The other companies did not immediately respond to queries for comment.

Google has pledged to steer clear of tracking individual online activity when it begins implementing a new system for targeting ads without the use of so-called “cookies.”

The internet giant’s widely used Chrome browser recently began testing an alternative to the tracking practice that it believes could improve online privacy while still enabling advertisers to serve up relevant messages.

view counter

© AFP 2020

Previous Columns by AFP:
Tags:

http://feedproxy.google.com/~r/Securityweek/~3/1FztLbb27_k/us-lawmakers-press-online-ad-auctioneers-over-user-data


SecureDrop Workstation Gets Post-Audit Security Refresh

The open-source SecureDrop Workstation has undergone a security makeover after a third-party security audit flagged multiple problems, including a high-risk bug that could allow an attacker to plant files on target machines.

The SecureDrop Workstation audit, conducted by Trail of Bits and financed by the New York Times, warned that the high-risk directory traversal bug could be leveraged for code execution attacks.

“The high severity finding details case where a malicious SecureDrop server could create files in arbitrary paths in the sd-app VM, which may allow for a code execution,” according to the audit report [PDF].

“When the SecureDrop Workstation client downloads a file, it stores it in a location derived from the filename returned by the server. However, since this location is not sanitized properly in all cases, an attacker who controls responses from the server can make the client save files in arbitrary paths on the filesystem. An attacker can use this vulnerability to plant files that potentially enable further vulnerabilities.”

The Trail of Bits code auditors found two cases when a malicious SecureDrop server could plant files.

Overall, the security assessment gave SecureDrop workstation a positive security bill of health. 

“We were unable to achieve a direct compromise of the Workstation from the position of an Internet-based attacker during our engagement,” Trail of Bits said, but made it clear this doesn’t imply that such a compromise exists or that SecureDrop Workstation is free of bugs.

SecureDrop Workstation is currently managed by the Freedom of the Press Foundation. Based on Qubes OS, the platform enables secure and encrypted communications between news organizations, journalists, sources and whistleblowers. It is currently being used in a limited pilot.

The Foundation said the audit report confirmed some its  assumptions around the use of virtualization to segment sensitive workloads and was pleased with the finding that the system system “represents a complex but well researched product that has been thoughtfully designed.”

None of the issues identified were directly exploitable by an attacker, and require either compromise of the SecureDrop server, or code execution in certain key VMs within the SecureDrop Workstation, the Foundation said.

Over the course of their engagement (6 person-weeks with two pen-test/code audit engineers), Trail of Bits found and documented 1 high-risk, 6 medium-risk, 7 low and 12 informational disclosure problems.

The audit confirmed that the high-severity and six of the medium-severity issues have already been patched and released, with the fixes validated by the auditing team. 

The Foundation said it is also investigating potential architectural improvements, including the creation of a custom RPC service to handle opening of files.

“In addition to addressing the findings surfaced in this report, we are also implementing feedback from current pilot participants, and planning new features around export and integration to other communication tools. We are in the process of expanding the pilot to several other news organizations, and hope to provide general availability later this year,” the Foundation said.

view counter

Ryan Naraine is Editor-at-Large at SecurityWeek and host of the popular Security Conversations podcast series. Ryan is a journalist and cybersecurity strategist with more than 20 years experience covering IT security and technology trends. He is a regular speaker at cybersecurity conferences around the world.
Ryan has built security engagement programs at major global brands, including Intel Corp., Bishop Fox and Kaspersky GReAT. He is a co-founder of Threatpost and the global SAS conference series. Ryan’s career as a journalist includes bylines at major technology publications including Ziff Davis eWEEK, CBS Interactive’s ZDNet, PCMag and PC World.
Follow Ryan on Twitter @ryanaraine.

Previous Columns by Ryan Naraine:
Tags:

http://feedproxy.google.com/~r/Securityweek/~3/160J-vA58qQ/securedrop-workstation-gets-post-audit-security-refresh