Telemetria e raccolta di dati, impossibile disattivarla su device Android e iOS
La telemetria è la capacità di un sistema di rilevare a distanza dati operativi relativi ad un device connesso in rete. Ci sono diversi tipi di apparecchi per vari usi, anche gli smartphone rientrano in questo campo di attività, con brutte sorprese per gli utenti finali.
I due giganti tecnologici, infatti, grazie a questo sistema possono sfruttare i dati raccolti per identificare e profilare gli utenti, a partire dalle loro ricerche e dai loro acquisti, ma anche tracciando i movimenti e gli spostamenti, quindi la posizione.
Ogni 4-5 minuti i sistemi operativi Android e iOS si connettono ai rispettivi server back-end per trasmettere i dai raccolti. Non c’è modo, sembra, di evitare tutto questo, perché anche disattivando la telemetria pare che lo scambio di dati avvenga comunque.
Il collegamento al server avviene anche se il telefono non è utilizzato, basta poi toccare anche per sbaglio lo schermo per riattivare l’opzione di telemetria, che è automatica.
Questo è il caso di app abbastanza popolari come Google Search, Google Maps, Google Assistant, YouTube e Google Doc, nel caso di Android, mentre per l’iOS parliamo di Siri, Safari e iCloud ad esempio.
Impossibile disattivare la telemetria
Una conferma di questo arriva dal ricercatore Douglas Leith, in una nota nel report accademico dedicato alla ricerca, secondo cui: “Sia iOS che Android continuano a trasmettere la telemetria del device anche se l’utente ha scelto consapevolmente di disattivare questa funzione”.
Inoltre, lo studioso ha anche scoperto che la quantità di dati raccolti in telemetria da Android per Google è 20 molte più grande di quella ottenuta da Apple tramite iOS.
Nei primi 10 minuti di avvio di Android, Google Pixel invia 1 MB circa di dati ai server della casa madre, contro i 42 KB inviati dall’iPhone verso Apple nello stesso periodo di tempo.
Anche se inattivo, il device con sistema operativo Android invierà sempre 1 MB di dati ogni 12 ore, contro i 52 KB di Apple.
Websites of EU Mobile Providers Fail to Properly Secure User Data: Report
Sensitive data pertaining to the customers of top mobile services providers in the European Union is at risk of compromise due to improperly secured websites, data security and privacy firm Tala reveals.
An analysis of the websites of 13 of the top mobile telecom companies in the EU has revealed that none of them has in place even the minimum necessary protections to be considered secure.
“With over 235 million customers between them, none of the mobile providers scored a passing grade for website security. Where a score of 80+ is considered reasonable and 50 is barely a passing grade, none of the mobile providers analyzed comes close,” Tala says in a new report.
Despite the lack of proper website protections, however, during online sign-up, the telcos collect a significant amount of sensitive data from their customers, including names, emails, addresses, dates of birth, passport numbers, payslips, and even banking details in some cases.
All of the gathered data, Tala claims, might be at risk of compromise through vulnerabilities and the use of third-party code: the average number of JavaScript integrations was found to be 162, while forms were found exposed to an average of 19 third parties.
All of the websites, the report reveals, use dangerous JavaScript functions that open the door to cross-site scripting (XSS), the most common type of website vulnerability. The highest number of JavaScript integrations on a single site was 735.
The sensitive data that customers enter on the websites of these mobile opertors is also potentially exposed through the forms employed to gather the data, as these connect to a large number of domains, revealing extensive data sharing, “25% more than the global Alexa 1000 average for websites,” Tala notes.
“When website owners fail to secure data as it is entered into their websites, they’re effectively leaving it hanging; the only reason it’s not being stolen is that criminals haven’t taken it. Yet,” the company points out.
The research also revealed that none of the analyzed websites had in place the necessary protections to prevent unintentional data exposure, and any piece of third-party code running on the website could be used to “modify, steal or leak information through client-side attacks enabled by JavaScript,” the report reads.
While the data sharing in most cases was done through whitelisted, legitimate applications, the website owner wasn’t always aware of the type of data that these applications would collect, or the extent of the data collection.
“Even whitelisted apps can be exploited to exfiltrate data, with significant implications for data privacy, and by extension, GDPR. Unfortunately, the analysis indicates that none of the EU telcos analyzed here has sufficient awareness of the risk,” Tala notes.
Dutch Data Protection Authority Fines Booking.com Over Incident Notification
The Dutch Data Protection Authority announced on Wednesday that it has issued a fine of €475,000 (roughly $550,000) to online travel agency Booking.com for failing to report a data security incident within the required timeframe.
According to the privacy watchdog, the incident took place in December 2018 and it involved cybercriminals using voice phishing (vishing) and social engineering to trick the employees of 40 hotels in the United Arab Emirates into handing over their credentials for their Booking.com accounts.
The cybercrooks then used that access to obtain information on more than 4,000 individuals who had booked a hotel through Booking.com. They also managed to access payment card information belonging to nearly 300 people and attempted to phish the card information of others by posing as Booking.com employees over the phone or email.
The Dutch agency fined Booking.com because the company is based in the Netherlands. The travel company learned about the data breach on January 13, 2019, but only notified the Data Protection Authority on February 7 — the incident should have been reported within 72 hours. Impacted customers were notified by Booking.com on February 4.
Contacted by SecurityWeek, Booking.com highlighted that the fine is related to the late notification and is not connected to the company’s security practices or its handling of the incident.
“A small number of hotels inadvertently provided their Booking.com account login details to online scammers, but there was no compromise of the code or databases that power the Booking.com platform. After receiving the first reports of suspicious activity, we began working to understand and resolve the issue, but unfortunately didn’t get the matter escalated as fast as we would have liked internally,” the company said in an emailed statement.
It added, “We have since taken additional steps to improve awareness and education amongst our partners and employees on important privacy measures and general security processes, while also working to further optimize the speed and efficiency of our internal reporting channels. The protection and security of personal data is and will remain a top priority at Booking.com.”
Eduard Kovacs (@EduardKovacs) is a contributing editor at SecurityWeek. He worked as a high school IT teacher for two years before starting a career in journalism as Softpedia’s security news reporter. Eduard holds a bachelor’s degree in industrial informatics and a master’s degree in computer techniques applied in electrical engineering.
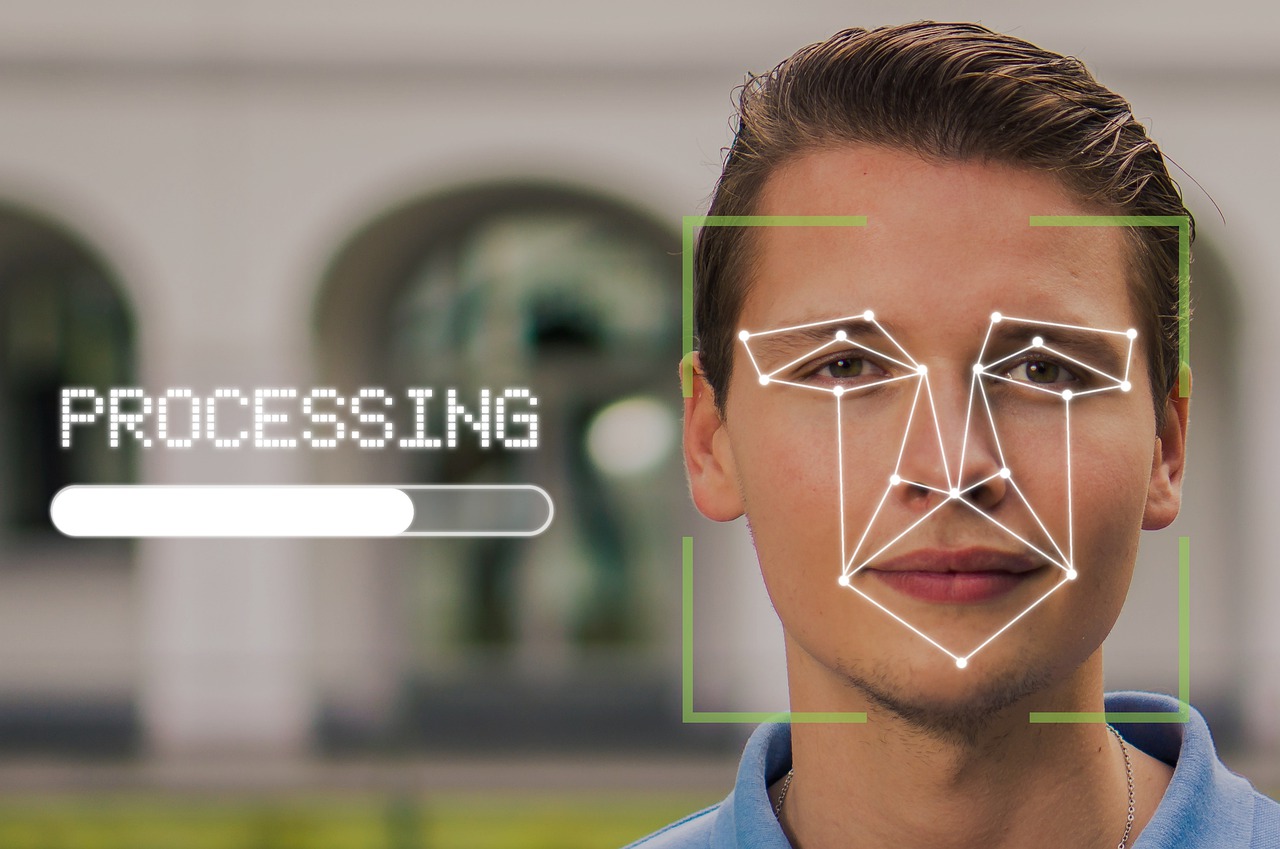
Il governo di Pechino sta puntando tutto sull’AI per identificare le persone tramite sistemi biometrici, ma si moltiplicano gli abusi.
Sono strumenti suggestivi ma ancora lontani da essere affidabili. I sistemi di riconoscimento facciale soffrono ancora di qualche “piccolo” problema a livello di sicurezza e la dimostrazione arriva dalla Cina, uno dei paesi che ha investito di più sull’implementazione dei di autenticazione biometrica.
Il governo di Pechino, infatti, sta utilizzando il riconoscimento facciale in qualsiasi ambito: dal controllo sociale alla gestione degli abbonamenti del trasporto pubblico per arrivare ai rapporti con la Pubblica Amministrazione.
I problemi, però, non mancano e secondo organi di stampa cinesi si stanno moltiplicando i casi in cui gruppi di hacker sfruttano le vulnerabilità dei sistemi di riconoscimento facciale per aggirare i controlli o mettere a segno vere e proprie truffe.
L’ultimo caso, in ordine di tempo, riguarda un procedimento penale che ha coinvolto due truffatori che hanno messo in piedi uno schema che gli permetteva di sottrarre denaro (circa 500 milioni di Yuan, pari a 65 milioni di euro) attraverso rimborso dell’IVA illegittimi.
Stando a quanto riporta una fonte di stampa locale (il testo è in cinese ma la versione inglese di Google Translator lo rende abbastanza intellegibile) i due imputati per truffa avrebbero usato una tecnica piuttosto semplice per ingannare i sistemi governativi.
Dopo essersi procurati le fotografie di ignari cittadini e averle “animate” utilizzando una semplice applicazione, i due truffatori avrebbero trovato il modo di “dirottare” il video così ottenuto per sostituire le riprese della fotocamera dello smartphone.
Grazie a questo stratagemma, i criminali sarebbero riusciti ad accedere ai sistemi governativi e registrare delle società di facciata, per poi emettere false fatture e incassare i rimborsi IVA.
Il caso, però, sarebbe solo la punta dell’iceberg. La stessa tecnica verrebbe utilizzata, per esempio, allo scopo di ingannare i sistemi che regolano l’accesso in azienda per simulare la presenza sul posto di lavoro.
Insomma: dalle parti di Pechino si stanno facendo i conti con una tecnologia che mostra ancora elementi di immaturità e che con l’evoluzione dei deep fake rischia di entrare in una vera crisi.
The financial impact from a March 1 cyber-attack on CompuCom, a wholly-owned subsidiary of ODP Corporation, is expected to reach the $28 million range, the company said.
Following the incident, which resulted in some of the managed services provider’s systems being infected with malware, customer services and internal operations were suspended, but ODP now says that significant progress was made in restoring services.
Although no technical details on the incident were revealed, ODP claims that “the down time experienced and related impact due to the malware incident” will impact the revenue for March, with the financial results for the first fiscal quarter of 2021 likely impacted.
Thus, ODP estimates the loss of revenue to be between $5.0 million and $8.0 million, mainly the result of temporarily suspending services to certain customers.
Furthermore, the company expects expenses of up to $20 million associated with the incident, with approximately $10 million to be accrued during the first quarter of 2021.
These expenses, ODP says, are related to service restoration efforts and to addressing “certain other matters resulting from the incident.” Some of these expects might be covered by insurance, the company adds.
While delivery capabilities were substantially restored by March 17, the service delivery for all customers is only expected to be restored by the end of March 2021. CompuCom also took steps to harden the security of its systems.
ODP will provide further information on its first quarter financial performance during its first quarter earnings call, currently scheduled for May 5, 2021.
Report: US Gov Executive Order to Mandate Data Breach Disclosure
A proposed executive order would set new rules on the disclosure of data breaches that also affect United States government agencies, according to a Reuters news report.
The report said the executive order, which could be released as soon as the next week, would require software vendors to notify U.S. government customers of cyber-security breaches that also affect them.
Furthermore, the order is expected to force federal agencies to improve their security posture through the adoption of multi-factor authentication and data encryption within their environments.
When it comes to programs deemed critical, vendors might be forced to provide a “software bill of materials,” detailing program components and offering increased visibility into resources that could introduce additional vulnerabilities.
Per the order, software vendors would be asked to work together with specialized government agencies, such as the FBI and CISA, when investigating cyber-incidents.
Likely a reaction to the recent SolarWinds attacks, the order is expected to impact the interaction between major software vendors and government agencies.
More than one hundreds organizations, including multiple federal agencies, have been confirmed to be affected by the SolarWinds hack, but the overall number of victims could be greater.
What’s more, the SolarWinds attack is only one of the many cyber-incidents involving private companies that also has a major impact on government agencies. A December 2020 cyber-attack was linked to an assault on FireEye, which tests the defenses of thousands of customers, including federal, state and local governments.
In September 2020, Tyler Technologies, which provides software and services for state and local governments, disclosed a ransomware incident. However, the company said that software hosted for its clients was not affected.
Europe and the United States will use a thaw in ties to strike a pact that would allow for the exchange of private data across the Atlantic, replacing previous agreements struck down by an EU court.
Facebook, Google, Microsoft and thousands of other companies want such a deal to keep the internet traffic flowing without facing significant legal jeopardy over European privacy laws.
Last year, the European Court of Justice “raised important questions on how to ensure protection of privacy when data crosses the Atlantic,” EU Justice Commissioner Didier Reynders said in a speech to the American Chamber of Commerce to the EU.
“Finding this solution is a priority in Brussels and in Washington DC,” he added a day after stepping up talks with US Commerce Secretary Gina Raimondo.
As “like-minded partners” the two sides “should be able to find appropriate solutions on principles that are cherished on both sides of the Atlantic,” he said.
The third attempt for a new data arrangement would succeed deals that were invalidated after succesful lawsuits arguing that US security laws violated the fundamental rights of EU citizens.
The legal onslaught was led by Max Schrems, an Austrian activist and lawyer who began his campaign after the revelations by Edward Snowden of mass digital spying by US agencies.
Businesses have since resorted to legally uncertain workarounds to keep the data flow moving, with hope that the two sides could come up with something stronger in the long term.
Reynders said a deal would require that “complex and sensitive” issues are solved “that relate to the delicate balance between national security and privacy”.
The deal would have to cover important issues, including guarantees of access to courts and clearly enforceable individual rights.
“The only way to achieve this is to develop a new arrangement that is fully compliant with the (EU court’s) Schrems II judgement. This is in our mutual interest,” Reynders added.
The EU has concluded similar agreements with 12 entities and countries, including Japan, Switzerland, Canada, Israel, and is in the process of concluding negotiations with South Korea.
In February, Brussels gave an initial green light to the transfer of personal data to the UK, which left the EU’s direct jurisdiction this year after a post-Brexit transition period.
Facebook finally explains its mysterious new wrist wearable
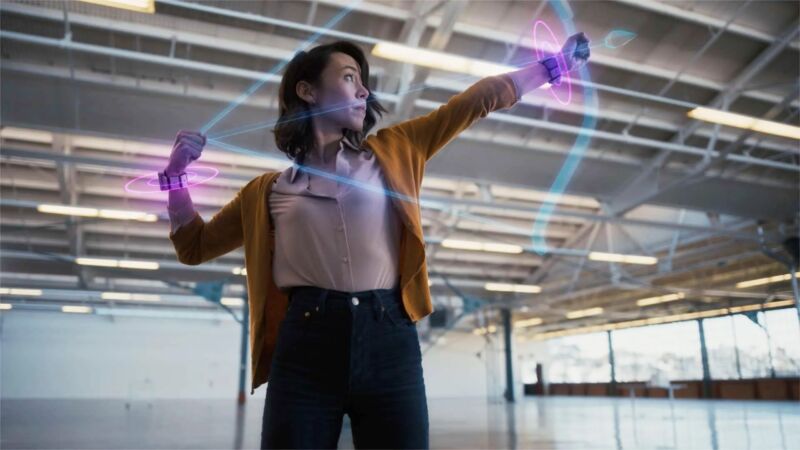
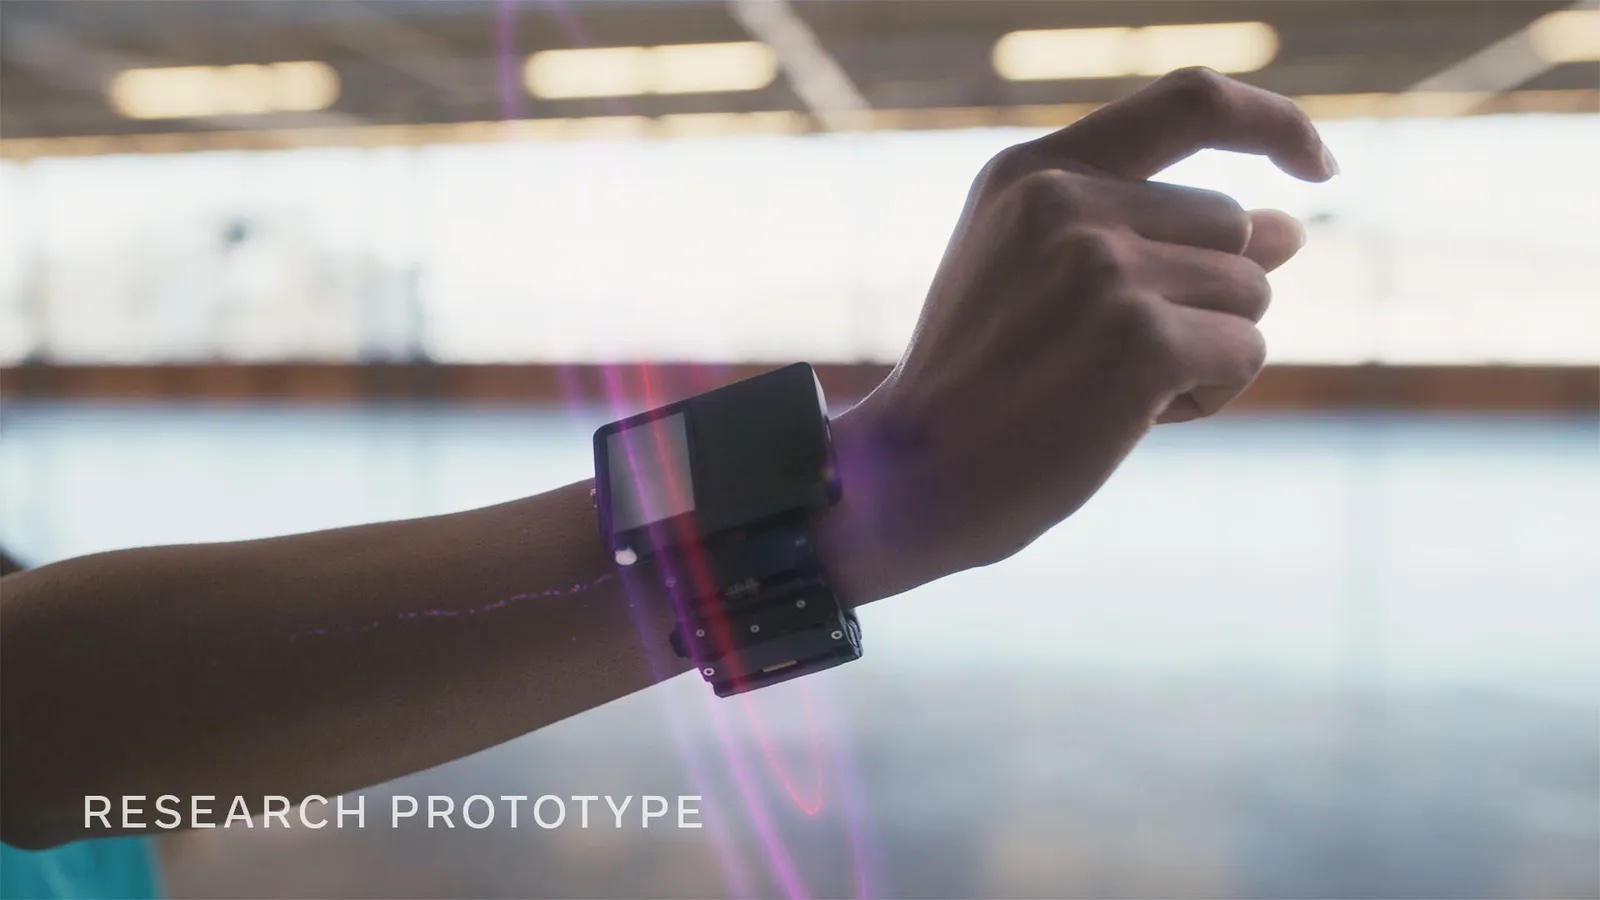
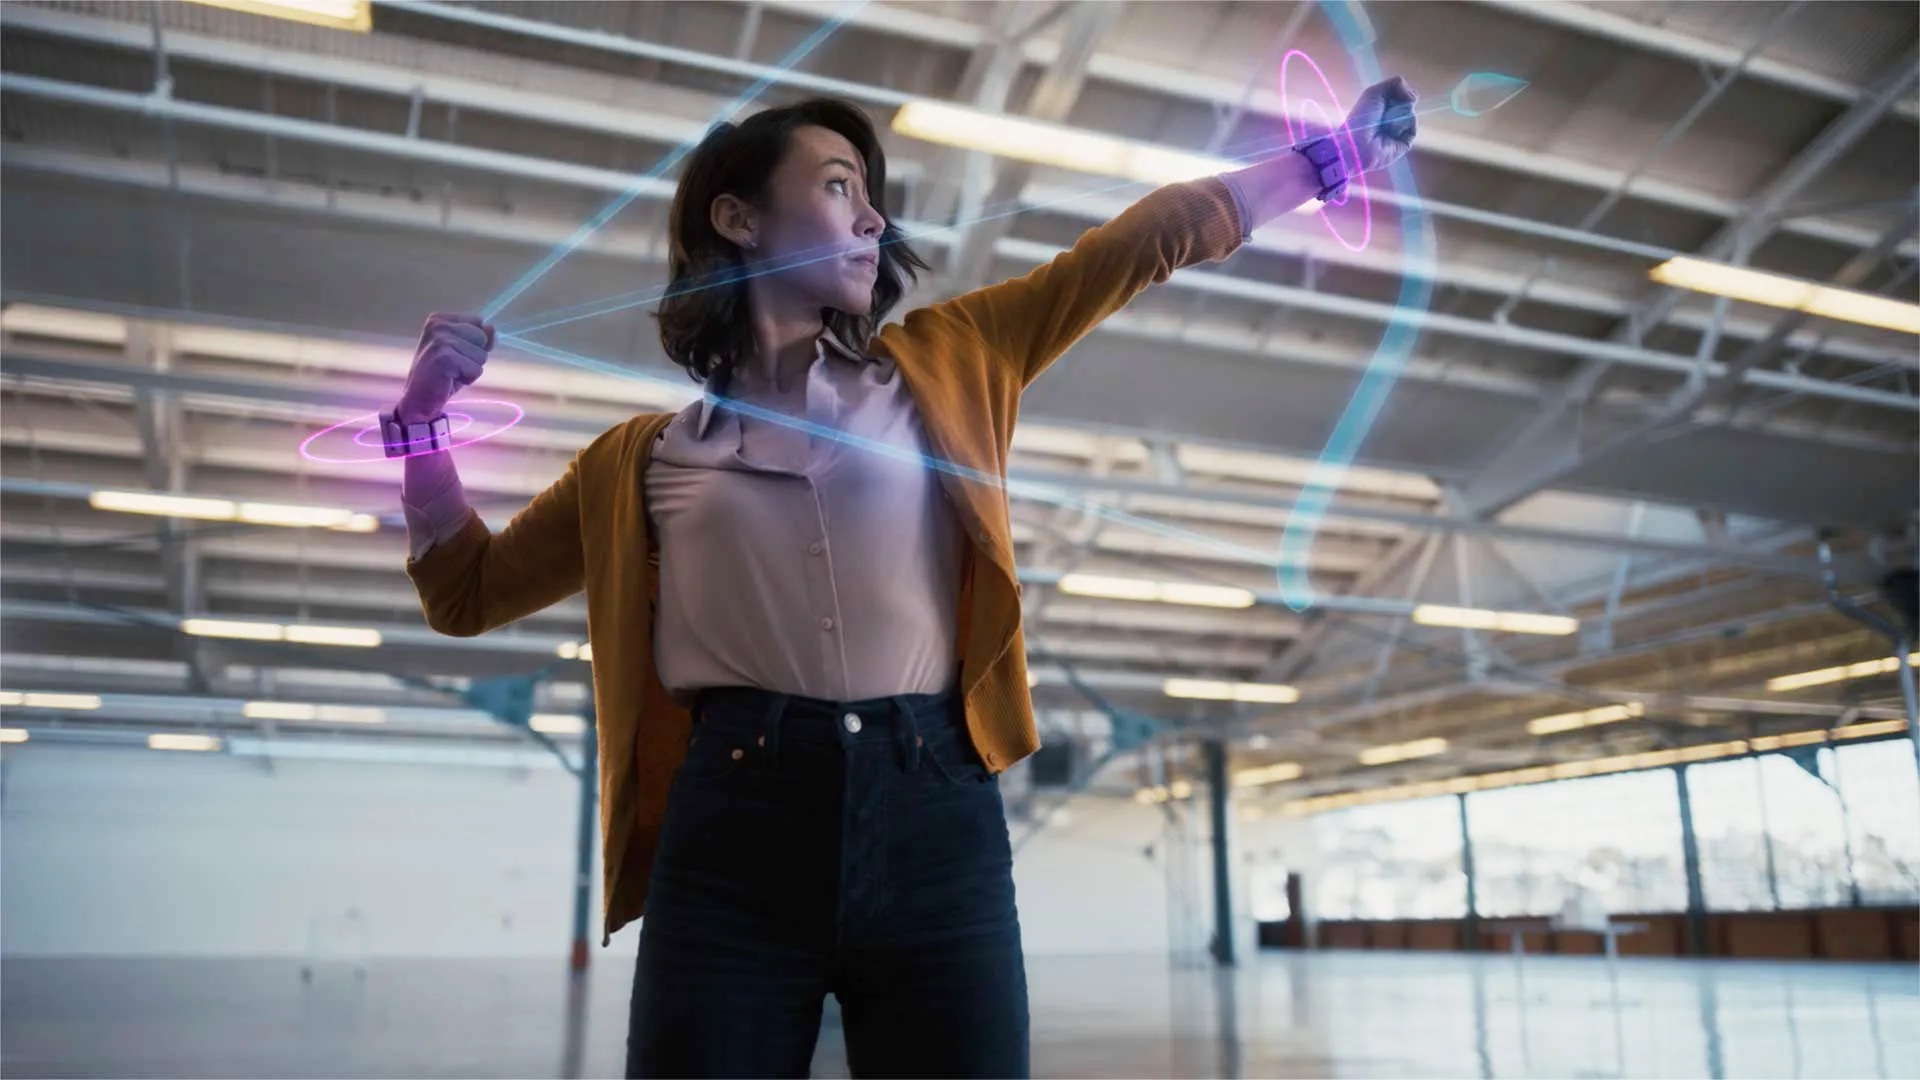
Enlarge/ Facebook is developing a wrist-worn wearable that senses nerve activity that controls your hands and fingers. The design could enable new types of human-computer interactions.
It first appeared on March 9 as a tweet on Andrew Bosworth’s timeline, the tiny corner of the Internet that offers a rare glimpse into the mind of a Facebook executive these days. Bosworth, who leads Facebook’s augmented and virtual reality research labs, had just shared a blog post outlining the company’s 10-year vision for the future of human-computer interaction. Then, in a follow-up tweet, he shared a photo of an as yet unseen wearable device. Facebook’s vision for the future of interacting with computers apparently would involve strapping something that looks like an iPod Mini to your wrist.
Facebook already owns our social experience and some of the world’s most popular messaging apps—for better or notably worse. Anytime the company dips into hardware, then, whether that’s a very good VR headset or a video chatting device that follows your every move, it gets noticed. And it not only sparks intrigue, but questions too: why does Facebook want to own this new computing paradigm?
In this case, the unanswered questions are less about the hardware itself and more about the research behind it—and whether the new interactions Facebook envisions will only deepen our ties to Facebook. (Answer: probably.) In a media briefing earlier this week, Facebook executives and researchers offered an overview of this tech. In simplest terms, Facebook has been testing new computing inputs using a sensor-filled wrist wearable.
It’s an electromyography device, which means it translates electrical motor nerve signals into digital commands. When it’s on your wrist, you can just flick your fingers in space to control virtual inputs, whether you’re wearing a VR headset or interacting with the real world. You can also “train” it to sense the intention of your fingers, so that actions happen even when your hands are totally still.
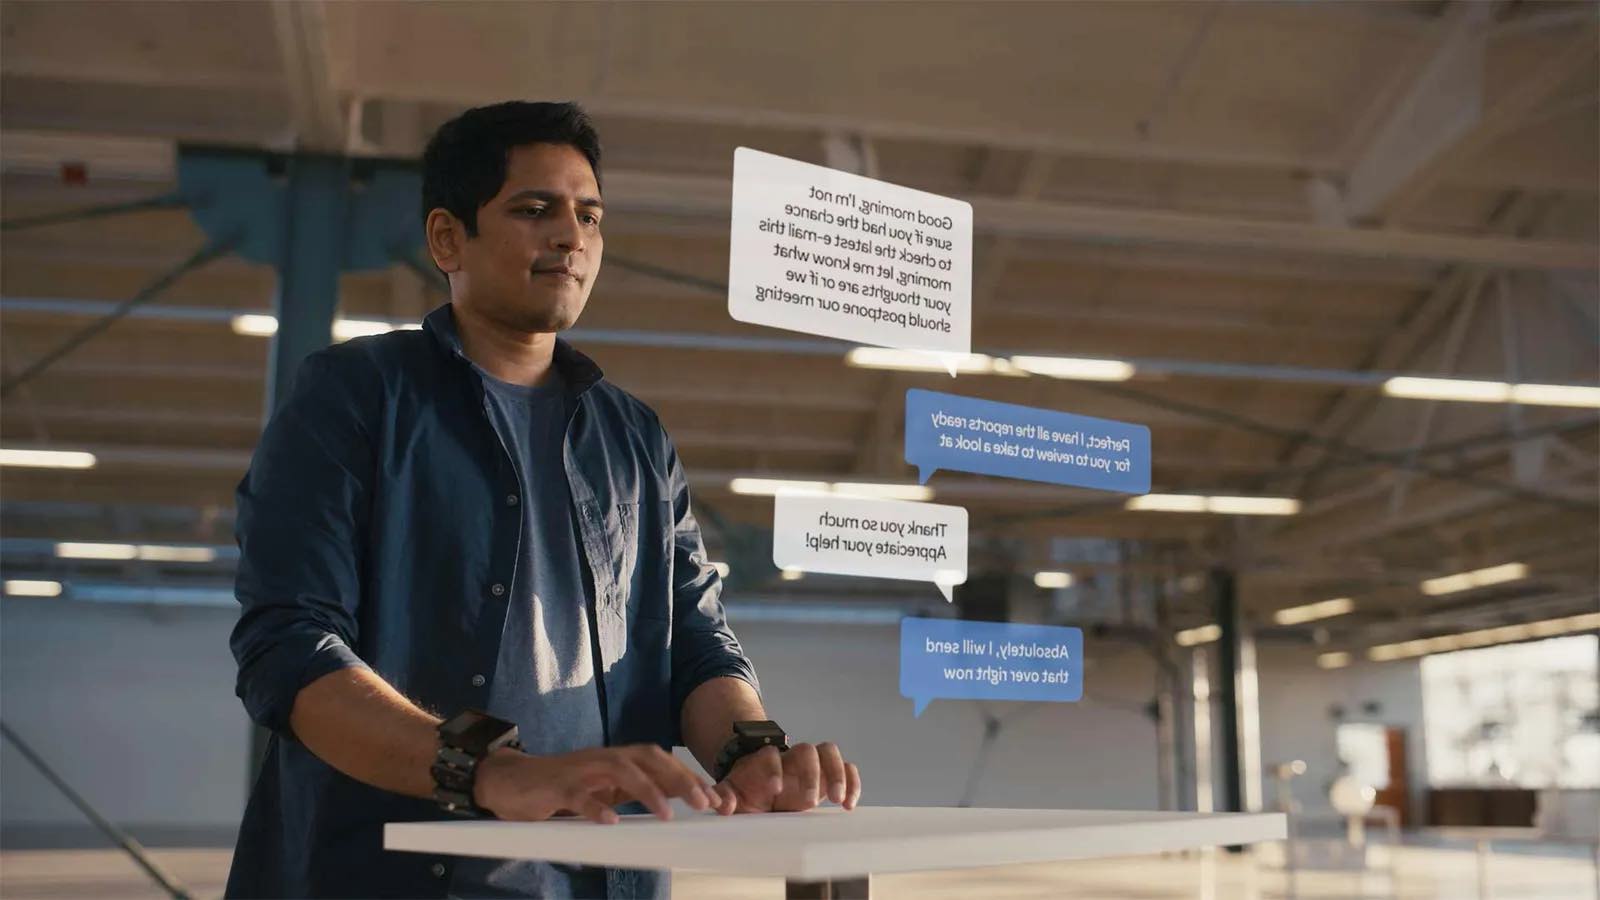
Enlarge/ Facebook’s vision for its wrist-worn device includes being able to type on a virtual desktop keyboard.
This wrist wearable doesn’t have a name. It’s just a concept, and there are different versions of it, some of which include haptic feedback. Bosworth says it could be five to 10 years before the technology becomes widely available.
All of this is tied to Facebook’s plans for virtual and augmented reality, technologies that can sometimes leave the user feeling a distinct lack of agency when it comes to their hands. Slip on a VR headset and your hands disappear completely. By picking up a pair of hand controllers, you can play games or grasp virtual objects, but then you lose the ability to take notes or draw with precision. Some AR or “mixed reality” headsets like Microsoft’s HoloLens have cameras that track spatial gestures, so you can use certain hand signals and the headset will interpret those signals … which sometimes works. So Facebook has been using this EMG wearable in its virtual reality lab to see if such a device might enable more precise hand-computer interactions.
But Facebook has visions for this wrist tech beyond AR and VR, Bosworth says. “If you really had access to an interface that allowed you to type or use a mouse—without having to physically type or use a mouse, you could use this all over the place.” The keyboard is a prime example, he says; this wrist computer is just another means of intentional input, except you can carry it with you everywhere.
Bosworth also suggested the kitchen microwave as a use case—while clarifying that Facebook is not, in fact, building a microwave. Home appliance interfaces are all different, so why not program a device like this to understand, simply, when you want to cook something for 10 minutes on medium power?
In the virtual demo Facebook gave earlier this week, a gamer was shown wearing the wrist device and controlling a character in a rudimentary video game on a flat screen, all without having to move his fingers at all. These kinds of demos tend to (pardon the pun) gesture toward mind-reading technology, which Bosworth insisted this is not. In this case, he said, the mind is generating signals identical to the ones that would make the thumb move, but the thumb isn’t moving. The device is recording an expressed intention to move the thumb. “We don’t know what’s happening in the brain, which is full of thoughts, ideas, and notions. We don’t know what happens until someone sends a signal down the wire.”
Bosworth also emphasized that this wrist wearable is different from the invasive implants that were used in a 2019 brain-computer interface study that Facebook worked on with the University of California at San Francisco; and it’s different from Elon Musk’s Neuralink, a wireless implant that could theoretically allow people to send neuroelectrical signals from their brains directly to digital devices. In other words, Facebook isn’t reading our minds, even if it already knows a heck of a lot about what’s going on in our heads.
Researchers say there’s still a lot of work to be done in the area of using EMG sensors as virtual input devices. Precision is a big challenge. Chris Harrison, the director of the Future Interfaces Group in the Human-Computer Interaction Lab at Carnegie Mellon University, points out that each individual human’s nerves are a little bit different, as are the shapes of our arms and wrists. “There’s always a calibration process that has to happen with any muscle-sensing system or BCI system. It really depends on where the computing intelligence is,” Harrison says.
And even with haptic feedback built into these devices, as Facebook is doing with some of its prototypes, there’s the risk of visuo-haptic mismatches, where the user’s visual experience—whether in AR, VR, or real space—does not correlate to the haptic response. These points of friction can make these human-computer interactions all feel frustratingly unreal.
Even if Facebook can overcome these obstacles in its research labs, there’s still the question of why Facebook—largely a software company—wants to own this new computing paradigm. And should we trust it? This hugely powerful tech company that has a track record of sharing user data in “exchange for other equally or more valuable things,” as WIRED’s Fred Vogelstein wrote in 2018? A more recent report in MIT Technology Review highlights how a team at Facebook assembled to tackle “responsible AI” was undermined by leadership’s relentless quest for growth.
Facebook executives said this week that these new human-computer interaction devices will perform as much computing as possible “on device,” which means the information isn’t shared to the cloud; but Bosworth won’t commit to how much data ultimately might be shared to Facebook or how that data will be used. The whole thing is a prototype, so there’s nothing substantive to tease apart yet, he says.
“Sometimes these companies have cash piles large enough to basically invest in these huge R&D projects, and they’ll take a loss on such things if it means they can be front-runners in the future,” says Michelle Richardson, director of the Data and Privacy Project at the nonprofit Center for Democracy and Technology. “But with companies of any size, any product, once it’s built, it’s so difficult to overhaul it. So anything that can start the conversation on this before the devices are built is a good thing.”
Bosworth says Facebook wants to lead this next paradigm shift in computing because the company sees tech like this as fundamental to connecting people. If anything, this past year has shown us the importance of connecting—of feeling like you’re in person, Bosworth says. He also seems to believe he can earn the required trust by not “surprising” customers. “You say what you do, you set expectations, and you deliver on those expectations over time” he says. “Trust arrives on foot and leaves on horseback.” Rose-colored AR glasses, activated.
Zuckerberg: Facebook could be in “stronger position” after Apple tracking change
Apple CEO Tim Cook on stage during an Apple event in September 2018.
With Apple’s big app-tracking policy change just around the corner, Chinese companies drew a warning from Cupertino that their efforts to circumvent the change will not be successful. At the same time, Facebook CEO Mark Zuckerberg appeared to shift his messaging about the change.
Several months ago, Apple announced that it will require user opt-in for IDFA (Identifier for Advertisers), a tool that advertisers use to identify and track users across apps and websites. If users opt in, it will be business as usual. But if they decline, the app in question will not be able to use that tracking method. The change will apply to all iPhone and iPad apps, and it will take full effect in iOS 14.5, which is due out sometime in the next few weeks.
ByteDance, Baidu, and others push back
Press coverage so far has focused on US and European countries grappling with the change, particularly Facebook, which ran ads and looked into the possibility of an antitrust lawsuit to battle Apple’s decision. Several reports over the past few days have indicated that some major Chinese tech companies are no less determined to fight or get around Apple’s new policy.
Baidu, Tencent, and ByteDance are among the Chinese tech companies seeking workarounds. Bloomberg reports that these companies have sought multiple ways to collect data and track users despite Apple’s policy, including fingerprinting, “which uses device-specific information such as the IMEI number and location to create a unique identifier.” And they are also testing a system called CAID. Developed by a government think tank and the China Advertising Association, this system can be used “as a substitute if the user’s IDFA is unavailable.”
The companies’ efforts led Apple to release a statement clarifying that the upcoming changes apply to all apps from companies around the world, not just those developed and maintained in the United States:
The App Store terms and guidelines apply equally to all developers around the world, including Apple. We believe strongly that users should be asked for their permission before being tracked. Apps that are found to disregard the user’s choice will be rejected.
The actions of these companies nonetheless threaten to put Apple in a difficult position. China accounts for at least 15 percent of Apple’s business. Although it’s too early to make absolute predictions and it depends on the role the Chinese government chooses to play here, it is plausible that this situation could escalate to the point where Apple would have to make a decision about continuing to do business there or changing course to make special ad tracking rules for that country that differ from those in place in other regions.
Zuckerberg changes tune
Speaking in a Clubhouse chat on Thursday, Zuckerberg took a more positive stance regarding Facebook’s ability to thrive with the upcoming change. “We’ll be in a good position,” he said. “We’ll be able to manage through.”
Facebook had previously run full-page newspaper ads suggesting Apple’s change could mortally wound countless small businesses, and Facebook CFO David Wehner posited last year that the change would lead to a 50% drop for its lucrative Audience Network advertising business.
Zuckerberg also took an aggressive initial stance against the change in the company’s last quarterly earnings call, and The Information reported that he was working with legal counsel to build an antitrust case against Apple as a way to battle the policy shift.
But yesterday, Zuckerberg went so far as to say:
It’s possible that we may even be in a stronger position if Apple’s changes encourage more businesses to conduct more commerce on our platforms by making it harder for them to use their data in order to find the customers that would want to use their products outside of our platforms.
While the messaging differs, the companies’ planned actions don’t seem likely to change. Apple will still begin requiring Facebook’s apps ask users for permission to track them, and Facebook still plans on acquiescing to the change so it can keep making its apps and services available to iOS users.
https://arstechnica.com/?p=1750949
One company wants to sell the feds location data from every car on Earth
Enlarge/ Cars driving down I-80 in Berkeley, California, in May, 2018 when there were still places to go.
There is a strange sort of symmetry in the world of personal data this week: one new report has identified a company that wants to sell the US government granular car location data from basically every vehicle in the world, while a group of privacy advocates is suing another company for providing customer data to the feds.
A surveillance contractor called Ulysses can “remotely geolocate vehicles in nearly every country except for North Korea and Cuba on a near real-time basis,” Vice Motherboard reports.
“Among the thousands of other data points, vehicle location data is transmitted on a constant and near real-time basis while the vehicle is operating,” the company wrote in a sales pitch document obtained by Vice. As roughly 100 million new cars are manufactured worldwide each year that are “increasingly connected to the manufacturer, other vehicles, infrastructure, and their owners, it becomes apparent that telematics will revolutionize intelligence,” the document adds. Ulysses claims it can currently access more than 15 billion vehicle locations around the world every month, and it estimates that by 2025, 100 percent of new cars will be connected and transmitting gigabytes of collectible data per hour.
Vice said the office of Sen. Ron Wyden (D-Ore.), who serves on the Senate Intelligence Committee and often advocates for privacy issues, provided it with the document. “Sen. Wyden is conducting an ongoing investigation into the sale of personal data, particularly via data brokers, to put some sunlight on this shady industry,” Keith Chu, a representative for Wyden’s office, told Vice. “Our office is continuing to perform oversight into where data brokers are acquiring Americans’ information and who they’re selling it to.”
Ulysses does not currently have any contracts with the US government but has worked in the past with US Special Operations Command (SOCOM), Vice reports. That contract, which ran from 2016-2017, involved data SOCOM used “to deepen our understanding on how foreign competitors used economic and financial tools against US interests” in Central and South America and in Africa.
Meanwhile, in California…
If Ulysses does snag a federal contract, it would be joining a long line of other firms that sell personal user data to the government.
The Washington Post reported last month that ICE also purchased access to a database chock-full of consumer information to track immigrants. The database ICE used, CLEAR, includes more than 400 million phone, water, electricity, and other utility documents the agency would otherwise not have been able to access on its own, according to the Post.
A coalition of privacy advocates in California is now suing Thomson Reuters, which operates CLEAR, alleging that it violates state privacy law by collecting and sharing personal information without individuals’ consent.
“When we look at the ways that these data brokers are remaking our country, the Fourth Amendment concerns are terrifying,” Surveillance Technology Oversight Project Executive Director Albert Fox Cahn, who is participating in the suit, told the Post. “But the way that they’re allowing companies to track millions without the most basic consent is deeply alarming as well.”
Sen. Wyden also told the Post he plans to introduce federal legislation soon to close the loopholes that allow such data sales. “I do think that there’s going to be a new focus on privacy in this session,” Wyden said. “I think as more and more states pass privacy legislation, pressure builds for Congress to finally pass federal legislation.”


 Tags:


 Tags:


 Tags:


 Tags:


 Tags: