Research: Security Agencies Expose Information via Improperly Sanitized PDFs

Most security agencies fail to properly sanitize Portable Document Format (PDF) files before publishing them, thus exposing potentially sensitive information and opening the door for attacks, researchers have discovered.

An analysis of roughly 40,000 PDFs published by 75 security agencies in 47 countries has revealed that these files can be used to identify employees who use outdated software, according to Supriya Adhatarao and Cédric Lauradoux, two researchers with the University Grenoble Alpes and France’s National Institute for Research in Computer Science and Automation (Inria).

The analysis also revealed that the adoption of sanitization within security agencies is rather low, as only 7 of them used it to remove hidden sensitive information from some of their published PDF files. What’s more, 65% of the sanitized files still contained hidden data.

“Some agencies are using weak sanitization techniques: it requires to remove all the hidden sensitive information from the file and not just to remove the data at the surface. Security agencies need to change their sanitization methods,” the academic researchers say.

PDF files, the researchers note, represent collections of indirect objects (eight types of objects: arrays, boolean, dictionaries, names, numbers, streams, strings, and the null object) that are used to store data. These objects may include hidden data not visible when viewing the PDF.

Per the NSA, there are 11 main types of hidden data in PDF files, namely metadata; embedded content and attached files; scripts; hidden layers; embedded search index; stored interactive form data; reviewing and commenting; hidden page, image and update data; obscured text and images; PDF comments that are not displayed; and unreferenced data.

Metadata associated with images within a PDF file can be used to gather information about the author, the same as comments and annotations that haven’t been removed before publishing, and PDF metadata.

There are several tools that can be used for sanitizing PDF files, including Adobe’s Acrobat, and there are four levels of sanitization: Level-0: full metadata (no sanitization), Level-1: partial metadata, Level-2: no metadata, and Level-3: properly cleaned files (full sanitization, with all objects having been removed).

For their research, the academics used a set of 39,664 PDF files. Of these, 1,783 (4%) were found to include author name, 30,155 (76%) contained metadata on the PDF producer tool, and 16,805 (42%) revealed the operating system used.

The files also leaked email addresses – including official ones – (in 52 files), hardware brand (581 files), and paths (1,814 PDFs).

“During our analysis we observed that many agencies include more than one author publishing the PDF files. It is possible to download all the PDF files published on a security agency’s website and observe the author habits, OS trends,” the researchers note.

The analysis also allowed for the identification of 159 employees at 19 agencies that haven’t updated tools over a period of two years, which could be abused by threat actors in targeted attacks, especially since nearly half of the PDF files leaked operating system data.

While 9,509 (24%) of the analyzed PDF files have been sanitized before publishing, only 3,313 (8%) were sanitized with Level-3. The researchers note that only 3 agencies out of 7 that appear to care about sanitization are doing it properly.

“The issue is that popular PDF producer tools are keeping metadata by default with many other information while creating a PDF file. They provide no option for sanitization or it can only be achieved by following a complex procedure. Software producing PDF files need to enforce sanitization by default. The user should be able to add metadata only as an option,” the academics conclude.

Related: Adobe Open Sources Tool for Sanitizing Logs, Detecting Exposed Credentials

Related: Researchers Disclose New Methods for Replacing Content in Signed PDF Files

view counter

Ionut Arghire is an international correspondent for SecurityWeek.

Previous Columns by Ionut Arghire:
Tags:

http://feedproxy.google.com/~r/Securityweek/~3/EN-iO9AUvgc/research-security-agencies-expose-information-improperly-sanitized-pdfs


Sorveglianza di massa per gli utenti di internet, sotto accusa gli Affari Interni britannici

La navigazione di internet non è mai davvero in solitaria, abbiamo imparato nel tempo che ci può sempre essere qualcuno che ci spia, che ci segue più o meno di nascosto. Sappiamo anche, in linea di massima, chi può essere questo qualcuno e a volte è lo Stato.

Sorveglianza di massa su internet

Negli ultimi due anni, nel Regno Unito, l’Home Office, il ministero degli Affari Interni (omologo del nostro ministero dell’Interno), sta sperimentando diversi sistemi e strumenti di raccolta dati sulle attività dei cittadini online, per quello che le associazioni di attivisti per i diritti di internet e per la difesa della privacy hanno chiamato senza mezzi termini: “un sistema di sorveglianza di massa statale”.

<!-- LARGE RECTANGLE POST - CORPO TESTO

-->

Sostanzialmente, secondo l’accusa, lo Stato avrebbe costruito e testato silenziosamente una tecnologia di sorveglianza in grado di registrare e memorizzare la navigazione web di ogni singola persona in tutto il Paese per poi dare vita a dei “record di dati segreti”.

I primi test sarebbero partiti nel 2019.

L’accusa

Gli attivisti dell’Open Rights Group denunciano una campagna governativa di “raccolta e conservazione di massa di dati su quello che i cittadini fanno su internet”, in piena violazione delle leggi sulla privacy, senza la minima trasparenza necessaria in questo tipo di operazioni, almeno per non destare sospetti e timori tra la popolazione.

Tutto è nato da un Rapporto esclusivo pubblicato su Wired UK, in cui si delinea un piano dell’Home Office di monitoraggio di massa sull’utilizzo di internet, finalizzato al miglioramento dei livelli di sicurezza nazionale e di operatività delle Forze dell’Ordine nella lotta al crimine organizzato e al terrorismo interno ed internazionale.

Secondo il documento, gli Affari Interni stanno collaborando con la National Crime Agency per raccogliere numerosi “record di connessione Internet” (o ICR), che contengono informazioni sui siti web visitati da parte degli utenti, su cosa è stato visto e scaricato.

La difesa

Sull’argomento, l’Home Office ha dichiarato pubblicamente che si tratta di una raccolta di metadati, non riferibili a nessuno in particolare, neanche riferibili a contenuti specifici che si sono selezionati nella ricerca, o alle stesse pagine web navigate.

La sperimentazione portata avanti dal Governo ha coinvolto due provider nazionali e si fa scudo dell’Investigatory Powers Act 2016, con l’obiettivo di capire come raccogliere i dati sull’utilizzo di internet da parte dei cittadini, quali dati raccogliere e come poterli usare nelle indagini di polizia.

Dei principali provider internet del Regno Unito, solo Vodafone ha confermato di non essere coinvolta in alcun test che implichi l’archiviazione dei dati di navigazione riferibili a singoli cittadini. I portavoce di BT, Tre e Virgin Media, invece, si sono rifiutati di fornire commenti su qualsiasi tipo di azione riferibile all’IPA.

https://www.key4biz.it/sorveglianza-di-massa-per-gli-utenti-di-internet-sotto-accusa-gli-affari-interni-britannici/349998/


Data Privacy Management Firm DataGrail Raises $30 Million

California-based data privacy management company DataGrail this week announced that it raised $30 million in a Series B funding round.

The company previously raised $5.2 million in a Series A round in 2019. The latest funding round was led by Felicis Ventures, with participation from HubSpot, Okta, Next47 (venture firm backed by Siemens), Basis Set Ventures, Operator Collective, and previous investors.

DataGrail provides a platform designed to help organizations simplify, automate and scale their privacy programs. The platform, which automates data subject requests, is powered by a live data map that enables customers to know exactly where data lives on their systems, with any changes being automatically reflected.

DataGrail provides integration with more than 900 apps and infrastructure, and integrations are maintained by the company itself.

The company says its services are used by millions of consumers through firms such as Overstock, RH, Databricks and Outreach.

“Privacy laws, like CCPA and GDPR, give people the right to have their data deleted, or refuse its sale, but modern organizations are ill-prepared for the Privacy Era,” said Daniel Barber, CEO and co-founder of DataGrail. “To combat the massive privacy challenges businesses face today, we’ve built a platform that makes it remarkably easy to untangle what’s become a spider web of data across the entire tech stack. DataGrail elegantly solves this near-impossible task for organizations that want to do right by their customers.”

Related: Data Governance and Security Provider Privacera Raises $13.5 Million

Related: Developer Security Firm Snyk Raises $300 Million at $4.7 Billion Valuation

Related: Aqua Security Achieves Unicorn Status After $135 Million Funding Round

Related: XDR Firm Cynet Raises $40 Million Series C Funding

view counter

Eduard Kovacs (@EduardKovacs) is a contributing editor at SecurityWeek. He worked as a high school IT teacher for two years before starting a career in journalism as Softpedia’s security news reporter. Eduard holds a bachelor’s degree in industrial informatics and a master’s degree in computer techniques applied in electrical engineering.

Previous Columns by Eduard Kovacs:
Tags:

http://feedproxy.google.com/~r/Securityweek/~3/D5ZCcd5u09A/data-privacy-management-firm-datagrail-raises-30-million


Facial Recognition Company Sued by California Activists

Civil liberties activists are suing a company that provides facial recognition services to law enforcement agencies and private companies around the world, contending that Clearview AI illegally stockpiled data on 3 billion people without their knowledge or permission.

The lawsuit, filed Tuesday in Alameda County Superior Court in the San Francisco Bay Area, contends that the New York-based firm violates California’s constitution and seeks an injunction to bar it from collecting biometric information in California and requiring it to delete data on Californians.

The lawsuit says the company has built “the most dangerous” facial recognition database in the nation, has fielded requests from more than 2,000 law enforcement agencies and private companies, and has amassed a database nearly seven times larger than the FBI’s.

The lawsuit was filed by four activists and the groups Mijente and Norcal Resist, who have supported causes such as Black Lives Matter and have been critical of the policies of U.S. Immigration and Customs Enforcement, which has a contract with Clearview AI.

“Clearview has provided thousands of governments, government agencies, and private entities access to its database, which they can use to identify people with dissident views, monitor their associations, and track their speech,” the lawsuit contends.

The lawsuit said Clearview AI scrapes dozens of internet sites, such as Facebook, Twitter, Google and Venmo, to gather facial photos. Scraping involves the use of computer programs to automatically scan and copy data, which the lawsuit says is analyzed by Clearview AI to identify individual biometrics such as eye shape and size that are then put into a “faceprint” database that clients can use to ID people.

The images scraped include those posted not only by individuals and their family and friends but also those of people who are inadvertently captured in the background of strangers’ photos, according to the lawsuit.

The company also offers its services to law enforcement even in cities that ban the use of facial recognition, the lawsuit alleges.

Several cities around the country, including the Bay Area cities of Alameda, San Francisco, Oakland and Berkeley, have limited or banned the use of facial recognition technology by local law enforcement.

“Clearview AI complies with all applicable law and its conduct is fully protected by the First Amendment,” said a statement from attorney Floyd Abrams, representing the company.

The company has said it saw law enforcement use of its technology jump 26% following January’s deadly riot at the U.S. Capitol.

Facial recognition systems have faced criticism because of their mass surveillance capabilities, which raise privacy concerns, and because some studies have shown that the technology is far more likely to misidentify Blacks and other people of color than whites, which has resulted in mistaken arrests.

However, Clearview AI’s CEO, Hoan Ton-That, said in a statement that “an independent study has indicated the Clearview AI has no racial bias.”

“As a person of mixed race, having non-biased technology is important to me,” he said.

He also argued that the use of accurate facial recognition technology can reduce the chance of wrongful arrests.

The lawsuit said Facebook, Twitter, Google and other social media firms have asked Clearview AI to stop scraping images because it violated their terms of service with users.

Clearview AI also is facing other challenges. A lawsuit filed in Illinois alleges the company violates that state’s biometric privacy act, while privacy watchdogs in both Canada and the European Union have issued statements of concern.

Clearview stopped operations in Canada last year. But privacy commissioners this year asked the firm to remove data on Canadian citizens, with one commissioner arguing that the system puts all Canadians “continually in a police lineup.”

Related: Canada Probe Concludes Clearview AI Breached Privacy Laws

Related: Facial Recognition: IT and Police in Delicate Dance

view counter

Previous Columns by Associated Press:
Tags:

http://feedproxy.google.com/~r/Securityweek/~3/FoRE_AJa5zY/facial-recognition-company-sued-california-activists


Tausight Raises $20M to Protect Healthcare Data

Patient data protection provider Tausight this week announced that it has raised $20 million in Series A funding.

The new funding, Tausight says, will help expand the go-to-market team and invest in a healthcare-specific solution designed to identify security flaws in clinical workflows.

The new funding round was co-led by existing investors Polaris Partners and Flare Capital Partners. New investor .406 Ventures also participated.

Founded in 2018 and based in Boston, Mass., Tausight aims to help organizations ensure the confidentiality, integrity, and availability of patients’ protected health information (PHI).

Tausight’s offerings help healthcare provider CIOs, CISOs, and IT organizations understand the risk associated with the manner in which PHI is used, and help them secure access to clinical workflows and PHI.

“Existing cybersecurity solutions address critical aspects of securing the healthcare IT system but are not adequately addressing hidden vulnerabilities found in clinical workflows – Tausight was created to close this gap and solve this vital problem,” Tausight CEO Dave Dickinson said.

Related: Snyk Raises $300 Million at $4.7 Billion Valuation

Related: Cyber Insurance Provider Corvus Raises $100 Million

Related: OwnBackup Achieves ‘Unicorn’ Status With $167.5M Funding

view counter

Ionut Arghire is an international correspondent for SecurityWeek.

Previous Columns by Ionut Arghire:
Tags:

http://feedproxy.google.com/~r/Securityweek/~3/gSsIrOndL-8/tausight-raises-20m-protect-healthcare-data


Chrome, i cookie di terze parti e il gioco delle tre carte di Google

La rubrica “Digital & Law” è curata da D&L Net e offre una lettura delle materie dell’innovazione digitale da una prospettiva che sia in grado di offrire piena padronanza degli strumenti e dei diritti digitali, anche ai non addetti ai lavori. Per consultare tutti gli articoli clicca qui.

Articolo dell’avv. Mario Montano di Studio Legale Lisi- Componente del D&L Net

Il così chiacchierato addio di Chrome ai cookies di terze parti a partire dal 2022 non è una novità assoluta. Infatti era un’azione già conosciuta da anni, basti pensare a Safari di Apple e Firefox Focus della Mozilla Foundation che bloccano di default i cookies di terze parti.

<!-- LARGE RECTANGLE POST - CORPO TESTO

-->

Google e l’addio ai cookie di terze parti su Chrome

La vera notizia è semmai che la società che detiene il monopolio delle attività di advertising, Google, ha deciso di rinunciare allo strumento più utilizzato dalle società pubblicitarie per tracciare gli utenti, profilarli e scambiare la loro esperienza sul web, le loro impression, nei Real Time Bidding (RTB), le aste in tempo reale degli spazi pubblicitari online. Bisogna chiarire che i cookie sono solo uno degli strumenti utilizzati per tracciare e profilare gli utenti e che oggi, con un po’ di esperienza, è possibile bloccare quasi del tutto. Inoltre, altri e più sofisticati strumenti sono stati sviluppati negli ultimi anni, come: local storage; indexedDB; webSQL; Service worker.

Quest’ultimo merita un breve approfondimento.

Service worker

È uno script eseguito in background dal browser, integratosi con le Progressive Web App (PWA), un ibrido a metà strada tra una pagina web e un’applicazione nativa. Questo permette di gestire le notifiche push, la sincronizzazione in background e il salvataggio dei dati in locale, che consente la navigazione offline. Fra non molto il service worker permetterà di implementare nelle PWA nuove e più pervasive funzionalità, come la geofencing e la sincronizzazione periodica.

Google e PWA

Ritorniamo su Google, è stata proprio quest’ultima, nel 2015, a coniare il termine Progressive Web App e ad annunciare la finedelle Chrome apps in favore delle PWA a partire dal 2022, anno in cui è previsto,  l’abbandono dei cookies di terze parti.

Google ha chiarito che se la pubblicità digitale non evolve verso un modello che tenga conto delle crescenti preoccupazioni degli utenti rispetto alla protezione dei dati personali, a rischio è il futuro stesso del web libero e gratuito così come si presenta oggi. Secondo Google, infatti, bloccare i cookie di terze parti favorisce l’uso opaco e fraudolento del fingerprinting, metodo che consente di creare un profilo unico dell’utente basato sull’hardware, il software, i componenti aggiuntivi e perfino le preferenze del browser, tracciando l’utente per mesi, anche dopo aver eliminato i dati del browser o aver scelto di navigare in modalità anonima, ignorando le indicazioni dell’utente sul fatto di non voler essere tracciato.

Per conservare la asserita gratuità, libertà del web e al contempo rispettare la privacy degli utenti, Google ha avviato Sandbox Privacy, un progetto aperto agli stakeholder e alle autorità di regolamentazione che si propone di sviluppare un ecosistema privacy-oriented.

Non solo Privacy

Uno dei componenti del SendBox è la Federated Learing Technology, tecnologia di IA basata sulla machine learning. L’intento è di utilizzare la cronologia di Chrome per creare dei raggruppamenti omogeni degli utenti, i quali vengono successivamente assegnati a un gruppo chiamato “flock”. Ogni utente sarà in seguito identificato con il proprio flock name, che lo colloca all’interno del gruppo di utenti con le medesime caratteristiche.

Il tentativo di Google di superare la profilazione fondata sui cookie di terze parti con un sistema di clusterizzazione degli utenti, se da una parte potrebbe garantire una maggiore protezione dei dati personali, dall’altra rischia di esacerbare le discriminazioni già presenti nella targhettizzazione. Non è, quindi, solo una questione di privacy: la profilazione per gruppi omogeni di utenti permetterebbe comunque agli inserzionisti di utilizzare le caratteristiche etniche, i convincimenti politici o religiosi, il genere o l’età per inviare pubblicità mirata e potenzialmente discriminatoria. Non solo, si rischierebbe di agevolare e potenziare tutte quelle attività tese a influenzare il pensiero politico delle masse, confinando in bolle sempre più omogenee e isolate gli utenti con caratteristiche simili, rappresentando un rischio concreto per i principi democratici.

Nella recente Risoluzione del Parlamento europeo del 20 ottobre 2020 recante “raccomandazioni alla Commissione concernenti il quadro relativo agli aspetti etici dell’intelligenza artificiale, della robotica e delle tecnologie correlate”, si ricorda che “l’analisi dei dati e l’IA influenzano sempre di più le informazioni rese accessibili ai cittadini” e che “tali tecnologie, se utilizzate impropriamente, possono mettere in pericolo i diritti fondamentali alla libertà di espressione e all’informazione, nonché la libertà e il pluralismo dei mezzi di comunicazione”[1]. Il Parlamento europeo auspica uno sviluppo antropocentrico delle soluzioni di IA, a tutela della dignità, dell’autonomia e della sicurezza umane.

Chrome: il gioco delle tre carte di Google

Quella di Google non è una crociata contro l’uso spregiudicato e disinvolto dei cookie di terze parti o il fingerprinting come vorrebbe farci credere, quanto, piuttosto, forse una strategia ben congegnata per continuare a fare profitti con l’advertising, settore nel quale è e vuole rimanere leader, sviluppando tecnologie, come le PWA e sistemi di IA in grado di offrire all’utente servizi più rapidi ed efficienti, ma, al contempo, raccogliendo in maniera sempre più opaca e insondabile i suoi dati, accrescendo, come detto, il rischio di discriminazioni.

Un gioco delle tre carte quello di Google che, di fronte a una maggiore consapevolezza degli utenti e una legislazione sempre più rigorosa sull’uso di cookie di terze parti e sulla profilazione in rete, “sceglie di cambiare rotta perché nulla cambi”, forte della posizione dominante di Chrome.

E se iniziassimo a scegliere servizi più rispettosi dei diritti degli utenti? Le alternative non mancano e alla fine una buona conoscenza ed informazione potrebbe far vacillare Big G.

https://www.key4biz.it/chrome-i-cookie-di-terze-parti-e-il-gioco-delle-tre-carte-di-google/349771/


Hackers access security cameras inside Cloudflare, jails, and hospitals

Hackers access security cameras inside Cloudflare, jails, and hospitals
Getty Images

Hackers say they broke into the network of Silicon Valley startup Verkada and gained access to live video feeds from more than 150,000 surveillance cameras the company manages for Cloudflare, Tesla, and a host of other organizations.

The group published videos and images they said were taken from offices, warehouses, and factories of those companies as well as from jail cells, psychiatric wards, banks, and schools. Bloomberg News, which first reported the breach, said footage viewed by a reporter showed staffers at Florida hospital Halifax Health tackling a man and pinning him to a bed. Another video showed a handcuffed man in a police station in Stoughton, Massachusetts, being questioned by officers.

“I don’t think the claim ‘we hacked the internet’ has ever been as accurate as now,” Tillie Kottmann, a member of a hacker collective calling itself APT 69420 Arson Cats, wrote on Twitter.

Hardcoded credentials

Kottmann told Ars that the hack was made possible after Verkada exposed an unprotected internal development system to the Internet. It contained credentials for an account that had super admin rights to the Verkada network. Once inside the network, the hackers said they had access to feeds from 150,000 cameras, some of which provided high-definition video and used facial recognition.

In a statement, a Verkada spokesperson wrote: “We have disabled all internal administrator accounts to prevent any unauthorized access. Our internal security team and external security firm are investigating the scale and scope of this issue, and we have notified law enforcement.”

A Cloudflare representative, meanwhile, wrote:

This afternoon we were alerted that the Verkada security camera system that monitors main entry points and main thoroughfares in a handful of Cloudflare offices may have been compromised. The cameras were located in offices that have been officially closed for nearly a year. As soon as we became aware of the compromise, we disabled the cameras and disconnected them from office networks. To be clear, no customer data or processes have been impacted by this incident.

Tesla didn’t immediately respond to a request for comment.

Kottmann is a Switzerland-based software engineer who last year leaked 20GB of Intel source code and proprietary data. Other companies whose data has reportedly been breached by Kottmann include AMD, Microsoft, Adobe, Lenovo, Qualcomm, and Motorola. Those breaches also relied on hardcoded credentials in Internet-exposed repositories.

Kottmann said the hackers collected about 5GB of data from Verkada but could have obtained much more.

https://arstechnica.com/?p=1748489


I cyber criminali attaccano il forum Maza dedicato al cyber crimine


Il sito vittima di un data breach a opera di pirati informatici. L’attacco ha permesso di sottrarre le informazioni di tutti gli utenti registrati.

È possibile fare conto su una qualche forma di fiducia tra cyber criminali? La risposta è no. A confermarlo è il recente cyber attacco ai danni di Maza, un forum russo che (almeno in teoria) non avrebbe alcun motivo di preoccuparsi di subire un attacco.

Maza, infatti, è uno dei forum più frequentati dai pirati informatici, che lo usano per la compravendita di malware e exploit.

L’attacco, secondo quanto si legge in un report della società di sicurezza Flashpoint,  avrebbe consentito agli hacker di sottrarre un gran numero di informazioni dal database del sito, tra cui gli ID, le email usate per la registrazione, le password (protette da algoritmi di hashing) e gli eventuali contatti su Skype, Yahoo, AIM e ICQ.

Maza è attivo dal 2003 e rappresenta un vero punto di riferimento per i cyber criminali che operano sul territorio russo. L’accesso è ristretto a pochi “afecionados” che, al suo interno, possono tranquillamente scambiare informazioni e risorse con i loro colleghi.

forum Maza

L’attribuzione dell’attacco è ancora tutta da chiarire: il messaggio comparso sulle pagine di Maza sembra infatti essere stato tradotto in lingua russa utilizzando un sistema di traduzione automatico, elemento che farebbe pensare a una pista che conduce all’estero.

Secondo i ricercatori di Flashpoint, però, potrebbe trattarsi di un classico “false flag”, cioè un indizio inaffidabile che avrebbe come unico scopo quello di confondere le acque.

Non è escluso, quindi, che si possa trattare di u n “lavoro dall’interno” simile a quello cui si è assistito negli ultimi tempi e che ha coinvolto altri siti simili a Maza.

Condividi l’articolo


Articoli correlati

Altro in questa categoria


https://www.securityinfo.it/2021/03/05/i-cyber-criminali-attaccano-il-forum-maza-dedicato-al-cyber-crimine/?utm_source=rss&utm_medium=rss&utm_campaign=i-cyber-criminali-attaccano-il-forum-maza-dedicato-al-cyber-crimine


Dpo per Pa ed aziende? La formazione in live webinar

Non esiste un albo professionale per i Data Protection Officer (DPO).
Il DPO è designato (art. 37 del GDPR) dal titolare o dal responsabile del trattamento, in base ad un contratto.

La formazione

Per essere nominato DPO di un’azienda pubblica o privata è fondamentale l’approfondita conoscenza della normativa e delle prassi in materia di data protection e privacy, nonché delle norme e delle procedure amministrative che caratterizzano lo specifico settore di riferimento.

<!-- LARGE RECTANGLE POST - CORPO TESTO

-->

Il live webinar

Dunque, come formarsi per diventare consulenti ed i referenti Privacy delle aziende nel settore pubblico e privato che intendono specializzarsi e ricoprire in futuro il ruolo di Data Protection Officer?

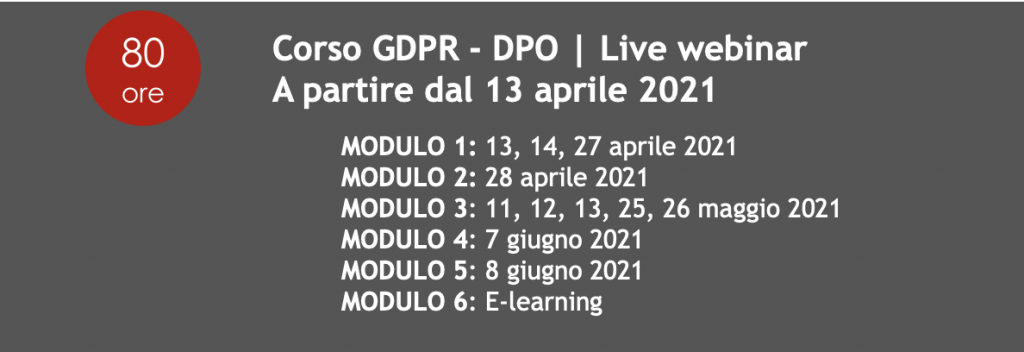
Tra i corsi di formazione, vi segnaliamo quello organizzato da Labor Project, giunto alla 46esima edizione, della durata di 80 ore da seguire in live webinar.

Per conoscere i docenti e il costo.

https://www.key4biz.it/dpo-per-pa-ed-aziende-la-formazione-in-live-webinar/348696/


South Africa Opposes WhatsApp-Facebook Data Sharing

South Africa’s information regulator has protested WhatsApp’s plans to share user data with Facebook, vowing to engage directly with the popular messaging app to ensure its compliance to national privacy laws.

In January, WhatsApp asked all its users to accept new terms allowing it to share more private information with its parent company Facebook for advertising and e-commerce purposes.

The proposition sparked global outrage, forcing the company to delay its plans and clarify its privacy and security terms.

South Africa opposes WhatsApp-Facebook data sharing

Widespread confusion about WhatsApp’s future plans was compounded when it announced that European Union (EU) users would not be forced to agree to share personal information with Facebook.

Non-EU users, meanwhile, have been told they will be partially cut off from the messaging app if they do not accept its revised terms by May 15.

South Africa’s Information Regulator (IR) on Wednesday said the new privacy policy violated the country’s Protection of Personal Information Act.

“WhatsApp cannot without obtaining prior authorisation from the IR… process any contact information of its users for a purpose other than the one for which the number was specifically intended at collection,” the IR said in a statement.

The regulator added that it was “very concerned” about EU users gaining higher privacy protection than their counterparts in Africa.

“Our legislation is very similar to that of the EU,” noted IR Chair Pansy Tlakula.

“We do not understand why Facebook has adopted this differentiation between Europe and Africa.”

The IR said it had invited Facebook to “a round-table discussion regarding the issues raised” to ensure full compliance of the new terms with South African law.

Under the new terms, merchants using WhatsApp to chat with customers will be able to share data with Facebook, allowing the social networking platform to better target its advertisements.

WhatsApp has defended the policy, claiming it is simply building new ways to chat or shop with businesses “that are entirely optional”.

Related: WhatsApp Defends Encryption as It Tops 2 Billion Users

Related: Tech Giants Show Support for WhatsApp in Lawsuit Against Spyware Firm

Related: Vulnerability in WhatsApp Desktop Exposed User Files

view counter

© AFP 2020

Previous Columns by AFP:
Tags:

http://feedproxy.google.com/~r/Securityweek/~3/QWvsOvNC9ck/south-africa-opposes-whatsapp-facebook-data-sharing