Twitter sotto indagine Ftc per violazione della privacy, potrebbe costargli fino a 250 milioni di dollari
La Federal Trade Commission (Ftc), Agenzia federale per la libera concorrenza e la tutela dei consumatori, ha avviato un’indagine su Twitter per violazione della legge sulla privacy negli Stati Uniti, secondo quanto riportato da diverse testate come Cnn, Bloomberg e New York Times.
Nella comunicazione all’azienda, l’Antitrust USA ha rilevato un utilizzo improprio dei dati personali, come numeri di telefono ed indirizzi email, per indirizzare e profilare annunci pubblicitari.
L’indagine su Twitter
L’indagine, che riguarda il periodo 2013-2019, è arrivata subito dopo la presentazione dei dati finanziari del secondo trimestre 2020 (683 milioni di dollari di ricavi) e potrebbe costare a Twitter un esborso compreso tra 150 e 250 milioni di dollari.
La società, con sede a San Francisco, ha già parzialmente ammesso degli “errori” nell’utilizzo dei dati di contatto generalmente forniti dagli utenti alla piattaforma per rendere più efficaci le misure di sicurezza dell’account (autenticazione a due fattori).
Una prima conferma dell’uso improprio dei numeri di telefono delle persone iscritte sul social c’è già stata e proprio per finalità commerciali illecite. La piattaforma però ha sempre dichiarato di non poter sapere con esattezza quanti utenti fossero o meno coinvolti.
I precedenti
Nel 2011 Twitter aveva già chiuso un accordo con l’Ftc proprio per la protezione della privacy degli utenti. Due anni prima, infatti, dopo un cyber attacco di vasta portata, migliaia di account furono violati e utilizzati per far partire messaggi fraudolenti.
In quell’accordo, Twitter si impegnava a proteggere i dati personali dei suoi utenti, pena una multa di 16.000 dollari per ogni record violato.
Le azioni di Twitter hanno perso l’1%, chiudendo a 36,39 dollari.
Negli ultimi mesi Twitter è stato al centro della scena anche per altre faccende più legate alla politica e alla cyber sicurezza, come lo scontro con il Presidente Donald Trump e il mega hack che ha coinvolto utenti celebri come Joe Biden, Elon Musk, Jeff Bezos e Bill Gates.
App Covid, allarme dei medici europei: a rischio privacy e sicurezza dei cittadini
Allarme generale del Comitato permanente dei medici europei (Cpme) a seguito delle dichiarazioni del Governo di Londra sulla possibilità effettiva di violazione della privacy degli utenti dopo il download dell’applicazione per il tracciamento dei contatti (contact tracing).
Il 20 luglio scorso, il Dipartimento della salute del Governo britannico ha comunicato, in una lettera all’Open Rights Group, la possibilità concreta di una violazione del regolamento generale europeo sulla protezione dei dati (Gdpr).
Il Comitato dei medici europei, in un documento, ha espresso diverse preoccupazioni relative all’uso di tale app e di altre simili per possibili accessi non autorizzati ai dati sensibili delle persone.
I rischi più seri sono stati individuati nella violazione dei dati sanitari e nella raccolta di non autorizzata di dati relativi agli spostamenti e la posizione degli individui (location data) per finalità che esulano quelle sanitarie.
Ma visto che si tratta di accessi non autorizzati a tali dati, la stessa sicurezza informatica dei device è messa a rischio.
Serve quindi una seria valutazione dell’impatto delle app dedicate al Covid-19 in termini di sicurezza informatica, di privacy e di trattamento dei dati dei cittadini.
Una valutazione che però, hanno spiegato dal Cpme, deve avvenire prima del lancio delle app, non a posteriori, ad app scaricata, mentre sono necessarie anche delle valutazioni periodiche da cui trarre sempre informazioni aggiornate su quanto accade ai nostri dati.
Violare il regolamento generale europeo sul trattamento dei dati (Gdpr) significa andare incontro a sanzioni fino a 20 milioni di euro, o a multe pari al 4% delle entrate globali.
La multa più grande inflitta in Europa, per il violazione del Gdpr, è stata decisa in Francia, contro Google nel 2019, per una cifra di 50 milioni di euro.
App anti-Covid. Germania, Svizzera e Danimarca contro Google: non garantisce la privacy, raccolti dati sugli spostamenti
Dopo le tante promesse e le strette di mano tra Google e i Governi alle prese con la pandemia di Covid-19, in molti cominciano a chiedersi se il gigante di Mountain View non abbia preso tutti in giro, riguardo il tema scottante della privacy e la riservatezza dei dati delle persone.
Nel momento più critico della diffusione del virus e del suo impatto sanitario e sociale, Google ed Apple avevano presentato a diversi Paesi una soluzione tecnologica per il monitoraggio degli spostamenti e soprattutto dei contagi.
App anti-Covid e privacy
Il cosiddetto contact tracing poteva essere effettuato nel pieno rispetto delle leggi sulla privacy attraverso un software libero, che avrebbe agito rispettando la riservatezza di ognuno.
In poche parole, si cercava solo di monitorare la pandemia, non gli spostamenti dei singoli durante la giornata. E invece le cose sono andate molto diversamente.
Germania, Svizzera, Lettonia e Danimarca, ad esempio, dopo aver scoperto che i dati personali relativi agli spostamenti venivano non solo tracciati, ma anche raccolti dal sistema operativo di Google per smartphone, il popolare Android, hanno subito chiesto alla multinazionale un confronto chiarificatore.
Berna ha subito chiesto a Google di modificare le impostazioni del sistema operativo relative alla posizione dell’utilizzatore. La Danimarca, dal canto suo, ha suggerito a Mountain View di aprire rapidamente un tavolo di confronto sulla faccenda.
Il problema, secondo quanto riportato da un articolo del New York Times, è che il software anti-Covid ha bisogno che sia attivato il GPS sullo smartphone, cosa che in automatico fa raccogliere ad Android i dati relativi a posizione e spostamenti o locationdata.
Sia Google, Sia Apple, hanno rigettato le accuse. Apple ha sostenuto che il suo sistema operativo iOS non funziona in questo modo, mentre da Google semplicemente si ribadisce il rispetto assoluto delle leggi sulla privacy.
Un problema di cyber sicurezza
Ulteriore problema, segnalato dagli esperti di cybersecurity, è che le app anti-virus, che sono state sviluppate rapidamente un po’ ovunque nel mondo, potrebbero favorire non solo la violazione della privacy, ma attacchi informatici di varia natura, tra cui frodi e truffe online, phishing e ransomware, furti di identità, attività di spionaggio (anche considerando che questi applicazioni sono scaricate sui device utilizzati a lavoro).
Ad oggi, superano i 20 milioni di download le app anti-virus sviluppate da diversi Governi in tutto il mondo, secondo l’articolo del NYT.
Il Garante privacy europeo: “Protezione dati non solo diritto fondamentale ‘europeo’ ma globale
L’EDPS, dopo aver evidenziato l’importanza dei livelli di sicurezza per la protezione dei dati personali (soprattutto per il trasferimento in paesi terzi, come gli Stati Uniti nel caso di specie) oltre il territorio dell’Unione europea, sottolinea che nel mondo oramai è cambiata e cresciuta la sensibilità sulla protezione dei dati personali; ne è dimostrazione la maggiore legiferazione a livello globale e l’ulteriore impegno europeo (da ultimo dimostrato con la nuova Convenzione 108+ adottata dal Consiglio d’Europa).
È un argomento talmente comune che l’EDPS si spinge a confermare un’idea, già adottata da molti, secondo cui l’effettiva protezione dei dati personali (anche rispetto al diritto di ricorrere dinanzi a tribunali indipendenti) è più di un diritto fondamentale “europeo” ma è un diritto fondamentale ampiamente riconosciuto in tutto il mondo.
Su questo solco, l’EDPS confida che gli Stati Uniti possano trovare occasione nel promuovere riforme legislative di sistema per spostarsi verso un quadro giuridico globale in materia di protezione dei dati e privacy, che garantisca all’interessato quei diritti così come riaffermati dalla Corte di Giustizia nella sua ultima pronuncia.
Un singolo cittadino europeo non può attivarsi per tutelare i suoi dati in Usa
Invero, l’EDPS rileva che la pronuncia in commento, pur confermando in linea di principio la validità delle clausole contrattuali standard (SCC), ha evidenziato i rischi connessi al trattamento dei dati fuori dall’Unione Europea ed ha sostanzialmente accolto con favore le argomentazioni della Corte di Giustizia secondo cui – attualmente – non sussistono effettive ed adeguate garanzie che il singolo interessato possa realmente attivarsi per la tutela dei suoi diritti rispetto al trattamento dei dati trasferiti verso un Paese terzo.
US-EU Privacy Shield data sharing agreement struck down by court
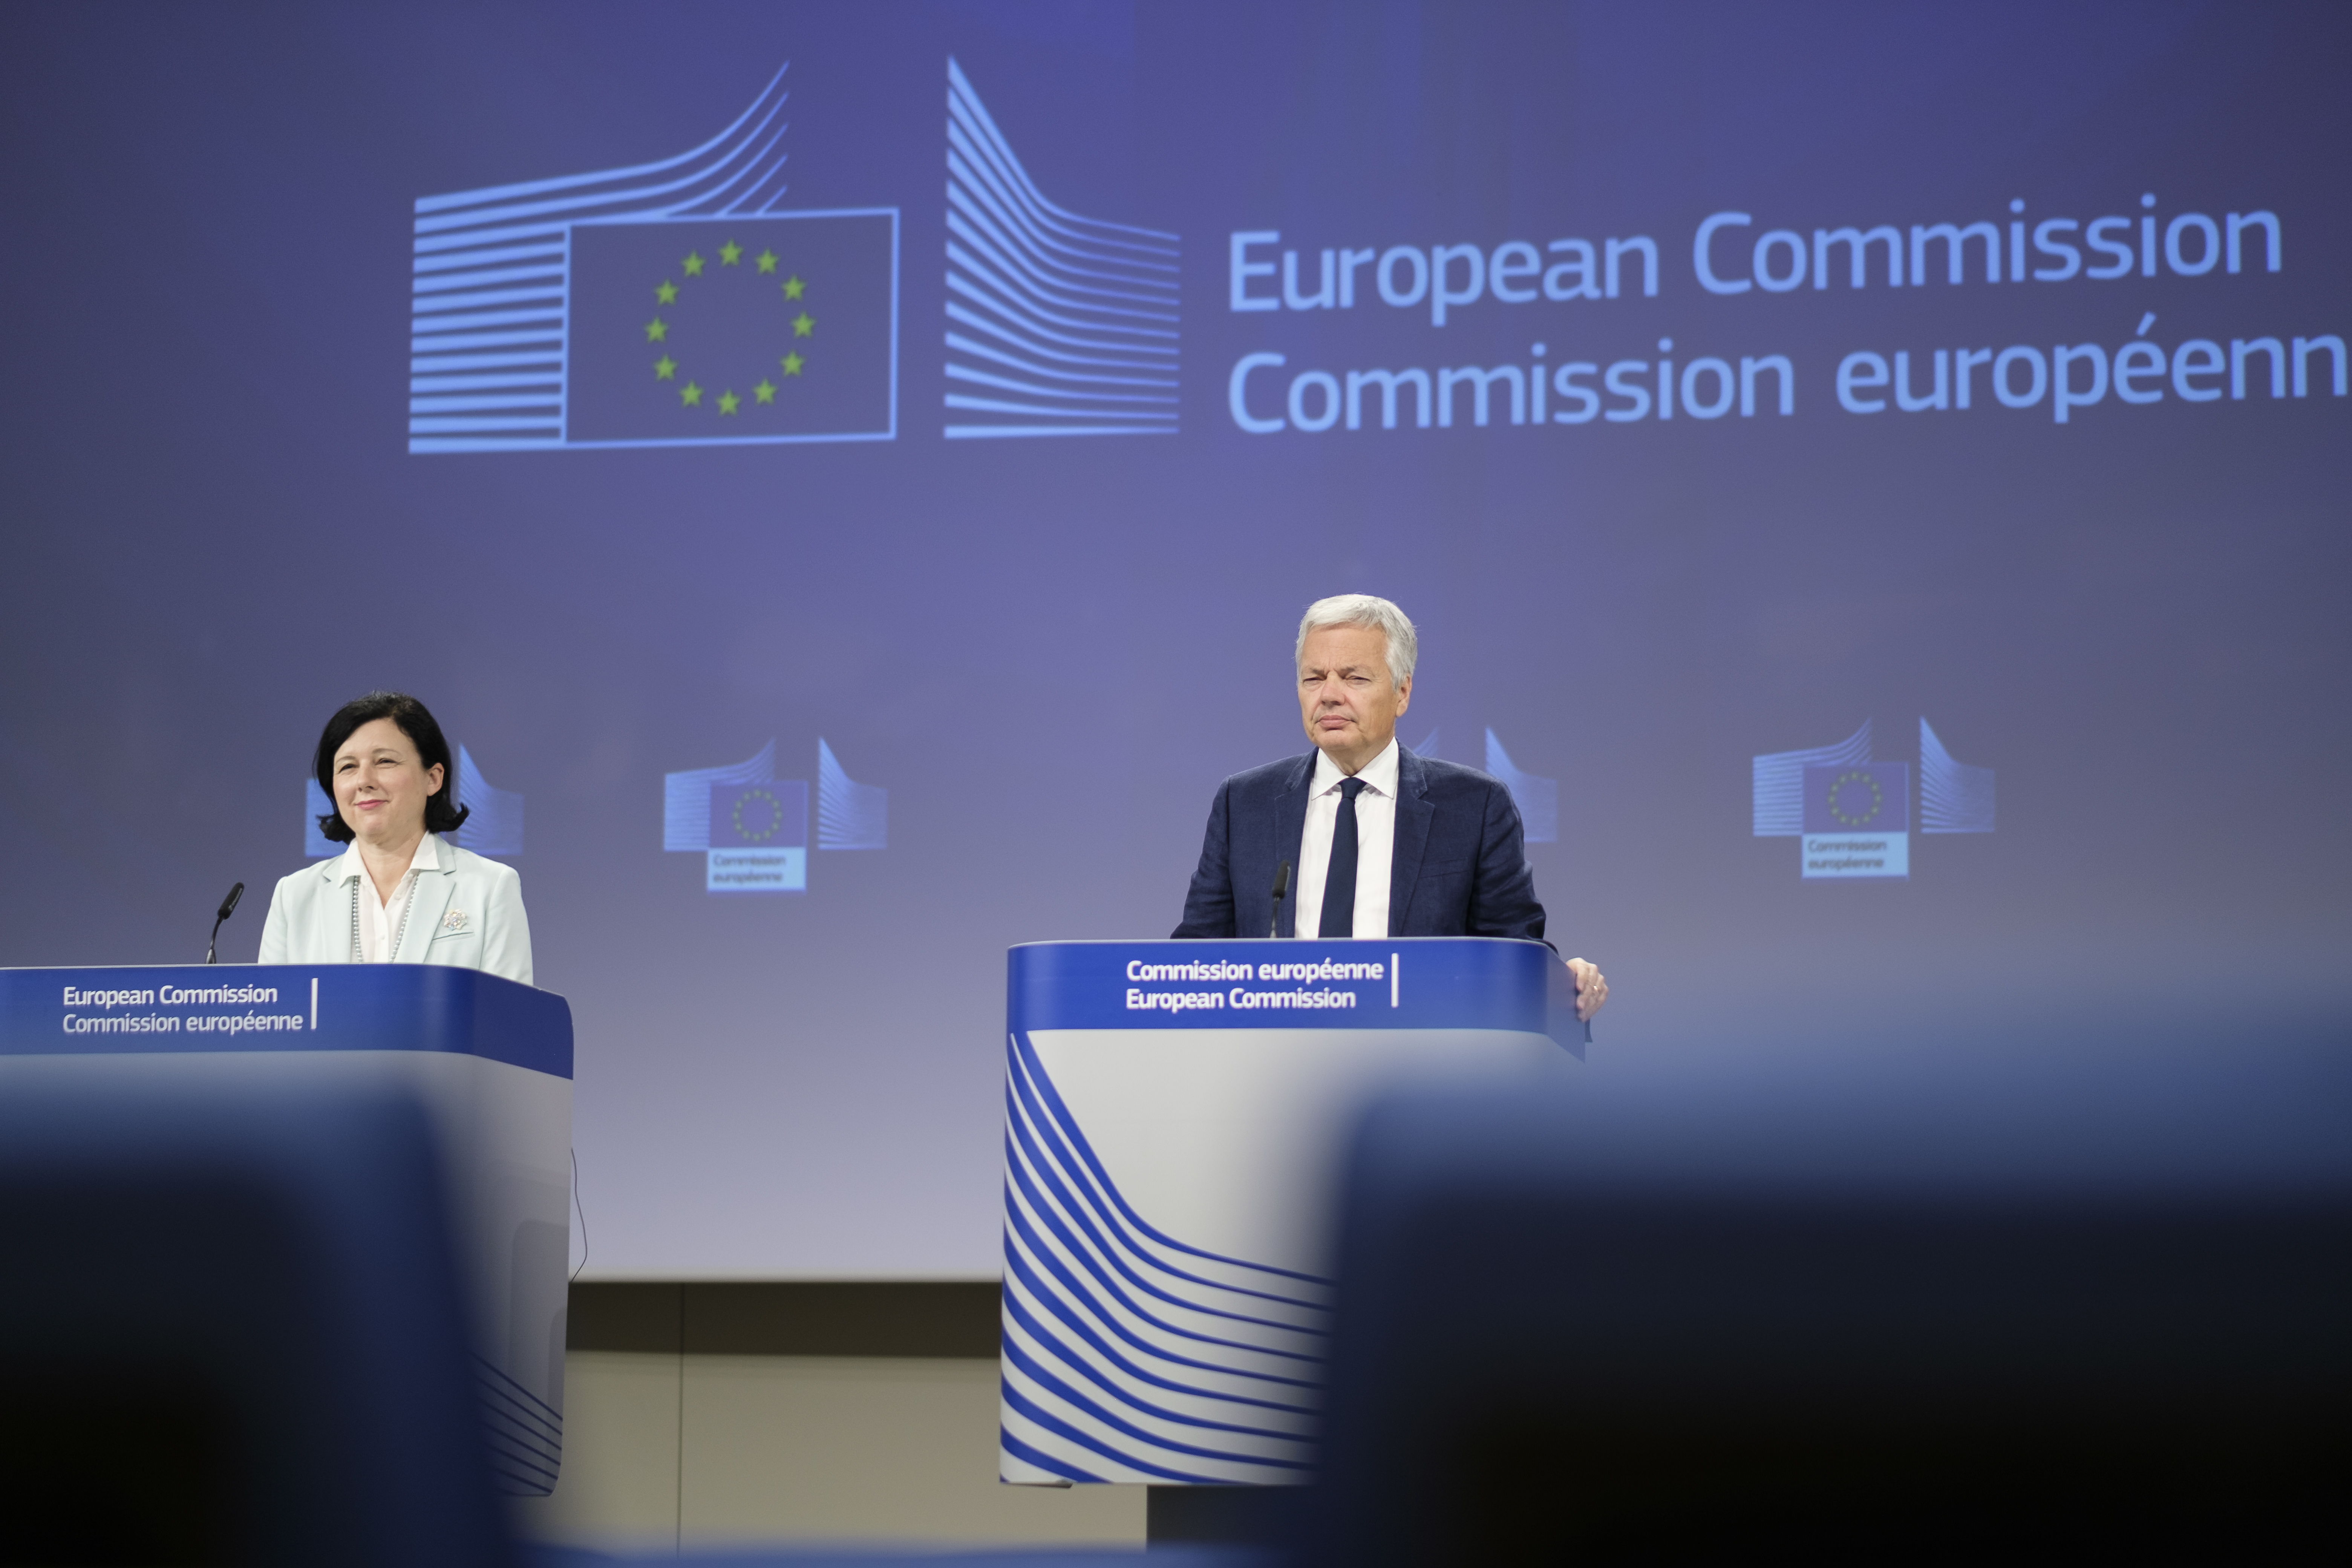
Enlarge/ EU Commissioner for Values and Transparency – Vice President Vera Jourova (L) and the EU Commissioner for Justice Didier Reynders (R) are talking to media during the EU Commission press conference on data protection at International Level on July 16, 2020 in Brussels, Belgium.
Europe’s highest court today struck down the agreement by which companies operating in the EU are allowed to transfer data to the United States. The court ruled that the agreement leaves European customers’ data too exposed to US government surveillance.
The agreement, known as Privacy Shield, has been in place since 2016, and more than 5,000 companies operate under its terms. Boiled down, the Court of Justice of the European Union (CJEU) basically ruled that US law is too weak to protect EU citizens’ data to the extent EU law demands. As the court put it in a press release (PDF):
The limitations on the protection of personal data arising from the domestic law of the United States, on the access and use by US public authorities of such data transferred from the European Union… are not circumscribed in a way that satisfies requirements that are essentially equivalent to those required under EU law.
As a result of the case, US companies doing business in Europe or handling data from European clients will either have to negotiate new individual data-handling arrangements, called Standard Contract Clauses (SCC), with the EU or stop porting data from European operations into the US. The ruling applies to data that companies such as Facebook move around to US servers for internal reasons, but it does not affect “necessary” data transfers, such as take place when someone in Europe sends an email to a recipient in the US, books a flight or a hotel on a US website, or does something equally mundane.
Privacy Shield?
From 2000 to 2015, the agreement governing the sharing of EU customer data between Europe and the United States was called Safe Harbor. The CJEU invalidated Safe Harbor in 2015, following a legal challenge from Maximillian Schrems, a privacy advocate from Austria. In the wake of the Snowden revelations, Schrems alleged the Safe Harbor agreement (which permitted NSA access to EU citizens’ personal data) stood in conflict with EU law. The court agreed and invalidated the Safe Harbor framework in October 2013.
EU lawmakers, together with the US Department of Commerce, rapidly pulled together the Privacy Shield framework after Safe Harbor was tossed, and the European Commission adopted it in 2016. The framework, however, faced deep skepticism before lawmakers even voted to adopt it. EU regulators warned before the deal was even formally signed that “Privacy Shield, as it stands, is not robust enough to withstand future legal scrutiny before the court.”
Regulators also warned at the time that Privacy Shield might be in conflict with Europe’s sweeping privacy law, the General Data Protection Regulation (GDPR). EU lawmakers adopted that law in 2016, and it has been in effect since 2018.
Schrems in 2016 joked to Ars that although he wanted someone to file suit, he personally wasn’t necessarily interested in being the one to do so. As it turns out, however, he did—the case on which the CJEU ruled today is commonly called Schrems II—and once again won.
“It is clear that the US will have to seriously change their surveillance laws, if US companies want to continue to play a major role on the EU market,” Schrems said in a statement after the CJEU ruling. “This judgment is not the cause of a limit to data transfers, but the consequence of US surveillance laws.”
Slow change
Major US tech companies were quick to deliver assurance that the ruling will not substantially change their operations in Europe for the time being, with many confirming they already use SCCs in addition to Privacy Shield agreements.
“If you are a commercial customer, you can continue to use Microsoft services in compliance with European law,” Microsoft wrote in a corporate blog post. “The court ruling does not change your ability to transfer data today between the EU and US using the Microsoft cloud.”
Microsoft also plans to “work proactively with the European Commission and the US government to address the issues raised by the ruling,” the company added.
Facebook representative Eve Nagle issued a statement saying, “We welcome the decision of the Court of Justice of the European Union to confirm the validity of Standard Contractual Clauses for transfers of data to non-EU countries.” The statement added that Facebook, “like many businesses,” is now “carefully considering the findings and implications of the decision” and “looks forward to regulatory guidance in this regard.”
Replacement?
Tech trade groups wasted no time calling on US and EU regulators to quickly develop a firm regulatory framework to replace the now-defunct Privacy Shield.
“The collapse of the Privacy Shield will disproportionately affect small- to medium-sized businesses that make up 70 percent of the companies using the Privacy Shield,” said Morgan Reed, president of the App Association, which represents more than 5,000 app developers globally. “This decision leaves thousands of US and EU companies without a much-needed data sharing mechanism and will significantly disrupt the transatlantic data market, worth hundreds of billions of dollars. We urge the European Union and the US government to negotiate a replacement as quickly as possible to guarantee legal certainty for all businesses who use cross-border data transfers and to ensure the continued growth of the transatlantic data economy.”
The Computer & Communications Industry Association—which represents many of the large tech companies you’ve heard of including Amazon, Facebook, and Google—echoed the sentiment. “This decision creates legal uncertainty for the thousands of large and small companies on both sides of the Atlantic that rely on Privacy Shield for their daily commercial data transfers,” CCIA Senior Manager of Public Policy Alexandre Roure said. “We trust that EU and US decision-makers will swiftly develop a sustainable solution, in line with EU law, to ensure the continuation of data flows which underpins the trans-Atlantic economy.”
https://arstechnica.com/?p=1692235
Ars readers hated this startup’s privacy policy—so the company changed it
Enlarge/ This isn’t the relationship you want to see between a company with access to your private data and its affiliates.
When we covered subscription-based search engine startup Neeva in June, most reader focus wasn’t on the search engine itself so much as its privacy policy, which left much to be desired—particularly given the option Neeva gives its users to search their email via the service. Shortly after publication, Neeva CEO Sridhar Ramaswamy reached out to Ars to discuss what went wrong and how the company planned to fix it.
Updated privacy policy
The especially noxious Affiliates and Advertising Partners sections of Neeva’s original Privacy Policy have been entirely removed.
Jim Salter
The earlier reference to advertising was also removed. The major impact here is to what degree you might expect a third-party tracking cookie to show up inside Neeva itself.
Jim Salter
The last update to Neeva’s privacy policy tightens its policies on data retention.
Jim Salter
Ramaswamy told Ars that the company’s intention was to provide a secure and privacy-respecting platform from the start. But, he added—and we’re paraphrasing here—”lawyers will be lawyers,” and it was “on him” that he had not inspected the policies drafted by the company’s legal counsel closely enough. He told us that he heard our readers’ feedback loud and clear, and he pledged to overhaul the policy to bring it in line with the company’s actual vision.
The gallery above displays the three areas in the policy that have changed since the call with Ars. Both references to third-party advertising—and tracking technologies associated with such advertising—have been entirely removed. The major impact here lies in expectations for third-party intrusions into the Neeva site itself, and it’s an important one—there isn’t much point in paying a monthly subscription in return for privacy if your search metadata might be leaking to the public giants you’re trying to avoid in the first place.
The section on “Affiliates” was also cleanly removed. Although it consisted of a single line only—”Affiliates. We may share personal information with our affiliated companies”—that single line, now removed, effectively nullified nearly every possible guarantee of privacy.
Under “Third Party Disclosure,” an odd “data sale canary” statement—”We have not sold consumers’ personal information in the preceding 12 months”—was replaced with the much clearer “We do not and never have sold consumers’ personal information.” The relationship of Neeva, its service providers, and consumer data also received some clarification.
Finally, Neeva’s data retention policy received an update and expansion. It now clearly states that automatically collected data will be deleted after 90 days and that customer-provided information (such as logins and payment credentials) will be kept “only as long as necessary to fulfill the purpose(s) for which it was collected.” Exceptions include laws, audits, and Terms of Service enforcement.
The only thing we weren’t certain about is why data retention might be necessary to enforce ToS. We reached out to Ramaswamy again for clarification:
Example situation where this might apply: We cancel an account for abusing our terms of service and need to ensure that variants of the account don’t come back… Obviously, we would do this only under situations where there was a problem.
Ramaswamy also issued a public statement expounding on what was changed in the privacy policy and why, along with hints as to what price point the service’s users can expect to see once it goes live.
Focus on features
C++ programmers generally get treated to information on sexually transmitted diseases when searching for help with functions in the Standard Library.
We pointed out that anyone searching for “std::” rather than “std” is unlikely to want information about gonorrhea. A week later, Neeva had a fix.
Privacy-policy gaffes weren’t all that Ramaswamy wanted to talk with Ars about. He explained that the company’s vision revolves in part around providing better and more nimble service to a necessarily smaller group of customers than the large, free search engines can or will. He told us that user feedback submitted through text boxes in the Neeva interface directly populated the company’s private GitHub repository with new tickets, and he went on to stress how generally open to feature requests the company is.
By the time Ars spoke to Ramaswamy, the comment section on our original coverage was very active—and one complaint about search engines in general had made quite a splash. Ars reader sir_trackmenot complained:
Std::(anything) on Google always includes “I have these sores, is it a STD thing” results which pisses me off. Does someone in my office have an STD that they’re looking up?
Searching (std list), without the parentheses, I get a “featured snippet” with a list of sexually transmitted diseases, followed by over two pages of std::list stuff before the next disease link shows up.
Searching (std::list) I get no featured snippet, but just under half a page of results (4) before the disease links take over.
Searching (“std::list”) is even worse. Now the top 3 hits are disease links, followed by a mix lead by a Microsoft docs page for the c++ standard library list class which doesn’t actually include the phrase “std::list” anywhere on the page or in source (but since it is about the std::list class, it’s not necessarily a *bad* result, just not what one would expect when using quotation marks).
When we pointed this out to Ramaswamy—and suggested treating “std::” as an entirely different search term than “std” alone—he excitedly declared that this would be an easy fix and that this was exactly the kind of feedback the company looks for from subscribers. A week later, he forwarded us a before-and-after gallery of searching the term std::list on Neeva demonstrating the impact that the fix made.
Caution is still advised
We believe it’s a good sign that Neeva responded rapidly to feedback with clarifications to its privacy policy, both simplifying and tightening it. Such responsive and substantial changes are a good sign of the company’s bona fide intent to provide the sort of privacy most users will expect from a search engine.
While this is well and good for search of publicly indexed data—webpages, weather reports, and so forth—we’re not sure it goes far enough, or even can go far enough, for users who choose to provide their email to Neeva to be indexed also. It’s difficult to overstate the amount of damage that can be done by a bad actor with access to someone’s email account—just ask Wired writer Mat Honan, whose online life got rolled up like a rug eight years ago by an attacker who wanted his three-letter Twitter handle.
Even with all the good intentions in the world, providing a third party service credentials to access your email account represents substantial additional risk. The information in that account can be used to gain access to nearly every service imaginable—both online and, increasingly, offline as well. Even more care needs to be taken with business email—an employer’s own confidentiality policies can easily be violated by giving third parties access to a company email account.
https://arstechnica.com/?p=1691279
Hong Kong downloads of Signal surge as residents fear crackdown
d3sign / Getty
The secure chat app Signal has become the most downloaded app in Hong Kong on both Apple’s and Google’s app stores, Bloomberg reports, citing data from App Annie. The surging interest in encrypted messaging comes days after the Chinese government in Beijing passed a new national security law that reduced Hong Kong’s autonomy and could undermine its traditionally strong protections for civil liberties.
The 1997 handover of Hong Kong from the United Kingdom to China came with a promise that China would respect Hong Kong’s autonomy for 50 years following the handover. Under the terms of that deal, Hong Kong residents should have continued to enjoy greater freedom than people on the mainland until 2047. But recently, the mainland government has appeared to renege on that deal.
Civil liberties advocates see the national security law approved last week as a major blow to freedom in Hong Kong. The New York Times reports that “the four major offenses in the law—separatism, subversion, terrorism and collusion with foreign countries—are ambiguously worded and give the authorities extensive power to target activists who criticize the party, activists say.” Until now, Hong Kongers faced trial in the city’s separate, independent judiciary. The new law opens the door for dissidents to be tried in mainland courts with less respect for civil liberties or due process.
This has driven heightened interest among Hong Kongers in secure communication technologies. Signal offers end-to-end encryption and is viewed by security experts as the gold standard for secure mobile messaging. It has been endorsed by NSA whistleblower Ed Snowden.
One of Signal’s selling points is that it minimizes data collection on its users. When rival Telegram announced it would no longer honor data requests from Hong Kong courts, Signal responded that it didn’t have any user data to hand over in the first place.
Bloomberg has also reported on the surging adoption of VPN software in Hong Kong as residents fear government surveillance of their Web browsing.
https://arstechnica.com/?p=1690144
Detroit police chief cops to 96-percent facial recognition error rate
Enlarge/ CCTV security guard in the mall building.
Detroit’s police chief admitted on Monday that facial recognition technology used by the department misidentifies suspects about 96 percent of the time. It’s an eye-opening admission given that the Detroit Police Department is facing criticism for arresting a man based on a bogus match from facial recognition software.
Last week, the ACLU filed a complaint with the Detroit Police Department on behalf of Robert Williams, a Black man who was wrongfully arrested for stealing five watches worth $3,800 from a luxury retail store. Investigators first identified Williams by doing a facial recognition search with software from a company called DataWorks Plus. Under police questioning, Williams pointed out that the grainy surveillance footage obtained by police didn’t actually look like him. The police lacked other evidence tying Williams to the crime, so they begrudgingly let him go.
Now Vice’s Jason Koebler reports that Detroit Police Chief James Craig acknowledged the flaws with its facial recognition software at a Monday event.
“If we would use the software only [to identify subjects], we would not solve the case 95-97 percent of the time,” Craig said. “That’s if we relied totally on the software, which would be against our current policy … If we were just to use the technology by itself, to identify someone, I would say 96 percent of the time it would misidentify.”
As Craig notes, police officers in Detroit aren’t supposed to arrest someone based solely on the results of a facial recognition search. And the Detroit police claimed that they didn’t do that in the Williams case. A police spokeswoman told The New York Times that “the investigator reviewed video, interviewed witnesses, [and] conducted a photo lineup” before arresting Williams.
But this “investigation” was rather flimsy. The “photo lineup” consisted of showing photos to a security contractor who was not an eyewitness; he had only viewed the same surveillance footage police had used in the first place.
Research has found that the accuracy of facial recognition software varies by the race of the subject, with Black suspects being identified less often than white ones. And Koebler points out that the DPD’s own statistics show the technology being used almost exclusively on Black suspects. According to police data, 68 out of 70 facial recognition searches were done on Black suspects, while two had a race code of “U”—probably short for “unknown.”
The ACLU has called on the Detroit Police Department—and other police departments—to stop using facial recognition technology for investigations in light of its high error rate and racially disparate impact. Boston’s city council voted to ban the use of facial recognition technology last week.
https://arstechnica.com/?p=1688306
Tutti i rischi di sicurezza delle infrastrutture pubbliche
La digitalizzazione dei servizi pubblici e governativi consente un miglioramento a livello di efficienza, ma sono protette in maniera adeguata?
Quando si parla di informatica e strumenti digitali, il termine “aperto” suscita immediata simpatia. Che si tratti di codici sorgenti o database, l’idea che le informazioni siano accessibili a tutti ci rassicura. Esiste però un rovescio della medaglia, rappresentato dai rischi di sicurezza.
A spiegarlo in un intervento pubblicato su Bleeping Computer è il ricercatore Ax Sharma, che mette sotto la lente d’ingrandimento tutti gli usi “distorti” che potrebbero essere fatti di queste informazioni da parte di soggetti malintenzionati, come un governo ostile.
Il suo ragionamento parte da un report che ha pubblicato un paio di settimane fa riguardo l’esposizione dei dati di un database utilizzato per il riconoscimento automatico delle targhe tramite videocamere nel Regno Unito.
Nel corso dello studio, Sharma ha infatti scoperto che molte delle videocamere in questione sono liberamente accessibili a chiunque. Non si tratta di un errore di configurazione, ma di una scelta dettata dalla legislazione britannica in tema di trasparenza.
La domanda che il ricercatore si pone riguarda la possibilità che informazioni del genere (si tratta di videocamere per il monitoraggio del traffico) possano essere utilizzate per provocare danni alla collettività. La risposta, purtroppo, è affermativa.
Informazioni del genere per esempio, potrebbero essere utilizzate per massimizzare i danni di un attacco terroristico o un sabotaggio ai danni dei sistemi che gestiscono il traffico.
Anche quando non si parla di dati “aperti”, rimane il problema della percezione del rischio e del livello di protezione che viene garantito ai dati. Se le cosiddette “infrastrutture critiche” (come centrali elettriche, impianti nucleari e simili) possono godere di particolari protezioni, lo stesso non si può dire di infrastrutture altrettanto sensibili ma la cui importanza è meno evidente, per lo meno agli occhi dell’opinione pubblica.
Uno degli esempi portati da Sharma è quello dei servizi di emergenza sanitaria, che negli ultimi mesi sono finiti sotto stress a causa della pandemia da Covid-19. Un attacco in grado di mandare in tilt i sistemi in un periodo del genere, sottolinea il ricercatore, avrebbe conseguenze catastrofiche.
Insomma: la declinazione “pubblica” della trasformazione digitale ha in sé aspetti terribilmente delicati e contemperare trasparenza, libertà di accesso e sicurezza non è certamente facile. Un tema, questo, su cui le pubbliche amministrazioni dovrebbero probabilmente avviare una (seria) riflessione.
TikTok and 53 other iOS apps still snoop your sensitive clipboard data
In March, researchers uncovered a troubling privacy grab by more than four dozen iOS apps including TikTok, the Chinese-owned social media and video-sharing phenomenon that has taken the Internet by storm. Despite TikTok vowing to curb the practice, it continues to access some of Apple users’ most sensitive data, which can include passwords, cryptocurrency wallet addresses, account-reset links, and personal messages. Another 53 apps identified in March haven’t stopped either.
The privacy invasion is the result of the apps repeatedly reading any text that happens to reside in clipboards, which computers and other devices use to store data that has been cut or copied from things like password managers and email programs. With no clear reason for doing so, researchers Talal Haj Bakry and Tommy Mysk found, the apps deliberately called an iOS programming interface that retrieves text from users’ clipboards.
Universal snooping
In many cases, the covert reading isn’t limited to data stored on the local device. In the event the iPhone or iPad uses the same Apple ID as other Apple devices and are within roughly 10 feet of each other, all of them share a universal clipboard, meaning contents can be copied from the app of one device and pasted into an app running on a separate device.
That leaves open the possibility that an app on an iPhone will read sensitive data on the clipboards of other connected devices. This could include bitcoin addresses, passwords, or email messages that are temporarily stored on the clipboard of a nearby Mac or iPad. Despite running on a separate device, the iOS apps can easily read the sensitive data stored on the other machines.
“It’s very, very dangerous,” Mysk said in an interview on Friday, referring to the apps’ indiscriminate reading of clipboard data. “These apps are reading clipboards, and there’s no reason to do this. An app that doest have a text field to enter text has no reason to read clipboard text.”
The video below demonstrates universal clipboard reading:
[embedded content]
KlipboardSpy: How malicious apps on iPhone and iPad abuse the Universal Clipboard on your Mac.
Back in the news
While Haj Bakry and Mysk published their research in March, the invasive apps made headlines again this week with the developer beta release of iOS 14. A novel feature Apple added provides a banner warning every time an app reads clipboard contents. As large numbers of people began testing the beta release, they quickly came to appreciate just how many apps engage in the practice and just how often they do it.
This YouTube video, which has racked up more than 87,000 views since it was posted on Tuesday, shows a small sample of the apps triggering the new warning
[embedded content]
iOS14 Catches Apps Spying on Your Clipboard
TikTok in the spotlight
Recent headlines have focused particular attention on TikTok, in large part because of its massive base of active users (reported to be 800 million, with an estimated 104 million iOS installs in the first half of 2018 alone, making it the most downloaded app for that period).
TikTok’s continued snooping has gotten extra scrutiny for other reasons. When called out in March, the video-sharing provider told UK publication The Telegraph it would end the practice in the coming weeks. Mysk said that the app never stopped the monitoring. What’s more, a Wednesday Twitter thread revealed that the clipboard reading occurred each time a user entered a punctuation mark or tapped the space bar while composing a comment. That means the clipboard reading can happen every second or so, a much more aggressive pace than documented in the March research, which found monitoring happened when the app was opened or reopened.
To reproduce: 1. Have something on your clipboard. Eg copy some text from Notes or a website 2. Open TikTok and start typing in any text field 3. You learn from iOS 14 beta each time an app “pastes” – but in this instance I didn’t request it, and none of that text appears in UI
Following the beta release of iOS14 on June 22, users saw notifications while using a number of popular apps. For TikTok, this was triggered by a feature designed to identify repetitive, spammy behavior. We have already submitted an updated version of the app to the App Store removing the anti-spam feature to eliminate any potential confusion.
TikTok is committed to protecting users’ privacy and being transparent about how our app works. We look forward to welcoming outside experts to our Transparency Center later this year.
On background, a spokesperson said that TikTok for Android never implemented the anti-spam feature.
I sent follow-up questions asking (1) if the TikTok version for Android monitored clipboards for any other reason, (2) if any clipboard text was uploaded from the device, and (3) why TikTok didn’t remove the monitoring as promised in March. The spokesperson has yet to respond. This post will be updated if a reply comes later.
Not just TikTok
In all, the researchers found the following iOS apps were reading users’ clipboard data every time the app was opened with no clear reason for doing so:
App Name — BundleID
News
ABC News — com.abcnews.ABCNews
Al Jazeera English — ajenglishiphone
CBC News — ca.cbc.CBCNews
CBS News — com.H443NM7F8H.CBSNews
CNBC — com.nbcuni.cnbc.cnbcrtipad
Fox News — com.foxnews.foxnews
News Break — com.particlenews.newsbreak
New York Times — com.nytimes.NYTimes
NPR — org.npr.nprnews
ntv Nachrichten — de.n-tv.n-tvmobil
Reuters — com.thomsonreuters.Reuters
Russia Today — com.rt.RTNewsEnglish
Stern Nachrichten — de.grunerundjahr.sternneu
The Economist — com.economist.lamarr
The Huffington Post — com.huffingtonpost.HuffingtonPost
The Wall Street Journal — com.dowjones.WSJ.ipad
Vice News — com.vice.news.VICE-News
Games
8 Ball Pool™ — com.miniclip.8ballpoolmult
AMAZE!!! — com.amaze.game
Bejeweled — com.ea.ios.bejeweledskies
Block Puzzle —Game.BlockPuzzle
Classic Bejeweled — com.popcap.ios.Bej3
Classic Bejeweled HD —com.popcap.ios.Bej3HD
FlipTheGun — com.playgendary.flipgun
Fruit Ninja — com.halfbrick.FruitNinjaLite
Golfmasters — com.playgendary.sportmasterstwo
Letter Soup — com.candywriter.apollo7
Love Nikki — com.elex.nikki
My Emma — com.crazylabs.myemma
Plants vs. Zombies™ Heroes — com.ea.ios.pvzheroes
Pooking – Billiards City — com.pool.club.billiards.city
PUBG Mobile — com.tencent.ig
Tomb of the Mask — com.happymagenta.fromcore
Tomb of the Mask: Color — com.happymagenta.totm2
Total Party Kill — com.adventureislands.totalpartykill
5-0 Radio Police Scanner — com.smartestapple.50radiofree
Accuweather — com.yourcompany.TestWithCustomTabs
AliExpress Shopping App — com.alibaba.iAliexpress
Bed Bath & Beyond — com.digby.bedbathbeyond
Dazn — com.dazn.theApp
Hotels.com — com.hotels.HotelsNearMe
Hotel Tonight — com.hoteltonight.prod
Overstock — com.overstock.app
Pigment – Adult Coloring Book — com.pixite.pigment
Recolor Coloring Book to Color — com.sumoing.ReColor
Sky Ticket — de.sky.skyonline
The Weather Network — com.theweathernetwork.weathereyeiphone
Shortly after the report was published, 10% Happier: Meditation and Hotel Tonight promised to stop the behavior and quickly followed through. TikTik also promised to stop but has never done so, Mysk said. None of the other apps has stopped either, he said.
Clipboard reading done right
In some cases, clipboard reading can make apps much more useful. The UPS iPhone app, for instance, pulls text from the clipboard and in the event the text matches the characteristics of a tracking number, the app prompts the user to track the corresponding package. Google Chrome also pulls text and, in the event it’s a URL, will prompt the user to browse to it. The Pixelmator photo editor reads data only if it’s an image. If it is, Pixelmator will prompt the user to open it for editing. In all three cases, the data reading has a clear use case and is transparent.
TikTok and the other offending apps, by contrast, access the clipboard for no clear reason and with no indication they are doing so. For many apps, it’s hard to see any legitimate performance or usability reason for the access. Mysk said that Apple plans to credit his and Haj Bakry’s research as a catalyst for the new clipboard notification put into iOS 14.
The clipboard reading Haj Bakry and Mysk reported raises concerns that likely extend to those using Android and possibly other operating systems. Mysk said that clipboard reading in Android apps is “even worse” than iOS because the OS APIs are so much more lenient. Until version 10, for instance, Android allowed apps running in the background to read the clipboard. iOS apps, by contrast, can read or query clipboards only when active (that is, running in the foreground).
Mysk said that Apple’s notification feature is a good start but, ultimately, Apple and Google should do more. One possibility is to make clipboard access a standard permission, just as access to a mic or camera is now. Another possibility is to require app developers to disclose precisely what clipboard data is accessed and what the app does with it.
For now, users should remain aware that any data stored in the clipboard—despite it being inconspicuous to the naked eye—can be regularly accessed by apps that in many cases aren’t even installed locally on the device. When in doubt, flush the clipboard data by copying a character, word, or other piece of innocuous data.