Anonymous festeggia il Natale violando i siti di ASL e ospedali


Gli hacktivist hanno fatto strage dei sistemi informatici nel settore sanitario. “Chi dovrebbe trattare con cura i nostri dati non fa il lavoro per cui viene pagato”.

Un modo costruttivo per passare il tempo durante le feste di Natale? Gli hacktivist di Anonymous Italia l’hanno trovato avviando una campagna di attacchi nei confronti di numerosi siti Internet di Aziende Sanitarie Locali e strutture ospedaliere italiane. L’obiettivo è sempre il solito: dimostrare che i dati dei cittadini italiani sono gestiti in maniera inadeguata.

La “rivendicazione” dell’attacco è stata pubblicata sul blog ufficiale di Anonymous Italia, accompagnata da un fotomontaggio in cui gli hacktivist si sono divertiti a reinterpretare il presepe inserendo personaggi della politica italiana. La stessa immagine è comparsa su alcuni dei siti violati.
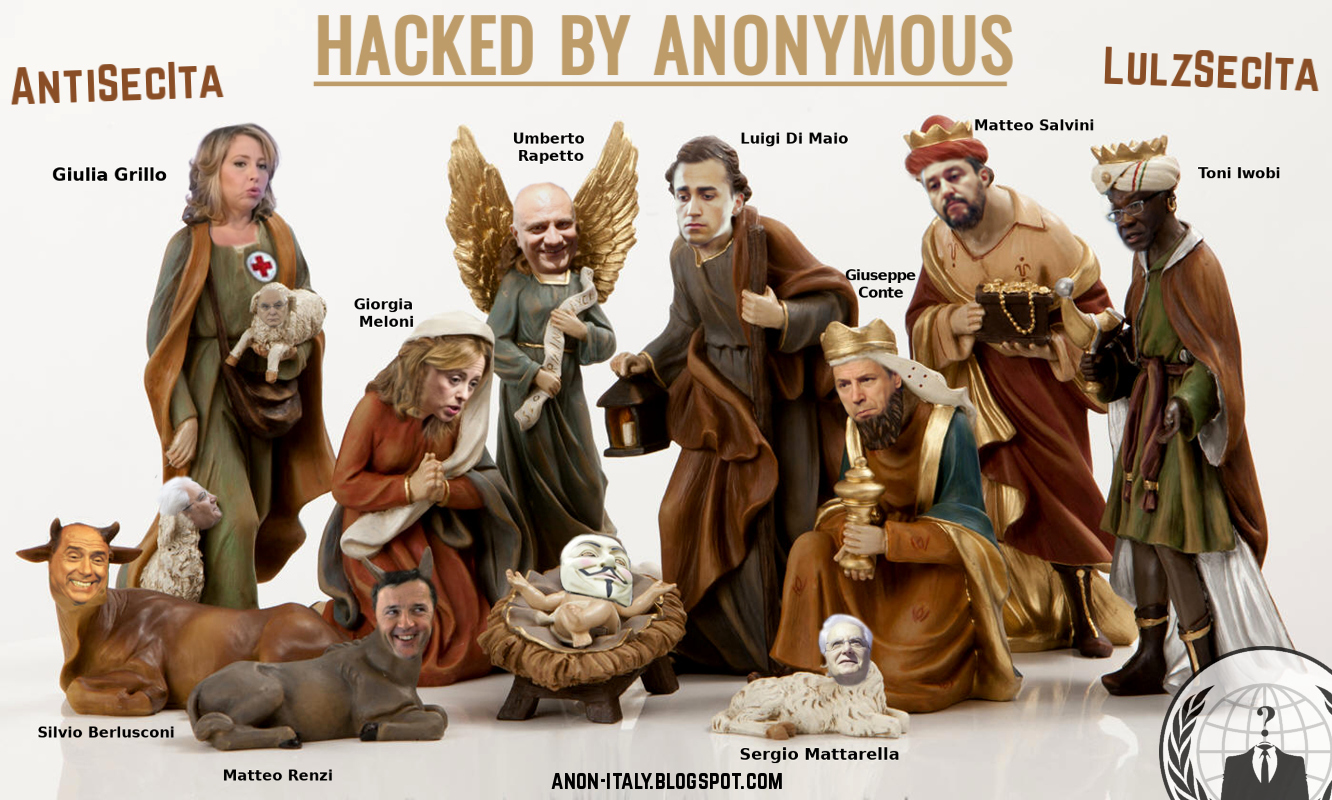
Anonymous Italia

Nel comunicato, gli hacker puntano il dito contro un sistema sanitario che, oltre a dover garantire cure mediche e salute del territorio, dovrebbe proteggere le informazioni personali dei pazienti. “Chi ci governa, e chi dovrebbe trattare con cura i nostri dati/privacy, non fa il lavoro per cui viene profumatamente pagato” chiosano sul loro blog.

L’azione, si legge sul blog, è stata portata insieme a gruppi differenti (e piuttosto conosciuti nel nostro paese) come LulzSecIta e AntiSecIta, che da sempre si riconoscono in quella “galassia informale” che siamo abitutati a chiamare Anonymous.

Anonymous Italia

Guardando quali e quante organizzazioni gli Anon sono riusciti a violare, però, si può concordare sul fatto che il livello di sicurezza del sistema sanitario nazionale non è precisamente “da manuale”.

L’elenco degli istituti caduti sotto i loro colpi comprende le ASL di Caserta, Rieti e Viterbo, l’ospedale San Giovanni di Roma, ISS, Agenas, Difarma, Federsanità, ASST Lariana e l’ULSS21 di Legnano.

Una vera strage, che dimostra ancora una volta come le varie normative, partendo dal GDPR e passando dalla direttiva NIS (Network and Information Security), stentino a trovare applicazione proprio in quei settori in cui sarebbe più necessario.

I file pubblicati su Internet, a differenza di quanto accaduto in passato in casi simili, non comprendono i dati personali dei pazienti ma soltanto la struttura dei database sottratti. Insomma: gli hacker si sono limitati a dimostrare di avere la possibilità di accedere a tutti i dati presenti sui server, senza però diffonderli.

Please follow and like us:


Articoli correlati
Altro in questa categoria

https://www.securityinfo.it/2018/12/27/anonymous-festeggia-il-natale-violando-i-siti-di-asl-e-ospedali/


Alexa May Be Recording More Than You Realize

Executives may need to reconsider whether Amazon’s Alexa personal assistant is listening to more than just their commands. Or perhaps the telephone conference attendee who pauses to gather details from Alexa is giving the device more than just his or her own comments.

Privacy concerns over just how much information is received and stored by personal assistants are not new — but have now been quantified. An EU citizen, exercising his GDPR rights, asked Amazon for information on all his personal information held by the firm. What he received, two months later, was a link to a 100Mb zip file containing 1,700 Alexa audio files. He doesn’t own an Amazon Echo device and has never used the Alexa service; and it was not his voice that was recorded.

Strike 1 against Amazon for breaching the privacy of the true owner. Strike 2 comes with the detail of those recordings.

Forbes magazine set the scene in August 2018. Charles Radclyffe, a visiting fellow at the University of Bristol, wrote, “When you press the ‘mute’ button on an Amazon Echo, the top ring glows with a red indicator to confirm that Alexa is no longer listening. It’s elegant, simple, but disguises a very deep design problem. Alexa is designed to be always listening. The default is therefore for the microphone to be on, the light to be off.”

This is confirmed by the recordings received by the EU citizen. He reportedly contacted Amazon, but received no reply. The link to the downloadable file became inactive — but he had already downloaded it. He shared his story and the files with c’t magazine, part of the Heise group.

c’t magazine examined the files to see if they could determine the true owner of the recordings. They succeeded. But in doing so, they also discovered the amount of data stored by Alexa. They discovered the ‘victim’ of the Amazon error had a girlfriend, and were able to identify her. They heard the surname of a friend who they identified via social media, giving them a view of his wider circle of friends. They even heard him in the shower.

When the magazine contacted this person, he was shocked — and confirmed that he had heard nothing from Amazon even though the original recipient of the files had reported the error. Neither party heard anything from Amazon until three days after c’t magazine contacted it.

Amazon subsequently told Reuters, “This unfortunate case was the result of a human error and an isolated single case. We resolved the issue with the two customers involved and took measures to further optimize our processes. As a precautionary measure we contacted the relevant authorities.”

Unfortunately, this is not the first privacy incident involving Alexa. In May 2018, the KIRO 7 news service reported another incident: Alexa recorded and sent a private conversation between a couple to one of the husband’s employees. The employee immediately called back and told them to unplug their Alexa devices, fearing they had been hacked.

Amazon’s explanation was that Alexa first misinterpreted something in the conversation as a wake-up command, and then misinterpreted other comments as an instruction to send the recording to the employee. While this is possible, it does confirm that the use and location of Alexa devices — and any other personal assistant — should be carefully considered.

Earlier this year, Alexa was awarded the Bielefield, Germany, Big Brother ‘data octopus’ award. By design, it must always be listening in order to know when to act — these two incidents demonstrate that this listening can lead to privacy complications.

Related: Amazon Alexa Can Be Used for Snooping, Researchers Say 

Related: Siri, Alexa, Google Now Vulnerable to Ultrasound Attacks

Related: Amazon Echo, Google Home Vulnerable to BlueBorne Attacks 

view counter

Kevin Townsend is a Senior Contributor at SecurityWeek. He has been writing about high tech issues since before the birth of Microsoft. For the last 15 years he has specialized in information security; and has had many thousands of articles published in dozens of different magazines – from The Times and the Financial Times to current and long-gone computer magazines.

Previous Columns by Kevin Townsend:

Tags:

http://feedproxy.google.com/~r/Securityweek/~3/wknqyXfq5P0/alexa-may-be-recording-more-you-realize


Usate HolaVPN? Smettete subito!


Un’analisi di Trend Micro mette a nudo tutti i difetti del servizio: niente crittografia dei dati, indirizzo IP in chiaro e un uso “discutibile” del traffico degli utenti.

Lo scopo di una VPN (Virtual Private Network) dovrebbe essere quello di proteggere il traffico Internet e garantire all’utente la possibilità di navigare anonimamente evitando eventuali sistemi di tracciamento o identificazione.

Usiamo il condizionale perché, come dimostra la cronaca recente, la maggior parte delle VPN in circolazione non offrono esattamente quello che promettono. Anzi.

Il mese scorso, un’indagine di Metric Labs aveva già messo in luce come molte applicazioni gratuite di questo genere tracciassero la navigazione degli utenti, fornendo i dati addirittura alle autorità cinesi.

Ora ci pensa Trend Micro a sganciare un’altra “bomba” sui servizi VPN gratuiti, pubblicando un report che analizza le caratteristiche di HolaVPN, un’applicazione free utilizzata da almeno 175 milioni di persone, di cui 8 milioni solo attraverso l’estensione di Chrome.

HolaVPN viene proposta come una “VPN collettiva”, che consente di navigare in maniera anonima grazie alla collaborazione tra gli utenti. È organizzata a nodi, un po’ come Tor, e promette di “evitare la censura” e migliorare le prestazioni di navigazione.

HolaVPN

Peccato che chiamarla “VPN” sia una netta forzatura. Prima di tutto Hola non usa alcun sistema di crittografia per proteggere i dati inviati e ricevuti, aprendo la strada a qualsiasi tipo di attacco Man in The Middle.

Non solo: l’assenza di crittografia permette anche di individuare l’indirizzo IP dell’utente. Questo significa che potrà anche “superare la censura”, ma che il PC può essere tracciato. Per chi vuole navigare in un paese in cui il Web è censurato, l’anonimato non è un optional.

Passando alle modalità con cui HolaVPN monetizza i servizio (non ha pubblicità) i ricercatori di Trend Micro spiegano che il modello di business è basato sulla vendita a terze parti della banda messa a disposizione dagli utenti.

In pratica, Hola (o meglio la sua sussidiaria Luminati) vende un servizio proxy sfruttando come punti di uscita gli utenti di HolaVPN. Una manna per i pirati informatici, che possono utilizzare il servizio per offuscare l’IP delle loro botnet.

La conferma arriva dalle analisi dei ricercatori, secondo i quali l’85% del traffico viene dirottato verso pubblicità mobile. Tradotto: qualcuno lo sta utilizzando per portare a termine frodi pubblicitarie, simulando traffico inesistente attraverso la rete di HolaVPN.

Please follow and like us:


Articoli correlati
Altro in questa categoria

https://www.securityinfo.it/2018/12/18/usate-holavpn-smettete-subito/


Irish Data Authority Probes Facebook Photo Breach

The Irish data watchdog on Friday launched an investigation into Facebook, after the social media titan admitted a “bug” may have exposed unposted photos from up to 6.8 million users.

The Irish Data Protection Commission (DPC) probe will take place under strict new European privacy laws outlined in the General Data Protection Regulation (GDPR).

It follows a similar probe launched in October — when Facebook admitted a security breach exposed 50 million user accounts.

“The Irish DPC has received a number of breach notifications from Facebook since the introduction of the GDPR on May 25, 2018,” said head of communications Graham Doyle.

“With reference to these data breaches, including the breach in question, we have this week commenced a statutory inquiry examining Facebook’s compliance with the relevant provisions of the GDPR.”

The Irish DPC has primary European jurisdiction over Facebook as the California-based firm has established its international headquarters in Dublin.

GDPR legislation gives regulators vast powers to sanction firms failing to sufficiently secure personal data.

Corporations can be fined up to four percent of their annual global turnover if they neglect to conform.

That means Facebook faces a theoretical fine of 1.4 billion euros ($1.6 billion), based on its 2017 annual revenue of 35.2 billion euros ($40.6 billion).

On Friday Facebook said using the social media login and granting permission to third-party applications to access photos may have led to the unintended breach between September 13 and 25.

“When someone gives permission for an app to access their photos on Facebook, we usually only grant the app access to photos people share on their timeline,” engineering director Tomer Bar announced in a message to developers.

“In this case, the bug potentially gave developers access to other photos, such as those shared on Marketplace or Facebook Stories.”

The earlier October DPC investigation was launched after Facebook admitted attackers exploited a vulnerability in the website’s code in a manner which could have granted access to private accounts.

That probe has been touted as the first major test of GDPR legislation.

Facebook is already under scrutiny as a result of its role in the Cambridge Analytica (CA) data scandal.

Following revelations from a whistleblower it was revealed that tens of millions of users had their personal data hijacked by CA, a political firm working for Donald Trump in 2016.

view counter

© AFP 2018

Previous Columns by AFP:

Tags:

http://feedproxy.google.com/~r/Securityweek/~3/E0b5Qr9go14/irish-data-authority-probes-facebook-photo-breach


‘No Evidence’ of Huawei Spying, Says German IT Watchdog

Germany’s IT watchdog has expressed scepticism about calls for a boycott of Chinese telecoms giant Huawei, saying it has seen no evidence the firm could use its equipment to spy for Beijing, news weekly Spiegel reported Friday.

“For such serious decisions like a ban, you need proof,” the head of Germany’s Federal Office for Information Security (BSI), Arne Schoenbohm, told Spiegel, adding that his agency had no such evidence.

Huawei has faced increasing scrutiny over its alleged links to Chinese intelligence services, prompting countries like the United States, Australia and Japan to block it from building their next-generation, super-fast 5G internet networks.

The US has put pressure on Germany to follow suit, Spiegel wrote.

Schoenbohm said BSI experts had examined Huawei products and components from around the world.

They had also visited Huawei’s newly opened lab in Bonn, where German clients can inspect the firm’s cyber security measures and the software behind its products.

But some observers raised eyebrows at the BSI’s apparent dismissal of cyber security risks concerning Huawei.

“I believe it’s wrong to suggest that the concerns about Chinese espionage are unfounded and easy to detect,” telecom security expert Ronja Kniep told AFP.

“Even if Huawei has no official relationship with the Chinese government, that doesn’t mean Chinese services aren’t using the company and its technology as vehicles for espionage.”

All three of Germany’s main mobile network operators use infrastructure provided by Huawei, Spiegel pointed out.

The Chinese firm is also the brand behind some of Germany’s most popular mobile phones.

Related: Under Fire Huawei Agrees to UK Security Demands

Related: AT&T Backs Away From Deal to Supply China Made Huawei Phones

Related: New Zealand Halts Huawei From 5G Upgrade Over Security Fears

Related: EU Should Worry About Huawei, Other Chinese Firms

view counter

© AFP 2018

Previous Columns by AFP:

Tags:

http://feedproxy.google.com/~r/Securityweek/~3/3OeYEVxPCl0/no-evidence-huawei-spying-says-german-it-watchdog


Photos of 6.8 Million Facebook Users Exposed by API Bug

Facebook Discloses Photo API Bug Affecting 6.8 Million Users

Facebook revealed on Friday that a bug related to its Photo API could have allowed third-party apps to access users’ photos, even ones that were supposed to be private.

According to the social media giant, its internal team discovered a bug in the Photo API that impacted users who had utilized Facebook Login and allowed third-party apps to access their photos.

Applications that are granted access to photos are normally allowed to access only images shared on a user’s timeline. However, due to this flaw, developers could have accessed other photos as well, including ones shared on Facebook Marketplace or via Stories, or photos that were only uploaded to the social media service but not posted.

The vulnerability exposed photos for 12 days, between September 13 and September 25, 2018. Facebook believes the bug impacted up to 6.8 million users and 1,500 applications built by over 870 developers. The company pointed out that only apps granted access to photos by the user could have exploited the flaw.

Facebook says it’s notifying impacted people via an alert in their account and it also plans on releasing tools early next week that will allow developers to determine which of their users may have been affected by the issue. Developers will be instructed to delete photos obtained as a result of this bug.

Facebook announced this week that it has paid out more than $1.1 million through its bug bounty program in 2018, with roughly $7.5 million paid by the social media giant since the launch of its program in 2011.

The $1.1 million has been awarded to researchers from over 100 countries for more than 700 valid reports.

Facebook has been hit by several privacy and security incidents this year, which has resulted in the company expanding its bug bounty program and significantly increasing rewards for some types of vulnerabilities.

Related: The Scandals Bedevilling Facebook

Related: Industry Reactions to Facebook Hack

Related: Facebook App Exposed Data of 120 Million Users

view counter

Eduard Kovacs (@EduardKovacs) is a contributing editor at SecurityWeek. He worked as a high school IT teacher for two years before starting a career in journalism as Softpedia’s security news reporter. Eduard holds a bachelor’s degree in industrial informatics and a master’s degree in computer techniques applied in electrical engineering.

Previous Columns by Eduard Kovacs:

Tags:

http://feedproxy.google.com/~r/Securityweek/~3/nL68yZt839c/photos-68-million-facebook-users-exposed-api-bug


Rhode Island Sues Alphabet Over Google+ Security Incidents

A government organization in Rhode Island announced on Wednesday that it has filed a lawsuit against Google’s parent company, Alphabet Inc., over the recent security incidents involving the Google+ social network.

The Employees’ Retirement System of Rhode Island filed a motion in the Northern District of California asking to lead a shareholder class action against Alphabet. The Internet giant has been accused of misleading federal regulators and shareholders by failing to “disclose ongoing breaches in private user information from its social media platform Google+.”

“Google had an obligation to tell its users and investors that private information wasn’t being protected,” commented Rhode Island General Treasurer Seth Magaziner. “Instead, Google executives decided to hide the breaches from its users and continued to mislead investors and federal regulators. This is an unconscionable violation of public trust by Google, and we are seeking financial restitution on behalf of the Rhode Island pension fund and other investors.”

The lawsuit focuses on the two recent incidents involving Google+. The first was brought to light in October, when Google announced its decision to shut down the social network. The announcement also disclosed the existence of an API bug that exposed the personal information of as many as 500,000 users.

The company said the flaw, which it had discovered in March, gave hundreds of third-party apps access to information such as name, email address, occupation, gender and age. However, there was no evidence that the vulnerability was actually exploited.

The initial plan was to shut down Google+ by the end of next August, but Google has decided to do it four months earlier, in April 2019, after discovering another API vulnerability, this time one that affected roughly 52 million users.

The recently discovered flaw was introduced in November via a software update and it allowed applications to view profile information, including name, occupation, age, and email address, even if the account was configured to be private.

Shortly after Google disclosed the first incident, a group of US senators sent the company a letter asking for additional information, particularly regarding the decision to keep the incident a secret.

Related: Industry Reactions to Google+ Security Incident

Related: Google Tightens Rules Around App Permissions

Related: New Lawsuit Claims Marriott Still Exposes Customer Information

Related: Over 30 Lawsuits Filed Against Intel for CPU Flaws

view counter

Eduard Kovacs (@EduardKovacs) is a contributing editor at SecurityWeek. He worked as a high school IT teacher for two years before starting a career in journalism as Softpedia’s security news reporter. Eduard holds a bachelor’s degree in industrial informatics and a master’s degree in computer techniques applied in electrical engineering.

Previous Columns by Eduard Kovacs:

Tags:

http://feedproxy.google.com/~r/Securityweek/~3/mZyKpLkq82s/rhode-island-sues-alphabet-over-google-security-incidents


Super Micro: No Malicious Hardware Found on Motherboards

California-based Super Micro told customers on Tuesday that it has conducted a thorough investigation in response to a Bloomberg article claiming that Chinese spy chips had been planted on its servers, but found no evidence of malicious hardware.

Bloomberg reported in early October that the Chinese government planted tiny spy chips in Super Micro products in an effort to spy on Apple, Amazon and tens of other major companies in the United States.

While Bloomberg stands by its story, all the tech firms mentioned in its article, including Super Micro itself and Apple, have strongly denied the allegations. Furthermore, even government agencies in the US and UK have denied investigating such incidents, as claimed by Bloomberg.

In a letter published on Tuesday, Super Micro’s CEO, Charles Liang, its SVP and Chief Compliance Officer, David Weigand, and SVP and Chief Product Officer, Raju Penumatcha, told customers that an investigation conducted with the assistance of a third-party firm “found absolutely no evidence of malicious hardware” on Supermicro motherboards.

“A representative sample of our motherboards was tested, including the specific type of motherboard depicted in the [Bloomberg] article and motherboards purchased by companies referenced in the article, as well as more recently manufactured motherboards,” Super Micro officials said.

“As we have stated repeatedly since these allegations were reported, no government agency has ever informed us that it has found malicious hardware on our products; no customer has ever informed us that it found malicious hardware on our products; and we have never seen any evidence of malicious hardware on our products,” they added. “Today’s announcement should lay to rest the unwarranted accusations made about Supermicro’s motherboards.”

The company has also provided some information about how it protects the integrity of its products and even published a video showing its quality assurance process.

The stocks of Super Micro and Chinese tech firms Lenovo and ZTE tumbled as a result of Bloomberg’s report. Super Micro shares have started to recover, but they’re still only at $16, compared to roughly $20 before Bloomberg ran its story.

Related: Apple Tells Congress Chinese Spy Chip Story Is False

Related: Industry Reactions to Chinese Spy Chips

view counter

Eduard Kovacs (@EduardKovacs) is a contributing editor at SecurityWeek. He worked as a high school IT teacher for two years before starting a career in journalism as Softpedia’s security news reporter. Eduard holds a bachelor’s degree in industrial informatics and a master’s degree in computer techniques applied in electrical engineering.

Previous Columns by Eduard Kovacs:

Tags:

http://feedproxy.google.com/~r/Securityweek/~3/Vg5i65buMsw/super-micro-no-malicious-hardware-found-motherboards


Secure Messaging Applications Prone to Session Hijacking

Secure messaging applications such as Telegram, Signal and WhatsApp can expose user messages through a session hijacking attack, Cisco’s Talos security researchers warn. 

The three applications, all of which offer end-to-end encryption, claim to be able to keep users’ messages secure by encrypting them and preventing third parties from accessing them. According to Talos, however, this is not exactly true, as conversations could be exposed in certain scenarios. 

One of the main issues, the researchers say, is the fact that these applications assume that their users are security-educated and that they understand the risks of enabling certain settings on their devices. With hundreds of millions of users using these apps, this clearly isn’t the case. 

The applications, Talos points out, encrypt the content of all communication between users, without third parties involved. Thus, the service provider or anyone sniffing network traffic, should not be able to read the content at any point. However, there’s no assurance about security while the data is processing or when the message is on the user device. 

The instant messaging apps also support the major mobile device platforms and a desktop version, and Talos discovered that an attacker could use malware to hijack a session from a desktop version and access the data without the user knowing or before they would realize a hijack has been performed. 

On Telegram, the session hijacking is most likely to happen without users noticing it, which results in the attacker receiving all messages sent or received by the victim. The attacker can use the stolen session information to establish a new session and the user is never alerted on the issue. In fact, the user has to specifically check if there is an additional session in use. 

Signal, on the other hand, handles the session hijacking as a race condition, meaning that both the user and attacker application compete for the session. Thus, the user receives an error message on the desktop application (no alert is displayed on the mobile device), but the attacker already has access to all contacts and previous chats that were not deleted.

The attacker can prevent the race condition by deleting the session information from the user’s desktop, meaning they would be prompted to re-link. The second session will only be visible from the mobile device, but will have the same name as the attacker-controlled session. 

“Therefore, the attacker will have the ability to view all messages and even impersonate the victims. The messages sent by the attacker will reach the victim’s legitimate devices, but the attacker can delete them while sending them, avoiding detection. If the impersonation is done using the “Disappearing messages” feature, it will be even harder for the victim to identify the imitation,” Talos says. 

In WhatsApp, a notification is displayed when the second session is opened on a desktop, in the application that is online when the second session is created. The user is prompted to choose one session to continue, and the attacker has access to all contacts and previous messages until the user makes a decision. They can also impersonate the user during that time. 

According to Talos, an attacker could even bypass the warning mechanism and keep their session live. For that, they would need to stop the application on the victim machine, then launch WhatsApp with the hijacked session, and then disable the network interface on their machine, and only enable it after the victim’s WhatsApp application has been launched again. 

The security researchers discovered that the mobile version of Telegram too is prone to session abuse, as it allows for “shadow sessions to coexist on the same device based on the same phone number while handling it in different applications.” Thus, an attacker could read all messages and contacts on Telegram until the session is terminated (user has to specifically request termination). 

On Android, a malicious app granted the “read SMS” and “kill background process” permissions could create a shadow session without any user intervention. Normally, if the user tries to register the same phone number again, Telegram sends a code over the Telegram channel. However, if the registration isn’t completed in a specific timeframe, Telegram sends a new code over SMS, which is read by the malicious app. 

“Secure instant messaging applications have a solid track record of protecting the information while in transit, even going as far as protecting the information from their own servers. However, they fall short when it comes to protecting application state and user information, delegating this protection to the operating system,” Talos concludes.

Related: Telegram Leaks User IP Addresses

Related: Researchers Find Flaw in WhatsApp

view counter

Ionut Arghire is an international correspondent for SecurityWeek.

Previous Columns by Ionut Arghire:

Tags:

http://feedproxy.google.com/~r/Securityweek/~3/wYmt1u9wWK4/secure-messaging-applications-prone-session-hijacking


Google+ bug exposes non-public profile data for 52 million users

The Google Plus (G+, or Google +) social network logo is seen in the company's offices behind Android toys on August 21, 2014 in Berlin, Germany.
Enlarge / The Google Plus (G+, or Google +) social network logo is seen in the company’s offices behind Android toys on August 21, 2014 in Berlin, Germany.

Two months after disclosing an error that exposed the private profile data of almost 500,000 Google+ users, Google on Monday revealed a new leak that affects more than 52 million people. The programming interface bug allowed developers to access names, ages, email addresses, occupations, and a wealth of other personal details even when they were set to be nonpublic.

The bug was introduced in a release that went live at an undisclosed date in November and was fixed a week later, Google officials said in a blog post. During the time the bug was active, developers of apps that requested permission to view profile information that a user had added to their Google+ profile received permission to view profile information about that user even when the details were set to not-public. What’s more, apps with access to users’ Google+ profile data had permission to access non-public profile data that other Google+ users shared with the consenting user. In all, the post said, 52.5 million users are affected.

“The bug did not give developers access to information such as financial data, national identification numbers, passwords, or similar data typically used for fraud or identity theft,” Monday’s post said. “No third party compromised our systems, and we have no evidence that the developers who inadvertently had this access for six days were aware of it or misused it in any way.”

Google said it was in the process of notifying consumer users who were affected. The post also said that Google is notifying affected enterprise customers by contacting administrators and sending them a list of affected users. Monday’s post didn’t say how many of the affected users were consumers versus enterprise customers.

The leak Google disclosed in October exposed non-public profile data from 2015 to 2018. It, too, was the result of a programming interface bug. Google said at the time that it would shut down the Google+ social networking service to consumers because of the “significant challenges” it faced in meeting users’ privacy expectations. Google also said at the time that it planned to gradually wind down the service to consumers over a 10-month period to give them a lengthy window to transition to other services.

On Monday, Google said it planned to expedite the closure from August 2019 to April. Google said it still planned to give users the opportunity to transition off of consumer Google+ and would provide them with information on ways to safely and securely download their data and move it to other services, if wanted.

While Google said it had no evidence either data leak was actively exploited, it has no way of assuring users that developers haven’t accessed the profile data that was supposed to be non-public. That means users should assume all profile data of this type is now in the public domain, regardless of how they had set up their permissions. The best way for users to protect themselves is to remove all data from profiles, close the accounts, and manually remove the Google+ app from their devices as soon as possible.

https://arstechnica.com/?p=1426049