Meta Paid $78,000 Bounty for Vulnerability Exposing Customer Support Data
A security researcher says he has received a significant bug bounty from Meta after discovering a critical vulnerability that exposed customer support data.

The vulnerability was discovered and reported to Meta in January 2026 by independent researcher Rony K Roy. The initial report to the social media giant described a security hole of limited severity, but further analysis revealed that the flaw’s impact was much higher than initially believed. 

According to Roy, Meta rolled out patches in April and had not found any evidence of malicious exploitation.

The researcher disclosed his findings last week and told SecurityWeek that he received a $78,000 bug bounty from Meta. 

Meta has not responded to SecurityWeek’s request to confirm Roy’s claims, but he is indeed listed as one of the top researchers on the company’s bug bounty leaderboard for 2026.

Roy initially believed he had identified an authorization issue in Meta Horizon Managed Solutions, an enterprise platform for managing Meta Quest devices and users. It turned out to be a broader issue affecting Meta’s backend support infrastructure.

Advertisement. Scroll to continue reading.

The researcher’s analysis led to the discovery of a vulnerability involving missing authorization, broken access control, and insecure direct object reference (IDOR) issues. 

When chained, these flaws could have been exploited to enumerate Meta support case numbers and obtain support requests.

According to Roy, an attacker could have exploited the vulnerability to obtain email and chat conversations between users and Meta support, support case details, files submitted to the company via support requests, and personal and contact information shared by users with Meta support.

In addition, an attacker could have created support requests on behalf of organizations that use Meta Horizon Managed Solutions, modified support workflows (including changing case status), and added unauthorized subscribers to support cases.

Related: Exploitation of ServiceNow Vulnerability Seen Days After Disclosure

Related: Zimbra Update Patches Critical Vulnerabilities

Related: OpenSSL Silently Fixes ‘HollowByte’ DoS Vulnerability

https://www.securityweek.com/meta-pays-78000-bounty-for-vulnerability-exposing-customer-support-data/

SonicWall Zero-Days Exploited to Deliver Custom Malware for Weeks Before Patch

Two recently patched SonicWall appliance zero-days were exploited by threat actors for weeks before patches were released, according to cybersecurity firm Volexity.

SonicWall released a public advisory for the vulnerabilities on July 14, informing customers that CVE-2026-15409 and CVE-2026-15410 had been exploited in the wild.

Remote, unauthenticated attackers can exploit the flaws to hack SMA1000 secure remote access appliances. SonicWall has made available hotfix releases to address the security holes.

Volexity, which assisted the vendor’s investigation into the attacks, attributed the exploitation of the zero-days to a threat actor it tracks as UTA0533. 

The security firm believes exploitation started as early as June 22.

The company on Friday shared IoCs and other technical details related to the attacks, but it has not linked UTA0533 to any known threat actor and the group’s motivation remains unclear. However, based on Volexity’s description, the attack appears more consistent with state-sponsored APT activity rather than a profit-driven cybercrime operation.

Advertisement. Scroll to continue reading.

Once the attackers compromised the targeted SonicWall appliances, they deployed custom malware named KnuckleBall, which injected two other tools into legitimate processes: a tailored Java webshell named OrangeTail, and an open source proxy named Suo5.

“With root access, the threat actor could access stored or cached credentials, capture network traffic, and potentially intercept credentials processed by the appliances,” Volexity said. 

The security firm added, “Although UTA0533 demonstrated significant capability in compromising the SonicWall appliances, available evidence suggests the threat actor was less successful moving laterally or gaining access to other systems.”

CISA has added CVE-2026-15409 and CVE-2026-15410 to its KEV catalog, which currently includes 17 flaws affecting SonicWall products.

Related: WP2Shell WordPress Vulnerabilities Exploited in the Wild

Related: Fresh SharePoint Vulnerability Exploited Soon After Disclosure

Related: Splunk, Zoom Patch Critical Vulnerabilities

Related: Nightmare Eclipse Drops ‘LegacyHive’ Windows Zero-Day

https://www.securityweek.com/sonicwall-zero-days-exploited-to-deliver-custom-malware-for-weeks-before-patch/


OpenSSL Silently Fixes ‘HollowByte’ DoS Vulnerability

A vulnerability in OpenSSL could allow attackers to cause a server’s memory to be exhausted before any security handshake, Okta’s red team discovered.

Referred to as HollowByte, the denial-of-service (DoS) bug could be triggered via a malicious payload of only 11 bytes that declares a larger incoming message body to trigger a buffer pre-allocation that is not immediately freed.

HollowByte existed because older OpenSSL iterations pre-allocated receive buffer sizes based on the incoming message body length declared in the handshake message’s 4-byte header.

The pre-allocation occurred before any data arrived, and an attacker could send an 11-byte payload to trigger an unvalidated buffer allocation of up to 131 KB.

“The worker thread then blocks, waiting indefinitely for data that will never arrive,” Okta explains.

Additionally, because the GNU C Library (glibc) retains small-to-medium memory allocations for potential reuse and does not immediately return them to the OS when a connection drops, although OpenSSL frees the buffer, multiple successive payloads could be sent to exhaust the server’s memory.

Advertisement. Scroll to continue reading.

“By launching waves of connections with randomized claimed sizes, an attacker prevents the allocator from reusing those freed chunks,” Okta explains.

“Even after the attacker disconnects, the server remains permanently bloated. The only way to reclaim that memory is to terminate the process,” it adds.

In real-world testing, a 1 GB RAM system became unresponsive after 547 MB of memory was fragmented and frozen.

On a 16 GB RAM system, “the attack successfully locked up 25% of the system’s total memory while staying safely under the connection ceiling, meaning standard connection-limiting defenses won’t stop it,” Okta says.

Apache, NGINX, Node.js, Python, Ruby, PHP, MySQL, PostgreSQL, and other types of applications, servers, runtimes, and databases that use OpenSSL are impacted unless they upgrade to a patched version of the open source library.

Patches for HollowByte were silently included in OpenSSL version 4.0.1 and silently backported to versions 3.6.3, 3.5.7, 3.4.6, and 3.0.21. Now, the library increases the buffer size as bytes actually land and no longer trusts the handshake header for buffer growth.

Related: Chrome 150 Update Patches Severe Memory Safety Bugs

Related: Nightmare Eclipse Drops ‘LegacyHive’ Windows Zero-Day

Related: Vulnerabilities Patched by Fortinet, Ivanti, ServiceNow

Related: SonicWall Issues Urgent SMA Patch Warning for Two Zero-Day Exploits

https://www.securityweek.com/openssl-silently-fixes-hollowbyte-dos-vulnerability/


Capital One Open Sources AI-Powered ‘VulnHunter’ Security Tool

Financial services giant Capital One has released an internally developed AI-powered security tool to the public as open source.

Dubbed “VulnHunter”, the tool was designed to find and fix software vulnerabilities at the code level, but Capital One says it is not a traditional, passive vulnerability scanner.

“We designed VulnHunter with a developer-first mindset to solve a massive industry pain point: overwhelming false positives that create friction and slow down daily workflows,” Chris Nims, EVP & Chief Information Security Officer (CISO) at Capital One, explained in a LinkedIn post.

“It represents a shift in defensive tooling with an agentic reasoning workflow to identify potentially exploitable defects, map prospective attack paths, and propose highly targeted code remediations,” the company says.

Available on GitHub, along with a quickstart guide, architecture documentation, and example workflows showing how the tool traces code paths and generates remediations, users currently need access to Claude Opus 4.8 and access to a working Claude Code environment.

“Modern software supply chains are deeply interconnected. A single vulnerability in a widely-used open-source component can ripple across thousands of enterprises simultaneously. We’re open-sourcing VulnHunter because no single organization can solve this challenge alone,” Capital One said. “The defensive tools to address this reality need to be just as widely distributed, tested, and improved as the codebases they protect.”

Advertisement. Scroll to continue reading.

Capital One claimed that, when using VulnHunter internally, it was able to quickly and efficiently identify and remediate vulnerabilities across thousands of repositories, spanning tens of business areas.

https://www.securityweek.com/capital-one-open-sources-ai-powered-vulnhunter-security-tool/


Chrome 150 Update Patches Severe Memory Safety Bugs

Google has released a Chrome 150 security update that resolves seven memory safety bugs, including critical and high-severity use-after-free vulnerabilities.

The browser refresh patches three critical-severity use-after-free flaws impacting Chrome’s CameraCapture, GPU, and Network components. All three weaknesses were discovered by Google.

Additionally, the update fixes three high-severity use-after-free issues in Cast, Ozone, and Aura; Google discovered these vulnerabilities as well.

The seventh security defect is an out-of-bounds read and write flaw in the V8 JavaScript engine that was identified by OpenAI Codex Security. Google has yet to determine the bug bounty amount to be paid for the finding.

Google makes no mention of any of these security defects being exploited in the wild, but users are advised to update their browsers as soon as possible, as threat actors have targeted memory safety issues in Chrome.

For years, the internet giant has been hardening the browser against the exploitation of memory safety bugs, including by transitioning to memory-safe programming languages such as Rust.

Advertisement. Scroll to continue reading.

Since April, the internet giant has patched over 1,400 Chrome vulnerabilities, including hundreds of memory safety flaws, most of which were discovered by Google, likely through the use of AI.

The latest Chrome iteration is now rolling out as versions 150.0.7871.128/.129 for Windows and macOS and as version 150.0.7871.128 for Linux.

Related: Critical Vulnerabilities Patched With Fresh Chrome 150, Firefox 152 Updates

Related: WP2Shell WordPress Vulnerabilities Exploited in the Wild

Related: Fresh SharePoint Vulnerability Exploited Soon After Disclosure

Related: Legacy Systems, Real-World Impacts: The Reality of OT Security

https://www.securityweek.com/chrome-150-update-patches-severe-memory-safety-bugs/


WP2Shell WordPress Vulnerabilities Exploited in the Wild

Two newly patched WordPress vulnerabilities are being exploited in the wild, with attacks beginning shortly after they came to light. 

The vulnerabilities have been dubbed WP2Shell and they are officially tracked as CVE-2026-60137 and CVE-2026-63030. 

According to Searchlight Cyber, whose researchers discovered the flaws, WordPress versions 6.9.0 through 6.9.4 and 7.0.0 through 7.0.1 are affected. 

“The attack has no preconditions and can be exploited by an anonymous user in a stock install of WordPress with no plugins,” the security firm warned.

WordPress announced patches on Friday with the release of versions 6.9.5 and 7.0.2. 

“Due to the severity, the WordPress.org team have enabled forced updates via the auto-update system for sites running affected versions,” WordPress developers said. 

Advertisement. Scroll to continue reading.

Cloudflare has also rolled out rules to detect exploitation and protect customers whose installations were not immediately patched. 

CVE-2026-60137 is a high-severity SQL injection bug and CVE-2026-63030 is a critical arbitrary code execution vulnerability. Chaining the two flaws enables an attacker to achieve unauthenticated remote code execution on affected WordPress websites. Threat actors can exploit these vulnerabilities to take control of targeted sites. 

While Searchlight Cyber has not made public any details to prevent abuse, PoC exploits have already been made public by others. 

WP2Shell exploited in the wild

The in-the-wild exploitation of the WP2Shell vulnerabilities has been confirmed by several cybersecurity firms. One of them is the WordPress security company Patchstack.

Hexastrike started seeing exploitation attempts in its honeypots over the weekend, and on Sunday the company said it had already assisted with incident response in several attacks. Hexastrike has shared some recommendations for detecting and investigating intrusions.

WatchTowr has also seen in-the-wild exploitation attempts.  

“This is going to hurt,” the company’s CEO and founder, Benjamin Harris, told SecurityWeek. “WordPress runs on hundreds of millions of websites globally. Some of those will be auto-patched by their hosting providers, but plenty will not, and that is where the damage will be done.”

Harris added, “This is also the latest example in a clear trend of vulnerabilities being surfaced by AI-assisted tooling, representing a significant shift in both how our industry finds these issues and how quickly attackers weaponize them. We saw PoCs appear within hours of disclosure, where historically that would have taken 24 hours or more. The window between disclosure and exploitation has collapsed, and WordPress is simply today’s reminder of it.”

Related: Attackers Exploit Gravity SMTP Plugin Flaw to Harvest Valuable WordPress Data

Related: 15,000 WordPress Websites Cleaned Up in SocGholish Botnet Takedown

Related: Everest Forms Vulnerability Exploited to Hack WordPress Sites

https://www.securityweek.com/wp2shell-wordpress-vulnerabilities-exploited-in-the-wild/


AI Data Centers Are Being Built Faster Than They Can Be Secured

The use and reliance on AI is the biggest single growth area in technology. But AI is enormously energy-intensive and requires a new quality of data center. 

The demand is fueling rapid growth in AI data center builds. The danger is that those building this new type of data center, at speed, do not readily understand the difference between traditional data centers and AI data centers – and the result is leaving the new AI data centers open to a new scale of risk. 

Traditional data centers are primarily data processing warehouses serving a known clientele. AI data centers are more akin to high power data compute factories serving a larger and unknown clientele. Traditional data centers can comprise a series of independent servers, an AI data center must function as a single engine capable of massive parallel processing to handle a much greater computational demand. AI data centers simply cannot be built in the same way as traditional data centers.

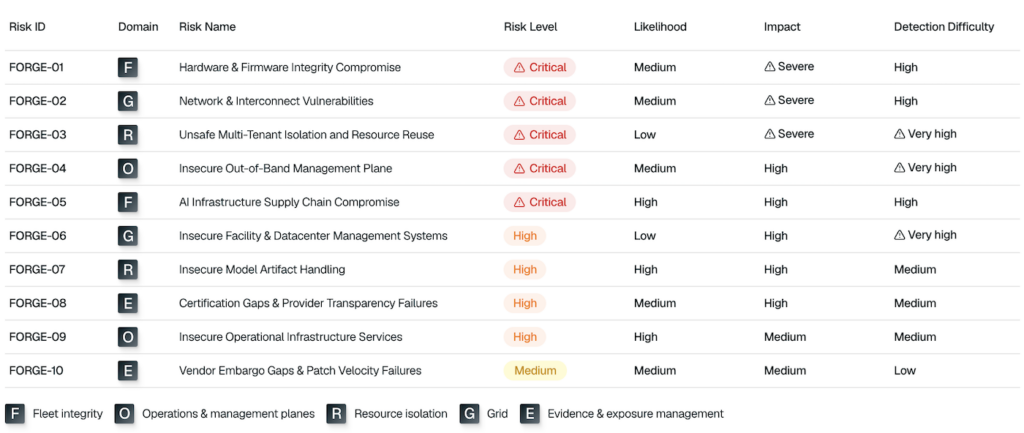
Lava Labs has examined and now reports (PDF) on the security needs of AI data centers (The Top 10 Data Center and AI Infrastructure Security Risks) and concludes they are being built faster than they are being secured. Both traditional data centers and new AI data centers carry largely similar risks; but AI changes their exploitability and blast radius: “Systems originally designed for trusted operators are now supporting high-value, multi-tenant workloads from unrelated customers,” it notes.

The Lava Labs report lists the top ten AI data center and infrastructure security risks, naming them ‘Forge’ (because the purpose is to ‘harden the metal beneath the model’).

  • Forge 01: firmware and hardware integrity compromise
  • Forge 02: network and interconnect vulnerabilities
  • Forge 03: unsafe multi‑tenant isolation and resource reuse
  • Forge 04: insecure out‑of‑band management plane
  • Forge 05: AI infrastructure supply chain compromise
  • Forge 06: insecure facility and data center management systems
  • Forge 07: insecure data and artifact handling
  • Forge 08: certification gaps and provider transparency failures
  • Forge 09: insecure operational infrastructure services
  • Forge 10: vendor embargo gaps and patch velocity failures

The sequencing of these risks is primarily based on severity. Risks 01 to 05 operate below the operating system, are difficult to detect, and have a cluster-wide blast radius. Risks 06 to 09 are generally easier to detect and recover from. Risk 10 is the easiest to detect and remediate; and is the least likely to cause catastrophic tenant compromise.

FORGE IDs are ordered by severity, from highest to lowest. The matrix groups each risk by domain and shows its likelihood, impact, and detection difficulty.

The risks arise because the nature of AI breaks the basic trust model of traditional data centers. For 03, 07, and 08. AI introduces unrelated commercial tenants, high‑value workloads, and GPU nodes that are reassigned between customers. 

For 01, 06 and 10, new hardware realities from the dense GPU clusters require complex firmware stacks, have extreme thermal sensitivity, and a larger blast radius for facility failures. 

Advertisement. Scroll to continue reading.

For 02, the required high performance fabrics such as InfiniBand, RoCE, RDMA, and NVLink are often unencrypted, poorly monitored, and highly privileged. Weak fabric isolation can expose paths to discovery, abuse, or lateral movement. 

In 04 and 09, an operational concentration of privilege can result from a heavy reliance on BMC automation, Redfish/IPMI, firmware pipelines, and orchestration systems.

For 05 and 10, a scarcity of GPU processors often means that new AI data centers opt for processors that are less suitable, with weaker isolation that can lead to more likely supply chain compromise.

The functional purpose of Lava Labs analysis and report is threefold: to expose the unique risks of AI data centers; to prioritize the most severe risks, thus effectively providing a triage sequence; and to provide example attack scenarios and practical mitigations for those risks.

The moral from the Lava Labs analysis is, yes, you will need a new data center to feed your AI; but, no, you cannot use your existing data center model as a design blueprint.

Learn More at the AI Risk Summit | Ritz-Carlton, Half Moon Bay

Related: Trump’s New AI Plan Leans Heavily on Silicon Valley Industry Ideas

Related: Pentagon Paid Out $290,000 for Vulnerabilities in Air Force Data Center

Related: Intel TDX Connect Bridges the CPU-GPU Security Gap

https://www.securityweek.com/ai-data-centers-are-being-built-faster-than-they-can-be-secured/


Splunk, Zoom Patch Critical Vulnerabilities

Splunk and Zoom this week announced patches for multiple vulnerabilities across their products, including several critical and high-severity security defects.

Only three of the five advisories that Splunk published address flaws that are specific to its products, while the other two resolve dozens of bugs in third-party components.

The Splunk-specific issues include CVE-2026-20296 (a high-severity command safeguards bypass), CVE-2026-20297 (a high-severity path traversal), and CVE-2026-20298 (a medium-severity information disclosure).

Successful exploitation of these weaknesses could allow attackers to access credentials and data, write files outside the intended application directory, and view stored credential hashes.

Patches for all three were included in Splunk Enterprise versions 10.4.1, 10.2.5, 10.0.8, and 9.4.13, which also address critical- and high-severity vulnerabilities in Golang, Go compiler, OpenSSL, and other third-party libraries.

Zoom published four advisories that resolve as many vulnerabilities across its clients and tools for Windows.

Advertisement. Scroll to continue reading.

The most severe is CVE-2026-53412 (CVSS score of 9.8), a critical bug in Zoom’s Workplace and Workplace VDI Client for Windows that could allow remote, unauthenticated attackers to mount account takeover attacks.

The company’s updates also resolve three high-severity flaws: a time-of-check-to-time-of-use (TOCTOU) race condition and two privilege elevation issues.  

Neither Splunk nor Zoom makes any mention of these vulnerabilities being exploited in the wild.

Related: F5 Patches Multiple NGINX, BIG-IP Vulnerabilities

Related: Nightmare Eclipse Drops ‘LegacyHive’ Windows Zero-Day

Related: Old UEFI Shims Expose Systems to Secure Boot Bypass

Related: CISA Urges Immediate Patching of Exploited SharePoint Vulnerabilities

https://www.securityweek.com/splunk-zoom-patch-critical-vulnerabilities/


F5 Patches Multiple NGINX, BIG-IP Vulnerabilities

F5 on Wednesday announced an out-of-band security rollout that patches eight vulnerabilities in NGINX and BIG-IP.

The most severe flaw is CVE-2026-42533 (CVSS score of 9.2), a critical issue in NGINX Plus and NGINX Open Source that could be exploited via crafted HTTP requests to cause a heap buffer overflow and restart the NGINX worker process.

“A vulnerability exists in NGINX Plus and NGINX Open Source when a map directive uses regex matching and a string expression references the map’s regex capture variables before referencing the map output variable. Alternatively, the same result could be achieved by using a non-cacheable variable in a string expression under certain conditions,” F5 explains.

An attacker can exploit the security defect without authentication, but only under conditions they cannot control. On systems with Address Space Layout Randomization (ASLR) disabled, the attacker can achieve code execution.

F5’s patches also resolve several high-severity NGINX bugs, including weaknesses in the ngx_http_slice_module module and the ngx_http_ssi_module module that can be exploited without authentication.

Successful exploitation of the flaws allows attackers to leak memory contents, restart the NGINX worker process, or cause a use-after-free in the NGINX worker process to modify memory or restart the process.

Advertisement. Scroll to continue reading.

Two high-severity vulnerabilities addressed in NGINX Ingress Controller could allow authenticated attackers to inject arbitrary NGINX configuration directives to delete files and disable services, or create or modify Ingress or TransportServer resources to cause a denial-of-service (DoS) condition.

F5 also resolved a high-severity security defect in BIG-IP that could be exploited by remote, unauthenticated attackers to increase memory resource utilization when an HTTP/2 profile is configured on a virtual server, causing a DoS condition.

F5 makes no mention of any of these vulnerabilities being exploited in the wild. Additional information can be found in the company’s out-of-band security notification.

Related: Trend Micro, Tanium, ESET, and Tenable Patch Severe Product Vulnerabilities

Related: Vulnerabilities Patched by Fortinet, Ivanti, ServiceNow

Related: ICS Patch Tuesday: Vulnerabilities Fixed by Siemens, Schneider, Rockwell

Related: Critical Vulnerabilities Patched With Fresh Chrome 150, Firefox 152 Updates

https://www.securityweek.com/f5-patches-multiple-nginx-big-ip-vulnerabilities/


Nightmare Eclipse Drops ‘LegacyHive’ Windows Zero-Day 

Nightmare Eclipse, the disgruntled security researcher who has been dropping zero-day exploits targeting Microsoft products, released another unpatched Windows vulnerability this week, right on the July 2026 Patch Tuesday.

The fresh exploit, named LegacyHive, is a local privilege escalation bug in the Windows User Profile Service that allows an attacker to load other users’ hives, including those of administrators.

Also known as Chaotic Eclipse, Nightmare Eclipse released proof-of-concept (PoC) exploit code that works on systems running Microsoft’s July 2026 patches.

“The PoC requires another standard user credentials and a third username (which can be an administrator account), if the PoC is successful, it will end up mounting the target user hive in current user classes root,” the researcher explains.

Unlike previously dropped zero-day exploits from Nightmare Eclipse, LegacyHive was released with a stripped PoC to prevent the security defect’s in-the-wild exploitation.

According to the researcher, the exploit originally did not require user credentials and allowed any hive to be loaded, not just the usrclass.dat hive. That is still possible, the researcher says, but would require some work.

Advertisement. Scroll to continue reading.

To date, Nightmare Eclipse released over half a dozen zero-days in Microsoft products, including BlueHammer, RedSun, and UnDefend, which have been exploited in attacks, along with GreenPlasma, RoguePlanet, YellowKey, and GreatXML.

Microsoft has yet to acknowledge the LegacyHive exploit. SecurityWeek has emailed the company for a statement and will update this article if it responds.

Related: Unpatched Cursor Vulnerability Exposes Users to Code Execution

Related: CISA Urges Immediate Patching of Exploited SharePoint Vulnerabilities

Related: Windows Bind Link Attacks Can Hide Malware From EDR Tools

Related: Progress Confirms Zero-Day Vulnerability Behind ShareFile Disruption

https://www.securityweek.com/nightmare-eclipse-drops-legacyhive-windows-zero-day/