New Side-Channel Vulnerability Leaks Sensitive Data From Intel Chips

A newly revealed side-channel attack can leak encrypted data from Intel microprocessors that use a Simultaneous Multithreading (SMT) architecture.

read more

http://feedproxy.google.com/~r/Securityweek/~3/0L9TlL_VPIM/portsmash-new-side-channel-vulnerability-leaks-sensitive-data-intel-chips-CVE-2018-5407


ICS Devices Vulnerable to Side-Channel Attacks: Researcher

Side-channel attacks can pose a serious threat to industrial control systems (ICS), a researcher warned last month at SecurityWeek’s ICS Cyber Security Conference in Atlanta, GA.

read more

http://feedproxy.google.com/~r/Securityweek/~3/7AOBSYBONhg/ics-devices-vulnerable-side-channel-attacks-researcher


Sauter Quickly Patches Flaw in Building Automation Software

A serious vulnerability that allows an attacker to steal files from an affected system has been found by a researcher in a building automation product from Swiss-based Fr. Sauter AG. It took the vendor only 10 days to release a patch.

read more

http://feedproxy.google.com/~r/Securityweek/~3/M0feWehs6Jo/sauter-quickly-patches-flaw-building-automation-software


Bluetooth bugs bite millions of Wi-Fi APs from Cisco, Meraki, and Aruba

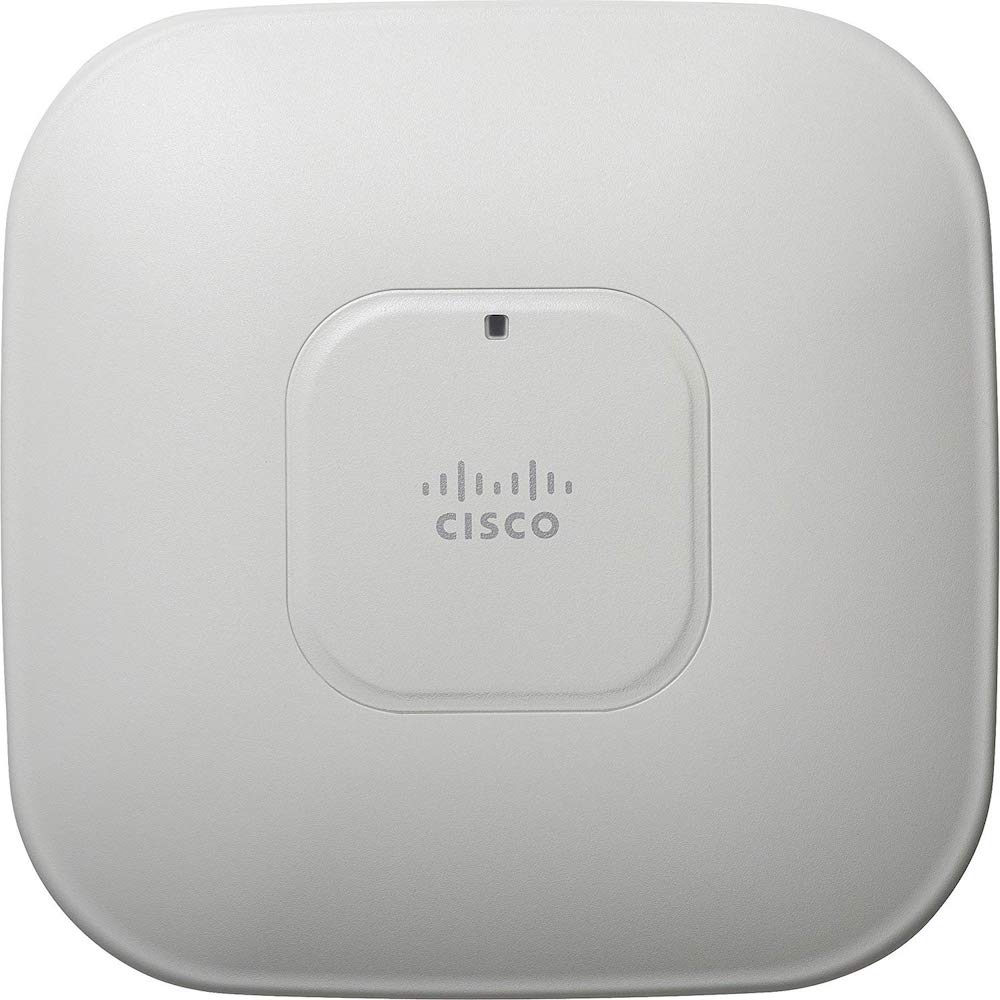
A Cisco Aironet access point.

Enlarge / A Cisco Aironet access point. (credit: Cisco)

Millions of Wi-Fi access points sold by Cisco, Meraki, and Aruba have two critical vulnerabilities being patched that could allow hackers to run malware inside the sensitive networks that use the gear. While the flaws open corporate networks to some scary attacks, the real-world likelihood of them being exploited is debatable.

In a report published Thursday, security firm Armis said two flaws it found in Bluetooth Low Energy chips manufactured by Texas Instruments can be used to hack the APs that embed them. The BLE chips offer a variety of enhancements to traditional Wi-Fi APs. Retailers, for instance, can use them to monitor customer movements inside stores by monitoring the Bluetooth beacons sent by the customers’ phones. Hospitals can use BLE to keep track of Bluetooth-enabled medical equipment. Cisco (which also makes Meraki gear) and Aruba have both issued patches that users of affected gear should install as soon as possible.

Unfortunately, hackers can also make use of the vulnerable BLE chips to take control of the APs. Attackers armed with small Bluetooth-enabled devices need only two minutes to transmit exploits that install malicious firmware on the vulnerable chips. From there, the malware could install AP firmware that monitors communications, infects end users, or spreads to other parts of a corporate network.

Read 22 remaining paragraphs | Comments

https://arstechnica.com/?p=1405131


Bluetooth Chip Flaws Expose Enterprises to Remote Attacks

Millions of access points and other networking devices used by enterprises around the world may be exposed to remote attacks due to a couple of vulnerabilities discovered by researchers in Bluetooth Low Energy (BLE) chips made by Texas Instruments.

read more

http://feedproxy.google.com/~r/Securityweek/~3/UjjPTNLNQ7o/bluetooth-chip-flaws-expose-enterprises-remote-attacks


Cisco Warns of Zero-Day Vulnerability in Security Appliances

Cisco informed customers on Wednesday that some of its security appliances are affected by a serious vulnerability that has been actively exploited.

read more

http://feedproxy.google.com/~r/Securityweek/~3/LLS7qR23mR0/cisco-warns-zero-day-vulnerability-security-appliances


iOS Lockscreen Bypass Abuses New Group FaceTime Feature

Just hours after Apple announced the availability of a new FaceTime feature in iOS, iPhone enthusiast Jose Rodriguez, known for his YouTube channel videosdebarraquito, found a way to bypass a device’s lockscreen by abusing the newly introduced functionality.

read more

http://feedproxy.google.com/~r/Securityweek/~3/36lLwPDy8Ig/ios-lockscreen-bypass-abuses-new-group-facetime-feature


Apple Patches Passcode Bypass, FaceTime Flaws in iOS

Security updates released by Apple on Tuesday for its macOS, iOS, tvOS, watchOS, Safari, iCloud and iTunes products address tens of new vulnerabilities.

read more

http://feedproxy.google.com/~r/Securityweek/~3/Jj5v1YkNChg/apple-patches-passcode-bypass-facetime-flaws-ios


Internet-Exposed HMIs Put Energy, Water Facilities at Risk: Report

Malicious actors could cause serious damage to organizations in the energy and water sectors by targeting their human-machine interfaces (HMIs), according to a report released by Trend Micro on Tuesday.

read more

http://feedproxy.google.com/~r/Securityweek/~3/TfzJm2iPo3Y/internet-exposed-hmis-put-energy-water-facilities-risk-report


92% of External Web Apps Have Exploitable Security Flaws or Weaknesses: Report

According to new research, 98% of leading companies across the U.S. and Europe are vulnerable to cybercriminals through their web applications. While this figure may seem high, it will surprise neither the companies themselves nor independent security experts.

read more

http://feedproxy.google.com/~r/Securityweek/~3/5Xm6tytDmLg/92-external-web-apps-have-exploitable-security-flaws-or-weaknesses-report