Stymied by browsers, attackers embed Flash 0-day inside MS Office document

Enlarge (credit: Qihoo 360)

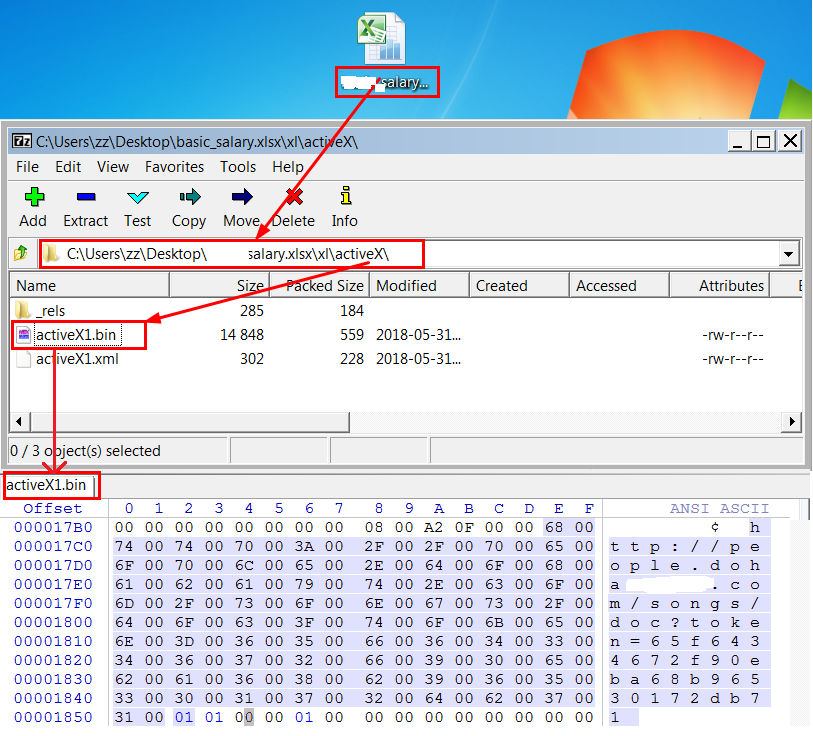
As browser makers make it increasingly hard to exploit vulnerabilities in Adobe Flash and other plugins, hackers targeting diplomats in the Middle East tried a new approach this month: using Microsoft Office to remotely load Flash content that used a potent zero-day flaw to take control of computers.

On Thursday, Adobe published a patch for the critical vulnerability, indexed as CVE-2018-5002. The stack-based buffer overflow was being triggered in an Office document that embedded a link to a Flash file stored on people.dohabayt.com. Once executed, the malicious file then downloaded a malicious payload from the same domain. That’s according to researchers from security firms Icebrg and Qihoo 360, which independently discovered the attacks and privately reported them to Adobe and wrote about it here and here.

Over the past few years, browser makers have begun to block Flash content by default, a change that has gone a long way to preventing drive-by attacks that exploit critical vulnerabilities in Adobe’s widely used media player. By contrast, at least some versions of Microsoft Office still download Flash with little or no user interaction, Icebrg CEO William Peteroy told Ars. To prevent downloads, users should ensure their installations prevent Flash from loading at all or at least don’t load Flash without explicit permission.

Read 7 remaining paragraphs | Comments

https://arstechnica.com/?p=1322989


Serious Flaws Found in Philips Patient Monitoring Devices

Researchers have discovered serious vulnerabilities in patient monitoring devices from Philips. The vendor has shared some recommendations for mitigating the risks until patches are made available.

read more

http://feedproxy.google.com/~r/Securityweek/~3/u3KSTRx8-6o/serious-flaws-found-philips-patient-monitoring-devices


Adobe Patches Flash Zero-Day Exploited in Targeted Attacks

[Updated] Security updates released by Adobe on Thursday for Flash Player patch four vulnerabilities, including a critical flaw that has been exploited in targeted attacks.

read more

http://feedproxy.google.com/~r/Securityweek/~3/cP1EmGTExnE/adobe-patches-flash-zero-day-exploited-targeted-attacks-1

Three months later, a mass exploit of powerful Web servers continues

Enlarge (credit: Malwarebytes)

More than 115,000 websites—many run by major universities, government organizations, and media companies—remained wide open to hacker takeovers because they hadn’t installed critical patches released 10 weeks ago, security researcher Troy Mursch said Monday. A separate researcher reported on Tuesday that many of the sites were already compromised and were being used to surreptitiously mine cryptocurrencies or push malware on unsuspecting visitors.

Infected pages included those belonging to the University of Southern California, Computer World’s Brazil site, and the Arkansas Judiciary’s Courts and Community Initiative, which were causing visitors’ computers to run resource-intensive code that mines cryptocurrency, Jérôme Segura, lead malware intelligence analyst at antivirus provider Malwarebytes, told Ars.

Segura said a Harvard University page that earlier was also infected with mining malware had since been defaced, presumably by a different party. Meanwhile, a Western Michigan University page that earlier was infected with code that pushed a malicious browser extension was later repaired. Segura reported his findings Tuesday and has indexed more than 900 infected sites here.

Read 4 remaining paragraphs | Comments

https://arstechnica.com/?p=1322425


Mirai Variants Continue to Spawn in Vulnerable IoT Ecosystem

Mirai is the archetypal IoT botnet, first achieving infamy with a 665 Gbps DDoS attack against the KrebsOnSecurity website in September 2016. Within days, a second Mirai attack targeted the French hosting firm, OVH, with an attack that peaked at nearly 1 Tbps.

read more

http://feedproxy.google.com/~r/Securityweek/~3/qzcdlaQmuec/mirai-variants-continue-spawn-vulnerable-iot-ecosystem


Flaw in F-Secure Products Allowed Code Execution via Malicious Archives

A critical vulnerability affecting many consumer and corporate products from F-Secure could have been exploited for remote code execution using specially crafted archive files.

read more

http://feedproxy.google.com/~r/Securityweek/~3/JBIZS4Ed2Sk/flaw-f-secure-products-allowed-code-execution-malicious-archives


Many Drupal Sites Still Vulnerable to Drupalgeddon2 Attacks

At least 115,000 websites powered by version 7 of the Drupal content management system are still vulnerable to Drupalgeddon2 attacks, despite patches being available since late March.

read more

http://feedproxy.google.com/~r/Securityweek/~3/PSj38Vgjmz8/many-drupal-sites-still-vulnerable-drupalgeddon2-attacks


Apple Patches Dozens of Flaws in macOS, iOS, Safari

Apple has released a set of updates to address dozens of vulnerabilities in products including macOS, iOS, Safari, tvOS, watchOS, and iTunes and iCloud applications for Windows.

read more

http://feedproxy.google.com/~r/Securityweek/~3/QAckkESxMWg/apple-patches-dozens-flaws-macos-ios-safari


Tens of Vulnerabilities Found in Quest Appliances

Researchers at Core Security say they have discovered a total of more than 60 vulnerabilities in disk backup and system management appliances from Quest. The IT management firm has released patches, but threatened to take legal action against Core if it disclosed too many details.

read more

http://feedproxy.google.com/~r/Securityweek/~3/dI7-CPNinhE/tens-vulnerabilities-found-quest-appliances


WordPress Disables Plugins That Expose e-Commerce Sites to Attacks

Researchers discovered vulnerabilities in ten WordPress plugins made by a company for e-commerce websites powered by the WooCommerce platform. WordPress disabled many of them after the developer failed to release patches.

read more

http://feedproxy.google.com/~r/Securityweek/~3/S7g13A7qDGw/wordpress-disables-plugins-expose-e-commerce-sites-attacks