Unofficial Patch Released for Zero-Days Affecting Dasan Routers

An unofficial patch has been released for the zero-day vulnerabilities affecting a large number of routers made by South Korea-based Dasan Networks.

read more

http://feedproxy.google.com/~r/Securityweek/~3/0CJZiyB86oQ/unofficial-patch-released-zero-days-affecting-dasan-routers


Unpatched Flaws Expose Lantech Industrial Device Servers to Attacks

Two critical vulnerabilities have been discovered by a researcher in industrial device servers from Taiwan-based industrial networking solutions provider Lantech. The flaws can be exploited remotely even by an attacker with a low skill level, but the vendor has not released any patches.

read more

http://feedproxy.google.com/~r/Securityweek/~3/MOO0k-umqWI/unpatched-flaws-expose-lantech-industrial-device-servers-attacks


Logitech Patches Several Flaws in Harmony Hub

FireEye researchers have discovered several vulnerabilities in the Logitech Harmony Hub home control system. The vendor has released a firmware update that patches the flaws.

read more

http://feedproxy.google.com/~r/Securityweek/~3/fyWeu8yQfDU/logitech-patches-several-flaws-harmony-hub


Hackers Target Flaws Affecting a Million Internet-Exposed Routers

Just a few days after they were disclosed, malicious actors started targeting a couple of flaws affecting routers made by South Korea-based Dasan Networks. There are roughly one million potentially vulnerable devices accessible directly from the Internet.

vpnMentor on Monday disclosed the details of two vulnerabilities in Gigabit-capable Passive Optical Network (GPON) routers made by Dasan and distributed to users by ISPs that provide fiber-optic Internet.

One of the flaws (CVE-2018-10561) allows a remote attacker to bypass a router’s authentication mechanism simply by appending the string “?images/” to a URL in the device’s web interface. The second vulnerability (CVE-2018-10562) can be exploited by an authenticated attacker to inject arbitrary commands.

Researchers warned that cybercriminals could combine the two security holes to remotely take control of vulnerable devices and possibly the victim’s entire network.

A Shodan search shows that there are roughly one million GPON home routers exposed to the Internet, a majority located in Mexico, Kazakhstan, and Vietnam.

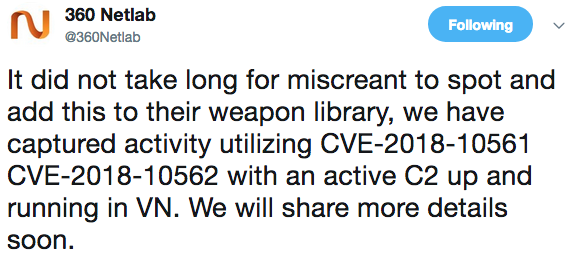
The Network Security Research Lab at Chinese security firm Qihoo 360 reported on Thursday that it had already started seeing attempts to exploit CVE-2018-10561 and CVE-2018-10562. The company has promised to provide more details soon.

Hackers target Dasan router vulnerabilities

The fact that cybercriminals have started exploiting these vulnerabilities is not surprising considering that devices made by Dasan have been known to be targeted by botnets.

Researchers revealed in February that the Satori botnet had ensnared thousands of Dasan routers by exploiting a remote code execution vulnerability disclosed in December 2017 by Beyond Security, which claimed the vendor had ignored repeated attempts to report the issue.

vpnMentor said its attempts to report CVE-2018-10561 and CVE-2018-10562 to Dasan were also unsuccessful before its disclosure, but a representative of the manufacturer did reach out to the company after details of the security holes were made public.

Related: Remotely Exploitable Vulnerability Discovered in MikroTik’s RouterOS

Related: Flaws Affecting Top-Selling Netgear Routers Disclosed

view counter

Eduard Kovacs (@EduardKovacs) is a contributing editor at SecurityWeek. He worked as a high school IT teacher for two years before starting a career in journalism as Softpedia’s security news reporter. Eduard holds a bachelor’s degree in industrial informatics and a master’s degree in computer techniques applied in electrical engineering.

Previous Columns by Eduard Kovacs:

Tags:

http://feedproxy.google.com/~r/Securityweek/~3/IM5TGlBYSCM/hackers-target-flaws-affecting-million-internet-exposed-routers


Intel Working on Patches for 8 New Spectre-Like Flaws: Report

Researchers have discovered a total of eight new Spectre-like vulnerabilities, including flaws that may be more serious and easier to exploit, according to German magazine c’t.

The flaws were reportedly identified by several research teams, including Google Project Zero, whose employees were among those who initially discovered the Meltdown and Spectre attack methods. C’t, which is owned by Heise, claims it has obtained the information exclusively and confirms the existence of the vulnerabilities and their severity.

The new vulnerabilities, dubbed “Spectre Next Generation” or “Spectre-NG,” are said to affect processors from Intel and at least some ARM chips. AMD processors are currently being analyzed to determine if they are impacted as well.

Intel has confirmed that it’s working on patching some vulnerabilities, but it has not provided any details. C’t reports that Intel will release updates in two waves – the first expected in May and the second in August.

There are currently two main versions of the Spectre vulnerability: variant 1 and variant 2. Variant 1 attacks can be mitigated using software updates, but variant 2 requires microcode updates as well. C’t says Microsoft is also working on mitigations, which indicates that the Spectre-NG flaws require both software and firmware updates.

Of the eight Spectre-NG flaws, four have been classified as high severity and four as medium severity, with CVE identifiers being prepared for each issue.

While the risk and attack scenarios are similar to the original Spectre, c’t says there is one exception. One of the flaws can be exploited to execute arbitrary code in virtual machines and compromise the host system, and the attack is relatively easy to conduct, especially compared to the original Spectre. Cloud service providers such as Cloudflare and Amazon are reportedly affected the most.

On the other hand, c’t reports that the Spectre-NG flaws are unlikely to be exploited at scale against personal and corporate computers.

“Assuming they prove to be legitimate, the group of vulnerabilities coined as ‘Spectre-NG’ may pose significantly higher risks to cloud operators and multi-tenant environments than the original variants of Spectre. The information provided to the German technology site Heise seems to imply that a few of the eight new vulnerabilities facilitate VM-escape mechanisms, allowing a threat actor to compromise the hypervisor and/or other tenants from their own VM, apparently with little-to-no effort,” Craig Dods, Chief Security Architect at Juniper Networks, told SecurityWeek.

“As a point of reference, Spectre v1/v2 were quite difficult to use for the purposes of VM-escape within cloud environments. The details that are available for ‘Spectre-NG’ hint that it’s incredibly easy to use, but we won’t know for sure until we can see what the actual problems are,” Dods added.

Satya Gupta, CTO and co-founder of Virsec, is not surprised that new variants of the Spectre attack have emerged.

“Now that the core vulnerabilities of speculative execution have been publicized, many well-funded hacking groups globally are racing to find new ways to exploit them. These are advanced attacks exploiting small, but repeatable flaws that skip important security controls in literally billions of processors,” Gupta said via email. “While not all applications will be vulnerable and some compensating controls will be effective, the attackers are relentless and will continuously search for cracks in other defenses that allow Spectre to be exploited.”

Several other side-channel attack methods have been identified since the disclosure of Spectre and Meltdown, including ones dubbed BranchScope, SgxPectre, and MeltdownPrime and SpectrePrime.

view counter

Eduard Kovacs (@EduardKovacs) is a contributing editor at SecurityWeek. He worked as a high school IT teacher for two years before starting a career in journalism as Softpedia’s security news reporter. Eduard holds a bachelor’s degree in industrial informatics and a master’s degree in computer techniques applied in electrical engineering.

Previous Columns by Eduard Kovacs:

Tags:

http://feedproxy.google.com/~r/Securityweek/~3/qMdTQVP8tfI/intel-working-patches-8-new-spectre-flaws-report


Microsoft Makes Hyper-V Debugging Symbols Public

Microsoft Logo

In an attempt to improve Hyper-V technology, which Microsoft considers central to the security of its cloud services, the software giant has released Hyper-V debugging symbols to the public.

Microsoft is now offering access to most Hyper-V-related symbols through the public symbol servers, starting with symbols for Windows Server 2016 with an installed April 2018 cumulative update.

“We would like to share with the security community that we have now released debugging symbols for many of the core components in Hyper-V, with some exceptions such as the hypervisor where we would like to avoid our customers taking a dependency on undocumented hypercalls for instance,” Microsoft announced.

This move, the company says, should prove handy for partners building solutions leveraging Hyper-V, for developers attempting to debug specific issues, and to security researchers to better analyze Hyper-V’s implementation and report any vulnerabilities as part of the Microsoft Hyper-V Bounty Program.

Microsoft is offering consistent rewards for vulnerabilities discovered in the Hyper-V client running on Windows 10 (latest builds of Windows Insider Preview slow) and Windows Server 2016 (latest available version).

The highest payouts reach $250,000 for eligible Critical Remote Code Execution bugs in Hypervisor and Host Kernel. Microsoft is also willing to pay up to $20,000 for issues discovered in Remotefx, Legacy Network Adapter (Generation 1) and Fibre Channel Adapter.

At this year’s Pwn2Own hacking competition, Microsoft was willing to pay up to $150,000 for vulnerabilities in the Hyper-V client, the highest rewards offered at the event.

Developers and security researchers interested in learning more on Microsoft’s Hyper-V Bounty Program should head to this TechNet article.

The list of components that now have debugging symbols made public was published by the Microsoft Virtualization team in a blog post last week.

The set is likely to be updated as the company decides to make more symbols public: “With newer releases, we are evaluating whether we can make even more symbols available,” Microsoft’s Lars Iwer notes.

A limited set of virtualization-related symbols that haven’t been released as of now includes storvsp.pdb, vhdparser.pdb, passthroughparser.pdb, hvax64.pdb, hvix64.pdb, and hvloader.pdb.

Related: Microsoft Launches Windows Bug Bounty Program

Related: Hackers Awarded $267,000 at Pwn2Own 2018

view counter

Ionut Arghire is an international correspondent for SecurityWeek.

Previous Columns by Ionut Arghire:

Tags:

http://feedproxy.google.com/~r/Securityweek/~3/KmgEkmKGUsk/microsoft-makes-hyper-v-debugging-symbols-public


Meltdown Patch in Windows 10 Can Be Bypassed

A researcher has discovered that a mitigation implemented by Microsoft in Windows 10 for the Meltdown vulnerability can be bypassed. The tech giant says it’s working on an update.

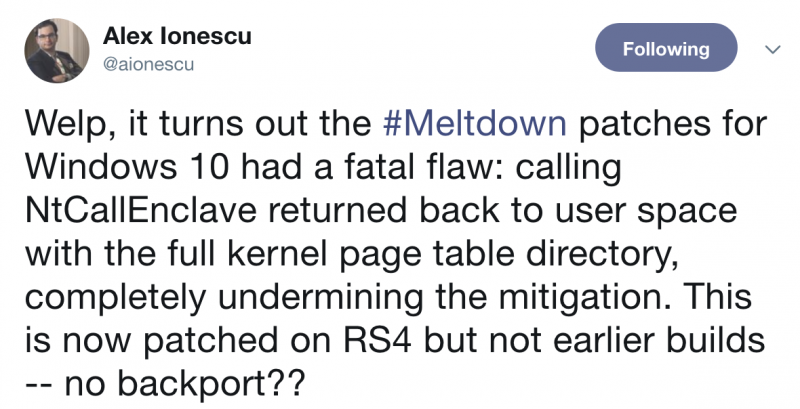
According to Windows internals expert Alex Ionescu, a Meltdown mitigation in Windows 10 has what he describes as “a fatal flaw.”

“Calling NtCallEnclave returned back to user space with the full kernel page table directory, completely undermining the mitigation,” Ionescu wrote on Twitter.

Meltdown mitigation in Windows 10 bypassed

The researcher said Microsoft included a patch for this issue in the recently released Windows 10 version 1803, also known as April 2018 Update, Redstone 4 and RS4.

Microsoft told SecurityWeek that the company is working on providing an update for Windows 10 version 1790, also known as the Fall Creators Update, which appears to be the only version affected.

While the Meltdown mitigation bypass is interesting from a research perspective, exploitation requires local code execution privileges and the risk of malicious attacks is low.

The patches released by Microsoft for the Meltdown vulnerability have caused problems from day one. Shortly after the Meltdown and Spectre flaws were disclosed in early January, users started complaining that Microsoft’s updates had been causing Windows to break down on computers with AMD processors.

More recently, a researcher discovered that Meltdown mitigations for Windows 7 and Windows Server 2008 R2 introduced a serious privilege escalation vulnerability that may be worse than Meltdown.

Related: Microsoft Releases More Patches for Meltdown, Spectre

Related: Microsoft Releases More Microcode Patches for Spectre Flaw

Related: Windows Updates Deliver Intel’s Spectre Microcode Patches

view counter

Eduard Kovacs (@EduardKovacs) is a contributing editor at SecurityWeek. He worked as a high school IT teacher for two years before starting a career in journalism as Softpedia’s security news reporter. Eduard holds a bachelor’s degree in industrial informatics and a master’s degree in computer techniques applied in electrical engineering.

Previous Columns by Eduard Kovacs:

Tags:

http://feedproxy.google.com/~r/Securityweek/~3/MncoKzGJFLM/meltdown-patch-windows-10-can-be-bypassed


Android Phones Vulnerable to Remote Rowhammer Attack via GPU

A team of researchers has shown how malicious actors could leverage graphics processing units (GPUs) to launch Rowhammer attacks remotely against Android smartphones.

read more

http://feedproxy.google.com/~r/Securityweek/~3/M4XUVWO8Jsc/android-phones-vulnerable-remote-rowhammer-attack-gpu


Industrial Networks Easy to Hack From Corporate Systems: Study

Hackers could in many organizations easily gain access to industrial environments from the corporate network, according to an analysis conducted by Positive Technologies.

read more

http://feedproxy.google.com/~r/Securityweek/~3/YbMFiy3Yu4k/industrial-networks-easy-hack-corporate-systems-study


Industry CMO on the Downstream Risks of “Logo Disclosures”

Cybersecurity Marketing Teams Would Benefit From an Ethics Desk

Jennifer Leggio, chief marketing officer at Flashpoint, is an executive with more than a decade’s experience in managing corporate cyber security marketing at the highest levels — much of the time seeking and advocating a greater ethical stance in marketing. At last month’s Hack in the Box Conference in Amsterdam, she delivered a keynote presentation entitled, ‘A Risk Assessment of Logo Disclosures’.

The basic premise is that failures in the coordinated approach to vulnerability disclosures can seem attractive from an initial marketing perspective, but are damaging to both the industry and its users. The ultimate problem comes from the different missions between security product development and sales teams: the first is purposed to reduce harm, while the latter is purposed to sell product.

In between these teams sit the researchers, whose function is to find weaknesses in security products so that they can be strengthened, and their users better protected. Researchers wish to have their expertise acknowledged, while developers wish to fix their products securely. Between them they have evolved the process known as coordinated disclosure: researchers report their findings to the developer who fixes the faults, and both coordinate simultaneous disclosure of the vulnerability and its fix.

Logos for VulnerabilitiesIt’s a process — when it works — that ensures the developer fixes the product as rapidly as possible, while the vulnerability does not become a zero-day exploit for use by cybercriminals, overseen by a CERT ‘referee’. The problem comes from undue pressure from marketers, possibly supported by the firm’s business leaders. This is the subject of Leggio’s keynote presentation: the violation of disclosure process to try to diminish competitors, sell more product, or unethically highlight research prowess.

It’s a complex issue because it cuts both ways. Research firms, probably at the behest of marketing, can disclose vulnerabilities ahead of coordination to maximize the publicity of their discovery (and therefore, their visible expertise). Similarly, developers can usurp the agreed coordination date to get fixes out before there is any indication that there was a vulnerability, thereby minimizing any perceived product weakness and negative criticism.

Both have possibly happened in recent months. On March 13, a virtually unknown Israeli firm announced the existence of 13 flaws in AMD chips, after giving AMD just 24 hours to fix them. “It very much felt like a marketing stunt,” Leggio told SecurityWeek.

Two days later, Trail of Bits blogged that they had earlier been retained by CTS to confirm the existence of the AMD flaws — which they did — but commented, “Our recommendation to CTS was to disclose the vulnerabilities through a CERT.” CTS did not follow this advice. This allowed the controversial company Viceroy Research to publish a statement on the same day as CTS disclosed the vulnerabilities:

“These findings demonstrate that AMD’s key products, and it basis for profitability and growth, the EPYC and Ryzen processors, contain severe and pervasive security flaws that put users and organizations at an unacceptable and damaging risk.”

This statement bears all the hallmarks of an attempt to short AMD stock. In January, Moneyweb had described Viceroy Research as a “three-man firm… headed by a previous social worker and two Australian youngsters.” It concluded, “there are doubts as to whether Viceroy conducts its own research or if it is merely a front for other investors that seek to avoid the limelight but profit from it.”

It is possible, then, that unknown investors immediately attempted to profit from the uncoordinated disclosure — a perfect example of the downstream risks highlighted by Leggio.

But it’s not just the researchers that sometimes break the process. Also in March 2018, Core Security released details of a vulnerability in router manufacturer MikroTik’s RouterOS. Core and MikroTik agreed on coordinated disclosure, but just before the agreed date, MikroTik quietly fixed the flaw in an OS update. Whether by design or accident, this allowed the manufacturer to avoid making any disclosure or public recognition of the pre-existing vulnerability. 

The risk here is to the end user. Without ever hearing about potential problems, the user can easily assume that there are no problems. It’s a false sense of security that is patently dangerous since compromised MikroTik routers are an important part of IoT botnets. According to one firm, compromised MikroTik routers comprised 80% of a botnet (probably Reaper) that was used in a DDoS attack against Dutch financials in January 2018.

It is such downstream risks of upfront marketing-led breaches of the coordinated disclosure process that Leggio discussed in her keynote presentation. Key to her proposal is the introduction of an ethics or ‘standards desk’ overseeing marketing decisions just as some newspapers have a standards desk overseeing the more contentious news stories. 

Marketing teams pushing for external disclosure, she told SecurityWeek, “should have it go through an ethical evaluation to ensure that it’s not compromising any bigger picture — like an LEA investigation — and/or is not tipping-off a cybercriminal that there might be an exploit in their malware that could help law enforcement. You’re basically using coordinated disclosure to help cyber criminals harden their own stuff — needs to be some review there.”

It requires, she added, “a shift in culture and a shift in mindset, making sure that business leaders understand that their sales teams, their marketing teams, their finance teams, their legal teams and so on, are all responsible for making sure that there is an ethical delivery in the message.”

Leggio’s talk is available in the video below:

view counter

Kevin Townsend is a Senior Contributor at SecurityWeek. He has been writing about high tech issues since before the birth of Microsoft. For the last 15 years he has specialized in information security; and has had many thousands of articles published in dozens of different magazines – from The Times and the Financial Times to current and long-gone computer magazines.

Previous Columns by Kevin Townsend:

Tags:

http://feedproxy.google.com/~r/Securityweek/~3/AAp29N_Q1uQ/industry-cmo-downstream-risks-logo-disclosures