Cisco on Wednesday released patches for three vulnerabilities in IOS XR software, as part of its September 2025 security advisory bundled publication.
Tracked as CVE-2025-20248 (CVSS score of 6), the first of the bugs is a high-severity issue in the IOS XR installation process that could allow attackers to bypass image signature verification.
Successful exploitation of the flaw, Cisco explains, could lead to unsigned files being added to an ISO image, which could then be installed and activated on a device.
Because of the potential bypass of the image verification process, Cisco has raised the security impact rating of the advisory from medium to high.
The second IOS XR issue resolved this week is CVE-2025-20340 (CVSS score of 7.4), a bug in the software’s Address Resolution Protocol (ARP) implementation that could be exploited by adjacent, unauthenticated attackers to cause a denial-of-service (DoS) condition.
“This vulnerability is due to how Cisco IOS XR Software processes a high, sustained rate of ARP traffic hitting the management interface. Under certain conditions, an attacker could exploit this vulnerability by sending an excessive amount of traffic to the management interface of an affected device, overwhelming its ARP processing capabilities,” Cisco explains.
The third security defect is a medium-severity issue in IOS XR’s ACL processing feature that could allow unauthenticated, remote attackers to send traffic to a vulnerable device and bypass configured ACLs for the SSH, NetConf, and gRPC features.
Tracked as CVE-2025-20159 (CVSS score of 5.3), the flaw exists because IOS XR packet I/O infrastructure platforms for SSH, NetConf, and gRPC have not supported management interface ACLs.
Advertisement. Scroll to continue reading.
Cisco says it is not aware of any of these vulnerabilities being exploited in the wild. Users are advised to apply the available patches as soon as possible, as hackers are known to have exploited Cisco bugs.
High-severity vulnerability in Passwordstate credential manager. Patch now.
The maker of Passwordstate, an enterprise-grade password manager for storing companies’ most privileged credentials, is urging them to promptly install an update fixing a high-severity vulnerability that hackers can exploit to gain administrative access to their vaults.
The authentication bypass allows hackers to create a URL that accesses an emergency access page for Passwordstate. From there, an attacker could pivot to the administrative section of the password manager. A CVE identifier isn’t yet available.
Safeguarding enterprises’ most privileged credentials
Click Studios, the Australia-based maker of Passwordstate, says the credential manager is used by 29,000 customers and 370,000 security professionals. The product is designed to safeguard organizations’ most privileged and sensitive credentials. Among other things, it integrates into Active Directory, the service Windows network admins use to create, change, and modify user accounts. It can also be used for handling password resets, event auditing, and remote session logins.
On Thursday, Click Studios notified customers that it had released an update that patches two vulnerabilities.
The authentication bypass vulnerability is “associated with accessing the core Passwordstate Products’ Emergency Access page, by using a carefully crafted URL, which could allow access to the Passwordstate Administration section,” Click Studios said. The company said the severity level of the vulnerability was high.
What to know about ToolShell, the SharePoint threat under mass exploitation
Microsoft fixed the vulnerability pair—CVE-2025-49706 and CVE-2025-49704—two weeks ago as part of the company’s monthly update release. As the world learned over the weekend, the patches were incomplete, a lapse that opened organizations around the world to the new attacks.
Q: What sorts of malicious things are attackers doing with these newer ToolShell exploits?
A: According to numerous technical analyses, the attackers first infect vulnerable systems with a webshell-based backdoor that gains access to some of the most sensitive parts of a SharePoint Server. From there, the webshell extracts tokens and other credentials that allow the attackers to gain administrative privileges, even when systems are protected by multifactor authentication and single sign-on. Once inside, the attackers exfiltrate sensitive data and deploy additional backdoors that provide persistent access for future use.
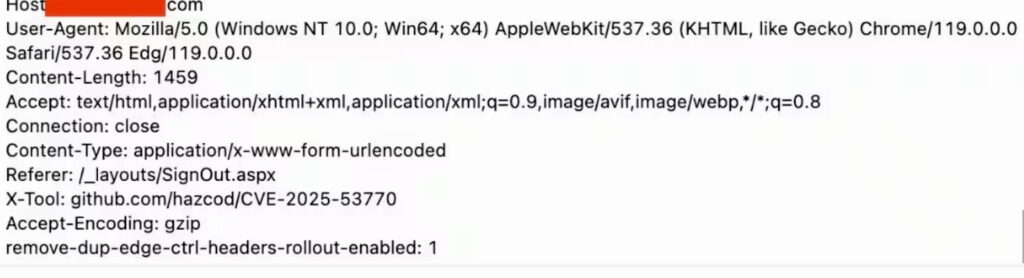
For those who want more technical details, the opening volley in the attack is POST Web requests the attackers send to the ToolPane endpoint. The requests look like this:
Credit: Akamai
Microsoft said these requests upload a malicious script named spinstall0.aspx, or alternatively spinstall.aspx, spinstall1.aspx, spinstall2.aspx, and so on. The script contains commands for retrieving a SharePoint server’s encrypted MachineKey configuration and returning the decrypted results to the attacker through a GET request.
Q: I maintain an on-premises SharePoint server. What should I do?
A: In short, drop whatever else you were doing and take time to carefully inspect your system. The first thing to look for is whether it has received the emergency patches Microsoft released Saturday. Install the patch immediately if it hasn’t already been done.
Patching the vulnerability is only the first step, since systems infected through the vulnerability show few or no signs of compromise. The next step is to pore through system event logs in search of indicators of compromise. These indicators can be found in numerous write-ups, including those from Microsoft and Eye Security (at the links above), the US Cybersecurity and Information Security Agency, and security firms Sentinel One, Akamai, Tenable, and Palo Alto Networks.
Google finds custom backdoor being installed on SonicWall network devices
Researchers from the Google Threat Intelligence Group said that hackers are compromising SonicWall Secure Mobile Access (SMA) appliances, which sit at the edge of enterprise networks and manage and secure access by mobile devices.
The targeted devices are end of life, meaning they no longer receive regular updates for stability and security. Despite the status, many organizations continue to rely on them. That has left them prime targets by UNC6148, the name Google has given to the unknown hacking group.
“GTIG recommends that all organizations with SMA appliances perform analysis to determine if they have been compromised,” a report published Wednesday said, using the abbreviation for Google Threat Intelligence Group. “Organizations should acquire disk images for forensic analysis to avoid interference from the rootkit anti-forensic capabilities. Organizations may need to engage with SonicWall to capture disk images from physical appliances.”
Lacking specifics
Many key details remain unknown. For one thing, the attacks are exploiting leaked local administrator credentials on the targeted devices, and so far, no one knows how the credentials were obtained. It’s also not known what vulnerabilities UNC6148 is exploiting. It’s also unclear precisely what the attackers are doing after they take control of a device.
The lack of details is largely the result of the functioning on Overstep, the name of custom backdoor malware UNC6148 is installing after initial compromise of the devices. Overstep allows the attackers to selectively remove log entries, a technique that is hindering forensic investigation. Wednesday’s report also posits that the attackers may be armed with a zero-day exploit, meaning it targets a vulnerability that’s currently publicly unknown. Possible vulnerabilities UNC6148 may be exploiting include:
CVE-2021-20038: An unauthenticated remote code execution made possible by a memory corruption vulnerability.
CVE-2024-38475: An unauthenticated path traversal vulnerability in Apache HTTP Server, which is present in the SMA 100. It can be exploited to extract two separate SQLite databases that store user account credentials, session tokens, and seed values for generating one-time passwords.
CVE-2021-20035: An authenticated remote code execution vulnerability. Security firm Arctic Wolf and SonicWall reported in April that this vulnerability was under active exploitation.
CVE-2021-20039: An authenticated remote code execution vulnerability. There have been reports that this vulnerability was under active exploitation to install ransomware in 2024.
CVE-2025-32819: An authenticated file deletion vulnerability that can be exploited to cause a targeted device to revert the built-in administrator credentials to a password so that attackers can gain administrator access.
Threat posed by new VMware hyperjacking vulnerabilities is hard to overstate
Three critical vulnerabilities in multiple virtual-machine products from VMware can give hackers unusually broad access to some of the most sensitive environments inside multiple customers’ networks, the company and outside researchers warned Tuesday.
The class of attack made possible by exploiting the vulnerabilities is known under several names, including hyperjacking, hypervisor attack, or virtual machine escape. Virtual machines often run inside hosting environments to prevent one customer from being able to access or control the resources of other customers. By breaking out of one customer’s isolated VM environment, a threat actor could take control of the hypervisor that apportions each VM. From there, the attacker could access the VMs of multiple customers, who often use these carefully controlled environments to host their internal networks.
All bets off
“If you can escape to the hypervisor you can access every system,” security researcher Kevin Beaumont said on Mastodon. “If you can escape to the hypervisor, all bets are off as a boundary is broken.” He added: “With this vuln you’d be able to use it to traverse VMware managed hosting providers, private clouds orgs have built on prem etc.”
VMware warned Tuesday that it has evidence suggesting the vulnerabilities are already under active exploitation in the wild. The company didn’t elaborate. Beaumont said the vulnerabilities affect “every supported (and unsupported)” version in VMware’s ESXi, Workstation, Fusion, Cloud Foundation, and Telco Cloud Platform product lines.
Critical WordPress plugin vulnerability under active exploit threatens thousands
Thousands of sites running WordPress remain unpatched against a critical security flaw in a widely used plugin that was being actively exploited in attacks that allow for unauthenticated execution of malicious code, security researchers said.
The vulnerability, tracked as CVE-2024-11972, is found in Hunk Companion, a plugin that runs on 10,000 sites that use the WordPress content management system. The vulnerability, which carries a severity rating of 9.8 out of a possible 10, was patched earlier this week. At the time this post went live on Ars, figures provided on the Hunk Companion page indicated that less than 12 percent of users had installed the patch, meaning nearly 9,000 sites could be next to be targeted.
Significant, multifaceted threat
“This vulnerability represents a significant and multifaceted threat, targeting sites that use both a ThemeHunk theme and the Hunk Companion plugin,” Daniel Rodriguez, a researcher with WordPress security firm WP Scan, wrote. “With over 10,000 active installations, this exposed thousands of websites to anonymous, unauthenticated attacks capable of severely compromising their integrity.”
Rodriquez said WP Scan discovered the vulnerability while analyzing the compromise of a customer’s site. The firm found that the initial vector was CVE-2024-11972. The exploit allowed the hackers behind the attack to cause vulnerable sites to automatically navigate to wordpress.org and download WP Query Console, a plugin that hasn’t been updated in years.
Thousands of Linux systems infected by stealthy malware since 2021
This Reddit comment posted to the CentOS subreddit is typical. An admin noticed that two servers were infected with a cryptocurrency hijacker with the names perfcc and perfctl. The admin wanted help investigating the cause.
“I only became aware of the malware because my monitoring setup alerted me to 100% CPU utilization,” the admin wrote in the April 2023 post. “However, the process would stop immediately when I logged in via SSH or console. As soon as I logged out, the malware would resume running within a few seconds or minutes.” The admin continued:
I have attempted to remove the malware by following the steps outlined in other forums, but to no avail. The malware always manages to restart once I log out. I have also searched the entire system for the string “perfcc” and found the files listed below. However, removing them did not resolve the issue. as it keep respawn on each time rebooted.
After exploiting a vulnerability or misconfiguration, the exploit code downloads the main payload from a server, which, in most cases, has been hacked by the attacker and converted into a channel for distributing the malware anonymously. An attack that targeted the researchers’ honeypot named the payload httpd. Once executed, the file copies itself from memory to a new location in the /temp directory, runs it, and then terminates the original process and deletes the downloaded binary.
Once moved to the /tmp directory, the file executes under a different name, which mimics the name of a known Linux process. The file hosted on the honeypot was named sh. From there, the file establishes a local command-and-control process and attempts to gain root system rights by exploiting CVE-2021-4043, a privilege-escalation vulnerability that was patched in 2021 in Gpac, a widely used open source multimedia framework.
Attackers exploit critical Zimbra vulnerability using cc’d email addresses
Attackers are actively exploiting a critical vulnerability in mail servers sold by Zimbra in an attempt to remotely execute malicious commands that install a backdoor, researchers warn.
The vulnerability, tracked as CVE-2024-45519, resides in the Zimbra email and collaboration server used by medium and large organizations. When an admin manually changes default settings to enable the postjournal service, attackers can execute commands by sending maliciously formed emails to an address hosted on the server. Zimbra recently patched the vulnerability. All Zimbra users should install it or, at a minimum, ensure that postjournal is disabled.
Easy, yes, but reliable?
On Tuesday, Security researcher Ivan Kwiatkowski first reported the in-the-wild attacks, which he described as “mass exploitation.” He said the malicious emails were sent by the IP address 79.124.49[.]86 and, when successful, attempted to run a file hosted there using the tool known as curl. Researchers from security firm Proofpoint took to social media later that day to confirm the report.
On Wednesday, security researchers provided additional details that suggested the damage from ongoing exploitation was likely to be contained. As already noted, they said, a default setting must be changed, likely lowering the number of servers that are vulnerable.
Security researcher Ron Bowes went on to report that the “payload doesn’t actually do anything—it downloads a file (to stdout) but doesn’t do anything with it.” He said that in the span of about an hour earlier Wednesday a honey pot server he operated to observe ongoing threats received roughly 500 requests. He also reported that the payload isn’t delivered through emails directly, but rather through a direct connection to the malicious server through SMTP, short for the Simple Mail Transfer Protocol.
“That’s all we’ve seen (so far), it doesn’t really seem like a serious attack,” Bowes wrote. “I’ll keep an eye on it, and see if they try anything else!”
In an email sent Wednesday afternoon, Proofpoint researcher Greg Lesnewich seemed to largely concur that the attacks weren’t likely to lead to mass infections that could install ransomware or espionage malware. The researcher provided the following details:
While the exploitation attempts we have observed were indiscriminate in targeting, we haven’t seen a large volume of exploitation attempts
Based on what we have researched and observed, exploitation of this vulnerability is very easy, but we do not have any information about how reliable the exploitation is
Exploitation has remained about the same since we first spotted it on Sept. 28th
There is a PoC available, and the exploit attempts appear opportunistic
Exploitation is geographically diverse and appears indiscriminate
The fact that the attacker is using the same server to send the exploit emails and host second-stage payloads indicates the actor does not have a distributed set of infrastructure to send exploit emails and handle infections after successful exploitation. We would expect the email server and payload servers to be different entities in a more mature operation.
Defenders protecting Zimbra appliances should look out for odd CC or To addresses that look malformed or contain suspicious strings, as well as logs from the Zimbra server indicating outbound connections to remote IP addresses.
Proofpoint has explained that some of the malicious emails used multiple email addresses that, when pasted into the CC field, attempted to install a webshell-based backdoor on vulnerable Zimbra servers. The full cc list was wrapped as a single string and encoded using the base64 algorithm. When combined and converted back into plaintext, they created a webshell at the path: /jetty/webapps/zimbraAdmin/public/jsp/zimbraConfig.jsp.
Systems used by courts and governments across the US riddled with vulnerabilities
Getty Images
Public records systems that courts and governments rely on to manage voter registrations and legal filings have been riddled with vulnerabilities that made it possible for attackers to falsify registration databases and add, delete, or modify official documents.
Over the past year, software developer turned security researcher Jason Parker has found and reported dozens of critical vulnerabilities in no fewer than 19 commercial platforms used by hundreds of courts, government agencies, and police departments across the country. Most of the vulnerabilities were critical.
One flaw he uncovered in the voter registration cancellation portal for the state of Georgia, for instance, allowed anyone visiting it to cancel the registration of any voter in that state when the visitor knew the name, birthdate, and county of residence of the voter. In another case, document management systems used in local courthouses across the country contained multiple flaws that allowed unauthorized people to access sensitive filings such as psychiatric evaluations that were under seal. And in one case, unauthorized people could assign themselves privileges that are supposed to be available only to clerks of the court and, from there, create, delete, or modify filings.
Failing at the most fundamental level
It’s hard to overstate the critical role these systems play in the administration of justice, voting rights, and other integral government functions. The number of vulnerabilities—mostly stemming from weak permission controls, poor validation of user inputs, and faulty authentication processes—demonstrate a lack of due care in ensuring the trustworthiness of the systems millions of citizens rely on every day.
“These platforms are supposed to ensure transparency and fairness, but are failing at the most fundamental level of cybersecurity,” Parker wrote recently in a post he penned in an attempt to raise awareness. “If a voter’s registration can be canceled with little effort and confidential legal filings can be accessed by unauthorized users, what does it mean for the integrity of these systems?”
The vulnerability in the Georgia voter registration database, for instance, lacked any form of automated way to reject cancellation requests that omitted required voter information. Instead of flagging such requests, the system processed it without even flagging it. Similarly, the Granicus GovQA platform hundreds of government agencies use to manage public records could be hacked to reset passwords and gain access to usernames and email addresses simply by slightly modifying the Web address showing in a browser window.
And a vulnerability in the Thomson Reuters’ C-Track eFiling system allowed attackers to elevate their user status to that of a court administrator. Exploitation required nothing more than manipulating certain fields during the registration process.
There is no indication that any of the vulnerabilities were actively exploited.
Word of the vulnerabilities comes four months after the discovery of a malicious backdoor surreptitiously planted in a component of the JAVS Suite 8, an application package that 10,000 courtrooms around the world use to record, play back, and manage audio and video from legal proceedings. A representative of the company said Monday that an investigation performed in cooperation with the Cybersecurity and Infrastructure Security Agency concluded that the malware was installed on only two computers and didn’t result in any information being compromised. The representative said the malware was available through a file a threat actor posted to the JAVS public marketing website.
Parker began examining the systems last year as a software developer purely on a voluntary basis. He has worked with the Electronic Frontier Foundation to contact the system vendors and other parties responsible for the platforms he has found vulnerable. To date, all the vulnerabilities he has reported have been fixed, in some cases only in the past month. More recently, Parker has taken a job as a security researcher focusing on such platforms.
“Fixing these issues requires more than just patching a few bugs,” Parker wrote. “It calls for a complete overhaul of how security is handled in court and public record systems. To prevent attackers from hijacking accounts or altering sensitive data, robust permission controls must be immediately implemented, and stricter validation of user inputs enforced. Regular security audits and penetration testing should be standard practice, not an afterthought, and following the principles of Secure by Design should be an integral part of any Software Development Lifecycle.”
The 19 affected platforms are:
Parker is urging vendors and customers alike to shore up the security of their systems by performing penetration testing and software audits and training employees, particularly those in IT departments. He also said that multifactor authentication should be universally available for all such systems.
“This series of disclosures is a wake-up call to all organizations that manage sensitive public data,” Parker wrote. “If they fail to act quickly, the consequences could be devastating—not just for the institutions themselves but for the individuals whose privacy they are sworn to protect. For now, the responsibility lies with the agencies and vendors behind these platforms to take immediate action, to shore up their defenses, and to restore trust in the systems that so many people depend on.”