Serious Flaws Affect Dell EMC, VMware Data Protection Products

Data protection products from both Dell EMC and VMware are impacted by three potentially serious vulnerabilities discovered by researchers at Digital Defense.

EMC told customers that its Avamar Server, NetWorker Virtual Edition and Integrated Data Protection Appliance products have a common component, the Avamar Installation Manager (AVI). This component is affected by vulnerabilities that can be combined to take complete control of a system.

The most serious of the flaws, CVE-2017-15548, allows a remote attacker to bypass authentication and gain root access to the system. The vulnerability is related to the fact that authentication is performed via a POST request that includes the username, password and a parameter named wsUrl.

“The wsURL parameter can be an arbitrary URL that the Avamar server will send an authentication SOAP request to, that includes the user provided username and password,” Digital Defense explained. “If the Avamar server receives a successful SOAP response, it will return a valid session ID. The attacker doesn’t require any specific knowledge about the targeted Avamar server to generate the successful SOAP response, a generic, validly formed SOAP response will work for multiple Avamar servers.”

The second vulnerability, CVE-2017-15549, allows an authenticated attacker with low privileges to upload malicious files to the server.

“The saveFileContents method of the UserInputService class takes a single string parameter and splits it on the ‘\r’ character,” researchers said. “The first half of the parameter is a path, including the filename, and the second half of the string is the data that should be written to that path. The web server is running with root privileges, so arbitrary files can be written to arbitrary locations.”

The third security hole, CVE-2017-15550, has been described as a path traversal issue that allows an authenticated attacker with low privileges to access arbitrary files on the server.

“The getFileContents method of the UserInputService class doesn’t perform any validation of the user supplied filename parameter before retrieving the requested file from the Avamar server. Additionally, the web server runs as root, so any file can be retrieved using this vulnerability,” researchers said.

Combining the flaws allows a remote attacker to take complete control of a vulnerable system.

EMC Avamar Server 7.1.x, 7.2.x, 7.3.x, 7.4.x and 7.5.0, EMC NetWorker Virtual Edition (NVE) 9.0.x, 9.1.x and 9.2.x, and EMC Integrated Data Protection Appliance 2.0 are impacted. EMC has released patches for each of the affected products.

Digital Defense told SecurityWeek that there are more than 100 Avamar server instances accessible from the Internet – according to the Shodan search engine – which experts say is unexpected considering that the affected products are backup and deduplication appliances.

While a blog post from Digital Defense and some media reports describe the flaws as “zero-days,” the vendor has released patches prior to disclosure and there is no evidence of exploitation in the wild.

The vulnerabilities also affect VMware’s vSphere Data Protection (VDP) product. VMware informed customers of the issues on January 2, but it did not reference Digital Defense or EMC. Digital Defense told SecurityWeek that VMware’s VDP is a derivative of the EMC product and EMC informed VMware of the security bugs.

view counter

Eduard Kovacs is a contributing editor at SecurityWeek. He worked as a high school IT teacher for two years before starting a career in journalism as Softpedia’s security news reporter. Eduard holds a bachelor’s degree in industrial informatics and a master’s degree in computer techniques applied in electrical engineering.

Previous Columns by Eduard Kovacs:

Tags:

http://feedproxy.google.com/~r/Securityweek/~3/O73XL3cQ4BY/serious-flaws-affect-dell-emc-vmware-data-protection-products


Qualcomm Working on Mitigations for Spectre, Meltdown

Qualcomm has confirmed that some of its products are affected by the recently disclosed Spectre and Meltdown vulnerabilities, but the company says mitigations are being deployed.

The chipmaker has provided few details, but claims it has been working with ARM and others to assess the impact of the flaws. Mitigations have been developed and Qualcomm is in the process of incorporating them into impacted products.

“We are in the process of deploying these mitigations to our customers and encourage people to update their devices when patches become available,” the company stated.

Qualcomm’s processors, used in devices from several major vendors, include CPU, GPU, modem, audio, and camera components. Some of the systems rely on ARM CPU cores that have been confirmed to be affected by the Spectre (CVE-2017-5753 and CVE-2017-5715) and Meltdown (CVE-2017-5754) vulnerabilities.

For example, the Snapdragon 653, 652 and 650 platforms use ARM Cortex-A72 processors, which ARM says are vulnerable to both Spectre exploits and a variant of the Meltdown attack. Moreover, the Snapdragon 845 mobile platform, which Qualcomm unveiled just a few weeks ago, uses a customized version of the Cortex-A75, which is also vulnerable to both Spectre and Meltdown attacks.

Qualcomm is not the only vendor using ARM technology in its products. Apple, whose A-series system-on-a-chip (SoC) also uses ARM processing cores, confirmed that some of its devices are affected.

Raspberry Pis also use ARM cores, but the Raspberry Pi Foundation announced that the models found in its devices – specifically ARM1176, Cortex-A7, and Cortex-A53 – are not impacted by Spectre or Meltdown.

The Meltdown and Spectre attacks allow malicious applications to bypass memory isolation mechanisms and access potentially sensitive data, including passwords, photos, documents, emails, and data from instant messaging apps.

Billions of devices using Intel, AMD and ARM processors are affected and researchers believe attacks are not easy to detect. Experts are concerned that we may soon witness remote attacks.

Attacks can be prevented using kernel page table isolation (KPTI) and a mitigation named Retpoline developed by researchers at Google. Intel, Apple, Microsoft, Google, Amazon and others have already started rolling out patches and workarounds.

However, the mitigations can introduce performance penalties of up to 30 percent for affected processors. While Intel said regular users should not notice any difference and several tech giants claimed they had not seen any meaningful performance impact, some AWS customers have reported problems, and tests conducted by Red Hat showed penalties of up to 19% in the case of operations involving highly cached random memory.

Related: Industry Reactions to Meltdown, Spectre Attacks

view counter

Eduard Kovacs is a contributing editor at SecurityWeek. He worked as a high school IT teacher for two years before starting a career in journalism as Softpedia’s security news reporter. Eduard holds a bachelor’s degree in industrial informatics and a master’s degree in computer techniques applied in electrical engineering.

Previous Columns by Eduard Kovacs:

Tags:

http://feedproxy.google.com/~r/Securityweek/~3/b1QghetwvQo/qualcomm-working-mitigations-spectre-meltdown


Several Vulnerabilities Patched in Advantech WebAccess

Taiwan-based industrial automation company Advantech has released an update for its WebAccess product to address several vulnerabilities, including ones rated high severity.

Advantech WebAccess is a browser-based software package for human-machine interfaces (HMI) and supervisory control and data acquisition (SCADA) systems. According to ICS-CERT, the product is used in the United States, Europe and East Asia in sectors such as critical manufacturing, energy, and water and wastewater.

Researchers have once again found several vulnerabilities in this HMI/SCADA product. One of the most serious, based on its CVSS score of 8.2, is CVE-2017-16724, which has been described as a stack-based buffer overflow. These types of security holes typically allow an attacker to crash the application and possibly even execute arbitrary code.

The identifier CVE-2017-16728 has been assigned to several untrusted pointer dereference vulnerabilities that can be exploited to cause the application to crash.

Experts also identified a path traversal flaw that can be exploited to access files on the targeted device (CVE-2017-16720), and a SQL injection vulnerability caused by the lack of proper sanitization of user input (CVE-2017-16716).

The least serious weakness, classified as medium severity, allows an attacker to crash the application using specially crafted inputs.

The vulnerabilities have been patched by Advantech with the release of WebAccess 8.3. The vendor says all prior versions are affected.

A report published last year by Trend Micro’s Zero Day Initiative (ZDI) showed that it had taken Advantech, on average, 131 days to patch vulnerabilities, which was significantly better compared to many other major ICS vendors. ZDI published more than 50 advisories for Advantech vulnerabilities in 2017, which was roughly half the number published in the previous year.

Several of the flaws were reported through ZDI by researchers Steven Seeley, Zhou Yu and Andrea Micalizzi. ZDI has prepared advisories for the vulnerabilities, but it has yet to make them public. The list of experts credited by ICS-CERT for finding the flaws also includes Michael Deplante.

Seeley was also credited for finding two remote code execution vulnerabilities in Advantech WebAccess in November.

Related: Advantech Patches Flaws in WebAccess SCADA Software

Related: Advantech WebAccess Flaws Allow Access to Sensitive Data

Related: Authentication Flaw Found in Advantech ICS Gateways

view counter

Eduard Kovacs is a contributing editor at SecurityWeek. He worked as a high school IT teacher for two years before starting a career in journalism as Softpedia’s security news reporter. Eduard holds a bachelor’s degree in industrial informatics and a master’s degree in computer techniques applied in electrical engineering.

Previous Columns by Eduard Kovacs:

Tags:

http://feedproxy.google.com/~r/Securityweek/~3/6IPLWGEsDbU/several-vulnerabilities-patched-advantech-webaccess


Ubuntu Preps Patches for Meltdown, Spectre CPU Flaws

Ubuntu security updates planned for January 9 will patch the recently disclosed Meltdown and Spectre CPU vulnerabilties, Canonical has announced.

Impacting billions of devices around the world, Meltdown and Spectre are two new side-channel attacks targeting CPUs from Intel, AMD and ARM. Residing in the CPU architecture, the flaws impact Windows, MacOS, Linux, and many other operating systems.

The attacks abuse three different flaws and can be leveraged to bypass memory isolation and access sensitive data such as passwords, photos, documents, and emails.

Experts are warning of the risk of remote exploitation of Spectre vulnerabilities in targeted or mass attacks and tech companies such as Microsoft, Google, Apple, and others have already revealed plans to address the issues in their products.

On Thursday, Intel announced patches for its CPUs, saying it would address the bugs in 90% of the CPUs produced over the past five years.

Intel is said to have been aware of the vulnerabilities since April 2017, and other companies were informed on the matter a while ago as well, including Canonical, which has been working on fixes for the past couple of months.

According to the company, “essentially every operating system, hardware, and cloud vendor in the world” agreed to a coordinated release date of January 9, 2018, but the news on Meltdown and Spectre broke earlier. However, patches for Ubuntu won’t be available until the planned release date.

“By design, operating system updates would be available at the same time as the public disclosure of the security vulnerability.  While it happens rarely, this an industry standard best practice, which has broken down in this case,” Canonical explains.

Ubuntu 64-bit x86 (aka, amd64) should receive updated kernels by Jan 9, or sooner if possible. The updates will be released for Ubuntu 17.10 (Artful) — Linux 4.13 HWE; Ubuntu 16.04 LTS (Xenial) — Linux 4.4 (and 4.4 HWE); Ubuntu 14.04 LTS (Trusty) — Linux 3.13; and Ubuntu 12.04 ESM (Precise) — Linux 3.2 (an Ubuntu Advantage license is required for the 12.04 ESM kernel update).

In April, Ubuntu 18.04 LTS (Bionic) will ship with a 4.15 kernel, which includes the KPTI patchset as integrated upstream, the company says.

“Ubuntu optimized kernels for the Amazon, Google, and Microsoft public clouds are also covered by these updates, as well as the rest of Canonical’s Certified Public Clouds including Oracle, OVH, Rackspace, IBM Cloud, Joyent, and Dimension Data,” Canonical explains.

The company also warns that a reboot will be required to activate the update, as the kernel fixes are not Livepatch-able. The update includes “hundreds of independent patches, touching hundreds of files and thousands of lines of code,” and the complexity of the patchset is not compatible with the Linux kernel Livepatch mechanism.

Related: Intel Patches CPUs Against Meltdown, Spectre Exploits

Related: Tech Giants Address Critical CPU Vulnerabilities


view counter

Ionut Arghire is an international correspondent for SecurityWeek.

Previous Columns by Ionut Arghire:

Tags:

http://feedproxy.google.com/~r/Securityweek/~3/I1NjBHlNN1o/ubuntu-preps-patches-meltdown-spectre-cpu-flaws


Industry Reactions to Meltdown, Spectre Attacks: Feedback Friday

Researchers disclosed this week the details of two new attack methods allowing malicious actors to gain access to sensitive information stored in a device’s memory by exploiting security holes in Intel, AMD and ARM processors.

The attacks, known as Spectre and Meltdown, have already been addressed by several vendors, including Microsoft, Apple and Google, and Intel and others are also working on rolling out patches.

Billions of PCs, mobile devices and cloud instances are vulnerable to attacks leveraging the Spectre and Meltdown vulnerabilities, and some fear we will soon witness remote exploitation attempts.

Experts comment on the Meltdown and Spectre vulnerabilities

Industry professionals have commented on various aspects of Meltdown and Spectre, including their impact, what users and organizations need to do, and the lessons that can be learned.

And the feedback begins…

Sam Curry, Chief Security Officer, Cybereason:

“The recent revelation of a major chip design security flaw is quite technical and gets to the underlying architecture and interface of physical memory and virtual memory, which is a big part of all practical, modern computing. It’s important to note that no one is immune by default to this chip design flaw and that it may impact a wider set of chips and manufacturers over time. In trying to find ways of improving overall security in memory management, researchers have uncovered a very long running set of flaws that could mean the ability to exploit a lot of systems very deeply.


This is so fundamental that it’s likely they knew about the flaw, so it’s going to be important to watch how they handle the situation and how the narrative and history unfold. The chip vendors are playing this calmly, but this is likely the calm before the storm. It’s too early to point fingers yet, but eyes are on the entire chip industry now. Also in spite of the early attention on Intel, this class of threats effects other chip sets. Now is the time for everyone in the chip game to take care of their own business. No excuses.”

Michael Daly, CTO, Cybersecurity & Special Missions, Raytheon:

“The Intel vulnerability reinforces the need for everyone to stay on top of the latest patches. We learned that hard lesson with the Wannacry attack that quickly spread to 150 countries.


In this case, the most immediate and significant risk exists in the cloud services provider environments and in private data centers. The threat seems to be the grabbing of passwords/hash-values and encryption keys from memory and then using these to install additional malware.


Until these systems can all be patched, it will be even more important to watch for unauthorized processes (applications) and other evidence of tampering, such as increased processor usage and file drops. When the patches are issued, their deployment should be prioritized because criminals and nation-state adversaries apparently have had a couple of months head start.”

Ryan Kalember, SVP, Cybersecurity Strategy, Proofpoint:

“Like most organizations, chip manufacturers have long prioritized speed over security—and that has led to a tremendous amount of sensitive data placed at risk of unauthorized access via Meltdown and Spectre. While the vast majority of computing devices are impacted by these flaws, the sky is not falling. Both vulnerabilities require an attacker to be able to run their code on the device they are attacking. The typical consumer is still vastly more likely to be targeted by something like a phishing email than a targeted attack exploiting Meltdown or Spectre. However, these vulnerabilities break down some of the most fundamental barriers computers use to keep data safe, so cloud providers need to act quickly to ensure that unauthorized access, which would be very difficult to detect, does not occur.


If there is some good news, it’s fortunate that these vulnerabilities were discovered and responsibly disclosed by respected researchers as opposed to being exploited in a large scale, potentially-damaging global attack.”

Bryce Boland, Asia Pacific Chief Technology Officer, FireEye:

“Vulnerabilities like this are extremely problematic because they permeate so much of the technology around us that we all rely upon. Resolving this issue will take time and incur costs. In many cases, this cost includes security risks, rectification effort and even computing performance.


These vulnerabilities can have big implications. Many services can be exposed and affected. Hardware vendors will address the underlying design issue, though vulnerable systems will likely remain in operation for decades. In the meantime, software vendors are releasing patches to prevent attackers from exploiting these vulnerabilities. This will also impact system performance which may have a cumulative effect in data centers for anyone using cloud services and the internet.


Large organizations will need to make a risk management decision as to how quickly they update their systems, as this can be disruptive and costly.


We are yet to understand the full impact of this development, and not all details are available. At this stage, exploitable code is not publicly available. Nation state hackers typically use these types of vulnerabilities to develop new attack tools, and that’s likely in this case.”

Christian Vezina, Chief Information Security Officer, VASCO Data Security:

“What I find interesting is that with the ever increasing amount of software code of out there, security researchers are still discovering 20+ years old vulnerabilities. Unfortunately the processor level vulnerabilities that have been published recently seem to indicate a trend: Everyone drop what you are doing and start patching your systems [again].”

Ben Carr, Vice President of Strategy, Cyberbit:

“Vulnerabilities like Meltdown only highlight the breadth of the potential issue we face no matter the investment. Meltdown potentially affects Intel processors going back to 1995. While many are rushing to find a fix after the disclosure, one must admit that this is why nation state actors don’t really have to try that hard to find a way in. At its core, it just isn’t that difficult.


In the cybersecurity industry, we must realize that we have maxed out on our ability to lock down systems and networks. It has become critical that we look to ways not only to prevent but to defend.”

Michael Lines, VP of strategy, risk and compliance, Optiv:

“The Meltdown and Spectre security flaws are affecting billions of devices, but the fundamental challenges that organizations face remain the same as every other major vulnerability that has been announced. Fixing these security flaws is going to be a long-term issue to resolve because, one, patches are needed across a vast array of operating systems, and two, patches for Spectre are still to be developed and released.


These widespread vulnerabilities underscore the importance of having ongoing risk assessment processes in place, as well as well-oiled TVM processes – both as part of a robust information security program. Risk assessment should cover both awareness and management of the issue at the board and C-suite level. These flaws are going to bring a lot of ‘doom and gloom,’ but organizations’ ability to react in an efficient and predictable way is what is most critical. Don’t panic, prepare a rational plan based on patch availability and system sensitivity, execute your plan, and monitor progress.”

Prof. Yehuda Lindell, chief scientist and co-founder, Dyadic:

“The important take-away from these attacks is very simple – computation leaks secrets! There has been a huge body of work showing that secret cryptographic keys and private information can be stolen by running software on the same machine and utilizing the properties of modern complex processors that don’t provide true separation between processes. In the past it has been shown how the machine’s cache and even clock can be used by one process to steal secrets from another. Meltdown and Spectre go a step further by utilizing the way that modern processors achieve speedups through something called “speculative execution”.


As a result, if you are computing on private information or carrying out cryptographic operations on a machine, and an attacker can run code on the same machine, then you are not safe. This includes the case that an attacker breaches your network, but is primarily of relevance in cloud environments where by definition different customers run their applications on the same machine.”

Jeff Tang, Senior Security Researcher, Cylance:

“The biggest impact is for companies relying on shared computing resources in the cloud – such as virtual private servers, virtual machines, and containers – which place them at higher risk of an attacker employing these new techniques to extract secrets (passwords, encryption keys, and other sensitive data). Administrators should check with their hosting provider to determine the appropriate steps to deploy mitigations which may include applying software updates and rebooting the virtual machine.


Administrators should prioritize patch testing and validation of the newly released Microsoft security update and deploy them to shared workstations and hypervisor based systems which are at higher risk of being targeted by attackers hoping to maximize their impact.”

Joseph Carson, Chief Security Scientist, Thycotic:

“The latest Intel, ARM and AMD chip security flaw is a major issue for multiple reasons, the security risk has the potential for simple code running in a web browser. This could allow for a cybercriminal to access sensitive data in protected memory which could include passwords, login keys or sensitive data that is typically protected. The patch of such a flaw is a major challenge as a firmware update typically requires a reboot so for servers running critical systems, this results in unplanned downtime. With the fix having a potential performance impact of up to 30%, this means critical systems already running at full power could require costly upgrades to ensure operational stability.


With these cyber risks, it means that most companies will approach patching systems with extreme caution as many companies still prioritise business operations over security issues. The impact for many companies not having the systems operational is sometimes greater than the risk of a cyberattack but cyberattacks do not come cheap either as seen with cyberattacks like WannaCry and NotPetya in 2017 costing some companies up to 300 million USD. The systems at higher risk are those that are internet connected, meaning they are easily accessible by cybercriminals and those systems used by employees, who regularly use them for browsing the internet, so these systems should be the priority for any organisation that takes cybersecurity seriously.”

view counter

Eduard Kovacs is a contributing editor at SecurityWeek. He worked as a high school IT teacher for two years before starting a career in journalism as Softpedia’s security news reporter. Eduard holds a bachelor’s degree in industrial informatics and a master’s degree in computer techniques applied in electrical engineering.

Previous Columns by Eduard Kovacs:

Tags:

http://feedproxy.google.com/~r/Securityweek/~3/vBe8l08UuuQ/industry-reactions-meltdown-spectre-attacks-feedback-friday


Intel Patches CPUs Against Meltdown, Spectre Exploits

Intel has been working with its partners to release software and firmware updates that should protect systems against the recently disclosed CPU attacks. The company expects patches to become available for a majority of its newer products by the end of next week.

Researchers this week disclosed the details of Spectre and Meltdown, two new side-channel attacks targeting CPUs from Intel, AMD and ARM. The attacks, which leverage three different flaws, can be used to bypass memory isolation mechanisms and gain access to sensitive data, including passwords, photos, documents, and emails. Experts have warned that malicious actors may soon start to remotely exploit the Spectre vulnerabilities in targeted or mass attacks.

AMD has insisted that there is a “near zero risk” to its customers and ARM says only a few of its Cortex processors are impacted.

Intel informed customers on Thursday that system manufacturers have been provided firmware and software updates that address Spectre and Meltdown for processors launched in the last five years – experts believe nearly every Intel processor made since 1995 is impacted. It will now be up to system manufacturers to distribute the patches.

“By the end of next week, Intel expects to have issued updates for more than 90 percent of processor products introduced within the past five years,” Intel said.

In response to concerns that mitigations for the Spectre and Meltdown vulnerabilities can introduce performance penalties of as much as 30 percent, Intel pointed out that average users will not notice any difference.

“While on some discrete workloads the performance impact from the software updates may initially be higher, additional post-deployment identification, testing and improvement of the software updates should mitigate that impact,” Intel said.

The company cited Apple, Microsoft, Amazon and Google, all of which said the mitigations did not create any noticeable performance issues.

The best protection against these attacks is the use of kernel page table isolation (KPTI), a hardening technique designed by a team of researchers at the Graz University of Technology in Austria to isolate kernel space from user space memory. Google, whose researchers independently found the flaws, also developed a novel mitigation named Retpoline.

Microsoft, Apple, Google, Red Hat, VMware and other major tech firms have already started releasing software updates and workarounds to resolve the vulnerabilities.

Intel was hit the hardest by Spectre and Meltdown and the company’s stock lost 6 percent in value shortly after the disclosure. The company’s CEO, Brian Krzanich, sold all the stock he was legally allowed to, worth roughly $24 million, just before the news broke, which has raised insider trading concerns. Intel claims Krzanich had been planning on selling stock for months, but Intel has reportedly known about the vulnerabilities since April 2017.

view counter

Eduard Kovacs is a contributing editor at SecurityWeek. He worked as a high school IT teacher for two years before starting a career in journalism as Softpedia’s security news reporter. Eduard holds a bachelor’s degree in industrial informatics and a master’s degree in computer techniques applied in electrical engineering.

Previous Columns by Eduard Kovacs:

Tags:

http://feedproxy.google.com/~r/Securityweek/~3/9WIKYxZBECQ/intel-patches-cpus-against-meltdown-spectre-exploits


Google Apps Script Allowed Hackers to Automate Malware Downloads

Researchers at Proofpoint discovered recently that Google Apps Script could have been abused by malicious hackers to automatically download malware hosted on Google Drive to targeted devices.

Google Apps Script is a JavaScript-based scripting language that allows developers to build web applications and automate tasks. Experts noticed that the service could have been leveraged to deliver malware by using simple triggers, such as onOpen or onEdit.

In an attack scenario described by Proofpoint, attackers uploaded a piece of malware to Google Drive and created a public link to it. They then used Google Docs to send the link to the targeted users. Once victims attempted to edit the Google Docs file, the Apps Script triggers would cause the malware to be automatically downloaded to their devices. Researchers said attackers could have used social engineering to convince the target to execute the malware.

Google has implemented new restrictions for simple triggers in an effort to block malware and phishing attacks triggered by opening a document.

While there is no evidence that this method has been exploited in the wild, malicious actors abusing Google Apps Script is not unheard of. A cybercrime group using the infamous Carbanak malware at one point leveraged the service for command and control (C&C) communications.

“SaaS platforms remain a ‘Wild West’ for threat actors and defenders alike. New tools like Google Apps Script are rapidly adding functionality while threat actors look for novel ways of abusing these platforms. At the same time, few tools exist that can detect threats generated by or distributed via legitimate software-as-a-service (SaaS) platforms,” explained Maor Bin, security research lead of Threat Systems Products at Proofpoint. 

“This creates considerable opportunities for threat actors who can leverage newfound vulnerabilities or use ‘good for bad’: making use of legitimate features for malicious purposes,” he added.

A few months ago, Google announced the introduction of new warnings for potentially risky web apps and Apps Scripts.

Related: Google Patches Vulnerabilities in Caja Tool

Related: Google to Scrutinize Web Applications Requesting User Data

Related: Google Tightens OAuth Rules to Combat Phishing

view counter

Eduard Kovacs is a contributing editor at SecurityWeek. He worked as a high school IT teacher for two years before starting a career in journalism as Softpedia’s security news reporter. Eduard holds a bachelor’s degree in industrial informatics and a master’s degree in computer techniques applied in electrical engineering.

Previous Columns by Eduard Kovacs:

Tags:

http://feedproxy.google.com/~r/Securityweek/~3/yXRCftAU9b8/google-apps-script-allowed-hackers-automate-malware-downloads


Hackers Expected to Remotely Exploit CPU Vulnerabilities

Security experts believe hackers will soon start to remotely exploit the recently disclosed vulnerabilities affecting Intel, AMD and ARM processors, if they haven’t done so already.

Researchers disclosed on Wednesday the details of Spectre and Meltdown, two new attack methods targeting CPUs. The attacks leverage three different flaws and they can be used to bypass memory isolation mechanisms and gain access to sensitive data, including passwords, photos, documents, and emails.

The affected CPUs are present in billions of products, including PCs and smartphones, and attacks can also be launched against cloud environments.

The best protection against these attacks is the use of kernel page table isolation (KPTI) and affected vendors have already started releasing patches and workarounds.

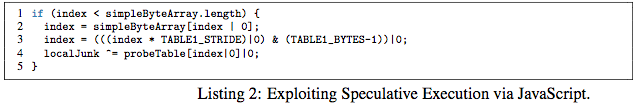
While the main attack vector is via local access (e.g. a piece of malware installed on the targeted machine), researchers say remote attacks via JavaScript are also possible, particularly in the case of Spectre.

Researchers have developed a proof-of-concept (PoC) for Google Chrome that uses JavaScript to exploit Spectre and read private memory from the process in which it runs.

Spectre attack JavaScript PoC

Mozilla has conducted internal experiments and determined that these techniques can be used “from Web content to read private information between different origins.” While the issue is still under investigation, the organization has decided to implement some partial protections in Firefox 57.

Google pointed out that attacks are possible via both JavaScript and WebAssembly. The company informed customers that current versions of Chrome include a feature named Site Isolation that can be manually enabled to prevent attacks. Chrome 64, which is scheduled for release on January 23, will contain mitigations in the V8 JavaScript engine. Other hardening measures will be included in future versions, but the tech giant warned that they may have a negative impact on performance.

Microsoft has also confirmed that attacks can be launched via JavaScript code running in the browser. The company has released updates for its Edge and Internet Explorer web browsers to mitigate the vulnerabilities.

Since a JavaScript PoC is available, experts believe it’s only a matter of time until malicious actors start exploiting the flaws remotely. While some say state-sponsored actors are most likely to leverage these attacks, others point out that mass exploitation is also possible, particularly via the ads served by websites.

That is why some experts have advised users to disable JavaScript in their browser and install ad blockers.

Mike Buckbee, security engineer at Varonis, noted that while exploitation via the browser might not give attackers access to files, they are still likely to find valuable data in the memory, including SSH keys, security tokens and passwords.

While affected vendors say there is no evidence that Spectre and Meltdown have been exploited prior to their disclosure, the researchers who discovered the vulnerabilities warn that attacks are not easy to detect.

Researcher Jake Williams said, “It’s reasonable to assume that most nation states had Spectre and Meltdown before public announcement. If by some miracle they weren’t already using these, they will be now.”

Bryce Boland, Asia Pacific Chief Technology Officer at FireEye, agrees. “Nation state hackers typically use these types of vulnerabilities to develop new attack tools, and that’s likely in this case,” he said.

Sam Curry, Chief Security Officer at Cybereason, also believes sophisticated actors will likely exploit the flaws, if they haven’t done so already.

“This isn’t yet doom and gloom but the tension will rise. And don’t be surprised if it comes to light that a nation state is already using this or if a catalyst in the form of hack or research further heats this up and makes it a more clear-and-present risk in 2018,” Curry told SecurityWeek.

view counter

Eduard Kovacs is a contributing editor at SecurityWeek. He worked as a high school IT teacher for two years before starting a career in journalism as Softpedia’s security news reporter. Eduard holds a bachelor’s degree in industrial informatics and a master’s degree in computer techniques applied in electrical engineering.

Previous Columns by Eduard Kovacs:

Tags:

http://feedproxy.google.com/~r/Securityweek/~3/U3W1S0UidKc/hackers-expected-remotely-exploit-cpu-vulnerabilities


Tech Giants Address Critical CPU Vulnerabilities

Several major tech companies have started releasing patches and mitigations for the recently disclosed Meltdown and Spectre vulnerabilities affecting CPUs from Intel, AMD and ARM.

The flaws exploited by the Meltdown and Spectre attacks, tracked as CVE-2017-5715, CVE-2017-5753 and CVE-2017-5754, allow malicious applications to bypass memory isolation mechanisms and access data as it’s being processed. This can include passwords, photos, documents, emails, and data from instant messaging apps.

Billions of PCs, smartphones and cloud instances are affected, and while there is no evidence of attacks in the wild, researchers said exploitation attempts are unlikely to be detected.

Meltdown

Attacks can be prevented using kernel page table isolation (KPTI), a hardening technique designed to improve security by isolating kernel from user memory. However, the mitigation can introduce performance penalties of up to 30 percent for affected processors.

Researchers had initially planned on disclosing the security holes on January 9, but disclosure was moved up due to media reports and speculation surrounding the topic. Affected tech companies have already started informing users about the risks and the availability of patches and mitigations.

Intel, AMD and ARM

Initial reports claimed only Intel CPUs were affected by the vulnerabilities. While Intel was hit the hardest, some of the flaws affect AMD and ARM as well.

Intel has informed customers that it’s working with manufacturers and operating system vendors to address the issues. The company also reassured customers that performance penalties will not affect regular computer users and will be mitigated over time.

Spectre

AMD is apparently only affected by the Spectre vulnerabilities (CVE-2017-5753 and CVE-2017-5715), and the company claims the risk to its processors is “near zero” thanks to their architecture.

In the case of ARM, the company says only its Cortex-A75 processors are affected by all three vulnerabilities. Cortex R7, R8, A8, A9, A15, A17, A57, A72 and A73 processors are vulnerable to Meltdown attacks and affected by the CVE-2017-5715 Spectre flaw. Other existing products and future processors are not affected, the company said.

ARM has provided kernel patches for Linux users and advised customers using Android and other OSs to check for updates from their respective vendor.

Google

Google has patched the vulnerabilities in its Cloud platform, but some users may need to manually perform some tasks.

“Google Compute Engine used VM Live Migration technology to perform host system and hypervisor updates with no user impact, no forced maintenance windows, and no mass reboots required. However, all guest operating systems and versions must be patched to protect against this new class of attack regardless of where those systems run,” Google said.

The company has informed Android users that while the risk of attacks is small, the latest Android security updates do provide additional protection against Spectre and Meltdown.

Microsoft

Microsoft started implementing protections in Windows a few months ago. The company informed customers on Wednesday that it released several updates to help mitigate the vulnerabilities in Windows client and server products. It has also released a tool designed to tell customers if protections are enabled.

Microsoft is also working to ensure that customers of its Azure cloud platform are not vulnerable to Meltdown and Spectre attacks.

“The majority of Azure infrastructure has already been updated to address this vulnerability. Some aspects of Azure are still being updated and require a reboot of customer VMs for the security update to take effect,” the company said.

Apple

Apple has yet to make any public statements, but security expert Alex Ionescu reported that version 10.13.2 of macOS High Sierra, which Apple released on December 6, does fix the vulnerabilities.

Xen, Amazon Web Services (AWS), DigitalOcean, Rackspace

The Xen Project said systems running any version of the Xen hypervisor are affected. Due to the accelerated disclosure, the organization has not had time to create patches, and mitigations are available for only one of the security holes.

AWS, which uses Xen, told customers, “All but a small single-digit percentage of instances across the Amazon EC2 fleet are already protected. The remaining ones will be completed in the next several hours, with associated instance maintenance notifications.”

Rackspace, which also uses Xen, is currently investigating the issue. DigitalOcean has also launched an investigation, but the company has blamed Intel’s embargo for not determining potential impact sooner.

Mozilla

Mozilla has conducted some internal experiments and found that it is possible to use techniques similar to Meltdown and Spectre from web content to read private date between different origins. The full extent of the issue has yet to be determined, but some partial mitigations have already been added to Firefox

Red Hat

Red Hat has classified the vulnerabilities as important and it has already developed kernel updates for affected versions of Red Hat Enterprise Linux.

“We are working with our customers and partners to make these updates available, along with the information our customers need to quickly secure their physical systems, virtual images, and container-based deployments,” said Chris Robinson, manager of Product Security Assurance at Red Hat.

nVIDIA

nVIDIA said its GPU hardware does not appear to be impacted by Meltdown and Spectre, but some system-on-a-chip (SoC) products using ARM CPUs are vulnerable. The company is working on identifying affected products and preparing mitigations.

view counter

Eduard Kovacs is a contributing editor at SecurityWeek. He worked as a high school IT teacher for two years before starting a career in journalism as Softpedia’s security news reporter. Eduard holds a bachelor’s degree in industrial informatics and a master’s degree in computer techniques applied in electrical engineering.

Previous Columns by Eduard Kovacs:

Tags:

http://feedproxy.google.com/~r/Securityweek/~3/L4lGbOBhH6w/tech-giants-address-critical-cpu-vulnerabilities


Intel, AMD Chip Vulnerabilities Put Billions of Devices at Risk

Details of “Meltdown” and “Spectre” Attacks Against Intel and AMD Chips Disclosed

Researchers have disclosed technical details of two new attack methods that exploit critical flaws in CPUs from Intel, AMD and other vendors. They claim billions of devices are vulnerable, allowing malicious actors to gain access to passwords and other sensitive data without leaving a trace.

There have been reports in the past few days about a critical flaw in Intel CPUs that allows an attacker to gain access to kernel space memory. It turns out that there are actually two different attacks and researchers say one of them impacts AMD and ARM processors as well.

AMD representatives have claimed that their products are not vulnerable, which has contributed to the company’s stock going up 7 percent. Intel released a statement saying that the vulnerabilities are not unique to its products after its shares lost 4 percent in value.

Meltdown and Spectre

The side-channel attacks, dubbed Meltdown and Spectre by researchers, allow malicious applications installed on a device to access data as it’s being processed. This can include passwords stored in a password manager or web browser, photos, documents, emails, and data from instant messaging apps.

Attacks can be launched not only against PCs, but also mobile devices and cloud servers. While there is no evidence of exploitation in the wild, researchers pointed out that the attacks don’t leave any traces in traditional log files and they are unlikely to be detected by security products – although security products may detect the malware that launches Meltdown and Spectre.

Meltdown was discovered independently by Jann Horn of Google Project Zero, researchers from Cyberus Technology, and a team from the Graz University of Technology in Austria. Spectre was found independently by Horn, and a group of experts from various universities and companies. Technical papers and proof-of-concept (PoC) code have been published for each of the attack methods, and Intel, Microsoft, ARM and Google Project Zero are expected to publish their own advisories.

Memory isolation mechanisms found in modern computer systems should normally prevent applications from reading or writing to kernel memory or accessing the memory of other programs. However, the Meltdown and Spectre attacks bypass these protections.Meltdown

Meltdown, named so because it “melts” security boundaries normally enforced by hardware, can be leveraged to read arbitrary kernel memory locations. A malicious unprivileged app can use it to read memory associated with other programs and even virtual machines in cloud environments. The vulnerability behind Meltdown is tracked as CVE-2017-5754.

Researchers say it’s unclear if Meltdown affects ARM and AMD processors, but it has been confirmed to impact nearly every Intel processor made since 1995, specifically CPUs that implement a system known as out-of-order execution.

Spectre, on the other hand, has been confirmed to affect not just Intel, but also AMD and ARM processors. However, AMD claims there is a “near zero risk” to its processors due to their architecture.

Desktops, laptops, smartphones and cloud servers are impacted, but the vulnerability is more difficult to exploit compared to Meltdown.

The attack has been named Spectre because its root cause is speculative execution and it will “haunt us for quite some time” due to the fact that it’s not easy to fix. The CVE identifiers CVE-2017-5753 and CVE-2017-5715 have been assigned to Spectre.Spectre

Spectre breaks isolation between different applications and it allows an attacker to trick programs that follow best practices to leak secrets stored in their memory.

“Meltdown breaks the mechanism that keeps applications from accessing arbitrary system memory. Consequently, applications can access system memory,” researchers explained. “Spectre tricks other applications into accessing arbitrary locations in their memory. Both attacks use side channels to obtain the information from the accessed memory location.”

Mitigations

Meltdown attacks can be prevented using kernel page table isolation (KPTI), a hardening technique designed to improve security by isolating the kernel space from user space memory. It’s based on the KAISER system developed last year by a team of researchers at Graz University.

KPTI has already been implemented in the Linux kernel and Microsoft has been working on a similar system for Windows. Apple is also said to be working on patches for macOS.

Cloud providers that use Intel CPUs and Xen paravirtualization are impacted. Amazon Web Services (AWS) and Microsoft Azure have been working on patches and they have informed customers that cloud instances will need to be rebooted in the upcoming days to apply security patches.

Google has addressed the vulnerabilities in its Cloud products and services. The company pointed out that while attacks are not easy to launch against Android devices, the latest Android security updates do provide additional protection.

Spectre attacks are more difficult to block. However, researchers say it’s possible to prevent specific known exploits using software patches.

Intel addresses concerns of performance penalties introduced by mitigations

Since KPTI has already been implemented in the Linux kernel before the disclosure – this actually led to experts figuring out that there was a serious vulnerability in Intel CPUs – several tests have been conducted to determine the impact of the mitigation on performance.

The researchers who developed the KAISER method reported a negative impact of only 0.28 percent on performance, but tests conducted now showed that performance penalties can reach as much as 30 percent, depending on what types of operations are being conducted.

Michael Schwartz, one of the researchers involved in the discovery of the Meltdown and Spectre vulnerabilities, has confirmed for SecurityWeek that there definitely can be a significant performance penalty for certain types of workloads.

“We ran some benchmarks on our initial KAISER implementation which showed only small performance impacts on modern CPUs. However, we guess that the performance penalties reported by other people (something between 5% – 30%) are realistic on older CPUs and unusual workload (e.g., many syscalls),” Schwartz said.

Intel has reassured customers that any performance impacts are workload-dependent and they should not be significant for the average user. Furthermore, the chip maker says performance impact will be mitigated over time.

* Updated with information on Google patches

view counter

Eduard Kovacs is a contributing editor at SecurityWeek. He worked as a high school IT teacher for two years before starting a career in journalism as Softpedia’s security news reporter. Eduard holds a bachelor’s degree in industrial informatics and a master’s degree in computer techniques applied in electrical engineering.

Previous Columns by Eduard Kovacs:

Tags:

http://feedproxy.google.com/~r/Securityweek/~3/ik7qMbPfijc/intel-amd-chip-vulnerabilities-put-billions-devices-risk