After Major Cloud Hacks, Microsoft Unveils ‘Secure Future Initiative’

In response to a spate of embarrassing hacks, Redmond pushes ‘Secure Future Initiative’ promising faster cloud patches, better management of identity signing keys and products with a higher default security bar.

The post After Major Cloud Hacks, Microsoft Unveils ‘Secure Future Initiative’ appeared first on SecurityWeek.

https://www.securityweek.com/after-major-cloud-hacks-microsoft-unveils-secure-future-initiative/


Mass Exploitation of ‘Citrix Bleed’ Vulnerability Underway

Thousands of Citrix NetScaler ADC and Gateway instances remain unpatched against a critical vulnerability that is being widely exploited, security researchers warn.

The flaw, which had been exploited as a zero-day since August, is tracked as CVE-2023-4966 (CVSS score of 9.4) and is now referred to as ‘Citrix Bleed’. It allows unauthenticated attackers to leak sensitive information from on-prem appliances that are configured as an AAA virtual server or a gateway.

Citrix released patches for the bug on October 10 and warned last week that threat actors are actively exploiting the vulnerability in the wild to perform session hijacking, which allows them to completely bypass authentication, including multi-factor authentication protections.

Over the past few days, security researchers have started raising the alarm on CVE-2023-4966 being widely exploited, with multiple threat actors, including ransomware groups, targeting internet-accessible NetScaler ADC and Gateway instances.

The ongoing mass exploitation started around the same time Assetnote published a technical writeup of the vulnerability and a proof-of-concept (PoC) exploit for it.

According to security researcher Kevin Beaumont, however, the mass exploitation has not necessarily been triggered by the PoC publication, as “it was clear multiple groups had already obtained technical details”.

By exploiting the vulnerability, attackers gain memory access to NetScaler ADC and Gateway appliances, which allows them to extract session cookies and attempt to bypass authentication. This means that even patched instances are at risk of exploitation, as the session tokens persist in memory.

Advertisement. Scroll to continue reading.

The compromised cookies allow the attackers to replay the sessions for authentication. All they need to do is type ‘aaaaaaaaaaaaaaaaaaaaaaaa’ until they are in, Beaumont says.

“This cookie is issued post-authentication, which can include multi-factor authentication checks. An attacker with access to a valid cookie can establish an authenticated session to the NetScaler appliance without knowledge of the username, password, or access to a multi-factor authentication token or device,” Google’s cybersecurity arm Mandiant explains.

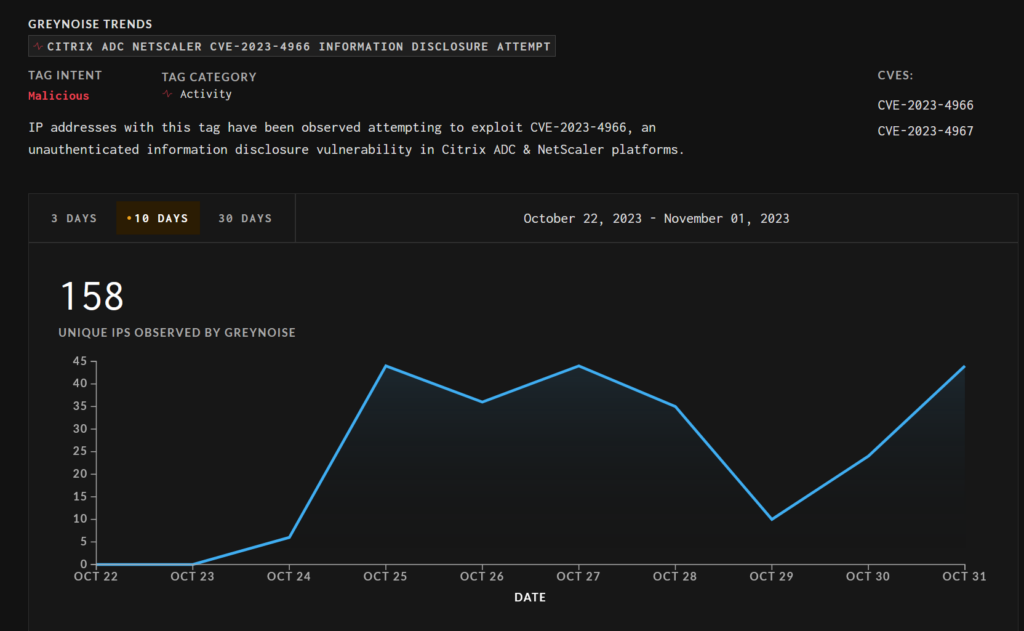
Over the weekend, Beaumont warned that attackers had stolen the session tokens of over 20,000 exploited NetScaler servers. As of November 1, data from Greynoise shows 158 unique IP addresses being used to target vulnerable instances over the past 10 days.

Warning that roughly half of NetScaler customers have yet to apply the patches, including telecommunication, electric, food, and government organizations, Beaumont last week published a scanner to help identify vulnerable NetScaler servers. 

To fully address the issue, organizations should apply the available patches and then kill all active and persistent sessions, Citrix pointed out last week, underlining that there are no known workarounds or mitigations beyond these recommended actions.

“If you are using an affected build, we urge you to install the recommended updates immediately, as this vulnerability has been identified as critical. We are aware of targeted attacks in the wild using this vulnerability,” the tech giant said.

On Tuesday, Mandiant said it is currently tracking four threat actors actively targeting CVE-2023-4966, compromising NetScaler servers, and performing various post-exploitation activities.

Threat actors have deployed various tools for reconnaissance and credential theft, remote monitoring and management (RMM) tools for persistent access, a backdoor called FreeFire, living-off-the-land binaries, and utilities for lateral movement, Mandiant said.

According to Mandiant, because NetScaler does not log requests associated with the bug, organizations can hunt for exploitation attempts using “web application firewalls (WAF) or other network appliances that record HTTP/S requests directed toward the NetScaler ADC or Gateway appliances”.

The cybersecurity firm has published comprehensive instructions on how organizations can identify evidence of session hijacking, along with indicators-of-compromise (IoCs) to aid hunters.

Mandiant has seen attacks targeting government, legal and professional services, and technology organizations in the Americas, EMEA, and the APAC regions.

“Given the widespread adoption of Citrix in enterprises globally, we suspect the number of impacted organizations is far greater and in several sectors,” it noted.

Related: US Gov Expects Widespread Exploitation of Atlassian Confluence Vulnerability

Related: In-the-Wild Exploitation Expected for Critical TeamCity Flaw Allowing Server Takeover

Related: Live Exploitation Underscores Urgency to Patch Critical WS-FTP Server Flaw

https://www.securityweek.com/mass-exploitation-of-citrix-bleed-vulnerability-underway/


Chrome 119 Patches 15 Vulnerabilities

Google on Tuesday announced the release of Chrome 119 to the stable channel with patches for 15 vulnerabilities, including 13 reported by external researchers.

Three of the externally reported bugs have a severity rating of ‘high’, and are described as inappropriate implementation in Payments (CVE-2023-5480), insufficient data validation in USB (CVE-2023-5482), and integer overflow in USB (CVE-2023-5849).

Google says in its advisory that it has paid out $16,000 for the first flaw and $11,000 for the second, and that it has yet to determine the amount to be awarded for the third issue.

Of the remaining 10 security defects reported by external researchers, eight are rated ‘medium severity’, and two have a severity rating of ‘low’.

Half of the medium-severity bugs are use-after-free issues impacting Chrome’s Printing, Profiles, Reading Mode, and Side Panel components. The other half includes two incorrect security UI issues and two inappropriate implementation flaws in Downloads.

The low-severity defects addressed this week include an inappropriate implementation in WebApp Provider and an incorrect security UI in ‘Picture In Picture’, Google notes.

The internet giant says it has paid out over $40,000 in bug bounty rewards to the reporting researchers. However, with the bounties for three of the bugs yet to be determined, the final amount might be much higher.

Advertisement. Scroll to continue reading.

As usual, Google is keeping access to the bugs restricted “until a majority of users are updated with a fix”.

The latest Chrome iteration is now rolling out to users as version 119.0.6045.105 for Linux and macOS, and as versions 119.0.6045.105/.106 for Windows.

Chrome for Android too was updated on Tuesday, bringing the same security fixes as the desktop version of the browser, Google says. Chrome 119 was pushed to iOS as well.

Google makes no mention of any of these vulnerabilities being exploited in the wild.

Related: Firefox, Chrome Updates Patch High-Severity Vulnerabilities

Related: Chrome 118 Patches 20 Vulnerabilities

Related: Google Patches Chrome Zero-Day Reported by Apple, Spyware Hunters

https://www.securityweek.com/chrome-119-patches-15-vulnerabilities/


Atlassian CISO Urges Quick Action to Protect Confluence Instances From Critical Vulnerability

Enterprise software maker Atlassian on Monday urged all Confluence Data Center and Server customers to patch their instances against a critical-severity vulnerability that can be exploited without authentication.

The security defect, tracked as CVE-2023-22518 (CVSS score of 9.1), is described as an improper authorization bug that impacts all Confluence versions.

While it did not share technical details on the flaw in its advisory, Atlassian instead drew attention to the high impact successful exploitation would have.

“As part of our continuous security assessment processes, we have discovered that Confluence Data Center and Server customers are vulnerable to significant data loss if exploited by an unauthenticated attacker,” Atlassian CISO Bala Sathiamurthy notes.

“There are no reports of active exploitation at this time; however, customers must take immediate action to protect their instances,” Sathiamurthy continues.

According to Atlassian, the vulnerability has no impact on confidentiality, as no data exfiltration can occur from exploiting it.

The issue has been addressed with the release of Confluence Data Center and Server versions 7.19.16, 8.3.4, 8.4.4, 8.5.3, and 8.6.1.

Advertisement. Scroll to continue reading.

Customers that are unable to apply the patches are advised to back up their instances and block internet access to them until they can be patched.

“Instances accessible to the public internet, including those with user authentication, should be restricted from external network access until you can patch,” Atlassian notes.

The company also notes that, as per its policy regarding critical vulnerabilities, the patches will be back ported, and that new maintenance releases for all versions covered by the policy will become available.

“Atlassian Cloud sites are not affected by this vulnerability. If your Confluence site is accessed via an atlassian.net domain, it is hosted by Atlassian and is not vulnerable to this issue,” the software maker notes.

Related: US Gov Expects Widespread Exploitation of Atlassian Confluence Vulnerability

Related: Atlassian Patches Remote Code Execution Vulnerabilities in Confluence, Bamboo

Related: Organizations Warned of Critical Confluence Flaw as Exploitation Continues

https://www.securityweek.com/atlassian-ciso-urges-quick-action-to-protect-confluence-instances-from-critical-vulnerability/


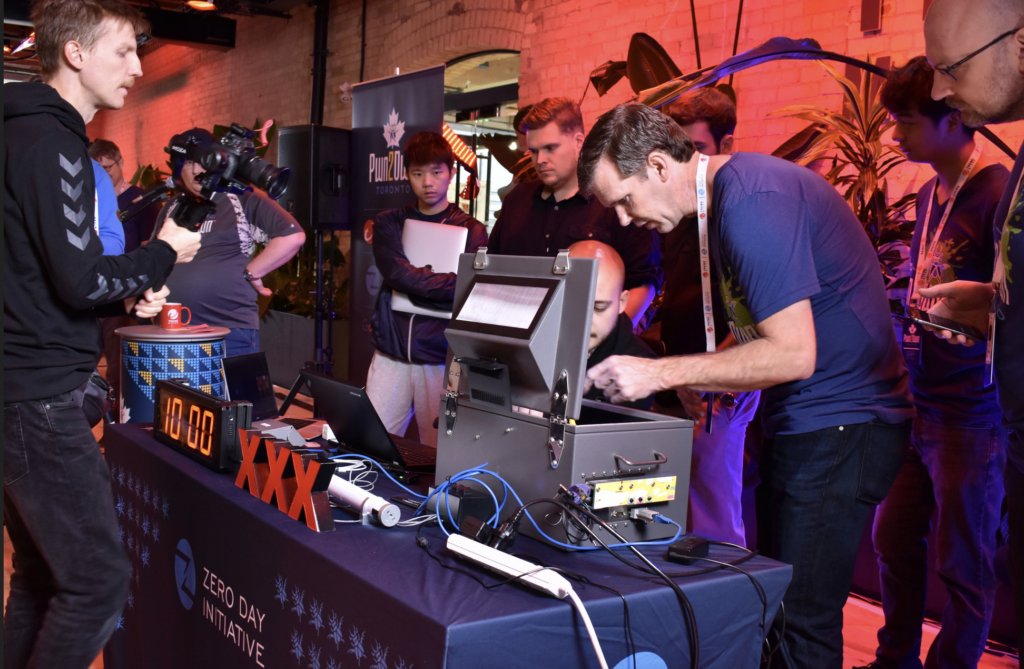
Hackers Earn Over $1 Million at Pwn2Own Toronto 2023

The Zero Day Initiative’s Pwn2Own Toronto 2023 hacking competition concluded on Friday with two new zero-day exploits, bringing the total demonstrated vulnerabilities to 58.

Over the course of four days, participants successfully exploited routers, printers, smart speakers, NAS products, surveillance systems, and mobile phones, earning more than $1 million in rewards.

Following a busy first day of the competition, when 18 exploits were demonstrated and more than $400,000 earned in rewards, participants showcased 15 exploits on the second day, eight on the third day, and three on the last day.

The highest reward, of $100,000, was awarded on the second day of the contest to Chris Anastasio, for bugs in the P-Link Omada Gigabit router and one in the Lexmark CX331adwe printer.

Throughout the competition, team Viettel demonstrated multiple exploits, earning a total of $180,000 in rewards. Team Orca of Sea Security was also able to successfully demonstrate multiple exploits, earning roughly $116,000, while Pentest Limited earned $90,000 in rewards.

Interrupt Labs, Star Labs SG, a Devcore intern, ANHTUD, Claroty, team ECQ, Sina Kheirkhah, Binary Factory, Synacktiv, Rafal Goryl, Sonar, ToChim, Nguyen Quoc Viet, and others also demonstrated successful exploits, though not all of them targeted new vulnerabilities.

Some of the demonstrated exploits chained two or three vulnerabilities, but most of them were single-bug exploits. Many of the exploits led to remote code execution.

Advertisement. Scroll to continue reading.

All the vulnerabilities have been reported to the vendors, who have 90-days to address them before details are made public.

The total paid out at Pwn2Own Toronto 2023 was higher than last year, when 26 contestants signed up for 66 exploits and earned close to $1 million throughout the four-day event.

Related: Over $1 Million Offered at New Pwn2Own Automotive Hacking Contest

Related: Hackers Earn $180,000 for ICS Exploits at Pwn2Own Miami 2023

Related: Hackers Earn Over $1 Million at Pwn2Own Exploit Contest

https://www.securityweek.com/hackers-earn-over-1-million-at-pwn2own-toronto-2023/


F5 Warns of Critical Remote Code Execution Vulnerability in BIG-IP

Security and application delivery solutions provider F5 on Thursday warned customers of a critical-severity vulnerability in its BIG-IP product.

Tracked as CVE-2023-46747 (CVSS score of 9.8) and impacting the Traffic Management User Interface of the solution, the vulnerability allows an unauthenticated attacker to execute arbitrary code remotely.

“This vulnerability may allow an unauthenticated attacker with network access to the BIG-IP system through the management port and/or self IP addresses to execute arbitrary system commands. There is no data plane exposure; this is a control plane issue only,” F5 explains in an advisory.

According to Praetorian Security, which identified the bug, CVE-2023-46747 is a request smuggling issue that allows an unauthenticated attacker to gain full administrative privileges on an impacted BIG-IP system.

The flaw, Praetorian says, is closely related to CVE-2022-26377, a request smuggling flaw in the Apache HTTP Server, and can be exploited to bypass authentication and execute commands as root.

All BIG-IP systems with the Traffic Management User Interface exposed to the internet are affected by this vulnerability.

According to F5, the issue is rooted in the configuration utility component. BIG-IP versions 13.x through 17.x are impacted and F5 has released hotfixes for all of them.

Advertisement. Scroll to continue reading.

A shell script has been released for BIG-IP versions 14.1.0 and later to mitigate the issue. Details on how the script can be used are available in F5’s advisory.

According to Praetorian, there are more than 6,000 internet-facing instances of the application, all potentially at risk of exploitation. Some of these belong to government entities and Fortune 500 companies.

Technical details on this vulnerability will be released after most BIG-IP users have patched their instances.

BIG-IP users are advised to install the available patches as soon as possible. They should also restrict access to the Traffic Management User Interface.

“The portal itself should not be accessible at all from the public internet,” Praetorian notes.

F5 makes no mention of CVE-2023-46747 being exploited in malicious attacks.

Related: F5 BIG-IP Vulnerability Can Lead to DoS, Code Execution

Related: Critical Vulnerability Exploited to ‘Destroy’ BIG-IP Appliances

Related: F5 Warns BIG-IP Customers About 18 Serious Vulnerabilities

https://www.securityweek.com/f5-warns-of-critical-remote-code-execution-vulnerability-in-big-ip/


Critical Mirth Connect Vulnerability Could Expose Sensitive Healthcare Data

Open source data integration platform Mirth Connect is affected by a remote code execution vulnerability that can be exploited without authentication, cybersecurity firm Horizon3.ai warns.

Developed by NextGen HealthCare, Mirth Connect is a cross-platform interface engine that healthcare organizations rely on for information management.

Tracked as CVE-2023-43208, the newly disclosed issue is a bypass for a critical-severity RCE flaw (CVE-2023-37679, CVSS score of 9.8) that was disclosed in August 2023 and which was addressed with the release of Mirth Connect version 4.4.0.

According to Horizon3.ai, CVE-2023-37679 was said to only impact Mirth Connect instances using Java 8 or below, but further analysis of the vulnerability has revealed that, in fact, all Mirth Connect installs are impacted, regardless of the Java version they use.

Furthermore, the cybersecurity firm’s investigation has revealed that the patch for CVE-2023-37679 can be bypassed, and reported the findings to NextGen HealthCare, which released Mirth Connect version 4.4.1 to address the new issue.

“This is an easily exploitable, unauthenticated remote code execution vulnerability. Attackers would most likely exploit this vulnerability for initial access or to compromise sensitive healthcare data,” Horizon3.ai says.

For the time being, Horizon3.ai refrains from releasing technical details or an exploit for CVE-2023-43208, but warns that the methods for exploitation are well known.

Advertisement. Scroll to continue reading.

“We have verified that Mirth Connect versions going as far back as 2015/2016 are vulnerable,” the cybersecurity firm notes.

Horizon3.ai also points out that Mirth Connect appears to be deployed mostly on Windows machines, where it typically runs with System privileges, suggesting that the impact of a successful attack would be critical.

Additionally, the cybersecurity firm notes that it has identified more than 1,200 unique Mirth Connect instances that are directly accessible from the internet.

Mirth Connect users are advised to update to version 4.4.1 of the platform as soon as possible.

Related: Dozens of RCE Vulnerabilities Impact Milesight Industrial Router

Related: Exploitation of Recent Citrix ShareFile RCE Vulnerability Begins

Related: Fortinet Patches Critical RCE Vulnerability in FortiNAC

https://www.securityweek.com/critical-mirth-connect-vulnerability-could-expose-sensitive-healthcare-data/


Hackers Earn $350k on Second Day at Pwn2Own Toronto 2023

Hackers have earned roughly $350,000 in rewards after demonstrating successful exploits against a variety of devices on the second day of the Zero Day Initiative’s Pwn2Own Toronto 2023 competition.

Just as on the first day of the hacking contest, NAS devices, printers, smart speakers, and mobile phones were hacked on Wednesday, with successful exploits also demonstrated against routers.

The highest reward went to Chris Anastasio, who earned $100,000 for exploits targeting a vulnerability in the P-Link Omada Gigabit router and one in the Lexmark CX331adwe printer, ZDI announced.

On the second day of the competition, a Devcore intern earned $50,000 for a stack buffer overflow issue in the TP-Link Omada Gigabit router and two flaws in the QNAP TS-464 NAS device.

Team Orca of Sea Security also earned $50,000 on Wednesday, for a bug in the Synology RT6600ax router and a three-bug chain against the QNAP TS-464 NAS device.

Rewards of $30,000 were handed out for a command injection in the Wyze Cam v3 security camera and an out-of-bounds write issue in the Sonos Era 100 smart speaker.

ZDI also announced high rewards for an improper input validation bug and a permissive list of allowed inputs flaw in Samsung Galaxy S23 ($25,000), a stack-based buffer overflow issue in the HP Color LaserJet Pro MFP 4301fdw ($20,000), and a stack-based buffer overflow vulnerability in the Canon imageCLASS MF753Cdw printer ($10,000).

Advertisement. Scroll to continue reading.

Additionally, multiple low-tier rewards were handed out for exploits targeting known vulnerabilities in QNAP TS-464, Wyze Cam v3, Synology BC500, and Canon imageCLASS MF753Cdw.

Overall, ZDI says, participating hackers have earned more than $800,000 in rewards on the first two days of the competition, which is set to conclude on Friday.

Related: Hackers Earn $400k on First Day at Pwn2Own Toronto 2023

Related: Over $1 Million Offered at New Pwn2Own Automotive Hacking Contest

Related: Hackers Earn $180,000 for ICS Exploits at Pwn2Own Miami 2023

https://www.securityweek.com/hackers-earn-350k-on-second-day-at-pwn2own-toronto-2023/


iLeakage Attack Exploits Safari to Steal Sensitive Data From Macs, iPhones

A team of academic researchers has disclosed the details of a new Spectre-style side-channel attack that exploits Safari to steal sensitive information from Macs, iPhones and iPads.

Described as a timerless speculative execution attack and named iLeakage, the new method can be used to induce Safari to render an arbitrary webpage and harvest information from that page. 

The attacker needs to lure the targeted Safari user to a malicious website, which then automatically opens the site from which they want to steal information. This is possible because the rendering process handles both the iLeakage attack website and the targeted site.

iLeakage was discovered by researchers from the University of Michigan, Georgia Institute of Technology, and Ruhr University Bochum, who this week published a paper detailing their findings. 

The experts showed how the attack could be used to obtain passwords and other sensitive information. They published video demos showing how the iLeakage attack can be leveraged to steal Instagram credentials autofilled by a password manager, email subject lines from a Gmail inbox, and a user’s YouTube watch history. 

The findings were reported to Apple in September 2022, but the tech giant has so far only made available a mitigation for Safari on macOS, and it’s not enabled by default, in addition to being unstable, according to the researchers.

Apple told SecurityWeek that the proof of concept developed by the researchers advances the company’s understanding of these types of threats. Apple plans on further addressing the issue in its next scheduled software release.

Advertisement. Scroll to continue reading.

On one hand, there is no evidence that iLeakage has been exploited in the wild and the attack is not easy to conduct. “[It] requires advanced knowledge of browser-based side-channel attacks and Safari’s implementation,” the researchers said.

On the other hand, the experts noted that the attack would be difficult to detect since it runs in Safari and does not leave any trace in system log files.

On macOS, iLeakage only impacts Safari because other browsers such as Edge, Firefox and Chrome use different JavaScript engines, the researchers said. However, on iOS the attack can work with other browsers as well because Chrome, Edge and Firefox are basically ‘wrappers on top of Safari’.

“iLeakage shows that the Spectre attack is still relevant and exploitable, even after nearly 6 years of effort to mitigate it since its discovery,” the researchers noted. 

Related: Nearly All Modern CPUs Leak Data to New Collide+Power Side-Channel Attack

Related: New GPU Side-Channel Attack Allows Malicious Websites to Steal Data

Related: New ‘Inception’ Side-Channel Attack Targets AMD Processors

https://www.securityweek.com/ileakage-attack-exploits-safari-to-steal-sensitive-data-from-macs-iphones/


Hackers Earn $400k on First Day at Pwn2Own Toronto 2023

The Pwn2Own Toronto 2023 hacking contest kicked off yesterday and participants successfully hacked NAS, printers, mobile phones, and other types of devices, earning a total of more than $400,000 on the first day.

The highest reward of the day went to team Orca of Sea Security, which executed a two-vulnerability exploit chain (out-of-bounds read and use-after-free) against the Sonos Era 100 speaker, earning $60,000.

The Pentest Limited team earned the second highest reward of the day, at $50,000, for an improper input validation exploit targeting the Samsung Galaxy S23 mobile phone.

The team also earned a $40,000 reward for a two-bug exploit chain (denial-of-service and server-side request forgery) leading to the compromise of Western Digital’s My Cloud Pro Series PR4100 network-attached storage (NAS) product.

Two other $40,000 rewards were earned for exploits targeting the Xiaomi 13 Pro mobile phone (team Viettel – single-bug exploit) and the QNAP TS-464 NAS device (team ECQ – a three-bug exploit chain involving a server-side request forgery and two injection flaws).

Vulnerabilities in the Synology BC500 IP camera were also exploited on the first day of the contest, with hackers earning roughly $50,000 for the exploits.

Additional exploits targeting the Xiaomi 13 Pro and the Samsung Galaxy S23 were demonstrated as well and earned the hacking teams more than $40,000 in rewards.

Advertisement. Scroll to continue reading.

The participating teams and individual hackers also pwned the Canon imageCLASS MF753Cdw and the Lexmark CX331adwe printers, earning more than $60,000 for their exploits.

According to ZDI, not all the exploits demonstrated on the first day of Pwn2Own Toronto 2023 were new, but participants still earned lower-tier rewards for their efforts.

The hacking competition will continue until Friday, with exploits to be demonstrated in the NAS devices, smart speakers, printers, mobile phones, and surveillance systems categories.

Missing from the contest are smart vehicles, which will be present at Pwn2Own Automotive, set to be hosted at the Automotive World conference, in January 2024, in Tokyo, Japan. It will be the first Pwn2Own competition dedicated to automotive.

Related: Mikrotik Belatedly Patches RouterOS Flaw Exploited at Pwn2Own

Related: VMware Patches Critical Vulnerability Disclosed at Pwn2Own Hacking Contest

Related: ZDI Discusses First Automotive Pwn2Own

https://www.securityweek.com/hackers-earn-400k-on-first-day-at-pwn2own-toronto-2023/