Censys Banks $75M for Attack Surface Management Technology
Michigan startup Censys has deposited $75 million in new funding as venture capital investors continue to bet big on technology to help organizations automate the finding and fixing of serious security problems.
Censys said the new financing included a $50 million Series C venture round and $25M in debt funding led by SVB Capital, Silicon Valley Bank.
The Series C was led by Decibel Partners, GV, Greylock and Intel Capital and included new investors Ascension Ventures and Four Rivers Partners.
Censys, based in Ann Arbor, competes with the likes of Randori, Bishop Fox, NCC Group, CyCognito and a wave of new startups hawking tools to help defenders with Internet-wide scans for exposed corporate assets.
The company claims it has built the most complete and accurate collection of global internet infrastructure data and provides technology to enrich the data with context to drive security decisions.
Since its last raise, a $35 million round led by Intel Capital, Censys said it recorded 130% annual recurring revenue (ARR) growth, a key metric used by subscription-based SaaS companies.
Censys counts prominent organizations like Google, NATO, the Swiss Armed Forces, and the U.S. Department of Homeland Security among its customer base.
Advertisement. Scroll to continue reading.
The attack surface management category has grown in importance to solve problems with vulnerability and patch management, especially for software and other assets that are exposed to the internet.
VMware vCenter Flaw So Critical, Patches Released for End-of-Life Products
Virtualization technology powerhouse VMware is calling urgent attention to a critical remote code execution flaw haunting its vCenter Server and VMware Cloud Foundation products.
The company said the vulnerability, tagged as CVE-2023-34048, allows a malicious hacker with network access to launch remote code execution exploits.
A critical-severity advisory from VMware described the bug as an out-of-bounds write issue in its implementation of the DCE/RPC protocol. The company flagged the bug with a CVSS severity score of 9.8/10.
Due to the critical nature of this issue, VMware also released patches for older, end-of-life products, including vCenter Server 6.7U3, 6.5U3, VCF 3.x, and vCenter Server 8.0U1. Asynchronous vCenter Server patches for VCF 5.x and 4.x are also available.
The bulletin also documents a second moderate-severity flaw — CVE-2023-34056 — that could lead to the partial disclosure of information.
A malicious actor with non-administrative privileges can exploit this to access unauthorized data, VMware said, urging vCenter Server and Cloud Foundation users to urgently apply the available updates.
In a separate advisory covering security problems in VMware Aria Operations for Logs, the company warned that exploit code for an authentication bypass flaw has been published online, adding to the urgency to apply available patches.
Advertisement. Scroll to continue reading.
“An unauthenticated, malicious actor can inject files into the operating system of an impacted appliance which can result in remote code execution,” VMWare warned.
The VMware Aria Operations for Logs vulnerability, tracked as CVE-2023-34051, carries a maximum CVSSv3 base score of 8.1/10.
Number of Cisco Devices Hacked via Zero-Day Remains High as Attackers Update Implant
The number of Cisco devices hacked through the exploitation of two new zero-day vulnerabilities remains very high, but recent scans appeared to show a significant drop due to the attackers updating their implant.
Unidentified hackers have been exploiting the Cisco IOS XE vulnerabilities tracked as CVE-2023-20198 and CVE-2023-20273 to create high-privileged accounts on affected devices and deploy a Lua-based backdoor implant that gives them complete control of the system.
Patches are now available for both vulnerabilities.
Shortly after Cisco disclosed the existence of the first flaw, the cybersecurity community started scanning the internet for compromised devices and quickly found that as many as 50,000 switches and routers had the malicious implant.
A few days later, the scans showed that the number of hacked devices dropped to 100, with some speculating that the attackers were trying to hide the implant. The security community warned that many devices were likely still compromised, even if they did not show up during scans.
Cisco and others have confirmed that the attackers have updated the implant and compromised devices cannot be identified any longer using the initial scan method.
However, NCC Group-owned security firm Fox-IT found a new fingerprinting method and identified nearly 38,000 Cisco devices still hosting the implant.
Advertisement. Scroll to continue reading.
Vulnerability intelligence firm VulnCheck has confirmed that thousands of devices are still under the attackers’ control.
Cisco has confirmed uncovering a new variant that “hinders identification of compromised systems”. This second version, which attackers started deploying on October 20, has roughly the same core functionality, but adds a preliminary check for a specific HTTP authorization header.
“The addition of the header check in the implant by the attackers is likely a reactive measure to prevent identification of compromised systems. This header check is primarily used to thwart compromise identification using a previous version of the curl command provided by Talos. Based on the information assessed to date, we believe the addition of the header check in the implant likely resulted in a recent sharp decline in visibility of public-facing infected systems,” Cisco explained.
The networking giant has shared indicators of compromise (IoCs) and instructions for checking whether a device has been hacked.
It’s worth noting that the implant deployed by the threat actor is not persistent — it gets removed if the device is rebooted — but the high-privileged account created through the exploitation of CVE-2023-20198 remains on the device even after it has been restarted.
This malicious campaign is reminiscent of the recent operation in which a China-linked APT targeted Barracuda ESG appliances. The attackers gained deep access to targeted systems, to the point where the vendor and the FBI urged victims to replace compromised devices.
The latest high-severity Citrix vulnerability under attack isn’t easy to fix
Getty Images
A critical vulnerability that hackers have exploited since August, which allows them to bypass multifactor authentication in Citrix networking hardware, has received a patch from the manufacturer. Unfortunately, applying it isn’t enough to protect affected systems.
The vulnerability, tracked as CVE-2023-4966 and carrying a severity rating of 9.8 out of a possible 10, resides in the NetScaler Application Delivery Controller and NetScaler Gateway, which provide load balancing and single sign-on in enterprise networks, respectively. Stemming from a flaw in a currently unknown function, the information-disclosure vulnerability can be exploited so hackers can intercept encrypted communications passing between devices. The vulnerability can be exploited remotely and with no human action required, even when attackers have no system privileges on a vulnerable system.
Citrix released a patch for the vulnerability last week, along with an advisory that provided few details. On Wednesday, researchers from security firm Mandiant said that the vulnerability has been under active exploitation since August, possibly for espionage against professional services, technology, and government organizations. Mandiant warned that patching the vulnerability wasn’t sufficient to lock down affected networks because any sessions hijacked before the security update would persist afterward.
Successful exploitation could result in the ability to hijack existing authenticated sessions, therefore bypassing multi factor authentication or other strong authentication requirements. These sessions may persist after the update to mitigate CVE-2023-4966 has been deployed. Additionally, we have observed session hijacking where session data was stolen prior to the patch deployment, and subsequently used by a threat actor.
The authenticated session hijacking could then result in further downstream access based upon the permissions and scope of access that the identity or session was permitted. A threat actor could utilize this method to harvest additional credentials, laterally pivot, and gain access to additional resources within an environment.
Mandiant provided security guidance that goes well beyond the advice Citrix provided. Specifically:
• Isolate NetScaler ADC and Gateway appliances for testing and preparation of patch deployment.
Note: If the vulnerable appliances cannot be prioritized for patching, Mandiant recommends that the appliances have ingress IP address restrictions enforced to limit the exposure and attack surface until the necessary patches have been applied.
• Upgrade vulnerable NetScaler ADC and Gateway appliances to the latest firmware versions, which mitigate the vulnerability.
• Post upgrading, terminate all active and persistent sessions (per appliance).
– Connect to the NetScaler appliance using the CLI.
• To terminate all active sessions, run the following command: kill aaa session -all
• To clear persistent sessions across NetScaler load balancers, run the following command (where is the name of the virtual server / appliance): clear lb persistentSessions
• To clear existing ICA sessions, run the following command: kill icaconnection -all
• Credential Rotation
– Due to the lack of available log records or other artifacts of exploitation activity, as a precaution, organizations should consider rotating credentials for identities that were provisioned for accessing resources via a vulnerable NetScaler ADC or Gateway appliance.
– If there is evidence of suspicious activity or lateral movement within an environment, organizations should prioritize credential rotation for a larger scope of identities if single factor authentication (SFA) remote access is allowed for any resources from the Internet.
• If web shells or backdoors are identified on NetScaler appliances, Mandiant recommends rebuilding the appliances using a clean-source image, including the latest firmware.
Note: If a restoration of an appliance is required using a backup image, the backup configuration should be reviewed to ensure that there is no evidence of backdoors.
• If possible, reduce the external attack exposure and attack surface of NetScaler appliances by restricting ingress access to only trusted or predefined source IP address ranges.
The advice is warranted given the track record from previous exploitation of critical Citrix vulnerabilities. For example, Citrix disclosed and released a patch for a separate 9.8 vulnerability on July 18. Three days later, according to Internet scans by security organization Shadowserver, more than 18,000 instances had yet to apply the critical update.
By then, according to the US Cybersecurity and Infrastructure Security Administration, the vulnerability was already under active exploit. In the subsequent weeks, Shadowserver and security firms F-Secure and IBM Security Intelligence tracked thousands of exploitations used for credential theft.
What Mandiant’s guidance amounts to is this: If your organization uses either NetScaler ADC or NetScaler Gateway that’s on-premises, you should assume it has been hacked and follow the guidance provided. And yes, that includes patching first.
https://arstechnica.com/?p=1977305
Number of Cisco Devices Hacked via Unpatched Vulnerability Increases to 40,000
The number of Cisco devices hacked through the exploitation of an unpatched IOS XE vulnerability has reached approximately 40,000, according to multiple cybersecurity firms.
The exploited vulnerability is CVE-2023-20198, a critical flaw affecting the IOS XE web interface that can be exploited by remote, unauthenticated attackers for privilege escalation.
Cisco has yet to release patches and the company warned that the vulnerability has been exploited as a zero-day since at least mid-September.
CVE-2023-20198 allows threat actors to create high-privileged accounts on targeted devices and take complete control of the system. In some cases, attackers have been observed delivering an implant that enables them to execute arbitrary commands.
Cisco said in some cases the implants were delivered via an older flaw tracked as CVE-2021-1435, but a previously unknown vulnerability may have also been exploited because the implant was also spotted on systems patched against CVE-2021-1435.
Vulnerability intelligence company VulnCheck conducted an internet scan shortly after the zero-day’s existence came to light and found 10,000 compromised switches and routers, but noted that the number would likely increase as its scanning had been ongoing.
While VulnCheck has yet to provide an update, a scan conducted by the internet search engine Censys on October 17 showed 67,000 internet-exposed IOS XE web interfaces, including more than 34,000 hosts that appeared to have been backdoored. Another scan conducted by Censys the next day showed that the number of hacked systems increased to nearly 42,000.
Advertisement. Scroll to continue reading.
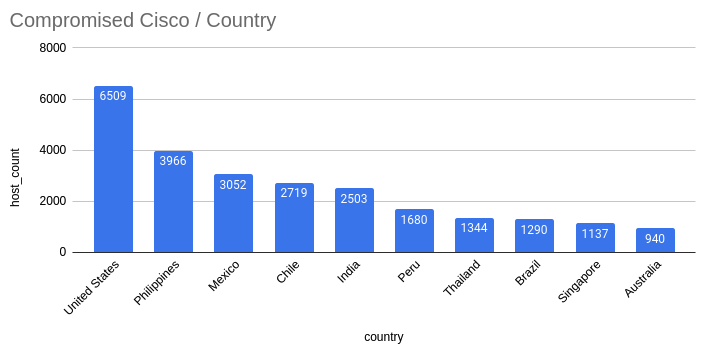
A majority of the compromised Cisco devices appear to be in the United States, followed by the Philippines and Latin America. India, Thailand, Singapore and Australia also have a significant number of infections.
LeakIX, which scans the internet for vulnerable systems, initially reported seeing the malicious implant on roughly 30,000 Cisco devices, but its latest scan detected an additional 10,000 compromised systems.
Threat intelligence company GreyNoise has been using its honeypots to track attack attempts and as of October 19 it has seen attacks originating from 230 unique IP addresses.
Three Months After Patch, Gov-Backed Actors Exploiting WinRAR Flaw
Malware hunters in Google’s Threat Analysis Group (TAG) say government-backed hacking groups from different countries are feasting on a well-documented security flaw in the popular WinRAR file archiving utility more than three months after patches were released.
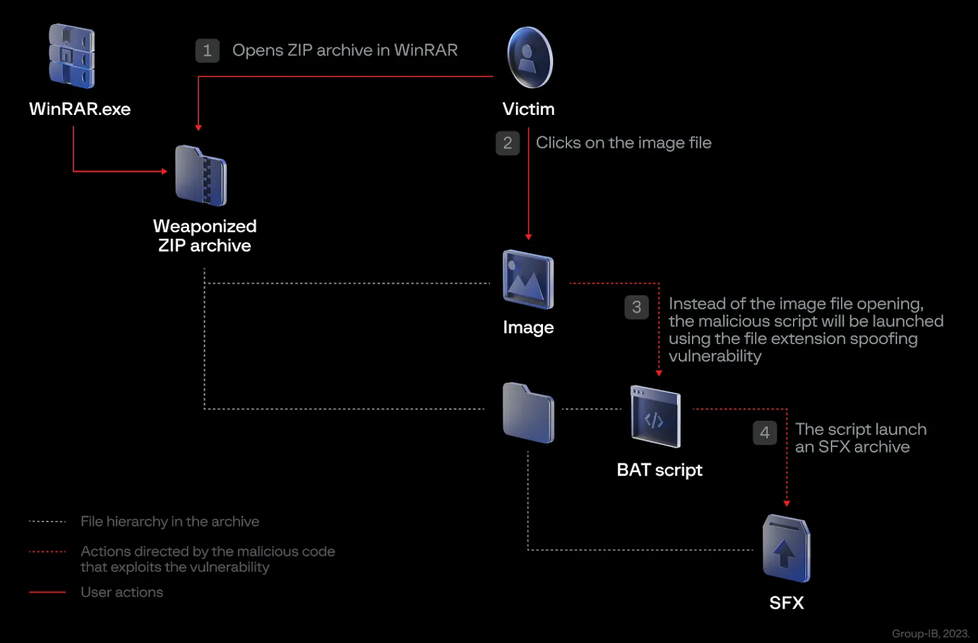
The WinRAR code execution vulnerability, tracked as CVE-2023-38831, was fixed in July after zero-day exploitation was detected but now, three months later, Google says APT groups linked to Russia and China are still using the exploit with success.
“Cybercrime groups began exploiting the vulnerability in early 2023, when the bug was still unknown to defenders. A patch is now available, but many users still seem to be vulnerable,” Google’s Kate Morgan said in a note documenting the APT discoveries. “After a vulnerability has been patched, malicious actors will continue to rely on n-days and use slow patching rates to their advantage.”
Morgan said the flaw, which allows attackers to execute arbitrary code when a user attempts to view a benign file (such as an ordinary PNG file) within a ZIP archive, has been known since at least April 2023 and immediately attracted the interest of threat actors.
“Hours after the blog post [about zero-day exploitation] was released, proof of concepts and exploit generators were uploaded to public GitHub repositories. Shortly after that, TAG began to observe testing activity from both financially motivated and APT actors experimenting with CVE-2023-38831,” Morgan added.
In one case, Google TAG detected the Russia-linked Sandworm delivering decoy PDF documents and malicious ZIP files exploiting the WinRAR bug. Sandworm, aligned with Russian Armed Forces’ Main Directorate of the General Staff (GRU) Unit, used the exploit to deliver a commodity infostealer that is able to collect and exfiltrate browser credentials and session information from infected machines.
Morgan documented another incident where APT28, another hacking team linked to Russian GRU, used a free hosting provider to serve CVE-2023-38831 to target users in Ukraine.
Advertisement. Scroll to continue reading.
Google said it also caught government-backed groups linked to China launching WinRAR exploits in targeted attacks against users in Papua New Guinea.
“The widespread exploitation of the WinRAR bug highlights that exploits for known vulnerabilities can be highly effective, despite a patch being available. Even the most sophisticated attackers will only do what is necessary to accomplish their goals,” Morgan warned.
Software security defects in the WinRAR tool are constantly being targeted by cybercriminals and APT groups. SecurityWeek has reported on multiple WinRAR exploitation incidents recently, including usage by financially motivated hackers against traders and .gov-backed advanced threat actors.
US Gov Expects Widespread Exploitation of Atlassian Confluence Vulnerability
US cybersecurity agency CISA, the FBI, and the Multi-State Information Sharing and Analysis Center (MS-ISAC) warn organizations of potential widespread exploitation of a recent zero-day vulnerability in Atlassian Confluence Data Center and Server.
Remotely exploitable without authentication, the flaw is described as a broken access control issue leading to privilege escalation. The issue impacts on-premises Confluence instances only.
“This recently disclosed vulnerability affects certain versions of Atlassian Confluence Data Center and Server, enabling malicious cyber threat actors to obtain initial access to Confluence instances by creating unauthorized Confluence administrator accounts,” CISA, FBI, and MS-ISAC note in an advisory (PDF).
Because it allows threat actors to modify critical configuration settings, the flaw may be used for more malicious actions than the creation of administrative accounts, the advisory reads.
“Threat actors can change the Confluence server’s configuration to indicate the setup is not complete and use the /setup/setupadministrator.action endpoint to create a new administrator user. The vulnerability is triggered via a request on the unauthenticated /server-info.action endpoint,” the three agencies say.
CISA added CVE-2023-22515 to its Known Exploited Vulnerabilities catalog on October 5 and warns that, following the publication of proof-of-concept (PoC) exploit code, multiple threat actors have started targeting the flaw in attacks.
Advertisement. Scroll to continue reading.
“Due to the ease of exploitation, CISA, FBI, and MS-ISAC expect to see widespread exploitation of unpatched Confluence instances in government and private networks,” the advisory continues.
The vulnerability impacts Confluence Data Center and Server versions 8.0.0 to 8.5.1 and has been addressed with the release of versions 8.3.3, 8.4.3, and 8.5.2 of the product.
Organizations with internet-accessible Confluence Data Center and Server instances are advised to update to a patched release as soon as possible. They should also consider restricting network access until the updates are applied.
In their advisory, CISA, FBI, and MS-ISAC have included details on the exploitation of CVE-2023-22515, as well as indicators-of-compromise (IoCs) to help organizations hunt for malicious activity associated with the bug’s exploitation.
“CISA, FBI, and MS-ISAC strongly encourage network administrators to immediately apply the upgrades provided by Atlassian. CISA, FBI, and MS-ISAC also encourage organizations to hunt for malicious activity on their networks using the detection signatures and indicators of compromise (IOCs),” the US gov agencies note.
Cisco Devices Hacked via IOS XE Zero-Day Vulnerability
Cisco is warning customers that a new zero-day vulnerability impacting the company’s IOS XE software is being exploited to hack devices.
The critical vulnerability is tracked as CVE-2023-20198 and it has been described as a privilege escalation issue impacting the IOS XE web user interface, which comes with the default image. A remote, unauthenticated attacker can exploit the vulnerability to create an account that has the highest privileges — level 15 access — and use it to take control of the device.
“With this level of access, an attacker can modify network routing rules as well as open ports for access to attacker controlled servers for data exfiltration,” warned Scott Caveza, staff research engineer at Tenable. “When the attacker has this level of control and makes an administrative account with an innocuous name, it’s possible their activity could go undetected for quite some time.”
The vulnerability can be exploited from the network or directly from the internet if the targeted device is exposed to the web.
In a blog post published on Monday, Cisco’s Talos unit revealed that the company became aware of attacks exploiting CVE-2023-20198 on September 28, when its Technical Assistance Center (TAC) investigated unusual behavior on a customer’s device.
Further analysis showed that the malicious activity, which involved the creation of a new user account named ‘cisco_tac_admin’, started as early as September 18.
This activity appeared to end on October 1, but Cisco again started seeing malicious activity — presumably conducted by the same threat actor — on October 12.
Advertisement. Scroll to continue reading.
While the September activity did not involve other actions beyond the creation of a new account, in October the hackers also deployed an implant. This implant, consisting of a configuration file, allows the attacker to execute arbitrary commands at system or IOS level.
For interaction with the implant, a new web server endpoint needs to be created, and the implant is only activated if this web server is restarted, which did not happen in all cases observed by Cisco.
The threat actor delivered the implant by exploiting CVE-2021-1435, an IOS XE command injection vulnerability patched by Cisco in March 2021. However, the company has also seen the implant being installed on devices patched against CVE-2021-1435 and the delivery mechanism in this case remains unknown for the time being.
The networking giant also noted that the implant is not persistent — it’s removed when the device is rebooted — but the accounts created by the attackers remain even after the system has been restarted.
“Both [activity] clusters appeared close together, with the October activity appearing to build off the September activity. The first cluster was possibly the actor’s initial attempt and testing their code, while the October activity seems to show the actor expanding their operation to include establishing persistent access via deployment of the implant,” Cisco said.
The company’s blog post does not say who may be behind these attacks.
Cisco is working on a patch for CVE-2023-20198. Until it becomes available, the vendor recommends that customers disable the HTTP Server feature on their internet-facing systems. The company has also shared a list of indicators of compromise (IoCs) that organizations can use to check whether their devices have been hacked.
The US cybersecurity agency CISA has added CVE-2023-20198 to its Known Exploited Vulnerabilities Catalog, instructing government organizations to deploy mitigations by October 20.
WordPress Websites Hacked via Royal Elementor Plugin Zero-Day
Security researchers are warning of a critical-severity vulnerability in the Royal Elementor Addons and Templates WordPress plugin that has been exploited as a zero-day for more than a month.
Developed by WP Royal, the plugin helps domain admins build their websites without any coding experience. Royal Elementor has more than 200,000 active installations on the WordPress marketplace.
The exploited bug, tracked as CVE-2023-5360 (CVSS score of 9.8), is described as an insufficient file type validation in the plugin’s upload function, allowing unauthenticated attackers to upload arbitrary files to vulnerable sites, leading to remote code execution.
The flaw impacts all Royal Elementor versions prior to 1.3.79 and, according to WordPress security firm Defiant, has been exploited in malicious attacks since at least August 30.
To date, the security firm has seen more than 46,000 attacks attempting to exploit this vulnerability, with an increase in activity observed on October 3.
Most attacks, Defiant says, came from three different IP addresses and were aimed at deploying specific files on the target sites, to create a malicious administrator account.
According to Automattic’s WPScan team, which identified and reported the vulnerability, the attackers were seen deploying at least one malicious file into the /wpr-addons/forms/ directory.
Advertisement. Scroll to continue reading.
The plugin, Automattic explains, relied on a simple extension validation to ensure that only certain file types could be uploaded, but which allowed unauthenticated users to manipulate the list of allowed extensions.
“Upon investigation we found that wp_unique_filename WordPress function performs file name and extensions sanitization and, when combined with the file_validity function, would enable bad actors to manipulate the input and bypass the checks,” Automattic notes.
Site admins should check the /wpr-addons/forms/ directory for the presence of malicious PHP files, including one file creating a user account named ‘wordpress_administrator’.
Automattic also observed that threat actors have been exploiting the vulnerability to upload malware to the compromised websites.
Administrators and site owners are advised to update to Royal Elementor version 1.3.79, which patches the vulnerability. The patched version has been available since October 6.
Signal Pours Cold Water on Zero-Day Exploit Rumors
Privacy-focused messaging firm Signal is pouring cold water on widespread rumors of a zero-day exploit in its popular encrypted chat app.
“We have seen the vague viral reports alleging a Signal 0-day vulnerability. After responsible investigation *we have no evidence that suggests this vulnerability is real* nor has any additional info been shared via our official reporting channels,” Signal said late Sunday night.
Rumors of a Signal zero-day started circulating over the weekend with what appears to be a copy-pasted warning the “generate link preview” feature could be exploited to take full control of devices.
“To close the vulnerability, have everyone go to settings under your profile in signal> chats> deselect “generate link preview”. Also make sure your signal app is up to date,” according to the cryptic note.
The original source for the zero-day warning is unknown but Signal said it checked with its contacts across the US Government, since the copy-paste report claimed USG as a source. “Those we spoke to have no info suggesting this is a valid claim,” the company said on X, the social media site previously known as Twitter.
The feature, on by default on some Signal installations, displays a short summary and preview image of a URL being sent but experts have long warned that it provides attack surface to leak IP addresses, expose links sent in end-to-end encrypted chats, and unnecessarily downloading gigabytes of data quietly in the background.
Advertisement. Scroll to continue reading.
Interestingly, Apple’s optional LockDown Mode disables the iMessage link preview feature in response to malicious targeting by surveillance spyware vendors.