Multiple Security Issues Identified in Peloton Fitness Equipment

Internet-connected Peloton fitness equipment is plagued with numerous security issues that could allow attackers to obtain device information or deploy malware, cybersecurity firm Check Point reports.

An analysis of the software running on the Peloton Treadmill has revealed exposure to security risks associated with Android devices that are not updated to the most recent platform iterations, as well as risks posed by attackers with physical access to the device.

The treadmill, Check Point explains, runs Android 10, which does not contain patches for more than 1,000 vulnerabilities that have been addressed in the operating system over the past three years.

Furthermore, the device was found to have USB debugging enabled, meaning that an attacker with physical access could retrieve a list of all installed packages and could also obtain shell access, compromising the treadmill completely.

“Shell is fully accessible, which means that the application can be fetched for further security analysis. Cybercriminals could exploit vulnerabilities on apps and take advantage of the embedded binaries in /shell to make lateral movements,” Check Point explains.

An attacker could use specific commands to exfiltrate data from the treadmill, or they could exploit the existing applications, which are compiled using different SDK versions. Applications can also be fetched for reverse engineering and for extracting secrets.

According to Check Point, some applications on the device incorporate rooting detection mechanisms, but an attacker could use certain techniques to identify further vulnerabilities in the applications at runtime.

Advertisement. Scroll to continue reading.

Additionally, the cybersecurity firm identified hardcoded sensitive information on the device, such as a license key for a text-to-speech voice service. The service could be abused for denial-of-service (DoS), Check Point says.

Certain unprotected services were also identified on the treadmill, potentially allowing malicious applications to escalate privileges and gain access to sensitive data, or to abuse broadcast receivers and send the device into an infinite loop, preventing updates.

The security firm also discovered “differences in the signature scheme of the installed apps”, which could potentially expose the device to malicious attacks.

“The treadmill operating system includes numerous standard APIs that can be exploited to execute Android code, allowing attackers to carry out nefarious actions from a networking perspective and take advantage of the device’s always-on nature. Moreover, the presence of a webcam and microphone makes the treadmill vulnerable to eavesdropping attacks if a malware is installed,” Check Point says.

The cybersecurity firm was able to sideload a mobile remote access tool (MRAT) on the device, gaining full access to the treadmill’s functionality, including audio recording, taking photos, accessing geolocation, and abusing the network stack.

According to Check Point, the compromised device also provided “full access to the local area network”, which could be leveraged for additional malicious activities.

Using social engineering, Check Point notes, an attacker could gain access to a high-profile individual’s treadmill, either at their household or office, and could then install a backdoor on the device, thus gaining access to the network.

“With this access, the attacker can carry out lateral movement, steal personally identifiable information, launch ransomware attacks, access corporate credentials, or perform a denial-of-service attack. Essentially, once the attacker has remote control over the treadmill, they have a significant advantage and can escalate their attack surface,” Check Point notes.

After being informed of these issues, Peloton told Check Point that “they meet expected security measures for Android-based devices,” pointing out that physical access is required for exploitation.

Related: Perimeter81 Vulnerability Disclosed After Botched Disclosure Process

Related: Fortinet Patches Critical FortiOS Vulnerability Leading to Remote Code Execution

Related: Critical Vulnerability Can Allow Takeover of Mastodon Servers

https://www.securityweek.com/multiple-security-issues-identified-in-peloton-workout-equipment/


Two New Vulnerabilities Could Affect 40% of Ubuntu Cloud Workloads

Researchers at cloud security firm Wiz have discovered two easily exploitable privilege escalation vulnerabilities in Ubuntu’s OverlayFS module affecting 40% of Ubuntu cloud workloads.

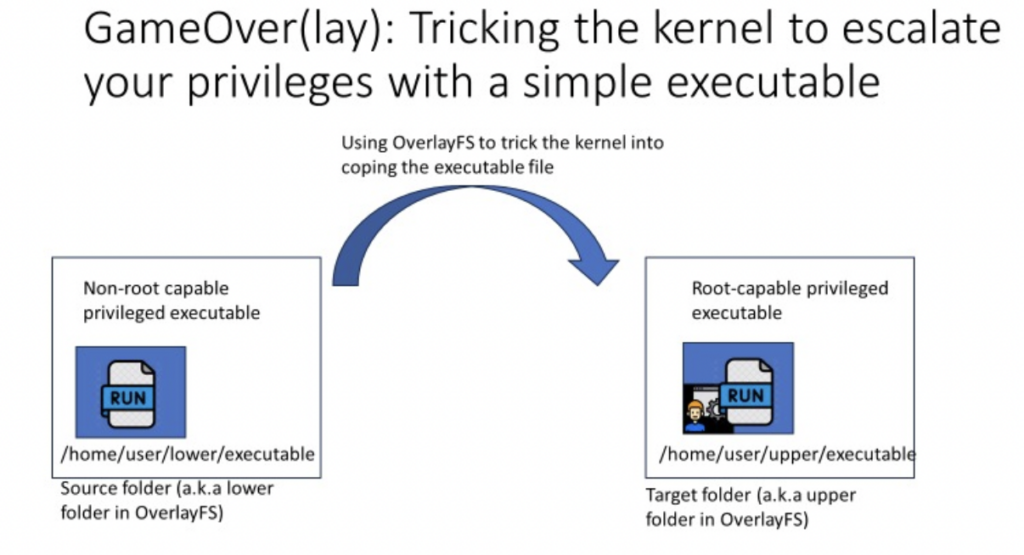
OverlayFS is a union filesystem that allows one filesystem to overlay another, enabling file modifications without changing the base. It allows users to copy files from the base to the upper layer and perform operations and maintain metadata that should not be possible in Linux. 

The Wiz researchers discovered a flaw in the Ubuntu-specific OverlayFS module that allows specialized executables to escalate privileges to ‘root’ on the affected machine. It is possible to trick the Ubuntu Kernel into copying this file to a different location, giving anyone who executes it root-like privileges. Wiz found two vulnerabilities which, together, the firm describes as GameOver(lay).

The flaw is similar in operation to a Linux Kernel vulnerability (CVE-2021-3493) discovered in 2021. However, Ubuntu had earlier modified its own kernel in 2018 in a manner that allowed subsequent mitigations to the General kernel to not fully remove the basic flaw from Ubuntu’s OverlayFS module.

“Subtle changes in the Linux kernel introduced by Ubuntu many years ago have unforeseen implications,” explains Ami Luttwak, co-founder and CTO at Wiz. “We found two privilege escalation vulnerabilities caused by these changes and who knows how many other vulnerabilities are still lurking in the shadows of the Linux kernel spaghetti?”

The Wiz researchers discovered two vulnerabilities in the Ubuntu OverlayFS module: CVE-2023-2640 and CVE-2023-32629 (together dubbed ‘GameOver(lay)’).

CVE-2023-2640 is enabled because the Ubuntu OverlayFS module does not convert file security capabilities before files are copied. As a result, an unprivileged user can create a new directory structure and enter a new user namespace with administrative-like capabilities. They can then mount and OverlayFS mount, ultimately creating a file with capabilities applicable to the init user namespace and effectively escalating the user’s privileges to root. 

“Successful exploitation of CVE-2023-2640,” say the researchers, “therefore results in the generation of a ‘capable’ file in the `upperdir` directory that grants root-equivalent capabilities to anyone who executes it.”

Advertisement. Scroll to continue reading.

CVE-2023-32629 is similar to CVE-2023-2640, but affects slightly different kernel versions, and exploitation results from a different code flow. The result is the same: “The file has capabilities that are applicable to the init user namespace,” say the researchers, “which effectively escalates the user’s privileges to root.”

These are not the first vulnerabilities found within OverlayFS. Earlier examples include CVE-2016-1576, CVE-2021-3847, CVE-2021-3493, and CVE-2023-0386. The Wiz researchers note that CVE-2021-3493 is so similar to one of the GameOver(lay) vulnerabilities that “its publicly available PoC can currently be used to exploit that vulnerability as is.”

Ubuntu fixed the vulnerabilities on July 24, 2023, and users are urged to update their kernels.

New York-based Wiz was founded in January 2020 by Ami Luttwak (CTO), Assaf Rappaport (CEO), Roy Reznik (VP R&D), and Yinon Costica (VP of product). Its latest funding round (Series D, February 2023) raised $300 million, bringing the total raised to date to $900 million and valuing the company at $10 billion.

Related: Wiz Says 62% of AWS Environments Exposed to Zenbleed Exploitation

Related: Orca Sues Wiz Over Alleged Cloud Security Patent Violations

Related: CISA Tells Organizations to Patch Linux Kernel Vulnerability Exploited by Malware

Related: Canonical Patches Privilege Escalation Vulnerability in Ubuntu

https://www.securityweek.com/two-new-vulnerabilities-could-affect-40-of-ubuntu-cloud-workloads/


Wiz Says 62% of AWS Environments Exposed to Zenbleed Exploitation

Researchers at cloud security startup Wiz are reporting that a whopping 62 percent of AWS environments may be exposed to the newly documented Zenbleed information leak vulnerability in AMD Zen 2 processors.

In a research note posted Wednesday, Wiz calculated that more than 60 percent of AWS environments are running EC2 instances with Zen 2 CPUs and may therefore be affected by the use-after-free memory corruption bug.

Zenbleed, discovered and documented by Project Zero’s Tavis Ormandy, impacts all Zen 2 processors, including Ryzen 3000 (PRO and Threadripper), 4000 (PRO), 5000, 7020, and Epyc (Rome). The issue can be exploited by malicious hackers to steal sensitive data, such as passwords and encryption keys.  It is tracked as CVE-2023-20593.

As previously reported, AMD has started releasing microcode updates and the vendor has also advised customers to apply AGESA firmware updates. For some products, the updates are expected to become available in the last quarter of 2023. 

Wiz researchers are amplifying the warnings, noting that the flaw can be exploited by an attacker with unprivileged access to an affected machine to escalate privileges or gain access to data.

The company said it combed through its data and found that a vast majority of cloud environments are running the vulnerable Epyc server (“Rome”), which is a CPU designed for data centers. 

Wiz is also noting that patches are available from Google Cloud Platform (GCP) while fixes from AWS are expected to be released once testing is complete.

Advertisement. Scroll to continue reading.

Related: AMD CPU Flaw ‘Zenbleed’ Can Expose Sensitive Information

Related: Intel, AMD Address Multiple Bugs With Patch Tuesday Bulletins

Related: Chipmaker Patch Tuesday: Intel, AMD Address Over 100 Vulns

Related: AMD Processors Expose Sensitive Data in ‘SQUIP’ Attack

https://www.securityweek.com/wiz-says-62-of-aws-environments-exposed-to-zenbleed-exploitation/


Microsoft Message Queuing Vulnerabilities Allow Remote Code Execution, DoS Attacks

Cybersecurity firm Fortinet has published details on three critical- and high-severity vulnerabilities patched recently in the Microsoft Message Queuing (MSMQ) service.

Two of these flaws, tracked as CVE-2023-21554 and CVE-2023-28302, could lead to remote code execution (RCE) and denial-of-service (DoS) and were addressed by Microsoft with its April 2023 Patch Tuesday updates. No CVE identifier has been provided for the third issue.

A proprietary messaging protocol, MSMQ supports communication between applications running on separate systems. It places messages that did not reach their destination in a queue and resends them as soon as the destination becomes reachable.

MSMQ runs as a standalone service, exposes TCP/IP and RPC ports to enable interaction over the network, and is implemented in both user-mode and kernel-mode components. Fortinet has identified three vulnerabilities that can be exploited over TCP port 1801.

The most severe of these issues is CVE-2023-21554 (CVSS score of 9.8), an out-of-bounds write flaw caused by the message header parser failing to validate a message header that has an arbitrary size.

“Some message headers […] allow attackers to specify an arbitrary size/length that is not properly sanitized,” Fortinet explains.

Message headers are organized sequentially and the parser adjusts the pointer based on the defined data structures for each header.

Advertisement. Scroll to continue reading.

“Since some message headers are not being validated, the pointer can be adjusted to point to an arbitrary location, an invalid address in this context, and potentially cause memory corruption when the pointer to the message header is dereferenced in the later part of the code,” Fortinet explains.

Leading to DoS, CVE-2023-28302 (CVSS score of 7.5) is described as an out-of-bounds read bug that impacts the same message header parser routine. The issue is that, while most of the message header is scrutinized, the data structure for the header is not validated.

The third bug is an out-of-bounds write flaw that occurs when data is dereferenced without any sanity check in specific functions. A malformed data structure can trigger the flaw in MSMQ’s kernel-mode component, the cybersecurity firm says.

Microsoft has released patches for all three vulnerabilities – and for CVE-2023-21769, another high-severity DoS flaw in MSMQ – in April and July 2023. Users are advised to install the available security updates as soon as possible.

Related: Microsoft Patches Critical Windows Vulns, Warns of Code Execution Risks

Related: Microsoft Patch Tuesday: 40 Vulnerabilities, 2 Zero-Days

Related: Microsoft Patch Tuesday: 97 Windows Vulns, 1 Exploited Zero-Day

https://www.securityweek.com/microsoft-message-queuing-vulnerabilities-allow-remote-code-execution-dos-attacks/


Code Execution Vulnerability Impacts 900k MikroTik Devices

More than 900,000 MikroTik devices are impacted by a RouterOS vulnerability leading to arbitrary code execution, vulnerability intelligence provider VulnCheck reports.

Tracked as CVE-2023-30799 (CVSS score of 9.1), the issue is described as a privilege escalation bug impacting RouterOS versions before 6.49.7 and RouterOS long-term versions through 6.48.6.

“A remote and authenticated attacker can escalate privileges from admin to super-admin on the Winbox or HTTP interface. The attacker can abuse this vulnerability to execute arbitrary code on the system,” a NIST advisory reads.

The vulnerability was initially disclosed in June 2022, at the REcon conference, but no CVE identifier was assigned to it. Proof-of-concept (PoC) code demonstrating how a root shell can be obtained on a RouterOS x86 virtual machine was also published at the time.

MikroTik patched the bug in RouterOS stable 6.49.7 in October 2022, without detailing it, VulnCheck says. Patches were released for the RouterOS long-term version as well.

According to VulnCheck, a Shodan search shows that there are many potentially vulnerable devices.

“In total, Shodan indexes approximately 500,000 and 900,000 RouterOS systems vulnerable to CVE-2023-30799 via their web and/or Winbox interfaces respectively,” VulnCheck notes.

Advertisement. Scroll to continue reading.

The issue, the firm says, should be taken seriously because it is rather easy to obtain RouterOS credentials and exploit this vulnerability to escalate privileges from admin to ‘super-admin’ – which provides the attacker with access to an arbitrary function call.

On the one hand, attackers can use default RouterOS credentials to compromise devices. On the other hand, they can use various tools to brute-force RouterOS devices, including API, web, and Winbox brute forcing tools (Shodan shows roughly 400,000 devices exposing the RouterOS API).

RouterOS ships with a default ‘admin’ user that is often not removed from devices and which is protected with a default empty string. Attackers can target an observable response discrepancy bug in the Winbox authentication scheme to determine the existence of the default account.

VulnCheck verified 5,500 of the hosts identified via Shodan and found that 60% contained the default admin user account.

“It wasn’t until RouterOS 6.49 (October 2021) that RouterOS started prompting administrators to update blank passwords. Even when an administrator has set a new password, RouterOS doesn’t enforce any restrictions. Administrators are free to set any password they choose, no matter how simple,” VulnCheck notes.

The vulnerability went under the radar because the initial exploit only targeted RouterOS x86 virtual machines. However, exploits that target RouterOS hardware have been released as well and administrators are urged to patch devices as soon as possible.

“Under normal circumstances, we’d say detection of exploitation is a good first step to protecting your systems. Unfortunately, detection is nearly impossible. The RouterOS web and Winbox interfaces implement custom encryption schemes that neither Snort or Suricata can decrypt and inspect. Once an attacker is established on the device, they can easily make themselves invisible to the RouterOS UI,” VulnCheck notes.

Related: Mikrotik Belatedly Patches RouterOS Flaw Exploited at Pwn2Own

Related: Microsoft Releases Open Source Tool for Securing MikroTik Routers

Related: MikroTik Confirms Mēris Botnet Targets Routers Compromised Years Ago

https://www.securityweek.com/code-execution-vulnerability-impacts-900k-mikrotik-devices/


TETRA Radio Standard Vulnerabilities Can Expose Military Comms, Industrial Systems

Five vulnerabilities, two deemed to be critical, have been found in the Terrestrial Trunked Radio (TETRA) standard. 

TETRA is the most widely used police radio communication system outside of the US. It is used by fire and ambulance services, transportation agencies, utilities, and military, border control and customs agencies in more than 100 nations globally — as well as the UN and NATO.

The vulnerabilities were discovered by cybersecurity firm Midnight Blue (Amsterdam, Netherlands) with funding from NLnet as part of the EU NGI0 PET fund. Midnight Blue reverse-engineered the proprietary TETRA Authentication Algorithm (TAA1) and TETRA Encryption Algorithm (TEA) and analyzed them for the first time. In this process they discovered a series of vulnerabilities that they call TETRA:BURST.

The firm has announced basic details but will be providing full technical details during upcoming security conferences, including Black Hat and DEF CON in August. “We have spent over two and a half years on our TETRA research, including a coordinated disclosure process that lasted over one and a half years. We will fully disclose our research results and present our work at various conferences throughout the year,” say the researchers.

The five vulnerabilities are:

  • CVE-2022-24401, critical: allows decryption oracle attacks leading to a loss of confidentiality and authenticity.
  • CVE-2022-24402, critical: a backdoor in the TEA1 encryption algorithm allows trivial brute-forcing on keys leading to a loss of confidentiality and authenticity.
  • CVE-2022-24404, high: lack of authentication on AIE allowing malleability attacks leading to a loss of authentication.
  • CVE-2022-24403, high: weak obfuscation on radio identities allowing user deanonymization.
  • CVE-2022-24400, high: a flaw in the authentication algorithm can lead to a loss of authenticity and a partial loss of confidentiality.

Midnight Blue calls out the first and third vulnerabilities as of immediate concern. “This could allow high-end adversaries to intercept or manipulate law enforcement and military radio communications.”

The company also raised concerns over the TEA1 encryption backdoor, which could pose a serious risk to critical infrastructure operators and their industrial control systems (ICS). 

“By exploiting this issue, attackers can not only intercept radio communications of private security services at harbors, airports, and railways but can also inject data traffic used for monitoring and control of industrial equipment. As an example, electrical substations can wrap telecontrol protocols in encrypted TETRA to have SCADA systems communicate with Remote Terminal Units (RTUs) over a Wide-area Network (WAN). Decrypting this traffic and injecting malicious traffic allows an attacker to potentially perform dangerous actions such as opening circuit breakers in electrical substations or manipulate railway signaling messages,” Midnight Blue explains.

Patches and mitigations (such as the use of E2EE) are specified.

Advertisement. Scroll to continue reading.

William Wright, CEO at Closed Door Security, commented, “This is an extremely concerning discovery from security researchers. No system, whether critical or trivial, should ever be marketed or deployed without continuous and proactive security testing.” It seems that too much reliance for security was placed on the proprietary nature of the TETRA standard.

He points out that since criminals are constantly looking for weaknesses in systems they can exploit to gain access to data, there is a possibility these bugs have already been discovered and used in the wild. “Furthermore,” he adds, “given the types of industries that rely on TETRA radio communications, this could have given adversaries access to sensitive information that could be extremely dangerous in their hands.”

Related: Metasploit’s New RFTransceiver Finds Security Flaws in IoT Radio Communications

Related: Cyprus Arrests Three in ‘Israeli Spy Van’ Probe

Related: Cyber Insights 2023 | The Geopolitical Effect

https://www.securityweek.com/tetra-radio-standard-vulnerabilities-can-expose-military-comms-industrial-systems/


AMD CPU Vulnerability ‘Zenbleed’ Can Expose Sensitive Information

AMD has started releasing microcode patches to address a Zen 2 processor vulnerability that can allow an attacker to access sensitive information.

The flaw, dubbed Zenbleed and officially tracked as CVE-2023-20593, was discovered by Google researchers as part of a new CPU research project and reported to AMD on May 15.

Google Information Security’s Tavis Ormandy, who led the research, announced the findings and the availability of technical details and a proof-of-concept (PoC) exploit on Monday. The issue was discovered through fuzzing.

“It took a bit of work, but I found a variant that can leak about 30 kb per core, per second,” Ormandy explained. “This is fast enough to monitor encryption keys and passwords as users login!”

No special calls or privileges are required for exploitation. The vulnerability can be exploited by a piece of malware deployed on the targeted device. Exploitation may even be possible through JavaScript code planted on a website, according to Cloudflare, which says it has already patched its impacted servers. 

AMD has published its own advisory for CVE-2023-20593.

“Under specific microarchitectural circumstances, a register in ‘Zen 2’ CPUs may not be written to 0 correctly. This may cause data from another process and/or thread to be stored in the YMM register, which may allow an attacker to potentially access sensitive information,” AMD said. 

Advertisement. Scroll to continue reading.

The vulnerability impacts all Zen 2 processors, including Ryzen 3000 (PRO and Threadripper), 4000 (PRO), 5000, 7020, and Epyc (Rome).

AMD has started releasing microcode updates and the vendor has also advised customers to apply AGESA firmware updates. For some products, the updates are expected to become available in the last quarter of 2023. 

As with many CPU patches, some users are concerned about the impact they may have on performance. No data appears to be available at the time of writing, but Ormandy suggested that it should not impact performance.  

Related: Intel, AMD Address Many Vulnerabilities With Patch Tuesday Advisories

Related: Chipmaker Patch Tuesday: Intel, AMD Address Over 100 Vulnerabilities

Related: AMD Processors Expose Sensitive Data to New ‘SQUIP’ Attack

https://www.securityweek.com/zenbleed-vulnerability-affecting-amd-cpus-can-expose-sensitive-information/


Ivanti Zero-Day Vulnerability Exploited in Attack on Norwegian Government

A new zero-day vulnerability affecting a product of US-based enterprise software provider Ivanti has been exploited in an attack aimed at the Norwegian government. 

Norwegian authorities announced on Monday that a dozen government ministries had been targeted in a cyberattack involving a previously unknown vulnerability. 

The country’s National Security Authority later clarified that the attack involved the exploitation of CVE-2023-35078, a zero-day vulnerability impacting Ivanti’s Endpoint Manager Mobile (EPMM), formerly known as MobileIron Core. 

EPMM is a widely used mobile management software engine that enables IT teams to set policies for mobile devices, applications, and content.

According to an advisory published on Monday by Ivanti for CVE-2023-35078, the flaw is an unauthenticated API access issue that can be exploited by remote threat actors “to potentially access users’ personally identifiable information and make limited changes to the server”.

“We have received information from a credible source indicating exploitation has occurred. We continue to work with our customers and partners to investigate this situation,” Ivanti said. “We are only aware of a very limited number of customers that have been impacted.”

The authentication bypass vulnerability has been rated ‘critical’ and it impacts all supported versions, including 11.10, 11.9 and 11.8, as well as older releases. The vendor has rushed to release a patch and organizations have been advised to install it as soon as possible due to how easy it is to exploit the flaw. 

Advertisement. Scroll to continue reading.

Security researcher Kevin Beaumont has set up a honeypot to monitor CVE-2023-35078 and he has already been seeing exploitation attempts.  

There are many internet-exposed systems, particularly in the United States and Europe. 

The vendor, whose offering includes cybersecurity products, has faced criticism for initially deciding not to make its advisory public — it was initially behind a paywall and exploitation information was hidden. 

The US Cybersecurity and Infrastructure Security Agency (CISA) has also released an alert, clarifying that the zero-day can be exploited by an attacker with access to specific API paths to obtain information such as name, phone number and other mobile device details.

The configuration changes that can be made by an attacker include creating an admin account that can make other modifications to the targeted system. 

CISA’s Known Exploited Vulnerabilities Catalog currently lists nine Ivanti product flaws — it does not include the latest zero-day. All of these security holes impact Pulse Connect Secure and MobileIron products, which Ivanti acquired in 2020. 

Related: Citrix Zero-Day Exploited Against Critical Infrastructure Organization

Related: Adobe Releases New Patches for Exploited ColdFusion Vulnerabilities

Related: Zero-Day Vulnerability Exploited to Hack Barracuda Email Security Gateway Appliances

https://www.securityweek.com/ivanti-zero-day-vulnerability-exploited-in-attack-on-norwegian-government/


Apple Patches Another Kernel Flaw Exploited in ‘Operation Triangulation’ Attacks

Apple on Monday pushed out major security-themed updates to its flagship iOS, macOS and iPadOS platforms, warning that at least one of the patched vulnerabilities has already been exploited in the wild.

The Cupertino device maker announced patches for critical code execution flaws in iOS and macOS, including a kernel bug that was used in an exploit chain documented by Russian anti-malware vendor Kaspersky.

According to Apple, the kernel flaw (CVE-2023-38606) affects both iOS, iPadOS and macOS-powered devices and was already actively exploited against versions of iOS released before iOS 15.7.1. 

“An app may be able to modify sensitive kernel state. Apple is aware of a report that this issue may have been actively exploited,” the company confirmed, crediting five different Kaspersky researchers with reporting the issue.

This is the second time Apple has pushed out fixes for software defects exploited as part of APT-style attacks on Kaspersky’s corporate network.  Kaspersky’s disclosure came on the same day Russia’s Federal Security Service (FSB) blamed US intelligence agencies for an ongoing spy campaign targeting thousands of iOS devices belonging to domestic subscribers and foreign diplomatic missions.

In all, Apple fixed at least 25 documented security bugs haunting iPhones and iPads, including multiple issues that expose mobile devices to code execution attacks.  The iOS 16.6 update also covers a WebKit bug that was first addressed in the recent Rapid Security Response rollout.

Apple also fixed security issues in its Safari browser (Safari 16.6), older versions of iPhones and iPads (iOS 15.7.8 and iPadOS 15.7.8), and macOS Ventura 13.5. 

Advertisement. Scroll to continue reading.

Related: Russia Blames US Intelligence for iOS Zero-Click Attacks

Related: Apple Denies Helping US Government Hack Russian iPhones

Related: Apple Patches iOS Flaws Used in Kaspersky ‘Operation Triangulation’

https://www.securityweek.com/apple-patches-another-kernel-flaw-exploited-in-operation-triangulation-attacks/


Over 20,000 Citrix Appliances Vulnerable to New Exploit

A new exploit technique targeting a recent Citrix Application Delivery Controller (ADC) and Gateway vulnerability can be used against thousands of unpatched devices, cybersecurity firm Bishop Fox claims.

Tracked as CVE-2023-3519 and patched last week, the critical-severity bug can be exploited to execute arbitrary code remotely, without authentication, on vulnerable appliances that are configured as a gateway or AAA virtual server.

Last week, CISA warned that attacks exploiting the flaw have been seen since June 2023, in at least one case targeting a critical infrastructure organization.

On Friday, Bishop Fox warned of a new way to exploit the vulnerability, one that can be used against any appliance that is set as a gateway or AAA virtual server and which exposes a specific route that is enabled by default on certain installations.

“The vulnerability is a simple unauthenticated stack overflow. This is made significantly worse by the fact that exploit mitigations do not protect the vulnerable function on some versions,” Bishop Fox notes.

“The vulnerable binary is compiled without PIE and with an executable stack, and on the VPX version, there is no stack canary. As a result, exploitation is trivial. Our exploit cleanly returns without crashing the vulnerable process,” the cybersecurity firm continues.

The exploit, the company says, is different from previously detailed exploitation techniques and does not require SAML to be enabled. However, technical details on the identified vulnerable route are not being disclosed now.

Advertisement. Scroll to continue reading.

Bishop Fox also notes that their analysis of the vulnerable appliances revealed the existence of roughly 61,000 Citrix Gateway login pages that are accessible from the internet, with more than half of these devices (roughly 32,000) unpatched against CVE-2023-3519.

Furthermore, the company claims that roughly 21,000 appliances that are unpatched also expose the vulnerable route, which renders them prone to the new exploitation technique.

Related: Citrix Patches Critical Vulnerability in Secure Access Client for Ubuntu

Related: Citrix Patches High-Severity Vulnerabilities in Windows, Linux Apps

Related: Citrix Patches Critical Vulnerability in Gateway, ADC

https://www.securityweek.com/over-20000-citrix-appliances-vulnerable-to-new-exploit/