Exploitation of ColdFusion Vulnerability Reported as Adobe Patches Another Critical Flaw

Adobe on Friday announced patches for a critical-severity vulnerability in ColdFusion that could be exploited to achieve arbitrary code execution.

Tracked as CVE-2023-38203 (CVSS score of 9.8), the flaw is described as “deserialization of untrusted data” in ColdFusion versions 2023, 2021 and 2018.

This typically allows an attacker to supply specially crafted data and trigger the execution of arbitrary code, potentially leading to complete system compromise.

According to Adobe, information on how this vulnerability may be used in attacks has been published online.

“Adobe is aware that a proof-of-concept blog was posted for CVE-2023-38203,” the company notes in an advisory.

On Friday, Adobe announced that the issue was patched with the release of ColdFusion 2023 Update 1, ColdFusion 2021 Update 7, and ColdFusion 2018 Update 17.

Patches for CVE-2023-38203 were released only days after Adobe patched another critical-severity ‘deserialization of untrusted data’ bug in ColdFusion, namely CVE-2023-29300 (CVSS score of 9.8).

Advertisement. Scroll to continue reading.

According to the Zero Day Initiative’s Dustin Childs, the first in-the-wild attacks targeting CVE-2023-29300 have already been spotted.

“Adobe released another update for ColdFusion today and note CVE-2023-38203 had been publicly disclosed. They also now say CVE-2023-29300 (patched Tues.) has active attacks in the wild,” he posted on Saturday.

ColdFusion users are advised to install the latest security updates as soon as possible.

Related: Adobe Patch Tuesday: Critical Flaws Haunt InDesign, ColdFusion

Related: Microsoft Warns of Office Zero-Day Attacks, No Patch Available

Related: Adobe Inviting Researchers to Private Bug Bounty Program

https://www.securityweek.com/exploitation-of-coldfusion-vulnerability-reported-as-adobe-patches-another-critical-flaw/


Critical Cisco SD-WAN Vulnerability Leads to Information Leaks

A remotely-exploitable critical vulnerability in the Cisco SD-WAN vManage software could allow unauthenticated attackers to retrieve information from vulnerable instances.

Tracked as CVE-2023-20214 (CVSS score of 9.1), the vulnerability exists because the REST API feature of vManage does not sufficiently validate requests.

The vManage API allows administrators to configure, control, and monitor Cisco devices over the network.

An attacker could trigger the vulnerability by sending a crafted API request to a vulnerable instance, to retrieve information from vManage, or send information to it.

“A vulnerability in the request authentication validation for the REST API of Cisco SD-WAN vManage software could allow an unauthenticated, remote attacker to gain read permissions or limited write permissions to the configuration of an affected Cisco SD-WAN vManage instance,” Cisco explains in an advisory.

The web-based management interface and the CLI are not impacted by this security defect, the tech giant explains.

To hunt for attempts to access the REST API, administrators are advised to examine a log file. The existence of requests in the log, however, does not indicate unauthorized access, Cisco explains.

Advertisement. Scroll to continue reading.

The tech giant notes that, while there are no workarounds to address this bug, implementing access control lists (ACLs) to limit vManage access mitigates the issue.

“In cloud hosted deployments, access to vManage is limited by ACLs that contain permitted IP addresses. Network administrators should review and edit the permitted IP addresses in the ACLs. In on-premises deployments, vManage access can be limited in a similar way by using ACLs and configuring permitted IP addresses,” Cisco explains.

The vulnerability has been addressed with the release of SD-WAN vManage versions 20.6.3.4, 20.6.4.2, 20.6.5.5, 20.9.3.2, 20.10.1.2, and 20.11.1.2. Versions 18.3 to 20.6.3.2 are not affected. Customers using SD-WAN vManage versions 20.7 and 20.8 are advised to migrate to a patched version.

Cisco’s security team says it is not aware of this vulnerability being exploited in attacks.

Related: Vulnerability in Cisco Enterprise Switches Allows Attackers to Modify Encrypted Traffic

Related: PoC Exploit Published for Cisco AnyConnect Secure Vulnerability

Related: Cisco Patches Critical Vulnerability in Enterprise Collaboration Solutions

https://www.securityweek.com/critical-cisco-sd-wan-vulnerability-leads-to-information-leaks/


Hackers Target Reddit Alternative Lemmy via Zero-Day Vulnerability

Several instances of the Reddit alternative Lemmy were hacked in recent days by attackers who had apparently exploited a zero-day vulnerability.

Lemmy is an open source software designed for running self-hosted news aggregation and discussion forums. Each Lemmy instance is run by a different individual or organization, but they are interconnected, allowing users from one instance to interact with posts on other servers. Currently there are more than 1,100 instances with a total of nearly 850,000 users. 

A few days ago, someone started exploiting a cross-site scripting (XSS) vulnerability related to the rendering of custom emojis. 

The attacker leveraged the vulnerability to deface pages on some popular instances, including Lemmy.world, the most popular instance, which has over 100,000 users.

“A couple of the bigger Lemmy instances had several user accounts compromised through stolen [JWT] authentication cookies. Some of these cookies belonged to admins, these admin cookies were used to deface instances. Only users that opened pages with malicious content during the incident were vulnerable,” Lemmy.world maintainers explained. 

They added, “Stolen cookies gave attackers access to all private messages and e-mail addresses of affected users.”

It appears that the attacker used the compromised pages to redirect users to hateful or shocking content. 

Advertisement. Scroll to continue reading.

Some Lemmy instances were preemptively shut down when the attack started. 

The vulnerability should now be patched, but users have also been advised to rotate their JWT secrets. 

Related: Google Researchers Discover In-the-Wild Exploitation of Zimbra Zero-Day

Related: Apple Re-Releases Urgent Zero-Day Patches With Fix for Website Access Issue

Related: Microsoft Warns of Office Zero-Day Attacks, No Patch Available

https://www.securityweek.com/hackers-target-reddit-alternative-lemmy-via-zero-day-vulnerability/


Google Researchers Discover In-the-Wild Exploitation of Zimbra Zero-Day

Google security researchers have discovered a Zimbra zero-day vulnerability that has been exploited in the wild. Users are being advised to manually patch their installations. 

Exploitation of the zero-day affecting the popular email and collaboration solution was discovered by Clement Lecigne from Google’s Threat Analysis Group (TAG).

A security update that includes a patch for the vulnerability is expected to be released later this month. In the meantime, users can manually apply mitigations provided by Zimbra. 

The vulnerability appears to be a cross-site scripting (XSS) bug impacting Zimbra Collaboration Suite 8.8.15. Exploitation of these types of flaws, which can be leveraged for remote code execution, typically requires user interaction. 

Zimbra developers noted that the flaw “could potentially impact the confidentiality and integrity of your data”, but their advisory does not explicitly say that the vulnerability has been exploited in the wild. Attackers often exploit Zimbra vulnerabilities to gain access to email servers. 

A CVE identifier has yet to be assigned to the vulnerability. 

It’s not uncommon for Zimbra vulnerabilities to be exploited in the wild, including XSS flaws. In some cases, Zimbra weaknesses have been exploited to hack more than 1,000 email servers. 

Advertisement. Scroll to continue reading.

According to Zimbra’s website, more than 200,000 organizations across 140 countries use its product for email and collaboration. 

CISA’s Known Exploited Vulnerabilities Catalog currently includes eight Zimbra flaws, but the cybersecurity agency has yet to add the latest zero-day.

Related: Zimbra Flaw Exploited by Russia Against NATO Countries Added to CISA ‘Must Patch’ List

Related: Critical Zimbra RCE Vulnerability Exploited in Attacks

Related: UnRAR Vulnerability Exploited in the Wild, Likely Against Zimbra Servers

https://www.securityweek.com/google-researchers-discover-in-the-wild-exploitation-of-zimbra-zero-day/


API Flaw in QuickBlox Framework Exposed PII of Millions of Users

Research into the widely used QuickBlox SDK and API led to the discovery of critical vulnerabilities built into chat and video applications used by industries including telemedicine, smart IoT, and finance.

The researchers from Claroty Team82 and Check Point Research (CPR) developed PoC exploits demonstrating that these vulnerabilities threatened the personal information of millions of users. They found they could access smart intercoms and remotely open doors, or leak patient data from telemedicine applications.

Developers using the QuickBlox framework must first create a QuickBlox account. This provides the credentials that will be used for the application, and a QB-Token that is used in further API requests.

When the application retrieves the QB-Token, users log in with both the application session and user credentials. However, the process requires the user to know the application credentials — which are usually simply inserted into the application and easily extracted by attackers.

Turning to the API, “We discovered a few critical vulnerabilities in the QuickBlox API that could allow attackers to leak the user database from many popular applications,” report the researchers. They found that anyone with an application-level session could obtain a list of users, retrieve PII, and generate multiple attacker-controlled accounts.

Through Google dorking and search engines such as BeVigil, the researchers then located dozens of other applications using the same QuickBlox framework and subject to the same vulnerability. Extracting the keys was more difficult in some applications than others (through encryption or code obfuscation), but the researchers assert, “Developers can only put in obstacles to complicate recovering the application key; which will always be accessible to attackers, whether it takes five minutes to extract or two hours.”

Advertisement. Scroll to continue reading.

The researchers examined how their discoveries could be used against different applications that incorporated QuickBlox. They provide a case study on Rozcom, an Israel-based provider of video intercoms for building entry. Separately investigating the Rozcom mobile app they found additional vulnerabilities and discovered that user IDs were produced by concatenating an individual building ID and the user’s telephone number.

Turning back to their QuickBlox vulnerabilities, the researchers noted, “Rozcom chose to use the user ID [the concatenation] as the user identifier in QuickBlox. And since we could leak the user database from QuickBlox we could get access to all of Rozcom users including Building IDs as well as the correlating users’ phone numbers.” 

Knowing the building ID and the user phone number ultimately allowed the researchers to impersonate a legitimate user (they had also found they could obtain the user’s authorization code). “This means,” explained the researchers, “the only requirement to retrieve a user’s credentials is their phone number, which we managed to leak using the QuickBlox vulnerability. Moreover, the authentication code is static. Therefore, attackers can easily login on behalf of any user and use the application’s functionality to its extent. This allows them to open the door/gate, open video streams and more; they now fully control the intercom device remotely.”

A diagram of a building with a cloud Description automatically generated

Using the same approach on a telemedicine app (unnamed, because at the time of writing it was still vulnerable), the researchers discovered they could use the QuickBlox vulnerability to log in on behalf of any user, whether patient or doctor. They found they were able to retrieve personal information including medical history, chat history, and medical files.

“Furthermore,” warned the researchers, “because full impersonation is possible by this attack, anyone can impersonate a doctor and modify information or even communicate in real time via chat and video with real patients on the platform on behalf of an actual physician.”

This joint research into QuickBlox demonstrates the potential scale of the threat from API flaws, especially where the flaw is in a framework used by multiple vendors and multiple applications. In this instance the researchers worked closely with QuickBlox. QuickBlox has fixed the vulnerabilities via a new secure architecture design and new API. Security, however, doesn’t simply depend upon vendors’ fixes – the telemedicine application was still vulnerable at the time of writing because the developer hadn’t incorporated the vendor’s fixes.

Related: OWASP’s 2023 API Security Top 10 Refines View of API Risks

Related: JumpCloud Says All API Keys Invalidated to Protect Customers

Related: Google Improves Android Security With New APIs

Related: Azure API Management Vulnerabilities Allowed Unauthorized Access

https://www.securityweek.com/api-flaw-in-quickblox-framework-exposed-pii-of-millions-of-users/


Popular WordPress Security Plugin Caught Logging Plaintext Passwords

The All-In-One Security (AIOS) WordPress plugin was found to be logging plaintext passwords from login attempts.

Installed on more than one million WordPress sites, the security and firewall plugin was designed to prevent cyberattacks such as brute-force attempts, warn when the default admin username is used for login, prevent bot attacks, log user activity, and eliminate comment spam.

It was discovered that AIOS version 5.1.9 writes plaintext passwords from login attempts to the database, which essentially provides any privileged user with access to the login credentials of all other administrator users.

The issue was identified roughly two weeks ago, when users started complaining about the insecure design flaw on the plugin’s support forums.

Earlier this week, the Updraft team maintaining the plugin released AIOS version 5.2.0 to address the issue and remove the logged passwords from the database.

However, plugin users have been complaining about the update breaking sites and not removing the password logs. AIOS version 5.2.1 was released on Wednesday to address these issues, but some users claim sites are still broken.

According to Patchstack CEO Oliver Sild, however, the AIOS maintainers should have also warned users of the password logging, so that they could reset their credentials if the same combinations were used on multiple sites, as this creates an attack surface for threat actors.

Advertisement. Scroll to continue reading.

“So far the developers haven’t even told the users to change all passwords. Due to the scale, we will 100% see hackers harvest the credentials from the logs of compromised sites that run (or has run) this plugin,” Sild tweeted.

All-In-One Security (AIOS) users are advised to update their installations as soon as possible. Based on WordPress statistics, hundreds of thousands of websites are still running a vulnerable version of the plugin.

Related: 200,000 WordPress Sites Exposed to Attacks Exploiting Flaw in ‘Ultimate Member’ Plugin

Related: Critical WordPress Plugin Vulnerabilities Impact Thousands of Sites

Related: Millions of WordPress Sites Patched Against Critical Jetpack Vulnerability

https://www.securityweek.com/popular-wordpress-security-plugin-caught-logging-plaintext-passwords/


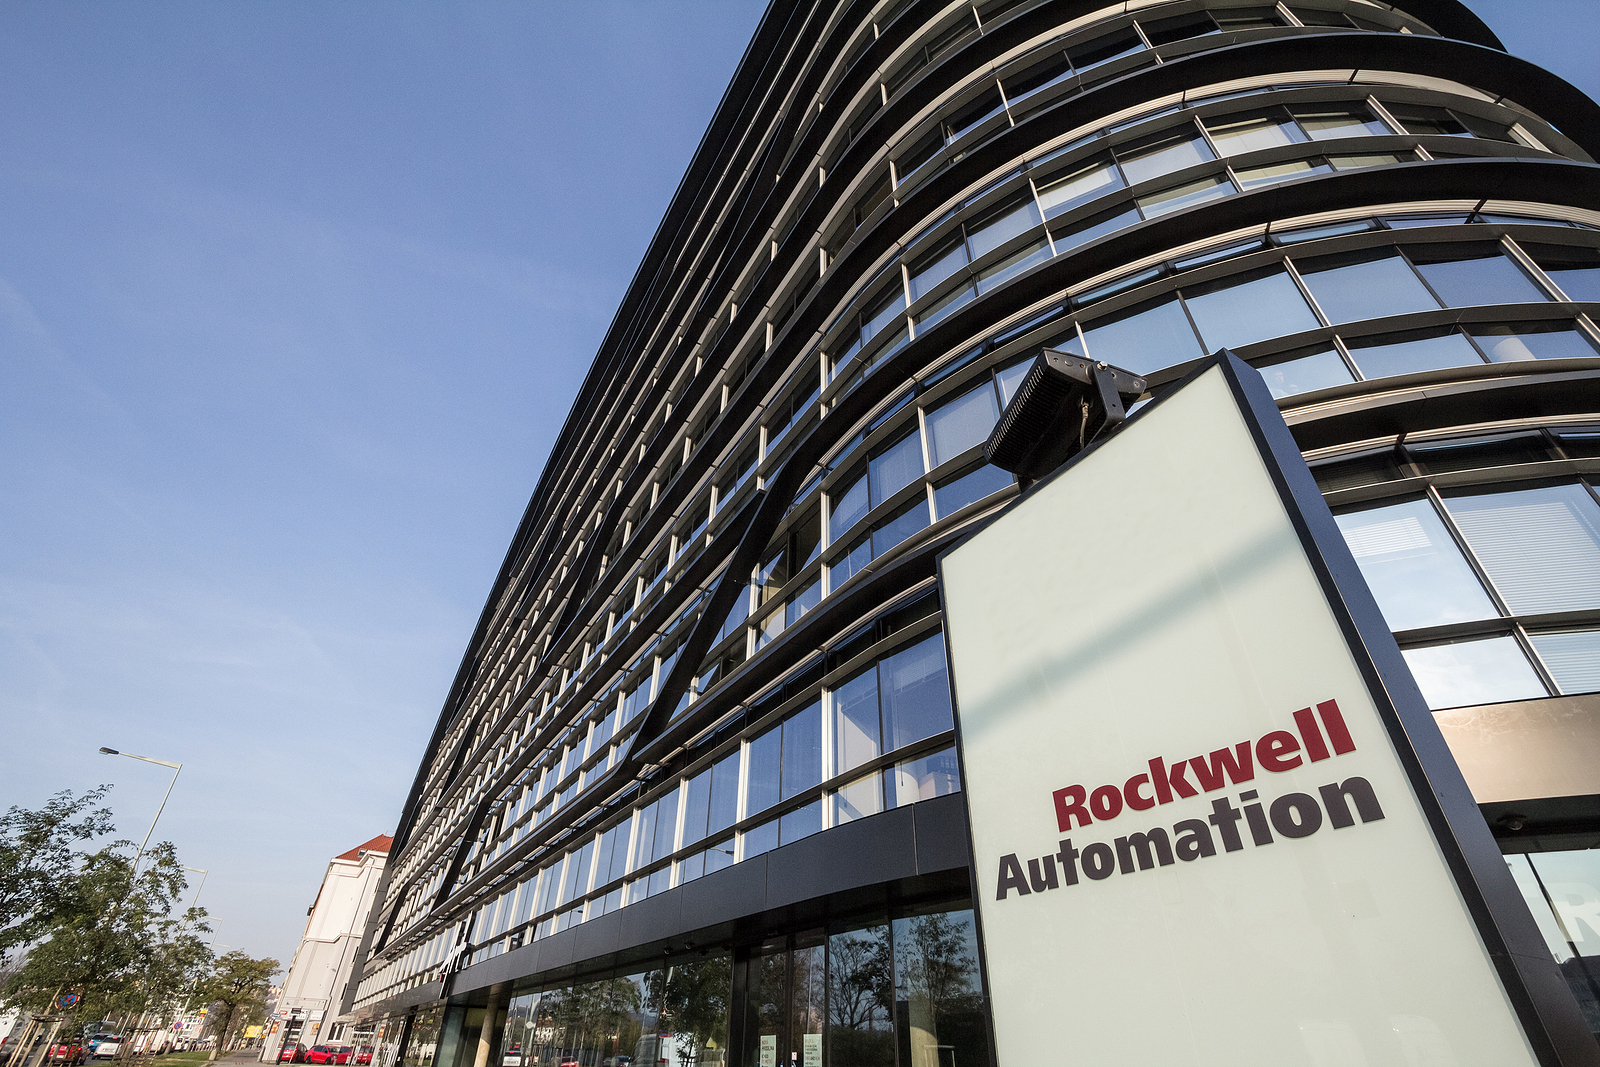
APT Exploit Targeting Rockwell Automation Flaws Could Threaten Critical Infrastructure

An unnamed advanced persistent threat (APT) group has set its sights on two Rockwell Automation product vulnerabilities that they could use to cause disruption or destruction in critical infrastructure organizations.

According to its advisory (only accessible to registered users), Rockwell has worked with the US government to analyze what it describes as a new exploit capability leveraging vulnerabilities in ControlLogix EtherNet/IP communication modules.

Specifically, 1756 EN2 and 1756 EN3 products are impacted by CVE-2023-3595, a critical flaw that can allow an attacker to achieve remote code execution with persistence on the targeted system by using specially crafted Common Industrial Protocol (CIP) messages. A threat actor could exploit the vulnerability to modify, block or exfiltrate data passing through a device.

1756-EN4 products are impacted by CVE-2023-3596, a high-severity denial-of-service (DoS) bug that can be exploited using specially crafted CIP messages. 

Rockwell Automation has released firmware patches for each impacted product and has shared potential indicators of compromise (IoCs), as well as detection rules.

“We are not aware of current exploitation leveraging this capability, and intended victimization remains unclear,” Rockwell said. “Previous threat actors cyberactivity involving industrial systems suggests a high likelihood that these capabilities were developed with an intent to target critical infrastructure and that victim scope could include international customers. Threat activity is subject to change and customers using affected products could face serious risk if exposed.”

The US Cybersecurity and Infrastructure Security Agency (CISA), which has helped Rockwell investigate the exploits, has also released an advisory to warn organizations about the vulnerabilities. 

Advertisement. Scroll to continue reading.

Industrial cybersecurity firm Dragos has also analyzed the vulnerabilities and the exploit, warning that it could — depending on the targeted ControlLogix device’s configuration — allow attackers to cause “denial or loss of control, denial or loss of view, theft of operational data, or manipulation of control for disruptive or destructive consequences on the industrial process for which the ControlLogix system is responsible”.

Dragos said the exploit capability appears to be the work of an unnamed APT, but the company has found no evidence of exploitation in the wild to date, and it’s unclear what organizations or sectors may be targeted. 

However, the company compared the type of access provided by CVE-2023-3595 to the zero-day flaw leveraged by a Russia-linked state-sponsored group in attacks involving the Trisis/Triton malware. 

“Both allow for arbitrary firmware memory manipulation, though CVE-2023-3595 targets a communication module responsible for handling network commands. However, their impact is the same,” Dragos explained.

The company noted, “Knowing about an APT-owned vulnerability before exploitation is a rare opportunity for proactive defense for critical industrial sectors.” 

News of the exploits emerged just weeks after it was reported that several US government departments had been investigating Rockwell’s operations at a facility in China, where employees might have access to information that could be used to compromise the systems of the company’s customers.

There has been some concern that employees could find vulnerabilities in Rockwell products and exploit them in zero-day attacks aimed at systems in the US. 

Related: New Vulnerabilities Allow Stuxnet-Style Attacks Against Rockwell PLCs

Related: Organizations Informed of Over a Dozen Vulnerabilities in Rockwell Automation Products

Related: Omron PLC Vulnerability Exploited by Sophisticated ICS Malware

https://www.securityweek.com/apt-exploit-targeting-rockwell-automation-flaws-could-threaten-critical-infrastructure/


Hardcoded Accounts Allow Full Takeover of Technicolor Routers

Multiple hardcoded credentials found on the Technicolor TG670 DSL gateway router allow attackers to completely take over devices, the CERT Coordination Center (CERT/CC) warns.

A broadband router for small offices and home offices, the Technicolor TG670 router allows administrators to authenticate over HTTP, SSH, or Telnet.

With the remote management functionality enabled, users gain complete administrative control over the router, which is not uncommon for SOHO routers.

According to a CERT/CC advisory, however, Technicolor TG670 DSL gateway routers running firmware version 10.5.N.9 contain multiple hardcoded service accounts that provide full administrative access to the device, over WAN.

On impacted devices with the remote administration feature enabled, CERT/CC says, access is also possible from external network interfaces, such as the internet.

“This account seems to have full administrative access to modify the device settings. Additionally, it appears that this account is not documented and cannot be disabled or removed from the device,” the CERT/CC advisory reads.

An attacker with knowledge of the default username and password for a hardcoded account can authenticate remotely and then “modify any of the administrative settings of the router and use it in unexpected ways”, CERT/CC notes.

Advertisement. Scroll to continue reading.

The remote administration function is enabled by default on the impacted routers, Code White security researcher Florian Hauser, who identified the hardcoded accounts, says.

Technicolor TG670 DSL gateway router users are advised to disable remote administration on their devices, to prevent potential exploitation attempts.

They are also encouraged to check with their service providers for the availability of security updates that address this vulnerability, which is tracked as CVE-2023-31808.

However, CERT/CC notes that Technicolor has not responded to its attempts to establish a communication channel, and it is unclear whether patches that address the hardcoded credentials were released.

SecurityWeek has emailed Technicolor for a statement on the matter and will update this article as soon as a reply arrives.

Related: PoC Exploit Published for Recent Ubiquiti EdgeRouter Vulnerability

Related: Asus Patches Highly Critical WiFi Router Flaws

Related: Details Disclosed for Exploit Chain That Allows Hacking of Netgear Routers

https://www.securityweek.com/hardcoded-accounts-allow-full-takeover-of-technicolor-routers/


Inside the Mind of the Hacker: Report Shows Speed and Efficiency of Hackers in Adopting New Technologies

The application of artificial intelligence is still in its infancy, but we are already seeing one major effect: the democratization of hacking.

The annual Bugcrowd report, Inside the Mind of a Hacker 2023, examines the attitudes held and methods used by the Bugcrowd pool of bug hunters. This year, the report focuses on the effect and use of artificial intelligence (AI) by hackers.

It also provides valuable insight into how malicious hackers will employ AI. For now, this is centered around the use of LLM GPTs, such as ChatGPT. There are numerous ‘specialist’ GPTs appearing, but for the most part they are wrappers around the GPT4 engine. ChatGPT remains the primary tool of hackers.

Seventy-two percent of Bugcrowd’s hackers do not believe AI will ever replicate their human creativity. Despite this, 64% already use AI in their hacking workflow, and a further 30% plan to do so in the future. “I agree completely with the majority that [AI] will not replace the security researchers/hacker,” says Timothy Morris, chief security advisor at Tanium. “Hacking requires skill (AI has that) but also creativity that comes from understanding context (AI does not have that). While AI may get better over the years, I don’t see it as a replacement.”

Nevertheless, it is the combination of human creativity with AI workflow support that is changing the face of hacking – and while that is good in the hands of ethical hackers, it is concerning in the hands of malicious hackers.

According to the report, which analyzed roughly 1,000 survey responses from hackers on the Bugcrowd Platform, hackers are already using and exploring the potential of AI in many different areas. The top use cases are currently automating tasks (50%), analyzing data (48%), identifying vulnerabilities (36%), validating findings (35%), conducting reconnaissance (33%), categorizing threats (22%), detecting anomalies (22%), prioritizing risks (22%), and training models (17%). 

To achieve these ends, hackers have been treating AI as just another tool in their toolset. The first requirement is to understand the tool, and the second is to learn how to use it. With ChatGPT, this falls into two categories – understanding how its designated purpose can be used beneficially, and learning how to bend it to the hackers’ will elsewhere.

Advertisement. Scroll to continue reading.

The former is primarily used for report generation and language translation with speed and accuracy. (Malicious hackers are using the same capabilities in the production of compelling phishing campaigns.)

The latter is the use of prompt engineering to bypass ChatGPT’s filters that are designed to prevent malicious or illegal use of the tool. Prompt engineering is similar in concept to social engineering – while social engineering is the ability to persuade users to do something they shouldn’t, prompt engineering is the ability to persuade AI to do something it shouldn’t.

“Elite hackers view AI, not as a threat, but as a tool that augments their abilities, providing them with a competitive edge,” comments Craig Jones, VP of security operations at Ontinue. “Their perspective demonstrates a symbiotic relationship between hackers and AI, where AI complements and enhances the creative problem-solving skills that define hackers’ expertise.”

Casey Ellis, the founder and CTO of Bugcrowd, believes we should view the arrival of AI in the context of the history of hacking. Hackers are making use of what is available – just as they did with the arrival of Metasploit 20 years ago. It was designed for good but also used for bad. “Metasploit was a boon for hunters,” he said, “but they still had to understand how to use it and apply their own creativity to its application.”

There have been other tooling developments adopted by hackers since then – but AI has one fundamental difference. “Technologies that improve the efficiency of a hacker aren’t necessarily that easy for the layperson to understand,” he continued; “but with ChatGPT, everyone is talking about it and using it.” AI is equally available to ‘not yet hackers’ and non-technologists.

This could become more important given another finding in the report – hackers joining Bugcrowd are getting younger. The number of hackers aged 18 or younger has doubled over the last year, and 62% are aged 24 or younger.

Ellis noted that the approach to computing and security from youngsters today is different to previous generations. Today’s youngsters have grown up using technology, while previous generations had to learn about it. “When I learned about hacking, I was very much concerned with the plumbing of technology and the internet,” said Ellis. “But this under-18 cohort have had their experience of the internet abstracted to the extent they’re not necessarily aware that it’s even there. They don’t necessarily understand the technology, but they understand the interface and business logic and how to exploit the design of systems and applications in a way that I probably never will.”

AI will be able to explore business logic more easily than it can explore coding flaws in compiled applications. The overall effect is that AI will provide speed, scale, and efficiency to everyone, not just the traditional technologically adept hacker. AI introduces democratization to the hacker and potential hacker.

For now, most hackers are limited by the limitations of ChatGPT, but we should be aware that this may not always be the case. ChatGPT is trained on the content of the internet, and further learns from the data it receives through prompts. Imagine the hacking potential of a GPT trained by an adversarial nation state on the source code of target applications, and learning not from the general public but from its use by elite nation state hackers.

Bugcrowd’s Inside the Mind of the Hacker demonstrates the speed and efficiency of hackers in adopting new technologies to assist their hunting and improve their reporting. For now, that translates into scale – creatively found vulnerabilities weaponized and exploited with exponentially faster speed. It is likely to get worse.

Related: Biden Discusses Risks and Promises of Artificial Intelligence With Tech Leaders in San Francisco

Related: ChatGPT’s Chief Testifies Before Congress, Calls for New Agency to Regulate Artificial Intelligence

Related: Malicious Prompt Engineering With ChatGPT

Related: Cyber Insights 2023 | Artificial Intelligence

https://www.securityweek.com/inside-the-mind-of-the-hacker-report-shows-speed-and-efficiency-of-hackers-in-adopting-new-technologies/

Citrix Patches Critical Vulnerability in Secure Access Client for Ubuntu

Citrix on Tuesday announced the release of patches for a critical-severity vulnerability in the Secure Access client for Ubuntu that could be exploited to achieve remote code execution (RCE).

According to Citrix’s advisory, however, exploitation of the issue, which is tracked as CVE-2023-24492 (CVSS score of 9.6), requires user interaction.

“A vulnerability has been discovered in the Citrix Secure Access client for Ubuntu which, if exploited, could allow an attacker to remotely execute code if a victim user opens an attacker-crafted link and accepts further prompts,” a NIST advisory reads.

Citrix has not provided technical details on the flaw, but announced that version 23.5.2 of the Secure Access client for Ubuntu addresses it.

On Tuesday, the tech giant also announced patches for a high-severity elevation of privilege vulnerability in the Secure Access client for Windows.

Tracked as CVE-2023-24491 (CVSS score of 7.8), the issue allows an attacker with access to an endpoint with Standard User Account and a vulnerable client to elevate privileges to that of NT Authority\System.

The vulnerability has been resolved with the release of Secure Access client for Windows version 23.5.1.3.

Advertisement. Scroll to continue reading.

Citrix has credited Rilke Petrosky of F2TC Cyber Security for reporting both vulnerabilities.

Citrix customers are advised to update their installations as soon as possible, by replacing the vulnerable client on the Citrix ADC or Gateway, if it is distributed via the SSL VPN upgrade control feature of ADC or Gateway.

However, the tech giant also releases the Secure Access clients on a standalone basis, and customers can simply install/update the patched version directly on user devices. 

The company makes no mention of any of these vulnerabilities being exploited in attacks, but it is not uncommon for unpatched Citrix products to be targeted in malicious attacks. Additional details on the bugs can be found on Citrix’s security bulletins page.

Related: Citrix Patches High-Severity Vulnerabilities in Windows, Linux Apps

Related: NSA Outs Chinese Hackers Exploiting Citrix Zero-Day

Related: Citrix Patches Critical Vulnerability in Gateway, ADC

https://www.securityweek.com/citrix-patches-critical-vulnerability-in-secure-access-client-for-ubuntu/