PoC Tool Exploits Unpatched KeePass Vulnerability to Retrieve Master Passwords

A researcher has published a proof-of-concept (PoC) tool that exploits an unpatched KeePass vulnerability to retrieve the master password from the program’s memory.

An open source password manager primarily designed for Windows, KeePass can also be used on macOS and Linux, through the open source .NET-compatible framework Mono.

Tracked as CVE-2023-32784, the issue impacts KeePass 2.x versions and allows an attacker to retrieve the cleartext master password from a memory dump. The flaw is exploitable even on workspaces that have been locked or are no longer running.

“The memory dump can be a KeePass process dump, swap file (pagefile.sys), hibernation file (hiberfil.sys), or RAM dump of the entire system. The first character cannot be recovered,” a NIST advisory reads.

The issue is that the custom-developed textbox that KeePass uses for password entry creates a leftover string in memory for each character typed, security researcher Vdohney explains.

“Because of how .NET works, it is nearly impossible to get rid of it once it gets created. For example, when ‘Password’ is typed, it will result in these leftover strings: •a, ••s, •••s, ••••w, •••••o, ••••••r, •••••••d,” the researcher notes.

Vdohney’s PoC tool, called KeePass 2.X Master Password Dumper, searches the memory dump for these patterns to retrieve any typed password – because KeePass uses the same textbox in password edit boxes as well, those passwords can be recovered too.

Advertisement. Scroll to continue reading.

According to the researcher, even if multiple passwords are typed in the same session, these strings should be ordered in memory, meaning that the tool can be used to retrieve all passwords.

“Apart from the first password character, it is mostly able to recover the password in plaintext. No code execution on the target system is required, just a memory dump,” the researcher notes.

While a fix for this vulnerability has been included in the test versions of KeePass 2.54, the official release will become available only in July.

The patch adds a Windows API function call to avoid the creation of managed strings. Additionally, KeePass now creates dummy fragments in memory, which are mixed with the correct fragments.

Even if the official patch is months away, there is no reason to panic, Vdohney says. The vulnerability cannot be exploited remotely, meaning that, unless the computer is already infected with malware, users should not be worried about this flaw’s exploitation.

“If your computer is already infected by malware that’s running in the background with the privileges of your user, this finding doesn’t make your situation much worse,” the researcher notes.

Related: Chrome 113 Security Update Patches Critical Vulnerability

Related: WordPress Field Builder Plugin Vulnerability Exploited in Attacks Two Days After Patch

Related: Microsoft: Iranian APTs Exploiting Recent PaperCut Vulnerability

https://www.securityweek.com/poc-tool-exploits-unpatched-keepass-vulnerability-to-retrieve-master-passwords/


Cisco Says PoC Exploits Available for Newly Patched Enterprise Switch Vulnerabilities

Cisco this week announced patches for critical-severity vulnerabilities in multiple small business switches and warned that proof-of-concept (PoC) code that targets them exists publicly.

Identified in the web-based user interface of the impacted switches, the flaws can be exploited remotely, without authentication, to execute arbitrary code with root privileges.

The root cause of these issues, Cisco notes in an advisory, is the improper validation of requests sent to the web interface. The bugs can be exploited by sending crafted requests through the web-based user interface.

According to Cisco, these vulnerabilities are not dependent on one another, meaning that any of them can be exploited without having to exploit the others.

Tracked as CVE-2023-20159, CVE-2023-20160, CVE-2023-20161, and CVE-2023-20189, the vulnerabilities have a CVSS score of 9.8.

Cisco has released software updates to address all four, along with five other high-severity flaws that can also be exploited by unauthenticated, remote attackers via crafted requests. Four of them could lead to a denial-of-service (DoS) condition, while the fifth allows attackers to read unauthorized information.

The flaws were addressed with the release of firmware version 2.5.9.16 for 250 series smart switches, 350 series managed switches, and 350X and 550X series stackable managed switches, and with firmware version 3.3.0.16 for business 250 series smart switches and business 350 series managed switches.

Advertisement. Scroll to continue reading.

Small business 200 series smart switches, small business 300 series managed switches, and small business 500 series stackable managed switches are also impacted, but Cisco does not plan to update these devices, as they have entered the end-of-life (EoL) process.

The tech giant also notes that PoC code targeting these vulnerabilities is already available, but that it is not aware of malicious attacks targeting them.

This week, Cisco also announced patches for multiple medium-severity bugs in IOS XE ROM Monitor (ROMMON) software, Smart Software Manager (SSM) On-Prem, Identity Services Engine (ISE), DNA Center software, and Business Wireless Access Points (APs).

Additional information on the addressed vulnerabilities can be found on the Cisco security advisories page.

Related: Cisco Warns of Critical Vulnerability in EoL Phone Adapters

Related: Cisco Working on Patch for Vulnerability Reported by NATO Pentester

Related: Cisco Patches Critical Vulnerabilities in Industrial Network Director, Modeling Labs

https://www.securityweek.com/cisco-says-poc-exploits-available-for-newly-patched-enterprise-switch-vulnerabilities/


Teltonika Vulnerabilities Could Expose Thousands of Industrial Organizations to Remote Attacks

Researchers at industrial cybersecurity companies Otorio and Claroty have teamed up to conduct a detailed analysis of products made by Teltonika and found potentially serious vulnerabilities that can expose many organizations to remote hacker attacks.

Teltonika Networks is a Lithuania-based company that makes LTE routers, gateways, modems and other networking solutions that are used worldwide in the industrial, energy, utilities, smart city, transportation, enterprise, and retail sectors.

Researchers at Otorio and Claroty have analyzed the company’s RUT241 and RUT955 cellular routers, as well as the Teltonika Remote Management System (RMS), a platform that can be deployed on-premises or in the cloud for monitoring and managing connected devices. 

The research resulted in the discovery of eight types of security holes, which the US Cybersecurity and Infrastructure Security Agency (CISA) described briefly in an advisory published on May 11. 

The vendor has been notified and it has released patches for both the RMS platform and the RUT routers. 

Otorio and Claroty on Monday released their own blog post providing a more detailed description of the findings. 

The RMS vulnerabilities can be exploited for arbitrary code or command execution with elevated privileges, obtaining information, and routing a connection to a remote server. The router vulnerabilities allow arbitrary code or command execution. 

“Some of our vulnerabilities and [exploit] chains do not require any permission/credentials for the devices,” explained Noam Moshe, vulnerability researcher at Claroty. “Currently, thousands of devices are internet-facing (meaning they are accessible from the internet), and some of the vulnerabilities are exploitable from the internet. In addition, some of our chains allow us to attack devices that may not be internet-facing by gaining access to the cloud-based management platform.”

Advertisement. Scroll to continue reading.

Moshe told SecurityWeek that 4G routers are typically used to connect remote IIoT/IoT sites or devices to the internet and — by exploiting vulnerabilities in these routers — attackers might be able to gain access to the internal network connected to the targeted device. 

“This means that attackers would be able to access thousands of organizations’ internal IIoT/IoT networks, vulnerable devices, internal services, etc.,” Moshe said.

Eran Jacob, security research team leader at Otorio, believes thousands of industrial environments worldwide are exposed to attacks due to these vulnerabilities. 

“These routers are typically connected directly to internal industrial environments and OT devices (vulnerable by design), amplifying the potential consequences,” Jacob told SecurityWeek. 

Related: Organizations Informed of Over a Dozen Vulnerabilities in Rockwell Automation Products

Related: Building Automation System Exploit Brings KNX Security Back in Spotlight 

https://www.securityweek.com/teltonika-vulnerabilities-could-expose-thousands-of-industrial-orgs-to-remote-attacks/


WordPress Field Builder Plugin Vulnerability Exploited in Attacks Two Days After Patch

Threat actors were seen adopting public proof-of-concept (PoC) exploit code targeting a cross-site scripting (XSS) vulnerability in the Advanced Custom Fields WordPress plugin only two days after a patch was released, Akamai reports.

Tracked as CVE-2023-30777, the high-severity vulnerability could allow attackers to inject malicious scripts and other payloads into vulnerable websites. The code would be executed when guests visit the website.

Resulting from an improper sanitization of output in a function configured as an extra handler for a WordPress hook, the issue can be triggered on default plugin installations and does not require authentication for successful exploitation.

CVE-2023-30777 was addressed with the release of Advanced Custom Fields version 6.1.6 on May 4. The patch was included in version 5.12.6 of the plugin as well.

Exploitation attempts targeting the vulnerability, Akamai says, started ramping up on May 6, two days after the patch and one day after technical information on the bug were published.

According to Akamai, the most interesting aspect of the observed attacks was the fact that they were using the same PoC exploit that WordPress security company Patchstack, which identified the vulnerability, published on May 5.

The threat actor behind this increasing volume of attacks that targeted organizations across multiple sectors does not appear sophisticated, given their “complete lack of effort to create a new exploit code”, Akamai notes.

Advertisement. Scroll to continue reading.

With more than two million WordPress websites using Advanced Custom Fields, exploitation of CVE-2023-30777 will likely continue. Users are advised to update their installations as soon as possible.

Related: 1 Million WordPress Sites Impacted by Exploited Plugin Vulnerability

Related: Abandoned WordPress Plugin Abused for Backdoor Deployment

Related: WordPress Plugin Vulnerability Exposed Ferrari Website to Hackers

https://www.securityweek.com/wordpress-field-builder-plugin-vulnerability-exploited-in-attacks-two-days-after-patch/


CISA: Several Old Linux Vulnerabilities Exploited in Attacks

The US Cybersecurity and Infrastructure Security Agency (CISA) has added several Linux and Linux-related flaws to its known exploited vulnerabilities (KEV) catalog.

The agency added seven new vulnerabilities to its KEV catalog on Friday: Ruckus AP remote code execution (CVE-2023-25717), Red Hat Polkit privilege escalation (CVE-2021-3560), Linux kernel privilege escalations (CVE-2014-0196 and CVE-2010-3904), Jenkins UI information disclosure (CVE-2015-5317), Apache Tomcat remote code execution (CVE-2016-8735), and an Oracle Java SE and JRockit issue (CVE-2016-3427).

The Ruckus product vulnerability has been exploited by a DDoS botnet named AndoryuBot. 

However, there do not appear to be any public reports describing exploitation of the other vulnerabilities added to CISA’s catalog. Technical details and proof-of-concept (PoC) exploits are available, which is not surprising considering that some of them have been known for a decade. 

One aspect all the vulnerabilities appear to have in common is their connection to Linux, which indicates that they might have been leveraged in attacks on Linux systems. NIST’s advisories for each security hole include references to advisories posted by various Linux distributions to describe impact of these flaws and the availability of patches. 

At least some of these issues may have been exploited in attacks targeting Android devices — Linux kernel vulnerabilities being exploited in Android attacks is not unheard of.

CISA also pointed out a connection between two of the vulnerabilities. The Apache Tomcat flaw exists because a component was “not updated to take account of Oracle’s fix for CVE-2016-3427”. 

Advertisement. Scroll to continue reading.

However, it’s unclear if the weaknesses have been exploited by the same threat actor or whether multiple of these issues have been chained or used as part of the same attack.

The agency only adds a vulnerability to its catalog if it has reliable evidence of exploitation in the wild. It’s possible that it has privately obtained the information about active exploitation for these flaws.

This is not the first time CISA has been the first to sound the alarm regarding the exploitation of a Linux vulnerability. Nearly one year ago, the agency warned organizations about the vulnerability known as PwnKit being exploited. 

Related: 557 CVEs Added to CISA’s Known Exploited Vulnerabilities Catalog in 2022

Related: CISA Warns of Attacks Exploiting Oracle WebLogic Vulnerability Patched in January

Related: Three Innocuous Linux Vulnerabilities Chained to Obtain Full Root Privileges

https://www.securityweek.com/cisa-several-old-linux-vulnerabilities-exploited-in-attacks/


WordPress Plugin Vulnerability Exposed Ferrari Website to Hackers

A vulnerability discovered in the official website of luxury sports car maker Ferrari could have exposed potentially sensitive information, according to a cybersecurity firm.

The issue was discovered in March by researchers at Char49, a company that provides penetration testing, auditing and training services. Ferrari addressed the weakness within a week.

The researchers noticed that the ‘media.ferrari.com’ domain is powered by WordPress and it was running a very old version of W3 Total Cache, a plugin installed on more than a million websites. 

The plugin was affected by CVE-2019-6715, a flaw that can be exploited by an unauthenticated attacker to read arbitrary files. Exploitation of the vulnerability allowed the researchers to obtain the ‘wp-config.php’ file, which stores WordPress database credentials in clear text. 

Char49’s David Sopas told SecurityWeek that the exposed database stored information associated with the media.ferrari.com domain. 

While the researchers did not dig too deep in order to avoid breaking responsible disclosure rules, Sopas noted that the vulnerability could have been exploited to access other files on the web server, including ones that could contain information that is of value for threat actors.  

After being notified, Ferrari patched the vulnerability by updating the WordPress plugin. 

Advertisement. Scroll to continue reading.

While in this case there is no indication that the security hole directly exposed customer or other sensitive information, it’s important for high-profile companies such as Ferrari to ensure that none of their systems are vulnerable. 

In March, Ferrari admitted being targeted in a ransomware attack in which hackers stole customer information.

Related: Thieves Use CAN Injection Hack to Steal Cars

Related: 16 Car Makers and Their Vehicles Hacked via Telematics, APIs, Infrastructure

Related: Several Car Brands Exposed to Hacking by Flaw in Sirius XM Connected Vehicle Service

https://www.securityweek.com/wordpress-plugin-vulnerability-exposed-ferrari-website-to-hackers/


1 Million WordPress Sites Impacted by Exploited Plugin Vulnerability

Exploitation of a critical vulnerability in the Essential Addons for Elementor WordPress plugin began immediately after a patch was released, WordPress security firm Defiant warns.

With over one million installations, the Essential Addons for Elementor plugin provides additional elements and extensions for the Elementor website building platform.

Tracked as CVE-2023-32243 (CVSS score of 9.8), the critical-severity vulnerability is described as an unauthenticated privilege escalation that can be exploited to take over any user account.

“It is possible to reset the password of any user as long as we know their username thus being able to reset the password of the administrator and login on their account,” explains Patchstack security researcher Rafie Muhammad, who identified the flaw.

The issue exists in a password reset function that changes the password of any user account without validating a password reset key first.

An unauthenticated attacker could exploit the bug to reset the password of any user account if they know the email or username of that user.

The vulnerability impacts Essential Addons for Elementor versions 5.4.0 to 5.7.1 and was addressed this week with the release of version 5.7.2.

Advertisement. Scroll to continue reading.

The patch adds a check to the password reset function to validate the reset password process.

Muhammad identified and reported the vulnerability on May 8. The first exploitation attempts targeting this bug were observed on May 11, when Essential Addons for Elementor version 5.7.2 was released.

“Wordfence blocked 151 attacks targeting this vulnerability in the past 24 hours,” Defiant notes in an advisory. It’s worth noting that the number of attacks seen by Defiant is rapidly increasing.

Essential Addons for Elementor users are advised to update their installations as soon as possible.

Related: Vulnerability in Field Builder Plugin Exposes Over 2M WordPress Sites to Attacks

Related: Abandoned WordPress Plugin Abused for Backdoor Deployment

Related: Elementor Pro Plugin Vulnerability Exploited to Hack WordPress Websites

https://www.securityweek.com/1-million-wordpress-sites-impacted-by-exploited-plugin-vulnerability/


Details Disclosed for Exploit Chain That Allows Hacking of Netgear Routers

Industrial and IoT cybersecurity firm Claroty on Thursday disclosed the details of five vulnerabilities that can be chained in an exploit potentially allowing threat actors to hack certain Netgear routers.

The vulnerabilities were first presented at the 2022 Pwn2Own Toronto hacking competition, where white hat hackers earned a total of nearly $1 million for exploits targeting smartphones, printers, NAS devices, smart speakers and routers.

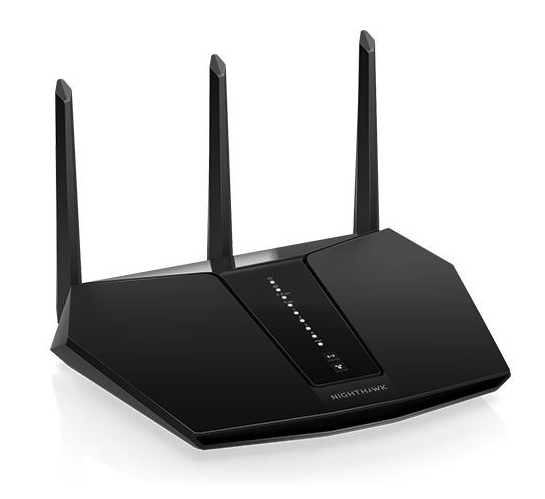
Claroty’s router exploit, which targeted Netgear’s Nighthawk RAX30 SOHO router, earned the company’s researchers $2,500 at Pwn2Own. 

The flaws used in the exploit chain are tracked as CVE-2023-27357, CVE-2023-27367, CVE-2023-27368, CVE-2023-27369, and CVE-2023-27370. They were all patched by Netgear with the release of firmware version 1.0.10.94 in early April.

Three of the vulnerabilities have been rated ‘high severity’ and their exploitation can lead to remote code execution, authentication bypass and command injection. Chaining all the flaws can have a significant impact.

“Successful exploits could allow attackers to monitor users’ internet activity, hijack internet connections and redirect traffic to malicious websites, or inject malware into network traffic,” Claroty warned on Thursday. 

“An attacker could also use these vulnerabilities to access and control networked smart devices (security cameras, thermostats, smart locks), change router settings including credentials or DNS settings, or use a compromised network to launch attacks against other devices or networks,” the company added. 

One mitigating factor is that executing the exploit requires access to the LAN — it’s not a WAN attack that can be executed from the internet, which is why it earned a smaller reward at Pwn2Own. 

Advertisement. Scroll to continue reading.

“These vulnerabilities require an attacker to have your WiFi password or an Ethernet connection to your network to be exploited,” Netgear explained in its advisory.

Related: Netgear Neutralizes Pwn2Own Exploits With Last-Minute Nighthawk Router Patches

Related: Game Acceleration Module Vulnerability Exposes Netgear Routers to Attacks

https://www.securityweek.com/details-disclosed-for-exploit-chain-that-allows-hacking-of-netgear-routers/


Mass Event Will Let Hackers Test Limits of AI Technology

No sooner did ChatGPT get unleashed than hackers started “jailbreaking” the artificial intelligence chatbot — trying to override its safeguards so it could blurt out something unhinged or obscene.

But now its maker, OpenAI, and other major AI providers such as Google and Microsoft, are coordinating with the Biden administration to let thousands of hackers take a shot at testing the limits of their technology.

Some of the things they’ll be looking to find: How can chatbots be manipulated to cause harm? Will they share the private information we confide in them to other users? And why do they assume a doctor is a man and a nurse is a woman?

“This is why we need thousands of people,” said Rumman Chowdhury, a coordinator of the mass hacking event planned for this summer’s DEF CON hacker convention in Las Vegas that’s expected to draw several thousand people. “We need a lot of people with a wide range of lived experiences, subject matter expertise and backgrounds hacking at these models and trying to find problems that can then go be fixed.”

Anyone who’s tried ChatGPT, Microsoft’s Bing chatbot or Google’s Bard will have quickly learned that they have a tendency to fabricate information and confidently present it as fact. These systems, built on what’s known as large language models, also emulate the cultural biases they’ve learned from being trained upon huge troves of what people have written online.

The idea of a mass hack caught the attention of U.S. government officials in March at the South by Southwest festival in Austin, Texas, where Sven Cattell, founder of DEF CON’s long-running AI Village, and Austin Carson, president of responsible AI nonprofit SeedAI, helped lead a workshop inviting community college students to hack an AI model.

Carson said those conversations eventually blossomed into a proposal to test AI language models following the guidelines of the White House’s Blueprint for an AI Bill of Rights — a set of principles to limit the impacts of algorithmic bias, give users control over their data and ensure that automated systems are used safely and transparently.

Advertisement. Scroll to continue reading.

There’s already a community of users trying their best to trick chatbots and highlight their flaws. Some are official “red teams” authorized by the companies to “prompt attack” the AI models to discover their vulnerabilities. Many others are hobbyists showing off humorous or disturbing outputs on social media until they get banned for violating a product’s terms of service.

“What happens now is kind of a scattershot approach where people find stuff, it goes viral on Twitter,” and then it may or may not get fixed if it’s egregious enough or the person calling attention to it is influential, Chowdhury said.

In one example, known as the “grandma exploit,” users were able to get chatbots to tell them how to make a bomb — a request a commercial chatbot would normally decline — by asking it to pretend it was a grandmother telling a bedtime story about how to make a bomb.

In another example, searching for Chowdhury using an early version of Microsoft’s Bing search engine chatbot — which is based on the same technology as ChatGPT but can pull real-time information from the internet — led to a profile that speculated Chowdhury “loves to buy new shoes every month” and made strange and gendered assertions about her physical appearance.

Chowdhury helped introduce a method for rewarding the discovery of algorithmic bias to DEF CON’s AI Village in 2021 when she was the head of Twitter’s AI ethics team — a job that has since been eliminated upon Elon Musk’s October takeover of the company. Paying hackers a “bounty” if they uncover a security bug is commonplace in the cybersecurity industry — but it was a newer concept to researchers studying harmful AI bias.

This year’s event will be at a much greater scale, and is the first to tackle the large language models that have attracted a surge of public interest and commercial investment since the release of ChatGPT late last year.

Chowdhury, now the co-founder of AI accountability nonprofit Humane Intelligence, said it’s not just about finding flaws but about figuring out ways to fix them.

“This is a direct pipeline to give feedback to companies,” she said. “It’s not like we’re just doing this hackathon and everybody’s going home. We’re going to be spending months after the exercise compiling a report, explaining common vulnerabilities, things that came up, patterns we saw.”

Some of the details are still being negotiated, but companies that have agreed to provide their models for testing include OpenAI, Google, chipmaker Nvidia and startups Anthropic, Hugging Face and Stability AI. Building the platform for the testing is another startup called Scale AI, known for its work in assigning humans to help train AI models by labeling data.

“As these foundation models become more and more widespread, it’s really critical that we do everything we can to ensure their safety,” said Scale CEO Alexandr Wang. “You can imagine somebody on one side of the world asking it some very sensitive or detailed questions, including some of their personal information. You don’t want any of that information leaking to any other user.”

Other dangers Wang worries about are chatbots that give out “unbelievably bad medical advice” or other misinformation that can cause serious harm.

Anthropic co-founder Jack Clark said the DEF CON event will hopefully be the start of a deeper commitment from AI developers to measure and evaluate the safety of the systems they are building.

“Our basic view is that AI systems will need third-party assessments, both before deployment and after deployment. Red-teaming is one way that you can do that,” Clark said. “We need to get practice at figuring out how to do this. It hasn’t really been done before.”

https://www.securityweek.com/mass-event-will-let-hackers-test-limits-of-ai-technology/


Microsoft Makes Second Attempt to Patch Recent Outlook Zero-Day

Microsoft this week released patches for a severe vulnerability that bypassed mitigations rolled out for a no-interaction Outlook zero-day leading to credential theft.

Tracked as CVE-2023-29324, the bug was addressed in the Windows MSHTML component as part of the May 2023 Patch Tuesday updates.

The vulnerability was discovered by Akamai security researcher Ben Barnea as a bypass of fixes released in March 2023 to resolve CVE-2023-23397, a critical Outlook flaw exploited by Russian APTs for roughly a year before it was resolved.

CVE-2023-23397 could allow an unauthenticated attacker to send an email reminder containing a sound notification specified as a path, causing the Outlook client to retrieve the sound from a remote SMB server and send the Net-NTLMv2 hash in the negotiation message.

“An unauthenticated attacker on the internet could use the vulnerability to coerce an Outlook client to connect to an attacker-controlled server. This results in NTLM credentials theft. It is a zero-click vulnerability, meaning it can be triggered with no user interaction,” Barnea explains.

To resolve the issue, Microsoft added a call to the MapUrlToZone Windows API function to check that the path is not referring to an internet URL and replace the sound with a default reminder if it does.

While analyzing the patch for CVE-2023-23397, Barnea discovered that MapUrlToZone could be tricked into thinking that a remote path is a local one, by sending a crafted URL in the reminder message, which would bypass Microsoft’s mitigations and cause the Outlook client to connect to the remote server.

Advertisement. Scroll to continue reading.

The vulnerable MSHTML platform, Microsoft explains, continues to be used in Windows by the Internet Explorer mode in Microsoft Edge, as well as by other applications, through the WebBrowser control.

To fully resolve the issue, the tech giant recommends installing patches for both CVE-2023-23397 and CVE-2023-29324. Users who install Security Only updates should install the IE Cumulative updates to mitigate the bug.

Related: Microsoft Warns of Outlook Zero-Day Exploitation, Patches 80 Security Vulns

Related:Microsoft Will Name Threat Actors After Weather Events

Related: Microsoft Shares Resources for BlackLotus UEFI Bootkit Hunting

https://www.securityweek.com/microsoft-make-second-attempt-to-patch-recent-outlook-zero-day/