Chainguard Trains Spotlight on SBOM Quality Problem

Software engineers tracking the quality of software bill of materials have stumbled on a startling discovery: Barely 1% of all SBOMs being generated today meets the “minimum elements” defined by the U.S. government.

According to new data from software supply chain security startup Chainguard, SBOMs being generated by existing tools fail to meet the minimum data fields needed inside an SBOM to enable the management of software vulnerabilities, licenses, and inventory tracking.

“Only one percent of SBOMs were entirely conformant with the minimum elements. The minimum elements appear to be a high bar for SBOMs. Further research will need to address whether the standard is too high, whether SBOM generation tools must evolve, or whether the underlying software artifacts lack necessary package metadata,” Chainguard security data scientist John Speed Meyers explained.

Chainguard’s researchers collected about 3,000 SBOMs for analysis using four SBOM creation tools from a list of popular Docker Hub containers and used an NTIA conformance checker tool to measure SBOM conformance with minimum elements.

The team said the minimum element data fields include information about each software component (supplier, name, version, unique ID, relationships) and also metadata about the SBOM itself, including the author and the time of creation.

After parsing the data, the Chainguard team found the majority of SBOMs lacked specified suppliers for their components while about 1,000 SBOMs failed to specify a name or version for all components.

The latest Chainguard discovery is sure to add fuel to an ongoing debate over the value and quality of SBOMs to help mitigate supply chain attacks. 

A high-powered lobbying outfit representing some of the biggest names in technology has already signaled strong objection to the government’s SBOM mandate, arguing that “it is premature and of limited utility” because SBOMs are not currently scalable or consumable. 

The ITI lobbying outfit, which counts Amazon, Microsoft, Apple, Intel, AMD, Lenovo, IBM, Cisco, Samsung, TSMC, Qualcomm, Zoom and Palo Alto Networks among its prominent members, described the current SBOM process as immature. 

“At this time, it is premature and of limited utility for software producers to provide an SBOM. We ask that OMB discourage agencies from requiring artifacts until there is a greater understanding of how they ought to be provided and until agencies are ready to consume the artifacts that they request,” the group said.

In its research, Chainguard called attention to the ITI objections, cautioning that its findings are not meant to be viewed as evidence for what it called a cynical argument that SBOMs are “immature” and not yet “consumable.” 

“This analysis suggests that standard SBOMs already provide a great deal of information but not enough to satisfy  the minimum elements. Additionally, this research implies that the push to make SBOMs “everywhere” should be accompanied by an effort to measure and improve the quality of SBOMs,” the company said.

A tool-by-tool analysis suggests that none of the tools appear to consistently create minimum elements-compliant SBOMs,” Chainguard added.

Still, the company is advising caution against dismissing the usefulness of SBOMs. “The results suggest lots of variability: some SBOMs are high-quality, some are low-quality,” it said.

The SBOM mandate was included in a cybersecurity executive order issued last May, sending security leaders scrambling to understand the ramifications and prepare for downstream side-effects.

Related: Big Tech Vendors Object to US Gov SBOM Mandate

Related: Microsoft Releases Open Source Toolkit for Generating SBOMs 

Related: Cybersecurity Leaders Scramble to Decipher SBOM Mandate

view counter

Ryan Naraine is Editor-at-Large at SecurityWeek and host of the popular Security Conversations podcast series.
Ryan is a veteran cybersecurity strategist who has built security engagement programs at major global brands, including Intel Corp., Bishop Fox and GReAT. He is a co-founder of Threatpost and the global SAS conference series. Ryan’s past career as a security journalist included bylines at major technology publications including Ziff Davis eWEEK, CBS Interactive’s ZDNet, PCMag and PC World.
Ryan is a director of the Security Tinkerers non-profit, an advisor to early-stage entrepreneurs, and a regular speaker at security conferences around the world.
Follow Ryan on Twitter @ryanaraine.

Previous Columns by Ryan Naraine:
Tags:

https://www.securityweek.com/chainguard-trains-spotlight-sbom-quality-problem


Cisco Patches High-Severity SQL Injection Vulnerability in Unified CM

Cisco on Wednesday announced patches for a high-severity SQL injection vulnerability in Unified Communications Manager (CM) and Unified Communications Manager Session Management Edition (CM SME).

Designed as enterprise call and session management platforms, Cisco Unified CM and Unified CM SME ensure the interoperability of applications such as Webex, Jabber, and more, while also maintaining availability and security.

Tracked as CVE-2023-20010 (CVSS score of 8.1), the vulnerability exists because user input is improperly validated in the web-based management interface of the platforms. The bug allows a remote, authenticated attacker to launch an SQL injection attack on a vulnerable system.

“An attacker could exploit this vulnerability by authenticating to the application as a low-privileged user and sending crafted SQL queries to an affected system. A successful exploit could allow the attacker to read or modify any data on the underlying database or elevate their privileges,” Cisco notes in an advisory.

The security defect impacts Cisco Unified CM and Unified CM SME versions 11.5(1), 12.5(1), and 14, and was addressed in version 12.5(1)SU7 of the applications. A patch will also be included in version 14SU3, which is scheduled for March 2023.

On Wednesday, the tech giant also informed customers of a medium-severity URL filtering bypass vulnerability in AsyncOS software for Email Security Appliance (ESA). A remote, unauthenticated attacker could exploit the bug using crafted URLs.

This week, Cisco also announced patches for three medium severity bugs in Expressway Series and TelePresence Video Communication Server (VCS).

Impacting the API and web-based management interfaces of these products, the flaws could be exploited by an authenticated, remote attacker to write files or access sensitive data on a vulnerable device. All Expressway Series and TelePresence VCS releases prior to 14.0.7 are impacted.

Cisco says it is not aware of any of these vulnerabilities being exploited in the wild. Further information on the flaws can be found on Cisco’s product security page.

Related: Cisco Warns of Critical Vulnerability in EoL Small Business Routers

Related: Cisco Patches High-Severity Bugs in Email, Identity, Web Security Products

Related: Cisco Secure Email Gateway Filters Bypassed Due to Malware Scanner Issue

view counter

Ionut Arghire is an international correspondent for SecurityWeek.

Previous Columns by Ionut Arghire:
Tags:

https://www.securityweek.com/cisco-patches-high-severity-sql-injection-vulnerability-unified-cm


CSRF Vulnerability in Kudu SCM Allowed Code Execution in Azure Services

A cross-site request forgery (CSRF) vulnerability impacting the source control management (SCM) service Kudu could be exploited to achieve remote code execution (RCE) in multiple Azure services, cloud infrastructure security firm Ermetic has discovered.

A web-based Git repository manager, Kudu is the engine behind several Azure App Service features, supporting the deployment and management of code in Azure. The service is used by Functions, App Service, Logic Apps, and other Azure services.

Administrators can manage Azure applications from the SCM panel, which uses Kudu and which requires Azure Active Directory (AAD) authentication. The SCM panel is deployed by default by the App Service, Function Apps, and Logic Apps Azure services.

“If the user has authenticated to their Microsoft account through the browser, they can simply navigate to the SCM panel and log in. Otherwise, they need to log in manually with their Microsoft authorized credentials,” Ermetic notes.

The CSRF vulnerability in Kudu could be exploited to deploy a malicious ZIP file to the victim’s Azure application, which could result in code execution and application takeover. Ermetic calls the attack EmojiDeploy.

Successful exploitation of the security defect could allow an attacker to run code as the www user, steal or tamper with sensitive data, launch phishing campaigns, and even move laterally to other Azure services.

“The vulnerability enables RCE and full takeover of the target app. The impact of the vulnerability on the organization as a whole depends on the permissions of the applications managed identity. Effectively applying the principle of least privilege can significantly limit the blast radius,” Ermetic notes.

According to Ermetic, attackers targeting the vulnerability would need to exploit a same-site misconfiguration, to bypass an origin check, and then exploit a vulnerable endpoint, which would eventually lead to RCE.

Specifically, Ermetic discovered that the Same-Site attribute for the SCM panel’s cookie was set to “None”, meaning that no protection was being offered against cross-origin attacks, and that the SCM server would accept requests containing special characters, leading to cross-origin protections bypass.

“This finding allows an attacker to create a wildcard DNS record for his own domain and send cross-origin requests with special characters that eventually will be accepted by the server origin check,” Ermetic explains.

The researchers also discovered that, when processing requests to the ZIP ‘deploy to application’ feature available through the SCM, the server does not validate or require the headers sent by the client, which would bypass existing CSRF mitigations.

“After some investigation, the SCM Server in this particular zipdeploy endpoint accepts text/plain Mime-types. We can encode our zip payload and use text/plain for CSRF,” Ermetic notes.

The EmojiDeploy attack can be performed via a browser, but exploitation of the vulnerability requires for the attacker to have SCM or Microsoft account cookies in their browser.

The vulnerability was reported to Microsoft in October 2022 and the tech giant addressed it in December through stronger origin checks on the server and by changing the same-site cookie value to ‘Lax’. Microsoft awarded a $30,000 bug bounty for the issue.

Related: Azure Services SSRF Vulnerabilities Exposed Internal Endpoints, Sensitive Data

Related: Microsoft Patches Azure Cross-Tenant Data Access Flaw

Related: Microsoft Patches Vulnerability Allowing Full Access to Azure Service Fabric Clusters

view counter

Ionut Arghire is an international correspondent for SecurityWeek.

Previous Columns by Ionut Arghire:
Tags:

https://www.securityweek.com/csrf-vulnerability-kudu-scm-allowed-code-execution-azure-services


Vendors Actively Bypass Security Patch for Year-Old Magento Vulnerability

Vendors and agencies are actively bypassing the security patch that Adobe released in February 2022 to address CVE-2022-24086, a critical mail template vulnerability in Adobe Commerce and Magento stores, ecommerce security firm Sansec warns.

The CVE-2022-24086 bug (CVSS score of 9.8) is described as an improper input validation bug in the checkout process. It could be exploited to achieve arbitrary code execution, with in-the-wild exploitation observed roughly one week after patches were made available for it.

The initial fixes were found to be easily bypassed, and Adobe issued a second round of patches and a new CVE identifier (CVE-2022-24087) for the bug only days later. A proof-of-concept (PoC) exploit targeting the flaw was released around the same time.

To address the vulnerability, Adobe removed ‘smart’ mail templates and replaced the old mail template variable resolver with a new one, to prevent potential injection attacks.

However, the move caught many vendors off guard, and some of them “had to revert to the original functionality.” In doing so, they unknowingly exposed themselves to the critical vulnerability, despite having applied the latest security patch, Sansec explained.

The security firm has observed some vendors attempting to reintroduce the functionality of the deprecated resolver into production Magento stores, either by overriding the functionality of the new resolver, or by copying code from older versions of Magento and using it as a preference.

“We have observed this risky behavior at multiple agencies as well as extension vendors, likely to avoid the need to update their email templates to be compatible with the new [resolver],” Sansec added.

The company said some vendors attempted to mitigate security risks by adding to the ordering systems basic filtering on unsafe user inputs, but that does not prevent exploitation, given that the vulnerability can be triggered from other subsystems as well, if they touch email.

Related: Magento Vulnerability Increasingly Exploited to Hack Online Stores

Related: Malware Infects Magento-Powered Stores via FishPig Distribution Server

Related: CISA Urges Orgs to Patch Recent Chrome, Magento Zero-Days

view counter

Ionut Arghire is an international correspondent for SecurityWeek.

Previous Columns by Ionut Arghire:
Tags:

https://www.securityweek.com/vendors-actively-bypass-security-patch-year-old-magento-vulnerability


Azure Services SSRF Vulnerabilities Exposed Internal Endpoints, Sensitive Data

Cloud security company Orca has published details on four server-side request forgery (SSRF) vulnerabilities impacting different Azure services, including two bugs that could have been exploited without authentication.

SSRF flaws, Orca explains, typically allow attackers to access the host’s IMDS (Cloud Instance Metadata Service), enabling them to view information such as hostnames, MAC addresses, and security groups.

Furthermore, such security defects could be exploited to retrieve tokens, execute code remotely, and move to another host.

Impacting Azure Functions and Azure Digital Twins, the two unauthenticated vulnerabilities could be exploited without an Azure account to send requests on behalf of the server.

The remaining two security issues, which were identified in Azure API Management and Azure Machine Learning, require authentication for successful exploitation.

All four vulnerabilities are non-blind SSRF (full SSRF) issues, allowing an attacker to fetch any request and retrieve the output, Orca’s researchers say. Such flaws can typically be exploited via XXE (XML external entity), SVG files, a proxy, PDF rendering, vulnerable query string in the URL, and more.

“The discovered Azure SSRF vulnerabilities allowed an attacker to scan local ports, find new services, endpoints, and sensitive files – providing valuable information on possibly vulnerable servers and services to exploit for initial entry and the location of sensitive information to target,” Orca says.

The issues could be exploited to request any URL by abusing the server, but various mitigations that Microsoft has implemented prevented the researchers from exploiting the newly identified bugs to reach IMDS endpoints.

The unauthenticated flaw in the Azure DigitalTwins Explorer service was caused by a bug in the user input validation following a request, while the issue impacting the Azure Functions service resided in a NodeJS based function.

The authenticated vulnerability in Azure API Management allowed the researchers to enumerate all open ports on the vulnerable server, review all of them, and retrieve more sensitive data, including Git client version, the empty refs list, and the git-scm capabilities.

The Azure Machine Learning service bug, Orca says, allowed the researchers to retrieve any endpoint.

Orca reported the vulnerabilities to Microsoft between October and December 2022. Patches were released shortly after each report, with the last vulnerability addressed on December 20.

UPDATE: Microsoft has published its own blog post, clarifying that the vulnerabilities were “low risk as they do not allow access to sensitive information or Azure backend services.”

Related: Microsoft Patches Vulnerability Allowing Full Access to Azure Service Fabric Clusters

Related: Azure Service Fabric Vulnerability Can Lead to Cluster Takeover

Related: Microsoft Azure Vulnerability Allowed Code Execution, Data Theft

view counter

Ionut Arghire is an international correspondent for SecurityWeek.

Previous Columns by Ionut Arghire:
Tags:

https://www.securityweek.com/azure-services-ssrf-vulnerabilities-exposed-internal-endpoints-sensitive-data


Researchers: Brace for Zoho ManageEngine ‘Spray and Pray’ Attacks

Security researchers tracking a known pre-authentication remote code execution vulnerability in Zoho’s ManageEngine products are warning organizations to brace for “spray and pray” attacks across the internet.

The vulnerability, patched by Zoho last November, affects multiple Zoho ManageEngine products and can be reached over the internet to launch code execution exploits if SAML single-sign-on is enabled or has ever been enabled.

According to researchers at automated penetration testing firm Horizon3.ai, the CVE-2022-47966 flaw is easy to exploit and a good candidate for so-called “spray and pray” attacks. In this case, the bug gives attackers complete control over the system or an immediate beachhead to launch additional compromises.

“Once an attacker has SYSTEM level access to the endpoint, attackers are likely to begin dumping credentials via LSASS or leverage existing public tooling to access stored application credentials to conduct lateral movement,” the company said in a note documenting its work creating IOCs to help businesses hunt for signs of infection.

Horizon3.ai red-teamer James Horseman is calling attention to exposed attack surfaces that put thousands of organizations at risk. “Shodan data shows that there are likely more than a thousand instances of ManageEngine products exposed to the internet with SAML currently enabled,” Horseman said, estimating that roughly 10% of all Zoho Management products may be sitting ducks for these attacks.

“Organizations that use SAML in the first place tend to be larger and more mature and are likely to be higher value targets for attackers,” Horseman warned.

Although Zoho issued patches late last year, Horseman notes that some organizations are still be tardy on deploying the fixes. “Given how slow enterprise patch cycles can be, we expect that there are many who have not yet patched.”

“We want to highlight that in some cases the vulnerability is exploitable even if SAML is not currently enabled, but was enabled sometime in the past. The safest course of action is to patch regardless of the SAML configuration of the product,” Horseman added.

Zoho boasts that about 280,000 organizations across 190 countries use its ManageEngine product suite to manage IT operations.  

The Indian multinational firm, which sells a wide range of productivity and collaboration apps to businesses, has struggled with zero-day attacks and major security problems that have been targeted by nation-state APT actors.

The US government’s cybersecurity agency CISA has added Zoho vulnerabilities to its federal ‘must-patch’ list because of known exploitation activity.

Related: U.S. Agencies Warn of APTs Exploiting Zoho Zero-Day 

Related: Zoho Working on Patch for Zero-Day ManageEngine Vulnerability

Related: CISA Adds Zoho Flaws to Federal ‘Must-Patch’ List 

view counter

Ryan Naraine is Editor-at-Large at SecurityWeek and host of the popular Security Conversations podcast series.
Ryan is a veteran cybersecurity strategist who has built security engagement programs at major global brands, including Intel Corp., Bishop Fox and GReAT. He is a co-founder of Threatpost and the global SAS conference series. Ryan’s past career as a security journalist included bylines at major technology publications including Ziff Davis eWEEK, CBS Interactive’s ZDNet, PCMag and PC World.
Ryan is a director of the Security Tinkerers non-profit, an advisor to early-stage entrepreneurs, and a regular speaker at security conferences around the world.
Follow Ryan on Twitter @ryanaraine.

Previous Columns by Ryan Naraine:
Tags:

https://www.securityweek.com/researchers-brace-zoho-manageengine-spray-and-pray-attacks


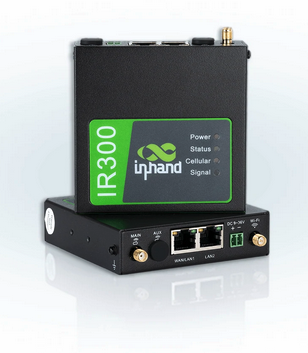
InHand Industrial Router Vulnerabilities Expose Internal OT Networks to Attacks

A series of vulnerabilities affecting industrial routers made by InHand Networks could allow hackers to bypass security systems and gain access to internal operational technology (OT) networks from the internet.

The US Cybersecurity and Infrastructure Security Agency (CISA) last week published an advisory to inform organizations about five vulnerabilities identified by a researcher at industrial cybersecurity firm Otorio in InHand’s InRouter302 and InRouter615 cellular routers.

The vendor has released firmware updates that should patch these vulnerabilities.InHand router vulnerabilities

According to CISA, most of the vulnerabilities are related to message queuing telemetry transport (MQTT) and their exploitation could lead to command/code execution and information disclosure.

One of the security holes has been assigned a ‘critical’ severity rating, two have been rated ‘high severity’ and two are medium-severity issues.

Matan Dobrushin, VP of research at Otorio, told SecurityWeek that the vulnerabilities impact both the cloud management platform and the device’s firmware.

“Chaining these vulnerabilities together can allow an attacker to remotely execute code as root on all connected InRouter302 and InRouter615 devices directly from the internet,” Dobrushin explained.

The affected devices are used for industrial robots, oil wells, elevators, medical equipment, electric car charging stations, and smart meters.

“We are certain that there are tens of thousands of devices that are impacted by these vulnerabilities, affecting thousands of critical sites around the globe,” Dobrushin warned.

Roni Gavrilov, the Otorio researcher credited for finding these flaws, provided additional information on impact in a LinkedIn post.

“Successful exploitation of industrial wireless IoT may allow an attacker to bypass all of the security layers protecting the internal OT network at once, enabling access directly to connected PLCs, HMIs and field devices on the attacked site, easily impacting the process and potentially propagating the attack to the control center,” the researcher said.

This is not the first time Otorio has found vulnerabilities in InHand routers. In 2021, the company reported finding more than a dozen security flaws in one of the vendor’s cellular routers.

In addition, in 2022, Cisco’s Talos threat intelligence and research unit reported finding 17 vulnerabilities in the InRouter302 product.

Related: 10 Vulnerabilities Found in Widely Used Robustel Industrial Routers

Related: Several Vulnerabilities Expose Phoenix Contact Industrial 4G Routers to Attacks

view counter

Eduard Kovacs (@EduardKovacs) is a contributing editor at SecurityWeek. He worked as a high school IT teacher for two years before starting a career in journalism as Softpedia’s security news reporter. Eduard holds a bachelor’s degree in industrial informatics and a master’s degree in computer techniques applied in electrical engineering.

Previous Columns by Eduard Kovacs:
Tags:

https://www.securityweek.com/inhand-industrial-router-vulnerabilities-expose-internal-ot-networks-attacks


Hack the Pentagon 3.0 Bug Bounty Program to Focus on Facility Control Systems

The US Department of Defense (DoD) is getting ready to launch the third installment of its ‘Hack the Pentagon’ bug bounty program, which will focus on the Facility Related Controls System (FRCS) network.

Hack the Pentagon was launched in 2016 on HackerOne, when the DoD invited ethical hackers to find and report security defects in Pentagon’s public web pages.

In 2018, the DoD announced a continuous Hack the Pentagon program running year-long on Bugcrowd and targeting vulnerabilities in hardware and physical systems and other high-value assets.

According to a draft solicitation released on Friday, as part of Hack the Pentagon 3.0, DoD will rely on ethical hackers to identify vulnerabilities in FRCS.

The DoD’s FRCS includes control systems that are used to monitor and control equipment and systems related to real property facilities, such as HVAC, utilities, physical security systems, and fire and safety systems.

“The overall objective is to obtain support from a pool of innovative information security researchers via crowdsourcing for vulnerability discovery, coordination and disclosure activities and to assess the current cybersecurity posture of the FRCS network, identify weaknesses and vulnerabilities, and provide recommendations to improve and strengthen the overall security posture,” the draft reads.

Per the document, the DoD is looking to engage with a private organization that has expertise in commercial crowdsourcing, to select “a private community of skilled and trusted researchers, which may be limited to US persons only” to participate in the program.

For previous bug bounty programs – which also included Hack the Air Force, Hack the Army, Hack the Marine Corps and Hack the Defense Travel System – in addition to working with HackerOne and Bugcrowd, the DoD partnered with Synack to vet participating researchers.

The draft also makes it clear that the DoD will establish the eligibility criteria for the participating researchers, and that participants will have to be able to perform reverse engineering, source code analysis, and network and system exploitation.

“The bounty execution or ‘challenge phase’ itself is expected to last no more than 72 hours in person,” the draft reads.

Related: DoD Launches ‘Hack US’ Bounties for Major Flaws in Publicly Exposed Assets

Related: ‘Hack DHS’ Participants Awarded $125,000 for Over 100 Vulnerabilities

Related: DoD Announces Results of Vulnerability Disclosure Program for Defense Contractors

view counter

Ionut Arghire is an international correspondent for SecurityWeek.

Previous Columns by Ionut Arghire:
Tags:

https://www.securityweek.com/hack-pentagon-30-bug-bounty-program-focus-facility-control-systems


Most Cacti Installations Unpatched Against Exploited Vulnerability

Most internet-exposed Cacti installations have not been patched against a critical-severity command injection vulnerability that is being exploited in attacks.

An open-source web-based network monitoring and graphing tool that offers an operational monitoring and fault management framework, Cacti is a front-end application for the data logging utility RRDtool.

In early December 2022, the tool’s maintainers announced patches for CVE-2022-46169, a critical-severity (CVSS score 9.8) command injection flaw that could allow unauthenticated attackers to execute code on the server running Cacti, if a specific data source was used.

The security defect consists of an authentication bypass, where an unauthenticated attacker can access a specific file, and an improper sanitization of an argument during the processing of a specific HTTP query for a polling ‘action’ defined in the database.

Users can define actions for the monitoring of hosts (pollers) and the issue impacts a poller type that executes a script. An attacker able to bypass authentication can supply the specific argument that is passed along to the execution call unsanitized, achieving command injection.

Cacti versions 1.2.23 and 1.3.0, released on December 5, include patches for this vulnerability.

A few days after SonarSource published a technical analysis of CVE-2022-46169 on January 3, The Shadowserver Foundation warned that it had logged the first exploitation attempts targeting the security defect.

“Using Cacti? We started to pick up exploitation attempts for Cacti unauthenticated remote command injection CVE-2022-46169 including subsequent malware download. These started Jan 3rd. Make sure to patch & not expose your Cacti instance to the Internet,” Shadowserver said.

This week, attack surface management firm Censys revealed that, out of 6,400 internet-accessible Cacti hosts that it has identified, only 26 were running a patched version of the tool. Most of these servers are in Brazil, with Indonesia and the US rounding up the top three.

With exploitation of this vulnerability underway, organizations are advised to update Cacti to a patched version as soon as possible.

Related: Google Documents IE Browser Zero-Day Exploited by North Korean Hackers

Related: Fortinet Ships Emergency Patch for Already-Exploited VPN Flaw

Related: Omron PLC Vulnerability Exploited by Sophisticated ICS Malware

view counter

Ionut Arghire is an international correspondent for SecurityWeek.

Previous Columns by Ionut Arghire:
Tags:

https://www.securityweek.com/most-cacti-installations-unpatched-against-exploited-vulnerability


Exploitation of Control Web Panel Vulnerability Starts After PoC Publication

Security researchers are observing exploitation attempts targeting a critical Control Web Panel (CWP) vulnerability, following the publication of proof-of-concept (PoC) code in early January.

Formerly CentOS Web Panel, CWP is a popular, free web hosting panel for enterprise-based Linux systems, offering support for the management and security of both servers and clients.

Tracked as CVE-2022-44877 (CVSS score of 9.8), the exploited vulnerability allows unauthenticated attackers to achieve remote code execution (RCE) on impacted systems.

The security defect is a misconfiguration in functionality that logged incorrect entries on the panel, allowing attackers to insert commands that would be executed on the server, CloudSEK explains in a technical analysis of the PoC.

A NIST advisory notes that “login/index.php in CWP 7 before 0.9.8.1147 allows remote attackers to execute arbitrary OS commands via shell metacharacters in the login parameter.”

The issue was identified and reported by Gais Cyber Security researcher Numan Turle and patches were released for both the admin panel and the user panel in October 2022.

On January 3, 2023, Turle published a PoC exploit targeting the vulnerability, along with a video demonstrating the bug in action.

Soon after, attackers started exploiting the vulnerability in malicious attacks, with both cybersecurity firm GreyNoise and nonprofit security organization The Shadowserver Foundation warning of active exploitation attempts.

“We are seeing CVE-2022-44877 exploitation attempts for CWP (CentOS Web Panel/Control Web Panel) instances. This is an unauthenticated RCE. Exploitation is trivial and a PoC published. Exploitation was first observed Jan 6th,” Shadowserver said.

Shadowserver also notes that it sees roughly 38,000 CWP instances exposed to the internet daily. According to CloudSEK, a Shodan query has revealed the existence of over 400,000 servers.

Patches for CVE-2022-44877 were included in CWP7 version 0.9.8.1147. CWP users are advised to update to this or a newer version of the management panel as soon as possible.

Related: Cisco Confirms In-the-Wild Exploitation of Two VPN Vulnerabilities

Related: Apple Warns of macOS Kernel Zero-Day Exploitation

Related: Atlassian Expects Confluence App Exploitation After Hardcoded Password Leak

view counter

Ionut Arghire is an international correspondent for SecurityWeek.

Previous Columns by Ionut Arghire:
Tags:

https://www.securityweek.com/exploitation-control-web-panel-vulnerability-starts-after-poc-publication